Cyber Criminals Sharing GPT-4 API Keys for Free – GBHackers – Latest Cyber Security News

0
[ad_1]

Recently, a script kiddie has been banned for sharing the stolen OpenAI API keys with many users on Discord for the r/ChatGPT subreddit.

Developers can seamlessly incorporate OpenAI’s language model, GPT-4, into their applications using API keys.
Oftentimes, developers unintentionally leave their keys embedded in their code, creating an opportunity for account theft that can be exploited with minimal effort.

The individuals who possess the stolen API keys can effectively deploy GPT-4 while accumulating charges for its users under the compromised OpenAI account.

Sharing GPT-4 API Keys for Free

Starting from March or even earlier, a user named “Discodtehe” has been skillfully extracting API keys from the source code shared on Replit, the software collaboration platform.

Discodtehe acquired unauthorized access to a highly valuable OpenAI account, which boasted a usage limit of $150,000.

On r/ChimeraGPT, the individual generously distributed complete unrestricted access to the GPT-4 and GPT-3.5-turbo, leading to a community of over 700 members who promptly accumulated usage charges on compromised accounts. Motherboard report says.

How the hacker obtained entry underscores a significant security concern that paid users of OpenAI should carefully evaluate.

There has been a noticeable surge in the usage of at least one stolen OpenAI API key in the past few days by “Discodtehe.”

Several screenshots were shared, depicting the progressive account usage increase over time. A recent screenshot reveals that the current month’s usage amounts to $1,039.37 out of the total allocation of $150,000.

However, Discodtehe has been extracting vulnerable API keys for extended periods. Discodtehe didn’t stop at scraping tokens; it went a step further.

According to Vice’s findings, in March, Discodtehe openly boasted about their exploit and stated:-

“I recently scraped repl.it and uncovered more than 1000 functional OpenAI API keys. Remarkably, I didn’t even conduct a comprehensive scrape; I roughly examined around half of the results.”

Discord and Reddit cannot trace the existence of “Discodtehe.” But, the cybersecurity analysts stressed the ongoing risk posed by the multitude of exposed API keys.

Stop Advanced Email Threats That Target Your Business Email – Try AI-Powered Email Security


[ad_2]
Source link
Netflix’s Password-Sharing Crackdown a Success

0
[ad_1]

Despite many people being vocal about cancelling Netflix after the password-sharing crackdown started in the US, it appears that the opposite has happened. Many more are signing up for the service, meaning that the password-sharing crackdown is a success for Netflix.

According to a data analytics company, Antenna, Netflix actually saw a huge spike in subscribers signing up for the service, in the four days after it notified users about the new policies on May 23.

Average daily signups rose to 73,000 during this time, which is a 102% increase over Netflix’s previous 60-day average. Antenna also notes that Netflix added 100,000 subscribers on May 26th, and another 100,000 on May 27. That’s more than what Netflix grabbed when the pandemic first started in March and April of 2020.

Netflix used to promote password-sharing, now it’s charging you extra for it

For years, before streaming really got as popular as it is now, Netflix used to tout how great password-sharing was. However, now it has realized that it is costing them billions a year. So the new policy for Netflix is that users will need to pay $7.99 per month for any user that lives outside of your household. That’s basically an entirely new Netflix subscription added to your account.

After announcing this, Netflix did warn investors about a “cancel reaction”. But so far, it looks like it’s the opposite. Now this could just be those that were sharing passwords, signing up for Netflix on their own, or just signing up for free trials. On the flip side, we also don’t know how many people cancelled Netflix during this time. So while it sounds like good news, it could turn out that more people cancelled than signed up.

Either way, it does look like it’s a good move for Netflix, even if the majority of us disagree with this move.


[ad_2]
Source link

YouTube TV has a new, smaller discount for NFL Sunday Ticket

0
[ad_1]

Ahead of NFL Sunday Ticket launching on YouTube TV and YouTube Primetime Channels later this year, Google has launched a new discount for those that sign up now.

Previously, you could get $100 off of your first year of NFL Sunday Ticket. Now, it’s just $50 off. Still a nice discount, but not quite as nice as it used to be. This new discount will be available until September 19.

Here’s what the new pricing looks like with this $50 discount:

  • NFL Sunday Ticket on YouTube TV – $299
  • NFL Sunday Ticket + RedZone on YouTube TV – $339
  • NFL Sunday Ticket in YouTube Primetime Channels – $399
  • NFL Sunday Ticket + RedZone in YouTube Primetime Channels – $439

Why is NFL Sunday Ticket so expensive?

NFL Sunday Ticket is the most expensive sports streaming service out there, and it’s easy to explain why. With NFL Sunday Ticket, you get every single NFL game, in the pre-season, regular season and post-season. There’s no blackouts, which itself explains the pricing.

But because of the deals that the NFL has in place with CBS and FOX for broadcasting the games, the NFL has to price local games even higher. And since NFL Sunday Ticket does offer every single NFL game, it means that it has to be a lot more expensive.

By contrast, something like MLB.TV is only $149 for the season. But the big caveat here is that there are blackouts for local games. So if you live in the San Francisco area, you can’t watch the Giants games on MLB.TV. That’s where NFL Sunday Ticket comes out on top. And is more than twice as expensive, for many fewer games.

For football fans, NFL Sunday Ticket moving to YouTube is a big deal. Now you don’t need to have a big old satellite dish on your roof for it. Nor do you even need to pay for cable TV. Since you can get it with and without YouTube TV. Obviously, it’s cheaper with YouTube TV, but if you don’t want to watch cable TV, then it’s smarter to get it with YouTube Primetime Channels.


[ad_2]
Source link

Update Chrome now! Google patches actively exploited zero-day

0
[ad_1]

Google has released a Chrome update for a zero-day for which an exploit is actively being used in the wild.

Google has released an update which includes two security fixes. One of these security fixes is for a zero-day about which Google says it’s aware that an exploit for this vulnerability exists in the wild.

How to protect yourself

If you’re a Chrome user on Windows, Mac, or Linux, you should update as soon as possible. Android users will also find an update waiting.

The easiest way to update Chrome is to allow it to update automatically, which basically uses the same method as outlined below but does not require your attention. But you can end up lagging behind if you never close the browser or if something goes wrong—such as an extension stopping you from updating the browser.

So, it doesn’t hurt to check now and then. And now would be a good time, given the severity of the vulnerabilities in this batch. My preferred method is to have Chrome open the page chrome://settings/help which you can also find by clicking Settings > About Chrome.

If there is an update available, Chrome will notify you and start downloading it. Then all you have to do is relaunch the browser in order for the update to complete.

screenshot of up to date ChromeChrome is up to date

After the update the version should be 114.0.5735.106 for Mac and Linux, and 114.0.5735.110 for Windows, or later.

Zero day

Google never gives out a lot of information about vulnerabilities, for obvious reasons. Access to bug details and links may be kept restricted until a majority of users are updated with a fix. However, from the update page we can learn a few things.

The vulnerability was reported by Clément Lecigne of Google’s Threat Analysis Group. This could indicate that Google found this vulnerability while researching an active attack, which matches the fact that an exploit for the vulnerability exists in the wild.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The CVE for the zero-day is:

CVE-2023-3079: a type confusion in V8 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page.

Type confusion vulnerabilities are programming flaws that happen when a piece of code doesn’t verify the type of object that is passed to it before using it. Type confusion can allow an attacker to feed function pointers or data into the wrong piece of code. In some cases, this can lead to code execution.

In other cases, type confusion vulnerability leads to an arbitrary heap write, or heap spray. Heap spraying is a method typically used in exploits that places large amounts of code in a memory location that the attacker expects to be read. Usually, these bits of code point to the start of the actual code that the exploit wants to run in order to compromise the system that is under attack.

At the heart of every modern web browser sits a JavaScript interpreter, a component that does much of the heavy lifting for interactive web apps. In Chrome, that interpreter is V8.

An attacker can exploit this vulnerability by using a specially crafted piece of HyperText Markup Language (HTML). It needs user interaction, which could be easier than it sounds. HTML is the standard markup language for documents designed to be displayed in a web browser and these documents (webpages) can contain JavaScript. Potentially this means that by opening the wrong website, which contains such a specially crafted JavaScript, the browser could be compromised.

Users of other Chromium based browsers, like Edge, should be on the lookout for updates as well, as this one is likely to affect all Chromium based browsers.


We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using Malwarebytes Vulnerability and Patch Management.


[ad_2]
Source link

Sony Xperia Pro-I II may include two 1-inch camera sensors

0
[ad_1]

It has been about a year and a half since the Sony Xperia Pro-I handset arrived. It’s about time for the second-gen model to show itself. Well, the first rumors regarding the device just surfaced. According to this info, the Sony Xperia Pro-I II could include two 1-inch camera sensors.

The Sony Xperia Pro-I II may end up including two 1-inch camera sensors

So, what’s going on? Well, a sketch of the Sony Xperia Pro I II surfaced, along with some concept renders based on that sketch. We cannot confirm this sketch is valid, though, so take this info with a grain of salt.

Sony Xperia Pro I II sketch 1

As you can see in the sketch, there are two large camera sensors on the back. The original Sony Xperia Pro-I did have a 1-inch camera on the back, but that camera was not made for smartphones.

Today, we have the Sony IMX989 1-inch camera sensor, specifically made for smartphones. The rumors claim that the Sony Xperia Pro-I II will include two 1-inch camera sensors. This is just a wild rumor at this point.

Will Sony use two IMX989 sensors, or…?

Sony could opt to include two IMX989 units here, or something else entirely. The company actually created a brand new camera sensor for the Xperia 1 V, so we wouldn’t be surprised if something else ends up being used in the Xperia Pro-I II.

Now, the rumors also claim that the phone will be equipped with a “double-layer transistor stacked pixel sensor”. Sony could actually utilize the largest sensor(s) to date in this phone. We’ll have to wait and see.

You can check out the renders based on the sketch above in the gallery that follows. These are not leaked renders or anything of the sort, so keep that in mind.

We still don’t know when will this phone launch. If Sony intends to stay in line with the Xperia Pro-I launch timeframe, however, you can expect it to arrive in October. The first-gen model launched on October 26, 2021.


[ad_2]
Source link

Apple makes Skiff the default encrypted email service for iOS

0
[ad_1]

In this day and age, where hackers are constantly finding new ways to infiltrate your device and gain unauthorized access, finding secure communication channels has become a top priority. And although there are many encrypted messaging apps and VPNs available on the internet, none of them come close to providing that default experience. Now, in an effort to solve this issue, Apple is making Skiff, an encrypted email service, one of the default emailing options on all iOS devices.

What is Skiff?

Founded by Andrew Milich (CEO) and Jason Ginsberg (CTO) in 2020, Skiff aims to make privacy protection accessible to all users without requiring the technical expertise of setting up a secure firewall or VPN. The company operates on a zero-trust privacy approach, ensuring that it neither stores nor collects any sensitive user information, including location data. Moreover, all communications on the platform are end-to-end encrypted and open-sourced, enabling independent audits and ensuring transparency.

“We firmly believe that protecting your privacy online should be effortless rather than a privilege limited to the tech-savvy or cryptography experts,” said CEO Andrew Milich.

How did Skiff become the default mail app for Apple?

While it may seem like becoming the default email app for Apple was straightforward considering Skiff’s features, the real journey involved over a year of continuous product improvements, including enhanced offline support, secure sign-in options, and seamless compatibility with all email links on iOS. These efforts ultimately caught the attention of Apple, and its inclusion will be a significant step forward in making secure email services more accessible to the general public.

“We are thrilled that Apple has made privacy a key priority and has worked with us to seamlessly integrate end-to-end encrypted email with iOS,” said Milich.

Finally, for those users who want to make Skiff their default email app, the process is quite simple. Just go to the App Store, download the Skiff Mail app on your iOS device, and navigate to Settings > Skiff Mail to set it as the default choice.


[ad_2]
Source link

Victims’ faces placed on explicit images in sextortion scam

0
[ad_1]

We take a look at some new developments in sextortion cases via a warning issued by the FBI.

The FBI has issued a warning about criminals digitally manipulating people’s faces on to pornographic images—known as deepfaking—and then using those images to harass or extort money out of their victim in a practice known as sextortion.

The FBI said the victims include children. From the release:

The FBI continues to receive reports from victims, including minor children and non-consenting adults, whose photos or videos were altered into explicit content. The photos or videos are then publicly circulated on social media or pornographic websites, for the purpose of harassing victims or sextortion schemes.

To hear that children are now being inserted into deepfake creations is horrifying, though perhaps unsurprising. The way these attacks work is that potential victims are contacted through a variety of methods, most commonly by instant messaging apps. Here’s how the FBI describes sextortion:

Sextortion, which may violate several federal criminal statutes, involves coercing victims into providing sexually explicit photos or videos of themselves, then threatening to share them publicly or with the victim’s family and friends. The key motivators for this are a desire for more illicit content, financial gain, or to bully and harass others. Malicious actors have used manipulated photos or videos with the purpose of extorting victims for ransom or to gain compliance for other demands (e.g., sending nude photos).

There’s a few different ways sextortion attacks can play out. One of the most basic forms is sending emails to people whose login details have been exposed in a password breach. The email claims to have nude photographs of the recipient, and threaten to release the photos unless the recipient pays up. There are no images, it’s all a lie. 

The more traditional form of sextortion is where a fraudster convinces the person they’re speaking to that they’re interested in romance, obtains revealing images of the victim, and then uses those images for blackmail. The victim is asked to pay money, often wired or through digital currency, or else the images will be sent to the victim’s friends and family. As it’s usually easy to build up a picture of someone’s network on social media like Facebook and Twitter, the pressure may well be too much for the person on the receiving end of such a scam.

That’s how it usually works. With deepfakes on the scene, a lot of the pre-scam work can simply be discarded. Now fraudsters go and grab some photos of their target, and feed those images into their faking tool of choice. All of that social engineering, the possibility of the victim not falling for it and sending revealing images is completely done away with. Why bother, when you can just swipe a photograph and press a few buttons?

The end result is the same. In fact, it’s arguably much worse as the pornographic movie creations thrown together by these tools are almost always a lot more graphic than anything a target would probably come up with. The pressure to pay up is going to be immense, and realistically non-internet savvy relatives or friends may not have even heard the word “deepfake” before. What are the chances of them knowing a file landing in their mailbox is fraudulent?

There are several general pieces of advice we can give when talking about the different sextortion tactics which exist:

  • Don’t engage: report. If you’re shown evidence of stolen images, report to your local authorities and the FBI as soon as you can. Never engage with the sextortionist.
  • Be cautious about what you say to someone online. When asked certain questions, be vague and never give specifics.
  • Remember that online, people can pretend to be someone they’re not, and can even look and sound like a different person with today’s technology.
  • Personalize your security and privacy settings. Lock down your accounts as much as you can, and keep as much hidden from public view as possible.
  • Data is typically forever. Remember that once you send something to someone—whether they’re a stranger, a romantic partner, relative, or friend—you have no control over where it goes next.

Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Here’s a first look at Meta’s Twitter competitor app

0
[ad_1]

Back in March, a report surfaced stating that Meta is working on an Instagram-branded Twitter competitor. Well, Meta held an employee preview of that Twitter alternative app, and screenshots surfaced, giving us a first look at the app itself.

Take a first look at Meta’s Twitter competitor app

The internal name for this app is ‘Project 92’, while the official name could be ‘Threads’. Now, the screenshots that surfaced are included below this paragraph, in case you’d like to take a peek.

Meta Twitter competitor app screenshots

If it looks familiar, there’s a good reason for it. It basically looks like Instagram’s UI, but without images. So, what’s this app all about? Well, it seems like Meta noticed an opportunity when Elon Musk took over Twitter, and it’ll try to compete directly with the service.

According to Chris Cox, who is Meta’s Chief Product Officer (CPO), this app will utilize the ActivityPub social networking protocol. In other words, it’ll allow users to migrate their Instagram accounts and followers to the new platform.

If you decide to use this app, your Instagram account info will be there for you

Mr. Cox also flat out said that this app will be “our [Meta’s] response to Twitter”. If you switch, your Instagram account info will be there, waiting for you.

Based on reports, Meta is currently in talks with a number of celebrities to start using the platform. Those people include Oprah Winfrey, Dalai Lama, DJ Lime, and so on.

Meta started developing this app back in January, and it’s expected to launch it in the near future. Meta, of course, wants to do it as soon as possible, but it also wants to offer a compelling product.

Twitter has been criticized left and right since Elon Musk took over, for its actions. It has also been praised in some ways, but one thing is for sure, it has been at the center of attention. It will be interesting to see if Meta can actually launch a compelling Twitter alternative and lure users.


[ad_2]
Source link

Apple Vision Pro Zeiss lens inserts might be $300

0
[ad_1]

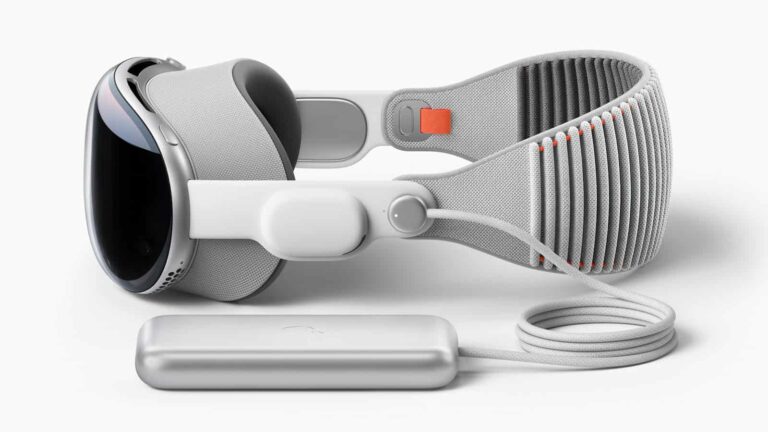
When Apple announced the Vision Pro headset during WWDC23, it also announced a pair of Zeiss vision correction inserts that could slot into each eye of the headset over the displays.

These magnetically attach to the inside of the headset and can easily be taken out when not needed. Say for example, when someone else who doesn’t need vision correction wants to use the headset. As the lenses are made by Zeiss and they’re for an Apple product, they probably won’t be anywhere near inexpensive. Apple didn’t officially announce pricing but that doesn’t mean there isn’t a potential range.

A tweet from Bloomberg’s Mark Gurman suggests that Apple could charge anywhere from $300 to $600 per pair for the Zeiss vision correction inserts. Turning an already expensive product into a setup that could end up costing more than some high-end gaming PCs. And that’s before you factor in the price of any other potential accessories, as well as taxes and fees.

Apple Vision Pro Zeiss inserts will be necessary for some users

Chances are if you’re willing to spend $3,499 on an AR/VR headset, you’re probably willing to spend the extra $300-$600 you might need for these Zeiss inserts. But that won’t necessarily apply to every user. Surely there will be some that either can’t or would prefer not to spend that extra money.

But for people where vision correction lenses would be necessary, the only option would be to not buy the headset. At least if they couldn’t spend the extra money on the lens inserts. More to the point, if these prices are accurate it really puts into perspective how much this setup will cost.

At minimum you’re looking at $3,799. And at most you’re looking $3,999. Assuming you aren’t counting the tax or any extra money for additional add-ons. All that being said, eventually, these prices are likely to go down. Even if it might be a while.


[ad_2]
Source link

Key role targeted cyber attacks are on the rise

0
[ad_1]

Research by Ponemon Institute and cyber security company BlackCloak has found that hackers have been directly targeting C-suite executives and their family members with cyber attacks via their personal email addresses. 

In Understanding the serious risks to executives’ personal cybersecurity and digital lives, which was released on June 5, researchers found that 42 percent of organizations said that an executive or an executive’s family member had been the direct target of a cyber attack. This targeted threat vector is also referred to as key employee/role targeting. 

Cyber Security Hub research has found that more than one in four (26 percent) cyber security professionals believe that key employee/role targeting will have the biggest impact on cyber security in 2023.

The Ponemon Institute and BlackCloak institution found that executives and their families are targeted with a number of threat vectors including social engineering-, malware– and network infiltration-based attacks.

Chris Pierson, founder and CEO of BlackCloak, explained to cyber security news site Cybersecurity Dive that “cybercriminals have realized that most executives are almost completely unprotected outside of their corporate accounts and devices”, meaning that they are particularly vulnerable to these attacks. 

The research also found that this issue represents a significant part of cyber security employee’s roles. On a scale from one to ten, where ten represents something intensely time-consuming, 35 percent of respondents rated the amount of time they spent on key role targeting as a nine or ten. 

Read more about social engineering attacks in Cyber Security Hub’s guide to this manipulate threat vector. 


[ad_2]
Source link