YouTube is making changes to the audio on videos on your Android TV and Google TV, so you don’t have to keep grabbing the remote to fix the volume. This new feature, called “stable volume”, automatically makes quiet parts louder and loud parts quieter.
If you’re watching YouTube on your TV, you might have noticed that some videos are louder than others. Maybe you’re watching a video and someone is whispering, so you turn up the volume. Then the next video starts, and it’s super loud, then you have to scramble to quickly turn the volume back down. It can be a pain, and it’s not great for your ears.
However, YouTube is looking to fix this problem by adding “stable volume” to the YouTube app. With stable volume turned on, you shouldn’t have to adjust the volume as much as YouTube will do it for you. The feature tries to keep all the audio at a similar level, so you won’t be surprised by sudden loud noises or struggle to hear quiet parts.
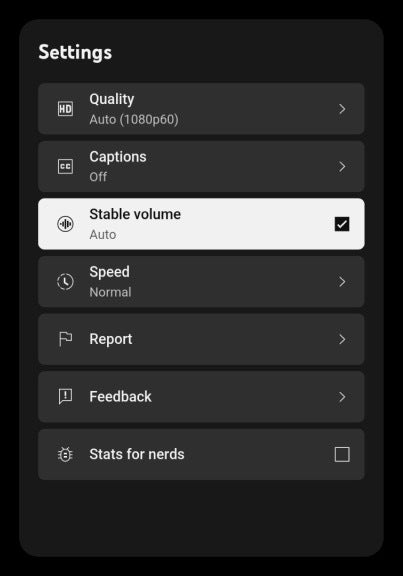
The “stable volume” feature can be accessed by playing a video on YouTube, and then tapping on the gear icon. You should then see a toggle for stable volume, which is turned on by default. However, if you prefer to have your volume settings as you had them before, you can always turn the feature off.
Google and Android TV audio settings with “stable volume” turned on | Image credit — 9to5Google
Stable volume isn’t exactly a new feature, as it has been available on the mobile version of YouTube for some time now. However, it is new on the smart TV version of YouTube, and as such, it might not be perfect. For example, it might not work well with music videos or videos that have a lot of different sounds. If you’re a music lover, you might not like how stable volume changes the way music sounds.
That said, for most people, stable volume should be helpful. If you’re tired of constantly adjusting the volume on your TV, you might want to give it a try in the latest YouTube v4.40.303 version on your Google or Android TV.
Cybersecurity firm Resecurity reports that cybercriminals are selling stolen digital identities of Singaporeans on the Dark Web with prices starting at $8. Researchers found numerous instances of stolen identity information on Dark Web and underground cyber crime platforms, including the leading Russian language marketplace for stolen identities ‘XSS’.
Researchers noted that the number of underground vendors selling stolen identity data of Singapore citizens in 2024 Q2 has increased by 230% compared to 2023. The spike was identified by metrics like the sudden increment in the mentions of “Singpass” (Singapore Personal Access) on the Dark Web.
“Our statistics show that starting from April 15th, 2024, we have registered a significant increase in data dumps with a significant number of records (from 10,000 and more) being offered by multiple actors this month.”
Resecurity
As per Rsecurity’s report shared with Hackread.com ahead of publishing on Monday, throughout Q1/Q2 2024, infostealers and social engineering techniques remained a key cause of Singpass accounts compromise, which can be exploited for money laundering. In June 2024, Resecurity recovered over 2,377 compromised Singpass accounts from the Dark Web and notified affected individuals.
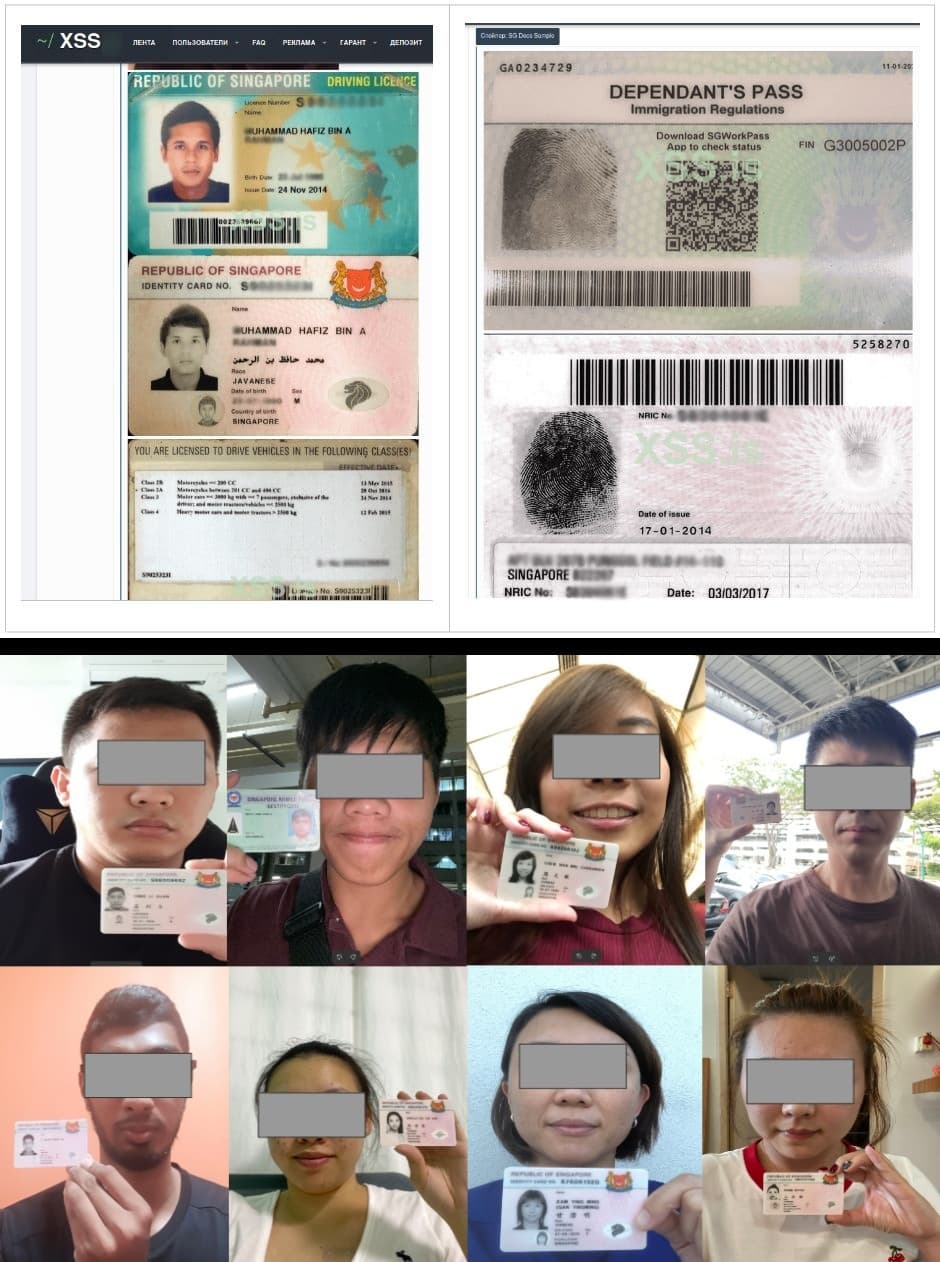
Screenshot from the data being sold (Credit: Rsecurity)
Between October 2023 and June 2024, several underground vendors monetized stolen identity data, including passports, identity cards (IC), and sanitized driving licenses. Moreover, cybercriminals are selling national ID templates for Know Your Customer (KYC) purposes (passports, driving licenses, utility bills and banking statements), and offering services to create forged documents, verify accounts, and pass KYC checks.
This suggests undisclosed data breaches affecting Singapore citizens, leading to a surge in leaked KYC documents, primarily involving selfies, which the Singaporean government requires for verification purposes.
Additionally, these Dark web platforms are selling compromised access to sensitive data from critical sectors such as healthcare, lending, e-commerce, and financial platforms. However, these malicious attacks do not end there. Researchers have also found evidence of several scam groups targeting citizens through telemarketing or customer support services.
It is concerning that the stolen data includes biometric information such as fingerprints and facial data, which can be illegally reused for forged documents, access manipulation, and other malicious scenarios by cybercriminals. Using Deep Fakes and AI-powered techniques, nation-state and foreign actors will need this data for intelligence gathering and infiltration activities.
Compromised digital identities expose Singaporeans to risks like financial loss, identity theft, and reputational damage. It is, therefore, crucial they are cautious of phishing attempts, use multi-factor authentication (MFA), and stay informed on the latest cybersecurity threats.
Webkit vulnerabilities in PS4 and PS5 refer to bugs found in the Webkit engine used by their web browsers.
These bugs, discovered in browsers like Safari and Chrome, can also exist in PS4 and PS5 because they share the same Webkit codebase.
While a Webkit bug alone isn’t enough for a jailbreak, it can be a crucial first step, and exploiting such a vulnerability along with a kernel exploit (giving more system access) can potentially lead to a PS4/PS5 jailbreak.
The PPPwn exploit alone is not sufficient for a PS5 jailbreak due to the console’s strong security mitigations. A usermode exploit is likely needed in conjunction with PPPwn for a workable PS5 exploit.
While PPPwn is triggered during an internet connection, Webkit exploits run in the web browser, making it challenging to exploit them sequentially.
However, Webkit exploits are generally positive signs for the PS5 hacking scene as they potentially offer avenues for future exploits.
Attackers were able to take advantage of a recently patched Safari/WebKit vulnerability by exploiting a JavaScript engine assumption, and certain properties, like prototypes, are unconfigurable.
The bug enabled them to be configured, essentially creating type confusion.
By manipulating this, attackers could gain access to properties that should be inaccessible, potentially through the Spread opcode used in the analysis phase.
This highlights the danger of unexpected side effects when assumptions about data types are broken.
confusion vulnerability code snippet
The code crafts a scenario for a potential type of confusion vulnerability.
By inheriting from `Function`, the `Base` class gains access to the built-in `prototype` property, and assigning a number to `super.prototype` during construction might corrupt the prototype chain.
A getter is defined on a non-existent `arr` variable to manipulate `victim [1]` when the `prototype` getter is called, which, combined with a large loop manipulating `victim` elements and a final type conversion using a potentially attacker-controlled ‘flag’, creates an environment where writing to `arr[0]` could overwrite the `prototype` of another object with the value of `victim [1]`, potentially leading to unexpected behavior.
firmware impacted by the vulnerability.
A potential Webkit vulnerability is reported to be affecting PS4 and PS5 consoles.
Users can see if their devices are susceptible by testing a specific URL through the console’s browser with DNS redirection.
According to Wolo, the test exploits the vulnerability by feeding a malicious webpage that triggers an “Out of Memory” or “Not enough system memory” error message, indicating a successful exploit on PS4 firmware versions 10.00 to 11.02 and PS5 firmware versions 6.00 to 8.60.
FreeWebinar! 3 Security Trends to Maximize MSP Growth -> Register For Free
Last week, a reliable industry insider said that Samsung’s Galaxy S25 series may ship with a Snapdragon chip globally. There may not be an Exynos version of any model anywhere. Another source has now suggested the same, though it says the Korean firm is trying hard not to do that. It is desperate to keep a dual-chip strategy for its next flagships.
Samsung is racing against time to make an Exynos chip for the Galaxy S25
Last year’s Galaxy S23 series was Samsung‘s first and only S-series flagship lineup to lack an Exynos version. The company shipped the phones with the Snapdragon 8 Gen 2 globally. This year, it used the Snapdragon 8 Gen 3 in the Galaxy S24 Ultra globally but sold the other two models with the Exynos 2400 in some markets, including Europe.
Samsung was presumed to do the same with the Galaxy S25 series, selling the new flagships in Snapdragon and Exynos versions depending on the market. However, renowned analyst Ming-Chi Kuo recently said that the company is struggling with the yield of the Exynos 2500, leaving it no other option but to ship the Galaxy S25 trio with Qualcomm’s Snapdragon 8 Gen 4 globally.
A new report from ZDNet Korea validates Samsung’s yield issues. According to the publication, the yield rate of the Exynos 2500 was in single digits in the first quarter of 2024. The company improved the yield in the second quarter but it is still hovering under 20%. In simpler terms, Samsung is producing only 20 usable chips from a possible 100, which is a massive production waste.
The report adds that Samsung must achieve at least a 60% yield rate for the Exynos 2500 to enter mass production. More importantly, it must do that by the end of the third quarter or in the early fourth quarter, i.e., between September and October. If the yield remains low, the company will have to exclusively use the next-gen Snapdragon chip in the Galaxy S25 series.
The switch to GAA architecture may be giving Samsung problems
The Exynos 2500 is a 3nm chip. Samsung is employing the more advanced GAA transistor architecture for its new process node. It appears this switch is giving the company problems. TSMC, which will produce the Snapdragon 8 Gen 4 on its 3nm process, is sticking to the FinFET architecture. If Samsung fails to introduce Exynos 2500 to the Galaxy S25 series, it might bemoan the GAA upgrade.
That said, the Korean tech titan still has 3-4 months in hand. It might be enough to turn the tide and release an Exynos version of its next flagship. Fans may not be happy about it, though. Exynos chips have troubled Galaxy users too much for them to trust it anymore, even if early leaks hint at huge improvements. We should get a clearer picture of Samsung’s situation in a few months.
A new method of distributing the Remcos Remote Access Trojan (RAT) has been identified.
This malware, known for providing attackers complete control over infected systems, is being spread through malicious Word documents containing shortened URLs.
These URLs lead to the download of the Remcos RAT, which can be used for data theft, espionage, and other malicious activities.
Understanding the infection chain and recognizing the signs of such attacks is crucial for mitigating these threats.
Infection Chain Analysis
According to the Forcepoint blogs, the attack begins with an email containing a .docx attachment designed to deceive the recipient.
Upon examining this file, a shortened URL is found, indicating malicious intent. This URL redirects to download a variant of the Equation Editor malware in RTF format.
By exploiting the Equation Editor vulnerability (CVE-2017-11882), the malware attempts to download a VB script composed of a lengthy sequence of concatenated variables and strings, likely encoded or obfuscated.
These strings form an encoded payload, which may be decoded or executed later in the script.
The VB script deobfuscates to PowerShell code that tries to download a malicious binary via a steganographic image and reverse Base64 encoded strings.
Although a command and control (C2) call is made, there’s also a TCP reconnect, suggesting that the C2 might be unavailable.
Passive DNS analysis identified the C2 domains, but they are currently inactive.
Detailed Breakdown of the Attack
The document (SHA1: f1d760423da2245150a931371af474dda519b6c9) contains two critical files: settings.xml.rels and document.xml.rels located at word/_rels/.
The settings.xml.rels file reveals a shortened URL responsible for downloading the next stage of the infection:
Running the .docx file in a sandbox environment reveals it contains the CVE-2017-0199 vulnerability.
Upon exploiting this vulnerability, the document attempts to connect to a remote server to download a malicious file.
The attacker uses a URL shortener service to mask the malicious URL, making it difficult for the victim to recognize the risk and helping bypass security filters that might flag suspicious URLs.
Further investigation into the \word\embeddings folder reveals embedded PDF files within oleObject bin files.
The PDF file appears benign, showing a bank transaction between a company and a bank. However, the real threat lies in the RTF file (SHA1: 539deaf1e61fb54fb998c54ca5791d2d4b83b58c) downloaded via the shortened URL.
This file exploits the Equation Editor vulnerability to download a VB script (SHA1: 9740c008e7e7eef31644ebddf99452a014fc87b4).
Obfuscation and Payload Delivery
The VB script is a long string of concatenated variables and strings, potentially encoded or obfuscated data.
The important variable, “remercear,” is constructed by repeatedly concatenating various string literals, suggesting it holds encoded information or commands.
After deobfuscation, the PowerShell code attempts to download a malicious binary from two different URLs.
The first URL uses steganography to hide the malware within an image:Steganographic Image
The image contains a long Base64-encoded string, the first six bytes of which decode to ‘MZ’, indicating the presence of a Windows executable.
The second URL communicates with an IP address to retrieve a TXT file containing a reverse Base64 encoded string.
This adds a layer of obfuscation, evading simple detection mechanisms.
Using tools like Cyber Chef, the string is reversed, and Base64 is decoded to reveal the malicious payload (SHA1: 83505673169efb06ab3b99d525ce51b126bd2009).
Monitoring the processes reveals a connection to a potential C2 server (IP: 94[.]156[.]66[.]67:2409), which is currently down, resulting in a TCP reconnect.
The use of shortened URLs in Word documents to distribute the Remcos RAT highlights the evolving tactics of cybercriminals.
By understanding the infection chain and recognizing the signs of such attacks, individuals and organizations can better protect themselves against these threats.
Always be cautious of unsolicited emails with attachments, and avoid clicking on shortened URLs from unknown sources.
Samsung may announce the date for its next Unpacked tomorrow, June 26. Multiple leaks say the company will open pre-reservations for the Galaxy Z Fold 6 and Galaxy Z Flip 6 this Wednesday. It usually starts accepting pre-reservations for new flagships or foldables immediately after announcing the Unpacked date. The announcement also usually comes two weeks before the event, and June 26 falls exactly two weeks before the rumored July 10 date for the next Unpacked.
Samsung to open Galaxy Z Fold 6 and Flip 6 pre-reservations before Unpacked
Since February, we have only heard one date for Samsung’s next Unpacked—July 10. The company is allegedly taking the big launch event to Paris, France to commemorate its sponsorship ties with the Olympic Games (this year’s sporting event is taking place in Paris). The Unpacked will happen around two weeks before the Olympics begin on July 26. This ensures the new products go on sale just when the games begin, allowing Samsung to promote them to the masses.
As the Unpacked draws closer, the company has ramped up its preparations for the arrival of the new foldables and other products. Folks over at SamMobile recently received a message from a Samsung Experience Store in India saying that they can pre-reserve the Galaxy Z Fold 6 and Galaxy Z Flip 6 starting on June 26, 2024. The message didn’t explicitly name the unannounced foldables for obvious reasons but used the codenames Q6 and B6 that leaks have revealed before.
X user @tarunvats33, who has a decent track record of Samsung leaks, also confirmed separately that pre-reservations for the Galaxy Z Fold 6 and Galaxy Z Flip 6 will open in India on June 26. He also shared a poster but it looks fake. In the image below, see how there is no space between “Fold” and “6” but some space between “Flip” and “6”. The poster also lacks a hyphen (-) joining “Pre” and “Reserve”. That’s not to say the reported date may be fake too.
An official announcement may come anytime now
As said earlier, Samsung’s flagship and foldable pre-reservations usually coincide with its official Unpacked announcement. It announced the Galaxy S24’s Unpacked on January 3, exactly two weeks before the event on January 17 (both on a Wednesday). June 26 falls on a Wednesday, and so does July 10 exactly two weeks later. Joining the dots, the Korean firm may announce its next Unpacked tomorrow. Alongside the new foldables, the event should also bring new watches, wireless earbuds, and the Galaxy Ring.
Internet research firm Ookla’s latest test report reveals that T-Mobile’s 5G services are still the fastest in the US. Thanks to the additional 2.5GHz spectrum, the telco’s median download performance on 5G networks has increased by nearly 30Mbps. The most noticeable change in T-Mobile’s 5G services after the allocation of the new spectrum is seen in the rural areas of the nation.
T-Mobile’s 5G services were fastest in March at 287.14Mbps
According to Ookla’s latest intelligence report, T-Mobile’s 5G services were the fastest in the US in March 2024. The carrier managed to achieve a median download speed of 287.14Mbps on its 5G networks. The company’s download speeds increased by 29.64Mbps within a month after the deployment of the additional 2.5GHz 5G spectrum. While the telco’s download speeds dropped to 275.50Mbps in May, it’s still the fastest 5G provider in the US.
Furthermore, the report suggests that 5G services of all telecom operators, especially T-Mobile, have seen a boost in rural areas. As per the data, the company added more download speeds in these regions thanks to the recent mid-band spectrum deployments. T-Mobile put the 2.5GHz mid-band spectrum to good use. It finally received the additional spectrum from the FCC after the 5G SALE Act was signed by President Biden in December 2023.
Verizon and AT&T’s 5G download speeds were 224.67Mbps and 145.36Mbps, respectively
Verizon took second spot on Ookla’s test results by offering a maximum download speed of 224.67Mbps in March. The company provided 22 percent slower 5G services than the market leader T-Mobile. As for AT&T, it lagged far behind in March with the median 5G download speeds of 145.36Mbps.
Verizon was also able to put its C-band mid-range 5G spectrum to good use which it purchased a few years ago. The additional spectrum allowed the company to play catch-up with T-Mobile in Q4 2023. Verizon was also able to boost its 5G performance in rural areas. AT&T unfortunately only saw a minor boost in median 5G download speeds in rural regions across the nation.
The report indicates that all telecom carriers in the US are prioritizing improvements in the 5G download performance. It will likely continue throughout the year. After stabilizing their download speeds, the telcos are expected to focus on maintaining latency and offering higher upload speeds as well.
The ability to seamlessly stream content from your personal devices to hotel TVs is about to get a whole lot easier. LG, in partnership with SONIFI, a leading provider of hospitality technology, is set to roll out Google Cast support to over half a million hotel rooms by this fall. This means that guests can easily cast their favorite shows, movies, and music from their phones, tablets, or laptops directly to their in-room LG TV, regardless of whether they use Android, iOS, Windows, ChromeOS, or macOS.Google Cast, previously known as Chromecast, has long been a popular way to connect devices to TVs at home. However, its availability in hotel rooms has been limited. This new initiative aims to change that by making it a standard feature in LG-equipped hotel rooms worldwide. The technology works by allowing users to “cast” or mirror the content from compatible apps and websites directly onto the TV screen.The implementation will be integrated with SONIFI’s existing STAYCAST platform, which already allows guests to sign in to their streaming accounts on the TV and automatically logs them out at the end of their stay. This ensures a secure and convenient experience for guests while also maintaining privacy. To this, Michael Kosla, Senior Vice President at LG Business Solutions USA, said:
With embedded casting, it’s one less device to install, configure, manage and monitor in the guest room, creating operational efficiencies for hotels and a convenient amenity for guests.
The partnership between LG and SONIFI is a significant step towards making hotel rooms more user-friendly and personalized. By allowing guests to access their preferred content on the big screen, it enhances the overall entertainment experience during their stay. Kara Heermans, SONIFI’s Senior Vice President of User Experience and Product Management, said the below regarding this collaboration:
We’re excited to launch a simple casting deployment option with the security, reliability, and ease of use hotels and guests expect. It’s a great experience for staff and guests alike, who still get 24/7 support from SONIFI, just like with STAYCAST today.
With the rollout planned for this fall, travelers can soon expect to find Google Cast readily available in a wide range of hotels. This move by LG and SONIFI is not only a win for guests but also for hotels, as it provides a valuable amenity that can attract and retain customers. I know as a traveler, I’ll be really thankful to be able to stream my favorite shows and movies and not beholden to whatever is currently playing on cable TV.
Attackers are leveraging a new infection technique called GrimResource that exploits MSC files.
By crafting malicious MSC files, they can achieve full code execution within the context of mmc.exe (Microsoft Management Console) upon a user click.
It offers several advantages for attackers by bypassing the need for macros (disabled by default) and providing low-security warnings, making it ideal for gaining initial access while evading detection.
The first GrimResource sample was uploaded to VirusTotal in early June, highlighting a potentially emerging threat.
Reference to apds.dll redirect in StringTable
A novel attack technique, GrimResource, exploits an unpatched XSS vulnerability in apds.dll to achieve initial access and code execution on Windows systems, where attackers craft malicious MMC files containing references to the vulnerable APDS resource in the StringTable.
This triggers arbitrary JavaScript execution within the context of mmc.xe, and by abusing DotNetToJScript functionality, attackers further escalate privileges to arbitrary code execution.
The attack chain uses a transformNode obfuscation technique to circumvent ActiveX security warnings, followed by an obfuscated VBScript that sets the target payload in environment variables.
A custom.NET loader named PASTALOADER leverages these variables to inject the final payload (e.g., Cobalt Strike) into a newly spawned dllhost.exe process using a combination of DirtyCLR, function unhooking, and indirect syscalls for stealth.
Payload injected into dllhost.exe
An existing detection for suspicious execution via Microsoft Common Console (MSC) files was designed to catch a different technique involving the Console Taskpads attribute.
It looks for a specific pattern in process creation: a child process spawned by a parent mmc.exe process that launched an MSC file with a wildcard argument but didn’t match known legitimate MMC file locations or whitelisted executables.
GrimResource detected
An attacker can exploit the.NET COM object functionality through a non-standard Windows Script Interpreter (WSH) script engine called DotNetToJScript, which utilizes a trusted process to allocate executable memory (RWX) on behalf of a malicious VBScript or JScript script.
The detection relies on identifying this abnormal memory allocation pattern along with the call stack involving specific DLLs (mscoree.dll, combase.dll, jscript.dll, vbscript.dll, jscript9.dll, and chakra.dll) that link the.NET process to the WSH script engine.
Monitoring for suspicious file open events (apds.dll) by mmc.exe can expose attempts to execute scripts through the MMC console.
apds.dll being invoked in the MSC StringTable
They can leverage MMC console files (MSC files) to execute malicious scripts by exploiting a vulnerability in APDS (Advanced Protocol Detection Service) to redirect the user to a malicious webpage, which creates a temporary HTML file (redirect.html) in the user’s INetCache folder.
The Elastic security team can spot this attack by connecting events like the MMC process beginning with an MSC file and creating a redirect.html file.
YARA rules can be used to find the specific features of the malicious MMC console file.
FreeWebinar! 3 Security Trends to Maximize MSP Growth -> Register For Free
The OnePlus Watch 2R could launch in a couple of days
This information comes from Max Jambor, a well-known tipster. He’s almost never wrong when it comes to OnePlus information, so we have no reason to doubt this either. Just to be clear, the OnePlus Watch 2R name could be used outside of China only. The watch could have a different name in China when it arrived in a couple of days.
The OnePlus Watch 2R, based on its name, could be a cheaper variant of the OnePlus Watch 2. The tipster only said the name of the watch, nothing in addition to that. So keep that in mind.
What will its name in China be? Well, the OnePlus Watch 2 is mentioned. This may confuse many of you, but the OnePlus Watch 2 only launched outside of China, never in OnePlus’ homeland. So, from that point of view, this does make sense. You can check out our OnePlus Watch 2 review if you’re interested.
The new watch will likely have a round display
What we know about this watch is that it will have a circular display and that its body will be made out of metal. That’s basically everything we know about the OnePlus Watch 2R. Its price tag will also be lower than that of the OnePlus Watch 2, though, of course.
In addition to this smartwatch, OnePlus will announce the OnePlus Ace 3 Pro smartphone. A very powerful handset. The OnePlus Pad Pro will also arrive, as will the OnePlus Buds Pro 3 earbuds.