A Great deal for Content Creators

0
[ad_1]

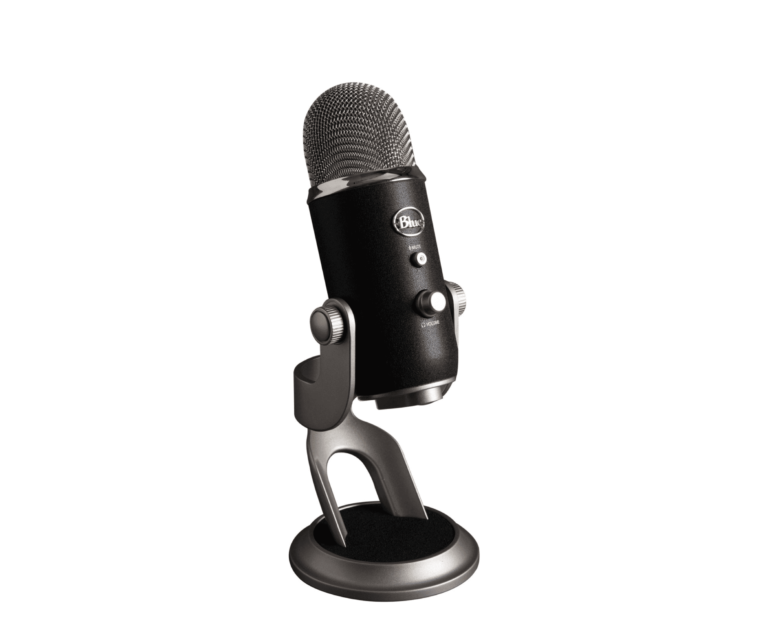
Today, Amazon has a great deal on the Blue Yeti Microphone, dropping the price to just $84.99. That’s down from its regular price of $129.99. So this is a great time to pick one up.

Blue Yeti Microphone – Amazon

Why you should buy the Blue Yeti Microphone

The Blue Yeti Microphone is a versatile and powerful microphone that is perfect for a variety of applications, including podcasting, streaming, voiceovers, and music recording. It is also a great choice for beginners, as it is easy to use and set up.

The Yeti features four different polar patterns, which allow you to record in a variety of settings. The cardioid pattern is best for recording vocals or instruments that are directly in front of the microphone. The omnidirectional pattern picks up sound from all directions, making it ideal for recording group conversations or ambient sounds. The bidirectional pattern picks up sound from both the front and back of the microphone, making it great for recording interviews or duets. The stereo pattern picks up sound from both the left and right sides of the microphone, making it ideal for recording music.

The Yeti also features a built-in headphone jack with zero-latency monitoring, so you can hear yourself as you record. This is a great feature for beginners, as it allows you to make sure that your levels are correct and that you are not clipping.

The Yeti is a high-quality microphone that is built to last. It is made of durable materials and features a sturdy metal stand. The Yeti also comes with a carrying case, so you can take it with you on the go.

If you are looking for a versatile and powerful microphone that is perfect for a variety of applications, then the Blue Yeti Microphone is the perfect choice for you. It is easy to use, sounds great, and is built to last.

Here are some of the benefits of buying the Blue Yeti Microphone:

  • Versatile and powerful microphone that is perfect for a variety of applications
  • Easy to use and set up
  • Features four different polar patterns
  • Built-in headphone jack with zero-latency monitoring
  • High-quality microphone that is built to last

Here are some of the things to consider when buying the Blue Yeti Microphone:

  • The Yeti is a large microphone, so it may not be ideal for everyone
  • The Yeti is not a portable microphone, so you will need to find a place to set it up if you want to use it on the go
  • The Yeti is a bit more expensive than some other microphones on the market

Overall, the Blue Yeti Microphone is a great choice for anyone who is looking for a versatile and powerful microphone that is perfect for a variety of applications. It is easy to use, sounds great, and is built to last. If you are considering buying a new microphone, then the Yeti is definitely worth considering.

Blue Yeti Microphone – Amazon


[ad_2]
Source link

Bruteforce Attack to Bypass User Authentication

0
[ad_1]
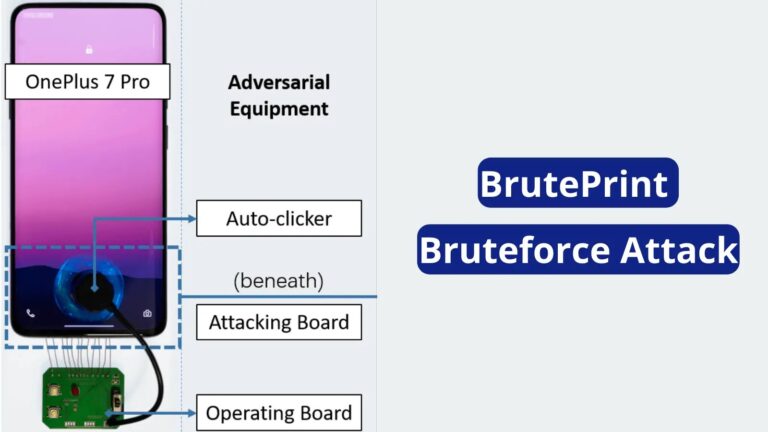
BrutePrint

A novel assault named ‘BrutePrint’ has been unveiled by the joint efforts of Tencent Labs and Zhejiang University researchers, enabling the forceful extraction of fingerprints on contemporary smartphones. 

This method circumvents user authentication, granting unauthorized access and full control over the targeted device.

Chinese researchers successfully bypassed existing security measures on smartphones, such as attempt limits and liveness detection, using two zero-day vulnerabilities, enabling them to perform brute-force attacks and gain unauthorized access to accounts, systems, or networks.

Here below we have mentioned those exploited zero-day vulnerabilities:-

  • Cancel-After-Match-Fail (CAMF)
  • Match-After-Lock (MAL)

BrutePrint Authentication bypass

Furthermore, analysts discovered a concern in protecting biometric data transmitted via the Serial Peripheral Interface (SPI) of fingerprint sensors. 

This inadequacy creates an opportunity for threat actors to perform man-in-the-middle (MITM) attacks, which enables the interception and hijacking of fingerprint images.

A comprehensive assessment was conducted on ten widely used smartphone models to evaluate the effectiveness of both BrutePrint and SPI MITM attacks. 

The results revealed that these attacks successfully allowed unlimited attempts on all Android and HarmonyOS-based devices from Huawei, while iOS devices exhibited a limited vulnerability with an additional ten attempts possible.

The fundamental concept behind BrutePrint involves carrying out an unrestricted sequence of fingerprint image submissions to the targeted device, persisting until a match is found with the user-defined fingerprint, without any imposed limits on the number of attempts.

By obtaining physical access to the target device, accessing a fingerprint database, and using affordable equipment of $15 approximately, attackers can launch a BrutePrint attack, manipulating the False Acceptance Rate (FAR) to increase the acceptance threshold for fingerprint matches and achieve easier unauthorized access.

BrutePrint exploits the CAMF flaw, injecting a checksum error in the fingerprint data, which bypasses protection systems and allows attackers to attempt infinite fingerprint matches on smartphones without being detected.

Exploiting the MAL vulnerability empowers attackers to deduce the authentication outcomes of the fingerprint images they test on the target device, even when the device is in a “lockout mode” state.

The BrutePrint attack bypasses the lockout mode by utilizing a mechanism called MAL and employs a “neural style transfer” system to modify fingerprint images in the database to resemble the target device’s sensor scans, increasing the likelihood of successful authentication.

Devices Tested Against BrutePrint

Through a series of experiments conducted on a selection of ten Android and iOS devices, the researchers discovered that each device exhibited susceptibility to at least one identified flaw.

While Android devices are vulnerable to brute-forcing attacks due to allowing unlimited fingerprint attempts, iOS devices have robust authentication security measures in place that effectively prevent such attacks.1

The researchers discovered that while certain iPhone models are vulnerable to CAMF, the limited number of fingerprint attempts (up to 15) makes it impractical to brute-force the owner’s fingerprint, and all tested Android devices are susceptible to the SPI MITM attack, except iPhones which encrypt fingerprint data on the SPI, rendering any interception ineffective.

While BrutePrint may appear to have limitations due to the need for prolonged access to the target device, its potential for enabling thieves to unlock stolen devices and extract private data, as well as the ethical concerns and privacy rights implications for law enforcement during investigations, raise significant issues regarding rights violations and the safety of individuals in overpowering countries.

Shut Down Phishing Attacks with Device Posture Security – Download Free E-Book


[ad_2]
Source link

The new Motorola Razr listed online before launch

0
[ad_1]

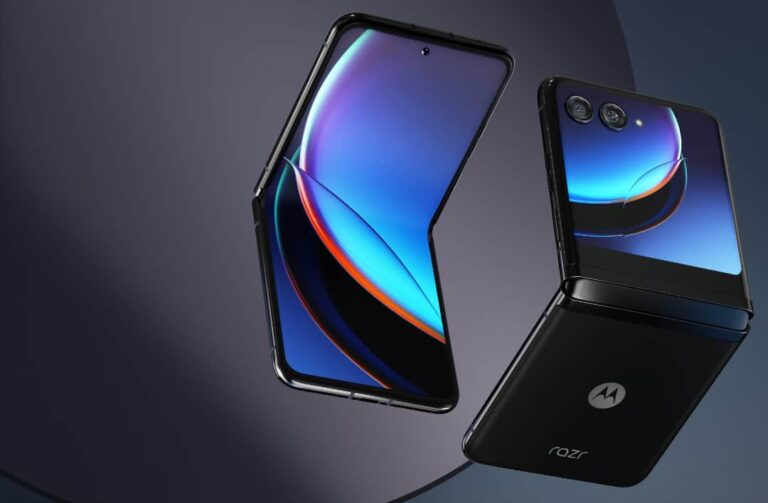
Between the announcement of the Google Pixel Fold and the upcoming Galaxy Z foldables, we’re following news about the new Motorola Razr. We don’t know exactly when Motorola plans to unveil this phone, but we have some more leaked information on it. The Motorola Razr was listed online before the official launch.

Since this involves leaked information, you’ll want to take it with a grain of salt. The information came from a site called Extra.com (via a tweet). We’re not 100% sure if the information is correct, but we should be able to find out more as time goes on.

The upcoming Motorola Razr was listed online before launch

There’s a lot of excitement around this phone, as it’s set the take on Samsung’s Galaxy Z flip 5. What’s probably most notable about it is the mass of the outer display. It’s going to encompass most of the top half of the phone and envelope the two outer camera lenses.

Based on a recently leaked video, the screen will be big enough to run full apps without even having to open the phone. The Razr might have a dedicated list of specially formatted apps that can take advantage of the more square display. No company has done this yet.

The online listing reveals some of the phone’s potential specs. For the inner display, it looks like it might have a massive 6.9-inch FHD+ pOLED display. Powering the phone, we could have the Snapdragon 8+ Gen 1 SOC, and it will run with Android 13 out of the box.

As for the camera, the specs point to the outer cameras being a 32-megapixel camera and an 8-megapixel camera. The 32-megapixel camera is most likely the main camera, and the 8-megapixel camera might be an ultrawide camera. As for the inner camera, things get a little confusing. We only see one punch hole on the internal display, but this listing points to two cameras- a 12-megapixel camera and a 13-megapixel camera. We’re going to have to wait for more information on that.

Other features listed include NFC and wireless charging. The leak says that there will be no expandable storage. As time goes on, we will get more official information about this phone.


[ad_2]
Source link

Have an easier time learning a new skill with these 3 tips

0
[ad_1]

The many quarantine and lockdown restrictions that were imposed during the pandemic gave us a new perspective on how we use our precious time. The work from home setup opened our eyes to how much time we actually waste in our morning commutes and going back home, while also allowing us to explore all the free time we suddenly had in ways that we may not have been able to before.

Even when everything is going back to normal, many companies have chosen to implement a hybrid work setup that combines both office and work from home days, giving employees and workers a bit more freedom to explore other hobbies, interests and goals outside of work with the free time they never really had before the pandemic.

Many are also using this time to pick up a new skill that they’ve always wanted to learn about, but it might seem like a daunting thing to go in as a complete beginner, especially as an adult. It might be easier to simply give up and tell yourself that it’s too late for you, but learning something new never has an age limit. Naturally, it will be hard and tiring, but here are a few ways to set yourself up for success!

Tip #1: Find a Good and Reliable Resource

Whether you’re learning a foreign language or trying your hand out at coding, the first step is to always find a reputable resource that can guide you through your learning journey. This can be anything from a textbook or even an online resource like a website or training program—it really depends on how you prefer to learn.

The importance of finding a primary resource is that the last thing you want is to have spent so much time studying something, only to realize that you were learning something outdated or incorrect, which is something that can happen if you simply bounce around different websites on the internet.

And apart from being a consolidated reference of everything you need to learn, as well as a curated study guide of sorts, these resources can also come with practice exercises and quizzes that you can use to test out your knowledge and see whether you’ve understood the lesson correctly.

Tip #2: Take Good Notes

While having a resource is all well and good, it might be hard to flip through hundreds of pages or scroll back and forth between lessons when you want to remember something. That’s why taking good and detailed notes is very important in a successful learning process.
Lesson notes allow you to process the information much more effectively, while also letting you take these down in a way that’ll be easier for you to refer to, such as illustrations, diagrams and flowcharts rather than simple blocks of text from your resource.

The medium you use to take notes is ultimately up to you and how you learn the best. Some people enjoy the feeling of writing handwritten notes as it helps them process the information better, while others prefer the convenience and efficiency of taking notes on a computer instead.

Tip #3: Have a Dedicated Work Environment

Needless to say, you’re not gonna feel any motivation to study if you’re doing it in your bed. Having a dedicated workspace will help you concentrate better, especially once you begin to associate and connect productivity with the area that you’ve chosen.

A work environment has to be free of any distractions, such as unnecessary gadgets and disruptive noises and people. It should only have the things that you need to learn effectively such as a study lamp, a notebook and a pen for those who prefer the more traditional mode of learning, or your laptop and a charging socket nearby for those who study better with technology.

These are the basics that you’ll need to successfully learn a lesson, but there are more things that you can add based on your needs and preferences. If you’re looking for more ways to raise your productivity levels, visit Temu!

Temu has a wide selection of high quality and affordable products ranging from over 29 categories and 250 subcategories that customers can’t get enough of. And with more than a thousand items being added each day, there’s something for everyone over at Temu!

Check out Temu’s official website or download the Temu mobile app today!


[ad_2]
Source link

WhatsApp is looking out for you with this upcoming feature

0
[ad_1]

Data security is extremely important especially when it comes to messaging apps like WhatsApp. This is why the company has encrypted backups. According to WABInfo, WhatsApp will prompt you to re-enter the password you used to encrypt your message backups.

WhatsApp is currently rolling this feature out, so there’s a chance that you might not have it just yet. This feature was spotted in WhatsApp version 2.23.9.74 (23.9.77 for iOS). If you’re on an older version of WhatsApp, you’ll want to update it when you have the chance. Go to your respective app store, and search for WhatsApp. There, check and see if you see the update button.

WhatsApp will remind you to put in the password you used to encrypt your chat backups

Since WhatsApp is a platform that plenty of people use for business, encryption is crucial. You don’t want your important business messages to be swooped up by a bad actor. A few years ago, WhatsApp allowed people to encrypt their chat backups. You can save encrypted backups of your chats to Google Drive or iCloud.

When you enable this feature, you will be prompted to put in a password. Either that, or you will lock it with a 64-digit encryption key. So, if you want to gain access to your encrypted chats, you will need to re-enter that password.

This new feature coming to Whatsapp will give you a pop-up prompting you to re-enter the password you used to encrypt your chats. This is to make sure that it is correct. It’s easy to set a password and forget it.

This is like a security checkpoint to make sure that you remember your credentials. So, make sure that you remember the password you set for your encrypted backups. You never know when you’ll need to access them again. Since the rollout has just begun, you should expect to see it hit your phone within the next couple of weeks.


[ad_2]
Source link

A week in security (May 15-21)

0
[ad_1]

The most interesting security-related news of the week from May 15-21.

Last week on Malwarebytes Labs:

Stay safe!


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Samsung will unveil improved 3nm and 4nm chip processes in June

0
[ad_1]

Samsung has some major foundry-related announcements lined up for next month. The company plans to unveil its improved 3nm and 4nm chip manufacturing processes at the 2023 Symposium on VLSI Technology and Circuits. The event is scheduled to take place between June 11 and 16 in Kyoto, Japan.

According to the program details published by the organizers of the six-day event, Samsung will announce its second-generation 3nm process (SF3) during the conference. The company is employing the GAA (Gate-All-Around) fabrication technology in its 3nm chips. The second-gen solution will use more advanced Multi-Bridge-Channel Field-Effect Transistors (MBCFET) with additional optimizations over the current process (SF3E).

Compared to Samsung’s current 4nm EUV (Extreme Ultraviolet) chips (aka SF4), which employ the FinFET fabrication tech, SF3 chips bring a 22 percent improvement in speed and are 34 percent more power efficient. These chips also allow for a smaller logic area, with the company claiming a 21 percent decline in chip size. The Korean firm doesn’t detail the difference in speed and power efficiency between SF3 and SF3E 3nm chips, though.

Additionally, Samsung will debut its most upgraded 4nm chips (SF4X) at the VLSI Symposium 2023 next month. These chips will seemingly be targeted at the HPC (High Performance Computing) application. The next-gen solutions will bring a ten percent boost in performance while simultaneously reducing power consumption by 23 percent. “This SF4X
technology provides tremendous performance benefits for various applications in a wide operation range,” the official paper states.

Samsung expects its improved 3nm chips to help boost foundry share

Samsung is desperate to improve its foundry share. The Korean behemoth is the world’s second-largest semiconductor foundry, but it only has a market share of about 15 percent. In comparison, its arch-rival TSMC captures about 60 percent of the market. The company is hoping for 3nm chips to improve its share. It is betting on the use of the more advanced GAA tech to lure customers to its side. TSMC is sticking to the FinFET architecture for one more generation. It plans to switch to the GAA tech with 2nm solutions in 2025.

There are already reports that Samsung has won orders for some of Qualcomm’s Snapdragon 8 Gen 4 chips for next year. Google may also stick to Samsung for the Tensor G4 after briefly considering a switch to TSMC. So early signs are looking quite promising for the Korean behemoth. But only time will tell whether it can get any closer to its Taiwanese rival in the semiconductor foundry business over the next few years.


[ad_2]
Source link

9 vulnerabilities impact Cisco Small Business Series

0
[ad_1]

If you’re using one of the affected products from the Cisco small business range, you need to patch immediately.

Vulnerabilities have been found and fixed in the web-based user interface of various Cisco products in the Small Business Series. These nine issues are tied to the web-based user interface of the products, and in a worst case scenario could lead to denial of service (DoS) conditions or arbitrary code execution.

Affected products

The vulnerabilities affect all of the below if running vulnerable firmware:

  • 250 Series Smart Switches
  • 350 Series Managed Switches
  • 350X Series Stackable Managed Switches
  • 550X Series Stackable Managed Switches
  • Business 250 Series Smart Switches
  • Business 350 Series Managed Switches
  • Small Business 200 Series Smart Switches
  • Small Business 300 Series Managed Switches
  • Small Business 500 Series Stackable Managed Switches

Exploits

  • CVE-2023-20159: Cisco Small Business Series Stack Buffer Overflow
  • CVE-2023-20160: Cisco Small Business Series Switches Unauthenticated BSS Buffer Overflow Vulnerability 
  • CVE-2023-20161: Cisco Small Business Series Switches Unauthenticated Stack Overflow Vulnerability
  • CVE-2023-20189: Cisco Small Business Series Switches Unauthenticated Stack Buffer Overflow Vulnerability

The four vulnerabilities above could allow an unauthenticated remote attacker to execute arbitrary code on an affected device. This is because of improper validation of requests sent to the web interface. A crafted request sent through the web interface could result in the attacker executing arbitrary code with root privileges on an affected device.

  • CVE-2023-20024: Cisco Small Business Series Switches Unauthenticated Heap Buffer Overflow Vulnerability
  • CVE-2023-20156: Cisco Small Business Series Switches Unauthenticated Heap Buffer Overflow Vulnerability
  • CVE-2023-20157: Cisco Small Business Series Switches Unauthenticated Heap Buffer Overflow Vulnerability
  • CVE-2023-20158: Cisco Small Business Series Switches Unauthenticated Denial-of-Service Vulnerability

The four vulnerabilities above could allow for a denial of service (DoS) condition on an affected device. As above, this is due to crafted requests being improperly validated when sent to the web interface.

  • CVE-2023-20162: Cisco Small Business Series Switches Unauthenticated Configuration Reading Vulnerability

This final vulnerability could allow a remote attacker to read unauthorised information on an affected device. This is, as with the other flaws, improper validation of requests sent to the web interface.

Mitigation

Two products confirmed as being not vulnerable to the issue are:

  • 220 Series Smart Switches
  • Business 220 Series Smart Switches

However, for those web-based user interfaces that are affected, Cisco has released software updates to fix the vulnerabilities. Cisco states that product users “should obtain security fixes through their usual update channels”.

There are no workarounds to address these vulnerabilities. In other words, if you’re unable to apply an update for the time being, your devices will remain vulnerable until they’re applied.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Galaxy A14 5G and more Samsung devices bag May update

0
[ad_1]

Samsung‘s recent budget 5G smartphone, the Galaxy A14 5G is receiving the latest security patch. The company has released the May 2023 SMR (Security Maintenance Release) for the phone in Asia and Latin America. A wider rollout should follow soon. The Galaxy Tab S6 Lite, meanwhile, is now widely picking up this month’s security update.

The May 2023 update for the Galaxy A14 5G comes with the firmware build number A146BXXU2BWE1 in Asia. The rollout is live in India, Sri Lanka, and a few more countries in the region. Samsung’s official changelog mentions that the device is getting some system stability and reliability improvements along with the latest security fixes. Users in Latin America, meanwhile, don’t appear to be getting anything extra here. The update carries the build number A146MUBS2AWE1. Note that the Galaxy A14 5G has already picked up One UI 5.1 in Asia but not in Latin America.

This update for the Galaxy A14 5G should soon expand to other regions, including Europe and the US. Meanwhile, Galaxy Tab S6 Lite users in several markets can now look forward to receiving the May SMR. Samsung first released the latest security patch for the affordable tablet in its homeland South Korea last week. But today, the update is widely available in Asia, Africa, Australia, Latin America, and Europe (via). The new firmware build number is P615NKOS5FWD2. The update doesn’t bring any additional goodies and isn’t yet available for the 2022 version of the Galaxy Tab S6 Lite.

Samsung’s May update patches dozens of security issues in Galaxy devices

While the May update may not contain anything notable on the user-facing side, there are plenty of hidden goodies here. More precisely, the May SMR brings more than 70 vulnerability fixes to the Galaxy A14 5G and Galaxy Tab S6 Lite. As detailed in Samsung’s monthly security bulletin, over 50 of those are Android OS patches coming from Google and partner vendors. The remaining patches are Galaxy-specific coming directly from the Korean brand. At least six security issues patched this month were labeled critical by the respective vendors.

If you’re using either of these Samsung devices or any other for that matter, you can manually check for updates from the Settings app. Go to the Software update menu and tap on Download and install. If the device finds a pending OTA (over the air), you will be prompted to download it straightaway. But if you don’t see any update, wait some time and check again. You may also get a notification once the OTA release reaches your unit.


[ad_2]
Source link

ChatGPT: Cybersecurity friend or foe?

0
[ad_1]

There are a lot of benefits to ChatGPT, but many in the security community have concerns about it. Malwarebytes’ CEO Marcin Kleczynski takes a deep dive into the topic.

If you haven’t heard about ChatGPT yet, perhaps you’ve just been thawed from cryogenic slumber or returned from six months off the grid. ChatGPT—the much-hyped, artificial intelligence (AI) chatbot that provides human-like responses from an enormous knowledge base—has been embraced practically everywhere, from private sector businesses to K–12 classrooms.

Upon its launch in November 2022, tech enthusiasts quickly jumped at the shiny new disruptor, and for good reason: ChatGPT has the potential to democratize AI, personalize and simplify digital research, and assist in both creative problem-solving and tackling “busywork.” But the security community and other technology leaders have started raising the alarm, worried about the program’s potential to write malware and spread mis- and disinformation.

Do you think your organization should embrace ChatGPT? Or do you believe implementing the platform will compromise your company’s cybersecurity posture? Read on to learn more about the pros, cons, conversations, and controversies surrounding ChatGPT, including a call to (halt) action from technology leaders.

Why ChatGPT security concerns are both overblown and valid

Artificial intelligence (AI) was once a science fiction cautionary tale—stories consistently warned against designing machines capable of surpassing human ingenuity. But over the last 20 years, AI has transitioned from the stuff of nightmares to mainstream adoption. From the first Roomba in 2002 to the first virtual assistant (Siri) in 2011, AI has slowly and steadily penetrated the consumer technology market, often with little comprehension from buyers that artificial intelligence is actually powering the functionality behind their favorite devices.

As of November 2022, people can no longer ignore the artificial elephant in the room. Enter: ChatGPT. Developed by OpenAI, ChatGPT (Chat Generative Pre-Trained Transformer) is an AI-powered chatbot that uses an enormous and sophisticated language model to generate human-like responses in text format. ChatGPT amassed an incredible 100 million users within two months of its explosive launch, and its website receives over 1 billion visitors per month.

Unlike other chatbots, which are typically only able to produce canned replies on a few subjects, ChatGPT can mimic the style of celebrity CEOs, craft business pitches, compose music and song lyrics, answer test questions, simulate an entire chat room, write computer code, and much more. For example, Malwarebytes asked ChatGPT to write the opening paragraph of a novel about an antiquated antivirus program that relies on signature-based detection to stop new and emerging threats.

Here’s what the program came back with:

“The antivirus program blinked to life, its archaic interface flickering on the outdated CRT monitor. The program’s once cutting-edge signature-based detection technology was now decades out of date, unable to keep pace with the rapidly evolving landscape of digital threats. But for the small team of programmers responsible for maintaining the program, it was still their best line of defense against the unrelenting tide of new and unknown viruses that threatened to breach their systems. As they watched the program scan through the code, line by line, they knew that they were fighting an uphill battle – but they had no other choice but to keep trying.”

Such articulate, detailed responses caused a near frenzy upon ChatGPT’s initial release. Many corporate customers and app developers have rushed to implement the platform, and its newer Dall-E program for generating images, into their business processes and products. However, the security community and those wary of artificial intelligence’s steady drumbeat forward have warned organizations to exercise caution over a myriad of potential risks.

Because of its meteoric rise into public consciousness and rapid adoption, the generative AI chatbot has been the subject of continuing, complex conversations about its impact on the cybersecurity industry, threat landscape, and humanity as a whole. Will ChatGPT be the sentient harbinger of death some have claimed? Or is it a unicorn that’s going to solve every business, academic, and creative problem? The answer, as usual, lies somewhere in the gray.

Security pros of ChatGPT

AI can be a powerful tool for cybersecurity and information technology professionals. It will change the way we defend against cyberattacks by improving the industry’s ability to detect and respond to threats in real time. And it will help businesses shore up their IT infrastructure to better withstand the constant stream of increasingly-sophisticated attacks. Most effective security solutions today, including Malwarebytes, already employ some form of machine learning. That’s why some in the security community argue that generative AI tools can be safely deployed to strengthen an organization’s cybersecurity posture as long as they’re implemented according to best practices.

Increases efficiency

ChatGPT can increase efficiency for cybersecurity staff on the front lines. For one, it can significantly reduce notification fatigue, a growing concern within the field. With companies grappling with limited resources and a widening talent gap, a tool like ChatGPT could simplify certain labor-intensive tasks and give defenders back valuable time to commit to higher-level strategic thinking. ChatGPT can be trained to identify and mitigate network security threats like DDoS attacks when used in conjunction with other technologies. It can also help automate security incident analysis and vulnerability detection, as well as more accurately filter spam.

Assists engineers

Malware analysts and reverse engineers could also benefit from ChatGPT’s assistance on traditionally challenging tasks, such as writing proof-of-concept code, comparing language- or platform-specific conventions, and analyzing malware samples. The chatbot can also help engineers learn how to write in different programming languages, master difficult software programs, and understand vulnerabilities and exploit code.

Trains employees

ChatGPT’s security applications aren’t limited to Information Security (IS) personnel. The program can help close the security knowledge gap by assisting in employee training. Cybersecurity training is crucial for organizations interested in mitigating cyberattacks and fraud, yet IT departments are often far too busy to offer more than a single course per year. ChatGPT can step in to offer insights on identifying the latest scams, avoiding social engineering pitfalls, and setting stronger passwords in concise, conversational text that may be more effective than a lecture or slide presentation.

Aids law enforcement

Finally, ChatGPT has the potential to assist law enforcement with investigating and anticipating criminal activities. In a March 2023 report from Europol, subject matter experts found that ChatGPT and other large language models (LLMs) opened up “explorative communication” for law enforcement to quickly gather key information without having to manually search through and summarize data from search engines. LLMs can significantly speed up the learning process, enabling a much faster gateway into technological comprehension than was previously thought possible. This could help officers get a leg up on cybercriminals whose understanding of emerging technologies have typically outpaced their own.

Security concerns overblown

Not long after ChatGPT was first introduced, the inevitable hand wringing by technology decision-makers took hold. In a February survey of IT professionals by Blackberry, 51 percent predicted we are less than a year away from a successful cyberattack being credited to ChatGPT, and 71 percent believed nation states are likely already using the technology for malicious purposes.

The following month, thousands of tech leaders, including Steve Wozniak and Elon Musk, signed an open letter to all AI labs calling on them to pause the development of systems more powerful than the latest version of ChatGPT for at least six months. The letter cites the potential for profound risks to society and humanity that arise from the rapid development of advanced AI systems without shared safety protocols. More than 27,500 signatures have since been added to the letter.

However, even when ChatGPT is engaged in ominous activities, the outcomes at present are rather harmless. Since OpenAI allows developers to modify its official APIs, some have tested a few nefarious theories by creating ChaosGPT, an internet-connected “evil” version that runs actions users do not intend. One user commanded the AI to destroy humanity, and it planned a nuclear winter, all while maintaining its own Twitter account, which was ultimately suspended.

ChaosGPT tweet

So maybe ChatGPT isn’t going to take over the world just yet—what about some of the more realistic security concerns being voiced, like the ability to develop malware or phishing kits?

When it comes to writing malicious code, ChatGPT isn’t yet ready for prime time. In fact, the platform is a terrible programmer in general. It’s currently easier for an expert threat actor to create malware from scratch than to spend time correcting what ChatGPT has produced. The fear that ChatGPT would hand script kiddies the programming power to produce thousands of new malware strains is unfounded, as amateur cybercriminals lack the knowledge to pick up on minor errors in code, as well as the understanding of how code works.

One of our researchers recently embarked on an experiment to get ChatGPT to write ransomware, and despite the chatbot’s initial protests that it couldn’t “engage in activities that violate ethical or legal standards, including those related to cybercrime or ransomware,” with a little coaxing, ChatGPT eventually complied. The result: snippets of ransomware code that switched languages throughout, stopped short after a certain number of characters, dropped features at random, and were essentially incoherent and useless.

Since the primary focus of ChatGPT’s training was in language skills, security pros have been most anxious about its ability to generate believable phishing kits. While the chatbot can produce a clean phishing email that’s free from grammatical or spelling errors, many modern phishing samples already do the same. The AI tool’s phishing skills begin and end with writing emails because, again, it lacks the coding talent to produce other elements like credential harvesters, infected macros, or obfuscated code. Its attempts so far have been rudimentary at best—and that’s with the assistance of other tools and researchers.

ChatGPT can only pull from what’s already in its public database, and it has only been trained on data up until 2021. Even today, there are simply not enough well-written phishing scripts in the wild for ChatGPT to surpass what cybercriminals have already developed. In addition, OpenAI has safety protocols that explicitly prohibit the use of its models for malware development, fraud (including spam and scams), and invasions of privacy. Unfortunately, that hasn’t stopped crafty individuals from “jailbreaking” ChatGPT to get around them.

ChatGPT security cons

Just because some of the worst fears about ChatGPT are overhyped doesn’t mean there are no justifiable concerns. According to the NIST AI Risk Management Framework published in January, an AI system can only be deemed trustworthy if it adheres to the following six criteria:  

  1. Valid and reliable
  2. Safe
  3. Secure and resilient
  4. Accountable and transparent
  5. Explainable and interpretable
  6. Fair with harmful biases managed

However, risks can emerge from socio-technical tensions and ambiguity related to how an AI program is used, its interactions with other systems, who operates it, and the context in which it is deployed.

Racial and gender bias

There are many inherent uncertainties in LLMs that render them opaque by nature, including limited explainability and interpretability, and a lack of transparency and accountability, including insufficient documentation. Researchers have also reported multiple cases of harmful bias in AI, including crime prediction algorithms that unfairly target Black and Latino people and facial recognition systems that have difficulty accurately identifying people of color. Without proper controls, ChatGPT could amplify, perpetuate, and exacerbate toxic stereotypes, leading to undesirable or inequitable outcomes for certain communities and individuals.

Lack of verifiable metrics

AI systems suffer from a deficit of verifiable measurement metrics, which would help security teams determine whether a particular program is safe, secure, and resilient. What little data exists is far from robust and lacks consensus among AI developers and security professionals alike. What’s worse, different AI developers interpret risk in different ways and measure it at different intervals in the AI lifecycle, which could yield inconsistent results. Some threats may be latent at one time but increase as AI systems adapt and evolve.

Cybercriminal experimentation

Despite its struggles with malicious code, ChatGPT has already been weaponized by enterprising cybercriminals. By January, threat actors in underground forums were experimenting with ChatGPT to recreate malware variants and techniques described in research publications. Criminals shared malicious tools, such as an information stealer, an automated exploit, and a program designed to phish for credentials. Researchers also discovered cybercriminals exchanging ideas about how to create dark web marketplaces using ChatGPT that sell stolen credentials, malware, or even drugs in exchange for cryptocurrency.

Vulnerabilities and exploits

There are few ways to know in advance if an LLM is free from vulnerabilities. In March, OpenAI temporarily took down ChatGPT because of a bug that allowed some users to see the titles of other people’s chat histories and first messages of newly-created conversations. After further investigation, OpenAI discovered the vulnerability had exposed some user payment and personal data, including first and last names, email addresses, payment addresses, the last four digits of credit card numbers, and card expiration dates. While OpenAI claims, “We are confident that there is no ongoing risk to users’ data,” there’s no way (at present) to confirm or deny whether personal information was exfiltrated for criminal purposes.

Also in March, OpenAI massively expanded ChatGPT’s capabilities to support plugins that allow access to live data from the web, as well as from third-party applications like Expedia and Instacart. In code provided to ChatGPT customers interested in integrating the plugins, security analysts found a potentially serious information disclosure vulnerability. The bug can be leveraged to capture secret keys and root passwords, and researchers have already seen attempted exploits in the wild.

Privacy concerns

Compounding worries that vulnerabilities could lead to data breaches, several top brands recently chastised employees for entering sensitive business data into ChatGPT without realizing that all messages are saved on OpenAI’s servers. When Samsung engineers asked ChatGPT to fix errors in their source code, they accidentally leaked confidential notes from internal meetings and performance data in the process. An executive at another company cut-and-pasted the firm’s 2023 strategy into ChatGPT to create a slide deck, and a doctor submitted his patient’s name and medical condition for ChatGPT to craft a letter to his insurance company.

Chat with ChatGPT

Both privacy and security concerns have prompted major banks, including Bank of America, JPMorgan Chase, Goldman Sachs, and Wells Fargo, to restrict or all-out ban ChatGPT and other generative AI models until they can be further vetted. Even private companies like Amazon, Microsoft, and Walmart have issued warnings to their staff to refrain from divulging proprietary information or sharing personal or customer data on ChatGPT as well.

Social engineering

Finally, cybercriminals wouldn’t be cybercriminals if they didn’t capitalize on ChatGPT’s wild popularity. Because of its accelerated growth, ChatGPT was forced to throttle its free tool and launch a $20/month paid tier for those wanting unlimited access. This gave threat actors the ammunition to develop convincing social engineering schemes that promised uninterrupted, free access to ChatGPT but really lured users into entering their credentials on malicious webpages or unknowingly installing malware. Security researchers also found more than 50 malicious Android apps on Google Play and elsewhere that spoof ChatGPT’s icon and name but are designed for nefarious purposes.

ChatGPT’s disinformation problem

While vulnerabilities, data breaches, and social engineering are valid concerns, what’s causing the most anxiety at Malwarebytes is ChatGPT’s ability to spread misinformation and disinformation on a massive scale. That which enamors the public most—ChatGPT’s ability to generate thoughtful, human-like responses—is the very same capability that could lull users into a false sense of security. Just because ChatGPT’s answers sound natural and intelligent doesn’t mean they are accurate. Incorrect information and associated biases are often incorporated into its responses.

OpenAI CEO Sam Altman himself expressed worries that ChatGPT and other LLMs have the potential to sow widespread discord through extensive disinformation campaigns. Altman said the latest version, GPT-4, is still susceptible to “hallucinating” incorrect facts and can be manipulated to produce deceptive or harmful content. “The model will boldly assert made-up things as if they were completely true,” he told ABC News.

In the age of clickbait journalism and social media, it can be challenging to discern the difference between fake and authentic content, propaganda or legitimate fact. With ChatGPT, bad actors can use the AI to quickly write fake news stories that mimic the voice and tone of established journalists, celebrities, or even politicians. For example, Malwarebytes was able to get ChatGPT to write a story in the voice of Barack Obama about the earthquake in Turkey, which could easily be modified to spread disinformation or collect fraudulent payments through fake donation links.

Educational concerns

In education, mis- and disinformation are especially troubling byproducts of ChatGPT that have led some of the biggest school districts in the US to ban the program from K–12 classrooms. From its lack of cultural competency to its potential to undermine human teachers, academia is understandably apprehensive. For every student using ChatGPT to research debate prompts or develop study guides, there’s another abusing the platform to plagiarize essays or take exams.

The education industry might be willing (for now) to let teachers use ChatGPT for simple tasks like creating lesson plans and emailing parents, but the tool will likely remain off-limits for students, or at least highly regulated in public schools. Educators are aware that over-reliance on AI-powered tools and generated content could lead to a decrease in problem solving, creativity, and critical thinking—the very skills teachers and administrators aim to develop in students. Without them, it’ll be that much harder to recognize and avoid misinformation.

Final verdict

Suggesting that ChatGPT is low risk and unworthy of the security community’s attention is like putting your head in the sand and pretending AI doesn’t exist. ChatGPT is only the start of the generative AI revolution. Our industry should take its potential for disruption—and destruction—seriously and focus on developing safeguards to combat AI threats. Halting “dangerous” research on advanced models ignores the reality of rampant AI use today. Instead, it’s better to demand NIST’s criteria for trustworthiness and establish regulation around the development of AI through both government intervention and corporate security innovation.

Some artificial intelligence regulation is already on the books: the 2022 Algorithmic Accountability Act requires US businesses to assess critical AI algorithms and provide public disclosures for increased transparency. The legislation was endorsed by AI advocates and experts, and it sets the stage for future government oversight. With AI laws proposed in Canada and Europe as well, we’re one step closer to providing some important guardrails for AI. In fact, expect to see changes (aka limitations) implemented to ChatGPT in the near future in response to a country-wide ban by the Italian government.

Just as cybersecurity relies on commercial software to defend people and businesses, so too might generative AI models. New companies are already springing up that specialize in AI vulnerability detection, bot mitigation, and data input cleansing. One such company, Kasada Pty, has been tracking ChatGPT misuse and abuse. Another new tool from Robust Intelligence, modeled after VirusTotal, scans AI applications for security flaws and tests whether they’re as effective as advertised or if they have issues around bias. And Hugging Face, one of the most popular repositories of machine learning models, has been working with Microsoft’s threat intelligence team on an application that scans AI programs for cyberthreats.

As organizations look to integrate ChatGPT—whether to augment employee tasks, make workflows more efficient, or supplement cyberdefenses—it will be important to note the program’s risks alongside its benefits, and recognize that generative AI still requires an appreciative amount of oversight before large-scale adoption. Security leaders should consider AI-related vulnerabilities across their people, processes, and technology—especially those related to mis- and disinformation. By putting the right safeguards in place, generative AI tools can be used to support existing security infrastructures.

Awareness alone won’t solve the more nebulous threats associated with ChatGPT. To bring disparate security efforts together, the AI community will need to adopt a similar modus operandi to traditional software, which benefits from an entire ecosystem of government, academia, and enterprise that has developed over more than 20 years. That system is in its infancy for LLMs like ChatGPT today, but continued diligence—plus a learning model of its own—should integrate cybersecurity in a symbiotic relationship.  The benefits of ChatGPT are many, and there’s no doubt that generative AI tools have the potential to transform humanity. In what way, remains to be seen.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link