Paramount Plus subscriptions jump in price at the end of June

0
[ad_1]

Back in February, Paramount announced that it would be raising the prices of its Paramount Plus subscription service plans later this year. That meant users would indeed be seeing more money leave their accounts every month to continue enjoying what Paramount Plus has to offer.

The only thing is Paramount didn’t mention when exactly the changes were happening. As part of the announcement, Paramount said that prices for Paramount Plus would be increasing sometime in Q3. That’s a pretty broad window though. And could be anytime between July and September. Now the company has given a more firm date, stating that prices will be going up in June. Specifically on June 27, The Verge reports.

For those who were either unaware or simply don’t remember, these increases apply to the ad-supported and premium plans. The previously $4.99 ad-supported plan will now cost $5.99 a month. Meanwhile the premium plan will go up from $9.99 to $11.99. The premium plan will stay ad-free.

Paramount Plus prices aren’t technically changing for everyone

There’s one segment of subscribers who won’t see a price increase. And that’s anyone who was already subscribed to Paramount Plus Premium with Showtime. The changes happening on June 27 will simply be doing away with the $9.99 ad-free Premium plan that didn’t have Showtime included. But Paramount already offered an $11.99 plan that did included Showtime.

So the change here is that anyone who wants an ad-free experience will need to go with the more costly plan option. Even if they don’t plan to watch any Showtime content. Although, if you’re planning to keep Paramount Plus Premium and just pay the higher fee, you might as well take advantage of what’s being offered.

Showtime does have some pretty good content to watch after all. That being said, this is also just another streaming service raising prices in a sea of options that have already done the same thing. So it won’t be surprising if people decide to cut things off.


[ad_2]
Source link

Matter 1.1 update is finally here, but it may not be what you expect

0
[ad_1]

After over six months in existence, the Matter 1.1 update is finally here for users. Since the rollout of this feature, a ton of users have put it to use across their smart home devices.

For over six months, those using the Matter smart home connectivity feature have had a hard time using this platform. Most major smart home devices are yet to fully support this feature as manufacturers are slow to roll out support. This makes it hard for devices to seamlessly connect despite not coming from the same manufacturer.

According to the CSA, this Matter 1.1 update will improve the all-around user experience. But it seems like it fails to improve the experience as it focuses on a different issues.

The Matter 1.1 update squashes bugs instead of giving support to more smart home appliances

According to users using the latest Matter 1.1 update, it fails to impress. The CSA says that this update helps create an improved path forward for developers. This leads users to expect much from this update, but… they may be disappointed.

The Verge points out in a recent article that the Matter 1.1 update falls short in an important area. After testing out the new update, The Verge made some observations. This update focuses on fixing a bug that displays various devices as being offline despite being connected to the platform.

Regardless of how small this fix might be, it is a significant improvement for users. With this fix, users will be able to tell what devices are connected to the Matter platform for controls. But the issue of running smart home devices from different manufacturers on Matter proves challenging for most users.

The source says that it’s hard to get the multi-admin control to work properly: “It’s anything but easy to get a device paired to one platform working on another.” This seems to be a result of different flows for various smart home platforms, as Matter finds it hard to decide which platform to work with.

The CSA seems to be relying on platforms like Google Home, Amazon Alexa, Samsung SmartThings, and Apple Home to fix this issue.


[ad_2]
Source link

EDR vs MDR for business success

0
[ad_1]

Learn more about EDR and MDR and which is right for your business.

Did you miss our recent webinar on EDR vs. MDR? Don’t worry, we’ve got you covered!

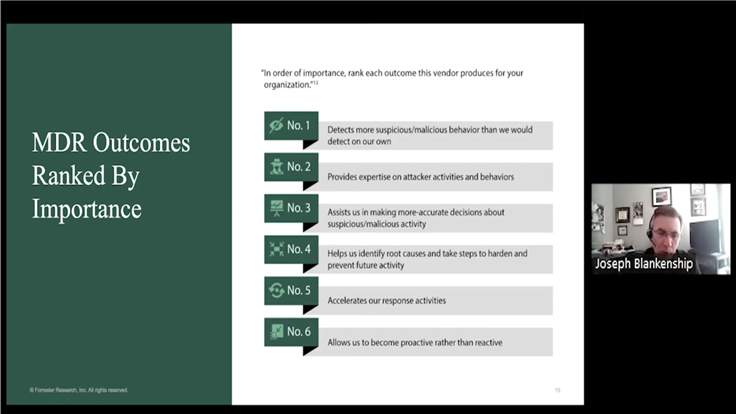
In this blog post, we’ll be recapping the highlights and key takeaways from the webinar hosted by Marcin Kleczynski, CEO and co-founder of Malwarebytes, and featuring guest speaker Joseph Blankenship, Vice President and research director at Forrester.

  • Introducing EDR and MDR: The webinar began with an overview of EDR and MDR. The speakers explained that EDR provides visibility into endpoint activity, while MDR offers 24/7 monitoring and management of security technologies and incident response services. They also pointed out that EDR solutions can be challenging for businesses without dedicated security teams and that building an in-house SOC can be expensive and difficult.
  • Limitations of Endpoint Protection and EDR: The speakers discussed the limitations of endpoint protection and EDR, specifically when it comes to advanced threats like ransomware or Advanced Persistent Threats (APTs) that use Living off the Land (LOTL) attacks and fileless malware. These threats can hide in memory and blend in with normal activity, making them difficult to detect without trained specialists who are proactively hunting for them.
  • How MDR Can Help: To address these challenges, the speakers spoke about outsourcing to an MDR provider. MDR providers work with clients to understand their security technology stack, make recommendations, and agree on response actions to take. Incident response and threat hunting are part of the MDR service, and the provider will have a plan in place to shut down threats, contain them, and eradicate them so businesses can get back to.. erm… business.
  • Which Is Right for Your Business? The choice between EDR and MDR comes down to the resources you have available and the level of security you require. If you have a dedicated security team and the resources to manage and maintain an EDR solution, EDR may be the right choice for you. However, if you lack dedicated security resources, MDR may be a better option as it provides continuous monitoring and incident response services.

Want to learn more about EDR and MDR and which is right for your business? Be sure to watch the full webinar recording on-demand and get valuable insights from industry experts on how to improve your security operations and protect against ransomware and fileless malware.

Watch now!


[ad_2]
Source link

May update widely available for US Galaxy S20, Fold 2 & Note 10

0
[ad_1]

Samsung‘s May 2023 update is available for a bunch of Galaxy smartphones in the US. The company is widely rolling out the latest security patch to the Galaxy S20 series, Galaxy Z Fold 2, and Galaxy Note 10 series. It has already updated dozens of other models to the new SMR (Security Maintenance Release).

The May SMR is available for both carrier-locked and unlocked variants of the Galaxy S20, Galaxy S20+, and Galaxy S20 Ultra in the US. Samsung is pushing the update with firmware build numbers G98*USQS4HWE1 and G98*U1UES4HWD5 for the two variants, respectively (via). The rollout is already live on most networks, with the remaining few following soon. The devices aren’t getting anything apart from the latest security fixes (more on that later).

The pattern remains the same for the Galaxy Z Fold 2. Samsung has widely released the May SMR for both carrier-locked and unlocked units of its 2020 foldable. Users can look forward to receiving the update with the build number F916USQS2JWE4 or F916U1UES2JWE3 depending on their variant. Once again, there aren’t additional goodies here. This update is all about the latest batch of monthly security fixes from Samsung and Google.

If you’re using a Galaxy Note 10 or Galaxy Note 10+ in the US, the latest security patch is available for your phone as well. That’s regardless of whether you have a factory-unlocked unit or a carrier-locked one. Samsung has got all of you covered. The new build number for the former group is N97*USQU7HWE1, while that for the latter is N970U1UEU7HWE1. For a change, this update contains more than the May security patch.

Unfortunately, nothing much on the user-facing side of things again. According to Samsung’s official changelog, the latest update for the Galaxy Note 10 series in the US brings revised Terms & Conditions. The company says that you are agreeing to those revised terms for your device, which include the Dispute Resolution Agreement with arbitration terms, by installing this update.

These Galaxy devices are getting a host of security fixes with the May update

The May 2023 update for Samsung’s Android smartphones contains fixes for more than 70 security issues. These include at least six critical flaws, some of which allowed remote code execution. If you’re using any of the aforementioned Galaxy devices stateside and haven’t received the May SMR yet, you should soon. Watch out for a notification about the OTA (over the air) release in the coming days. You can also manually check for updates from the Settings app.


[ad_2]
Source link

Popular Chinese Android TV boxes are preloaded with malware: Report

0
[ad_1]

Android TV boxes are a popular way for users to revive their old TVs and prolong their lifetime by converting them into smart ones. However, according to a new report from TechCrunch, popular Android TV boxes from Chinese companies like AllWinner and RockChip come preloaded with malware capable of launching coordinated cyberattacks.

Security researcher Daniel Milisic first uncovered this problem when he purchased an AllWinner T95 box last year and discovered that the firmware was infected with malware, which enabled bad actors to establish a connection with the TV box and install any desired app or payload. While not as well-known as Google’s Chromecast or Amazon’s Fire TV Stick, these Chinese Android TV boxes have received positive reviews due to their affordable price and advertised features.

How does the malware work?

The default payload found on these compromised Android TV boxes is clickbot, a type of malware that generates revenue by automatically clicking on ads in the background. Therefore, as soon as a user powers on their TV, the malware receives instructions from servers and starts making money.

However, upon further investigation, Milisic also discovered that his T95 box was part of a larger botnet comprising thousands of compromised Android TV boxes worldwide. In addition to the AllWinner T95, other models from AllWinner and RockChip, such as the AllWinner T95Max, RockChip X12 Plus, and RockChip X88 Pro 10, also come with pre-installed malware.

Stay protected

While the investigation did prompt the bad actors to take down the command-and-control servers, Milisic claims that the botnet could easily resurface with new infrastructure at any given time. Therefore, it is the responsibility of retailers like Amazon to ensure that the products they sell do not pose any harm to consumers. On the other hand, users should also exercise caution before purchasing an Android TV box from Amazon and, if possible, only consider reputable brands like Google and Nvidia. Although cheaper options may seem tempting due to their affordability and customization options, compromising data security and privacy is not worth the risk.


[ad_2]
Source link

Identity crisis featuring Alec Muffett Lock and Code S04E11

0
[ad_1]

This week on Lock and Code, we speak with longtime security researcher about the eerily similar attempts across the globe to weaken the Internet to achieve one specific, social goal.

On January 1, 2023, the Internet in Louisiana looked a little different than the Internet in Texas, Mississippi, and Arkansas—its next-door state neighbors. And on May 1, the Internet in Utah looked quite different, depending on where you looked, than the Internet in Arizona, or Idaho, or Nevada, or California or Oregon or Washington or, really, much of the rest of the United States. 

The changes are, ostensibly, over pornography. 

In Louisiana, today, visitors to the online porn site PornHub are asked to verify their age before they can access the site, and that age verification process hinges on a state-approved digital ID app called LA Wallet. In the United Kingdom, sweeping changes to the Internet are being proposed that would similarly require porn sites to verify the ages of their users to keep kids from seeing sexually explicit material. And in Australia, similar efforts to require age verification for adult websites might come hand-in-hand with the deployment of a government-issued digital ID. 

But the large problem with all these proposals is not that they would make a new Internet only for children, but a new Internet for everyone.

Look no further than Utah. 

On May 1, after new rules came into effect to make porn sites verify the ages of their users, the site PornHub decided to refuse to comply with the law and instead, to block access to the site for anyone visiting from an IP address based in Utah. If you’re in Utah, right now, and connecting to the Internet with an IP address located in Utah, you cannot access PornHub. Instead, you’re presented with a message from adult film star Cheri Deville who explains that:

“As you may know, your elected officials have required us to verify your age before granting you access to our website. While safety and compliance are at the forefront of our mission, giving your ID card every time you want to visit an adult platform is not the most effective solution for protecting our users, and in fact, will put children and your privacy at risk.”

Today, on the Lock and Code podcast with host David Ruiz, we speak with longtime security researcher Alec Muffett (who has joined us before to talk about Tor) to understand what is behind these requests to change the Internet, what flaws he’s seen in studying past age verification proposals, and whether many members of the public are worrying about the wrong thing in trying to solve a social issue with technology. 

“The battle cry of these people have has always been—either directly or mocked as being—’Could somebody think of the children?’ And I’m thinking about the children because I want my daughter to grow up with an untracked, secure private internet when she’s an adult. I want her to be able to have a private conversation. I want her to be able to browse sites without giving over any information or linking it to her identity.”

Muffett continued:

“I’m trying to protect that for her. I’d like to see more people grasping for that.”

Tune in today.

You can also find us on Apple Podcasts, Spotify, and Google Podcasts, plus whatever preferred podcast platform you use.


Malwarebytes Privacy VPN can encrypt your connection when using public WiFi, and it can block companies and websites from seeing your IP address and location to identify who you are, where you live, or what you’re doing on the Internet.

TRY NOW


Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)

Additional Resources and Links for today’s episode:

“A Sequence of Spankingly Bad Ideas.” – An analysis of age verification technology presentations from 2016. Alec Muffett.

“Adults might have to buy £10 ‘porn passes’ from newsagents to prove their age online.” – The United Kingdom proposes an “adult pass” for purchase in 2018 to comply with earlier efforts for online age verification. Metro. 

“Age verification won’t block porn. But it will spell the end of ethical porn.” – An independent porn producer explains how compliance costs for age verification could shut down small outfits that make, film, and sell ethical pornography. The Guardian. 

“Minnesota’s Attempt to Copy California’s Constitutionally Defective Age Appropriate Design Code is an Utter Fail.” – Age verification creeps into US proposals. Technology and Marketing Law Blog, run by Eric Goldman. 

“Nationwide push to require social media age verification raises questions about privacy, industry standards.” – Cyberscoop.

“The Fundamental Problems with Social Media Age Verification Legislation.” – R Street Institute.

YouTube’s age verification in action. – Various methods and requirements shown in Google’s Support center for ID verification across the globe. 

“When You Try to Watch Pornhub in Utah, You See Me Instead. Here’s Why.” – Cheri Deville’s call for specialized phones for minors. Rolling Stone. 

[ad_2]
Source link

The WhatsApp message editing feature arrives for all users

0
[ad_1]

A long-awaited feature, WhatsApp message editing, is finally making its way to users. About six years ago, the internet got the announcement that this feature was in the works. For some unknown reasons, WhatsApp held back from rolling out this feature up until now.

A recent WhatsApp blog post carries details introducing this feature to users around the world. This new feature will change how users chat with their friends and family, giving them more control over their typographical errors. If you have ever wished that you could correct an error in a message you sent to someone, then this feature is for you.

Most users will be pleased to get this feature on their devices as it’d be effective while chatting. So if users make a typographical error or want to change the context of their message, they can do so with just the tap of a button. This article will cover the use of this feature and how you can access it as an everyday WhatsApp user.

How to make use of the new WhatsApp message editing feature

Social media platforms such as Twitter provide this feature for their users to help them make corrections to their posts. Now, WhatsApp is helping users take the stress off whenever they make a mistake while texting. Previously, most users would correct the error with a follow-up message that is followed by an asterisk sign to denote that it is a correction to a mistake.

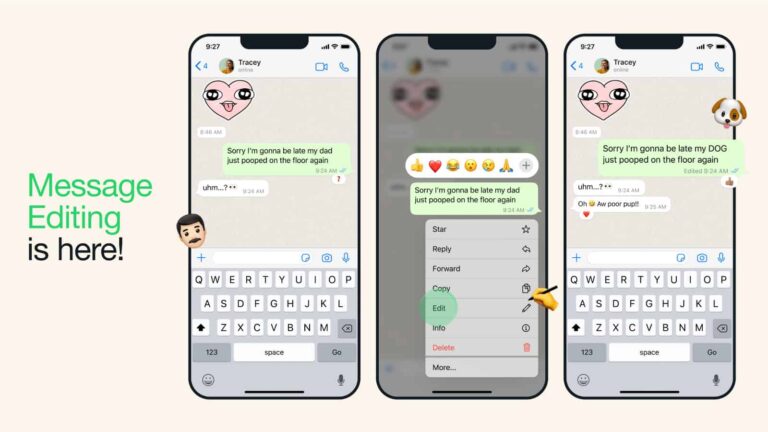
With an update coming to WhatsApp, users will no longer need to use an asterisk sign to denote a correction. With an edit button integrated into the chat option layout, users will be able to correct and resend messages. Each edited message will come with a sign to show the recipient that the sender made some corrections to the message.

For each message sent, WhatsApp gives users a 15-minute time frame to make an edit if need be. After this time elapses, the user won’t be able to edit the message however they please. The time given, 15 minutes, is more than enough for a user to detect and correct errors while chatting.

With this feature, users won’t sound funny after making a mistake while texting their friends. They can quickly edit the message and easily move on with the conversation. To make an edit, users should hold down the message and select the edit option in the pop-up menu.

After this they can clear the error and type in the correction, then afterwards resend the message. The recent message replaces the previous one but comes with a sign to show that it was edited. A coming update to the WhatsApp mobile application on the Google Play Store and App Store will bring this feature to users.


[ad_2]
Source link

Meta is about to sign a licensing deal with Magic Leap

0
[ad_1]

Meta and Magic Leap are in talks to close an IP licensing and manufacturing deal. The deal will allow both companies to form a coalition against Apple’s growing interest in AR.

Despite its promising future, the AR space has not yet been able to turn into a profitable area of business for companies like Meta and Apple. According to the latest reports, Meta is losing over $13 billion annually on Reality Labs, and the downfall is expected to continue. However, Meta has no plan to give up on AR and wants to revive its business by signing a licensing deal with the rival company Magic Leap.

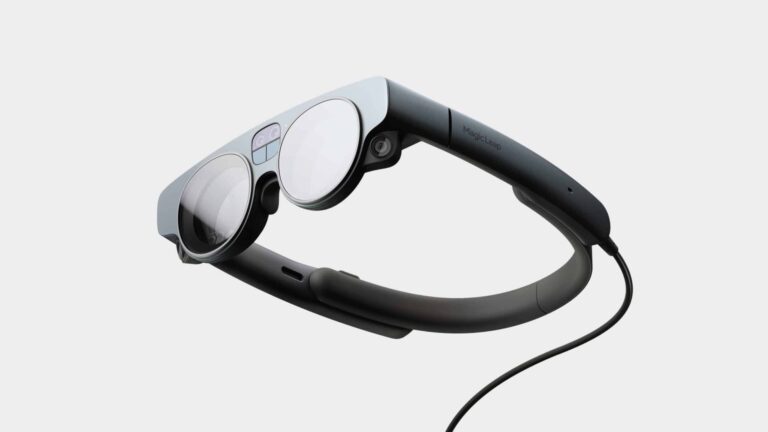
The agreement details are yet to be discovered, but it’s unlikely that companies would agree to launch a joint product. Instead, Meta could access Magic Leap optical tech and hand over producing its VR headsets to the fellow startup. Additionally, this partnership will let Meta produce its VR products domestically and reduce reliance on China. Reports already suggested that Meta could launch its AR glasses in 2027.

Meta and Magic Leap will sign an IP licensing deal

Neither Meta nor Magic Leap has yet responded to the news. But Magic Leap called these partnerships a “significant line of business” that offers a “growing opportunity” to the company, according to Financial Times.

Magic Leap is one of the most creative startups in the AR space. Its optics are incredibly popular among manufacturers. Last year, the CEO Peggy Johnson said in a blog post that a growing number of businesses are interested in licensing their IP and using their patented manufacturing process.

Meta CEO Mark Zuckerberg had laid out his visions for the company’s future, with AR being an essential part of it. However, investors are unhappy with this decision. As the company reported $13.7 billion in operating losses for AR and VR in 2022. The tech giant also lost another $10 billion in Reality Labs in 2021.

Meta could also face growing competition in the AR space in the coming years. Apple is reportedly planning to enter the AR market. And Samsung is pegging itself into the market by adding more AR-driven features to Galaxy devices.


[ad_2]
Source link

EU strikes Meta’s Facebook again with a fresh $1.3 billion fine

0
[ad_1]

Meta’s Facebook is in the spotlight again after how it handled EU citizens’ data, resulting in a rather large fine. This issue has made the EU fine Meta a whopping $1.3 billion over the Facebook data, which is the highest the company has had to pay. Such a fine won’t be given to any company without ample evidence and proof that the company broke some laws.

Sources of this information say that the fine came after “a lengthy investigation” found Meta guilty of violating a privacy rule. Regarding user data, the EU requires big tech firms to operate all EU citizen data within the region. But a series of investigations point out that Facebook has been moving user data out of the EU region, hence violating the user data policy.

To enforce their privacy law and punish violators, the EU is now imposing a $1.3 billion fine on Meta. But why these strict laws, and is there any threat if EU citizens’ data gets to other regions? In this article, we will look into this issue and the reason the EU demands these strict data regulations.

The reason behind the EU fine on Meta’s Facebook data transfers

In a bid to protect their citizens’ data, the EU came up with the bloc’s key digital privacy rules. This rule requires the data of EU citizens to be handled within servers located within the EU. With this rule in place, companies operating within the EU with access to user data can’t transfer this data to other regions.

For these companies, moving user data across a wide range of servers is quite easy. But, this action is risky as it exposes user data to regions with little or no user data regulations. In these regions, user data might not be safe, hence leading to threats to various cyberattacks.

Over the past few years, the EU has been beefing up its data protection regulations for its citizens. These regulations aim to protect their users from any element aiming to tamper with their data stored with big tech firms. But for some reason, Facebook, despite being aware of the bloc’s key digital privacy rules, moved data from EU servers to US servers.

Data protection regulations in the US aren’t as strict as they are in the EU, hence leaving certain loopholes. Meta’s actions put the data of EU citizens at risk of getting into the wrong hands. But despite the already existing EU-US Privacy Shield, moving data from the EU to the US isn’t advisable.

The court in charge of this case ruled the EU-US Privacy Shield as being invalid. For now, the Ireland Data Protection Commission requires that Meta’s Facebook stay clear of any data transfer for the next five months. Within this period, the EU, and the US can work on protecting data transferred between both regions.


[ad_2]
Source link

Microsoft system-preferred multifactor authentication aims to improve security

0
[ad_1]

In a bid to protect organizations and users from security threats, Microsoft is rolling out system-preferred multifactor authentication. This new system will pick the best authentication method for a user’s device. Some might kick against this method as it takes the freedom to pick any authentication away from the user.

Microsoft outlines the reasons why it is taking away this freedom from users. According to them, this action will not only protect individual users but also organizations from security threats. Currently, some users leave their devices and accounts vulnerable to attacks by choosing the wrong MFA system. This might be as a result of ignorance regarding the best MFA systems to use, or laziness to complete the procedures some systems require. Whatever the most common case may be, Microsoft is here to help you decide the best MFA system for yourself or your organization.

Get better security on your devices with the Microsoft system-preferred multifactor authentication

Multifactor authentication (MFA) is a very important aspect when it comes to protecting personal information. This system is designed to verify the user before granting access to specific data. There are various authentication methods available to users, with each offering a different level of security.

Some users make the mistake of selecting the wrong authentication method. This leaves their devices open to attacks from bad actors looking for the weakest link to break into confidential information. Without the right authentication method, a user, or a company, is open to malicious attacks that can breach the devices’ first layer of security.

Microsoft has identified this as a problem and is ready to proffer solutions to this issue. To solve this problem, users will now rely on the system-preferred multifactor authentication from Microsoft to pick the right method. This system will pick the best and most secure authentication method the user can sign in with.

For companies, the admin will be able to set up policies to guide the authentication method selection process. Integrating this service with a company’s workforce will require using the admin UX in the Azure Portal or via GraphAPI. With this, firms and their workers can rest easy knowing that they are making use of the most secure authentication method available on the system.

This feature is currently rolling out to users and companies as Microsoft managed (enabled). For now, admins can disable this feature whenever they want to, but all of that will change. After its rollout phase, users or tenants will no longer be able to disable this feature, as only the admin will have sole control of this feature.


[ad_2]
Source link