Attackers are now using GhostTouch attacks to hack your phone

0
[ad_1]

It comes as no surprise that threat actors and hackers have always used malware and phishing attacks to infiltrate devices and gain unauthorized access. However, according to new research from China’s Zhejiang University and Germany’s Technical University of Darmstadt, threat actors are now using a new technique called GhostTouch, which exploits electromagnetic signals to mimic gestures like swiping and tapping on the targeted device.

This new technique eliminates the need to install malware and allows threat actors to gain unauthorized access to smartphones, potentially compromising sensitive data, including passwords and banking applications.

As of now, nine smartphone models, including the iPhone SE (2020), Samsung Galaxy S20 FE 5G, Redmi 8, and Nokia 7.2, have been identified as vulnerable to this exploit.

Public places prone to GhostTouch attacks

While the idea of attackers remotely hacking your phone might sound alarming, it is important to note that threat actors need to be near their victims to carry out the attack. As a result, public places like libraries, cafes, or conference lobbies become the prime targets for such attacks.

Additionally, given that people keep their phones face down in quiet environments, such as the library, threat actors can take advantage of this situation by placing their hacking equipment nearby and emitting electromagnetic signals within a range of 40 mm.

However, it is important to note that these attacks are not inconspicuous. In fact, users will observe their phones seemingly operating on their own. But unfortunately, since the occurrences of glitches where the phone registers false touches are relatively common, many users may not even realize that a hacking attempt has taken place.

How to stay protected

While there is no foolproof solution to safeguard against GhostTouch attacks, users can take several steps to prevent hackers from gaining access. These include implementing robust security mechanisms like PIN codes, swipe patterns, or biometric authentication and refraining from placing their phones face down on tables.


[ad_2]
Source link

New Android & Google Device Vulnerability Reward Program

0
[ad_1]
Google's Device Vulnerability Reward

Google’s Device Vulnerability Reward Program helps the company identify security flaws in its operating system and devices.

To promote additional security research in areas of their products that will have a greater impact and protect the users’ security, Google is launching a new quality rating system for security vulnerability reports.

“We are pleased to announce that we are implementing a new quality rating system for security vulnerability reports to encourage more security research in higher impact areas of our products and ensure the security of our users,” Google.

Based on the level of information given in the report, this system will assign vulnerability reports a High, Medium, or Low-quality rating. Further, Google is raising the incentives for the most critical flaws to $15,000.

“The highest quality and most critical vulnerabilities are now eligible for larger rewards of up to $15,000!” Google said.

Significant Elements of the Report

  • Accurate and detailed description

A report should correctly and completely characterize the vulnerability, including the name and version of the affected device.

A proof-of-concept that successfully illustrates the vulnerability should be included in a report comprising video records, debugging output, or other pertinent data.

A report should contain a step-by-step procedure for reproducing the vulnerability on an eligible device running the most recent version.

A report should include evidence or analysis demonstrating the type of problem and the level of access or execution obtained.

Google also said it would no longer assign a Common Vulnerabilities and Exposures (CVE) classification to concerns of moderate severity, only to those of critical and high severity.

“Starting March 15th, 2023, Android will no longer assign Common Vulnerabilities and Exposures (CVEs) to the most moderate severity issues. CVEs will continue to be assigned to critical and high-severity vulnerabilities”, Google.

Google believes encouraging researchers to produce high-quality reports would strengthen the overall security community and its ability to take appropriate action.

“We believe that this new system will encourage researchers to provide more detailed reports, which will help us address reported issues more quickly and enable researchers to receive higher bounty rewards,” Google.

Struggling to Apply The Security Patch in Your System? – 
Try All-in-One Patch Manager Plus


[ad_2]
Source link

Galaxy Tab S7 FE, S6 Lite & A22 5G bag Samsung’s may update

0
[ad_1]

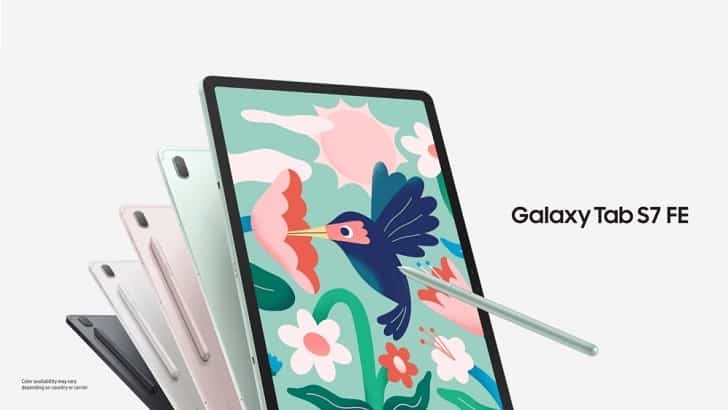
A few more Galaxy devices are picking up Samsung‘s May 2023 security update today. The company has released the latest security patch for the Galaxy Tab S7 FE, Galaxy Tab S6 Lite, and Galaxy A22 5G in some markets. A wider rollout should be just around the corner.

The May SMR (Security Maintenance Release) for the Galaxy Tab S7 FE is currently available in Europe and Latin America. The new firmware build number in the former market is T733XXS3CWD1, while that in the latter is T735XXU3CWE1. Users in Europe are only getting this month’s security patch but the update in Latin America brings One UI 5.1 as well. Note that the Galaxy Tab S7 FE has already received the One UI 5.1 update in Europe and most other regions.

For the Galaxy Tab S6 Lite, Samsung has begun rolling out the May SMR in its home country South Korea. The update comes with the firmware build number P615NKOS5FWD2 and doesn’t bring any goodies. It’s all about this month’s security fixes. This tablet has also already picked up One UI 5.1 in most markets. The latest security patch should be widely available for it in the coming days. Samsung has yet to release the May SMR for the 2022 refresh of the Galaxy Tab S6 Lite.

The Galaxy A22 5G is another Samsung device that recently started picking up the May SMR. The company has released the update in several Latin American countries, including Argentina, Bolivia, Brazil, Colombia, Guatemala, Mexico, Panama, the Dominican Republic, Trinidad & Tobago, and Uruguay. The updated firmware build number for this mid-range smartphone in the region is A226BRUBS5DWE1 (via). Its 4G-only sibling has yet to receive the latest security patch anywhere.

The May update for these Galaxy devices patches dozens of security flaws

This month’s security update for Samsung’s Galaxy devices contains more than 70 vulnerability patches. These include both Android OS issues and other problems specific to Samsung products. At least six of those were critical security flaws that could allow threat actors to remotely take control of your affected phone or tablet without you knowing about it.

Along with these security fixes, the May update for the Galaxy Tab S7 FE in Latin America also brings tons of new features and improvements that are part of One UI 5.1. If you’re using any of these devices, watch out for a notification about the latest update in the coming days. You can also manually check for new updates from the Settings app.


[ad_2]
Source link

How safe is your smartphone?

0
[ad_1]

In the digital age, the security of our personal data has never been more important. With smartphones playing an integral part in our daily lives, understanding the security features offered by the operating systems that power these devices is essential. Android, the world’s most popular mobile operating system, offers a multitude of security features designed to keep your data safe. This article delves into the security features provided by Android and explores how safe your smartphone really is.

Google Play Protect

Google Play Protect is a key security feature in Android devices. This system continually works in the background to keep your device, data, and apps safe. It automatically scans your device for potentially harmful apps (PHAs) and warns you if it detects anything suspicious.

In addition to scanning your device, Google Play Protect also verifies apps before you download them from the Google Play Store. This proactive approach helps to prevent any threats from entering your device in the first place. It’s a robust system that ensures the apps you download are safe and that your device stays secure.

Biometric Security Features

Biometric security features provide an additional layer of protection for Android devices. These features include fingerprint scanners, facial recognition, and even iris scanners on some devices. They provide a quick and secure way to unlock your device, authenticate payments, or sign-in to apps.

Biometric data is stored securely on your device, and Android uses strong encryption to protect this information. Additionally, Android’s BiometricPrompt API provides developers with a system-wide standard for biometric authentication, ensuring that apps that use biometrics, including banking apps or online casinos, offer a consistent and safe experience.

Encryption and Secure Boot

Android devices use encryption to protect your data, even if your device falls into the wrong hands. When your data is encrypted, it’s transformed into a form that can only be read with the correct decryption key.

Android also uses a feature called secure boot to ensure that your device hasn’t been tampered with. When your device boots up, it performs a series of checks to verify the integrity of the software. If it detects anything abnormal, it won’t boot, keeping your data secure.

Regular Security Updates

Regular security updates are an essential part of keeping Android devices safe. Google releases monthly security updates for Android, which include fixes for any security vulnerabilities that have been discovered.

Manufacturers are responsible for delivering these updates to their devices. Google has worked with manufacturers to ensure that more devices receive these important updates, helping to keep all Android devices safer.

Android’s Open-Source Advantage

Android’s open-source nature is often viewed as a security advantage. Because anyone can view and inspect Android’s source code, it’s continually scrutinized by researchers and developers worldwide. This widespread examination helps to identify and fix potential security issues quickly.

However, this openness can also be a double-edged sword, as it potentially allows malicious actors to find vulnerabilities. That’s why the quick patching of identified vulnerabilities and regular system updates are crucial to maintaining Android’s overall security.

Sandbox Isolation

An often overlooked but crucial Android security feature is the concept of sandboxing. Sandboxing isolates apps from each other, restricting their ability to interact with other apps or access data they aren’t permitted to use.

When you download an app from the Google Play Store, it runs in its own sandbox, separate from other apps on your device. This means that even if an app is compromised, the potential damage is limited because the malicious app can’t access data from other apps or sensitive system resources without explicit permission.

Moreover, Android’s permission system works hand in hand with sandboxing. Apps must request permission to access sensitive data like your contacts, location, or camera, and you have the control to grant or deny these requests. This combination of sandboxing and permission requests provides a strong defence against potential security threats.

Two-Factor Authentication (2FA)

Two-factor authentication, or 2FA, is a vital security feature that Android users can leverage to protect their accounts and personal data. By requiring a second form of identification, in addition to the usual password, 2FA significantly reduces the risk of unauthorized access.

In the context of Android, Google facilitates 2FA through prompts sent to your mobile device or via Google Authenticator, an app that generates time-based verification codes. When you try to log in to your Google account from a new device, you’ll need to provide both your password and the code generated by the Authenticator or the prompt on your phone.

Using 2FA on your Android device provides an additional layer of security, especially for critical accounts such as your primary email or Google account. By requiring something you know (your password) and something you have (your phone to receive or generate the 2FA code), it becomes much more challenging for malicious actors to gain unauthorized access to your accounts.

Conclusion

With features like Google Play Protect, biometric security, encryption, secure boot, and regular security updates, Android offers a robust security framework designed to keep your device and data safe. The open-source nature of Android also contributes to its security, despite posing unique challenges.

Whether you’re using your Android device for everyday tasks, managing financial transactions, or enjoying online casinos on MrCasinova.com, it’s crucial to understand these security features. By staying informed and ensuring you’re using an updated device, you can have peace of mind knowing that your Android smartphone is well equipped to protect your data.
[ad_2]
Source link

Android 13 QPR3 Beta 3.2 rolling out with a host of bug fixes

0
[ad_1]

Google is rolling out yet another Android 13 QPR3 beta update to Pixel devices. The latest release, labeled Beta 3.2, comes about two weeks after Beta 3.1 and brings a host of bug fixes. Android 13 QPR3 stable build will roll out next month as a new Feature Drop for Pixels, the third such quarterly release based on Android 13.

According to Google’s official release notes, Android 13 QPR3 Beta 3.2 fixes an input synchronization issue with the system UI that caused the Pixel devices to incorrectly read touch inputs or completely stop reading touch inputs sometimes. The company has also patched the issue of Wi-Fi calls disconnecting unexpectedly. Another bug that prevented the devices from detecting the SIM card during the setup process or even during regular usage has also been fixed.

Additionally, Google has removed a bug that didn’t allow Pixels to register IMS over Wi-Fi after leaving LTE coverage and entering Wi-Fi coverage. Last but not least, Android 13 QPR3 Beta 3.2 eliminates the reliability issue with cellular connectivity. Pixel users who have installed previous beta builds have been reporting a sudden drop in signal strength and internet speed. The latest update will patch this issue. The Beta 3.1 update also patched several issues present in earlier Android 13 QPR3 releases.

Android 13 QPR3 Beta 3.2 is rolling out to eligible Pixel devices

Google started rolling out the Android 13 QPR3 Beta 3.2 update to Pixel devices on Tuesday, May 16. It will be available to all eligible devices via an OTA (over the air) update within the next few days. Eligible devices include all models from Pixel 4a to Pixel 7 series running any earlier QPR3 beta build. The newly-launched Pixel 7a isn’t eligible. It arrived too late for the QPR3 beta. Google will push the next Feature Drop to it, though.

For the Pixel 6, Pixel 6 Pro, and Pixel 6a on Verizon’s network, the latest build number is T3B3.230413.009.A1. For all other devices, including these three on other networks, it’s T3B3.230413.009. The former group is still on the April security patch while the rest of the Pixel lineup is running the May security patch. If you’re wondering which QPR3 beta build you’re currently on, you can refer to Google’s release notes here for more information.

Note that Google has already launched an Android 14 beta program. Those who have enrolled in it won’t receive Android 13 beta updates. If you want to try out the next major Android update early on your Pixel phone, you can enroll your device here. Google doesn’t seem to have opened the program to the Pixel 7a yet. The stable Android 14 update should arrive sometime in August.


[ad_2]
Source link

YouTube algorithm is exposing young gamers to gun violence

0
[ad_1]

In this day and age of short-form video content, YouTube’s recommendation algorithm has made it the go-to platform for entertainment, education, and everything in between. However, a recent report from the Tech Transparency Project (TTP), a nonprofit watchdog group, suggests that the YouTube algorithm is now leading young boys interested in video games towards videos centred around school shootings and gun violence.

The incident came to light when researchers from the Tech Transparency Project created new YouTube accounts and pretended to be two 9-year-old boys and two 14-year-old boys. Once the accounts were live, they watched hours of video game content, including Roblox, Halo, and Grand Theft Auto, and recorded their recommendations over 30 days.

After analyzing the data, the researchers then discovered that the YouTube algorithm was promoting content related to gun violence and weapons to all gamer accounts. However, the volume of such content was significantly higher for users who clicked on the recommended videos. These videos included graphic demonstrations of the destructive power of guns, scenes depicting school shootings and other mass shooting events, and guides on how to convert a handgun into a fully automatic weapon. Furthermore, the platform even monetized some of these videos, thus violating its own policies.

“Children who aren’t old enough to buy a gun shouldn’t be able to turn to YouTube to learn how to build a firearm, modify it to make it deadlier, or commit atrocities,” said Justin Wagner, director of investigations at Everytown for Gun Safety.

YouTube’s response

In response to the report, a YouTube spokesperson emphasized the existence of the YouTube Kids app and stated, “We welcome research on our recommendations, and we’re exploring more ways to bring in academic researchers to study our systems. But in reviewing this report’s methodology, it’s difficult for us to draw strong conclusions. For example, the study doesn’t provide the context of how many overall videos were recommended to the test accounts, and also doesn’t give insight into how the test accounts were set up, including whether YouTube’s Supervised Experiences tools were applied.”


[ad_2]
Source link

Facebook & Instagram Begun Rolling Out Paid Blue Tick

0
[ad_1]
Facebook Paid Blue Tick

Meta is introducing Meta Verified on Facebook and Instagram. The popular social networking platform will now permit anyone who agrees to pay the price to have a blue tick on their profile.  

Previously, Twitter sold the blue tick exclusively given to well-known people. Also, Instagram’s policy permitted influencers, politicians, celebrities, and those working in the media to have a blue checkmark next to their name.

The Service Provides Protection From Impersonation

The company offers Facebook and Instagram users a blue tick starting at £9.99 per month, much like Elon Musk’s Twitter Blue.

To be eligible, subscribers must be at least 18 years old and provide a valid government ID. In the US, Australia, and New Zealand, the feature is already accessible. In the following weeks, it will be available to UK people.

Those who Meta has approved will receive a verified badge, which the tech company claims will provide them with “proactive impersonation protection,” which helps stop anyone from impersonating online. 

According to the statement, verified users will also have “access to a real person” if they run into any problems with their accounts.

The service is aimed at creators who want to establish their authenticity on social media, protect their accounts from impersonation, and gain access to more features and support; it also provides direct access to customer support, exclusive stickers, and 100 “Stars” per month on Facebook.

According to sources, users verified on Facebook and Instagram would no longer be required to pay for Meta’s paid verification plan. Rules could alter if Meta decides to remove the legacy accounts.

Users who are “a public figure, celebrity, or brand and meet the account and eligibility requirements,” as stated on the platforms’ support pages, may still apply for a verified badge. This is in addition to joining Meta Verified.

Following the Twitter Blue subscription

Following the launch of Musk’s premium Twitter Blue subscription in November 2022, action was taken.

Particularly, on April 20, Musk withdrew what became known as “legacy” verification ticks from account users, reserving the “verified” blue badge for those who had paid for Twitter Blue and authenticated their phone numbers.

A paid layer that boosts prominence has been added to monetize the platforms in various ways. At the time, Meta CEO Mark Zuckerberg stated that he had projected an increase in the company’s growth but that it had not occurred.

Struggling to Apply The Security Patch in Your System? – 
Try All-in-One Patch Manager Plus


[ad_2]
Source link

PharMerica breach impacts almost 6 million people

0
[ad_1]

US pharmacy giant PharMerica has reported a cybersecurity incident that affects over 5.8 million people. The data theft has been claimed by ransomware group Money Message.

US pharmacy giant PharMerica has notified over 5.8 million people about a security incident in which it says personal information and medical information may have been obtained by cybercriminals. The Data Breach Notification lists the total number of persons affected as 5,815,591.

An investigation was started after PharMerica noticed suspicious activity on its network. The investigation showed that an unauthorized party accessed PharMerica computer systems on March 12-13, 2023, and that this party may have had access to certain personal information. The incident was noticed on March 14, and a week later PharMerica identified that the personal information accessed included names, dates of birth, Social Security numbers, medication lists and health insurance information.

Ransomware group Money Message has claimed responsibility for the attack. The gang claims that they encrypted almost the entire PharMerica infrastructure, and has published parts of the stolen data to their leak site.

screenshot of Money Message leak site showing PharMerica

Image courtesy of BleepingComputer

Money Message is a new ransomware which targets both Windows and Linux systems. As we mentioned in our May ransomware review, Taiwanese PC parts maker MSI also fell victim to Money Message.

On its website PharMerica says:

“At this point, PharMerica is not aware of any fraud or identity theft to any individual as a result of this incident, but is nonetheless notifying potentially affected individuals to provide them with more information and resources. The notice will include information on steps individuals can take to protect themselves against potential fraud or identity theft. PharMerica has arranged for complimentary identity protection and credit monitoring services for potentially affected individuals.”

An extra point of concern is that a relative large part of the people affected by the breach have passed away, which makes it unlikely that relatives will regularly monitor their credit reports, making any cybercrime related to the stolen data even more difficult to detect and stop.

What to do if you’ve been caught in a data breach

There are some actions you can take if you are, or suspect you may have been, the victim of a data breach.

  • Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened, and follow any specific advice they offer.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop or phone as your second factor. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for fake vendors. The thieves may contact you posing as the vendor. Check the vendor website to see if they are contacting victims, and verify any contacts using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Apple Personalize Voice feature is coming to the iPhone very soon

0
[ad_1]

Part of the features coming to iPhones and other Apple products is the Personalize Voice feature. Most of the features that will make their way to the public will help Apple devices be more accessible to users. In this article, we will focus on a feature that will adapt to an Apple device user’s voice for real-time usage.

Apple says that it’d be helpful if your smartphone could speak for you when necessary. Well, devices like the Google Pixel can talk to their users during calls. They do this with the text-to-speech feature which enables users to type the sentences and the device reads them aloud.

This is a cool feature, but Apple is looking at the bigger picture here as it makes this feature even better. Instead of using a computerized voice to read aloud sentences during calls, Apple aims for something different and special. With this feature, users will be able to hear their voice read aloud typed sentences.

More accessibility coming to iPhones with the Personalize Voice feature

This feature aims to help users with some sort of speech impediment make calls. Users will be able to use this feature on apps like FaceTime and also during in-person conversations. Simply type out what you wish to say and the Apple device will read it aloud to your hearing.

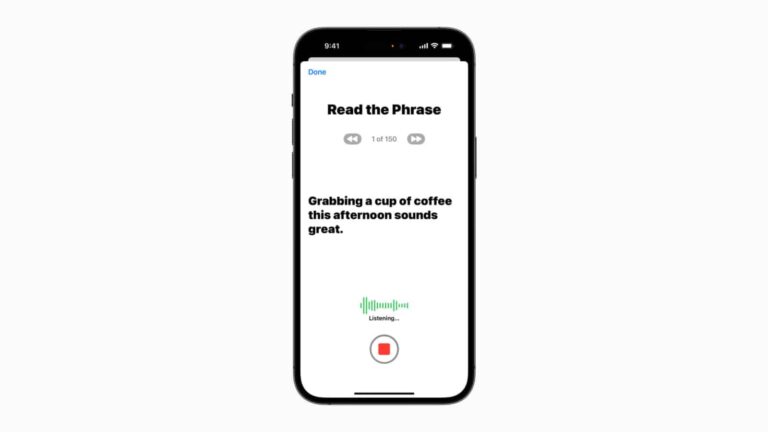
But what makes this feature interesting is that it will sound like the user while reading aloud. To set this up, users will have to read along with random text prompts that Apple will make available. While reading these prompts, the device will record the user’s voice for real-time usage.

There will be about 150 prompts for users to read through, this will help train the device to mimic their voice. The entire process will take about 15 minutes and after this, the Personalize Voice feature will be ready for usage. Once the setup process is complete, users can now type out sentences to be read aloud with their voice during calls.

All sentences this feature reads out remain private and secure, so users can feel at ease using it. During calls, users can chip in commonly used phrases like ‘How are you doing’ without having to type them out. This will change the way most users interact with their iPhones and other Apple products.

While this feature is designed to help those with speech impediments, it can also be put to use by anyone. This feature alongside others will become available to users globally after the coming Apple event. Will you be eager to listen to your voice during calls with the use of this feature?


[ad_2]
Source link

1Password is finally rolling out passkey support

0
[ad_1]

It’s no secret that no one has ever been a fan of remembering their passwords. However, the recent LastPass data breach has prompted many individuals to consider alternative password managers like 1Password. Now, to capture the market even further, 1Password will finally roll out passkey support starting June 6th, which will allow users to access websites and services without having to type in usernames and passwords.

While the announcement of passkey support is a step in the right direction towards a passwordless future, 1Password doesn’t plan to immediately grant access to replace your master password. Initially, the rollout will begin in beta, and users will need to download the 1Password beta browser extension, available for Safari, Firefox, and Chromium-based browsers. Furthermore, passkey support for mobile devices is still under development and will not be available with the current beta access.

What are Passkeys?

Developed by the FIDO authentication standards, passkeys are a form of authentication technology that generates two cryptographic keys: one public and one private, associated with the user’s account. Therefore, when a user attempts to log in to a service using passkeys, 1Password will use the public key to verify the person’s identity by matching it with the private key. This process ensures stronger security, as passkeys are resistant to phishing attempts. Additionally, since one of the key pairs is stored on the user’s device, login information remains secure even in the event of a data breach.

Moreover, the fact that 1Password does not rely on Apple’s iCloud passkey support or Google’s Password Manager makes it a better choice for users who use both iOS and Android simultaneously. Additionally, users can also securely share their passkeys with their family members.

Although companies like Google and Apple consider passkeys to be the future, the technology is still relatively new. 1Password itself maintains a list of sites and services that support passkeys, and it only has 38 entries listed. Therefore, even with more sites adopting passkeys, we still have a long way to go before we eliminate the need for passwords.


[ad_2]
Source link