Why we should be more open about ransomware attacks

0
[ad_1]

Paying the ransom and not saying a word about what happened is what cybercriminals would like us all to do.

The UK’s National Cyber Security Centre (NCSC) has published an article that reflects on why it’s so concerning when cyberattacks go unreported, saying:

…we are increasingly concerned about what happens behind the scenes of the attacks we don’t hear about, particularly the ransomware ones.

One of the main reasons is that with visibility, it is easier to get a good picture of what is going on, what methods the criminals are using, and maybe even who they are. Another argument is that paying the ransom and keeping quiet about the fact that you have been attacked has a few negative consequences:

  • Paying the ransom funds the criminal ecosystem.
  • Not doing a thorough, third-party investigation could leave the access method used by the criminals wide open for the next attack.
  • If the news of the cyberattack gets into the public domain later it can be much more damaging than communicating about it straight away.
  • Good backups often restore encrypted systems faster and more effectively than paying a ransom for a decryptor provided by the criminals. Decryptors can be slow, and they have been known to fail (even though the criminals will tell you they work seamlessly).

Depending on the country an organization is based in, whether they handle data under GDPR regulations, whether they are a government contractor, what sector they are active in, or whatever other reasons, some organizations have a legal obligation to notify one or more authorities about a cyberattack.

This has led to some misconceptions in the past. For example, for some time researchers were under the impression that SamSam ransomware, one of the earliest “big game” ransomware gangs, specifically targeted healthcare providers. Later it turned out that most of its victims were in the private sector, but because a lot of the healthcare victims were obliged by law to report the attacks and none of the private sector victims were, the reported incidents painted a skewed picture of what was actually happening.

There are some obvious reasons why organizations would want to keep attacks under wraps. One of them is the fear of the fines involved in a data breach. Some ransomware gangs actually use these fines as an argument to persuade victims to pay a ransom. The NCSC provided an example of a ransomware message that stated:

The ransom demand is £50 million. If you pay, you’ll avoid a regulator fine of £600 million which is 0.5% of your annual profit.

The NCSC goes on to say that a data leak isn’t the only reason for a fine, and you won’t always be fined if data is leaked. From what we have seen, trying to cover a data leak up and then getting exposed later on, will drive the penalty to the max.

The stats in our monthly ransomware reports are based on known ransomware attacks, published by ransomware gangs on their Dark Web sites and Telegram channels. This means we only have visibility on successful attacks where the victim refused to pay. Estimates by experts like Allan Liska are that this is just the tip of the iceberg. We might be seeing only 10% of what is really going on. While there are no reasons to believe that this could change the proportions, in some cases it might.

  • If there are still ransomware gangs without a leak site, we would lack visibility. (At the moment we do not believe any of the major players operate without a leak site or a Telegram channel to leak stolen data.)
  • Ransomware gangs may not publicise attacks that fail to steal valuable data—news of failures would likely put off affiliates and have a negative impact on their income.

Basically, the NCSC is asking victims to do the right thing and allow us to learn from successful attacks, which can help others to avoid falling victim to the same methods. We do understand that some organizations feel they have no other choice but to pay. But even then, investigate the incident and share your findings so others may learn.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Galaxy A52s 5G & Galaxy A72 get Samsung’s May update

0
[ad_1]

Samsung has released the May 2023 update for a couple of premium mid-range smartphones from 2021. The Galaxy A52s 5G and Galaxy A72 follow the Galaxy A52 to the latest security update party. The new SMR (Security Maintenance Release) has been already rolled out to dozens of other Galaxy devices.

The May SMR for the Galaxy A52s 5G is currently available in a handful of countries in Latin America. Users in Mexico are getting this update with the firmware build number A528BXXS3EWD5. That for users in Bolivia, Peru, Brazil, Uruguay, Colombia, and Paraguay is A528BXXS3EWD4. The update doesn’t seem to bring any new features or improvements. Samsung is only pushing the latest security fixes to the device. A global rollout should follow in the coming days. The Galaxy A52s 5G wasn’t released in the US.

The latest security update is also available to the Galaxy A72 in Latin America. The rollout began recently with the firmware build number A725MUBU5DWE1 in Argentina. The build number suggests the update contains more than just the latest security fixes. Maybe it brings One UI 5.1. Unfortunately, Samsung hasn’t yet added this release to its update tracker. So we can’t confirm anything. We expect the update to reach more markets in the coming days. Like the Galaxy A52s 5G, this phone also didn’t arrive in the US.

As usual, you will receive a notification once this update becomes available for your Galaxy A52s 5G or Galaxy A72. You can also manually check for updates from the Settings app. Go to the Software update menu and tap on Download and install. If an update is available, you will be prompted to download it. But if you don’t see any pending OTA (over the air) update today, wait a few days and check again. The May SMR contains fixes for more than 70 security flaws, including at least six critical issues across the Galaxy family.

Galaxy A52s 5G and Galaxy A72 should get the Android 14 update

Samsung released the Galaxy A52s and Galaxy A72 in September and March of 2021, respectively. Both devices came running Android 11 out of the box. They have since picked up updates to Android 12 and Android 13. Based on Samsung’s update policy, they should get one more major Android OS release. So the Android 14 will probably reach the two premium mid-range models. The rollout is expected to begin later this year but the Galaxy A52s and Galaxy A72 may not receive it until next year.


[ad_2]
Source link

The future of Android security

0
[ad_1]

Most people got introduced to Androids when they were watching Dragon Ball Z and knew them as robots that looked like humans. Even though that’s the main definition of the word, times have changed, and it now stands for phones that use an Android operating system.

Always battling for the top spot with iPhones in all aspects, there’s been a general debate that Android security pales in comparison. Most of the world uses Android, so let’s look at the future and how tomorrow’s threats can be defeated today.

The current state of Android security

Based on the most recent data, there are 3.6 billion people using Android devices, and there are more than 24000 different devices. It’s the Windows of mobile. This operating system is straightforward to code, open-source, and extremely widespread. Thus, making it the prime target for cyber attackers and hackers. Phishing attacks, data breaches, viruses, and malware are much more prevalent than the iPhone.

However, there’s a reason for that. There are only 14 models of the iPhone, but Android devices come in all shapes and sizes. Different manufacturers can play with the hardware and the software, making patching nearly impossible. Even when an update is released, most people ignore it, leading to even more security breaches.

Of course, this doesn’t mean they aren’t safe to use. Two-factor authentication, encrypted data, antiviruses, VPNs, and biometric authenticators added multiple layers of protection, which raised the level of security and decreased malicious content and apps by a large margin.

The Future of Android Security

The most significant part of Android is that it evolves rapidly. For example, artificial intelligence and machine learning can bulletproof this operating system’s security level. Most people are familiar with ChatGPT, but that’s only one piece of the technology. Machine learning algorithms can be trained on attacks that happened in the past and churn out new models that have much better protection. Not only that, AI can identify the patterns of user behavior and analyze them.

Now, here’s where it gets really interesting. Your phone could become a companion that recognizes when someone else is using the device. It will be trained on your typing speed to know whether it’s you using messaging applications. Your finger movement is unique, which can be tracked and used to see whether the phone is being used by someone else. These subtle cues are much stronger than a regular password.

Apart from artificial intelligence and machine learning, there’s blockchain technology. Hackers won’t be able to steal data or tamper with it because new storage systems could be added to keep everything in a decentralized manner. Medical records, transactions, and other sensitive data will be kept securely, meaning that even if a hacker gets a hold of a device, they won’t be able to find what they’re looking for.

What are the challenges?

The diversity of Android models and devices is both a blessing and a curse. Billions of people have an easy and affordable way to use the internet. But not all of them have the necessary knowledge to protect themselves from threats. A consistent security solution is nearly impossible because some devices are outdated, and users would need to replace them with newer models.

Next on the list is the number of existing applications that get deployed daily. Cybercriminals are always trying to attach malware to applications in the Play Store, which can exploit the data of those who download them. Of course, Google is well aware of the problem, and they’ve deployed Play Protect, App Signing, and stricter requirements for apps. But, there are still cracks where malware can pass through.

How can you be safe?

Rule number one is to always download applications from the Play Store. Don’t root your phone and install APKs that can compromise your device. When you drop the shields and firewalls, it’s easy for an unsuspecting app to spy on you.

Most people bring their phones when traveling and connect to every possible internet source. Unless you’ve got a VPN, don’t use public Wi-Fi. Hackers can make fake hotspots to breach your device and steal your data.

The same thing’s true at home. Your smart TV is probably unprotected while connected to your router. Use a VPN for Android TV and any other IoT device to ensure no prying eyes start spying on you.

Furthermore, whenever you see a software update, download and install it immediately. The five minutes it takes to reboot your device also enhances the operating system and ensures you’re protected against the newest attacks. You might hit snooze on your alarm, but don’t hit the snooze on an update!

Finally, don’t use your social media accounts to log into apps. The good, old-fashioned way of entering an email is much better than a one-click login with your Facebook. There’s one reason for that. If your device gets hacked, all your friends and family will likely be too. Launching a phishing attack when someone has your account will be incredibly easy because no one will doubt whether it’s you.

Should you just get an iPhone?

Even though it’s tempting to ditch your Android because of security reasons, the main culprit behind a breach is user behavior. If you follow all the cybersecurity norms and tips, you’ll be completely safe from prying eyes, hacks, and malware. Take care of your devices so that they can care for you!


[ad_2]
Source link

WhatsApp tests the ability to edit sent messages

0
[ad_1]

WhatsApp, the popular instant messaging app, has released a new beta version for Android – version 2.23.10.13. This latest update brings several new features and improvements to the app, including the ability to edit sent messages for some select users.


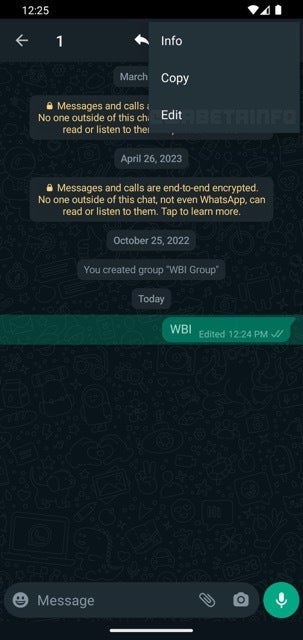
The key feature rolling out with this update would allow users to edit messages they have already sent. This feature has been highly requested by WhatsApp users for some time, as it would give them the ability to correct mistakes or clarify unclear messages that were perhaps sent accidentally.


As reported by WABetaInfo, the feature works by allowing users to tap on a sent message and select the “Edit” option from the top menu. They could then make changes to the message, and the edited version would be visible to all recipients of the original message.
However, there are some limitations to the feature – edited messages will still show a notification that they have been edited, and there will be a limit on how much time users have to edit their messages after they have been sent. The current time limit to edit a message is within 15 minutes of sending it and you cannot edit a message that you sent from a different device. Once edited, the message will show an “edited” label on it to notify other users that the message is no longer the original one.

Not all users enrolled in the WhatsApp Beta Program are currently able to test this feature, as it appears to be rolling out to only a certain amount of users, suggesting a staged rollout. Hopefully this won’t take long to roll out to the stable version of WhatsApp, as I anticipate it would likely be welcomed by many users. However, it remains to be seen if and when the feature will become widely available to all.


[ad_2]
Source link

Hackers Overcome Microsoft Default Macro Block

0
[ad_1]
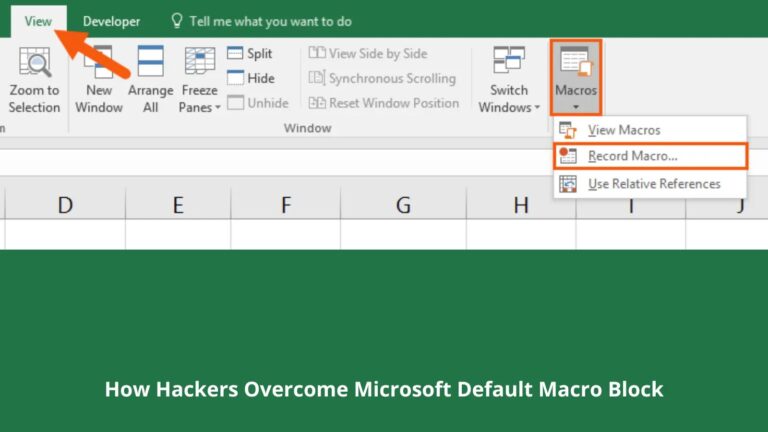
Microsoft Default macro Block

There has been a shift in threat actor behavior in recent years. Observations by threat researchers showed a peak in their change of activities.

Ever since, Microsoft disabled macros by default, which was extensively exploited by threat actors and paved the initial way for ransomware attacks.

In October 2021, Microsoft announced they would block XL4 and VBA macros by default for MS Office users, which was rolled out in 2022. Proofpoint analysis and report showed how threat actors experimented with payload delivery, old file types, and unpredictable attack chains.

As per the reports from Proofpoint research conducted between January 2021 and March 2023,

  • Threat actors are researching the most effective way to infiltrate, which has no reliable or consistent technique. Multiple methods are in use.
  • A new technique implemented by one threat group is adopted by several other groups later.
  • Several malware delivery methods are under testing phases by many sophisticated e-crime actors.

There has been a downslope in campaigns using macros. Compared to 2021, macros-based campaigns have reduced by up to 66% in 2022. There has been minimal usage of macros-based campaigns in 2023.

Macros-based campaigns [Source: Proofpoint]

Alternatively, ISO attachment-based campaigns were adopted initially, which bypasses the macros restriction, which works around the mark-of-the-web (MOTW) attribute restriction. However, it was fixed by Microsoft in November 2022.

In addition, HTML smuggling, PDF-based campaigns, and OneNote explosions were several other methods that threat actors adopted.

According to February 2023 campaigns, nine different attack chains are followed by threat actors currently.

  • Zip Attachment → OneNote File → HTA → Qbot DLL
  • OneNote Attachment → HTA → CURL → Qbot DLL
  • URL → Zip → OneNote File → HTA → CURL→ Qbot DLL
  • PDF Attachment → Actor-Controlled URL → Zip → ISO → LNK → CMD → EXE → Qbot DLL
  • OneNote Attachment → WSF → JScript → PowerShell → Qbot DLL
  • PDF Attachment → OneDrive URL → JavaScript File → PowerShell → Qbot DLL
  • OneNote Attachment → CMD → PowerShell → Qbot DLL
  • OneNote Attachment → CHM → PowerShell → Qbot DLL
  • HTML Attachment → Pop Up → HTML Smuggling → Zip → Password → IMG → LNK → CMD → REG → WSF → PowerShell → Qbot DLL

A Complete detailed analysis of the report has been published by Proofpoint, which shows various techniques and methods used by threat actors.

Users must be aware when downloading or opening any malicious attachments and be vigilant about these threat actors.

Struggling to Apply The Security Patch in Your System? – 
Try All-in-One Patch Manager Plus


[ad_2]
Source link

Windows 11 is showing its first signs of Rust

0
[ad_1]

We take a look at the slow introduction of programming language Rust into the Windows 11 kernel in an effort to make it more memory safe.

Some important changes are heading to Windows which should make the operating system quite a bit more secure than it is now. At the end of April, Microsoft’s VP of OS Security and Enterprise referenced upcoming changes to Windows involving the programming language Rust.

Rust matches the performance of languages like C and C++ while being easier to debug and maintain, and—most importantly—memory safe. It is highly desired by some programmers—you can see his excitement in the below talk from Blue Hat IL 2023:

At the time, he cautioned that “rewriting Windows in Rust isn’t going to happen anytime soon”. However, he also mentioned that Rust would be making an appearance in the operating system’s Kernel “in the next several weeks or months”.

That moment has now arrived for folks on the Windows 11 Insider program:

Why is this such good news? Well, the kernel is the core component of a computer operating system and is crucial to how it functions. It’s one of the first things to fire up when a computer is switched on, and then it sits in memory permanently, mediating between the computer’s applications and hardware.

If an attacker successfully compromises a kernel, they can expect to have full control over the device it’s running on, which is of course very bad indeed. These issues aren’t just Windows specific—you can end up with a kernel disaster on a Mac, or over in Linux land, too.

A big part of kernel exploitation is focused on memory management. Traditionally, the most popular coding languages for kernels have been C and C++, which provide excellent performance and lots of flexibility, and a lot of rope to hang yourself with when it comes to security. When people with bad intentions stroll into town, one of the key places they prod around is in the realm of memory. Bugs and errors in this area can lead to exploitation, and making the memory unstable can cause malfunctions or allow for malicious code.

A huge part of this is the dreaded buffer overflow attack, which has been around since the 1970s. This is when data written to a buffer spills out and overwrites nearby memory. When the system’s memory is tampered with in this way it can lead to all manner of exploitation.

Despite endless attempts to get programmers to write more secure code, improvements to the underlying languages, and mitigations like Windows Address Space Layout Randomization (ASLR), buffer overflows continue to be a huge problem. The only way to root them out completely is to switch away from C and C++ to a memory safe language like Rust that can manage memory automatically.

This approach has already proven to be more reliable than hoping programmers will do the right thing: The adoption of memory safe languages in Android, which predates Windows by several years, has lead to signficiant decline in memory safety vulnerabilities on that platform.

According to Google, in situations where Rust has been used on low-level Android components instead of C++, there have been “zero memory safety vulnerabilities discovered.”

The work of switching out C++ for Rust in Windows 11 has already begun. As per The Register, the Microsoft Windows graphics interface device is currently being ported to Rust to the tune of 36,000 lines of Rust code, and there’s a system call (SysCall) in the Windows kernel right now which is implemented in Rust.

While the “wouldn’t it be nice” dream of replacing all pieces of C and C++ in Windows with safer, better alternatives is likely impossible, big and important strides in memory safety are finally being made. What we have here is yet another good reason to finally make the leap from Windows 10 to 11.


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Galaxy S23 Tac Edition is made specifically for the US military

0
[ad_1]

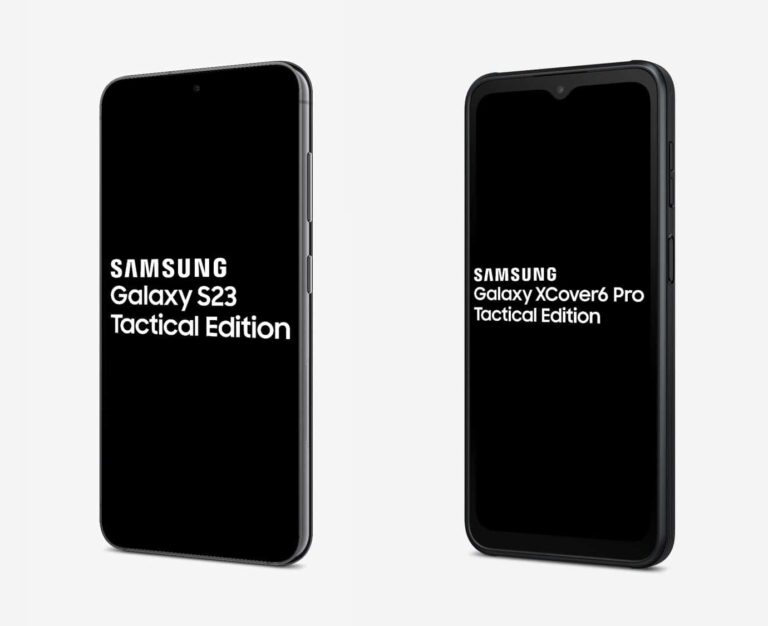
Samsung has launched a special edition Galaxy S23 in the US. The Galaxy S23 Tactical Edition is a unique phone made specifically for the United States Department of Defense (DOD) personnel. The company has also added the Galaxy XCover 6 Pro to the Tactical Edition portfolio.

Samsung launches new Tactical Edition Galaxy devices for DOD personnel

The Galaxy S23 and Galaxy Xcover 6 Pro Tactical Edition are mission-ready devices equipped with advanced capabilities based on military security requirements. These mobile devices are part of a comprehensive partner ecosystem that includes custom software and features. Samsung ships the devices with purpose-built drivers that support tactical radio and mission device protocols.

They let DOD personnel access drone feeds and laser rangefinder information while simultaneously offering conventional cellular capabilities, including LTE, CBRS (Citizens Broadband Radio Service), Bluetooth, and Wi-Fi. A stealth mode lets operators LTE and e-911 and mute all radio frequency broadcasting for completely off-grid communications. The Tactical Edition devices also offer secure tactical communication systems.

For on-device security, Samsung has equipped the devices with its defense-grade security platform Knox. Its Knox Dual Data at Rest (DualDAR) service is an NSA (National Security Agency) approved security service that provides dual-layer encryption to protect confidential data even when the device is powered off or in an unauthenticated state. It ensures the secure storage of sensitive information or safe use of the devices in mission-critical environments.

The Galaxy S23 and Galaxy Xcover 6 Pro Tactical Edition devices also come preloaded with special apps. Samsung names the Android Team Awareness Kit (ATAK) and the Battlefield Assisted Trauma Distributed Observation Kit (BATDOK). ATAK and BATDOK. The former helps improve the real-time situational awareness of operators through mapping, messaging, and geo-fencing. All team members can simultaneously see the necessary information on their screens.

The latter, meanwhile, helps collect and distribute real-time patient encounter information. It enables medics quickly obtain a patient’s treatment history and also monitors the vitals of patients. They can then convey the information forward for advanced care if needed. These apps come with an optimized interface along with support for the programmable side button on the Galaxy Xcover 6 Pro. The devices also seamlessly integrate with a range of peripherals.

Along with all these tailored customizations, the Galaxy S23 and Galaxy Xcover 6 Pro Tactical Edition also benefit from the devices’ existing set of security features and durability. The former has Gorilla Glass Victus+ protection and an Armor Aluminum frame. It includes a rugged military-grade case as well. The latter, meanwhile, has a MIL-STD-810H standard ruggedness. Both models boast an IP68 rating and night vision mode as well. Military personnel can also leverage Samsung DeX to quickly create a desktop experience without needing one.

The latest Tactical Edition devices will arrive later this summer

Samsung has collaborated with the DOD for special edition products for over a decade now. It has launched Tactical Edition versions of its latest Galaxy devices in the past as well. The Galaxy S20 Tactical Edition in 2020 was the last such device. The company has now come up with two more. It unveiled the Galaxy S23 and Galaxy Xcover 6 Pro Tactical Edition devices at the national convention for the United States Special Operations Forces (SOF Week 2023) last week. Samsung will release the devices later this summer.


[ad_2]
Source link

Apple’s M3 Pro-powered MacBook Pro to have improved performance

0
[ad_1]

Apple is already testing its M3 Pro-powered MacBook Pro, and it features some improvements. According to Bloomberg’s Mark Gurman, the Cupertino-based tech company is preparing to shock the tech community. One can also say that they are preparing to live up to the standard they have set for the performance of their MacBook Pro devices.

This is the case because ever since Apple ditched Intel processors, it’s been one performance improvement to the other. The launch of the M-series processor line has been a breakthrough for Apple fans and creatives. MacBooks powered with this processor series perform outstandingly well, and they keep getting better with every new generation.

Now, it is time for netizens to welcome a new entry into the Apple M-series processor line-up. Under consideration in this article will be the Pro entry in the coming processor series. What should Apple users expect from this processor and what device will it power?

Better performance comes with the M3 Pro-powered MacBook Pro

In a recent Power On newsletter from Mark Gurman the tipster pointed out the presence of an M3 Pro processor. This chip will succeed the current M2 Pro that is in use on the current 14-inch MacBook Pro. Certainly, netizens and Apple fans alike can expect some upgrades with this processor.

Details regarding this new processor are still a bit sparse, as it might not launch anytime soon. However, Mark Gurman confirmed from his sources that this processor is already in its testing phase. It’ll pack some upgrades in terms of performance and efficiency in comparison with the M2 Pro chip that is currently available.

The coming M3 Pro chip is to pack a higher memory limit that might take it to 36GB for power users. Currently, users can only get the M2-powered MacBook Pro with 16GB worth of memory capacity. But with the launch of the M3 Pro-powered MacBook Pro, Apple fans might be able to get it with more unified memory.

Coming over to its CPU and GPU cores, the M3 Pro-powered MacBook Pro will get some improvements. Currently, the available testing chips run on 12 CPU and 18 GPU cores, which is an improvement from the M2 Pro chip. Other M3 Pro chips might kick up the CPU and GPU cores, but the chip is made up of six high-performance cores.

These cores will take care of the intensive tasks that a user will run on the system. It also features six efficiency cores for tasks that do not require much power. These details prove that Apple is improving the performance of their MacBook Pro device. This device will likely launch by the end of this year or at the start of next year.


[ad_2]
Source link

COVID-19 exposure alerts system shuts down in the majority of U.S. states

0
[ad_1]

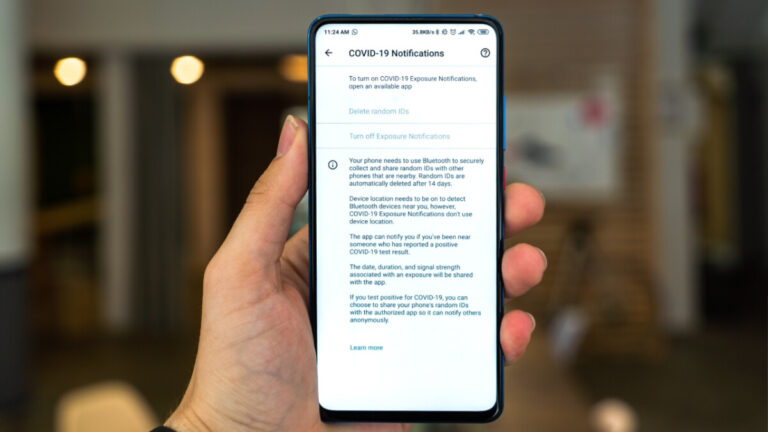
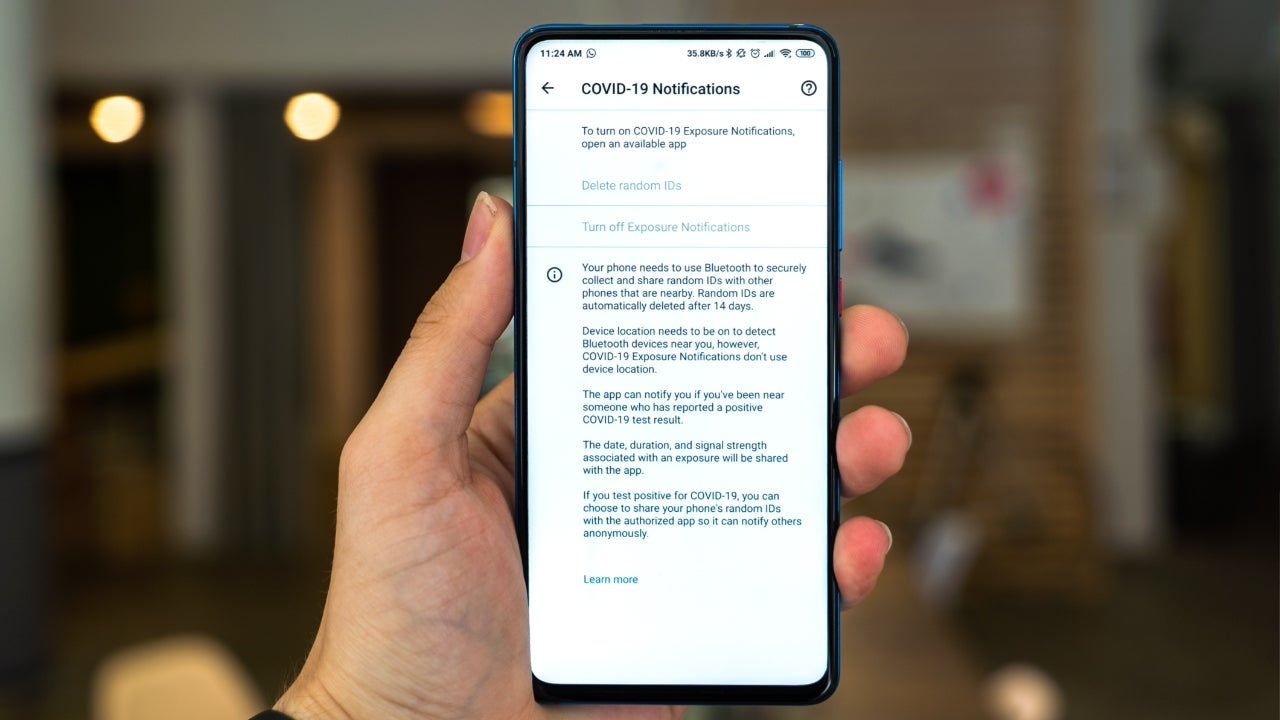
Effective May 11th, 2023, COVID-19 was no longer considered a Public Health Emergency in the U.S. As a result, the COVID-19 Exposure Notifications System (ENS) responsible for letting you know when you have most likely been in contact with someone who has tested positive, is being shut down in the majority of states.

The COVID-19 Exposure Notification System (ENS) revolutionized the way in which public health officials fought against the pandemic by making it possible for users to receive alerts on their smartphones once their device detected that it had been in close proximity to an individual who had recently tested positive and reported their status through the system. This allowed for those that were potentially exposed to take swift action and get tested.
This was possible largely thanks to the efforts of Apple and Google in the early days of the pandemic, both of which raced to develop a unified approach to exposure notifications. It was initially unveiled in April 2020, but it wasn’t until September of that same year that the feature was fully integrated into numerous Android and iOS devices through OS updates.
Once a feature used by a total of 28 states, as the pandemic restrictions loosened so did states’ response to implementing exposure notification solutions. Finally, as Apple, Google and the Association of Public Health Laboratories (APHL) discontinued their support and servers, so did the remaining states that were still making use of it.

Thanks to the utilization of the ENS, though, the expertise and know-how acquired will pave the way for a more efficient and effective public health system in the future. There is no longer a need to start from square one, since a solid foundation has already been established. To that, APHL Program Manager of National Server Operations, Emma Sudduth added:

As we move forward and look to the future, it is important to remember the role that technology played in our every day lives during the pandemic. We often think of this being limited to video conferencing and how being connected through social media allowed us to stay active and productive. However, the use of technology for exposure alerts proves that when working together towards a common goal, incredible things can be created.


[ad_2]
Source link

New Russian-Linked Malware Strain Detected

0
[ad_1]

Mandiant, a cybersecurity enterprise, has released a fresh report revealing a new malware strain, named “PIPEDREAM,” being employed by Russian cybercriminals to target American energy firms, intending to exfiltrate sensitive information.

The report highlights that these cyber invaders are using an assortment of tactics to penetrate energy firms, such as spear-phishing campaigns, capitalizing on software security flaws, and employing social engineering strategies. They have managed to infiltrate various energy companies’ networks, enabling them to seize sensitive data such as customer details, proprietary information, and financial records.

The cybercriminals are reportedly tied to the Russian government, focusing on US energy companies to potentially disrupt the American energy industry. The stolen data could be used to conduct subsequent cyber-attacks against these firms, according to the report.

This information emerges amid escalating tensions between the US and Russia, with allegations from the US about Russian interference in the 2016 presidential election and Russia’s alleged hacking of numerous US government agencies.

The report underscores that American energy corporations are prime targets for cyber invasions. The vitality of these companies to the US economy and their role in energy production and distribution make them attractive targets. A successful cyber-attack could have considerable consequences for the US economy.

The findings emphasize the urgency for energy firms to bolster their defenses against cyber-attacks. Recommendations include the implementation of robust security measures like strong password policies, multi-factor authentication, and regular software updates. Additionally, educating employees about cyber threats and defensive measures is vital.

The findings serve as a stern warning to US energy corporations. They must amplify their defenses against cyber threats and stay informed about emerging threats.

PIPEDREAM Malware Strain: A Closer Look

PIPEDREAM is a modular malware capable of stealing various sensitive data types, including customer information, intellectual property, and financial data. It is typically delivered to its targets through phishing emails or by exploiting software vulnerabilities. Once installed on a system, PIPEDREAM can exfiltrate data and transmit it back to the cybercriminals. The malware is notably sophisticated and challenging to detect and eliminate.

Cybersecurity Measures for Energy Corporations

Here are some protective measures energy companies can adopt to shield themselves from cyber-attacks:

  • Adopt stringent security protocols, including robust passwords, multi-factor authentication, and timely software updates.
  • Educate personnel about cyber threats and protective measures.
  • Develop a contingency plan for responding to and recovering from a cyber-attack.

By adhering to these guidelines, energy companies can enhance their defense against cyber-attacks.


[ad_2]
Source link