Periscope camera will be exclusive to the iPhone 15 Pro Max

0
[ad_1]

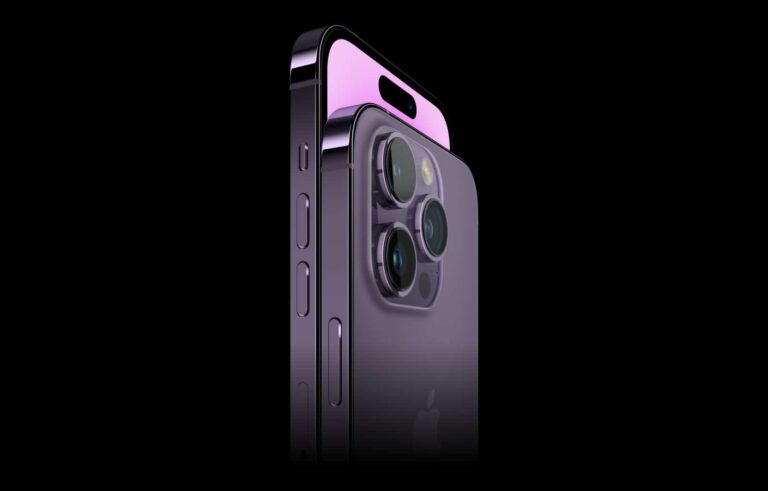
Yet another source has confirmed that a periscope camera will be exclusive to the iPhone 15 Pro Max model. In other words, the iPhone 15 Pro will not feature it, and neither will any other iPhone 15 handset.

Apple will use a periscope camera exclusively on the iPhone 15 Pro Max model

This info comes from Unknown21 also known as @URedditor, a tipster. He says that he “received independent confirmation” for this information. He doesn’t have any additional details, but he’s certain this will be the case.

Now, some of you probably know that this rumor has been going around for quite some time now. Considering the level of confidence Unknown21 showed here, we do consider this to be a shoo-in.

The rumors started back in January-February, when a report stated that only the ‘Pro Max’ model will get a periscope camera. That info came from Ming-Chi Kuo, a well-known Apple analyst. In March, he changed the story, as he seemingly suggested the iPhone 15 Pro will also get it. Then, last month, Ice Universe said that only the ‘Pro Max’ is getting it, once again reversing the story.

Nothing is set in stone just yet, but this info seems to be accurate

Nothing is set in stone just yet, of course. This is still a rumor, albeit seemingly a reliable one. Apple tends to offer the same camera hardware on both its ‘Pro’ models, so this comes as a surprise. The iPhone 15 Pro Max will not only be larger and have a larger battery, it will also have an advantage in the camera department.

The iPhone 15 Pro and Pro Max will launch in September, alongside the iPhone 15 and iPhone 15 Plus. The two phones were tipped to include solid-state buttons, but that won’t be happening, it seems. Apple decided to push back that feature to the iPhone 16 Pro series.

All four iPhone 15 models will include a Type-C port at the bottom, and also a Dynamic Island cutout at the top of the display. The bezels on the iPhone 15 Pro and Pro Max will be considerably thinner compared to current-gen devices. In fact, they’ll allegedly be the thinnest on the market.


[ad_2]
Source link

Ransomware attack on MSI led to compromised Intel Boot Guard private keys

0
[ad_1]

The leaked data after the ransomware attack on MSI includes private keys which could be used to bypass Intel Boot Guard

On April 7, 2023 MSI (Micro-Star International) released a statement confirming a cyberattack on part of its information systems. While the statement does not reveal a lot of tangible information, this snippet is important:

“MSI urges users to obtain firmware/BIOS updates only from its official website, and not to use files from sources other than the official website.”

As we mentioned in our May ransomware review, Taiwanese PC parts maker MSI fell victim to ransomware gang Money Message. Money Message is a new ransomware which targets both Windows and Linux systems. In April, criminals used Money Message to hit at least 10 victims, mostly in the US, and from various industries, including MSI.

The Money Message gang claimed to have stolen 1.5TB of data during the attack, including firmware, source code, and databases.

Money Message leak site showing countdown for MSI

Image courtesy of BleepingComputer

When the $4 million ransom demand was not met, Money Message began leaking the MSI data on its data leak site.

According to BleepingComputer, a Money Message operator said in a chat with an MSI agent:

“Say your manager, that we have MSI source code, including framework to develop bios, also we have private keys able to sign in any custom module of those BIOS and install it on PC with this bios.”

Researchers are now starting to unravel the significance of the stolen data.

tweets by researchers

The leaked data includes private keys, some of which appear to be Intel Boot Guard keys. Having the signing keys potentially allows an attacker to create fake firmware updates that would bypass Intel Boot Guard. Intel Boot Guard is a hardware-based technology intended to protect personal computers against executing fake UEFI (Unified Extensible Firmware Interface) firmware.

A bypass could provide an attacker with full access to a system, access secure data or use it for any number of malicious purposes. Boot Guard is a key element of hardware-based boot integrity that meets the Microsoft Windows requirements for UEFI Secure Boot. Secure Boot is an option in UEFI that allows you to make sure that your PC boots using only software that is trusted by the PC manufacturer.

Binarly compiled a list of 57 MSI PC systems which have had firmware keys leaked, and 166 systems which have had Intel Boot Guard BPM/KM keys leaked. Among them are household names like Lenovo and HP.

Update from vendor websites

Although no attacks of this kind have been found in the wild and Binarly, after a lengthy and detailed analysis, states that “the leaked Boot Guard keys are intended for debug building lines and most likely we will never see such devices in the wild,” the advice to obtain firmware/BIOS updates only from official vendor’s websites is solid.

Also watch out for phishing emails claiming that you need new firmware for whatever reason. They are likely from sources that are trying to trick you into installing malware. As a PC user there is not much you can do about this incident, but be prudent. We will keep you posted here in case there are any developments or more news becomes available.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes EDR and MDR remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Users complain about Pixel 7 Pro volume buttons falling apart

0
[ad_1]

The Google Pixel 7 Pro is one of the year’s most anticipated smartphones. It has been praised for its sleek design, high-quality camera, and powerful processor. However, some users have reported a problem with the volume buttons falling apart.

The issue seems to be affecting a few users, but it is still a cause for concern. According to Android Central, the volume buttons on the Pixel 7 Pro are not holding up well over time. Users on Reddit and Google Support page have also reported that the buttons have become loose or have fallen off completely.

Users that utilize their device’s volume buttons to regulate the sound will find this annoying. Changing the volume or turning off the sound entirely without working volume buttons can be challenging. Users were also concerned that the warranty might not cover the problem because some Google reps claim that the problem results from the “mishandling” of the phones.

Pixel 7 Pro volume buttons are falling off

It’s unclear what is causing the volume buttons to fall apart on the Pixel 7 Pro. Some speculate that it may be due to a manufacturing defect, while others believe it may be related to the device’s design.

Most complaints about Pixel 7 Pro buttons are submitted in the new year. Which shows users bought devices for Christmas, but they’re now dealing with loose buttons after just a few months.

A user wrote, “It’s been less than a week since I got my Pixel 7 Pro, and already the volume button has fallen off, and I’ve lost it! Where can I get a replacement from? I can’t find anywhere online.”

Google has acknowledged the problem and stated that the “team is aware of the issue.” However, this is not something you expect to see in a $900 smartphone, and Google certainly needs to address it in the upcoming Pixel 7 Pro devices.


[ad_2]
Source link

Privoro SafeCase for Galaxy S22 can remotely disable cameras/mics

0
[ad_1]

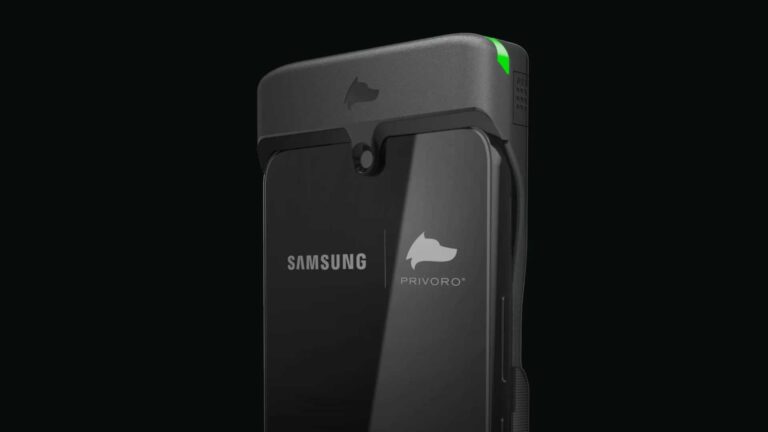
US-based tech company Privoro has launched a special protective case for the Samsung Galaxy S22. In addition to protecting the phone from cracks and breaks during falls, it offers hardware-level protection from spyware as well. Called SafeCase, it lets you remotely disable cameras, microphones, and all wireless connections to prevent attackers from spying on you.

The Privoro SafeCase is a unique protective cover for the Galaxy S22. It is a bulky case that makes the device a lot thicker and taller. The company has fitted it with a security system that protects the phone from dangerous security attacks. Along with remotely disabling cameras and microphones, you can also disconnect the cellular network, Wi-Fi, Bluetooth, and NFC to prevent or stop attacks.

This case has a hardware-to-hardware integration between its security system and the Galaxy S22’s Hardware Device Manager (HDM). The latter is an additional security layer on the Samsung smartphone that doesn’t rely on the operating system (OS). Unlike most other security features, HDM doesn’t fail even if the OS is compromised. It can bypass the OS to keep the hardware peripherals of the device safe.

Privoro is leveraging this hardware-level security to give users peace of mind. Its SafeCase for the Galaxy S22 doesn’t allow attackers to access the phone’s cameras, microphones, and other hardware peripherals even if they gain OS-level access to those device components. It can also stop “radio-specific location tracking with high certainty while still using other capabilities on their phone.”

The Privoro SafeCase draws power from the Galaxy S22

According to Privoro, the SafeCase communicates with the Galaxy S22’s HDM over Bluetooth Low Energy (BLE). It promises a secure Bluetooth connection in all scenarios. Even if the connection is compromised, the case can create a “secure tunnel” to keep everything safe (via). The case’s security system seemingly draws power from the phone. It has a USB Type-C connector at the bottom that plugs into the device’s charging port.

The security features offered by the Privoro SafeCase make it an ideal solution for government agencies and organizations more than individuals. The company will seemingly make this case available for more devices in the future. It says it is just “starting with the Galaxy S22”. Unfortunately, it hasn’t even shared the price and availability details of the case for the Galaxy S22. It’s also unclear if Privoro will offer the SafeCase for only the base Galaxy S22 model or the Galaxy S22+ and Galaxy S22 Ultra as well.

Samsung Galaxy S22 Privoro SafeCase 2


[ad_2]
Source link

Elon Musk says Twitter will start purging inactive accounts and follower counts will drop

0
[ad_1]

Twitter has announced that it will soon begin purging inactive accounts on the platform. This move is part of Twitter’s efforts to free up usernames that have been taken up by inactive accounts.
The announcement was made by Twitter CEO, Elon Musk, via a tweet yesterday while also confirming that this action may cause a dip in follower count. However, the decision is sparking a conversation on whether this is a good idea or not. 
One of the main concerns is the question of what exactly constitutes “several years” as the requirement to have an old Twitter account deactivated. There are several accounts on Twitter that haven’t been active in a long time, however, they include tweets that have been shared extensively and removing the account would most likely cause broken links.
Although having an accurate count of how many real users follow you is important, some are concerned that this move will undoubtedly start a “land grab” for old and desirable usernames, such as those that are shorter in length or represent real names.
When challenged on the above issues, Musk responded by assuring that old accounts will indeed be archived, preserving old tweets. This solves one of the issues raised but there are still many details about this new policy that have not been shared yet or made public on Twitter’s inactive account policy help page.

Twitter’s inactive account purge is part of a larger effort by the company to streamline its platform and reduce the number of bots. That said, the timing for this new policy is also consistent with a Twitter executive allegedly reaching out to NRP to reportedly “threaten” with reassigning its handle now that the news organization stopped posting less than a month ago.

It remains to be seen how this will play out and we will hopefully be getting more details soon. I imagine there are plenty of users that have been waiting on the opportunity to grab a better handle, and this may just be the best time to do that.


[ad_2]
Source link

Fake system update drops Aurora stealer via Invalid Printer loader

0
[ad_1]

Not all system updates mean well, and some will even trick you into installing malware.

Malvertising seems to be enjoying a renaissance as of late, whether it is from ads on search engine results pages or via popular websites. Because browsers are more secure today than they were 5 or 10 years ago, the attacks that we are seeing all involve some form of social engineering.

A threat actor is using malicious ads to redirect users to what looks like a Windows security update. The scheme is very well designed as it relies on the web browser to display a full screen animation that very much resembles what you’d expect from Microsoft.

The fake security update is using a newly identified loader that at the time of the campaign was oblivious to malware sandboxes and bypassed practically all antivirus engines. We wrote a tool to ‘patch’ this loader and identified its actual payload as Aurora stealer. In this blog post, we detail our findings and how this campaign is connected to other attacks.

A convincing “system update”

Windows users are quite familiar with system updates, often interrupting hours of work or popping up in the middle of an intense game. When that happens, they just want to install whatever needs to be installed and get on with their day.

A threat actor is buying popunder ads targeting adult traffic and tricking victims with what appears to a system security update.

Figure 1: A fake system update hijacks the screen

As convincing as it looks, what you see above is actually a browser window that is rendered in full screen. This becomes more obvious when downloading the update file named ChromeUpdate.exe.

Figure 2: The ‘Chrome update’ downloaded from the web browser

Fully Undetectable (FUD) malware

While the file name appears as ChromeUpdate.exe, it uses the Cyrillic alphabet such that certain characters look similar but are different on disk. Its hex representation is %D0%A1hr%D0%BEm%D0%B5U%D1%80d%D0%B0t%D0%B5.exe as can be seen in the image below:

Figure 3: Hex encoding and Cyrillic alphabet

When we first ran the sample into a sandbox, we could not see anything obvious or that it was even malicious. The file would simply run and exit quickly. Over a couple of weeks, we collected nine different samples that looked more or less the same.

We also noticed that the threat actor was uploading each of his new builds to VirusTotal, a service owned by Google, to check if they were being detected by antivirus engines. The first user to submit each new sample always uploaded them from Turkey (country code TR) and in many instances the file name looked like it had come fresh from the compiler (i.e. build1_enc_s.exe).

Figure 4: User submissions to VirusTotal

While VirusTotal is no replacement for a full endpoint security product, with its 70 AV engines it is usually a good indicator to quickly check if a file is malicious or not. For more than 2 weeks, the samples had 0 detection on VT and it wasn’t until a blog post by Morphisec that detections started to appear. This new loader is called Invalid Printer and so far appears to have been used exclusively by this threat actor to bypass security products.

Figure 5: VirusTotal detections coincide with blog release

We actually stumbled upon Morphisec’s blog thanks to Threatray which identified similarities with a file we submitted to their sandbox. The service’s built-in OSINT identified similar samples and linked them with security articles. 

Figure 6: Threatray analysis page

Patching the loader

Invalid Printer performs a check on the computer’s graphic card and specifically its vendor ID which it compares against known manufacturers such as AMD, NVidia. Virtual machines and sandboxes in general do not use real hardware and will fail to pass the check.

We were able to patch the samples we had collected and identify their payload. The patch consists of replacing the graphics card check with a random number and always returning true, therefore allowing the file to run in any sandbox.

Figure 7: Python script to patch loader

The automated malware unpacking service from OpenAnalysis UnpacMe now supports properly unpacking samples using the Invalid Printer loader. It allowed us to determine what malware family is being distributed as well as indicators of compromise. For example, one of our samples (31c425510fe7f353002b7eb9d101408dde0065b160b089095a2178d1904f3434) has the same command and control server (94.142.138[.]218) as one mentioned in Morphisec’s blog.

Figure 8: UnpacMe results page

In this specific malvertising campaign, the payload used was the Aurora Stealer, a popular piece of malware that is designed to harvest credentials from systems.

Campaign stats

The threat actor is using a panel to track high level stats about visitors to the fake system update web page. Based on the numbers from this panel, there were 27,146 potential unique victims and 585 of them downloaded the malware during the past 49 days.

Figure 9: Panel showing browser visits and downloads

Figure 10: Browser user-agents, IP addresses and geolocation

War and Russia references

We believe there is a single threat actor behind this malvertising campaign and others such as the one Morphisec uncovered. The malware author seems to take a very high interest in creating FUD malware and constantly uploads it to VirusTotal to verify, always using the same submitter profile.

We couldn’t help but notice a possible reference to the war in Ukraine left within the fake Chrome Update page and commented out:

Figure 11: Commented HTML code

Some of the websites belonging to this threat actor were not loading malware but instead had a single YouTube video promoting the cities and landscapes of Russia:

Figure 12: YouTube video about Russia in 12K HDR 

Additionally, we found some connections with tech support scams and even an Amadey panel that also appears to belong to the threat actor.

Protection

Malwarebytes already protected users from this malvertising campaign by blocking the malicious ads involved. We detect the payloads as Spyware.Aurora.

Special thanks to Roberto Santos for help with the sample and binary patching.

Indicators of Compromise

Malvertising gate

qqtube[.]ru
194.58.112[.]173

Fake system update page

activessd[.]ru
chistauyavoda[.]ru
xxxxxxxxxxxxxxx[.]ru
activehdd[.]ru
oled8kultra[.]ru
xhamster-18[.]ru
oled8kultra[.]site
activessd6[.]ru
activedebian[.]ru
shluhapizdec[.]ru
04042023[.]ru
clickaineasdfer[.]ru
moskovpizda[.]ru
pochelvpizdy[.]ru
evatds[.]ru
click7adilla[.]ru
grhfgetraeg6yrt[.]site
92.53.96[.]119

Invalid Printer samples

d29f4ffcc9e2164800dcf5605668bdd4298bcd6e75b58bed9c42196b4225d590
5a07e02aec263f0c3e3a958f2b3c3d65a55240e5da30bbe77c60dba49d953b2c
193cec31ea298103fe55164ff6270a2adf70248b3a4d05127414d6981f72cef4
dac1bd40799564288bf55874543196c4ef6265d89e3228864be4d475258b9062
40b8acc3560ac0e1825755b3b05ef01c46bdbd184f35a15d0dc84ab44fa99061
31c425510fe7f353002b7eb9d101408dde0065b160b089095a2178d1904f3434
398faa3aab8cce7a12e3e3f698bc29514c5b10a4369cc386421913e31f95cfdc
93b9199ca9e1ee0afbe7cf6acccedd39f37f2dd603a3b1ea05084ab29ff79df7
4c80bd604ae430864c507d723c6a8c66f4f5e9ba246983c833870d05219bd3e5

Aurora Stealer C2

103.195.103[.]54:443
94.142.138[.]218:4561

Amadey Stealer panel

193.233.20[.]29/games/category/Login.php

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link

Meta wants to show more ads in Facebook and Instagram Reels

0
[ad_1]

Meta has unveiled its plans to show more ads in Facebook and Instagram Reels, allowing creators to make money out of their shared videos.

Facebook Reels introduced its monetization program last year as a way for creators to make money by creating and sharing engaging Reels. Meta is now expanding the program and lets thousands of new creators join the test. However, the company is also considering a new payout model for creators.

According to the company’s announcement, the new model pays creators “based on the performance of their public reels, not the earnings of ads on their reels.” By performance, Meta means the number of plays and not other engagement factors. Of course, other signals might be incorporated into payouts in the future.

Meta restructures its payout model for Facebook and Instagram Reels

The new payout model means creators can make money by crafting more engaging Reels. Which could finally lead to stronger user retention on the platform. As for Instagram, Meta says a similar program will be rolled out to a small group of creators and advertisers in select markets in the coming weeks.

Meta adds that the restructured payout results from the company’s tests, arguing that performance-based payouts work better for both sides. Additionally, paying creators based on the earnings of ads could negatively affect their revenue as some factors might be out of their control.

Meta also announced the performance-based payout model would apply to In-Stream ads on Facebook. This is a part of the company’s initiative to support creators making all types of content.

Back in 2021, Meta launched a Reels Play bonus with over $35,000 monthly bonuses for creators. The company later slashed the money and then paused the program entirely amid its cost-cutting efforts. The new payout model for creators coincides with Meta’s plans to cut 10,000 jobs to reduce costs.


[ad_2]
Source link

The Cactus ransomware encrypts itself to avoid getting spotted

0
[ad_1]

Cybersecurity experts have identified the new Cactus ransomware, and it is a master of disguise. It does this uniquely, hence making even the beefed-up antivirus software packages not notice its existence. This sounds quite scary because anyone can have this virus on their system whilst having antivirus software running.

The new malware executes itself in a series of ways, as identified by some cybersecurity experts. One of its methods of execution involves it hiding itself from any antivirus software that might be available on the user’s system. It harps upon the weakness of antiviruses and endpoint security solutions out there to keep itself concealed in plain sight.

Information regarding this ransomware was provided by the folks at Kroll. The firm’s risk and financial advisory solutions team have been able to spot this malware and make it known to the public. Here is everything you need to know about this masquerading malware that hopes to hold your files for ransom.

The new master of disguise in the cybersecurity world is the Cactus ransomware

The new Cactus ransomware has three main modes of executing itself in a system. In this article, the main focus will be just one of the ways it executes on a system. This method of execution makes the Cactus ransomware go undetected even by antivirus software packages.

If you are familiar with antivirus software products and endpoint security solutions, you’d know that they can’t read encrypted files. Well, one of the ways the new Cactus ransomware executes itself in a system is by encryption. With the use of an AES key, a bad actor can deploy this ransomware to a system, where it will exist as an encrypted file.

Cybersecurity experts have been able to understand how this ransomware operates. It all starts with the bad actors providing this ransomware with a unique AES key that they also have access to. With the AES key, the ransomware’s configuration file and public RSA key can be decrypted.

After this, the bad actor can then encrypt the malware file and then forward it to the target. These will get to the target’s system as a HEX string, which is hardcoded in the bad actor’s binary. After the malware gets into the target’s system, the bad actor decodes the HEX string.

This will give them access to the user’s data which they can then access with the AES key. The entire encryption process makes the Cactus ransomware hard to detect. It can easily exist on a system, causing damage whilst being ignored by the installed antivirus or endpoint security solution.

The Cactus ransomware is a master of disguise and hides in plain sight. But this malware also has two other ways to execute on a target’s computer system. Executing it using encryption and another method together makes this malware more lethal. More research and work will go into better understanding this ransomware and how to prevent its attacks.


[ad_2]
Source link

WhatsApp Android bug has been found to give the app continuous access to the microphone

0
[ad_1]

WhatsApp, the popular messaging app owned by Facebook, has been found to include a bug that allows the app to continue accessing the microphone even after the user has closed it. This bug was discovered by several users, but brought to the spotlight by a Twitter engineer who noticed it happening on his Pixel 7 Pro.
The bug appears to be affecting several Android devices, including different Samsung and Pixel models, as well as several different versions of the Android app. However, WhatsApp has responded by claiming that the issue lies with Android and not the app itself.
In several of these reports, microphone activity from the app has been spotted in Android’s Privacy Dashboard as well as through the visible green dot notification on the Android status bar. However, WhatsApp states that this seems to be a bug on Android that mis-attributes information in the privacy dashboard and has asked Google to further investigate.

Unfortunately, WhatsApp’s response didn’t come until after Elon Musk took to his own Twitter account to share his opinion on the matter. As you can probably guess by now, his reaction was not positive, accusing the company of not being trustworthy. 

This latest bug could further erode users’ trust in the app, so it is important that Google take a look at the issue and respond accordingly. Hopefully this fix comes sooner rather than later.


[ad_2]
Source link

Google Photos on tablets is about to get better

0
[ad_1]

Google has been working on making Android a better place for tablets, and the company hasn’t stopped yet. A new report states that Google will make Google Photos better for tablets. This will mainly influence the photo editing feature of the app.

Editing pictures on Google Photos has always been a very optimized experience for smartphones. You have your photo up top with the options displayed in a carousel on the bottom. However, some people like to use larger screens to edit their photos. If a person wants to use their tablet to edit photos, the app would rotate to portrait orientation.

This will make it pretty frustrating to use because the photo, if taken in landscape orientation, would be shrunken to fit in the portrait orientation. This pushes people to edit on their phones instead.

But, Google is going to make editing in Google Photos on tablets better

This is the latest in a long line of Google products to get much-needed tablet optimizations. According to a tweet from Nail_Sadykov (via Phone Arena), the editing UI in Google Photos will be formatted to work in landscape.

Instead of being pushed to the top, the photo you’re editing will be on the left side, and that will take up most of the screen. On the right side, you will see all of your editing tools. On the upper right of the screen, you’ll see icons for the different categories (Suggestions, Crop, Adjustments, Tools, and Markup).

Under the bar, you’ll see each section expanded with large Material You buttons and UI elements. Under the Adjustments tool, each of the sliders (brightness, contrast, HDR, etc.) will be displayed all on one plane, rather than being separated into their own sections.

So, the interface will be much better suited for people who want to edit photos on their tablets. This is great, as there are a ton of tablets out there that have amazing displays. Editing photos on them should be a breeze.

At this point, we have no idea when Google plans to roll out this change. Since there are live screenshots, it appears that the feature is pretty well developed. Hopefully, Google will roll this out soon. We also can’t rule out the company announcing this during Google I/O which is happening tomorrow.


[ad_2]
Source link