AresLoader Malware Attacking Citrix Users

0
[ad_1]
AresLoader

Cyble Research and Intelligence Labs (CRIL) has recently detected AresLoader, a novel loader that is found to be disseminating numerous malware families.

Malware loaders are designed to deploy and execute diverse malware strains on the targeted computer system of the victim.

To evade detection by antivirus software, loaders often employ various tactics such as encryption or obfuscation of the malicious payload, rendering it harder to detect by security measures.

AresLoader

In 2022, AresLoader, a loader malware coded in the C programming language, emerged for the first time.
It has been identified that this loader was distributed through Telegram channels and malicious forums.

AresLoader, developed by the same threat actors behind the AiD Locker ransomware and distributed as Malware-as-a-Service (MaaS).

There is a monthly fee of $300 for AresLoader, which includes five build images.

There is also suspicion that the members of this group have ties with a hacktivist group based in Russia.

Technical Analysis

The notorious AresLoader follows a complex modus operandi. The initial loader binary serves as a container for the embedded code that is further injected in multiple stages, resulting in a complex chain of malicious activities.

During further analysis, it was noticed that the methods of extraction and injection of the loader code in each binary are inconsistent throughout the entire code.

By constantly updating their infection techniques, the threat actors evade the security measures implemented by the AV tools, and not only that even, there have also been multiple malware strains that have been observed to be using this loader.

Apart from this, CRIL discovered a GitLab repository distributing the AresLoader malware that is located at:-

  • hxxps[:]//gitlab.com/citrixchat-project/citrixproject/

While it has been detected that threat actors are actively targeting Citrix users with this repository masquerading as “citrixproject.”

During the execution of AresLoader, the malware utilizes a 32-bit binary compiled in C, which invokes the CreateWindowEx() API using the following elements:-

  • GLSample (Class name)
  • OpenGL Sample (Window name)

This distinct characteristic is one of the many ways cybersecurity experts identify and track the loader.

In an attempt to complicate the detection and analysis of this malware, API hashing is employed, and here the APIs that are targeted belong to:- 

Following is a list of API functions that the loader retrieves:-

  • pLdrFindResource_U
  • pLdrAccessResource
  • pNtAllocateVirtualMemory
  • pNtQueueApcThread
  • pNtTestAlert

Decrypting the resource data obtained earlier is the next step in the process, and then from the .rdata section, a key is acquired to accomplish this complete process.

The decryption loop begins immediately after the memory has been allocated, and the temporarily allocated memory is used to store the newly decrypted PE file.

Moreover, using a POST request, AresLoader registers the victim with the C&C server using additional information obtained from the victim’s system.

Recommendations

Here below, we have mentioned all the recommendations offered by the security experts:-

  • Do not download files from unknown websites. 
  • Ensure that a reputable antivirus and internet security software package protects your connected devices, such as your PC, laptop, and mobile phone. 
  • Ensure you verify the authenticity of all links and attachments in an email before opening them. 
  • Protect employees from threats such as phishing and untrusted URLs by educating them about the risks. 
  • The beacon should be monitored at the network level to prevent data exfiltration by malware or attackers.
  • Ensure that employee systems are protected by a Data Loss Prevention (DLP) solution.

Building Your Malware Defense Strategy – Download Free E-Book


[ad_2]
Source link
Google teases the Pixel 7a before the launch

0
[ad_1]

Google has said to announce some exciting devices this year, and one of them is coming very soon. As we know, Google I/O is happening next Wednesday, and we expect to see it unveil its latest mid-range phone. Well, ahead of the announcement, the Google India Twitter account posted a teaser for the Pixel 7a.

The Pixel 7a isn’t the only device we’re expecting to be announced during Google I/O. If the rumors hold true, then Google will also unveil the Pixel Tablet and its rumored Pixel foldable phone. If you’re excited to hear about these devices, Google I/O will kick off next Wednesday, May 10th. Be sure to mark your calendar.

Google posts a teaser for the Pixel 7a

So far, we’ve probably seen this phone from every angle via leaks. Just recently, we had a couple of leaks showing this device in several colors including an interesting blue color. This is the color that we see in the teaser.

In the teaser, we only see the top of the phone, and it’s from the back. The dual camera package is facing the audience, and it shows us that the camera visor will be metal just like with the Pixel 7 phones. Since this is only a teaser, the company is leaving a lot to the imagination, as the picture gradually blurs.

Pixel 7a teaser full

Along with the picture, the Tweet also states that the Pixel 7a will come to Flipkart on May 11th. That’s likely when the pre-orders are going to begin, and general sales are expected to come in the following weeks. However, we will have to wait and see if that’s what Google is planning.

The Pixel 7a is expected to use Google’s Tensor G2 SoC, which is the same processor powering the Pixel 7 and Pixel 7 Pro. We expected to retain similar dimensions to the Pixel 6a. So, if you have that phone, you will feel right at home with a Pixel 7a. The Pixel 6a was one of the most popular mid-range phones of 2022, so the Pixel 7a should be able to fill those shoes.


[ad_2]
Source link

T-Mobile suffers its second data breach in 2023

0
[ad_1]

After suffering its second-biggest data breach back in January, impacting over 37 million people, T-Mobile has recently disclosed yet another data breach. And although this time, the breach was not extensive and only impacted over 800 people, threat actors did manage to get their hands on vast amounts of user information.

According to Bleeping Computer, the breach, which occurred between February 24th and March 30th, compromised user’s names, contact information, account numbers, phone numbers, account PINs, social security numbers, government IDs, dates of birth, balance due, internal codes, and the number of lines. While T-Mobile claims the hackers did not gain access to call records or personal financial account information, this amount of exposed data provides cybercriminals with enough information to commit identity theft and other forms of fraud.

“In March 2023, the measures we have in place to alert us to unauthorized activity worked as designed, and we were able to determine that a bad actor gained access to limited information from a small number of T-Mobile accounts between late February and March 2023,” says T-Mobile.

T-Mobile’s response

T-Mobile says that after first detecting the data breach, they were quickly able to mitigate it by resetting the account PINs for affected users. Additionally, the company is also offering two years of free credit monitoring and identity theft detection services through Transunion myTrueIdentity.

“We notified a small number of customers that our systems and processes worked to detect and stop a bad actor who was accessing accounts using compromised credentials,” said T-Mobile in a statement to CNET.

This latest data breach once again highlights the ever-growing importance of implementing stringent security measures to prevent cyber attacks. While, on the one hand, companies should implement strict security policies, provide ongoing employee training, and perform regular security audits, users, on the other hand, should regularly update their PINs and passwords, enable 2FA, and refrain from sharing sensitive information online.


[ad_2]
Source link

Nothing foldable smartphone concept has LED lights on the hinge

0
[ad_1]

Nothing has released only one smartphone thus far, the Nothing Phone (1). The Nothing Phone (2) is expected to launch this year. Some of you may wonder if Nothing plans to launch a foldable smartphone, well, while we can’t answer that yet, a Nothing foldable smartphone concept did surface.

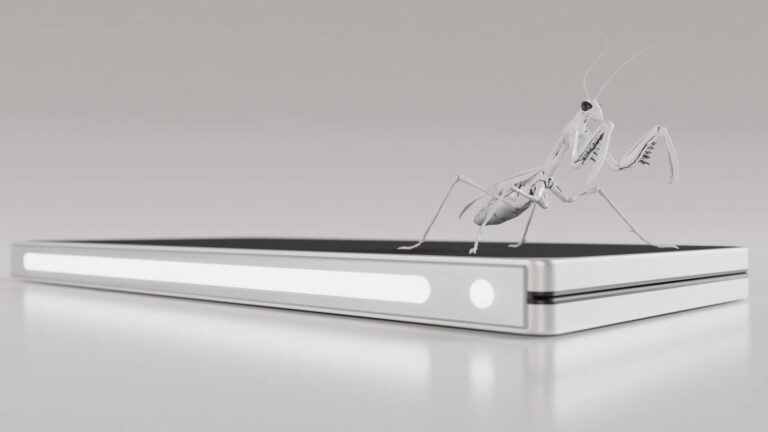
This Nothing foldable smartphone concept has LED lights on the hinge itself

This concept has been shared by Brandon Paul aka 3DPCat/BitJewel, and was reshared by Nothing on Twitter. He created some nice-looking renders, envisioning a Nothing-branded foldable smartphone.

The first thing I personally noticed are the LED lights in the first image included in the gallery below. These LED lights are placed on the outer part of the hinge itself. One long strip, and a smaller circular light. These make for really nice design detail.

This foldable device has flat sides all around, and the hinge itself is also boxy and unusual. The device seems to be impossibly thin when folded, but that’s not surprising considering this is a concept phone.

There is no display camera hole on the main panel

It seems to be made out of metal and glass, and there is no display camera hole on the main display. We presume that the designer envisioned an under-display camera for this phone. The bezels around the main display are also quite thin.

Nothing is a rather new company, and it probably has no plans to release a foldable smartphone anytime soon. Who knows, Nothing maybe is testing such a device, but we don’t expect it to arrive soon.

The company is now fully focused on the Nothing Phone (2) which is expected to arrive in a couple of months. The Nothing Phone (1) launched in July last year, so it’s easily possible its successor is coming in July this year.


[ad_2]
Source link

Samsung bans employees from using AI tools like ChatGPT

0
[ad_1]

Samsung has reportedly banned its employees from using generative AI tools such as ChatGPT and Google Bard on company-owned devices and internal networks. The move comes after some employees inadvertently leaked confidential information through ChatGPT a few weeks back.

Samsung bans the use of ChatGPT and Bard on official devices

Like many other companies, Samsung also planned to use generative AI tools for business growth. It hoped AI to help boost its faltering chip business. However, things didn’t pan out as planned. Shortly after the company gave its employees access to ChatGPT to speed up various processes in mid-March, reporters emerged that the AI chatbot leaked confidential semiconductor information.

This happened after some Samsung employees fed internal data to the AI tool created by Microsoft-backed OpenAI. Where they erred is that they didn’t realize that the likes of ChatGPT and Bard permanently store any information fed to them. These tools use the information for learning purposes. But in the process, they could also end up sharing the information with other users. And since they store the data on external servers, it’s difficult for Samsung to retrieve and delete it.

It’s unclear what information Samsung employees inadvertently leaked through ChatGPT. However, the leaks happened in three separate instances within three weeks. The company has now sent a memo to employees ordering them to stop using the AI tool on official devices and internal networks. Employees are also advised not to feed any company-related information to generative AI tools on their personal devices. They are also barred from sharing personal data that could reveal the company’s intellectual property.

According to a Bloomberg report, Samsung has warned its employees that breaking these policies could cost them their jobs. “We ask that you diligently adhere to our security guidelines and failure to do so may result in a breach or compromise of company information resulting in disciplinary action up to and including termination of employment,” part of the memo reads. The memo was sent to employees at one of Samsung’s biggest divisions on Monday, the report states.

Samsung is developing its own AI tools for internal use

Samsung may have banned the use of ChatGPT and Bard on its official devices, but it still sees AI going a long way in boosting its business. The company is reportedly creating its own generative AI tools for internal use. It plans to use those tools “for translation and summarizing documents as well as for software development”. At the same time, Samsung is also working on ways to block external AI services from obtaining sensitive company information. ChatGPT recently added an “incognito” mode where it doesn’t save conversations for learning purposes.

“Interest in generative AI platforms such as ChatGPT has been growing internally and externally. While this interest focuses on the usefulness and efficiency of these platforms, there are also growing concerns about security risks presented by generative AI,” Samsung told staff. “HQ is reviewing security measures to create a secure environment for safely using generative AI to enhance employees’ productivity and efficiency. However, until these measures are prepared, we are temporarily restricting the use of generative AI,” the memo added.


[ad_2]
Source link

Critical Vulnerabilities Spotted In Zyxel Firewall

0
[ad_1]

Heads up, Zyxel users! The vendors have patched a few critical vulnerabilities in Zyxel Firewall that could allow remote command execution attacks. Users must rush to update their devices with the latest software releases to receive the patches.

Multiple Vulnerabilities Found In Zyxel Firewall

Zyxel – the Chinese technology and networking giant – has patched multiple Firewall vulnerabilities with the latest releases.

Specifically, the vendors have addressed three security vulnerabilities affecting their Firewall devices.

The first of these is a critical-severity remote command execution vulnerability, CVE-2023-28771 (CVSS 9.8). According to Zyxel’s advisory, the flaw existed due to improper message handling, allowing an unauthenticated remote adversary to execute OS commands on the target firewall devices. Exploiting the flaw required the attacker to send maliciously crafted data packets to the target device.

The devices affected by this vulnerability include ATP ZLD V4.60 to V5.35, USG FLEX ZLD V4.60 to V5.35, VPN ZLD V4.60 to V5.35, ZyWALL/USG ZLD V4.60 to V4.73. Zyxel has credited TRAPA Security for detecting and reporting this flaw.

The next vulnerability, CVE-2023-27990, is a high-severity (CVSS 8.8) cross-site scripting (XSS) vulnerability in Zyxel firewalls. Exploiting this flaw could let an authenticated adversary with admin privileges store malicious scripts on the target device. The scripts would execute if a user visits the Logs page.

Then, the third vulnerability, CVE-2023-27991, could also allow OS command injection attacks. The flaw impacted the CLI command of firewalls, allowing an authenticated attacker to execute remote commands.

According to Zyxel’s advisory, these two vulnerabilities affected the ATP ZLD V4.32 to V5.35, USG FLEX ZLD V4.50 to V5.35, USG FLEX 50(W)/USG20(W)-VPN ZLD V4.16 to V5.35, and VPN ZLD V4.30 to V5.35. Zyxel attributed Alessandro Sgreccia from Tecnical Service SRL for reporting both vulnerabilities.

Patches Rolled Out

Zyxel patched all three vulnerabilities with the latest software releases for vulnerable devices. Specifically, the patched releases include ATP ZLD V5.36, USG FLEX ZLD V5.36, VPN ZLD V5.36, ZyWALL/USG ZLD V4.73 Patch 1 (bug fix for CVE-2023-28771), and USG FLEX 50(W) / USG20(W)-VPN ZLD V5.36 (bug fix for CVE-2023-27990, CVE-2023-27991).

While the updates might reach the affected automatically, users must check for possible updates for their devices manually to ensure receiving the patches in time.

Let us know your thoughts in the comments.


[ad_2]
Source link

Android 13 with May security patch is rolling out to Pixels

0
[ad_1]

Google has started rolling out Android 13 with a May security patch to the Pixels. After the previous couple of security updates got delayed, it’s nice to see that the one for May is rolling out on time.

Android 13 with May security patch is now hitting Google’s Pixel phones

This update has started rolling out to the Pixel 4a, 4a 5G, 5, 5a, 6, 6 Pro, 6a, 7, and 7 Pro. Do note that the rollout is staged, so it may take some time to reach all devices, as per usual.

As far as security issues are concerned, 18 of them are resolved in the Android 13 May patch dated 2023-05-01, and 29 for 2023-05-05. It is also worth noting that vulnerabilities range from moderate to high. Two additional security fixes are listed in Google’s dedicated bulletin, though.

This update is mostly focused on security fixes, of course, but some additional changes are also listed. The changelog mentions a “fix for issue occasionally causing lock screen UI elements to overlap with home screen launcher interface”. Another change is noted, but only for the Pixel 7 Pro: “Improvements for touch screen response in certain conditions”.

We’re getting the next Pixel Feature Drop in a month, so stay tuned for that

So, there’s not much to talk about here. That was to be expected, though. The June update is the quarterly update that we’re waiting for. That will be Google’s Pixel Feature Drop update, of course.

As mentioned earlier, this update is rolling out in stages. The rollout has started, but if you’re unwilling to wait for the update to reach your device, you can always install it manually. You’ll find both factory images and OTA update files by clicking here. Make sure to download the files for your device, though, of course.


[ad_2]
Source link

Samsung is hoping 3nm chips to improve its foundry share

0
[ad_1]

Samsung has reportedly improved the yield rates of its 3nm semiconductor chips and is now trying to win back customers that it lost to foundry rival TSMC in recent times. According to the Korean media, the company is sending 3nm prototypes to fabless chipmakers in an attempt to sway them on its side.

It is weaponizing the use of Gate-All-Around (GAA) transistor architecture in its pitch. The GAA tech is said to be more efficient in terms of performance, power, and chip size than the FinFET (Fin field-effect transistor) architecture used by TSMC.

Samsung is desperately trying to close the gap with TSMC in the foundry market

Samsung has long played second fiddle to TSMC in the semiconductor foundry industry. The latter has stretched the gap up top in recent months as the former struggled with its yield rates.

Several fabless companies switched from Samsung to TSMC for manufacturing their next-gen solutions due to this issue. The Taiwanese firm started the mass production of 3nm chips after Samsung but it has already achieved better yield.

However, the latest word from the industry is that Samsung has improved its 3nm yield rates to about 60-70 percent in recent months. It is now desperately trying to steal a few customers from TSMC and close the gap to it in the foundry segment. The journey is quite long (the two firms had a market share of 15.8 percent and 58.8 percent respectively in Q4 2022), but the Korean firm is making its moves.

As said earlier, Samsung is producing its 3nm chips using the GAA architecture. TASM, on the other hand, is sticking to the FinFET tech for one more generation.

It plans to switch to GAA with 2nm chips in 2025. The Korean firm would be using this theoretical upper hand in architecture in its pitch to fabless companies as it sends them early prototypes. By the time TSMC moves to the GAA architecture, Samsung would have about two years of expertise in it.

It remains to be seen if the Korean giant manages to win back a few customers from TSMC. Most of its current 3nm clients are high-performance computing (HPC) companies that need high-performance and low-power semiconductors, the new report states. It also has some mobile customers, but the Taiwanese firm has already captured all the big names.

TSMC isn’t sitting idle either

It’s not like Samsung is making all the moves and TSMC is sitting idle. The Taiwanese firm reportedly held a foundry technology symposium in the US recently. It targeted major customers in the US and unveiled a roadmap for mass production of the next-gen advanced process.

The company has already secured large orders from Apple, AMD, MediaTek, Nvidia, and Qualcomm. It plans to start mass-producing 3nm chips for these customers early next year. TSMC will manufacture 3nm chips for HPC in 2025 and automobiles in 2026.


[ad_2]
Source link

A week in security (April 24 -30)

0
[ad_1]

The most interesting security related news of the week from April 24 till April 30

Last week on Malwarebytes Labs:


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Another image] Official image shows us main Pixel Fold display and its odd bezels

0
[ad_1]

UPDATE: In addition to the main display of the Pixel Fold, and the shot of the device in a folded state from a side, Evan Blass just shared another image. This one shows us the device in a folded state, but front the front, as you can see in the image below.

Google Pixel Fold official render leak 7

ORIGINAL ARTICLE: A well-known tipster, Evan Blass aka @evleaks, shared a couple of official Pixel Fold images over the weekend. He shared an official render showing the back side of the phone when unfolded, and the device from a profile when folded. What he did not show us is the phone’s main display. Well, you guessed it, the main Pixel Fold display just got shown in an official image.

The puzzle is complete, as the official image just showed us the main Pixel Fold display too

That image comes from the same source, actually. In addition to it, he showed us the Pixel Fold in another color when folded. Let’s start from the top, though. If you check out the first image in the gallery below the article, you’ll see the phone’s main display.

As you can see, we’re looking at rather odd bezel distribution here. The top and bottom bezels are thicker than the side bezels. This does look odd, and it may annoy some people, but at least it hides the cameras and all sensors inside the bezels. We don’t have to deal with a display camera hole.

Some people may consider those bezels to be a bit thick, and that’s understandable, especially the top and bottom ones. This panel also shows that Google is aiming at a horizontal aspect ratio when the phone is unfolded.

The phone’s main panel will have a 6:5 aspect ratio

The main display on the device will feature a 6:5 aspect ratio, as Evan Blass revealed. That will make its cover display rather short and wide. The cover display will measure 5.79 inches, while the phone itself will measure 139.7 x 79.5 x 12.1mm when folded. When folded, it will be wider than most regular smartphones. Evan Blass actually revealed the phone’s detailed specs, click here if you’d like to know more.

Having said that, the second image in the gallery below shows us a different color variant of a phone when folded. The image Blass first shared showed us the black model (Obsidian), this one leans towards the silver color. This color variant will be called ‘Porcelain’.

The Pixel Fold will be made out of metal and glass, and it’s coming later this month. The device will be announced during the Google I/O keynote on May 10. It is tipped to go on pre-order that day, and become available for purchase on June 27. It’s also said to cost $1,799.


[ad_2]
Source link