You need to delete yet another 38 Android apps before they load up your phone with malware

0
[ad_1]
You know how we told you around two weeks ago about more than 60 Android apps with a collective total of over 100 million Google Play downloads that were found to push invasive ads without the user’s permission and gather a host of sensitive information… also without notifying you or asking for approval?
While that particular security threat is officially behind us all, a new and extremely similar one has been discovered by the same McAfee researchers in the meantime, wreaking havoc on tens of millions of Android devices around the world.

What is this issue all about?

Although it’s part of the same large and malicious adware family as the previously identified “Goldoson” virus, this “HiddenAds” campaign might seem a little less harmful at first glance, doing, well, exactly what the name suggests.

Specifically, around 35 million (!!!) Android users worldwide have apparently been served ads in the background of their mobile gaming sessions recently with the main purpose of generating unlawful revenue for various shady companies and individuals.

That sounds like something that won’t greatly impact your user experience or data privacy, but anyone who’s ever accidentally installed this type of malware before knows precisely how annoying it can be to notice your phone slow down, freeze, or crash out of nowhere without being able to identify the culprit.

If you’ve experienced something like that of late, it’s possible that your mobile device is infected with “HiddenAds”… or a similar malware, especially if you happen to occasionally share said device with a child between the ages of 5 and, say, 15.

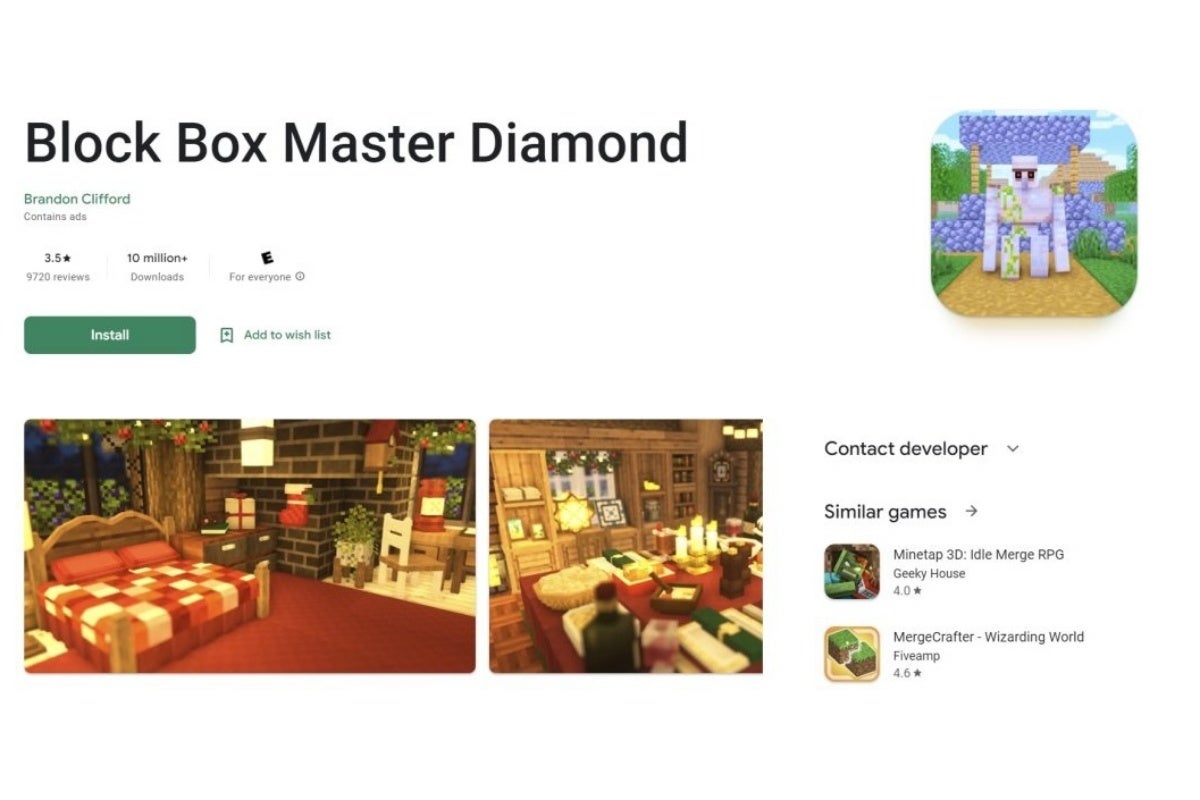
That’s because every single malicious app found to be part of this specific adware group emulates or, let’s be honest, downright rips off Mojang’s hugely popular Minecraft game. We’re talking incredibly similar titles mixing up the words “block”, “diamond”, “craft”, “sword”, “monster”, “forrest”, “builder”, and “rainbow” in slightly different ways to draw the attention of the most vulnerable mobile users of all.

These are all the apps you need to delete ASAP

  • Block Box Master Diamond
  • Craft Sword Mini Fun
  • Block Box Skyland Sword
  • Craft Monster Crazy Sword
  • Block Pro Forrest Diamond
  • Block Game Skyland Forrest
  • Block Rainbow Sword Dragon
  • Craft Rainbow Mini Builder
  • Block Forrest Tree Crazy
  • Craft Clever Monster Castle
  • Block Monster Diamond Dragon
  • Craft World Fun Robo
  • Block Pixelart Tree Pro
  • Craft Mini Lucky Fun
  • Block Earth Skyland World
  • Block Rainbow Monster Castle
  • Block Fun Rainbow Builder
  • Craft Dragon Diamond Robo
  • Block World Tree Monster
  • Block Diamond Boy Pro
  • Block Lucky Master Earth
  • Craft Forrest Mini Fun
  • Craft Sword City Pro
  • Block Loki Monster Builder
  • Block Boy Earth Mini
  • Block Crazy Builder City
  • Craft Sword Vip Pixelart
  • Block City Fun Diamond
  • Craft City Loki Rainbow
  • Craft Boy Clever Sun
  • Block City Dragon Sun
  • Craft Loki Forrest Monster
  • Lokicraft: Forrest Survival 3D
  • Craft Castle Sun Rain
  • Craft Game Earth World
  • Craft Lucky Castle Builder
  • Craftsman: Building City 2022
  • Craft Rainbow Pro Rain

If you’re thinking of discarding this threat as minor and unimportant… don’t. That’s because the malicious Android games listed above are ordered by popularity, starting with a title that was downloaded more than 10 million titles and three more with 5 million+ Google Play installs under their belt (each).

So, yeah, if you’re not extremely careful about every single thing you or your kid downloads from the official Play Store every single day, odds are your phone might need a little spring cleaning. And quickly! That’s especially true if you live in the US, Canada, South Korea, or Brazil, which were apparently the main countries targeted by this malware-spreading campaign.

For its part, Google seems to have fulfilled its secondary task of cleaning up the Play Store of these apps after failing the primary goal of keeping such threats away to begin with. But that doesn’t mean anything if you don’t also locate these apps and delete them from your devices before they can spread their tentacles and start performing other shady background activities besides pushing ads for dirty money.

[ad_2]
Source link

AuKill Malware Actively Used To Disable EDR In Ongoing Attacks

0
[ad_1]

Researchers have discovered a new malware that remained under the radar for quite some time. Identified is AuKill, it is a potent EDR kill malware that leverages BYOVD to disable EDR clients. The hackers have already used the tool in recent ransomware attacks.

AuKill Malware Disables EDR Via BYOVD

According to a recent post from Sophos, their researchers have found a previously-unreported malware actively used in the wild.

Identified as “AuKill,” the malware allows the attackers to disable EDR clients to evade the target systems’ security.

In brief, AuKill leverages the Bring Your Own Vulnerable Driver (BYOVD) technique to disable EDR. It uses the older driver version that the Microsoft utility “Process Explorer” version 16.32 used.

Specifically, the malware drops the older PROCEXP.SYS driver version to the C:\Windows\System32\drivers path – the location where the legitimate driver version also exists. It then kills the legit driver to take over its place with the (now)malicious driver. Besides, AuKill also drops its executable copy to the system’s temp folder to run as a service.

Once done, it then executes the payload with admin privileges that the attackers could gain through other means. (The malware won’t execute without admin privileges – a mandatory requirement that AuKill checks at the initial stage.)

After fulfilling all its requirements, AuKill then disables EDR by starting a sequence of threads to keep the service disabled.

Malware Already Used In Active Attacks

The researchers noticed AuKill playing an active role in recent ransomware campaigns. That two include Medusa Locker ransomware incidents that happened in January and February 2023 and a LockBit ransomware attack in February.

Until the time of disclosure, Sophos discovered six different AuKill malware variants, indicating the gradual improvements in its malicious functionalities.

Nonetheless, AuKill doesn’t seem unique as analyzing the malware revealed numerous similarities with the open-source tool Backstab, which has also been abused in malicious campaigns. Hence, it appears that the malware authors used multiple code snippets from Backstab to derive their own tool.

To prevent AuKill and other such threats involving BYOVD, the researchers advise users to keep their systems up-to-date. Also, users must deploy endpoint protection, tamper protection, and vulnerability management measures to prevent such attacks.

Let us know your thoughts in the comments.


[ad_2]
Source link

ChatGPT writes insecure code

0
[ad_1]

Researchers have found that ChatGPT, OpenAI’s popular chatbot, is prone to generating insecure code.

Research by computer scientists associated with the Université du Québec in Canada has found that ChatGPT, OpenAI’s popular chatbot, is prone to generating insecure code.

“How Secure is Code Generated by ChatGPT?” is the work of Raphaël Khoury, Anderson Avila, Jacob Brunelle, and Baba Mamadou Camara. The paper concludes that ChatGPT generates code that isn’t robust, despite claiming awareness of its vulnerabilities. 

“The results were worrisome,” the researchers say in the paper. “We found that, in several cases, the code generated by ChatGPT fell well below minimal security standards applicable in most contexts.”

“In fact, when prodded to whether or not the produced code was secure, ChatGPT was able to recognize that it was not. The chatbot, however, was able to provide a more secure version of the code in many cases if explicitly asked to do so.”

In the experiment, the researchers assumed the role of a novice programmer who doesn’t have security in mind. They asked ChatGPT to generate code, specifying in some cases that the code would be used in a “security-sensitive context.” What they didn’t do, however, was specifically ask the AI chatbot to create secure code or include certain security features.

ChatGPT generated 21 applications written in five programming languages: C, C++, HTML, Java, and Python. The programs are simple, with 97 lines of code at most.

In its first run, ChatGPT produced five secure applications out of 21. When prompted for changes, it made seven more secure applications from the remaining 16.

The authors note that ChatGPT can only create “secure” code when a user requests it. When tasked with creating a simple FTP server for file sharing, it generated code without applying input sanitization (where code is checked for harmful characters and removed where necessary). ChatGPT only added the security feature after the authors prompted it to do so.

“Part of the problem seems to be that ChatGPT simply doesn’t assume an adversarial model of execution,” the authors say, explaining why the AI bot cannot create secure code by default. Despite this, the bot readily admits to errors in its code.

“If asked specifically on this topic, the chatbot will provide the user with a cogent explanation of why the code is potentially exploitable. However, any explanatory benefit would only be available to a user who ‘asks the right questions’. i.e.; a security-conscious programmer who queries ChatGPT about security issues.”

Additionally, the authors point to the chatbot’s ethical inconsistency when it refuses to create attack code but will create insecure code.

It might refuse to create attack code, but there are ways round it. Malwarebytes Security Evangelist Mark Stockley decided to try to create ransomware using ChatGPT. The AI bot refused to create malware code at first, but Stockley found his way around the initial safeguards and managed to get it to create (admittedly quite dubious) ransomware anyway.

In an interview with The Register, one of the Université du Québec researchers said he had concerns about ChatGPT. “We have actually already seen students use this, and programmers will use this in the wild,” Khoury said. “So having a tool that generates insecure code is really dangerous. We need to make students aware that if code is generated with this type of tool, it very well might be insecure.”


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Nokia XR21 rugged phone is coming, and here are its specifications

0
[ad_1]

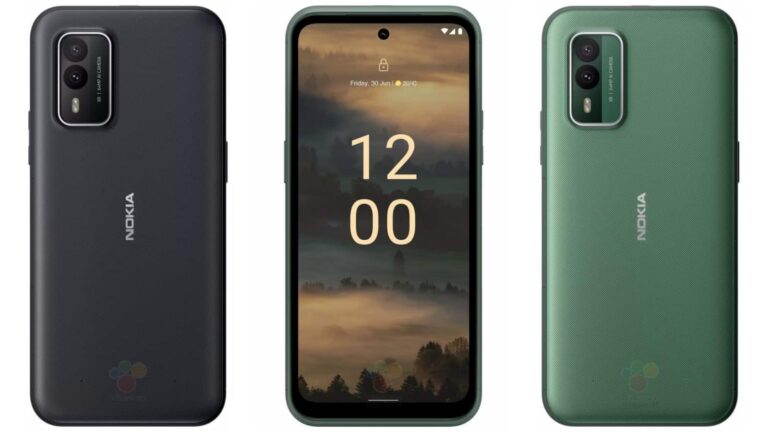
Yesterday, we shared images of the upcoming rugged phone from Nokia, and now its specifications surfaced. That’s not all, though. The source also confirmed the name of this handset, it’s not what was originally reported.

The Nokia XR21 will be the name of the company’s new rugged phone, and here are its specifications

The device appeared yesterday as the ‘Nokia Sentry 5G’, and everyone assumed it will be called the Nokia XR30. The Nokia XR20 launched back in 2021, so that’s why. It seems like the phone’s name will be the Nokia XR21, and not XR30.

This info comes from WinFuture, as does the spec list we’ll talk about. The Nokia XR21 won’t be a high-end smartphone, that much we knew. Still, its specs are nothing to scoff at, as long as the price is right.

Having said that, the phone will feature a 6.49-inch fullHD+ LCD display. It will be a 120Hz panel, and will be protected by the Gorilla Glass Victus. The Snapdragon 695 will fuel the phone.

You will also find 6GB of RAM on the inside, along with 128GB of storage. Android 12 will come pre-installed on the device, while the phone will also be IP68 certified for water and dust resistance.

A 4.800mAh battery will be included, while 33W charging will be supported

A 4,800mAh battery will power the device. 33W wired charging will also be included, but no wireless charging. A USB Type-C port will sit on the bottom, a 2.0 version of it. Bluetooth 5.1 will also be supported, as will WiFi 6.

The Nokia XR21 will include two cameras on the back. A 64-megapixel main camera (f/1.79 aperture) will be backed by an 8-megapixel zoom camera. You will also find two SIM card slots on the inside (+eSIM support), and an audio jack will also be included. The Nokia XR21 will weigh 235 grams.

The source also claims that Nokia will provide OS updates until May 2026, and security updates until May 2027. We still don’t know the price tag of the device, but it’s rumored to cost around $500. We’re not sure how accurate that is, so take that info with a grain of salt.


[ad_2]
Source link

Here’s what’s coming in iOS 17

0
[ad_1]

Apple is set to announce iOS 17 at WWDC in June, like they generally do. So far, the leaks about iOS 17 have been pretty underwhelming. Stating that it was more of a bug fixing and stability update – which is sorely needed on iOS right now.

But recently, we’ve been seeing more rumors about features coming to iOS 17. And today, there’s a new post over on Weibo detailing some of these changes. Now this poster was accurate about Apple revealing the iPhone 14 in yellow, so there is a track record here, though not a long one.

So what’s new in iOS 17?

So what is actually coming in iOS 17? Well according to this post, here’s what to expect:

  • Lock Screen font size options
  • A button to share custom Lock Screen designs with other iPhone users
  • Apple Music lyrics can be viewed on the Lock Screen
  • Apple Music design changes with simplified interface
  • App Library folders can be manually renamed
  • Control Center design changes
  • Flashlight brightness slider can be freely adjusted, like the volume slider

Again, nothing really ground-breaking here, and honestly a lot of these could be in a point update. But these are some nice changes to see coming in iOS 17. Particularly the ability to rename folders in the App Library. Since Apple’s sorting is not all that great right now.

This is likely not everything that is going to be new in iOS 17, and we’ll likely see some more leaks ahead of WWDC in June. Since we’re still a little over a month away at this point.

Apple will release the first developer beta for iOS 17 following the WWDC keynote on June 5. With the first public beta coming a month later, normally. And of course, the full rollout will come in September. Generally a few days before the new iPhone actually goes on sale. It’s normally between the iPhone announcement and launch.


[ad_2]
Source link

Git Project Flaws Let Attackers Execute Arbitrary Code

0
[ad_1]
Git Project Security Vulnerabilities

A fresh set of Git releases was made available to fix several security flaws. It gives attackers the ability to execute arbitrary code upon successful exploitation. Upgrades are advised for all users.

View of the Most Recent Batch of Releases On GitHub

To resolve two security flaws that affected versions 2.40.0 and earlier, CVE-2023-25652 and CVE-2023-29007, the Git project issued new versions.

Additional Windows-specific vulnerabilities, CVE-2023-25815, CVE-2023-29011, and CVE-2023-29012, were also fixed in Git.

Reports say new versions of the Git for Windows project were released with fixes for these five vulnerabilities.

“To protect against CVE-2023-25652 and CVE-2023-29007, users are encouraged to upgrade immediately”, GitHub reports.

With git apply –reject, the former may carry out controlled content writes at arbitrary paths.

The latter might be used to insert arbitrary configuration settings, which could execute arbitrary code.

The Windows-specific vulnerabilities affect users on multi-user computers, users working in Git CMD, and users using the SOCKS5 proxy connect.exe included in the Git for Windows distribution. Additionally, those who fit these categories are urged to upgrade immediately.

Upgrade To the Most Recent Git Release

GitHub suggests that the best defense against these vulnerabilities is an upgrade to Git 2.40.1. GitHub has taken severe measures to defend users from these attacks. Particularly,

  • It has scheduled a GitHub Desktop update that stops the exploitation of this vulnerability for release on April 26th, 2023.
  • Scheduled updates to upgrade the versions of Git used by GitHub Codespaces and GitHub Actions.

If you are unable to update right away, minimize your risk by doing the following:

  • Avoid using git apply –reject when working with patches from untrusted sources. Use git apply –stat to inspect a patch before applying it.
  • Avoid running git submodule deinit, git config –rename-section, and git config –remove-section on untrusted repositories or without prior inspection of your $GIT_DIR/config.

You can lower your risk on Windows by carrying out the following actions:

  • Avoid using Git for Windows on machines with shared accounts. Otherwise, create empty C:\mingw64 and C:\etc folders, and remove any write permission on them.
  • Avoid using Git CMD; if doing so is impossible, ensure it is started from a trusted directory.

“GitHub itself is not affected by these vulnerabilities. We do not use git apply –reject, nor Git’s configuration mechanism. GitHub does not use Git for Windows, and is thus not affected by those vulnerabilities, either”, GitHub said.

Struggling to Apply The Security Patch in Your System? – 
Try All-in-One Patch Manager Plus


[ad_2]
Source link

How attackers evade traditional AV and how to stop them

0
[ad_1]

Find threats camouflaging themselves in RAM.

When you hear about malware, there’s a good chance you think of sketchy executables or files with extensions like .DOCX or .PDF that, once opened, execute malicious code. These are examples of file-based attacks—and while they can be bad, they’re nothing compared to their fileless cousins.

As the name suggests, fileless attacks don’t rely on traditional executable files to get the job done but rather in-memory execution, which helps them evade detection by conventional security solutions.

In this post, we’ll explore topics like how fileless attacks work, why they’re effective, and what you can do to find and block fileless threats.

Fileless attacks explained

In contrast to file-based attacks that execute the payload in the hard drive, fileless attacks execute the payload in Random Access Memory (RAM). Executing malicious code directly into memory instead of the hard drive has several benefits, such as:

  • Evasion of traditional security measures: Fileless attacks bypass antivirus software and file signature detection, making them difficult to identify using conventional security tools.   
  • Increased potential for damage: Since fileless attacks can operate more stealthily and with greater access to system resources, they may be able to cause more damage to a compromised system than file-based attacks.
  • Memory-based attacks can be difficult to remediate: Since fileless attacks don’t create files, they can be more challenging to remove from a system once they have been detected. This can make it extra difficult for forensics to trace an attack back to the source and restore the system to a secure state.

Fileless attacks vs Living-off-the-land (LOTL) attacks

If you read our article on LOTL attacks, you may be confused: Aren’t fileless attacks and LOTL attacks the same thing? Well, yes and no.

LOTL attacks are anytime an attacker leverages legitimate tools to evade detection, steal data, and more, while fileless attacks refer purely to executing code directly into memory. While both types of attacks often overlap, they are not synonymous.

Think of fileless attacks as an occasional subset of LOTL attacks. Fileless attacks can and often do leverage LOTL techniques to execute payload into memory, but they can also do so without leveraging a legitimate system tool or process at all.

PowerShell script extracted from a Microsoft Word document. If macros are enabled, it would execute the code in memory upon being opened. Source.

For example, an attacker can use PowerShell to download and execute a malicious payload directly in memory, without writing it to the disk. In this case, the attack is both LOTL (since PowerShell is a legitimate tool) and fileless (as the payload is executed in memory).

On the other hand, an attacker injecting malicious JavaScript into a website can exploit browser vulnerabilities and execute payloads in memory. This fileless attack executes code without writing to the hard drive, but doesn’t qualify as LOTL as it doesn’t use a legitimate system tool or process.

5 different ways fileless attacks execute code in memory

Once an attacker gains access through phishing or exploiting vulnerabilities, they can execute malicious code in memory using several methods, some of which may overlap with LOTL techniques.

Below are five common techniques used in fileless attacks:

  • PowerShell: A legitimate scripting that can execute malicious code directly in memory. As mentioned earlier, this technique overlaps with LOTL attacks as it leverages a built-in system tool.
  • Process hollowing: Process hollowing is a fileless technique where attackers create a new process in a suspended state, replace its memory content with malicious code, and then resume the process. The malicious code executes in memory without writing to the disk.
  • Reflective DLL injection: In this fileless attack, attackers load a malicious Dynamic Link Library (DLL) into a legitimate process’s memory without writing it to the disk. The DLL is executed directly in memory, evading detection by traditional security software.
  • JavaScript and VBScript: Fileless attackers can use JavaScript or VBScript to run malicious code directly in memory within a web browser or other applications that support these scripting languages.
  • Microsoft Office macros: Fileless attackers can use malicious macros embedded in Microsoft Office documents to execute code in memory when the document is opened. This method takes advantage of the legitimate macro functionality, making it an example of an LOTL technique as well.

Note that fileless attacks often rely on exploiting vulnerabilities in system components in each of these instances (such as Office or web-browsers) to execute their code. 

Preventing and spotting fileless attacks: Quick tips

Prevention Method Description
Keep software and systems updated Regularly update your operating systems, applications, and security software to patch vulnerabilities that could be exploited by fileless attackers.
Regularly review security logs Examine security logs for unusual activity or patterns that could indicate a fileless attack, such as unexpected PowerShell usage or excessive network connections.
Employ behavioral analytics Use advanced threat detection tools that employ behavioral analytics to identify and block fileless attacks based on their unique behavior patterns.
Restrict macro usage Limit the use of Microsoft Office macros by disabling them or allowing only digitally signed and trusted macros.

Malwarebytes EDR and Exploit Protection: Safeguarding against fileless attacks

Malwarebytes Exploit Protection can effectively block many fileless attacks by monitoring and reinforcing application behavior, hardening applications, and ensuring advanced memory protection.

To configure Exploit Protection Advanced settings, follow these steps:

Exploit Protection settings in a policy in Malwarebytes EDR.

Here’s an overview of the protection layers offered by Malwarebytes EDR Exploit Protection:

  • Application Hardening: By enforcing security measures like DEP and ASLR, and disabling potentially vulnerable components like Internet Explorer VB Scripting, Application Hardening reduces the attack surface and makes it more difficult for fileless malware to exploit weaknesses in applications.
  • Advanced Memory Protection: This layer prevents fileless malware from executing payload code in memory by detecting and blocking techniques such as DEP bypass, memory patch hijacking, and stack pivoting, thereby stopping the attack before it can cause harm.
  • Application Behavior Protection: This layer also detects and blocks exploits that do not rely on memory corruption, such as Java sandbox escapes or application design abuse exploits. Options include Malicious LoadLibrary Protection, Protection for Internet Explorer VB Scripting, Protection for MessageBox Payload, and protection against various Microsoft Office macro exploits. 
  • Java Protection: These settings protect against exploits commonly used in Java programs. By guarding against Java-specific exploits, such as web-based Java command execution and Java Meterpreter payloads, Java Protection can effectively prevent fileless attacks that leverage Java vulnerabilities to infiltrate systems and execute malicious code.

Fighting fileless threats with Malwarebytes EDR: Configuring Suspicious Activity Monitoring in Nebula

Malwarebytes Endpoint Detection and Response (EDR) offers an effective solution to detect and mitigate fileless malware threats by monitoring potentially malicious behavior on endpoints. The Suspicious Activity Monitoring feature in Nebula uses machine learning models and cloud-based analysis to detect questionable activities. In this section, we will outline how to configure Suspicious Activity Monitoring in Nebula.

To enable Suspicious Activity Monitoring in your policy:

  • Log in to your Nebula console.
  • Navigate to Configure > Policies.
  • Click “New” or select an existing policy.
  • Choose the “Endpoint Detection and Response” tab.
  • Locate “Suspicious Activity Monitoring” and enable it for the desired operating systems.

Suspicious Activity monitoring detections in Nebula showing a possible fileless attack. On the right, we see the command line context for this process in our organization.

Advanced Settings offer additional options for activity monitoring. To configure these settings:

  • In the same “Endpoint Detection and Response” tab, find the “Advanced Settings” section.
  • Enable “Server operating system monitoring for suspicious activity” to extend monitoring to server operating systems. 
  • Enable “Very aggressive detection mode” to apply a tighter threshold for flagging processes as suspicious. 
  • Toggle “Collect networking events to include in searching” to ON (default) or OFF, depending on your preference. Turning it OFF decreases traffic sent to the cloud.

Flight Recorder Search

Flight Recorder Search collects all endpoint events within its search functionality. By configuring Suspicious Activity Monitoring in Malwarebytes EDR through the Nebula platform, you can effectively counter fileless malware threats by monitoring processes, registry, file system, and network activity on the endpoint. 

Respond to fileless attacks quickly and effectively

Managed Detection and Response (MDR) services provide an attractive option for organizations without the expertise to manage EDR solutions. MDR services offer access to experienced security analysts who can monitor and respond to threats 24/7, detect and respond to fileless attacks quickly and effectively, and provide ongoing tuning and optimization of EDR solutions to ensure maximum protection. 

Stop fileless attacks today


[ad_2]
Source link

Samsung is already rolling out May 2023 update to Galaxy devices

0
[ad_1]

Samsung has made it a habit of releasing the latest monthly security patches way ahead of schedule. It often starts pushing a new security update several days before we hit the new month. The Korean behemoth has done it again. It has begun seeding the May 2023 Android security patch to its Galaxy devices. But unlike most past instances, the company is starting with an entry-level model this time around. The Galaxy A10e is picking up the May SMR (Security Maintenance Release) ahead of flagship models.

The May update for the Galaxy A10e is currently available for users in Samsung’s home country South Korea. The rollout began earlier this week with the firmware build number A102NKOS3CWD1, SamMobile reports. Since May is still a few days away, we don’t have details of the patch. It’s unclear which vulnerabilities have been fixed with the latest monthly security release for Android devices. As usual, there should be several dozen fixes here, including a few Galaxy-specific ones coming directly from Samsung.

Don’t expect anything apart from the latest security fixes, though. Samsung launched the Galaxy A10e in July 2019. The entry-level smartphone is now in its last legs (fourth year in the market). It stopped receiving major Android updates since Android 11 and will soon stop getting security patches too. The May SMR could be the penultimate update for it. The 2019 handset isn’t covered under the Korean firm’s extended update policy that promises five years of security updates for Galaxy devices.

Nonetheless, if you’re using the Galaxy A10e, you may receive the May update sooner or later. It’s not guaranteed, though. Samsung may not push the May SMR to this phone outside of South Korea. The US version recently received the April update (firmware version A102USQSFCWC3 for carrier-locked units and A102U1UESFCWD1 for unlocked units), which never reached the company’s homeland. It may now skip the May release in other markets. As usual, you can check for new updates from the Settings app on your phone.

Samsung will soon release the May update for other Galaxy devices

The Galaxy A10e may not get the May update everywhere but Samsung will soon release the latest SMR for other Galaxy devices. Despite beginning with a budget handset, flagship models should still get the priority once it starts a wider rollout. The Galaxy S23 series should sit high on this priority list, though not necessarily at the top. We will let you know as and when these updates come.


[ad_2]
Source link

Google takes legal action to take down CryptBot malware

0
[ad_1]

It’s no secret that over the past few years, threat actors have become more sophisticated in their efforts to scam people of their hard-earned money and steal personal information. One of the methods which the threat actors have recently been using to infiltrate systems is the CryptBot malware. This malicious software steals sensitive information such as passwords, cookies, and credit card information and sells it to other malware makers and distributors. However, Google has finally taken action and disrupted the malware’s infrastructure and distributors.

In the blog post announcing the decision, Google revealed that the CryptBot malware, which spread through malicious apps such as a fake Google Chrome and Google Earth Pro, infected around 670,000 computers last year, compromising users’ personal information and selling it for data breach campaigns. However, Google’s recent action will help prevent new infections and slow the malware’s growth.

“Lawsuits have the effect of establishing both legal precedents and putting those profiting, and others who are in the same criminal ecosystem, under scrutiny. This litigation is another step forward in holding cybercriminals accountable, by not just targeting those that operate botnets, but also those that profit from malware distribution,” reads the company’s blog post.

How did Google take down the malware?

Google’s actions against the malware came after the company identified the malware’s Pakistan-based distributors with the help of its Threat Analysis Group (TAG) and took legal action against them. Google filed a legal complaint against many major CryptBot distributors and secured a temporary court order to hamper the developers’ ability to spread the malware. With the order, Google was able to take down the current and future domains linked to the distribution of the malware.

While Google’s action against the malware distributors is commendable, considering its brand identity was at stake, the incident highlights the need for users to take necessary precautions while browsing the web. These include downloading apps and software from credible sources, keeping operating systems up to date, and installing antivirus software.


[ad_2]
Source link

Magecart threat actor rolls out convincing modal forms

0
[ad_1]

It’s hard to put individuals at fault when the malicious copy is better than the original. This credit card skimmer was built to fool just about anyone.

To ensnare new victims, criminals will often devise schemes that attempt to look as realistic as possible. Having said that, it is not every day that we see the fraudulent copy exceed the original piece.

While following up on an ongoing Magecart credit card skimmer campaign, we were almost fooled by a payment form that looked so well done we thought it was real. The threat actor used original logos from the compromised store and customized a web element known as a modal to perfectly hijack the checkout page.

While the technique to insert frames or layers is not new, the remarkable thing here is that the skimmer looks more authentic than the original payment page. We were able to observe several more compromised sites with the same pattern of using a custom-made and fraudulent modal.

This skimmer and associated campaigns represent one of the most active Magecart attacks we have been tracking in recent months.

Smooth checkout 

We identified a compromised online website for a Parisian travel accessory store running on the PrestaShop CMS. A skimmer we previously identified as Kritec, was injected and loading malicious JavaScript that altered the checkout process. In the following section, we will compare the checkout process when the skimmer is active and when it is not.

Fraudulent payment form

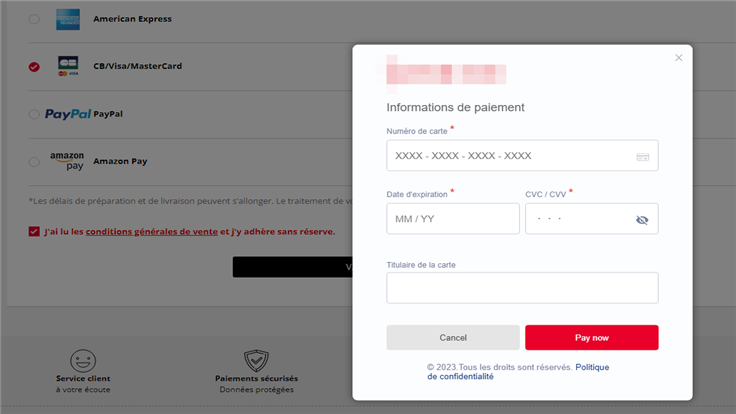
What we see here is the use of a ‘modal‘ which is a web page element displayed in front of the current active page. The modal disables and grays out the background so that the user can focus on the presented element instead. This is an elegant way for website owners to keep their customers on the same web site and have them interact with another form.

Figure 1: Compromised store loads fake payment modal

The problem is that this modal is entirely fake and designed to steal credit card data. It may sound hard to believe given everything matches to the original brand and feel of the site. Before digging further into why it is fraudulent, we will take a look at the same online store when the skimmer has been disabled.

Actual (real) payment form

In order to view this legitimate sequence, we first had to block the skimmer when requesting the e-commerce page. In our case, we simply blocked the connection to the malicious domain where the skimmer is hosted. As a result, the website will display what the original payment form should be (prior to the compromise).

Figure 2: Legitimate payment form when same store is not compromised

The actual payment flow for this merchant is to redirect users to a third-party processor hosted by Dalenys, now part of Payplug, a French payment solutions company. So rather than display a modal, it loads the webpage for the payment processor to allow the user to enter their banking information. Once that is validated, it will take them back to the merchant page.

Malicious modal

The malicious modal is built very cleanly and contains an animation that displays the store’s logo in the middle and then moves it back up. We have to give credit where credit is due: this is a very well done skimmer that is actually a smoother user experience than the store’s default. We should also note that the malware author is not only well versed in web design, they also use proper language (French) for each form field.

Figure 3: A closer look at the fake modal

However, we noticed a small mistake in the hyperlink for Politique de confidentialité (terms of use). That link redirects to the terms of use for Mercardo Pago, a payment processor used in South America. It is likely the threat actor copied the data from a previous template and did not notice their mistake. This is just a detail, and does not affect the functionality of the skimmer at all.

We can try to look for this erroneous hyperlink within the skimmer source code in order to confirm that the modal was created by the threat actor. The skimmer is rather complex and heavily obfuscated but we can see that HTML content is generated dynamically and goes through a decodeURIComponent routine.

Figure 4: Extracting code from the skimmer to reveal connection with the modal

If we step through the code until the modal is loaded, we can grabbing the Base64 value corresponding to the HTML content. One we have it, we can convert it to plain text and finally see the reference to mercadopago, that is proof that the skimmer is the one rendering this beautiful modal. In fact, we can see the whole thing is an iframe called v.ECPay:

Figure 5: The iframe created by the skimmer to display the modal

Full payment flow

We recreated the payment flow from the perspective of a customer shopping via that compromised store. We can see that upon selecting the credit card payment option, the malicious modal is loaded and will harvest their payment card details.

A fake error is then displayed briefly “votre paiment a été annulé” (your payment was cancelled) before the user is redirected to the real payment URL:

Figure 6: Payment process flow with the skimmer active

On the second attempt, the payment will go through and victims will be unaware of what just happened.

The skimmer will drop a cookie which will serve as an indication that the current session is now marked as completed. If the user was to go back and attempt the payment again, the malicious modal would no longer be displayed (instead the real payment method by the external processor Dalenys will be used).

Figure 7: Cookie dropped by skimmer once data has been stolen

Ongoing, covert campaigns

We now believe this Kritec skimmer is part of the same compromises with injections into vulnerable websites where malicious code is placed within the Google Tag Manager script. It is possible multiple threat actors are involved in those campaigns and customizing skimmers accordingly.

While many hacked stores had a generic skimmer, it appears the custom modals were developed fairly recently, maybe a month or two ago. The threat actor is using different domains to host the skimmer but names them in a similar way: [name of store]-loader.js.

We crawled several thousand e-commerce sites and found more fraudulent modals, in different languages.

Figure 8: A Dutch e-commerce site with the fake modal

Figure 9: A Finnish e-commerce site with the fake modal

Discerning whether an online store is trustworthy has become very difficult and this case is a good example of a skimmer that would not raise any suspicion.

If you are a Malwarebytes customer, you will get a notification and block when attempting to make a purchase from a store that has been compromised by this skimmer.

Figure 10: Skimmer being blocked by Malwarebytes

Indicators of Compromise

Domain names

genlytec[.]us
shumtech[.]shop
zapolmob[.]sbs
daichetmob[.]sbs
interytec[.]shop
pyatiticdigt[.]shop
stacstocuh[.]quest

IP addresses

195.242.110[.]172
195.242.110[.]83
195.242.111[.]146
45.88.3[.]201
45.88.3[.]63

YARA rule

rule kritecloader
{
 strings:
     $string = "'fetchModul'"
     $string2 = "'setAttribu'"
     $string3 = "'contentWin'"
     $string4 = "'zIndex'"

condition:
    all of them
}


Whether you are visiting an online store from home or while at work, web protection is a critical layer in your overall defense. Malwarebytes Premium for consumers and Endpoint Protection for businesses provide real-time protection against threats like Magecart.

TRY NOW

[ad_2]
Source link