What is a virtual board room and what are its benefits?

0
[ad_1]

Modern businesses have long felt the impact of the virtual boardroom on the company as a whole. If you still think that this technology is used exclusively for conducting various kinds of video conferences, you are mistaken. At this point, it is an exceptional technology that can optimize entire business processes. At this point, we will look at some features of this software so that you can rationally choose it as the main one for your company. We’ll show some of the advantages that you need to consider when selecting this technology. We’ll look at what it is in general and give a precise definition that will help you further in your choice.

A board portal, what does it mean exactly?

The board meeting portal software is a versatile tool for modern businesses that can significantly enhance meetings and overall performance. It features built-in in-house conferencing or integrates with popular platforms such as Google or Microsoft servers. While video conferencing is a key feature, the software’s real value lies in its enhanced security and secure storage for meeting documents. It also offers various tools to facilitate decision-making for administrative or senior staff. Discover the many functions and tools of this software in the following discussion. Essentially, the boardroom portal is designed to automate and provide a paperless solution for businesses, which can alleviate overworked workflows and exhausted employees.

Streamlining Business Processes: Essential Features of Board Portal

Boardroom portals offer a plethora of innovative features that can revolutionize the way your company operates. Automation is at the core of this software, which can bring a level of efficiency that traditional methods simply cannot match. By using cloud computing on third-party servers with military-grade encryption and physical security measures, a board portal provides an unparalleled level of protection for your data.

  • Say goodbye to paperwork, thanks to secure cloud storage. With all your documents stored digitally, you no longer need to worry about buying paper and ink. Plus, in case of a natural disaster, your documents will be safe and secure. Accessing your files is easy—simply log in to your account via an app or web browser, and use eSignature to sign any necessary documents.
  • A unique video conferencing tool with an abundance of features that cannot be found elsewhere. As we have mentioned earlier, a virtual board software is a distinctive creation that exclusively focuses on executing intricate business processes and is equipped with a plethora of interesting functionalities to support those processes. In case you have any unresolved issues or your strategy is incomplete, these tools can provide valuable assistance during discussions, as none of the negotiation participants will be distracted or delay the conference in any way.
  • All interactions through boardroom portals are equipped with a fundamental level of security that extends to both online board meeting and data logging. This includes secure storage for recordings that only authorized personnel can access and personal accounts that are protected from potential intruders. To ensure maximum security, additional layers of protection such as isolation from the general internet and two-factor authentication are also implemented.

These are the core features that you will find in all software examples, and it’s crucial to keep that in mind.

The Promising Future of Board Portal Technology

According to independent researchers, the board management software has a bright future and is among the most promising corporate tools for business growth and optimization of resources. It can help you achieve a lot in terms of business development and automation.

  • The board portal can help you streamline your document management, potentially saving you time. Dealing with documents can be a time-consuming task, but the board portal aims to mitigate this. Its comprehensive set of tools simplifies document management and improves existing documents through smart indexing and file organization, among other features.
  • Keeping track of all meetings is crucial for ensuring effective communication and decision-making within a paperless meeting solution company. With a board portal, you can rest assured that every meeting is documented and monitored closely. This will help you avoid missing any key moments and reduce the number of unproductive meetings. Plus, you can access and review any meeting at any time.
  • Incorporating modern advancements, board portals utilize technologies like artificial intelligence and the Internet of Things. Artificial intelligence optimizes file organization and monitors meeting activity, while the Internet of Things connects various devices on a local Wi-Fi network to track user and employee performance. From webcams to coffee machines, all devices are part of a single system.

Board portal software is a great asset that helps you effectively conduct meetings and manage employee activities, making it an important resource for businesses that want to stay relevant in today’s marketplace.


[ad_2]
Source link
Lockbit Ransomware Aims To Target macOS Systems

0
[ad_1]

After wreaking havoc with Windows and Linux systems, the LockBit ransomware gang now intends to target macOS devices. However, researchers believe the malware may not be as successful on Mac due to Mac’s innate security.

LockBit Ransomware To Target macOS Systems

In a recent tweet, the MalwareHunterTeam disclosed encountering a new LockBit ransomware variant. Identified as “locker_Apple_M1_64” by the researchers, the new malware seems the first such attempt to target Mac specifically.

LockBit is a potent ransomware available as RaaS, initially targeting Windows, and later, Linux systems. During the past years, LockBit has executed numerous terrifying cyberattacks aimed at big services, like UK’s suburban train systems, the Swiss helicopter maker firm, and more. It then gradually improvised as LockBit 2.0, conducting even more severe attacks such as the Italian energy firm.

Later on, another ransomware variant, LockBit 3.0, also surfaced online, exhibiting more malicious capabilities. And the threat actors appeared more motivated to improve the malware as they announced a bug bounty program.

And now, it seems perfectly timed for the threat actors to take the lead in the RaaS world by announcing a dedicated Apple ransomware.

Following MalwareHnterTeam’s disclosure, vxunderground also confirmed having the malware samples.

While the ransomware initially escaped the radar of almost antivirus solutions, following this disclosure, VirusTotal now shows that many robust services have started flagging the malware samples.

Can LockBit Really Harm Macs?

Though LockBit successfully stirred up the cybersecurity realm by confirming its initiatives for targeting macOS. But can it hurt Mac devices as severely as Windows and Linux?

The researcher Patrick Wardle believes otherwise. As elaborated in his blog post, although the malware can reach Apple Macs, but it cannot successfully infect them – at least, for now. That’s because of macOS’s inherent security design that most malware find difficult to bypass.

In the case of the LockBit “locker_Apple_M1_64” variant, its first weakness lies in code signing. Wardle highlighted that the malware is signed as “ad-hoc,” and macOS doesn’t allow running such apps on the systems.

Besides, the researcher also deeply analyzed the malware and found nothing specific in it which could enable the ransomware to run on Macs. So, at present, this variant looks like nothing serious for Mac users.

Specifically, Apple has implemented SIP (and now read-only system volumes) to protect OS-level files. This means even if ransomware finds its way onto a macOS system it won’t (easily) be able to mess with core OS files. Apple has also added (TCC) protections to user files founds in (now) protected directories such as ~/Desktop, ~/Documents, etc. etc. This means, that without an exploit or explicit user-approval users files will remain protected.

Nonetheless, it doesn’t mean that Apple devices will remain immune to ransomware for eternity. Also, there have been several instances where Mac devices endured malware attacks. Wardle also pointed out that such a step from a large ransomware group shouldn’t appear trivial to the security community.

Therefore, it remains crucial for Apple, security professionals, and users to remain vigilant about protecting their Macs from such threats.


[ad_2]
Source link

Remembering some of the worst Android phones of all time

0
[ad_1]

Even the staunchest android fan will admit that android devices haven’t always hit the mark. In fact, it’s no secret that we’ve been exposed to a number of stinkers over the years.

In previous times, manufacturers tried to impact the space with a variety of android phones that really didn’t deliver. We aren’t just talking about horrific Chinese knock-offs here either, instead devices by respected brands, such as Motorola and Samsung, that were flawed. Of course, this particular topic is ultimately subjective, but there is no doubt that the android category has been filled with shoddy devices over the years.

Thankfully, in the modern world, innovation has improved things. Now, in 2023, android users can capture high-quality images that outdo the digital cameras of old, people can explore gaming options like the buffalo game show, a type of live casino game that features a croupier as host and enables gamers to experience casino life in the palm of their hands, while Android phones can also help us find love with a few swipes or stream live sport, too. In order to get here, though, we’ve had to endure some seriously dodgy phones. Let’s look at some of the worst of them below.

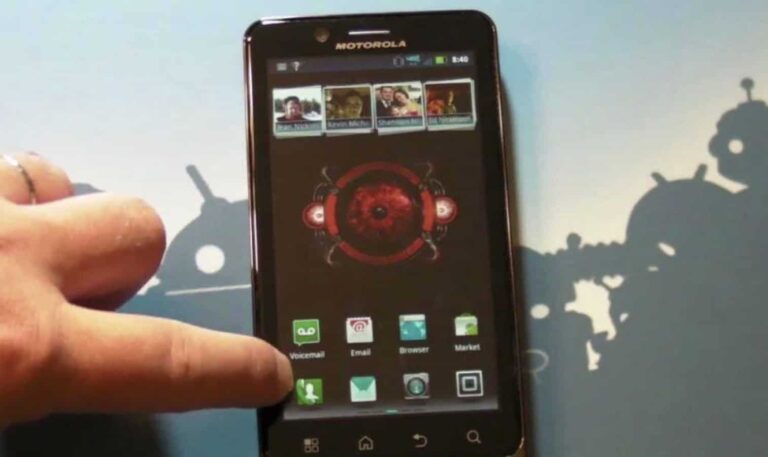
The Motorola DROID Bionic bombed massively

If you’re an avid android user and know about the history of android phones, then you’ve probably stumbled across the Motorola DROID Bionic before. It’s fair to say that this particular device bombed spectacularly, too, with a delayed release being credited with two or three redesigns that didn’t tickle many people’s fancy. When the phone eventually did hit the shelves, it was riddled with bugs that made it feel like nothing short of a lazy release. The problems were extensive from the offset, but the phone was still being marketed to potential customers. In fairness, the device was eventually corrected in the following months, but what came before that put many consumers off. What a shambles.

The HTC EVO 3D provided a miserable experience

A device that created a lot of hype thanks to its “revolutionary” 3D camera that was apparently going to change the game, the HTC EVO 3D was a massive letdown. While the camera did deliver a solid photo-taking experience, it wasn’t anything like the manufacturers hyped it up to be. Throw in the phone’s shocking battery life and its rather poor design that chipped easily, and it’s fair to say that the HTC EVO 3D really didn’t live up to expectations.

Samsung Galaxy Note 7 caught fire for no apparent reason

Despite the Samsung Galaxy Note 7 offering a range of impressive features, such as its solid battery and its lovely curved display, the fact that users were sending back devices and avoiding serious accidents due to the phone catching on fire made it a nightmare. Exploding phones aren’t new, of course, but the fact that it happened with a highly anticipated device, and that it was recalled initially only to then start catching on fire again, will go down as one of Samsung’s worst moments ever.

You wouldn’t give the Kyocera Echo to your worst enemy

Kyocera Echo image 893483984
Source: https://twitter.com/x3isofficial

It’s probably no surprise that Kyocera failed to hit the right notes, given the brand’s horrific track record, but the Kyocera Echo was expected to buck the trend. Sadly, and somewhat predictably, it was an absolute disaster. Not only did the device resemble a brick, but the over-exaggerated bezel was a pain. Additionally, while the two 3.5-inch screens promised a lot and sounded intriguing initially, they resulted in a truly painful user experience that was nothing but a classic case of terrible engineering.


[ad_2]
Source link

The role of branding in digital marketing strategies

0
[ad_1]

In today’s digital world, branding has become a crucial aspect of marketing strategies. A brand is much more than just a logo or a name; it represents the identity and reputation of a company. Digital marketing has opened a whole new world of opportunities for businesses to establish their brand and connect with their target audience. The rise of digital marketing has made it easier for businesses to reach their target audience and establish a strong online presence.

However, with the growing competition, it has become challenging for companies to stand out and create a lasting impression on their customers. This is where branding comes into play. By developing a strong brand identity, companies can differentiate themselves from their competitors and create a loyal customer base. This article will explore the role of branding in digital marketing strategies and how it can help businesses stand out in a crowded market.

Understanding Branding in Digital Marketing

“Branding” is the process that provides a company with an exclusive identity. It includes everything from the logo, name, colors, tone of voice, and overall personality of the company. In digital marketing, branding goes beyond just creating a visual identity. It also involves creating a consistent experience for customers across all digital channels, including social media, websites, email marketing, and mobile apps.

By working with a reputable branding agency, businesses can create a unique brand identity that reflects their values and resonates with their customers. Whether it’s developing a new logo or creating a consistent brand voice across all digital channels, branding services in Los Angeles can help businesses differentiate themselves from their competitors and establish a strong online presence.

Importance of Branding in Digital Marketing

Branding is crucial for businesses that want to establish a strong online presence and connect with their target audience. Here are some of the key benefits of branding in digital marketing:

  • Differentiation: A strong brand identity helps businesses stand out from their competitors and create a unique image in the minds of their customers.
  • Recognition: Consistent branding across all digital channels can help businesses build brand recognition and increase their visibility.
  • Trust and Loyalty: A well-established brand creates a sense of trust and loyalty among customers, making them more likely to make repeat purchases.
  • Increased Engagement: A strong brand identity can lead to increased engagement on social media, email marketing, and other digital channels.

Building a Strong Brand Identity

Building a strong brand identity requires a strategic approach. Here are some of the key steps to creating a strong brand identity:

Defining Your Brand

Establishing what your brand stands for is the first step in creating a strong brand identity. Identifying your mission, values, and distinctive selling points is a part of this. By understanding what sets your brand apart, you can create a message that resonates with your target audience.

Creating a Brand Voice

The tone and personality of your brand are reflected in its brand voice. It should be consistent across all digital channels and reflect the values of your brand. Your brand voice should be tailored to your target audience and help you connect with them on a deeper level.

Consistency in Branding

Consistency is key when it comes to branding. Your brand identity should be consistent across all digital channels, including your website, social media profiles, email marketing, and mobile apps. This creates a cohesive brand experience for your customers and helps build brand recognition.

Incorporating Your Brand in All Marketing Channels

Incorporating your brand identity into all marketing channels is crucial for establishing a strong online presence. This includes creating visually appealing graphics and messaging that align with your brand voice. By creating a consistent brand experience across all channels, you can establish trust and recognition among your target audience.

The Connection Between Branding and SEO

Branding and SEO are interconnected in digital marketing. A strong brand identity can have a positive impact on your search engine rankings. By establishing a recognizable brand, you can increase your brand mentions and backlinks, which are important factors for SEO.

Additionally, having a consistent brand identity across all digital channels can help search engines identify your brand and improve your visibility in search results.

Measuring the Success of Your Branding Efforts

Measuring the success of your branding efforts is essential for optimizing your digital marketing strategy. Here are the two most important metrics you should monitor:

Tracking Brand Awareness

Tracking brand awareness involves monitoring brand mentions and social media engagement. By tracking your brand mentions, you can identify areas where you need to improve your brand messaging and increase your visibility.

Analyzing Brand Engagement

Analyzing brand engagement involves monitoring your website traffic, email open rates, and social media engagement. By tracking these metrics, you can identify which digital channels are driving the most engagement and adjust your strategy accordingly.

Common Branding Mistakes to Avoid

Avoiding common branding mistakes is crucial for establishing a strong brand identity. Here are some typical branding missteps that you should stay away from:

Inconsistent Branding

Inconsistent branding can confuse your target audience and undermine your brand identity. To avoid this, make sure that your brand messaging and visuals are consistent across all digital channels.

Not Understanding Your Target Audience

Not understanding your target audience can lead to ineffective branding efforts. To create a strong brand identity, you need to understand the needs and preferences of your target audience.

Ignoring Brand Reputation

Ignoring your brand’s reputation can negatively affect your digital marketing strategy. Make sure that you monitor your online reputation and address any negative feedback or reviews.

Conclusion

In conclusion, branding is a crucial aspect of digital marketing strategies. By creating a strong brand identity, businesses can differentiate themselves from their competitors and establish trust and loyalty among their customers. Building a strong brand identity requires a strategic approach, including defining your brand, creating a consistent brand voice, and incorporating your brand identity into all digital channels. Measuring the success of your branding efforts is also essential for optimizing your digital marketing strategy.


[ad_2]
Source link

Your Chrome tabs and bookmarks could soon be found using the Pixel launcher search bar

0
[ad_1]
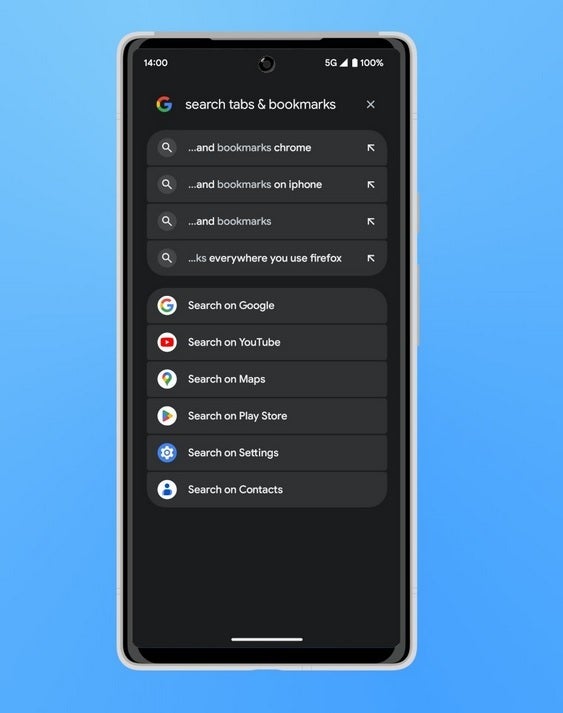
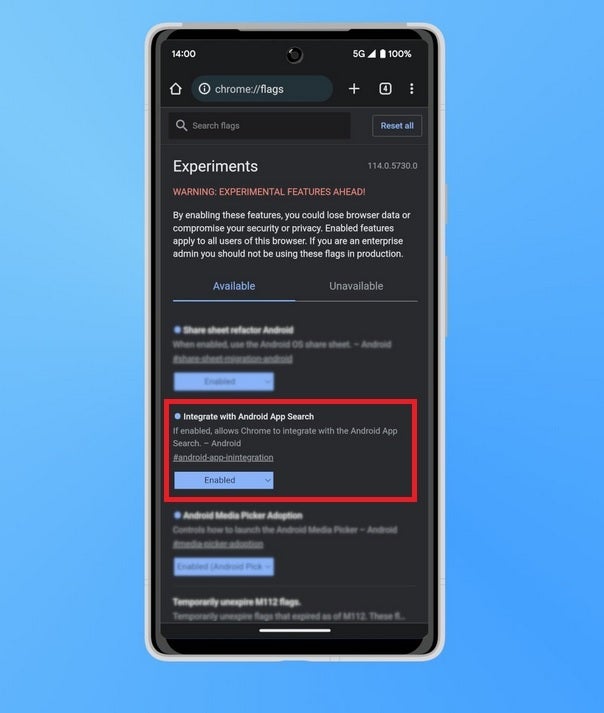
A Chrome feature flag called “Integrate with Android App Search” was spotted by LanceAdams on Telegram (via mobile tech journalist Mishaal Rahman, AndroidPolice) indicating that Chrome tabs and bookmarks could be found and opened by using the search bar on the Pixel Launcher.  A previous version of the flag made it clear what it will do: “Donate the tabs and bookmarks to Android App Search.” A feature flag, found on developer options, allows you to enable or disable a new feature without having to install an update.
While this feature should debut on Pixel models, it could end up on other Android handsets outside of the Pixel series. Last year it appeared that Google was going to allow the Pixel Launcher search bar to search from inside additional apps while it would also appear on third-party launchers. So far, though, we haven’t seen this come to light. With the discovery of the “Integrate with Android App Search” flag, it’s possible that we could soon see the Pixel Launcher search bar appear on third-party launchers and grab info from inside more apps.


If you don’t own a Pixel but have a thing for the Pixel Launcher’s search bar, a third-party app called the Pixel Search app is available from the Play Store. The app is free and the developer behind it, Rushikesh Kamewar, has 15 apps already available in the Google Play Store. The only thing the app can’t do that the real Pixel Launcher search bar can is search for is system settings although Kamewar says that such a feature will eventually be added to the app.

Being able to search for your Chrome apps from the Pixel Launcher search bar will allow users to return to their Chrome browsing session without having to reopen the app. It also will allow users to reduce the number of Chrome tabs they have open, and make it easier to find Chrome bookmarks.


[ad_2]
Source link

Google Authenticator Major Update Brings Cloud Backup Feature

0
[ad_1]
Google Authenticator

Google Authenticator was launched in 2010, which provides additional security for various applications by providing authentication codes for every sign-in.

This prevents attackers from account takeover on any application linked with Google Authenticator.

Google has launched various authentication mechanisms like Google Password Manager, Sign in with Google, Google Authenticator, One-tap sign-in to Google account, etc.

Google Authenticator

Google has also been working on simplifying the process of secure sign-in.

Though Google Authenticator can provide better protection and advantage to security, it still has a great drawback.

If a user loses the device in which this Google authenticator is installed, they face an account lockout as they cannot log in without the authentication codes.

However, Google has now released a new feature in Google authenticator that will help overcome the problem of devices lost/stolen.

This new update on Google authenticator has the option to backup codes to users’ Google accounts as a safety mechanism. This update is now available for both Android and iOS platforms.

“With this update we’re rolling out a solution to this problem, making one-time codes more durable by storing them safely in users’ Google Account. This change means users are better protected from the lockout and that services can rely on users retaining access, increasing both convenience and security.” reads the post from Google.

Google also stated they have been working on a “passwordless future.” Google has partnered with the FIDO alliance for a convenient and secure authentication offering like “passkeys.”

Users must update their Google authenticator application on their devices to use this feature.

Building Your Malware Defense Strategy – Download Free E-Book


[ad_2]
Source link

Galaxy Z Fold 5 will be shorter, narrower, & thinner than Fold 4

0
[ad_1]

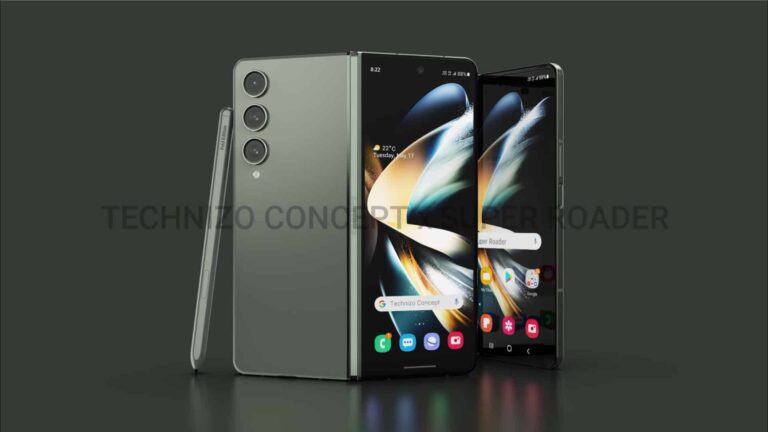
We have long known that Samsung‘s upcoming foldable smartphone Galaxy Z Fold 5 will be thinner and lighter than its predecessor. The device will also fold gapless thanks to the new waterdrop hinge. Reputed tipster Ice Universe has now compared how it stacks up against the 2022 model in terms of dimensions and weight. They have also given us a visual showing the difference between the two foldables.

According to the new report, the Galaxy Z Fold 5 will measure 154.9 x 129.9 x 6.1mm when unfolded. In comparison, the Galaxy Z Fold 4 measures 155.1 x 130.1 x 6.3mm. So the new foldable is 0.2mm shorter, 0.2mm narrower, and 0.2mm thinner than its predecessor when unfolded. This change has helped Samsung cut its weight by nine grams, down from 263 grams to 254 grams. But that isn’t it.

The dimensions of the Galaxy Z Fold 5 in a folded state will reportedly measure 154.9 x 67.1 x 13.4mm. While the length and breadth are unchanged from the 2022 model, the new hinge makes the upcoming device a lot thinner when folded. We are talking about 0.8-2.4mm thinner than the Galaxy Z Fold 4. Last year’s foldable didn’t fold evenly or gapless, measuring between 14.2-15.8mm in thickness when folded. The new model is just 13.4mm thick.

Despite these changes in dimensions, Samsung is reportedly keeping the screen sizes unchanged from last year. The Galaxy Z Fold 5 will still get a 7.6-inch folding screen on the inside and a 6.2-inch secondary display on the outside. The company has seemingly cut the bezels a bit to make this happen. You won’t notice any difference between the two foldables in mockups shared by Ice Universe, though. We are talking about factions of a millimeter, so this isn’t something immediately noticeable to the naked eye.

Samsung Galaxy Z Fold 4 vs Fold 5 comparison

The Galaxy Z Flip 5 will get a bigger cover display

Samsung may be keeping the cover display unchanged on the Galaxy Z Fold 5, but it’s a different story for the Galaxy Z Flip 5. The clamshell foldable will get a much bigger screen on the outside. It will feature a 3.4-inch squarish panel on the top half of its back. Last year’s model has a 1.9-inch rectangular panel. The Flip model will also get the same waterdrop hinge as the Fold, so it should be thinner and lighter too. You can expect more leaks and rumors about the new Samsung foldables in the coming days. The company is planning to launch the Galaxy Z Fold 5 and Galaxy Z Flip 5 in late July.


[ad_2]
Source link

GhostToken GCP vulnerability allowed hacking of Google accounts

0
[ad_1]

Zero-day flaws are at the top when it comes to online security risks, as they allow hackers to exploit a vulnerability that is unknown to the software vendor. Recently, Google’s Cloud Platform (GCP), a popular data storage and management tool, became the target of one of these exploits, allowing attackers to gain access to people’s Google accounts, including data in Gmail, Drive, Docs, Photos, and more.

Although the Israeli cybersecurity startup Astrix Security discovered and reported the vulnerability back in June 2022, Google is now rolling out a patch to address the issue.

How does the vulnerability work?

Dubbed GhostToken, the vulnerability allowed hackers to make a malicious GCP app of their own and advertise it through the Google marketplace. Therefore, if a user installed the malicious GCP app and authorized it by linking it to an OAuth token, hackers would then gain access to the user’s Google account.

Additionally, to make it impossible for the victims to remove the app, hackers could hide it by deleting the linked GCP project, putting the app in a “pending deletion” state and making it invisible on the Google application management page. To make matters worse, attackers could repeat this process of hiding and restoring the malicious app every time they needed access to the victim’s data.

While the impact of the attack depended on the permissions a victim gave to the app, once the attackers had access to the Google account, they could hold a “ghost” token, which granted them access to the data indefinitely.

Google’s solution

Google’s recent update has finally fixed the vulnerability by making sure that GCP OAuth applications in a “pending deletion” state will now appear on the “Apps with access to your account” page. Therefore, allowing users to remove these applications and prevent any attempts at hijacking their accounts.

Moreover, to help stay protected from future vulnerabilities and exploits, users should also regularly check their app management page to verify that all third-party applications only have the necessary permissions for their intended functions.


[ad_2]
Source link

GhostToken Zero-Day Vulnerability Found In Google Cloud

0
[ad_1]

A severe zero-day vulnerability, identified as the “GhostToken” flaw, could allow an adversary to infect a target Google Cloud with malicious apps. Google patched the flaw before public disclosure.

GhostToken Zero-Day Vulnerability In Google Cloud

As elaborated in a recent post from Astrix Security, the GhostToken zero-day vulnerability could allow infecting the target Google Cloud with malicious apps.

Specifically, the flaw affected the Google account application management page – the option allowing users to review the apps in use. An adversary could connect malicious apps to the account, and hide them permanently from the user. As a result, the respective Google account’s user could never know the presence of the malicious app, inadvertently continuing to use an infected account.

Briefly, the flaw exists due to how an app connects to a Google account via a token. As the researchers explained, an app gains the access token to the respective account right after the Google user installs it from the Google Marketplace.

Regarding how they came across the issue, the researcher stated,

“While running our usual analysis process, a tokens.list API call had returned an odd result – a token of an OAuth application which had its displayText identical to the clientId field.

The researchers found the reason behind the weird displayText field behavior being the deletion of an OAuth application client. They then became curious about what would happen to the access token if they restore the app scheduled for deletion. (Google allows restoring an app scheduled for deletion within 30 days.)

They noticed that the refresh token, created before initiating the deletion, became re-enabled following the restoration. Eventually, they could use this refresh token to get the access token that they could exploit to access the respective Google account.

Hence, they deduced that someone with malicious intentions could easily delete and restore their malicious app to maintain stealthy yet persistent access to the victim’s Google account to steal sensitive data.

Google Patched the Vulnerability

According to the researchers, an adversary could exploit GhostToken vulnerability to access sensitive information from the target account’s Google Drive, Calendar, Photos, Google Docs, Google Maps (location data), and other Google Cloud Platform services.

Upon discovering the flaw, they reported the matter to Google in June 2022. While Google acknowledged the flaw in August 2022, it took them all the while until April 2023 to release a patch.

Still, Google managed to release the fix before the bug could suffer active exploitation. The patch includes showing the OAuth app tokens for apps scheduled for deletion in the users’ app management option.

Though the tech giant has released the fix, Google users must also review their accounts for any unrecognized apps. Also, users should ensure to provide minimal access permissions to third-party apps as a precaution.

Let us know your thoughts in the comments.


[ad_2]
Source link

Black Basta ransomware attacks Yellow Pages Canada

0
[ad_1]

Yellow Pages Canada has suffered a cyberattack by the Black Basta ransomware group.

The Canadian Yellow Pages Group has confirmed it recently became victim of a cyberattack. The Black Basta ransomware group has claimed responsibility for this attack by posting about Yellow Pages on the “Basta News” leak site.

When such a post shows up, it usually means that negotiations with the victim have stopped and that the ransomware group is getting ready to sell the data it managed to get its hands on during the attack.

Based on the most recent leaked information and an outage of the Yellow Pages website Canada 411 at the beginning of April, it is likely the attack occurred between March 15 and April 7. Attackers using Black Basta have been known to be active on a victim’s network for two to three days before running their ransomware.

Canada is ranked first if you look at the number of ransomware attacks divided by GDP.

top 10 countries ransomware attacks per GDPNumber of ransomware attacks per $1T GDP

Black Basta is not very different from other ransomware groups in the way it operates. Similar to others, the gang’s attacks frequently begin with initial access gained through phishing attacks. A typical attack might start with an email containing a malicious document in a zip file. Upon extraction, the document installs the Qakbot banking trojan to create backdoor access and deploy SystemBC, which sets up an encrypted connection to a command and control server. From there, CobaltStrike is installed for network reconnaissance and to distribute additional tools.

As is the overarching trend for ransomware groups these days, Black Basta’s primary goal is to steal data so that it can hold the threat of leaked data over its victims. The data is generally stolen using the command line program Rclone, which filters and copies specific files to a cloud service. After the data is copied, the ransomware encrypts files with the “.basta” extension, erases volume shadow copies, and presents a ransom note named readme.txt on affected devices. Attackers using Black Basta may be active on a victim’s network for two to three days before running their ransomware.

On the leak site, Black Basta provided samples of highly sensitive information about several people. Included are copies of Canadian passports, Quebec and British Columbia driver’s licenses, Régie de l’assurance- maladie du Québec (RAMQ health insurance) cards, and a tax return containing one individual’s social insurance number.

Franco Sciannamblo, YP’s Senior Vice President Chief Financial Officer commented in a statement to BleepingComputer:

“Based on our investigation to date, we have reason to believe that the unauthorized third party stole certain personal information from servers containing YP employee data and limited data relating to our business customers.”

All impacted individuals and the appropriate privacy regulatory authorities have been notified about the attack.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link