YouTube Music sends an ominous notification that forebodes an unwanted change

0
[ad_1]
So, picture this: you are chilling with your smartphone, which is one of the best phones around, because you are just stylish like that. Your phone is new, so you trust that it can stay safe from malware on its own.

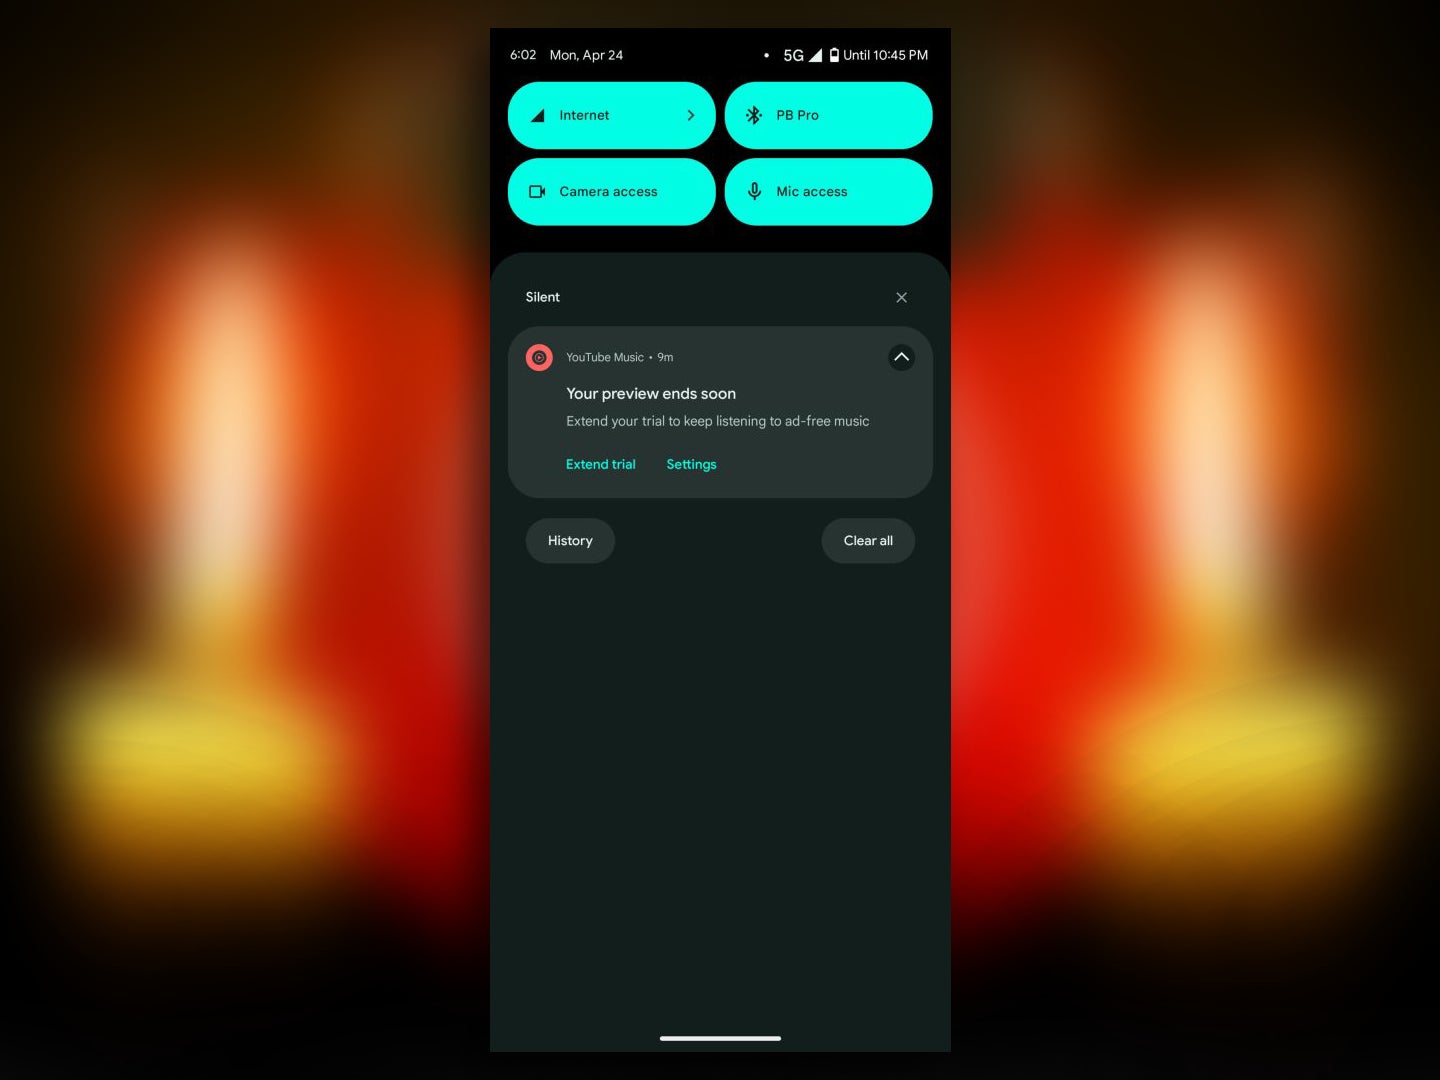
Then suddenly, out of nowhere, YouTube Music — which you’ve got installed on your smartphone — rings you up with a notification, stating:

“Your preview ends soon”

What is a preview? Is your subscription ending early because of some sort of change in recurring payment dates?! Did YouTube Music try to charge you without any valid reason?! How many paid days of service did you lose because of this?

Or did Google make an oopsie and send possibly thousands of users a false notification, alarming them for no reason? Spoilers: Yes. Yes it did. 

As 9to5Google details, Google somehow sent a notification to existing premium YouTube subscribers, both on iOS and Android. Given that the app has more than 80 million active subscribers worldwide, we can only hope that it wasn’t sent out to all of them.When the notification was selected, it led users to the “Get Music Premium” page, which is precisely where users could confirm their subscription status. And in most cases, the page absolutely confirmed that everything was in order. If users select their profile from the top left, they could also verify their billing date too, just in case. And guess what: it was not changed. 

As of now, the Big G hasn’t commented on the situation, but we’re likely to not get any comment at all. This was probably just a minor mishap with a major impact, though little consequence. Or a test for en-masse notifications, which was triggered in a very wrong, yet slightly amusing way.

Either way, after you check and verify that your YouTube Music subscription is properly set up, you shouldn’t have anything else to worry about. Unless your phone is haunted, in which case you should check this guide to see if it’s safe to dip in holy water.


[ad_2]
Source link

CISA Warns Of PaperCut Software Vulnerabilities Under Attack

0
[ad_1]

The print management software firm PaperCut has recently alerted users about two severe vulnerabilities that allow remote attacks. US CISA has also confirmed active exploitation for one of these vulnerabilities.

CISA Alerts About PaperCut MF/NG Vulnerabilities

PaperCut has recently issued an emergency update for its users, rolling out patches for two severe vulnerabilities.

As described in its advisory, PaperCut has disclosed two different vulnerabilities affecting its print management software. Besides elaborating on the flaws, the firm also confirmed active exploitation of one of these vulnerabilities, as alerted by Trend Micro.

Regarding the flaws, the first of these is a remote code execution vulnerability (CVE-2023–27350) that allows an unauthenticated remote attacker to target PaperCut Application Server. The flaw received a critical severity rating with a CVSS score of 9.8. PaperCut hasn’t disclosed more details about this vulnerability as it confirmed its active exploitation based on the reports from Trend Micro.

The second issue (CVE-2023–27351) also allows remote attacks from an unauthenticated adversary to steal sensitive information stored in PaperCut MF or NG. That includes usernames, email addresses, full names, card numbers, and department or office details of the users. This vulnerability received a high-severity rating with a CVSS score of 8.2. Thankfully, the bug received a patch before exploitation.

Following this emergency disclosure, the cybersecurity firm also shared a detailed analysis of the attacks exploiting the RCE flaw.

According to their report, the attacks seemingly target around 1800 vulnerable PaperCut servers, which the attackers abuse to spawn RMM tools like Atero and Syncro on the target devices for persistent access. They have also shared a PoC for the flaw.

While the exact identity of the threat actors exploiting this vulnerability remains veiled, Huntress researchers suspect Russian threat actors behind it. Briefly, while not directly linked, they somehow find Truebot malware related to this activity, which eventually leads back to the Cl0p ransomware and Silence entities.

CISA Also Alerts About PaperCut Flaws

The US CISA has also added the under-attack vulnerability CVE-2023–27350 to its list of actively exploited bugs.

PaperCut has released the patches for both vulnerabilities in the MF and NG software with versions 20.1.7, 21.2.11, and 22.0.9, respectively.

While the firm urges deploying the updates, it also advised some precautionary measures for the systems where an immediate update is not possible. These mitigations include blocking inbound traffic from external IPs to the web management ports 9191 and 9192, blocking all incoming traffic to the web management portal on the firewall to the server to prevent lateral movement of potential attackers, and applying an allow list.

Let us know your thoughts in the comments.


[ad_2]
Source link

iOS Lockdown Mode effective against NSO zero-click exploit

0
[ad_1]

Apple’s Lockdown Mode has shown that it can do what it was designed to do by notifying users about an NSO exploit.

Apple’s Lockdown Mode feature alerted a victim to one of the latest NSO exploits, according to a report by Citizen Lab.

Lockdown Mode notification related to the PWNYOURHOME exploitimage courtesy of Citizen Lab

This is a huge deal since it shows how useful Lockdown Mode can be, even against exploits developed by one of the world’s most notorious commercial spyware producers.

Pegasus spyware, developed by NSO Group, has featured in many news stories, after being found to have been used against journalists, politicians, State Department employees, embassy workers, and activists.

We talked about Pegasus infections in our podcast Lock and Code, which can be listened to in full here:

As Pegasus has become publicly scrutinized, NSO Group has expanded its product line. Citizen Lab found several new zero-click chains that it was able to tie to the NSO group with high confidence.

The report describes three of them in detail:

  • PWNYOURHOME: An iOS 15 and iOS 16 zero-click exploit which involves the HomeKit functionality built into iPhones and works even if the victim has never configured a “Home” inside HomeKit.
  • FINDMYPWN: An iOS 15 zero-day, zero-click exploit which is associated with the iPhone’s built-in Find My functionality.
  • LATENTIMAGE: An iOS 15 zero-click exploit which is also believed to use the iPhone’s Find My feature.

The use of multiple attack surfaces can be handled in two very different ways. You can play a game of whack a mole and patch the vulnerabilities as they get uncovered, which is certainly necessary and common practice, but it has the disadvantage of being responsive rather than preventive. And the report also stipulates that NSO is getting better at hiding itself and its traces on infected devices, which makes it harder to find and analyze the exploits they used.

The other way of minimizing the risk of exploits is to build with security in mind. Think of design decisions like memory safe programming languages, and sandboxing applications so a vulnerability in one does not lead to a compromised device and stays limited to the app. But also features like Apple’s Lockdown Mode which puts an iPhone into a state where it is more difficult to attack.

Lockdown Mode is available for iOS 16, iPadOS 16 and macOS Ventura. It is designed to provide a safer environment for users that are at a higher risk.

You could say it was introduced with Pegasus in mind. And although Apple refers to Lockdown Mode as “an extreme, optional protection,” the limitations don’t actually sound particularly difficult to live with.

  • Messages: Most message attachment types other than images are blocked and some features, like link previews, are unavailable.
  • Web browsing: Certain complex web technologies, like just-in-time (JIT) JavaScript compilation, are disabled unless the user excludes a trusted site from Lockdown Mode.
  • Apple services: Incoming invitations and service requests, including FaceTime calls, are blocked if the user has not previously sent the initiator a call or request.
  • Wired connections with a computer or accessory are blocked when iPhone is locked.

Configuration profiles cannot be installed, and the device cannot enroll into mobile device management (MDM), while Lockdown Mode is turned on. A device that was enrolled in Mobile Device Management before Lockdown Mode is enabled remains managed. System administrators can install and remove configuration profiles on that device.

Even though it’s very good news that Lockdown Mode proved it was able to notify a target about an ongoing attack, there are some caveats. The Citizen Lab report also mentions that NSO may have figured out a way to correct the notification issue, since Citizen Lab has had no new reports about it. NSO could have done this, for example, by fingerprinting Lockdown Mode. And since Lockdown Mode is not available for iOS 15 it only provides protection against the PWNYOURHOME exploit. The others didn’t work on iOS 16 anyway.

Enabling Lockdown mode

So, how do you turn on Lockdown Mode? If you consider yourself a target for commercial spyware or are willing to live with some minor inconveniences for a higher level of security, here’s what you can do.

How to enable Lockdown Mode on iPhone or iPad:

  • Open the Settings app
  • Tap Privacy & Security
  • Under Security, tap Lockdown Mode and tap Turn On Lockdown Mode
  • Tap Turn On Lockdown Mode
  • Tap Turn On & Restart, then enter your device passcode.

And you’re all set. If you feel that the limitations are a bit too strict for your convenience, don’t turn it off immediately because there are ways to exclude apps or websites from Lockdown Mode. While your device is in Lockdown Mode, you can exclude an app or website in Safari from being impacted and limited. Exclude only trusted apps or websites and only if necessary.

To exclude a website while browsing: Tap the Page Settings button , then tap Website Settings. Then turn off Lockdown Mode.

To exclude an app or edit your excluded websites:

  • Open the Settings app
  • Tap Privacy & Security
  • Under Security, tap Lockdown Mode
  • Tap Configure Web Browsing
  • Exclude websites or apps from Lockdown Mode on iPhone

To exclude an app, turn that app off in the menu. Only apps that you have opened since enabling Lockdown Mode and which have limited functionality appear on this list.

To edit your excluded websites, tap Excluded Safari Websites > Edit.


We don’t just report on iOS security—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your iOS devices by downloading Malwarebytes for iOS today.
[ad_2]
Source link

Only base Galaxy S24 could ship with the Exynos 2400 SoC

0
[ad_1]

There are contradicting reports about the return of Samsung‘s Exynos chips to its Galaxy S series flagships. Some say next year’s Galaxy S24 lineup will ship with the Exynos 2400 processor in some markets, while others say the company will equip its next-gen flagships with a Snapdragon chipset globally. A new rumor passed along on Twitter has now given a fresh twist to this saga. According to tipster @RGcloudS, only the base Galaxy S24 may come with an Exynos chip.

The tipster isn’t 100 percent sure about this information, but an industry source has told them that Samsung could ship the smaller Galaxy S24 model with the Exynos 2400 processor in select markets. In other areas, it will use the Snapdragon 8 Gen 3 for Galaxy, which would be a Samsung-exclusive overclocked version of Qualcomm’s next-gen flagship processor. This year’s Galaxy S23 series uses a similar overclocked version of the Snapdragon 8 Gen 2.

The Galaxy S24+ and Galaxy S24 Ultra, meanwhile, will use the new Snapdragon processor globally. The idea is to show the world that Samsung has fixed the Exynos issues. By only using the Exynos 2400 on the base Galaxy S24, the company isn’t risking the sales of its next-gen Ultra flagship, which usually attracts more crowd. At the same time, it will also be able to give a demo of its improved chip fabrication process. Samsung may also make the base model cheaper to drive sales.

An Exynos-powered Galaxy S24 may be a tough sell

In a welcome change, Samsung shipped the Galaxy S23 series with a Snapdragon processor globally this year. This change was appreciated by fans and experts alike, as Exynos processors that the company used in its flagships in some markets in the past have always had performance and power efficiency issues. The 2023 models brought a massive leap in battery life and everyday performance over their respective predecessors.

Considering this, it seems a no-brainer for Samsung to stick to this Snapdragon exclusivity for the Galaxy S24 series. However, the company has other ideas. It doesn’t want to spend more money on purchasing Qualcomm processors while its semiconductor division that makes Exynos chips suffer from declining demand. The Korean firm is now mulling going back to Exynos next year, even if that means taking a hit to sales of the base Galaxy S24 model.

That said, early rumors about the Exynos 2400 have been promising. Samsung is expected to offer a ten-core CPU setup and a much-improved GPU based on AMD’s RDNA2 technology. Hopefully, the company has left behind all the Exynos woes and will start afresh with the Exynos 2400. It eventually plans to make custom processors for Galaxy flagships. But ahead of that, Samsung needs to regain the reputation it lost over the years by offering underperforming Exynos chips.


[ad_2]
Source link

iPhone 15 Pro Max may not get new main camera sensor after all

0
[ad_1]

We’ve been seeing a ton of conflicting rumors regarding the upcoming iPhones thus far. Yesterday, a rumor claimed that the iPhone 15 Pro Max will feature a brand new main camera sensor (Sony’s IMX903 sensor), but a new rumor claims that it won’t.

The iPhone 15 Pro Max may not get a new main camera sensor after all

To bring you some perspective. Yesterday’s information got shared by Ice Universe, a well-known tipster. He specifically mentioned the iPhone 15 Pro Max, not the regular ‘Pro’ model, though he did not elaborate on that.

Now, a different tipster. Revegnus, claims that the iPhone 15 Pro Max will not have a new main camera sensor. He says that the phone will stick with the same main camera the iPhone 14 Pro series uses, the Sony IMX803.

Revegnus made things even more confusing in the comments

He claims that the Sony IM903 is in Apple’s plans, but for the iPhone 16 Pro. He probably meant the iPhone 16 Pro series, so both models. What’s even more confusing is his comment. One of his followers wrote “Ice says 15PM uses imx 903?”, and Revegnus simply said “yes”, without giving out an explanation.

Is it possible he made a mistake in his original tweet, and wanted to write ‘iPhone 15 Pro’ instead of ‘iPhone 15 Pro Max’? Or perhaps he just acknowledged that Ice Universe has the wrong info by saying “yes” in the comments? It’s anyone’s guess.

It has been almost a day at this point, since Revegnus tweeted out the rumor, and shared his comment. He did not ping back to elaborate on what he wanted to say, so… yes, it’s quite confusing at this point.

iPhone-related rumors are all over the place

First, we had the saga with the iPhone SE 4, then the saga with the iPhone 15 Pro series’ solid-state buttons, and now this. Either Apple is pushing out fake info to confuse tipsters, or some of them have really poor sources.

We’ll get more info regarding this moving forward, while all iPhone 15 models are expected to launch in September.


[ad_2]
Source link

Snapchat uses ChatGPT to haul a million new premium subscribers

0
[ad_1]

It’s the era of artificial intelligence! After ChatGPT made headlines with its powers to write, draw and code, other companies started to integrate the powerful AI into their services. (By the way, check out our poll: “Do you think AI language models (ChatGPT, Bard) are the future of information search?” and see how we’re doomed).Back to the news story! Snapchat reported on its annual partner summit, held in its hometown of Santa Monica, California (story featured in Time), that the Snapchat+ premium service grew by 3 million users in the past year.

The most interesting part is that 1 million of these premium users (paying $3,99 monthly) came in the past 11 weeks, right after Snapchat+ integrated My AI, an artificial intelligence model powered by ChatGPT.

“What we essentially see is that when we release new features, that gets more people excited about signing up or trying Snapchat+. We definitely saw some nice momentum with My AI,” said Snap Chief Executive Officer Evan Spiegel.

Snapchat will soon be opening the My AI feature to all users, according to what the company said last Wednesday. Which is a bold move, given the extra money that My AI has generated since its debut in Snapchat+.

My AI can do most of the things ChatGPT can, including writing content, answering questions, and leading basic conversations.

Also Read:


[ad_2]
Source link

Microsoft Changed the Taxonomy of Naming the Hacker groups

0
[ad_1]
Microsoft Taxonomy

Microsoft has initiated the naming taxonomy for threat actor groups. Over the years, threat actors have evolved massively, leading to confusion about which threat actor was responsible for which threat activity.

To solve this, Microsoft has introduced this naming taxonomy and categorized them based on their origin and activity.

Though threat intelligence has emerged massively, it must still be an organized data resource that can help protect and prioritize based on the hacking groups confronted.

Weather-based Hacking group name taxonomy

Microsoft has relied on weather condition names for naming these hacking groups as this can be easy to remember and spread the word.

Categorization

Microsoft has categorized threat actors into five main groups based on their operations.

  1. Nation-state – These threat actors work on behalf of or are directly supported by a nation/state. They specifically target government agencies, intergovernmental organizations, espionage, financial gain, or as an act of retribution.
  2. Financially Motivated – These threat actors target an organization or an individual as a part of a financial motive. These threat actors/ groups did not seem to be linked with nation-state actors. The best examples of these threat actors are ransomware operators, phishing groups, or other groups with purely money-minded activities.
  3. Private Sector Offensive actors (PSOAs): These are threat actors who were once known as legal organizations but later seemed to have been involved in activities like creating malware, selling weapons and surveillance software to cyber criminals who use them for illegal purposes, or targeting any white-collar individuals. The best example of this kind of threat actor was the QuaDream company which was shut down recently for its malicious activities.
  4. Influence Operations: These are the threat actors that spread misinformation among people to disrupt or manipulate people’s interests. This kind of threat actor is also involved in political manipulations for malicious purposes.
  5. Groups in Development: This category set by Microsoft includes threat actors whose origin and way of operations are yet to be confirmed. In other words, these include threat actors still in developmental phases and involved in small-scale malicious attacks.

Microsoft has also released complete information on their new weather name taxonomy, including the family name, their origin or country of operation, and their category.

Building Your Malware Defense Strategy – Download Free E-Book


[ad_2]
Source link

A week in security (April 17

0
[ad_1]

The most interesting security related news from the week of April 17 – 23.

Last week on Malwarebytes Labs:


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

You’re stuck with Snapchat My AI if you don’t pay up

0
[ad_1]

Snapchat recently made its AI chatbot, My AI, available to the public, and people are definitely using it. However, if you want to unpin My AI, then you’ll need to pay for it.

If you’re unfamiliar with My AI, this is the AI chatbot powered by ChatGPT, and it’s integrated right into the app. You’ll know you have it if you see a new chat conversation in your feed. If you see it, then you can start talking to it immediately.

It’s a chatbot, so you’re able to talk to it about just about anything and get a human-like response. Since it’s powered by ChatGPT, you can also use it to generate written content. There’s a lot that you can do with My AI.

You can’t unpin My AI unless you pay

This is rather ironic considering that My AI started as a Snapchat+ exclusive feature. This exclusivity netted the subscription service a million more users over the past 11 weeks.

Now that it’s available, non-paying users can use it, but the conversation is automatically pinned to the top of your chat feed. There are people who don’t like that. Some don’t want an extra chat cluttering up the feed, and others just don’t want anything to do with AI.

Well, we have bad news for those people. According to 9to5mac, if you want to unpin My AI, you need to be a Snapchat+ user. That’s right, the subscription that exclusively offered My AI is required to get rid of it.

This might not seem like the biggest issue for the company, but it means some trouble for the app itself. The report states that this prompted users to flood the Snapchat app in the Apple App Store with 1-star reviews.

It seems that Snapchat is aggressive about pushing AI on its users. AI is the next major frontier in tech, and many companies are making a pivot toward it. It’s just unfortunate that people are forced to see My AI when they don’t want to.


[ad_2]
Source link

According to some Google employees, Bard AI chatbot is just a charade

0
[ad_1]

The artificial intelligence battle led to the birth of Google’s Bard AI chatbot, a rival to the Bing ChatGPT chatbot. But some employees at Google don’t think much of Bard like their employers want you to, it seems. What exactly can be the reason behind the rejection Bard is getting from its people?

Well, many might argue that the reports only cite a trifling sum of Google workers. Some people making up this list of those kicking against Bard are ex-Google staff. But regardless of the size of the opposition, it is a wise course to take into account the reason for their aversion.

It boils down to the abilities of the Bard AI chatbot when put to use by people. The outlined issues are also the case with Bard’s greatest rival, the Bing AI chatbot. Funny enough, the staff at Google have labelled this AI platform as “worse than useless”. This sounds a bit too harsh coming from Googlers, hence drawing more attention to Bard’s performance.

The misleading responses of Google’s Bard AI chatbot put it under intense scrutiny from its makers

Over the past few months, Microsoft has made the headlines as a result of its integration of ChatGPT into its browser. This brought the AI chatbot into Bing and Skype, but users have been able to spot some flaws. These flaws come as a result of the Bing AI chatbot not knowing the limits of a conversation, threatening users, and falsifying information.

Shortly after Microsoft announced the integration of ChatGPT into Bing, Google was already preparing to announce the Bard AI chatbot. Well, it seems like Google employees are pointing out noticeable flaws in the AI chatbot, following its arrival.

These flaws are quite similar to those that came to the spotlight with the ChatGPT chatbot. Bard now provides false information to users and gives dangerous advice, hence threatening user safety. Google’s rush might be the main cause of these issues that their employees are pointing out in Bard’s usage.

Reports have it that the internal safety team had advised that the chatbot not be launched. Instead, these flaws be fixed to foster the launch of a more stable and user-friendly product. Now, Google will have to focus on fixing these issues to ensure that those making use of this product will be able to get safe and accurate responses for their searches.

Just like Microsoft’s Bing AI chatbot, Bard comes with some flaws. Many might argue that it is normal for any new AI product, but such issues are pushing certain countries to ban AI chatbots. The AI chatbot industry needs to undergo refining before it can sit with the majority as being safe for usage.


[ad_2]
Source link