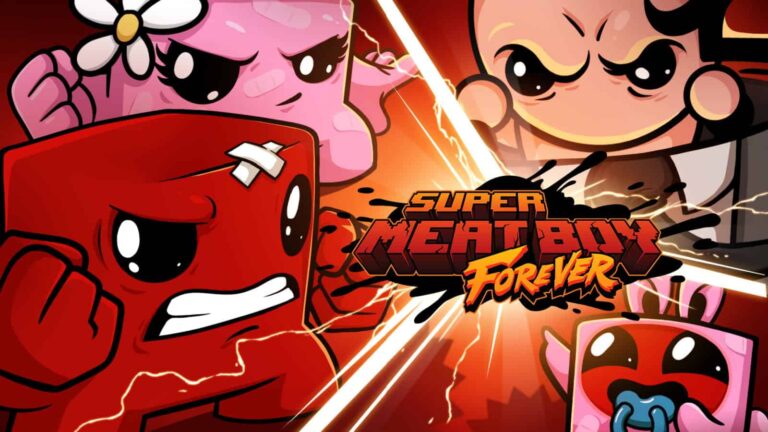
Do you remember Super Meat Boy, the game for Xbox 360 that came out what feels like forever ago? If you don’t, it was a tough as nails game that ground you down till there was potentially nothing left of your sanity. Initially it released on the Xbox 360 back in 2010, and it then later came to PS4, PS Vita, Wii U, Windows, Linux, Mac, and eventually Nintendo Switch.
Even if you never played it with its original release, chances are you may have seen or experienced in some form. Now Super Meat Boy is back to test your patience in Super Meat Boy Forever, the mobile adaption to this popular platformer. And it can be yours for only $0.99.
The game released on April 20 on both Android and iOS, and is a direct successor to the original Super Meat Boy, taking place a few years after those events.
Super Meat Boy Forever changes up the formula
While the challenge is still there, you might notice some things that are different about this game from the original. For instance, the original Super Meat Boy allowed players to control the movement of the character entirely. In this new game, controls are somewhat automated. Specifically the movement.
Meat Boy will now move automatically. But you can still control other things like jumping and attacks. It’s a slight twist but overall still a ton of fun if you like platforming games with a steep challenge. The game should provide hours up hours of fun. As the developers say it contains “thousands of level chunks that can be combined in endless ways.”
Levels are also randomly composed so no two playthrough should really ever feel the same. For $0.99, this is a proper steal considering the level of quality gamers are getting. You can pick it up right now on Google Play, and you can check out the trailer above.
YouTube TV is getting a pretty big update, at least for the Apple TV. Which has seen quite a few problems for YouTube TV in recent months. According to a post from a YouTube Community Manager on r/YouTubeTV, the update is v1.13+ and it’s available now. This update includes fixes for the app opening up to a black screen, enabling YouTube TV’s HDR implementation and also addressing 4K playback issues.
Now that’s not all that’s new with YouTube TV. It has also announced that it has found the cause for 5.1 audio and video sync being off. And they are testing out a fix for it now.
Of course, the post also talks about NFL Sunday Ticket, and says that you can still sign up for it now and save $100 on the first year. You can do this by going to your Memberships page and signing up.
Picture quality improvements
Another big emphasis here is that the team is experimenting with picture quality improvements. It’s testing some transcoding changes, and that includes a bitrate increase for live 1080p content, over the next few weeks. This is going to target devices that support the VP9 codec, and high-speed internet connections. The team plans to roll this out by the summer, if all goes well.
Finally, YouTube TV has said that they are continuing to make changes to Multiview, which rolled out in time for March Madness. It is planning to make some more improvements ahead of the NFL Season. Though it did not give any specifics about what changes Multiview might receive.
So, there’s some pretty big updates for YouTube TV, as well as some changes. Making that price increase to $72.99 per month almost worth it. While many complain about the price increases, YouTube TV does still have the best platform for streaming live TV right now.
YouTube TV has announced via a post on their official Reddit account that it has made some updates to improve picture quality on its apps. The updates have been implemented in response to complaints from users about the streaming quality of YouTube TV and some major bugs specifically on the Apple TV platform.
Apple TV Fixes
On the Apple TV, a major update (version 1.13+) is coming which will address difficulties with the app opening up to a dark screen, will allow HDR implementation, and fix some bugs with 4k playback. Not addressed with this app version, but available in the app store very soon, will be a solution to the issue in which the application would crash on the first-generation 4K Apple TV when it is left on.
Lastly, the team offered an immediately solution for users experiencing a momentary black screen when switching between content, explaining that this is happening because of the SDR/HDR transitioning that is taking place. The fix involves either setting SDR as content as your default format or disabling range matching altogether, both of which you can change from the Settings > Video and Audio menu.
Aside from the major fixes for Apple TV, the team also announced some new features that will impact all platforms where YouTube TV runs, including mobile.
Improvements everywhere else
YouTube TV successfully implemented “Multiview” to all its subscribers in response to the fervent demand during March Madness. Now, the company is working on further enhancements to the feature in order to ensure a seamless experience once the NFL season rolls around. No specific updates were shared in the blog post about what type of enhancements we will see, but as the Football season draws near, we can expect to receive more details soon.
Since we are on the subject of Football and the NFL, YouTube TV added that its users can now access NFL Sunday Ticket by navigating to the “Memberships” page in their settings. Alternatively, they can head to the “Movies & TV” section on YouTube to sign up for the service or explore the various plans that are currently available. For a limited time, interested parties can sign up for a full season package at a discounted price until June 6th.
YouTube TV is also addressing the issue of picture quality on their streams by conducting a series of tests on transcoding modifications in the next few weeks. The tests will involve a boost in bitrate for live 1080p content on all devices that are compatible with the VP9 codec and that benefit from fast internet connectivity. Assuming a successful outcome of these tests, the intention is to make this a permanent fixture by the upcoming summer season.
In its announcement, the YouTube TV team also claimed to have identified the root cause of the audio/video synchronization problems that have been plaguing the app lately and which occur when the surround sound feature is enabled. Now that they’ve done their research on this, the team states that it is now actively working on a solution and will be conducting tests in the near future.
These updates are part of YouTube TV’s ongoing efforts to improve the service and make it more competitive with other live TV streaming services, such as Hulu with Live TV, Sling TV, and PlayStation Vue. Recent significant price increases and the loss of several regional sports channels have caused many subscribers to drop the service and look for solutions elsewhere, so YouTube TV could definitely use a boost in subscriptions at this time and introducing new features along with fixing ongoing issues is not a bad way to go about it.
Researchers have recently found that the ICICI Bank systems misconfiguration caused data leakage, exposing more than 3.6 million customers’ sensitive data.
ICICI Bank, a multinational Indian bank, operates in 15+ countries worldwide and boasts a market value exceeding $76 billion with 5,000+ branches across India.
The Indian government declared ICICI Bank’s resources as “critical information infrastructure” in 2022, signifying that any harm may have severe implications on national security.
Data Leak
Threat actors target financial services and organizations more frequently than other sectors. And in this case, if they managed to gain complete access to the leaked data, it could damage both the bank and its customers.
ICICI Bank’s sensitive data and its clients’ information were exposed when the Cybernews research team found a misconfigured and publicly accessible Digital Ocean bucket with over 3.6 million files on February 1.
Here below, we have mentioned the types of data leaked:-
Bank account details
Credit card numbers
Full names
Dates of birth
Home addresses
Phone numbers
Emails
In addition to leaking bank statements and filled-in KYC forms, the bucket exposed clients’ passports, IDs, and Indian PANs (taxpayer identification numbers).
In the storage, CVs of current employees of the bank, as well as job applicants, were found. This is another indication that the leak also affected staff at the bank.
The impact of the leak is expected to be severe due to the massive amount of personal data is leaked, which can potentially damage:-
Reputation of the bank
Expose internal processes of the bank
Compromise the safety and security of clients’ sensitive data
Compromise the safety and security of employees’ sensitive data
According to the report, Leaked data could enable threat actors to engage in identity theft and fraud, such as creating accounts in individuals’ names without their knowledge using stolen credentials and personal information.
Not only that, even as a result, spear phishing campaigns may target employees, businesses, and individuals whose data has been exposed, putting them at risk.
Alert : Many Users Are Receiving This Type Of SMS Or E-mail From ICICI Bank As A Precautionary Measure.
AFAIU, They Are Aware Of Such Data Leak By Merchant Where We’ve Transacted Before.
Also, selling data on the dark web is a potential risk, and ICICI Bank could also become a target of ransomware attacks.
Company’s Response
After identifying the issue, the security researchers immediately contacted the following entities in an attempt to report this loophole:-
ICICI Bank
Indian Computer Emergency Response Team (CERT-IN)
As soon as they reported the issue to ICICI Bank, they acted immediately, and on March 30, they restricted all public access to their Digital Ocean bucket.
When security experts at Cybernews tried to get an official comment from the communication team of the ICICI Bank, they received the following reply via email from the bank:-
“Thanks for your email. With regards to it, we do not know which incident you are referring to.”
Later when they tried to establish their communication with the bank’s Corporate Communications Team, they rejected the email sent by a Cybernews journalist.
Recommendations
Here below, we have mentioned all the recommendations that the security analysts provide:-
It is recommended that cloud storage buckets be secured as much as possible to prevent such data leaks.
ICICI Bank must notify its customers of the data leak so they can minimize the risk and further damage that may occur.
Bank should directly guide all its users to report any suspicious activity immediately to ICICI Bank to identify and avoid fraudulent emails, websites, and calls.
Passwords must be changed, and vital login details should be created for those affected.
Make sure to enable 2-Factor authentication.
Follow us on LinkedIn & Twitter for Daily Cyber Security News Updates.
T-Mobile has cemented itself as a pretty competitive carrier in the past decade. Offering plans that are cheaper than the competition, and in a lot of ways better. But even T-Mobile doesn’t just have a single plan, it has multiple plans that you can choose from. Each of which are great in their own right.
However, which one is going to be the best for you, and how you use your phone, and your lifestyle? That’s what we are here to determine. In this article, you’ll learn the best postpaid plan, the best plan for those do a lot of traveling, the best prepaid plan and the best MVNO that you can choose to use T-Mobile’s network.
Postpaid vs Prepaid vs MVNO
Before we get started, it’s important to talk about the differences between Postpaid, Prepaid and MVNO. Postpaid are customers that pay for their service after they have received it. That means your final bill will be larger than your first bill. Prepaid essentially means that you pay for your service before you receive it. And MVNO stands for Mobile Virtual Network Operator, they essentially buy access to T-Mobile’s network at wholesale rates. Which is why it can be a lot cheaper than getting a postpaid plan.
When it comes to coverage, all three will offer the same coverage, if they are on the same network. The difference here is going to be in busy areas. On a network tower, Postpaid customers get priority, followed by prepaid customers. MVNO customers are at the very bottom, however a T-Mobile-owned MVNO may be a bit higher than other MVNO’s, as it’s still a T-Mobile company. Metro by T-Mobile is one that is owned by T-Mobile.
Smartphone selection is another difference here. While postpaid customers get access to almost all smartphones that are available, prepaid and MVNO’s have far fewer options for customers. They also usually do not offer any financing, so you’d need to go through a third-party, like Samsung (and buy unlocked).
Now that you know the difference between postpaid, prepaid and MVNO, let’s get started.
Best overall T-Mobile Plan: Go5G
Starting April 23, 2023, T-Mobile’s plans will move to the Go5G and Go5G Plus plans, with the Magenta and Magenta Max plans being online exclusives. However, the Go5G plans are a better value. So we have updated this post accordingly.
Go5G was announced on April 20, 2023, and while it is priced higher than the Magenta plan, it does include more. So this plan will be priced at $75 per month for a single line, $55 per line per month for two lines, $25 for three lines and four lines. These prices also include taxes and fees, which is really nice to see.
When it comes to data, Go5G does include 100GB of premium data. Which basically means that after you hit that 100GB of data, your data will likely be slowed. It also includes 15GB of high-speed data for the hotspot, and unlimited at 600Kbps. You’ll also get unlimited talk and text in Mexico and Canada and 10GB of high-speed data.
Now when it comes to the perks, you will get Netflix Basic on all family plans. As well as Apple TV+ for six months. Finally, for traveling, you’ll get 4 full-flight streaming sessions a year, and then unlimited 1 hour streaming and unlimited in-flight texting.
Go5G Plus is the best plan from T-Mobile for travelers, because it offers unlimited premium data, as well as more in-flight data. But let’s talk about pricing first. This one is going to cost you $90 for a single line. $60 per line for two lines, and $35 per line for three and four lines.
With Go5G Plus, you get unlimited premium data, that means you will never be slowed down, which is huge. When it comes to the mobile hotspot, you’re going to get 50GB of high-speed data, and then unlimited 600Kbps. In Mexico and Canada, you get unlimited talk and text, plus 15GB of high-speed data. And for other countries, you’ll get up to 5GB of high-speed data and unlimited text in 215 countries.
Now onto the perks. With Go5G Plus, you will get Netflix Basic on all single lines, or Netflix Standard on family plans. You also get Apple TV+ included. For flights, you will get full-flight texting and WiFi with streaming, where available.
Best T-Mobile Prepaid Plan: T-Mobile Connect 2.5GB
T-Mobile’s prepaid plans are super simple, and start at just $15, which is the plan we chose as their best prepaid plan. T-Mobile Connect 2.5GB will cost you $15 per month.
This plan is super simple, no real gotchas, or perks here. You get unlimited talk, text and data. With 2.5GB of high-speed data and then throttled afterwards. If you don’t use much data, are at home all the time, then this plan is going to be perfect.
T-Mobile Connect also has a 5.5GB plan for $25 per month.
For the best T-Mobile MVNO, what better than Metro by T-Mobile (formerly MetroPCS) which is of course owned by T-Mobile.
Metro by T-Mobile has plans that are as low as $30/month offering you unlimited talk, text and data, with 5GB of high-speed data.
You can get unlimited high-speed data from Metro by going with its $50 plan. That also gives you 15GB of hotspot data, and 100GB Google One Membership. It’s $60 plan gives you all that, plus Amazon Prime is included in the price.
We are still finding out the full potential of generative AI and how it could help people. As you know, Google has its own AI chatbot that you’re able to try out now. This chatbot, named Bard, can do a lot of stuff, as Google gave it the ability to debug code.
When we found out that ChatGPT could write actual code, we were all dumbfounded. Well, Google Bard can also do that, but the company is looking to crank that capability up to 11. According to a blog post released today, Google Bard will offer several services that will help you write code.
This approach is meant to be much more substantial than what we see with ChatGPT. Yes, Bard can generate code for you, but it’s focusing more on helping learn and grow as programmers so that they won’t need AI in the future.
Google will help you in more than 20 programming languages including C++, Python, Java, Javascript, Go, and Typescript. This means that the code you’re learning is pretty much covered.
So, as stated, Bard can generate code for you. Just ask it what you want it to generate and you’ll get a response. You can also paste in your own code and ask it to make alterations. What’s neat is that you can easily export the generated code to your Google Colab.
This feature comes in handy when you want it to debug code for you. If you’re writing code, and you want to check it for errors. That’s a handy tool if you’re looking to double-check your work.
Google still wants to teach you
The most notable thing about this update is that Bard will actually teach you about the code you’re working on. It will explain why the code works or doesn’t work rather than just writing it out for you. This gives you the ability to learn about coding.
This is crucial, as it can be tempting for people with no coding background to rely on AI to generate code for them. However, without knowing the fundamentals of programming and just typing in requests, a person could have a much harder time making a proper and stable app.
Google updated Bard with this capability today, so you can access it now.
So, in case you aren’t quite up to speed with the happenings in the world of AI — it is now more than just a thing. Is it just a fad though? Well, considering that we’re likely to see it powering features on some of the best phones to come out in 2023… Probably not.
But that is because AI can do loads more than just act as a “shortcut” for your Google search or next university assignment. It can generate music, write software code, create visual arts and even play RPG games with you. And ChatGPT specifically is really good at that last one!
While the technology itself is impressive, it is what users do with the results that will come to define how the public views it. And, unfortunately, we’ve got loads of negative examples.
This latest one is about a song, which sounds like a legitimate collaboration by RNB stars Drake and The Weeknd. The track is called “Heart On My Sleeve” and until recently, you could find it on all of the major music streaming platforms. Without proper credit.
Apple led the charge against the song by allegedly removing from their platform first.
But how does one credit something like that anyway? The AI created it, but it can’t bear the fruits of its labor, for it does not need them. The user who prompted it exerted some form of creativity, but that is based on what the AI model knows about the performers. And as for the musicians themselves… Well, they didn’t play a direct role in the equation. The song went viral and its creator, going by @ghostwriter, got approximately 629,439 streams from it on Spotify alone. The platform’s lowest rate is about $0.003 per stream, so that amounts to somewhere around $1,888. But the song was also on all other major streaming platforms.
BBC released a report which highlights the comments of Universal Music — publisher of the aforementioned artists — which, to no one’s surprise, is claiming that this is a form of copyright violation. The publisher stated that AI platforms have a “legal and ethical responsibility” to combat this sort of usage.
Apple led the string of takedowns, removing it from its Apple Music streaming service. Deezer, Tidal, TikTok, Spotify and YouTube followed suit closely after, but the source quotes that the song can still be found online.
Copyright specialists from the UK have commented that the current legislation is nowhere near prepared for this sort of shenanigans. This means that songs like this could potentially be seen as completely original by the law, depending on how deep the deepfake is.
But as we can see from the example here, publishers aren’t ready to take this sitting down. AI was sure to have a huge impact on all of our lives, but who would’ve thought that it would extend to a necessity to change copyright laws, huh?
Days after the horrifying cyberattack, more details about the 3CX incident surface online as Mandiant discloses its investigations. As revealed, the cyber attack on 3CX systems linked back to another supply-chain attack on a separate firm.
3CX Cyber Attack Update: Mandiant Shares Its Investigations
After investigating the matter for weeks, the cybersecurity firm Mandiant has shared insights about what happened with 3CX.
As revealed in its post, its team could trace back the 3CX cyberattack’s link with another supply-chain attack that affected Trading Technologies Inc.
While the researchers have shared the detailed technical analysis of the malware, the incident timelines, and the attack flow in their post, here’s a quick review.
Specifically, 3CX caught the malware from a trojanized version of Trading Technologies’ software installer X_TRADER. Analyzing the malicious software made Mandiant discover the embedded VEILEDSIGNAL backdoor that executed the attack.
The modular backdoor executed the attack in steps, downloading malicious DLLs and other payloads. Alongside this backdoor, two other modules added to its functionality by providing C2 injection in the process and listening Windows communication.
The malware infiltrated the 3CX network through this Trading Technologies app, after which, the attackers spread laterally on the 3CX network. During this process, the attackers kept harvesting credentials and compromised Windows and macOS systems alike, deploying malicious DLLs and backdoors.
Tracing back this UNC4736 malware activity led the researchers to deduce a North Korean threat actor behind the attack.
Earlier this month, 3CX admitted suffering a terrible cyberattack on its network that also affected its customers. It turned out that the attackers exploited the firm’s app to roll out malicious updates to the customers.
At that time, 3CX confirmed hiring Mandiant for investigating the cyber attack, and now, the security firm has shared the update.
While 3CX became a potent indicator of Trading Technologies’ supply-chain attack, the researchers suspect that there may be some other victim firms. But they may or may not have noticed and reported the compromise on their networks yet.
A joint advisory about a Cisco vulnerability by several US and UK agencies gives us a peek inside the minds of ideologically motivated cybercriminals
In a joint advisory, the UK National Cyber Security Centre (NCSC), the National Security Agency (NSA), the Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) have released information about APT28’s exploitation of Cisco routers in 2021.
Now please don’t stop reading because you think this is old news. If you think 2021 is long ago, maybe you will be surprised to learn that the vulnerability used in these attacks was actually discovered in 2017.
Cisco published workarounds and updates for this vulnerability in June of 2017. Nevertheless, the advisory says that the mentioned tactics, techniques, and procedures (TTPs) may still be being used against vulnerable Cisco devices.
The Simple Network Management Protocol (SNMP) is an application-layer protocol that provides a standardized framework and a common language for monitoring and managing devices in a network. SNMP is designed to allow network administrators to monitor and configure network devices remotely, but it can also be abused to obtain sensitive network information and, if vulnerable, exploit devices to penetrate a network. In 2021, APT28 used infrastructure to masquerade SNMP access into Cisco routers worldwide.
This was possible because the SNMP subsystem of Cisco IOS and IOS XE Software contains multiple vulnerabilities that could allow an authenticated, remote attacker to remotely execute code on an affected system or cause an affected system to reload. These vulnerabilities affect all releases of Cisco IOS and IOS XE Software prior to the first fixed release and they affect all versions of SNMP-Versions 1, 2c, and 3. An attacker could exploit these vulnerabilities by sending a crafted SNMP packet to an affected system via IPv4 or IPv6.
Enter Jaguar Tooth, the name of the malware that APT28 used to obtain further device information and enabled unauthenticated access via a backdoor. The actor obtained this device information by executing a number of commands via the malware and send them out over trivial file transfer protocol (TFTP). The information includes discovery of other devices on the network.
Discovery and countermeasures
Should you be worried about this threat? That depends on your threat model. If there is a reason for state actors to be interested in you in some way, then the answer is yes. This is the type of threat that the UK’s Minister and Secretary of State for National Investment Security, Mr Dowden, is referring to when he talks about groups that are ideologically motivated, rather than financially motivated.
If you suspect your router has been compromised, you can follow Cisco’s advice for verifying the Cisco IOS image. If that does not take away your suspicion, you should:
Revoke all keys associated with that router. When replacing the router configuration be sure to create new keys rather than pasting from the old configuration.
Replace both the ROMMON and Cisco IOS image with an image that has been sourced directly from the Cisco website, in case third party and internal repositories have been compromised.
To prevent falling victim to this specific threat there are some steps you should take:
Do not use SNMP if you are not required to configure or manage devices remotely. If you do need it, use a limiting allow list for SNMP messages to prevent unauthorized users from accessing your router.
Review your password policy and adapt it where necessary.
Use logging tools to record commands executed on your network devices.
We don’t just report on vulnerabilities—we identify them, and prioritize action.
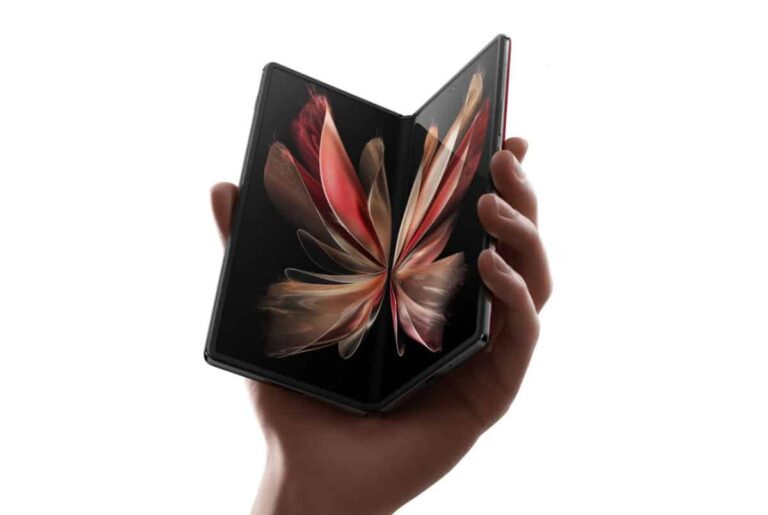
Vivo has announced its second-gen book-style foldable smartphone, the Vivo X Fold 2. This is technically the company’s third book-style foldable, but the Vivo X Fold+ was a mid-gen device, kind of.
In any case, the Vivo X Fold 2 does bring a number of improvements over its predecessor, and one of the main ones is its weight. This thing is a lot lighter than the Vivo X Fold 2. That device weighed 311 grams, while this one weighs 278 grams. That’s still hefty, but do keep in mind that this is a large foldable phone.
The Vivo X Fold 2 foldable is now official, and it does resemble the company’s “regular” flagships
The Vivo X Fold 2 launched in China, and at this point, we’re not sure if it will be coming to more markets. The device definitely looks like a cousin to the flagship Vivo X90 series that the company announced not long ago.
This is also a flagship-grade phone, but a foldable one. More on that soon, let’s quickly go over its design. As you can see in the provided images, the device has vegan leather on the back. It has a circular camera island on the back, with ZEISS optics on board. It does fold flat, and its frame is made out of metal.
The Vivo X Fold 2 is fueled by the Snapdragon 8 Gen 2 SOC, while it also includes 12GB of LPDDR5X RAM and 256GB or 512GB of UFS 4.0 flash storage. So, Vivo didn’t really cut corners here.
It has two 120Hz displays, each of which has an in-display fingerprint scanner
The main display measures 8.03 inches, and it’s a QHD+ (2160 x 1916) Samsung E6 AMOLED panel. This is an LTPO display, and it offers a refresh rate of up to 120Hz. HDR10+ is supported, as is Dolby Vision, while the display can go up to 1,800 nits of brightness at its peak.
The second panel is a 6.53-inch fullHD+ (2520 x 1080) unit. This is also Samsung’s E6 AMOLED display with a 120Hz refresh rate. This panel goes up to 1,600 nits of brightness at its peak.
120W wired charging is included, as is 50W wireless charging
A 4,800mAh battery is on board. The device supports 120W wired charging, in addition to 50W wireless charging. Reverse wireless charging is also a part of the package, by the way.
Android 13 comes pre-installed on the device, along with OriginOS 3 in China. If it launches globally, you’ll get Vivo’s Funtouch OS on top of it. There are two in-display fingerprint scanners included here, one for each of the phone’s displays. These are ultrasonic fingerprint scanners, by the way.
The phone has two SIM card slots (2x nano SIM), and it does support 5G connectivity (SA/NSA). Bluetooth 5.3 is included in the package too, of course.
You will find three compelling cameras on the back, with ZEISS optics
A 50-megapixel main camera (Sony’s IMX866 sensor, f/1.75 aperture, OIS, ZEISS T* coating, V2 chip) is backed by a 12-megapixel ultrawide camera (Sony’s IMX633 sensor, 108-degree FoV, f/2.0 aperture) on the back. The third camera on the back is a 12-megapixel portrait telephoto unit (f/1.98 aperture). A single 16-megapixel selfie camera (f/2.45 aperture) is also included, on each of the two displays.
The Vivo X Fold 2 measures 161.29 x 143.43 x 5.95mm when unfolded, and 161.29 x 73.42 x 12.9mm when folded. Do note that this goes for the Black model, the Red and Blue models are a bit thicker at 13.2mm, for some reason. Those are the three color options this phone comes in, by the way. They’re officially called Shadow Black, China Red, and Azure Blue colors.
The two Vivo X Fold 2 models are priced at CNY8,999 ($1,380) and CNY9,999 ($1,455) in China. Both models include 12GB of RAM, but their storage units are different (256GB and 512GB).