KFC owner suffers ransomware-related data breach

0
[ad_1]

US fast-food corporation Yum! Brands, which owns franchises including KFC, Pizza Hut and Taco Bell, has suffered a data breach following a ransomware attack.

The cyber attack, which took place on January 18, 2023, involved a malicious actor gaining unauthorized access to Yum! Brands’ network. The ransomware attack resulted in approximately 300 restaurants within the UK being temporarily shut down due to the IT systems affected by the attack.

Once discovered, Yum! Brands said the attack “took steps to lockdown impacted systems, notified federal law enforcement authorities, worked with leading digital forensics and restoration teams to investigate and recover from the incident and deployed enhanced 24/7 detection and monitoring technology”.  

After the incident was contained, the fast-food corporation initiated an investigation into the attack to see if any personal data had been stolen. It determined that the files accessed by the malicious actor during the attack contained private customer data.

The data stolen in the breach includes the names and ID card numbers of some customers including driver license numbers. In a notice of the breach sent to those affected, Yum! Brands said there was “no evidence of identity theft or fraud” being committed with the stolen data.

In a report filed with the US Securities and Exchange Commission regarding the attack, Yum! Brands said that it had “incurred, and may continue to incur, certain expenses related to this attack including expenses to respond to, remediate and investigate this matter”. The organization said it “does not expect this event to have a material adverse impact on its business, operations or financial results”. 


[ad_2]
Source link

Unmasking NIS2: Europe’s Secret Weapon Against Cybersecurity Threats – Latest Hacking News

0
[ad_1]

As cyber threats continue to grow, Europe, with its highly digitalized economy, has become a prime target. In fact, the number of cyberattacks on European businesses has soared to unprecedented heights, with a 108% increase in attacks against key sectors since 2020. To combat this alarming trend, the European Parliament has introduced NIS2, a new cybersecurity directive aimed at enhancing the Union’s cyber resilience.

NIS2 brings tighter requirements and a renewed emphasis on risk management and incident response, forever changing the way EU businesses tackle cybersecurity. In this blog post, we’ll delve into the far-reaching consequences of NIS2 for European cybersecurity and provide essential insights to help businesses adapt and thrive in this new regulatory landscape.

Unpacking The NIS2 Directive

NIS2, short for Network and Information Security Directive, is a new EU cybersecurity directive aimed at improving cybersecurity in the European Union. Adopted and entered into force on 16 January 2023, the directive sets out new cybersecurity requirements for organizations categorized as critical infrastructure.

Building on its predecessor NIS1, which was adopted in 2016, NIS2 expands its coverage to include sectors such as energy, transport, healthcare, finance, public administration, water supply, and many more. While the previous directive only focused on so-called essential services and digital service providers, NIS2 eliminates this distinction and instead divides affected entities into two categories: essential entities and important entities, where size, societal function/sector, and annual turnover is the deciding factor for whether NIS2 applies to a given organization.

In addition, NIS2 strengthens requirements for risk management, incident reporting, and cooperation between EU Member States in case of cyber incidents. Overall, NIS2 represents a significant step forward in EU cybersecurity regulations, and organizations that fall under its scope should take note of the new requirements to ensure compliance.

How NIS2 Will Impact EU Cybersecurity

NIS2 is set to have a significant impact on EU cybersecurity by mandating far-reaching security measures to improve risk management and incident response practices, increasing regulatory oversight, and introducing an unprecedented element of management compliance accountability. Some of the ways NIS2 will change EU cybersecurity include:

New cybersecurity requirements for businesses:

  • NIS2 introduces a core set of 10 minimum measures that organization must implement to manage risk, including measures such as access control, incident management, and business continuity management.
  • Businesses are required to conduct due diligence on the security of supply chains to ensure that third-party suppliers also adhere to NIS2 security standards.
  • Early-warning reports must be submitted within 24 hours of an incident.

Increased focus on risk management and incident response:

  • Businesses must develop incident response plans that cover various scenarios and conduct regular security assessments to identify vulnerabilities and weaknesses.
  • Reporting of incidents to competent authorities is required, and must include all relevant information, such as the scope and impact of the incident, the systems and data affected, and the measures taken to contain and mitigate the incident.

Greater regulatory oversight and enforcement:

  • Designated national authorities will be responsible for ensuring compliance with the directive through audits and inspections.
  • The authorities will have the power to request information, conduct investigations, and issue fines or penalties for non-compliance.

Personal liability for management bodies:

  • Management bodies, including directors and senior managers, may face personal liability for cybersecurity incidents resulting from their failure to implement security measures or to respond adequately to a cyber threat.
  • This means that they may be held accountable and face legal or financial consequences for their actions or inactions related to cybersecurity.
  • The personal liability requirement aims to encourage management bodies to take cybersecurity seriously and to prioritize the implementation of appropriate security measures to protect EU citizens’ personal data.


NIS2 and EU businesses: Implications and Opportunities

The overall impact of NIS2 on EU businesses is going to be massive.

With an estimated 160.000 affected entities across 15 different sectors, critical infrastructure organizations across all of Europe will have to address this new regulatory reality.

What’s more, all third-party suppliers providing services to these organizations must also meet the new requirements, multiplying the actual number of affected companies. Adding to the seriousness of this major policy change, executive teams will be forced to put cybersecurity on the board agenda because of the unprecedented introduction of management compliance accountability, which makes management bodies personally liable for non-compliance.

These changes will undoubtedly cause a surge in cybersecurity investments, compliance consulting, and relevant cybersecurity training as boards realize the potential business-crippling, legal consequences of negligence and non-compliance.

NIS2 will be a reality check for organizations that have been lacking in their security efforts. The directive will usher in a new security standard that – if widely implemented – will increase European businesses’ ability to withstand the destructiveness of tomorrow’s cyberthreats.

How To Prepare for NIS2

To prepare for compliance with NIS2, European critical infrastructure operators and providers in their supply chain must first conduct comprehensive risk assessments. This will help identify vulnerabilities and weaknesses that needs to be addressed following the new NIS2 standards. It will also provide insights into the effectiveness of existing security measures, which is another crucial element of the new requirements.

Member States have until 17 October 2024 to transpose the directive into national law. This gives affected organizations 16 months to assure that their cyber defense level is on par with the directive’s requirements.

Denmark-based business password management solution, Uniqkey, has published the infosite nis2directive.eu, offering accessible information on NIS2 to the public. The site includes all information relevant to the NIS2 directive, sourced from official, public sources, and curated for easy consumption. They also offer a practical whitepaper on the subject for anyone looking for tangible, tool-specific suggestions for how to achieve NIS2 compliance.

If you’re a European business operating within any of the 15 covered sectors – or providing services to any such organization – getting familiar with the Directive’s requirements will be essential to surviving the upcoming regulatory transition.
[ad_2]
Source link

April Pixel Watch update rolls out bringing security upgrades

0
[ad_1]

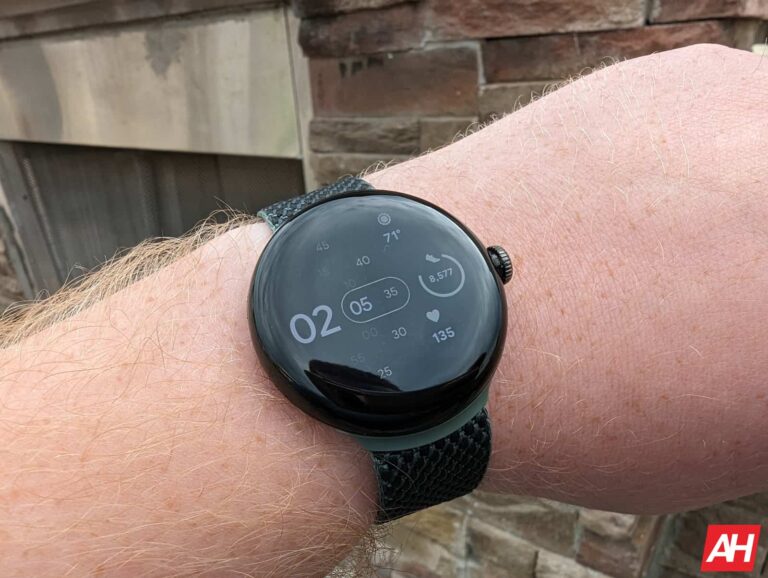
Users of the Google Pixel Watch are getting the April update with improvements. This update is coming alongside the April update for Pixel smartphones, and both updates are similar. For some reason, the new features and improvements are not bulky but seem to hit the nail on the head.

Basically, this update comes along with important security patches. This is also the case with the April update for Pixel devices, it is a security update. Some users might find it annoying that the new update only brings security improvements to the smartwatch.

This might be the case because the previous update comes with tons of features. Well, a security update is also essential for your smartwatch, hence making this update quite important. Pixel Watch users can make do with the features rolled out with the previous update.

Details on the April update for the Google Pixel Watch 

The latest update to the Pixel Watch comes with security upgrades for users around the world. There are no new features with this update, just a security improvement. The previous update came with a ton of new features for users to benefit from.

Some of these features include new Watch Faces, rotating the digital crown to wake, touch sensitivity, alarms, and so on. These features improve the overall user experience whilst making this smartwatch from Google more interesting to use. Considering the number of new features the previous update came with, it is hard to complain about the lack of new features with this new update.

This update’s security improvements help to patch up some loose ends and ensure user data security. A similar security upgrade is rolling out for Pixel devices that are eligible to receive updates. Just like the update made available for the Pixel Watch that coming to Pixel devices patches up any security flaws.

For Pixel watch users, to ensure that you get this update, you need to make sure your Watch is running on Wear OS 3.5. To confirm this, head over to your watch’s system update page in settings and refresh it. If you aren’t up-to-date, all pending updates will be listed for you to install.

If you are up-to-date, then you can proceed to install the April update. This update is currently rolling out to Pixel Watches globally, so if you are yet to get yours, don’t panic. The update will become available to users globally in the coming days.


[ad_2]
Source link

Google TV adds FAST Channels to the Live Tab

0
[ad_1]

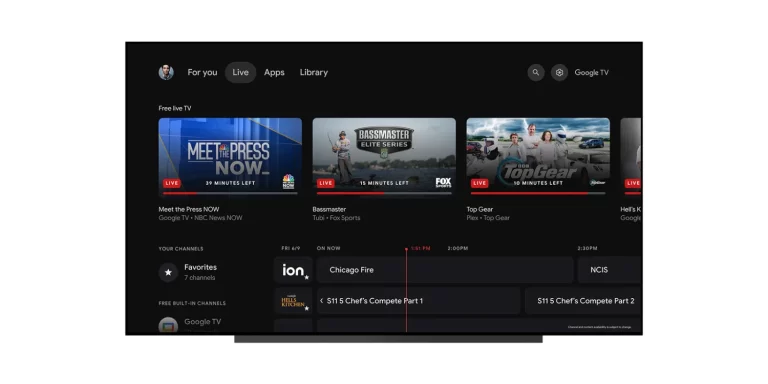
Today, Google is announcing a big new update for Google TV. The big change here is that Google is adding FAST channels into the Live Tab. That includes channels from Tubi, Plex, Haystack and Google TV into that tab. With that change, this means you’ll be able to browse over 800 channels of free and premium programming. This includes news channels like NBC, ABC, CBS and FOX.

There’s definitely going to be content there for everyone. From blockbuster movies, to popular series, and even sports available for free. That’s the beauty of FAST channels.

You can “favorite” channels to show at the top of the guide

Also part of this update today, Google is adding the ability to favorite channels, which will now show up at the top of the guide. Making it easier to find those channels the next time you look for something to watch.

Google will also organize all of the channels into an easier and faster browsing experience. With over 800 channels available, it could be pretty tough to find a good channel and something to watch. So this should make it a lot easier.

On top of that, Google is also keeping the premium live TV subscriptions in the Live Tab. That includes YouTube TV and Sling TV. Basically, the Live Tab will now show ALL of the channels that you have. Which is what it should have always been, but with the rise of FAST, it’s great to see Google TV adding support.

Google says that the new live TV experience is rolling out to Google TV devices in the US. That includes Chromecast with Google TV, as well as Google TV sets from Sony, TCL, Hisense and Philips. Google says that they plan to bring this new experience to eligible Android TV devices later this year.


[ad_2]
Source link

Third-party app brings the Pixel Launcher’s search experience to all Android phones

0
[ad_1]
There are non-Pixel Android users who would love to have the search experience of the Pixel Launcher on their phones. And now a third-party app called the Pixel Search app brings this experience to other Android phones. Tech journalist Mischaal Rahman tweeted (via AndroidAuthority) that “This app looks great! The search feature of many OEM launcher apps isn’t nearly as good as the Pixel Launcher’s unified search. This new app seems to replicate the Pixel Launcher search experience quite well!”
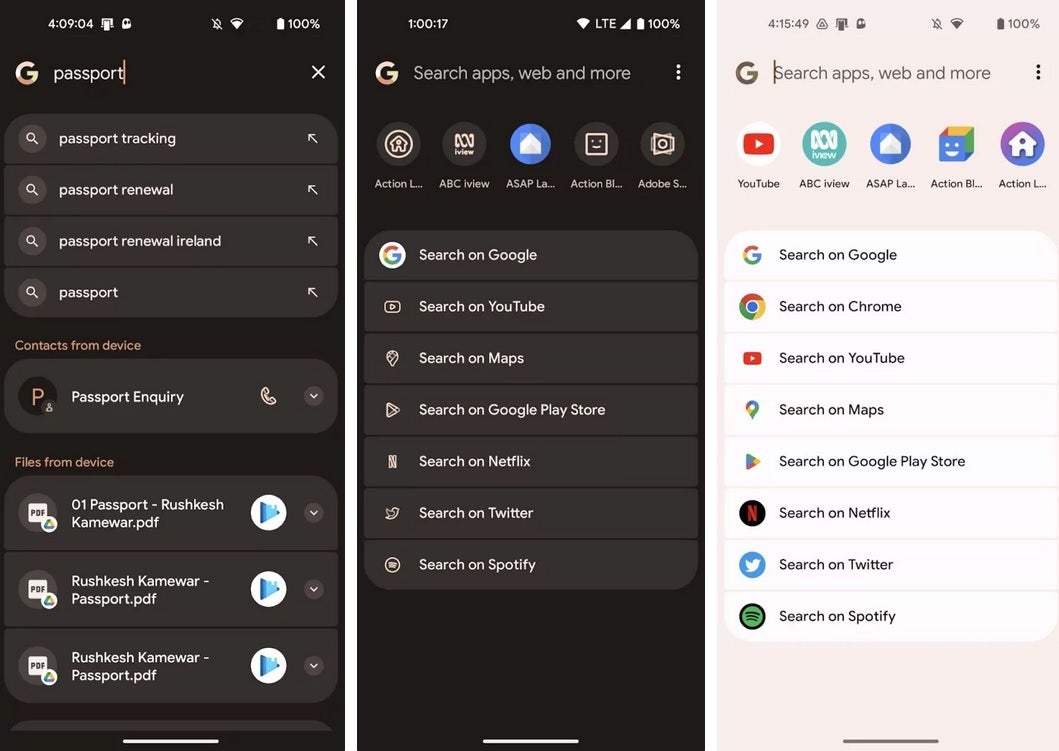
The app’s developer writes, “Pixel Search is the ultimate search app that allows you to find anything on your phone with ease. You can quickly search through your apps, contacts, web suggestions, and files without having to open multiple apps. Pixel Search is designed with a clean and intuitive interface that makes it easy for anyone to use.” Once installed, users can open Pixel Search by tapping on the icon or its Material You-themed widget. The widget also includes a shortcut to Google Discover and Google Voice search.

Pixel Search has the familiar search field on the top of the display, just like the Pixel Launcher, and right underneath are the icons for the last four apps visited-just like the Pixel Launcher. And if you tap on the three-dot icon on the right of the display, you can change the theme, change the app you want to use for searches and select a quick launch option that will automatically open the first search result. The latter is a feature that search on the real Pixel Launcher doesn’t have.

One thing that the Pixel Search app can’t do is search for system settings. But apparently, this is something that the developer is looking to add in the future. Speaking of the developer, Rushikesh Kamewar has already listed 15 additional apps in the Google Play Store. And by the way, the Pixel Search app is free.

[ad_2]
Source link

Major Hack Hits South Korean Exchange GDAC, $13.9M Stolen

0
[ad_1]

According to GDAC, stolen cryptocurrencies include 61 Bitcoins, 350.5 Ethers, 10 million of the WEMIX gaming currency, and $220,000 worth of Tethers.

South Korean cryptocurrency exchange and blockchain platform GDAC has fallen victim to a devastating hack, resulting in the theft of approximately $13.9 million worth of various cryptocurrencies.

GDAC CEO Han Seunghwan made the announcement on April 10 2023, revealing that the attack had occurred on the morning of April 9th 2023, when the hacker gained control of some of the exchange’s hot wallets.

The stolen cryptocurrencies include 61 Bitcoin, 350.5 Ether, 10 million of the WEMIX gaming currency, and $220,000 worth of Tether. This amounts to around 23% of GDAC’s total custodial assets, as stated in the announcement. In response to the attack, GDAC has halted all deposits and withdrawals and has initiated emergency server maintenance.

GDAC has taken swift action by reporting the hack to the police, informing the Korea Internet & Security Agency (KISA), and notifying the Financial Intelligence Unit (FIU) of the loss incurred due to the attack. The exchange is also urging other crypto exchanges not to honour any deposits made from the address used by the attacker.

Seunghwan expressed the challenges of confirming the timeline for resuming deposits and withdrawals, citing the ongoing investigation as a reason for the uncertainty.

Unfortunately, this incident is not isolated, as centralized exchange hacks continue to plague the cryptocurrency industry. In January 2022, Crypto.com suffered a hack that resulted in a loss of over $15 million.

In November 2019, the South Korean cryptocurrency exchange UPbit was hacked after which attackers managed to steal $50 million worth of Ether. Nevertheless, the GDAC hack will only harm investors’ trust in online crypto exchanges.

As the cryptocurrency market continues to grow, security remains a critical concern. Exchanges and investors alike must remain vigilant and implement robust measures to safeguard against potential cyber threats. GDAC’s unfortunate experience serves as a reminder of the importance of stringent security protocols in the ever-evolving landscape of cryptocurrencies.

  1. Bitcoin falls after Korean exchange loses $40M to hack
  2. BitGrail crypto exchange hacked; $160m in Nano stolen
  3. Coincheck crypto exchange hacked; $534 Million Stolen

[ad_2]
Source link

A week in security (April 3

0
[ad_1]

The most interesting security related news from the week of April 3 – 9.

Last week on Malwarebytes Labs:

Stay safe!


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Galaxy Z Fold 5, Flip 5 display size & weight seemingly finalized

0
[ad_1]

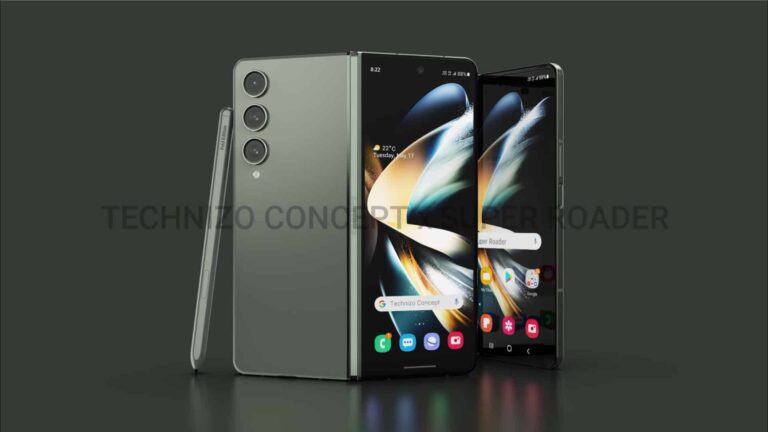
Samsung is hard at work on making its next-gen foldables more appealing and attractive as the competition grows. The upcoming Galaxy Z Fold 5 and Galaxy Z Flip 5 will address several complaints with its earlier foldable smartphones. These include the display crease, cover display limitation, thickness, and weight. While we are still months away from the final product, a reputed tipster has shared “100%” correct details about the display size and the weight of the new foldables.

According to tipster Ice Universe, the Galaxy Z Flip 5 will feature a 6.7-inch inner folding display and a 3.4-inch cover display. While the main screen is unchanged from last year’s Galaxy Z Flip 4, the secondary screen on the outside is huge this year. We are calling a 3.4-inch screen huge because the 2022 and 2021 models featured a 1.9-inch panel. Rumors are that the new Flip phone from Samsung will get a square-shaped display on the outside (an aspect ratio close to 1:1). It will be much more useful than the earlier solution.

The Galaxy Z Fold 5 isn’t getting the same treatment when it comes to the display, though. The new model will feature a 7.6-inch inner folding display and a 6.2-inch cover display. That’s unchanged from the past two generations of Samsung’s Fold series foldables. While we don’t have any complaints with the main display of the Galaxy Z Fold 4, the secondary screen has a rather tall aspect ratio of 23.1:9 (down from 25:9 on the Galaxy Z Fold 3). Many users requested the company to make the screen wider. It’s unclear if there’s any change to the aspect ratio this year.

The Galaxy Z Fold 5 will be lighter

Coming to weight, the Galaxy Z Flip 5 will reportedly weigh 187 grams. That’s the same as the Galaxy Z Flip 4. However, Samsung has cut some mass from the Fold model. The Galaxy Z Fold 5 will be “just” 254 grams heavy. That’s down nine grams from last year’s Galaxy Z Fold 4 (263 grams). There have been reports of the company trying to cut weight by four grams more, but those efforts seemingly weren’t fruitful. That’s based on the tipster’s claim that these specs are “100%” accurate.

That said, the 2023 Samsung foldables are still at least four months away. The Galaxy Z Fold 5 and Galaxy Z Flip 5 won’t debut ahead of August. That’s plenty of time for more leaks and rumors. If multiple sources corroborate the same information, it would feel more accurate. Rest assured, we will keep you posted with all the latest information about the upcoming foldable smartphones.


[ad_2]
Source link

YouTube adds 5 new features to its Premium tier

0
[ad_1]

Over the past few years, YouTube has been introducing a range of new features to entice users to subscribe to its premium plan, though long-requested features like queuing have been forgotten. Now, as part of these ongoing efforts, the platform has recently introduced five new features aimed at enhancing the video-watching experience and potentially making it more enjoyable with friends and family.

One of the most significant new features is the “1080p premium” tier of video quality, which offers a higher bitrate for playback. As a result, premium users can now enjoy extra crisp and clear videos with lots of detail and motion. However, the enhanced 1080p quality level is currently only available on iOS devices, but YouTube plans to roll out the feature to all users soon.

“Whether you’re an avid sports fan or locked in on the latest gaming videos, this new feature will bring an even deeper visual quality to our members,” says YouTube.

Making YouTube Premium a social experience, adding queuing and more

In an effort to make watching videos a more social experience, YouTube is introducing a new feature called “Meet Live Sharing,” allowing everyone to view the same YouTube video together, regardless of whether they have a Premium subscription or not. The feature is currently only available for Android devices, and in the coming weeks, iOS users will be able to access it via FaceTime.

“Through Meet Live Sharing on Android devices, Premium members can host Google Meet sessions where all attendees, regardless of whether they are Premium or free users, can watch YouTube videos together,” reads YouTube’s blog post.

After being in testing for some time now, YouTube is finally rolling out a queueing system for phones and tablets that allows users to create a queue of videos, add new ones, and change the position of the ones already there. Additionally, the new Smart Downloads feature will automatically download recommended videos through Wi-Fi to users’ mobile devices for offline watching at a later time.

Moreover, YouTube is also introducing a “continue watching” feature that allows users to resume watching their videos from the last point they left off, regardless of the device they are using.


[ad_2]
Source link

Samsung’s phones and tablets will continue to be protected by McAfee

0
[ad_1]

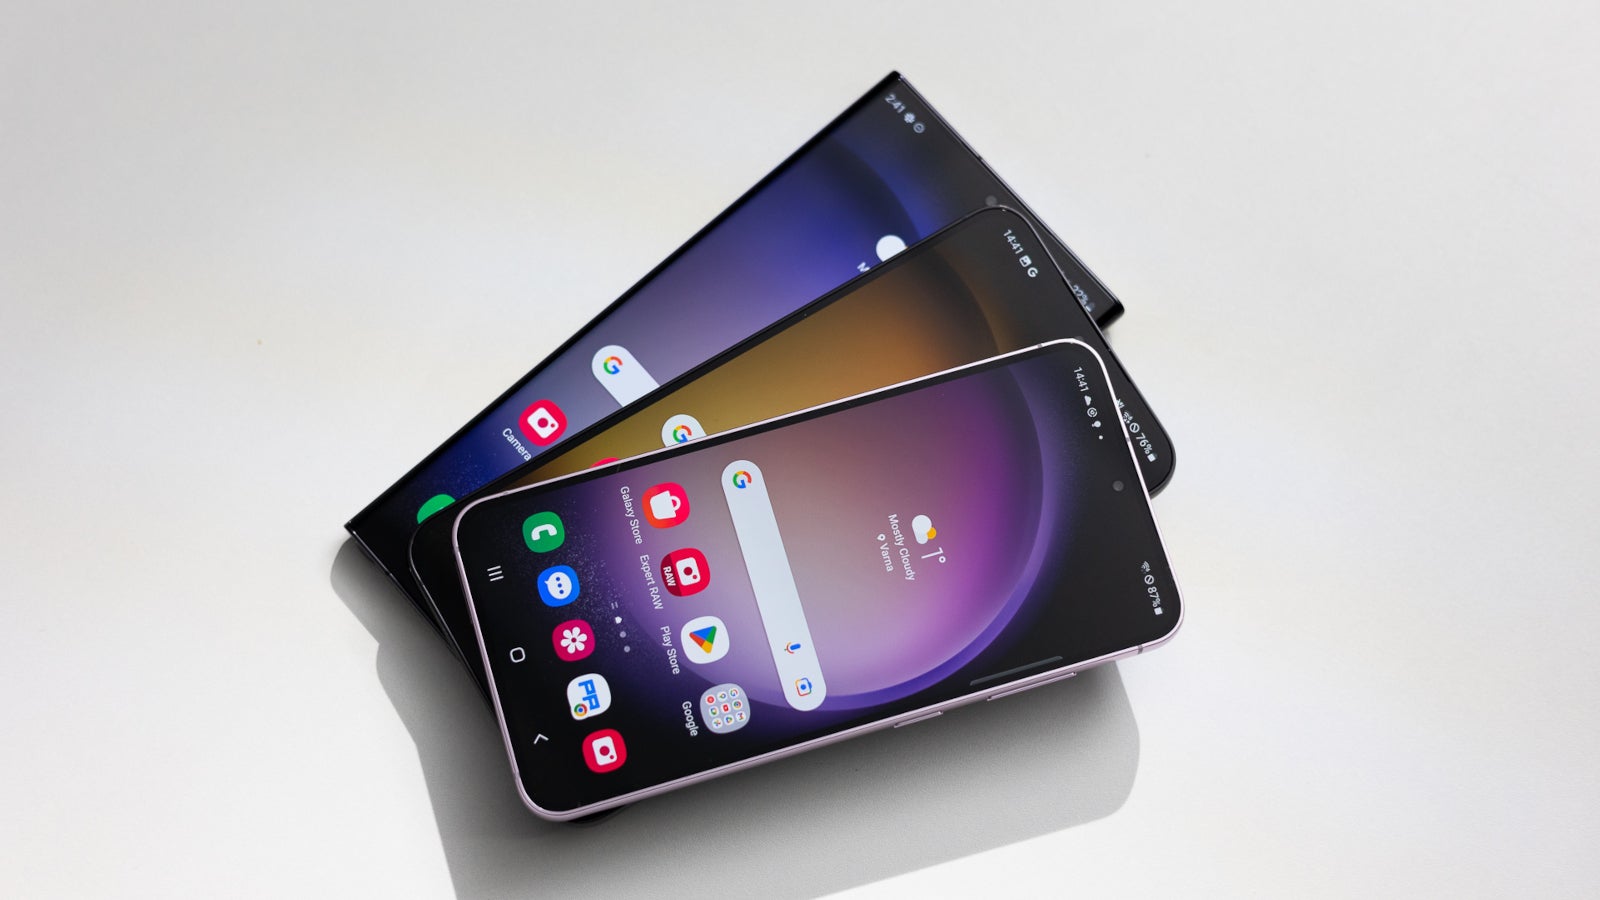
Security and privacy are the main buzzwords for every company that promises to provide them, usually for a high price. McAfee is one of the most iconic names that activates in the security field and after nine years of partnership with Samsung, the company announced an extension of that partnership that will probably go beyond the 10-year mark.“When purchasing the latest Samsung product, the last thing users want to think about is its security. Consumers should be able to enjoy what the internet has to offer, from banking to browsing social media, with the benefit of protections against potential risks online. Our almost decade-long partnership with Samsung extends our award-winning online protection to Samsung’s customers and advances our mission to empower consumers to live their lives online with confidence.”Under the continuing partnership, Samsung smartphones such as the new Galaxy S23 series, as well as the Galaxy Book3 series, will come pre-installed with antivirus protection developed by McAfee. It’s pretty simple and totally not unheard of, especially in a world where security and privacy are so treasured by phone users.

Of course, in addition to smartphones, McAfee will also protect Samsung’s tablets and PCs. Protection against malware is more important than many phone users realize these days. Although the free availability of security solutions isn’t yet something that customers are taking into consideration when looking to buy a new phone, it’s worth checking out if you plan to spend a lot of money.

We’re not sure if McAfee announcement includes names like Galaxy S23 Ultra, Galaxy S23+ and Galaxy S23 just because they’re so popular in the United States, but we would expect other Samsung smartphones and tablets to benefit from the same level of security protection, not just the most expensive ones.

Until we get confirmation, the Galaxy S23 Ultra, Galaxy S23+, Galaxy S23 and the Galaxy Book 3 series are the only ones that come with McAfee security solutions just about everywhere on the globe.

[ad_2]
Source link