How to delete a Google review

0
[ad_1]

Google reviews are a great way to get some insight into an establishment’s reputation. They’re especially useful if you’re going to be spending money at said establishment. The thing is that there will come a time when you’ll need to delete a Google review that you wrote.

Maybe you made a mistake. Maybe your opinion of the place changed over time. Whatever the reason, it’s possible to scrub a review that you left for a business. How? Here’s a handy guide to show you.

Before we start

We have a ton of handy How-To articles here at AH to help you on your tech journey. You can check out How To Quickly Translate Text On Your Android Device. If you’re into artificial intelligence, you can check out How To Use ChatGPT. Lastly, you can boost your Gmail experience by reading How To Use Gmail Keyboard Shortcuts.

How to delete a Google review

So, these steps teach you how to delete a Google review that you yourself wrote about a business. Obviously, if you want to get rid of a review that someone wrote about your business, it’s not that easy of a process. It’s possible to have a comment about your business removed, but it’s a much different process. We’ll explain later on in the article.

Using your phone

So, the first step to deleting your review is finding it. If you’re using your phone, tap on your profile picture in the upper right corner of the Google Maps app. In the popup, tap on the Your profile button- if this is your first time going there, you’ll see a page asking you to set up your public profile. Just tap Not now if you want to avoid any extra steps.

Delete google review 5

On your profile page, it will show you the images you posted from different businesses. Scroll down to the Reviews section. In this section, it will show you a list of the reviews that you posted starting with your most recent one.

On the review, tap on the three-dot menu on the right side of the screen. In the resulting dropdown menu, you’ll see the option to delete the review. When you tap on it, you’ll see a confirmation screen pop up. It will ask you if you’re sure that you want to delete that review. The process can not be undone.

Delete google review 6

Using your computer

Deleting a review using your computer is similar, but there are some differences. Go to the Google Maps website and click on the “hamburger-style” menu on the top left of the UI. In the resulting panel, tap on the Your contributions button.

The panel will change to show you a list of your reviews and pictures. On the top of the panel, you’ll see tabs that let you control what contributions you see. If you don’t see the review you want to delete right away, you can click on the Reviews tab.

Delete google review 3

When you find the review that you want to delete, click on the three-dot menu on the right of the item. After that, you’ll see a popup appear giving you the option to delete the message. Just like on mobile, Maps will confirm that you really want to delete the review.

Delete google review 4

Whether you’re using your phone or your computer, you have the option to simply edit your review. So, if you have a change of heart, but you don’t want to completely delete your review, you can just edit it. The Edit review button is right above the Delete review button on the menu.

How to remove a review that someone wrote about your business

Now, this is not a surefire thing. Obviously, it’s not fair for you to just remove any sort of negative comment a person says about your establishment. However, there are exceptions. There are people who leave untruthful, offensive, or troll reviews just to drive down your business. At that point, it’s necessary to step in.

Getting a review removed is a pretty involved process, and there’s no guarantee that it will work. But, why not give it that old college try?

On your phone, go to the Google Maps app and tap your profile picture on the top right of the screen. There, you’re going to tap on the Your business profile button. It will be right under the regular profile button.

It will show you a dashboard with different tabs that you can navigate to. Tap on the Reviews tab. There, you’re going to find the review in question and tap on the three-dot menu on the right side.

On the menu, Tap on the Report button. This will take you to a UI where you can type up why you’re reporting the review. This is a very important step, as you’re making your case for why you’re reporting the review. So, you’ll need to be detailed in your report and outline why the comment is generally inappropriate.

After that point, you’ll need to wait several days for Google to weigh in and tell you its decision.

Why a review could be reported

Now, it’s highly unlikely that Google will remove a comment because it hurt your feelings. So, if a customer says something like “Horrible service!”, whether you agree with it or not, that’s something that you’re going to have to deal with.

Reporting a review is something that you should do if the review is downright offensive, unnecessary, irrelevant, spam, or obviously a troll. Think of it like the comment section on a social media site. So, if you’re running a nail salon, and you get a review reading, “The food here is terrible”, you should report it.

If a review says something like “These [offensive term] can’t make a burger”, then you’ll be able to report it.  So, you get the picture. While it’s not a surefire thing, it’s still worth a try.


[ad_2]
Source link
Samsung estimates Q1 2023 profit to drop 96%, hit a 14-year low

0
[ad_1]

Samsung has shared its earnings estimates for the first three months of 2023, and the figures are unsightly for its investors and well-wishers. The company is staring at an eye-popping 96 percent year-on-year (YoY) decline in profit in Q1 2023. It is hoping to take home just about KRW 0.6 trillion (roughly $450 million), down from KRW 14.12 trillion (nearly $11 billion) in Q1 2022. Overall consolidated sales revenue for the first quarter of the year is expected to clock in at around KRW 63 trillion (roughly $47 billion).

Samsung reports a massive profit decline in Q1 2023 amid dwindling chip demand

Samsung made truckloads of money in 2021 and started 2022 with a bang. However, midway through last year, the company’s earnings started to decline. A drop in demand for semiconductors, particularly memory chips, severely affected its business.

Since the majority of the Korean firm’s income comes from the semiconductor business, the drop hit where it hurts the most. By the end of 2022, its yearly profits were down 16%. More notably, the Q4 income hit an eight-year low.

In its financial outlook for 2023, Samsung said it isn’t expecting much improvement. The company estimated its earnings from the semiconductor business to be halved this year. While it hasn’t shared its detailed earnings report for the first quarter yet (it will come in April end), early estimates point to a gloomy future.

On average, the world’s largest smartphone maker, which also leads the industry on several other fronts, made just about $150 million in the first three months of 2023. This is its lowest quarterly profit in 14 years (since the 2008 economic recession).

The Korean media recently reported that Samsung will also post its first-ever quarterly loss from the semiconductor business since 2008 in Q1 2023. It could lose about KRW 4 trillion or more than $3 billion from the memory chips unit.

Looking at the company’s earnings estimates, it may have made about as much from all other businesses in the first quarter. Overall, it just about broke even between January and March 2023. We’ll have to wait for the full report to find out where Samsung made the most money this past quarter.

Samsung will not scale back semiconductor investments

Despite losing money from semiconductors, Samsung doesn’t plan to scale back investment. Many rivals have reduced their spending in the business until the market rebounds. But, the Korean firm sees continued investment and innovation as the key to staying afloat in the long term.

It has even borrowed about $16 billion from its sister firm to fund the planned investments. Time will tell whether Samsung reaps the benefits of these investments anytime soon. Stay tuned for its full Q1 2023 earnings report later this month.


[ad_2]
Source link

Microsoft adds Bing’s AI chatbot to the Android SwiftKey app; feature will improve your texts

0
[ad_1]
Thanks to its investment in OpenAI, Microsoft has been adding access to AI chatbot ChatGPT to everything. Bing, of course, has ChatGPT integration, and enabling a flag on both the Android and iOS version of the Edge app will put a button on the Edge toolbox giving you one-tap access to the conversational AI chatbot. Now Microsoft is adding Bing Chat AI to its popular third-party QWERTY app for Android, SwiftKey.
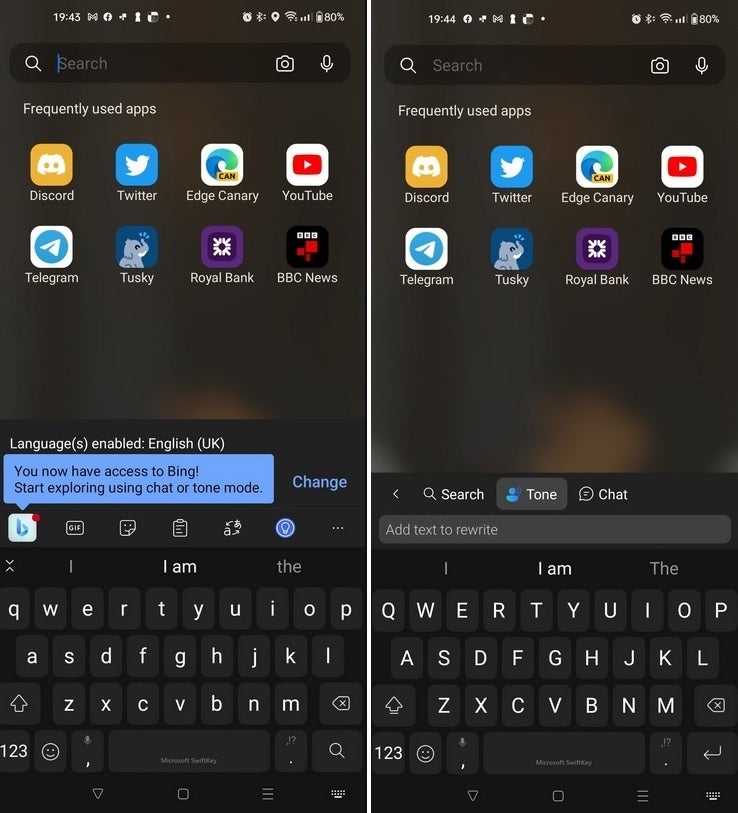
Per The Verge, with this integration, SwiftKey for Android users will be able to access the chatbot like they already can on Bing. The process starts by installing the SwiftKey Beta app from the Google Play Store which can be done by tapping on this link. After opening the app, you will need to sign in with your Microsoft Account information. Microsoft’s CTO of mobile and commerce Pedram Rezaei said on Twitter that the feature is “slowly rolling out.” Some Android users say that they have not yet seen the chatbot after installing the app.

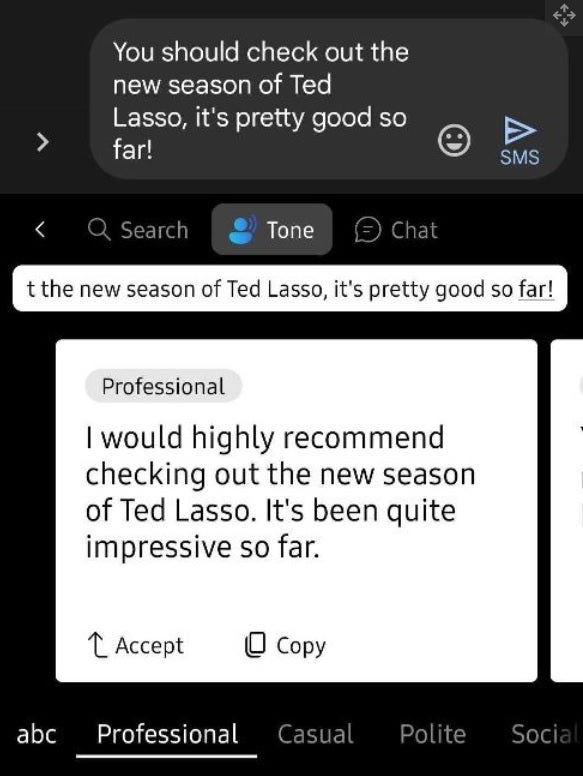
Android users with the SwiftKey Beta app installed will be able to access Bing AI from a button above the keys. Tapping that button opens the search feature and Bing Chat which accesses the AI chatbot. In addition, with the SwiftKey for Android app, users will be able to improve text messages by typing what they want to write in a field and having the AI feature rewrite it using different tones. On Bing and Edge, the same functionality can be used to create documents and emails.

Last year Microsoft pulled SwiftKey from iOS before bringing it back. You can install the app for your iPhone by clicking on this link. Microsoft might feel pressured to quickly integrate the AI chat feature with the iOS version of SwiftKey considering the competition from other iOS third-party QWERTY keyboard apps with AI functionality.

Google is expected to integrate many of its apps including Search, Gboard, and others with its conversational AI chatbot Bard.


[ad_2]
Source link

IoT garage door exploit allows for remote opening attack

0
[ad_1]

Multiple exploits are impacting a line of smart products for the home.

A popular and reasonably cheap garage door controller is making waves in the news, and not in a good way. Ars Technica reports that the $80 devices created by Nexx are suffering from a number of security issues which could compromise the safety of your home.

A Medium post by researcher Sam Sabetan reveals the details.

At the tail end of 2022, Sam discovered a “series of critical vulnerabilities” in the Nexx range of smart devices. These issues not only affected garage door openers, but also smart plug switches and alarms too.

Working with the US Cybersecurity and Infrastructure Security Agency (CISA), five CVEs were eventually assigned. As per the advisory, successful exploitation of these vulnerabilities could allow an attacker to receive sensitive information or hijack devices and not a huge amount of technical ability is required to perform the attacks.

Developers keep making the hard coded password mistake

What are some of the issues at play here? Well, one of the biggest is that hard coded credentials are used to talk to Nexx servers. What this means is that the password shipped with the product can never be changed. If someone finds out what it is, either from a list online or by socially engineering the victim, the game is indeed up.

As Ars Technica notes, this alongside controllers broadcasting unencrypted email addresses along with messages needed to open or close doors all means a fairly easy win for a competent attacker. Indeed, someone could potentially open your garage door from the other side of the planet if they wanted to. Sabetan estimates that somewhere in the region of more than 40,000 devices might be impacted by this issue, both commercial and residential users.

Additional vulnerabilities include smart alarm impersonation, which would allow attackers to ultimately control the branded home alarm system that the Nexx smart alarm controller operates.

Elsewhere, we have smart alarm hijacking which could allow an attacker to essentially remove all control from a home alarm out of the owner’s hands, granting them full access in the process.

The suggested fix: replace these devices

This is all very bad. Worse, Sabetan reports that Nexx has “consistently ignored communication attempts from myself, the Department of Homeland Security, and the media”. One has to wonder if the company is unwilling or unable to fix the issue. With this in mind, the only real advice which Sabetan has is the same as when you realise your phone is running an abandoned app. As painful as it may be to start reorganising how your physical home meshes with the digital world, it’s time to start ripping everything out and look for other home security solutions.

From the CISA mitigations page, which doesn’t go quite as far as Sabetan’s advice to remove all of the Nexx products from your home or place of business:

  • Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the Internet.
  • Locate control system networks and remote devices behind firewalls and isolate them from business networks.
  • When remote access is required, use secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as its connected devices.
  • CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures.

The Internet of Things can be a perilous place, and the lack of effective security in these tools we entrust our homes to is far from ideal. If you have devices and apps being used to power your home, alarms, doors, windows, or anything else, now is the time to check if those passwords are hard coded.


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link
Best HDMI Cables for your TV

0
[ad_1]

An HDMI cable is almost needed as much as a USB-C cable at this point, because it is used by just about everything. From your gaming consoles, to your laptop, to even your streaming devices like a Roku or Chromecast. But not every HDMI cable is created equal. You might head to Best Buy and find a cheap HDMI cable and think that’s a great option. It might be, it might not be.

Here in this article, we are rounding up the very best HDMI cable that you can pick up for your TV in 2023.

Best HDMI Cables

This list has HDMI cables that can support 4K Ultra HD resolution, as well as a couple of 8K models available. While majority of us don’t have a 8K TV, that will change in the future, so you might as well invest in a good 8K HDMI cable now.

Product nameCostWhere to buy
Monoprice 6′ High Speed HDMI Cable$6.98Amazon
Best Buy Essentials 6′ 4K HDMI Cable$6.99Best Buy
Cable MAtters 48Gbps 8K HDMI Cable$10.49Amazon
Philips 4′ High Speed HDMI Cable with Ethernet$9.19Target
Insignia 25′ 4K HDMI Cable$79.99Best Buy
Rocketfish 4′ 8K High Speed HDMI 2.1 Cable$39.99Best Buy

Monoprice 6′ High Speed HDMI Cable

51pBqQUe GL SL1200

  • Price: $6.98
  • Where to buy: Amazon

Monoprice is a pretty popular name in the world of cheap cables. And that’s because they offer cheap, but good cables. And this one here is a six-foot long HDMI cable. That’s going to be plenty long enough for most TVs and entertainment setups. And it’s also the most common lenght here.

This is a “premium certified” cable, which means that it is guaranteed to perform at a specific level. That level is 4K at 60Hz. Since this does not support HDMI 2.1, it won’t do 4K at 120Hz, unfortunately.

This is the cheapest cable on this list, but not by a huge margin. The next option is just a penny more expensive actually.

Monoprice High Speed HDMI Cable – Amazon

Best Buy Essentials 6′ 4K HDMI Cable

6472356 sd

This is Best Buy’s in-house brand, so yes it’s still cheap, but this is still a pretty good HDMI cable. It’s going to be perfect for most people and can support 4K at 60Hz. It can also support up to 18Gbps bandwidth. Ensuring a great picture and sound experience with this particular HDMI cable.

It also uses nickel-plated connectors, allowing it to resist corrosion for long-lasting use. So you won’t need to replace this anytime soon.

Best Buy does sell this particular HDMI cable in three lengths: 3-foot, 6-foot and 12-foot. So if you do need something shorter, or a bit longer, they have you covered here.

Best Buy Essentials 6′ 4K HDMI Cable – Best Buy

Cable Matters 8K HDMI Cable

61O4 dPc9GL SL1500

  • Price: $10.49
  • Where to buy: Amazon

If you just bought a 8K TV, then you’re going to want to buy this 8K HDMI cable. While it’s not the best, it will get the job done. It is able to do 8K at 60Hz and 4K at 240Hz. It also supports eARC over HDMI, so you can use it for a soundbar as well. And still get Dolby Atmos and DTS X Surround Sound 7.1 and 5.1 here.

This is backwards compatible with HDMI 2.0 cable and does support RGB HDR 12-bit color and Dolby Vision. So you’ll be able to take full advantage of all the features of your TV with this cable.

Cable Matters 8K HDMI Cable – Amazon

Philips 4′ High-Speed HDMI Cable

best hdmi cable

  • Price: $9.19
  • Where to buy: Target

This is a shorter HDMI cable, this time from Target. It’s a good option for a smaller TV, or a setup where your consoles and streaming devices are closer to your TV. As a shorter cable means that the signal has to go less distance to get to your TV.

It’s a HDMI 2.0 cable here, so that means it is capped out at 4K at 60Hz. Which is perfectly fine for most people. It’ll still work perfectly fine with your Apple TV, Fire TV, Roku or any other device.

Philips 4′ High-Speed HDMI Cable – Target

Insignia 25′ 4K HDMI Cable

best hdmi cable

If you have a very elaborate setup, then this HDMI cable might be needed. This is a 25-foot long HDMI cable that is capable of 4K at 60Hz, since it is still HDMI 2.0. This particular cable is available in smaller sizes, should you not need a 25-foot cable.

This is also rated to be used within a wall. So if you are trying to do a setup where everything is hidden, this is a pretty good option, to be quite honest.

Insignia 25′ 4K HDMI Cable – Best Buy

Rocketfish 4′ 8K High Speed HDMI 2.1 Cable

best hdmi cable

This is the best HDMI cable to get for 8K and/or HDMI 2.1. If you have a PlayStation 5 or an Xbox Series X with a HDMI 2.1 compatible TV, then this is the cable you want. It’s one of the few that can do HDMI 2.1 at a decent price. That’s going to give you 4K at 120Hz, or 8K at 60Hz. It can even support up to 10K, though we have not seen any 10K TVs just yet.

On top of that, it also supports VRR or Variable Refresh Rate, which is a big feature for the PlayStation 5 and Xbox Series X.

This is a very high-quality HDMI cable from Rocketfish, and you can tell by just how thick the cable is here. It is in-wall rated, and comes in a four-foot length. While this is a HDMI 2.1 cable, it is backwards compatible with older HDMI standards, so you can use it with other devices too.


[ad_2]
Source link
EU Chips Act is set to be approved this month

0
[ad_1]

After the United States’ initiative to boost its semiconductor manufacturing capabilities and reduce its reliance on Taiwan, the EU is also taking significant steps to strengthen its semiconductor industry with its own Chips Act.

According to a report from the South China Morning Post, the European Union plans to reduce its dependence on US and Asian suppliers with a $47 billion investment, aiming to increase the EU’s share of global chip output to 20% within a decade.

While initially, the European Commission proposed funding only for advanced chip plants, in the wake of the global chip shortage, the EU governments and lawmakers further expanded the scope to include the entire value chain, including older chips and research and design facilities.

Additionally, this expansion is also in response to the growing importance of Belgium-based IMEC, a leading innovation hub in nanoelectronics and digital technologies. With over 600 major industry players, lawmakers see IMEC as a significant reason to invest more in research and development.

Funding negotiations and potential deal clinching

EU countries and lawmakers will meet at the European Parliament’s monthly session in Strasbourg on April 18th to negotiate the funding details for the Act. And, according to sources familiar with the matter, the likelihood of clinching a deal is high. However, discussions so far have pointed to a €400 million shortfall, but the EU executive has reportedly secured the bulk of the funds.

Moreover, the EU’s move to provide funding for the entire value chain will also address the complaints of smaller EU countries about being left out after Intel and STMicroelectronics announced plans to build chip manufacturing facilities in Germany and France, respectively.

The EU Chips Act is a significant step towards boosting the European semiconductor industry and its success will be crucial in securing the EU’s position in the global technology landscape and reducing its reliance on Taiwan and the United States.


[ad_2]
Source link

Ransomware Gang Leaked 600GB of Data

0
[ad_1]
Ransomware Gang Leaked

The ransomware gang responsible for the February attack on the City of Oakland, California, released a second data dump. The dump consisted of nearly 600 gigabytes of files that contained stolen municipal data, exposing critical information on thousands of employees in the city.

Play, the threat group responsible for the ransomware attack, posted the second leak on their site, following up with their first data dump at the beginning of March, with Oakland’s data sizing up to 10 gigabytes.

The leak included thousands of former and current city employees and a massive 12 years of city roster. It also had several police misconduct allegations and scanned bank accounts.

Oakland City Hall statement reads, “As a further community update, we recently became aware that the same unauthorized third party claiming responsibility for the ransomware incident has posted additional data allegedly taken from our systems during the incident in February to a website not searchable via the traditional Internet.”

Since the attack in February, Oakland has recovered some of the services disrupted during the breach, including its 311 line, which serves as a government contracting portal and online permit application system.

Nevertheless, the attack still affects the City significantly, with the threat group frequently leaking stolen data. In accordance with this second data dump, a union representing Oakland Police Department officers had filed a claim of nearly $25,000 for every police officer whose data had been leaked in the breach.

The association also released a statement accusing city leaders, including Mayor Sheng Thao and City administrator G. Harold Duffey of refusing to answer and hiding the extent of the ransomware attack.

“Oakland city leaders talk about accountability, yet there has been zero accountability and a deafening silence for the safety and financial security of the city’s valued employees. This city is truly broken when city employees learn more about releasing their confidential information from the media than their employer, whose incompetence and sloppy security allows these data breaches to occur.” said Barry Donelan, the association’s president.

Oakland city officials are still investigating this issue and dealing with the clashes between the Officer’s Union and the city leaders. A similar clash between Washington D.C.’s Metropolitan Police Department and the city officials was due to the 2021 data breach incident.

Looking for an all-around patching solution – Try Patch Manager Plus


[ad_2]
Source link

Malwarebytes’ 15-year journey in business cybersecurity

0
[ad_1]

It’s time to buckle up and embark on a whimsical journey through the twists and turns of Malwarebytes’ evolution.

As we raise a glass to toast Malwarebytes’ 15th anniversary of boldly venturing into the realm of business cybersecurity, we’re feeling nostalgic.

It’s time to buckle up and embark on a whimsical journey through the twists and turns of Malwarebytes’ evolution. From modest beginnings to becoming a titan in business cybersecurity, we’ve got a tale to tell, so take your seats, grab your popcorn, and enjoy the show!

Act I: Humble Beginnings (2008 – 2012)

In the late 2000s, Malwarebytes tiptoed into the business sector with corporate licensing for its consumer anti-malware product. It was a modest start, but hey, every masterpiece starts with a single brushstroke, as they say.

2012 marked a milestone as Malwarebytes introduced Anti-Malware Small Business Edition, a tailored solution with features beyond the Home edition, like XML Logging and Advanced Command Line Parameters & Controls. Now we were cooking with gas!

Act II: Malwarebytes Takes the Stage (September 2012 – 2016)

With the grand entrance of Malwarebytes Enterprise Edition (MEE) in late 2012, our business offerings went from a fresh-faced newcomer to a seasoned performer. MEE delivered centrally deployed, administered, and monitored threat protection and malware remediation to an audience of businesses, governments, and educational institutions.

Our performance received rave reviews, and the likes of The University of Alabama, NextGen Healthcare, and several Fortune 1000 companies lined up for an encore. Malwarebytes CEO Marcin Kleczynski summed it up in 2013, promising more show-stopping acts in the future:

“We have been making great progress since the launch of MEE, and this is just the start. Over the next year we’ll be releasing a new enterprise product, and there will be tremendous opportunities within our growing channel program,” said Kleczynski. “We’re carving out a new space in endpoint security by offering a solution that protects enterprises from zero-day malware incidents that AVs struggle to detect.”

And you best believe that Marcin was true to his word.

Act III: The Plot Thickens (June 2014 – 2016)

In 2014, Malwarebytes launched the Anti-Malware Remediation Tool, a sleek, portable solution for businesses to eliminate malware with minimal fuss. This was swiftly followed by Malwarebytes Endpoint Security, a triple-threat bundle combining Anti-Malware for Business, the Management Console, and Anti-Exploit for Business.

Act IV: The Cloud Age (2017 – 2018)

The year 2017 marked a turning point as Malwarebytes unveiled Nebula 1.0, a cloud-based console that propelled us into the world of cloud security management. Nebula 1.0 featured Malwarebytes Incident Response and Endpoint Protection, showcasing our innovative machine learning approach to Anomaly Detection.

In 2018, we expanded our portfolio with Endpoint Protection for Mac, Endpoint Detection and Response (EDR) for Windows endpoints, EDR Ransomware Rollback, and EDR Endpoint Isolation. Our growing repertoire of features ensured that no businesses’ platform was left unprotected.

Act V: OneView to Rule Them All (2019)

2019 saw the introduction of OneView, a multitenant console designed for Managed Service Providers (MSPs). This innovation allowed MSPs to effortlessly manage multiple clients’ cybersecurity needs from one central command center.

With Malwarebytes OneView, MSPs could now deliver the exceptional protection and remediation capabilities their clients demanded, without compromising on efficiency or profitability.

Act VI: Windows Servers and Beyond (2020 – 2021)

We didn’t rest on our laurels in 2020, enhancing our EDR offerings with support for Windows Servers and the addition of Flight Recorder Search for advanced visibility and search capabilities.

In 2021, Malwarebytes extended its protective umbrella to include EDR for Mac and Cloud Sandbox, followed by Threat Hunting Alerts and Brute Force Protection, ensuring cyber threats were kept at bay.

Act VII: A Smorgasbord of Enhancements (2022)

In 2022, Malwarebytes broadened its horizons, embracing an Active Response Shell for EDR and EDR for Linux-based systems. We also introduced Device Control, Vulnerability Assessment, and Patch Management Modules to empower administrators in their ongoing battle against exploits and other cyber threats.

But wait, there’s more! Malwarebytes added a DNS/Web Content Filtering Module and a Cloud Storage Scanning Module to the mix, rounding off a delectable buffet of cybersecurity enhancements. Oh, and did we mention our venture into Managed Detection and Response (MDR) services? We just can’t help ourselves!

Act VIII: The Mobile Frontier (2023 and beyond)

As we set our sights on the future, 2023 marked our foray into Mobile Protection for iOS, Android, and Chromebook platforms. The introduction of an Application Block Module gave administrators even greater control over app installations on devices.

As we continue to innovate and expand our offerings, we’re committed to rolling out products that enable resource-constrained IT professionals to save valuable time and resources while being protected from the latest threats. Upcoming offerings include enabling centralized administration on-the-go, extending award-winning protection to more threat vectors, and providing continuous monitoring and guidance so that IT people can easily secure their environments while focusing on other critical tasks.

Curtain Call

From a humble anti-malware solution in 2008 to the leading provider of business cybersecurity in 2023, Malwarebytes’ story is one of tenacity, innovation, and the occasional dad joke. As we celebrate our 15th anniversary, we look back with pride and look forward with anticipation, knowing that the best is yet to come.

Keep an eye on our blog and press center for the latest goodness for Malwarebytes for Business!


[ad_2]
Source link

Microsoft Edge Workspace allows you to share your browser tabs

0
[ad_1]

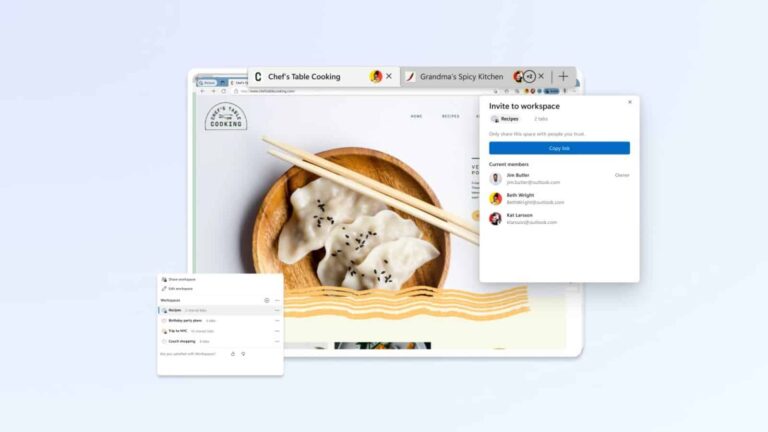
The new Microsoft Edge Workspace feature is becoming available to some users for testing. This new testing version brings a clearer picture of what the feature is all about. If you collaborate with colleagues or classmates on lots of topics, then you might need to pay close attention to this article.

From the latest public preview of this feature, users can finally get a glimpse of its functions. The new workspace function makes cross-collaboration easy within a team working on a project. It does this by letting members of the team share their browser tabs with others.

This makes it easier to get your project research sources vetted by other members of your team. But there are a few things to take note of before rushing in to make use of this new workspace feature. In this article, you will get to know more about this feature and how you can put it to good use.

Microsoft Edge Workspace takes cross-collaboration to a new level

Are you struggling with getting information on your research work across to your team? If yes, you might need to put the Microsoft Edge Workspace feature to good use once available. With this feature, you can bring together a ton of web pages under a labelled group and then share the group with others.

Users can add a name or label these groups for easy identification while sharing. For visual identification, users can also add colours to point out each group in case they have more than one saved. So, what are the procedures to take before opening a new workspace to share with team members?

The first step to take is to open a new workspace tab, failure to do this will mean your progress won’t be saved. With the most recent update, the workspace tab sits at the top left-hand corner of the screen. Once your new workspace tab is open, you can start your research and open as many web pages as you wish.

It is advisable to name your workspace and add colour to make it stand out from other workspace tabs you might have saved. When your research is complete, you can share it with others by clicking the “Invite” button. This will pull up a small window and you are to select “Copy Link” and send it to team members.

Those you are sharing this link to need to have the Edge browser to view the workspace. Once anyone clicks on the link you send and accepts the invite, you’d get notified. Their name and icon will pop up on your workspace, so you can know those that viewed your research work.

Students and other professionals will find this feature interesting as it improves teamwork. Only a preview for this feature is available for download at this moment and you can get it now. Step up your working experience with the new Microsoft Edge Workspace feature.


[ad_2]
Source link

Twitter blocks access to its API, even for those willing to pay

0
[ad_1]

Twitter seems to have officially cut off free access to its API. Over the past few days, several developers have reported that their third-party Twitter clients have stopped working. This ban also affects many researchers, journalists, academic institutions, bot makers, nonprofits, and other developers that use Twitter’s API for various purposes. The company has already announced multiple paid tiers of its APIs.

Twitter has been working on this change since early this year. In mid-January, it abruptly blocked third-party clients without any warning or notice. The company later announced that it would not allow free access to its APIs to anyone. Developers would require to pay to use its APIs. The paid API was supposed to be available in early February but was delayed indefinitely as Twitter needed more time to complete the redesign.

Finally, Twitter announced its new paid API tiers in late March. It did keep a “Free” tier, but with little access. The company said it’s designed for “write-only use cases and testing the Twitter API”. The new free version of Twitter API offered too little for many developers to continue their work without paying the social media giant anything. Unsurprisingly, they decided to shut down their projects.

For those willing to pay, Twitter launched a $100 per month “Basic” tier that is ideal for “hobbyists or prototypes”. The “Enterprise” tier, on the other hand, is for “businesses and scaled commercial projects”. It will have varying monthly subscription plans, likely based on individual use cases. Reports say the Enterprise tier could start at a staggering $42,000 per month.

Twitter has now blocked access to the old free version of its API

A week after this announcement, Twitter has now shut down the existing free version of its API. Everyone, including those willing to pay the exorbitant cost of the Enterprise tier, has lost access. Developers say they have already signed up for the paid version. But instead of making necessary changes to their API access, Twitter has cut off access entirely without notice.

“When Twitter announced these new tiers last week, we immediately sought to sign up for the Enterprise tier,” Echobox said in a recent . “We still have had no response from Twitter’s enterprise sales team and our access to the API was cut off without notice yesterday”. Likewise, Twitter has many suspended third-party clients that signed up for the Enterprise tier. These include Tweet Deleter, Tweet Hunter, Tweet Archivist, Tweet Shelf, and more. As of this writing, Twitter hasn’t said a word on the matter. We will let you know as soon as we have more information.


[ad_2]
Source link