Chinese Hackers Using KEYPLUG Backdoor

0
[ad_1]
Chinese HackerscKEYPLUG Backdoor

It has been reported by the Recorded Future’s Insikt Group that RedGolf, a Chinese state-sponsored threat actor group, was using a backdoor designed especially for Windows and Linux systems called KEYPLUG to infiltrate networks.

As one of the world’s most prolific threat groups, RedGolf has been active against a variety of industries around the world for many years.

RedGolf Infrastructure & TTPs

There is a history of this group developing and using a variety of custom malware families over the years. It has demonstrated an ability to weaponize newly reported vulnerabilities quickly.
Here below, we have mentioned the recently reported malware families used by this group:-
The industries and organizations primarily targeted by RedGolf are:-

  • Aviation
  • Automotive
  • Education
  • Government
  • Media
  • Information technology
  • Religious organizations

Apart from this, there are a number of public and zero-day flaws that the RedGolf threat group has historically exploited for the purpose of gaining initial access to internet-facing devices, including:-

KEYPLUG Malware

During 2021 and 2022, RedGolf targeted US state government entities using KEYPLUG, a custom and modular Linux backdoor.

Several KEYPLUG samples and infrastructures that RedGolf used from at least 2021 until 2023 have been identified by Insikt Group.

In a campaign that compromised the security of at least six state governments in the USA, RedGolf heavily used the KEYPLUG platform between May 2021 and February 2022, as first exposed by Google-owned Manidant in March 2022.

KEYPLUG C2, including the following, supports a total of 5 network protocols:-

Technical Analysis

In October 2022, Malwarebytes published information on a separate set of attacks exploiting an unexplored implant dubbed DBoxAgent to use KEYPLUG on government entities in Sri Lanka early in August of that year.

As Recorded Future puts it, these campaigns appear to share a very close connection with RedGolf’s campaign, which was also attributed to Winnti  (aka APT41, Barium, Bronze Atlas, or Wicked Panda).

According to security analysts, the latest RedGolf activity has not yet been associated with any specific victimology.

Due to the overlaps between this action and previously reported cyber espionage campaigns, they believe these activities may be conducted for intelligence purposes instead of financial gain or profit.

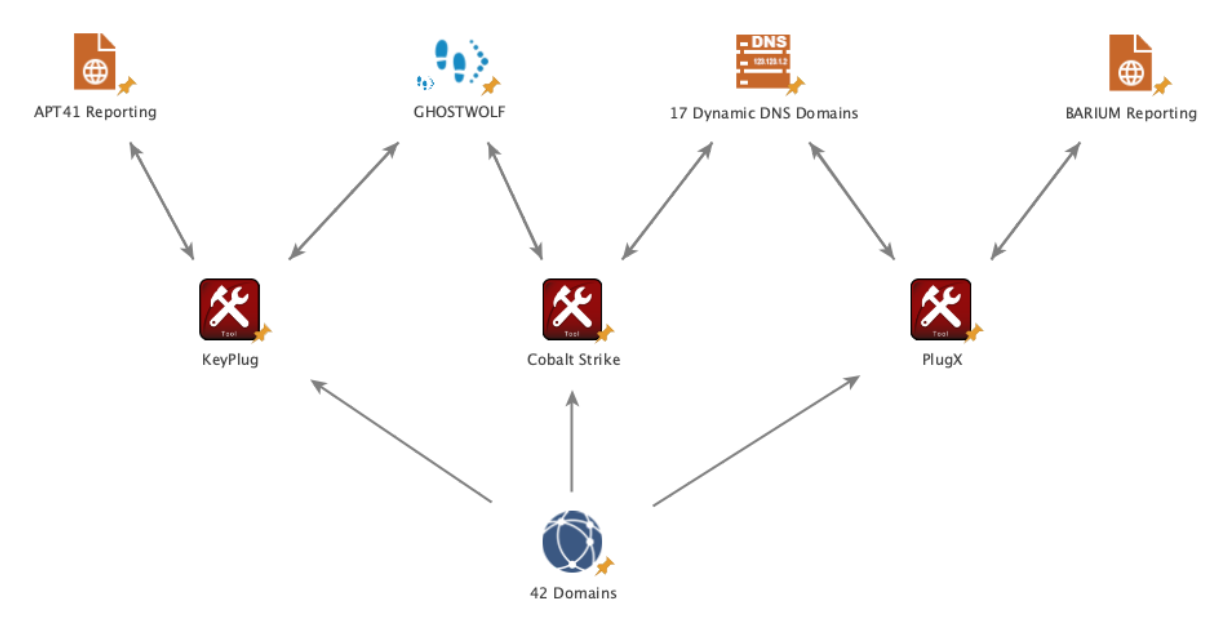
Furthermore, it was noted that the hacking group used other tools such as Cobalt Strike and PlugX in addition to the KEYPLUG samples and its operational infrastructure, which is codenamed GhostWolf.

42 IP addresses comprise the GhostWolf infrastructure and are used as commands and controls for the KEYPLUG system.

To gain initial access to targets’ networks, RedGolf will keep demonstrating the operational tempo that will allow it to rapidly exploit vulnerabilities in externally facing enterprise appliances and quickly weaponize those vulnerabilities.

Recommendation

To defend against RedGolf attacks, organizations are required to follow the mitigations recommended by the experts that we have mentioned below:-

  • Ensure that patches are applied regularly.
  • Check access to the devices connected to the networks external to the organization.
  • Identify the command and control infrastructure used by threat actors and block it.
  • To monitor for malware, intrusion detection, and prevention systems need to be configured in a way that they detect malware.

Searching to secure your APIs? – Try Free API Penetration Testing

Related Read:


[ad_2]
Source link
Several Moto phones gain Google ARCore support

0
[ad_1]

AI might be the main buzzword of 2023, but AR is still relevant. Google supports AR developers, and that’s why it adds devices to its ARCore list. Well, according to Android Police, Google added several Moto phones to its ARCore list.

You can develop AR applications for Android devices, but you want to be sure that most of them can run it. This is where the ARCore list comes in. Google will take devices and certify that their hardware is up to par with a certain standard. If the device passes, then you know that it’ll most likely run your application.

Several Moto devices were added to the ARCore list

Motorola hasn’t been gracing the headlines as it did back in the day. The company, like most, is being overshadowed by the likes of Google, Samsung, and Apple. However, that’s nothing new. However, it’s still able to make a bit of a buzz with its new devices.

Google certified six more Moto phones for its ARCore program. This means that these phones’ cameras and motion-tracking are on par. Not only that, but it also means that their processors are powerful enough to handle the load of AR applications.

This list consists of the Motorola Edge (2022), Motorola G32, Motorola Edge 30 Fusion, Motorola Edge Neo, Motorola Edge 30 Ultra, and Motorola Razr (2022). While it seems odd that a person would want to use a foldable phone for AR, it’s on the list.

Along with these Motorola phones, there are other phones on this list, and they include the OnePlus 10T, Oppo F21s Pro 5G, Xiaomi 12T Pro, Xiaomi Redmi Note 11 Pro+, and so on.

What’s next for Motorola?

If you’re a Motorola fan, then you should know that the company is working on bringing some new powerful devices to the smartphone market. Right now, we’re following rumors and leaks about the Motorola Edge 40 phones. If you’re interested in knowing more information about these phones, you can click here.


[ad_2]
Source link

iPhone 15 Pro solid-state buttons will be customizable

0
[ad_1]

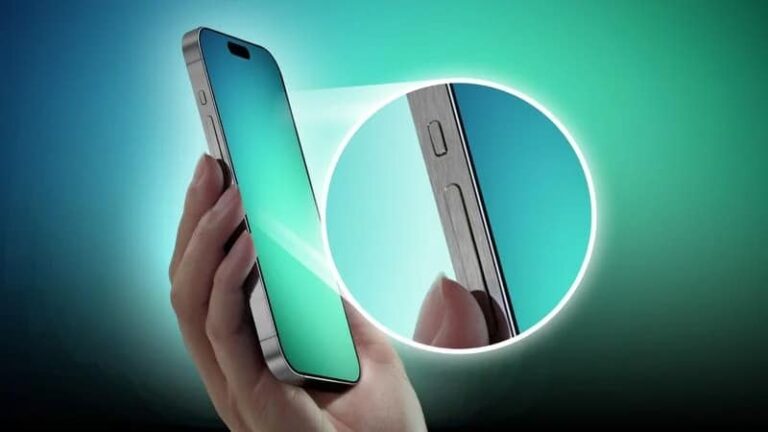
The iPhone 15 Pro series will include solid-state buttons, and they will be customizable. We knew that solid-state buttons are coming, but the second part of that sentence is kind of new.

This info comes from ‘hitherto’, which MacRumors claims is a reliable source. He shared new information on MacRumors forums. The tipster said that the ‘Pro’ models will feature a new sensitivity toggle in the Settings.

The iPhone 15 Pro series is set to offer customizable solid-state buttons

That toggle will allow users to customize buttons to work properly with cases, gloves, and so on. The usual case makers will probably get further instructions from Apple regarding the whole situation.

These buttons will use a new Force Touch-style mechanism and Taptic Engine feedback. It’s also worth noting that the source who shared this info is the same one that revealed that iPhone 15 Pro models will use a new ultra-low energy chip. That chip will allow solid-state buttons to remain functional when your phone runs out of battery.

So, just to be clear, the iPhone 15 Pro models will not only have solid-state power and volume rocker buttons, but the alert slider is also becoming a thing of the past. It will be replaced by an ‘Action’ button, which will have a similar goal, but it’ll feel different to use.

The ‘Pro’ series will also include a periscope camera, it seems

The iPhone 15 Pro and Pro Max/Ultra are also tipped to include a periscope camera. That camera will seemingly replace the 3x telephoto camera on current-gen models.

All iPhone 15 models will feature a Dynamic Island, and a Type-C port at the bottom. Apple may limit that Type-C port, though, and require special cables to either use it at all, or use it to its full capability.

Apple will announce its brand new iPhones later this year, in September. Four models are expected, the iPhone 15, iPhone 15 Plus, iPhone 15 Pro, and iPhone 15 Pro Max/Ultra.


[ad_2]
Source link

You can now virtually try out a Samsung device, right from your iPhone

0
[ad_1]

Samsung really wants iPhone users to get a taste of what using a Samsung device is like, and to make sure of it, it has released a new web app that allows them to try out the One UI interface right from their existing devices.

As reported by 9to5Google, the new “Try Galaxy” demo tool. can be accessed directly from its website, where you are then prompted to scan a QR code for the link to access the experience. The demo features a selection of interactive apps and features drawn from across the One UI platform, specifically One UI 5.1 on the Galaxy S23, Galaxy Z Flip 4, and Galaxy Z Fold 4 devices.
The “Try Galaxy” app was launched a year ago to highlight the features found in the One UI platform and was recently updated to include more elements from the Galaxy experience, such as the camera, the performance, and the connected ecosystem. However, this latest update is mostly focusing on enticing iPhone users as it is no longer usable with other Android devices.

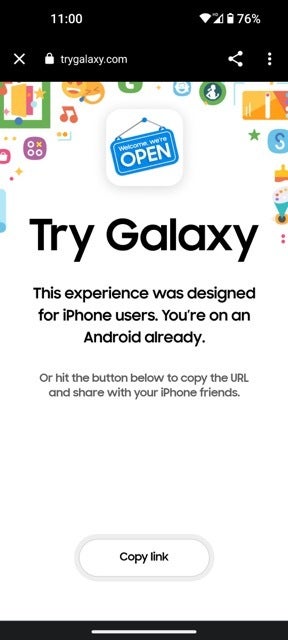
Currently, accessing the website from another Android device will return a message stating that the experience was designed specifically for iPhone users, alluding to the fact that Samsung is not interested in using this app to lure users away from other Android devices, such as the Pixel.

However, when using an iPhone, you are given access to a comprehensive demo of One UI, including the ability to use themes and even SMS – using fake text messages that is. Interestingly, RCS messaging is not shown on this demo, which seems like an odd omission. Additionally, you can try more of Samsung’s core apps such as the object eraser tool, Samsung Health, Smart Switch, and Kids Mode.

Overall, the Samsung Galaxy Demo is an excellent opportunity for iPhone users to get a feel for the interface that is known as One UI. The demo is intuitive to use and packed with a variety of features that give users the ability to personalize the user experience in accordance with their preferences. The demo is also compatible with any model of iPhone that is running iOS 15 or newer and an excellent method to get a feel for One UI before making any purchasing decisions.

[ad_2]
Source link

Study Reveals WiFi Protocol Vulnerability Exposing Network Traffic

0
[ad_1]

Researchers have discovered a major security vulnerability in the WiFi protocol that risks data exposure to snoopers. They demonstrated two attack strategies exploiting the flaw, which could allow an adversary to meddle with traffic, client connections, and more.

WiFi Protocol Vulnerability Exposes Data

According to a recent study, the existing WiFi protocol IEEE 802.11 has an innate security vulnerability in its design that risks users’ privacy. The researchers from Northeastern University and imec-DistriNet, KU Leuven, have shared their findings in a detailed research paper.

The researchers observed the flaw in the WiFi protocol’s built-in power-save mechanisms that conserve power for receiving devices in sleep mode. During such phases, the WiFi devices buffer or queue WiFi frames, however, in a rather unsecured state. That’s because the 802.11 standards lack appropriate security contexts for buffered frames.

Hence, an adversary may trick an access point into leaking frames in plaintext, exposing users’ data. The adversary may also manipulate the WiFi frames’ header to disconnect the target client (receiving device) or induce a denial of service.

Moreover, an attacker may also trick target access points to encrypt frames before queuing, thus evading WiFi’s encryption.

To demonstrate this vulnerability, the researchers designed different attack strategies, which they confirmed to work against a wide range of operating systems. At the same time, they used WiFi devices from popular vendors, such as Cisco, Asus, and D-Link, in their study. The team also made the exploit code public on GitHub as MacStealer tool.

Following this research’s public disclosure, Cisco acknowledged the matter via a dedicated advisory. Besides admitting the vulnerability’s impact on its WiFi devices, Cisco also confirms the proposed remedial strategies from the researchers to be working for Cisco devices. Also, they recommend implementing TLS encryption on the data in transit to render any intercepted data unusable for potential attackers.

The researchers will present their findings at BlackHat Asia 2023, scheduled for May 9-12, 2023.

Let us know your thoughts in the comments.


[ad_2]
Source link

Amazon’s 4-Series Fire TV models are heavily discounted

0
[ad_1]

If you’ve been looking for a TV lately, then Amazon has you covered. Today, it is discounting its 4-Series Fire TV models, by a pretty wide margin. Some of the models are at all-time lows right now. Which is really impressive. Right now the 43″ model is on sale for $239, that’s down from $369. While the 50″ is down to $259, from its regular price of $449. And finally, the 55″ model is down to just $339, which is down from its regular price of $519.

Amazon 4-Series Fire TV – Amazon

Why should you buy the Amazon 4-Series Fire TV?

You’re probably wondering why you would want to buy the Amazon 4-Series Fire TV? Well, aside from the price, these are actually really good TVs. Despite being part of Amazon’s mid-range TV lineup, they are worth picking up for a second bedroom, or even in your main entertainment space.

As mentioned above, the 4-Series does come in three sizes, 43-, 50-, and 55-inches. So not the largest, nor the smallest in TV sizes here. But definitely something for everyone.

These are 4K TVs, with HDMI 2.0 included. There’s also a HDMI 2.1 eARC port included, but it does not support [email protected] for gaming, unfortunately. And that’s because the TV actually only does 60Hz.

There’s HDR support here with HDR10, but no Dolby Vision. Amazon saves the Dolby Vision for its higher-end TVs, which makes sense. At this price, you wouldn’t really expect to have Dolby Vision.

On the audio side, there is support for Dolby Digital Plus. It’s okay, but not the best there is. TV speakers in general aren’t that great. So if you want to get Dolby Atmos, you can hook up a soundbar to this TV, using that HDMI eARC port found on it.

Finally, it is running on Fire TV. Giving you access to all of your favorite apps. These include Amazon Prime Video, Netflix, YouTube, YouTube TV, Hulu and so much more. It also has Alexa included, and Alexa is always-listening. Now you can turn that off if you wish. Then you’ll need to press the microphone button the remote to access it.

The Amazon 4-Series are really great TVs to have in your home, especially at these prices.


[ad_2]
Source link

Heat alerts are coming to Google search within the year

0
[ad_1]

Considering the surge in temperatures around the world, Google search plans to roll out heat alerts. This feature will come in handy for locals as well as those visiting an area at any time of the year. Making use of this feature will be straightforward as it will only require users to search for a keyword.

In this case, that keyword will be ‘heatwave’ and it will pull up the temperature of various areas. It can be your exact location or a place that you wish to visit or are just curious about. Armed with this tool, you will be able to stay clear of areas where there is a temperature surge.

This is an innovative idea from Google, and it will also be a functional feature. Some representatives from Google have also shared a thing or two about this coming feature and what users can expect. There are also a few other existing features similar to this that netizens can also put to good use.

Get notified on temperature surges with the heat alerts coming to Google search

This amazing feature will be available for use in certain regions in the coming months. The senior director of products for health and social impact at Google search, Hema Budaraju, has confirmed the coming of this feature. It aims at helping people adapt to the climate changes currently plaguing the world.

Over the past few years, the temperature in most areas of the world has seen a significant spike. This can come as a shock to tourists and locals who haven’t been keeping up to date with the local news. Most people don’t turn on the TV to check what the weather will be like, but they are constantly on their smartphones.

It will make a lot of sense to give such people weather alerts directly to their smartphones. This is exactly what Google search is doing with the coming heat alerts feature. So, instead of turning on the TV to check the weather forecast, you can simply search ‘heatwave’ via the Google app and get the temperature of your area.

If the temperature in your region is high, you will get an alert informing you to stay indoors. Knowing that heat is now the leading cause of weather-related casualties, it is good to have a feature like this. Tourists or those aiming to travel for different purposes to regions with soaring temperatures will also get alerts not to make that trip.

Once available, this feature will help protect the lives of millions of Google search users. The heat alert Google search feature will be joining the flood and wildfire alert features that launched some months ago. This shows Google’s technological efforts toward improving the health of its users.


[ad_2]
Source link

A Twitter competitor is offering checkmarks to all that may lose them in April

0
[ad_1]
Twitter is in a turbulent period of growth, thanks to all of the changes that Elon Musk is making to the social media platform. But the competition — which is ever growing — is taking all of this as an opportunity to increase their user bases substantially.

Twitter Blue — the subscription service that grants users the ever-coveted blue checkmark — has launched, but its full effects are due on April 1. Just in time for April fools, everyone who has earned a checkmark will be forced to pay in order to keep it. Quite the number, eh?

But ex-Twitter employees aren’t just sitting around, doing nothing about it. The company’s previous CEO is launching his own version of Twitter, called Bluesky. But while that platform is still under development, T2 — an invite-only alternative, also founded by Twitter employees — has rushed to launch in order to seize this unique opportunity.

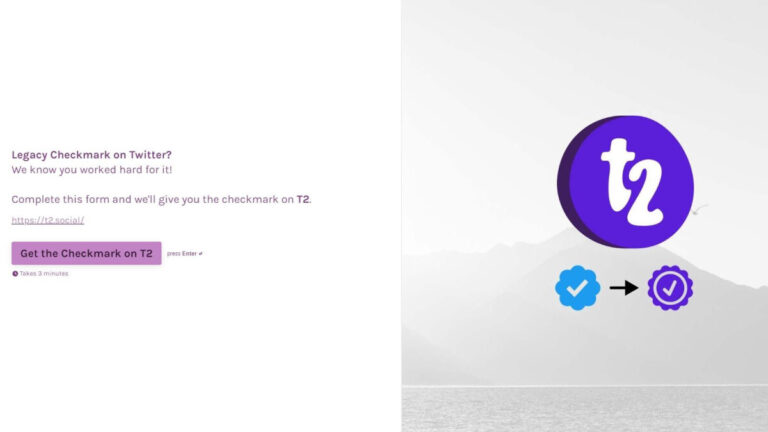
So, T2’s plan is pretty simple: the platform is offering a free verified checkmark on their service, to anyone, who has previously earned it on Twitter. Naturally, this is a limited time offer, as after the upcoming changes, that data won’t be available anymore. This also means that anyone who’s taken advantage of Twitter Blue won’t make the cut in T2’s eyes.

An important note here is that this will carry over for anyone, who is still on the T2 waitlist too. Said wait may be worth it too, as the company has been teasing some upcoming changes. A redesign, for starters, and other milestones too, introduced by the newly-onboarded ex-Discord exec, who is acting as T2’s CTO (chief technology officer).

It will take quite a lot of time, effort and updates to get anywhere near Twitter’s core user base, but providing something of immense value for free is a great way to lure users in. After all, possibly thousands will be losing their checkmark in less than a day. Why not gain something out of it? After all, it’s free.


[ad_2]
Source link

Smart home assistants at risk from NUIT ultrasound attack

0
[ad_1]

We take a look at research for an IoT attack called NUIT, capable of hijacking voice assistants via ultrasonic attack.

A new form of attack named “Near Ultrasound Inaudible Trojan” (NUIT) has been unveiled by researchers from the University of Texas. NUIT is designed to attack voice assistants with malicious commands remotely via the internet.

Impacted assistants include Siri, Alexa, Cortana, and Google Assistant.

This attack relies on abusing the high sensitivity of microphones found in these IoT devices. They’re able to pick up what is described as the “near-ultrasound” frequency range (16kHz – 20kHz), and this is where NUIT lurks.

A NUIT sound clip can be played on the targeted device’s speaker which allows for the voice assistant to be attacked on the device itself, or even another device altogether.

There are 2 different ways to launch this attack. One is where NUIT is happening on the targeted device itself. This could be, for example, a rogue app or an audio file. Below you can see a video where the NUIT attack results in an unlocked door.

The second form of attack is where the first device containing a speaker is used to communicate with a second device containing a microphone. This is the daisy-chain style approach, where all of the cool technology in all of your devices slowly comes back to haunt you. As researchers note, a smart TV contains a speaker and a quick blast of YouTube could be all that’s needed. Even unmuting a device during a Zoom call could be enough to send the attack signal to your phone sitting next to the computer as the meeting is taking place.

In terms of being successful via NUIT attack, social engineering plays a large part. Bogus websites, apps, and audio could all be entry points for voice assistant shenanigans.

Once access to a device is gained, an attacker lowers the device’s volume. This is so the device owner is unable to hear the assistant responding to commands being sent its way. Meanwhile, the speaker needs to be above a specific noise level so the attack can actually take place. As long as all of this takes place, the bogus command length has to be below 77 milliseconds or it won’t work.

In terms of current impact, researchers say that Siri devices “need to steal the user’s voice”. Meanwhile, the other 16 devices tested can be activated through use of a robot voice or indeed any other voice at all for that matter.

The NUIT attack is listed as being due to appear at the upcoming USENIX Security Symposium in August, which will give a complete overview of how this works. For now, the advice for possible defences against this new form of attack listed by the researchers include the following:

  • Use earphones. If the microphone can’t receive malicious commands, then the compromise can’t take place.
  • Awareness is key. Be careful around links, apps, and microphone permissions.
  • Make use of voice authentication. If you’re on an Apple device, now is the time to fire that up.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

OPPO Find N3 may lose its charm by being larger than expected

0
[ad_1]

OPPO released two book-style foldables thus far, the Find N and Find N2. The OPPO Find N3 is expected to launch later this year, and it may be larger than expected.

The fact the OPPO Find N and Find N2 were so compact was a part of their charm. When folded, they are perfect for one-handed use, when unfolded, you have a large 7.1-inch display to work with.

Those two phones managed to interest quite a few people, even though they only launched in China. I’ve reviewed both devices, and they do feel entirely different to use than any other book-style foldable, in a good way. On top of that, the build quality is outstanding.

The OPPO Find N3 may be larger than expected with an 8-inch display

Based on the latest rumors, however, the OPPO Find N3 may be larger than its predecessors. This info comes from Digital Chat Station, a well-known Chinese tipster. He claims that an 8-inch main display will be included. It will allegedly offer a resolution of 2268 x 2440 pixels, and a 120Hz refresh rate.

If true, that would basically bring the phone to the level of the Galaxy Z Fold 4 and other book-style foldable in terms of size. For some, that’s great, for others, not so much. The OPPO Find N and Find N2 were basically the only ones in the segment. Not a single other book-style foldable was close size-wise.

The Snapdragon 8 Gen 2 SoC is also rumored

In any case, the tipster shared some more info about the device. He claims that the Snapdragon 8 Gen 2 will fuel the phone. On top of that, a 50-megapixel main camera (Sony’s IM890 sensor) is tipped, along with a 48-megapixel ultrawide camera (Sony’s IMX581 sensor), and a 32-megapixel telephoto camera.

20-megapixel and 32-megapixel selfie cameras were also mentioned by the tipster. The same goes for a 4,805mAh battery. The Find N3 will be very thin, if the tipster is to be believed.

It remains to be seen if this info is accurate, though. The Find N3 is not expected to arrive until the very end of the year.


[ad_2]
Source link