BFSI Sector at the Forefront of Cyberattacks

0
[ad_1]
BFSI Sector

In recent years, the BFSI Sector (Banking, Financial Services, and Insurance) has become a primary target for cyber attackers.

A 2022 report by IBM revealed that the average cost of a data breach in the financial industry reached a staggering $5.97 million per incident. The New York Federal Reserve reports that financial institutions face 300 times more cyber attacks than other industries. 

It’s a concerning trend that underscores the urgent need for stronger BFSI cybersecurity measures.

Why Do Attackers Target the BFSI Sector?

There are several reasons why attackers target this sector, and the trend is only increasing, posing an alarming threat to the industry.
The BFSI sector has always been a lucrative target for cybercriminals due to the vast amounts of sensitive financial and personal data it holds. With technological advancements, banks, and financial institutions have significantly invested in digital infrastructure, making them more vulnerable to cyber-attacks.

The rising adoption of online banking, mobile payments, and other digital financial services has provided new avenues for cybercriminals to launch attacks.

Attackers can exploit vulnerabilities in banking systems to gain unauthorized access to financial and personal data, which they can use to conduct identity theft, fraud, and other malicious activities.

The COVID-19 pandemic has accelerated the digital transformation of the BFSI sector, resulting in an increased reliance on digital channels for financial transactions. This has led to a rise in cyber attacks targeting the industry, as attackers have become more adept at exploiting vulnerabilities in digital systems.

The rising risk owing to the increasing number of smartphone users, growing adoption of connected devices, and surging e-commerce sector has increased the security concerns in the BFSI market. 

The BFSI sector is often seen as a symbol of power and influence, making it an attractive target for hacktivists and nation-state actors. These attackers may have political or ideological motives, such as disrupting the financial systems of a particular country or stealing financial data for espionage purposes.

The BFSI sector is heavily regulated, and attackers may target it to create reputational damage or demonstrate regulatory compliance vulnerabilities. This can lead to legal and financial consequences for the targeted organizations.

Attackers have become increasingly sophisticated in their methods, and the BFSI sector remains one of the most challenging to defend against cyber attacks. The BFSI sector faces many threats, including phishing attacks, ransomware attacks, and distributed denial of service (DDoS) attacks. These attacks are often well-funded and well-organized, making it difficult for organizations to defend themselves effectively.

The implications of a successful cyber attack on the BFSI sector can be catastrophic. A single attack can lead to massive financial losses, reputational damage, and loss of customer trust. For example, a successful ransomware attack can cripple banking systems, causing significant disruption to financial markets and the broader economy.

Biggest Cybersecurity Threats Faced by BFSI Sector

Phishing Attacks

Phishing attacks are one of the most common cyberattacks in the BFSI sector. In a phishing attack, cybercriminals use emails or other digital communication channels to trick individuals into providing sensitive information. 

Phishing attacks often target customers of banks and other financial institutions by posing as legitimate entities, such as the bank or a financial institution. Once the customer provides their information, cybercriminals can use it for fraudulent activities.

Ransomware Attacks

Ransomware attacks on banks rose by 1318% in the first half of 2021, with U.S. banks paying around $1.2 billion in ransomware payments. 

In a ransomware attack, cybercriminals use malware to encrypt the victim’s data, making it inaccessible. The attackers then demand a ransom in exchange for the decryption key. 

Ransomware attacks on the BFSI sector can be particularly damaging as they can disrupt financial operations and compromise customer data.

Malware

Malware attacks are also a significant threat to the BFSI sector. Malware is software designed to harm computer systems, steal data, or disrupt operations. Malware attacks can be launched through various methods, including email attachments, malicious links, and infected websites. 

Malware attacks on the BFSI sector can lead to financial loss, reputational damage, and legal liabilities.

DDoS and Web App Attacks

A DDoS attack is when hackers attempt to break into your systems by paralyzing them with traffic. The main target is to get personal data while the organization analyzes and diagnoses the crashed web app. 

Botnets and zombie computers organize an attack against a particular network. DDoS attacks’ most significant strength is the speed with which the information is transferred and stolen. Another variant of these attacks is ransomware, which can steal data without the user’s knowledge.  

Vulnerability Exploitation

Attackers may look for vulnerabilities in the BFSI sector, including exploiting software vulnerabilities.

The state of application security report for Q4 2022 revealed that AppTrana WAF detected over 61,000 vulnerabilities, including over 1,700 critical and high-risk ones that remained open for over 180 days. 

It is crucial to patch these vulnerabilities promptly to mitigate potential risks. Virtual patching can effectively mitigate the risks by providing immediate security measures to address the vulnerabilities before attackers can exploit them.

Major BFSI Data Breaches

Let’s look at some high-profile data-breach cases that affected top BFSI companies and their impact on the same.

Morgan Stanley Data Breach- July 2021

Morgan Stanley is a multi-national banking giant in the BFSI sector; the breach was revealed on July 2nd, 2021. It impacted millions of records of their corporate clients’ data. It involved a third-party vendor, Guidehouse, which provided account maintenance. 

The attackers accessed information by exploiting a vulnerability in the vendor’s server. The team patched the vulnerability within five days.  

Robinhood Data breach- November 2021

Robinhood rose to fame for the wallstreetbets controversy and later stopped people from buying shorted stocks, but in November of 2021, they were in the news for yet another reason. With about 18.9 million retail clients, a breach exposed the sensitive information of more than 7 million customers. 

A vishing call led to the breach as one of the company’s customer representatives was misled into revealing critical information. This transpired into an investigation and a $20 Million fine on Robinhood. Training employees on threat awareness and cyber security in the banking sector is key to avoiding such a situation. 

Flagstar Data breach – December 2021

In 2021, Flagstar Bank experienced a data breach that compromised thousands of its customers’ personal and financial information. The incident was discovered in January 2021, and the bank immediately launched an investigation.

The data breach reportedly occurred due to a vulnerability in one of Flagstar’s online systems. The attackers were able to exploit this vulnerability and gain access to sensitive customer information, including names, addresses, Social Security numbers, and account numbers.  

Flagstar Bank notified affected customers of the data breach and offered free credit monitoring services. The bank also implemented additional security measures to prevent future data breaches, such as enhancing its network security protocols and strengthening its employee training programs.

9 Ways to Improve cybersecurity in BSFI Sectors

  1. WAF and DDoS Protection are mandatory

BFSI organizations rely heavily on web applications like online banking portals to interact with customers. These web applications are prime targets for cybercriminals, who can exploit vulnerabilities in the application to gain unauthorized access to sensitive data or inject malware. 

Implementing a WAF helps protect against these attacks and reduce the attack surface by blocking malicious traffic before it reaches the web application. 

By adding threat monitoring intelligence systems, financial institutions can gain greater visibility into web-based attacks and enhance their ability to identify and block malicious traffic.

DDoS protection is a solution designed to mitigate the impact of DDoS attacks. It can include traffic monitoring, rate limiting, and specialized hardware or software to filter out malicious traffic. DDoS protection can help prevent downtime and ensure that online services remain available to customers during attacks.

By implementing these measures, BFSI organizations can significantly improve their security posture and protect their customer’s sensitive data and transactions.

  1. Regular Security Audits

Whenever a new feature is launched, or a third-party tool is integrated, vulnerabilities arise from the gaps within integrations as tech teams focus on developing and fixing instead of the cybersecurity perspective. 

Threat actors find exploitable vulnerabilities and classify them according to the flaws in the system, like computers, networks, and communications. 

Regular security audits are essential to identify vulnerabilities in the system and address them before cybercriminals can exploit them. These audits should include a review of security policies, procedures, and controls to ensure they are up-to-date and effective. 

Continuous monitoring of networks, applications, and systems can help identify and mitigate threats before they result in data breaches. Implementing automated monitoring and alert systems can help detect and respond to threats in real time.

  1. Provide Cybersecurity Awareness Training 

Cybercriminals overload the LAN with false address resolution protocol packets (ARP) that help them tap into the traffic routing and redirect it to read the information. The process is called ARP spoofing; it affects the network and communications. Brand spoofing also happens when scammers impersonate a person/corporation to trick users into sharing information and making payments. 

Employees are often the weakest link in the security chain, as they may unwittingly fall prey to phishing scams or other forms of social engineering. Providing regular training on cybersecurity best practices can help reduce the risk of such attacks. This training should cover topics such as password hygiene, recognizing phishing emails, and avoiding suspicious links.

  1. Implement a zero-trust Methodology

Thanks to the zero-trust concept, only those who are permitted to have access are given it. This minimizes the possibility of the hacker gaining access to private data while stealing the credentials. 

Implementing a zero-trust methodology can be a practical step toward enhancing security in the BFSI sector. This methodology assumes that no user or device should be automatically trusted, and all access requests must be carefully scrutinized and verified before granting access.

  1. Regulation of third-party integrations

Third-party integrations are commonly used in the BFSI sector to provide additional functionality and services to customers. While third-party integrations can be beneficial, they can also pose significant security risks. Therefore, regulation of third-party integrations is vital to secure BFSI. 

Third-party risk management is important as it can expose various financial, legal, and reputational risks. Financial companies can request third-party vendors undergo regular audits to verify compliance with applicable laws and regulations.

Third-party integrations often require access to sensitive customer data, including personal and financial information. Therefore, it is essential to regulate third-party integrations to maintain data privacy with numerous legal and regulatory requirements to protect customer data. Regulating third-party integrations can help ensure that these requirements are met and that organizations remain compliant.

  1. Secure mobile applications

The surge in mobile fraud application transactions, which has risen by more than 600% since 2015, highlights the urgent requirement for strong mobile security strategies. While mobile applications provide customers with the convenience of banking from anywhere in the world, the growing number of threats has made customers hesitant to opt for this facility. 

Given the widespread adoption of mobile devices for conducting financial transactions, it is imperative to prioritize the development of secure mobile applications.

  1. Implement Two-Factor Authentication (2FA)

Two-factor authentication is an extra layer of security that requires users to provide two forms of identification before accessing their accounts. This can be done by requiring a password and a verification code sent via text message or a mobile app.

 2FA is an effective way to prevent unauthorized access to sensitive information, as it makes it more difficult for cybercriminals to gain access to accounts even if they have obtained the password.

  1. Use Encryption

Encryption is a reliable method to safeguard confidential information from being accessed without authorization. It involves converting plain text data into an unreadable format using an encryption key. The data can only be deciphered using the key known only to authorized users. Implementing encryption for data at rest and in transit can help protect against data breaches and theft.

  1. Implement Access Controls

Access controls are a crucial component of any security program. They ensure that only authorized users have access to sensitive data and systems. This can be done by implementing role-based access control (RBAC), which assigns users permissions based on their job function. It’s also important to regularly review access controls to ensure they are still appropriate and effective.

In conclusion, the BFSI sector faces an alarming threat from cyber attackers, who are becoming increasingly sophisticated in their methods. Organizations in the sector must take proactive steps to protect themselves from cyber attacks, as the consequences of a successful attack can be severe. By prioritizing cybersecurity and investing in robust security measures, the sector can continue to serve as a critical engine of economic growth and prosperity.


[ad_2]
Source link
Google Pixel 8 Pro Night Sight might be better thanks to this feature

0
[ad_1]

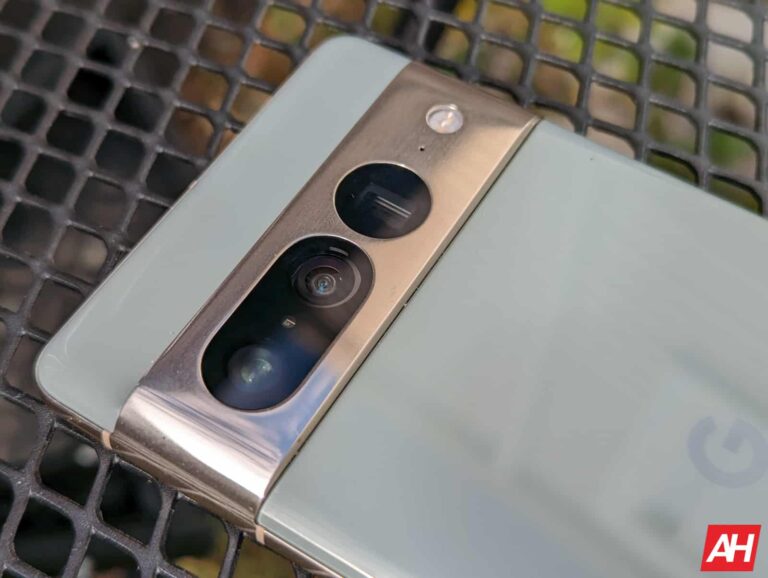
According to available reports, the Google Pixel 8 Pro Night Sight photography feature might get some improvements. If you are a Pixel user, you’d notice first-hand the improvements the brand’s night photography has undergone. With the launch of the Google Tensor processor, photography saw a notable improvement and keeps getting better.

But to firmly establish its place before the competition, there is a need to continue innovating. For this reason, the coming Google Pixel 8 series will pack new and improved photography features. A new report points out the Night Sight feature will also get some improvements.

The sources claim to have spotted a telephoto ability on the Pixel 7 Pro that will make its way to the device’s successor. This ability improves the quality and details of pictures taken with the telephoto camera. They claim that this feature will be adopted into the imaging process when taking night shots with the Pixel 8 Pro.

Multi-camera Super Res Zoom might come to the Google Pixel 8 Pro Night Sight feature

With the launch of the Google Pixel 7 series, the company introduced a new photography feature. They call this the Mulit-camera Super Res Zoom, and it helped users take better telephoto shots. By zooming a little into a shot, the Google Pixel 7 Pro will make use of two camera lenses to take the photo.

The lenses in question are the Main and the Telephoto lens, with both taking shots from different perspectives. A wider frame shot is taken by the main camera and a zoomed-in shot is taken by the telephoto camera. After both photos are taken, they are merged into one picture, providing better quality and more details.

This merging process is done without the user even being aware. The result is the only thing the user sees after hitting the shutter button. Well, it seems like the Google Pixel 8 Pro Night Sight feature will also adopt this imaging process.

Sources claim that the Multi-camera Super Res Zoom will be exclusive to the Google Pixel 8 Pro. According to them, the codename of this night photography feature coming to the Google Pixel 8 Pro is “Hawk” or “FusionZoom.” So not only will this device use this dual camera capturing technology for telephoto shots, but also for night shots.

It will work the same way that it does when taking zoomed-in telephoto shots on the Google Pixel 7 Pro. This feature might even work better since the Google Pixel 8 Pro will launch with a new and more powerful processor. More details on this night photography feature and other details on the Google Pixel 8 series will be made available in the coming months.


[ad_2]
Source link

FuboTV rebrands and hires Ryan Reynolds for new ad campaign

0
[ad_1]

Hot on the heels of selling Mint Mobile to T-Mobile, Ryan Reynolds is joining another company. This time it’s FuboTV, who announced a rebranding today. Essentially removing the “TV” from its name. So now, they are just Fubo.

Fubo is out to make sure that everyone knows that even after this rebrand, it is still the same company and service. Fubo has hired Ryan Reynolds and his Maximum Effort Productions to spearhead the new ad campaign. Which also includes NBA Hall of Famer, Kevin Garnett, and NFL quarterback and commentator Mark Sanchez. It makes sense that Reynolds would bring these two on-board, since Fubo is all about sports.

“fuboTV has grown in size and scope, with multiple brands under our global umbrella, since we launched our core cable TV replacement product in 2015,” Fubo co-founder and CEO David Gandler said. “Alongside our continued growth, our consumers have affectionately shortened our name to Fubo and we feel that name represents the premium media brand we are today. We’re building on this momentum with an updated visual identity and new ad campaign, created in partnership with Ryan Reynolds’ Maximum Effort, to continue to drive profitable growth as we head into baseball season.”

Fubo was the fastest growing live TV streamer in the fourth quarter of 2022

This rebranding is highlighting the company’s emphasis on efficient growth. After growing and adding 224,000 new subscriber additions in the fourth quarter of 2022, they were the fastest growing live TV streamer. That number is actually pretty incredible, seeing as all other streamers added 371,000 in that time frame.

Fubo says that the new logos and branding will start to roll out across Fubo products in the coming months. With this new rebranding launching during the World Baseball Classic and at the start of the MLB season, the new ad campaign is summed up with a single line “If Sports built a streaming service”. And then it highlights what Fubo offers.


[ad_2]
Source link

Pixel Watch is getting the big March 2023 update widely

0
[ad_1]

Last week, Verizon announced that the Pixel Watch is receiving the March 2023 update. However, Google didn’t confirm the rollout from its side. A week later, we now have official confirmation that the big new update is available for the first-gen Google smartwatch.

This month’s update for the Pixel Watch is a massive one. It contains plenty of exciting goodies, not least the fall detection feature that has been in development and testing for the past few months. Following this update, your wrist wearable will be able to detect a hard fall and automatically connect you to emergency services. The automatic dialing feature may be geo-restricted in some markets, though.

Additionally, the Pixel Watch will now show you the time even when the device is turned off due to a low battery. A digital clock will briefly appear on the screen upon crown push, alongside a red low battery indicator. The haptic crown can also turn on AOD (always-on display) after the latest update. This is in addition to the existing ability to enable AOD in the settings on your watch. You can also use the smartphone companion app.

Google has also improved the touch sensitivity of the Pixel Watch display. The battery-saver button in the quick settings gets improvements too, with it now activating in a single tap. As part of the March Feature Drop, the Pixel Watch is picking up mono-audio which limits the disorientation of split audio. New color correction and greyscale modes further optimize the display for various color preferences.

Google says a separate update for the Clock app in the coming weeks will fix the alarm problem in the Pixel Watch. many users have reported that alarms don’t go off on time. Some start ringing early while others go off well after the time. Keep a tab on the Play Store for this update.

The March 2023 update for the Pixel Watch is rolling out widely

The March update for the Pixel Watch comes with the firmware build number RWDA.230114.008.R1, the same that Verizon revealed last week. For users in Japan and Taiwan, it’s RWDA.230114.008.J2. The update is rolling out widely and should be available for all eligible users around the world within the next few days. Along with the aforementioned new features, this release also contains plenty of bug fixes and improvements. You can go to Settings > System > System updates to manually check for new updates for your Pixel Watch.


[ad_2]
Source link

CASPER Attack Targets Air-Gapped Systems Via Internal Speakers

0
[ad_1]

Researchers have found another way that potentially risks the security of air-gapped systems. Dubbed as CASPER attack, the strategy presents a cover channel attack allowing data exfiltration from an air-gapped system via a nearby smartphone.

CASPER Attack Targeting Air-Gapped Systems

Researchers from the School of Cyber Security at Korea University, Seoul, devised the CASPER attack to extract data from air-gapped systems.

According to the researchers, numerous studies have demonstrated how such cover attacks are possible on air-gapped systems using external speakers. However, today, not many computers have external speakers in such a setup. Nonetheless, such systems still remain vulnerable to cyberattacks. That’s what the researchers demonstrated by targeting air-gapped systems with internal speakers on the motherboard.

The attack strategy involves exploiting the internal speakers of an air-gapped system’s motherboard to generate high-frequency sounds carrying the information. A nearby smartphone (within 1.5m) can then serve as a receiving device for those sounds to decipher the data.

In their experiment, the researchers encoded the data in Morse code (for alphabets) or binary code (when transferring images and other files). They used an Ubuntu 20.04.1 64-bit system as the target system infected with malware that allowed them root privileges to exploit the internal speaker and a Galaxy Z Filp3 5G smartphone as the receiver device. The researchers observed the rate of data transference as around 20 bits/second maximum using this method.

Limitations And Countermeasures

Since the CASPER attack typically relies on internal speakers, removing them, or ensuring selective installation of internal speakers can be a countermeasure to prevent this attack. Besides, installing devices to detect unusual signals in inaudible frequencies around air-gapped systems can also help prevent such covert attacks.

As for the limitations, the researchers specifically mentioned the slow data transfer rate which, if not made it impossible, makes it difficult to be used in a real-world attack scenario.

Details about the entire experiment are available in the researchers’ detailed research paper available here.

Let us know your thoughts in the comments.


[ad_2]
Source link

Apple Users in South Korea Can Finally Use Apple Pay 

0
[ad_1]

Apple Pay South Korea

After months of regulatory delays, Apple Pay has finally launched in South Korea, allowing contactless payment using the iPhone, Apple Watch, iPad, and Mac. 

Apple has been working to bring Apple Pay to South Korea but has suffered several setbacks. 

First, the tech giant experienced challenges when registering as an electronic financial business operator in the country. Further delays occurred when regulators had to assess whether Apple Pay violated the Korean payment system.

Despite these challenges, the South Korean financial regulators finally approved Apple Pay in February. Furthermore, a new report revealed that Apple users in the country can start using the payment service today.

“Apple Pay is available from today in South Korea,” says Duncan Olby, who is leading Apple Pay, Wallet, and Payment for international markets, at a press conference in Seoul. “Users can add their credit and debit cards on Wallet for their iPhone, Apple Watch, iPad, and Mac.” 

That said, Apple Pay is currently limited to Hyundai Card users. At the time of writing, no other local card providers have participated in the tech giant’s payment system. 

Here’s a possible reason. 

Low NFC Terminal Adoption Could Hinder Apple Pay in South Korea

Slow NFC (near-field communication) terminal adoption among South Korean retailers could hinder Apple Pay. Indeed a report suggests that only 10 percent of 2.9 million local retailers in the country enabled NFC in their credit card terminals. 

However, a new trend could begin soon. 

According to a Counterpoint report, more retailers are expected to install NFC terminals by the end of the year. The report further suggests that iPhone and Apple Watch users in South Korea will likely switch to Apple Pay, boosting peer competition. These include Samsung Pay, Kakao Pay, and Naver Pay. 

“Many of our users here have been eager to use Apple Pay for their everyday spending in-store, online and in-apps,” says Jennifer Bailey, vice president of Apple Pay and Apple Wallet. “So we are thrilled to roll out and make seamless and secure payments available across top merchants in South Korea.”


[ad_2]
Source link

OPPO Pad 2 tablet announced as a rebranded OnePlus Pad

0
[ad_1]

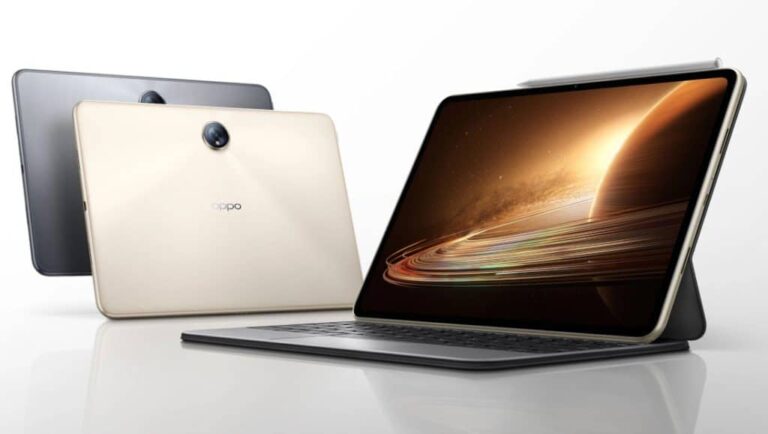
OPPO hosted a press announcement in China today, during which it announced its Find X6 and Find X6 Pro flagship smartphones. The OPPO Pad 2 also got announced during the event, though it was overshadowed by the two phones.

The OPPO Pad 2 is essentially a rebranded OnePlus Pad

It turns out the OPPO Pad 2 tablet is a rebranded OnePlus Pad, as we expected. Not only do the two phones look the same, but they have almost identical spec sheets too.

This tablet is made out of metal and glass, and includes a circular camera island on the back, which has an odd placement. When you hold the device in landscape form, it’s centered up top. That’s not a placement we see on tablets all that often.

The device features an 11.6-inch 2800 x 2000 LCD display with a 144Hz refresh rate. This panel does have Dolby Vision support, and hardware-level blue light reduction too.

It is fueled by the MediaTek Dimensity 900 SoC

The MediaTek Dimensity 9000 SoC fuels this tablet, which is MediaTek’s 4nm processor. The OPPO Pad 2 includes 8GB or 12GB of LPDDR5 RAM, along with 256GB or 512GB of UFS 3.1 flash storage, respectively.

OPPO Pad 2 image 1

Android 13 comes pre-installed on the device, along with ColorOS 13.1 skin. A 9,510mAh battery is also included in the package, and it supports 67W SuperVOOC charging. A 67W charger is included in the box.

This tablet has four speakers, and Dolby Atmos support. It includes a 13-megapixel main camera (f/2.2 aperture), and an 8-megapixel front-facing camera (f/2.0 aperture).

The OPPO Pad 2 comes in two color options, while OPPO announced some accessories for it too

The device supports Bluetooth 5.3, and Wi-Fi 802.11ax. It comes in Light Gold and Nebula Gray color options. This tablet’s pricing starts at CNY2,999 ($436) for the 8GB RAM + 256GB storage variant. It goes all the way up to CNY3,999 ($582) for the 12GB RAM + 512GB storage option.

Now, OPPO also announced a smart touch keyboard alongside this tablet. That keyboard is priced at CNY599 ($87). The OPPO Pencil stylus also got shown off, and it’s priced at CNY499 ($72). There’s no word on the OPPO Pad 2’s global availability, though it most likely won’t launch globally. The OnePlus Pad is basically its global version.

OPPO Pad 2 image 2


[ad_2]
Source link

OnePlus lets you test drive the OnePlus 11 for 100 days

0
[ad_1]

So, OnePlus recently launched the OnePlus 11. It’s an affordable flagship one with some killer features. Now, according to Phone Arena, the company is letting people test out the OnePlus 11 for 100 days to see if they can conform to the “Shape of power”. If they don’t like the phone, the company will return their money.

Not too long after Samsung launched its Galaxy S23 phones, OnePlus hit us with its latest flagship phone. The OnePlus 11 is a powerful and sturdy phone, as we say with Jach Nelson’s durability test. The company has a lot of faith in this phone, so it’s doing what it can to raise awareness of it.

You can try out the OnePlus 11 for 100 days

This is available for US customers of the phone. When you buy the phone, you’ll be able to take advantage of this promotion. You’ll pay for the phone (starting at only $699). However, if you want to return the phone within 100 days of getting it, then the company will give you a full refund.

There are a few things that you need to know before you start adding the phone to your cart. Some of these things are obvious. Now, when you return the device, it will need to be in working condition. Also, it can’t have any cosmetic damage other than typical wear and tear. So, don’t return a broken device.

Now, if you want to take advantage of this deal, you need to register your phone within 15 days of getting it. That’s important to remember, as you won’t get the refund if you don’t.

According to the fine print, you won’t actually have a full 100 days with the phone., The 100 days officially start when the device ships. So, by the time that it actually reaches your hands, a few days will have passed. Lastly, if you want to take advantage of this deal, you’ll need to order your phone by April 30th. That gives you 41 days, so that’s ample time.

What is this phone all about?

The OnePlus 11 has a 6.7-inch 1440p+ AMOLED display that runs at 120Hz. It can reach a peak brightness of 800 nits, as well. Powering the device, we have the Snapdragon 8 Gen 2 SoC backed up by up to 16GB of RAM and up to 512GB of storage.

As for the camera, we have the 50MP main camera with a 32MP telephoto and a 48MP ultrawide camera. Up front, there’s a 16MP selfie camera. Keeping the lights on, there’s a large 5000mAh battery. In the US, it supports 80W fast charging (it’s 100W in other markets)

Order the OnePlus 11


[ad_2]
Source link

iPhone users finally get Material You redesign for Google Translate

0
[ad_1]

It has been almost two years since Google introduced its revamped design language dubbed Material You to Android phone, alongside Android 12. Gradually, all of the Google applications started adopting the new dynamic look and received a visual update to go along with Androids new look. But what about the same Google apps that are available on iOS?
Well, it goes without saying that the applications Google has on Apple‘s App Store had much less priority, which is why for a long time we did not see the Material You redesign come to them. In fact, it is only now that we see the first fully updated app, which in this case happens to be Google Translate.

As for why the company has chosen to refresh Google Translate first is unclear, as there are many other apps that are used daily by a much larger number of iPhone owners.

Here’s how Google Translate looks now on iOS:

As it is with other Material You updates, the buttons and basically everything that you can tap on now takes more of the screen real estate, making it easier for the user to navigate the UI. This also makes the overall look of the app arguably cleaner and more simple to look at.

Here is how the app used to look before Google released the server-side update to introduce Material You:

All of the functionalities have been kept, as you can see. The main difference is in the app’s focus, which is now placed more heavily on input. It is easier to initiate a translation via voice, typing, or handwriting after tapping on the pen icon. The shrift is bigger and much more readable than before too.

Of course, this being a Google application on an iOS device, there are some features missing that are present on the Android version. One of them is the ability to long-press on languages to swap languages. You also cannot swipe down on while in the main screen.

One last small note is that while on the Android version of Google Translate the app adapts the color for accents to the wallpaper the phone is using, here it just defaults to blue. None of these missing functionalities, however, are too significant for the end user experience.


[ad_2]
Source link

Ferrari Hacked – Attackers Gained Access to IT Systems

0
[ad_1]

A threat actor recently contacted Ferrari S.p.A., an Italian luxury sports car manufacturer headquartered in Maranello, demanding a ransom for access to specific client contact information.

The company suffered a significant data breach, and consumers’ personal information may now be at risk. According to reports, a hacker accessed the company’s IT system and demanded a ransom for the information.

“We regret to inform you of a cyber incident at Ferrari, where a threat actor was able to access a limited number of systems in our IT environment,” in breach notification letters to customers, Ferrari makes this statement.

Information Exposed in the Breach

According to the company, customers’ names, addresses, phone numbers, and email addresses were among the information exposed in the breach.

Ferrari has not yet discovered evidence that payment information, bank account numbers, or other private payment information were accessed or compromised.

Ferrari breach notification letter

The firm confirms that the hack did not affect the company’s operational processes.

Threat Actor Demanding a Ransom

“Ferrari S.p.A., its wholly-owned Italian subsidiary, was recently contacted by a threat actor with a ransom demand related to certain client contact details,” says the company

“Upon receipt of the ransom demand, we immediately started an investigation in collaboration with a leading global third-party cybersecurity firm.”

Ferrari states this is against company policy because paying ransoms supports criminal activity and allows threat actors to continue their attacks.

“As a policy, Ferrari will not be held to ransom as paying such demands funds criminal activity and enables threat actors to perpetuate their attacks,” the company added.

Reports say that upon discovering the breach, Ferrari also informed the appropriate authorities about the incident and is collaborating with a cybersecurity firm to determine the extent of the consequences.

The company claims it has collaborated with third-party experts to strengthen its systems further and is confident in its resilience.

“We believed the best course of action was to inform our clients and thus we have notified our customers of the potential data exposure and the nature of the incident,” says the company.

Network Security Checklist – Download Free E-Book

Related Read

RansomEXX Gang Hacked Ferrari – Over 7GB of Internal Documents Stolen


[ad_2]
Source link