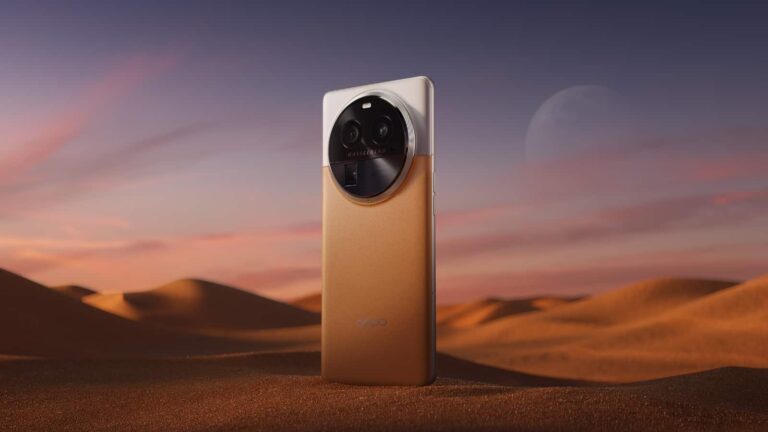
OPPO Find X6 Pro is official with 1-inch camera sensor & much more

0
[ad_1]

OPPO has just announced its new Find X6 series of flagship phones. It consists of the OPPO Find X6 and Find X6 Pro, though the ‘Pro’ model steals the show here, of course. It is a phone with more powerful specs, and a 1-inch camera sensor. That is the variant we’ll focus on here.

Before we begin, do note that the two phones got announced in China only. The last time I talked to OPPO, the company did not have any plans for a global launch, at least not for the ‘Pro’ model. We’ll see if that will change moving forward.

The OPPO Find X6 Pro is finally official with an immensely powerful camera hardware

The OPPO Find X6 Pro has a large circular camera island on the back, which protrudes quite a bit. The device is made out of metal and glass, though there is a variant that combines glass with vegan leather on the back (brown + white).

A centered display camera hole can be found on the front of the phone. Speaking of which, that display is curved towards the sides, and the back side also curves into the frame. The power/lock button sits on the right side, while the separate volume up and down buttons are located on the left.

Let’s talk about the cameras here, first, as that is what OPPO focused on the most in its press materials. There are three cameras included on the back of the phone. OPPO says that it approached developing this phone with a philosophy all three are main cameras, in a way. It wanted all three cameras to be equally useful.

A 1-inch camera sensor is included here, and Hasselblad helped optimize these cameras

The main camera does stand out, spec-wise. OPPO is using Sony’s IMX989 sensor here, which is a 1-inch camera sensor used in the Xiaomi 13 Pro and Vivo X90 Pro. That 50-megapixel camera has a 3.2um post-binning pixel size, f/1.8 aperture, 23mm focal length, OIS support, and a 1G+7P lens.

OPPO Find X6 Pro render image 6

The 50-megapixel ultrawide camera utilizes Sony’s IMX890 sensor. It has a 2um post-binning pixel size, f/2.2 aperture, 15mm focal length, macro mode, and a 7P lens. The third camera is a 50-megapixel periscope telephoto unit (Sony’s IMX890 sensor, 2um post-binning pixel size, f/2.6 aperture, 3x optical zoom, 65mm focal length, OIS). The MariSilicon X imaging NPU is also a part of the package here. Hasselblad helped tune these cameras, while you’ll also notice the company’s logo on the back.

A single 32-megapixel selfie camera (Sony’s IMX709 sensor) can be found on the front side of the device. That camera also comes with a 7P lens module.

This is the brightest display in any phone to date

There is a 6.82-inch QHD+ (3168 x 1440) LTPO AMOLED display included on the front. That display has a 120Hz refresh rate (adaptive), and it’s protected by the Gorilla Glass Victus 2. It gets up to 2,500 nits of peak brightness, which is a new record.

The phone is fueled by the Snapdragon 8 Gen 2 SoC. OPPO included 12GB or 16GB of LPDDR5X RAM here, depending on the model you get. The 12GB RAM model includes 256GB of UFS 4.0 flash storage, while the 16GB RAM model comes in both 256GB and 512GB UFS 4.0 storage options.

100W wired & 50W wireless charging is included here

There are two SIM card slots included in the phone, while the device comes with Bluetooth 5.3 support. A 5,000mAh battery can be found on the inside, while the phone supports 100W wired charging, and 50W wireless charging. 10W reverse wireless charging is also supported. Do note that a 100W charger is also included in the package. Android 13 comes pre-installed, with OPPO’s ColorOS 13.1.

There are, of course, two speakers included on the device too. The OPPO Find X6 Pro measures 164.8 x 76.3 x 9.1mm (glass model), and the glass + vegan leather model is a bit thicker at 9.5mm. Speaking of which, the glass model comes in black and green options, while the glass + leather model combines brown and white colors on the back.

We still don’t know the phone’s price, but we’ll update this article later today, as soon as OPPO announces the pricing.


[ad_2]
Source link
Experts from Global Triangles weigh In

0
[ad_1]

With millions of people checking out on a mobile device, using Android and iOS devices in particular, it is no understatement that the mobile user-experience is an important consideration today. Although some payment processors like Stripe went above and beyond to incorporate both GPay for Android and Apple Pay for iOS in a responsive manner depending on browser type, the key question many people have is which shopping cart to use when creating websites that are fit for a mobile-first world.

Magento, Shopify, and WooCommerce are among the most popular ecommerce platforms offering their clients a wide variety of features and benefits that allow customizable sites to host online ecommerce sites. They are all strong competitors in the ecommerce market today, and all come with their own set of advantages and disadvantages.

All three platforms provide their users with a wide range of excellent tools that can be used to enhance their customer engagement and online marketing, but naturally, they all come with their own set of limitations. This is why it is vital for online business owners and those interested in starting an ecommerce site to sell their products or services, assess the pros and cons of each platform and make an informed choice on what works for them and what doesn’t.

But which one is truly the best? Experts from Google Triangles, a well-known ecommerce developer, share their input.

Overview of Magento, Shopify, and WooCommerce

Shopify

Shopify is a type of web software that allows you to build your own online store. Users of Shopify can choose from a wide variety of themes that can be customized to fit their business’s needs. One of the critical missions of Shopify is to provide even the most novice users with an easy-to-use interface that puts them in the driver’s seat of creating their dream business. The platform also offers developers access to CSS, HTML, and Liquid.

WooCommerce

WooCommerce is an open-source shopping cart plugin designed particularly for WordPress sites. WooCommerce is typically used to create and manage online e-commerce sites. With this software, beginners can turn a regular website into a fully functional online store with the click of a button. Users of WooCommerce are provided with a variety of tools that can assist with product displays, sales management, and payment gateways.

Magento

Magento, the Adobe owned open-platform, is most-well known for its scalability, customizability, and dynamic built-in tools. Famous brands such as Ford Accessories, Bulgari, Coca-Cola, Olympus, Asus, and HP use the platform to serve their ecommerce needs, so it is no wonder that Magento has solidified its place as a strong competitor in the ecommerce industry today.
Since its 2007 release, Magento has undergone a series of changes and improvements, making it a fierce competitor in a rapidly changing industry. Magento also offers two eCommerce platforms: Magento Open Source and Magento Commerce.

Cons

Shopify

  • Complex processes may be time consuming.
  • Reduced built-in capabilities may require other applications to boost the site.
  • Monthly costs can be expensive when adding the expenses associated with their high transaction fees and other applications that may be required.
  • No email storage access and requires users to find a different provider for setting up an email address for their store.

WooCommerce

  • Added costs. Even though the plugin installation is free, users must pay additional fees for hosting web domains, SSL certificates, and any other premium themes or widgets needed to enhance their site.
  • Customer support can be challenging.
  • Inflexible. WooCommerce can only be used in conjunction with WordPress.
  • Lack of scalability. The platform is an excellent option for small to medium-sized businesses, but you may need additional help handling traffic and sales if your business snowballs.

Magento

  • Investment is high (you pay for top quality).
  • May require technical skills and knowledge as your site grows.
  • Slow-loading speed at times.
  • Advanced yet complex system.

Pros

Shopify

  • Shopify hosts a platform that allows high-level inventory management, which makes shop expansion easier.
  • The platform allows for selling products/services on several platforms, such as Facebook, Instagram, and eBay.
  • Design utility and adaptability, providing clients with various free and paid themes. Users are also to design their own themes if they wish.
  • Over 100 payment methods to choose from.

WooCommerce

  • Limitless add-on extensions that allow site customization.
  • Access to the WooCommerce community, tutorials, and help articles.
  • Installation is free since it is a WordPress plugin.
  • Wide variety of payment gateways such as PayPal, Stripe, Square, and more.

Magento

  • Most advanced scalability that can be customized to suit clients’ individual needs and goals.
  • Offers a powerful free open-source community version.
  • Advanced data reporting and metrics of critical insights on orders, customers, and products.
  • Mobile-friendly and dynamic. This allows for the ideal mobile-friendly customer experience, which could positively boost sales and customer engagement.

The Choice is Yours – Although Magento Has Interesting Upsides:

Whatever you decide, it is essential to consider your business needs and goals for the present and future. All three platforms are popular for a reason and have their own set of advantages and limitations. In summary, the ultimate decision comes down to what best aligns with your business’s mission and capacity.

But if you’d ask us: it does seem like Magento could be the stronger competitor due to its advanced scalability, and advanced data reporting that will provide you with vital insights on how you could advance and maintain the growth of your online business. It also has one of the most dynamic and scalable features, giving you the most control over your website. Finally, before firing away with any web developer, we suggest you look at the top alternatives in the market.


[ad_2]
Source link

Meta Verified: Everything you need to know

0
[ad_1]

To much backlash, Twitter introduced a paid verification system. For a monthly fee, users could gain access to additional features and perks along with the much-coveted verification checkmark. While this made Twitter the laughingstock of the social media world, it seems that Meta also came out with its own paid verification program.

So, what is this program all about? Why should you get it? More importantly, is it worth your money? Here’s everything you need to know about this program.

What is Meta Verified?

Meta Verified is a subscription service that will grant users on Facebook and Instagram exclusive perks and features. As time goes on, we won’t be surprised to see the list of perks increase. For now, there is a handful of goodies that the program will offer.

The perks

For starters, there’s the coveted verification badge. You’ll have a unified verification badge that you’ll see on both your Facebook and Instagram profiles.

With Meta Verified, you’ll have proactive account monitoring. This means that the company will keep an eye on your account to ensure that there aren’t any impersonators out there trying to emulate your account. As accounts gain notoriety, they see an increase in other accounts trying to impersonate them to scam unsuspecting individuals.

If you’re Meta Verified, you’ll have exclusive access to a human assistant who will assist you with common issues. This means that you won’t need to navigate help forums and automated phone services to get assistance for most issues.

Next, with the subscription, your posts will have a wider reach compared to free users. This means that you’ll have a boost in the algorithm making it easier for people to discover your posts.

[UPDATE: The wider reach is only available for users in Australia and New Zealand. It’s not available for users in the US]

Meta notes that the effect on your account will vary depending on your audience size. If you have a smaller following, then you’re likely to see a more substantial difference than if you have a larger following.

Verified members will have exclusive stickers on their accounts. They’ll show up on Reels and Stories to show people that they’re verified.

Each verified member will get 100 stars every month on Facebook. Stars are a proprietary Facebook currency that you can give to creators. They’re like Bits for Twitch.

How much does Meta Verified cost?

At the time of writing this post, it’s currently being tested in Australia and New Zealand. While that’s true, the prices are presented in USD, so we don’t expect it to be different when it eventually hits the states.

If you sign up through the apps on Android or iOS, it costs $14.99/month (AUD 19.99). However, if you sign up for it through the web, then the price drops 20% to $11.99/month (AUD 24.99). 

The reason for this is that Meta needs to pay 30% of its earnings to Apple and Google whenever someone signs up on their app store. So, Meta is charging more for people who sign up that way to offset this fee.

At this time, there is no yearly subscription plan.

Who can sign up?

Currently, only personal accounts are eligible for verification. This means that you can’t verify your business or organization just yet. However, that functionality will come down the pipeline.

I’m already verified. Will my account be affected?

There’s already a verification program present on Facebook and Instagram. Meta stated that with Meta Verified, accounts that have previously been verified, will not be affected. However, that doesn’t mean that there won’t be changes in the long term.

According to the company’s blog post, previously-verified accounts won’t be affected in the short term, but it will eventually be “evolving the meaning of verified accounts on [its] apps.”

This means that sometime down the road, Meta could bring a major change to accounts that are already verified. At the moment, we don’t know what the company plans on doing to previously-verified accounts.

How do I get Meta Verified?

At the time of this writing, the program is only available to users in Australia and New Zealand [UPDATE: Now available in the US]. When it does make it to more markets, it will be a relatively involved process. This is because you’ll need to verify your identity before you can verify your account. You’ll need to submit a picture of your government-issued ID in order to sign up to be verified. You must also be at least 18 years old and enable two-factor authentication.

If you’re signing up for Meta Verified, you’ll need to use an account that has a minimum posting history. This is to help ensure that only true users of the platform are applying to be verified. It will help minimize bots and trolls gaining verification

Lastly, you’ll need to be at least 18 years old. There’s no way of getting past that, as you’ll need to present your ID when signing up.

One thing to know is that when you sign up, the name on the account must match the name on your ID. This means that your account can only have your real name. After your account is verified, you can not change your name, photo, or account information without going through the verification process again.

Can I be verified if I have strikes on my accounts?

Meta didn’t mention whether ToS strikes have any weight on your application process. Just know that, if you’ve wracked up any serious strikes on your account, then you run the risk of having your verification application rejected. Make sure that you read through the terms of service if you have any questions.

After you are verified, Meta didn’t state whether ToS strikes will have your account unverified or simply banned.

When will it come to other markets?

Meta has been testing this program out in Australia and New Zealand. The company eventually brought it to the US market. It’s currently still in testing, so it will expand to other markets as time goes on.


[ad_2]
Source link

Snapchat gives more control to parents over sensitive content

0
[ad_1]

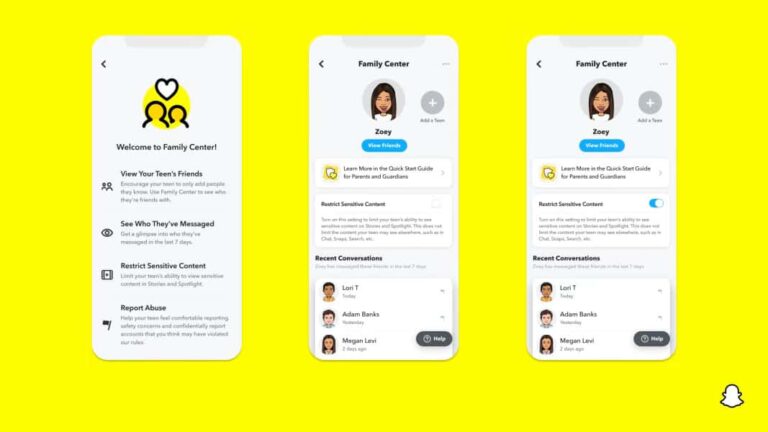
Snapchat Family Center has added a new feature that gives parents more control over the content on their kid’s feeds. The new feature is known as Content Controls, and it’s now accessible in the Family Center settings.

Protecting children from harm and abuse has become a concern for parents, online platforms, and lawmakers. Social media platforms allow parents to regulate the content their kids watch.

The lawmakers also want platforms to be more transparent about the data they collect and measure to protect underage users. As one of the teenagers’ most popular social apps, Snapchat now provides parents with even more tools to moderate content.

The Content Controls on Snapchat Family Center allows parents to filter out Stories from specific publishers or creators. Deciding on whether the Stories are sensitive is all on parents, and Snapchat would not intervene.

Snapchat Family Center adds Content Controls to allow parents to regulate content

In order to activate Content Controls, parents first need to have an existing Family Center set up with their teen. Then, they need to select “Restrict Sensitive Content” in the Family Center settings.

“We hope these new tools and guidelines help parents, caregivers, trusted adults, and teens not only personalize their Snapchat experience but empower them to have productive conversations about their online experiences,” Snapchat said.

The platform also specified examples of “sensitive or suggestive” content in its Content Guidelines for community members. The guideline warns publishers and creators that their content might be restricted due to new Content Controls.

Meanwhile, Snapchat says it’s working on new AI tools for its Family Center. Last month, the app revealed its AI chatbot called My AI, which is only available to Snapchat+ users and relies on OpenAI technology. The experimental chatbot gives parents more insights into their children’s usage of My AI.

Snapchat now has over 750 million monthly active users and is immensely popular among teenagers. However, it has already come under the FBI and DOJ radar over online drug sales accusations. The platform now hopes to reduce children’s exposure to harmful content by giving more content regulation tools to parents.


[ad_2]
Source link

A week in security (March 13

0
[ad_1]

The most interesting security related news from the week of March 13 to 19.

Last week on Malwarebytes Labs:

Stay safe!


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Samsung treats Galaxy A51 5G users in the US with One UI 5.1

0
[ad_1]

Samsung‘s One UI 5.1 update is available for the Galaxy A51 5G in the US. The rollout began recently for the carrier-locked variants. Factory-unlocked units should get it soon. The new One UI version has yet to reach the 4G model of the Galaxy A51.

The One UI 5.1 update for the carrier-locked Galaxy A51 5G comes with the firmware build number A516USQUBGWC1 in the US (via). As of this writing, the big update is available to users on T-Mobile’s prepaid virtual network Metro. Samsung should soon expand the release to other networks. A wider rollout covering unlocked units and the 4G model should follow in the coming days.

The Galaxy A51 5G is getting a host of new features and improvements with this update. One UI 5.1 brings enhanced image remastering with the ability to remaster downloaded GIFs for better resolution and clarity. A shared family album in Gallery gives 5GB of storage for up to six people to quickly share photos and videos. New gestures enhance your multitasking experience. Resizing windows and entering split-screen mode is now easier.

Improved Modes & Routines let you choose multiple wallpapers that automatically change based on your activity. The weather widget is now richer while you’re getting a battery widget that lets you check the battery level of your connected devices. Last but not least, Samsung Internet adds continuous browsing across compatible connected devices. Long story short, One UI 5.1 has plenty of new features to be excited about.

Galaxy A51 5G is also getting the February security update

This update brings the February 2023 Android security patch to the Galaxy A51 5G in the US. It isn’t the latest monthly SMR (Security Maintenance Release) available for Galaxy devices. Samsung has already pushed the March SMR to dozens of models. But last month’s patch is a fairly recent one. The device will get a newer security release in the coming months. It is eligible for biannual security updates at least until April of next year.

The Galaxy A51 5G will not get feature updates anymore, though. One UI 5.1 is the last such software release for this 2020 mid-range smartphone, It debuted with Android 10 and received updates until Android 13. The device isn’t eligible for Android 14. Nonetheless, if you’re using this phone in the US, the latest update has plenty of goodies for you. Go to Settings > Software update and tap on Download and install to check for updates manually. If you don’t see any updates today, wait a few days and check again.


[ad_2]
Source link

Doxxers posed as police officers to obtain information from social media companies

0
[ad_1]

Two individuals have been charged with being members of ViLE, a group of doxxers that even impersonated police officers to obtain persoanl information about their victims

In a press release the U.S. Attorney’s Office, Eastern District of New York revealed details about the complaint against two individuals that are charged with wire fraud and conspiracy to commit computer intrusions.

More specifically, the defendants are suspected of extortion with the threat of doxxing. Doxxing, also known as doxing, is the act of publishing personal information about an individual without their consent. This information can include addresses, phone numbers, email addresses, and even financial details.

Allegedly, the defendants threatened to publish or otherwise use personal information about the victims unless they paid to have their information removed from or kept off the website.

The defendants, of which one is still at large, belonged to a group called Vile. Members of ViLE sought to collect victims’ personal information, such as names, physical addresses, telephone numbers, social security numbers, and email addresses. ViLE runs its own website which they use to post that information unless the victim complied with their demands.

As stated by United States Attorney Peace. 

“As alleged, the defendants shamed, intimidated and extorted others online. This Office will not tolerate those who impersonate law enforcement officers and misuse the public safety infrastructure that exists to protect our citizens.”

The second sentence of that statement indicates how the defendants were able to get their hands on the personal information. What the defendants are charged with is that they unlawfully used a police officer’s stolen password to access a restricted database maintained by a federal law enforcement agency. They used the police officer’s credentials to access without authorization a nonpublic, password-protected web portal maintained by a U.S. federal law enforcement agency, whose purpose is to share intelligence from government databases with state and local law enforcement agencies. Said database contains (among other data) detailed, nonpublic records of narcotics and currency seizures, as well as law enforcement intelligence reports. 

The two suspects are also charged with accessing without authorization the email account of a foreign law enforcement officer. They abused this access to defraud social media companies by making purported emergency requests for information about the companies’ users. For example, one of the defendants used an official email account to pose as a Bangladeshi police officer in communication with US-based social media platforms.

The same Bangladeshi police account was used to request data about the user of  an online gaming platform. When caught they threatened to sell the platform’s information on the Dark Web. An associate posed as a US local police officer and sent a forged subpoena to one of the platform’s vendors, seeking registration details about their administrators.  The vendor did not provide the information.

Data breach

There are some actions you can take if you are, or suspect you may have been, the victim oif a data breach.

  • Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened, and follow any specific advice they offer.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication. Where possible, use a FIDO2 2FA device. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for fake vendors. The thieves may contact you posing as the vendor. Check the vendor website to see if they are contacting victims, and verify any contacts using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

March update live for Galaxy Z Fold 2 and Galaxy A12 in the US

0
[ad_1]

Samsung is rolling out the March 2023 Android security patch to the Galaxy Z Fold 2 and the Galaxy A12 in the US. The latest security update has already been pushed to all other recent foldables and flagship models stateside. The new release contains more than 60 vulnerability patches.

The March SMR (Security Maintenance Release) for the Galaxy Z Fold 2 in the US is currently limited to carrier-locked units. The update comes with the firmware build number F916USQS2JWC1 and is available for users on Sprint and T-Mobile networks. Samsung should expand the release to factory-unlocked units in the coming days. The firmware version may vary slightly but the content will remain the same.

Speaking of content, don’t expect any new features or improvements here. The 2020 foldable model is only getting this month’s vulnerability fixes. It recently picked up the One UI 5.1 update with tons of goodies. Samsung is now improving the security level of the phone. Those with an unlocked Galaxy Z Fold 2 in the US know that their device hasn’t received One UI 5.1 yet. The March SMR for your foldable may arrive bundled big update.

Coming to the Galaxy A12, the story is a little different. It’s an entry-level phone that arrived on the market at the far end of 2020. The device debuted running Android 10 out of the box. It picked up updates until Android 12 and that’s all it will ever get. Samsung will not push Android 13 to it, and that eliminates the possibility of One UI 5.1 as well. Security updates also come a few and far between for this phone.

But as we speak, Samsung is pushing the March SMR to the Galaxy A12 in the US. The update is available for the unlocked variant with firmware version A125U1UES5CWC3. As you can see in the official changelog, the entry-level handset isn’t getting anything apart from the latest security patch. A wider release covering carrier-locked units should follow in the coming days.

March update for Galaxy devices patches more than 60 vulnerabilities

The March SMR for Galaxy devices contains fixes for more than 60 vulnerabilities across the Galaxy lineup. About 20 of those issues are Galaxy-specific and were duly patched by Samsung. The rest are issues in Android OS and other partner components that various Android OEMs use. They affect the entire Android ecosystem. Respective vendors of those components patched the issues. If you’re using the Galaxy Z Fold 2 or Galaxy A12 in the US, you can check for a new update with all of these vulnerability patches from the Settings app.


[ad_2]
Source link

FBI launches investigation against TikTok for spying on journalists

0
[ad_1]

It’s no secret that over the past few years, TikTok has been under a lot of scrutiny regarding its data privacy practices. However, when reports of the company firing employees for using the app to spy on the locations of two journalists emerged last year, it sparked a new wave of controversy. Now, the FBI and the Department of Justice are also looking into the matter and have launched an investigation against TikTok over national security concerns.

The incident was first confirmed in an internal ByteDance investigation, where the company found out that some employees accessed data on American journalists’ TikTok accounts to figure out which employees were leaking information to reporters. While ByteDance says they immediately fired the involved employees, this security lapse has caused US lawmakers to question the company’s privacy practices as they worry that the Chinese government is using TikTok to gather intelligence on US citizens.

The details of the investigation are still unclear, but Forbes says TikTok has already received subpoenas from the Department of Justice, and the FBI has also started conducting interviews related to the matter.

In response to the investigation, ByteDance stated, “We have strongly condemned the actions of the individuals found to have been involved, and they are no longer employed at ByteDance. Our internal investigation is still ongoing, and we will cooperate with any official investigations when brought to us.”

Mounting pressure on TikTok

This development also comes at a time when US regulators have been mounting pressure on ByteDance to sell off the US division or face a complete ban. However, TikTok has rejected the demand for divestiture, stating that it won’t address the government’s concerns. Instead, the company proposed “Project Texas,” a $1.5 billion initiative that would store US user data domestically and subject the company to an auditing process conducted by American tech giant Oracle.


[ad_2]
Source link

The Malware That Infects Systems with Multiple Families

0
[ad_1]

Currently, DotRunpeX malware appears to be primarily distributed through phishing emails and malicious Google Ads, presenting a significant threat to users’ systems.

A new malware that distributes multiple known malware families, including Agent Tesla, FormBook, Ave Maria, NetWire, LokiBot, Raccoon Stealer, Remcos, RedLine Stealer, Vidar, and Rhadamanthys, has been discovered by Checkpoint researchers.

Dubbed DotRunpeX, the malware is a new injector written in .NET, created using the Process Hollowing technique, and used to infect systems with different malware families.

The researchers noted that DotRunpeX is being actively developed. Its infection chain invades the system as a second-stage malware, usually deployed via a downloader or loader delivered via malicious attachments in phishing emails.

Additionally, it can leverage malicious Google Ads that appear in search results to direct unsuspecting users when they search for commonly used software such as LastPass and AnyDesk and send them to copycat sites delivering trojanized installers.

DotRunpeX: The Malware That Infects Systems with Multiple Families
A malicious Google Ad and phishing email that drop the malware (Image: Check Point)

Though the injector is fairly new, there are several similarities it shares with its previous versions. For example, the injector’s name is derived from its version information, which is the same for both versions across all samples the researchers analyzed. They also noted that it contained ProductName – RunpeX.Stub.Framework.

Their analysis revealed that each malware sample had an embedded payload of a specific malware family to be injected, which becomes possible by abusing the vulnerable procexp.sys process explorer driver incorporated into the malware for obtaining kernel mode execution.

They analyzed publicly shared data by independent researchers regarding DotRunpeX but learned that the malware was misattributed to a well-known malware family. Furthermore, they learned that the first-stage loader and the second-stage loader had no connection.

The most recent activity of DotRunpeX was detected in October 2022. It was noticed that using the KoiVM virtualizing protector adds an extra obfuscation layer. These findings were somewhat similar to a malvertising campaign discovered by SentinelOne in February 2023. In that instance, the loader and injector components were referred to as MalVirt.

Researchers suspect that the malware may be operated by Russian-speaking groups, given the references to the language in its code.

  1. New YTStealer Malware is Hijacking YouTube Channels
  2. YouTube Tutorial Videos Spread Vidar, Raccoon Malware
  3. Adsense abused: 11,000 sites hacked in a backdoor attack
  4. Google Drive behind most malicious Office doc downloads
  5. Google Ads drop FatalRAT in fake messenger, browser apps

[ad_2]
Source link