Sadly, the Android Auto and Google Maps integration is still a mishmash

0
[ad_1]

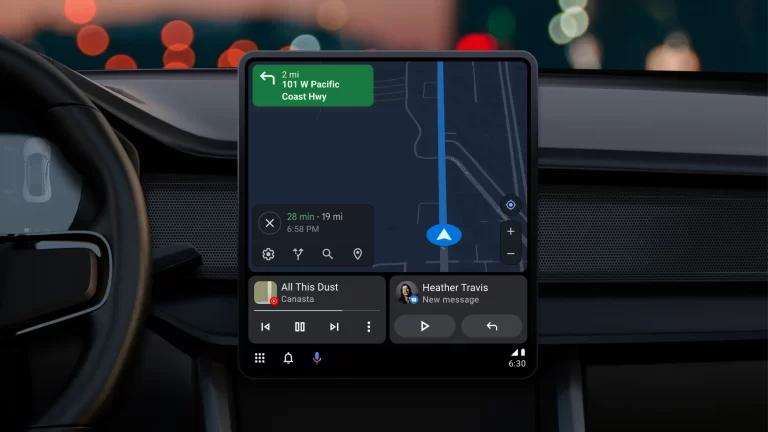
Over the past few weeks, Android Auto and Google Maps on vehicle infotainment systems haven’t been working together perfectly. Using both platforms while driving hasn’t been as smooth as users expect. The Google Maps integration into the Android Auto platform has been facing serious GPS issues.

These issues are a result of some upgrades to the Google Maps platform. With this upgrade, the integration between the two platforms hasn’t been working perfectly. This has led to difficulties in navigating, as the GPS location feature was directly affected by this upgrade.

Lots of users have been complaining about this issue over the past few weeks. A reliable source has provided a fix to this issue to help Android Auto users rely on their map navigations once again. Here is everything you need to know about this quick fix.

A fix to the Android Auto and Google Maps integration issue

If you use Android Auto and Google Maps on your vehicle, you might notice this navigation issue. It prompts the system to display false routes and incorrect GPS locations. This is quite misleading, especially while navigating an area which you aren’t familiar with.

An actual fix to the cause of this issue is not available at this moment. But there is now a way to work around it to avoid getting wrong directions and GPS locations while driving. The available fix involves your Android device since your car’s infotainment system relies on it to run Android Auto.

So, on your Android device, long press on the Google Maps app icon then select the app info option. This is located at the top right-hand side of the pop-up window that will appear on your screen. Pressing the app info button will redirect you to the app’s settings.

You will find a list of settings options, select the “Permission” button, which is the second on the list. This will pull up a list of permissions that you can grant the Google Maps app. Now select the first option on the list which is “Location” this will pull up another window.

In this new window are four options to select from on how you want the Maps app to access your device’s location. To fix the Android Auto and Google Maps navigation issue, you need to check the “Allow all the time” option. This will help Google Maps on the vehicle to make use of your device’s location as you drive.

According to available sources, this navigation issue is a result of Android Auto treating the Google Maps app as a background app. The fix will prevent your car’s Android Auto system from using its built-in antenna, hence making it rely on your device’s real-time location. You can also take the steps mentioned above on the Google Maps app on your car’s navigation system.


[ad_2]
Source link

Bally Sports owner files for Bankruptcy

0
[ad_1]

After missing an interest payment last month, Bally Sports owner, Diamond Sports Group (DSG) entered into a 30-day grace period. Where it needed to pay its bills, or file for bankruptcy. Well, after using up almost the entire 30-day grace period, DSG has decided to file for Chapter 11 bankruptcy.

DSG has agreed to terms with the majority of creditors, which has allowed them to eliminate over $8 billion in debt. This clears the way for DSG to restructure  and attempt to continue to broadcast games as a standalone company.

“Diamond intends to use the proceedings to restructure and strengthen its balance sheet, while continuing to broadcast quality live sports productions to fans across the nation. DSG expects that its Bally Sports regional networks will continue to operate in the ordinary course during the Chapter 11 process,” said the company in a statement.

What does this mean for the upcoming MLB season?

For Baseball fans, this really couldn’t have come at a worse time. With Opening Day about two weeks away. But DSG says that it will continue to broadcast the games of the 42 teams that it has broadcast rights to.

That does not include the handful of teams that Bally Sports dropped the rights to earlier this week. Those included the Arizona Diamondbacks, Cincinnati Reds, Cleveland Guardians, and San Diego Padres. The MLB would broadcast them instead, on MLB.TV in-market.

After the bankruptcy announcement, the MLB did reaffirm that it is able to step in and continue to provide fans access to their teams should Diamond fall short of their agreements. “Despite Diamond’s economic situation, there is every expectation that they will continue televising all games they are committed to during the bankruptcy process,” the MLB said in a prepared statement. Also stating that “Major League Baseball is ready to produce and distribute games to fans in their local markets in the event that Diamond or any other regional sports network is unable to do so as required by their agreement with our clubs.”

RSNMLBNBANHL
Bally Sports ArizonaPhoenix SunsArizona Coyotes
Bally Sports DetroitDetroit TigersDetroit PistonsDetroit Red Wings
Bally Sports FloridaMiami MarlinsOrlando MagicFlorida Panthers
Bally Sports IndianaIndiana Pacers
Bally Sports Kansas CityKansas City Royals
Bally Sports MidwestSt. Louis CardinalsSt. Louis Blues
Bally Sports New OrleansNew Orleans Pelicans
Bally Sports NorthMinnesota TwinsMinnesota TimberwolvesMinnesota Wild
Bally Sports OhioCleveland CavaliersColumbus Blue Jackets
Bally Sports OklahomaOklahoma City Thunder
Bally Sports SoCalAnaheim Ducks
Bally Sports San Diego
Bally Sports SouthAtlanta BravesAtlanta HawksNashville Predators
Bally Sports SoutheastCharlotte HornetsCarolina Hurricanes
Bally Sports SouthwestTexas RangersDallas MavericksDallas Stars
Bally Sports SunTampa Bay RaysMiami HeatTampa Bay Lightning
Bally Sports TennesseeMemphis GrizzliesNashville Predators
Bally Sports WestLos Angeles AngelsLA ClippersLos Angeles Kings
Bally Sports WisconsinMilwaukee BrewersMilwaukee Bucks
Bally Sports Great Lakes

For now, nothing is really changing for sports fans, except for those four teams we reported on Monday. That’s the Diamondbacks, Reds, Guardians and Padres. Those fans will need to watch games on MLB.TV this season.


[ad_2]
Source link

Spotify HiFi is still not dead, but we don’t have a release date either

0
[ad_1]
Heey, it’s been two years since Spotify announced Spotify HiFi. Not to mention that more than a year has passed since the company indefinitely delayed the release. So, come on, in today’s day and age, where everyone is rushing to do the next big thing, there’s no real hope for Spotify HiFi to make a comeback, right? Well, apparently not! Company co-president Gustav Söderström sat down for an interview with The Verge, where he basically confirmed that Spotify is still working on the best way to provide high quality music to its audiophilic users.

Söderström commented that Spotify had to postpone the release of this high-end tier of music streaming in order to better adapt to the market. He gives very few details from there on out, but HiFi costs and deals with music labels were mentioned as factors too.


Söderström went on to state that Spotify wants to do something unique with HiFi. By the sound of things, the plan isn’t to just follow the established trend and copy what the competitors are up to, but come up with a unique way to deliver on this upgraded service.That being said, the co-president is confident about Spotify HiFi still being on the table. While no specific end-date has been mentioned, as per Söderström’s own words, it will be a real thing at “some” — undefined, and likely distant — point in time.

Why distant? Well, because Spotify is currently quite busy with redesigning major UI elements or figuring out ways to incorporate AI into its platform. One of the major talking points of the interview is centered around the fact that Spotify is looking to copy some of TikTok’s homework. While HiFi audio is certainly a great selling point, it doesn’t seem to be that important for now.


[ad_2]
Source link

Threat Actors Deliver Malware Using AI-Generated Youtube Videos

0
[ad_1]
Threat Actors Spread Stealer Malware

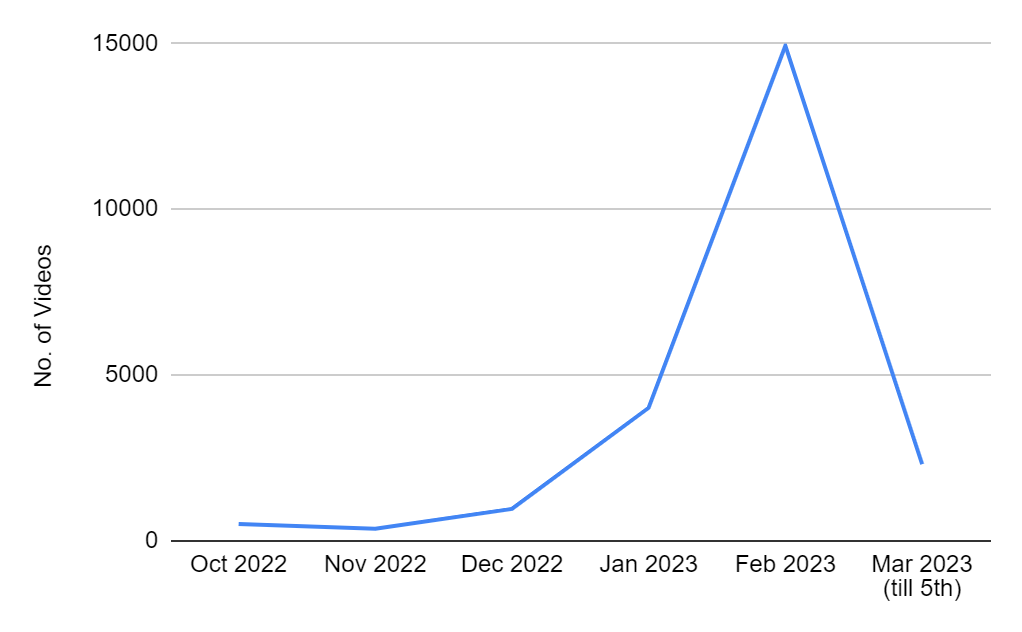
The cybersecurity analysts at CloudSEK recently asserted that monthly YouTube videos containing links to stealer malware, such as Vidar, RedLine, and Raccoon, have increased by 200-300% since November 2022.

These videos are supposed to be tutorials; however, it has been reported that they are instructions on getting pirated versions of licensed software, such as:-

  • Adobe Photoshop
  • Premiere Pro
  • Autodesk 3ds Max
  • AutoCAD

This software can only be acquired by paying, but threat actors claim to provide the proper instructional guide to obtain them for free in these videos.

According to the report shared by CloudSEK to cybersecuritynews.com, hackers are using YouTube video links to spread malware. A common technique used by cyber criminals is to post a video that appears to be legitimate but contains a malicious link in the description or within the video itself.

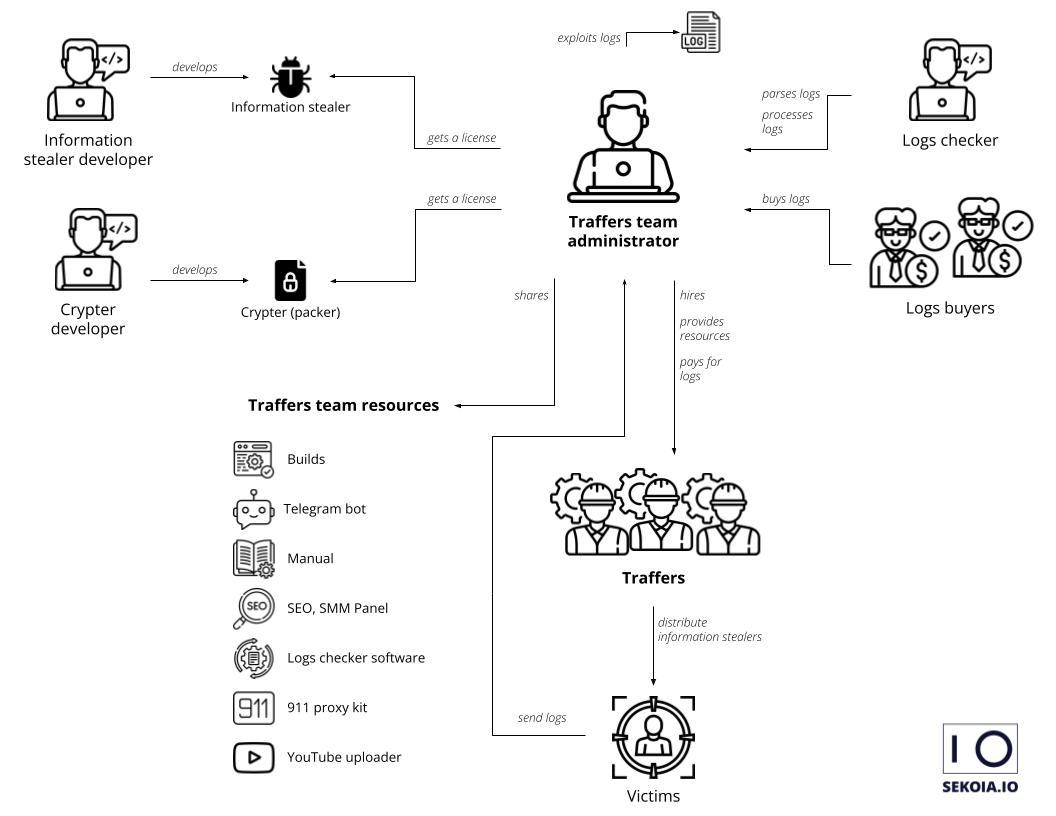
Information Stealer Ecosystem

Infostealer is specifically designed to steal sensitive information from the target computer. For example, it can steal passwords, credit card numbers, bank account numbers, and other sensitive information from the target system.

The intruder installs the info stealer system onto the computer. Once it is activated, it steals information from the computer and uploads it to the attacker’s command and control (C&C) server.

Here below, we have mentioned all data that are being targeted by the attackers from the victim’s system:

  • Passwords
  • Cookies
  • Extension data
  • Auto-fills
  • Credit card details
  • Debit card details
  • Crypto wallet data 
  • Crypto wallet credentials
  • Telegram data 
  • Telegram credentials
  • .txt files
  • Excel sheets
  • PowerPoint presentations
  • IP address
  • Malware path (Redline and Vidar only)
  • Timezone
  • Location
  • System specifications

Distributing malware via Youtube

Youtube is a popular platform for attackers to reach millions of users easily. It is still difficult for threat actors to maintain long-term active accounts on the platform due to the platform’s regulations and the review process.

It is common for the video to be removed and the account to be banned as soon as there appear to be a few users affected by the video.

In order to circumvent the platform’s algorithm and review process, threat actors are always looking for new ways to get around the algorithm.

Taking Over Popular & Less Popular Accounts

As a means of reaching a large audience in a short period of time, threat actors target popular accounts that have 100K or more subscribers.

In such a case, YouTubers should inform Youtube of the account thief, and they should be able to access their accounts within a few hours after they report them. But there is a possibility that hundreds of users could have fallen victim to this scam within a few hours.

In contrast, the average user, who does not upload videos on a regular basis on YouTube, may not even realize that their account has been taken over for a significant time as they do not upload videos regularly. 

Threat actors target these accounts despite the fact that their reach is limited, as videos uploaded to them remain available for extended periods of time.

Automated & Frequent Video Uploads

Security researchers have thoroughly investigated the frequency of uploading videos containing malicious links for crack software to Youtube. They have found that 5-10 such videos are posted every hour.

Regularly adding videos to the site helps to make up for the videos that are deleted or taken down. In addition, they ensure that the malicious videos will be accessible at any given time if a user searches for a tutorial on how to download cracked software.

Using Region-Specific Tags, Obfuscated Links, Fake Comments, and AI-Generated Videos

In order to deceive the YouTube algorithm, threat actors add a wealth of tags to the video that will make sure it appears as a top result and will deceive the YouTube algorithm into recommending the video to the user.

As a way of making their video look like a legitimate one, the threat actors also use fake comments and Region-Specific Tags.

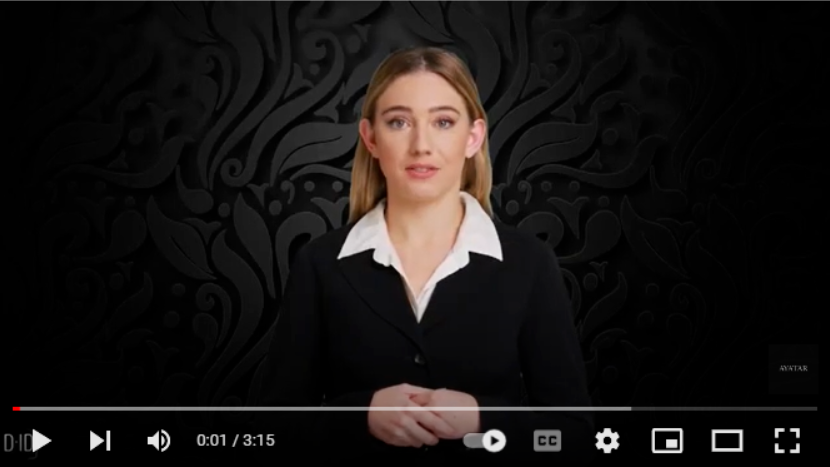
Video featuring humans, especially those with certain facial features, undeniably gives viewers a sense of familiarity and trustworthiness. That’s why the threat actors use AI-Generated videos as well as obfuscated links.

Recommendations

As a result of the vast increase in threats to organizations, it is imperative to keep them protected. There has been a consensus among security experts that organizations need to adopt the following things:-

  • Robust threat monitoring practice to be more secure.
  • Make sure to closely monitor the changing Tactics, Techniques, and Procedures used by the threat actors.
  • Awareness campaigns must be conducted.
  • Ensure that users are equipped with the knowledge to identify potential threats in advance.
  • Make sure to use complex passwords and not use any user passwords.
  • Use a robust security system and AV tool.
  • Ensure that two-factor authentication is enabled.

Related Read:


[ad_2]
Source link

“Just awful” experiment points suicidal teens at chatbot

0
[ad_1]

Startup Koko has been criticized for experimenting with young adults at risk of harming themselves. Worse, the young adults were unaware they were test subjects.

After getting in hot water for using an AI chatbot to provide mental health counseling, non-profit startup Koko has now been criticized for experimenting with young adults at risk of harming themselves. Worse, the young adults were unaware they were test subjects. 

Motherboard reports the experiment took place between August and September 2022. At-risk subjects, aged 18 to 25, were directed to a chatbot after posting “crisis-related” keywords like “depression” and “sewer-slide” on Discord, Facebook Messenger, Telegram, and Tumblr. They were then randomly assigned to a group that received a “typical crisis response” (call the crisis hotline), or a “one-minute, enhanced crisis response Single-Session Intervention (SSI)” powered by AI.

Rob Morris, Koko co-founder and Stony Brook University professor, carried out the experiment with his psychology peers, Katherine Cohen, Mallory Dobias, and Jessica Schleider. The study says it aims to show social media platforms that pointing young adults to crisis hotlines isn’t enough. Morris says he wants to show that an AI chatbot intervention is more effective in supporting young adults struggling with mental health issues.

However, this appears to only look good on paper.

Before Koko performs what it was designed to do, it first presents its privacy policy and terms of service (ToS), telling users their anonymous data may be shared and used for research. Here lies the first problem: Consent to take part in the project is given by agreeing to Koko’s privacy policy and ToS. As we all know, a great majority of people online normally don’t read these. Presumably, it’s not the first thought for at-risk young adults either.

When asked about provisions for true consent, Morris tells Motherboard, “There are many situations in which the IRB would exempt researchers from obtaining consent for very good reasons because it could be unethical, or impractical, and this is especially common for internet research. It’s nuanced.” An IRB, or institutional review board, is also called a research ethics committee. Essentially, they’re the group protecting human research subjects.

The second problem involves data. The preprint reveals that subjects provided their age, gender identity, and sexual identity to the researchers. Such datasets may be anonymous, but studies show these can still be traced back to specific individuals with a high accuracy of 99.98 percent. “Most IRBs give a pass to ‘de-identified’ research as they claim there can be no privacy or security harms. But, in this case, they are collecting demographic information which could be used to identify users,” said Eric Perakslis, the chief science and digital officer at the Duke Clinical Research Institute, Motherboard reports.

And the last problem, which alarmed and appalled researchers and psychologists alike, was that the experiment was carried out as “nonhuman subjects research.” This means subjects have been stripped of due safety- and privacy-related protections.

“Completely, horribly unethical. Mucking around in an experimental manner with unproven interventions on potentially suicidal persons is just awful,” New York University bioethics professor Arthur Caplan was quoted as saying.

“If this is the way entrepreneurs think they can establish AI for mental diseases and conditions, they had best plan for a launch filled with backlash, lawsuits, condemnation and criticism. All of which are entirely earned and deserved.”

“I have not in recent years seen a study so callously asleep at the ethical wheel. Dealing with suicidal persons in this way is inexcusable,” he added.


Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link

Hiring Freezes, Bonuses Delayed, and More

0
[ad_1]

tim cook defends app store monopoly

Amidst the current economic uncertainties impacting the tech industry, Apple is also encountering challenges. According to a new report from Bloomberg, Apple has implemented changes in the budget as it scrutinizes and reviews expenses and spending.

According to the report, Apple is delaying bonuses for some teams, freezing hiring across more departments, and reducing travel budgets for many teams. The company is also requiring SVP’s approval for more budget items and closely monitoring how often employees come into the office versus working remotely.

In addition to these changes to its expenses, Apple is also making changes to the bonus schedule. Previously, Apple used to distribute bonuses and promotions once or twice a year, depending on the division, with payments occurring in April and October. However, the company is now transitioning to an annual bonus schedule, where bonuses will only be paid out in October for all teams.

In the past, Apple typically doled out bonuses and promotions once or twice per year depending on the division. The twice-a-year teams usually saw that happen in April and October. Under the new plan, that group won’t see bonuses or promotions next month, and all divisions will move to an annual schedule — with the payments occurring only in October.

Despite this shift, employees will still receive their full bonuses. The move applies to engineers and other non-managers as well as mid-level managers, but not senior employees at the director level and above.

Apple has also decided to expand its hiring freeze to encompass additional roles. Unlike many tech companies, Apple has avoided layoffs within the company. While tech giants like Amazon, Google, and Meta have laid off thousands of employees recently, Apple has looked at other ways to cut costs amid economic uncertainty. 

Source: Bloomberg


[ad_2]
Source link

Rumor says Google eyeing Summer launch for Pixel Fold & Pixel 7a

0
[ad_1]

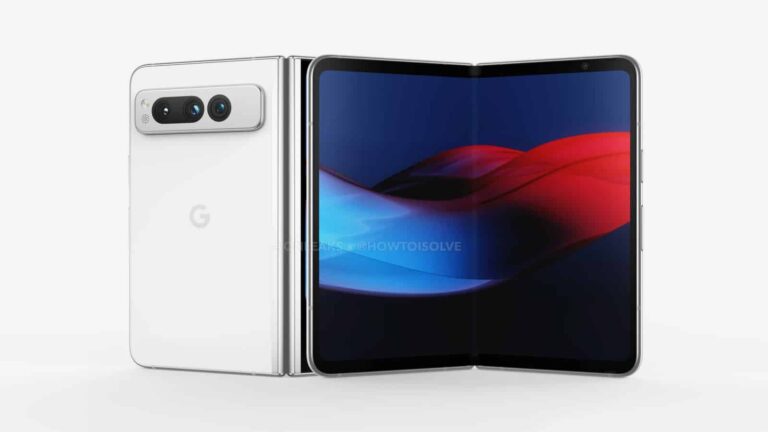
The Pixel Fold and Pixel 7a will be Google’s next big devices in the Pixel lineup, and it appears that they may be set to launch in the Summer. According to a retail listing that was spotted by 9To5Google, the plan is to launch the two devices in June of this year. Google is also expected to unveil these devices officially at its upcoming Google I/O event in May. Which would fit with the June timeframe for a Pixel Fold and Pixel 7a launch.

Using past Pixel devices as an example here, Google typically releases its newest Pixel phones just a few weeks after it announces them. The listing apparently didn’t mention pricing for the Google Pixel Fold or the Google Pixel 7a. So there’s still no word on a confirmed cost. But there are other interesting details about both devices the retail listing uncovers.

The Google Pixel Fold will launch this Summer in two colors

Although the pricing is still unclear, foldables generally aren’t cheap phones. And Google’s Pixel Fold shouldn’t be any different there. If you’re more concerned with colors than price, it looks like you’ll have two options with the Fold. According to the listing, the phone will come in Carbon and Porcelain. In addition to colors, the Fold was listed in a 256GB model. Although a 512GB model has been leaked prior to this latest rumor.

When it comes to the Pixel 7a, the phone is said to be coming in Carbon, Cotton, and Arctic Blue. As for storage, 128GB appears to be the only option buyers will have. The listing also mentions case color options. Which include Jade, Carbon, Cotton, and Arctic Blue for the Pixel 7a. With the retail listings now having been spotted, there isn’t a whole lot left to learn of these two devices, it seems.


[ad_2]
Source link

ChatGPT technology might come to General Motors vehicles

0
[ad_1]

General Motors seeks to incorporate AI driving assistants into its vehicles using ChatGPT and Bing technology. According to ZDNet, the carmaker is currently working with Microsoft, and the technology might come to Chevrolet, Cadillac, Buick, and GMC cars in the next few years.

Artificial intelligence (AI) is changing everything. It’s safe to say that after unveiling ChatGPT, the world will never be the same. Companies in different industries leverage AI more than ever, and automakers want to stay caught up. As the largest car manufacturer in the US, General Motors is also working on an AI driving assistant for its future vehicles.

The report continues that GM plans to develop a human-to-car relationship that can automate many driving parts. The company was already spotted working on a voice assistant based on ChatGPT technology. The GM’s voice assistant reportedly uses Microsoft’s Azure cloud service, which means the company can access the core technology of Dall-E, ChatGPT, and Bing.

General Motors is developing an AI driving assistant by ChatGPT technology

Most modern cars use advanced technologies like automatic braking, semi-autonomous driving, and collision warning. While these are becoming standard vehicle features, companies like GM want to take the initiative to make driving safer by automating specific actions.

The idea of bringing a voice assistant to a car seems genuine as AI rapidly grows. Voice assistants on smartphones and smart speakers are mostly used to issue commands like playing music or reading the latest news headlines. In vehicles, however, a voice assistant can notify the driver of remaining fuel, tires pressures condition, or how to fix a specific issue. Novice drivers might also be able to receive tutorials from the virtual assistant.

Yet, the scope of AI in vehicles should be examined, but it can be very helpful in eliminating distractions. For example, drivers can use voice assistants to adjust the temperature or find a specific location on the navigation app. This prevents drivers from taking their eyes off the road and encourages safe driving.


[ad_2]
Source link

Clop ransomware is victimizing GoAnywhere MFT customers

0
[ad_1]

The Clop ransomware gang has claimed responsibility for attacking several GoAnywhere MFT customers by exploiting a vulnerability in the managed file transfer software’s administrative interface.

According to information gathered by BleepingComputer, the Clop ransomware group has claimed responsibility for the ransomware attacks that are tied to a vulnerability in the Fortra GoAnywhere MFT secure file-sharing solution.

As we reported on February 8, Fortra released an emergency patch (7.1.2) for an actively exploited zero-day vulnerability found in the GoAnywhere MFT administrator console.

GoAnywhere MFT, which stands for managed file transfer, allows businesses to manage and exchange files in a secure and compliant way. According to its website, it caters to more than 3,000 organizations, predominantly ones with over 10,000 employees and 1B USD in revenue.

Some of these organizations are considered vital infrastructure such as local governments, financial companies, healthcare organizations, energy firms, and technology manufacturers.

The day after the release of the GoAnywhere patch, the Clop ransomware gang contacted BleepingComputer and said they had used the flaw over ten days to steal data from 130 companies. At the time it was impossible to confirm this claim, but after two earlier victims, Community Health Systems (CHS) and Hatch Bank disclosed that data was stolen in the GoAnywhere MFT attacks, the Clop leak site now shows seven new companies. At least two of them reportedly have been breached using the GoAnywhere MFT vulnerability.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The CVE of the exploited vulnerability is CVE-2023-0669, and described as a pre-authentication command injection vulnerability in the License Response Servlet due to deserializing an arbitrary attacker-controlled object.

It is unknown whether these victims were targeted during the time that there was no patch available for the vulnerability or later. Recent scans showed that around 1,000 administrative consoles are publicly exposed to the internet. The Web Client interface, which is the one that is normally accessible from the public internet, is not susceptible to this exploit, only the administrative interface.

Mitigation

If your GoAnywhere MFT administration portal is exposed to the Internet, you are under urgent advice to download the security patch from the Product Downloads tab at the top of the GoAnywhere account page which you will see after logging in.

If for some reason you can’t install the patch, Fortra says you should follow the mitigation steps it put out, which involves implementing some access control wherein the administrator console interface should only be accessed from trusted sources, or disabling the licensing service altogether. There is also a technical mitigation configuration shared in the advisory that is only visible after logging in (which can be done with a free account if you are interested).

On the file system where GoAnywhere MFT is installed, edit the file [install_dir]/adminroot/WEB_INF/web.xml

 Find and remove (delete or comment out) the following servlet and servlet-mapping configuration in the screenshot below.

 Before:

 <servlet>

      <servlet-name>License Response Servlet</servlet-name>

      <servlet-class>com.linoma.ga.ui.admin.servlet.LicenseResponseServlet</servlet-class>

      <load-on-startup>0</load-on-startup>

 </servlet>

 <servlet-mapping>

      <servlet-name>Licenses Response Servlet</servlet-name>

      <url-pattern>/lic/accept/</url-pattern>


After:

 <!–

 Add these tags to comment out the following section (as shown) or simply delete this section if you are not familiar with XML comments

 <servlet>

      <servlet-name>License Response Servlet</servlet-name>

      <servlet-class>com.linoma.ga.ui.admin.servlet.LicenseResponseServlet</servlet-class>

      <load-on-startup>0</load-on-startup>

 </servlet>

 <servlet-mapping>

      <servlet-name>Licenses Response Servlet</servlet-name>

      <url-pattern>/lic/accept/</url-pattern>

 </servlet-mapping>

  –>


Restart the GoAnywhere MFT application

If GoAnywhere MFT is clustered, this change needs to happen on every instance node in the cluster.

If you have questions, our support team is here to help.  Please contact Support via the portal https://my.goanywhere.com/, email goanywhere.support@helpsystems.com, or phone 402-944-4242 for assistance.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW

[ad_2]
Source link

Apple Launches the iPhone 14 and iPhone 14 Plus in Yellow Today

0
[ad_1]

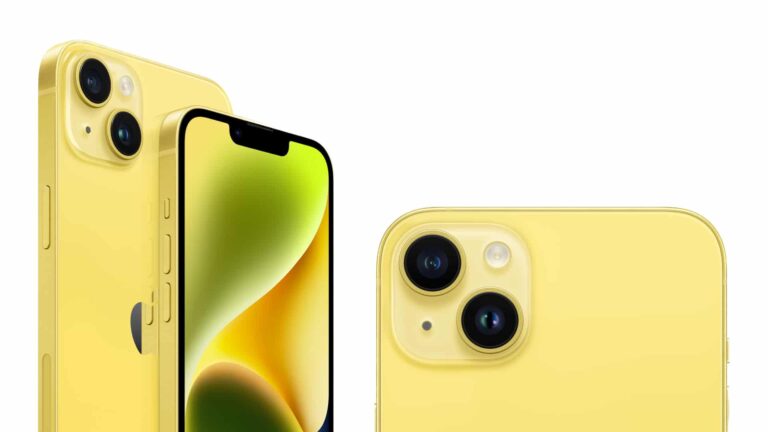
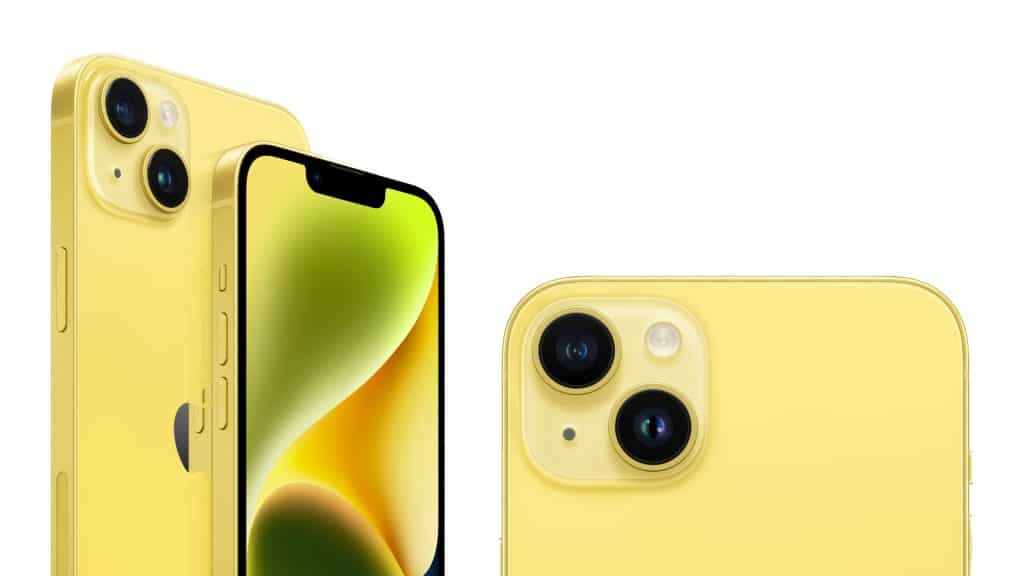
iPhone 14 Yellow Color

The iPhone 14 and 14 Plus launched today in yellow color and are available for pickup and same-day delivery in the United States and other countries. 

Talks of a new color option for the iPhone 14 models started as a rumor on the Chinese Social media platform Weibo earlier in the month. However, a report from Bloomberg’s Mark Gurman and another independent statement by Mac Otakara quickly confirmed the claim. 

On March 7, Apple finally announced the iPhone 14 and 14 Plus in yellow, adding to the existing shades — Midnight, Starlight, (PRODUCT)RED, Blue, and Purple options — in the lineup.

“People love their iPhone and rely on it every day for all that they do,” said Bob Borchers, Apple’s vice president of Worldwide Product Marketing. “And now there’s an exciting addition to the lineup with a new yellow iPhone 14 and iPhone 14 Plus.”  

However, the device was only available for pre-order; until now. 

Starting today, customers can purchase the iPhone 14 and iPhone 14 Plus in the Yellow color without pre-ordering. Instead, they only have to use the App Store app or Apple online store to order the yellow device for pickup.

Here’s a breakdown of the purchase process: 

  • Select the “I’ll pick it up” option at checkout 
  • Enter your postal or ZIP code
  • Pick the nearest Apple Store location

After that, customers can choose their preferred pickup date for the device, including a 15-minute check-in window. Meanwhile, previous online pre-orders began arriving to customers today. 

There’s just one small question: 

 Are There Any Changes on the Yellow iPhone 14 Model?

The answer is a resounding no! Besides the new finish, the iPhone 14 and iPhone 14 Plus remains the same. 

So you would get a 6.1 or 6.7-inch device with the familiar Ceramic Shield front cover, flat edges, and an aerospace-grade aluminum enclosure. Internally, the device still has a dual-camera system, a powerful A15 Bionic chip, and the same battery life. 

So why did Apple release the new color option? 

Apple releases new color shades in the spring to boost sales midway through the iPhone’s product cycle. Last year, the tech giant rolled out a new Green color for the iPhone 13 and iPhone 13 mini, while the iPhone 13 Pro models got a new Alpine Green color. So there’s a precedent. 

Buyers in Australia, Canada, China, France, Germany, India, Japan, South Korea, the U.K., and the United States can purchase the Yellow iPhone 14 models today. The shade is also available in over 60 other countries and regions.  


[ad_2]
Source link