Misleading Data Safety Labels on the Google Play Store

0
[ad_1]
Google Play Store Privacy

According to a Mozilla analysis, the majority of the top apps’ data privacy labels on the Google Play Store are false or deceptive.

“Google Play Store’s misleading Data Safety labels give users a false sense of security. Honest nutrition labels help us eat better. It’s time we have honest data safety labels to help us better protect our privacy”, Jen Caltrider, Project Lead, Mozilla

TikTok and Twitter do not share your personal information with third parties, contrary to what the Data Safety labels in the Google Play Store would have you believe. 

Nonetheless, the privacy rules of the apps clearly mention that they share user data with platforms, advertisers, ISPs, and a wide range of other companies.
“In nearly 80 percent of the apps reviewed, Mozilla found that the labels were false or misleading based on discrepancies between the apps’ privacy policies and the information apps self-reported on Google’s Data Safety Form”, reports Mozilla.

Researchers have determined that the system falls short of assisting users in making more informed decisions regarding their privacy prior to making a purchase or downloading one of the 2.7 million apps available on the store.

Misleading Data Safety Labels on the Google Play Store

The 20 most popular paid apps and the 20 most popular free apps on the Google Play Store were compared for the study’s privacy policies and labeling. Afterward, a rating of “Poor,” “Needs Improvement,” or “OK” was given to each app. 

It gave a “Poor” rating to 40% of the examined apps, including Facebook, Twitter, and Minecraft, since their Data Safety Forms contained discrepancies.

Notably, only 15% of apps, including Candy Crush Saga, Google Play Games, and others, received an “Ok” rating because their privacy policies closely matched their disclosures, while 37.5% of apps, including YouTube, Google Maps, Gmail, WhatsApp Messenger, TikTok, and Instagram, were rated as “need improvement”. 

While Terraria, League of Stickman Acti, and UC Browser – Safe, Fast, Private did not complete the form, three other apps did.

“Consumers care about privacy and want to make smart decisions when they download apps. Google’s Data Safety labels are supposed to help them do that. Unfortunately, they don’t. Instead, I’m worried they do more harm than good,” said Jen Caltrider.

“When I see Data Safety labels stating that apps like Twitter or TikTok don’t share data with third parties it makes me angry because it is completely untrue. Of course, Twitter and TikTok share data with third parties. Consumers deserve better. Google must do better.”

The Data Safety form has flaws that make it simple for apps to offer false information. Additionally, Google releases itself from the obligation to validate the information given by apps by noting in its Data Safety Labeling that apps “are responsible for providing complete and accurate declarations,” according to the report.

“The history of nutrition labeling shows that it’s possible to create a standardized system that becomes part of the cultural fabric and makes a positive difference in people’s daily lives,” said Caltrider

Recommendation

Mozilla suggests that Google and Apple implement a global, standardized data privacy system on their platforms as a solution to the issue. 

Mozilla also urges the companies to take more responsibility for assuring the accuracy of the data the applications disclose and to clarify and expand their enforcement action against apps.

Network Security Checklist – Download Free E-Book


[ad_2]
Source link
DNA testing company fined after customer data theft

0
[ad_1]

DNA Diagnostics Center, a leading DNA testing company, failed to protect client data it inherited from another company it acquired years before.

DNA Diagnostics Center (DDC), an Ohio-based private DNA testing company, last week reached a settlement deal with the Ohio and Pennsylvania state attorneys general in relation to a 2021 breach that saw the theft of 45,000 residents‘ personal details. Overall the attack compromised over 2.1 million customers who had undergone genetic testing across the US.

The company will pay a total fine of $400,000 for Ohio and Pennsylvania—and has promised to tighten its information security.

What happened in the 2021 breach

When DDC acquired Orchid Cellmark, a British company also in the DNA testing industry, as part of its business expansion in 2012, the company didn’t know that it also inherited legacy databases that kept personally identifiable information (PII) in plain text form. According to court documents, “the Breach’s impacted databases, containing sensitive personal information, were inadvertently transferred to DDC without its knowledge. Moreover, DDC asserts it was not aware that these legacy databases existed in its systems at the time of the Breach—more than nine years after the acquisition.”

DDC said it conducts both inventory assessment and penetration testing on its systems. But since it was unaware of the unused databases, they were not included during the tests as the assessments focused only on those with active customer data.

In May 2021, one of DDC’s MSPs (managed service providers) began sending automated alerts over a two-month period about suspicious activities within its network. Court documents didn’t reveal why DDC didn’t act on the alerts, but three months after, the same MSP notified DDC again, this time about Cobalt Strike malware activity in its network. This triggered the company’s incident response plan.

According to the investigation, an attacker logged into the old VPN (virtual private network) that DDC used before migrating to a new one using a compromised employee account. It’s not known how this account ended up in the attacker’s hands, but they were able to harvest Active Directory (AD) credentials from a domain controller, a server providing security authentication for users. Weeks after, the attacker used a test account with administrator privileges to establish persistence in the now-compromised environment. They then unleashed Cobalt Strike.

In the following weeks, the attacker accessed five servers and copied 28 databases. They then exfiltrated data from DDC using a decommissioned server. Finally, in September, the attacker contacted DDC to extort payment for all the data they had. The company paid up to have all copied data deleted.

No threat group has owned up to the attack.

The Commonwealth took issue with DDC engaging in “deceptive or unfair business practices by making material misrepresentations in its customer-facing privacy policy concerning the safeguarding of its customers’ personal information.” Evidence of this was when DDC “disseminated, or caused to be disseminated” statements in its Privacy Policy, stating the company is committed to protecting the information of its clients. Yet, the Commonwealth alleges it “failed to employ reasonable measures to detect and prevent unauthorized access to its computer network,” leading to the compromise of Pennsylvanians’ data. 

“Negligence is not an excuse for letting consumer data get stolen,” said Ohio Attorney General Dave Yost in a statement. Acting Attorney General Michelle Henry added, “The more personal information these criminals gain access to, the more vulnerable the person whose information was stolen becomes.”

Terms of settlement

DDA is required to develop an information security program that is “reasonably designed” to protect user data. An employee or third-party service provider with appropriate credentials and expertise must be assigned to oversee the prram.

The company is also ordered to conduct comprehensive annual risk assessments of its networks where sensitive client data are stored, maintain an asset inventory, create and implement an incident response plan, and remove any assets that are not used or necessary for business purposes. 

Lastly, DDA must create and implement security measures for the overall protection of personal data it stores, including regularly updating software, controlling user access (such as the use of two-factor authentication), conducting network penetration testing, segmenting the network, and maintaining a central log management system, among others.

The infosec program must be developed and implemented within 180 days (six months).


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Sony Xperia 5 V appears with Snapdragon 8 Gen 2 & 16GB of RAM

0
[ad_1]

The Sony Xperia 5 V has just surfaced online with the Snapdragon 8 Gen 2 SoC, and 16GB of RAM. Needless to say, these are immensely powerful specs. The device appeared on Geekbench, and the listing revealed some additional details.

The Sony Xperia 5 V is coming with Snapdragon 8 Gen 2 & 16GB of RAM

The phone appeared with the ‘Sony XQ-DQ72’ model number. It managed to score 1,439 points in the single-core, and 5,071 points in the multi-core test. Do note that this may be a pre-production unit, though.

The listing reveals that Android 13 will come pre-installed on the device. Other than that, and the SoC and RAM info, nothing else got revealed on Geekbench. This is plenty to go on, though.

The Sony Xperia 5 V will be smaller than the flagship Xperia 1 V. The Xperia 5 IV included a 6.1-inch display, and something similar is expected here. Considering its clean software, and high-end specs, this phone may appeal to those of you who want a more compact device.

The Sony Xperia 5 V will compete with the likes of the Galaxy S23, and the upcoming ASUS ZenFone 10 this year, presuming that ASUS sticks to a compact form factor. Those will be the three high-end compact devices out there.

We’re not sure when will the device launch, though

The thing is, we don’t know when will this handset arrive. The Xperia 5 III launched in April 2021, while the Xperia 5 IV arrived in August 2022. So your guess is as good as ours. Also, Sony usually takes its sweet time to make a phone available to purchase after it launches.

We do hope that the company will change its ways this year. Sony’s smartphones are appealing in their own right, so it would be nice to see them arrive sooner this time around.


[ad_2]
Source link

iPhone 15 Pro in “special edition” dark red color gets shown off early

0
[ad_1]

Plenty of iPhone 15 and iPhone 15 Pro info surfaced recently, and some graphic info came from 9to5Mac. The site first shared the iPhone 15 Pro CAD-based renders, and then showed us the iPhone 15 and iPhone 15 Pro side-by-side. The same source is now back to show us what a “special edition” iPhone 15 Pro will look like in its dark red color.

The iPhone 15 Pro will be available in a “special edition” dark red color

As many of you know, iPhone tends to offer its ‘Pro’ model in a special edition color every year. Well, this time around, it seems like that color will be dark red. 9to5Mac partnered up with Ian Zelbo to show us what the phone will look like.

If you check out the image below, you’ll see a mock-up of the device, based on CAD renders, and with a very dark red color applied to it. The color hex of $410D0D was used here, but the final product may look a bit different, of course.

iPhone 15 Pro dark red image CAD 1

The standard iPhone 15 models may arrive in either a light blue, or a pink color

What about the standard iPhone 15 models, the iPhone 15 and iPhone 15 Plus? Well, the source says that Apple is testing light blue and pink colors (shown below the paragraph). It is noted that it’s still very early, and Apple could change its mind.

What is interesting is that Apple is rumored to switch to Titanium this year, for the Pro models. It will allegedly replace stainless steel with titanium. So it will be interesting to see what will the final product look like.

The entire iPhone 15 series is expected to arrive in September, as per usual. We do already have plenty of information on the changes we can expect, though. All iPhone 15 products will include a Type-C port at the bottom, and a Dynamic Island too.

The iPhone 15 Pro series devices will include thinner bezels this time around, and a frame made out of Titanium. The iPhone 15 vanilla model may actually have a slightly larger display than the iPhone 15 Pro this time around, a 6.2-inch panel vs a 6.1-inch one.


[ad_2]
Source link

Beware of this new malware hitting YouTube and Facebook accounts

0
[ad_1]

There’s a new malware roaming free online right now. It hijacks people’s social media accounts, steals login credentials, and mines cryptocurrencies using people’s devices, reports TechRadar.

New malware exploits users’ YouTube and Facebook account


The info comes from researchers from Bitdefender’s Advanced Threat Control Team (ATC), which found a new strain of malware named S1deload Stealer. The malware tries to avoid being detected by antivirus programs by using DLL sideloading. In the second half of 2022, malicious users were able to infect hundreds of users.Bitdefender products detected more than 600 unique users infected with this malware between July and December 2022, Dávid Ács, a researcher from Bitdefender, stated.

The malware needs to be downloaded and run by the victims themselves. It was hidden in archives (.zip files) that allegedly had adult content. When the victims downloaded and run the “content”, they didn’t find what they were looking for but instead got their devices infected with an infostealer.

Here’s what this malware is capable of. First, it can download a headless Chrome browser that runs in the background. It opens YouTube vids and Facebook posts and rakes up views. It can also download and run an infostealer that decrypts login credentials saved in browsers, as well as session cookies.

When it comes to a Facebook account, it tries to analyze it. It looks for whether the account administrates any Facebook pages or groups, if it pays for ads, or if it’s linked to a business manager account. All in all, you can imagine this makes the account even more valuable.

And then it can go ahead and download, install, and run a cryptocurrency miner. It mines the BEAM cryptocurrency for hackers. By the way, the hacker can also use the stolen credentials to spam on social media and try to infect even more machines.

A more techy explanation of the malware’s actions can be found on Bleeping Computer’s article. The moral of the story: don’t download shady things from the internet.


[ad_2]
Source link

Hackers Use Open-Source Tools to Attack Shipping Companies

0
[ad_1]
Hackers Use Open-Source Tools

There has been an emergence of a new security threat that has been causing havoc among the Asian shipping and medical laboratory industries.

It’s a never-before-seen threat group dubbed Hydrochasma, actively targeting the shipping and medical organizations that are engaged in research and treatment of the COVID-19 vaccine.

Symantec, a company under Broadcom, has been monitoring the activities of cybercriminals since October of last year. Their ultimate aim seems to be the acquisition of valuable information.

Modus Operandi of Attack

Hydrochasma’s modus operandi is unique in that they employ open-source tools and LotL techniques during their attacks. This enables them to carry out their malicious activities without leaving behind any traces that could potentially expose their identity. 

This method of operation poses a challenge to those attempting to track and attribute the attacks to specific threat actors.

The origin and affiliation of this threat actor have not been determined, nor has any evidence yet been collected as to its origin. 

The utilization of pre-existing tools seems to serve a dual purpose for Hydrochasma:- 

  • To evade attribution efforts
  • To enhance the stealthiness of their attacks

By leveraging these tools, they can mask their activity and blend in with legitimate network traffic, making it more challenging for security experts to detect and respond to their malicious activities.

Attack Chain

Most likely, Hydrochasma infected its host with a phishing email in order to spread its infection. Initial signs of Hydrochasma’s presence on a targeted system are often indicated by the appearance of a lure document, with a file name that is crafted to appear as if it were an email attachment written in the native language of the victim organization. 

This is an attempt to deceive the target into thinking that the document is legitimate and relevant to their work. Here below we have mentioned those attachment names:-

  • Product Specification-Freight-Company Qualification Information wps-pdf Export.pdf[.]exe
  • University-Development Engineer[.]exe

Once the attacker gains access to a machine, they utilize this access to deploy a Fast Reverse Proxy (FRP), which has the potential to expose servers that are located behind a firewall to the public web.

Tools Used

Here below we have mentioned all the tools that are dropped by the intruder on the affected system:-

  • Gogo scanning tool
  • Process Dumper (lsass.exe)
  • Cobalt Strike Beacon
  • AlliN scanning tool
  • Fscan
  • Dogz proxy tool
  • SoftEtherVPN
  • Procdump
  • BrowserGhost
  • Gost proxy
  • Ntlmrelay
  • Task Scheduler
  • Go-strip
  • HackBrowserData

It is extremely difficult to relate the activity to any specific threat group when a large number of publicly available tools are used. 

There was no evidence that any data was taken from any of the targeted computers by Hydrochasma according to researchers from Symantec. Hydrochasma on the other hand utilizes certain tools that allow remote access to the system, which could result in data being extracted from the system.

This attack appears to have been motivated by a mission to gather intelligence, as indicated by the sectors targeted.

Network Security Checklist – Download Free E-Book


[ad_2]
Source link
Lehigh Valley Health Network targeted by BlackCat ransomware

0
[ad_1]

The Lehigh Valley Health Network stated it was the target of a cybersecurity attack by a ransomware gang known as BlackCat

In a statement issued Monday morning, Lehigh Valley Health Network said it had been the target of a cyberattack attributed to a ransomware gang known as BlackCat. The Network is made up of 13 hospital campuses, as well as other health facilities, and is based in Pennsylvania.

BlackCat

The ransomware-as-a-service (RaaS) group BlackCat, also known as ALPHV and Noberus, is currently one of the most active groups, and has been associated with Russia. In our recent February ransomware review it came in second after Lockbit, based on the number of known attacks.

In December, 2022, the Office of Information Security and Health Sector Cybersecurity Coordination Center issued an extensive Analyst Note which identified BlackCat as a “relatively new but highly-capable” ransomware threat to health care providers.

BlackCat uses double extortion and sometimes triple extortion to make victims pay the ransom. That means that besides encrypting files, the gang also threaten to publish the stolen data on a so-called “leak site”, and at times, threaten their victims with DDoS attacks.

The attack

According to the health network, the attack targeted the network supporting Delta Medix, a physician practice in Lackawanna County. The unauthorized activity was detected on February 6, 2023 and involved a computer system used for patient images for radiation oncology treatment and other sensitive information.

The health network is investigating the full scope of the attack, but says services have not been disrupted, although its websites seem to be offline for the moment. It was unable to say yet whether any specific patient’s personal or sensitive information was compromised, but promised to inform any affected individuals if it discovers that was the case.

No ransom

The Lehigh Valley Health Network said it has refused to pay a ransom, but did not disclose the demanded amount. According to the US Department of Health and Human Services (HHS) The BlackCat group has demanded ransoms as high as $1.5 million in previous cybersecurity attacks against the healthcare sector.

Dr. Brian Nester, the health network’s president and CEO said:

“BlackCat demanded a ransom payment, but LVHN refused to pay this criminal enterprise. We understand that BlackCat has targeted other organizations in the academic and health care sectors. We are continuing to work closely with our cybersecurity experts to evaluate the information involved and will provide notices to individuals as required as soon as possible. Attacks like this are reprehensible and we are dedicating appropriate resources to respond to this incident.”

Recent reports indicated that ransomware revenue went significantly down over 2022, likely due to companies’ increasing unwillingness to meet the ransom demands.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Write an incident response plan. The period after a ransomware attack can be chaotic. Make a plan that outlines how you’ll isolate an outbreak, communicate with stakeholders, and restore your systems.

We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Artifact, from Instagram co-founders, is available to everyone

0
[ad_1]

We’re used to seeing former members of major companies spin off and start their own ventures. Instagram co-founders Kevin Systrom and Mike Krieger started a company called Artifact, and its app is now available to everyone.

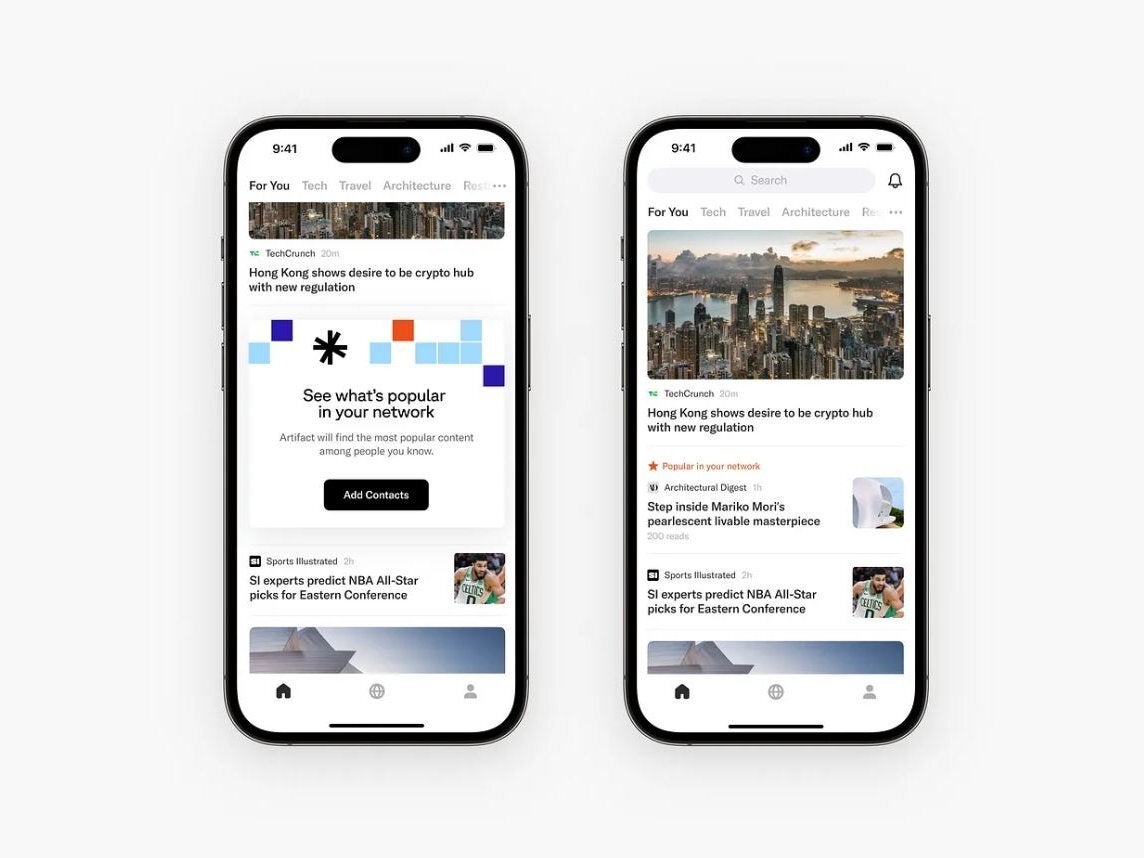
Artifact is a news curation app with the simple goal of giving you news articles based on your interests. A large part of the company’s marketing is that it uses artificial intelligence to deliver your news. It aims to give you exactly the kind of articles that you need without the noise.

This sounds like an interesting idea, but the app wasn’t ready for mass downloading just yet. You needed to join a waitlist if you wanted to gain access to the app. This was unfortunate for people who were excited about the app.

Fortunately, Artifact is now available for everyone to download

People who are tired of waiting for this app to make it to everyone should rejoice. Kevin Systrom just posted a tweet letting us know that the wait is now over. It was accompanied by a sizzle reel showing a little of what the app is about.

As stated before, it’s an article curation app that gives you articles about only what you want to see. When you get the app, you can enter it and start reading articles. However, if you want to transfer your data to another device, you have the ability to create an account. It’s not the whole email address and password shebang. You only need to use your phone number.

Artifact UI

Then, you’re able to pick 10 or more topics that you want to receive articles about. At the moment, there are 54 topics that you can choose from. These include tech, science, TV & Movie, celebrities, cars, fashion, and so on. You have to pick at least 10 when you’re setting up your profile, but you can adjust your selection later.

After you set up your profile, you’ll see a main feed of articles that are curated by your reading history. Also, if you only want to read articles about a specific topic, you can select one of the tabs up top.

This is a useful app if you want to keep up to date with the latest headlines. Click on the link below to download it for the Google Play Store.

Download Artifact


[ad_2]
Source link

Consoles in 2023: what to choose?

0
[ad_1]

The console wars are a never-ending battle, making it difficult to choose the best system. But in 2023, three systems have risen above the rest: PlayStation 5, Xbox Series X, and Nintendo Switch OLED. All of them are different in terms of characteristics and price, so everyone can enjoy the gameplay without taking out loans and worrying about the question, “can you go to jail for debt” if you don’t pay them.

So if you’re looking for your perfect gaming companion – read on! With these consoles offering superior graphics and immense power – there’s something out there that will meet all of your gaming needs.

The popularity of the gaming industry

The gaming industry continues to gain popularity across the world, with Statista predicting an increase in worldwide video game users from 3.2 billion people in 2021 to 3.6 billion by 2026. This rapid growth trend will likely continue as many prominent companies have released new products and technology components over the past few years.

Statista image 8398349348

As these new innovations add value to the gaming experience, such as expanding online connectivity, increasing graphical capabilities, and offering immersive virtual experiences, it is no surprise that more people are hoping to jump into the action.

The market size of the video game industry already surpasses the movie box office revenues, with its revenue reaching over fifty-two billion USD globally in 2019 and expected to grow at a CAGR of 10.31%.

With web gaming becoming increasingly popular amongst gamers due to its ease of access, diverse gameplay options, and affordability through free-to-play titles, casual gamers can join in on all of the fun, allowing for even faster growth within this ever-growing entertainment sector.

Console vs. PC: what is better?

The answer largely depends on personal preference when choosing between a console or PC for gaming. Consoles are often preferred for those looking for a more cost-effective option and greater convenience.

Consoles also provide gamers access to exclusive titles that cannot be found on PC and easy-to-navigate menus and controllers designed specifically with gaming in mind. On the other hand, PCs offer their own benefits, such as faster loading times, higher graphical fidelity, and better modding support.

Additionally, PCs come with more customization options than consoles which may appeal to those looking for even further performance optimization beyond what is available out of the box. Ultimately both consoles and PCs provide an excellent platform for gaming, and which one you choose depends on your own specific needs and preferences.

The Xbox Series X

The Xbox Series X is the must-have console for the gamer who wants to experience gaming in its highest form. With 12 teraflops of processing power, games will run at up to 120 frames-per-second and 8K resolution, offering lightning-fast loading times and unbeatable graphics.

Plus, with over 50 classic games available via backwards compatibility, gamers can have access to a huge selection of classic titles from the last two generations of Xbox. With improved audio capabilities too, Dolby Atmos support provides incredible sound quality.

The new Quick Resume feature allows gamers to switch between games instantly and pick up where they left off. The Xbox Series X gives players all they need in their latest generation console.

The PlayStation 5

With the release of the PlayStation 5, gamers have more powerful hardware and incredible gaming options than ever before. With a high-performance CPU and GPU combination, games that look and feel realistic have never been better.

This next-generation console supports high-quality visuals while reducing the loading time, allowing players to get into the thick of their games faster.

Its graphics look impressive, and its innovative storage means far fewer downloads, so fans can start playing right away. Whether it’s triple-A exclusives or free-to-play titles, PlayStation 5 owners are sure to love having access to some of the best video games available today.

Nintendo Switch Lite

The Nintendo Switch Lite has become a must-have for families everywhere! Combining the best of both worlds – portability, and versatility – this console is the perfect blend of entertainment for busy households.

It provides access to a wide variety of family-friendly games that any age can enjoy, and it’s small enough to take on road trips or keep in the living room. Whether you’re looking for educational titles, racing games, puzzles, virtual reality experiences, or at-home sing-alongs, the Nintendo Switch Lite has something to offer everyone in your family.

With its child-friendly design and parental control options, it’s easy to see why it has become one of the most popular consoles for young gamers.

The Xbox Series S

The Xbox Series S is a great console for those looking for a budget-friendly option. It has an 8-core AMD Zambezi processor and 10GB of RAM, so you’ll see a noticeable performance increase over the previous Xbox One series models.

It also features faster load times, improved frame rates, and increased resolution. However, it is important to remember that while the Series S is great in terms of its value proposition, some of its more powerful rivals will be able to outperform it in various games.

Of course, with access to backward compatible games from all generations of Xbox consoles up to the Xbox 360, plenty of titles are available so long as you say within the Series S’ price range.

The Nintendo Switch with OLED

The Nintendo Switch, with an OLED display, is the latest handheld gaming console to take the industry by storm. This portable powerhouse provides the user with stunning visuals and superior performance, taking mobile gaming to a new level.

Supports for wireless Joy-Con controllers and HD rumble provide a more immersive experience than ever before. With its sleek design, strong battery life, ergonomic shape, and lightweight portability, you can be sure of an enjoyable gaming session no matter where you are. Whether on a plane or at home in your living room – the Nintendo Switch OLED allows gamers to have an amazing experience unlike anything else on the market today.

Conclusion

In conclusion, the market for gaming consoles has become more robust due to the recent production of new and improved consoles like Nintendo Switch OLED, Xbox Series X, PlayStation 5, Nintendo Switch Lite, and Xbox Series S.

While each console is designed differently with varying capabilities and features, they all offer exciting gameplay experiences that are sure to please gamers of any kind.

Whether you’re looking to invest in a powerful gaming console or a cheaper option that still delivers on performance, there’s an option out there for everyone. Researching and comparing the available consoles goes a long way towards finding what best suits your budget and gameplay needs.


[ad_2]
Source link

Artifact: the AI-powered news app, created by Instagram co-founders, is now live

0
[ad_1]
So you probably know what a news feed client is. Even if you are not using one, basically any platform that can serve up a curated list of news topics from across different publications is considered a news feed. And nowadays, even if you aren’t interested in keeping up with the latest news, feeds are everywhere: even in your browser! Well, yesterday a new fighter entered the fray: Artifact. The app is created by two of the co-founders of Instagram, and is noteworthy for being powered by AI. Said AI is working in the background to get a grasp of what sort of stories you are into, while still offering some handy tools to filter out anything that isn’t to your liking.

So basically, the goal here is to help users create an ultra-curated feed of content. Sounds a tad familiar to some prolific social media networks, but let’s not digress.

Artifact is live right now and available for both iOS and Android smartphones. The app is free and will allow you to use it without signing up via phone number, but you can also do that if you’d like to save your profile. And we’ll get back to why that might be important a bit later on again.

The setup process is really simple and easy to follow. The app provides you with a list of topics from which you can choose the ones you are interested in. Then you can add any paid subscriptions to news publications you might have. Naturally, the app will want to send you notifications about breaking news, but you can kindly decline the offer.

The AI will need some help in order to get to know you better though. You’ll have to read at least 25 stories per day for a 14-day period in order for it to start recommending the type of content you are looking for. It is kind of cool that the app has a dedicated section to show your progress towards this goal.

On that same section, you can also sign up through adding a mobile number in order to save your progress. And you might want to do that, especially if you’ve opted to complete the aforementioned 14-day challenge. The app has no indication of the sign-up costing anything, and it doesn’t look like it would pester you restlessly through SMS pokes.

Given that Artifact is developed by co-founders of Instagram, is it any wonder that it also has some social features? Not annoying ones, mind you. You can invite some friends to the app, and it will periodically let you know what type of content they are interested in, which is an interesting way of peeping on your buddies online.

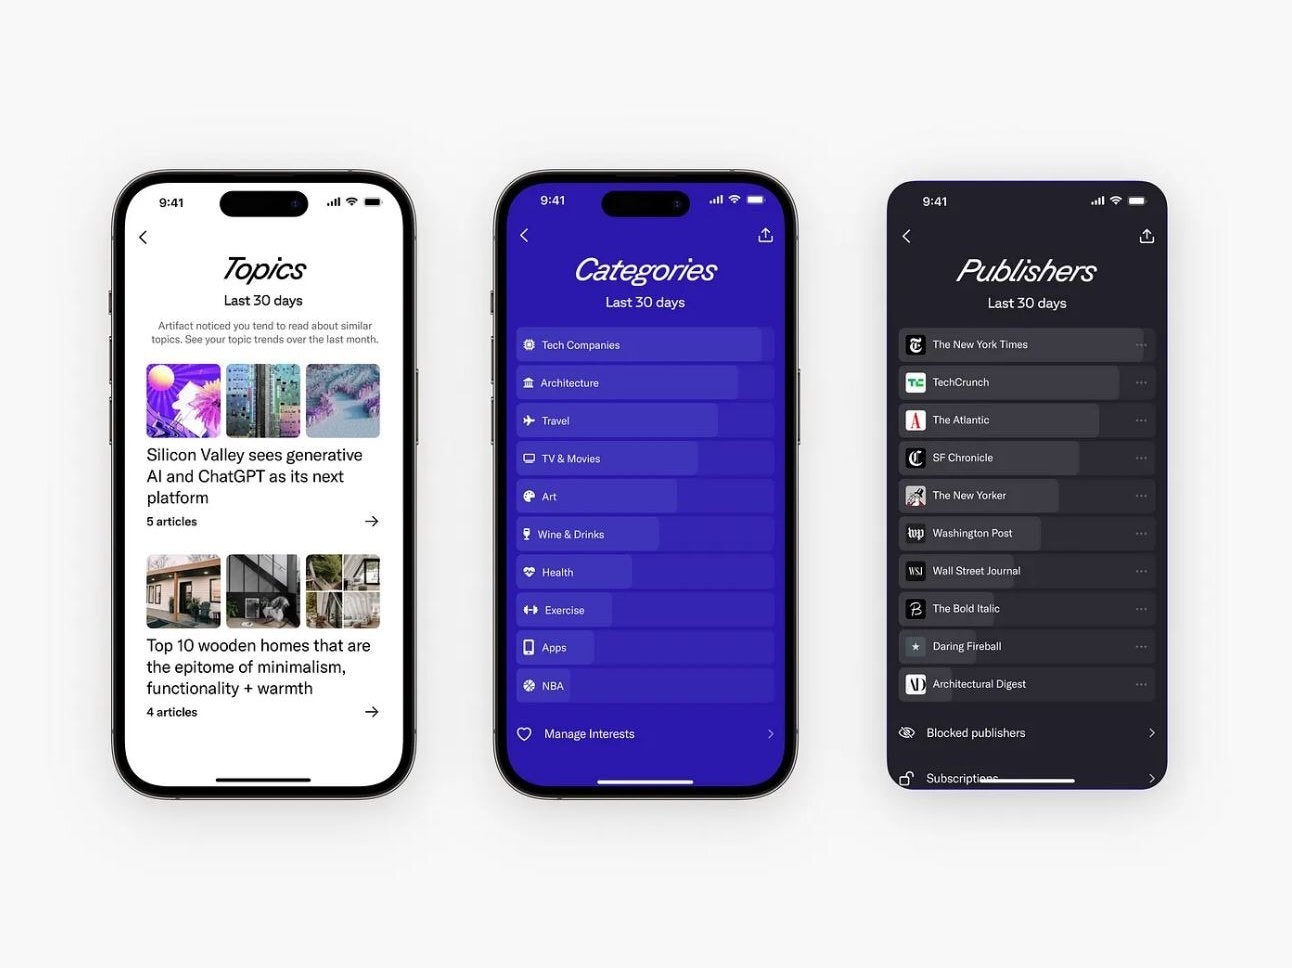
In typical news feed fashion, you’ve got the ever-coveted Read Later list, but you also have a Reading History section, so that you can get back to an article that you’ve come to appreciate over time. If you use the app long enough, it will even provide you with stats like what your favorite publications and topics are, which is always neat. This may be the next hit Year in Review type of thing, but for non-audiophiles!

Overall, Artifact is simple to set up, very easy to navigate and the browsing experience is so fluid that it is kind of addicting. But again, is it any wonder, given who conceptualized it? While it is too early for us to tell if the AI is truly as good as it is made out to be, but even beyond that, Artifact is a great first choice for anyone looking to get into “the know”.


[ad_2]
Source link