Transcription Security Essentials: How to Protect Your Data in the Digital Age – GBHackers – Latest Cyber Security News

0
[ad_1]

In the digital age, protecting your data is more important than ever. With hackers becoming increasingly sophisticated in their methods of stealing sensitive information, it’s essential that businesses and individuals alike take steps to secure their data. As transcriptions can contain large amounts of sensitive data, it’s important to take extra measures to secure them.

In this article, we’ll explore some of the basic steps you can take to protect your data with transcription security essentials.

What is Transcription Security?

Transcription security is the process of protecting transcription data from unauthorized access or manipulation. This includes not only physical measures such as encryption and secure servers but also virtual measures such as strict access control and rigorous review procedures. The goal of transcription security is to ensure that only authorized users can access and use the data. Secure transcription practices help protect the data from malicious actors, as well as accidental or deliberate misuse.

Are All Transcription Services Secure?

No. Not all transcription services are secure. In fact, many transcription services don’t provide adequate security measures to protect your data from unauthorized access or manipulation. It’s important to do your research when selecting a transcription service and make sure that they provide adequate security protocols.
How Can a Company’s Security Be Checked?

There are several ways to check a company’s security protocols. The most common method is to contact the transcription service and ask for a copy of their security policies and procedures. Make sure the security policies cover all aspects of data protection, such as encryption, access control, and physical security.

Additionally, check to see if the transcription service is compliant with industry-standard security certifications, such as HIPAA and ISO/IEC 27001. A secure transcription service will also offer regular vulnerability scans and penetration tests to identify and fix security flaws.

Moreover, you can research the company online to see if there have been any reports of data breaches or other security incidents. Also, you can consult a third-party security expert to assess the transcription service’s security systems.

Basic Steps You Can Take to Protect Your Data

In addition to selecting a secure transcription service, there are several basic steps you can take to protect your data:

Use strong passwords for all accounts

Using strong passwords and changing them regularly is an important step in protecting your data. Make sure to use a combination of upper and lowercase letters, numbers, and special characters for your passwords.

Regularly back up your data

It’s important to regularly back up your data in case of a security breach or other emergency. You should store the backups in a safe and secure location, such as an off-site server or cloud storage.

Limit access to data

Restricting data access to only those who need it is a key part of protecting your data. Make sure that all users have the appropriate permissions and that they only access the data they need. An example of a case where this might be important is if you are working with confidential medical or financial data, an employee with no need to access that information should not have access.

Enforce two-factor authentication

Two-factor authentication adds an extra layer of security by requiring users to enter a code sent to their phone or email address before they can access the data. This makes it much more difficult for unauthorized users to gain access to the data. Although hacks are still possible, two-factor authentication can help to deter malicious actors.

Regularly monitor your data for any suspicious activity

Monitoring your data for any suspicious activity is a key part of keeping it safe. Make sure to regularly review logs and other security systems to ensure that no one is attempting to gain unauthorized access. When it comes to cybersecurity on speech-to-text services, data can be compromised in many ways if not properly secured and monitored like phishing attacks, malware, and brute force attacks.

Keep all digital devices and software up-to-date

Outdated software and devices are much more vulnerable to security threats, so it’s important to keep them up-to-date. Make sure to regularly check for updates and patch any security flaws. Microsoft CEO Satya Nadella advised, “keep your systems up to date and be vigilant about monitoring your data.”

Conclusion

In conclusion, it’s important to select a transcription service that has strong security protocols in place. Additionally, you can take basic steps to protect your data, such as using strong passwords and regularly backing up your data. Finally, make sure to keep all digital devices and software up-to-date and regularly monitor your data for any suspicious activity. For individuals and businesses that are looking for a secure speech-to-text service, following these steps can help ensure that their data is protected and secure.


[ad_2]
Source link
Royal Mail schools LockBit in leaked negotiation

0
[ad_1]

The LockBit gang has released a chat history showing its negotiations with Royal Mail.

The LockBit group has finally given up any prospect of extracting a ransom from Royal Mail and published the files it stole from the company in a recent ransomware attack. The leak brings weeks of negotiations to a close, leaving Royal Mail without a decryptor, and LockBit without a payday.

Royal Mail files are leaked on the LockBit dark web site

Malwarebytes regards LockBit as one of the five most serious cyberthreats facing businesses in 2023. It was the most widely used ransomware-as-a-service (RaaS) in 2022, by far. It accounted for almost a third of all known RaaS attacks last year, and the largest ransom demand it made was a staggering $50 million. In February 2023 it asked Royal Mail for $80 million.

Alongside the leaked files, the LockBit gang have released a chat history that shows the negotiations between the two parties. Perhaps the group is trying to justify its decision to call off the negotiation and leak the stolen files, or perhaps it’s a warning to other victims.

You could read this as a failed negotiation or a missed opportunity for Royal Mail, but I don’t. I think the chat between Royal Mail and LockBit shows something quite different.

I suspect that Royal Mail never intended to pay a ransom. It certainly showed no willingness to engage with the ludicrous $80 million that was demanded of it, and it seems to have had the LockBit negotiator dancing to its tune throughout.

The negotiation began on January 12, 2023, and like any Internet chat, the conversation takes place between two avatars who may or may not be who they say they are. When the LockBit negotiator asks who they’re talking to, the Royal Mail’s representative says “I work in our IT.”

LockBit and Royal Mail introduce themselves

Maybe they did work in IT, but having spent years working in IT myself, and after seeing how the Royal Mail’s representative conducted themselves, I will simply say they aren’t like anyone I ever met. Perhaps they’re just naturally good negotiators, or perhaps they listened to our recent podcast about ransomware negotiations, but there is every chance they were actually a professional ransomware negotiator.

In the podcast, ransomware negotiator Kurtis Minder reveals that the first job in a situation like this is to play for time, without annoying the representative of the ransomware gang. A good way to lower the temperature is to adopt the ransomware gang’s self-serving vernacular, he says, and the Royal Mail’s “IT guy” does this in subtle ways, such as referring to LockBit’s criminal activity as “penetration testing.” Ransomware gangs like that sort of nonsense for some reason—maybe it helps them sleep at night.

Playing for time is important because it allows the victim to gather as much information as possible, understand their options, and decide their best response. They need to understand which systems are affected, how the organization can function without them temporarily, and what it will take to restore or rebuild them. They will also have numerous stakeholders to involve and duties to fulfill: Legal obligations must be met, law enforcement involved, cyberinsurance rules followed, customers and suppliers informed, and so on.

Royal Mail consistently succeeds in playing for time with LockBit. Although the first 24 hours of the chat are peppered with urgent and vaguely menacing language designed to rush the victim—“don’t delay,” “hurry up,” “our patience is not infinite”—LockBit is quickly dragged into the weeds. The first two weeks of negotiation were almost entirely devoted to a tedious conversation about decrypting large files.

LockBit and Royal Mail discuss large files

According to Royal Mail’s negotiator “my management have heard that your decryptor might not work on large files.” (This tactic of invoking a demanding or difficult to please manager will be familiar to anyone who’s ever haggled with a salesperson over a car.) Whether Royal Mail’s curiosity about large file decryption was genuine or a ruse, it created a role reversal in the conversation, with Royal Mail asking the questions and LockBit providing the answers, to prove that it can meet Royal Mail’s needs.

The Royal Mail negotiator also tried to earn trust by positioning themselves as a reasonable go between who’s trying to do the best for both parties. They consistently used language like “I am trying to help our Senior Team understand this,” “I am still trying to work with you here,” “I am doing what I can to drive things forward.”

When the conversation finally turned to money, it quickly found more weeds. This time the thorny undergrowth was formed by a disagreement about who LockBit had actually attacked. LockBit thought it was talking to Royal Mail. The victim told them they’re Royal Mail International, a loss-making subsidiary of Royal Mail with a vastly smaller turnover.

LockBit asked for a ransom of $80 million, 0.5 percent of Royal Mail’s annual global turnover. Royal Mail retorted that using LockBit’s calculation, a good “starting figure” would be $4 million, based on Royal Mail International’s finances.

At this point in the negotiation LockBit actually acknowledged what it was dealing with. “You are a very clever negotiator,” they wrote, “I appreciate your experience in stalling and bamboozling.”

LockBit calls Royal Mail a "clever negotiator"

They might have appreciated it, but they didn’t seem able to do anything about it. By this point in the negotiation, Royal Mail was dictating the timeline: “We will not have anything new to speak about until Monday,” “Please confirm you will wait for their [the board’s] decision on Monday”.

LockBit did as it was told and waited. Finally, the last message from Royal Mail arrived on February 6, 2023. It suggested that the company probably never had any intention of paying. “To be honest with you I have heard that they [the board] might not want to pay you for this,” it said. “In our perspective the files got leaked when you took them from our system, and paying you won’t undo that in any way.”

The end of the negotiation

Ransomware attacks can be devastating, and it’s hard to say that being on the end of one is ever a “win” for the target. However, most experts agree that all you can ever do is reduce the chances an attack will occur and reduce the impact if it does. You can only ever play the hand you’re dealt, and we think given the hand they were playing, Royal Mail’s negotiation came as close to a win as a loss like this ever does.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Write an incident response plan. The period after a ransomware attack can be chaotic. Make a plan that outlines how you’ll isolate an outbreak, communicate with stakeholders, and restore your systems.

We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Best Fitness Trackers – February 2023

0
[ad_1]

Whether it’s to upgrade from your current device or finally start that workout program you’ve been meaning to get into, a new fitness tracker can help you stay on target and these are some of the best trackers you can find.

With the holidays now over, a fitness tracker might be just the ticket for staying in or getting back into shape. They’re designed to help you reach your fitness goals, and most of them do a pretty good job at it.

There are tons of fitness trackers out there though. Amazon is swimming in them. How do you separate the ones you should consider from the ones that aren’t worth your time?

That’s what this guide is here to help you do. We’ve picked the best fitness trackers to help you meet your fitness goals in 2022.

Best Fitness Trackers – Summary

Below you’ll find a short summary on the list of top 10 best fitness trackers we’ve picked. The summary includes the cost of each tracker, and where to buy if you’re short on time. Below the summary you’ll find a slightly longer description of each item along with the where to buy links.

CostWhere to buy
Xiaomi Smart Band 7From $46.30Amazon, Walmart
Fitbit Inspire 3$78.95Amazon, Best Buy, Walmart
Garmin Vivosmart 4From $98.55Amazon, B&H, Newegg, Walmart, Office Depot, Best Buy, Kohl’s
Samsung Galaxy Watch Active 2From $88.31Amazon, B&H, Walmart, Target, Best Buy
Amazon Halo$69.99Amazon, Best Buy
Garmin Fenix 7 SeriesFrom $689.95Amazon, GameStop, Adorama, Macy’s
Amazfit Band 7$49.99Amazon, Best Buy
Garmin Lily$199.99Amazon & Various Other Retailers
Fitbit Charge 5From $124.76Amazon, Fitbit, Best Buy, B&H, Target

Xiaomi Smart Band 7

Xiaomi Mi Smart Band 6 image 2


The Smart Band 7 is another one of those trackers that’s great to have if you just want something simple yet functional. It’s stylish to the point that you can swap the band color out for a decent amount of options, and it does just the necessary basics when it comes to features.

While it won’t be as feature-packed as something like the Fitbit Charge 5, it also usually costs under $50. Which is less than of what the Fitbit Charge 5 costs. So there’s a huge incentive there to consider this over other trackers.

It’s capable of smartphone notifications, tracks 120 different activities, and has a new blood oxygen sensor as well as better battery life than the Mi Band 6. For those that don’t need a lot out of their tracker, this is a win/win.

Xiaomi Smart Band 7

Fitbit Inspire 3

Fitbit Inspire 3

If you’re looking for a tracker that will suit the majority of users, then the Inspire 3 from Fitbit is one you should consider. It’s Fitbit’s latest tracker in the entry level offering tier.

Featuring a big enough display for easy visibility of your activity data, time, and more as you wear the tracker during workouts or just daily life. The Inspire 3 features Fitbit’s popular Active Zone Minutes feature to help keep you motivated.

As you go through the day, any activities you do that get your heart pumping will rack up these minutes. Walking, running, and anything else really where you’re moving around should count. Then as the week ends Fitbit can tell you if you’ve reached your weekly goal.

The Inspire 3 also tracks sleep, and it has 24/7 heart rate tracking. It also comes with improved battery life that lasts for up to 10 days, and now comes with a full color AMOLED display.

Fitbit Inspire 3


Garmin Vivosmart 4

Garmin Vivosmart 4

The Garmin Vivosmart 4 is a little bit of an older tracker as it was officially released in 2018, but when it comes to Garmin this is the latest tracker the company has released that isn’t a full-on watch.

It’s also still a very capable tracker with all the necessary fitness-related features you’d need for keeping track of your exercise.

It comes with built-in Pulse OX sensor as well so you can measure your blood oxygen saturation levels, if that’s a feature you were looking for.

Garmin offers this device in a range of different color options just in case you wanted something other than the standard black model. And as long as you’re not using the Pulse OX sensor, the battery should last up to seven days.

Garmin Vivosmart 4 – Various Retailers

Samsung Galaxy Watch Active 2

Samsung Galaxy Watch Active 2 Review 14

In the market for a smartwatch that has fitness tracker features? Look no further than the Galaxy Watch Active 2.

We thought it was a great smartwatch and consider it the only smartwatch you should buy. If you want the best, Samsung has you covered.

From a simple and sleek design to meaningful and functional features like advanced sleep tracking and the touch bezel, the Galaxy Watch Active 2 is the perfect companion to anyone who wants to get into shape.

It can measure your stress levels too. Which is important if you have a busier life with a hectic schedule. Not to mention it’s comfortable. And it comes in a few different color options, with the added benefit of swapping out your band for something more stylish if the event calls for it.

Want to swap out your watch face? It can do that too. You can even take pictures and easily add those as your custom watch face through the companion app.

Samsung Galaxy Watch Active 2 – Various Retailers

Amazon Halo

Amazon Halo

Amazon’s Halo tracker is one of the new kids on the block here. And it comes in at a pretty decent price.

What separates the Halo from other trackers on this list is its ability to recognize your tone when you speak. It then uses this data to tell you how you sound to others. For instance it can tell you if you sounded angry during a certain conversation at some point in the day.

It also tracks sleep, steps, and other activities. Though, it doesn’t have a display to interact with so all of the data it picks up from exercise and daily stuff is visualized in the companion app.

So this might be the perfect tracker for someone who doesn’t want yet another screen to have to interact with.

Amazon Halo – Amazon, Best Buy

Garmin Fenix 7 Series

Garmin Fenix 7 Series

Most of the trackers on here are priced at a relatively affordable cost. None of those are the Fenix 7 series from Garmin though.

This is a premium multisport GPS watch and is the tracker to buy if you want the best of the best with nearly every feature under the sun.

The Fenix 7 comes in a series of different models, each having something a little different. They’re relatively close in features though.

For example all of them offer Garmin Pay so you can make mobile payments, Meanwhile the Fenix 7x Sapphire Solar allows you to charge the battery with solar energy. Meaning you can charge it as you wear it outside during exercises and adventures. So long as there’s enough sun around to provide the energy it needs.

The Fenix 7 series also offers mapping features, music integration, and PacePro technology for grade-adjusted pace guidance during your runs and outings. You can track your heart rate and measure your blood oxygen saturation levels too thanks to the integrated PulseOX and Heart Rate sensors.

The price for this one is steep. But if you’re serious about your fitness and want something that offers features that you won’t find elsewhere, the Fenix 6 is where to look.

Garmin Fenix 7 Series

Amazfit Band 7

Amazfit Band 7

The Amazfit Band 7 is a great tracker to go for if you want something that won’t cost you an arm and a leg. It comes with a slightly higher price than our previous favorite from Amazfit, the Band 5, but it also comes with notable upgrades. Such as the jump from 15 days of battery life to 18 days, as well as a larger color display for more glanceable interaction.

The tracker shows off important data like step counting, heart rate, the time, smartphone notifications and more. It even has Alexa built-in so you can use the tracker to not only ask Alexa questions, but control smart home appliances and devices like smart ovens, lights, or thermostats.

It also features blood oxygen saturation monitoring and you can customize the face with tons of different available options to choose from. And one of the best fitness trackers on this list.

Amazfit Band 7

Garmin Lily

Garmin Lily

The Garmin Lily is the perfect tracker for anyone that doesn’t want a fully-fledged fitness tracker or smartwatch on their wrist. It offers some of the more staple features you’ll find in most trackers like blood oxygen saturation tracking, heart rate tracking, and GPS while looking like a more traditional watch.

Because of the more traditional style it also more easily fits in with just about anything in your wardrobe. It comes in a variety of colors as well, and can even track stress, hydration, sleep and more.

Garmin Lily

Fitbit Charge 5

Fitbit Charge 5 4

The Charge 5 is Fitbit’s latest tracker in the long-running line of this model, bringing a few notable improvements to the table. Such as the all-new color OLED touchscreen, sensors on the sides of the tracker, stress management features, built-in GPS and more. It also comes with a free 6-month membership to Fitbit Premium. Which is a pretty good thing to have if you get invested in using this tracker every single day.

It’s also got silent alarms with Smart Wake, and a lot of the typical stuff like heart rate tracking, smart notifications, and sleep tracking. There’s plenty of band options for customization of the style too. Overall this is one of the best fitness trackers out there and one of Fitbit’s best to date.

Fitbit Charge 5


[ad_2]
Source link

Florida Attorney General proposes new policy to flag foreign-owned apps

0
[ad_1]

Over the past few years, concerns over national security with Chinese-owned apps like TikTok have skyrocketed. In an effort to combat this problem and make consumers aware of the potential risks of installing an app, Florida Attorney General Ashley Moody has proposed a new policy to flag foreign-owned and developed apps with a special icon or designation.

Moody’s concerns over TikTok stem from the app’s data privacy practices and national security risks. While other states and government entities have taken steps to ban TikTok on government devices, Moody’s proposal focuses on informing consumers of the risks associated with foreign-owned and developed apps.

She also cited Pushwoosh, a Russian malicious code discovered in thousands of apps on the App Store, including those of The Centers for Disease Control and Prevention (CDC) and the US Army, as one of the major reasons that prompted her to write letters to Google CEO Sundar Pichai and Apple CEO Tim Cook.

Empowering Consumers to Make Informed Decisions

According to Moody, the lack of transparency in app stores poses a significant risk to American citizens. Her proposal aims to empower consumers by providing clear and easy-to-understand information about the origin of an app, enabling them to make more informed decisions about their data privacy and security. By adding a foreign-owned or developed designation to apps related to certain countries, consumers will have access to the highest level of transparency and protection.

“Consumers have a right to know if these countries are related to the origination, development, or ownership of these applications. Informing consumers of this foreign-based status allows consumers to decide whether or not they want to subject themselves, or this country, to the inherent and increased risks associated with such foreign applications,” reads her letter.

It’s not clear whether Apple or Google will flag foreign-owned apps in response to Moody’s proposal, as they already label the developer and include links to their website. However, with the growing concerns about data privacy and security, app stores need to take action to protect their users.


[ad_2]
Source link

YouTube may be planning to lock 1080p at higher bitrate for its Premium subscribers

0
[ad_1]
Ad tracking has been scrutinized (and for a reason) in the past couple of years. And although this is good if you don’t like to be tracked, it has another effect – many social media platforms are now looking into paid subscriptions. And while that isn’t necessarily bad on its own, locking free features behind a paywall is a surprise not many users are pleased to see. Now, Android Police reports that YouTube may be testing reserving high bitrate 1080p resolution to paying users.

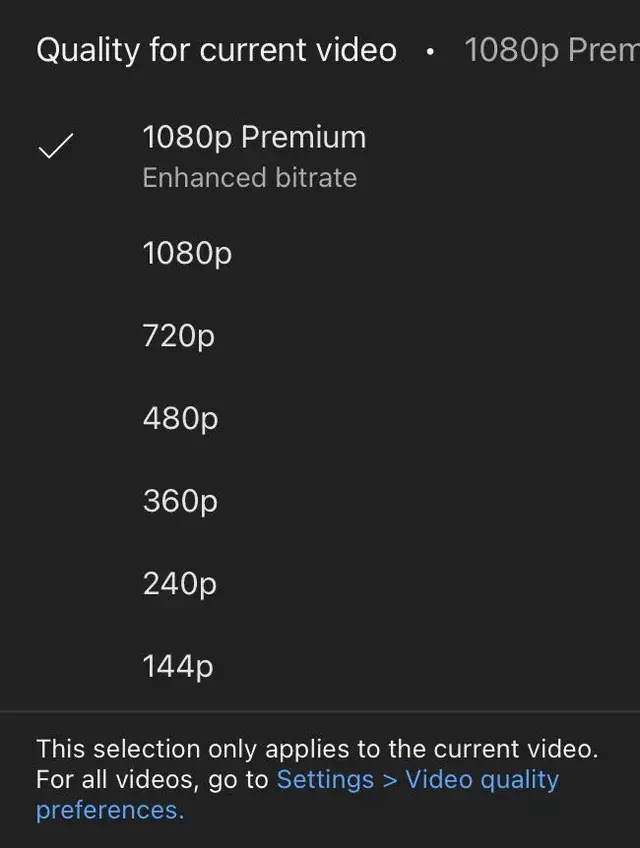
YouTube seems to be testing 1080p Premium with enhanced bitrate


One user has spotted the change and shared a screenshot on Reddit. The screenshot shows an option 1080p Premium, which sits on top of a ‘standard’ 1080p option for video resolution.

As Android Police rightfully notes, at first glance this may look like a way to brand full HD videos with higher-than-usual frame rates as reserved for paid subscribers. However, YouTube may be looking into locking 1080p videos in 60 or 120 fps behind this paywall.


Given the fact that the option says “Premium” it isn’t far-fetched to believe it is referring to YouTube Premium, which is the platform’s paid subscription option. Another similar experiment was conducted last year, but there the 2160p60 setting was Premium and the caption read “Tap to upgrade”. But that makes a little bit more sense than, for example, locking 1080 at 60fps behind a paywall. But we’ll see – this is by far info that’s not yet confirmed (and it’s unclear whether it will happen).

Recently, YouTube had a change in CEO as Susan Wojcicki resigned after spending nine years as YouTube’s CEO. Changes in a company’s strategy are inevitable when the head is changed.

YouTube Premium currently costs $12 a month and it gives you access to ad-free videos, background playback, offline video downloading, and YouTube Music Premium. For now, YouTube Music and Premium’s subscription base is growing, and it’s been reported at around 80 million users in Q4, 2022.

All in all, there are interesting things ahead in 2023 for YouTube and YouTube Premium. Of course, it’s early to say whether or not this 1080p Premium will be 60 fps or 120 fps, or something more exclusive… but hopefully the change doesn’t make free features now locked behind a paywall – that would be, let’s just say it, a bummer.


[ad_2]
Source link

Russian Malware Developer Behind NLBrute Extradited to US

0
[ad_1]

Numerous cybercrime groups, including REvil, Dharma, and Netwalker, have used NLBrute.

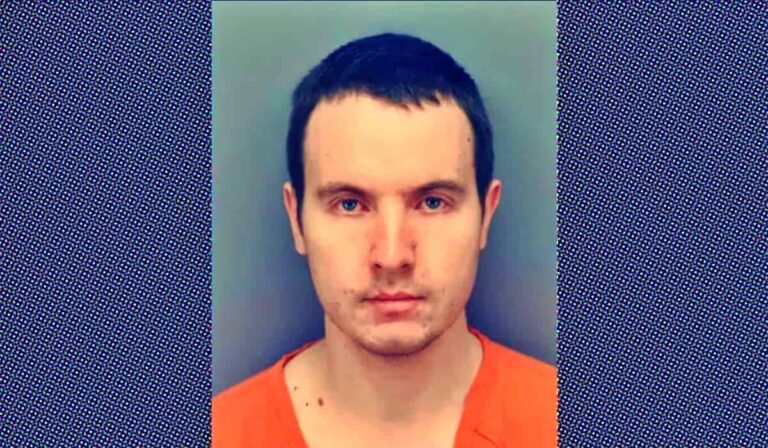
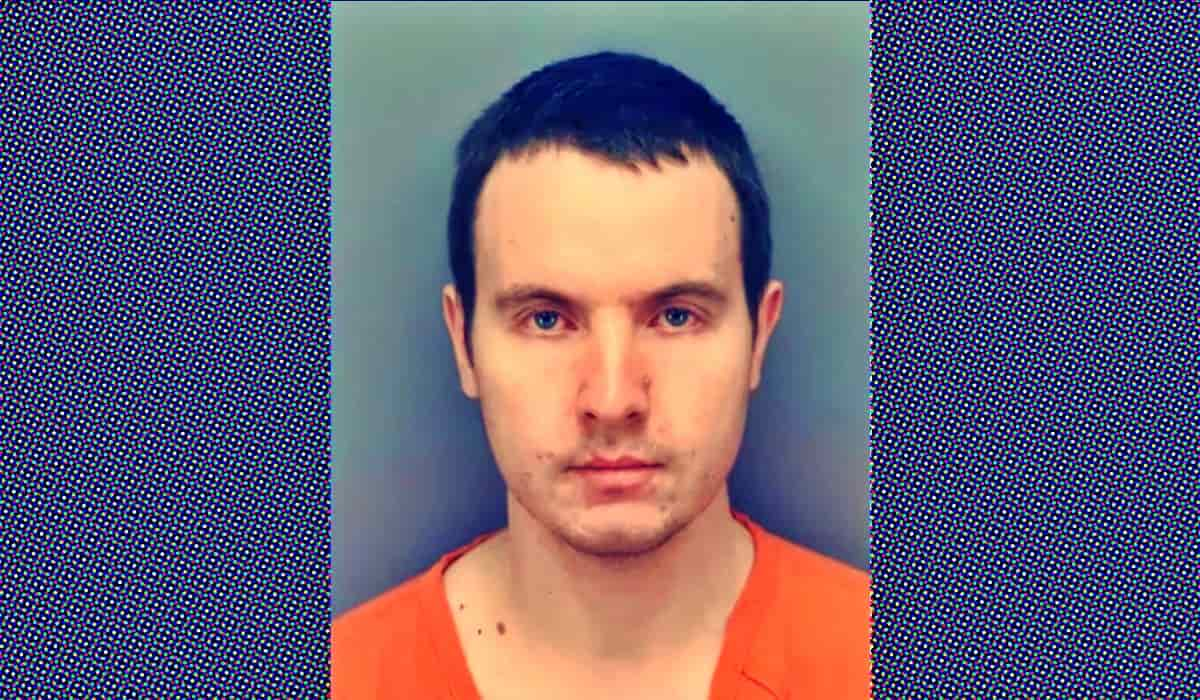
A 28-year-old Russian national, Dariy Pankov a/k/a “dpxaker.”, was arrested in the Republic of Georgia on October 4, 2022, and, upon request, extradited to the United States, where he appeared before Magistrate Christopher P. Tuite on 21st February 2023. 

Pankov is charged with conspiracy, access device fraud, and computer fraud. The Department of Justice’s press release explains that Pankov was behind the creation of a brute force attack tool known as “NLBrute”.

A brute force attack uses trial-and-error to guess the login credentials of password-protected systems. 

Pankov marketed, sold, and had others sell NLBrute, which was used by numerous cybercrime groups, including REvil, Dharma, and Netwalker. He also sold stolen credentials on dark web websites that specialize in the sale and purchase of access to compromised computers.

Russian Malware Developer Behind NLBrute Extradited to US
Dairy Pankov, a.k.a. dpxaker (Image source: Pinellas County Sheriff’s Office)

Cybercriminals purchased the login information and used it in various malicious campaigns, including tax fraud and ransomware attacks. Pankov obtained more than $350,000 in illicit sales.

Igor Litvak, Pakov’s attorney, told CNN that his client will plead not guilty and maintain his innocence. Pankov faces a maximum sentence of 47 years in federal prison if convicted on all counts. He is currently being held in the Pinellas County Jail outside of Tampa, where he was booked on Monday.

  1. US Sentence Ukrainian to 4 Years for Brute-forcing
  2. Colombia arrests suspect wanted by US over Gozi virus
  3. Extradited Alleged ShinyHunters Hacker Pleads Not Guilty
  4. Russian hacker jailed in US over $19M fraud, 100M data theft
  5. Ukrainian Member of REvil Ransomware Gang Extradited to US

[ad_2]
Source link

Russian Radio Stations Hacked with Fake Missile Alerts

0
[ad_1]

According to local media, a female voice rendered the fake alerts from several radio stations, including Yumor FM, Relax FM, Comedy Radio, Humor FM, and Avatoradio. The false warning announced an air raid and requested the listeners to seek shelter quickly.

Millions of Russian citizens in over a dozen cities were baffled to hear unusual radio alerts, sirens, and text messages this Wednesday morning. These warnings were about missile strikes and air raids on Russia.

However, the Russian government’s Ministry of Emergency Situations later announced that these were fake warnings and blamed hackers for airing false alerts on commercial radio stations.

According to local media, a female voice rendered the fake alerts from several radio stations, including Yumor FM, Relax FM, Comedy Radio, Humor FM, and Avatoradio. The false warning announced an air raid and requested the listeners to seek shelter quickly.

“Attention, an air raid warning is being announced. Go to the shelter immediately. Attention, Attention, the threat of a missile strike.”

These bogus warnings were broadcast in ten cities, including Kazan, Tyumen, Pyatigorsk, Nizhny Novgorod, Voronezh, Magnitogorsk, Novouralsk, Ufa, and Stary Oskol. Loud sirens followed these warnings, and civilians were urged to seek out air raid shelters. Some people recorded these false warnings on camera.

Locals in the cities where the warnings were broadcast, such as the Kurgan and Belgorod regions, promptly informed citizens that these were false warnings. The ministry noted that the warnings were caused by an attack on a satellite operator’s infrastructure.

Moreover, government officials stated that an unauthorized “tie-in is going in the air,” clarifying that the alarm signals were fake. Authorities claim that the perpetrators could be linked to the Kyiv regime.

A tweet shared by Anonymous with Hackread.com claims that it was the Anonymous hacktivist collective behind the hacking spree.

Earlier, a Denial of Service attack (DDoS attack) disrupted Russian President Vladimir Putin’s address to the nation on state media sites. Ukrainian hackers claimed responsibility for the attack.

“As a result of a hacker attack on the servers of some commercial radio stations in some regions of the country, information was broadcast about an alleged announcement of an air raid warning and a threat of a missile strike,” the ministry’s statement read.

It is worth noting that most stations airing these alerts are owned by Russia’s leading media company, Gazprom-Media. Furthermore, the alerts were aired just two days before the first anniversary of the Russian invasion of Ukraine.


[ad_2]
Source link

First software update for the Galaxy S23 series is rolling out widely

0
[ad_1]

A couple of days back, Samsung released the first software update for the Galaxy S23 series. The rollout began in Europe. But the company has wasted no time to bring it to other regions. The update is now available for Galaxy S23 users in Asia and Africa as well, including in Samsung‘s homeland South Korea. We expect the company to release the update in the US over the next few days.

Galaxy S23 units sold in Europe, Asia, and Africa bear the same model number (SM-S911B for the base model, SM-S916B for the Plus, and SM-S918B for the Ultra). So the updated firmware version for the phones in these regions is the same — S91*BXXU1AWBD. But the South Korean versions ship with the model number SM-S91*N. The latest update comes with firmware version S91*NKSU1AWBD in the country.

The story is similar for Galaxy S23 phones in Taiwan, Hong Kong, and China as well. The new Samsung flagships bear the model number SM-S91*0 in these markets. Users are getting the new update with the firmware build number S91*0ZHU1AWBD. But regardless of the firmware version, the latest update for the Galaxy S23, Galaxy S23+, and Galaxy S23 Ultra has the same changelog everywhere.

The February update for the Galaxy S23 reaches more markets

Samsung’s changelog for the first firmware release for the Galaxy S23 series doesn’t go into detail. It only states that the package contains some optimizations and the February 2023 Android security patch. The latest SMR (Security Maintenance Release) patches more than 50 vulnerabilities.

Samsung’s security bulletin says seven of those are Galaxy-specific. Those vulnerabilities don’t exist in Android devices from other brands. They patch flaws in Fingerprint TA, Secure Folder, and other systems apps and services.

The remaining 40-odd vulnerabilities patched by this month’s security update are part of Google’s latest ASB (Android Security Bulletin). They patch flaws in Android OS and other partner components. The Android maker labeled five of those as critical vulnerabilities that could potentially allow remote code execution if a threat actor exploited them in the wild. It could pave the way for them to remotely control your phone.

If you are one of the early buyers of Samsung’s latest flagships, you might want to install this update as soon as possible to stay safe from these vulnerabilities. You can go to the Software update menu in the Settings app and tap on Download and install to check for updates manually or wait for a notification prompting you to download the update. For users in the US, we will let you know when Samsung releases the update stateside.


[ad_2]
Source link

How to watch MLB without Cable in 2023

0
[ad_1]

Baseball is back. America’s pastime is starting this month with Spring Training, and then Opening Day in late March. So how can you watch all of the action? Well that is what we are here to tell you.

Will the Houston Astros make it back to the World Series in October? Well, we have over 162 games to find out. The baseball season is quite long, lasting from April (technically, March 30) through September. With the playoffs lasting through October and the World Series at the very end of the month. Last year, we saw the Houston Astros take on the Philadelphia Phillies and win 4-2 in a six-game series. Can they repeat?

When is opening day?

Opening Day is set to take place on March 30, 2023. This year, all 30 MLB teams will be playing on Opening Day. That’s the first time since 1968 that every team has played on Opening Day, which is quite shocking. Here’s the full schedule for Opening Day.

  • Atlanta Braves at Washington Nationals – 1:05 p.m. ET
  • San Francisco Giants at New York Yankees – 1:05 p.m
  • Baltimore Orioles at Boston Red Sox – 2:10 p.m.
  • Milwaukee Brewers at Chicago Cubs – 2:20 p.m.
  • Detroit Tigers at Tampa Bay Rays – 3:10 p.m.
  • Philadelphia Phillies at Texas Rangers – 4:05 p.m.
  • Pittsburgh Pirates at Cincinnati Reds – 4:10 p.m.
  • Colorado Rockies at San Diego Padres – 4:10 p.m.
  • Toronto Blue Jays at St. Louis Cardinals – 4:10 p.m.
  • Minnesota Twins at Kansas City Royals – 4:10 p.m.
  • New York Mets at Miami Marlins – 4:10 p.m.
  • Chicago White Sox at Houston Astros – 7:08 p.m.
  • Los Angeles Angels at Oakland Athletics – 10:07 p.m.
  • Arizona Diamondbacks at Los Angeles Dodgers – 10:10 p.m.
  • Cleveland Guardians at Seattle Mariners – 10:10 p.m.

What channels show MLB games?

The majority of the games are going to be on regional sports networks or RSNs. So depending on where you live, you might be able to get that from YouTube TV, FuboTV or DIRECTV Stream. Bally Sports RSNs for example are only on FuboTV and DIRECTV Stream.

What about the national games? Well, those are typically on Fox, FS1, TBS, ESPN, MLB Network or Apple TV Plus. Fox, FS1, TBS and ESPN are available on most streaming TV platforms. MLB Network is available on many, but not all – for example, YouTube TV just removed it for the 2023 season.

Now when it comes to Apple TV Plus, subscribers can watch Friday Night Baseball each Friday throughout the season. Apple TV Plus has two games each Friday. Some are on at the same time, while others will be doubleheaders.

cjytpolejercnmqtay9k

How to watch the MLB without cable

Now lets talk about how you can watch the MLB without cable. The best option will be MLB.TV, if you want to watch multiple teams. But if you want to watch your home team (and you live in that market), then your local RSN is going to be the best option.

MLB.TV

MLB.TV is great because it allows you to watch every single game throughout the league. But there is one catch. Local games are not available on MLB.TV. That means that if you live in the Seattle market, you can’t watch Mariners games on MLB.TV. So it’s not quite a replacement for having the RSN available that plays the Mariners games. But if you’ve moved, and want to watch the Red Sox in Seattle, then it’s a good option.

MLB.TV is not going to be cheap though. The full season will be $149, or 119 if you want a single team. You can also pay monthly for $25/month, but that comes out to being a lot more expensive. MLB.TV does also include minor league and spring training games.

YouTube TV

YouTube TV is my personal favorite for watching sports, even though they don’t have Bally Sports RSNs. YouTube TV does have FOX, FS1, TBS and ESPN however. And as noted before, they have dropped the MLB Network, effective for 2023. So you get the majority of the nationally televised games on YouTube TV.

As far as RSNs go, YouTube TV does have the NBC Sports RSNs, but not Bally Sports. NBC Sports is available in a few markets. One of the best parts of having YouTube TV is that you can record every single game. Since it gives you unlimited cloud DVR.

FuboTV

FuboTV is a service that is built for sports. It has a lot of great sports networks available, but for Baseball, it carries all of the networks. And it has also just added Bally Sports RSNs once again. Though some of those RSNs won’t be available until the baseball season starts in April, so you might miss out on spring training.

FuboTV does start at $74.99, so it is more expensive than YouTube TV. But that does get you over 147 channels, along with 1,000 hours of cloud DVR included. It does offer a free trial which you can check out here.

DIRECTV Stream

DIRECTV Stream also has all of the channels for nationally televised games. And it starts at $74.99 per month as well. However, if you want to get the RSNs that will cost you a bit more. You would need their $99/month plan that includes the RSNs, and that does include Bally Sports.

DIRECTV Stream’s Choice package includes 105 channels, allows you to stream on unlimited devices in your home and gives you unlimited cloud DVR storage like YouTube TV does. You can sign up for DIRECTV Stream here.

Sling TV

Sling TV is the cheapest option here. It starts at just $40 per month. And with the Sling Orange package, you’ll get access to ESPN and TBS. With Sling Blue you’ll get FOX (in select areas) and FS1. Or you can get both packages for $45 per month.

MLB Network is available as a add-on. In the Sports Extra add-on, you’ll get the SEC Network, ACC Network, Longhorn Network, Pac-12 Network, ESPN-U, ESPNEWS, MLB Network, NBA TV, beinSports, Tennis Channel, NHL Network and the MLB Strike Zone for $11 per month. So to get all of those networks, you’ll need to pay $56 per month. And Sling TV does not have any RSNs.

Hulu + Live TV

Hulu + Live TV is another good option here. It does include ESPN, FOX, FS1 and TBS for the national games. But it does not have the MLB Network. It also has some RSNs, but not Bally Sports. So keep that in mind.

Hulu does start at $69.99, which does include ESPN+, as well as 85 of the top cable channels, unlimited screens, the Hulu library and unlimited DVR. You can sign up here. 


[ad_2]
Source link
TikTok incorporates Research API in order to provide transparency for state and nonprofit researchers

0
[ad_1]
There’s never a dull moment with TikTok. Even if there are periods of calm, sooner or later, there is always a new conspiracy or dangerous trend that revolves around the dangerously popular social platform. So much so that state officials are politely asking Big Tech to outright ban TikTok.

The company behind the short form video platform doesn’t take this sitting down though. And while they could retaliate and fight this move, they opted for peace and transparency. The company outright invited officials to examine their business and algorithm as closely as they want to.

Now, in an attempt to prove their claim to that invitation, the company has unveiled the integration of a brand new API — Application Programming Interface, think of it as a mini-software that does a specific thing — which provides public data on accounts and content to researchers worldwide.

While this includes both state researchers and nonprofit organizations, the worldwide part is a bit of a goal, as the API is currently available in the US only. And is that any wonder, considering that the States is where TikTok gets the most blame, as its popularity is skyrocketing with American youths?

The API has already received feedback from Content and Safety Advisory Councils and that feedback has even been implemented. TikTok public relations states that the company is looking forward to receiving more feedback in the future from nonprofit researchers too.

But what type of data will these researchers have access to? Well, here’s a breakdown:
  • Public user profile data, like usernames
  • Public content data, like comments, captions subtitles
  • Performance data, meaning likes, views and favorites
  • Public data for keywords and their performance

Not at all malicious or user-threatening. Neat! Basically, this sounds like a compilation of everything that you can find on the platform itself, but presented in a way that does not require weeks of tracking in order to find everything you may need.

The API is live now, and if you are part of a nonprofit organization that may need stats like those mentioned above, the application process is available here. While we can’t say that this will help TikTok leave the deep waters the company has found itself in, we are eager to see how things will go from here on out.


[ad_2]
Source link