Samsung is already working on the next big One UI update

0
[ad_1]

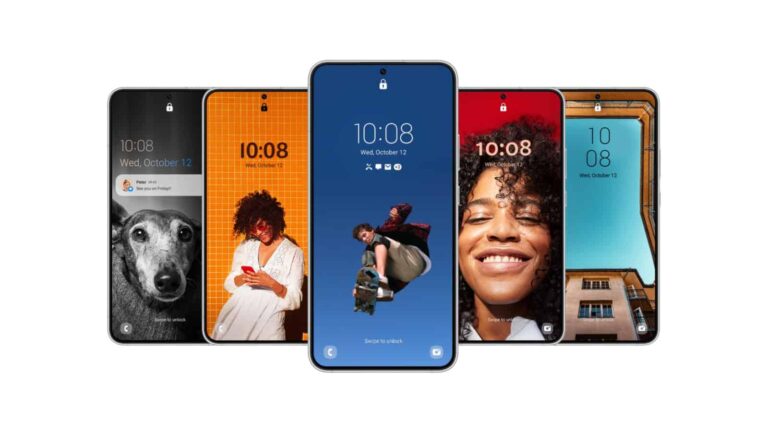
Samsung arguably offers the best software support in the Android space today. The pace at which it releases new security and feature updates is unmatched by any other OEM. The One UI 5.1 rollout is a testament to that. The Korean firm brought the latest One UI version to eligible Galaxy devices just over a week after the Galaxy S23 launch. As One UI 5.1 reaches more models around the world, the company has already started working on the next big One UI update.

Twitter user Tarun Vats (@tarunvats33) recently spotted a new One UI test build for Samsung’s Galaxy Z Fold 4. The company is testing the firmware for the South Korean version of its 2022 foldable. The updated firmware build number is F936NKSU1DWB9. For reference, the device currently runs the firmware version F936NKSU1CWB1. While these alphanumeric characters may not look meaningful to most, if you’re familiar with Samsung’s firmware numbers, you can already tell it’s a major One UI update and not just a regular feature or security update.

For the uninitiated, the fourth-to-last character in a firmware number determines whether it’s a major update. Every new Galaxy device ships with a firmware build that has “A” in that place. With each major feature update, that changes to B, C, D, and so on. If you closely look at the above-mentioned firmware numbers for the Galaxy Z Fold 4, the current build has “C” in the fourth-to-last place, while the test build has “D”. So we are looking at a major update here. It could either be a new One UI version (something newer than One UI 5.1) or a major Android update.

Samsung may be developing One UI 5.1.1 for its 2023 foldables

Unfortunately, we can’t tell what Samsung is developing. It usually debuts new foldables with a new One UI version (Galaxy Z Fold 4 debuted with One UI 4.1.1 while other Galaxy devices were on One UI 4.1). It’s possible that the company is working on Android 13-based One UI 5.1.1 or something along that line for the Galaxy Z Fold 5 and Galaxy Z Flip 5, which will arrive in the second half of the year. But we can’t rule out that the Korean firm is developing an early build of Android 14-based One UI 6.0.

Android 14 won’t be official until sometime after the new foldables arrive on the market. But Google will start releasing developer previews and beta builds within the next few months. Maybe we will get clarity on the new firmware build that Samsung is testing on the Galaxy Z Fold 4 around that time. We will keep you posted.


[ad_2]
Source link

The Samsung 837 store space in NYC has been reopened

0
[ad_1]

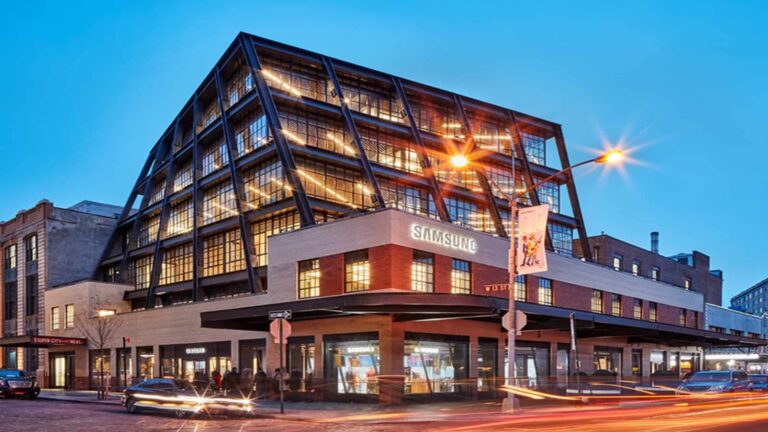
After being closed for a while, the Samsung 837 store space in NYC has finally reopened. To celebrate this reopening event, Samsung is inviting its fans over to visit the store. On display at the store will be the Korean tech giant’s latest smart home appliances and devices.

This store offers fans the opportunity to have an in-person interaction with various Samsung products. The company will also use this avenue to advertise its products to the public. There is a lot to expect from Samsung after the reopening of this store in New York City.

Samsung is bringing its products closer to its fans with the reopening of their 837 store

Samsung is not only reopening its 837 store in New York City, but it’s also redesigning the interior. This will improve the experience whenever fans stop by to check out the latest smart home appliances and devices. Fans began trooping into the reopened store on the 22nd of February for the opening ceremony.

Visitors during this ceremony get the opportunity to be among the first people to step into the store since it closed down. To help combat the Coronavirus outbreak, Samsung made the wise choice to close down its experience store. The store was closed in March 2020 following the pandemic, but it is finally time for it to reopen.

This store will pack the latest Samsung devices for fans to interact with in an immersive environment. Products ranging from smartphones in different segments, Smart TVs, smart home appliances and so on will be on display. Visitors will get to experience how these gadgets and appliances work in their unique ecosystem.

The store will also retail these products to visitors that are willing to buy any. Fans can also benefit from the buy online and pick up in-store program that will soon kick off. If you are a Samsung fan living in or around New York City, you can always stop by the just reopened Samsung 837 store space.


[ad_2]
Source link

Spotify launches new feature powered by AI to enhance music curation

0
[ad_1]

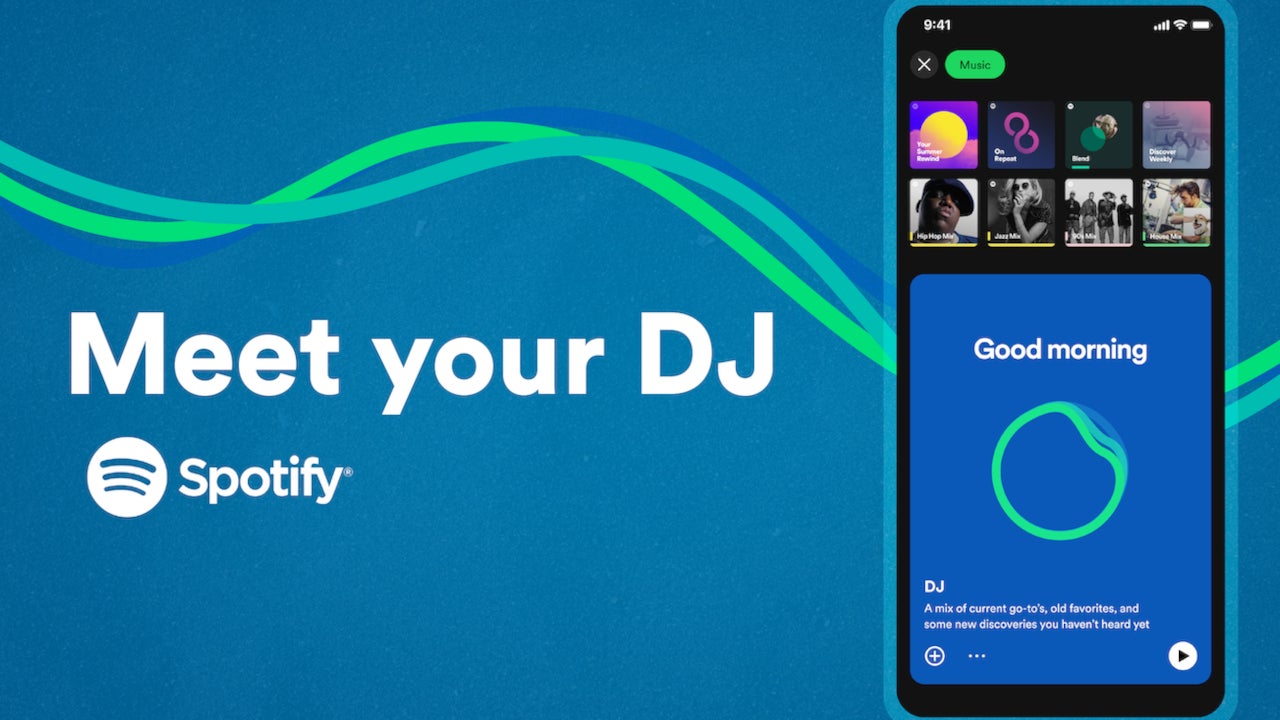
As more companies adopt AI (artificial intelligence), many services are getting new features that are now fully automated and less curated by human touch. Spotify’s new AI DJ is meant to bring personalization to a new level.

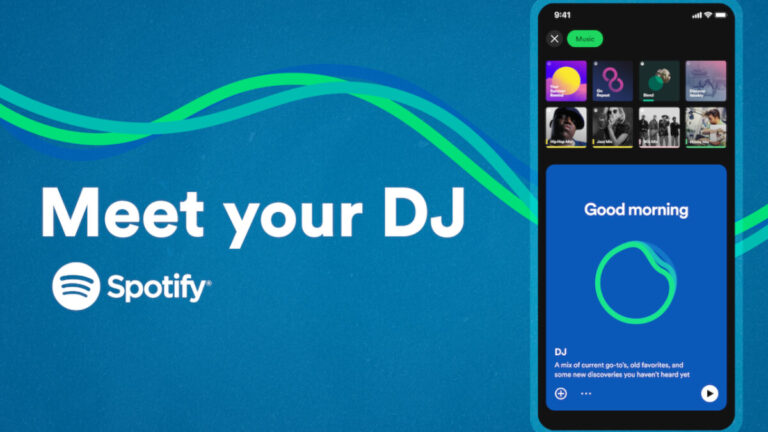
In an announcement earlier today, the music streaming service explains that its new feature is a personalized AI guide that “knows you and your music taste so well that it can choose what to play for you.” It might sound frightening at first glance, but it’s exactly what many customers are looking for when using Spotify on a daily basis.

Granted, the new DJ feature powered by AI is only rolling out in beta, it promises to provide customers with a curated lineup of music, as well as commentary around the tracks and artists that it thinks the user likes “in a realistic voice:”

Among the many capabilities of the AI DJ, Spotify mentions the ability to sort through the latest music. Not to mention that it can also look back at some of the old favorites and serve more songs that the user might not have listened to for a long time.

The AI DJ assesses your actions all the time and after each review, it tries to deliver a stream of songs picked specifically for you. More importantly, it refreshes the lineup based on feedback on a regular basis.

If you don’t like a song picked by the DJ, you can tap the dedicated button and it will skip to a new track. As with all these AI-powered features, the more you use the DJ, the faster it learns what you like, so the better your recommendations will be in the end.

The new DJ feature is available via the Music Feed on Home in the Spotify mobile app for iOS and Android devices. Simply tap Play on the DJ card and the app will do the rest. You’ll be getting music and short commentary on the songs and artists specifically picked for you. Don’t forget that you can skip a song by tapping the DJ button at the bottom right of the screen.


[ad_2]
Source link

How Covid-19 impacted cyber security

0
[ad_1]

Survey methodology and respondent profiles

The results in this report are from the Cyber Security Hub survey which we fielded to subscribers from May and June 2020 to benchmark actual results from H1 2020 vs. expectations for H2 2020. A balanced representation of the enterprise cyber security mindset, the largest segment of survey respondents (41 percent) describes their job function as cyber security. The next largest segment is IT at (27 percent) followed by corporate management at (9 percent).

Qualified respondents were truly cross industry coming from automotive, education, financial services, government, healthcare/life science, manufacturing, media/telecommunications, retail/consumer packaged goods (CPG), technology, travel/hospitality and utilities/oil and gas/energy.

Also read: CISO Stratgies for proactive threat prevention

Pandemic dynamic

There were potentially alarming responses to our global pandemic related questions in this mid-year survey. When asked “Has your approach to security changed as a result of the global pandemic and an increasingly remote workforce?” 40 percent said no.

Has your approach to security changed as a result of the global pandemic and an increasingly remote workforce?

Roughly two in five cyber security organizations have not changed their approach to security as a result of the global pandemic. Such a large percentage of the CISO community not having changed their approach to cyber security as a result of the global pandemic that has hurdled us all into a new workforce infrastructure is truly concerning.

How the cyber security landscape has changed due to the pandemic:

  • Network infrastructure use has changed
  • Endpoints have changed
  • Access management has changed
  • Collaboration tools have changed
  • The concept of insider threat has changed
  • Enterprise cloud infrastructure has changed- no matter where you were in your cloud migration
  • Data in transit has changed
  • Myriad threat vectors have changed
  • Vulnerability management has changed
  • Cybercriminal attacks have changed

Why did 40 percent of the cyber security community not change their approach?

In addition to an inert mindset change from a significant portion of the community, the reduction in staff due to financial pressures on companies during the pandemic was similarly concerning. A past potential insider threat now had the potential to become a nefarious external threat.

Has your IT/Security staff been reduced as a result of the global pandemic?

As reported on Cyber Security Hub in Why Is Top Cyber Security Talent Suddenly In Flight, when asked about the 19 percent unemployed DevOps/DevSecOps community Parag Deodhar, director of information security, Asia Pacific for VF Corporation noted: “when people do not have access to enough money, food or resources, there will be more actors coming up”. Deodhar explained also that the pandemic has expanded the threat landscape, meaning that “not only were folks pushed [towards cyber crime], but also, the landscape open[ed] up for folks as well.”

Jamal Hartenstein, who has worked with the department of defense on military bases as a part of joint task forces and has experience with every branch of service, notes that there was industry realization that organizations needed to be more proactive and better focus on detection and that the global pandemic has accelerated that focus.

When asked what about his perception, he explains that, “if you do not increase your security measures, you have exponentially just multiplied in magnitudes the risk based on all the threat and vulnerability and risk.”

Changing cyber security mindset

We asked survey respondents to share how their cyber security approach was changing. Here is a sample of their responses:

  • Fully remote working cyber security teams
  • Implementing a zero-trust network strategy to provide scalability and flexibility whilst improving network security
  • Adding contractors and outsourcing
  • Rethinking cyber security strategy through the context of the pandemic
  • Adjusting to changes in environment, operations and business
  • Constantly monitoring all situations to better understand the the issues and concerns
  • Introducing awareness programs, online trainings and increased system auditing
  • Changed training and awareness program to cater for changes in workforce practices, e.g. remote working
  • Focusing on what is needed to support remote working employes and ensuring that employees have safety in front of mind when returning to the office
  • Making adjustments for the fact most endpoints are now remote to ensure that they remain secure
  • An increased focus more messaging and content that will resonate better with a remote workforce-emphasize security controls that protect remote workers and mobile
  • Increasing security for both mobile and critical infrastructure
  • Increased use of multi-factor authentication
  • Greater emphasis on cloud-based protection to accommodate home-based workers
  • Working to combat the increased difficultly in quickly identifying and mitigating issues remotely
  • More expertise and focus on DevSecOps
  • Increased use of automation to detect changes to controls. This means we are automatically being notified of the change, responding to and addressing the incident, analyzing itand rectifying the control(s).
  • Streamlining the operational cost of IT to remove unnecessary spending and services that are not being used
  • More user training and simulated phishing campaigns
  • Proactively monitoring threats and regular updating our security strategy to combat new challenges
  • More stringent compliance with regards to minimum security requirements to prevent data leakage
  • Decreasing the time taken to follow through on incident reports from security and threat intelligence tools

In 2021, 40 percent of the cyber security community said they had not changed their mindset in the face of the global pandemic, while 20 percent of top cyber security talent was made redundant. With this in mind, it was unsurprising that 67 percent of the cyber security community reported their budgets were decreasing or staying the same.

May 2019-June 2020 cyber security budget reported as decreasing or staying the same

While over two thirds of cyber security professionals noted their budget was staying the same or decreasing in July 2020, just one year ago 59 percent reported an increase in budget in the Mid-Year Market repor 2019. This means the pandemic had a significant impact on cyber security spend.

In the wake of the global pandemic with attacks on the rise, it would be expected that cyber security budgets would increase to combat this. Those in the cyber security community, however, disagree with 62 percent expecting budgets will decrease or stay the same.

May 2019-June 2020 planned cyber security budget increase in the next 6 months

State of affairs

Overall state

Do you feel as though the overall state of cyber security, meaning resiliency, compliance, awareness, etc., is improving?

Taking a step back shows that the industry feels that things are positive and getting better. When asked “Do you feel as though the overall state of cyber security, meaning resiliency, compliance, awareness, etc., is improving?” 84 percent said ‘yes’.

Threat vectors

What is the most dangerous threat vector, in your opinion?

Security issues

Most security issues at my organization are caused by…

The top three areas of focus for respondents during the pandemic were security awareness, detection and incident response and access controls, inkeeping with the results of the last three Cyber Security Hub surveys. Just outside of that group is elevating cyber security with top-level management, a topic that was similarly highlighted over the previous two surveys.

As a majority of cyber security budgets had not yet shifted in the face of a momentous societal occurrence, how money is spent became all the more important. Endpoint security went from the fifth highest to the second highest spend in the from November 2019 to June 2020, most likely as a response to employees working from home and therefore increasing the chance of an endpoint being used as a vector for attack.

Solution priority

Last six months

Which solutions have been the biggest priorities for you in the last 6 months?

While compliance priority decreased 17 percent from 2019 to 2020, this may be because those in cyber security had finished making the inital major chanegs needed to comply with GDPR. The 9 percent increase in SIEM focus showed that the community was looking to further adopt automation tools, potential due to the decrease in workforce and need to streamline cyber security.

Executive Q&A

Expert perspective from Sam McLane, head of security engineering at Arctic Wolf

What are your thoughts on the top threat vector being email?

Whether it is cloud or devices perimeter, there is a level to which a human element can make them fail but it is rare. Generally, people who play with firewalls tend to be security savvy. So, if they make a mistake, for example opening up a hole for a vendor or for an audit and then not shutting it down, that is generally when they are overworked.

Corporate email and personal email relies on common security awareness and intelligence, and the lowest common denominator usually wins. Malicious actors can go and find the CFO administrative assistant’s Facebook page, find out who their kids are and what school they go to, then easily craft an email that will make the CFO think, “Hey, my secretary just asked me to contribute to her son’s scholarship fund on GoFundMe.”

People naturally want to trust and playing on that trust is so easy to do and to make it look good. Especially in this Covid-19 world while most of us are working from home, you drop your guard a little bit because you are in unfamiliar surroundings. You are in that home setting rather than that work setting. That is what scares the tar out of me about email.

What are your thoughts on industry talent?

If you have got a great team, each member usually does one thing well. Even if you have already got the technology in place, can one person take care of firewall, compliance, intrusion detection, threat intelligence? Can they execute on multiple things? Each of these takes time, and if each member has to take care of three of them, how are they actually going to get each done well?

Our biggest customer was bringing in three new technologies simultaneously. Each technology takes six months to get right. They tried to go it alone with vendor products and failed. When they came to us they said, “We missed a breach,” because either their SIEM or SOAR were not tuned properly, or they never got our end point fully deployed.

What is the answer to a perceived talent shortage?

I am not sure how much of a shameless plug this should be, but a different way to deal with the staffing issue depending upon where you are is to rely on third parties who may have more people. One of our key selling advantages is that because we deal with thousands of customers, I can take that really good smart security person, and maybe she can look at a bank in the morning and hotel chain in the afternoon and a web front the next day. So, we provide variety. We provide something always challenging to our talent. Complacency hopefully never sets in and I have got the staffing capabilities to have a person work on a project three months to avoid burnout. That is really difficult to do unless you are a Fortune 100 company.

“You drop your guard a little bit because you’re in unfamiliar surroundings.”

Sam McLane

Head of Security Engineering, Arctic Wolf

Cyber security and people

Challenges when building teams

When it comes to building out your security operations team, what is your biggest challenge?


There are two main issues that faced the cyber security community in building teams during the pandemic – a perceived shortage of talent and insufficient budget.

Skilled workers

The lack of skilled workers that culturally align with your organization is often cited as a “pain point” for security teams. What are you doing to win the war?

As nearly half of the community perceived a shortage of talent, it is important to consider what companies were doing to acquire talent during the pandemic. More than one in five respondents reported implementing mentor programs. Another 20 percent saw interns as the answer, with nearly 10 percent reported engaging with universities to procure employees.

It was not all change, however, as just under two in five noted that they were simply going to maintain current behaviors and activities to move forward.

Also read: Automating enterprise cyber security report

Security approach

Defense in depth vs. industry consolidation

Is “defense in depth” the answer or do enterprises desire more consolidation across their “point solutions”?

There was a marked shift in industry thinking from November 2019 to June 2020 around the concept of defense in depth. There was been a 10 percent composite swing from the concept of industry consolidation to defense in depth.

Industry frameworks

Do you leverage any of the following industry frameworks?

The industry craves standardization as so indicated by the continued increased use of industry frameworks.

mid_year_2020_ss29ZAjcUY0cONiLftxAhxSojrvbI7NDhAZONNBkD5MV 

Hacker sophistication

In 2020, the state actor hacker space was becoming ever more crowded. Unemployed cyber security talent was a new and looming threat. Dovetailing with cyber-criminal sophistication and collaboration was a brand-new wide-open threat landscape. This all put increased pressure on cyber security professionals.

Read the PDF report here
[ad_2]
Source link

Android voice chat app with 5m installs leaked user chats

0
[ad_1]

OyeTalk was leaking unencrypted data through unprotected access to Firebase, Google’s mobile application development platform that provides cloud-hosted database services.

A popular Android voice chat app, OyeTalk, has leaked private user data, including their unencrypted chats, usernames, and cellphone International Mobile Equipment Identity (IMEI) numbers.

With over five million downloads on Google Play, the app has compromised the privacy of all its users while simultaneously exposing them to malicious threats.

Android App OyeTalk Leaked Private User Chats
OyeTalk on Android

OyeTalk was leaking data through unprotected access to Firebase, Google’s mobile application development platform that provides cloud-hosted database services.

The researchers warned that malicious actors could have deleted the dataset, resulting in a permanent loss of users’ private messages, if the leaked data had not been backed up. 

According to the Cyber News blog post, Despite being informed of the data spill, the app developers failed to close off public access to the database. Google’s security measures had to step in, since the spill got too big, to close off the database.

This isn’t all. The developers also carelessly left sensitive information hardcoded in the application’s client-side, including a Google API (application programming interface) key and links to Google storage buckets. The exploitation of this security practice in the past has resulted in data loss or a complete takeover of user data stored on open Firebase or other storage systems.

It turns out, this was not the first occurrence of a data leak affecting OyeTalk. The researchers found that the database had been discovered and marked as vulnerable by unknown actors, likely with no malicious intent. The database contained specific fingerprints used to mark open Firebases, known as “Proof of Compromise” (PoC) and Evidence of Compromise (EoC) or Indicator of Compromise (IOC).

Repercussions

The repercussions of a data leak like the one that occurred with the OyeTalk voice chat app can be severe and far-reaching. First and foremost, the personal information of users can be compromised, leaving them vulnerable to scams.

Furthermore, the leak of personal data can also have a negative impact on the reputation of the app and the company behind it. Users may lose trust in the app and its ability to protect their data, leading to a decline in its user base and revenue. This can also result in legal consequences for the company, as they may face lawsuits and fines for violating data privacy laws.

Overall, the OyeTalk data leak can have significant and lasting consequences for users, the app and its company, and society at large. It underscores the importance of robust data protection measures and responsible handling of personal information and highlights the need for ongoing vigilance in the face of ever-evolving cybersecurity threats.

  1. 23 Android apps leaked sensitive data of 100m users
  2. GoKeyboard App Spying on Millions of Android Users
  3. Dune! game app leaked personal data of Android users
  4. Login Details of Tech Giants Leaked in Data Center Hacks
  5. Iranian hackers drop RatMilad Android spyware in VPN app

[ad_2]
Source link

Hackers Advertising New Info-Stealing Malware on Dark Web

0
[ad_1]

As of now, the Stealc malware targets only Windows devices and steals data from browsers, cryptocurrency wallets, messengers, and email clients.

Cybersecurity researchers from Sekoia have released details of new information-stealing malware called Stealc which has surfaced on several underground hacking forums and on the Dark Web.

According to researchers, a threat actor using the alias “Plymouth” has developed the malware and is advertising it on the dark web. This malware is different, as it simultaneously steals data from its victims and customers. It is also being promoted on Telegram channels.

Hackers Advertising New Info-Stealing Malware on Dark Web
The malware developer offering free samples for the malware on a Russian forum (Credit: Sekoia)

The threat actor stated that Stealc, currently at version 1.3.0, is fully featured and ready-to-use malware. It is not built from scratch but is based on other popular information-stealing malware such as Racoon, Vidar, and Redline Stealer. The malware is continually being upgraded; according to the researchers, it is tweaked every week. It was first spotted in January 2023.

How Does it work?

After it is installed on the target’s PC, the malware starts an anti-analysis check to ensure it isn’t running on a sandbox or a virtual environment. It loads Windows API functions and establishes a connection with the C2 center. It sends the attacker’s hardware identifier and device build name, after which the malware receives commands.

According to Sekoia’s blog post, this is when the malware starts collecting data from the browsers, extensions, and applications and executes its file grabber to exfiltrate all files to the C2 server. Once the entire data is stolen, Stealc self-erases and downloaded DLL files are removed from the device to avoid detection.

Stealc Capabilities

Some of Stealc’s features include a C2 center URL randomizer and an advanced log sorting and searching system. Moreover, the malware spares victims from Ukraine, uses legitimate third-party DLLs, and abuses Windows API functions. It is written in C and automatically exfiltrates data without requiring any interference from the attacker.

The malware can target 75 plugins, 22 browsers, and 25 desktop wallets. Furthermore, it can hide most of its strings using base64 and RC4.

Apart from advertising it on the Dark Web, the threat actor also deploys the malware on target endpoints by creating fake YouTube tutorials about cracking software. Or by offering links in the description, which deploys the info-stealer instead of the offered crack.

Researchers discovered over 40 C2 servers, leading them to conclude that Stealc is gaining traction quickly. Therefore, it is vital to make sure your security software is updated regularly and to avoid downloading and installing software from suspicious or unauthorized sources. Also, never open links or attachments from unknown sources.

  1. Dark Web Search Engines and How to Find Them
  2. Hackers selling Bitcoin ATM Malware on Dark Web
  3. Zombinder on Dark Web Adds Malware to Legit Apps
  4. Web Webinjects Marketplace “In The Box” Discovered
  5. L0rdix malware on dark web steals data, mines crypto

[ad_2]
Source link

Apple Secures Orders for TSMC’s 3nm Chips for iPhone 15 Pro and M3 Macs

0
[ad_1]

3nm chip apple tsmc

According to a report from DigiTimes, Apple has secured all orders for TSMC’s 3nm node process-based chipsets. These 3nm chipsets are expected to power upcoming iPhone 15 Pro and M3 Macs.

 A new report from DigiTimes has revealed that Apple has successfully acquired the entire initial supply of N3 chips from TSMC. TSMC, Apple’s main chipset supplier, began mass producing the 3nm process in late December and has been gradually increasing its process capacity. According to sources cited in the report, TSMC plans to produce 45,000 wafers per month by March.

Apple will reportedly use TSMC’s 3nm technology into for the A17 Bionic chip. This chipsert is likely power the iPhone 15 Pro and iPhone 15 Pro Max models this year. The 3nm node process will reportedly provide 35% better power efficiency over the previous 4nm process, which is currently used in the A16 Bionic chip.

In addition to this, Apple is also planning to release new 14 and 16-inch MacBook Pro models in 2024 that will be equipped with the M3 Pro and M3 Max chips built on TSMC’s 3nm process, according to Ming-Chi Kuo. The M3 Pro and M3 Max chips are expected to offer significant improvements in performance and power efficiency compared to the current 5nm chips such as the M2 Pro found in Apple’s current high-end Mac models.

Source: DigiTimes


[ad_2]
Source link

One UI 5.1 is rolling out widely to Galaxy Z Fold 3 and Flip 3

0
[ad_1]

Samsung is widely rolling out the One UI 5.1 update to the Galaxy Z Fold 3 and Galaxy Z Flip 3. The company began the rollout last week but it was initially limited to users in Asia. But today, the new One UI version is available for the 2021 foldable duo in Europe and Latin America as well. The update should soon reach the US too.

The One UI 5.1 update for the Galaxy Z Fold 3 arrives with the firmware build number F926BXXU3EWB1 in all of these regions. That for the Galaxy Z Flip 3 is F711BXXU4EWB1. As of this writing, the rollout in Latin America is limited to Argentina and Panama for both models. Samsung also hasn’t expanded the update beyond India and Thailand in Asia. But in Europe, the new One UI version is widely available for the two foldable smartphones. Hopefully, it won’t take the company much longer to go global with this update.

Galaxy Z Fold 3 and Galaxy Z Flip 3 users are getting tons of goodies with the latest firmware release. The changelog for the former is slightly bigger than that for the latter. That’s because the Fold model is getting a shortcut to Expert RAW in the stock camera app. It is also getting improvements to Samsung DeX. The company has made it easier to resize windows in split-screen mode. The changes allow for more efficient multitasking, something the Fold series foldables are already pretty good at.

Apart from those two features, the Galaxy Z Flip 3 is getting everything else that One UI 5.1 brings to its Fold counterpart. That includes new selfie effects in the stock camera app, Shared Family Album in the Gallery app, enhanced image remastering, new features, improved modes and routines that allow wallpapers to switch automatically based on your activity, a dynamic weather widget, smart settings suggestions, and more. You can find the full changelog for the Galaxy Z Fold 3 here and Galaxy Z Flip 3 here.

The Galaxy Z Fold 3 and Flip 3 are also getting the February security patch

The One UI 5.1 update also brings the February security patch to the Galaxy Z Fold 3 and Galaxy Z Flip 3. Samsung’s latest SMR (Security Maintenance Release) contains more than 50 vulnerability patches. At least five of those were critical flaws. You can install the new update to keep your foldable safe from those issues, while also getting a host of new features. Go to Settings > Software update and tap on Download and install to check for updates manually.


[ad_2]
Source link

Apple is winning the smartphone wars with Gen Z… in the US

0
[ad_1]

iPhones have long been the go-to choice for everyday consumers in the United States, while Android has appealed more to tech enthusiasts. However, a new report from the Financial Times suggests that Android may face an existential problem as Gen Z, or Zoomers, increasingly prefer Apple’s iPhone over the best Android phones, particularly in the US.

The report reveals that Gen Z is becoming more concerned about social ostracism for not owning an iPhone. And this social pressure is driving young people to purchase Apple products and services, leading to a growing market share across multiple categories. As a result, 34% of all iPhone owners in the US belong to Gen Z, while Samsung’s share is only 10%.

Since Apple has designed its ecosystem to make it difficult for consumers to use cross-platform devices, for every 100 iPhones sold, Apple also sells 26 iPads, 17 Apple Watches, and 35 pairs of AirPods, according to the research firm Canalys. These figures are impressive, especially considering that the average selling price of an iPhone is almost three times that of an Android device.

iMessage is the driving factor

One of the reasons behind Apple’s growing popularity amongst Gen Z is iMessage. The fact that it does not work well with Android forces people to either switch to an iPhone or remain with iOS at all costs. While some may argue that iMessage is only prevalent in the United States, a similar trend is evident in Europe, where iMessage is less popular, and Android has a larger market share. According to Canalys research, 83% of Apple users in western Europe under 25 intend to keep using an iPhone, while less than half of Android users in that group say they will stick with Android.

Although Google has been actively trying to combat the iMessage problem by promoting RCS (Rich Communication Services), it is highly unlikely that Apple will ever adopt RCS, as the company’s business model revolves around creating a closed ecosystem that ties its customers to its products and services.


[ad_2]
Source link

German airports hit with DDoS attack

0
[ad_1]

Seven German airports have had their websites targeted by a suspected distributed denial of service (DDoS) attack.

The attack, which took place on February 16, saw the websites of airports including Dortmund, Nuremburg and Dusseldorf taken offline. Larger German airports, including Munich, Berlin and Frankfurt were not targeted in the attack.

In a statement, the chief executive of Germain airport association, Flughafenverband ADV said “once again, airports fell victim to large-scale DDoS attacks,” but added that “according to the information we have so far, other systems are not affected”.

What is a DDoS attack?

Distributed denial of service attacks, or DDoS attacks, see malicious actors attempt to disrupt a site by overwhelming it or its infrastructure with a large amount of internet traffic. As DDoS attacks overwhelm a site’s bandwidth, this prevents users from accessing the site.

On June 1, 2022, Google reported that it had blocked the “largest” distributed denial of service (DDoS) attack on record, which had a peak of 46 million requests per second (rps).

The attack targeted a Google Cloud Armor user with HTTPS for a duration of 69 minutes and had 5,256 source IPs from 132 countries contributing to it. Google reported that the attack was the biggest Layer 7 DDoS attack reported to date and was 76 percent larger than the previous record.

In a blog post about the attack, Emil Kiner, senior product manager for Cloud Armor, and Satya Konduru, technical lead, both at Google, noted that the attack was akin to “receiving all the daily requests to Wikipedia…in just 10 seconds”. 


[ad_2]
Source link