How much would you pay for an original iPhone? One buyer spent over $63,000

0
[ad_1]

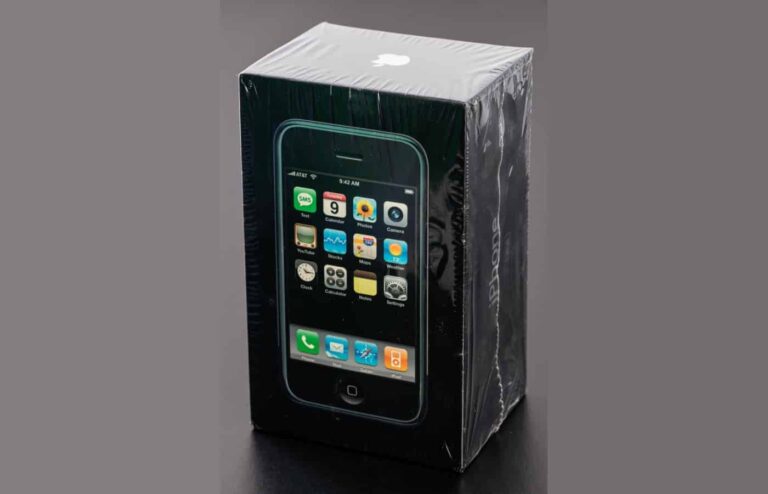
Someone actually paid $63,356 for a factory-sealed, first-gen iPhone at an auction. The iPhone was originally announced in 2007, and this one hasn’t even been unpacked yet. Well, someone was willing to pay really well for it.

Someone actually paid $63,356 for an original, factory-sealed iPhone

This is an 8GB Apple iPhone which cost $599 back when it launched in June of 2007. The auction, during which it was sold, started on February 2 with a starting bid of $2,500. It broke the $60,000 mark over the weekend, however, when it also ended (February 19).

There were actually 27 bids in between the starting bid, and the final one. The final price of $63,356 basically means that the phone sold for over 100 times more than what it originally cost back in 2007.

This smartphone was owned by Karen Green, who got it as a gift from friends over 15 years ago. She never opened it, as she was a Verizon customer, and the device only worked on AT&T’s network.

The phone was appraised with an estimated value of $5,000 back in 2019

She basically put it on a shelf, and never really got around to unboxing it, or selling it. Back in 2019, the device was appraised with an estimated value of $5,000. She finally decided to put it up for auction this month.

As you can see, she earned quite a bit of cash as a result. She probably never thought that such a high price will be reached. Karen Green already has a plan on what to do with the money too. She plans to open up a business, it seems.

It’s not exactly a secret that iPhones do keep their value over the years, so you can imagine what happens with factory-sealed ones, especially such a gem as the original one. Collectors are willing to pay crazy amounts to get ahold of such items, and this is a prime example.

Original iPhone factory sealed 2023


[ad_2]
Source link

Microsoft Patch Tuesday February Addressed 3 Zero-Day Flaws

0
[ad_1]

The second Patch Tuesday update bundle from Microsoft for February 2023 arrived with major vulnerability fixes. Specifically, it addressed 75 different security vulnerabilities, including three zero-day flaws. Users must rush to update their systems to avoid any malicious exploitation.

Microsoft February Patch Tuesday Updates Released

Zero-Day Flaws Fixed

The February Patch Tuesday from Microsoft addresses three zero-day vulnerabilities affecting different products. While all the vulnerabilities received important severity status, the active exploitation of the flaws makes them serious. Notably, all three vulnerabilities escaped any public disclosure, which suggests that the flaws directly caught the attention of criminal hackers.

Specifically, these vulnerabilities include,

  • CVE-2023-21823 (CVSS 7.8): a privilege escalation vulnerability in the Windows Graphics Component could allow an attacker to gain SYSTEM privileges
  • CVE-2023-21715 (CVSS 7.3): a security feature bypass flaw in Microsoft Office could let an authenticated attacker target a system by tricking the victim into opening a maliciously crafted file.
  • CVE-2023-23376 (CVSS 7.8): a privilege escalation in Windows Common Log File System Driver could allow SYSTEM privileges to an adversary.

Other Significant Bug Fixes

Alongside the three zero-day flaws, Microsoft has also fixed numerous other vulnerabilities across different products.

Specifically, these include nine critical-severity vulnerabilities in .NET and Visual Studio, Microsoft Protected Extensible Authentication Protocol (PEAP), Microsoft SQL ODBC Driver, Microsoft Word, and Visual Studio Code. Exploiting all these vulnerabilities could lead to remote code execution attacks. Thankfully, none of these flaws went under attack or caught attention before receiving the relevant patches.

Besides, the update bundle addresses 63 important severity vulnerabilities affecting Microsoft Defender, Azure DevOps Server, Microsoft Exchange Server, Microsoft SharePoint Server, Microsoft PostScript Printer Driver, Microsoft SQL Server, Power BI Report Server, Visual Studio, Windows Graphics Component, Windows Internet Storage Name Service (iSNS) Server, Windows MSHTML Platform, Windows Installer, and other components.

Exploiting these vulnerabilities could result in varying impacts, from remote code execution to privilege escalation, denial of service, and information disclosure.

While the February Patch Tuesday is huge, with 75 bug fixes, it did not include any patches for low-severity flaws. Given the severity of the issues, Microsoft users must update their respective systems with the latest software updates to receive all patches.

Let us know your thoughts in the comments.


[ad_2]
Source link

Google Pixel Fold to be heavier than the Galaxy Z Fold 4

0
[ad_1]

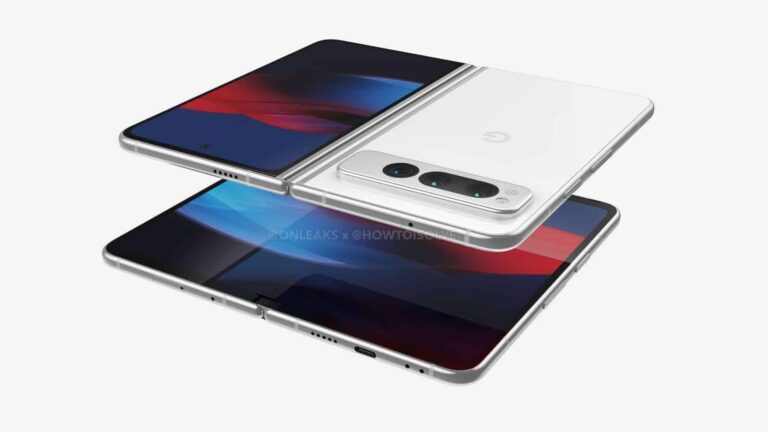
According to a new report, the Google Pixel Fold may be heavier than we thought. This handset may be heavier than the Galaxy Z Fold 4. This information comes from 9to5Google, and was provided by “a source”.

The Pixel Fold may be heavier than the Galaxy Z Fold 4, but pack a larger battery

For comparison’s sake, the Galaxy Z Fold 4 weighs 263 grams, so the Pixel Fold will weigh more than that. It will also include a larger battery based on this report, however. The Galaxy Z Fold 4 features a 4,400mAh battery. The Pixel Fold will seemingly have a battery size that is closer to, but still well below 5,000mAh.

When it comes to size, the Pixel Fold is tipped to feature a style similar to the OPPO Find N2. It will be around the same height at 140mm, but it will be wider by 7mm. The Find N2 is 72.6mm wide, so the Pixel Fold could be almost 80mm wide when folded.

The Galaxy Z Fold 4, once again, for comparison’s sake, is 67.1mm wide when folded, but it’s a lot taller at 155.1mm. This obviously points to the fact that the Pixel Fold will be similar in style to the Find N2, as it will have a more landscape-orientation main display when unfolded.

That main display is supposed to comfortably fit two apps side-by-side for proper multitasking. Its UI will also hopefully be well-optimized thanks to Google’s recent efforts focused on tablets and foldables.

The Pixel Fold will have a similar style to the OPPO Find N2, but be larger still

Considering the added width of the Pixel Fold, its main display will be larger than the Find N2’s main display. We don’t know the exact size, but the Find N2’s panel measures 7.1 inches, and this one will be larger than that.

The cover display will also be larger in diagonal than the Find N2’s due to its added width. So it will be larger than 5.54 inches for sure.

We still don’t know when will the Pixel Fold launch, but it’s rumored to arrive during Google I/O or alongside the Pixel 8 series later this year. The latter seems like a more probable outcome.


[ad_2]
Source link

What you can do with Ethereum

0
[ad_1]

Are you planning to venture into Ethereum-related activity and wondering what exactly you should do? Here are essential things you can do with Ethereum.

Even with the main developments in blockchain technologies, most people lack the slightest idea of what they can do with Ethereum. The truth is that Ethereum is one of the most promising developments you might want to try. In this case, Ethereum is a blockchain platform that people can use to create decentralized applications. Notably, the decentralized nature of the application aims to provide maximum security, particularly in data.

Just like Ethereum Code AI-system, you can gather ample information about Ethereum before you venture into any related businesses. Most Ethereum users today apply it mainly as a digital currency, although there are other ways to use it. If you are interested in Ethereum, here are some of the things you can do with it:

Build a Decentralized Finance

Most people who have developed decentralized finance can confirm that it is one of the best ventures that Ethereum offers. In this case, you can specialize in designing and establishing decentralized applications and exchanges. You can also consider minting stablecoins. Notably, people can use Ethereum to create smart contracts, which are part of the Decentralized Finance technology. Either way, Decentralized Finance is likely to offer more lucrative deals as far as using Ethereum is concerned.

Enhancing the Banking Systems

One of the most significant concerns in banking is security threats and illicit activities. Banks and other financial institutions have lost money to hackers due to a lack of the best security mechanisms. It is, therefore, essential to ensure that modern banks enhance their systems by applying secure technology. Banks now use Ethereum in their financial strategies based on its decentralized nature. In other words, Ethereum provides an environment with zero access to third parties. Therefore, it becomes tough for hackers to access information based on blockchain technology such as Ethereum.

Payment Mode

Another common way in which people can use Ethereum is to make payments. With the current advancement of the cryptocurrency industry, corporate worldwide are giving comprehensive payment methods options, including altcoins. The Ethereum technology has amply facilitated the development of a payment method widely accepted in the corporate sector. With a digital wallet, you can convert your local currency into Ethereum tokens and make payments using such.

In The Health Sector

The current evolution in data storage in the health sector has prompted the need for robust yet secure mechanisms that allow easy retrieval and sharing among various parties. Blockchain technology offers a decentralized platform that institutions and companies can use to store data. The best part is that data stored using blockchain technology can be in bulk and remain safe. And this is because blockchain technology operates as a cloud technology that can accommodate voluminous information. For instance, information regarding vaccine dissemination can be stored using the Ethereum technology and retrieved at any given point. The idea here is to regulate access to information easily achievable through blockchain technology.

Conclusion

The development of Ethereum has been a significant benefit in different application areas. Today, Ethereum stands second as the most influential cryptocurrency. And this implies that Ethereum has a robust infrastructure that allows easy use in other sectors. The best part is that Ethereum is highly secure in any application area. That way, users are guaranteed safety in their digital transactions and other applications. The above sectors are good examples of where Ether could work. So, if you have always wondered how to use Ethereum, this article has provided answers. Nevertheless, research further about this cryptocurrency to use it safely and effectively.


[ad_2]
Source link

Nmap – Best Network Monitor and Port Scanner Tool

0
[ad_1]

Nmap is an open source network monitoring and port scanning tool to find the hosts and services in the computer by sending the packets to the target host for network discovery and security auditing.

Numerous frameworks and system admins additionally think that its helpful for assignments, for example, network inventory, overseeing administration overhaul timetables, and observing host or administration uptime.

Nmap uses raw IP packets in novel ways to determine what hosts are available on the network, what services (application name and version) those hosts are offering, what operating systems (and OS versions) they are running, what type of packet filters/firewalls are in use, and dozens of other characteristics.

It was designed to rapidly scan large networks, but works fine against single hosts. it runs on all major computer operating systems, and official binary packages are available for Linux, Windows, and Mac OS X.

In addition to the classic command-line Nmap executable, the Nmap suite includes an advanced GUI and results in the viewer (Zenmap), a flexible data transfer, redirection, and debugging tool (Ncat), a utility for comparing scan results (Ndiff), and a packet generation and response analysis tool (Nping).

You can also take Master in Ethical Hacking & Penetration Testing Online course where you can learn more about NMAP and advance level Ethical hacking skills.

Nmap is …

  • Flexible: Supports dozens of advanced techniques for mapping out networks filled with IP filters, firewalls, routers, and other obstacles. This includes many port scanning mechanisms (both TCP & UDP), OS detection, version detection, ping sweeps, and more. See the documentation page.
  • Powerful: Nmap has been used to scan huge networks of literally hundreds of thousands of machines.
  • Portable: Most operating systems are supported, including Linux, Microsoft Windows, FreeBSD, OpenBSD, Solaris, IRIX, Mac OS X, HP-UX, NetBSD, Sun OS, Amiga, and more.
  • Easy: While NMAP offers a rich set of advanced features for power users, you can start out as simply as “nmap -v -A targethost“. Both traditional command line and graphical (GUI) versions are available to suit your preference.
  • Free: The primary goals of this  NMAP Project is to help make the Internet a little more secure and to provide administrators/auditors/hackers with an advanced tool for exploring their networks. it is available for free download, and also comes with full source code that you may modify and redistribute under the terms of the license.
  • Well Documented: Significant effort has been put into comprehensive and up-to-date man pages, whitepapers, tutorials, and even a whole book! Find them in multiple languages here.
  • Supported: While it comes with no warranty, it is well supported by a vibrant community of developers and users. Most of this interaction occurs on the Nmap mailing lists. Most bug reports and questions should be sent to the nmap-dev list, but only after you read the guidelines.
  • Acclaimed: Nmap has won various honors, including “Information Security Product of the Year” by Linux Journal, Info World and Codetalker Digest. It has been included in many magazine articles, a few motion pictures, many books, and one comic book arrangement. Visit the press page for further subtleties.
  • Popular: Thousands of people download every day, and it is included with many operating systems (Redhat Linux, Debian Linux, Gentoo, FreeBSD, OpenBSD, etc). It is among the top ten (out of 30,000) programs at the Freshmeat.Net repository. This is important because it lends Nmap its vibrant development and user support communities.

 TOP NMAP COMMEANDS:

1: To find out nmap version, run:

 # nmap --version

Sample outputs:

Nmap version 5.51 ( http://nmap.org )

2: To scan an IP address or a host name (FQDN), run:


 # nmap 1.2.3.4
 # nmap localhost
 # nmap 192.168.1.1

3:  Information out of the remote system:


 # nmap -v -A scanme.nmap.org
 # nmap -v -A 192.168.1.1

Sample outputs:

 Starting Nmap 5.00 ( http://nmap.org ) at 2012-11-19 16:38 IST
 NSE: Loaded 30 scripts for scanning.
 Initiating ARP Ping Scan at 16:38
 Scanning 192.168.1.1 [1 port]
 Completed ARP Ping Scan at 16:38, 0.04s elapsed (1 total hosts)
 Initiating Parallel DNS resolution of 1 host. at 16:38
 Completed Parallel DNS resolution of 1 host. at 16:38, 0.00s elapsed
 Initiating SYN Stealth Scan at 16:38
 Scanning 192.168.1.1 [1000 ports]
 Discovered open port 80/tcp on 192.168.1.1
 Discovered open port 22/tcp on 192.168.1.1
 Completed SYN Stealth Scan at 16:38, 0.27s elapsed (1000 total ports)

4:  Scan multiple IP address or subnet (IPv4):


 nmap 192.168.1.1 192.168.1.2 192.168.1.3
 ## works with same subnet i.e. 192.168.1.0/24
 nmap 192.168.1.1,2,3

You can scan a range of IP address too:

nmap 192.168.1.1-20

You can scan a range of IP address using a wildcard:

nmap 192.168.1.*

Finally, you scan an entire subnet:

nmap 192.168.1.0/24

5: Find out if a host/network is protected by a firewall:

 nmap -sA 192.168.1.254
 nmap -sA server1.gbhackers.com

6: Turn on OS and version detection scanning script (IPv4):

 nmap -A 192.168.1.254
 nmap -v -A 192.168.1.1
 nmap -A -iL /tmp/scanlist.txt 

7:  Scan a host when protected by the firewall:

 nmap -PN 192.168.1.1
 nmap -PN server1.gbhackers.com

8: Scan an IPv6 host/address:


 The -6 option enable IPv6 scanning. The syntax is:

 nmap -6 IPv6-Address-Here
 nmap -6 server1.gbhackers.com
 nmap -6 2607:f0d0:1002:51::4
 nmap -v A -6 2607:f0d0:1002:51::4

9:  How do I perform a fast scan:

 nmap -F 192.168.1.1

10: Display the reason a port is in a particular state:


 nmap --reason 192.168.1.1
 nmap --reason server1.gbhackers.com

11: Only show open (or possibly open) ports:

 nmap --open 192.168.1.1
 nmap --open server1.gbhackers.com

12: Show all packets sent and received:

 nmap --packet-trace 192.168.1.1
 nmap --packet-trace server1.gbhackers.com

13: Show host interfaces and routes:

This is useful for debugging (ip command or route command or netstat command like
 output using nmap)

 nmap --iflist

Sample outputs:

Starting Nmap 5.00 ( http://nmap.org ) at 2012-11-27 02:01 IST
 ************************INTERFACES************************
 DEV (SHORT) IP/MASK TYPE UP MAC
 lo (lo) 127.0.0.1/8 loopback up
 eth0 (eth0) 192.168.1.5/24 ethernet up B8:AC:6F:65:31:E5
 vmnet1 (vmnet1) 192.168.121.1/24 ethernet up 00:50:56:C0:00:01
 vmnet8 (vmnet8) 192.168.179.1/24 ethernet up 00:50:56:C0:00:08
 ppp0 (ppp0) 10.1.19.69/32 point2point up

**************************ROUTES**************************
 DST/MASK DEV GATEWAY
 10.0.31.178/32 ppp0
 209.133.67.35/32 eth0 192.168.1.2
 192.168.1.0/0 eth0
 192.168.121.0/0 vmnet1
 192.168.179.0/0 vmnet8
 169.254.0.0/0 eth0
 10.0.0.0/0 ppp0
 0.0.0.0/0 eth0 192.168.1.2


14: How do I scan specific ports:

 nmap -p [port] hostName
 ## Scan port 80
  nmap -p 80 192.168.1.1

## Scan TCP port 80
 nmap -p T:80 192.168.1.1

## Scan UDP port 53
 nmap -p U:53 192.168.1.1

## Scan two ports ##
 nmap -p 80,443 192.168.1.1

## Scan port ranges ##
 nmap -p 80-200 192.168.1.1

## Combine all options ##
 nmap -p U:53,111,137,T:21-25,80,139,8080 192.168.1.1
 nmap -p U:53,111,137,T:21-25,80,139,8080 server1.cyberciti.biz
 nmap -v -sU -sT -p U:53,111,137,T:21-25,80,139,8080 192.168.1.254

## Scan all ports with * wildcard ##
 nmap -p "*" 192.168.1.1

## Scan top ports i.e. scan $number most common ports ##
 nmap --top-ports 5 192.168.1.1
 nmap --top-ports 10 192.168.1.1

Sample outputs:

Starting Nmap 5.00 ( http://nmap.org ) at 2012-11-27 01:23 IST
 Interesting ports on 192.168.1.1:
 PORT STATE SERVICE
 21/tcp closed ftp
 22/tcp open ssh
 23/tcp closed telnet
 25/tcp closed smtp
 80/tcp open http
 110/tcp closed pop3
 139/tcp closed netbios-ssn
 443/tcp closed https
 445/tcp closed microsoft-ds
 3389/tcp closed ms-term-serv
 MAC Address: BC:AE:C5:C3:16:93 (Unknown)

nmap done: 1 IP address (1 host up) scanned in 0.51 seconds

Conclusion

Nmap can perform various scanning operation and it has been leading scanning tool in the security industry since its release in 1997, also its worlds leading port scanners to find out open ports and firewall. still, Nmap used by various organizations and penetration tester to find out loops and secure the network.

You can follow us on LinkedinTwitterFacebook for daily Cybersecurity updates also you can take the Best Cybersecurity course online to keep yourself updated.

Also Read:

SPARTA – Network Penetration Testing GUI Toolkit

SN1PER – A Detailed Explanation of Most Advanced Automated Information Gathering & Penetration Testing Tool

Masscan – World’s Fastest Scanner – Scan the Entire Internet in Under 6 Minutes

scanless – A Pentesting Tool to Perform Anonymous Port Scan on Target Websites

theHarvester-Advanced Information Gathering Tool for Pentesters & Ethical Hackers

[ad_2]
Source link

Vivo may be first to use Snapdragon 8 Gen 2 SoC in a foldable phone

0
[ad_1]

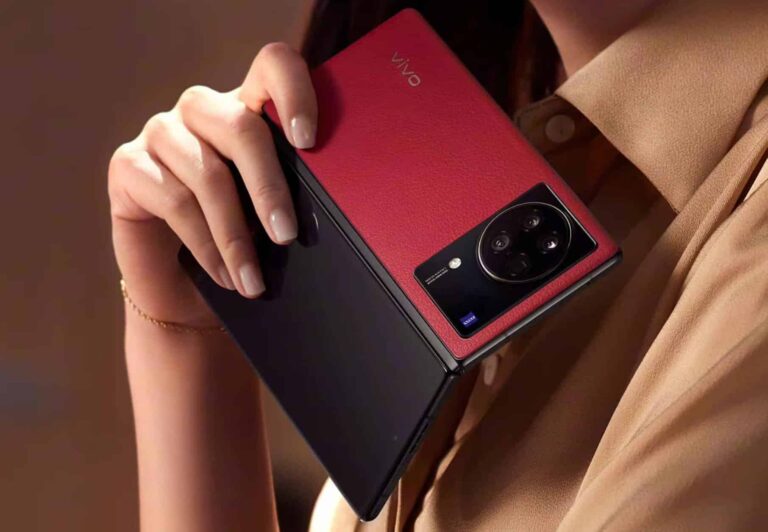
Vivo may actually be the first to use the Snapdragon 8 Gen 2 SoC in a foldable smartphone. This information comes from Digital Chat Station, a well-known Chinese tipster. He has a really good track record, so this is easily possible.

The Vivo X Fold 2 may be the first foldable phone to utilize the Snapdragon 8 Gen 2

The tipster shared this info via Weibo, while also adding what device he was talking about. The device in question is the Vivo X Fold 2, a direct successor to the Vivo X Fold that arrived last year. The Vivo X Fold launched in April 2022, and its successor is expected to follow this year. Chances are it will launch around the same time, so we could expect an April launch.

The tipster also shared some spec info when it comes to that device. The Vivo X Fold 2 will feature a 4,800mAh battery, it seems. It will also support 120W wired charging, which will charge up that battery in no time.

That is basically everything he shared. Chances are we’ll get more information about the phone in the next month or so. We’re not even sure if Vivo plans to keep the design similar, or will we see significant changes.

The Vivo X Fold actually has a similar style to the Galaxy Z Fold 4. It’s a book-style foldable, with a larger inner and outer display. It includes an 8.03-inch main panel, and a 6.53-inch secondary display.

The device will likely have top-of-the-line specs, and hopefully be lighter than its predecessor

Its successor will likely include such large displays as well. They may be a bit smaller/larger, but around the same size. We’re also guessing that Vivo will utilize LPDDR5X RAM in the new phone, along with UFS 4.0 storage, but it remains to be seen.

The Vivo X Fold was truly heavy at 311 grams, so we’re hoping that Vivo will be able to shave off some of the weight from the Fold 2. Foldables are usually quite hefty, but not to that level. The Vivo X Fold is actually a lot heavier than most of its direct competition.

It also remains to be seen if the Vivo X Fold 2 will make its way to global markets. The Vivo X Fold and Vivo X Fold+ did not, they remained exclusive to China.


[ad_2]
Source link

T-Mobile to shut down its 2G network in April next year

0
[ad_1]

T-Mobile is finally ready to retire its 2G GSM network. The company has revealed that it will end support for the three-generations old network spectrum on April 2, 2024. Other big wireless carriers in the US have already shut down their 2G services. AT&T pulled the plug on January 1, 2017, while Verizon reportedly retired the outdated network at the end of 2020.

T-Mobile announces its plan to retire the aging 2G network

T-Mobile didn’t provide many details about its plan to shut down 2G services. The carrier simply mentioned the date in an official support document on its website. It has likely also notified users about the impending sunset of the age-old wireless network. There may not be many people with a 2G-only phone today, so the change won’t affect a large population. But the few T-Mobile customers who are still using a basic phone with no 4G/5G support now have just over a year to get a smartphone.

“Moving customers who are on old networks onto modern, advanced high-speed networks means they will need to have phones and devices that can tap into the latest technologies. We’ll ensure that we support our customers and partners through the transition,” the carrier said. Users who are impacted by the shutdown of T-Mobile’s 2G network should get some sort of direct communication from the company in the coming months. It will likely provide them with instructions on how to upgrade to a new phone.

Note that a 3G phone won’t work. T-Mobile has already pulled the plug on its 3G UMTS network. Yes, it shut down the newer network ahead of 2G. The shutdown came on July 1 last year, a day after it retired Sprint’s 4G LTE network that it acquired following the high-profile merger in 2020. T-Mobile also shuttered Sprint’s 3G CDMA network on March 31 last year. By retiring its 2G network next year, the self-proclaimed Un-carrier is all set to fully embrace the latest wireless network spectrums.

T-Mobile is also ending support for Sprint SIM cards

As part of this network evolution, T-Mobile is also ending support for legacy Sprint SIM cards. Sprint customers who haven’t switched their SIMs with a T-Mobile-issued card after the two carriers merged a few years back must do now. The company recently sent a legal notice, as well as multiple email and SMS notifications, to those users asking them to replace their SIM cards by the end of April this year. On May 1, all Sprint-issued SIMs will be non-functional. Even emergency calls to 911 may not go through.


[ad_2]
Source link

HTTP Request Smuggling Vulnerability Riddled HAProxy

0
[ad_1]

A serious security vulnerability existed in HAProxy that could allow HTTP request smuggling attacks. The vulnerability affected almost all HAProxy versions, which the maintainer patched accordingly.

HAProxy Vulnerability Could Trigger HTTP Content Smuggling

The HAProxy maintainer, Willy Tarreau, has recently shared details about a serious HTTP request smuggling vulnerability in HAProxy.

HAProxy is a dedicated high-performance, open-source load balancer and reverse proxy tool for HTTP and TCP applications. It distributes workloads and improves the website’s performance via reduced response times and increased throughput.

According to Tarreau’s notice, he came to know of the vulnerability following a report from a team of researchers.

Briefly, the flaw existed in HAProxy header processing, allowing HTTP content smuggling attacks. A maliciously crafted HTTP request could trigger HAProxy to “drop some important headers fields” after parsing. In turn, it would create extra requests to the server, letting the subsequent requests bypass HAProxy filters.

An adversary could exploit the flaw to access restricted content, bypass URL authentication, or achieve other malicious purposes on a target website.

Tarreau explained that crafting such an attack was not trivial. But it wasn’t impossible either, particularly for an attacker acquainted with HTTP internals.

Bug Fix Released

HAProxy’s maintainer confirmed that the vulnerability affected almost app versions. These include HTX-aware versions 2.0 and above and non-HTX versions 1.9 and before or version 2.0 in legacy mode. However, the impact of the vulnerability isn’t the same across all versions.

Upon confirming the vulnerability, Tarreau started working on a fix, releasing it across all HAProxy versions. The patched versions include 2.8-dev4, 2.7.3, 2.6.9, 2.5.12, 2.4.12, 2.2.29, and 2.0.31.

For HAProxy users, the recommends upgrading to the patched version of their relevant branch as the best strategy to stay safe. Nonetheless, for those who cannot manage immediate upgrades, Tarreau has shared a workaround that rejects requests attempting to trigger the flaw with a 403 error. The admins can then note the rising 403 error entries in the log to identify exploitation attempts.

While this workaround serves well, it cannot guarantee foolproof security. So, upgrading to a patched version is the ultimate permanent solution.

Let us know your thoughts in the comments.


[ad_2]
Source link

Realme GT3 can fully charge in less than 10 minutes: video

0
[ad_1]

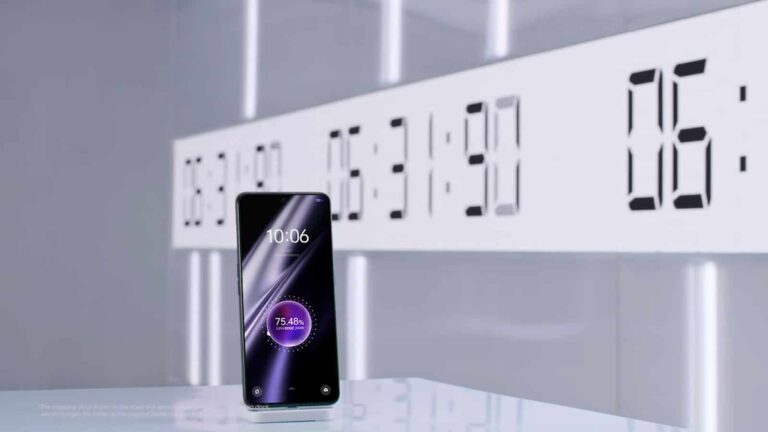
The upcoming Realme GT3 can fully charge in less than 10 minutes. The company decided to show us proof, so it released a new YouTube video. The phone fully charged in only 9 minutes and 37 seconds.

The Realme GT3 can fully charge in less than 10 minutes, as shown in the video

The Realme GT3 is set to become the world’s fastest-charging smartphone, as it utilizes OPPO’s 240W SuperVOOC charging. The phone actually includes a 4,600mAh battery on the inside, in case you were wondering.

It managed to reach a 20% charge in only 80 seconds. After 4 minutes, it stood at a 50% charge, before it finally reached a 100% charge status after 9 minutes and 37 seconds. You can check that out in the video embedded below.

The Realme GT3 is actually a global variant of the Realme GT Neo5, a phone that was launched in China. To be more accurate, it’s a global variant of the GT Neo5 240W, as two variants were announced.

The other variant supports 150W charging, which is also blazing fast. It also includes a 5,000mAh battery. We still don’t know if we’ll get a 150W variant of the Realme GT3 (global model), we’ll have to wait and see.

The device will launch on February 28

The Realme GT3 will become official on February 28. Realme will launch the phone at MWC 2023, in Barcelona. Now, its charging is its main selling point, but this phone will deliver really compelling specs in general.

It will include the Snapdragon 8+ Gen 1 SoC, along with LPDDR5X RAM and UFS 3.1 flash storage. A 6.74-inch AMOLED display will also be in use, and it will support a 144Hz refresh rate.

A 50-megapixel main camera will sit on the back of the phone, while Android 13 will come pre-installed on the phone. All in all, it will be quite a compelling smartphone.


[ad_2]
Source link

Microsoft readying Teams 2.0 with massive performance boost

0
[ad_1]

Microsoft is readying a major update for its remote collaboration and communication app Teams. The company has reportedly rebuilt the service from scratch to bring a significant boost in performance. Internally known as Microsoft Teams 2.0 or 2.1, the Windows giant is currently testing the updated version among employees. It plans to release a public preview next month.

Microsoft has rebuilt Teams for improved performance

Microsoft Teams is one of the most popular business communication services out there. The company regularly updates the platform to add new features and make improvements. With the launch of Windows 11, it integrated Teams into the system to enable faster loading and more efficient performance. Talking about the improvements, Microsoft’s then-head of engineering for Teams had said that the service will employ a new architecture that will help the company “add support for multiple accounts, work-life scenarios, release predictability, and scale up for the client”. Rish Tandon, who has since left Microsoft for Meta added that “it will be a journey but with Windows 11 we have taken key first steps.”

The so-called Microsoft Teams 2.0 is the end product of that journey. As Tandon previously revealed, the new version will move away from the Electron framework to Microsoft’s Edge Webview2 technology. This would give the company more control over the platform. The Windows maker is also switching to the React Javascript library from Angular. Last but not least, Teams 2.0 is leveraging Apollo GraphQL and will be powered by Microsoft Edge. All of these changes will bring a host of functional and aesthetic improvements.

Overall, the new Microsoft Teams will “significantly improve its system resource usage on PCs and laptops”. We are talking about a 50 percent drop in memory usage, while Teams will also tax the CPU less and effectively consume less power. This will improve the battery life of laptops. All in all, Microsoft Teams will open faster and feel smoother to use on your computer. It shouldn’t lag even on aging PCs or laptops, making remote collaboration and communication a more seamless experience.

The updated Microsoft Teams will be available to the public next month

Apart from Tandon’s announcement back in June 2021, Microsoft hasn’t shared many details about the new version of Teams. But sources familiar with the matter recently told The Verge that the company is broadly testing the service among employees, with a public preview planned for late March. It will reportedly offer a toggle to switch back to the current version of Teams if the update breaks something for users, or if they feel the need to for some other reason. We should hear more about Microsoft Teams 2.0 in the coming weeks.


[ad_2]
Source link