Managed service providers in cyber attacks

0
[ad_1]

If someone decides to rob a bank in 2024 without having slept in a cryochamber for 40 years, they probably will not be searching for a revolver. Instead, they might turn to cyber crime (or reconsider their plans altogether). They could take it a step further – not just targeting one bank or going one by one, but attacking them en masse. By hacking into a managed service provider (MSP), they can gain access to the infrastructure of numerous client organizations, including banks.

The example might seem humorous, but the reality is grim. Cyber criminals are increasingly targeting MSPs, and this rising threat is being reported globally, including in the US, UK and other countries.

The role of MSPs in cyber security breaches

The abbreviation MSP refers to contractors who offer clients comprehensive management of IT products using the infrastructure-as-a-service (IaaS) model. According to IBM, the primary reason for successful attacks on MSPs is compromised credentials of both the providers’ employees and their customers. Weak and compromised passwords account for one-third of these incidents. The most commonly found user accounts on the dark net include Microsoft Outlook and WordPress.

Another significant threat is software vulnerabilities. Over the past year, the number of vulnerabilities in cloud services has tripled, increasing by almost 200%, according to IBM. Here, too, criminals exploit security flaws in Microsoft Outlook and other widely used business products. However, there are also instances where specialized applications for MSPs become problematic.

One of the most notable examples involves a vulnerability found in the ConnectWise ManagedITSync plugin. Service providers use this plugin to integrate the ConnectWise Manage automation platform with Kaseya VSA, which handles remote monitoring and asset management. The discovered defect allowed for the modification of databases, the addition of new users, granting them full permissions and assignment of any tasks. In simpler terms, criminals could remotely download malware onto the devices of MSP customers.

Although the bug was quickly fixed, other issues with Kaseya VSA surfaced later. In 2021, at least three major MSPs and their clients were impacted by a vulnerability. For example, in Sweden, the web services of the large retail chain Coop were compromised, forcing the company to temporarily close about 800 stores.

READ: The top 10 APAC data breaches

Blackmailing and spying

Attacks on the MSP sector often involve the same criminal groups, many of which are ransomware gangs or those who lease their rogue software through a subscription model to other black hat hackers. Sometimes, criminals demand a ransom from the provider itself, but more frequently, they target its customers. Hackers commonly threaten to leak data. To illustrate the scale, consider three incidents involving well-known gangs.

1. Black Hunt

In January 2024, an attack on Tigo Business, a market leader in mobile communications, cloud services and hosting in Paraguay, came to light. The provider was targeted by the Black Hunt ransomware group. As a result of the attack, 330 of the provider’s servers were encrypted, causing immediate failure. Consequently, the web services of more than 300 client companies were disrupted.

The Black Hunt hackers first emerged at the end of 2022 and are active in South America. Typically, the criminals gain access to corporate networks and user devices, from which they launch ransomware attacks. Additionally, in their communications with victims, they mention the possibility of selling the obtained data on the dark net.

The primary entry point for these attacks is unsecured remote desktop protocols (RDPs). Once they gain access, the criminals clear the Windows event logs on the victims’ computers, delete shadow copies of NTFS records, disable the system restore capability and terminate Microsoft Defender. All of these actions occur covertly without the user’s awareness.

2. REvil

Another ransomware group has exploited vulnerabilities in famous software – Kaseya VSA. The most notable incident involving the REvil group and MSP contractors occurred in 2021. The group claimed to have infected both Kaseya itself and other service providers using its products. According to the criminals, this resulted in a million operating systems worldwide being affected. Previously, the group executed a similar attack using Sodin ransomware. Hackers primarily targeted MSPs through the Webroot remote access console.

READ: Five ransomware gangs and their tactics (part two)

3. APT29

At the end of February 2024, the Cybersecurity and Infrastructure Security Agency (CISA) reported that the APT29 group started to specialize in attacks on cloud services. Previously, they focused on exploiting on-premises vulnerabilities.

APT29, also known as Midnight Blizzard and Cozy Bear, is believed by some security experts to be operated by the Russian Foreign Intelligence Service. Typically, this group targets government structures and organizations in the US and European countries. The incidents often result in leaks of confidential information.

Typically, criminals gain access to a victim’s network through brute force attacks. However, according to a CISA report, in attacks on cloud servers, APT29 hackers more frequently use tokens, which allow them to access accounts without needing a password. The group also often employs the multi-factor authentication (MFA) bypass technique. Once they have accessed an organization’s cloud storage, group members add new devices to it and begin reconnaissance.

Defense strategies

The principle is straightforward: the fewer IT service providers you have, the lower the likelihood of attacks stemming from them. Another obvious piece of advice: it is better to verify a contractor’s reliability in advance. This is not just about whether attackers have previously targeted them. A company might be too new to have a significant history of such incidents, yet it can be just as reliable as its competitors. Additionally, not all market players are willing to share such information about themselves.

That is why it is advised to check if the service provider has the necessary regulatory and market compliance certificates. It is important to consider both industry-specific certifications like PCI DSS and general ones like ISO 27001.

DOWNLOAD: Threat report 2024: Cyber security in the era of AI

The important thing to remember is that having a closed case with paper security does not always ensure effective data security in practice. If you are unsure, it is best to ask the provider questions that fall within their area of responsibility. These include:

1. What type of data center houses its equipment?

Sometimes, what is labeled as a data center might just be a server room within a business center. In terms of physical security, this setup is typically less strong compared to a standalone data center with a fenced area. Also check how the access system is managed, whether there is round-the-clock security and if there is indoor and outdoor video surveillance.

2. How is network security arranged?

You should be concerned not only about mandatory network segmentation, which separates the provider and client networks. It is vital to understand how DDoS protection is organized: does the attacked company get routed to a blackhole, or is the entire cloud shielded at the L3/L4 level? The latest method allows for detecting threats earlier and avoiding an abrupt shutdown of the victim’s IP addresses.

3. What identity and access management practices are implemented?

It is preferable if provider and client administrators connect to resources using MFA and through remote desktop (VDI). Additionally, it is good if the contractor not only mandates updating access credentials every 90 days but also verifies password hashes to prevent brute-force attacks.

4. What vulnerability scanners are used?

All MSPs routinely scan their internal and cloud infrastructure. However, there are instances where, as per the agreement, some resources provided by the contractor to the client are also subjected to checks.

5. How is monitoring conducted and logs collected?

Many providers use logs from cloud software and devices to promptly detect anomalies and mitigate potential risks for themselves and their clients. This data facilitates faster incident response and investigations.

6. Are backups created and stored at a remote location?

It is important not to confuse backups with disaster recovery orchestration (and there are such misconceptions in practice). In the case of ransomware, there is a risk of replicating the same encrypted data to the backup site as on the primary one. Ensure your MSP backup strategy addresses these concerns comprehensively.

7. Do they provide training for staff?

Since people are the weakest link, staff training should focus on things like recognizing social engineering tactics. They should practice strong password habits and safe browsing. Employees also need to know how to report security incidents promptly.

All the mentioned criteria represent the basic standards that a trustworthy service provider should meet. Ideally, the provider goes beyond regulatory and client demands. For example, conducting pre-incident response (Pre-IR) tests is an optional step. If the provider takes this initiative and achieves positive results, it demonstrates a heightened commitment to safety concerns.

While there are many MSP-related threats out there, the reality is not as dire as one might think. Similar to other industries, only a small percentage of companies fall victim to hackers. In most cases, service providers employ strong measures and protections that prove effective across the board. If you happen to be that daring cyber criminal attempting to breach a reliable service provider, I pity your dark endeavors, but chances are, achieving your goal will be a tough nut to crack.


[ad_2]
Source link
Microsoft Details On Using KQL To Hunt For MFA Manipulations

0
[ad_1]

It is difficult to secure cloud accounts from threat actors who exploit multi-factor authentication (MFA) settings.

Threat actors usually alter compromised users’ MFA attributes by bypassing the requirements, disabling MFA for others, or enrolling rogue devices in the system.

They do so stealthily, mirroring helpdesk operations and making it hard to notice the noise of directory audit logs.

To protect themselves against this insidious attack vector on clouds, organizations need to strengthen monitoring and controls around MFA configuration changes.

Cybersecurity researchers at Microsoft recently detailed using the KQL (Kusto Query Language) to hunt for MFA manipulation.

With ANYRUN You can Analyze any URL, Files & Email for Malicious Activity : Start your Analysis

KQL Hunt For MFA Manipulations

Microsoft Entra audit logs record MFA setting changes, creating two entries: one with a descriptive activity name but lacking details and another “Update User” event showing modified properties in between much noise. 

Analyzing these in the Entra portal is difficult due to data volume, especially for large tenants. However, Kusto Query Language (KQL) can simplify this task. 

The cybersecurity analysts provided ready-to-use KQL queries for Azure Log Analytics and Microsoft Defender 365 Advanced Hunting to help analyze and detect MFA configuration changes in your own tenant.

Data flow of logs related to account manipulation (Source – Microsoft)

This allows enhanced monitoring even if audit logs are only retained for 30 days by default.

There are 3 MFA properties, and here below we have mentioned them:-

  • StrongAuthenticationMethod
  • StrongAuthenticationUserDetails
  • StrongAuthenticationAppDetail

The aim is to detect alterations in a user’s registered MFA and default methods.

Researchers used KQL to filter out entries from the logs that may have timestamps, actors, and targets alongside their changed, old, and new values. Rows are generated for multiple changed properties.

The results indicate modified MFA settings by certain users, the people who altered them, and where further investigation should concentrate.

Security analysts compare OldValue and NewValue to detect changes in MFA details like added or modified emails and phone numbers. The output shows examples that may or may not be expected. 

To hunt manipulations, they extend the query to look for MFA details added across multiple users within a timeframe, surfacing potentially rogue email addresses or phone numbers provisioned altogether. 

They can also monitor for users switching phone numbers to a different country code by checking if the first 3 characters changed between old and new values. 

These queries allow for identifying suspicious MFA configuration changes at scale.

DeviceName and DeviceToken identify devices registered for Authenticator App logins. Contrasting the OldValue and NewValue shows when users add or remove the devices. 

Checking DeviceToken across users detects if one device is registered across multiple accounts, potentially indicating compromised accounts used by an attacker to persist multi-factor access. 

While sometimes done by IT admins, reusing devices across accounts is generally insecure unless both belong to the same user.

As multi-factor authentication (MFA) becomes more widespread, attackers increasingly focus on MFA for initial access obtained through token hijacking or stealing and social engineering attacks.

Account authentication methods are frequently changed after a first compromise.

Knowing about Microsoft Entra Audit Logs of MFA modification events will help detect any suspicious activities related to MFA, such as illegal scenarios, across your organization, leading to quick investigation and remediation.

Looking for Full Data Breach Protection? Try Cynet's All-in-One Cybersecurity Platform for MSPs: Try Free Demo 


[ad_2]
Source link

Super Mario game used to spread malware

0
[ad_1]

A Trojanized installer for the popular Nintendo fan game Super Mario Forever has been used to spread malware.

This discovery was made cyber security company Cyble. Cyble’s researchers found that malicious actors were spreading a Monero (XMR) miner, a SupremeBot mining client and an open-source Umbral stealer all bundled with a legitimate installer for Super Mario Forever. 

Once successfully installed on a device and the game is launched, the malware then secretly executes malware files on the infected device. The XMR miner uses the infected device to mine for the cryptocurrency Monero. The miner operates discreetly in the background processes of the device, meaning the unauthorized mining is hidden from the victim.  
 
The XMR miner also harvests data from the victim’s computer, including the computer name, username, graphics processing unit and central processing unit and transfers it to a command and control center.

The SupremeBot mining client executes processes on the infected device to retrieve and execute malicious data-stealing software from a command and control center to the device. This then unloads the Umbral stealer onto the device’s process memory. The Umbral stealer then rapidly collects data off the device and sends it to the malicious actor who uploaded the Trojanized software via instant messaging platform Discord using webhooks.

Cyble noted that the Umbral stealer can execute the following processes:

  • Capturing screenshots  
  • Retrieving browser passwords and cookies  
  • Capturing webcam images  
  • Obtaining telegram session files and discord tokens  
  • Acquiring Roblox cookies and Minecraft session files  
  • Collecting files associated with cryptocurrency wallets.

Together, this malicious payload bundle can significantly impact victims, both monetarily via stolen cryptocurrency or fraudulent bank transfers and materially, through the impact crypto mining will have on their device. This is because crypto mining massively disrupts a system’s processes as well as depleting its resources.

Learn more about Trojanized malware with Cyber Security Hub’s ultimate guide to malware. 


[ad_2]
Source link

OnePlus 13 to get a camera boost, include three 50MP cameras

0
[ad_1]

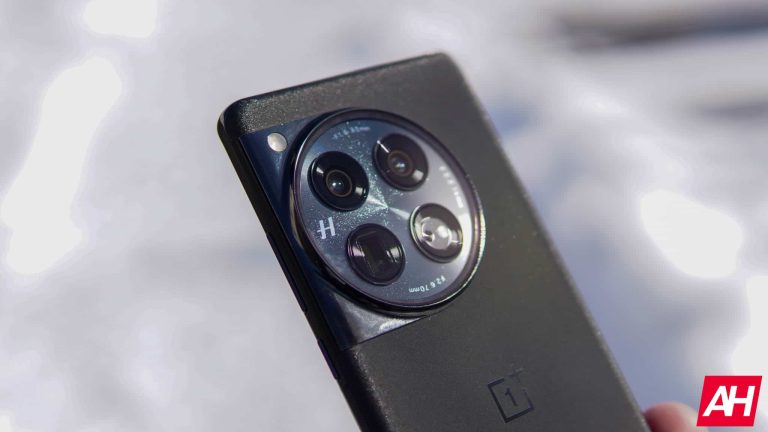
The OnePlus 13 will include three 50MP cameras based on a new rumor that surfaced online. This information comes from a well-known tipster, Digital Chat Station. He’s usually spot on, so we have no reason to doubt this info.

The OnePlus 13 will get a camera boost, and include three 50MP cameras on the back

The tipster said that the phone will feature an improved periscope telephoto camera. It will have a 50-megapixel unit, and 3x optical zoom. That camera will also come with Hasselblad boost.

As a reminder, the OnePlus 12 includes a 64-megapixel periscope telephoto camera with 3x optical zoom. That’s not the only camera that will see a change, however. The ultrawide unit will also be a 50-megapixel unit, instead of a 48-megapixel camera.

We’re still not sure what sensors will OnePlus use, as that’s a rather important detail. The main camera will stay a 50-megapixel unit, but OnePlus could end up using a different sensor. That detail is still under wraps.

OnePlus could end up using the Sony LYT-900 camera sensor

The OnePlus 12 uses Sony’s LYT-808 sensor for the main camera. That sensor is compelling, but it’s not as good as the Sony LYT-900 used by the OPPO Find X7 Ultra. Will the OnePlus 13 get a boost in that regard and use the LYT-900? It’s a possibility.

The device will be fueled by the Snapdragon 8 Gen 4. That’s a given. It will actually become one of the first smartphones to use that chip. The OnePlus 13 is expected to become official in November, at least in China.

The phone is also rumored to include a redesign, with a different camera island on the back. A 6,000mAh battery will allegedly also be included. The phone could lose wireless charging, though, unfortunately. It remains to be seen, but that’s what’s rumored at the moment.


[ad_2]
Source link

Acer SpatialLabs Eyes 3D Stereo Camera

0
[ad_1]

Acer’s new SpatialLabs Eyes camera brings 3D excitement to your photography

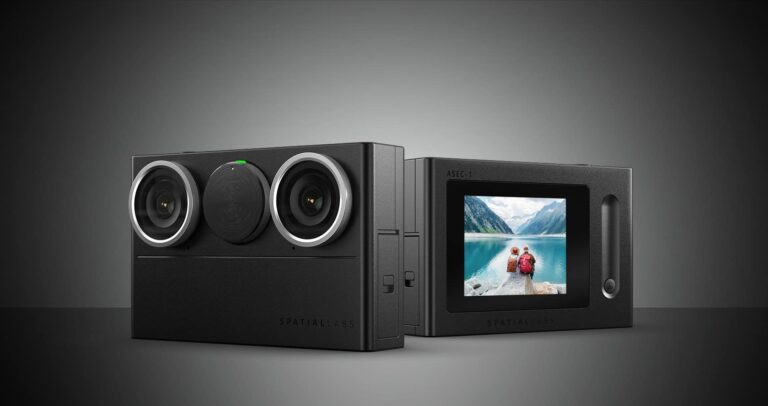
Acer brought some fun new products to Computex 2024 in Taiwan this week, one of which was its new SpatialLabs Eyes, a 3D stereo camera that’s designed for 3D photography, but is also perfect for content creation.

Whether you’re new to 3D photography or experienced with it, Acer says the SpatialLabs Eyes is an easy-to-use camera that will help bring your photos and videos to life. It features 8MP per eye and a built-in selfie mirror to help you get those perfect selfie shots. Acer plans to launch this camera in Q3 for $549. While we haven’t had the chance to use the camera, it caught our attention thanks to its compact nature and exciting 3D features, which is why it earned a Best of Computex 2024 award from Android Headlines.

Point-and-shoot photography becomes more fun with the SpatialLabs Eyes camera

Point-and-shoot photography has been around for ages with what feels like little movement forward when it comes to fun new features or experiences. Acer’s new SpatialLabs Eyes stereo camera changes all that. For starters, this is a compact camera. It’s small enough to fit in your pocket. Yet it’s not so small that you would find it annoying to use. On top of this, Acer designed it to be weatherproof. Which means you should be able to use it even in light rain.

Although you can use the camera out of the box without fiddling with settings, it does have a manual mode. Should you want more control over your image output, you can adjust quite a few things. ISO, white balance, and shutter speed settings are all available to tweak to your liking.

What’s more, is that you can use it for capturing 3D video in addition to photos. It’ll also have support for video conferencing apps like Zoom, Google Meet, and Microsoft Teams in Q3 alongside the camera. Acer says the camera’s “carefully calibrated lens alignment and advanced optical system allows for photographing subjects in greater 3D depth and detail.” You’ll need a SpatialLabs laptop or monitor to make the most of this camera. If you didn’t want one before, you’ll probably want one now.

Remember how we said this was easy to use? Well, it gets easier than just point-and-shoot. There’s a decent-sized touch screen on the back for menu and settings interaction. It supports microSD cards for storage and only weighs about 220g too. Acer has been pushing the envelope with cool new products and the SpatialLabs Eyes 3D stereo camera is the latest example of that. This is why we awarded it the Best of Computex 2024 award.


[ad_2]
Source link

Google Lens to simplify adding context to searches

0
[ad_1]
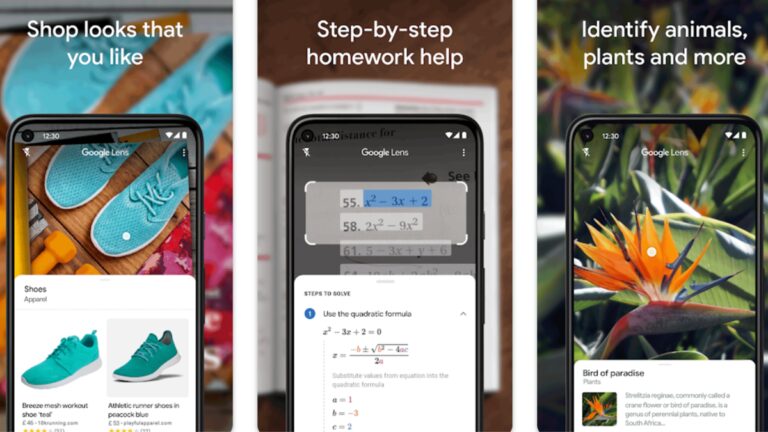
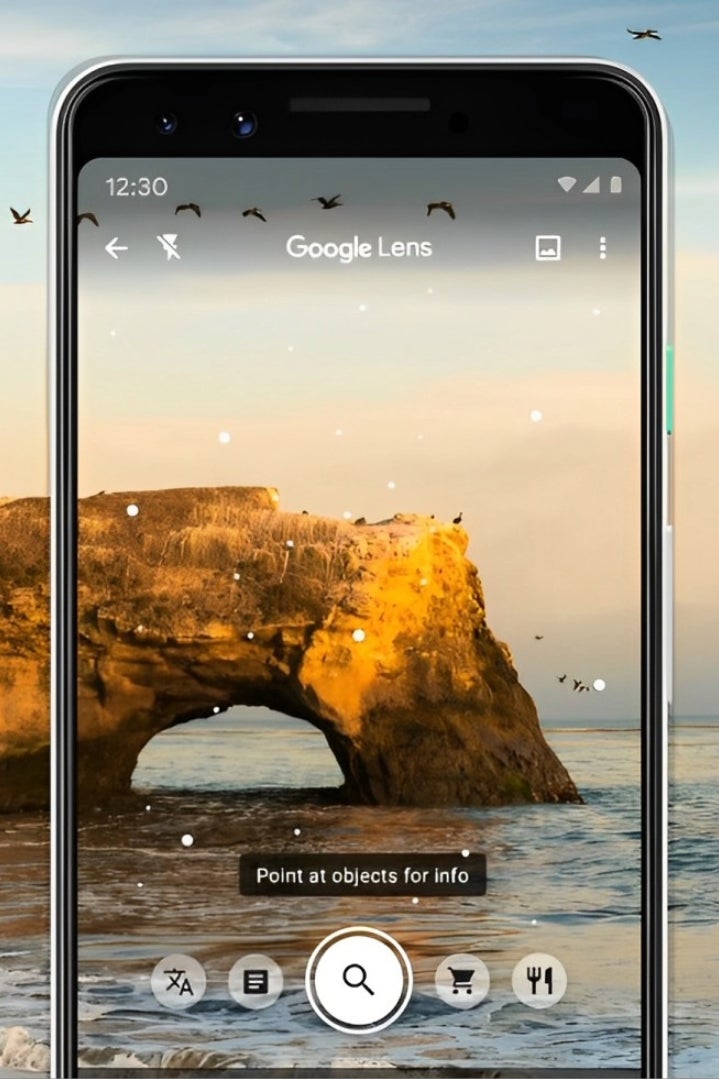
Google Lens is a cool tool that lets you use your phone’s camera to search the world around you. Just point your camera at something, and Google Lens will try to identify it using image recognition technology.

Once it recognizes the object, it gives you relevant info about it. But sometimes, an image search could use a little extra context. That’s why Google might improve Google Lens to accept more context.

Google Lens might soon make it easier to add context to your searches


A recent teardown of the Google app revealed some upcoming changes. It looks like Google is working on making it easier to start a search and add extra context. Now, you can press the shutter button to start a search, but soon, you will be able to tap and hold (i.e., long press) the shutter button to add context with your voice at the same time.Currently, when you use Google Lens for an image search, you press the shutter button to start the search. After the image search is done, you can add context by tapping on the voice search icon. This extra context can be in the form of voice or text.

So, with this upcoming update, adding context to your image search will be quicker and easier. Plus, it seems Google is also working on a feature that lets you search using video, not just still images.

If Google decides to roll out this handy feature, users will be able to record a video and add extra search context through voice at the same time.

However, none of these features are live in Google Lens yet, which you can access through Google Search. They might roll out in the future, but there’s no guarantee. Fingers crossed, though!

I mean, having more search options is always a plus, don’t you think? Especially when you’re in a rush or trying to find info about something you can’t quite put into words – and we all know those situations happen.

[ad_2]
Source link

WhatsApp Chats Vulnerable To Government Monitoring – Report

0
[ad_1]

WhatsApp engineers share their fears about the app being vulnerable to government monitoring via n internal report. While the WhatsApp structure doesn’t exhibit any vulnerability, the existing network monitoring techniques may help governments bypass the app’s encryption to monitor users’ app usage pattern.

Government May Bypass WhatsApp Encryption For Monitoring

According to an internal Meta report, WhatsApp engineers have noticed a severe security issue making WhatsApp users vulnerable to government monitoring. First disclosed by The Intercept, the report reveals WhatsApp employees’ fears for the privacy and security of their users.

As reported, the problem—or security lapse—isn’t because of any technical vulnerability. Meta spokesperson Christina LoNigro assured that no backdoors or vulnerabilities exist in WhatsApp’s workings. However, the problem exists because of the current network monitoring techniques governments employ, or may employ, to monitor their citizens’ digital activities.

Using network monitoring and traffic analysis, authorities can identify WhatsApp users—senders and receivers alike—and their locations (via the IP addresses), deducing whether a respective user is part of a WhatsApp group. While the exact chat contents remain veiled due to the underlying WhatsApp encryption, the metadata gathered via traffic analysis suffices for the authorities to profile target users.

Regarding the practical exploitation of this scenario, Meta officials mention Israel as a state targeting Palestinian WhatsApp users.

This security issue doesn’t typically risk WhatsApp only. Almost every service encrypting users’ communications can be surveilled in this manner. However, given WhatsApp’s huge user base (roughly 2 billion) and the typical pattern of WhatsApp traffic flowing through Meta servers, the risk is far greater for WhatsApp users.

Though the engineers have internally reported the matter to Meta management, there seem no specific plans from the management to address this issue anytime soon.

Is There A Fix?

While the report sounds terrifying, average WhatsApp users need not worry much about such monitoring since not all governments apply such intensive network monitoring. (Though, they may do it at any time as needed.)

Nonetheless, considering that the threat persists—particularly for citizens in authoritarian regimes—using means such as VPN may significantly help them avoid WhatsApp surveillance. While the VPN’s encryption would still be detectable, it will at least save users from the specific exposure of WhatsApp usage, encrypting all internet activities alike.

Besides, users must remain wary of WhatsApp spam messages, unsolicited calls, and group invites. Even with trusted contacts, users must avoid sharing sensitive details or information they don’t want snoopers to know. Instead, users may switch to other securer means of communication for sharing sensitive stuff.

Let us know your thoughts in the comments.


[ad_2]
Source link

Xiaomi MIX Flip to launch globally; Xiaomi MIX Fold 4 coming early

0
[ad_1]

This time around we have some exciting news regarding Xiaomi’s upcoming fodlable smartphones. The Xiaomi MIX Flip is expected to launch globally, while the Xiaomi MIX Fold 4 could arrive sooner than expected.

The Xiaomi MIX Fold is expected to launch globally

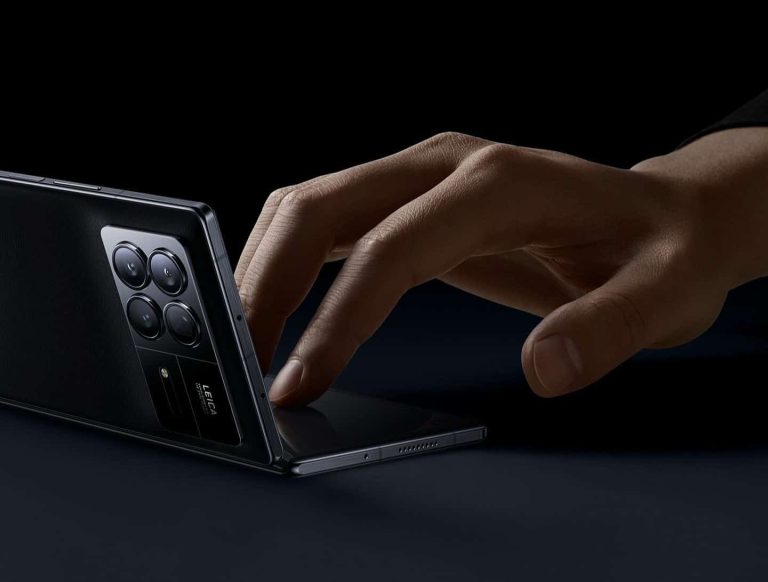
Let’s start with the Xiaomi MIX Flip, the company’s very first clamshell foldable. Why do we believe it will reach markets outside of China? Well, because it appeared in the GSMA’s IMEI database with the model number 2405CPX3DG. That’s important because the ‘G’ at the end stands for ‘global’. Models with that letter usually launch in markets outside of China.

The same phone also got certified in China but with a different model number. That model has the 2405CPX3DC model number. As you can see, it has the letter ‘C’ at the end, which stands for ‘China’.

As a reminder, that phone is expected to be fueled by the Snapdragon 8 Gen 3 processor. It will have a 50-megapixel main camera, a 12-megapixel ultrawide unit, and a 60-megapixel telephoto snapper… if the rumors are accurate. It’s expected to arrive at some point between July and September.

The Xiaomi MIX Fold 4 could arrive sooner than you think

What about the Xiaomi MIX Fold 4? Well, that phone could arrive sooner than expected. The Xiaomi MIX Fold 3 arrived in August last year, and this model could launch in July.

That info comes from ‘Smart Pikachu’, a Chinese tipster. In fact, the two foldables could launch during the same event, that would make sense for Xiaomi, that’s for sure. Both will likely launch in China first.

Do note that the Xiaomi MIX Fold series does not have a global variant yet. So, if the Xiaomi MIX Flip will launch globally, who knows, perhaps Xiaomi has huge plans for the Xiaomi MIX Fold 4 as well. Let’s hope that will be the case. That phone will be fueled by the Snapdragon 8 Gen 3 too, and it will have high-end specs in general.


[ad_2]
Source link

TECNO MEGABOOK T16 PRO and PRO Ultra

0
[ad_1]

Tecno has produced some stellar phones, but it also has a computer to match

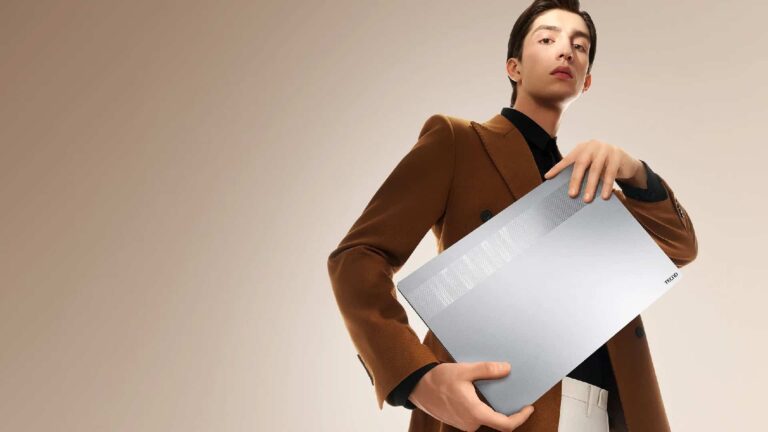
Tecno is the tech brand that wants to take on the world, as it’s been making some serious steps in that direction. Those who know the company know it as the brand that’s made some impressive phones. However, it showed off the MEGABOOK T16 Pro 2024 Ultra at Computex 2024, and it’s got some serious power.

Tecno makes computers as well as phones, and it also showed off its MEGABOOK K16S at the event. This is a 16-inch laptop with a lot of great features. The MEGABOOK T16 Pro 2024 Ultra, on the other hand, is a more advanced model, and it’s for people who want the most power from their computer.

This is a computer that’s designed for power users who need to get some serious work done. The computer has a sturdy metal body that lends to the overall great feeling in the hand. It will also keep it protected in the event of a fall.

As for the screen, you’re looking at a 16-inch screen with a 2.5K resolution. With that resolution, you can expect some pretty good visuals. It covers 100% of the sRGB color gamut and it has a peak brightness of 400 nits. Along with that, the screen also reduces glare.

This computer uses the Intel Core Ultra processor. It’s backed up by 16GB/32GB of RAM and 512GB/1TB of storage. As for the battery, this computer has a 99.99Wh battery, and it supports 100W charging.

Tecno touted this computer’s AI capabilities. It will have Copilot integrated, you should expect some great on-device AI processing from this computer. This is the device to get if you’re looking for a computer to handle your work life. This is why it received our award for Best of Computex 2024.


[ad_2]
Source link

Sonos app gets another big update that brings back some basic features

0
[ad_1]

After Sonos’ redesign app fiasco, the audio company vouched to listen to the feedback and bring back all the features that were removed when the refreshed version of the app was rolled out not long ago.

This will take time because in an attempt to make its app as streamlined as possible, Sonos removed a lot of the features that users were using very often. Basic features like “Play Next,” “Play Last,” “Shuffle All,” and the ability to search for songs in local/offline music library were no longer available when the new app was released.

Despite its attempts to defend the app’s new design, Sonos admitted that it now has a major issue as many users threaten to stop using and/or buying the company’s products.

New features added


The first update meant to fix some of the app’s problems was released last month, and Sonos promised to roll out a new one in June. Well, it looks like Sonos has kept its promise and a new update is now available for download. Here is what’s included and what Sonos plans to add to the app in the coming weeks:
  • Added support for the all new Sonos Ace headphones
  • Added sleep timer settings
  • Added “play next” and “add to end of queue”
  • Improved Home Feed scrolling
  • Improved setup reliability
  • Added WiFi configuration for products with BLE
  • Improved battery consumption for Bluetooth discovery
  • Improved ability to update older firmware systems
  • Further improved navigation for visually-impaired customers
  • Added VoiceOver support to read toast message automatically on iOS
  • Introduced mute button on iOS
  • Improved local library connectivity
  • Improved Trueplay setup on iOS
  • Added distance settings for surrounds
  • Added line-out settings for Sonos Port

New features incoming

Besides the pretty beefy changelog, Sonos also revealed some of the features that fans should expect to see in a future update. Keep in mind that most of these upcoming features have ETAs, but not all of them.
  • Continued improvements to navigation for visually impaired customers: mid-June
  • Playback controls including mute and volume numbers: June
  • Local music library search and playback: mid-June
  • Improved playback settings including Play Now: July
  • Create and edit local music library: July
  • Improved Autoplay settings: July
  • Improved Sub audio settings with Amp: July
  • Snooze alarms: TBD

Based on the roadmap above, the next update for the Sonos app should arrive in mid-June, but there’s also another one scheduled for July. If you’re using Sonos’ app to control your audio products, there are a lot of good things coming your way, so stay tuned.

[ad_2]
Source link