Tenable Acquires Eureka Security To Provide Data Security

0
[ad_1]

Tenable® Holdings, Inc., a leading Exposure Management company, has announced a definitive agreement to acquire Eureka Security, Inc., a prominent provider of data security posture management (DSPM) for cloud environments.

This strategic acquisition aims to bolster Tenable’s cloud security capabilities, providing comprehensive data security across cloud infrastructures.

Tenable’s acquisition of Eureka Security is set to close this month, marking a significant step in enhancing its cloud-native application protection platform (CNAPP).

Eureka Security’s DSPM technology offers security teams a holistic view of an organization’s cloud data security footprint, addressing policy drift and misconfigurations that pose risks to data.

By integrating these capabilities, Tenable aims to help customers identify critical evidence of cloud data risks, including the location of sensitive data, access permissions, and the severity of potential data compromises.

In the 2024 Tenable Cloud Security Outlook study, 95% of organizations reported experiencing cloud-related breaches in the past 18 months, with 92% of those breaches involving the exposure of sensitive data.

Analyze any MaliciousURL, Files & Emails & Configuration With ANY RUN : Start your Analysis

This acquisition underscores Tenable’s commitment to providing robust cloud security solutions that can mitigate such risks and improve overall security posture over time.

Enhancing Visibility and Control

Shai Morag, Senior Vice President and General Manager of Cloud Security at Tenable, emphasized the importance of this acquisition in advancing cloud security innovation.

“Eureka Security’s technology will enable Tenable to provide even better prioritization of cloud risks and identify toxic combinations beyond vulnerabilities, misconfigurations, and over-privileged access to include data at risk as well,” Morag stated.

This integration will offer security teams the context and prioritization guidance to make efficient and accurate remediation decisions.

Liat Hayun, Co-founder and CEO of Eureka Security, expressed enthusiasm about joining forces with Tenable.

“Eureka Security’s data-centric approach provides the visibility, control, and automation needed to navigate the dynamic cloud landscape while ensuring the highest level of security and compliance,” Hayun said.

“Integrating our capabilities into Tenable’s CNAPP offering creates a compelling capability for customers.

Tenable also brings an expansive customer base and solid go-to-market capabilities.

We couldn’t have found a better match to help us expand our global mission to reduce cloud data risk.”

Comprehensive Cloud Security Solution

Integrating Eureka Security’s DSPM capabilities will complement Tenable’s existing cloud security solutions, including unified CNAPP, cloud security posture management (CSPM), cloud workload protection, and cloud infrastructure entitlement management (CIEM).

This comprehensive suite of tools will provide security teams with the necessary context and prioritization to address cloud security challenges effectively.

Tenable’s acquisition of Eureka Security is not expected to have a material impact on revenue this year.

However, the long-term benefits of enhanced cloud security capabilities are anticipated to strengthen Tenable’s market position and provide significant value to its customers.

About Tenable

Tenable® is a leading Exposure Management company trusted by approximately 44,000 organizations worldwide to understand and reduce cyber risk.

As the creator of Nessus®, Tenable has extended its expertise in vulnerabilities to deliver the world’s first platform capable of securing any digital asset on any computing platform.

Tenable’s customers include approximately 65% of the Fortune 500, 50% of the Global 2000, and numerous large government agencies.

This press release contains forward-looking statements about Tenable’s acquisition of Eureka Security, Inc.

These statements involve substantial risks, uncertainties, and assumptions that could cause results to differ materially from those expressed or implied.

Forward-looking statements are based on Tenable’s current plans, objectives, estimates, expectations, and intentions and inherently involve significant risks and uncertainties, many of which are beyond Tenable’s control.

This acquisition represents a pivotal moment for Tenable as it continues to push the envelope in cloud security innovation, providing customers with best-in-class capabilities to effectively manage and mitigate cloud data risks.

Looking for Full Data Breach Protection? Try Cynet's All-in-One Cybersecurity Platform for MSPs: Try Free Demo 


[ad_2]
Source link
Google’s June 2024 update patches 37 vulnerabilities, Samsung adds 22 more

0
[ad_1]

Google has published the monthly Android Security Bulletin (ASB) for June 2024. This month’s security release for Android devices fixes 37 vulnerabilities, including three critical issues. Android OEMs will roll out these patches to their devices in the coming weeks. Some firms may bundle additional patches for issues exclusive to their products. Samsung, for example, is addressing 22 Galaxy-specific vulnerabilities with the June update.

June security update patches 37 vulnerabilities in Android devices

As usual, Google released the June 2024 ASB in two parts. The first part arrives with the 2024-06-01 security patch level and contains fixes for 19 high-severity vulnerabilities. The most severe vulnerability in this group could lead to “local escalation of privilege with no additional execution privileges needed.” Most of those exist on Android 12 through to Android 14, though a few don’t affect devices running the latest Android version.

In the second group, Google bundled 18 high-severity vulnerability patches marked under the security patch level 2024-06-05. These include issues across various partner components, including those from MediaTek, Imagination Technologies, ARM, and Qualcomm. This group also includes a kernel vulnerability that could “lead to local escalation of privilege in the kernel with no additional execution privileges needed.”

All of these patches will roll out to Pixel smartphones and tablets in the coming weeks. Google has yet to begin the rollout, though the wait may not be much longer now. Other Android manufacturers like Samsung, OnePlus, Oppo, Vivo, Xiaomi, and Tecno will also push these patches to their devices as the June security update. There is no evidence of any of these vulnerabilities being exploited in the wild. You should still update your device as soon as you can.

Galaxy devices get 22 additional security patches

Along with the 37 patches part of Google’s latest ASB, Samsung’s June update for Galaxy devices addresses another 22 vulnerabilities that don’t exist on Android devices from other brands. Called Samsung Vulnerabilities and Exposures (SVE) items, these issues affect various system apps, services, and components that make up the core of Galaxy products or Samsung’s custom Android skin, i.e., One UI.

This month’s release fixes a critical vulnerability in “chnactiv TA” that allowed local privileged attackers to lead to potential arbitrary code execution. The Korean firm also patched several high-severity issues, including a buffer overflow vulnerability in the bootloader that enabled physical attackers to overwrite memory. These patches will soon roll out to eligible Galaxy devices, including the Galaxy S24 series. We will let you know when the rollout begins.


[ad_2]
Source link

MSI Prestige 16 AI+ laptop

0
[ad_1]

The MSI Prestige 16 AI+ laptop effortlessly blends portability with AI functionality

MSI is one of the PC industry’s leading brands and for many good reasons. For one, it’s constantly pushing the envelope of innovation by releasing some exciting computing products. One of its latest offerings that we also found quite exciting is the Prestige 16 AI+, a slim AI laptop that blends seamless premium design with powerful AI functionality. Original models were announced back in December of 2023 and were already impressive.

However, the latest Prestige 16 AI+ is packed with even more powerful specs to keep you going, regardless of what your activities are,  and MSI promises noticeable boosts in AI performance. Specifically, up to three times more AI performance compared to previous models and up to 100 TOPS of AI Performance so more AI software or services can be driven locally.

Whether you’re using it for work, content creation, or anything else, the Prestige 16 AI+ is capable of handling your tasks with ease thanks to Intel’s powerful Lunar Lake Core Ultra processors. The laptop also sports a 99.9Wh battery for longevity. The last thing you want to worry about with a laptop for daily on-the-go use is how long you have before the battery dies and you need to plug it in.

The MSI Prestige 16 AI+ takes away that worry while maintaining a slim and light build that won’t you weigh you down. This allows you to keep doing what you’re doing efficiently thanks to the over 19 hours of battery life. These are some of the main reasons why the MSI Prestige 16 AI+ was awarded the Best of Computex 2024 award by Android Headlines.

MSI’s Prestige 16 AI+ weighs just 3.3 lbs. and is 0.75 inches ultra-thin

A laptop with over 19 hours of battery life is enticing, especially if you don’t have time to stop and plug things in very often. If that’s the case though, you also want something extremely portable. This laptop is exactly that. At just 3.3 lbs. and 0.75 inches thin, it’s extremely lightweight and ultra-thin with a Magnesium-Aluminum Alloy Chassis. This means you can slide it into a backpack or carry it around in your hands with ease. And because of the battery life, you can leave the charger at home.

Of course, the AI capabilities make this a slam dunk of a laptop for anyone who values powerful functionality. Intel’s Lunar Lake Core Ultra 7 and Core Ultra 9 processors deliver some real AI magic to the user experience. And MSI tops that off with its MSI AI Engine software. This software lets the laptop detect what you’re doing so it can adjust hardware settings to meet the demands of the activity, resulting in optimal performance. The MSI Prestige 16 AI+ also features a UHD+ display with a resolution of 3,840 x 2,400. So all of your content looks great.

On top of all that, you still get a laptop with plenty of ports. This is why we have awarded the MSI Prestive 16 AI+ the Best of Computex 2024 award.


[ad_2]
Source link

Twitch increases subscription prices in over 30 countries, including the US

0
[ad_1]

Not a month goes by without another price hike. Although most of the price changes aren’t that high, they pile up pretty fast and seeing how often it happens, we’ll soon have to decide which services to keep and which to drop.

Twitch is the latest company to announce price increases. Although the reasoning behind its decision seems noble, the fact still remains that you’ll have to pay more to support your favorite streamer.

That said, Twitch revealed that starting July 11, it will update Tier 1 subscription and gift sub prices on the web for current subscribers. More importantly, current subscribers will receive legacy pricing for their existing subscriptions until they choose to upgrade or cancel.

However, the “legacy pricing” is not available in all countries where Twitch made the Tier 1 subscription more expensive. It’s unclear where exactly this are available at the moment, but legacy pricing might be limited to several EU countries like Germany, Belgium, and Netherlands.

If you live in the EU and your subscription was previous €3.99 per month, you’ll most likely have to pay €4.99 per month starting July 11. However, Twitch users in the US have been hit with a similar price hike, as they will have to pay $5.99 per month, up from $4.99 per month.

On the bright side, Twitch says that it’s not changing the price of Tier 2 and Tier 3 subscription or gifted subscriptions. It’s also worth mentioning that the price changes apply to subscriptions purchased on desktop or mobile web, not on mobile apps (which will be updated in the coming months).


[ad_2]
Source link

Severe Vulnerability Fixed In Cisco Firepower Management Center

0
[ad_1]

Cisco recently addressed a high-severity vulnerability in its Firepower Management Center software with the latest update. The firm urged users to upgrade to the latest software releases to receive the patch, as no workarounds exist to mitigate the flaw.

Cisco Patched The Firepower Management Center Vulnerability

The networking giant Cisco recently fixed a high-severity SQL injection vulnerability in its Cisco Firepower Management Center software. Exploiting the flaw could let an authenticated remote adversary target vulnerable systems.

Firepower Management Center (FMC) is a dedicated administrative center from Cisco, providing users with a unified platform to manage different Cisco security products. This includes seamless management of firewalls, URL filtering, application control, intrusion prevention, and malware protection.

According to its advisory, the vulnerability affected the web-based management interface of the FMC software. The flaw existed due to an improper input validation in the web-based management interface. Consequently, an authenticated attacker could exploit the flaw by sending maliciously crafted SQL queries to the target system.

Exploiting the flaw required the attacker to have Read-Only credentials at the least. Once exploited, the flaw could let the attacker access data in the database, gain root privileges, and execute arbitrary codes on the target system.

This vulnerability received the CVE ID CVE-2024-20360, achieving a high-severity rating and a CVSS score of 8.8. It typically affected Cisco FMC software, and the tech giant confirmed Cisco Adaptive Security Appliance (ASA) Software or Cisco Firepower Threat Defense (FTD) Software to remain safe from this flaw.

The firm credited the security researcher with the alias SunD0y with reporting the flaw. Cisco also confirmed detecting no active exploitation attempts for this flaw in the wild.

To help users update their systems with the patched FMC releases, Cisco also released a Software Checker tool. Using this tool, users may search for the latest Cisco advisories addressing any security flaws with the latest releases.

Let us know your thoughts in the comments.


[ad_2]
Source link

ASUS Prime GeForce RTX 40 Compact GPUs

0
[ad_1]

ASUS debuts new compact NVIDIA GPUs at Computex 2024

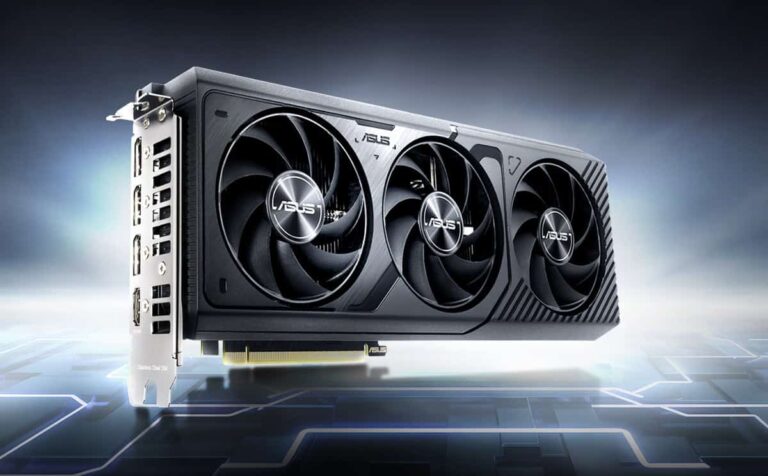
At Computex this week, ASUS had a slew of announcements to unveil, including new Prime GeForce RTX 40 compact GPUs, this is part of NVIDIA’s SFF-ready program – which stands for Small Form Factor. As GPUs continue to get larger and larger, it’s getting tougher and tougher to fit them into many cases. However, these new Prime GeForce RTX 40 models are much smaller and should fit in most cases.

ASUS is one of the first partners for NVIDIA with its SFF-ready program, and is offering the Prime GeForce RTX 4070 SUPER, Prime GeForce RTX 4070, and Prime GeForce RTX 4060 Ti. This is why ASUS has earned a Best of Computex 2024 award from Android Headlines.

ASUS focuses on function over design

With the new Prime GeForce RTX 40 GPUs, ASUS has decided to focus on function over design with these models. So they are available in a minimal design with a black-and-white color scheme, along with subtle RGB lighting effects. For those who are looking for a flashy GPU, this isn’t going to be what you’re looking for.

This fits right in with the ASUS Prime Ecosystem of PC DIY Components, allowing you to build or upgrade your rig with ease, which is important in the PC Master Race.

ASUS hasn’t yet confirmed pricing or availability for the Prime GeForce RTX 40 Compact GPUs, but that is pretty common for products announced at trade shows like Computex. ASUS did say, however, that they would “hit the shelves very soon”, typically that means within a month or two. So we can see these new compact GPUs available later this summer.

Taking NVIDIA’s best GPUs (so far) and shrinking them down into smaller GPUs that will fit in most cases is why we have awarded ASUS a Best of Computex 2024 award for the new Prime GeForce RTX 40 Compact GPUs.


[ad_2]
Source link

Acer Predator X34 X5 gaming monitor

0
[ad_1]

The Acer Predator X34 X5 monitor levels up your gaming

Gaming is about many things these days and one of those things can be having your games look as good as possible. Enter the Predator X34 X5 gaming monitor from Acer. The company’s latest iteration of the Predator X34 series. It features a stunning 34-inch OLED panel with an ultrawide design and a UWQHD resolution of 3,440 x 1,440. Suffice it to say, it’s a beautiful monitor to look at, even when there’s nothing on the screen.

Of course, it certainly looks better when you’re playing games on it than just sitting there. But its aesthetics do deserve to be appreciated. And it most certainly has some beautiful aesthetics. Not just because of the 1800R curved panel, but also the sleek metal stand that the monitor sits on. Which by the way, allows the monitor to tilt and swivel. You can adjust the height too. I had the opportunity to try one of the older Predator X34 monitors out and it was one of the best gaming monitors I’ve ever played games on. Acer has only made the monitor better with all the upgrades.

The new Predator X34 X5 monitor also comes with multiple HDMI 2.1 ports as well as DisplayPort 1.4 and USB Type-C connectivity. This is why the Acer Predator X34 X5 earned the Best of Computex 2024 award from Android Headlines.

The Acer Predator X34 X5’s 240Hz refresh helps games look ultra-smooth

A monitor with a fast refresh rate can really boost the gaming experience. While not absolutely necessary, a monitor with a fast refresh rate certainly makes gameplay smoother and it can give you an advantage in multiplayer games. The Acer Predator X34 X5 delivers here with a 240Hz panel with a lightning-fast 0.03ms response time. Additionally, it features two 5-watt speakers built-in. Whether you’re using this monitor for a console or PC, the built-in speakers mean you don’t need to have external audio sources to hear your games or other content.

The monitor also has a built-in KVM switch. Meaning if you have two PCs hooked up to it, you can use one keyboard and mouse to swap between the two pretty effortlessly. Additionally, the Acer Predator X34 X5 supports both AMD FreeSync Premium Pro and NVIDIA G-Sync. This is easily one of Acer’s best gaming monitors to date, and it’s why we awarded the Predator X34 X5 the Best of Computex 2024 award.


[ad_2]
Source link

Google Maps users will have to decide when they want Google to auto-delete Timeline data

0
[ad_1]
Google is making a change to how it keeps your Google Maps location data. Once backed up using cloud-based servers, this information will end up being stored on-device instead. An email sent by Google to Maps users says that they have until December 1st to save all of their old journeys on their devices before this data is deleted. Keep in mind that Google is changing the name of the feature you might know as Location History to Timeline.
Timeline (formerly Location History) is a personal map that allows you to remember routes and trips you’ve taken and places that you’ve visited in the past so that you can visit them again. Per The Verge, instead of having all of this data connected to your Google account, it will be stored on your iOS or Android phone. This means that you will no longer be able to view your Timeline from the web starting in December. Moving this data on-device is supposed to improve the privacy of the information since it won’t be stores in the cloud.

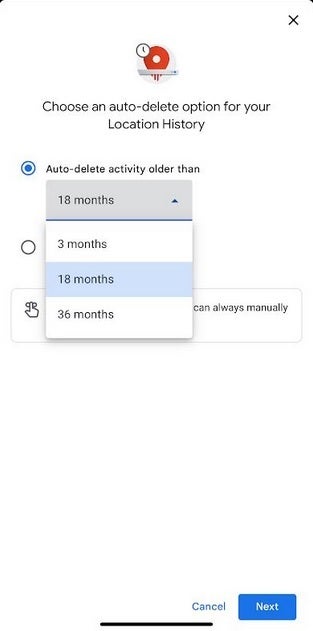
But as we noted, if you use Google Maps, you will have a decision to make. You have until December 1st to decide how long you want to keep your Timeline data on your phone. You can choose to keep all data on-device until you delete it yourself, or select to have the data automatically deleted after 3 months, 18 months, or 36 months. If you fail to make a decision by December, Google will move the first 90 days of your travel history to the first device you sign into Google with. Any data older than 90 days will be deleted.

You can decide when you want Timeline data removed from your device automatically by opening the Google Maps app and tapping on the profile icon on the right side of the search bar on the top of the screen. Next, tap on Your timeline followed by the three-dot menu icon on the upper right of the display. From the pop-up menu that appears at the bottom of the screen, choose About timeline. Under the section marked Your choices, tap the link that says Go to settings.

You’ll be sent to a page titled Activity controls. Look for the Auto-delete line that says underneath Choose an auto-delete option. There is a small arrow on the right side. Tap it and you’ll have two choices. One says Don’t auto-delete activity. Tap on that if you don’t want Google to automatically delete your Timeline data from your phone. Or, you can select the other option which says Auto-delete activity and choose to have Timeline data older than 3 months, 18 months, or 36 months deleted automatically. Tap the one you want and Google will automatically remove your Timeline data older than the choice you made.

No matter what you select, Google allows you to delete any Timeline data from your phone manually.


[ad_2]
Source link

Iranian State Hackers Partner Up for Large-Scale Attacks, Report

0
[ad_1]

A Check Point Research (CPR) report reveals that state-sponsored hackers and threat actors are employing sophisticated tactics to target organizations and nations, posing a significant threat that demands immediate solutions.

The company focused on Void Manticore, an evolving threat to those opposing Iranian interests. It revealed the complicated tactics they employ to destroy their target, including a complex web of online personas, strategic collaborations, and sophisticated attack methodologies.

State-Sponsored Actors- An Evolving Threat

Void Manticore is linked to Iran’s Ministry of Intelligence and Security (MOIS) and is known for its destructive wiping attacks and sophisticated influence operations. The actor operates under various online personas, such as “Karma” in Israel and “Homeland Justice” in Albania. 

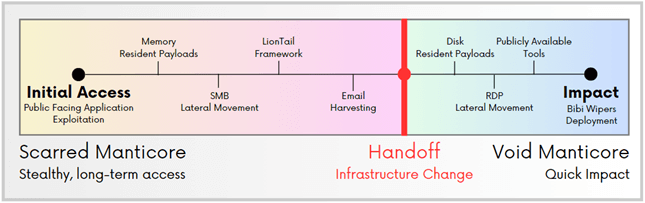
Their operations are notably influenced by their collaboration with Scarred Manticore, another Iranian MOIS-affiliated group. Both engage in a systematic handoff of targets, with Scarred Manticore accessing and exfiltrating data from targeted networks and then transitioning control to Void Manticore. 

“This strategic partnership not only amplifies the scale and impact of their attacks but also poses a formidable challenge for cybersecurity defenders,” Check Point Team noted in the blog post.

Void Manticore Modus Operandi

Void Manticore’s tactics are straightforward yet effective. Utilizing basic tools, they establish access to target networks and then deploy a range of custom wipers designed for Windows and Linux systems. Some wipers target specific files or file types while others attack the system’s partition table, rendering all data on the disk inaccessible.

Moreover, they engage in manual data destruction activities, including shared drive manipulation, to further amplify the impact of their attacks. They mostly use the CI Wiper, Partition Wipers like the LowEraser, and the BiBi Wiper.

Their most recent attacks involved the BiBi Wiper (named after Israeli Prime Minister Benjamin Netanyahu), which can corrupt files and disrupt system functionality. The group has also targeted INSTAT in Albania and multiple Israeli entities.

Iranian State Hackers Partner Up for Large-Scale Attacks, Report
The Void Manticore and Scarred Manticore connection (Screenshot: CPR)

How to Stay Safe?

Void Manticore aims to not just steal but destroy your data and cause chaos. This digital hit-and-run serves as a reminder of the constantly evolving nature of online threats. To protect yourself, stay vigilant by updating software with the latest security patches, be wary of online strangers, and use strong passwords.

  1. Hackers Target Israeli Rocket Alert App Users with Spyware
  2. Iran’s Scarred Manticore Targets Middle East with LIONTAIL Malware
  3. Deadglyph Backdoor Linked to Stealth Falcon APT in the Middle East
  4. Hackers Send Fake Rocket Alerts to Israelis via Hacked Red Alert App
  5. Hacktivists Trageting Critical ICS Infrastructure in Israel and Palestine

[ad_2]
Source link

Best of Computex 2024: ASUS ROG Ally X

0
[ad_1]

ASUS unlocks your gaming capabilities with the ROG Ally X

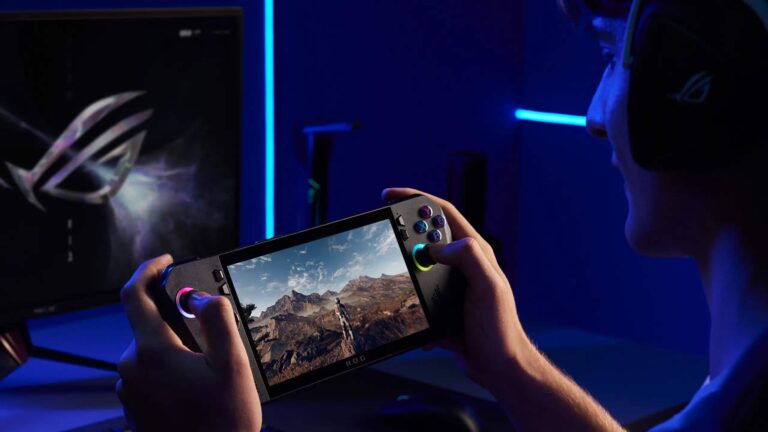
When ASUS launched the ROG Ally in 2023, it was positioning the handheld as your one-stop shop for playing all of your games, and not just those in your Steam library. While the Ally was and is still a very cool PC gaming handheld, the ROG Ally X brings in several improvements that make this the go-to choice between it and the older models. The ROG Ally X still uses the same AMD Ryzen Z1 Extreme APU, but it beefs up the RAM and battery and updates the SSD support for a much better gaming experience.

Let’s start with the battery life. The ROG Ally X features an 80Wh battery so you can keep playing games for longer without having to plug the handheld in. While we haven’t tested it, you can probably expect at least an additional hour of gameplay if not more. That’s pretty exciting if you have long commutes and like to play games during that time. But ASUS didn’t stop there. The ROG Ally X also has an updated design. Things aren’t massively changed here. But they have been improved in small, meaningful ways.

Like the bottom corners of the unit that rest against your palms. On the original ROG Ally, these were sharp angular lines and corners. The ROG Ally X makes things a little more ergonomic by giving these corners a more pronounced curve. This is likely to make it more comfortable to hold for longer. Speaking of ergonomics, the ROG Ally X also has more defined curves and depth for the hand grips on the back. Giving your fingers ever so slightly more room to rest back there. Because of these improvements, we’ve awarded the ASUS ROG Ally X the Best of Computex 2024 award.

The ROG Ally X has loads of meaningful improvements

A bigger battery is one of many improvements ASUS made to its handheld. It also now has 24GB of RAM compared to 16GB. This will help you allocate the APU’s resources more evenly across both the system and gaming activities, so games and tasks can run more optimally. One of the slickest upgrades though is the jump to Full M.2 2280 SSD support. The old ROG Ally uses a smaller SSD form factor. However, the new ROG Ally X is compatible with full M.2 2280 SSDs. So you can more easily upgrade the handheld’s storage if you want.

Plus, the system now comes with 1TB of internal storage as standard compared to 512GB. ASUS also made the cooling fans thinner and more efficient and even made the joysticks a little closer to the d-pad and face buttons so they’re easier to move your thumbs between. All in all, it should be a noticeably more enjoyable gaming experience than before. This is why we gave the ASUS ROG Ally X the Best of Computex 2024 award.


[ad_2]
Source link