Connect:fun Attacking Organizations Running FortiClient EMS

0
[ad_1]

A new exploit campaign has emerged, targeting organizations that utilize Fortinet’s FortiClient EMS.

Dubbed “Connect:fun” by Forescout Research – Vedere Labs, this campaign leverages a critical vulnerability identified as CVE-2023-48788.

The campaign has been active since at least 2022 and has recently been observed exploiting the security management solution with increased vigor.

The Vulnerability: CVE-2023-48788

CVE-2023-48788 is an SQL injection vulnerability found within Fortinet’s FortiClient EMS. SQL injection is a type of attack that allows an adversary to interfere with an application’s database queries.

It can be used to view data that the attacker cannot normally retrieve, such as user information, or to manipulate database information.

Fortinet published an advisory about this vulnerability on March 12, 2024, and the proof of concept (PoC) for the exploit was made publicly available on March 21, 2024.

This disclosure seemingly acted as a catalyst for increased exploitation attempts by threat actors.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

The Connect:fun campaign is particularly notable for its use of ScreenConnect and Powerfun as post-exploitation tools, marking it as Vedere Labs’ first-ever named campaign.

The incident that brought this campaign to light involved a media company whose FortiClient EMS was vulnerable and exposed to the internet.

The attack was not an isolated event. Scanning activity from the IP address 185[.]56[.]83[.]82 was observed targeting FortiClient EMS across various customer networks.

This activity began on March 21 and persisted through several days, indicating a concerted effort by the attackers to exploit the vulnerability across multiple potential victims.

The exploitation of CVE-2023-48788 poses a significant threat to organizations, as it can lead to unauthorized access and control over the FortiClient EMS.

This control can result in further malicious activities, including data theft, lateral movement within the network, and potentially a full-scale breach of the organization’s cyber defenses.

Mitigation and Defense Strategies

In response to the Connect:fun campaign, organizations are urged to take immediate action to protect their networks:

  • Apply the Patch: Fortinet has released a patch to address CVE-2023-48788. Organizations should apply this patch without delay to close the vulnerability.
  • Monitor Traffic: It is crucial to monitor the traffic reaching FortiClient EMS for signs of exploitation. An intrusion detection system (IDS) can be instrumental in identifying and responding to malicious activities.
  • Web Application Firewall (WAF): Deploying a WAF can help block potentially malicious requests and provide an additional layer of security.
  • Leverage IoCs and TTPs: Indicators of Compromise (IoCs) and Tactics, Techniques, and Procedures (TTPs) shared by cybersecurity researchers can be used to detect and prevent attacks.

Organizations using Fortinet’s FortiClient EMS must take proactive measures to secure their systems against this and other similar threats.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link
New Vulnerability “LeakyCLI” Leaks AWS and Google Cloud Credentials

0
[ad_1]

Cloud infrastructure is the backbone of modern technology, and its security hinges on the tools developers use to manage it. However, a recently discovered vulnerability dubbed “LeakyCLI” exposes a critical weakness in these tools, potentially granting unauthorized access to sensitive cloud credentials.

This vulnerability affects the command-line interfaces (CLIs) used by major cloud providers like Amazon Web Services (AWS) and Google Cloud Platform (GCP). Security researchers at Orca Security identified LeakyCLI, which can inadvertently expose environment variables containing sensitive information like passwords and access keys within logs.

The Flaw and the Risk

CLIs are typically designed for use in secure environments. However, the integration with Continuous Integration and Continuous Deployment (CI/CD) pipelines, which automate development processes, introduces a security risk. LeakyCLI bypasses secret labelling mechanisms within CI/CD pipelines, potentially printing sensitive credentials to logs that shouldn’t contain them.

“CLI commands are by default assumed to be running in a secure environment,” explains an Orca advisory. “But coupled with CI/CD pipelines, they may pose a security threat.” This vulnerability creates a prime target for attackers employing social engineering tactics.

Deja Vu: Echoes of the XZ Utils Attack

In some way, the LeakyCLI vulnerability resembles a recent incident involving the open-source project XZ Utils, a popular data compression tool. In that case, a malicious actor gained the maintainer’s trust through flattery, claims of expertise, and ultimately, malicious code insertion. LeakyCLI exposes credentials, making them even more valuable to attackers who might also leverage social engineering to compromise projects.

Securing the Cloud: Recommendations for Developers

Security researchers recommend several measures to mitigate the risks associated with LeakyCLI:

  • Eliminate Secrets in Environment Variables: Instead of storing sensitive information like passwords and keys in environment variables, leverage dedicated secrets management services offered by cloud providers like AWS Secrets Manager or Google Cloud Key Management Service.
  • Multi-Factor Authentication (MFA): Enforce strong authentication protocols like MFA for all users accessing cloud resources and project repositories.
  • Granular Access Control: Grant users only the level of access required for their specific tasks within projects.
  • Code Reviews: Implement rigorous code review processes to identify and remove any vulnerabilities that might be introduced accidentally or maliciously.
  • Community Vigilance: Foster a strong and vigilant development community to identify suspicious activity and report potential threats promptly.

While both AWS and Google Cloud Platform were notified of LeakyCLI, they maintain that the current behaviour falls within the expected design parameters. However, the security community is urging cloud providers to consider implementing additional protection within their CLIs to prevent sensitive information from leaking into logs, especially within automated CI/CD workflows.

The LeakyCLI vulnerability goes on to show how cloud security can be at risk. Therefore, developers and cloud providers alike must work together to implement robust security measures and remain vigilant against these ever-sophisticated threats.

  1. SSH Remains Most Targeted Service, Says Cado’s Cloud
  2. Chinese APT Posing as Cloud Services to Spy on Cambodia
  3. Massive Cloud Database Leak Exposes 380 Million Records
  4. Supply Chain Attack HitTelegram, AWS Alibaba Cloud Users
  5. Cloudflare Hacked After State Actor Leverages Okta Breach

[ad_2]
Source link

WhatsApp now has new chat filters for spotting unread messages

0
[ad_1]

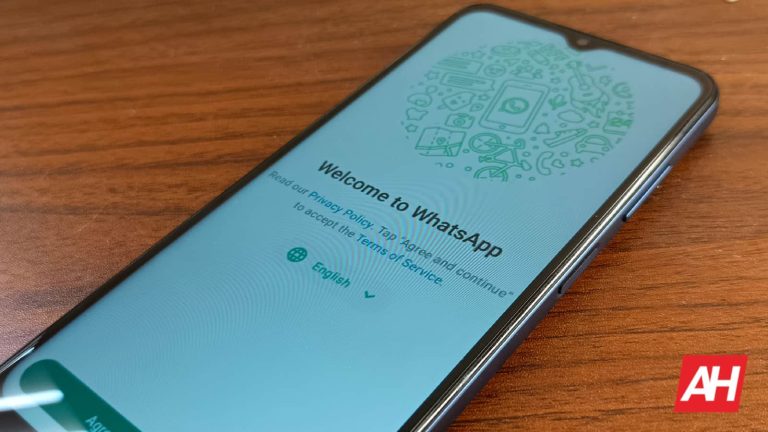
Starting today, WhatsApp is rolling out chat filters which will keep all your messages organized. The new feature will be available from next week and will cater to users who tend to leave unread messages as it is. Worth noting that last month a new feature was rolled out for WhatsApp users which lets pinning multiple messages per chat.

Despite being among one of the best end-to-end encrypted Android messaging apps, WhatsApp never had a permanent solution for unread messages. Although you can see the badge count on the app’s icon, you still need to search within the app to spot such messages. But, with chat filters rolling out, WhatsApp users can take a sigh of relief.

WhatsApp’s new chat filters will help you keep up with all your unread messages

WhatsApp’s new chat filters will let users quickly go through all the unread messages. Now you don’t have to scroll through the extensive chat list to spot unread messages. The new update will let you choose from three different filters visible at the top of the chat list.

Talking of the new WhatsApp chat filters, there’s the “All” filter which will display the all-messages view that you usually see when you enter the app. Secondly, there is the “Unread” filter that will only show chats with unread messages. Notably, this will also feature all those messages that you marked as “unread.” The filter will make it easier for you to reply to all the WhatsApp messages that you haven’t replied to.

Lastly, you will see the “Groups” filter which will display both read and unread messages from all your group chats. It will make spotting your favorite group easy without looking out for them in the chat list. Not to forget, you’ll also see subgroups of Communities. Not to forget, the Groups chat filters will help WhatsApp users spot low-activity groups that often get hidden very down in the chat list.

Undoubtedly, the new filters will be handy for users who often miss reading chats and forget to reply. With new updates coming around, it is clear that Meta is more focused on elevating user experience in WhatsApp. In February, the company added a handy feature that lets Android users search WhatsApp messages by date. More recently, Meta has been also testing status update notifications in WhatsApp.


[ad_2]
Source link

Marshall launched its latest Bluetooth headphones and earbuds

0
[ad_1]

Most people use Marshall’s amplifiers, but the company makes more than those products. In fact, the company has a pretty popular line of high-quality headphones under its Major series. Marshall’s previous Major IV headphones were a great option for audio files, and the company has just one-upped itself. Marshall just launched its new Major V over-the-ear headphones along with its Minor IV earbuds.

The Marshall Major V headphones promise very great battery life

These are truly audiophile-level headphones. They aren’t designed to look sleek and slim, as they are very robust. The outer casing of these headphones resembles the casing of the company’s amplifiers. It’s a deeply textured material that both looks and feels high quality. They don’t only look robust, but they are also built very sturdily. They have a rugged design, and they’re also foldable so that you can pack them away whenever you need to travel.

This should come as no surprise, but these headphones are designed to give you high-quality audio. Marshall has a long lineage of quality audio equipment, and that is reflected and its wearable audio devices. These headphones have high-quality custom-tuned dynamic drivers that reduce noise and prioritize clarity. So, you’ll be able to hear your music much better.

One of the selling points of these headphones is the incredible battery life. Most over-the-ear headphones cap out at between 40 hours per charge and 65 hours per charge. However, Marshall is boasting over 100 hours of listening time on a single charge! That’s an incredible feat, and definitely a great reason to pick up these headphones. Obviously, battery life varies depending on usage. So, users may get above 100 hours while other users make it below that mark. They will be among the best Bluetooth headphones you can buy.

The Marshall Major V are available for pre-order today, and they will start shipping on April 23rd. They cost £129 (about $160 USD or $250 AU).

Marshall Major V Headphones (1)

Marshall also announced the Marshall Minor IV

The company also took the wraps off of the Minor IV earbuds. This is a set of quality TWS earbuds. The Marshall Minor IV share the same aesthetic as the Major V, as the carrying case has the same textured material. With these, you can still expect a commendable 30+ hours of battery life with the charging case included. They’ve been improved since the previous iteration with a better fit and better internals.

Adding to that, these earbuds are water and dust-resistant. So, if you get caught out in the rain or have an extra long and sweaty workout session, your earbuds will be just fine.

Pre-orders for these earbuds also start today with shipping starting on April 23rd. These earbuds cost £119 (about $148 USD or $231 AU).

Marshall Minor IV earbuds


[ad_2]
Source link

Google Maps update improves Android Auto navigation experience with 3D building syncing

0
[ad_1]
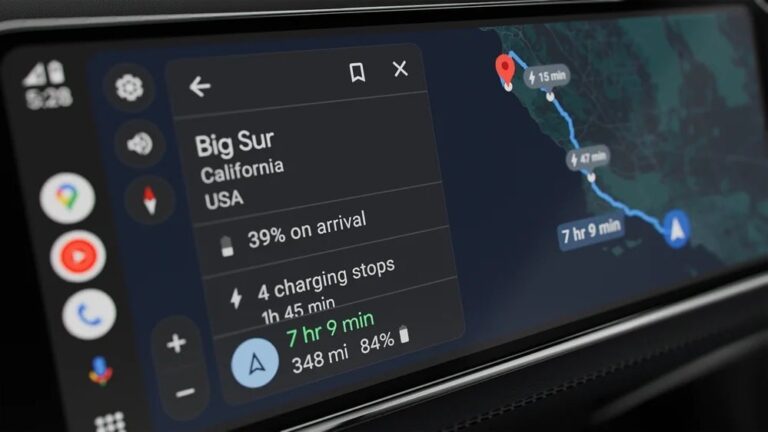
Google has continually enhanced Maps, improving our navigation experiences. The most recent Android update brings a significant improvement, especially for users who use Android Auto for directions while driving. The new update is centered around 3D buildings and their representation in Google Maps.
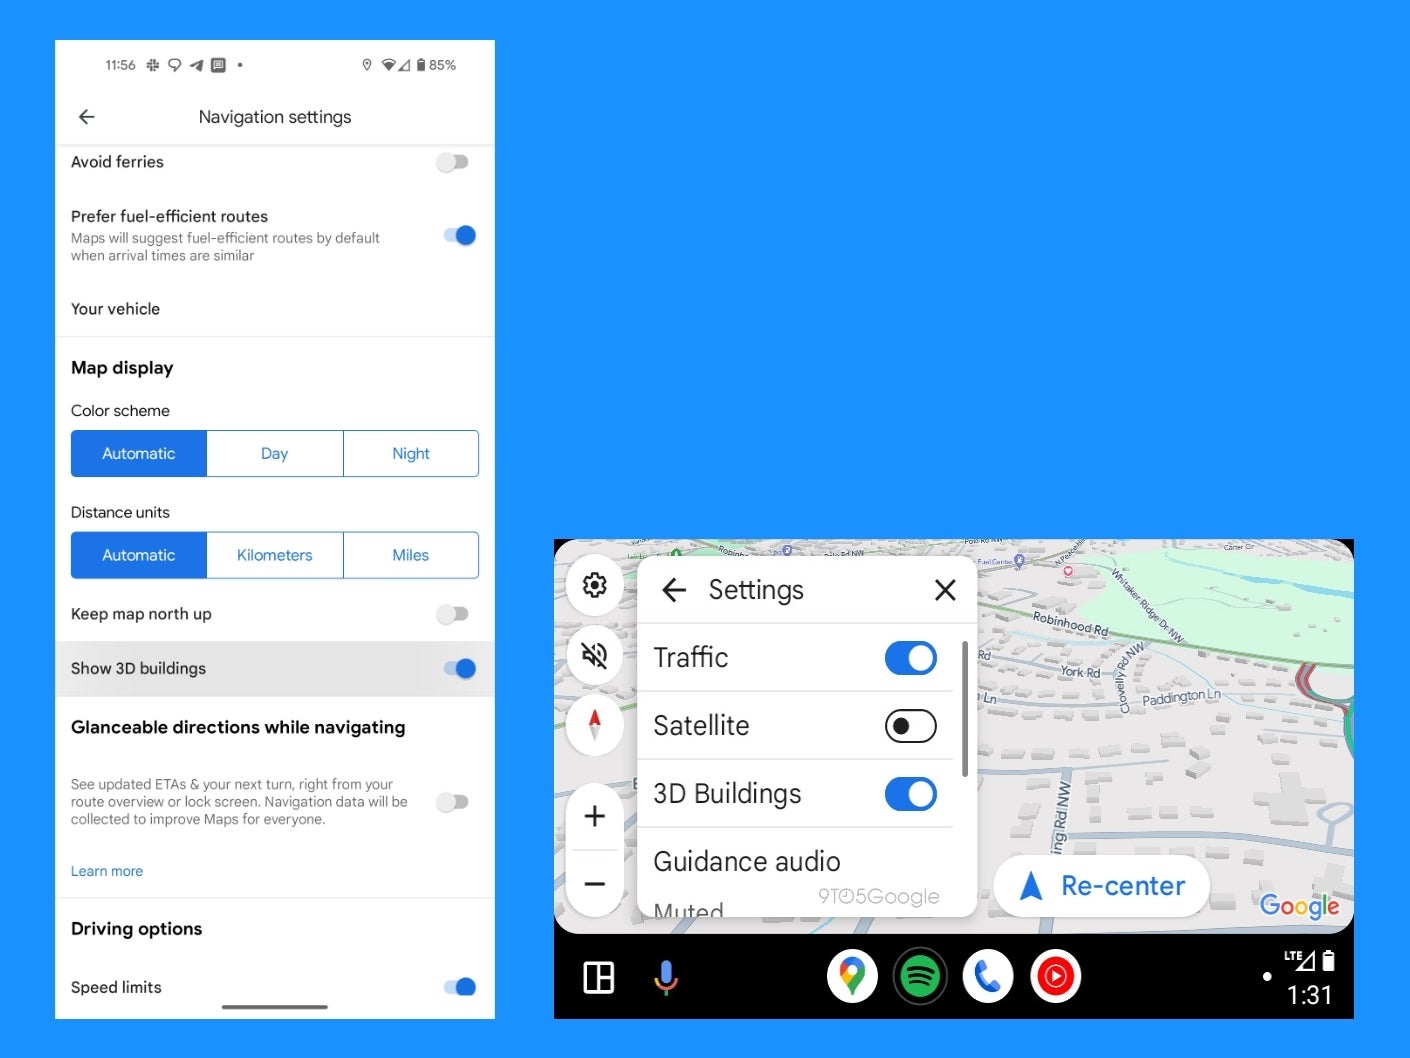
In the past, turning off the 3D buildings feature in Google Maps on your Android device did not affect Android Auto. Even if you disabled the feature on your phone, you would still see 3D buildings while using Android Auto, as it had its own separate setting for displaying them.

This latest update (Google Maps beta v11.125.0100), as spotted by 9to5Google, changes that. Now, when you toggle the “Show 3D buildings” setting within your Google Maps app, it seamlessly syncs with your Android Auto settings. If you turn it off on your phone, it also turns off in your car’s navigation view.

Image Credit: 9to5Google

This small change makes the user experience much smoother and easier. You no longer have to go to two different places to adjust the settings for a feature. As noted by the source, this update aligns with how Google Maps and CarPlay work on Apple devices, creating a more consistent experience across platforms.
Just remember, if you make changes to the 3D building settings while using Android Auto, they won’t show up on your car’s display right away. The settings sync when you first connect your phone to Android Auto. And keep in mind, this update is currently being rolled out in beta, so it might take a while before everyone gets it. Google often makes updates to its widely-used Maps application, and even a minor adjustment like this can have a noticeable impact on everyday usage. The recent modification demonstrates a dedication to enhancing the navigation experience on Android Auto, helping to make those extended car journeys a bit more seamless.

[ad_2]
Source link

Email Security Awareness Training – Empowering MSPs to Protect Clients

0
[ad_1]

In today’s digital landscape, email security has become a critical concern for businesses of all sizes. As cyber threats continue to evolve, it’s essential for Managed Service Providers (MSPs) to equip their clients with the necessary tools and knowledge to safeguard their email communications. That’s where TrustiFi’s Email Security Awareness Training comes into play.

Email has long been a prime target for cybercriminals, with phishing, malware, and other email-based attacks posing a significant risk to organizations.

Employees, often the first line of defense, can inadvertently expose their companies to these threats through simple mistakes or lack of awareness.

Empowering MSPs to Train and Protect

TrustiFi’s innovative solution empowers MSPs to provide their clients with comprehensive email security training and protection.

The module offers a user-friendly platform that allows MSPs to easily deploy and manage email security awareness programs, ensuring their clients’ employees have the knowledge and skills to identify and mitigate email-based threats.

*Gartner, “Market Guide for Email Security“, 13 February 2023, Ravisha Chugh, Peter Firstbrook, Franz Hinner. Use of Gartner, Inc. and/or its affiliates’ U.S. and international trademark and service mark is with permission. We reserve all rights. Gartner does not recommend technology users choose vendors with the highest ratings or other designations. Gartner research articles are views, not facts. Gartner disclaims all guarantees, including merchantability and fitness for a particular purpose, for this research.

Key Features of the Trustifi Email Security Awareness Training

  1. Interactive Training: The module features engaging, interactive training modules that cover a wide range of email security topics, from recognizing phishing attempts to implementing best practices for email hygiene.
  2. Simulated Phishing Attacks: MSPs can simulate phishing attacks to test their clients’ employees’ responsiveness and identify areas for improvement, helping to strengthen their overall email security posture.
  3. Reporting and Analytics: The module provides detailed reporting and analytics, allowing MSPs to track their clients’ progress, identify areas of concern, and measure the effectiveness of their email security awareness efforts.
  4. Customization: The Email Security Awareness training can be tailored to meet the specific needs and branding requirements of each MSP and their clients, ensuring a seamless integration into their existing security solutions.

The Benefits of Email Security Awareness Training

Email security awareness training from Trustifi equips individuals with the knowledge and skills to identify and mitigate these threats.

By educating employees on best practices for email usage, organizations can significantly reduce the risk of successful cyber attacks. Some of the key benefits of such training include:

  1. Improved Threat Detection: Trained employees are better equipped to recognize the signs of phishing attempts, malicious attachments, and other email-based threats, allowing them to take appropriate action to protect themselves and the organization.
  2. Reduced Vulnerability: By instilling a culture of email security awareness, organizations can minimize the likelihood of successful cyber attacks, which can have far-reaching consequences.
  3. Enhanced Compliance: Many industries have strict regulations regarding the handling of sensitive information. Email security awareness training can help organizations maintain compliance with these standards, reducing the risk of costly fines and legal penalties.
  4. Increased Productivity: When employees feel confident in their ability to navigate email securely, they can focus on their core responsibilities without the constant worry of potential cyber threats.

Empowering MSPs, Protecting Clients

By leveraging Trustifi’s Email Security Awareness Module, MSPs can empower their clients to take a proactive approach to email security.

By educating employees and testing their responsiveness, MSPs can help their clients reduce the risk of successful email-based attacks, ultimately safeguarding their businesses and protecting their valuable data.

Don’t let your clients fall victim to email-based threats. Explore how TrustiFi’s Email Security Awareness Module can help you strengthen your clients’ email security and position your MSP as a trusted partner in the fight against cyber threats.

Implementing Effective Email Security Awareness Training

Effective email security awareness training should be tailored to the specific needs and challenges of the organization. This may include:

  • Comprehensive Curriculum: The training should cover a wide range of topics, such as password management, identifying phishing attempts, and responding to suspicious emails.
  • Engaging Delivery: The training should be presented interactively and engagingly, using a variety of methods such as videos, simulations, and real-world case studies.
  • Ongoing Reinforcement: Email security awareness should be an ongoing process, with regular refresher training and updates to keep employees informed of the latest threats and best practices.
  • Measurable Outcomes: Organizations should track the effectiveness of their training program, using metrics such as the reduction in successful phishing attempts and the increase in employee reporting of suspicious emails.

By investing in email security awareness training, employees are empowered to defend themselves against cyber attacks, improving business security and resilience. Request a free demo here.


[ad_2]
Source link

Google Play Store purchases will use biometric authentication soon

0
[ad_1]

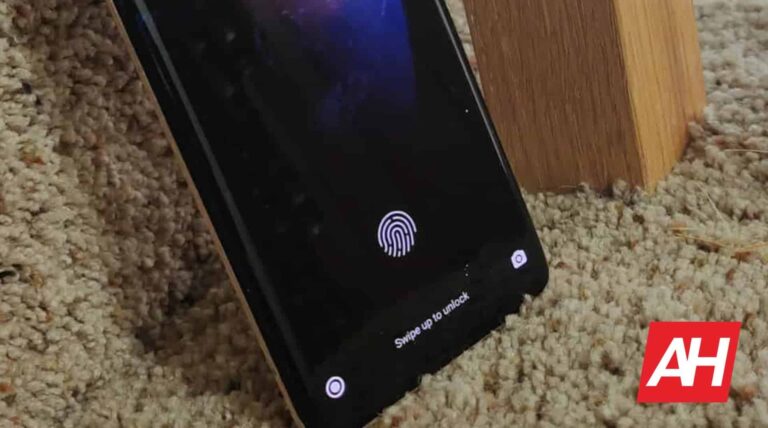
Google will give you the option to use biometric authentication when making purchases on the Google Play Store. This will be an alternative to using the synced Google account password. The Android OS developer has started sending out email notifications alerting Android smartphone users about the upcoming change.

Google Play Store will let you use biometric authentication to authorize payments

Google has started sending out emails to Android smartphone and smart device owners. The email is reportedly encouraging users to switch on biometric authentication for purchases made on the Play Store. The email states:

“On Google Play, you can set biometrics (fingerprint or face) as your purchase verification method on mobile devices that have biometric capability. If you set biometrics, it means you’ll be asked to verify it’s you with biometrics each time you make a purchase through Google Play.”

Google hasn’t switched over to biometric authentication entirely. Moreover, the company isn’t flipping the switch for everybody. Instead, Google has indicated that the change will take place over the next few weeks.

“In the coming weeks, there will be a change in how you confirm your setting when you choose biometric verification. For mobile devices, when you’re asked to confirm this setting, you’ll use your fingerprint or face instead of your Google Account password.”

Is Google making biometric authorization mandatory?

The email from Google states that switching on biometric authentication is voluntary. In other words, the search giant is merely urging Android device users to adopt a better and more secure method of authorization.

Google has been offering biometric authorization support for about 10 years now. Simply put, using a registered fingerprint or face to unlock a supported Android device and authorize transactions isn’t new. However, it appears Google is streamlining and simplifying the process, and this does enhance convenience. Incidentally, Google recently mandated every Google Wallet transaction would need authorization.

Opting to authorize with just a glance or a thumbprint is indeed way more convenient than typing in a password. However, Google has warned about the pitfalls of relying solely on biometric authentication.

Android smartphone users often register multiple fingerprints, including those of their spouses and children. Needless to say, this is risky. Moreover, with Google pushing hard for biometric authorization, anybody could authorize a payment with their registered fingerprint.

Hence, moving forward, it would be wise to limit fingerprint registration to responsible adults. Meanwhile, children could be given devices on which biometric authentication is disabled.


[ad_2]
Source link

Moto Razr 2024 Leaks Ahead of Launch, Certification Hints at Imminent Release

0
[ad_1]

Last year’s Moto Razr+ was one of the most popular foldable smartphones in various markets. The clamshell handset offered a large outer screen and a durable design, which were one of the key reasons for its success. Now the company is planning to launch the Moto Razr 2024 soon. Ahead of the launch, the Moto Razr 2024 leaked via the database of a certification agency in China.

The Moto Razr 2024 has been certified by the Radio Certification agency in China

A new Motorola smartphone with the model number XT2453-2 has been spotted in the Radio Certification agency’s database by Gizmochina. Notably, a previous Moto Razr 2024 leak indicated that this will be the model number of the device for the US market.

Apart from the model number, the certification database hasn’t revealed any other details about the Moto Razr 2024. However, since the device has passed the radio certification, its launch seems to be imminent. It’s worth mentioning that the company may launch the phone as the Moto Razr+ 2024 instead in select markets.

The Razr 2024 will retain the design of its predecessor, including a large outer display

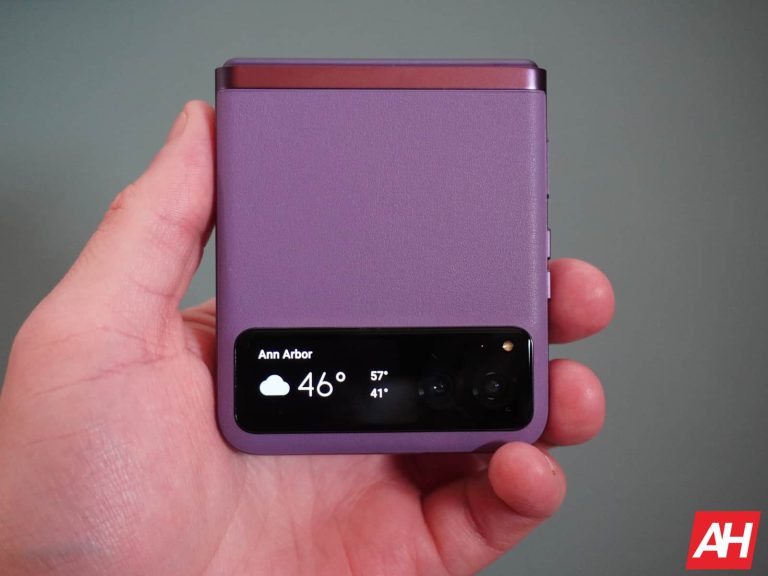
A recent Moto Razr 2024 leak revealed the design of the clamshell smartphone from all angles. It appears that Motorola’s next-gen foldable offering will have a design similar to its predecessor. The phone will continue to offer a massive outer display. It covers almost every part of the front of the device and even extends past the camera module.

Like the Moto Razr+ 2023, it will also have a punch-hole design on the front in the unfolded mode. One of the variants of the upcoming Moto Razr will be available in a dual-tone gray color hue. Once closed, some of the gray material of the rear will be visible on the front. Overall, it will be one of the best-looking foldable smartphones on the market.

Unfortunately, not many details regarding the specs of the Moto Razr or Moto Razr+ 2024 are available at the moment. However, the previous leak did suggest that it will have improved performance and battery life than the predecessor, thanks to the new Snapdragon processor. The brand hasn’t yet revealed when it will be launching the new Razr or Razr+ foldable smartphone.

Motorola Moto Razr+ 2024 radio certification


[ad_2]
Source link

Google says trigger-happy “Circle to Search” will be improved and Search and Lens results merged

0
[ad_1]

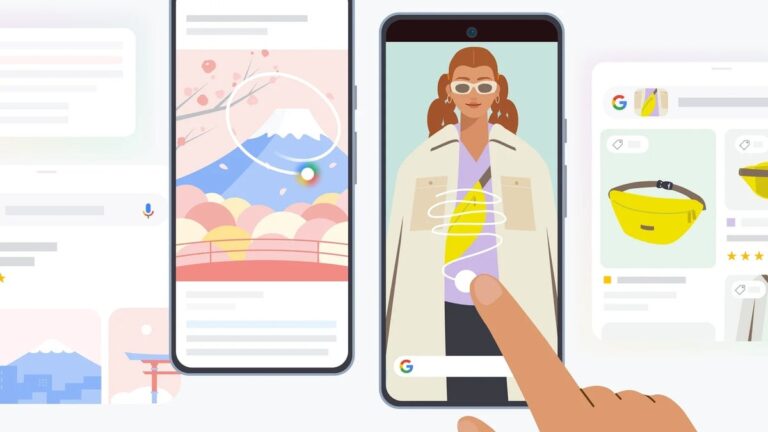
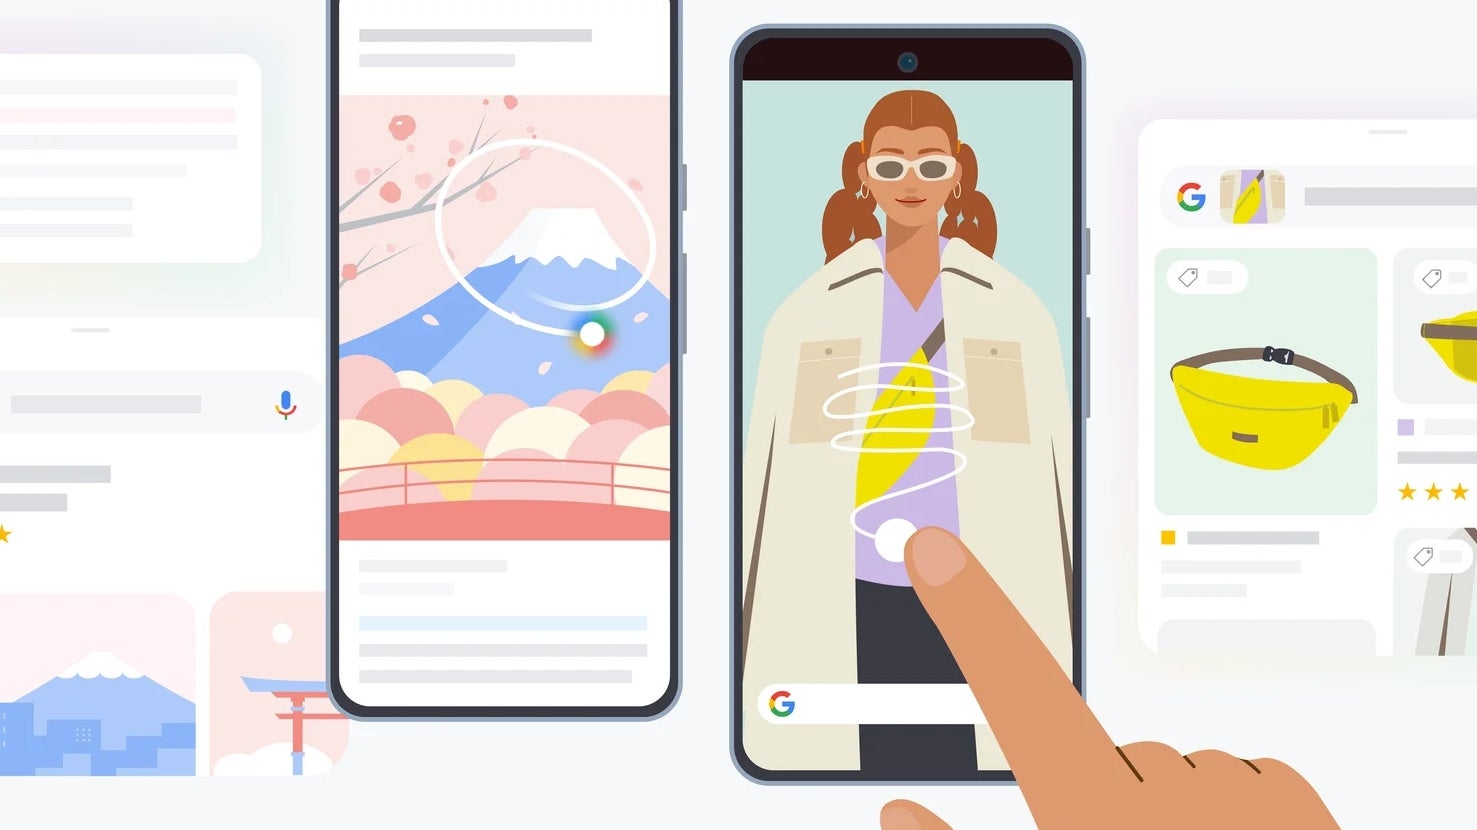
Google aims to streamline the way we search for information. We all know the handy Google search bar, the Assistant button, and now we have “Circle to Search.” It’s a great idea in theory, but like any new feature, it can be under-utilized and definitely has some kinks to work out – namely, it triggers a little too easily. Fortunately, Google is aware of the issue and promises improvements.Let’s rewind a bit. Circle to Search launched with the Samsung Galaxy S24, and it leverages some of Google Lens’s visual search magic. The premise is simple: long-press your navigation bar or home button, circle what you want to know more about, and watch your search results appear.

The main problem with the feature right now is that it is too easy to accidentally launch it when you’re navigating your phone using the familiar navigation bar gestures. While that bar is pretty wide, sometimes what you’re actually trying to do is go to the home page, not initiate a search. Google knows this, and in the recent “Made by Google” podcast, Erin Lynch and Alistair Pott — who worked closely with the team that made “Circle to Search” — admitted there are improvements to be made (thanks to 9to5Google for the tip).


It works, but not without hiccups

Google says Circle to Search depends on Google Lens for the tough stuff like image searches and text recognition. Their ultimate goal is to make the feature less prone to accidental triggers so that it only launches when you really want it to. To that, Erin Lynch added:


Big plans are in the works, even though changes might take a while. Google wants to add features like real-time translation and merge Lens and Search results for a super-powered tool. Lynch and Pott both expressed their hopes that the development process leads to a seamless user experience. The team behind Circle to Search has clearly worked hard on accuracy, especially for text copying, which seems to be a popular use for the tool internally, and they hope that will catch on with the users as well.

With fixes coming and even more possibilities in the works, Circle to Search looks like it’s a feature Google plans to stick with. It has the potential to change how we interact with information on our screens, but in its current form, it is not as popular as Google wants it to be. Now that it’s spreading to more devices, we’ll have to see how Google grows its capabilities.

[ad_2]
Source link

Personal Data Exposed in Massive Global Hack

0
[ad_1]

In a digital age where information is the new currency, the recent global hack has once again highlighted the urgent need for enhanced cybersecurity measures.

The breach was identified as Midnight Blizzard, from the Russian state-sponsored actor known as NOBELIUM. It has affected Millions of individuals and government agencies worldwide, underscoring the far-reaching consequences of cyberattacks and the critical importance of protecting sensitive information.

The Scope of the Breach

The scale of the global hack is staggering. Hackers gained unauthorized access to databases containing a wealth of personal data, including financial records, social security numbers, email addresses, and passwords.

The exposed information poses a significant risk of identity theft, financial fraud, and other forms of cybercrime.

The breach has impacted individuals across various sectors, including government agencies, businesses, and private citizens, highlighting the pervasive nature of cyber threats.

Implications for Individuals

The fallout from a hack can be devastating for individuals whose data has been compromised.

Identity theft, in particular, poses a significant threat. Hackers use stolen information to open fraudulent accounts, make unauthorized purchases, or even commit acts of impersonation.

Moreover, the exposure of sensitive personal information can erode trust and privacy, leaving individuals vulnerable to exploitation and manipulation.

Response and Accountability

After the breach, affected organizations must take swift and decisive action to mitigate the damage and restore trust.

This includes implementing robust cybersecurity measures, notifying affected individuals, and cooperating with law enforcement agencies to identify and apprehend the perpetrators.

Additionally, those responsible for the breach must be held accountable, whether they are individuals, criminal organizations, or state-sponsored actors. Holding perpetrators accountable prevents future attacks and conveys that protecting personal data is paramount.

Safeguarding Privacy in an Era of Cyber Threats

While the global hack serves as a sobering reminder of the dangers posed by cyberattacks, it also underscores the importance of proactive cybersecurity practices.

Individuals and organizations alike must remain vigilant in safeguarding sensitive information and adopting best practices for data protection.

This includes using strong, unique passwords, encrypting sensitive data, regularly updating security software, hiring the right cybersecurity company for monitoring, and being cautious when sharing personal information online.

Moreover, governments and regulatory bodies must enact robust data protection laws and regulations to hold organizations accountable for safeguarding personal data and provide recourse for individuals affected by breaches.

Hack Aftermath

The recent global hack exposed personal data, serving as a wake-up call for individuals, businesses, and governments alike. Cybersecurity must be a top priority in an interconnected world where data is increasingly valuable and vulnerable.

That is why Axios Security Group believes that by implementing robust security measures, fostering a culture of accountability, and advocating for more robust data protection laws, can be implemented together to mitigate the risks of cyber threats and safeguard the privacy and security of personal information.

Only through collective action can we effectively confront cybercrime and ensure a safer, more secure digital future.

About Axios Security Group

Axios Security Group is a trusted leader in comprehensive security solutions, offering organizations physical and digital protection.

With a dedicated team of experts, Axios created tailored security strategies to safeguard assets, personnel, and data.

Its physical security services range from on-site personal security to cutting-edge surveillance technologies, while our cybersecurity experts provide robust digital defenses, including threat detection and incident response.

Axios collaborates closely with each client to ensure our solutions align with their unique needs, industry regulations, and budgetary constraints.

Axios Security Group provides a vCSO (Virtual Security Officer) program in addition to physical and cyber security.

A vCSO (Virtual Chief Security Officer) is a C-suite-level security expert who enhances your company’s security. They bring strategic vision, devising comprehensive security plans encompassing digital information and physical asset protection.

By collaborating closely with your leadership team, a vCSO tailors security solutions to your unique needs, aligning them with your organizational goals and industry regulations.

This approach ensures that your organization is well-prepared to navigate the ever-evolving landscape of security challenges, creating a robust, adaptable, and resilient security infrastructure.

A vCSO provides all the same security expertise and protections for your organization at a 1/3 of the cost of a full-time CSO (Chief Security Officer.)

Contact us to learn how Axios Security Group can protect one of your most considerable corporate assets.

Contact
Contributor
Robin Carter
News Break
[email protected]
8004853983

[ad_2]
Source link