More users opt for alternative web browsers on iPhone

0
[ad_1]

The European Union’s Digital Markets Act (DMA) is actively reshaping how iPhone users access the web. In effect since March 2024, the DMA mandates Apple to offer users alternative web browsers during iPhone setup within the EU. This move decisively ends Apple’s practice of automatically steering users toward its Safari browser.

Before the DMA, iPhone users in the EU defaulted to Safari upon setting up their devices. Apple now presents up to 11 alternative browser options alongside Safari in curated choice screens for each EU country. These screens will be updated annually to ensure users have continuous choice in their browsing experience.

The DMA is transforming the browser landscape

While the DMA has only been in effect for a month, its impact is undeniable. According to Reuters, smaller browser companies are experiencing a surge in market share, a trend directly attributed to the new EU regulations. Aloha Browser, for instance, boasts a substantial user increase in the EU in March, while the established Opera browser sees record user numbers in the EU.

This upswing stems from multiple factors. The “choice screen” not only alerts users to alternatives beyond Safari but also allows smaller browsers to compete by highlighting their unique features and privacy-focused designs.

Will this transformation be a long-term trend?

While the initial user numbers favor alternative browsers, the long-term outlook remains uncertain. Some believe Safari’s brand recognition and user familiarity could help it retain a dominant market share despite the increased choice.

Another factor to consider is discoverability within the choice screen itself. With numerous browser options vying for attention, users might simply pick the first or most recognizable option, potentially limiting the visibility of smaller players.

The DMA’s impact on iPhone browsing habits is still unfolding. However, one thing is clear: the EU regulation is shaking up the mobile browser market, potentially creating a more diverse browsing experience for iPhone users.


[ad_2]
Source link

Elon Musk’s Grok has a new version that will help you understand memes

0
[ad_1]

Despite their appearance as nothing more than screenshots, simple drawings, or petite GIFs, memes can be surprisingly complex and meaningful, often conveying deep philosophical insights or life lessons.

That’s why, if ever in doubt, it’s better to ask somebody about a meme’s true meaning. Did I say “somebody”? Oops, I mean something.

Something like Grok, Elon Musk’s xAI creation. Now, Grok has a new version: Grok-1.5 Vision.

Mr. SpaceX/Neuralink/Tesla recently launched Grok-1.5 – that was shortly after Google unveiled Gemini 1.5 last month. Although Musk’s xAI claimed that Grok-1.5 LLM approaches the performance of GPT-4, it lacks multimodal capability. However, xAI’s newly announced Grok-1.5 Vision overcomes this limitation by seamlessly processing both textual and visual information (via MSPowerUser).

Connecting the digital and physical worlds


Grok-1.5 Vision (a.k.a. Grok-1.5V) represents xAI’s inaugural multimodal model designed to bridge the gap between digital and physical realms. According to a recent blog post by the company, Grok excels in benchmark testings, demonstrating superior real-world spatial understanding. Additionally, Grok-1.5V has the capability to interpret a diverse range of visual data, encompassing documents, diagrams, charts, screenshots, and photographs.

Some notable applications of Grok-1.5V include generating code from diagrams, calculating calorie counts, crafting bedtime stories based on drawings, or helping meme aficionados get a better understanding of memes.

xAI asserts that Grok-1.5V surpasses the competition’s latest AI creations, like Google’s Gemini Pro, in benchmark testings.

While Grok-1.5V is not currently available, xAI plans to release it soon for early testers and existing Grok users as a preview.


[ad_2]
Source link

Huawei developing its own chip-building equipment for a hefty price

0
[ad_1]

A recent report from Nikkei Asia informs that Huawei Technologies Co., the Chinese giant, is now working on developing its own chip-building equipment.

As you probably already know, the US has restricted the company’s access to its cutting-edge chip-manufacturing equipment and technologies, that are necessary for its smartphone and other businesses. Washington’s export controls have also prevented overseas companies such as ASML and Nikon from supplying lithography machines to Huawei. These are some of the most important tools in chip manufacturing.

Huawei is seemingly building in-house alternatives to overseas chip-building tools and technologies

Although, Huawei have managed to offer its consumers 5G phones such as the Huawei Mate 60 series, how they built the Kiron 9000s 5G chipset is still shrouded by mystery. In other words, we don’t know if the chip is entirely built on the company’s in-house technologies or if it still has contributions from overseas tools and technologies.

Now the news related to Huawei’s chip development is that they are aiming to develop their own lithography machines and many other necessary tools. Success here means less reliance on the US for building in-house Kirin chips, which is crucial for the company in the current scenario.

To achieve it, Huawei is reportedly investing nearly a whopping 12 billion yuan, which is equivalent to $1.66 billion. The company is building its new R&D center located in the Qingpu district of west Shanghai. The campus also houses a major chip development center, the new headquarters of HiSilicon Technologies (Huawei’s chip design unit), and research centers for wireless technologies and smartphones.

To start and speed up the development of its in-house chip-building equipment and technologies, the company is hiring experienced chip engineers who have previously worked with companies like Intel, TSMC, ASML (the designs and manufactures lithography machines used to make semiconductor chips), Lam Research, KLA and more. The company is reportedly offering as much as double the salary to the new employees as compared to the local chip manufacturers. However, there’s a catch.

Huawei’s work culture is getting more and more overwhelming

All this development reportedly comes at a cost to the chip engineers, says the report. Huawei’s existing 996 work culture is already a bit overwhelming. It means that the working time for its employees is from 9 am to 9 pm for 6 days a week. To Huawei, this was probably not enough to meet their new requirements (chips built completely in-house) in time. Here is an updated work schedule. “It will literally be 007 — from midnight to midnight, seven days a week. No days off at all” informs a chip engineer familiar with the matter. “The contract will be for three years, [but] the majority of people can’t survive till renewal.”


[ad_2]
Source link

Meta’s new AI-powered search bar starts showing up in Instagram

0
[ad_1]
It seems that more and more companies are trying to leverage the power of AI and implement many AI tools into their products. Meta’s efforts to shower users of its social apps in generative AI-powered tools continue to with a brand news search bar in Instagram.

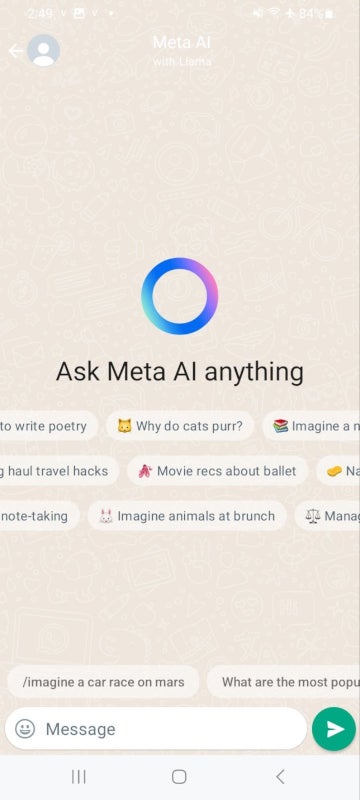
After the company has started testing its AI chatbot with WhatsApp users in India and other countries, Meta is now looking to add its AI in the Instagram search bar for both chat with AI and content discovery.

Over the weekend, TechCrunch reported that select Instagram users are now getting an improved search bar where they can start conversations in DM with Meta AI by doing search queries.

Those who are getting the new feature can ask questions or use any of the pre-loaded prompts. Aside from conversations, Meta’s AI can help Instagram users discover new content on the social network.

While Meta confirmed the experiment, it didn’t not say whether or not it’s using generative AI technology in search: “our generative AI-powered experiences are under development in varying phases, and we’re testing a range of them publicly in a limited capacity.”


[ad_2]
Source link

LightSpy Hackers Indian Apple Device Users to Steal Data

0
[ad_1]

The revival of the LightSpy malware campaign has been observed, focusing on Indian Apple device users.

This sophisticated mobile spyware, suspected to have origins in China, is being used for espionage, targeting a select group of individuals, including journalists, activists, politicians, and diplomats across Southern Asia.

The implications of such targeted attacks are vast, raising alarms about potential geopolitical motives behind the campaign.

Technical Details of the Attack:

Infection Vector: The initial infection is believed to have occurred through compromised news websites featuring content related to Hong Kong.

Visitors to these sites unknowingly download the malware, initiating the infection process.

Weaponization: Upon infection, a first-stage implant gathers device information and facilitates the download of further stages, including the core LightSpy implant and various plugins.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

These plugins are designed for specific spying functions, enhancing the malware’s ability to gather sensitive data from the infected device.

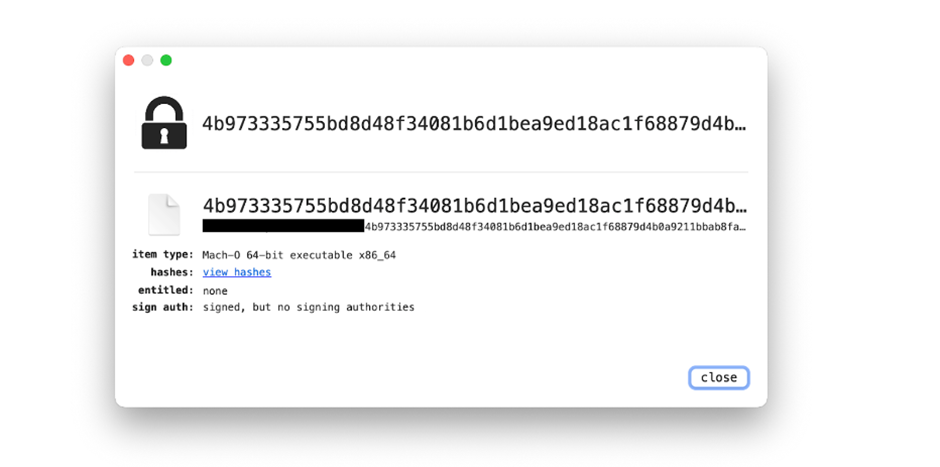
Hashes (md5, sha-256):

  • 4b973335755bd8d48f34081b6d1bea9ed18ac1f68879d4b0a9211bbab8fa5ff4
  • 2178d673779605ffb9cf7f2fa3ec8e97

File Information:

  • File Name: None
  • File Size: 430816 bytes
  • File Type/Signature: Mach-O64
Loader’s signature.
Loader’s signature.

Blackberry’s recent blog post highlights the resurgence of the espionage campaign, LightSpy.

This campaign is targeting Southern Asia, with a possible focus on India.

Execution Chain

The execution begins with a Loader, which loads the encrypted and decrypted LightSpy kernel.

This kernel acts as a complex espionage framework, capable of supporting various plugins for extended functionality.

These plugins are securely retrieved from the attacker’s server, decrypted, and executed within the system.

Hashes (md5, sha-256):

  • 0f66a4daba647486d2c9d838592cba298df2dbf38f2008b6571af8a562bc306c
  • 59ac7dd41dca19a25a78a242e93a7ded

File Information:

  • File Name: C40F0D27
  • File Size: 1252656 bytes
  • File Type/Signature: Mach-O64
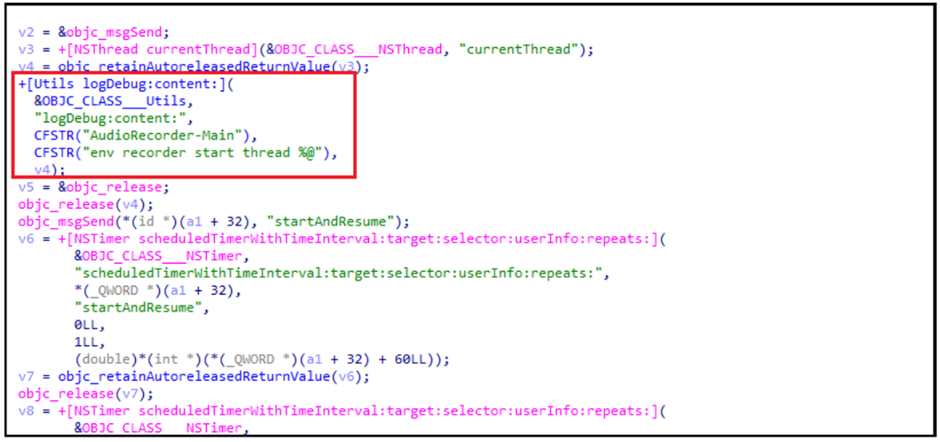
LightSpy's sound recording plugin.
LightSpy’s sound recording plugin.

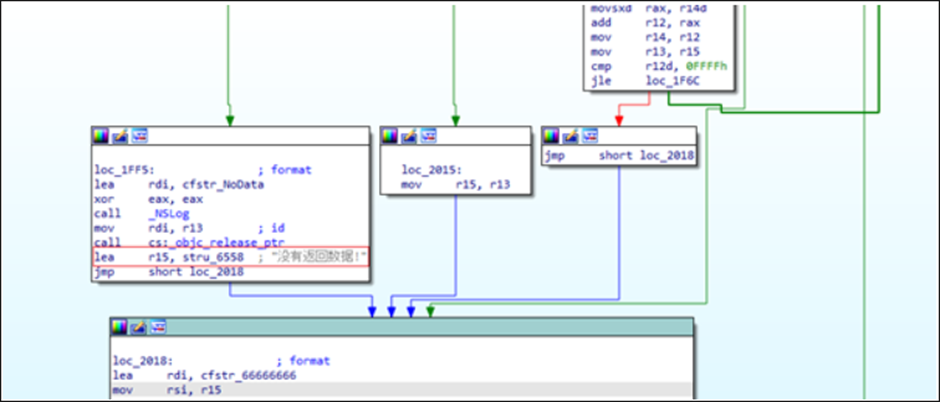
The F_Warehouse framework underpins LightSpy and offers many capabilities, including file exfiltration, audio recording, network surveillance, user activity tracking, application inventory, image capture, access to credentials, and device enumeration.

LightSpy Capabilities

One of LightSpy’s more invasive features is its ability to covertly record audio through the device’s microphone, capturing private conversations and surrounding sounds.

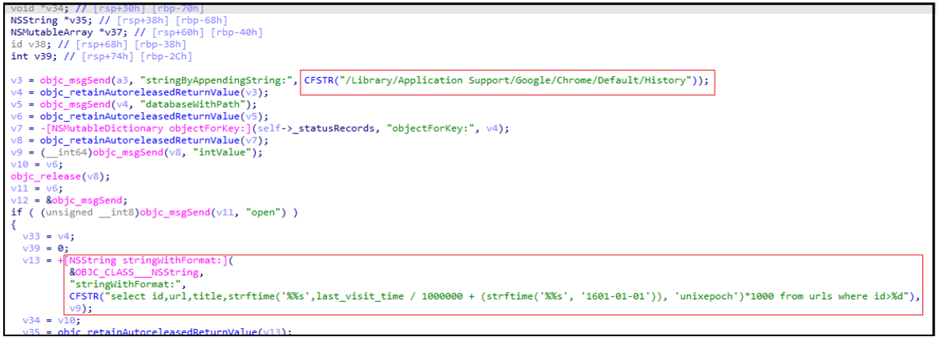
LightSpy meticulously tracks the browsing history of both Safari and Google Chrome, providing attackers with detailed insights into the victim’s online activities.

LightSpy's browsing information plugin.
LightSpy’s browsing information plugin.

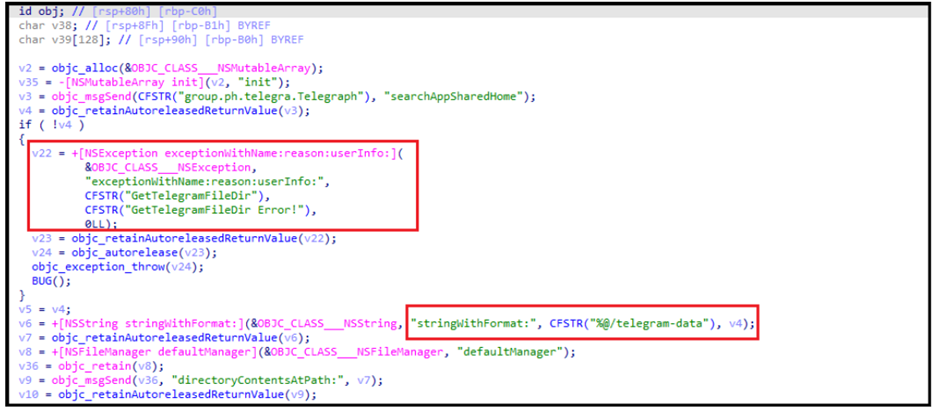
The malware explicitly targets data from popular messaging applications like Telegram, QQ, and WeChat, aiming to intercept private communications and gather sensitive information.

Code working with Telegram’s data.

Shell Command Execution

Beyond data exfiltration, LightSpy can execute shell commands received from the attacker’s server, potentially allowing complete control over the compromised device.

The presence of comments in Chinese within the plugin code suggests that the developers behind LightSpy are native Chinese speakers, hinting at the involvement of state-sponsored actors.

Code’s comments in Chinese language.

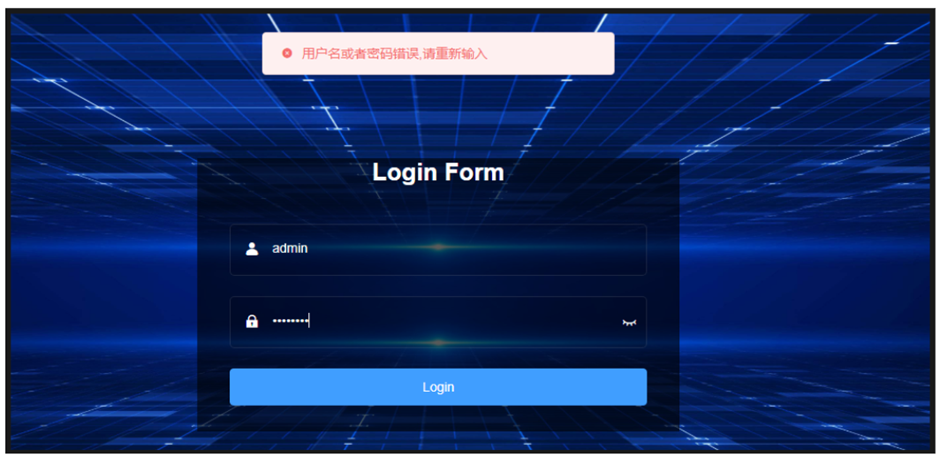
LightSpy communicates with a server at hxxps://103.27[.]109[.]217:52202, which hosts an administrator panel accessible on port 3458.

LightSpy's admin panel.
LightSpy’s admin panel.

The return of LightSpy, maintained by the “F_Warehouse” framework, marks a significant escalation in mobile espionage threats.

The expanded capabilities of this malware pose a severe risk to individuals and organizations in Southern Asia.

The evidence pointing towards Chinese-speaking developers specifically targeting individuals potentially involved in sensitive activities underscores the need for increased vigilance and robust security measures.

Understanding the tactics and techniques employed by LightSpy is crucial in mitigating its impact and protecting sensitive information.

Looking to Safeguard Your Company from Advanced Cyber Threats? Deploy TrustNet to Your Radar ASAP.


[ad_2]
Source link

Huawei rebranded its flagship lineup after 12 years

0
[ad_1]

Huawei has decided to rebrand its flagship smartphone lineup after 12 years. We’re talking about the ‘Huawei P’ lineup. We were expecting the Huawei P70 devices to arrive in the near future, but that won’t be the case. Well, they’ll arrive, but under a different name.

Huawei has decided to rebrand its flagship smartphone lineup after 12 years

Huawei has decided to rename the ‘Huawei P’ series into the ‘Huawei Pura’ smartphone lineup. This name signifies “purity and beauty” in Spanish, and it’s pronounced “piurua”. This is a huge change for the company following a 12-year stint with the ‘Huawei P’ series devices.

Do note that Huawei did not officially confirm the names of its upcoming flagships, but Digital Chat Station did. He’s one of the most reliable tipsters out of China.

Four Huawei Pura 70 series smartphones are on their way

According to one of the best-known tipsters in the business, four devices are coming. Huawei will release the Huawei Pura 70, Pura 70 Pro, Pura 70 Pro+, and Pura 70 Ultra. The ‘Ultra’ model will be a successor to the Huawei P60 Art that launched last year.

The Huawei Pura 70 Ultra will likely have the same specs as the Pura 70 Pro+, but it will include a different design. The Huawei Pura 70 Pro and Pura 70 Pro+ will differ in both battery life and photography departments.

The phones are right around the corner, but we still don’t have the launch date

You’re probably wondering when will these devices arrive. Well, we’re still not sure, as reports have been circulating regarding Huawei’s plans to postpone the launch event. This rebrand could have something to do with it.

The Huawei P70 series was rumored to arrive in April. We’re in the middle of April at the moment, and that didn’t happen. Huawei did announce some products a couple of days ago in China, including its very compelling new ultrabook.

The Huawei Pura 70 series could arrive later this month, though chances are Huawei will make the phones official next month, or even a bit later than that.


[ad_2]
Source link

Epic vs Apple continues: The iPhone maker denies violating App Store court order

0
[ad_1]

The clash between Epic Games, the maker of Fortnite, and Apple appears to persist, despite the Supreme Court’s decision to not hear appeals from either side.

However, just last month, the Epic vs Apple saga continued as Epic filed a motion asking the court to hold Apple in contempt. The Fortnite creator claimed that Apple had not adequately followed a court order to permit developers to link to external payment platforms, known as Apple’s anti-steering rules.

Apple rejects claims of a violation


Reuters reports that the iPhone maker has denied breaching the court order regarding its App Store and has urged a federal judge in California to dismiss a request by Epic Games to hold it in contempt.Apple presented its arguments in a filing to US District Judge Yvonne Gonzalez Rogers in Oakland, who oversaw Epic’s lawsuit in 2020. The lawsuit accused Apple of breaching antitrust laws due to its stringent controls on how consumers download apps and make payments within them.

In its filing, Apple criticized what it described as an attempt by Epic to make Apple’s “tools and technologies available to developers for free.” It stated that Epic aimed for the court to “micromanage Apple’s business operations in a way that would increase Epic’s profitability.”

Apple further stated:
 

Apple already told the court it did what was asked back in January, letting developers apply for an entitlement to add a link to their own website. But Epic thought this was just a “sham” because Apple still wanted to stop developers from seeking alternatives to the App Store with its rules.

Last month, Elon Musk’s X, Meta, Microsoft, and Tinder’s owner Match Group echoed Epic’s arguments, informing Rogers that Apple was in “clear violation” of the court’s order. In a related case against Alphabet’s Google, brought by Epic, a judge in San Francisco is anticipated to issue a separate injunction affecting the Google Play Store later this year.


[ad_2]
Source link

This Startup Aims To Simplify End-to-End Cybersecurity, So Anyone Can Do It – GBHackers on Security

0
[ad_1]

The Web3 movement is going from strength to strength with every day that passes. Slowly but surely, it’s building a new iteration of the internet that promises to give power back to the people through the concept of decentralization and data ownership. Yet for all of its promises, Web3 has become an incredibly dangerous place to navigate, with the industry ceaselessly being targeted by cybercriminals, hackers and fraudsters. 

The never-ending stream of Web3 security scandals hitting the headlines in the past couple of years has eroded much of the trust in the industry. In 2023, Web3 cyberattacks cost organizations and users more than $1.7 billion, according to a recent report by Chainalysis. The analysis highlighted 751 incidents involving Web3 projects that year, with the average cost of those incidents coming to $2.45 million. However, some of the attacks were far worse than others, with the top ten most damaging incidents accounting for $1.11 billion of the total losses. 

Web3 attacks come from multiple sources, with the 47 private key compromises identified being the most damaging, responsible for $880.9 million of the losses. Exit scams, phishing attacks and code vulnerabilities accounted for the rest of the industry’s losses. 

Cybersecurity Has A Complexity Problem

If Web3 is to live up to its billing as the future of the internet, it’s going to need to win over the public’s trust, and the only way to do that is by countering the aforementioned threats. But one of the main challenges is that the cybersecurity industry is awash with thousands of different products and services, causing considerable confusion for companies as they struggle to determine which blend of products they should rely on. 

With so many application monitoring services, observability tools, identity and access management solutions and firewall products around, companies have added numerous cybersecurity products to their arsenal, to the point where they’ve lost control. Their security is dependent on a mishmash of siloed tools that have no way to correlate with one another, leaving their defenses littered with holes. Although there’s a natural tendency to think that adding more defenses equates to stronger security, Web3 project leaders might do well to consider a more refined approach. 

Simplifying Cybersecurity For The Web3 Era 

Enter Resonance Security. This startup has created a powerful, full-spectrum cybersecurity platform that aggregates numerous tools and cybersecurity solutions, and combines them with automated security risk analysis to identify the most pressing vulnerabilities. Once that’s done, it then uses AI to suggest the best way to plug those gaps. By leveraging an AI concierge, Resonance can guide even novices through the necessary steps required to implement effective security. 

Resonance is led by its founder and chief executive officer Charles Dray, an entrepreneur who was among the first to realize that Web3 security can only be achieved by marrying it with traditional Web2-based cybersecurity solutions and techniques. 

Dray began his career in the traditional financial industry, where he spent time shoring up the defenses of major banks such as Citi, JPMorgan Chase and SMBC, only to pivot to the blockchain industry when he came to recognize the possibilities of decentralized finance and Web3. Having joined the Web3 security ecosystem, as one of the earliest Web3 security pioneers, he quickly recognized the urgent need for a more comprehensive solution. 

Resonance has spent the last couple of years building such a solution, and it’s ready for prime time with the debut of V1 of its platform, following a successful, year-long beta phase. The central element of Resonance V1 is its automated security risk analysis tool that provides each organization with an overall security score via a simple, easy-to-understand dashboard. This dashboard serves as the nerve center of the customer’s security efforts, and the security score helps to pinpoint the most urgent vulnerabilities and prevent cyberattacks effortlessly. One of the main advantages of this approach is it means Resonance can be used by any individual to test their project’s cyberdefenses, even if they have no background or experience in security at all. 

Identifying threats is the first order of business for Web3 security and Resonance provides the tools needed to do this extremely thoroughly. It’s a specialist in “offensive security”, with its engineers being among the best auditors in the business. Resonance provides blockchain and code audits that involve a detailed analysis of the underlying code used by Web3 platforms. In addition, its auditing services extend to smart contract code written in Cadence, Rust, Solidity and other common programming languages. These audits are crucial for any Web3 dApp to identify bugs and protect their users from vulnerabilities. 

Don’t Forget Web2!

With the code audits out of the way, Resonance goes further and conducts penetration testing on behalf of its customers, searching for vulnerabilities in the Web2 stack that hosts their dApps. This marriage of Web2 and Web3 security is essential, because every dApp still relies on legacy technology, yet this is often overlooked by the majority of Web3 products, Dray revealed. 

“It’s important to keep in mind that Web2 is the “foundation” of Web3, but many builders seem to forget this,” Dray told CPOMagazine. “But building Web3 on a weak foundation will inevitably spell trouble. It’s alarming, but many Web3 projects we have seen just get a smart contract audit and stop there, forgetting about the Web2 parts.”

Resonance’s penetration tests involve searching for bugs in the underlying infrastructure of both applications and browser extensions, as well as the cloud environments they’re hosted in. 

When it comes to shoring up defenses, Resonance is equally thorough, providing a suite of CI/CD and cloud security tools that can be integrated into application development processes, with support for cloud platforms such as AWS, Microsoft Azure and Google Cloud. Its website also lists vetted cybersecurity products from third-parties that can easily be implemented by any user, regardless of their technical skills. Through this approach, the company is amplifying cybersecurity to protect its customers against any kind of threat, even if it hasn’t built its own solution. 

Finally, Resonance complements these offerings with an extensive cybersecurity education program that allows its customers to expand their knowledge and awareness of the kinds of threats they need to deal with, as well as any new attack vectors that evolve over time. 

Resonance says its security stack is the only platform Web3 projects will ever need to bolster their security, automating the entire process so project developers can focus on building out their services. It all starts with the security scan, which is complemented by audits and pen tests to identify the biggest security holes. Then the AI concierge takes over, prioritizing the most urgent vulnerabilities and recommending ways to fix them. The education is really just the icing on the cake. 

Dray said his company’s primary goal is to make full-spectrum cybersecurity easy to implement through its patent-pending algorithm, which considers each customer’s technical level, budget, scope and timeframe, before creating a custom plan of action. 

“Projects often lack the guidance to determine what they need to do, due to the overwhelming number of cybersecurity products and services and a lack of time,” Dray said. “They usually give up and focus on marketing and growth. We make it possible to continue to focus on that while still protecting against cyberthreats.”

A Unique Proposition

Although it’s still a new player on the Web3 cybersecurity scene, Resonance has already made a big impact, building up a loyal customer base during its beta phase. This initial success stems from its realization of how Web2 security issues contribute to many of the threats that impact Web3 projects. 

“From the outset, Resonance demonstrated a deep understanding of the intricacies involved in securing Kado’s flows and technology stack,” said Kado.Money Chief Executive Emery Andrew. “Their team exhibited not only technical expertise but also a genuine commitment to addressing our unique security concerns.”  

As the adoption of blockchain and Web3 technology accelerates, there is a pressing need for a specialized cybersecurity platform to address the numerous risks and dangers in the industry. Resonance’s unique selling proposition lies in its comprehensive risk analysis, its automated guidance, its powerful offensive and proactive security offerings, and its willingness to embrace partnerships. 

By bundling these capabilities into a single, easy-to-use platform, Resonance seems set to play a leading role in securing the next version of the internet.
[ad_2]
Source link

A week in security (April 8 – April 14)

0
[ad_1]

April 12, 2024 – Wondering whether changing your SSN is an option. Read here what you need to qualify for a new SSN and what you need to get one.

April 11, 2024 – Apple has sent alerts to people in 92 nations to say it’s detected that they may have been a victim of a mercenary attack.

April 10, 2024 – Don’t wait for an online harassment campaign to unfairly target you or a loved one. Take these proactive steps today to stay safe.

April 10, 2024 – Find out what sensitive data of yours is exposed online today with our new, free Digital Footprint Portal.

April 9, 2024 – A man has pleaded guilty to assuming someone else’s identity for 35 years.


[ad_2]
Source link

Xiaomi 14T series specs leaked

0
[ad_1]

Xiaomi is working on the new Xiaomi 14T series. The features of the smartphones have been leaked. You might be wondering what the next generation T series models will offer. Just like the previous 13T series, the 14T series will feature advanced camera hardware, a high-performance processor, and more. Now, as the Android Headlines team, we find some clues in the Xiaomi HyperOS source code.

Xiaomi 14T series specs

Xiaomi 14T series consists of 2 models: Xiaomi 14T and Xiaomi 14T Pro. Some details of the 14T Pro were revealed. The first one was that the device was a rebranded version of the Redmi K70 Ultra. The HyperOS code confirmed that both models have the same “rothko” codename. This suggests that the Redmi K70 Ultra and Xiaomi 14T Pro will be a smartphone with similar specifications.

Seems that the device will come with an “N12” internal model number. The Xiaomi 13T Pro had an “M12” model number. On the processor side, the Xiaomi 14T Pro will feature the Dimensity 9300 SOC. This will differentiate it from all its competitors. Dimensity 9300 will impress users with high power efficiency and extreme performance.

However, our findings show that the two models are not exactly the same. For one, the Redmi K70 Ultra doesn’t support wireless charging. Xiaomi will be adding wireless charging only to the Xiaomi 14T Pro. While this is a negative for users in China, people who will be using the global version of the device should have no worries. Xiaomi 14T Pro will support wireless charging.

We learned that the Chinese manufacturer won’t deal with Leica for the Redmi K70 Ultra in order to reduce costs. Because, while the Xiaomi 14T Pro will have a telephoto camera, the Redmi K70 Ultra will not. Xiaomi HyperOS source code shows that the Redmi K70 Ultra will come with a macro camera. We find that the telephoto camera will be used only on the Xiaomi 14T Pro. This also confirms that the Xiaomi 14T Pro will be powered by Leica.

We expect the Xiaomi 14T Pro to be sold in many countries. 3 different model numbers provide information about the regions where the smartphone will be sold. These model numbers are as follows: “2407FPN8EG“, “2407FPN8ER“, and “A402XM“. The first model number represents the 14T Pro that will be sold in the Global market. The other model numbers belong to the 14T Pro version that will be sold in Japan. Xiaomi will make a deal with Softbank for the 14T series, as it did for the 13T series. Unfortunately, the 14T Pro will not be sold in India.

Now let’s come to what is known about Xiaomi 14T. Xiaomi 14T’s codename will be “degas”. The codename “degas” is inspired by the name of the famous French artist Edgar Degas. Another thing we know about the Xiaomi 14T is that the phone appears in the HyperOS source code with the internal model number “N12A“.

We have spotted the Xiaomi 14T in the database with the model numbers “2406APNFAG“, and “XIG06“. This device will be officially available in the global market. Xiaomi tends to offer some smartphones in specific regions; for example, a model available in Europe may not be available in India, and vice versa. The Xiaomi 14T series is expected to be sold in many regions except India. It’s also worth mentioning this. The model number “XIG06” represents the Japan version of the Xiaomi 14T. This indicates that the device will also be sold in Japan.

In the Xiaomi T series, the main difference between the standard model and the Pro model usually lies in the processor and battery specifications. For example, the cameras used in the Xiaomi 13T and 13T Pro are exactly the same, and even the battery capacities are the same, both phones have a 5000 mAh battery. The scene will probably be the same for the Xiaomi 14T series, two different phones with similar specs but different chipsets. Xiaomi offered the Dimensity 8200 Ultra in the 13T, while the 13T Pro came with the Dimensity 9200+.

You might be wondering about the launch dates. The Redmi K70 Ultra is expected to be introduced to China in August. You can expect the launch of the Xiaomi 14T series to happen in September. There is no information about their prices yet. We will keep you informed of new developments. Stay tuned.


[ad_2]
Source link