Despite fierce competition, TikTok keeps reigning supreme among video content platforms

0
[ad_1]

Achieving the prodigiousness and amplitude that TikTok accomplished is anything but an easy feat for the upcoming social media platforms of all kinds and purposes. It’s not a secret any longer that the vastness of this ubiquitous app stemmed from building a ground-breaking concept and turning this ambition from what seemed unrealistic and even too innovative to materialize into an easily accessible app within reach for anyone.

Other platforms aiming at the same goal were invented before TikTok, such as Vimeo, which caught traction rapidly, but was snuffed out just as briskly, leaving only the idea of a video-sharing platform behind as an heirloom for TikTok’s devs to work on. However, there are myriad key points where these two seemingly resembling platforms intersect, and the primary one is the uploading and sharing of video content from internaut to internaut with an easy click.

With all the magnitude achieved, people wonder whether anything better can commence and overshine TikTok, potentially bringing new opportunities to improve internauts’ lives in a more accessible and better-facilitated way. Some well-established platforms are struggling to rival and overtake TikTok, such as YouTube or Instagram, which developed resembling categories to gain some market shares. However, it appears that we should set aside such assumptions and premises, as TikTok secures its recognition as the primary avenue through which we can explore the world with just a click, and the following reasons stand as motivation. It remains the reigning avenue for creative inspiration and recommendation, catering to people’s need to learn newness right away without deep delving into instructional, long how-to content.

TikTok image 8339883983839983

TikTok, the anomaly: an unprecedented platform endorsed by academics

TikTok, the platform whose follower base count exceeded 1.5 billion, revolutionized the concept presented by Vimeo to become the largest and most popular video-content social media platform by niching in 15-second video shots from webcams or devices. To help the right audience reach suitable content and actually improve their knowledge in vast areas while developing new interests, possibilities that enabled video content creators to acquire likes and follows on TikTok emerged, bridging the gap between those sharing wisdom and those looking for it. This way, connecting with the targeted audience for whom one’s content is tailored has become easier than ever, ensuring that the platform’s users stay informed about even their most niche and unconventional interests.

This opportunity gave a voice to the voiceless and more, so professionals from the education and psychology systems now recommend individuals to take advantage of the platform’s prowess. Such endorsement has yet to be witnessed by other social media platforms since all that you can hear these days is how these avenues have transformed into a rather time-consuming and problematic addiction. Now, on-point hashtags such as “#teacher,” “#teachertok,” and “#teachersoftiktok” are witnessing increasing adoption rates on the back of their power in helping professors boost their knowledge to further spread it to disciples, ushering in a new era for education and deeper learning through alternative solutions.

Reasonably, TikTok is also to be consumed with precaution since it can rapidly transform into a not-so-healthy habit if one cannot make it through the day without accessing this app once or a few times. Yet, looking at the shared content, it’s safe to say that once the algorithm works in the user’s best interest, it can only reap the benefit of knowledge.
Stay alert and try to use the app solely for educational and entertainment purposes to ensure you’re only gaining the advantages of social media.

Deep learning and topics of high interest finally get tackled boldly

Since we’re now aware of one of the largest trends on TikTok, namely the professors’ involvement and their long-awaited outspeaking, it’s necessary to make a difference between implication by dint of puttering around but by emphasizing social and modern issues openly and daringly, tackling topics of the highest importance that get swept under the carpet by those possessing the power to change them for the better.

Likewise, professors are showcasing areas of improvement in the education system and beyond, so whether you’re into classroom decoration ideas, diverse and trending social justice topics, effective classroom management strategies, the resources are readily available at your fingertips.
Simultaneously, people can connect with those involved in the teaching and educational professions, including teachers, who can recommend all teaching-related matters. Advice, tips, tricks, and insights easily reachable and learned within seconds are what people can get when using TikTok beneficially.

TikTok is essentially a basic video content platform but with a twist

TikTok’s traction among users resembles a teenager’s adoration of pizza—it’s how things are. Yet, the TikTok algorithm is designed to help people from all areas of life improve their lifestyle, whether we look at start-ups and small businesses looking to grow their audience, talented individuals exploiting their flair and making careers, or simply those with entrepreneurial spirit kick off their project.

From TikTok to Hollywood, TikTokers with large followings made their way into the Hollywood world. They took it over, with myriad examples such as Addison Rae and Charli D’Amelio standing as proof of the power of free, endorsed expression. Being focused mainly on seconds-long videos, usually limited to less than 1-2 minutes, it’s easy to see why users prefer this platform for easily digestible, on-point video-englobed information, being no longer stuck with scrolling through endless streams of images or texts.

Time is being consumed more efficiently by anyone leveraging the platform, so give it a shot if you have something to say and want to be heard (or watched).

TikTok’s algorithm and bite-sized content approach are unparalleled

The TikTok algorithm is the best in the biz for recommending content to its user base thanks to its avant-garde recommending system that is continuously worked on and improved. Furthermore, its virality-driven features and snappy content provide a buffet of bite-sized video content to shape into the brainchild of trending challenges; this platform has transformed how the world consumes and regards content.

Drawing a parallel between this mammoth and an equally vast video-content platform, YouTube, one can observe that the former is exceptionally sculpted around short-sized videos, which appeals to the younger demographics.

As a fun fact, this bite-sized format led to the fame of the Creative Center – a place specially crafted for exploiting trend reports and coming trends. In contrast, a personalized commerce platform is offered for those looking to leverage in-app touchpoints such as live shopping, among other possibilities.

As you can see, gaining such unparalleled magnitude is anything but straightforward for any other media platform we know to date.


[ad_2]
Source link
Notepad++ Wants Your Help to Take Down the Parasite Website

0
[ad_1]

In a recent announcement, the team behind the widely acclaimed source code editor, Notepad++, has issued a call to arms for its user community.

The appeal comes in response to the emergence of a deceptive website that misleads users and poses significant security risks.

Here’s a closer look at the situation and how you can help.

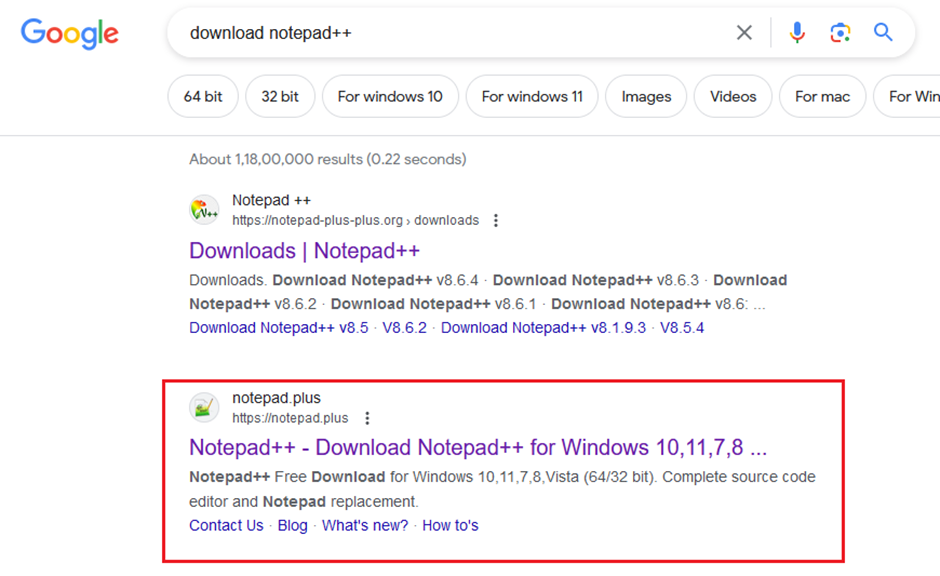
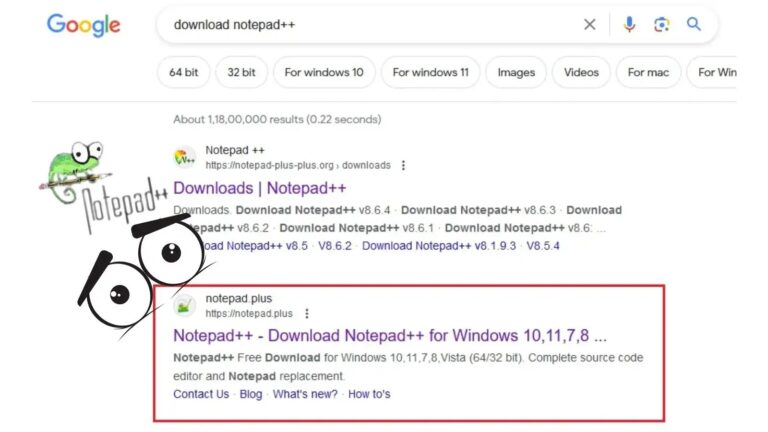
The website [https://notepad.plus/] has been masquerading as an official source for downloading Notepad++.

This has led to confusion among users, some of whom have been tricked into believing it is the legitimate site for the popular code editor.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

The creators of Notepad++ have received numerous complaints through emails, social media, and forums, highlighting this imposter site’s frustration and potential dangers.!

Fi A screenshot showing the misleading website’s interface, clearly indicating its attempt to mimic the official Notepad++ site

Hidden Dangers Lurking Behind Every Click

Despite its claims of being an “unofficial fan website created for general information/educational purposes only,” the site harbors malicious intentions.

It is littered with misleading advertisements that aim to profit from unsuspecting visitors and pose serious security risks.

These ads are designed to trick users into clicking on them, thereby compromising their online safety.

The Real Victim: Notepad++ and Its Community

The existence of [https://notepad.plus/] does more than mislead users; it actively diverts traffic away from the legitimate Notepad++ website, notepad-plus-plus.org.

This undermines the integrity of the Notepad++ community and threatens user safety by exposing them to potential security threats.

The Notepad++ team is urging its community to take action against this parasitic website.

By reporting the site as harmful, you can play a crucial role in protecting not only the Notepad++ community but also the broader internet ecosystem.

Your vigilance and prompt action can help maintain a safe and secure online environment for all users.!

The call to action from the Notepad++ team is a reminder of the power of community.

In the face of deceptive practices and online threats, standing together can make a significant difference.

By reporting the malicious website, you contribute to a safer internet, ensuring that the integrity and security of the Notepad++ community remain intact.

Secure your emails in a heartbeat! Take Trustifi's free 30-second assessment and get matched with your ideal email security vendor - Try Here


[ad_2]
Source link

X brings passkey support to iPhones globally

0
[ad_1]

Back in January, Elon Musk’s social media platform X rolled out support for passkey login for iOS devices. However, initially, this feature was only available in the US. But now, things have changed.

X has now introduced passkey support for iOS devices worldwide. This means that anyone with an iPhone can now use a passkey as a login option, providing a more secure and convenient way to access their iOS devices and accounts.

Curious about passkeys? Passkeys are built using public key cryptography from the WebAuthentication standard. Here’s how it works: when you sign up for an account, your device creates a special key pair – one public and one private – for that account.

 
The public key is sent to and stored securely by X, while the private key stays on your device. Your passkey is never shared with X, keeping things secure and reducing the risk of unauthorized access to your account.


Oh, and with passkeys, you can wave goodbye to trying to remember those long and complicated passwords. Instead, you can simply use your biometric data with Face ID or Touch ID to access your accounts.

 
Overall, passkeys offer two major benefits:


  • Easy login: With passkeys, logging in becomes a breeze. Once set up, you can use your passkey to access your account across various devices without the hassle of remembering or resetting a forgotten password.

  • Better security: Passkeys provide a higher level of security for your account. Because they are generated uniquely by your device, they are less susceptible to security threats such as fraudulent or unauthorized attacks. This helps keep your account safe and secure.

If you’re using X and have an iOS device, and, of course, you want to use a passkey as a login option, here’s what you need to do:

  1. Log in to the X app with the account you want to enable the passkey for.
  2. Click on “Your account” in the navigation bar.
  3. Select “Settings and privacy,” then click on “Security and account access,” and then “Security.”
  4. Under “Additional password protection,” click on “Passkey.”
  5. Enter your password when prompted.
  6. Select “Add a passkey” and follow the prompts.

[ad_2]
Source link

Top Israeli Spy Chief Identity Exposed In A Privacy Mistake

0
[ad_1]

Privacy mistakes could pose a serious threat to sensitive information or systems,, which threat actors could exploit for their gain.

These mistakes can include weak passwords, unsecured networks, and outdated software, making it easier for threat actors to infiltrate and exploit vulnerabilities.

Recently, a top Israeli chief’s identity was exposed through a mistake in privacy.

Top Israeli Spy Chief Identity Exposed

Israel’s elite Unit 8200 surveillance agency chief Yossi Sariel inadvertently exposed his identity online through an embarrassing lapse linked to a book he anonymously published on Amazon under the name “Brigadier General YS.” 

The 2021 book “The Human Machine Team” on AI transforming military-machine relations included an email address traceable to Sariel’s name and a private Google account with ID, maps, and calendar profiles after over 20 years in the shadows.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

While the IDF called it a “mistake” and said the email wasn’t personal, the exposure highlights security lapses surrounding one of the world’s most powerful spy chiefs comparable to the NSA director.

The security lapse exposes the identity of Yossi Sariel, shadowy Unit 8200 cyber intel chief who “lives and breathes” intelligence, but whose tenure is marred by controversy, reads The Guardian report.

Unit 8200 built vast Palestinian surveillance yet failed to prevent Hamas’ deadly 2023 assault on Israel.

Critics say its “technological hubris” compromised intelligence gathering. 

In the Gaza war, IDF embraced Sariel’s radical AI vision where machines undertake complex battlefield tasks, possibly preventing repeat intelligence failures.

The exposure further pressures the elite spy chief leading Israel’s powerful NSA equivalent.

Unit 8200 chief Yossi Sariel’s 2021 book promoted integrating AI for “human-machine teaming” in warfare, reflecting his vision of machines assisting intelligence like IDF’s controversial AI target recommendation systems deployed in the Gaza bombardment. 

The book, written under an alias after US research, conveyed the balance of humans with AI over full autonomy.

Its exposure of Sariel’s identity adds pressure on the elite but criticized spy head, once part of “The Choir” pushing intelligence overhaul. 

IDF defends AI tools as lawful target verification aids for researchers despite concerns over corrupting human oversight and ethical risks from unproven battlefield AI systems rapidly developed under Sariel’s leadership.

The public disclosure highlights increasing pressure on the boss of Israel’s elite Unit 8200, Yossi Sariel, whose 2021 book under an alias promoted an AI-driven “targets machine” that employed big data to fuse intelligence and warfare with a non-human focus on technology.

Sariel was subjected to unusual public censure for the Israeli intelligence agency Unit 8200’s “technological arrogance,” which led to fatal intel failure in the wake of the Hamas attack on Israel in 2023.

However, his leadership witnessed his technological vision conflicting with traditional intelligence techniques, as revealed by this latest security leak regarding his identification in conjunction with Israel reflecting over its worst intelligence letdown during his command.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link

TikTok plans to take on Instagram with new app for sharing photos

0
[ad_1]
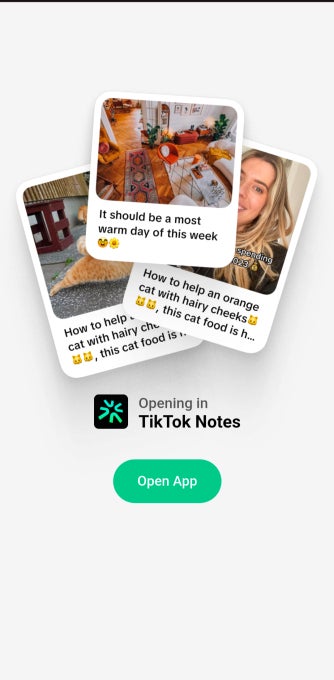
TikTok users have started to get pop-up notifications about a new app that the social network company plans to launch in the not-so-distant future. The app is called Notes and allows users to share photos much like Instagram.

TechCrunch reports that TikTok has already confirmed the Notes app was in development, but the company didn’t offer any timeframes for the release of the photo sharing app.


The notification that many TikTok users have been getting in the last couple of weeks mentions that Notes is “a new app for photo posts.” Also, TikTok explains that “your existing and future public TikTok photo posts will be shown on TikTok Notes.”

Thankfully, TikTok will offer the option to opt-out from the app: “if you prefer not to show your public TikTok photo posts on TikTok Notes, turn this off now.”


The upcoming Notes app is not the only project that TikTok is currently working on. The company is also experimenting with different formats such as text posts and longer videos.

[ad_2]
Source link

Google Rolls Out “Find My Device” Network for Android Users

0
[ad_1]

Google has announced the global rollout of its revamped Find My Device network.

This innovative feature is set to transform how Android users locate their misplaced devices and everyday items, leveraging a vast, crowdsourced network of over a billion Android devices.

Here’s a closer look at what this update entails and how it can benefit Android users worldwide.

1. Locating Offline Devices

One of the most groundbreaking aspects of the new Find My Device feature is its ability to locate compatible Android phones and tablets offline.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Users can ring their devices or view their location on a map within the app, providing a much-needed solution for finding devices that have been misplaced in silent mode or have run out of battery.

Notably, Pixel 8 and Pixel 8 Pro owners will enjoy an added advantage, as specialized hardware in these devices allows them to be found even if they are powered off or the battery is dead.

Google has released its updated version of the Find My Device network globally.

The upgraded network has improved features and functionalities, enabling users to locate and manage their lost or stolen devices easily.

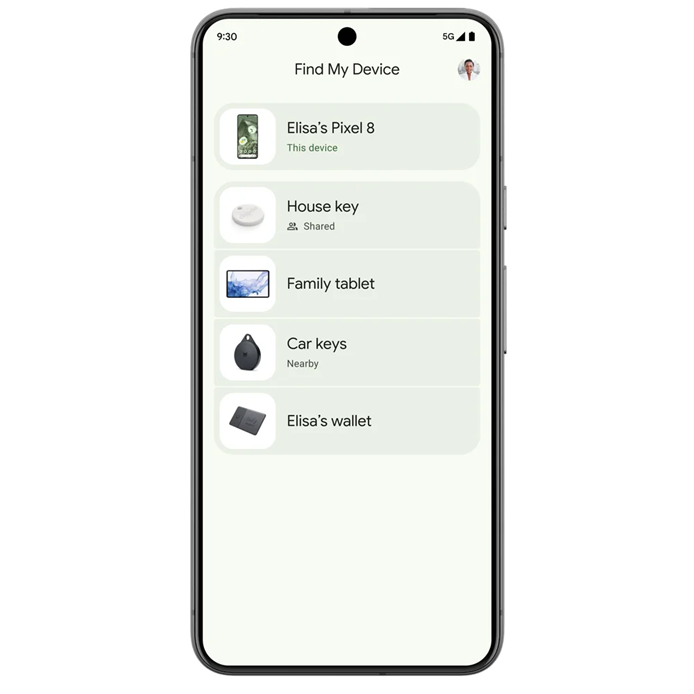
Starting in May, the Find My Device app will support locating everyday items such as keys, wallets, or luggage through Bluetooth tracker tags from brands like Chipolo and Pebblebee.

Source: Google

These tags are designed to be compatible with the Find My Device network and will feature unknown tracker alerts across Android and iOS platforms, enhancing security against unwanted tracking.

Users can expect additional Bluetooth tags from manufacturers such as Eufy, Jio, Motorola, and more later in the year.

3. Finding Nearby Items

The frustration of losing items right under our noses is all too familiar.

To address this, the Find My Device app will introduce a “Find nearby” button, aiding users in pinpointing the exact location of their lost device or everyday items equipped with Bluetooth tags.

This feature is set to search misplaced items more efficiently and less stressful.

4. Integration with Nest for Home Device Pinpointing

Losing items at home is a common occurrence.

The Find My Device app now integrates with Nest devices, offering users a reference point for the proximity of their lost device to home Nest devices.

This integration simplifies locating misplaced items within the home, saving time and reducing frustration.

5. Sharing Accessories with Friends and Family

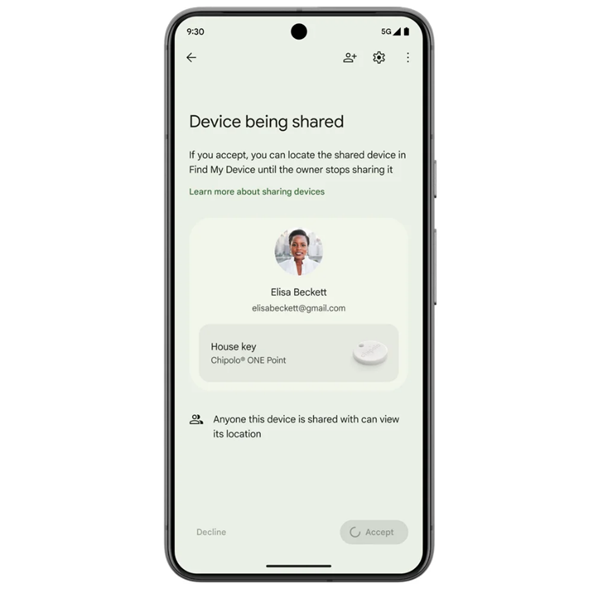
The updated Find My Device app also introduces the ability to share accessories with friends and family.

This feature allows users to keep track of shared items such as house keys, TV remotes, or luggage within the app, making it easier to locate shared items when they go missing.

Source: Google

Google emphasizes that the Find My Device network is secure by default and private by design.

It incorporates multi-layered protections, including end-to-end encryption of location data and aggregated device location reporting.

These features offer users peace of mind by safeguarding their personal information and providing additional protection against unwanted tracking.

The new Find My Device feature is compatible with Android 9 and above devices.

Users are encouraged to explore the full capabilities of the Find My Device network and stay tuned for upcoming software updates that will extend support to headphones from brands like JBL and Sony.

As Google continues to innovate and enhance the Android ecosystem, the Find My Device network stands out as a significant advancement in device security and user convenience.

Secure your emails in a heartbeat! Take Trustifi's free 30-second assessment and get matched with your ideal email security vendor - Try Here


[ad_2]
Source link

Hackers Launch DOS Attacks on Web Servers

0
[ad_1]

Researchers identified a significant vulnerability within the HTTP/2 protocol, potentially allowing hackers to launch Denial of Service (DOS) attacks on web servers.

The vulnerability tracked as CVE-2024-28182 has raised concerns among internet security experts and prompted responses from various technology vendors.

The CERT Coordination Center (CERT/CC) disclosed the vulnerability in a vulnerability note VU#421644.

It has been assigned the Common Vulnerabilities and Exposures (CVE) identifier CVE-2024-28182. This security flaw is particularly worrisome because it affects the HTTP/2 protocol, which is widely used for secure communications on the Internet.

Document
Stop Advanced Phishing Attack With AI

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Stopping 99% of phishing attacks missed by other email security solutions. .

Impact on Vendors and Products

This vulnerability has impacted several technology vendors. Arista Networks, a prominent player in the networking space, has confirmed that some of its products are susceptible to the identified threat.

The company has provided a detailed advisory on the affected products and their impact on its official website.

Fastly, a global cloud platform has also acknowledged the impact of vulnerability on its services.

The company’s statement, dated April 5, 2024, indicates that CVE-2023-45288 is among the affected vulnerabilities. However, Fastly has not yet received a statement from the vendor regarding several other CVEs.

The Go Programming Language is another affected entity, with its net/http and golang.org/x/net/http2 packages being vulnerable due to a lack of a limit on the number of headers for a request.

SUSE, a significant software company known for its Linux distributions, has also reported that its distributions contain affected packages.

The company has committed to shipping updated Go compilers and rebuilt Go packages once available.

The CVE-2024-28182 vulnerability allows attackers to exploit the HTTP/2 protocol by overwhelming a web server with a flood of data, leading to a DOS attack.

This attack can render the server unresponsive to legitimate traffic, effectively taking it offline and disrupting services.

Free Webinarfor DIFR/SOC Teams: Securing the Top 3 SME Cyber Attack Vectors - Register Here.

Responses and Mitigations

Since the vulnerability was discovered, affected vendors have been working on patches and updates to mitigate the risk.

Arista Networks has already provided information on the affected products and their steps to address the issue. Similarly, SUSE has announced plans to release updated compilers and packages to protect against the vulnerability.

The Importance of Timely Updates

The identification of CVE-2024-28182 underscores the importance of timely security updates and the need to monitor cybersecurity threats continuously.

Organizations using affected products are advised to follow the vendor’s guidance and apply necessary patches or updates as soon as possible to protect against potential attacks.

The discovery of the CVE-2024-28182 vulnerability in the HTTP/2 protocol reminds us of the ever-present risks in the digital landscape.

As cyber threats evolve, the collaboration between vendors, security researchers, and the broader cybersecurity community becomes increasingly crucial in identifying and mitigating such vulnerabilities.

Users and administrators are urged to stay vigilant and ensure their systems are up-to-date with the latest security measures.

Secure your emails in a heartbeat! To find your ideal email security vendor, Take a Free 30-Second Assessment.


[ad_2]
Source link

Exploring How Penetration Tests Are Classified

0
[ad_1]
How Penetration Tests Are Classified

In the dynamic and ever-evolving landscape of cyber security defenses, enterprise-grade penetration testing is one of the most crucial practices for organizations to adopt. 

With cyber criminals operating on a far more sophisticated level than ever, continuous and multi-layered security testing, across internal and external infrastructure, is key for enhanced resilience.

However, organizations may find that with such a broad spectrum of expanding threats and technologies, a targeted penetration testing service may be more suitable than others. 

This guide seeks to uncover those points of differentiation, how each type works and why and when they should be performed.

Understanding the different classifications of penetration testing is vital for security analysts to determine the best solution for their organization’s unique requirements.

Exploring The Dynamic Penetration Testing Space

In simple terms, penetration testing (pentesting as the vernacular) refers to exercises and strategies that exploit vulnerabilities and weaknesses in internal/external systems, 5G networks, or assets.

The main quirk of penetration testing solutions is that all exercises are cautiously performed to assess security controls and their effectiveness.

In other words, they act completely ethically despite the possibility that their actions may resemble or be similar to those of a cybercriminal or malicious entity.

Tests may involve using sophisticated social engineering techniques, phishing emails to access critical databases, accounts, and systems, or shared passwords to access sensitive data.

Deploying Email Managed Detection and Response is an essential part of the hardening of the system to prevent the intrusion of all types of attacks, including advanced phishing, BEC, etc.

Some attack methods may be visible and intrusive, while others may be covert and innocuous, bearing some similarities to red and purple team exercises that often take place without the organization’s security or IT staff’s prior knowledge. 

This methodology sounds fairly simple, but not all penetration testing exercises follow the same formula.

There are numerous types of pentesting, including tests on network services, web applications, and physical media that are available for firms to enlist.

What Do Tests Need?

Tests may be performed internally or externally to simulate and validate different attack vectors, with some penetration testing experts – usually outsourced professionals from an approved and verified cyber security provider – having complete, moderate or even zero knowledge of the incumbent environment or systems they are attempting to hack ethically. As such, tests may be deemed anything from black box to white box exercises.

“Scoping plays an essential role in any penetration testing engagement” says Mark Nicholls, Chief Research Officer of the CREST-approved penetration testing company, Kroll. “Our accredited security experts work with our customers to develop a testing program that aligns with the unique requirements of each organization.

Our experts enable businesses in a range of industries to uncover and address complex vulnerabilities across their internal and external infrastructure, whether that includes wireless networks, cloud services, web apps, mobile apps, APIs or network builds and configurations.“

While the end goals of penetration testing services may remain the same (i.e. evaluating specific aspects of an organization’s multi-layered security posture), it’s fair to say that not all tests are created equal. 

“The main goals of any penetration test are tied to our clients’ overarching business strategies,” Nicholls continues. “Many of our clients are regulated by third-party statutory bodies that mandate specific forms of security testing, while others need to build testing programs to support mergers and acquisitions, new application releases or other significant infrastructure changes.

Pentesting Examples

Businesses sector-wide may be facing more red tape and regulatory pressure to deploy specific compliant solutions and robust software that aligns with particular security frameworks. 

An application-specific penetration test can identify flaws and weaknesses in ‌native and server-side code that could expose the vendor and users to attacks.

Analysts then provide a report to the client’s appointed representative (usually a senior business leader) to provide direction and guidance for developers to follow that fixes errors while reducing risk exposure. 

Penetration testing reports can vary drastically, depending on the complexity and setup of a business’s infrastructure, its objectives, the tools, software and endpoints being tested, the perceived value of the assets, and so much more.

So it’s clear that penetration testing differs in approach, strategy, and execution from organization to organization. Broadly speaking, however, it’s important to decipher the sub-types of testing exercises.

Penetration Testing Types

Network penetration testing

Network service testing (or infrastructure testing) focuses on evaluating the security of an organization’s internal and external networks. 

This type of testing aims to identify vulnerabilities that could be exploited in the network infrastructure, such as firewalls, routers, switches, PCs, and other devices connected to a network.

Common network-based attacks include MITM (man in the middle), DNS, IPS/IDS, proxy server, FTP/SMTP and open port attacks, to name just a few.

Tests can be simulated from outside network perimeters or internally as if a perpetrator has already gained a foothold within the network and has moved laterally across the infrastructure.

Social Engineering Penetration Testing

Social engineering attacks target the human element of an organization’s security posture. In an ethical scenario, ‘malicious actors’ attempt to persuade and deceive users into divulging sensitive information, login credentials, and administrator access to critical systems. 

Social engineering pentesting techniques include phishing emails, vishing (voice phishing), tailgating, name-dropping, eavesdropping, and disguising oneself as a known entity or individual on the pretext of legitimacy.

Social engineering tests employee awareness, response time and tactics, and attitudes towards security.

Application Penetration Testing

Application penetration testing evaluates the security of web applications, desktop applications, and browsers and their components such as ActiveX and Silverlight. These complex tests evaluate the endpoints of every web-based application that interacts with – or is used by – the user. 

Software application development relies heavily on defined CI (continuous integration) and CD (continuous delivery) pipelines, in that developers regularly try to enhance and improve codebases.

Agile code deployment is preferred over batch methods, as sandbox environments (i.e. duplicate codebases) can be used to test functionality and usability before live deployment.

Penetration testing would exploit this architecture as part of its continuous code testing.

Client-side Penetration Testing

Client-side penetration testing evaluates the security of client-side components, such as web browsers, browser extensions, and client-side scripts. 

This type of testing aims to identify vulnerabilities that could be exploited through cross-site scripting (XSS), clickjacking, HTML injections, open redirection, malware infections and other client-side cyber attacks.

Wireless Penetration Testing

Wireless networks usually are the single resource that provides network connectivity to various internet of things (IoT) devices in an on-site environment, such as laptops, tablets, smartphones, servers, drives, and so on.

The right wireless pentesting involves identifying and examining the connection security of these devices and the siloed network.

Wireless penetration tests will usually require the complete identification of access points, invalid encryption methods (e.g. HTTPS), monitoring systems in place, misconfigurations, network duplicates, access point protocols (e.g. WPA3) and authentication mechanisms.

Any vulnerable access or unencrypted connection point can be divulged with the help of pentesting.

Physical Penetration Testing

Physical penetration testing assesses the physical security controls and measures in place to protect an organization’s facilities, data centers, and other critical infrastructure.

Physical barriers are often overlooked as far as cyber security is concerned. Still, if a criminal were to gain physical access to servers, drives, and assets, then they could knowingly exploit all connected data.

This testing involves ‌ethical attempts to gain physical access to restricted areas, bypassing security controls, and evaluating the effectiveness of physical security measures such as access control systems, surveillance cameras, and employee awareness.

Black Box, White Box, And Gray Box Penetration Testing

Penetration tests can also be classified based on the level of information provided to the testing team:

1.Black box (external) penetration testing: In this type of testing, the testing team has no prior knowledge of the target environment, mimicking the scenario of an uninformed and opportunistic external attacker.

2.White box (internal) penetration testing: In white box testing, the testing team has full knowledge and access to the target environment, including source code, system configurations, and networks, simulating an insider threat scenario. 

    3.Gray box penetration testing: Gray box testing falls between black box and white box testing. The testing team has partial knowledge of or access to the infrastructure or application, reflecting a scenario where an attacker has gained some information about the target.

    The right pentesting approach can provide valuable insights and direction to help organizations strengthen their security posture and navigate the complex threat landscape with increased confidence and peace of mind.


    [ad_2]
    Source link

    Samsung retakes the top spot from Apple, it’s selling most smartphones

    0
    [ad_1]

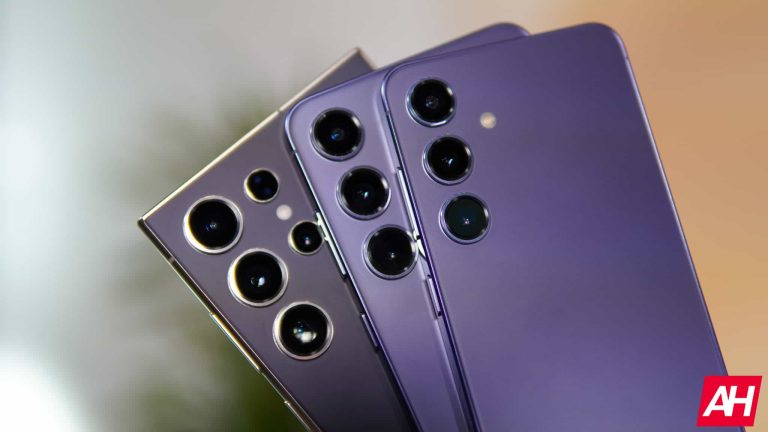
    According to a report shared by The Korea Times, Samsung has managed to retake the top spot from Apple, as the Korean giant is once again selling most smartphones. This information is actually based on info shared by Counterpoint Research, who shared it with The Korea Times.

    Samsung managed to retake its top spot from Apple, it’s once again selling most phones

    As a reminder, Apple managed to take over back in September last year. It seems like the Galaxy S24 series managed to help Samsung to regain its place on the throne, though.

    In February, Samsung sold 19.69 million smartphones and thus captured 20 percent of the market. Apple, on the other hand, sold 17.41 million smartphones in the same period and grabbed 18 percent of the market.

    Analysts say that Samsung enjoyed great sales numbers in the US and Europe, for its new phones. Those are the main reasons it managed to reclaim its throne, at least for now.

    Kim Rok-ho, a researcher at Hana Securities said “It is encouraging that Samsung regained the top spot by achieving a 20 percent global share with a positive response to the Galaxy S24 series in the U.S. and Europe”.

    Samsung did really well in both Europe and the US

    When it comes to the European markets alone, Samsung simply kept the lead, as it never lost it. It managed to grab 34 percent of the market. When it comes to the US, Samsung rose from 20 percent to 36 percent in January this year. Apple’s share fell from 64 percent to 48 percent in the same period.

    Apple managed to trump Samsung last year, looking at a year as a whole. That managed to raise an alarm at Samsung’s camp, to a degree. The Galaxy S24 series reactions were quite positive, it seems.

    Samsung is also planning a big event for July, during which it will launch its new foldables. It’s realistic to expect the company to keep its lead past that point, at least until Q4 this year. It remains to be seen, though.


    [ad_2]
    Source link

    Google is testing a new Short Videos filter for mobile

    0
    [ad_1]

    In case you haven’t realized over the past seven years, the vertically scrolling short video format is pretty popular. TikTok has revolutionized the way we watch content on our phones, and other companies like Instagram, YouTube, Snapchat, Facebook, etc. have followed suit to further strengthen that notion. Well, Google is making it easier to find short-form videos with the Short Videos search filter.

    Google is one of the main companies providing short-form videos because it owns YouTube. The video-sharing service has been pushing YouTube Shorts heavily ever since TikTok took off. In fact, the company announced that a quarter of YouTube shorts creators are receiving money for their videos. As time goes on, we expect that number to grow.

    Google is testing a new Short Videos search feature on mobile

    When you search for something on Google, and there are relevant video results, you’ll see them close to the top of the feed. The videos mostly consist of longer-form videos straight from YouTube, which is no issue. However, if you’re a person who can’t quite spend the time to watch a 10-minute video, and you need information wrapped in a 60-second package, then you will want to watch a short video.

    Well, Google is currently working on a new filter in the Google Search app for mobile. Currently, when you search for something on YouTube, you will see the search bar up top with a horizontally scrolling carousel of chips. These chips are the search filters, and they will show your results accordingly. For example, the Images chip will show you images relative to your search, and the Shopping chip will show you where to buy what you just searched for.

    Well, Google is testing a new Short Videos chip. As you can guess, this will filter your search results to show you a feed of short vertically scrolling videos. You’ll see a two-column feed of the videos. Obviously, since this is powered by Google, you should expect to see YouTube Shorts in the feed. However, it won’t exclusively show Shorts. In the screenshot below, we see that it will feature TikTok videos as well. Since we also see TikTok, we can realistically expect to see Instagram and Facebook Reels along with other short-form videos from across the web.

    This is only on mobile… for now

    Right now, we only have information on this tool coming to the mobile version of Google. However, it seems like Google will launch this feature on the web at some point. We will just have to wait for information on that to come out.


    [ad_2]
    Source link