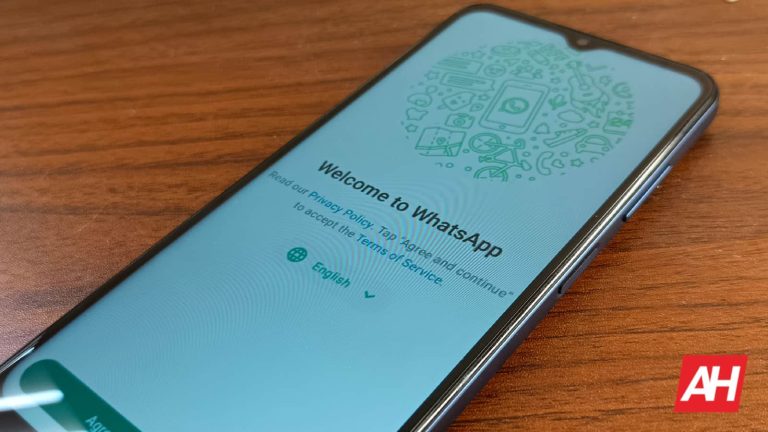
WhatsApp is testing status update notifications

0
[ad_1]

In WhatsApp, you have the ability to make status updates, and they’re a great way to clue people in on what’s going on in your life. Most of your biggest fans and closest friends will want to know what you have going on, so this potential feature will be perfect for them. According to a new report, WhatsApp is testing status update notifications.

Right now, WhatsApp is testing this feature. So, you’re going to want to take this news with a grain of salt. It was discovered in the WhatsApp beta for Android version 2.24.8.13. We don’t know exactly when/if WhatsApp is going to push this feature to the public. So, we are going to have to wait to see.

WhatsApp could bring status update notifications

Right now, we are still pretty much in the dark about how this new feature could function. The folks at WABetaInfo previously discovered a feature in the WhatsApp Android beta version 2.24.6.19. This alluded to a feature that will let you manually send notifications to specified contacts when you post a status update.

In the latest beta, it appears that WhatsApp is going to further refine this feature. Looking at the screenshot below, it seems that you will receive a notification if there is an unseen status update from one of your contacts. We’re not quite sure if you will receive this notification after some time has passed since the status update. In fact, we don’t know what will trigger the notification to be sent to you.

Whatsapp status mention notification

As noted by WABetaInfo, it’s possible that you will receive notifications when one of your Favorited contacts posts a status update. So, it will be easier for you to know what’s going on in their lives. This seems like the kind of small quality-of-life change that won’t greatly affect the WhatsApp experience. However, it will definitely make it a little bit better. This is similar to the minimal aesthetic that WhatsApp is testing.


[ad_2]
Source link
Politicians prefer TikTok amid security concerns

0
[ad_1]

Politicians seem to hate TikTok because of alleged security risks. However, these very politicians seem to prefer TikTok, claims a report by Reuters.

TikTok is undoubtedly one of the biggest social media platforms. Hence, it’s no wonder its popularity could be employed and perhaps exploited by politicians. In other words, despite berating TikTok in the parliament, lawmakers find it irresistible simply because the ultra-short video-sharing platform has become a social hub for millions of young voters.

TikTok remains a security concern and may influence elections, politicians fear

American legislators are on the verge of banning TikTok. A bill discussing the TikTok Ban recently passed with bipartisan support. It will now head to the US Senate.

Incidentally, US President Biden has already said he would sign the bill. As a consequence, TikTok’s parent company, ByteDance, may be forced to sell TikTok. If ByteDance doesn’t comply, the company’s apps may be banned from the US app stores and web hosting services.

TikTok is facing heat in multiple countries, including the EU, primarily over security and data management practices. Germany’s security agencies recently warned ByteDance could be sharing TikTok data with China’s government.

Additionally, several legislators have claimed that TikTok is so powerful, and its use is so widespread, that it could be used to influence users and voters. Needless to mention, politicians have raised similar concerns about Facebook and Twitter too. But these politicians want to utilize these very platforms.

European politicians prefer TikTok despite security risks

TikTok continues to remain a popular mass-media platform, especially among youngsters. Politicians prefer to use TikTok to gain inroads with the masses. What is concerning is that these very lawmakers have been discussing ways and means to ban, regulate, or limit TikTok.

TikTok is highly popular in the 16 to 25 age group. It has many first-time voters and politicians eager to tap into this promising vote bank. It is important to note that 16-year-olds in Germany can vote in the upcoming June European elections.

Simon Harris, Ireland’s prime minister-in-waiting has been dubbed the “TikTok Taoiseach”. French President Emmanuel Macron has amassed 4 million followers on TikTok. Needless to say, TikTok is a surefire way to reach out to the younger generation.

TikTok’s owner ByteDance continues to deny that its product is used for spying. Similarly, the Chinese government has also denied all allegations. Last year, TikTok launched a site to store European users’ data in Dublin and hired a third-party security firm to monitor data flows to address security and data management concerns.

It is worrying to note that despite security concerns, politicians prefer to use TikTok and continue to do so. It appears their thirst to connect with young voters outweighs any potential risks.


[ad_2]
Source link
Google Messages will soon start to warn you when tapping on links sent by unknown senders

0
[ad_1]
If you’re getting tired of annoying spam texts and shady links that often try to lure you into clicking them on your Messages app, you may be in luck. Found hidden in the code are signs that Google is stepping up security in its Messages app to give users an extra layer of protection.
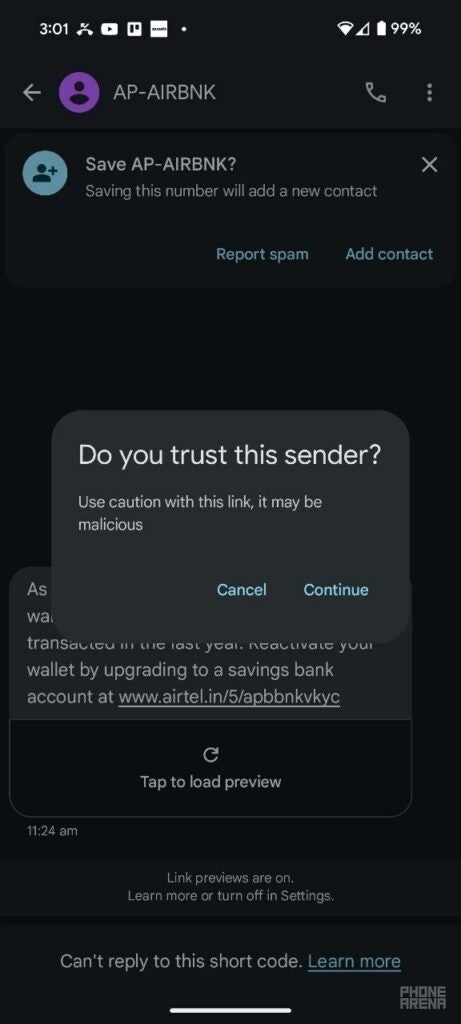
According to the folks at PiunikaWeb, a new pop-up warning system could be coming soon to Messages. This feature is designed to make you think twice before clicking on links in messages from people you don’t know, whether they’re coming through RCS or standard old SMS.

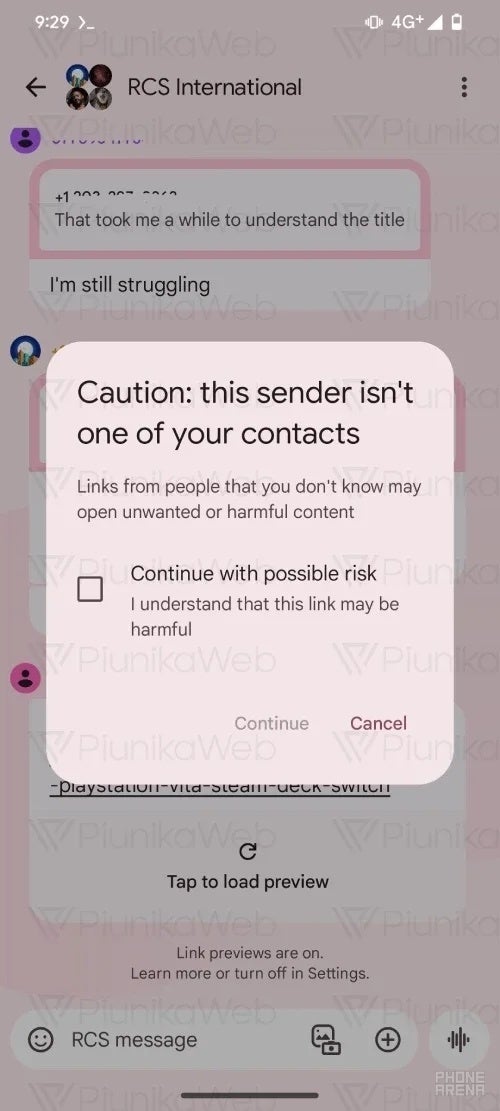
Imagine this: you get a text from an unknown number with some enticing link. Curiosity takes over, and you go to tap it. This new feature will immediately pop up a warning that says something like this: “Caution: this sender isn’t one of your contacts.” To open that link, you have to check a box acknowledging that there could be risks and then hit “Continue.”

Image Credit: PiunikaWeb

The idea is to make you think twice before clicking on links sent by senders you don’t know. This would hopefully snap us out of autopilot mode and make us consider twice whether those links are worth exploring.

Google Messages already has some link warnings, but this new feature looks more robust. Currently, it’s easy to breeze past those messages. This new system adds a little friction, forcing you to stop and think before taking a potentially risky action.

This feature popped up in a beta version of Google Messages, so we might see it rolling out to testers before landing in the main app. It’s yet another sign, on top of Google recently blocking RCS on rooted phones, that they’re taking security in the Messages app more seriously — and just in time for RCS to roll out for iOS devices, potentially giving the Google Messages app on Android a boost over third party solutions like WhatsApp.


[ad_2]
Source link
Google launches the Find My Device network

0
[ad_1]

Losing your device can be a scary thing, especially if you lose it in a public place. This is why Google has its Find My Device feature that lets you locate your device based on its most recent location. Well, according to a new report,  Google is taking this a step further, and it just launched its new Find My Device network.

For a while, Google had its Find My Device feature. You will either use a standalone app or the website to track the location of Android devices you’ve logged into with your Google account. It will show you the phone’s last recorded location with pretty good accuracy. It even allows you to make that device ring.

Google launched its Find My Device network

While the above-mentioned feature is convenient, it’s very different from the newly launched Find My Device network. The former requires that the lost device be connected to the internet. This will allow Google to tap into its location and let you know where it is. If your device is not connected to the internet, then Google will use its last recorded location, which is less accurate.

However, the Find My Device network is much more convenient and much more accurate. Much like Apple’s Find My network, Google’s implementation will use other Android phones as the network. These devices will connect and communicate with other devices seamlessly via Bluetooth. So, if you left your phone at a coffee shop, and you’re trying to locate it, other devices in the coffee shop will be able to communicate with your phone and get a bead on its location. The surrounding phones will then communicate with Google where your phone is.

This is very convenient because this means that the feature will still be able to work even if your phone is not connected to the internet. It just needs to have Bluetooth enabled. This is why Google is testing a Bluetooth Auto-on feature in Android 15.

Availability

Starting Monday, Google will launch the Find My Device network in the US and Canada. This will encompass over a billion Android devices, and it’s only going to expand as time goes on.

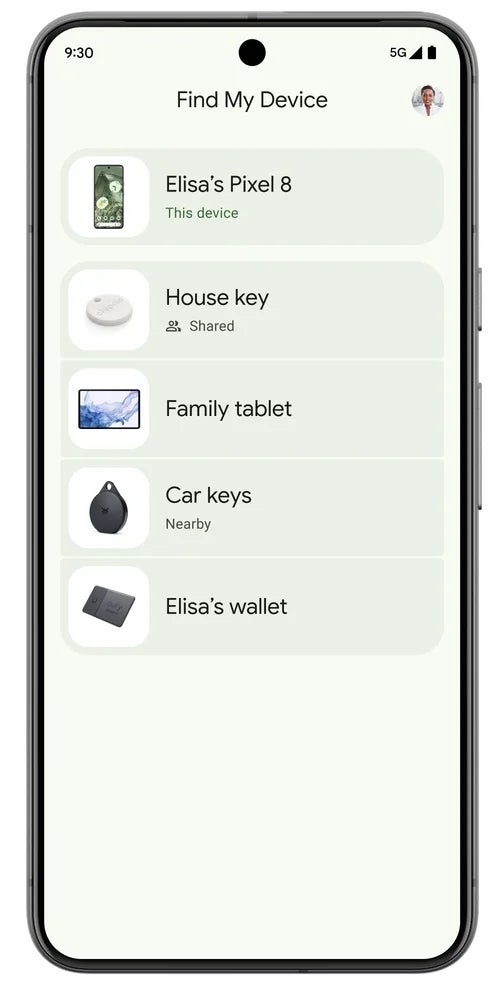
In order to use this feature, you will have to open the Find My Device app. Once you see the lost device listed, you will simply have to tap the “find nearby” button. What’s also neat is that, if you have Google Home devices, the network will show your device’s proximity to them.

That’s not all

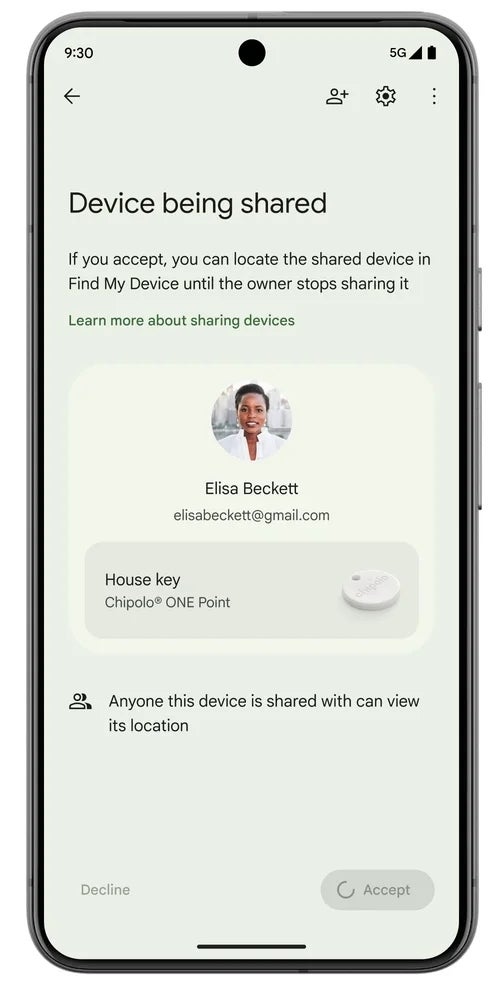
Along with this news, we also got word that several manufacturers will be manufacturing Bluetooth tags. These will be similar to Tile Bluetooth tags. You’ll attach the tag to an item that you want to keep track of. Then, using the Find My Device network, you will be able to pinpoint that item’s location. They’re perfect for locating non-Bluetooth-connected devices, keys, your wallet, etc.

Starting in May, Chipolo and Pebblebee will offer their own Bluetooth tags to purchase. However, it will not stop there. Companies like Motorola, Eufy, and Jio will also offer their own tags. This is another feature that will help bring the Android ecosystem one step closer to the seamless integration that Apple users enjoy


[ad_2]
Source link
TSMC to get $6.6 billion grant for U.S. expansion

0
[ad_1]

A major announcement was made today by the United States Commerce Department. The announcement reveals an unprecedented financial commitment to support semiconductor production within the country. Eventually, this strategic decision entails a considerable $6.6 billion subsidy granted to Taiwan Semiconductor Manufacturing Company (TSMC), a key chip supplier for tech giant Apple. Certainly, by leveraging the CHIPS and Science Act, this initiative marks a crucial advancement in enhancing the United States’ semiconductor manufacturing capabilities.

Accompanying the announcement, the White House detailed the subsidy specifics. TSMC is set to receive a significant cash injection to boost semiconductor production in Phoenix, Arizona. On top of that, the chipmaker will also gain access to $5 billion in loans and qualify for an investment tax credit of up to 25% of capital expenses. These attractive incentives are geared towards driving substantial growth for TSMC in the United States.

Unprecedented investment in U.S. semiconductor industry

TSMC has made a decision to invest $25 billion, marking a significant turning point in the U.S. semiconductor industry. This investment will bring their total investment in the sector to an unprecedented $65 billion. Hence, the investment makes it the largest foreign direct investment in a new U.S. project in history.

TSMC’s bold vision goes beyond just financial commitments. The chipmaker is planning to build a third fabrication plant in Arizona by 2030, strengthening its presence in the region. The first TSMC plant in Arizona will start making innovative 4nm chips next year. The second plant, originally designed for 3nm chip production, will also produce 2nm chips by 2028. The third plant will focus on producing 2nm chips, positioning itself as a leader in cutting-edge semiconductor technology. This marks an exciting step towards future technological advancements.

Impacts on Apple and the supply chain

The ramifications of this massive investment go far beyond TSMC and the semiconductor sector. Notably, Apple is set to benefit from TSMC’s increased chip production in the US. Nevertheless, at present, Apple’s most advanced chips are made in Taiwan utilizing TSMC’s state-of-the-art 3nm process. Consequently, the possibility of making chips, including stronger versions, within the U.S. marks a big shift in the company’s supply chain.


[ad_2]
Source link

Google’s new “Find My Device” network goes live, third-party Bluetooth tag support coming in May

0
[ad_1]
The highly anticipated Google Find My Device network is finally live in the U.S. and Canada, as announced today by the company via a blog post. Now, if you happen to misplace your phone, keys, or even your headphones, Google’s got your back.

Find My Device works by using the power of the Android network — created by a billion Android devices and the magic of Bluetooth. When enabled, your device will be anonymously and securely tracked by other Android devices that are nearby. This means that if you lose your phone, you can use another device to log in to your Find My Device account and see its location on a map. Here’s a quick rundown of the new features:


  • Offline Finding: The Pixel 8 and Pixel 8 Pro get the full offline experience, so now you can find them even if they’re offline or the battery’s dead.
  • Bluetooth Tag Support: Starting in May, tags from companies like Chipolo and Pebblebee will be trackable within Google’s system, with more brand support coming soon.
  • Locate Nearby Items: Zero-in on lost devices with a “Find Nearby” button. Perfect when your phone’s fallen behind the couch.
  • Nest Integration: Get an idea of how close lost devices are to your Nest devices at home.
  • Sharing Made Easy: Share digital keys, remotes, and more with people you trust to help find lost items.
  • Headphone Support: Headphones from JBL, Sony, and others will soon work with the network after a simple software update.

Image Credit: Google

Google’s built a crowdsourced network using a ton of Android devices worldwide. This upgraded Find My Device Network works on devices running Android 9 or later. So, if you’ve got a relatively recent Android phone, you should be good to go.

In the announcement, Google reiterated the fact that your own Android phone helps out the Find My Device network in the background without compromising your privacy. Google states that the network uses end-to-end encryption of your location data and first-of-its-kind aggregated location reporting, which makes unwanted tracking to a private location more difficult. This was the challenge the company was working on along with Apple before officially launching the service after unveiling it last year. With iOS 17.5 implementing these anti-stalking security measures and Google’s updated Find My Device network launching with these protections as well, both companies are now working together to keep smartphone enthusiasts secure.

[ad_2]
Source link

Galaxy A53 and A13 grab Samsung’s April 2024 update in the US

0
[ad_1]

Samsung‘s April 2024 security patch is quickly making its way into more Galaxy devices. Shortly after the Galaxy Z Fold 5, Galaxy Z Flip 5, Galaxy Tab S9 series, and Galaxy A52, we can confirm its availability for the Galaxy A53 and Galaxy A13. The latter two models are picking up the update in the US, while it is an international release for others. The Galaxy S24 series has already received the April SMR (Security Maintenance Release) globally.

April update available for the Galaxy A53 and A13 in the US

The Galaxy S24 series was the first to receive Samsung’s latest security update. The company began the rollout last month with some camera fixes in tow. The Korean firm waited a while before expanding the new SMR to other models, likely because it got busy with the One UI 6.1 update. However, the delay might have ended as the latest security patch is available for several Galaxy smartphones and tablets today.

As of this writing, the April SMR is available for the carrier-locked variants of the Galaxy A53 and Galaxy A13 on Verizon’s network in the US. The new firmware build numbers for the duo are A536VSQSADXC3 and A135USQS7DXC6, respectively. Samsung should soon roll out the update to the devices on other networks and gradually expand it to the unlocked units and international versions.

Note that we are talking about the 4G-only Galaxy A13 here. Samsung has yet to release the April update for the 5G version of the phone. Don’t expect anything big here, though. The update is all about security enhancements. The April SMR for Galaxy devices patches more than 40 security vulnerabilities, some of which are labeled as critical fixes by Samsung and Google. Watch out for a notification about the update in the coming days.

These Galaxy phones should get One UI 6.1

Samsung recently updated the Galaxy S23 series, Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Tab S9 series to One UI 6.1, which debuted with the Galaxy S24 series. The company will gradually push the new One UI version to more devices. The Galaxy A53 and Galaxy A13 should also get it, though they may be quite low in Samsung’s priority order.

These A series phones may also miss out on most of the new AI features found in One UI 6.1. There should still be plenty to be excited about. We will let you know when One UI 6.1 starts rolling out to more devices.


[ad_2]
Source link

Canada invests $2.4 billion to boost domestic AI capabilities

0
[ad_1]

The Canadian government has unveiled a new plan to pump $2.4 billion into artificial intelligence (AI) development and research over the next few years. Prime Minister Justin Trudeau announced the funding package. The government aims to advance Canada’s capabilities in AI and realize the full economic potential of the technology.

Most of the investment, $2 billion, will be used to boost high-performance computing infrastructure and resources. It can be used by Canadian AI researchers and startups. Currently, many rely on cloud services owned by foreign companies outside the country’s borders.

The new Sovereign Compute Strategy will seek to build secure, domestic computing capabilities that keep citizens’ data in Canada. According to Deputy Prime Minister Chrystia Freeland, this approach can improve national security by preventing foreign access to data.

Canada’s massive AI funding to drive innovation and safety

In addition to improved computing, $200 million will go to regional agencies to support the growth of early-stage AI companies in key industries. Healthcare, agriculture, clean tech, and manufacturing are just a few of the sectors that will benefit from incentivized AI integration. The goal is to foster homegrown innovation and ensure that economic opportunity extends to all regions.

Recognizing the rapid progress of generative AI, the government has committed $50 million to a new Safety Institute. Its researchers will work to proactively address potential downsides such as unintended biases, privacy violations, or dangerous applications. Another $5.1 million has been set aside to create an Office of the AI Commissioner to provide guidance, oversight, and accountability.

The bill has been in committee since September 2023, according to Trudeau. “We want to help companies adopt AI in a way that has a positive impact for everyone,” he explains. By funding this initiative, Canada is positioning itself to be a leader in the rapidly evolving AI industry.

Other major countries that are developing regulations around AI technology include the United States and China. However, all of these regulations remain speculative. AI technology is evolving rapidly, so it’s not surprising that it’s taking a long time to develop appropriate laws.


[ad_2]
Source link

AI-As-A-Service Providers Vulnerability : Cross-Tenant Attacks

0
[ad_1]

The fast acceptance of AI has serious security issues, as this necessitates strict security measures to be put in place for the protection of sensitive information within shared cloud AI infrastructure.

Wiz Research, a cybersecurity firm, in collaboration with AI-as-a-Service firms, recently discovered some common security flaws across the sector that could expose users’ personal data and models.

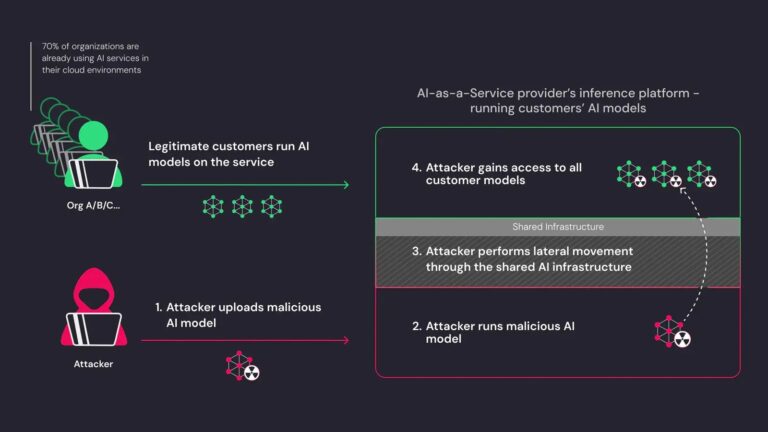
The implications of these findings have to be taken seriously considering AI services are now available in more than 70% of cloud environments.

AI-As-A-Service Providers Vulnerability

Malicious models pose a severe threat, enabling cross-tenant attacks and access to millions of private AI models and apps within AI-as-a-service providers. Wiz uncovered critical risks in Hugging Face’s environment:-

  • Shared inference infrastructure takeover risk via untrusted pickle-serialized models with potential remote code execution payloads.
  • Shared CI/CD takeover risk through malicious AI applications compromising the pipeline for supply chain attacks.

When securing AI/ML systems, several factors, such as the AI model being used, the application code that uses the model, and the inference infrastructure deploying the model, must be taken into account.

AI-As-A-Service Providers Vulnerability (Source -Wiz)

Malicious people can use various methods to attack each component, including malicious input for models, insecure application code that processes the results of a model, and pickled models that compromise inference infrastructures. 

This involves downloading unreliable AI models, similar to embedding untrustworthy codes into applications.

Hugging Face research team focused on isolation flaws in AI-as-a-service setups, examining the company’s major products: 

  • Inference API
  • Inference Endpoints
  • Spaces
Inference API (Source -Wiz)

However, Hugging Face’s analysis and warnings of insecure Pickle-based PyTorch models still allow inferring potentially malicious models. 

On the other hand, researchers developed a harmful PyTorch model that runs arbitrary code when loaded and remotely executes code by using Inference API to interact with it.

Researchers achieved shell-like functionality by hooking into Hugging Face’s post-deserialization inference results management code.

This demonstrates how untrusted AI models in shared compute services are at great risk due to inadequate isolation.

As a result of gaining a reverse shell through the Hugging Face Inference API, researchers realized that they were inside one pod within an Amazon EKS Kubernetes cluster.

They exploited common misconfigurations like querying the node’s IMDS to get the node role and cluster name via AWS permissions.

With node role privileges, these people got access to pod information as well as secrets that brought to light the risks of lateral movement and data leakage.

Moreover, it also executed code by using a malicious Dockerfile in Hugging Face Spaces, which demonstrated potential supply chain attack vectors caused by network isolation issues in the container registry. 

Researchers urged to allow IMDSv2 with Hop limits, apply tighter access controls, and impose authentication measures for securing shared AI environment.

Secure your emails in a heartbeat! Take Trustifi free 30-second assessment and get matched with your ideal email security vendor - Try Here

[ad_2]
Source link