The Legacy of a Security Breach

0
[ad_1]
The Legacy of a Security Breach
Keir Finlow-Bates
This article was authored and contributed by Keir Finlow-Bates, a passionate blockchain enthusiast and technologist.

Today over at Resonance Security I am going to look at one of the more unusual ways in which your approach to computer security can lead to an increase in public awareness of your company.

There are many motivations for starting a company: becoming wealthy, doing something interesting and useful, and leaving some kind of legacy or mark on history are three of the main ones that spring to mind.

About that legacy: imagine having the name of your corporation attached to a file representing one of the most significant hacks of the 21st century!

That’s quite notable, but probably not what the founders of one particular company were looking for with their startup.

We won’t rock you

In the middle of the 2000s, RockYou, Inc. was doing well as a widget-maker for social media companies like MySpace and Facebook. However, back in 2009, it suffered a data breach in which a hacker discovered an SQL database server with an unpatched ten-year-old bug, the database containing over 32 million usernames and passwords for user accounts.

That’s right — 32 million usernames, and their associated passwords. For comparison, that’s about 10% of the active monthly users that Facebook had at the time.
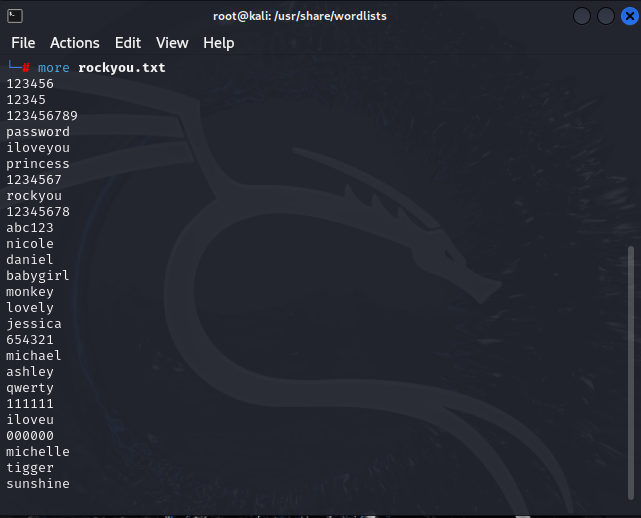
The passwords were stored in plain text.

Mud on your face, big disgrace

Not only did RockYou initially fail to notify their users, but it subsequently released a falsified official statement claiming that the breach was less severe than it was.

To be clear: it was a very, very serious breach.

A decade and a half ago, people were far worse at password security than they are now. Password managers were almost unheard of, for some unexplained bizarre reason some sites blocked the use of password managers for unspecified “security reasons”, and two-factor authentication was pretty much only affordable and available to business users.

Because people were told not to write down their passwords, this meant that most of the leaked credentials were being used on other websites. After all, who in their right mind is going to memorize twenty or thirty different random passwords? As a result, sites such as banks, online stores, health databases, social media, supposedly private online journals, and online games held accounts using the same passwords.

The legacy

For years the full list of RockYou passwords has been available to download by anyone. It is typically found in a file called rockyou.txt , and there are plenty of GitHub repositories out there where you can find it.

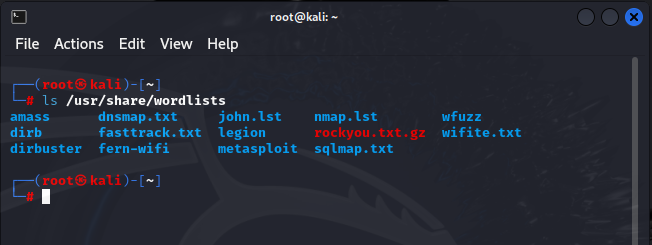
In Kali Linux, a Linux distribution designed and produced specifically for penetration testing, the RockYou text file is included during the installation by default.
Conclusion

Just imagine — with a little bit of security carelessness, you too can take your modestly successful company and in the process of destroying it, allow its name to live on forever.

Have we learned anything since 2009? Not always.

For example: in 2017 it was revealed that an old social media site called LiveJournal, dating back to the 90s (but still running to this day), suffered a breach in which 26 million unique usernames, email addresses, and plaintext passwords were extracted. It took them until 2019 to admit to the breach.

That’s right — passwords were still being stored in plaintext in 2017, and I would bet good money on there being more sites out are doing the same, even though we are a decade and a half on from the original RockYou breach.

I predict that the leakage of passwords will only end once we stop using passwords, and start using improved systems such as security keys and self-managed identity for our authentication systems.

In the meantime, you have to assume that any password you provide to a website will eventually be leaked, therefore:

  • use a password manager to generate long, random, unique passwords for your accounts,
  • protect access to the password manager with two-factor authentication, and
  • make sure the password you use for your password manager has never been used anywhere else.

Post-script

Don’t run off and look for a website that allows you to enter your password and see if it was ever revealed in a breach! I can guarantee it will be a phishing site. Instead, I recommend HaveIBeenPwned, where you can type in your email address, and retrieve a list of the companies and websites that have managed to leak your credentials to the dark web through bad security practices. Another option is the Resonance Data Leak Detector, which monitors if your credentials have been leaked 24/7 and automatically notifies you.

About Resonance Security

Resonance Security is a curated platform for end-to-end cybersecurity products and services. It functions as a concierge for your organization’s end-to-end cyber-security needs, aggregating valuable security offerings into one platform to spread awareness on what it takes to secure your technology stack end-to-end.

About the author

I’m Keir Finlow-Bates, often known as Blockchain Gandalf, and am primarily a blockchain researcher and inventor. I started on this journey in late 2010 by examining the original Bitcoin code, and have been obsessed with blockchain ever since.

I am also the author of two books on the topic: Move Over Brokers Here Comes The Blockchain, explaining blockchain, and Evil Tokenomics, illustrating through practical examples how web3 scams work. You can find more at my website: Thinklair.com

  1. The Forgotten Victims of Data Breach
  2. Solving the Cyber Security Problem: Mission Impossible
  3. Will good prevail over bad as bots battle for the internet?
  4. If a Cyber Security Report Falls in a Forest, Is Anyone Listening?

[ad_2]
Source link

Apple’s App Store opens the door to classic game emulators

0
[ad_1]

In recent months, Apple’s tight grip on its App Store policies has begun to loosen. Following regulations from entities such as the EU, the company has just updated its App Review Guidelines. It has further opened the door to retro game emulators and ROM downloads.

For the first time ever, emulators will be allowed on the App Store. This change means that iOS users may soon be able to play their favorite classic games from systems like Nintendo and Sega systems directly on their iPhones and iPads. However, Apple has also established many strict rules. Developers must ensure that any games they distribute are done so legally to avoid potential copyright issues with abandonware titles.

Some caution remains, though. In its guidelines, Apple lumps emulators in with mini apps and plugins. That means they must use HTML5 rather than native system APIs for things like hardware acceleration. This could severely limit the types of emulators that come to the platform. Consoles like the PlayStation may not emulate well without low-level access.

New App Store policy allows emulator apps, but with restrictions

Developers will have to work within Apple’s guidelines for what constitutes a properly “hosted” emulator. And, as with past reversals, Apple retains full control over the App Store ecosystem. If emulators are poorly implemented or violate other policies, a crackdown could always occur.

“You are responsible for all such software offered in your app, including ensuring that such software complies with these Guidelines and all applicable laws,” Apple writes in its App Review Guidelines.

As is often the case with Apple’s policies, the implementation and interpretation of these new guidelines will likely set a precedent that will shape the future of emulator apps on the App Store. The gaming community will be watching closely as developers begin to navigate these new waters, eagerly anticipating the arrival of their favorite classic games on iOS devices.


[ad_2]
Source link

AutoPro X accessory will bring Samsung DeX to your vehicle

0
[ad_1]

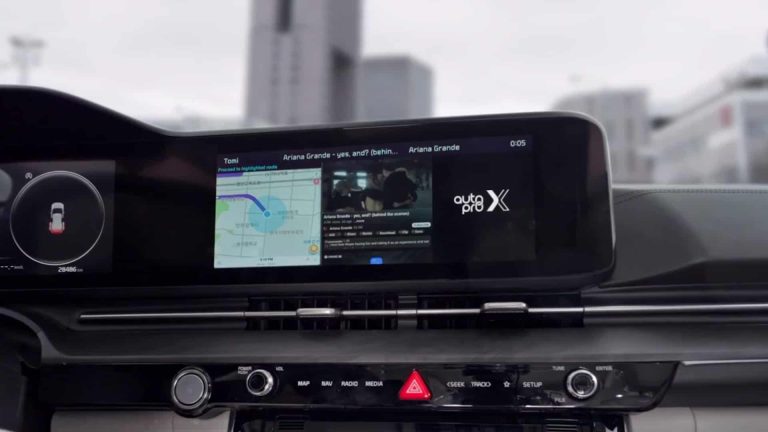
Have you ever wanted to have the capabilities of Samsung DeX in your car? Well, the AutoPro X accessory promises to make this possible. This is a device that enables the DeX interface and functions on your vehicle’s screen. Basically, like an Android Auto adapter, but specifically intended to use DeX.

For those who don’t know, Samsung DeX is a feature that offers a pseudo-desktop experience. It works by connecting a compatible Galaxy device to an external monitor or display. At first, the system worked only by cable, but then Samsung introduced Samsung DeX Wirelessly to offer more possibilities. This feature inspired the creation of similar ones, such as Motorola Ready For. Even Android 15 could natively bring something similar.

Samsung DeX experience in your vehicle will be possible thanks to AutoPro X

Returning to the AutoPro X accessory, it was launched through a Kickstarter campaign. There seems to be a lot of interest in a device of this type, so it didn’t take long for the team behind it (Mayton) to reach 100% of their funding goal.

One of the promises of AutoPro X is that you won’t need cumbersome configurations. Everything should be as easy as connecting it to your vehicle’s screen via USB. Another advantage of using this accessory is that you don’t have to rule out Android Auto since it also integrates the Google OS for cars. This will give the user great versatility in choosing what type of UI and functionalities they want to use in their vehicle.

DeX enables better multitasking

But what is the difference between Samsung DeX and Android Auto? Basically, the DeX UI is adapted to the style of a computer. This means that it is designed to make better use of keyboards and mice, although you can also use it by touching the screen. In addition, it enhances multitasking with the possibility of having multiple apps on the screen at the same time. Multitasking in DeX allows you to distribute apps in different segments of the screen or one on top of another.

Currently, we are about a week and a half away from the official launch of the AutoPro X accessory. It will be interesting to see the public’s response to this product and if it also inspires the arrival of other DeX-based accessories for cars.


[ad_2]
Source link

WhatsApp to roll out new photo library shortcut for faster sharing

0
[ad_1]
WhatsApp keeps rolling out new features regularly, and now it seems it is working on making it easier for everyone to open and share photos. According to WABetaInfo, a reliable source for WhatsApp updates, the Meta-owned messaging app is widely releasing a feature to quickly open the photo library.
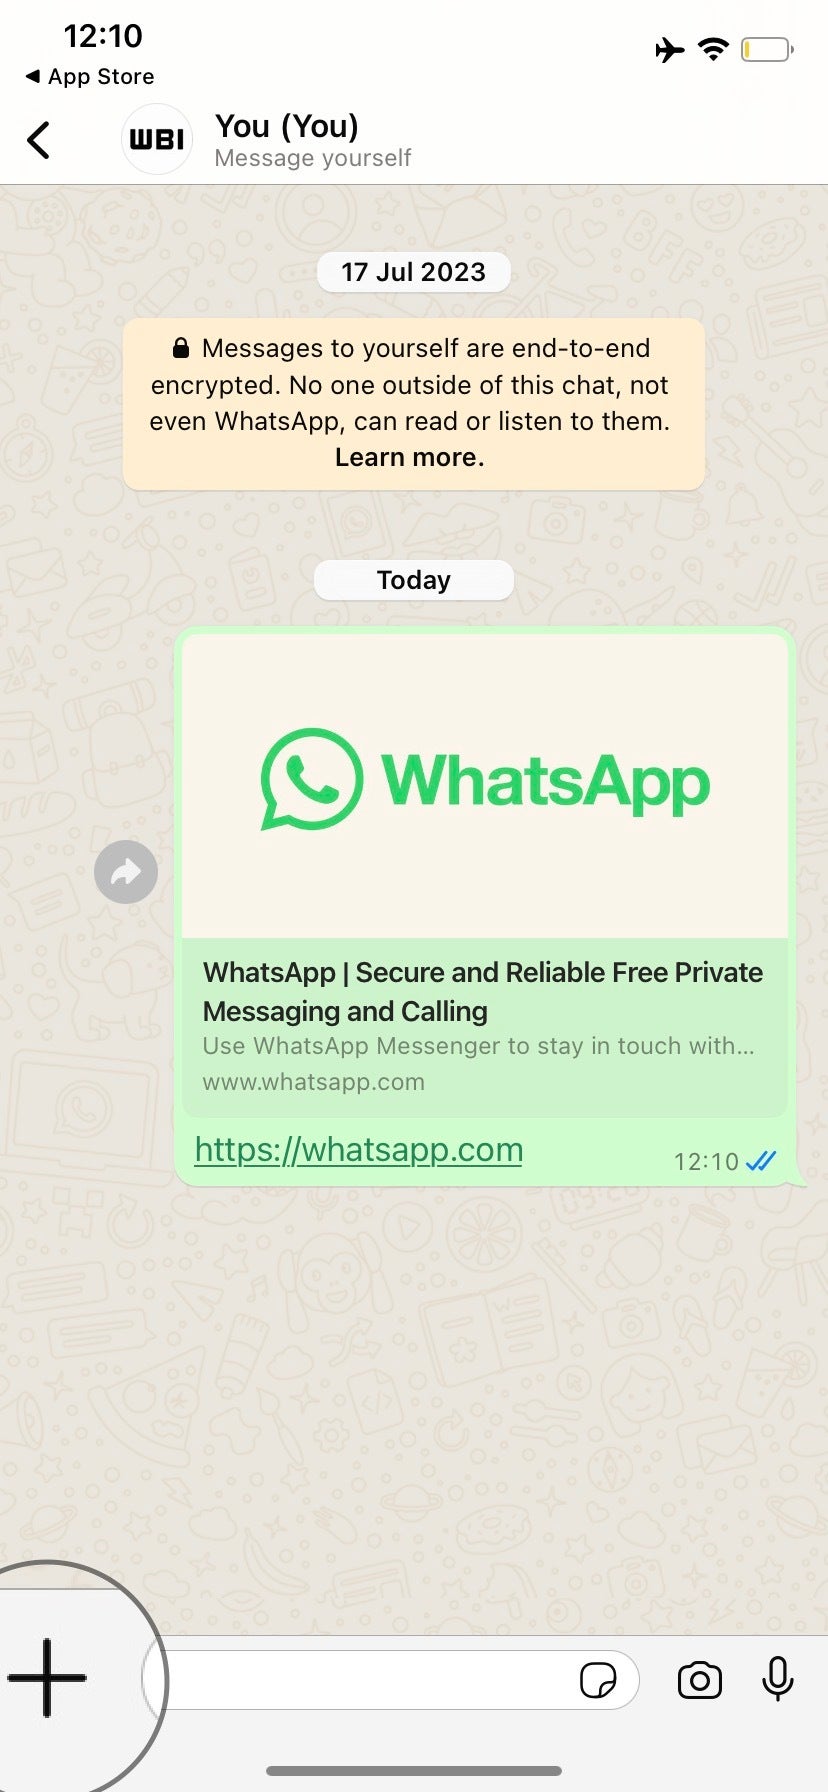
While the official changelog doesn’t offer much insight, the latest version of the iOS app, 24.7.75, has unveiled that this feature is now rolling out to all. Essentially, it’s a handy shortcut for swiftly accessing the photo library. Users can simply long-press the attach button within the chat bar, saving time by directly navigating to their photo library without any extra steps.

If you haven’t got this feature yet, keep in mind that it may be gradually rolled out to some accounts over the next few weeks, even though it’s not mentioned in the official changelog. As mentioned, the Meta-owned app frequently introduces new features, so installing all the latest updates will ensure you have access to the latest features and enhance your overall user experience.

On a different note, WhatsApp is gearing up to introduce a picture-in-picture option for videos. This means you will be able to watch videos while browsing through multiple chats or other parts of the app. Additionally, the app is set to receive a series of little tweaks, all aimed at enhancing the user experience.

As an example, WhatsApp is currently testing a redesign for its calling screen to make it easier for users to know where to tap to hang up. Moreover, a new simplified “Like” button for reacting to status updates could be introduced in a future app update.


[ad_2]
Source link

Veterinary Giant IT System Attacked by Hackers

0
[ad_1]

CVS Group, a leading veterinary service provider, has confirmed that it fell victim to a cyber-attack involving unauthorized access to a segment of its IT systems.

The company’s security protocols swiftly detected the breach, prompting an immediate response to contain the threat.

Upon discovering the breach, CVS Group decisively isolated the compromised systems.

The company temporarily shut down its IT systems to prevent further unauthorized access, adhering to its emergency response plan.

While effective in halting the attack, this necessary action has caused significant operational disruptions over the past week, particularly affecting the UK operations.

Specialist Intervention and Authority Notification

CVS Group has enlisted the expertise of third-party cybersecurity consultants to conduct a thorough investigation into the nature and scope of the incident.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

The company has also proactively informed the relevant authorities, including the Information Commissioner’s Office, due to the potential risk of compromised personal information.

The London Stock Exchange has published a blog post reporting a cyber attack on the IT system of CVS Group, a veterinary giant.

Impact on Services and Recovery Efforts

Despite the challenges posed by the cyber incident, CVS Group has managed to maintain high levels of clinical care across most of its practices.

IT services have been securely restored across most of the company’s locations.

However, the enhanced security measures have led to some systems operating less efficiently than before, which may continue to affect operations for the foreseeable future.

According to a tweet by Reuters, CVS Group, a significant player in the veterinary industry, has been hit by a cyber attack targeting its IT system.

Due to the cyber attack, CVS Group is transitioning to cloud-based practice management systems and IT infrastructure.

This strategic move aims to strengthen security across the company’s operations and improve operational efficiency.

Nonetheless, the transition will impact operations for several weeks as the company focuses on maintaining clinical care while enhancing security.

Ongoing Forensic Analysis and Commitment to Security

The forensic analysis of the cyber incident is still underway, and CVS Group is committed to taking all necessary measures to safeguard its business and client data.

The company assures that it will provide further updates as the situation evolves and more information becomes available.

CVS Group’s experience reminds us of the ever-present threat of cyber attacks on businesses of all sizes and sectors.

The company’s prompt and effective response highlights the importance of a robust cybersecurity strategy and response plan.

As CVS Group continues to recover and strengthen its IT systems, the veterinary community is watching closely, recognizing the critical need for cybersecurity vigilance to protect sensitive data and maintain operational integrity.

Secure your emails in a heartbeat! Take Trustifi free 30-second assessment and get matched with your ideal email security vendor- Try Here


[ad_2]
Source link

Spotify’s AI Playlists feature lets you create playlists using prompts

0
[ad_1]

Do you find it difficult to discover songs that match your current mood? Well, Spotify AI playlist feature can help you find the perfect songs for you based on your mood. All you need to do is input a prompt based on your mood or preferred song, and then the AI will generate a playlist of songs that match your prompt.

Turn your ideas into a playlist

Generative AI is the hottest trend in the market these days. You’ll find companies using this technology in their apps, smartphones, and other tech products. Now, this technology is coming to one of the best audio streaming platforms, Spotify, and will allow you to generate playlists with a prompt.

According to Android Authority, with the new AI Playlist feature, you simply need to enter a prompt, and the technology will tailor a playlist according to it. For instance, you can enter prompts like “music to keep me motivated during an intense gym session” or “romantic music for a candlelight dinner with my wife.”

FTR Infographic AI Playlist.

Once you’ve entered the prompt, Spotify will use LLM technology to understand your intent and then go through your listening history and preferences to create a playlist that matches your prompt.

If the playlist is not to your liking, you can refine it by entering further commands that contain changes you’d like to see in the playlist. For example, if you’d like more bass-heavy songs in the playlist, you can enter a prompt like “more bass.”

While you can be as creative as you want with your prompts, the guardrails around the Spotify AI playlist feature will prevent it from responding to your prompt if you enter offensive words or anything related to a current event or a particular brand. You can create playlists using prompts that refer to a place, animal, activity, movie character, color, or even a particular emoji.

Spotify confirmed working on the AI playlist feature last year

In December 2023, TechCrunch reported that Spotify has confirmed that they are working on the AI playlist feature. The confirmation came after a TikTok user, @robdad_, posted a clip showing an option under Your Library to create a playlist with a disclaimer at the bottom stating, “Powered by AI.”

Now, this feature has reached the beta testing phase and is currently available for Android and iOS Spotify Premium users in Australia and the UK.


[ad_2]
Source link

Sam Altman and Jony Ive looking for funding for their AI device

0
[ad_1]

Last fall, we covered the news that OpenAI CEO Sam Altman and former Apple design Chief Jony Ive were working on an AI-powered device. Back then, we didn’t know what sort of device these two were looking to create. Well, we still don’t know. However, Sam Altman and Jony Ive are looking for funding for their AI device.

Right now, we’re starting to see more AI devices come to the market. These are devices that are portable and internet-connected just like smartphones, but they lack a traditional smartphone interface. For example, the AI Pin from Humane has been making the rounds lately.

Also, we got our first look at the Rabbit R1 in action. These are devices that aim to put the smartphone out of commission at some point. However, that point may be years away.

Sam Altman and Jony Ive are looking for funding for their AI device

At this point, we don’t know what this device will look like. Ive is, ostensibly, leading the design department, but we don’t expect it to look like an iPhone. In fact, we don’t expect it to look like a phone at all. Also, we don’t know what sort of AI capabilities this device will have.

What we know is that the two geniuses are now looking for funding for this device. According to sources, Altman and Ive are seeking funding from investors to bring this device to fruition. The two are seeking at least $1 billion in funding.

That’s a pretty tall order, but both individuals have proven themselves in the tech and AI fields. Also, AI technology is all the rage. So, it seems likely that they will be able to secure funding. Right now, we don’t know what firms they are contacting or if they’ve been able to secure any funding just yet, but we know that the duo contacted SoftBank CEO Masayoshi Son.

More information about this device will come out as time goes on. We don’t know anything about the device or the business that’s going to build it. However, OpenAI may own part of the business.


[ad_2]
Source link

New Google Search filter might let you find short videos like Reels and YouTube Shorts easier

0
[ad_1]

Google Search is the go-to search engine for almost everything, with around 92% of all searches globally happening there. Whether you’re hunting for news, articles, images, places, or videos, you probably just Google it, right? And now, it seems like the tech giant is trying out another filter to add to the mix alongside Video, Images, News, Shopping, Books, and others.According to tipster and Android researcher AssembleDebug on X, Google is giving a shot at testing a new “Short videos” filter on mobile. It seems that this new filter might showcase short videos from platforms like YouTube Shorts, Instagram, TikTok, Snapchat, and more in the search results.
However, the filter is probably still in the early testing phase, so there’s no guarantee it’ll stick around as a permanent search filter. We’ll just have to wait and see if Google decides to roll with this experiment.The test was also recently spotted by SEO consultant Brodie Clark (via Android Police), who shared additional images of the new Short Videos search filter.

Once chosen, the Short Videos filter displays portrait-orientation content in a convenient two-column layout, such as Shorts from YouTube and videos from TikTok. The filter eliminates the need to add keywords like Reels, Shorts, or TikTok to your search query.

The short video format really took off thanks to apps like Snapchat and TikTok. Instagram Reels and YouTube’s Shorts jumped on the bandwagon soon after. And here’s a fun fact: stats reveal that a whopping 73% of consumers actually prefer short-form videos when looking for products or services. So, it’s not too shocking that Google decided to give this new filter a whirl.

These days, some creators specialize in crafting short-format content exclusively thanks to the format’s popularity, especially when it comes to informative content like tutorials and news snippets. Even LinkedIn is getting in on the action, experimenting with a new short video feed geared toward careers and professionalism.

[ad_2]
Source link

Multiple Cisco Small Business Routers Vulnerable to XSS Attacks

0
[ad_1]

Cisco has alerted its customers about a critical vulnerability affecting several Small Business RV Series Routers models.

This vulnerability, CVE-2024-20362, poses a significant risk, allowing unauthenticated, remote attackers to conduct cross-site scripting (XSS) attacks.

The affected models include the RV016, RV042, RV042G, RV082, RV320, and RV325 routers, widely used in small business environments for secure internet connectivity and VPN access.

The vulnerability stems from insufficient input validation in the web-based management interface of the affected routers.

Attackers can exploit this flaw by convincing users to click on a specially crafted link. This can lead to executing arbitrary script code in the context of the affected interface or the potential leakage of sensitive, browser-based information.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

The Common Vulnerabilities and Exposures (CVE) system has assigned this vulnerability the identifier CVE-2024-20362, with a base score of 6.1 on the Common Vulnerability Scoring System (CVSS).

This score reflects a moderate severity level, emphasizing the need for affected users to take immediate action to mitigate the risk.

Affected Products and Mitigation Strategies

The advisory specifies that all software releases for the RV016, RV042, RV042G, RV082, RV320, and RV325 routers are vulnerable.

In contrast, this vulnerability does not affect other models in the Cisco RV Series, such as the RV160, RV260, and RV340 series routers.

Given the absence of software updates to address CVE-2024-20362, Cisco has outlined specific mitigation strategies for affected customers.

Disabling remote management is recommended for the RV320 and RV325 models.

For the RV016, RV042, RV042G, and RV082 models, Cisco advises disabling remote management and blocking access to ports 443 and 60443, which can be achieved through the router’s web-based management interface.

Fixed Software

Cisco has announced that it will not release software updates to address this vulnerability, as the affected routers have entered the end-of-life process.

Customers are encouraged to consult these products’ end-of-sale and end-of-life announcements and consider migrating to newer models that continue receiving security updates and support.

This situation underscores the importance of regular security assessments and the prompt application of mitigations or upgrades to protect against evolving cybersecurity threats.

Customers are advised to regularly review Cisco’s security advisories and consult with the Cisco Technical Assistance Center (TAC) or their contracted maintenance providers to ensure their network infrastructure remains secure and resilient.

Secure your emails in a heartbeat! Take Trustifi free 30-second assessment and get matched with your ideal email security vendor - Try Here


[ad_2]
Source link

Samsung to invest $24 billion in new chip factory in the US

0
[ad_1]

Samsung plans to construct one more semiconductor manufacturing factory in the US, its third in the country. The new facility is planned in Taylor, Texas, where the company is currently building its second facility, The Wall Street Journal has learned. The Korean firm already operates a chip plant in Austin, Texas.

Samsung may double its chip investment in the US

In 2021, Samsung announced a $17 billion investment to construct a chip factory in Taylor. The factory is expected to be operational later this year. The latest estimates suggest the final cost of the facility will be more than $20 billion, potentially reaching $25 billion. The US government will reportedly support the Korean tech giant with federal funding of about $6 billion under the CHIPS and Science Act.

It appears that Samsung plans to use the grants and subsidies to increase its chip manufacturing capacity in the US. According to the WSJ, the planned second round of investment would bring the total to $44 billion, double what it would invest in the under-construction chip plant in Taylor. As we have seen with the current facility, depending on the market conditions, the total amount could increase as the construction proceeds.

Along with a semiconductor manufacturing facility, Samsung plans to construct a facility for advanced packaging and R&D (research and development). The new report says the initial estimated cost of the manufacturing site is $20 billion, while the packaging facility may cost $4 billion. The company will reportedly hold an event in Taylor next Monday, April 15, to announce its broadened investment plans.

It is a huge win for the US government

If Samsung’s plan materializes, it would massively boost the US semiconductor market. The Biden administration has been encouraging foreign chip companies to invest more in the country to expand their production capacity. That is the very purpose of the CHIPS and Science Act, to lure companies with grand, loans, and funding. The Act offers federal funding of $52.7 billion to chip firms, including $39 billion in direct grants.

TSMC, the world’s largest semiconductor foundry, is also building a new factory stateside. It will reportedly get funding of over $5 billion. American chip giant Intel may receive the biggest chunk of this pool, with rumors of over $10 billion in grants and loans and an additional $3.5 billion in grants for the production of military chips. It is unclear if Samsung will get another round of federal funding for its second chip factory in Taylor.


[ad_2]
Source link