Federal US authorities have asked Google for the names, addresses, telephone numbers, and user activity of accounts that watched certain YouTube videos, according to unsealed court documents Forbes has seen.
Of those users that weren’t logged in when they watched those videos between January 1 and 8, 2023, the authorities asked for the IP addresses.
The starting point of one of the investigations is an entity that uses the handle “elonmuskwhm” and is suspected of money laundering by selling Bitcoin for cash. As part of the investigation, agents sent the suspect links to tutorials on YouTube about mapping via drones and augmented reality software.Then they asked YouTube to send them data about the people that watched that video.
But those video tutorials were not private and had been watched over 30,000 times by the time the agents asked YouTube’s parent company Google for information about the viewers.
In another case, related to a bomb threat, the authorities asked for information about the viewers of eight selected live streams. One of those live streams has over 130,000 subscribers.
The police received a threat from an unknown male that there was an explosive placed in a trash can in a public area. When the police went to investigate the matter, they found out their actions were broadcasted through a YouTube live stream camera. Apparently similar events had taken place before, so for good reason law enforcement is after the evildoers.
But asking for data of that many viewers, many of which we can assume to be innocent bystanders, goes against what privacy experts believe to be reasonable. This type of digital dragnets go against the fourth amendment: freedom from unreasonable searches.
Albert Fox-Cahn, executive director at the Surveillance Technology Oversight Project (STOP) said:
“No one should fear a knock at the door from police simply because of what the YouTube algorithm serves up. I’m horrified that the courts are allowing this.”
According to the documents Forbes has seen, the court granted the order but asked Google not to make it public. We don’t currently know if Google complied with the request for information.
Google spokesperson Matt Bryant told Forbes:
“We examine each demand for legal validity, consistent with developing case law, and we routinely push back against over broad or otherwise inappropriate demands for user data, including objecting to some demands entirely.”
STOP condemned the US Department of Justice for securing a bulk warrant to track every YouTube user who watched the completely legal videos about mapping software for drones.
John Davisson, senior counsel at the Electronic Privacy Information Center, told Forbes:
“What we watch online can reveal deeply sensitive information about us—our politics, our passions, our religious beliefs, and much more. It’s fair to expect that law enforcement won’t have access to that information without probable cause. This order turns that assumption on its head.”
Warrants like these turn innocent people into suspects for no other reason than watching a perfectly legal video. The YouTube warrants are similar to geofence warrants, where court issues a search warrant to allow law enforcement to search a database to find all active mobile devices within a particular area.
These warrants turn the fear that certain online searches or your viewing history is going to put you on some kind of list, into reality. It also encourages users to use a VPN for even the most harmless activities and discourages YouTube visitors from logging in.
We don’t just report on privacy—we offer you the option to use it.
Privacy risks should never spread beyond a headline. Keep your online privacy yours by using Malwarebytes Privacy VPN.
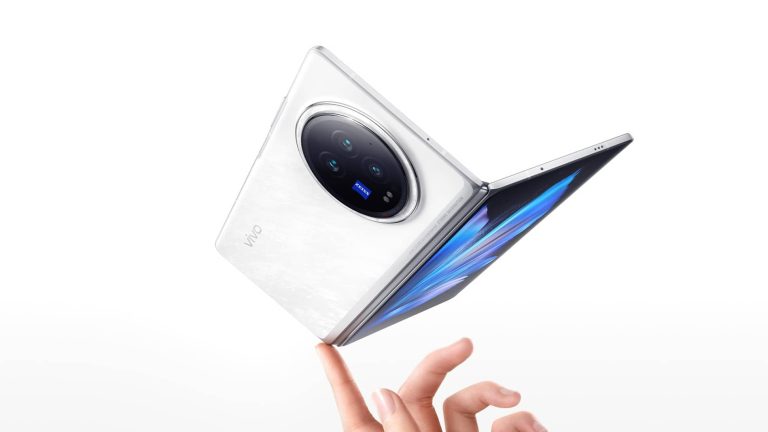
Vivo announced two smartphones today, the Vivo X Fold 3 and Vivo X Fold 3 Pro. The ‘Pro’ model is the more powerful of the two, even though they are very similar in a number of ways. They also have the same design, but the regular model does have some advantages.
The Vivo X Fold 3 is actually the thinnest and lightest foldable to date
The regular Vivo X Fold 3 is the lightest and thinnest foldable to date. It even trumps the HONOR Magic V2, which held that title thus far, and which managed to shock us at IFA 2023 in Berlin.
That being said, the VIvo X Fold 3 measures 4.65mm when unfolded, 10.2mm when folded, and it weighs only 219 grams. In comparison, the HONOR Magic V2 measures 4.8mm when unfolded, 10.1 when folded, and weighs 231 grams.
It is technically 0.1mm thinner when folded, but considering that the VIvo X Fold 3 is thinner when unfolded, and the fact that the difference is 0.1mm, we can safely say that Vivo takes the crown here.
The ‘Pro’ model is a bit thicker and heavier
The Vivo X Fold 3 Pro is thicker and heavier, though. It is 5.2mm thick when unfolded, 11.2mm when folded, and it weighs 236 grams. That is still great, very thin and not that heavy, but it’s nowhere close to what the regular model offers.
We focused as much on thickness and weight as that really does matter when it comes to foldable devices. Vivo managed to achieve something truly great here. That’s not all these two phones have to offer, though. They’re very powerful, and they also look really nice. Let’s touch upon the design first.
Both smartphones have very thin bezels around the main and cover displays. You’ll find display camera holes on both panels and a large circular camera island on the back. ZEISS’ optics are also included in the package. Both phones are made out of metal and glass, and they look very similar, though once again, the Vivo X Fold 3 is thinner and lighter.
Vivo X Fold 3 specifications
Let’s kick things off with the lighter and thinner phone, the Vivo X Fold 3. In terms of specs, it is inferior to its sibling. It comes with the Snapdragon 8 Gen 2 processor, with either 12GB or 16GB of LPDDR5X RAM. Its UFS 4.0 flash storage goes from 256GB to 1TB, depending on the variant.
An 8.03-inch main display is included here, with a resolution of 2,480 x 2200. That is an AMOLED panel and it has an adaptive refresh rate up to 120Hz. The external screen measures 6.53 inches, and it has a resolution of 2,789 x 1172 pixels. It’s also an AMOLED panel with an adaptive refresh rate.
A 5,500mAh battery is included here, as Vivo combines two batteries (3,020mAh + 2,480mAh units). 80W wired charging is supported, wireless charging is not.
The phone includes three 50-megapixel cameras on the back. The main one supports OIS, and it has a wide-angle lens with an f/1.75 aperture. The second camera is a 50-megapixel ultrawdie unit with an f/2.0 aperture lens. The third is a 50-megapixel portrait camera with an f/1.85 aperture. All cameras include T* coating from ZEISS.
There are two nano SIM card slots included in the phone. 5G is supported, of course, while Android 14 comes pre-installed with OriginOS in China. The device comes in black and white colors, and it includes a side-facing fingerprint scanner.
Vivo X Fold 3 Pro specifications
The Vivo X Fold 3 Pro comes in black and white colors too, and it is fueled by the Snapdragon 8 Gen 3 SoC. So it has a more powerful SoC than the regular Vivo X Fold 3. In terms of RAM, you’re getting 16GB of LPDDR5X RAM here with 512GB of UFS 4.0 flash storage.
The displays are the same as on the base model. There is an 8.03-inch inner panel with a resolution of 2480 x 2200 pixels. The outer display measures 6.53 inches and has a resolution of 2748 x 1172 pixels. Both are OLED displays with an adaptive refresh rate of up to 120Hz.
A 5,700mAh battery sits on the inside, and those are two batteries combined. The phone supports 100W wired charging, in addition to 50W wireless charging.
Two 50-megapixel cameras sit on the back, in addition to a 64-megapixel unit. The main 50-megapixel camera has a wide-angle lens with an f/1.68 aperture and OIS support. A 50-megapixel ultrawide camera with an f/2.0 aperture is also included. The third camera is a 64-megapixel periscope telephoto unit with an f/2.57 aperture lens. All cameras include T* coating by ZEISS.
Android 14 comes pre-installed on the phone with OriginOS on top of it. There are two nano SIM card slots here, and the phone is IPX8 certified for resistance to water. There are two ultrasonic fingerprint scanners here, one under the main display, and one under the cover panel.
Pricing
The Vivo X Fold 3 comes in four different variants with either 12GB or 16GB of RAM. The pricing starts at CNY6,999 and goes up to CNY8,999. The Vivo X Fold 3 Pro comes with 16GB of RAM with either 512GB or 1TB of storage. The two models cost CNY9,999 and CNY10,999, respectively. Vivo did not mention anything about their global availability just yet.
Hackers use 2FA (Two-Factor Authentication) phishing kits to overcome the additional security layer provided by 2FA.
These kits typically mimic legitimate login pages and prompt users to enter their credentials along with the one-time passcodes generated by their authenticator apps or sent via SMS.
Through proactive threat hunting, Sekoia analysts uncovered a new and widespread Adversary-in-The-Middle (AiTM) phishing kit called Tycoon 2FA in October 2023.
This Phishing-as-a-Service (PhaaS) platform has been actively used by multiple threat actors since at least August 2023 to conduct effective phishing attacks.
Continuous monitoring revealed Tycoon 2FA as one of the most prevalent AiTM kits, with over 1,100 associated domains identified between late October 2023 and late February 2024.
Technical Analysis
Phishing using QR codes increased in October 2023. Many AiTM phishing pages shared similarities like:-
Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:
The problem of vulnerability fatigue today
Difference between CVSS-specific vulnerability vs risk-based vulnerability
Evaluating vulnerabilities based on the business impact/risk
Automation to reduce alert fatigue and enhance security posture significantly
AcuRisQ, which helps you to quantify risk accurately:
The pages retrieved resources from codecrafterspro[.]com, which appeared central.
Other associated domains like codecrafters[.]su and devcraftingsolutions[.]com hosted phishing resources with a “Powered by TycoonGroup” login panel.
The tycoongroup[.]ws domain promoted Tycoon as the “best 2FA bypass phishing platform”, linking this infrastructure to the Tycoon 2FA phishing platform.
Login page of Tycoon 2FA administration panel (Source – Sekoia)
Researchers analyzed the victim-facing interactions without access to Tycoon’s source code.
It uses AiTM, with an attacker server hosting the phishing page, relaying inputs to the legitimate service, prompting MFA, and capturing session cookies after successful MFA.
The stolen cookies allow bypassing MFA by replaying the session, even if credentials were changed. The key operations of Tycoon are outlined below.
Main operations specific to the Tycoon 2FA phishing kit (Source – Sekoia)
There are a total 7 stages and here below we have mentioned them:-
Stage 0 – Spreading phishing pages
Stage 1 – Cloudflare Turnstile challenge
Stage 2 – Email extractor
Stage 3 – Redirection page
Stage 4 – Fake Microsoft authentication login page and sockets
Stage 5 – 2FA relaying
Stage 6 – Final redirection
The Tycoon 2FA phishing kit harvests credentials via fake Microsoft pages, with a C2 server collecting data over WebSockets.
The latest version added stealth tactics like only providing malicious resources after solving a CloudFlare challenge, using randomized URLs, and filtering traffic to evade analysis.
While previous versions used characteristic filenames for core functionality, the new changes make tracking more difficult.
However, Sekoia found heuristics correlating legitimate resource names, C2 response data size and resource lengths to continue monitoring the evolving Tycoon 2FA infrastructure.
Tycoon 2FA became widespread, and the developer enhanced stealth capabilities in the recent version.
With its ease of use and low price, it gained popularity among threat actors.
Sekoia identified over 1,200 associated domain names since August 2023 and believes the Tycoon Group operations are highly lucrative, expecting Tycoon 2FA to remain a prominent threat in the AiTM phishing market in 2024.
IoCs
0q5e0.nemen9[.]com
25rw2.canweal[.]com
35fu2.ouchar[.]ru
4343w.jgu0[.]com
43rw98nop8.m1p8z[.]com
4m2swl.7e2r[.]com
Cybersecurity Threats5me78.methw[.]ru
6j312.rchan0[.]com
77p3e.rimesh3[.]com
8000n.uqin[.]ru
8uecv.gnornamb[.]com
98q5e.ructin[.]com
9c43r.theq0[.]com
9oc0y2isa27.demur3[.]com
beacon.diremsto[.]com
bloggcenter[.]com
buneji.fiernmar[.]com
e85t8.nechsha[.]com
ex1uo.rhknt[.]ru
explore.atlester[.]ru
fiq75d.rexj[.]ru
fisaca.trodeckh[.]com
galume.aricente[.]com
gz238.uatimin[.]com
horizon.sologerg[.]com
jp1y36.it2ua[.]com
k348d.venti71[.]com
kjlvo.ningeona[.]com
kjsdflwe.nitertym[.]ru
l846d.ferver8[.]com
libudi.oreversa[.]com
n29k4.ilert[.]ru
n9zph.lw8opi[.]com
o6t94g.3tdx2r[.]com
oo99v.coqqwx[.]ru
p1v12.17nor[.]com
pmd8ot6xhw.3qjpc[.]com
q908q.refec7[.]com
r298y.sem01[.]com
rlpq.tk9u[.]com
roriku.orankfix[.]com
tlger-surveillance[.]com
tnyr.moporins[.]com
wasogo.shantowd[.]com
x12y.restrice[.]ru
xrs.chenebystie[.]com
xva.tjlpkcia[.]com
zaqaxu.dthiterp[.]ru
zekal6.tnjxb[.]com
zemj4f.ymarir[.]ru
Cryptocurrency Wallet Address
19NReVFKJsYYCCFLq1uNKYrUqQE2bB4Jwx used by Saad Tycoon Group
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
With the increasing popularity of Apache Kafka as a distributed streaming platform, ensuring its high availability has become a priority for businesses. The efficient management of Kafka clusters plays a significant role in maintaining a reliable and uninterrupted streaming infrastructure.
In this article, we will explore the best practices for Kafka management that will help organizations achieve robustness and seamless performance.
Understanding Kafka topics, partitions, and replication
Apache Kafka operates on a publish-subscribe messaging system, organizing data into topics. Each topic is further divided into partitions, allowing for parallel processing and scalability. Understanding the concept of topics, partitions, and replication is crucial for effective Kafka management.
Kafka replication ensures fault tolerance by creating multiple copies of data across different brokers. By replicating data, Kafka provides redundancy and allows for automatic failover in the event of a broker failure. A minimum replication factor of three is recommended to ensure durability and availability in case of failures. Additionally, partitioning data across multiple brokers provides load balancing and efficient resource utilization.
Proper management of Kafka topics, partitions, and replication is essential for high availability and fault tolerance. By distributing data across multiple brokers and ensuring replication, organizations can maintain uninterrupted access to data even in the face of failures or system outages. Implementing monitoring and alerting mechanisms can help administrators proactively identify and resolve any issues related to topics, partitions, or replication.
High availability and fault tolerance in Kafka clusters
High availability and fault tolerance are critical aspects of Kafka management. By implementing certain strategies and best practices, organizations can ensure that their Kafka clusters remain highly available even during unexpected failures or disruptions.
One key practice is setting up Kafka clusters across multiple data centers or availability zones. By distributing the clusters geographically, organizations can mitigate the risk of complete data loss in case of a disaster or a data center outage. Additionally, organizations should consider using Kafka’s built-in features, such as mirror maker or replication, to replicate data across different clusters, further enhancing fault tolerance.
Organizations should also implement proper monitoring and alerting mechanisms to achieve high availability. This includes monitoring the health and performance of Kafka brokers, producers, consumers, and overall cluster metrics. By closely monitoring key metrics such as message throughput, latency, and consumer lag, administrators can identify any potential issues early on and take appropriate actions to prevent disruptions.
Kafka management best practices for ensuring high availability
Ensuring the high availability of Kafka clusters requires adherence to certain best practices. By following these practices, organizations can minimize downtime, mitigate data loss, and ensure the continuous availability of Kafka clusters.
Firstly, organizations should regularly monitor and maintain the hardware and infrastructure on which Kafka clusters are running. This includes monitoring CPU, memory, and disk utilization, as well as network bandwidth. By proactively addressing any hardware or infrastructure bottlenecks, organizations can prevent performance degradation and maintain high availability.
Image credit: Hackread.com
Secondly, organizations should implement proper load-balancing techniques to distribute the workload evenly across Kafka brokers. This includes using tools like Apache ZooKeeper to manage consumer group coordination and rebalancing. Organizations can prevent any single broker from becoming a bottleneck and maintain high availability and performance by ensuring that the load is distributed evenly.
Thirdly, organizations should regularly review and tune Kafka configurations for optimal performance and reliability. This includes adjusting parameters such as replication factor, batch size, and message retention policies based on the application’s specific requirements and workload. By fine-tuning these configurations, organizations can optimize resource utilization, reduce latency, and improve the overall performance of Kafka clusters.
Monitoring Kafka clusters for performance and availability
Monitoring Kafka clusters is essential to ensure their optimal performance and availability. By closely monitoring key metrics and setting up alerts, administrators can proactively identify and resolve any issues that may impact the performance or availability of Kafka clusters.
Monitoring tools such as Apache Kafka Manager, Confluent Control Center, or third-party solutions like Prometheus and Grafana can provide valuable insights into the health and performance of Kafka clusters. These tools enable administrators to monitor key metrics such as message throughput, latency, disk utilization, and broker availability.
In addition to monitoring cluster metrics, organizations should also monitor individual producers’ and consumers’ health and performance. This includes monitoring the rate of produced and consumed messages, consumer lag, and any potential bottlenecks or issues with specific producers or consumers.
Administrators can be notified of any abnormal behaviour or performance degradation by setting up alerts based on predefined thresholds. This allows them to take immediate action, such as scaling up resources, rebalancing partitions, or investigating potential issues, ensuring the continuous availability and optimal performance of Kafka clusters.
Kafka cluster capacity planning and scaling
Proper capacity planning and scaling are essential for maintaining high availability and performance in Kafka clusters. By accurately estimating the required resources and scaling the clusters accordingly, organizations can ensure that Kafka can handle the expected workload without any disruptions.
Capacity planning involves analyzing historical data and predicting future growth to determine the required resources, such as CPU, memory, and disk space. When planning the capacity of Kafka clusters, it is important to consider factors such as message throughput, retention policies, and expected data growth.
Scaling Kafka clusters can be done horizontally by adding more brokers or vertically by increasing the resources allocated to each broker. When scaling horizontally, it is important to ensure proper load balancing and data distribution across the new and existing brokers. This can be achieved by using tools like Apache ZooKeeper to manage the coordination and rebalancing of partitions.
Organizations should also regularly review and adjust the capacity of Kafka clusters based on changing workloads and requirements. This includes monitoring resource utilization and performance metrics and scaling up or down as needed to maintain high availability and optimal performance.
Configuring Kafka for optimal performance and reliability
Configuring Kafka properly is crucial for achieving optimal performance and reliability. By fine-tuning various parameters and configurations, organizations can ensure that Kafka clusters operate efficiently and reliably under high-load scenarios.
One key configuration to consider is the replication factor. By setting a higher replication factor, organizations can ensure data durability and fault tolerance. However, a higher replication factor also increases the storage and network overhead. Therefore, it is important to strike a balance between durability and resource utilization based on the application’s specific requirements.
Another important configuration is the batch size, which determines the number of messages that Kafka produces or consumes in a single batch. Larger batch size can improve throughput but may increase latency. It is important to find the optimal batch size that balances throughput and latency based on the workload and application requirements.
Organizations should also consider configuring proper message retention policies to ensure data is retained for the required duration. This includes setting the retention period and configuring the cleanup policies to remove expired data. By properly configuring retention policies, organizations can optimize storage utilization and ensure that data is available for the required duration.
Conclusion and key takeaways
In conclusion, efficient management of Kafka clusters ensures high availability and reliable performance. By following the best practices discussed in this article, organizations can optimize their Kafka management techniques and enhance the reliability of their streaming architecture.
A Super app is a single application that offers various services within the app itself. It eliminates the need to install multiple apps. For example, WeChat is a messaging app that also offers online payment services.
As reported by Kedglobal, Samsung Financial Networks, which operates as a subset of Samsung Group’s financial affiliates, is pursuing the idea of a super app for mobile banking by collaborating with some leading commercial banks in its hometown of South Korea.
Samsung to launch a super app for mobile banking in South Korea
As the report reads, Samsung has sent its proposal to the country’s leading banks, including KB Kookmin, Shinhan, Hana, Woori, and internet-only K Bank AR, to promote the idea of a super app. The app will be based on Samsung’s Monimo, a local mobile app launched in 2022 to offer financial services to South Korean people.
After evaluating their business presentations, Samsung has yet to choose one partner among the five banks. A local bank executive told the outlet, “Having a Samsung brand in our banking business is a huge strength to become bigger in the Korean financial market.”
Samsung is barred from owning a bank in its hometown and doesn’t have a banking affiliate either. Thus, launching a super app for mobile banking gives the company a unique opportunity to tap into the financial market and expand its portfolio.
Samsung sees many rivals in its hometown
What will happen to Monimo after launching the super app remains to be seen. Meanwhile, the app has already disappointed Samaung due to its failure to attract users and rough competition in the South Korean market. Monimo currently has a few million users in the country. However, its rival app, Toss Bank, has over 20 million users.
When launching a super app for mobile banking, Samsung should still face major rivals in South Korea. Apps like the Shinhan Super SOL super from Shinhan Financial Group and KB Star Banking from KB Financial Group.
Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:
The problem of vulnerability fatigue today
Difference between CVSS-specific vulnerability vs risk-based vulnerability
Evaluating vulnerabilities based on the business impact/risk
Automation to reduce alert fatigue and enhance security posture significantly
AcuRisQ, that helps you to quantify risk accurately:
A recent tweet from the security intelligence provider ThreatMon reported that a threat actor shared the EagleSpy Android Remote Access Trojan (RAT) 3.0 Ultimate on a forum.
🚨 EagleSpy Android RAT 3.0 Ultimate Shared
A threat actor on the forum shared EagleSpy Android RAT 3.0, developed to target mobile phones.
Bypassing Banking Applications: The malware can circumvent security measures of banking apps, potentially allowing hackers to access users’ financial information.
Skipping the Black Screen: It can operate without triggering the black screen that signals another service is using an app, making its activities less detectable.
Bypassing Google Play Protection: EagleSpy can evade Google Play’s security checks, enabling the installation of malicious apps without detection.
Stealing Cookies and Login Credentials: The RAT can access and exfiltrate cookies and login details from all registered websites on the infected device, compromising users’ online accounts.
FUD (Fully Undetectable) Stub: It includes a feature to keep the APK (Android Package Kit) hidden from antivirus software, making it harder to detect and remove.
Stealing 2FA Google Authenticator Codes: Perhaps most alarmingly, it claims to be able to steal codes from Google’s two-factor authentication (2FA) app, which is widely used as an additional security measure.
EagleSpy Android RAT 3.0’s capabilities pose a significant threat to users, potentially allowing unauthorized access to sensitive personal and financial information.
The ability to bypass 2FA, a cornerstone of modern online security practices, is particularly concerning. This could lead to unauthorized account access, financial theft, and identity fraud.
The emergence of EagleSpy Android RAT 3.0 underscores the evolving threat landscape facing Android users.
By staying informed about these threats and taking proactive security measures, users can significantly reduce their risk of falling victim to such malicious software.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
Samsung is allegedly testing four Galaxy S25 Ultra prototypes. This is based on the information provided to PandaFlash. That info includes renders, which you’ll see below. Before we get down to it, though, take this info with a grain of salt. We have no way of knowing whether this is real or not.
The alleged Galaxy S25 Ultra prototypes have surfaced online
If you check out the image below, you’ll see four renders there. All of these actually remind us of the Galaxy S24 Ultra, which suggests that the design won’t change all that much. There are some differences between them, though.
The first prototype you can see has a similar frame as the Galaxy S24 Ultra, but it has thinner bezels. The second one has a flatter flame and extremely thin bezels. The third one has thinner left and right bezels, but the top and bottom ones are a bit thicker. The last prototype has a thinner frame with rounded frame edges.
These are all variations of the same design, pretty much. We only get to see the front side of the phone here, though. Even if one of these prototypes ended up being accurate, the back side could look different this time around.
We’ll have to wait for CAD-based renders to get a clearer idea of the phone’s design
Not a single credible Galaxy S24 Ultra image surfaced thus far, from the sources we usually get them from. Chances are that CAD-based renders will arrive first, but we’ll have to wait a bit longer to see those.
The Galaxy S25 Ultra will launch in January next year, almost certainly. We’re still far off, though, so things could change, it all depends on Samsung’s plans, we don’t know anything for certain just yet.
A recent security alert warns of three critical vulnerabilities actively exploited in the wild, of which the first is CVE-2023-48788, an SQL injection vulnerability in Fortinet FortiClient EMS.
Attackers can use SQL injection vulnerabilities to insert malicious SQL code into a program that depends on a database.
It can give attackers unauthorized access to sensitive information, modify data, or disrupt operations.
The second vulnerability (CVE-2021-44529) is a code injection vulnerability present in the Ivanti Endpoint Manager Cloud Service Appliance (EPM CSA).
Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:
The problem of vulnerability fatigue today
Difference between CVSS-specific vulnerability vs risk-based vulnerability
Evaluating vulnerabilities based on the business impact/risk
Automation to reduce alert fatigue and enhance security posture significantly
AcuRisQ, that helps you to quantify risk accurately:
Code injection vulnerabilities allow attackers to inject malicious code into a legitimate program or application.
In the case of CVE-2021-44529, it enables attackers to take control of the EPM CSA server, steal data, or install malware.
The third vulnerability (CVE-2019-7256) is an OS command injection vulnerability found in Nice Linear eMerge E3-Series devices, which allows attackers to execute arbitrary commands on the operating system of the affected device.
It can grant attackers complete control over the device, allowing them to steal data, install malware, or disrupt critical systems, as all three of these vulnerabilities are classified as critical due to the potential severity of an exploit.
As per CISA , a recent security alert highlights three critical vulnerabilities actively exploited by malicious actors, posing a significant risk to federal systems and affecting the following software and devices, which many people use: Nice Linear eMerge E3-Series devices (CVE-2019-7256), which may be used for IP telephony or videoconferencing, Fortinet FortiClient EMS (CVE-2023-48788); and Ivanti Endpoint Manager Cloud Service Appliance (EEM CSA, CVE-2021-44529).
Example of SQL Injection
The vulnerabilities themselves cover different injection techniques but achieve similar results: attackers can inject malicious code to gain unauthorized access, steal data, install malware, or disrupt system operations.
The vulnerabilities align with the established Binding Operational Directive (BOD) 22-01, which identified known exploited vulnerabilities as a major threat to federal systems.
The BOD mandates Federal Civilian Executive Branch (FCEB) agencies to address such vulnerabilities by designated due dates to safeguard their networks from active exploitation.
A security alert underscores the critical importance of promptly addressing vulnerabilities listed in a central catalog, known as vulnerability management, which is essential for maintaining a strong cybersecurity posture.
It involves proactively identifying, classifying, prioritizing, and remediating security weaknesses in systems and applications, while a specific directive (BOD 22-01) mandates vulnerability management for certain agencies, but all organizations are urged to follow suit.
Attackers are actively utilizing critical vulnerabilities in the central catalog and taking various forms, including SQL injection, code injection, and OS command injection vulnerabilities.
In a successful SQL injection attack, for instance, attackers can inject malicious SQL code into a program to steal data or disrupt operations, while code injection vulnerabilities allow attackers to inject malicious code into a target system to achieve similar ends.
OS command injection vulnerabilities grant attackers the ability to execute arbitrary commands on the operating system, potentially giving them full control over the affected device.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.
April 2024 security update starts rolling out to the Galaxy S24 series with camera fixes
Needless to say, this is quite early for an April update, as we’re still in March at this point. It’s not even the last day of March or anything like that, we have almost a week to go at this point. This update will spread to more markets soon.
As already mentioned, the update is rolling out to all three Galaxy S24 handsets. The firmware version is S92xNKSU1AXCA in Korea and S92xBXXU1AXCA in Europe, and the download size is 797.83MB and 920.97MB, respectively. So it’s not a small update by any means, and we presume that those camera updates are the main reason why.
Samsung improved the white balance accuracy and exposure when it comes to the camera. In addition to that, the low-light image quality has been improved too. The company also fixed up the color accuracy in the ExpertRAW camera app.
If you’ve been having issues with text clarity in high-zoom shots, don’t fret, as that should be better now too. The last entry says that support for videos with 480×480 pixels resolution in the Instant Slow Mo feature has been added.
This update is rolling out in stages in Korea and Europe. More markets are expected to follow in the coming days/weeks. Considering the size of the update, it may not be a bad idea to update via a WiFi connection, rather than mobile data. It’s up to you, though.
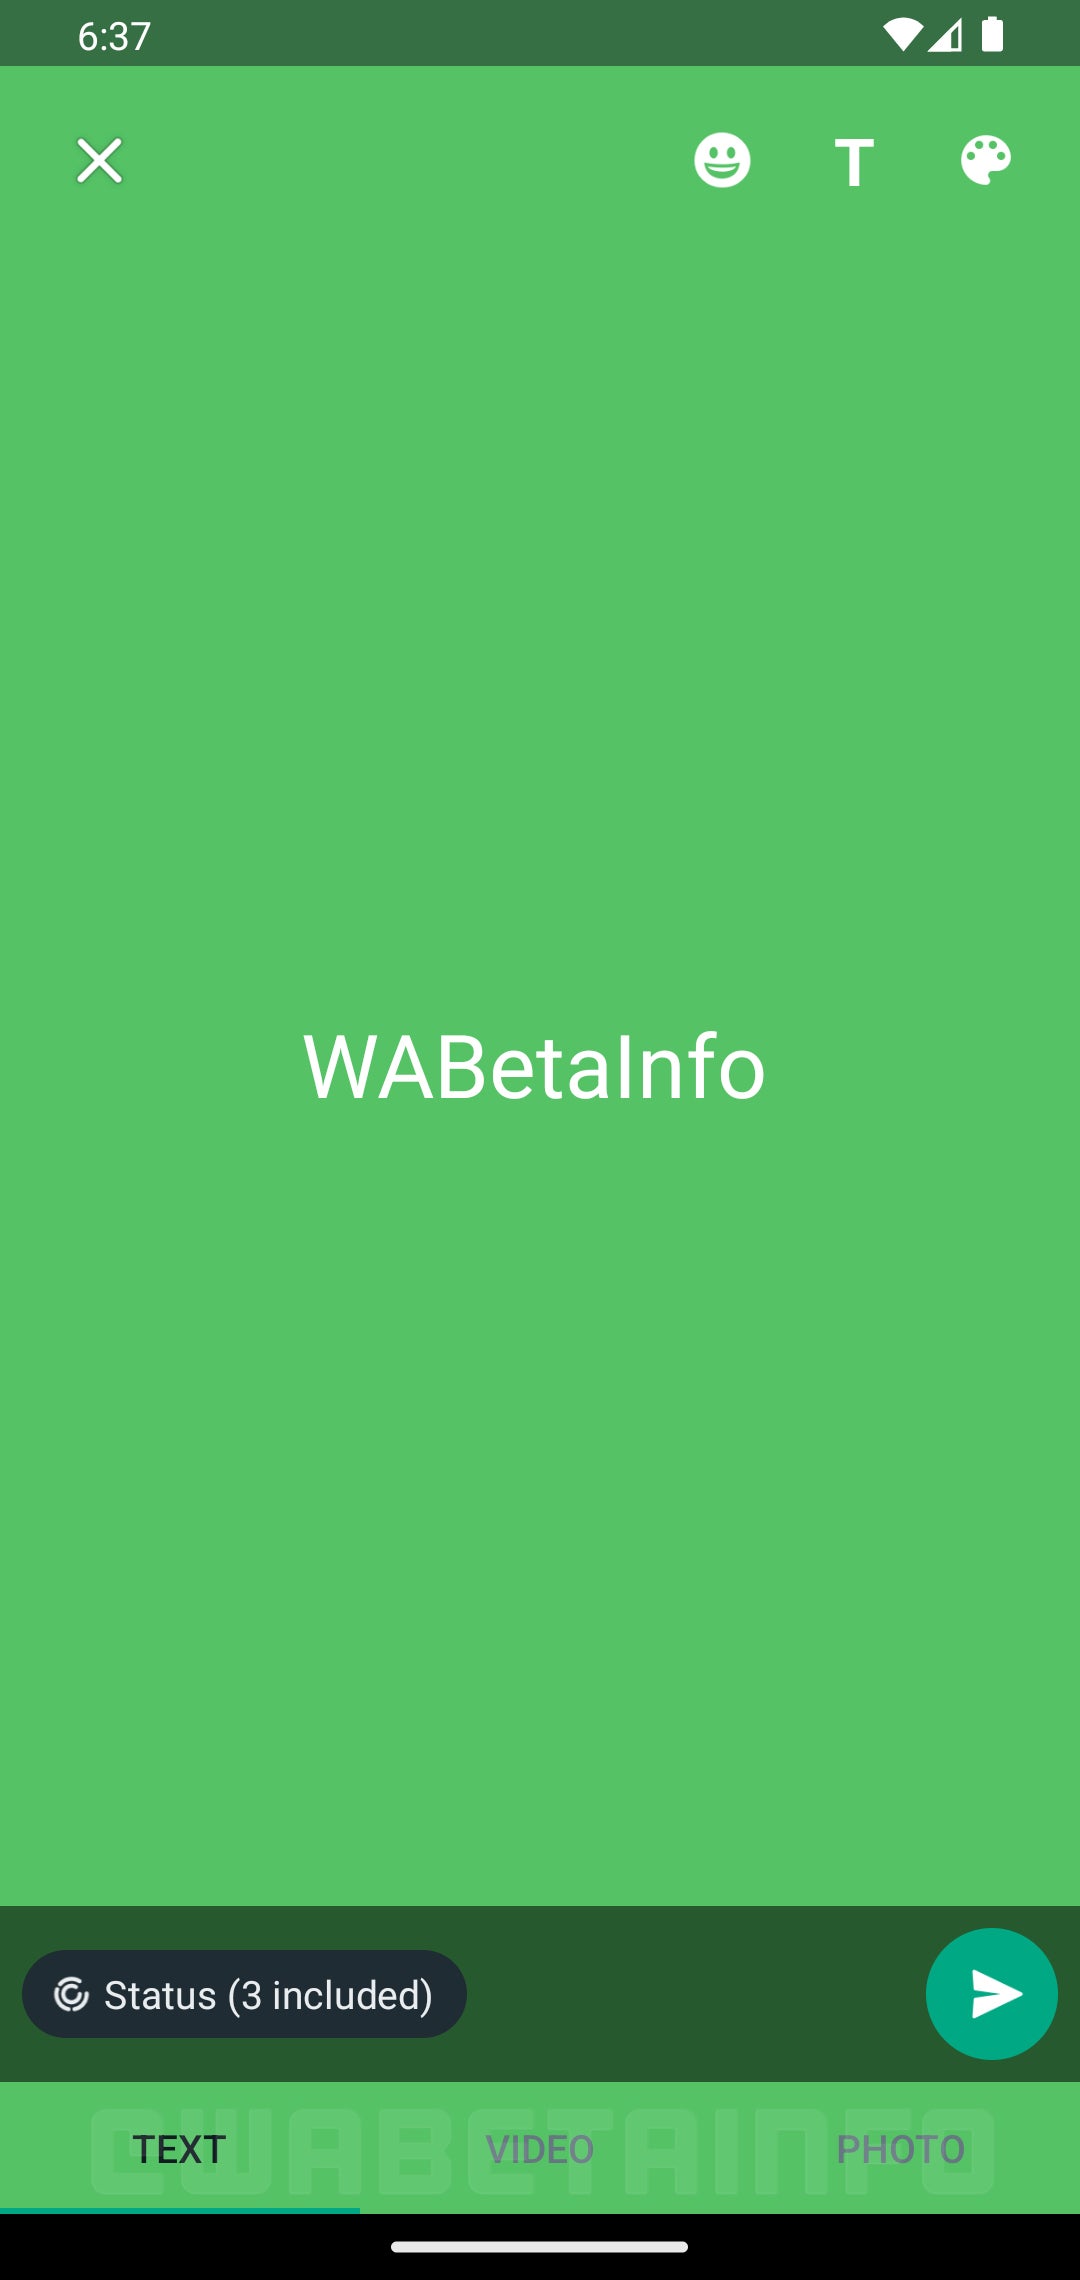
WhatsApp stands as one of the most widely used messaging apps globally, and ever since its acquisition by the tech giant Meta, it’s been evolving with more social media-like features. Recently, we reported on WhatsApp status updates becoming increasingly similar to Instagram stories, now allowing users to tag others. And it seems further changes are on the horizon for status updates.In the newest WhatsApp beta for Android (v2.24.7.16) update, the team at WABetaInfo uncovered a redesigned editor page for status updates. It now includes a Text option alongside the existing Video and Photo options at the bottom of the screen. Currently, WhatsApp only allows video and photo updates through the My Status option in the Updates tab.
Image Credit–WABetaInfo
In the screenshot, you can see that at the bottom of the screen, users will have the choice to select whether to share text, videos, or photos, making the sharing process even better. This new way of sharing status updates is still in the works and will be available in a future update of the app.
Right now, users can only get to the text-based status editor by tapping the pencil icon in the Updates tab. It’s good to know that WhatsApp doesn’t let you switch the status type (text, photo, video) once you’re in the editor/preview page. If you need to change it, you will have to go back and start over.
If the new update moves out of beta and becomes official, it could bring several benefits, especially by cutting down the number of steps needed to switch between text and media. With this choice integrated directly into the composer, users can swiftly switch between various types of content without having to leave the current screen. This will improve efficiency and convenience.