Hackers Claiming Unauthorized Access to the Fortinet Devices

0
[ad_1]

Hackers have claimed unauthorized access to Fortinet devices across various companies.

This breach highlights cybercriminals’ persistent threat to corporate security infrastructures and the importance of robust cybersecurity measures.

Overview of the Breach

A tweet from a dark-themed webpage has surfaced, showcasing a list of companies alongside details of their Fortinet device information.

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, which helps you to quantify risk accurately:

The list enumerates companies “A” through “J,” with each company having between 5 and 50 FortiGate devices.

A stylized eagle or bird emblem in the corner of the page suggests the identity of the hacker group or entity behind the unauthorized access.

Impact on Companies

The unauthorized access to Fortinet devices is a significant security concern for the affected companies. Fortinet devices, such as FortiGate firewalls, are integral to a company’s network security, providing a barrier against external threats.

The breach could allow hackers to monitor, disrupt, or even take control of a company’s network traffic, leading to data theft, service interruptions, or other malicious activities.

While the motives behind this breach remain unclear, such unauthorized access could be driven by various factors, including financial gain, espionage, or the challenge of breaching high-profile security systems.

The hackers may attempt to sell access to these devices on the dark web or use the compromised devices for more nefarious purposes.

Security Vulnerabilities

This incident underscores the vulnerabilities that even sophisticated security devices like those from Fortinet can have.

It serves as a stark reminder that no organization is immune to cybersecurity threats and that constant vigilance and updating of security protocols are essential.

To mitigate such risks, companies must regularly audit their security infrastructure, conduct penetration testing, and train employees on security best practices.

Response and Mitigation

In response to such incidents, companies are advised to immediately investigate the extent of the breach, identify any compromised systems, and take appropriate action to secure their networks.

This may include updating firmware, changing passwords, and implementing additional layers of security.

Fortinet and other cybersecurity firms often release patches and updates to address vulnerabilities, and companies must apply these updates promptly.

The unauthorized access to Fortinet devices across multiple companies is a severe incident that brings to light the ongoing battle between cybersecurity defenses and the ingenuity of hackers.

As cyber threats evolve, the need for comprehensive security strategies becomes more critical.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
Hackers Transform the Raspberry Pi into an Online Anonymity Tool – GBHackers on Security

0
[ad_1]

A new tool, GEOBOX, was advertised on the Dark Web that utilizes Raspberry Pi devices for fraud and anonymization, allowing users to spoof GPS locations, emulate network settings, mimic Wi-Fi access points, and bypass anti-fraud filters. 

Criminals were using multiple GEOBOX devices as proxies to enhance anonymity during an online banking theft investigation.

Attackers are believed to utilize more custom-made or modified devices in the future, creating challenges for law enforcement. 

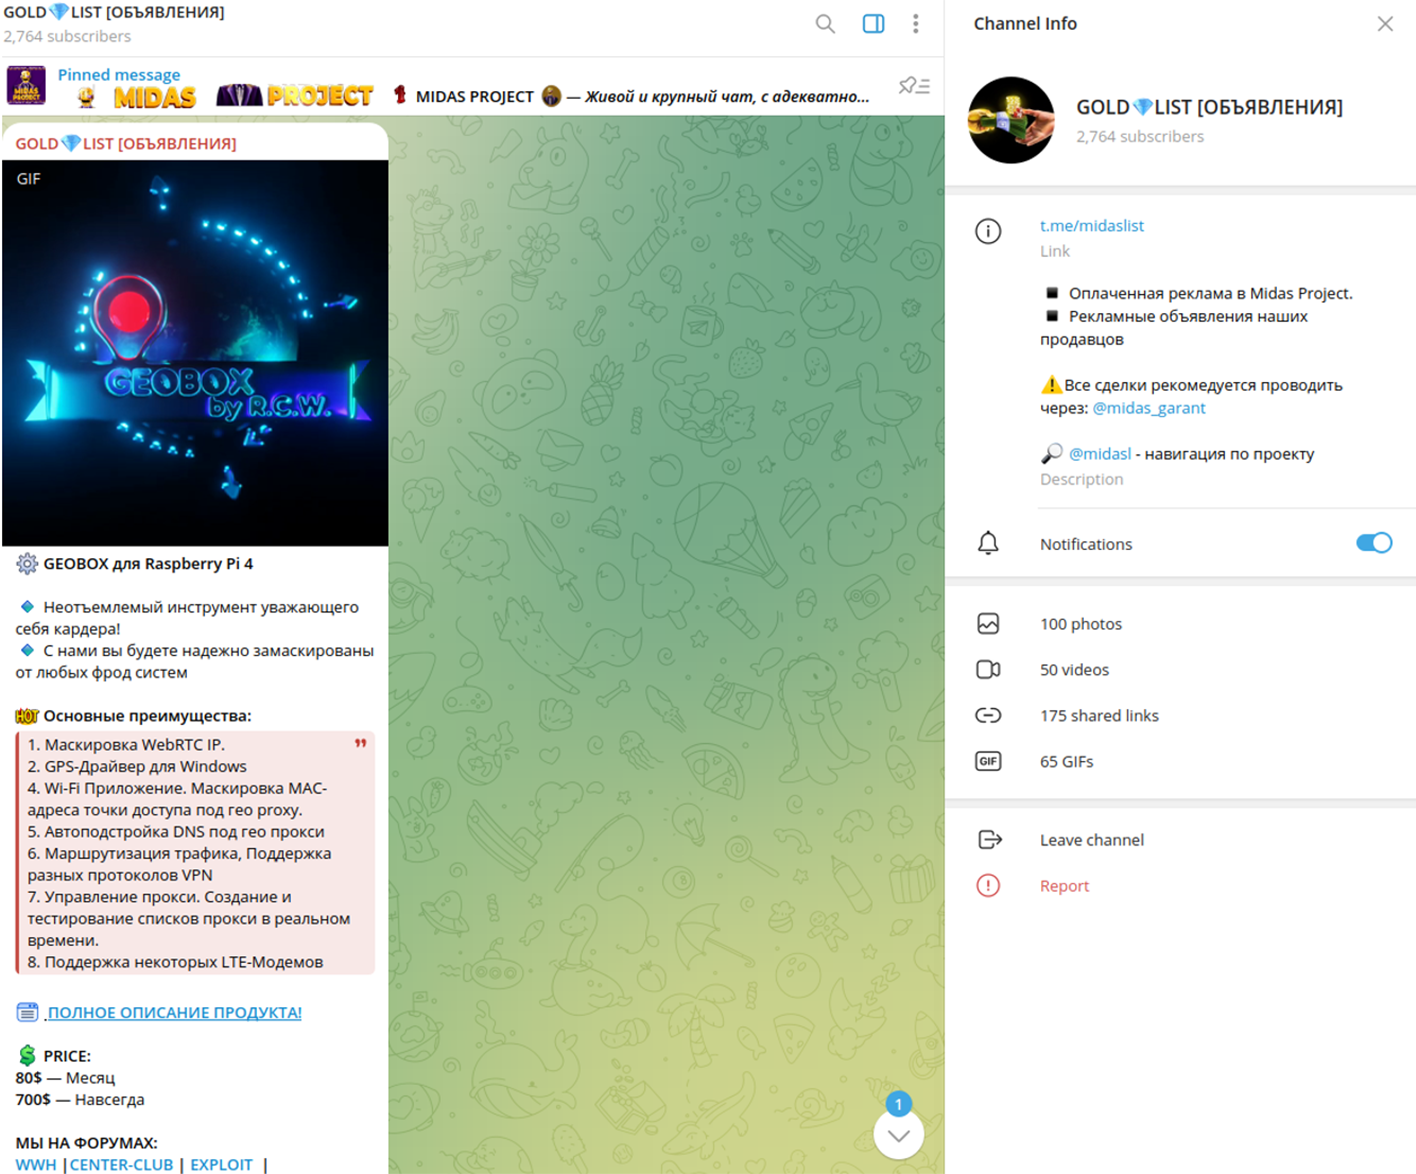
The tool is advertised on underground forums and Telegram for a fee of $700 for a lifetime or $80 monthly in cryptocurrency. 

Raspberry Pi i
Advertisement on Telegram

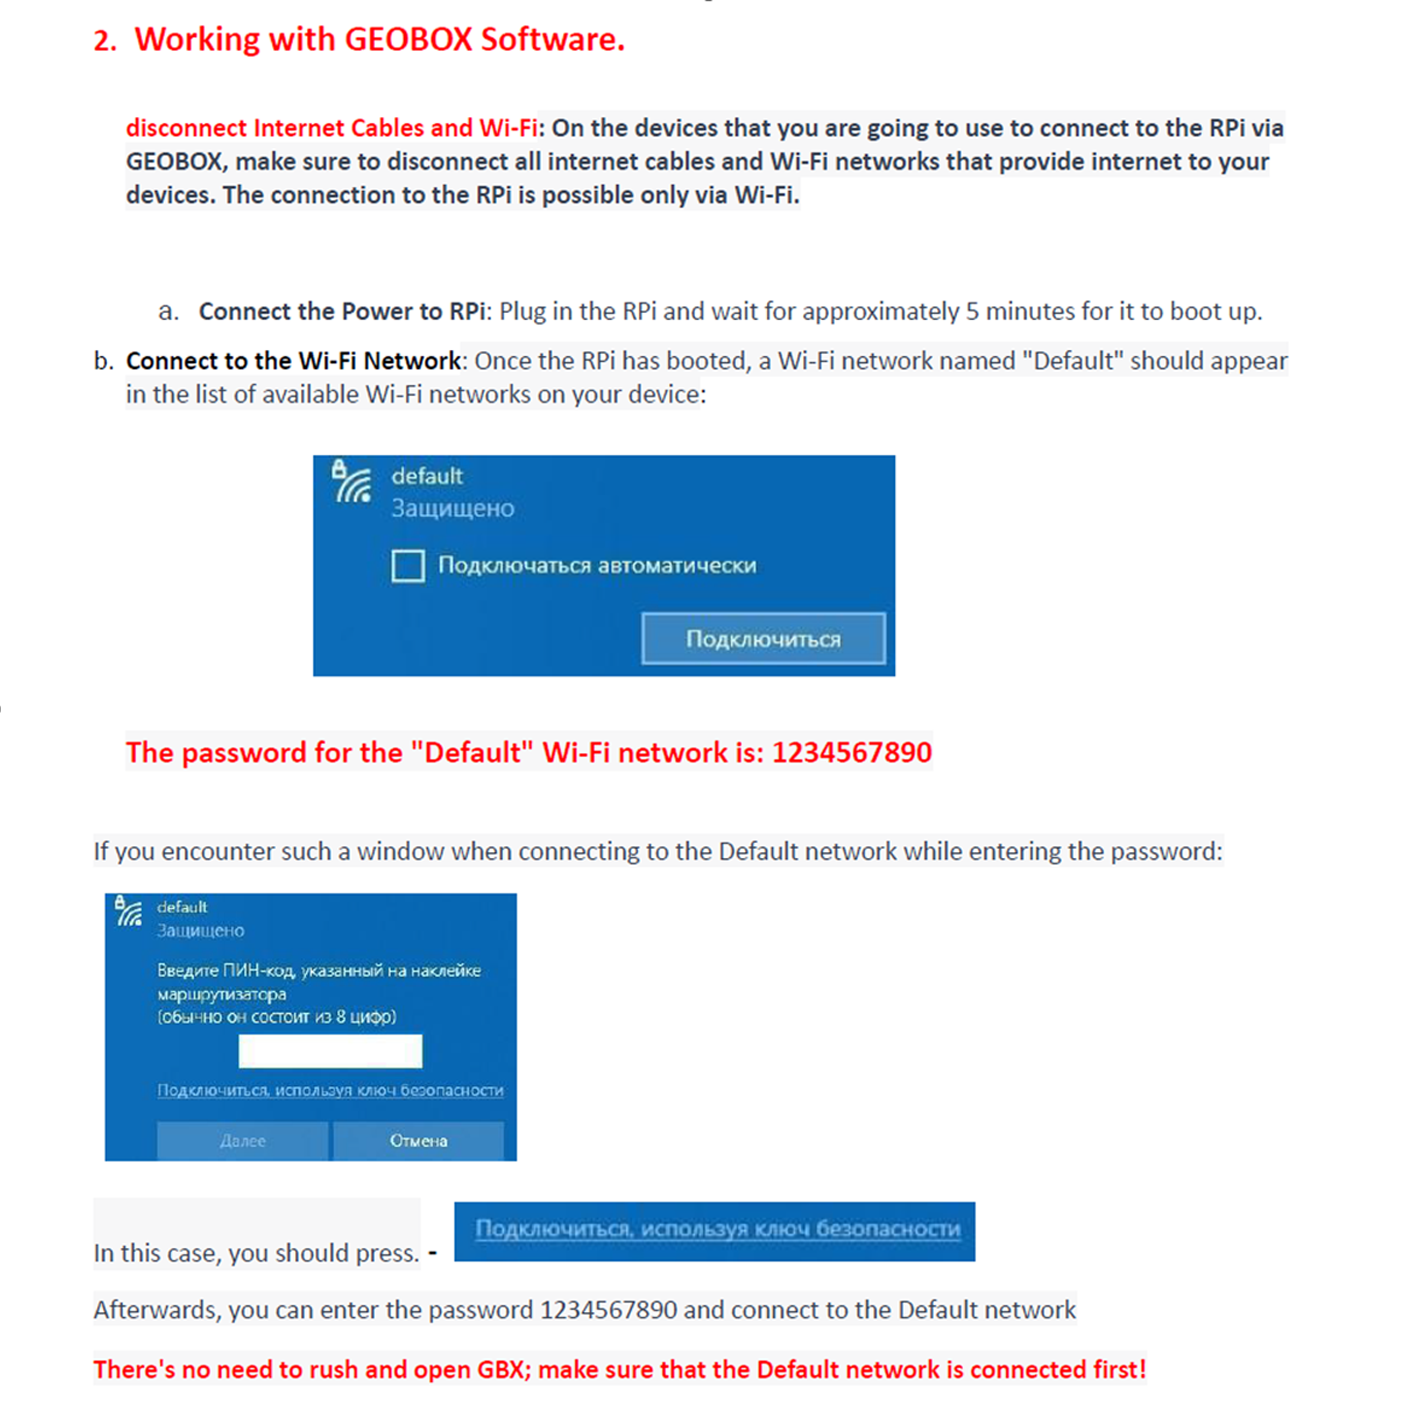
GEOBOX utilizes the Raspberry Pi to create an anonymous and fraudulent device, where a user manual with clear instructions is provided to simplify setup. 

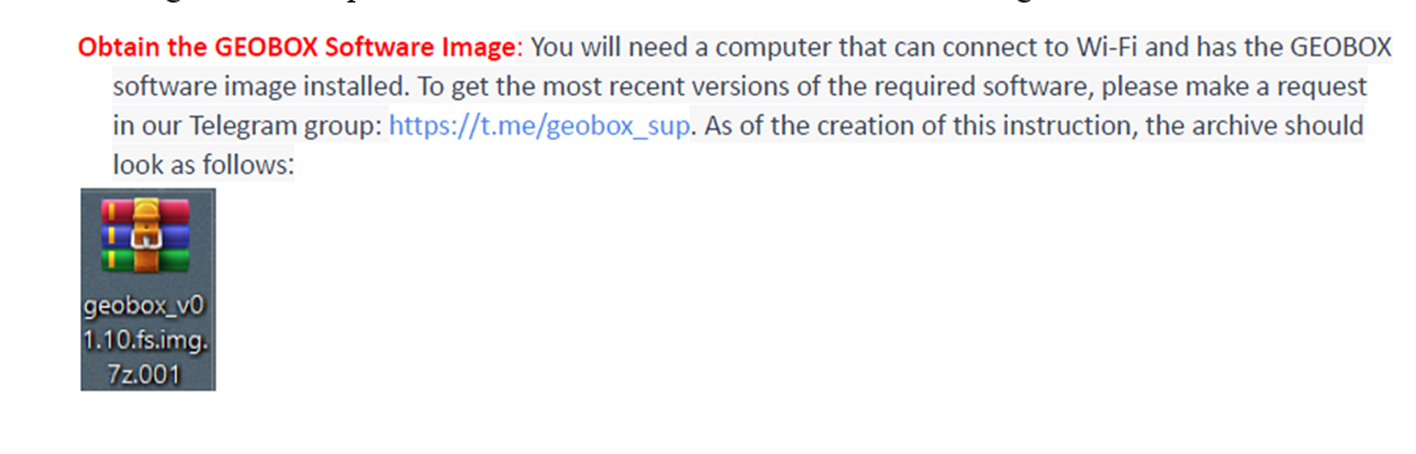
The manual includes SD card selection for optimal performance, guides users to download Raspberry Pi OS from the official website, and explains how to obtain the GEOBOX software image. 

Obtaining Geobox Software Image

After installing the OS, the user guide details how to use the GEOBOX software, activate the device, connect to the Internet, and configure GEOBOX functions. 

Raspberry Pi i
Working of Geobox Software

Feature of Geobox

A software suite designed for network configuration on the Raspberry Pi offers various functionalities, including managing multiple VPN connections with protocols like OpenVPN, L2TP, and Wireguard. 

Fatureset of the Geobox

Users can create and switch between VPN profiles for customized network routing, which supports creating cascaded VPN tunnels for enhanced anonymity and allows the configuration of proxy servers to manipulate DNS, GPS, and Wi-Fi MAC address information. 

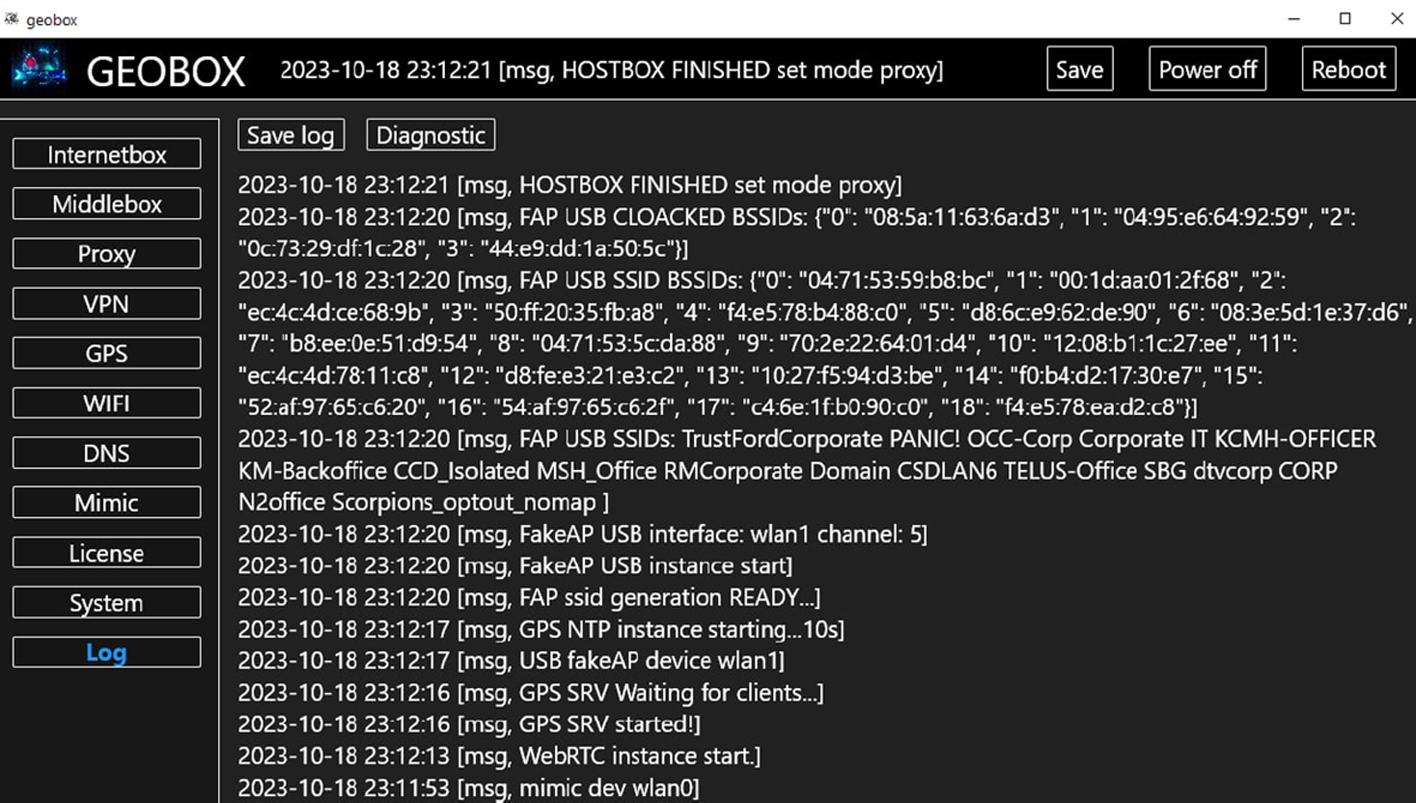
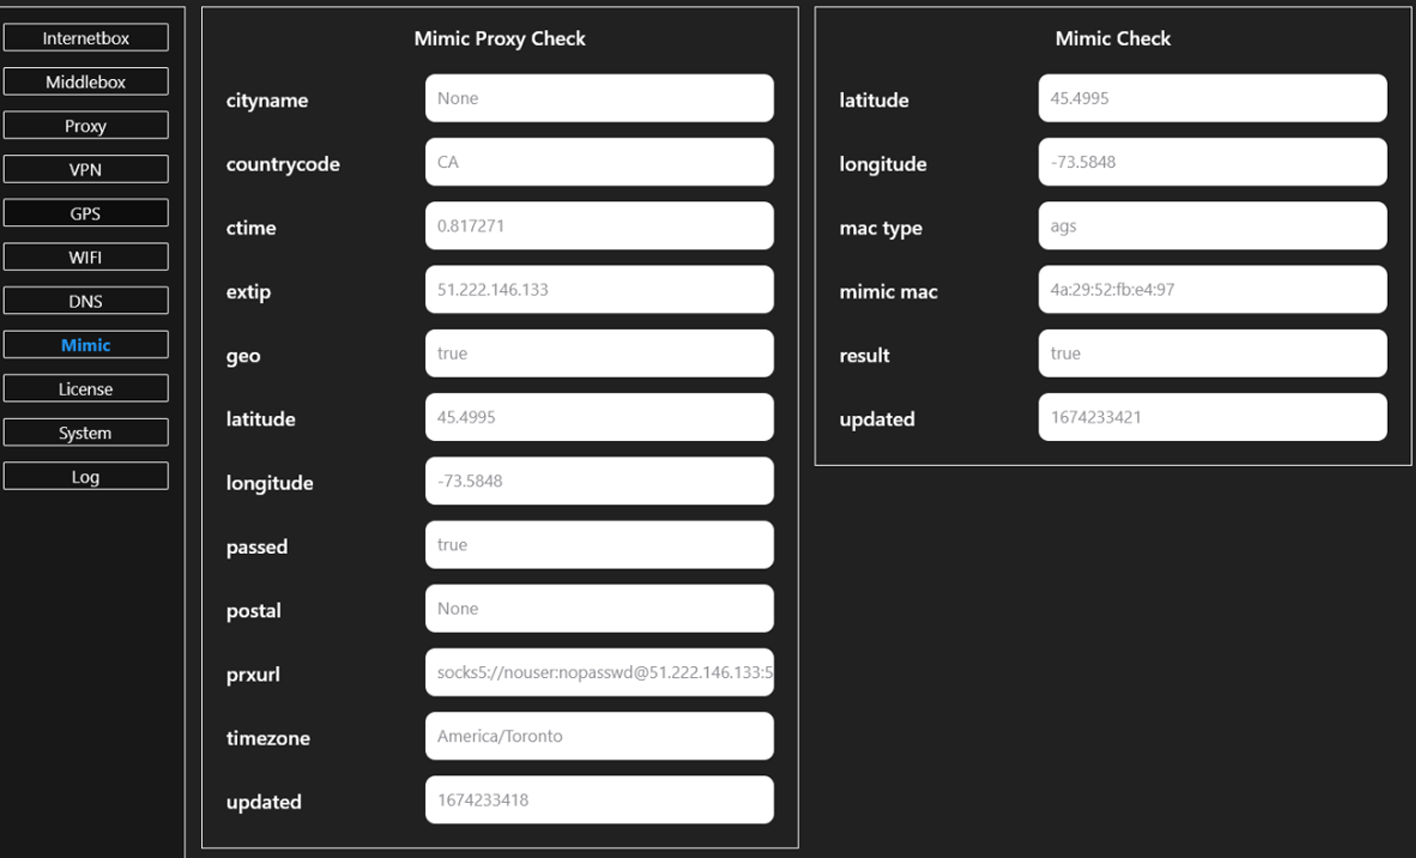
It provides a GPS emulator for devices lacking a GPS receiver and enables users to manage Wi-Fi network settings and DNS servers. For advanced users, GEOBOX offers a Mimic Tab to monitor data manipulation and a Log Tab for system diagnostics.

Document

Integrate ANY.RUN in Your Company for Effective Malware Analysis

Are you from SOC, Threat Research, or DFIR departments? If so, you can join an online community of 400,000 independent security researchers:

  • Real-time Detection
  • Interactive Malware Analysis
  • Easy to Learn by New Security Team members
  • Get detailed reports with maximum data
  • Set Up Virtual Machine in Linux & all Windows OS Versions
  • Interact with Malware Safely

If you want to test all these features now with completely free access to the sandbox:

Technical Insights

Geobox is a device that can be installed on a Raspberry Pi to anonymize online activity and manipulate geolocation and it achieves this by using WebRTC IP, GPS spoofing, and MAC address masking. 

Raspberry Pi i
Mimic Tab

The device is easy to use and provides a variety of functionalities through a web interface, including proxy server configuration, VPN connectivity, and altering Wi-Fi network parameters. 

It also poses a significant challenge to cybersecurity as it can be used to commit a variety of cybercrimes, such as cyber-attacks, dark web market operations, and financial fraud.

Resecurity discovered cybercriminals using GEOBOX with multiple LTE modems and proxy servers to anonymize connections, which makes tracing them difficult, especially for remote access. 

Criminals use short sessions to eliminate evidence, further impeding investigations, while easy access to GEOBOX raises concerns about its potential widespread use. The evolving threat landscape highlights the need for advanced security solutions and global cooperation to combat increasingly sophisticated cybercrime. 

Are you from SOC and DFIR Teams? – Analyse Malware Incidents & get live Access with ANY.RUN -> Start Now for Free.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
WhatsApp will reportedly let you use Meta AI straight from its search bar

0
[ad_1]
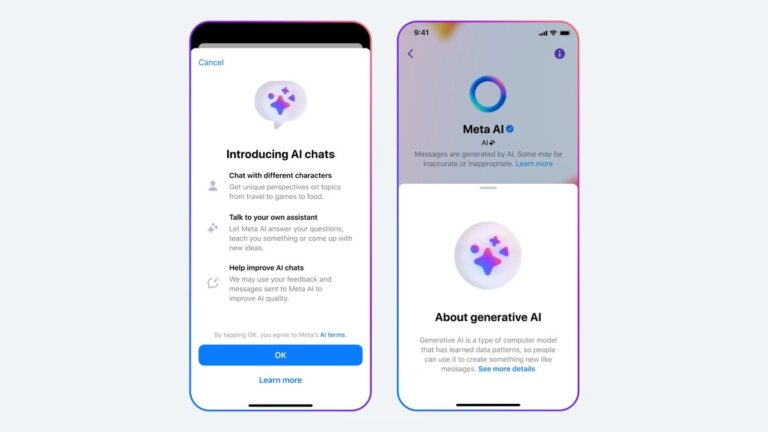
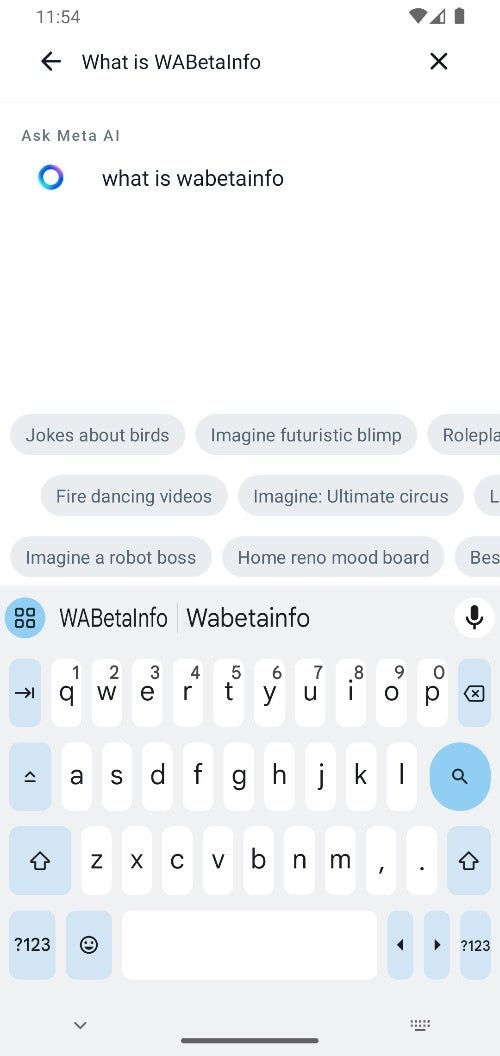
Artificial Intelligence (AI) is everywhere these days, and we’d be pretty naive not to admit that it is transforming how we use our devices on a daily basis. Meta is one company that has been at the forefront of integrating AI into its platforms, and WhatsApp, Messenger, and Instagram users in the US already have a taste of what it can do. But soon, interacting with Meta AI might become even more seamless.According to WABetaInfo, Meta is working on a new feature for WhatsApp that allows you to ask Meta AI questions directly from the app’s search bar. This means that it will no longer be necessary to manually start separate AI chats.

Image Source: WABetaInfo

We can see a new prompt that reads “Ask Meta AI” beneath the search bar in the screenshot above from WABetaInfo. This prompt would reportedly eliminate extra steps, make interacting with the AI incredibly more convenient, and wouldn’t require that unsightly Meta AI shortcut that got in the way of accessing your messages.In fact, if you’ve ever used ChatGPT, Meta AI will feel familiar, as it is designed as an all-around assistant. However, one advantage that this chatbot will have is that instead of having to hunt it down, you’ll simply type your question into the search bar. WhatsApp is even planning suggested prompts to get your creative AI juices flowing.

This feature is still under development and will likely appear in a future version of the app. In the meantime, WhatsApp is showing us that it is clearly all in on AI, as it is reportedly also working on implementing AI-powered image editing tools into its platform.

WhatsApp’s new features are a glimpse into a future where AI is woven deeply into our everyday apps. It’s likely just the beginning, and I’m excited to see what other innovations Meta and other tech giants have in store.


[ad_2]
Source link

EU Fitbit users to lose access to third party app and watch faces

0
[ad_1]

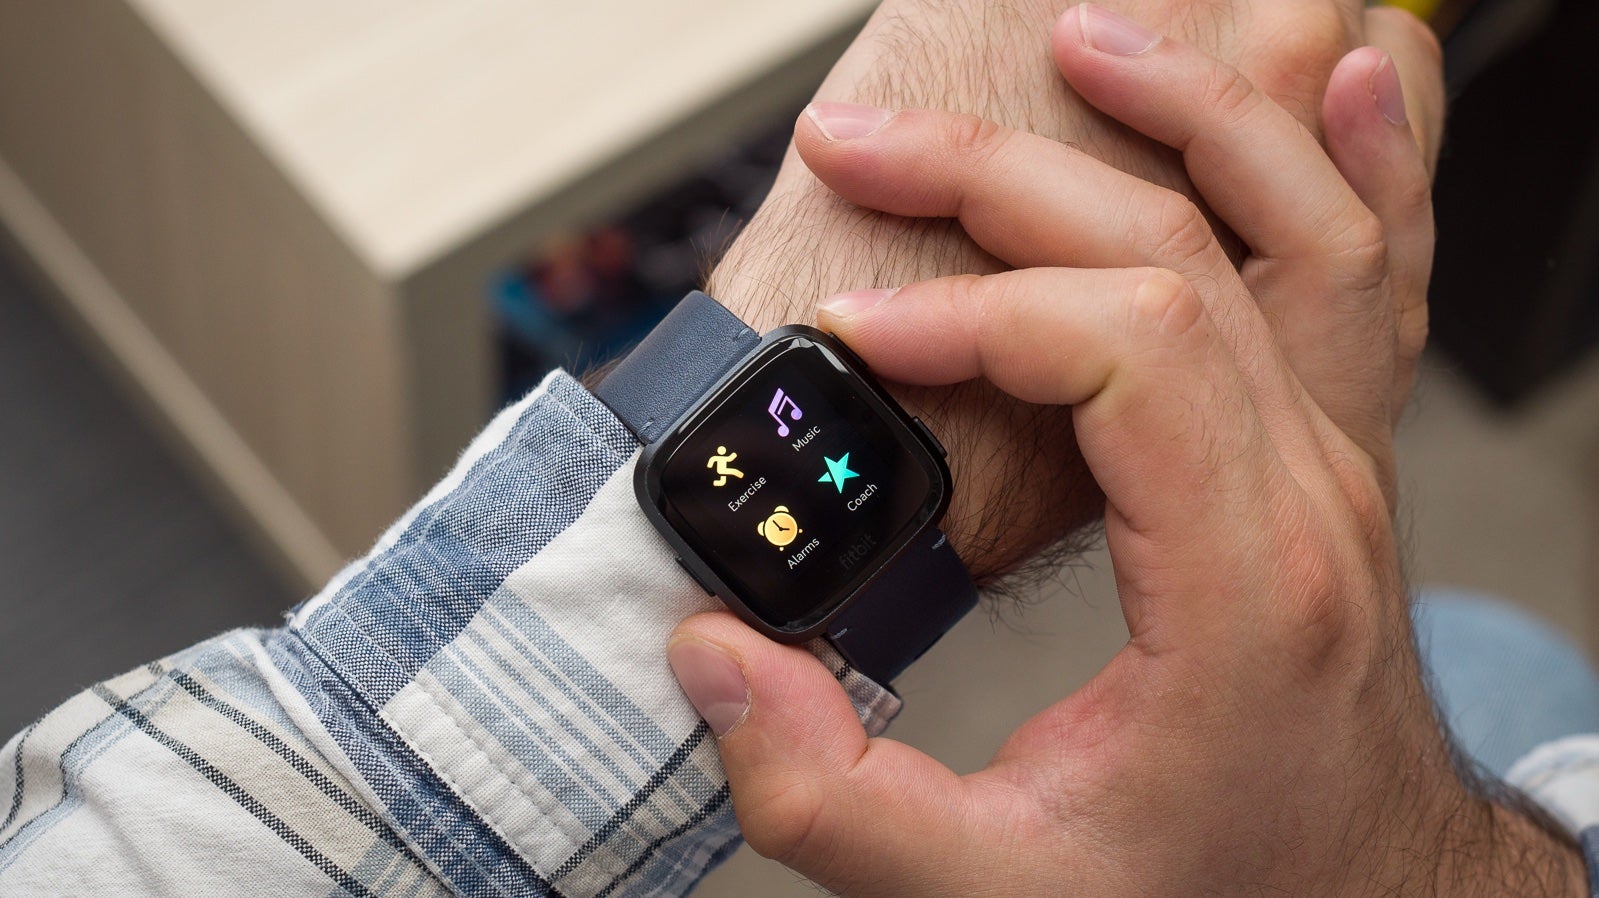
Fitbit users across the European Union should brace for a significant shift in the way they customize their smartwatches. Google has announced the removal of all third-party apps and clock faces from the Fitbit app gallery starting in June 2024.

Why the sudden change? The update points to newly imposed “regulatory requirements” from the EU as the reason. According to the support page where the change was quietly announced, EU Fitbit users will have until June 2024 to add any third-party apps or clock faces before that feature is shut down.

What happens after that? You will only be able to install apps and clocks developed by Fitbit and Google. However, according to Android Authority, existing third-party content on your Fitbit will continue to work after the deadline — you just won’t be able to install or download anything new. It is also important to note that U.S. users are unaffected, as this change is specific to the E.U.

This change will impact numerous popular Fitbit smartwatches, such as:

  • Fitbit Sense 2, Fitbit Sense
  • Fitbit Versa 4, Fitbit Versa 3, Fitbit Versa 2, Fitbit Versa Lite, Fitbit Versa
  • Fitbit Ionic

Meanwhile, the specific EU regulation fueling this shift is not cited in Google’s announcement, so it is difficult to say the exact reason(s) why this is happening. It leaves us wondering if this is a consequence of the EU’s Digital Markets Act (DMA) or some other regulatory framework Google must adhere to.This move does raise numerous questions regarding the user experience for Fitbit users in Europe, and more importantly, is this a sign of more restrictive tech regulations coming from the EU in the future? For now, all we can advise you on is to promptly download as many third party apps and clock faces as you think you may need for the future, before this restriction goes into effect.

[ad_2]
Source link

New Fitbit workout UI is now rolling out to the first-gen Pixel Watch

0
[ad_1]
Google’s original Pixel Watch was promised some love when the March Pixel Feature Drop was announced. One of the headline features was a revamped fitness tracking interface, bringing the first-generation smartwatch in line with the Pixel Watch 2‘s streamlined workout experience.

The previous Pixel Watch workout UI, while functional, wasn’t ideal. A single large metric dominated the screen, with three smaller stats crammed below. However, with the new update that — according to 9to5Google — is rolling out now, Google has abandoned this in favor of a layout that is more user-friendly and straight from the Pixel Watch 2.

New OG Pixel Watch Fitbitworkout UI based on Pixel Watch 2 | Source: Google

Now, your key exercise stats are displayed in a vertical list that you can easily swipe through. This provides a much clearer view, allowing you to check things like heart rate, calories burned, and elapsed time at a glance. This will definitely be more helpful while in the middle of a workout.

Heart rate zones also get a cool visual representation: a filled-in heart icon. Other subtle tweaks are also present, such as a change in the shape of the end, resume, and lock buttons, which are now pills instead of circles. These small changes add to the polish of the new UI.

These changes arrive via Fitbit 3.19 for Wear OS, which you’ll likely find waiting for you on the on-watch Play Store. There is one quirk that 9to5 mentioned regarding this update, and that is that you’ll likely have to restart your Pixel Watch after the update in order to see the new UI.

It’s very encouraging to see Google bringing features from the Pixel Watch 2 to the original Pixel Watch, which was lacking on many fronts when it first launched. The update will likely improve the user experience for health-conscious users who are still holding on to their original Pixel Watch.


[ad_2]
Source link

Sign1 Malware Hijacked 39,000 WordPress Websites

0
[ad_1]

A client’s website was experiencing random pop-ups as server side scanner logs revealed a JavaScript injection related to Sign1, which is a malware campaign that targets websites and has infected over 2,500 websites in the past two months and uses challenging techniques to evade detection.  

Daily server-side scans are crucial to detect changes like new malware, examine website logs, and identify changes in plugins, particularly those allowing custom code injection. 

Plugin changes

The plugins are attractive to attackers because they enable embedding malicious code and an investigation revealed malicious code embedded within a seemingly harmless custom CSS and JS plugin. 

While attackers abusing such plugins is common, this specific code displayed a unique and intriguing method.  

culprit nestled inside Custom CSS & JS

History Of The Sign1 Malware

Security researchers at Sucuri discovered a malware campaign targeting WordPress websites called Sign1, which injects malicious scripts into websites using custom HTML widgets or plugins. 

The malware uses base64-encoded parameters and time-based randomization to generate dynamic URLs that change every 10 minutes and fetch additional malicious scripts that can redirect visitors to scam sites or deliver unwanted ads. 

In the second part of 2023, it was also discovered to be a campaign, and researchers noticed that the malware was changing its concealment methods to avoid detection. 

Analysis Of The Malware

The code utilizes time-based randomization for verification purposes and retrieves the current Unix time (milliseconds since 1970-01-01) using Date.now(), which is then converted to seconds and aligned to a 10-minute interval, ensuring timestamps are consistent within that window. 

The value is expressed as a hexadecimal string, and a seemingly random string acts as a verification token, whereas requests for JavaScript files from a third-party domain include this token. 

use of the date.  now function near the top of the script

The server compares the token’s time component with the current time, likely rejecting requests with outdated or invalid timestamps, potentially to prevent unauthorized access or outdated data retrieval. 

Attackers injected a hard-coded array of numbers obfuscated with XOR encoding, while the key (40682) was readily available in the sample, allowing researchers to reverse the encoding and discover a newly registered domain. 

New values

The technique is common for attackers to mask malicious content while remaining detectable with knowledge of the key. 

Malicious Javascript code dynamically changes URLs in visitors’ browsers every 10 minutes, targeting visitors who haven’t visited the site through a major referrer (e.g., Google) and haven’t seen the pop-up before (checked by a cookie). 

Redirecting occurs

If conditions are met, the code injects another script to redirect users to scam sites (often VexTrio domains) by sending the current page URL, referrer, and browser language (base64 encoded) to a Traffic Distribution System (TDS). 

Downloads per day

Attackers utilize the popular Simple Custom CSS and JS plugins to achieve this, whereas the malware fetches additional scripts from domains registered shortly before the attack, making them difficult to block. 

The attackers switched hosting providers and used Cloudflare to further make it more difficult to understand their location by bypassing typical security scans as the malicious code resides in the database rather than server files. 

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter. 


[ad_2]
Source link
Government seeks personal information about who watched certain YouTube videos

0
[ad_1]

According to Forbes, Google was forced to turn over to government investigators the phone numbers, addresses, telephone numbers, and user activity of certain YouTube accounts. Also turned over was the IP addresses of some YouTube users who watched certain videos. The demand for information is the result of a criminal investigation that federal investigators are handling. The videos were sent by undercover police to a suspect accused of laundering cryptocurrency.
The suspect, who has the username “elonmuskwhm,” received links to publicly available YouTube tutorials that showed viewers how to do mapping via drones, and videos that discussed AR software. While these videos were viewed over 30,000 times, most of those views were unrelated to the case. Google was asked for the list of those who viewed these videos between January 1st and January 8th, 2023 although Forbes was not sure that Google had complied with the demand.

The demand for this information has set off some alarms although Google spokesperson Matt Bryant told Forbes, “With all law enforcement demands, we have a rigorous process designed to protect the privacy and constitutional rights of our users while supporting the important work of law enforcement. We examine each demand for legal validity, consistent with developing case law, and we routinely push back against over broad or otherwise inappropriate demands for user data, including objecting to some demands entirely.”

Those who concern themselves with privacy matters are unhappy to hear about the government requesting this information from Google. Albert Fox-Cahn, executive director of the Surveillance Technology Oversight Project said to Forbes, “It’s unconstitutional, it’s terrifying, and it’s happening every day.” 

Federal investigators say that the request for information was legally justified since the data demanded, “would be relevant and material to an ongoing criminal investigation, including by providing identification information about the perpetrators.” The government also noted that such requests were made by police in other states. In one case in New Hampshire, investigators were digging into bomb threats streamed live over YouTube. Police requested information about those who were viewing the live streams at certain times.


[ad_2]
Source link
Analyst says DOJ suit will result in Apple paying a hefty fine, and changing its business model

0
[ad_1]
Commenting about the suit, Ives told clients in a note, “We do not expect any business model changes for now, but Apple clearly is going to have to find a way to eventually settle this case, pay a hefty fine, and ultimately find some compromise with developers on the App Store structure down the road.” The analyst has an “Outperform rating” on Apple’s stock with a price target of $250. The shares closed Friday at $172.28.
The lawsuit, filed Wednesday morning by the Justice Department along with 16 state and district attorneys general, accused Apple of committing several antitrust violations including one that claims Apple blocked the development of a “super app” that would have made it easier for consumers to switch mobile platforms. Apple also was accused of causing the failure of the Amazon Fire Phone in 2014 and of making it difficult for manufacturers like HTC and LG to compete in the industry.

As Ives points out in his note to Wedbush clients, Apple has angered app developers by not allowing them to add a link to third-party payment processors for in-app purchases. Instead, outside of the EU, Apple collects 15%-30% of in-app purchases as it runs these transactions through its own in-app payment platform. As a result of the epic Epic v. Apple lawsuit, Apple does allow developers to include one link to a third-party payment processor but still takes a cut of 12% to 27%.

Meta Platforms, Microsoft, X, and Match Group have filed an amicus brief with the court hearing Epic’s claims that Apple has not followed the decision handed down by Judge Yvonne Gonzalez Rogers back in September 2021. While Apple’s cut of in-app payments has helped the company’s Services unit become Apple’s second-largest business segment after the iPhone (Services generated $85.20 billion in revenue during the last fiscal year, 2023), some changes to the App Store might be the end result of the DOJ’s lawsuit. That would be in addition to the massive fine that Apple will probably be forced to pay.

It probably is in the best interest of Apple not to get bogged down in a long and morale-draining lawsuit. A settlement would help the tech giant put this behind it without spending too much time and money on defending the firm. Besides wondering what constitutes a massive fine, it will be interesting to see what changes Apple is prepared to make to the App Store.


[ad_2]
Source link
WhatsApp working on implementing AI-powered image editing tools

0
[ad_1]
WhatsApp is reportedly working on introducing some new features that leverage artificial intelligence to edit images. These tools were first hinted at in September and have now been discovered within the platform’s latest beta version for Android.

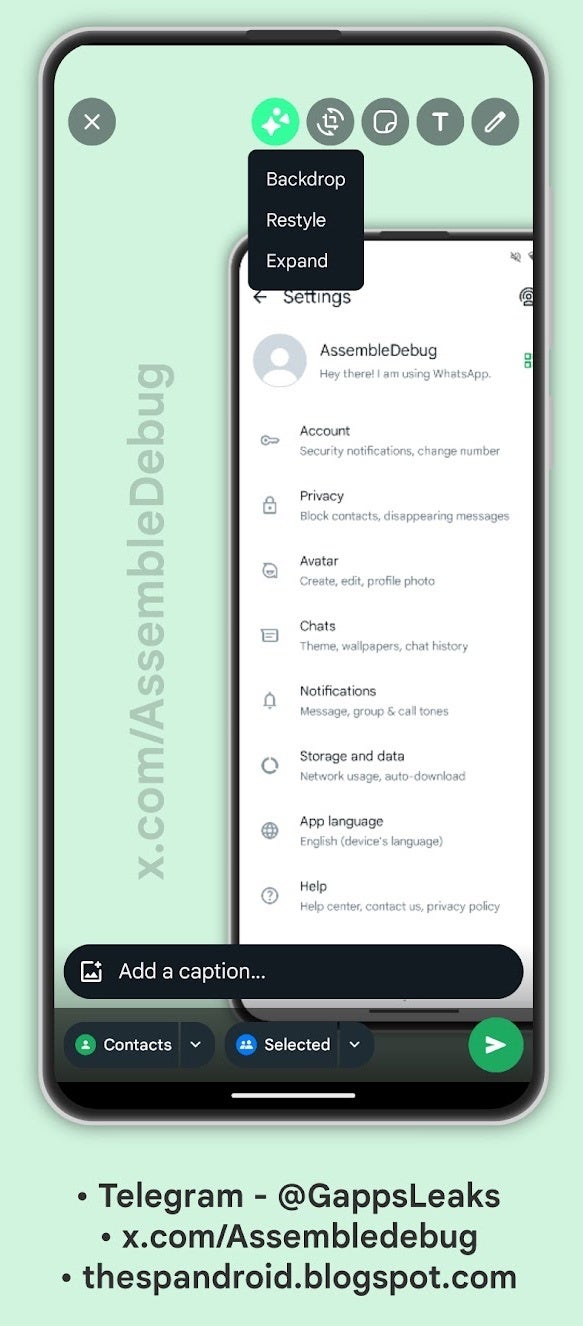
The tools were discovered during a code deep dive by @AssembleDebug of TheSPAndroid in version 2.24.7.13 of the WhatsApp Android beta app, revealing a variety of advanced editing options for users to enhance their photos with ease. These are not yet available to users but were enabled with some code tweaking. Among them are:

  • Backdrop: AI will generate your ideal background based on what you describe and replace it for you.
  • Restyle: Adds a splash of artistic flair to your images by applying AI-generated filters and styles.
  • Expand: This feature is believed to seamlessly extend your image’s background, intelligently filling in the gaps.

Source: TheSPAndroid

These tools will reportedly coexist with well-known features like cropping and stickers in WhatsApp’s current image editor under the “sparkle” icon. This news follows Meta’s (WhatsApp’s parent company) announcements of similar AI editing features for Instagram and Facebook. WhatsApp following those footsteps signals the company’s intention to bring these advanced tools to all of its user base across the apps currently under the Meta umbrella.

It’s worth noting that similar AI-driven features, like background expansion, already exist in established tools like Adobe Photoshop. However, while these existing competing products offer these tools, they are definitely far from perfect, although they have been getting better and better as time progresses and the technology becomes more advanced. This puts pressure on WhatsApp to deliver an intuitive and impressive user experience in order to stand out.

It seems these features are still in the early development phase and might not show up for some time in the stable version of the app. This means we will have to wait a bit longer to see exactly how AI will play a part in how users edit and share photos on WhatsApp.

[ad_2]
Source link
Google Keep testing an AI-assisted “help me create a list” feature and a new floating toolbar

0
[ad_1]
Google is steadily infusing its AI capabilities across its various products, and the latest recipient of this is Google Keep. The note-taking app now has a new feature that allows users to quickly create task lists and reminders using Gemini, Google’s AI-powered assistant.

Following the introduction of Gemini Workspace features for personal accounts, Google Keep is the latest app to receive an AI boost. Spotted by 9to5Google and Android expert Mishaal Rahman, a new experimental feature, “Help me create a list,” is now being tested with some Android users.

How does it work?

This generative AI tool simplifies list making. When creating a new Google Keep note, you’ll spot a wide “Help me create a list” button. Tap it, enter your list topic, and the AI generates a starting point for your list. The more detail you provide, the better the results, and you can also give feedback with a thumbs up or down to refine the AI’s suggestions over time.

“Help me create a list” joins the “Help me write” feature in Gmail as a mobile-focused use of Google’s Gemini AI. Other Gemini Workspace features currently focus on web apps like Docs, Sheets, Slides, and Meet.

A new look for Google Keep

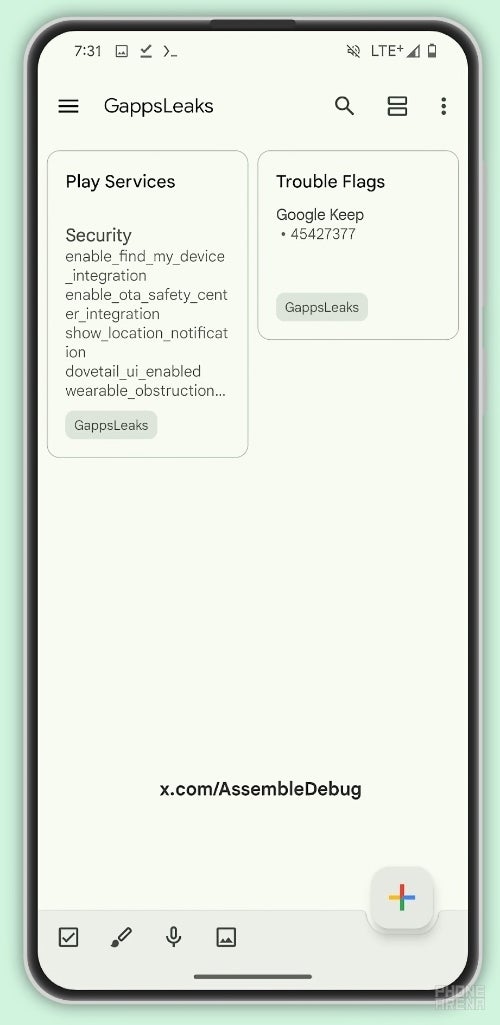
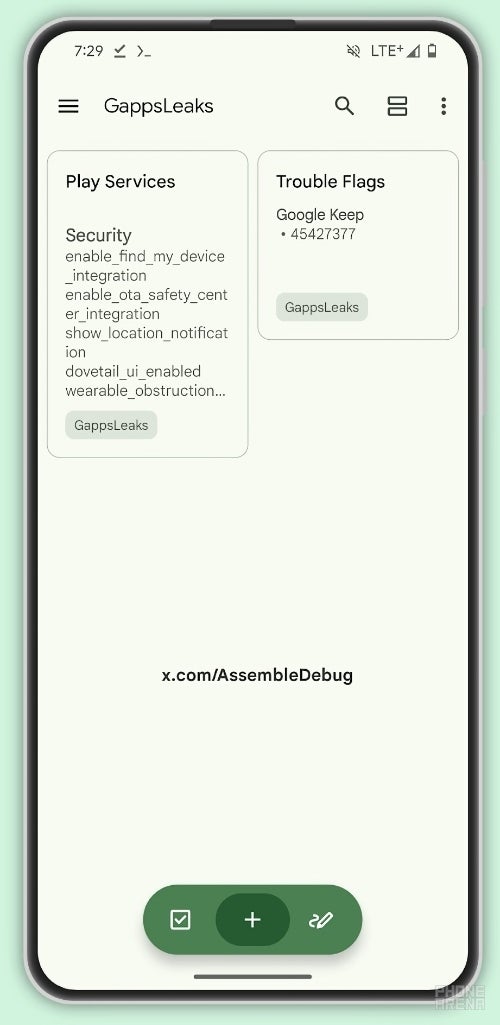
In addition to the AI addition, Google Keep is also testing a new floating bottom toolbar similar to the one that was recently rolled out to the Google Chat app. The separate buttons for audio and photo notes will disappear in favor of this more manageable bar, with these options available within a note.

Old vs. New Google Keep bottom toolbar

This new look was spotted by @AssembleDebug of TheSPAndroid in version 5.24.102 of the app and enabled via a flag, meaning it is not yet available to the public. However, once enabled, it was found to include options to quickly create a list or a drawing on either side and housing a central “new note” button. Notably, it uses Google’s Dynamic Color customization, and its smaller footprint allows for more note content to be visible at a glance.

[ad_2]
Source link