First smartphone with Snapdragon 8s Gen 3 is now official

0
[ad_1]

The very first smartphone with the Snapdragon 8s Gen 3 processor is now official. The device in question is called the Xiaomi Civi 4 Pro, and it was announced in China.

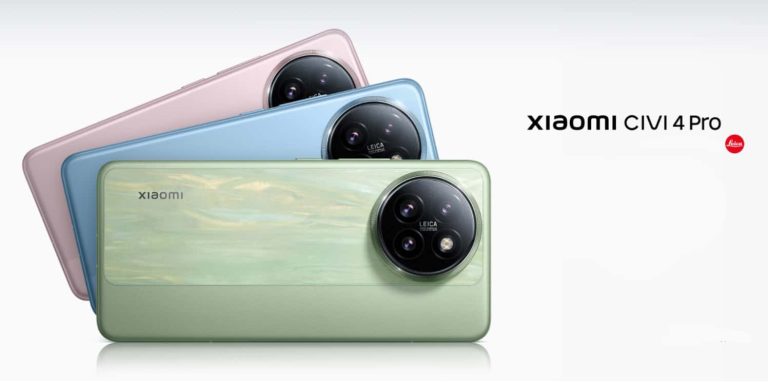
As you can see in the provided images, the device has flat sides and a flat display. There is a circular camera island on the back, in the top-left corner. Three cameras sit in there, and that module does protrude on the back.

The Xiaomi Civi 4 Pro is the very first smartphone fueled by the Snapdragon 8s Gen 3

You will notice a pill-shaped camera cutout on the front. That cutout is centered, and the bezels around the display are very thin. The phone’s backplate is flat, though it curves towards the frame on the edges.

The Xiaomi Civi 4 Pro features a 6.55-inch 2750 x 1236 OLED display with a 120Hz refresh rate. Its peak brightness is at 3,000 nits, and it supports HDR10+ content and Dolby Vision. 2,160Hz PWM dimming is also a part of the package.

The Snapdragon 8s Gen 3 fuels it, of course. Xiaomi included 12GB/16GB of LPDDR5X RAM here, and 256GB/512GB of UFS 4.0 flash storage. HyperOS comes pre-installed, while there are two nano SIM card slots included here too.

It supports 67W charging, and features an IR blaster at the top

A 4,700mAh battery sits inside the phone, and 67W wired charging is supported. The phone has an in-display fingerprint scanner, an optical one. An IR blaster sits at the very top of the phone.

A 50-megapixel main camera (Light Fusion 800 sensor, f/1.63 aperture, Hyper OIS, Leica Summilux lens) is backed by a 12-megapixel ultrawide unit (120-degree FoV, f/2.2 aperture, OmniVision OV13B10 sensor), and a 50-megapixel telephoto camera (2x optical zoom, f/1.98 aperture, OIS, Samsung JN1 sensor).

On the front, you’ll find a 32-megapixel main camera and a 32-megapixel secondary unit. One of them uses an OmniVision sensor, and the other a sensor from Samsung’s ISOCELL. The viewing angles are 78 degrees and 100 degrees, respectively.

It supports Bluetooth 5.4 and comes in four colors

The company did include a set of stereo speakers here, and Dolby Atmos support as well. Bluetooth 5.4 is supported, as is 5G connectivity.

The Xiaomi Civi 4 Pro comes in Sprpint Wild Green, Soft Mist Pink, Breeze Blue, and Starry Black colors. You can check them all out below. The pricing starts at CNY2,999 ($416) in China. Chances are that this phone will stay exclusive to China.


[ad_2]
Source link
Qualcomm intros Snapdragon 7+ Gen 3 with generative AI

0
[ad_1]

Qualcomm has officially announced the latest mobile platform in its Snapdragon 7 series, the Snapdragon 7+ Gen 3, which is poised to power the next generation of mid-range smartphones and drive the possibilities of on-device AI functions.

With deep integrations of generative AI capabilities, the Snapdragon 7+ Gen 3 is set up to deliver some exciting AI innovations for upcoming devices. Notably with support for multiple AI models including Large Language Models like Baichuan-7B, Llama 2, Gemini Nano, and Zhipu ChatGLM.

The Snapdragon 7+ Gen 3 will also be the first in the lineup to support Wi-Fi 7 technology. Further enhancing devices that use this mobile platform when it comes to ultra-fast wireless connectivity capabilities. “Snapdragon 7+ Gen 3 is packed with support for incredible on-device generative AI features and provides incredible performance and power efficiency while bringing Wi-Fi 7 to the Snapdragon 7 Series for the first time,” said Chris Patrick, senior vice president and general manager of mobile handsets at Qualcomm Technologies.

Wi-Fi 7 is still very new and there won’t be a lot of support for it just yet. But it promises tons of benefits over Wi-Fi 6 and Wi-Fi 6E. Including big boosts to speed. For mobile devices, the benefits of Wi-Fi 7 support are potentially just as vast. But one notable benefit of it is the improvements it can make to cloud gaming. Cloud gaming is something you would likely do a lot from your phone. Since it’s sort of the best use case for it right now. So, the inclusion of Wi-Fi 7 support is going to be great for phones running on this mobile platform. Though that’s hardly where it’ll end.

OnePlus will be one of the first smartphone brands to adopt the Snapdragon 7+ Gen 3

The Snapdragon 7+ Gen 3 will be a boon for mid-range devices. But it’s not yet clear which devices will be using this mobile platform. Qualcomm does, however, confirm some of the brands you’ll see picking it up. OnePlus will be one of the first brands to use the Snapdragon 7+ Gen 3, alongside other manufacturers like Realme and SHARP. Qualcomm says the first device to use this mobile platform will be announced in the next few months, but it’s staying tight-lipped about who the device comes from.

The chipset delivers a notable boost to photography and performance

View of pink flowering trees in park during autumn,Nami Island,South Korea

Qualcomm doesn’t delve too much into the specifics here but the Snapdragon 7+ Gen 3 does deliver some performance boosts. It’s tough to say if end users will notice these improvements. But they are there and chances are some consumers will pick up on it. Qualcomm says the Snapdragon 7+ Gen 3 has a 15% boost to CPU performance so usage on devices that have this chipset should feel snappier to the user.

Where performance boosts might be more noticeable is with any sort of tasks that are dependent on the GPU. Such as gaming. Because Qualcomm states there’s a 45% boost to GPU performance. The platform also delivers “top-notch photography features” with a little help from the generative AI capabilities, as well as support for spatial audio and LE audio. Overall any devices running on this platform are likely to be pretty decent. At least where the computing power is concerned.


[ad_2]
Source link

Epic is bringing its Games Store to iOS and Android platforms

0
[ad_1]

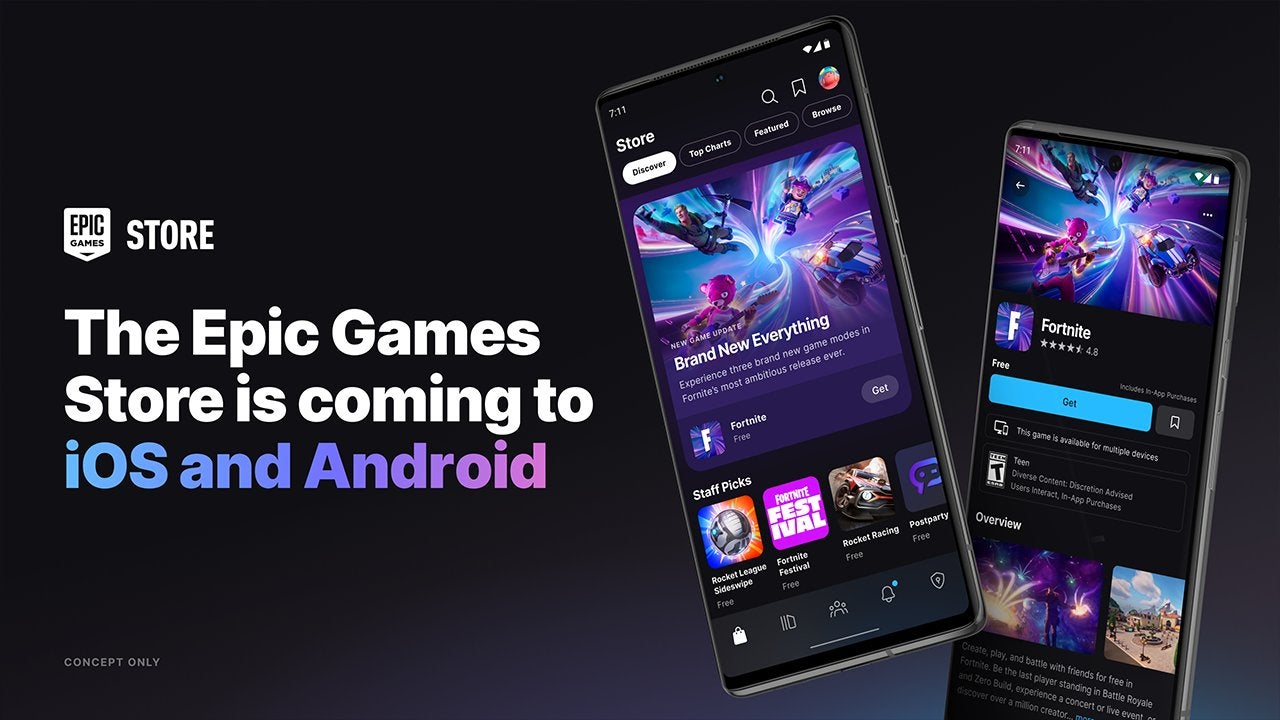
One of the biggest digital distribution online stores, Epic Games Store, is coming soon to iOS and Android platforms. The announcement was posted earlier today on Twitter in the form of a teaser, but no additional details were provided by Epic Games Store’s official account.

And since we’re talking about a distribution store, Epic couldn’t miss the chance to take a jab at Apple. The teaser claims that the upcoming Epic Games Store for mobile devices will offer “same fair terms, available to all developers, on a true multi-platform store – with amazing games for everyone.”

Epic and Apple have been trading blows over App Store fees for many years. The culmination of the conflict between the two giants peaked when Apple decided to remove Fortnite from the App Store.

Even after EU’s Digital Markets Act entered into force early this month, Apple defied the new regulations and removed Epic’s account from its store. Although the account was reinstated after a few days (and an expensive bill in the form of a €2 billion fine), it seems that Apple continues to play by its own rules.

Currently, Apple’s App Store and Google’s Play Store are the biggest, most popular app stores for Android and iOS devices, but a third alternative is definitely a good thing for developers, especially if the Epic Games Store will have lower fees than the other two.

[ad_2]
Source link

Authorities Dismantle Grandoreiro Banking Malware Operation

0
[ad_1]

Group-IB, a cybersecurity firm, helped INTERPOL and Brazil dismantle the Grandoreiro banking trojan operation, as their expertise in threat intelligence and investigation was key. 

Malware samples collected during independent investigations in Brazil and Spain (2020-2022) were analyzed by Group-IB and other partners, which helped track the constantly shifting infrastructure of the attackers and pinpoint the active command and control server. 

The combined effort led to the arrest of five administrators in January 2024.

Grandoreiro, a major threat since 2017, used phishing emails mimicking legitimate organizations to target victims in Spanish-speaking countries. 

The malware steals financial data by employing a multi-pronged approach, which monitors keystrokes to capture login credentials, simulates mouse clicks for potentially fraudulent transactions, shares the victim’s screen for real-time hijacking, and displays deceptive pop-ups to trick users into compromising information.

Targeting bank accounts, the malware specifically gathers usernames and bank identifiers, granting unauthorized access, which enables criminals to completely control the victim’s account and siphon funds. 

To launder the money, they employ a money mule network, likely transferring stolen funds to Brazil and estimates suggest the malware has defrauded victims of over EUR 3.5 million, with potential losses exceeding EUR 110 million if attempted thefts were successful. 

In response to a cybercrime campaign targeting Spanish banks with Grandoreiro malware, Brazilian and Spanish authorities independently collected samples between 2020 and 2022. 

To improve their investigations, they collaborated with INTERPOL’s Cyber Crime Unit, and Group-IB, a cybersecurity firm, joined the effort to analyze the malware samples. 

Their threat intelligence and cyber investigation specialists played a key role in dissecting the Grandoreiro samples, enabling investigators to track the malware’s ever-changing network infrastructure and pinpoint the command and control server’s IP address. 

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

Brazil and Spain leverage INTERPOL’s network and expertise

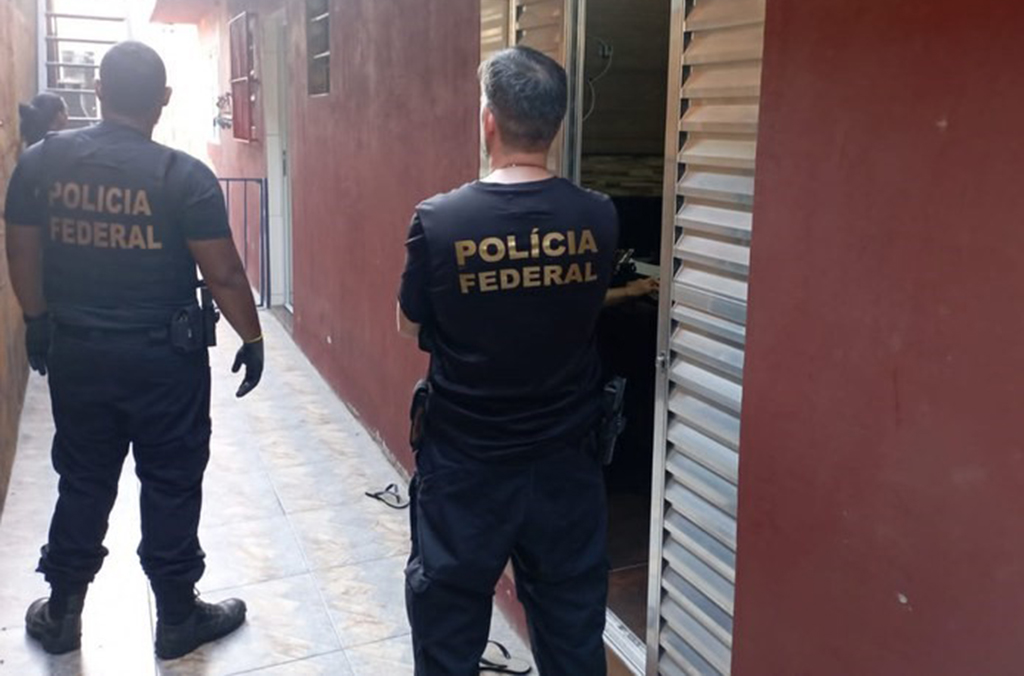
In August 2023, Brazil conducted raids across five states, arresting the programmers and operators behind the Grandoreiro banking malware. 

Police officers conducting the raids

INTERPOL’s Cyber Crime Unit Director, Craig Jones, emphasized the importance of information sharing in a successful cybercrime operation, highlighting INTERPOL’s role as a bridge between law enforcement and private entities in facilitating intelligence exchange. 

The collaboration paves the way for further regional cooperation against cybercrime, as INTERPOL is actively supporting ongoing investigations in Brazil, Spain, and other member countries. 

Group-IB’s investigation tracked a continuously evolving malware network infrastructure, identified the active C2 server IP, and shared it with INTERPOL to help in their operation. 

The operation resulted in the apprehension of five individuals responsible for the banking malware and court orders froze and seized assets, dismantling the criminal organization’s financial infrastructure and potentially recovering stolen funds.  

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Vivo X Fold 3 Pro price will be sky-high, details emerge

0
[ad_1]

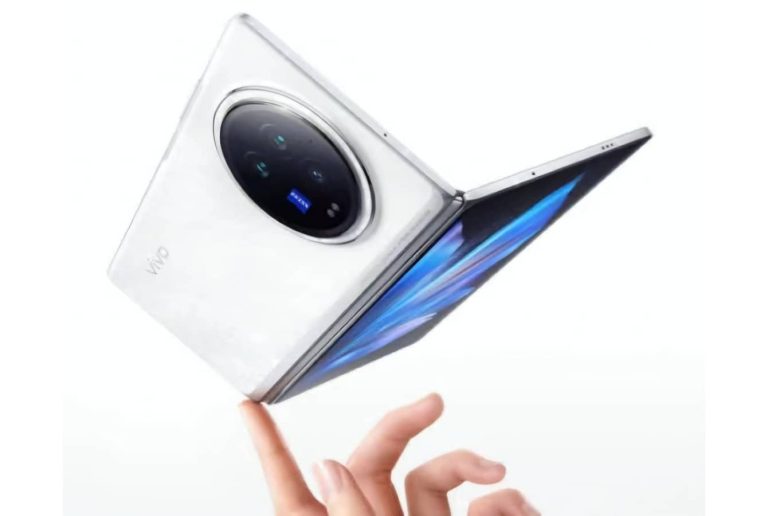
The Vivo X Fold 3 series will arrive on March 26. That’s the launch date that Vivo scheduled for China. Some more details surfaced, and it seems like the Vivo X Fold 3 Pro price will be sky-high.

The Vivo X Fold 3 Pro price tags have been revealed and they’re… extremely high

According to a promo poster shared by Whylabs, the device is coming in two configurations. The cheaper one will include 16GB of RAM and 512GB of storage, while the top-end one will arrive with 16GB of RAM and 1TB of storage.

The two models are set to cost CNY13,999 and CNY14,999. Transferred to dollars, those price tags read $1,945 and $2,083. Needless to say, these price tags are very high.

Vivo X Fold 3 Pro price tags leak

These prices are actually extremely high for foldables in global markets, let alone in China. Chinese prices are usually considerably lower. For example, the Xiaomi 14 starts at the equivalent of $546 in China, while globally it starts at €999 ($1,092).

Its price tag in markets outside of China would be ultra-premium

You can see a huge difference here. So imagine what would the price of the Vivo X Fold 3 Pro be if it actually arrived to global markets. With such differences, we’re looking at a price tag of over $2,500 most likely. That’s actually a detail that leads us to believe it’ll stay exclusive to China.

In any case, the company already revealed the design of the Vivo X Fold 3 series. You can check out the gallery below if you’d like to take a closer look at it.

Some spec details did get revealed already


What we know so far is that the Snapdragon 8 Gen 3 will fuel the Vivo X Fold 3 PRo. An 8.03-inch main display was mentioned, and a 6.53-inch cover panel. Samsung’s E7 AMOLED display will be used on both ends. A 120Hz refresh rate will be on offer, and both panels will be quite bright.

Powerful cameras are also tipped, and a 5,700mAh battery. The device is also said to support 120W wired charging and 50W wireless charging. We’ll know far more on March 26.


[ad_2]
Source link

YouTube TV’s Multiview feature now available on iOS devices

0
[ad_1]

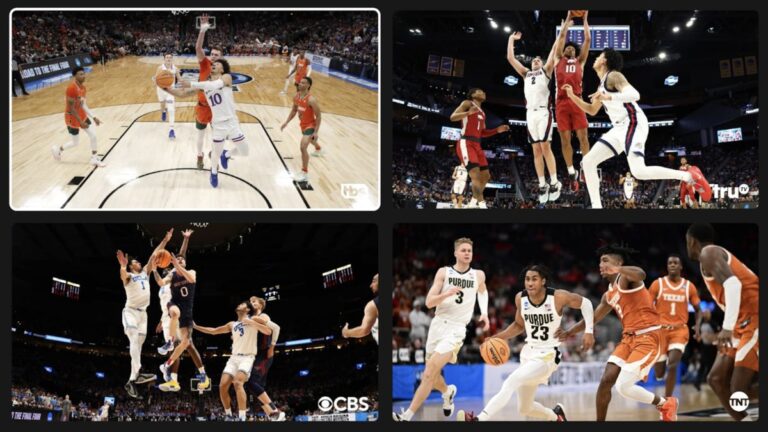
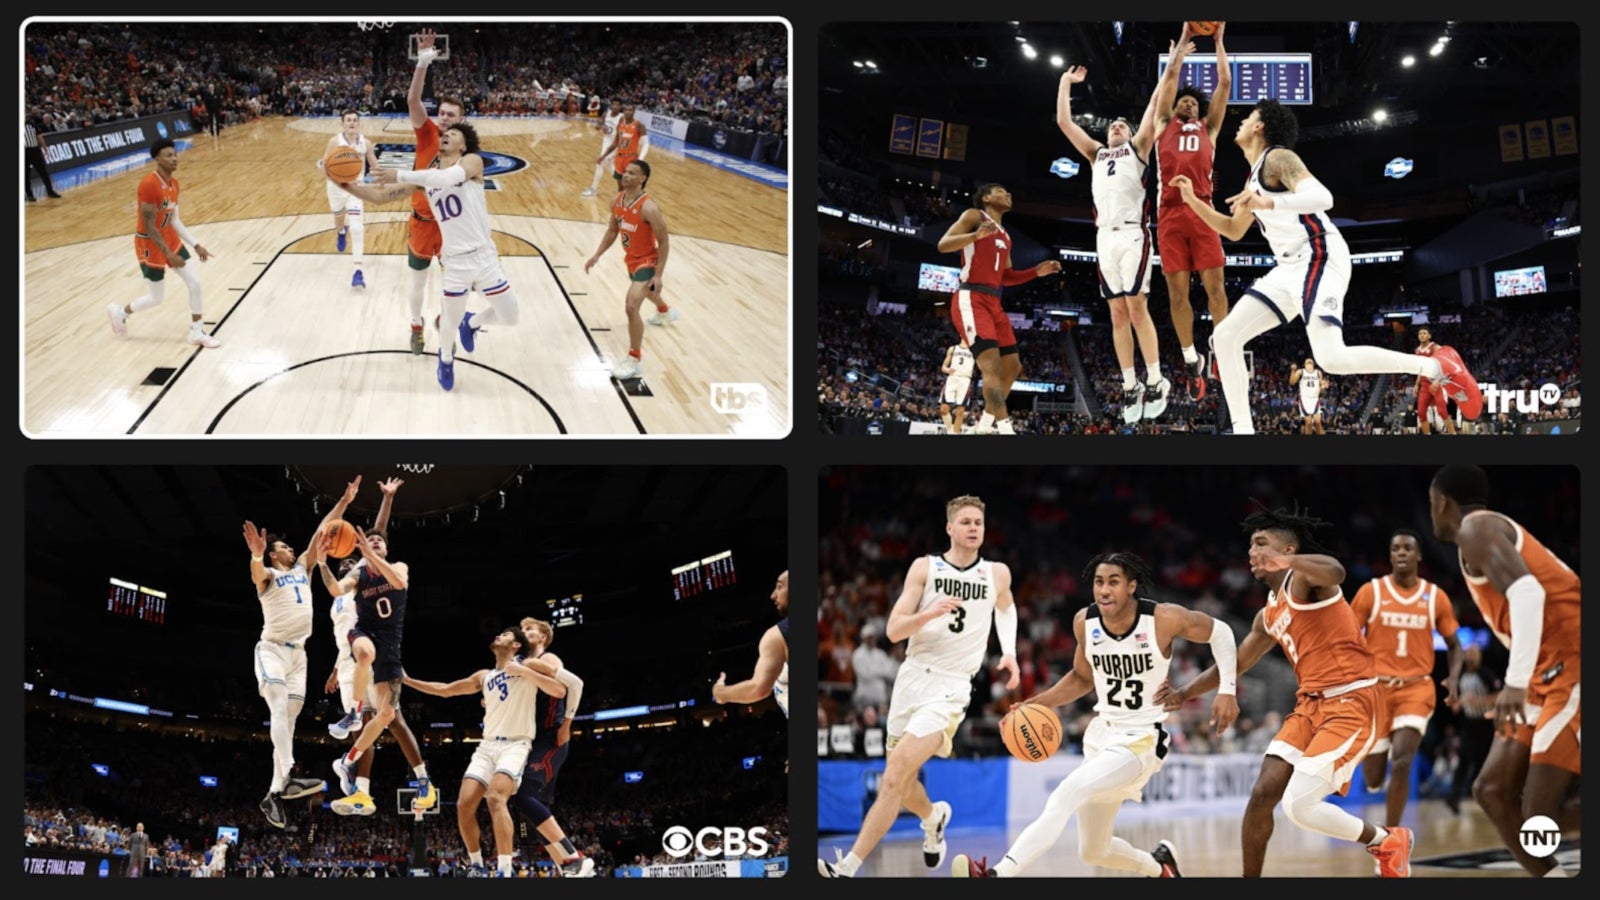
Google is working on a Multiview feature for YouTube TV and while some users benefit from having it, not everyone has access to this perk yet. Initially released on TVs, Multiview is now rolling out to iPhone and iPad, YouTube TV recently confirmed.

According to YouTube, in order to have access to Multiview, iPhone and iPad users must update the YouTube TV to version 8.11 (or a newer version).

The move doesn’t come as a surprise considering the fact that many users discovered that they received access to Multiview ahead of this week’s global rollout.

Although the iOS and TV versions of Multiview aren’t on par when it comes to functionality, at least it’s a start and Google can further improve the experience on iPhone and iPad.

As far as Android goes, it appears that Google isn’t really in a hurry to provide this feature to users of its mobile operating system. YouTube TV for Android will be getting the Multiview feature “in the coming months,” Google says, so there’s no actual ETA yet.


[ad_2]
Source link

Hackers Claimed to Breached the Israeli Nuclear Facility’s Network

0
[ad_1]

An Iranian hacker group has claimed to have infiltrated the networks of the Dimona nuclear facility located in Israel’s Negev desert.

Israeli cybersecurity teams are diligently working to verify the authenticity of the documents allegedly leaked during this cyber incident.

The details of these documents are currently under Israeli government censorship, which indicates the potential sensitivity of the information contained within them.

The leaked documents are said to encompass a range of materials, from invoices to internal correspondence, which could provide insights into the operations of one of Israel’s most secure facilities.

The full extent of the breach and the nature of the documents remain unclear as investigations continue.

Israeli Government and Cybersecurity Experts Respond

The Israeli government has not yet released an official statement regarding the breach. However, cybersecurity experts have been quick to weigh in on the situation.

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

CheckPoint Software, a leading Israeli cybersecurity firm, has noted that the hackers’ tactics are consistent with previous cyberattacks attributed to Iranian groups.

These attacks often involve releasing a threatening video to instill fear and uncertainty.

Experts have also expressed skepticism about the hackers’ claims, particularly the assertion that the town of Yeruham, located less than 10 miles from the Dimona facility, should be evacuated.

The hackers ominously stated that they have “their hand on the switch,” implying a level of control that cybersecurity professionals consider to be exaggerated.

As per the report by JNS, the hackers have boasted about obtaining thousands of documents, including PDFs, emails, Excel spreadsheets, Word files, and PowerPoint presentations.

Analysis by Cybersecurity Professionals

Cybersecurity analysts have been downplaying the severity of the hack, suggesting that the documents obtained are likely unclassified and not indicative of a significant security breach.

Experts agree that the hackers’ claims are overstated and that the actual risk posed by the leaked documents may be minimal.

Nevertheless, the incident has raised concerns about the robustness of cybersecurity measures at critical infrastructure sites.

It underscores the ongoing cyber warfare between nations and the need for constant vigilance in protecting sensitive information.

As the situation unfolds, the Israeli government and cybersecurity community will continue to assess the impact of the alleged breach.

The international community will be watching closely, as the implications of such an attack could have far-reaching consequences for national security and the geopolitical landscape.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Windows Server Updates Trigger Domain Controller Failures

0
[ad_1]

Recent updates for Windows Server have been linked to significant disruptions in IT infrastructure, with numerous reports of domain controllers experiencing crashes and forced reboots.

The issues have been traced back to the March 2024 cumulative updates for Windows Server 2016 and Windows Server 2022, explicitly KB5035855 and KB5035857.

Impact on Domain Controllers

The core of the problem lies in a memory leak within the Local Security Authority Subsystem Service (LSASS), a critical component of the Windows operating system responsible for enforcing security policies and managing user logins, access token creation, and password changes.

The LSASS process is essential for the stable operation of domain controllers, which are pivotal in managing network security and user authentication within an organization’s IT environment.

Administrators have observed that domain controllers exhibit steadily increasing LSASS memory usage after installing the March updates.

This escalation in resource consumption eventually leads to the system becoming unresponsive, culminating in crashes and automatic reboots.

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

Such behavior disrupts normal business operations and poses a risk to network security and data integrity.

Causes of Crashes and Reboots

The LSASS memory leak introduced by the updates is the direct cause of the crashes and reboots.

Memory leaks occur when a program incorrectly manages memory allocations, reducing performance and system stability as the available memory is gradually exhausted.

In the case of domain controllers, the LSASS process’s memory leak leads to an unsustainable load on the system, forcing a crash as a last resort to recover from the failure.

Affected Windows Server Versions

The reported issues specifically affect Windows Server 2016 and Windows Server 2022.

These versions are widely used in enterprise environments, meaning the impact of the problem is potentially vast, affecting organizations globally.

This is not the first time LSASS-related issues have been reported after Windows Server updates—previous incidents were recorded in December 2022 and March 2022—which raises concerns about the recurring nature of such critical vulnerabilities.

The sysadmin community has been vocal about the disruptions, with many taking to online forums such as Reddit to share their experiences and seek advice. Comments range from frustration over the repeated nature of these issues to concerns about the lack of immediate solutions or workarounds.

Some users have reported rolling back the updates as a temporary fix, while others are waiting for Microsoft’s official response or patch.

A particular comment on the Microsoft Tech Community Exchange Team Blog highlights the severity of the issue, with one user stating, “This is a disaster. We’ve had to roll back the updates on all our DCs to prevent the entire network from going down.”

LSASS Process Memory Leak

The LSASS process memory leak is not new, but its recurrence is troubling for Microsoft and its user base.

The memory leak leads to a gradual increase in memory usage by the LSASS process until the system can no longer function properly. This type of issue requires prompt attention and resolution to maintain the security and stability of affected systems.

Microsoft has not released an official statement or solution regarding the March 2024 updates and the resulting domain controller crashes.

This situation underscores the importance of thorough testing and quality assurance in software updates, mainly when they affect critical components of enterprise IT infrastructure.

As the situation develops, system administrators are advised to monitor official channels for updates and consider holding off on applying the problematic updates until a fix is confirmed.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

This is why you need a VPN on your devices

0
[ad_1]

We all know that it’s not particularly safe to join a public Wi-Fi network, where hackers and snoops can easily access your private data and wreak havoc with your devices.

What many of us don’t realize, however, is that browsing at home on our own secure Wi-Fi connections isn’t that much safer—at least, not if you don’t have a VPN like Surfshark installed.

If you’re not yet up to speed on this essential feature of modern internet security, a VPN—which stands for “Virtual Private Network”—uses encryption and anonymous servers to shield your internet data from prying eyes.

The technology behind VPNs is complicated, but in a nutshell, it replaces your IP address—a highly specific string of numbers denoting your real-world location, ISP, and a whole lot more—with an address linked to a server used anonymously by thousands of other people.

Without a VPN, collecting your data is about as difficult for a hacker as looking you up in the Yellow Pages. With a VPN, you’re about as easy to find as a specific water molecule in the Pacific ocean.

Internet security is the main reason that most users install a VPN. It lets them browse the internet safely and privately, even when their devices are connected to public wi-fi, where “man in the middle” attacks are commonplace.

But they do so much more.

For a start, a VPN lets you avoid those creepy targeted ads that seem to know exactly how old you are, where you live, and what kind of stuff you like to buy.

If marketers don’t know who you are, they can’t get all up in your face with quasi-personalized recommendations, leaving you free to make your own mind up in peace.

Then there’s the question of censorship and regional restrictions. The internet isn’t the same place for every country in the world, with many governments blocking certain types of content for political reasons.

Multiplatform iOS + macOS + TV

Likewise, companies often restrict the flow of content by region for commercial reasons. Ever tried Canadian Netflix? It’s a blast, and only people in Canada get to enjoy it.

A VPN lets you get around this problem by simply connecting your computer to an anonymous server in Canada.

Or, if you live in Canada but happen to be on holiday elsewhere, a VPN lets you connect with your native land and access your region-locked banking apps, local news services, and, yes, Netflix.

Plus, a VPN gives you access to region-locked video game betas, YouTube content, and much more.

Which, by the way, is not an invitation to do anything illegal online, safe in the knowledge that you won’t be caught. The terms of service for VPNs like Surfshark insist that users comply with all applicable laws—so behave yourself.

Security and access to restricted content are two of the best reasons to start using a VPN, but the list doesn’t stop there.

A VPN also solves the problem of ISP throttling, by preventing your ISP from knowing where traffic on its network is coming from. And you can use a VPN to get the best deals since the prices of products and services often vary by region.

If you’re looking to join the VPN movement, you could do a lot worse than take advantage of Surfshark’s current 83% off + two months free offer.

Surfshark is an award-winning option, and right now it’s an absolute steal.


[ad_2]
Source link

Neuralink’s brain-chip patient is playing Civilization VI for 8 hours straight with his mind

0
[ad_1]

In 2024, we may not have the flying cars people in the 1950s envisioned, but we already have a human with a chip installed in its brain that’s allowing him to do incredible stuff.

Like playing chess, and playing Civilization VI for 8 hours straight – all just by thinking about it, without actually interacting with the games’ interface.

Reuters reports the latest developments on Neuralink’s first brain-chip patient: 29-year-old Noland Arbaugh.

Neuralink is a neurotechnology company founded by Elon Musk with the goal of developing implantable brain–machine interfaces (BMIs). Its primary aim is to enable humans to communicate directly with computers and to enhance cognitive capabilities, potentially offering solutions for neurological conditions and integrating artificial intelligence with human cognition.

Also, Neuralink – and companies alike – is what gives many people nightmares. Yup, misuse of technology can and does happen, so brace yourselves.

Back to Neuralink’s first brain-chip patient, though. Neuralink livestreamed the patient using only his mind to play online chess.

Noland Arbaugh was paralyzed below the shoulder after a diving accident, and is now able to play chess on his laptop. The implant seeks to enable people to control a computer cursor or keyboard using only their thoughts.

“The surgery was super easy. I literally was released from the hospital a day later. I have no cognitive impairments. I had basically given up playing that game,” Arbaugh said, referring to the game Civilization VI, “you all (Neuralink) gave me the ability to do that again and played for 8 hours straight.”

In January, Neuralink implanted the chip in his brain, after receiving approval for human trial recruitment in the Fall of 2023. Back in 2022, the Neuralink project entered its human trial phase – prior to that, Neuralink carried out testing with primates, killing 15 of the 23 test monkeys.

Now, the patient zero with a brain chip appears to have fully recovered. This is great, but it’s remarkable that the patient is able to control a computer mouse using their thoughts, the startup’s founder Elon Musk said a month ago.

“Progress is good, and the patient seems to have made a full recovery, with neural effects that we are aware of. Patient is able to move a mouse around the screen by just thinking”, Musk said.


[ad_2]
Source link