Hackers Stolen 70 Million AT&T Sensitive Customers Data

0

[ad_1]

Cybersecurity researchers at vx-underground have reported that over 70 million records from an unspecified division of telecommunications giant AT&T have been leaked online.

The breach, one of the largest in recent times, has raised serious concerns about data security and privacy.

The Breach Exposed

The leaked data, posted on the hacker forum Breached, contains 73,481,539 records.

Document

Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

Vx-underground researchers have confirmed the authenticity of the data.

However, it remains uncertain whether the information was directly stolen from AT&T or through a third-party organization associated with the company.

Hacker Group Behind the Leak

The individual responsible for the data sale uses the online alias, Major Nelson. They claim the data was acquired from an unnamed AT&T division by the notorious hacker group @ShinyHunters in 2021.
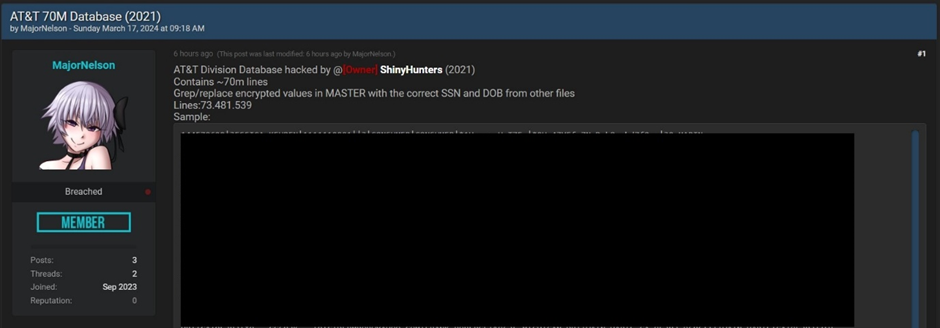
 AT&T Database
AT&T Database

ShinyHunters is infamous for its cyberattacks on several significant organizations, including Tokopedia, Homechef, Chatbooks.com, Microsoft, and Minted.

Security Affairs has reported that threat actors have leaked over 70 million records, which they allegedly stole from AT&T.

Data For Sale

In August 2021, ShinyHunters reportedly demanded $1 million for the entire database or $200,000 for partial access.

The RestorePrivacy website verified the authenticity of the data by analyzing a sample and finding it legitimate.

The leaked data includes sensitive customer information such as Name, Phone number, Physical address, Email address, Social security number, Date of birth, Sample Data Leak

AT&T’s Response

Despite the claims and the evidence presented by researchers and the hacker group, AT&T has denied any breach of their systems.

The telecommunications giant said in a statement, “Based on our investigation Thursday, the information that appeared in an internet chat room does not appear to have come from our systems.”

Implications for Customers

The alleged data breach threatens the affected customers, with the potential for identity theft, financial fraud, and other malicious activities.

The data in question could be used by cybercriminals to orchestrate targeted phishing attacks or to sell to other bad actors on the dark web.

As the situation unfolds, AT&T customers are advised to remain vigilant and monitor their accounts for suspicious activity.

It is also recommended that passwords be changed and credit monitoring services be considered to safeguard against potential identity theft.

With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
OSINT Tool To Detect Leaked Databases

0

[ad_1]

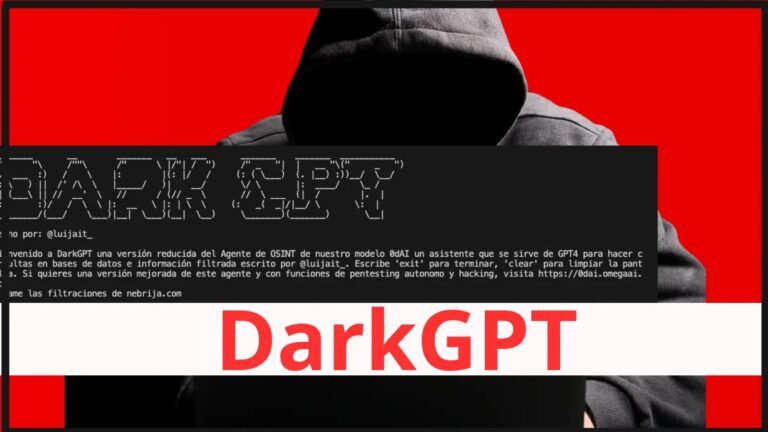
DarkGPT, your next-level OSINT (Open Source Intelligence) assistant. In this digital era, the ability to sift through vast amounts of data is invaluable, and DarkGPT, leveraging the power of GPT-4-200K, is designed to query leaked databases with precision.

A Spanish pentester with a “luijait” alias on Github recently unveiled an AI OSINT tool dubbed “DarkGPT” that helps detect leaked databases.

This resource article will guide you through the installation, setup, and usage of DarkGPT, ensuring you can integrate this powerful tool into your OSINT workflows.

Various tools powered by ChatGPT, such as OSINVGPT, PentestGPT, WormGPT,  BurpGPT and HackerGPT, have already been created for the cyber security community, and DarkGPT is now adding to this legacy.

Document

Free Webinar: Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

DarkGPT Installation:

Before diving into the world of DarkGPT, ensure that your system is equipped with Python, as the tool has been tested with Python 3.8 and higher versions. The installation process begins with cloning the DarkGPT repository from GitHub. Open your terminal and execute the following command:

git clone https://github.com/luijait/DarkGPT.git
cd DarkGPT

This will download the necessary files to your local machine and navigate you into the project directory.

Configuration:

To tailor DarkGPT to your needs, you’ll need to configure some environment variables. Start by duplicating the .env.example file and renaming it to .env. This file should be edited to include your personal API keys and usernames:

DEHASHED_API_KEY="your_dehashed_api_key_here"
DEHASHED_USERNAME="your_dehashed_username"
OPENAI_API_KEY="API_KEY from openai.com"

These credentials are crucial as they allow DarkGPT to interact with the respective APIs and databases securely.

Installation of Dependencies:

DarkGPT relies on several Python packages to function correctly. Install these dependencies by running the following command in your project directory:

pip install -r requirements.txt

This command will ensure all necessary libraries are installed, setting the stage for DarkGPT’s optimal performance.

DarkGPT Usage

With DarkGPT installed and configured, you’re ready to harness its capabilities. The tool can be invoked through the command line, where you can input your queries and receive insights from leaked databases. The intuitive interface of DarkGPT makes it user-friendly, even for those new to OSINT tools.

DarkGPT stands out with its robust features, including:

  • Integration with GPT-4-200K for advanced data processing.
  • Secure querying of leaked databases for comprehensive OSINT gathering.
  • Easy-to-use command-line interface for efficient operations.
  • Customizable environment settings to fit your specific intelligence needs.

DarkGPT is a potent addition to any OSINT professional’s toolkit. By following this course, you’ve equipped yourself with the knowledge to install, configure, and effectively use DarkGPT.

Integrating this AI assistant into your processes will unlock new possibilities for data analysis and intelligence gathering. Remember to use DarkGPT(GitHub) responsibly and in compliance with legal and ethical standards.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
U.S. Intelligence Agencies say that they have no proof that TikTok is a national security threat

0

[ad_1]

The Protecting Americans from Foreign Adversary Controlled Applications Act bill passed the House last week with approval from both sides of the aisle. The vote count was 352-65 in favor of the bill which now heads to the Senate where it faces a tougher time getting through. President Joe Biden already said that should the bill end up on his desk, he will sign it. The proposed legislation will ban apps that require U.S. users to submit a user profile and are under the control of U.S. adversaries such as Russia, China, North Korea, or Iran.

U.S. Intelligence has no proof that TikTok has worked with the Communist Chinese government

As far as TikTok is concerned, the bill would ban the platform in the States unless its owner, Chinese firm ByteDance, divests its holdings in the U.S. unit. The fear is that ByteDance is close to the Communist Chinese government and the personal data it collects on U.S. subscribers to TikTok is sent to a server in Beijing. Despite all of the concerns about TikTok, The Intercept reports that U.S. Intelligence has not been able to procure any evidence that TikTok deals with the Chinese government.
TikTok itself says that it has never shared user data with the Chinese government and would refuse to do so even if asked. TikTok CEO Shou Chew, who testified to Congress almost exactly one year ago, said this past week that as far as TikTok is concerned, “there’s no CCP (Communist Chinese Party) ownership.” Even though U.S. intelligence is fine with going along with lawmakers concerns about TikTok, agencies like the FBI and CIA have yet to find a definitive connection between TikTok and Beijing.

Consider a comment made by CIA Director William Burns to CNN back in 2022. Burns said that it was “troubling to see what the Chinese government could do to manipulate TikTok.” Note that Burns said that he was concerned about what the Chinese government could do with TikTok, not what the government has done.

Also in 2022, FBI Director Christopher Wray made a very similar comment when he said that TikTok’s “parent company is controlled by the Chinese government, and it gives them the potential to leverage the app in ways that I think should concern us.” Like the comment made by Burns, Wray talks about the potential for the Chinese government to use TikTok against the U.S. and doesn’t make it sound as though the FBI has any evidence that such a thing has happened.

Wray said this at another point in 2022, “I would say we do have national security concerns, at least from the FBI’s end, about TikTok. They include the possibility that the Chinese government could use it to control data collection on millions of users or control the recommendation algorithm which could be used for foreign influence operations if they so chose.” The word possibility tells us that the Chinese government has yet to use TikTok to obtain data about Americans.

Many countries, including the U.S., use social media to influence and manipulate citizens in other countries

The potential for the CCP to influence U.S. voters in November weighs on some U.S. government officials. On Tuesday, Director of National Intelligence Avril Haines, the highest-ranking intelligence official in the U.S. government, testified to the House Intelligence Committee and was asked if China would use TikTok to try and influence the 2024 U.S. presidential elections. Haines said, “We cannot rule out that the CCP could use it.”

But the truth is that many countries, including the U.S., use social media in an attempt to influence the outcome of foreign elections. Last Monday, in its annual Intelligence Community threat assessment, the report said, “TikTok accounts run by a [People’s Republic of China] propaganda arm reportedly targeted candidates from both political parties during the U.S. midterm election cycle in 2022.”

Reuters reported this week that when Donald Trump was president, he signed an order authorizing the CIA to use social media to influence and manipulate the public opinion of Chinese citizens. And the U.S. does this sort of thing with other countries and terrorist groups.

None of this matters when TikTok and China are involved as you can tell by the final vote of the proposed legislation in the House. As we said earlier, getting through the Senate is going to be a harder task.

[ad_2]

Source link

Google Phone app loses the Nearby Places search feature on Android

0

[ad_1]

Unsurprisingly, the Phone by Google dialer app is losing the Nearby Places search feature on Android. The change was announced by Google at the beginning of February, and the decision is now being enforced.

As spotted by 9to5google, the ability to search for businesses in the Phone by Google app has been removed. Instead of the “Search contacts & places” field at the top of the app, Google has added a “Search contacts” field that allows users to search for contacts, not places.

Not only that, but it looks like “Nearby Places” has been completely removed from the settings too, but this makes sense since this feature was supposed to use your location when searching for places.

According to Google, the decision to remove the Nearby Places search was based on the fact that “only a very small number of people use this feature.” Additionally, Google claims that the “vast majority of users go to Google Search or Maps when seeking business-related phone numbers.”

When it revealed the change to the Phone by Google app, the search giant said that the feature will be removed “in the coming months.” Well, it looks like the latest update is turning words into reality, so expect to lose this feature very soon if you didn’t already.

[ad_2]

Source link

Dark Web Market Admin Gets 42 Months Prison

0

[ad_1]

Sandu Boris Diaconu, a 31-year-old Moldovan national, has been sentenced to 42 months in federal prison for his role in operating a notorious dark web marketplace known as E-Root.

The sentencing was carried out by U.S. Senior District Judge James Moody, Jr. in Tampa, Florida, marking a pivotal moment in the fight against the illicit trade of compromised computer credentials on the dark web.

Diaconu’s guilty plea on December 1, 2023, came after charges of conspiracy to commit access device and computer fraud, along with possession of 15 or more unauthorized access devices.

His involvement in the E-Root Marketplace, a platform that facilitated the sale of access to compromised computers worldwide, including servers belonging to companies and individuals in the United States, has drawn significant attention from law enforcement agencies.

Document

Mitigating Vulnerability & 0-day Threats

Alert Fatigue that helps no one as security teams need to triage 100s of vulnerabilities.:

  • The problem of vulnerability fatigue today
  • Difference between CVSS-specific vulnerability vs risk-based vulnerability
  • Evaluating vulnerabilities based on the business impact/risk
  • Automation to reduce alert fatigue and enhance security posture significantly

AcuRisQ, that helps you to quantify risk accurately:

The E-Root Marketplace, under Diaconu’s administration, operated across a widely distributed network, employing measures to conceal the identities of its administrators, buyers, and sellers.

Compromised Computer Credentials

This marketplace allowed buyers to search for compromised computer credentials, such as Remote Desktop Protocol (RDP) and Secure Shell (SSH) access, based on various criteria, including price, geographic location, internet service provider, and operating system.

The operation of E-Root and its subsequent takedown is a testament to the collaborative efforts of international law enforcement agencies. Diaconu’s extradition from the United Kingdom in May 2021, following his arrest while attempting to leave the country, underscores the global reach and commitment to dismantling cybercriminal networks.

According to court documents, the E-Root Marketplace was instrumental in the sale of more than 350,000 compromised computer credentials, affecting victims across the globe and spanning all industries.

The marketplace’s operations have been linked to ransomware attacks and stolen identity tax fraud schemes, highlighting the extensive damage and risk posed by such illicit online platforms.

The sentencing of Diaconu is a clear message to cybercriminals about the serious consequences of engaging in the illicit sale of compromised computer credentials.

The U.S. Department of Justice, along with international partners, remains steadfast in its pursuit to disrupt and dismantle dark web marketplaces that threaten the security and privacy of individuals and businesses worldwide.

This case also emphasizes the importance of cybersecurity vigilance and the need for individuals and organizations to protect their digital assets against unauthorized access and exploitation.

As cybercriminals continue to evolve their tactics, the collaborative efforts of law enforcement and cybersecurity professionals are crucial in safeguarding against the pervasive threat of cybercrime.

With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
StopCrypt Ransomware Utilizing Multi-Stage Shellcodes To Evade Detection

0

[ad_1]

A new variant of StopCrypt ransomware has been discovered. It executes multi-stage shellcodes before launching a final payload containing the file encryption code.

This malware uses several techniques, such as detection evasion, a time-delaying loop of 600 million iterations, and several other mechanisms.

Moreover, the ransomware also uses scheduled tasks for its payload execution with command-line arguments, which are executed every five minutes. 

Technical Analysis

According to the reports shared with Cyber Security News, the malware infection cycle begins with creating a string of msim32.dll, but it is not even used in the ransomware execution process. 

Millions of iterations have been set up for a time-delay loop in which the same data is copied to a location with an incremental iteration value.

Similar techniques have been analyzed to be used throughout the malware execution to evade detection.

The evasion is due to the artificial extension time of the malicious code.

Incremental Iteration code (Source: SonicWall)

After this, the code allocates memory, using the LocalAlloc API and VirtualProtect to change the permissions of the memory block to READ, WRITE, and EXECUTE.

First Stage Payload

This stage resolves the required API using the Kernel_GetProcAddress API.

The ransomware creates API function calls by creating the function names or strings that contain the API names directly on the stack.

This is done as a replacement for using straightforward API calls that are easily detected and identified.

The addresses resolved by the malware are for the following APIs:

  • GlobalAlloc
  • VirtualAlloc
  • SetLastError
  • Sleep
  • CreateToolHelp32Snapshot
  • Module32First
  • CloseHandle 

CreateToolhelp32Snapshot is used in the malware code along with all of its modules to take a snapshot of the current process.

Moreover, the information about the first module of the process is extracted using Module32First API.

Snapshot code with all its modules (Source: SonicWall)

Second Stage Payload

The second stage of the malware performs the primary task of the shellcode, which is process hollowing.

The API functions created in this phase are resolved to the following addresses:

  • MessageBoxA
  • GetMessageExtraInfo
  • WinExec
  • CreateFileA
  • WriteFile
  • CloseHandle
  • CreateProcessA
  • GetThreadContext
  • VirtualAlloc
  • VirtualAllocEx
  • VirtualFree
  • ReadProcessMemory
  • WriteProcessMemory
  • SetThreadContext
  • ResumeThread
  • WaitForSingleObject
  • GetModuleFileNameA
  • GetCommandLineA
  • NtUnmapViewOfSection
  • NtWriteVirtualMemory
  • RegisterClassExA
  • CreateWindowExA
  • PostMessageA
  • GetMessageA
  • DefWindowProcA
  • GetFileAttributesA
  • GetStartupInfoA
  • VirtualProtectEx

The ransomware also checks the FileAttributes of a non-existent file for unknown purposes, which is speculated to be used to identify specific systems where the file might be present.

After certain operations, the ransomware calls the VirtualAlloc API to allocate memory with READ and WRITE permissions and store the path returned by the GetModuleFileNameA API.

Following this, the kernel32.GetStartupInfoA API is called for extracting startup information.

Final Payload

During the final process, the ransomware launches a resumed process with the parameter “Admin IsNotAutoStart IsNotTask” after which the ransomware creates a new directory in the C:\\Users\<user_name>\AppData\Local and copies the current malware image into it.

Further, it launches the icacls.exe process, the command-line utility used to view and modify access control lists (ACLs) in Windows.

The command used for executing icacls.exe denies the group permission to delete the specified file for “Everyone,” which prevents the ability to delete the malware.

Scheduled task (Source: SonicWall)

Additionally, the malware creates a scheduled task to execute a copy of the final payload with a command line argument -Task—every 5 minutes.

The ransomware encrypts the files and adds the .msjd extension to them, while putting a ransomware note under the name _readme.txt on every encrypted folder.

Ransom note (Source: SonicWall)

Indicators Of Compromise

  • GAV: StopCrypt.RSM (Trojan)

Are you from SOC and DFIR Teams? – Analyse Malware Incidents & get live Access with ANY.RUN -> Start Now for Free.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

TikTok is generating big bucks in the U.S. which might hike the price that the unit sells for

0

[ad_1]

Even though the U.S. government is working on legislation that would ban TikTok in the country (unless current parent ByteDance divests itself of the platform), there is no denying that the app is a huge success in the states. U.S. revenue totaled $16 billion last year and with strong results like that, if ByteDance does decide to sell its stake in TikTok, it could ask for and receive a larger sum than it originally expected.

The Financial Times cited five sources familiar with TikTok’s financial situation who said that not only was the $16 billion in revenue generated in 2023 the highest total in TikTok’s U.S. history, but the amount could push the value of the platform to a figure as high as $150 billion. What makes a divestiture of TikTok easy for ByteDance to stomach is the fact that most of the Chinese company’s revenue comes from its operations located in China. Since ByteDance is not a public company, its financial records are private.

ByteDance had total revenue of $120 billion last year, up 40% from 2022’s top-line number. And while ByteDance did have profits of $28 billion last year, TikTok is still spilling red ink which is something that any potential buyer is going to have to consider when formulating a bid. ByteDance is believed to have a close relationship with the Communist Chinese government and there is concern that TikTok collects U.S. user’s personal information and sends it to a server sitting on a desk in Beijing.

The Protecting Americans from Foreign Adversary Controlled Applications Act, which would ban TikTok in the U.S. unless divested by ByteDance, passed the House by a 352-65 margin. The bill is targeted at TikTok, but could also impact other apps that collect user profiles from U.S. users and are “controlled by a foreign adversary.” This means that such apps cannot be “subject to the direction or control” of someone in Russia, China, North Korea, or Iran. 

The bill now moves to the Senate where it is expected to have a harder time passing. If it does, the House and Senate reconcile any differences between their bills and vote. If the bill passes both the House and Senate, the next stop is the president’s desk and President Biden has said that he will sign the bill if it reaches his desk.

China, on the other hand, is opposed to a forced sale of TikTok although Beijing will have to sign off on any deal reached to buy the platform from ByteDance.

[ad_2]

Source link

Overplay turns your videos into mobile video games even without any coding knowledge

0

[ad_1]

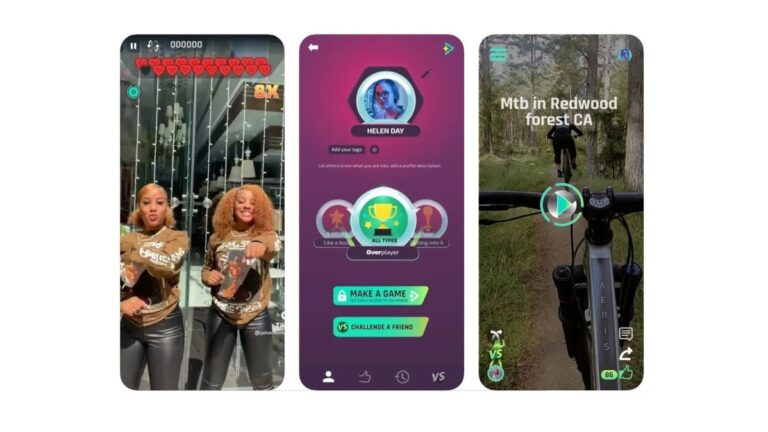
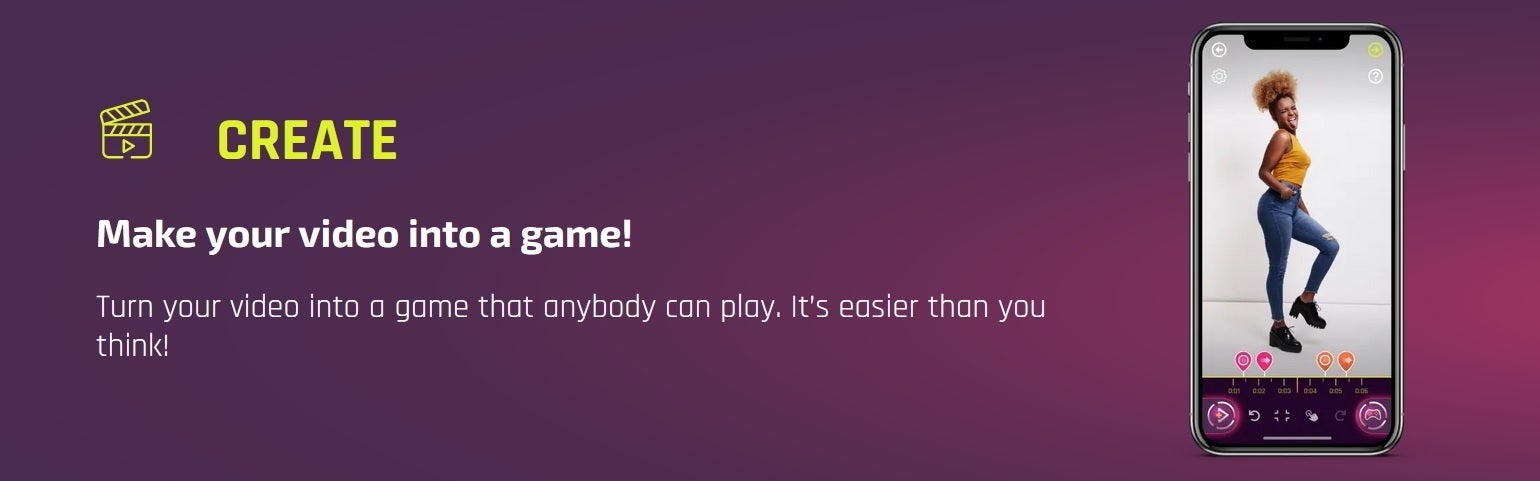
A company called Overplay recently got the opportunity to find a Shark Tank investor willing to join others who have funded the company. The firm will turn your video into a game using AI. The process is simple. Record a video on your smartphone and then upload the video to the Overplay platform. Overplay then turns the video into a mobile game without any coding required. Yes, without knowing a lick of coding, you can create a mobile game to share with friends. You can even try games made by other Overplay users.

The Overplay app is already available on the iOS App Store for the iPhone and the Google Play Store for Android handsets. Co-founder Dan Projansky says, “With Overplay, content creators and brands can seamlessly create games from their videos and connect with their followers in ways never seen before.” The other co-founder, Caroline Strzalka added, “This marks the beginning of a new era in digital content creation. The opportunities for the creative sector are endless.”

Over 1 million games have been played on Overplay and it has tallied more than 150,000 alpha app downloads. Perhaps it was not a surprise, but the Shark most well-versed in technology, Mark Cuban, was the only bidder for the company and agreed to invest $500,000 for 4% equity. Cuban will also get paid $500,000 for content creation and promotion.

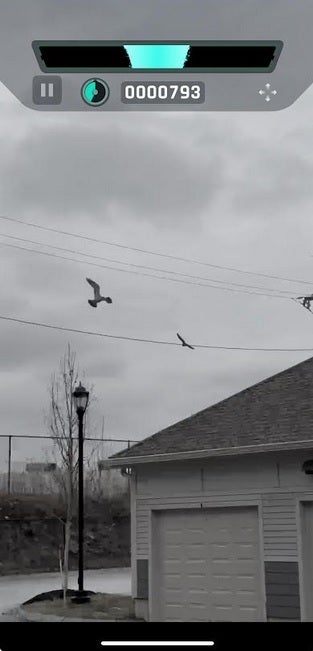
I installed the Overplay app and turned a video I took a few weeks ago of birds flying near my home into a video game. The goal of the game was to tap on the bird while in flight and points were awarded for each hit. And my coding knowledge is practically zilch.

While Overplay might turn those who passively watch videos into game players, we could see the platform used by advertisers to promote their brand and products by turning a simple video into a fun video game. This might be the best use of the platform since an addictive mobile game would be an easy way to keep a brand name in the minds of consumers.

[ad_2]

Source link
Hackers Claim Accessing 740GB of Data from Viber Messaging App

0

[ad_1]

Hackers Claim Accessing 740GB of Data from Viber Messaging App

Pro-Palestinian hackers calling themselves “Handala Hack” claim to have accessed 740GB of data from the messaging app Viber, including source code – Viber denies the breach but is investigating – Users are advised to change passwords.

Messaging app Viber is facing a potential data breach after a pro-Palestinian hacktivist group, Handala Hack, claimed responsibility for accessing its servers and stealing a trove of data.

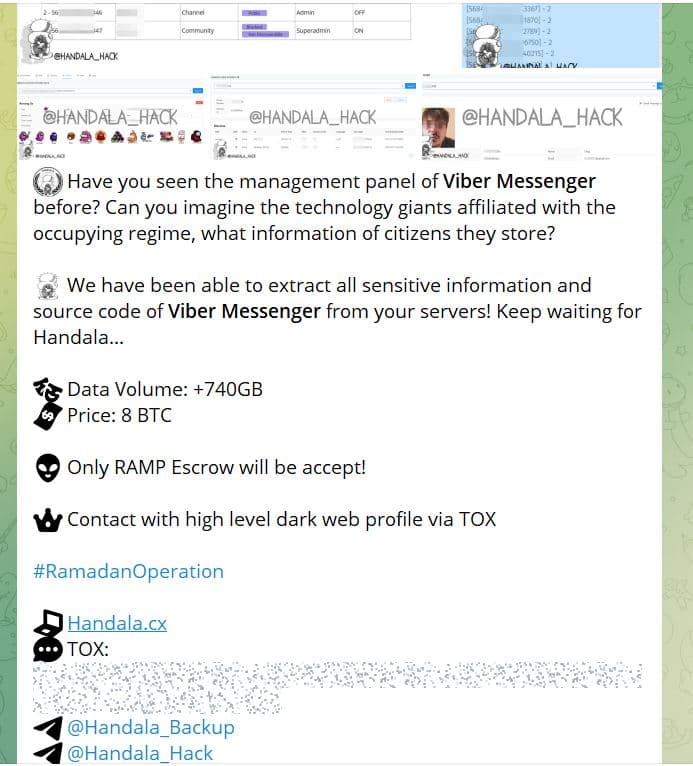
In its Telegram post, Handala Hack alleged they stole over 740GB of data, including Viber’s source code. The group demands a ransom of 8 Bitcoin, or $583,000, for the stolen information.

“Have you seen the management panel of Viber Messenger before? Can you imagine the technology giants affiliated with the occupying regime, what information of citizens they store?” the group’s post read. As seen by Hackread.com, the claim was accompanied by an image allegedly showing a directory listing.

Hackers Claim Accessing 740GB of Data from Viber Messaging App
Handala Hack group on Telegram (Screenshot credit: Hackread.com)

Viber, a messaging app introduced in 2010 and acquired by Japanese multinational firm Rakuten in 2014 for $900 million, has responded to the hackers’ claims.

The company has denied any evidence of intrusion into its systems or data compromise but confirmed that it has already launched an investigation to verify if a security breach has occurred. 

“We are aware of the claim and are investigating the validity of the alleged breach with utmost urgency,” the company said. “The security of our users’ data is our top priority,” the company reiterated.

If confirmed, this could be one of the largest data breaches in recent history. Experts opine that this breach, potentially involving personal messages, call logs, contact details, and financial information, can devastate Viber users. 

Handala Hack is a controversial group known for targeting Israeli entities and their allies to support the Palestinian cause. It has been active since establishing its Telegram channel in December 2023 and later joining Breach Forums.

Hackers Claim Accessing 740GB of Data from Viber Messaging App
Handala Hack group on Breach Forums (Screenshot credit: Hackread.com)

This group claims to have targeted Israeli infrastructure, healthcare providers, community centers, tech companies, media outlets, and defence contractors with sophisticated techniques.

Some of these techniques include phishing emails mimicking F5 BIG-IP zero-day security updates and SQL injection attacks, compromising databases and highlighting their intent to disrupt political messages through cyber means. Their claimed targets include Hadarom Port, Home Medics, Rosh Ha’ayin Municipal Society, and DRS RADA Technologies.

Whether verified or not, the incident involving Viber raises questions about the app’s data security practices. Viber needs to address user concerns by clearly explaining the situation and any potential risks to user data. 

In the meantime, Viber users should exercise caution and change their passwords, be cautious of phishing attempts, and stay informed about any updates regarding the alleged data breach by checking Viber’s official channels.

  1. Pro-Palestinian TA402 APT Using IronWind Malware
  2. Hacktivists Hit Critical ICS Infrastructure in Israel -Palestine
  3. Hackers Target Israeli Rocket Alert App Users with Spyware
  4. Palestinian Engineer Jailed for Hacking Israeli CCTVs & Drones
  5. Hamas-Linked Group Revives SysJoker Malware, Leverages OneDrive


[ad_2]

Source link

Hackers Trick Users to Install Malware Via Weaponized PDF

0

[ad_1]

In a sophisticated cyberattack campaign, malicious actors impersonating Colombian government agencies target individuals across Latin America.

The attackers are distributing emails containing PDF attachments, falsely accusing recipients of traffic violations or other legal infractions.

These deceptive communications are designed to coerce victims into downloading an archive that harbors a VBS script, initiating a multi-stage infection process.

Upon execution, the obfuscated VBS script triggers a PowerShell script, retrieving the final malware payload from legitimate online storage services through a two-step request process.

Infection Process

According to the ANY.RUN report was shared with GBHackers on Security; initially, the script acquires the payload’s address from resources such as textbin.net. It then proceeds to download and execute the payload from the provided address, which could be hosted on various platforms including cdn.discordapp(.)com, pasteio(.)com, hidrive.ionos.com, and wtools.io.

The attackers’ execution chain follows a sequence from PDF to ZIP, then to VBS and PowerShell, and finally to the executable file (EXE).

The culminating payload is identified as one of several known remote access trojans (RATs), specifically AsyncRAT, njRAT, or Remcos.

These malicious programs are notorious for their ability to provide unauthorized remote access to the infected systems, posing significant risks to the victims’ privacy and data security.

Here are some notable samples of this campaign: 1, 2, 3, 4.

sample 1

This campaign has been meticulously documented, with over 50 operation samples being analyzed.

Cybersecurity professionals and researchers are encouraged to consult the TI Lookup tool for detailed information on these samples, aiding in identifying and mitigating threats related to this campaign.

Document

Integrate ANY.RUN in Your Company for Effective Malware Analysis

Are you from SOC, Threat Research, or DFIR departments? If so, you can join an online community of 400,000 independent security researchers:

  • Real-time Detection
  • Interactive Malware Analysis
  • Easy to Learn by New Security Team members
  • Get detailed reports with maximum data
  • Set Up Virtual Machine in Linux & all Windows OS Versions
  • Interact with Malware Safely

If you want to test all these features now with completely free access to the sandbox:

The technique demonstrated by the attackers in this campaign is not exclusive to Latin American targets and may be adapted for use against various targets in other regions.

The cybersecurity community is urged to remain vigilant and employ robust security measures to protect against such sophisticated threats.

Are you from SOC and DFIR Teams? – Analyse Malware Incidents & get live Access with ANY.RUN -> Start Now for Free.


[ad_2]

Source link