Enhancing Blockchain Randomness To Eliminate Trust Issues Once For All

0
[ad_1]
Enhancing Blockchain Randomness To Eliminate Trust Issues Once For All

Blockchains lack true randomness, hindering applications like fair games, DeFi, and NFTs. Pyth Network’s “Pyth Entropy” solves this with provably fair, trustless random number generation. It’s fast, cost-effective, and easy to integrate

Blockchain developers have come up against a significant challenge when it comes to creating smart contracts that can execute randomness in a provably fair manner. Because most blockchain networks are limited to deterministic inputs and outputs, randomness is all but impossible to implement using standard architectures. 

Various solutions have been proposed to implement genuine randomness in blockchain applications, including the use of trusted third parties, blockhashes and Verifiable Random Functions or VRF, but none of these solutions are perfect. 

Why Do Blockchains Need Randomness?

Randomness is essential for many different kinds of blockchain applications. For instance, many blockchain-based games are built around the concept of randomness, such as the outcome of a fight between two players, which object the player discovers and so on. Randomness is also required to ensure fair NFT airdrops and mints, the allocation of tasks and resources and choosing samples for a consensus mechanism. Many dApps also have lottery-style mechanics that must be provably fair. 

Without randomness, none of the above applications can be demonstrated to be fair, as it’s easy for those with blockchain know-how to predict outcomes to their advantage. This is a big problem because the future of decentralized applications must be built on a foundation of trust and transparency. Participants in DeFi markets and blockchain games must be reassured that outcomes are fair and randomly selected, based on inputs. Betting protocols such as Lunabets, IDO auctions and random NFT lotteries must also be provably fair. 

We can illustrate the need for randomness in a blockchain-based poker game. The developer of the poker app must be able to prove to its players that the game uses a fair and unbiased algorithm. For instance, every time the deck of cards is shuffled and the players’ hands are dealt, players need to know that no one can manipulate the outcome. If it’s possible for any stakeholder to predict which cards are drawn, no one will trust the game. 

Developers could implement their own, black box algorithm like many traditional online poker games have done, but these obscure the inner workings of players. As such, the developer has no way to prove that the outcomes are random. Given the priority the Web3 industry places on trust, that simply won’t do for most users. 

However, implementing randomness is a challenge. To do so, the random outputs must be unbiased, unpredictable, verifiable and instantly available. The deterministic nature of most blockchains makes it difficult to fulfil these criteria, and so alternative solutions have been proposed. 

Different Approaches To Randomness In Blockchain

– Trusted Third-Parties

The simplest solution is to use a service provider to generate randomness. When the dApp user requests a random number, it’s generated by an off-chain provider that posts the results onto the blockchain. It’s an extremely easy-to-implement solution, but the problem is that everything is based on trust.

Participants need to trust that the randomness service provider is acting honestly. But there’s no guarantee of this, which makes it unsuitable for decentralized applications, especially those that involve high stakes, such as crypto games, betting applications and highly-prized NFT airdrops. 

– Blockhashes

An alternative method is to generate random numbers with the blockhash of a future block. When the user submits a request for a random number, it saves the or future block number. When the hash for that block is computed by network validators, the reveal transaction generates a random number. 

Once again it’s a simple solution, but trust is still a sore point, as users must trust the honesty of the validator. However, validators can reorder or omit transactions, which opens the door to the possibility of collusion between one participant and the validator to ensure that a favourable random number is generated. 

– Verifiable Random Functions

To ensure that single entities cannot influence the outcome of random number generation, verifiable random functions or VRFs have emerged as a popular solution. It’s a novel technique that relies on the collaboration of multiple participants to create a random number. 

A simple illustration of how VRFs work is this: f_s(x) = (y,p), with the random output “y” being deterministically computed from the input “x” and the secret key “s”. The function returns a “p”, which is proof that enables anyone to check that the “y” output is accurate. 

Typically, whenever randomness is requested, the input “x” is partially provided by the user and partially by the current blockhash. An off-chain service provider that holds the secret key “s” watches the blockchain for such requests, and submits on-chain responses “y,p”. The reveal transaction checks the proof “p” to ensure the “y” value is correct, before delivering the random output. 

While VRFs mitigate the need for trust, they also require the collaboration of the user, validator and service provider to generate the random number. However, there are concerns with this approach, as the service provider must be trusted not to censor any transactions. With VRFs, the service provider can simply choose not to submit it to the blockchain.

This opens the door to collusion, where the user submits a request for a coin flip, but collaborates with the service provider to only submit the request if the outcome is favorable. Developers can mitigate such attacks to an extent by ensuring the user cannot benefit from a failure to reveal. 

However, a second problem with VRFs is that the cryptography involved is quite complex and computationally intensive. Because blockchains generally don’t implement the necessary primitives for this cryptography, such requests can require excessive gas fees and multiple transactions to complete. 

A Superior Solution

The decentralized oracle protocol Pyth Network has emerged as one of the most widely-used crypto oracles, providing high-quality financial market data to blockchains at low latencies and with greater regularity than other protocols. 

Pyth has recently improved on an alternative approach to randomness generation called “commit-reveal” which involves the collaboration of untrusted parties. 

With commit-reveal, both the user and the service provider generate a secret random number and submit its hash, called a “commitment” to the blockchain. Then, in the reveal phase, both the user and service provider reveal their random numbers. Each party checks the revealed number generated by the other, with the random number generated being the hash of those two random numbers. It’s also possible for the blockhash to be included to add further randomness into the mix. 

It’s a novel idea that improves on the trust assumptions of VRF and it uses simpler cryptography, because only the hash function is required, making it easy for developers to implement. The same “liveness” problem remains, as both the user and the service provider can still halt the protocol by not revealing their random number, but developers can mitigate this in the same way as they would with VRF.

The downside of commit-reveal is that it requires more than two transactions, meaning higher gas fees. This is because the participants must first send their commitment, and then process the reveal phase, with the final random number being revealed in the third step. 

Pyth Entropy resolves this drawback with a more sophisticated version of commit-reveal, where the service provider can commit multiple numbers upfront, reducing the number of transactions involved in the process. In this way, it enables secure random numbers to be generated more rapidly, with minimal transactions, making it the ideal solution for dApps that rely on speed, such as NFT games, airdrops and mints, lotteries and more. 

Randomness Everyone Can Trust

Pyth Entropy has gained significant adoption since its launch last year and is now available on multiple EVM blockchains and Layer-2s, including LightLink, Chiliz, Arbitrum, Optimism, Mode, Zetachain and, more recently, Blast. 

Blast is a new Ethereum L2 and the first to offer native yield for ETH and stablecoins while powering faster and cheaper transactions. It leverages the capabilities of Ethereum’s Shanghai upgrade, which introduced features such as auto-rebasing for ETH and T-Bill yields for stablecoins via Blast USD (USDB). 

Blast’s integration with Pyth’s data oracles means dApps built on the network can access more than 400 low-latency price feeds for cryptocurrencies, foreign exchange pairs commodities and equities of exchange-traded funds. Already, Pyth has been adopted by dozens of Blast dApps. 

With Pyth Entropy, Blast dApps now have a way to quickly generate secure random numbers with zero trust issues at the lowest cost, ensuring they can rapidly deliver unbiased outcomes for users. Its applications extend to NFT mints and airdrops, blockchain games, SocialFi, prediction markets and more. Combined with the advantages of the Blast network, it will enable new experiences that aren’t possible on any other blockchain, eliminating trust issues once and for all. 

  1. Could Bitcoin Be The Future Of DeFi?
  2. The Rise of Blockchain Gaming and Secure Marketplaces
  3. 5 Ways Smart Contracts Are Making A Real-World Difference
  4. Exploring the Phenomenal Rise of Ethereum as a Digital Asset
  5. Web3 needs decentralized infrastructure beyond IPFS capabilities

[ad_2]
Source link

Motorola unveils its latest 2024 Moto G phones

0
[ad_1]

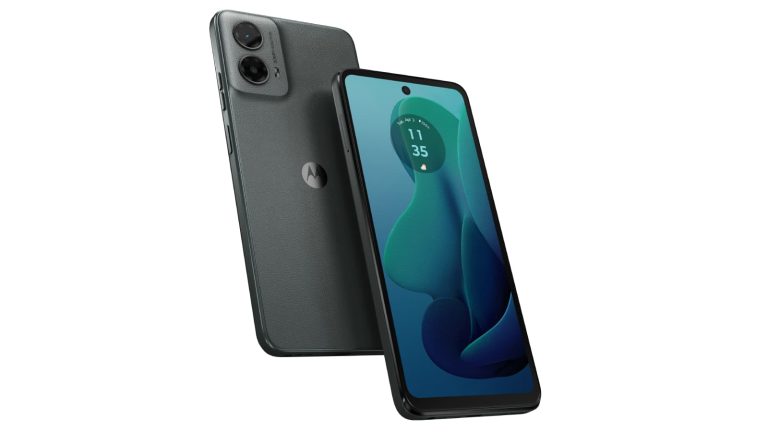
Motorola Moto G phones have been a mainstay in the company’s lineup for several years. These offer a solid mid-range phone experience with that classic Motorola flare. On Tuesday, Motorola just unveiled its Moto G 2024 Android phones, and they will continue Motorola’s tradition of providing a great smartphone experience at a low price.

These phones are the Moto G 5G – 2024 and the Moto G Power 5G – 2024. These two phones will offer a similar experience while adding their own special benefits.

Motorola announces its new Moto G – 2024 phones

This phone will give you the most basic experience of the pair. The Moto G 5G will come with a 6.6-inch 720p+ display that runs at a fluid 120Hz. While the resolution isn’t all that great, you’ll still be getting a smooth refresh rate. Also, Motorola makes pretty nice displays in general.

Moving on to the phone’s internals, the Moto G 5G comes with the  Snapdragon for 4 Gen 1 S0C. The performance will be decent, though it will not exactly be blazing fast. A nice addition is the 128GB of storage that you can expand that storage via a MicroSD card. The 4GB of RAM is also expandable up to 8GB through storage.

That’s for the camera, this phone will have a dual camera package. It will be sporting a 50-megapixel main camera that will bin down to about 12-megapixels.

Finishing off the specs, this phone comes with a large 5000mAh battery. This should give you up to two days of battery life on light to moderate usage.

The Moto G 5G starts at $199.99.

Moto G 5G 2024

Moto G power 5G – 2024

This phone will be a bit more advanced than the Moto G 5G. Starting off with the display, the Power edition will have a slightly bigger 6.7-inch display with a sharper 1080p+ resolution. The refresh rate will remain at 120Hz.

Powering this device, we have the decently powerful MediaTek Dimensity 7200 SoC. This is a decent performer. Also, this phone will share the same 128GB of expandable storage as the Moto G 5G. Also, it comes with 8GB of RAM that’s expandable up to 16GB using storage.

Moving on to the camera, the Moto G Power 5G will use the same 50-megapixel main camera that we saw on the Moto G 5G. So, pictures taken on this phone will look comparable.

Rounding out the specs, this phone has a large 5000mAh. What’s notable about it is that this phone supports 30W charging.

The Moto G power 5G starts at $229.99.

Moto G Power 5G 2024


[ad_2]
Source link

Snag Apple’s Upgraded AirPods Pro for only $189 at Amazon

0
[ad_1]

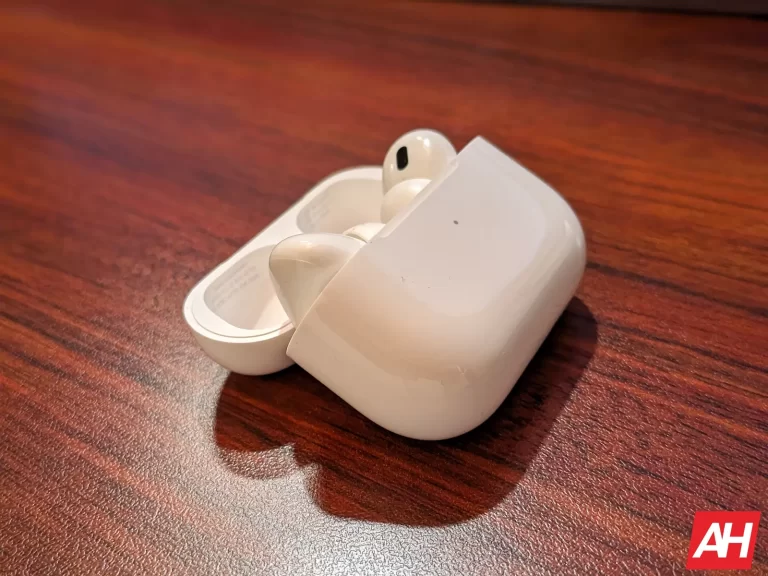
Apple’s new second-generation AirPods Pro with USB-C is still available at Amazon for only $189. That is an excellent price since Apple products rarely get discounted anyway.

These new AirPods Pro really don’t have much else new other than switching from Lightning to USB-C. However, if you are picking up the iPhone 15, this might be a good purchase. So you can completely ditch Lightning altogether.

Now, these do bring a new feature for Vision Pro, with Lossless audio for the Vision Pro. But that also requires spending $3,500 on the Vision Pro, which no one should do, unfortunately.

The Active Noise Cancellation technology in the AirPods Pro is incredibly effective. It blocks out a vast range of background noise, letting you focus on your music, podcasts, or calls even in the busiest environments. The AirPods Pro delivers well-balanced sound with crisp highs and satisfying bass. Combined with Spatial Audio, which simulates surround sound, they create a truly engaging listening experience.

You can pick up the new USB-C AirPods Pro from Amazon today

Buy at Amazon


[ad_2]
Source link

Open Source Tool that Detects Hacking Activity

0
[ad_1]

CloudGrappler is an innovative open-source tool designed to detect the presence of notorious threat actors in cloud environments.

This tool is a beacon of hope for security teams struggling to keep pace with the sophisticated tactics of groups like LUCR-3, also known as Scattered Spider.

CloudGrappler leverages the power of CloudGrep, a tool developed by Cado Security, to offer high-fidelity, single-event detections of activities associated with well-known threat actors in popular cloud platforms such as AWS and Azure.

It acts as a cyber detective, sifting through the vast amounts of data in cloud environments to identify suspicious and malicious activities that often go unnoticed.

Key Features of CloudGrappler

  • Threat Actor Querying: CloudGrappler excels in identifying activities demonstrated by some of the most notorious cloud threat actors. It utilizes a subset of activities from Permiso’s extensive library of detections to help organizations pinpoint threats targeting their cloud infrastructure.
  • Single-Event Detections: The tool provides a granular view of potential security incidents, enabling security teams to quickly and easily identify specific anomalies within their AWS and Azure environments.
  • Integration with CloudGrep: By incorporating a set of Tactics, Techniques, and Procedures (TTPs) observed in the modern threat landscape, CloudGrappler enhances its threat detection capabilities.
Document
Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

How CloudGrappler Works

CloudGrappler includes several components designed to streamline the threat detection process:

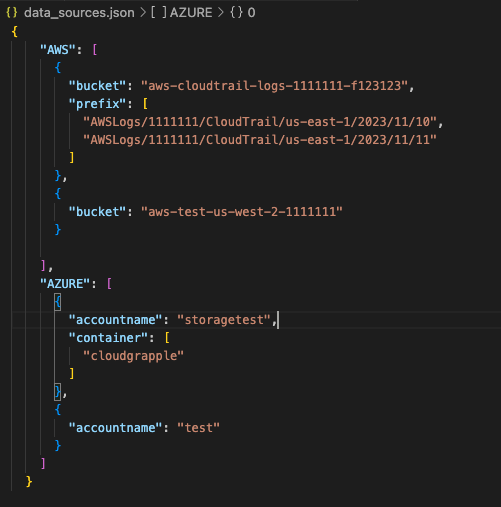
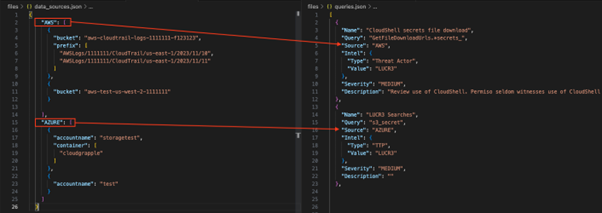
  • Scope Selector: Users can define the scope of their scanning through an integrated data_sources.json file, choosing to scan specific resources or a broader range of cloud infrastructure services.
  • Query Selector: The tool comes with a queries.json file containing predefined TTPs commonly used by threat actors. Users can modify these queries or add custom ones to tailor the scanning process.
  • Report Generator: After scanning, CloudGrappler produces a comprehensive report in JSON format, offering detailed insights into the scan results and enabling security teams to address potential threats swiftly.

It is based on a subset of activity from Permiso’s library of hundreds of detections, and it helps organizations detect threats targeting their cloud infrastructure.

Users have the ability to scan specific resources within their environment
Users can scan specific resources within their environment

Practical Applications

CloudGrappler is not just about detecting suspicious activities. it also provides valuable threat intelligence to help security professionals understand the risks in their environment and develop targeted response strategies.

Threat Activity
Threat Activity

The tool’s output includes information on the threat actor involved, the severity of the detected activity, and a description of the potential implications.

For those interested in enhancing their cloud security posture, CloudGrappler is available on GitHub.

The repository includes detailed instructions on setting up and using the tool, making it accessible to security teams of all sizes.

As cloud environments become increasingly complex and threat actors’ activities more sophisticated, tools like CloudGrappler are essential for maintaining a robust security posture.

CloudGrappler represents a significant step forward in the fight against cybercrime by offering an open-source solution for detecting and analyzing threats in cloud environments.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]
Source link

Google Files can now scan your documents within the app

0
[ad_1]

Google is adding a new Doc scanner feature to its Files app that allows users to effortlessly scan documents directly from the app without needing third-party scanners. A “scan” button has been appearing at the bottom of the Files app, as some users have noticed recently. Mishaal Rahman’s recent post on X describes how this feature works.

Goodbye third-party scanners: Google Files takes over document scanning

This new scan button provides two shooting modes: manual and “auto capture,” which, according to Android Central, means that Files by Google will have access only to the images you scan. The tap-to-capture button is accompanied by editing options like erase, cut, and rotate, in case there is a need for updating it.

After editing, the image you scanned now becomes a PDF and gets saved under the tab labeled “Document.” It first appeared on Google pixel devices but internal tests have shown it also emerged on the Motorola Edge Plus 2023. As of late, the company’s Files app underwent a facelift, which saw the removal of its bottom navigation bar.

The latest update makes it function more like the Google Drive app, thus making it more useful. The document scanner functionality uses Drive’s machine-learning GMS Ml-Kit Scanner, which was first introduced last December. With this technology, users can access quick editing tools right after they take a picture.

Scanner in Google Files

Although sources had indicated that it rolled out in 2020, reports now show wider availability across many devices, including smartphones that are receiving updates regularly. Another exciting element accompanying this feature is a smart search tool.

Intelligent scanning & search tools will make file navigation easier

People often need help finding their files quickly so they won’t waste time looking through every single item saved either within their phone or cloud storage service. It happens because many companies often store images without categorizing them according to file names making any search impossible.

Google’s smart search can check the contents of photos or docs saved on your device, so you can get results quickly while still inside the app. Organizing your images into an alphabetically sorted list can also help you efficiently browse through them, avoiding the need to scroll through thousands of pages.


[ad_2]
Source link

Is Instagram in trouble? TikTok might launch standalone photo app

0
[ad_1]
TikTok has been the big cheese in the short-form video game for quite some time now. It’s had such a massive impact that other giants like Facebook, Instagram, and YouTube jumped on the bandwagon, rolling out their own short video features like Reels & Shorts. But here’s the twist— now it seems TikTok is flipping the script and dipping its toes into the photo-sharing scene, taking a page out of Instagram’s playbook. According to TheSpAndroid (via Android Authority), the latest strings unearthed in the TikTok app’s version 33.8.4 point towards the possibility of a new app on the horizon—none other than TikTok Photos. Looks like the TikTok universe might be expanding into the realm of photo-sharing.
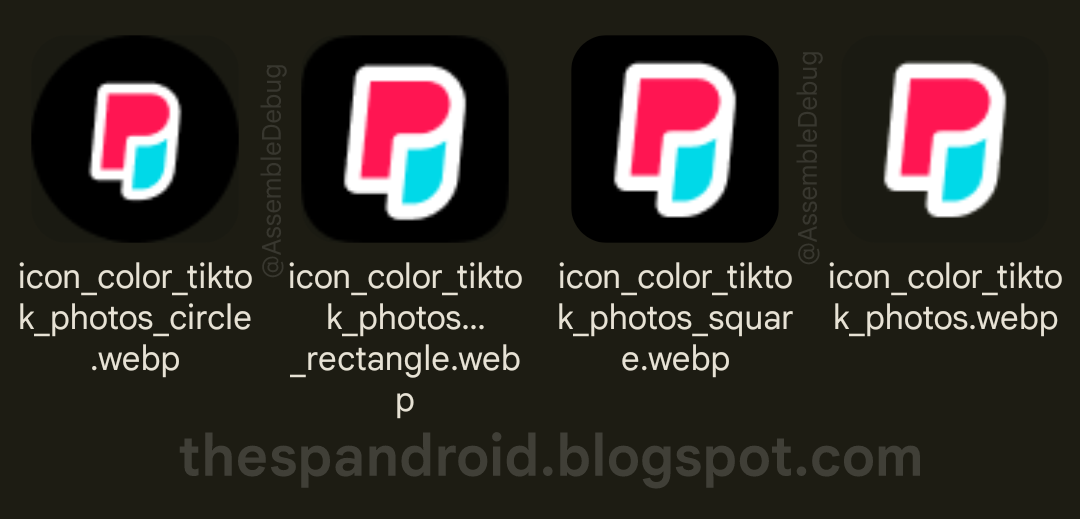
Although TikTok currently lets users share multiple photos in slideshow-style videos, it seems it is gearing up to level up the photo-sharing game with TikTok Photos. The code hints at a more focused photo experience, and here’s the kicker—it looks like users will have the option to sync their existing photo posts from the main TikTok app. On top of that, the leaked code spills the beans on the app’s icon. This icon rocks the same color vibe as the OG TikTok app. But, fair warning, this icon might still be in the experimental phase. Until the official launch, there’s a chance the look could get a makeover.

TikTok is keeping tight-lipped about an official launch date or even the existence of such an app, but the clues embedded in the app’s code are dropping some serious hints. Signs are pointing towards a potential imminent launch. When it comes to availability, it’s a safe bet to assume that TikTok Photos will probably be up for grabs on both Android and iOS devices.

If this leak pans out and ByteDance, TikTok’s parent company, is indeed gearing up for a standalone TikTok Photos app, it could signal some heavyweight competition heading Instagram’s way. TikTok, boasting a whopping 1 billion monthly active users, is one of the most widely used apps globally.

In 2023, social media was a major time-sucker, and TikTok was the undisputed champ, not just in terms of time spent but also in the dollars flowing into the app—especially in the US. Now, speaking of TikTok and the US, a recent House bill has thrown a curveball that could potentially bring the curtain down on the beloved by many video app.

This legislation comes with a bold ultimatum: TikTok faces the chopping block in the States unless its parent company, ByteDance, flips its interest in the app. ByteDance, a Chinese outfit, has US lawmakers breaking a sweat over TikTok’s ties to China. The fear? They’re concerned about the company scooping up personal data from TikTok users.

This bombshell sparked quite a reaction, with a Shark Tank investor stepping into the ring, saying he’d throw down the cash to snag TikTok and save it from the banhammer in the US.


[ad_2]
Source link

Muddled Libra Hackers Using Pentesting Tools To Gain Admin Access

0
[ad_1]

Threat actors use pentesting tools to identify vulnerabilities and weaknesses in target systems or networks.

These tools provide a simulated environment for testing potential attack vectors that allow threat actors to exploit security gaps and gain unauthorized access. 

By using pentesting tools, threat actors can assess the effectiveness of their methods and refine their strategies to maximize the impact of their attacks.

Cybersecurity researchers at Unit 42 of Palo Alto Networks discovered that Muddled Libra hackers are actively using the pentesting tools to gain admin access.

Muddled Libra Hackers

The Muddled Libra hacking group emerged in late 2022 with the 0ktapus phishing kit, offering prebuilt hosting, easy C2 connectivity, and bundled attack templates.

Document
Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

This kit enabled low-skilled attackers to emulate mobile authentication pages cheaply, gathering credentials and MFA codes for over 100 organizations. 

While previously documented as 0ktapus, Scattered Spider, and Scatter Swine, Muddled Libra clarified they are a distinct group using a common toolkit, social forum-based collaboration, and Agile-like team structure. 

Unit 42 attributed several complex supply chain attacks targeting cryptocurrency to Muddled Libra, who are adapting tactics and broadening their scope.

Evolved tactics of Muddled Libra (Source – Palo Alto Networks)

Unit 42 links incidents to Muddled Libra due to common tactics.

Muddled Libra shows a deep knowledge of targets, often from prior breaches and data brokers like Genesis and Russian Markets. 

Malware like Raccoon Stealer and RedLine Stealer harvests info from personal devices by exploiting BYOD policies and hybrid work setups, creating a prime target for data theft.

Muddled Libra attack chain (Source – Palo Alto Networks)

Muddled Libra uses lookalike domains in smishing attacks by exploiting the SMS link truncation.

They favor short-lived domains via Porkbun and Namecheap, and they are now adding Metaregistrar. 

The 0ktapus kit, which was adopted widely, requires little skill, targeting via smishing or direct social engineering. Helpdesk agents are key targets for password and MFA resets. 

Focus on maintaining access involves abusing RMM tools like Zoho Assist, AnyDesk, and TeamViewer.

Cloud platforms aid in establishing a foothold, but recent shifts indicate a move to an ‘encrypt and extort’ model, targeting larger organizations in the same industry.

Muddled Libra sticks to consistent discovery methods, using legit tools like SharpHound, ADRecon, and Angry IP Scanner. 

They aim for data and credential theft, sometimes adding BlackCat ransomware. They execute with PsExec or Impacket, leveraging the victim’s tools and RDP connections for stealth.

Defense Evasion Tactics

Here below, we have mentioned all the defense evasion tactics:-

  • Disabling antivirus and host-based firewalls
  • Attempting to delete firewall profiles
  • Creating defender exclusions
  • Deactivating or uninstalling EDR and other monitoring products
  • Standing up unmanaged cloud virtual machines
  • Elevating access in virtual desktop environments

Mitigations

Here below, we have mentioned all the mitigations:-

  • Implement MFA and SSO.
  • Enable security alerting and account lockout for repeated MFA failures.
  • Conduct user awareness training.
  • Maintain updated credential hygiene.
  • Monitor and restrict access to critical defenses using ITDR tools.
  • Restrict anonymization services at the firewall.
  • Utilize Next-Generation Firewall.
  • Implement XDR solutions.
  • Employ XSOAR or XSIAM for security automation.

IoCs

  • 104.247.82[.]11
  • 105.101.56[.]49
  • 105.158.12[.]236
  • 134.209.48[.]68
  • 137.220.61[.]53
  • 138.68.27[.]0
  • 146.190.44[.]66
  • 149.28.125[.]96
  • 157.245.4[.]113
  • 159.223.208[.]47
  • 159.223.238[.]0
  • 162.19.135[.]215
  • 164.92.234[.]104
  • 165.22.201[.]77
  • 167.99.221[.]10
  • 172.96.11[.]245
  • 185.56.80[.]28
  • 188.166.92[.]55
  • 193.149.129[.]177
  • 207.148.0[.]54
  • 213.226.123[.]104
  • 35.175.153[.]217
  • 45.156.85[.]140
  • 45.32.221[.]250
  • 64.227.30[.]114
  • 79.137.196[.]160
  • 92.99.114[.]231

With Perimeter81 malware protection, you can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits. All are incredibly harmful and can wreak havoc on your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Pixel 8 series getting support for display output over USB-C

0
[ad_1]

With its Pixel 8 series, Google’s recent move will completely change the game for individuals who want a desktop-like experience using their handsets. Through the latest Android beta, DisplayPort Alternate Mode is now reportedly available for Pixel 8 and Pixel 8 Pro users. Using the feature, they can connect their phones to external displays via USB port.

Pixel 8 display output paves the way for a DeX-like experience

Before, Google’s Pixel line did not support display outputs, which resulted in difficulty mirroring phone screens on external monitors by users. But display port alternate mode is a major departure that could open these devices to more capabilities like those in Samsung DeX mode.

The mode facilitates transmitting mobile display output via USB-C connectors as it stands. This means it has become far easier for Pixel 8 users to connect their phone to an external monitor using widely available HDMI adapters. On previous Google Pixels, the manufacturer allegedly disabled this feature using flags while it existed on the hardware level. However, Pixel 8 devices have updated to enable this mode.

The reason behind this move may suggest an interest from Google to improve its Android built-in desktop mode, one that has been under development since Android version 10. Even though the present desktop mode is basic and aimed at developers only, efforts are being made to point out enhanced usage for future Android releases. Perhaps from Android versions starting with number fifteen.

The feature may only be available for Pixel 8 devices and above

In the second beta released recently with Android 14 qpr3, Google changed the firmware so that Pixel 8’s Display Port Alternate mode would turn on by default, enabling users to mirror their screens or access the simple desktop modes. In addition, although the revamped desktop experience is still behind many flags, these steps indicate a move toward a flexible smartphone computing environment.

It raises questions about whether Android’s new-looked-at-desktop-mode would accompany Google’s new family of smartphones, the Pixel 9. On the other hand, users with older Pixel models (with no support for DisplayPort Alternate Mode) have a way out via DisplayLink adapters. These adapters allow screen sharing by capturing, compressing, and transmitting screen data to HDMI-enabled devices.


[ad_2]
Source link

French Government Hit with Severe DDoS Attack

0
[ad_1]

Several French government websites faced disruptions due to a severe Distributed Denial of Service (DDoS) attack, marking a concerning escalation in cyber threats against state infrastructure.

The attack commenced in the early hours of Sunday, rapidly escalating in intensity.

Cloudflare’s Radar service detected the onslaught, which saw a brief lull before resurging to sustain a significant level of disruption for approximately six hours.

The French government’s digital transformation agency, Direction interministérielle du numérique (DINUM), was quick to respond, attempting to erect digital barriers against the attackers.

Despite these efforts, Anonymous Sudan, a group claiming responsibility for the attack, declared DINUM’s defenses ineffective, with Cloudflare data indicating spikes in Layer 7 attacks in the following days.

Government Response

The office of Prime Minister Gabriel Attal acknowledged the cyberattacks, describing them as “conventional attacks of unprecedented intensity.”

Document
Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

A crisis cell was activated to deploy countermeasures, significantly reducing the impact on most services and restoring access to state websites.

Specialist services, including France’s information security agency ANSSI, were engaged in implementing filtering measures to mitigate the attack’s effects.

Despite the severity of the attack, by the time of reporting, access to the affected sites had been largely restored, with only minor disruptions remaining, as reported by the register.

Possible Russian Involvement

The cyberattack comes amid heightened tensions between France and Russia, particularly over French President Emmanuel Macron’s suggestion that European powers consider sending troops to support Ukraine against Russia’s invasion.

This proposal, condemned by Russian President Vladimir Putin, has led to speculation that the DDoS attack could be a manifestation of Russian displeasure.

Infosec firm FalconFeeds suggested that Anonymous Sudan did not act alone, indicating possible assistance from Russia, pro-Russian threat actor UserSec, and a group named 22C.

However, a security source told AFP that the attacks are not currently attributable to Russia directly.

According to a report by France24, the French state services have been targeted by a series of cyberattacks described as being of an “unprecedented intensity.”

Anonymous Sudan and Other Groups

Anonymous Sudan, which has claimed responsibility for the attack, is known for its cyber activities against countries it perceives as engaging in anti-Muslim actions or as enemies of Moscow.

The group’s motivations remain unclear, but its track record and the symbolism of its Guy Fawkes avatar point to a broader agenda of revolutionary protest.

This latest incident underscores cyber threats’ diverse and global nature, with groups like Anonymous Sudan leveraging DDoS attacks to target significant digital infrastructure.

This cyberattack follows a warning from Attal’s defense adviser about the potential targeting of significant events like the Olympics and European Parliament elections.

It also aligns with Defence Minister Sebastien Lecornu’s call for increased protection against sabotage and cyberattacks, particularly from Russia.

As France and other nations brace for future cyber offensives, the importance of robust digital defenses and international cooperation against cyber threats has never been more evident.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]
Source link

Google Wallet can now automatically add movie tickets & passes

0
[ad_1]

Google Wallet, Google’s mobile payment service, has been getting steady updates and features. Just near the end of February 2024, Google added support for 42 new US-based banks to grow the app further.

The latest Google Wallet update prioritizes user convenience instead of growth by making it significantly easier for users to store all their tickets and boarding passes in one place. This is done by having Google automatically add movie tickets and passes to Google Wallet.

All your movie tickets and passes in one place

During the Mobile World Congress, Google announced that updates would be rolling out for the Google Wallet service. One highlighted addition was expanding Google Wallet passes to Wear OS. The update made accessing boarding passes, movie tickets, gym memberships, loyalty cards, and more easier for Wear OS users.

Now, instead of having to manually add a boarding pass or ticket to your wallet, Google can automatically save it for you. This new feature was first reported by Android expert Mishaal Rahman, who was among the first to report that the OnePlus Pad was getting Android 14 in the US.

Thanks to this update, Google Wallet can now automatically add movie tickets and passes to its data when the user gets a confirmation email in Gmail. This automatic process will make storing tickets and passes in one place more streamlined and seamless. After all, users won’t have to interact with the ticket themselves, making the hassle of manually adding passes and tickets non-existent.

While this new feature is live for some global movie chains and airlines like AMC Theatres, more partners will join the list in the future. Google will likely add support for movie chains and airlines in batches, similar to how it does with banks.

Manually archive passes now

Google’s Google Wallet innovations don’t end here, as the company seemingly wants to make organizing passes as easy as possible.

Not only can Google Wallet automatically add movie tickets and passes through this update, but users can also manually archive various pass types. Archived passes go to the Wallet app’s dedicated “Archived Passes” section, allowing easier access.

Furthermore, this archiving feature isn’t limited to the app’s mobile version. Users can also archive passes in their Google Wallet using Wear OS, allowing them to organize and access their passes on the go.

These new features come after Google announced Google Pay’s June closure in the US. True to its word, the company is shifting its focus on making Google Wallet the definitive payment service.


[ad_2]
Source link