Italian DPA Asks OpenAI’s ‘Sora’ to Reveal Algorithm Information

0
[ad_1]

The Italian Data Protection Authority (DPA) has initiated a thorough investigation into OpenAI, the American tech giant, following its recent announcement of a cutting-edge AI model named ‘Sora.’

This new model can generate dynamic, realistic, and imaginative scenes from simple text prompts.

Amidst growing concerns over data privacy, the DPA is examining the potential impact ‘Sora’ could have on the handling of personal data within the European Union, with a specific focus on Italian users.

Seeking Transparency in AI Operations

To understand the intricacies of ‘Sora’ and its operations, the Italian DPA has laid out a series of questions for OpenAI.

Document
Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

The company is expected to respond within a 20-day window, addressing whether ‘Sora’ is currently accessible to the public and if it is being, or will be, made available to users in the European Union, particularly in Italy.

A critical aspect of the DPA’s inquiry revolves around the training process of the ‘Sora’ algorithm.

OpenAI must disclose detailed information on the nature of the data collected and processed for this purpose.

The authority is particularly interested in understanding whether any personal data is being used, and if so, whether it includes sensitive categories such as religious or philosophical beliefs, political opinions, genetic data, health information, or details about an individual’s sexual life.

Furthermore, the DPA seeks clarity on the sources from which this data is derived.

The Italian Data Protection Authority, Garanteprivacy, has initiated an investigation into OpenAI’s ‘Sora’ program.

OpenAI has been instructed to provide detailed information about the algorithm for generating short videos from text instructions.

Compliance with European Regulations

Should ‘Sora’ be offered to EU-based users, the Italian DPA demands that OpenAI confirm whether its user and non-user information protocols and the legal foundations for data processing align with the European Regulation’s stringent requirements.

In a recent tweet from researcher Luiza Jarovsky, The Italian Data Protection Authority has opened an investigation into OpenAI’s Sora.

The Italian DPA’s move underscores the growing global concern over the ethical use of AI and personal data protection.

As AI technology advances, regulatory bodies are increasingly vigilant in ensuring that companies like OpenAI operate transparently and follow established data protection laws.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]
Source link
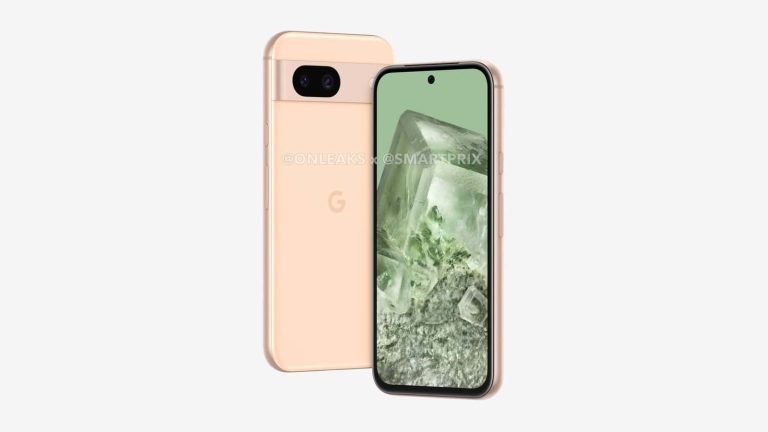
Google Pixel 8a is coming with a new battery feature

0
[ad_1]

A lot of rumors concerning the Google Pixel 8a have been making the rounds on the internet for the last few weeks. However, Google has now directly hinted at the upcoming Google Pixel 8a device along with a new battery-related feature. You may be aware of this battery-related feature that the brand recently removed from the Pixel devices. It is going to make its comeback through the forthcoming budget champ from the brand.

The battery stats feature is coming back with the Google Pixel 8a

Google had added a new battery stats feature with the Android 14 QPR 1 update on the Pixel devices. This new feature shows detailed stats about the battery and its recent usage, which was helpful in many ways. The feature shows details such as the manufacturing date, charging cycle, and the capacity of the battery. But as soon as the users started enjoying the feature, Google decided to roll it back. After the March update, the brand removed the feature from all the devices.

Reacting to this, users started raising questions about why Google removed the feature on the official issue tracker page. Addressing this, one of the brand’s officials responded by saying “We only enable this on Pixel 8a and beyond.” This response not only confirms that the removal of this feature was intentional but also confirms the existence of the Pixel 8a smartphone. The brand did not comment on why they removed the feature though.

The removal of this feature could be because of multiple reasons such as hardware incompatibility or maybe inaccurate data. However, as claimed by the brand, all the future Pixel devices launching after the Google Pixel 8a will have the battery stats feature. It is no doubt going to be a very useful addition.

What can we expect from the coming Pixel 8a device?

Google is expected to launch the Pixel 8a in the coming months. It will most probably launch in May, during the Google I/O 2024. It is going to be the budget champ of the whole Pixel 8 lineup. We don’t have much information about it. But as per the rumors and leaks, the device will offer a design similar to the existing Pixel 8 and 8 Pro devices. It will have a dual rear camera with a possible combination of a main wide with a secondary ultrawide lens. Tensor G3 chipset will fuel the device.


[ad_2]
Source link

Android 15 could bring a classic Windows feature for physical keyboards

0
[ad_1]

Computers are some of the most useful devices that we use in our daily lives. So it’s always true that smartphones start adopting features we typically see on computers. And we just got word that the classic Windows feature will be coming to Android smartphones. According to the report, Android 15 could bring Windows-style sticky keys for physical keyboards.

Many Windows users have dealt with the sticky key popup. It happens when they press the Shift key five times rapidly. Well, this feature could come in handy if you’re constantly holding down the Shift, CTRL, or ALT keys. With sticky keys activated, you can simply tap the shift key and press whatever secondary key you want rather than holding it down. The same thing goes for the CTRL and ALT keys. For example, rather than holding CTRL and pressing “S” to save your file, just press the CTRL key and press “S”.

Android 15 could get Windows-style sticky keys

Right now, this is very early information, so it should be taken with a grain of salt. Currently, Google is auditioning some Android 15 features via the Android 14 QPR 3 Beta. As such, this is very early information. There’s no telling if this feature will make it to the final build.

If you’re working on your tablet or phone, you are still likely to use the same keyboard shortcuts as your computer. As such, if you are a person who typically holds the Shift, CRTL, or ALT key down multiple times a minute, then sticky keys will greatly benefit you.

As discovered by Android software engineer Mishaal Ramen, the Android 14 QPR Beta 3 will let you enable this feature in the physical keyboard settings. Even though this is being tested in the Android 14 beta, it’s likely that this will become a feature in Android 15.

Also, this latest beta version brings a feature called Bounce Keys. This feature will make the system ignore keys that have been pressed within rapid succession.

Right now, people are still cracking into the new software to discover what to expect from Android. So, we are undoubtedly going to see more features pop up in the near future. Be sure to stay tuned if you want to know what to expect from Android 15.


[ad_2]
Source link

KrustyLoader Backdoor Attack Both Windows & Linux Systems

0
[ad_1]

Recent developments within the cybersecurity landscape have included the emergence of KrustyLoader, a sophisticated Rust-based backdoor that has caught the attention of multiple industry experts.

This malware, which boasts Windows and Linux variants, has been implicated in a series of targeted attacks, with significant implications for cybersecurity defenses across platforms.

Linux Variant

KrustyLoader’s Linux variant made headlines in late 2023 and early 2024 for its targeted attacks on Avanti devices.

These attacks are believed to be the handiwork of the China nexus threat actor group UNC5221.

The group exploited two critical vulnerabilities, CVE-2024-21887 and CVE-2023-46805, which allowed for unauthenticated remote code execution (RCE) or authentication bypass on Ivanti Connect Secure (ICS) and Ivanti Policy Secure Gateway devices.

Exploiting these vulnerabilities facilitated the download and execution of KrustyLoader, which subsequently deployed the post-exploitation toolkit Sliver.

Despite patches being released for these vulnerabilities, unpatched systems remain at risk.

Windows Variant

The Windows variant of KrustyLoader has also been under scrutiny. WithSecure, a cybersecurity firm, reported on threat actors exploiting ScreenConnect to deploy this variant.

The Windows version mirrors its Linux counterpart in functionality, serving as initial-stage malware that downloads and executes a second-stage payload, typically Sliver.

The infection chain detailed by WithSecure involves dropping a batch file, fetching the KrustyLoader payload from a predefined AWS S3 URL and executing it on the victim’s machine.

Document
Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

UNC5221 Group

The entity behind these sophisticated attacks, UNC5221 (also known as UTA0178), is a group with a China nexus, primarily focused on espionage.

Instead of opportunistic attacks, the group’s strategic targeting approach underscores its intent and capabilities. UNC5221’s arsenal is not limited to KrustyLoader; it also includes various other malware tools, such as the CHAINLINE backdoor, FRAMESTING webshell, and ZIPLINE backdoor.

The emergence of KrustyLoader and associated attacks underscore the evolving threat landscape and the continuous need for robust cybersecurity measures.

The cross-platform capabilities of KrustyLoader and the strategic intent of groups like UNC5221 highlight the importance of vigilance and timely patching of known vulnerabilities to safeguard against such sophisticated threats.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

IOCs

PolySwarm has multiple samples associated with KrustyLoader.

  • e1c31f503da20c8326b566ec042db1f0d3b56fe3579ae37398ff3f6fa5bc54d2
  • 415a70897761c65c3ff59b686d2b1c69a56df06cbf9fbff5dec03751b51d53db
  • c26da19e17423ce4cb4c8c47ebc61d009e77fc1ac4e87ce548cf25b8e4f4dc28
  • 47ff0ae9220a09bfad2a2fb1e2fa2c8ffe5e9cb0466646e2a940ac2e0cf55d04
  • 95ffea9b7c5c2e18f7fc801290d4bb2777c05e468e5b3e513a597c41ec9b36fc
  • c7ddd58dcb7d9e752157302d516de5492a70be30099c2f806cb15db49d466026
  • 41aa6b45277445d34060d8cd00a528b08636b86605bbafe643357f2614b66887
  • e47b86b8df43c8c1898abef15b8b7feffe533ae4e1a09e7294dd95f752b0fbb2
  • ef792687b8bcd3c03bed4b09c4722bba921536802afe01f7cdb01cc7c3c60815
  • 030eb56e155fb01d7b190866aaa8b3128f935afd0b7a7b2178dc8e2eb84228b0
  • f93e9bc9583058d82d2d3fe35117cbb9a553d54e7149846b2dc94446f0836201
  • 49062378ab3e4a0d78c6db662efb4dbc680808fb75834b4674809bc8903adaea
  • 816754f6eaf72d2e9c69fe09dcbe50576f7a052a1a450c2a19f01f57a6e13c17
  • bc7c7280855c384e5a970a2895363bd5c8db9088977d129b180d3acb1ec9148a

[ad_2]
Source link

Samsung Galaxy A55 & A35 are official as Cheap Galaxy S24 Alternatives

0
[ad_1]

Samsung‘s long-rumored mid-range smartphones, the Galaxy A55 and Galaxy A35, are finally official. The company launched the duo today. They have a lot in common, though there are enough differences for a substantial gap in the entry price. But before we get into the pricing details, let’s check the specs.

Galaxy A55 and Galaxy A35 specs

Samsung has equipped the Galaxy A55 and Galaxy A35 with a 6.6-inch Super AMOLED display with a Full HD+ resolution (1080×2340 pixels), 120Hz refresh rate, and Vision Booster. Both devices feature Gorilla Glass Victus+ for display protection and a glass back. However, only the former gets a metallic frame (aluminum). The latter has a plastic frame. The phones boast an IP67 rating for dust and water resistance.

The two Galaxy mid-rangers look identical thanks to Samsung’s new Key Island design. They sport three cameras on the back, aligned vertically with no housing. Both have a 50MP primary shooter with OIS (Optical Image Stabilization) and a 5MP macro camera. The ultrawide lens is a 12MP unit on the Galaxy A55, while it is an 8MP camera on the Galaxy A35. The selfie camera has a 32MP sensor on the former and a 13MP one on the latter.

The Galaxy A55 and Galaxy A35 can record 4K videos with their front and rear cameras. The phones also boast stereo speakers, Bluetooth 5.3, Wi-Fi 6, NFC (not available in some regions), USB Type-C 2.0, and an under-display fingerprint scanner. They are fueled by a 5,000mAh battery with 25W fast wired charging support. As you might expect, Samsung won’t give you a charging adapter in the retail box.

As far as the processor is concerned, the Galaxy A55 is powered by Samsung’s Exynos 1480. It has a maximum CPU speed of 2.75GHz and features a custom AMD-powered GPU. The phone is available in 8GB and 12GB RAM variants, paired with 128GB and 256GB storage options. The Galaxy A35, on the other hand, has last year’s Exynos 1380 chipset clocked at 2.4GHz. It tops out at 6GB RAM. You also have a microSD slot on both phones.

Samsung Galaxy A35 official 1

Four years of Android updates for both phones

The Galaxy A55 and Galaxy A35 ship with Android 14 and One UI 6.1. Samsung says both phones will get four major Android OS updates and five years of security patches. So you will get new features up to Android 18 and security updates until at least March 2029. Additionally, for the first time in the Galaxy A history, Samsung’s hardware-based and tamper-resistant security solution, Samsung Knox Vault, is coming to these phones.

The devices also feature the Samsung Knox security platform and Auto Blocker. The latter is an “opt-in package of additional security measures.” It can “block app installations from unauthorized sources, provide app security checks to scan for potential malware, and block potentially malicious commands and software installations to your device while connected by USB cable,” the company explains.

“With the Galaxy A series, we are expanding our latest technologies to a wider audience so that more people can benefit from them,” said TM Roh, Samsung’s head of mobile business. “We are excited to open up even more possibilities on the Galaxy A series this year, including offering Samsung Knox Vault for the first time on this lineup. We’re proud to enable Galaxy A series users to safely and reliably enjoy outstanding mobile experiences.”

Price and availability

Samsung has priced the Galaxy A55 at €479 (approx. $525) for the 8GB+128GB model and €529 (approx. $580) for the 8GB+256GB model in Europe. The price of the 12GB+256GB variant is not known. The Galaxy A35 starts at €379 (approx. $415) for its base variant with 6GB RAM and 128GB storage. For the 8GB+256GB model, you will have to shell out €449 (approx. $492). This phone is also available in an 8GB+128GB configuration but its price is not known.

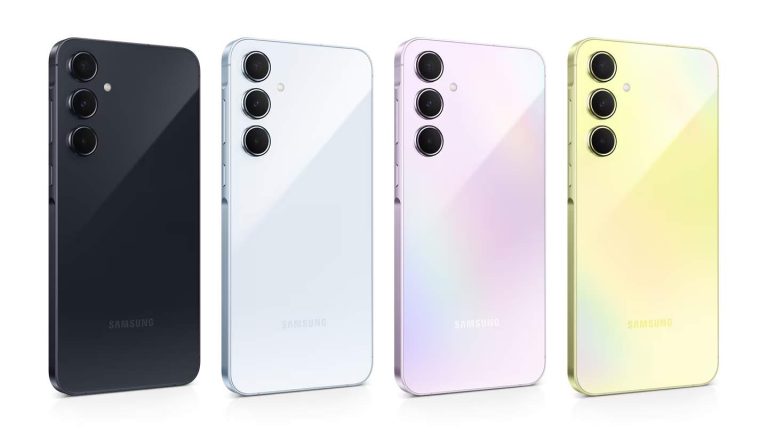
In some European markets, Samsung is offering a free pair of the Galaxy Buds FE with pre-orders of the Galaxy A55 and Galaxy A35. Both phones come in the same four colors: Ice Blue, Lavender, Lemon Yellow, and Navy Blue. The company will start shipping the devices in Europe on March 15. It will reveal the release date, pricing, and pre-order benefits for other markets, including the US, in due course.


[ad_2]
Source link

Hackers Compromised TeamCity Server To Install BianLian’s GO Backdoor

0
[ad_1]

BianLian attackers exploited a TeamCity vulnerability (CVE-2024-27198 or CVE-2023-42793) to gain initial access and move laterally within the network. 

They deployed a PowerShell backdoor disguised as legitimate tools that use two-layer obfuscation with encryption and string substitution to communicate with a Command and Control (C2) server. 

Researchers at Guidepoint Security linked this backdoor to the BianLian group based on its functionalities, SSL communication, and communication with a server identified as running BianLian’s GO backdoor. 

Escalating Threat: From TeamCity Breach to PowerShell Backdoor

After Attackers exploited a TeamCity vulnerability (CVE-2024-27198 or CVE-2023-42793) to gain initial access, attackers used various Windows commands to discover the network and pivot to two build servers. 

Legitimate Winpty tools were abused to run commands and deploy malicious tools, including a PowerShell script (web.ps1). Anti-virus identified DLLs associated with BianLian malware, hinting at web.ps1’s functionality. 

The attackers also used other malicious binaries and tools to communicate with their servers and steal credentials. Attackers were detected when they attempted to dump credentials using a Security Accounts Manager (SAM) technique. 

After failing to deploy their GO backdoor, attackers used a PowerShell backdoor with similar functionality, using two layers of obfuscation: encrypted byte array and string substitution.

The first layer was a simple encryption-decryption process that replaced the execution command with a command to write the decrypted content to a new file for easier analysis.

The second layer looked complex but after renaming variables through a “find-and-replace” approach, it became clear. 

Obfuscated Second Stage PowerShell Script

The script connects to a Command and Control (C2) server, likely for continuous operations, and uses methods related to SSL streams and TCP sockets, suggesting tunneling or backdoor functionalities.

Deobfuscated PowerShell Contents

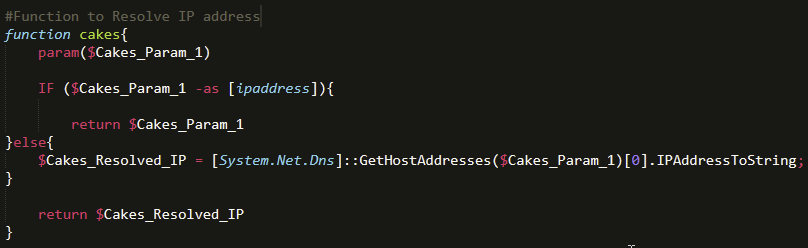
On analyzing a malicious PowerShell backdoor linked to the BianLian threat group, the backdoor, named “cakes” and “cookies” functions, uses an established SSL stream to communicate with the C2 server. 

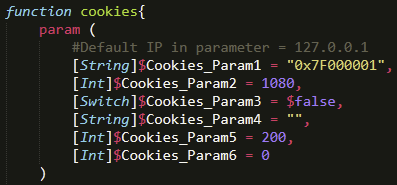
cookies function parameters

It leverages runspace pools for asynchronous execution and .NET PowerShell. The Create() method to invoke ScriptBlocks is more efficient and potentially harder to detect than traditional Invoke-Command or Invoke-Expression.

Similar to BianLian’s GO backdoor, this PowerShell backdoor uses certificates for authentication and validates the remote SSL certificate with 

After successful validation, it establishes an SSL stream and communicates with the C2 server for further instructions.

Analysis of the PowerShell script revealed a function call with a parameter (Cookies_Param1) converting to a specific IP (136.0.3.71) in decimal form. 

Establishing the SSL Connection

The OSINT investigation linked this IP to a server running the BianLian GO backdoor on March 6th, 2024, coinciding with the incident time frame. 

Detections for the BianDoor.D signature were observed before the PowerShell backdoor execution, and these findings strongly suggest that the PowerShell script is a BianLian GO backdoor variant.

Indicators of Compromise

INDICATORTYPEDESCRIPTION
web.ps1FilenamePowerShell Implementation of BianLian GO Backdoor
136[.]0[.]3[.]71IP AddressBianLian C2 Infrastructure
88[.]169[.]109[.]111IP AddressIP Address associated with malicious authentication to TeamCity
165[.]227[.]151[.]123IP AddressIP Address associated with malicious authentication to TeamCity
77[.]75[.]230[.]164IP AddressIP Address associated with malicious authentication to TeamCity
164[.]92[.]243[.]252IP AddressIP Address associated with malicious authentication to TeamCity
64[.]176[.]229[.]97IP AddressIP Address associated with malicious authentication to TeamCity
164[.]92[.]251[.]25IP AddressIP Address associated with malicious authentication to TeamCity
126[.]126[.]112[.]143IP AddressIP Address associated with malicious authentication to TeamCity
38[.]207[.]148[.]147IP AddressIP Address associated with malicious authentication to TeamCity
101[.]53[.]136[.]60IP AddressIP Address associated with malicious authentication to TeamCity
188[.]166[.]236[.]38IP AddressIP Address associated with malicious authentication to TeamCity
185[.]174[.]137[.]26IP AddressIP Address associated with malicious authentication to TeamCity
977ff17cd1fbaf0753d4d5aa892af7aaMD5Web.ps1
1af5616fa3b4d2a384000f83e450e4047f04cb57SHA1Web.ps1
7981cdb91b8bad8b0b894cfb71b090fc9773d830fe110bd4dd8f52549152b448SHA256Web.ps1
hxxp://136[.]0[.]3[.]71:8001/win64.exeURLBianLian C2 Infrastructure
hxxp://136[.]0[.]3[.]71:8001/64.dllURLBianLian C2 Infrastructure

[ad_2]
Source link

Xiaomi no longer lets you play YouTube videos in the background

0
[ad_1]

The latest update rolling out to Xiaomi devices removes the ability to play YouTube videos in the background without subscribing to YouTube Premium, 9to5google reports. This has been one of the most popular features on Xiaomi phones, and customers are already upset about its absence.

One of the most frustrating aspects of watching YouTube videos is that the video stops playing once the screen turns off. Google solved this issue without YouTube Premium. However, it requires users to pay up to $13.99 monthly for individual tiers. On the other hand, Xiaomi brought this feature to users for free, making it a convenient and popular choice.

Xiaomi removes the feature to play YouTube videos in the background

Meanwhile, as Android Authority notes, the company announced on its Mi Fans Telegram channel that the “Play video sound with screen off” feature will be removed from MIUI devices due to “compliance requirements.”

“Due to compliance requirements, we regret to inform you that we have removed the “Play video sound with screen off” function in the video toolbox feature and the “Turn off screen” function in the game toolbox feature through Over-The-Air (OTA) updates,” Xiaomi added. The features first came to Xiaomi devices with the Android-based MIUI 12 update.

Xiaomi has also listed the impacted devices, including some of the company’s best-selling phones. Such as the Xiaomi 14 and 13 Pro. The full list of impacted devices is shown in the screenshot below.

The company has yet to reveal the real reason behind removing such a popular feature from its devices. However, mentioning “compliance requirements” might hint at the possibility that Google and other content distributors pressured Xiaomi to abandon the feature, sparking curiosity among users.

Google is using any possible way to make users buy a YouTube Premium subscription

Any user who wants to play YouTube videos in the background with a turned-off screen must buy a Premium subscription. An ad-free experience and video downloading are other perks you get for $13.99 a month. If you want to continue watching YouTube videos in the background, you can download apps tailored to this need, such as Black Screen.

This is not the first time Google has cracked down on any service that offers its premium perks for free. In November, YouTube announced it would prevent users from watching videos unless they turned off ad blockers.

Xiaomi devices without YouTube playing in background


[ad_2]
Source link

Galaxy Z Fold 5, Flip 5, Fold 4 & Flip 4 get March update in the US

0
[ad_1]

Samsung‘s March 2024 update is quickly expanding to more Galaxy devices in the US. After the Galaxy S24 and Galaxy S23, the latest security patch is rolling out to the Galaxy Z Fold 5, Galaxy Z Flip 5, Galaxy Z Fold 4, Galaxy Z Flip 4, and Galaxy S23 FE. It is also widely available for the Galaxy S23 series.

Samsung pushes March update to more Galaxy devices in the US

The March 2024 SMR (Security Maintenance Release) is rolling out widely to all variants of the Galaxy Z Fold 5 in the US. The new firmware build numbers for the phone are F946USQS2BXBE (carrier-locked) and F946U1UES2BXBE (unlocked). As suggested by the build version and confirmed by the official changelog, the update only contains the latest security fixes (more on this later).

The same update is also rolling out to the Galaxy Z Flip 5 in the US. However, we can currently confirm the availability only for the carrier-locked variant. The update comes with the build number F731USQS2BXBE. The changelog is the same as the Fold mode, i.e., it a a pure security update. Samsung should soon push the new SMR to unlocked units and expand the rollout to both 2023 foldables globally.

The March security update for the Galaxy Z Fold 4 and Galaxy Z Flip 4 is also currently limited to carrier-locked units. The updated build numbers for the 2022 foldable duo are F936USQS4EXBD and F721USQS4EXBD, respectively. Unsurprisingly, neither model is picking up anything more than this month’s security fixes. You will have to wait longer for the One UI 6.1 feature update.

As far as security patches are concerned, Samsung has confirmed that the latest SMR contains three dozen Android OS fixes and nine Galaxy fixes. The March SMR is relatively small if you look at the number of fixes in the previous releases. Nonetheless, it patches some critical vulnerabilities, and you should install it on your Galaxy foldable as soon as it is available. You can check for updates from the Settings app.

The Galaxy S23 series is widely getting this update in the US

These security fixes are also widely rolling out to the Galaxy S23 series in the US. The rollout began last week for carrier-locked units. It is now available for unlocked units and the Galaxy S23 FE. The new build number for the flagships is similar to carrier-locked units (ends in BXBD). It is S711USQS2BXBF for the Fan Edition (FE) model. The changelog confirms it is only a security update.


[ad_2]
Source link

Samsung Galaxy Book 4 Edge pricing and specs leak

0
[ad_1]

Samsung is gearing up to launch its first laptop powered by the new Qualcomm Snapdragon X Elite SoC. Qualcomm’s new platform promises high performance and power efficiency. The upcoming laptop from Samsung, dubbed the Galaxy Book 4 Edge, could compete with Apple silicon-powered MacBooks.

Samsung is going to be one of the early adopters of the Snapdragon X Elite SoC

This upcoming device will be equipped with Qualcomm’s 12-core ARM CPU, featuring clock speeds of up to 4.3 gigahertz. This processor, incorporating the latest “Oryon” CPU architecture is reportedly developed by a team of former Apple chip designers. It aims to rival Apple’s M series processors, narrowing the disparity between Windows and MacOS-based devices.

Initial details about the Galaxy Book 4 Edge reveal a 14-inch display along with 16GB RAM and a 512GB SSD. It’s unclear about the storage and memory configurations at this point.

This upcoming potentially power-efficient Samsung laptop also comes at a premium price, with the high-end variant estimated to retail around 1800 euros (~$1,967). As WinFuture notes, this upcoming Galaxy Book is priced at a similar range as compared to the latest MacBook Air, which currently costs 1759 euros in Germany.

Despite its hefty price tag, the Galaxy Book 4 Edge is likely to justify its value proposition based on its power-efficient operation. Based on what Qualcomm showed off last year about the Snapdragon X Elite chip, Samsung’s new Galaxy Book should offer significantly longer battery life given that Samsung does not reduce the battery capacity.

Besides longer battery life, the Galaxy Book 4 Edge may also offer significantly better performance

For someone who is thinking about the potential performance gains, luckily we have some insights here. Qualcomm showed off two different machines running on the Snapdragon X Elite chip with 27W and 80W TDPs at the Snapdragon Technology Summit last year. Surprisingly, both of them outperformed the MacBook Air with an M2 chip in XDA Developers’ tests of Geekbench 6.2. The one with just 23W TDP scored 2,762 and 13,845 on single and multi-core tests respectively.

In comparison, the MacBook Air M2 only managed to harness 2,591 and 9,837 points on the tests respectively. Not to mention, the future of Windows on Arm devices looks promising.

We don’t know the exact launch date of the Galaxy Book 4 Edge at this point. However, Qualcomm’s new SoC won’t be here until “mid-2024,” confirmed president and CEO Cristiano Amon at Qualcomm’s Q1 2024 earnings call. So, you shouldn’t expect this Snapdragon X Elite-powered Galaxy Book to appear before the second half of this year.


[ad_2]
Source link

EU could launch investigations into DMA compliance plans

0
[ad_1]

The European Union’s new Digital Markets Act finally took effect last week, and that means the biggest companies in the technology industry were forced to comply. That includes the likes of Apple, Google, Meta, Microsoft, and more. These companies, designated as “gatekeepers” by the EU, are now subject to regulation. There is a financial incentive for the corporations to get it right, too. If they are not found to be in compliance, they could be heavily fined. The EU states that companies not found to be in compliance could be the subject of DMA investigations and fined up to 10% of their total revenue.

The following six companies are considered gatekeepers: Google, Apple, Amazon, Microsoft, Meta, and ByteDance. They have each had unique approaches to DMA compliance. In part, that’s because each company may have different obligations under the law. Gatekeepers have at least one “core platform service,” which the EU defines as those that are critical to business in the region. Different requirements may apply to each gatekeeper based on their core platform service. There is also some ambiguity here since the DMA is a new law that is yet to be tested.

However, it’s looking like the EU is likely to open investigations over the DMA. A report from Reuters predicts this, with a few caveats. The report says that EU regulators may only pick a few DMA investigations to pursue. “Microsoft, Amazon, and ByteDance may face less scrutiny initially as EU regulators focus their resources on one or two cases and ensure a case able to withstand a legal challenge, people familiar with the matter said,” per Reuters. This may be due to the time constraints related to the investigations, which stipulate regulators must report their findings in just one year.

Which companies could face EU investigations over the DMA?

That leaves Apple, Meta, and Google as the most likely targets for investigation. Apple might be the obvious choice because it has come under heavy fire for its DMA plans. It also has arguably been affected most by the DMA. That’s because the regulation forced it to open up iOS to third-party app stores, default browsers, and more. Apple has also been criticized for its new fee system, which heavily charges developers who use third-party distribution methods.

Another company that could face investigations is Google. No other company has more “core platform services” than Google, which has eight. Meta is also a possibility, as it wants to give users the option to opt into cross-platform data sharing. The truth is, that many companies don’t know exactly what the DMA requires. They might be testing the waters to find out what the true requirements are following investigations.


[ad_2]
Source link