xAI to open source Grok amid the ongoing clash with OpenAI

0

[ad_1]

Elon Musk today announced that xAI is going to open source the Grok chatbot. Notably, Grok is one of the competitors of OpenAI’s ChatGPT, the company Musk co-founded and recently filed a lawsuit for steering away from the non-profit mission. This lawsuit referred to OpenAI as a “closed-source de facto subsidiary” of Microsoft, which owns over 49% stake. In return, OpenAI said that Musk wanted to combine the company with Tesla and become its CEO in old emails. Now, let’s hop on to the recent development.

Elon Musk announces xAI will soon be open source

Elon Musk shared this update via a post on X, however, he didn’t delve into many details. According to him, the Grok chatbot could open source this week. At the same time, he fired shots at OpenAI. “OpenAI is a lie,” he replied to a user. Open sourcing the code of Grok means that developers could access and modify the code which could open doors for creativity. Among many who reacted to this post is Nothing CEO Carl Pei who called this move, “Based” and Perplexity boss Aravind Srinivas who reacted with a salute emoji.

Grok is accessible exclusively for those users who have subscribed to Premium+ on X. Musk, once referred to Grok as “based and loves sarcasm.” He reiterated that Grok has “little humor in its responses.”

This isn’t the first time for an Elon Musk-owned enterprise

Musk’s companies have a history of open-sourcing codes for users. Tesla, for example, made its patents public ten years ago, and now many car makers use its electric vehicle charging connector. Another Musk venture, X, released the code for its “For You” algorithmic feed last year, but it didn’t reveal much.

Meanwhile, The Wall Street Journal points out Musk might be thinking that by allowing other developers and researchers to explore Grok’s code, more people will use the model. Feedback from the developer community could also make Grok better. This makes sense since Grok hasn’t reached the same heights as its competitors, including Microsoft-backed ChatGPT and Google’s very own Gemini.


[ad_2]

Source link

Magnet Goblin Hackers Using Ivanti Flaws to Deploy Linux Malware

0

[ad_1]

Magnet Goblin Hackers Using Ivanti Flaws to Deploy Linux Malware

Hackers exploit unpatched Ivanti vulnerabilities to deploy malware on Linux systems. Magnet Goblin targets businesses using outdated software. Patch immediately and implement strong security measures to protect against these attacks.

Cybersecurity researchers at Check Point are warning of a malicious campaign targeting one-day vulnerabilities in Ivanti and other security software products, potentially impacting a wide range of organizations.

The culprit behind this campaign is a financially motivated hacker group known as Magnet Goblin. This group has been active since January 2022 and specializes in leveraging newly disclosed vulnerabilities, targeting public-facing servers and edge devices.

According to Check Point’s research, Magnet Goblin is using one-day security vulnerabilities to breach edge devices and public-facing services and deploy custom malware on Linux systems. For your information, after zero-day vulnerabilities are disclosed publicly and patches are released, they are referred to as one-day vulnerabilities.

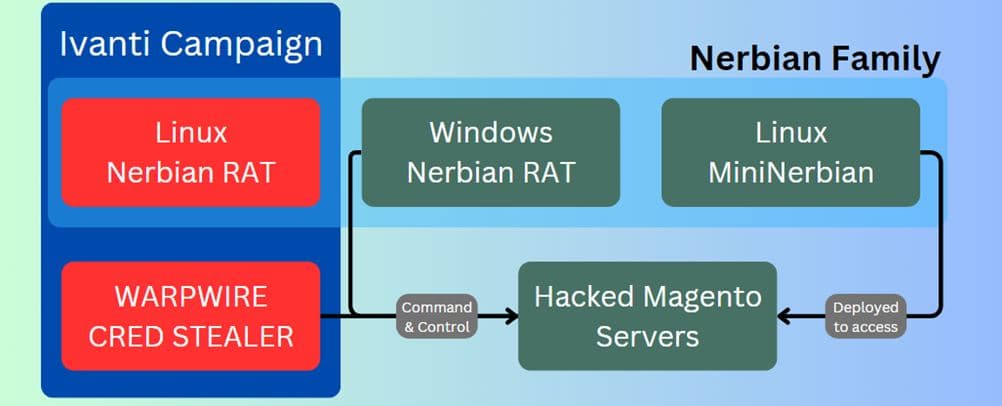
The attackers exploit unpatched servers like Ivanti Connect Secure VPN, Magento, Qlik Sense, and possibly Apache ActiveMQ to deploy a cross-platform remote access trojan (RAT) called Nerbian RAT, first documented by Proofpoint in 2022. It also utilized Nerbian RAT’s simplified variant, MiniNerbian, which allows arbitrary command execution from a C2 server. 

“NerbianRAT and MiniNerbian… these tools have operated under the radar as they mostly reside on edge devices. This is part of an ongoing trend for threat actors to target areas which until now have been left unprotected,” researchers noted.

NerbianRAT is downloaded from compromised systems with critical Ivanti Connect Secure flaws. While researching, CheckPoint discovered a 1-day vulnerability infection that led to the download of the NerbianRAT Linux variant.

The variant was used to execute various malicious activities on compromised systems, including modifying connection intervals, work time settings, and updating configuration variables.

Magnet Goblin leveraged CVE-2023-46805, CVE-2024-21887, CVE-2024-21888, and CVE-2024-21893 in Ivanti VPNs, CVE-2022-24086 in Magento, and CVE-2023-41265, CVE-2023-41266, and CVE-2023-48365 in Qlik Sense.

They used a JavaScript credential stealer called Warpwire and the open-source tunnelling tool Ligolo to exploit these vulnerabilities. Warpwire stealer is linked to mass Ivanti vulnerability exploitation and was used in a 2022 Magento server attack. In addition, they used remote monitoring tools ScreenConnect and AnyDesk, targeting Qlik Sense and Apache ActiveMQ.

It is worth noting that Ivanti issued a public advisory in January for CVE-2024-21887, a command injection vulnerability, urging users to patch their systems against wild exploitations. However, Check Point found that Magnet Goblin exploitations occurred within a day of patch issuance, targeting systems not yet patched with available fixed updates.

Magnet Goblin Hackers Using Ivanti Flaws to Deploy Linux Malware
Compromised Magento servers used in Magnet Goblin campaigns (Screenshot: Checkpoint)

John Gallagher, Vice President of Viakoo Labs at Viakoo commented on the findings stating, “It’s clear that Magnet Goblin is taking the easy route; using recently disclosed vulnerabilities to exploit poorly defended systems. With many edge and IoT devices and applications there is a lag time between when a vulnerability is disclosed and when a patch is available…and then another lag time between when the patch is released and when it is implemented.”

“Often the teams managing edge and IoT systems are outside of IT and may have different priorities or sense of urgency when it comes to patching. One can expect that one-day threats will be a major security issue, as the speed of AI can accelerate these specific types of threats. Until the speed of delivery by threat actors is matched by the speed of response by defenders this will be an ongoing security risk.”

Organisations of all sizes relying on Ivanti software for endpoint management and security are at potential risk. This includes companies in various sectors that utilize Ivanti to safeguard their critical infrastructure.

Therefore, patching Ivanti software is necessary to prevent exploitation along with increased monitoring, and adopting a layered security approach, including implementing Endpoint Detection and Response (EDR) solutions to strengthen the overall security of the network and devices.

  1. New Linux Malware Alert: ‘Spinning YARN’ Hits Docker
  2. Linux Malware “Migo” Exploits Redis for Cryptojacking
  3. Bifrost RAT Targets Linux Devices, Mimics VMware Domain
  4. Crypto Stealing PyPI Malware Hits Both Windows and Linux Users
  5. Mirai-based NoaBot Botnet Targeting Linux Systems with Cryptominer


[ad_2]

Source link

February update lands on Galaxy A53, A32 & A13 5G in the US

0

[ad_1]

Samsung‘s February 2024 security update is finally available for factory-unlocked units of the Galaxy A53 in the US. It comes more than a month after the carrier-locked variants picked up the update. The company is also pushing the new security patch to the Galaxy A32 and Galaxy A13 stateside. These devices may or may not get the March security update from Samsung.

The Galaxy A53 is widely getting Samsung’s February update in the US

The Galaxy A53 was one of the first Samsung devices to receive the February 2024 SMR (Security Maintenance Release) in the US. The 2022 mid-range device picked up the update early in February. However, the company only pushed it to the carrier-locked variants. We expected it to cover unlocked units soon but not to be. After making users wait for a whole month, Samsung has finally begun a wide rollout.

The latest update for the unlocked Galaxy A53 in the US comes with the firmware build number A536U1UES8DXA5. According to SamMobile, which first reported this rollout, the update is available for users on all major carrier networks, including AT&T, Bluegrass Cellular, C-Spire, Cellular South, Comcast, Cricket, DISH, MetroPCS, T-Mobile, US Cellular, Verizon, and Xfinity Mobile.

Like the carrier-locked Galaxy A53, unlocked units are also only getting last month’s security fixes. There are no new features or other changes in this package. Samsung fixed more than 60 security vulnerabilities (the vast majority were Android OS patches released by Google) in February. Some of those were critical security flaws that could allow threat actors to gain remote access to affected devices.

These security fixes are also rolling out to the Galaxy A32 and Galaxy A13 in the US. The update is currently available for the carrier-locked variant of the former and the unlocked variant of the latter, the same publication reports. The new build numbers are A326USQSCDXB2 and A136U1UES7DXB1, respectively. Unsurprisingly, the update only brings security fixes with no additional changes.

The March SMR is already rolling out to Galaxy devices

These Galaxy smartphones are getting the February update in the US just as Samsung is rolling out the March SMR to other models. The Galaxy S24 and Galaxy S23 have already received the new update. More will join the party soon. If you are using a Samsung phone or tablet, you can always check for updates by navigating to Settings > Software update and tapping the Download an Install option.

[ad_2]

Source link

Next-Gen LPDDR6 RAM Standard To Be Finalized Later This Year

0

[ad_1]

The specifications for next-gen Low-Power RAM, referred to as LPDDR6, are being finalized. Although the final standard for LPDDR6 should be announced later this year, the focus would be on further reducing power consumption and ensuring better data performance.

The JEDEC Solid State Technology Association has indicated it would announce the final specifications of the LPDDR6 RAM in the third quarter of this year. LPDDR6 succeeds the LPDDR5, LPDDR5X, and LPDDR5T RAM standards, commonly found in high-end laptops, smartphones, and tablets.

What Is LPDDR6 RAM?

The International Semiconductor Standards Organization (JEDEC) recently held discussions on next-generation mobile RAM standards in Lisbon, Portugal. The organization listened to more than 60 veterans from memory, system semiconductor, and Intellectual Property (IP) companies.

JEDEC is yet to announce the final specifications of the LPDDR6 standard. However, the organization did reportedly announce:

“We have held various discussions to confirm the LPDDR6 standard specification. (The standard specification) will be released in the third quarter of this year.”

The last formal LPDDR RAM standard, the LPDDR5, was announced five years ago. A significant leap over the LPDDR4 standard, RAM based on the LPDDR5 had a 50% performance boost, while boasting about 30% improved power efficiency.

While LPDDR4 RAM is capable of hitting 3.7Gbps speeds, the LPDDR5-based RAM can theoretically go up to 6.4Gbps. The LPDDR5X RAM from Samsung boasts of peak speed of about 8.5Gbps.

Although JEDEC hasn’t officially commented on the top speed, a post on AnandTech claims RAM based on the upcoming standard would cross the 10Gbps barrier. Some premium variants might even touch 13Gbps.

What Are The Advantages And When To Expect LPDDR6 RAM?

As the name suggests, LPDDR is meant for smart devices where each milliwatt of power is critical. In other words, power optimization is as important as raw performance.

As with any latest and greatest tech, the LPDDR6 RAM could be discovered inside upcoming flagship Snapdragon and MediaTek chipsets, expected to be announced next year. Some reports suggest the Qualcomm Snapdragon 8 Gen 5 could be the first SoC (System on a Chip) to pack LPDDR6 RAM. The upcoming Snapdragon 8 Gen 4 SoC is tipped to arrive in October this year. Hence, it might not pack RAM that’s based on a still-to-be-finalized standard.

After smartphones, “Ultra-Book” laptops from Samsung, ASUS, and Lenovo would feature LPDDR6-based RAM. In terms of RAM capacity, smartphones and tablets could boast anywhere from 16GB to 32GB of LPDDR6 RAM.

The biggest advantage of LPDDR6 RAM, besides improved speed and better power management, would be its ability to support on-device AI. Large-scale AI calculations, executed locally on smartphones, laptops, and tablet PCs, have been a long-standing demand. LPDDR6 could finally fulfill the same.

Needless to conclude, market leaders in RAM manufacturing such as Samsung, SK Hynix, and Micron would be waiting impatiently. However, consumers shouldn’t expect smartphones, tablets, and laptops with LPDDR6 RAM to arrive in 2025. That being said, the LPDDR5 standard is yet to trickle down to mid-range devices, let alone budget smartphones or laptops.


[ad_2]

Source link

Galaxy S24 global sales up 8% compared to Galaxy S23

0

[ad_1]

Samsung‘s Galaxy S24 flagships have enjoyed tremendous early success. The phones are selling well globally, breaking years-long records in some regions. We now have data that precisely tells how big of a success it has been for the Korean firm. According to market research firm Counterpoint, global Galaxy S24 sales in the first three weeks were up 8% compared to the Galaxy S23.

Galaxy S24 sales have grown worldwide

Samsung unveiled the Galaxy S24 series on January 17 and immediately opened pre-orders in some regions. Early buyers started receiving the phones about a week later. Counterpoint tracked the global sales of the lineup for three weeks between January 28 and February 17. Compared to the Galaxy S23 series over the same period last year, the new flagships sold 8% higher.

The growth was much higher in some regions. In Samsung’s homeland South Korea, the Galaxy S24 trio registered a 22% jump in sales. Increased demand in the UK, Germany, and France means sales in Western Europe grew 28%. In the US, Galaxy S24 sales were 14% higher than the Galaxy S23. An earlier report said Galaxy flagship sales in the US have reached a new high in eight years.

As expected, the Galaxy S24 Ultra is the top-selling model in the lineup. It accounted for 52% of all Galaxy S24 sales globally during the said period. The base Galaxy S24 accounted for 27%, and the Plus made up the rest (21%). It appears the Galaxy S24+ is selling better than its predecessor. Samsung’s decision to give it a RAM boost seems to be working.

If early signs are anything to go by, Samsung is on track to sell around 35 million Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra units combined globally this year. It would be a double-digit sales growth over the Galaxy S23 series. However, the company still has to overcome a lot of challenges for that. It must find a way to keep the new flagships relative on the market.

Samsung might retake the smartphone crown from Apple

After leading the global smartphone market for years (in terms of units sold), Samsung lost the crown to Apple in 2023. The iPhone maker surpassed the Korean giant by a few million units. While it would do all in its power to stay at the top this year, Samsung might retake the crown in 2024. A lot will depend on how well the newly launched mid-rangers, the Galaxy A55 and Galaxy A35, sell.

[ad_2]

Source link

Reports show that phishing attacks have increased by 40% in 2023

0

[ad_1]

Kaspersky, a renowned cybersecurity firm, reported a significant surge in phishing attacks thwarted by its anti-phishing system in 2023. The system successfully blocked over 709 million attempts to access phishing and scam websites.

Numerous platforms were exploited by threat actors

Among the pathways most frequently exploited by threat actors were messaging apps, artificial intelligence platforms, social media services, and cryptocurrency exchanges. The trend of increased phishing attacks observed in 2022 persisted in 2023. Notably, the attacks increased by over 40 percent throughout the last year.

The number of attempts to access phishing links reached a staggering 709,590,011. Scammers commonly propagated travel-related scams like counterfeit airline tickets and fake hotel deals. Additionally, the integration of technologies featuring built-in LLMs provided scammers with new avenues to exploit, while traditional tactics targeting high-profile releases, events, and premieres remained prevalent.

Kaspersky Cyber Security Solutions thwarted 62,127 attempts to redirect users via phishing and scam links on Telegram alone. It represents a significant 22% increase from the previous year. The majority of redirection attempts targeted users in Russia, followed by Brazil, Turkey, India, Germany, Italy, and Mexico. It indicates a global reach of these malicious activities.

Olga Svistunova, a security expert at Kaspersky, emphasized the importance of vigilance and skepticism in combating phishing threats. She advised users to exercise caution when opening emails and clicking links, particularly if the sender or content seems suspicious. Keeping an eye on the spelling of website URLs and the layout of the sites are also proven security measures when surfing the web. It reduces the risk of falling victim to phishing-based scams.

Kaspersky’s securelist summarizes that 45.60% of all emails sent worldwide and 46.59% of all emails sent in the Russian web segment were spam. Additionally, Kaspersky Mail Anti-Virus blocked 135,980,457 malicious email attachments.

Multifaceted tactics of cybercriminals in 2023

In 2023, cybercriminals employed a variety of tactics to exploit users. It includes phishing schemes targeting gamers with promises of exclusive game access and in-game valuables, fake tax refund websites preying on users seeking financial benefits, and deceptive lottery offers for work or student visas. Scammers also enticed users with promises of easy money through fraudulent schemes disguised as paid tasks or investment opportunities.

Additionally, attackers leveraged social networks and messaging apps to spread phishing links and scams, such as fake Meta ad credits and fraudulent WhatsApp bots. Moreover, the exploitation of artificial intelligence, with fake AI chatbots offering tech support or investment advice, further contributed to the diverse range of tactics employed by scammers.

[ad_2]

Source link

Release date, specs, price & more

0

[ad_1]

The Google Pixel 9 Pro is one of three Pixel flagships Google plans to announce this year. The Pixel 9 is also coming, as is the Pixel Fold 2. The Pixel 9 and Pixel 9 Pro are expected to launch at the same time, in October this year. We have a separate Pixel 9 preview article, in case you’re interested in that. The ‘Pro’ model will be the more powerful of the two, though, even though both devices will technically be flagship-grade.

At this point in time, we’re still quite some time away from the launch of the device. Therefore not a lot of information surfaced, but more is coming constantly. So we will keep updating the article, but for now, we’ll talk about what we know, and what we think we know about the device. So, let’s get to it, shall we?

This article will be regularly updated with new information on the Google Pixel 9 Pro (this is a preview article) — both official teasers and credible leaks, rumors, and insider claims — as it becomes available in the run-up to the release of the upcoming Android smartphone. This is the original posting of this article.

When will the Google Pixel 9 Pro be released?

The Google Pixel 9 Pro is expected to launch in October, alongside its sibling, the Pixel 9. The Pixel 7 series arrived on October 4, 2023, while the Pixel 8 series launched on October 6, 2023. Therefore, we do believe that the Pixel 9 series will also arrive in October. Well, unless Google has some major changes planned for this year. There’s a slight chance the event could take place in late September, we’ll see. We’re still months from the confirmation, though. Google likely won’t share the exact launch date until September.

What models are coming?

Last year, Google launched a single RAM variant of the Pixel 8 Pro, but that model arrived in several different storage options. The same is likely to happen this year. We probably won’t see more than one RAM variant of the Pixel 9 Pro. It’s very likely Google will stick with 12GB of RAM in the Pixel 9 Pro, but no info surfaced just yet, so it’s possible that will get upped to 16GB of RAM. It’s improbable, though. Google will use LPDDR5X RAM, though.

When it comes to storage, last year, the entry-level variant offered 128GB of storage. The same could end up being the case this year, though Google could up that to 256GB of storage. Chances are we’ll get several variants going up to 1TB of storage. Chances are Google will use UFS 4.0 flash storage this time around, while it used UFS 3.1 last year. The storage will not be expandable.

How much will the Google Pixel 9 Pro cost?

What about the Pixel 9 Pro price? Well, we still don’t have any information regarding that. The Pixel 8 Pro did start at $999 last year, and it would be preferable if Google kept that price tag intact. There is a chance the company will bump it to $1,099, though, or something of the sort. The Pixel 8a is expected to get a price bump, so the same could happen with the Pixel 9 Pro. We are hoping that won’t be the case, though, as the $999 price tag would be most appealing to consumers.

What will the Google Pixel 9 Pro look like?

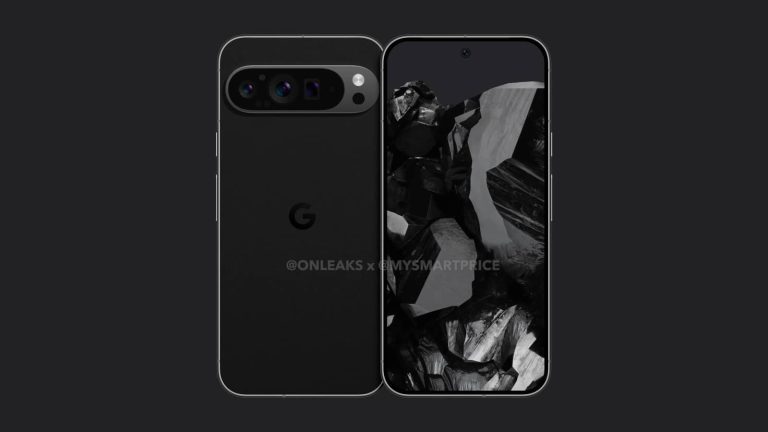
CAD-based Google Pixel 9 Pro renders did surface, so we have a good idea what the phone will look like. Google will redesign the Pixel 9 Pro, to a degree. The device will have flat sides (all around), that are slightly curved toward the edges. That is a completely different approach to what the Pixel 8 Pro delivered. That’s not all, though. The phone will also include a flat display, unlike its predecessor. The display will feature very thin bezels, and those bezels will be uniform. A display camera hole will sit at the top of the display, and it will be centered.

We’ll also see a difference on the back of the device. The back side will be flat this time around. The camera visor will not be connecting to the left and right sides of the frame, as it did on the Pixel 8 Pro. It will be a separate pill-shaped entity on the back, though it will still be covered by metal. This approach is more similar to what the Pixel Fold delivered. The phone would look rather weird if Google went to connect that camera visor to the sides, now that both the sides and the back are flat.

It will have very similar measurements as its predecessor

The Pixel 9 Pro is said to measure approximately 162.7 x 76.6 x 8.5mm. So it will measure approximately the same as the Pixel 8 Pro. Along with the CAD renders, it was said that the display will be a bit smaller this time around. The Pixel 9 Pro is said to have a 6.5-inch panel, not a 6.7-inch one. That is highly unlikely, however. Considering that the size will remain unchanged, and the bezels either remain the same or be thinner, the display will either be a 6.7-inch or a 6.8-inch panel.

The Google Pixel 9 Pro will be made out of metal and glass, just like its predecessor. Its main speaker will be located at the bottom, along with a Type-C USB port. Three cameras will sit inside its camera island on the back. We still don’t know what to expect in terms of weight.

What specs will the Google Pixel 9 Pro have?

What about the phone’s specifications? Well, not a lot of information surfaced thus far, but we can try and guess what we’ll get. What we do know is that the Google Tensor G4 processor will fuel the phone. That chip will be made using Samsung’s 4LPP+ 4nm process. That is the same process as for the Exynos 2400, by the way. Google is expected to make a switch to TSMC with the Tensor G5 in 2025, as that will be a “fully-custom” chip. The Tensor G4 is expected to bring improvements to the table, though, of course.

A 6.5-inch display was tipped by @OnLeaks when CAD renders to shared. We believe that won’t be the case, though. The dimensions of the device will basically remain the same, and the display will remain flat. If we had to guess, we’d say the phone would include a 6.7-inch or a 6.8-inch panel. That will be a QHD+ LTPO AMOLED display, with an adaptive refresh rate of up to 120Hz. The panel is expected to be quite bright and support HDR10+ content too.

Google is expected to make a jump to UFS 4.0 flash storage

Google will most probably include 12GB of LPDDR5X RAM inside of the device. There’s a slight chance we may get 16GB of RAM instead, but that’s not as likely. It’s almost certain only one RAM variant will be available. We do expect multiple storage versions, however, likely going all the way up to 1TB. Google is expected to use UFS 4.0 flash storage this time around. The storage will not be expandable, by the way.

We’re not sure about the battery capacity just yet, but a unit of around 5,000mAh is expected. The Pixel 9 series is expected to support Qi2 charging standard for wireless charging, though. The company most likely won’t increase the speed of wired charging, so 30W charging is expected. Google could still surprise us, though. Do expect the phone to be IP68 certified for water and dust resistance too, and include a set of stereo speakers. We don’t have any information on the phone’s cameras just yet. We are, however, expecting main, ultrawide, and periscope telephoto units on the back.

Should you wait to buy the Google Pixel 9 Pro?

At the time of writing this article, the Pixel 9 Pro launch is over 6 months away. The Pixel 8 Pro is an excellent smartphone, and we get to see various deals for it quite often. If you do need a new phone, getting the Pixel 8 Pro as we speak may not be a bad idea. The Pixel 9 Pro is expected to be an improvement, for sure, but we do feel like the Pixel 10 Pro will be a much bigger jump. So if you do plan on upgrading after 1.5-2 years, getting the Pixel 8 Pro now, and then jumping to the Pixel 10 Pro may not be a bad idea. If you can wait, however, do wait a bit more, as more Pixel 9 Pro is bound to surface in the coming weeks/months.
[ad_2]

Source link

Google Contacts is cleaning up its act with a decluttered view of connected apps

0

[ad_1]

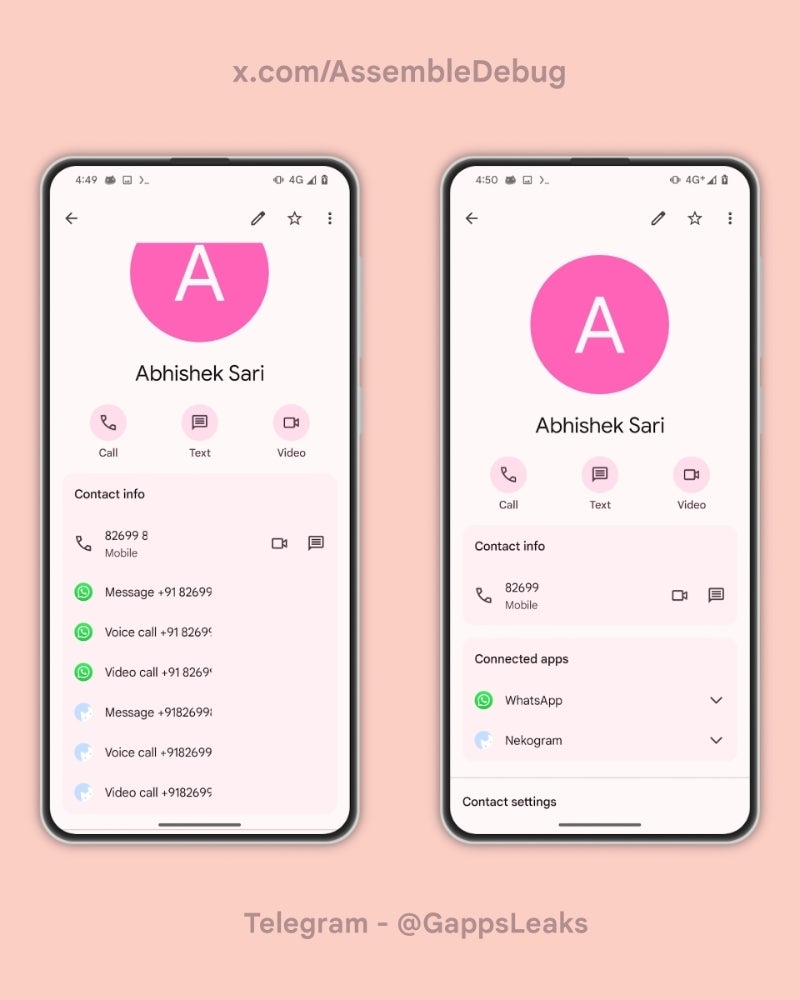
The Google Contacts app is getting a new update soon that will streamline the way you view your contacts’ information. When looking for a specific contact that you have tied to another app on your phone, the contact info will now show this information in a more organized way, likely improving your overall user experience.Spotted by The SP Android in version 4.26 of the app, contact info from connected apps such as WhatsApp or Telegram will now be grouped into a “Connected apps” section. Before the update, this information was shown as a list of phone numbers that would clutter up the contact’s details page. Now, with this new section, users can easily access and manage all connected app information in one convenient location that can be expanded for more details.

Image credit: The SP Android

As you can see in the screenshot above, which highlights the Contacts app’s UI before the update (left) and after (right), this update enhances the user experience. It does that by streamlining the display of contact information and improving overall organization. Users will now be able to quickly access important details from connected apps without having to sift through a cluttered list of phone numbers.

The “Connected apps” section appears to be not limited to just messaging apps but basically any app installed on your device that uses similar contact syncing. This usually involves granting the app in question access to your contact list, a step that not only allows the app to see your contacts but also uses this integration to provide a more personalized experience.

This update is rolling out gradually and is server-side, meaning it is not dependent on any app code tweaking or experimental flags. However, make sure you have the latest Google Contacts version (4.26) installed to receive this feature as soon as it is rolled out for your account.

[ad_2]

Source link

Going viral shouldn’t lead to bomb threats, with Leigh Honeywell: Lock and Code S05E06

0

[ad_1]

This week on the Lock and Code podcast…

A disappointing meal at a restaurant. An ugly breakup between two partners. A popular TV show that kills off a beloved, main character.

In a perfect world, these are irritations and moments of vulnerability. But online today, these same events can sometimes be the catalyst for hate. That disappointing meal can produce a frighteningly invasive Yelp review that exposes a restaurant owner’s home address for all to see. That ugly breakup can lead to an abusive ex posting a video of revenge porn. And even a movie or videogame can enrage some individuals into such a fury that they begin sending death threats to the actors and cast mates involved.

Online hate and harassment campaigns are well-known and widely studied. Sadly, they’re also becoming more frequent.

In 2023, the Anti-Defamation League revealed that 52% of American adults reported being harassed online at least some time in their life—the highest rate ever recorded by the organization and a dramatic climb from the 40% who responded similarly just one year earlier. When asking teens about recent harm, 51% said they’d suffered from online harassment in strictly the 12 months prior to taking the survey itself—a radical 15% increase from what teens said the year prior.

The proposed solutions, so far, have been difficult to implement.

Social media platforms often deflect blame—and are frequently shielded from legal liability—and many efforts to moderate and remove hateful content have either been slow or entirely absent in the past. Popular accounts with millions of followers will, without explicitly inciting violence, sometimes draw undue attention to everyday people. And the increasing need to have an online presence for teens—even classwork is done online now—makes it near impossible to simply “log off.”

Today, on the Lock and Code podcast with host David Ruiz, we speak with Tall Poppy CEO and co-founder Leigh Honeywell, about the evolution of online hate, personal defense strategies that mirror many of the best practices in cybersecurity, and the modern risks of accidentally becoming viral in a world with little privacy.

“It’s not just that your content can go viral, it’s that when your content goes viral, five people might be motivated enough to call in a fake bomb threat at your house.”

Leigh Honeywell, CEO and co-founder of Tall Poppy

Tune in today to listen to the full conversation.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


Listen up—Malwarebytes doesn’t just talk cybersecurity, we provide it.

Protect yourself from online attacks that threaten your identity, your files, your system, and your financial well-being with our exclusive offer for Malwarebytes Premium for Lock and Code listeners.

[ad_2]

Source link