OnePlus Open is finally getting Android 14 in the US

0

[ad_1]

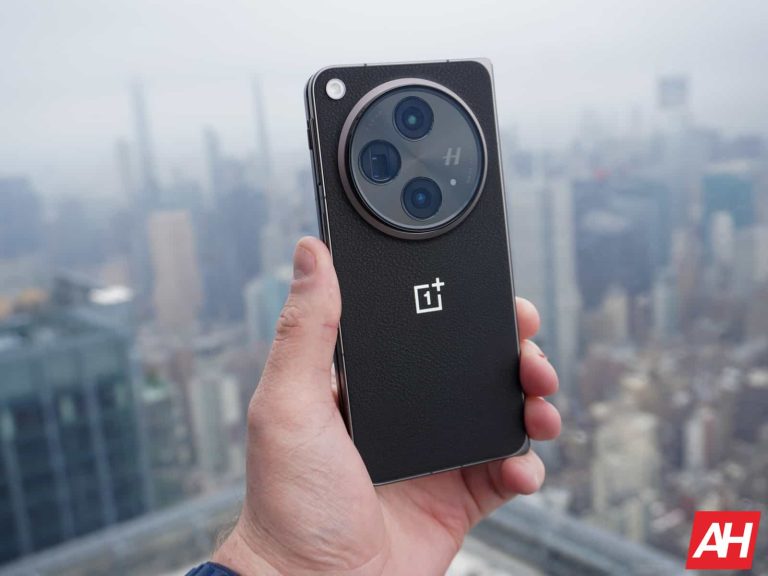
Android 14 has finally started rolling out to the OnePlus Open in the US. Why do I say ‘finally’? Well, the update started rolling out at the beginning of February, not in the US, though. It started arriving to users who were Closed Beta and Open Beta testers first, and only those in India.

Android 14 is finally coming to the OnePlus Open in the US

We hoped that the update would spread to other markets quicker than this, but there you have it. We had to wait for about a month and a half at this point. The update is finally rolling out in the US, though.

The update is marked as CPH2551_14.0.0.501(EX01). This update does bring OxygenOS 14 to the table, along with Android 14. The update itself weighs 2.54GB, so chances are you’ll want to be connected to Wi-Fi before you download it.

All the base Android 14 changes are included, but this changelog is focused on OxygenOS, of course. This update is bringing Aqua Dynamics to the table. It’s a new way of interacting with morphing forms. It allows you to view up-to-date information at a glance.

OnePlus added several new, interesting features

‘File Dock’ has been added, so you can now use drag and drop action to transfer files between apps and devices. The ‘Content Extraction’ feature is also included here. It can recognize and extract text and images from the screen with a single tap.

Cutting out objects/subjects from a photo also becomes a lot easier now, thanks to the ‘Smart Cutout’ feature. It allows you to cut out several subjects from a photo thanks to some help from AI.

The ‘Shelf’ has been improved too, as more widget recommendations have been added. The security has been improved, and so has Aquamorphic Design. Color styles have been changed, while new Aquamorphic-themes ringtones have been included too. OnePlus also tweaked the animations and the always-on display (AOD) OnePlus Open feature here.

This OnePlus Open update is rolling out in stages, as per usual. Some of you probably already got it, while it’s on the way to the rest, you may have to wait a bit, though.

[ad_2]

Source link
Qualcomm will launch new SoCs soon, maybe even a flagship chip

0

[ad_1]

Qualcomm is prepping to host an event as early as March 18 at 2:30 PM local time in China where it could introduce the latest flagship Snapdragon chip. Notably, the conference’s slogan is “Intelligence is in the core, and there is a dragon in it.” Per reports, the chip maker could announce the Snapdragon 8s Gen 3 and the Snapdragon 7+ Gen 3 chips. But take note that Qualcomm hasn’t announced anything about these developments yet. Both the chipsets are said to be built on the same architecture as the Snapdragon 8 Gen 3, which has been receiving praises since its launch.

Qualcomm may launch a flagship chip on March 18th

The news about the event comes from a post on Weibo, where the chip maker could announce at least two chips, including a flagship one. The Snapdragon 8s Gen 3 will steal the limelight of the event, while we anticipate the other chip, 7+ Gen 3, to power up budget smartphones releasing ahead.

Delving into the technicals of the upcoming chips, the Snapdragon 8s Gen 3 could boast one 3.01GHz Cortex-X4 core, four 2.61GHz Cortex-A720 cores, and three 1.84GHz Cortex-A520 cores, alongside an Adreno 735 GPU. Conversely, the Snapdragon 7+ Gen 3 could exhibit a similar architecture but with different clock speeds, including a 2.9GHz Cortex-X4 core, four 2.61GHz Cortex-A720 cores, and three 1.9GHz Cortex-A520 cores, completed by an Adreno 732 GPU.

Which phones will feature the upcoming Qualcomm Snapdragon chips?

The rumored candidates, according to folks at Gizmochina, include the Realme GT Neo6 series, Redmi Note 13 Turbo, Xiaomi Civi 4, OnePlus Ace 3V, Vivo Pad 3, and new devices in the iQOO Neo 9 series. These devices might feature either of the upcoming chips. Notably, the publication adds that we might’ve to wait until March 18 when Qualcomm will confirm the releases during its event. So, until then, you may have to take this information with a grain of salt. But regardless of that, we could say that new Qualcomm processors are on their way.

[ad_2]

Source link

PoC Exploit Released for OpenEdge and AdminServer.

0

[ad_1]

A Proof of Concept (PoC) exploit has been released for a vulnerability in the OpenEdge Authentication Gateway and AdminServer.

This vulnerability, CVE-2024-1403, affects multiple versions of the OpenEdge platform and could potentially allow unauthorized access to sensitive systems.

Understanding the Vulnerability(CVE-2024-1403)

The vulnerability arises when the OpenEdge Authentication Gateway (OEAG) or the AdminServer is configured with an OpenEdge Domain that utilizes the OS local authentication provider.

Document

Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox:

This configuration can lead to unauthorized access during login attempts due to a flaw in the authentication routines.

Specifically, the vulnerability allows authentication success to be incorrectly returned from an OE local domain under certain conditions, such as when unexpected content is present in the credentials passed during the login process.

Affected versions include OpenEdge Release 11.7.18 and earlier, OpenEdge 12.2.13 and earlier, and OpenEdge 12.8.0.

The vulnerability has been addressed in the latest updates: OpenEdge LTS Update 11.7.19, 12.2.14, and 12.8.1.

 Community Progress has addressed the issue and has Updates in OpenEdge LTS Update 11.7.19, 12.2.14, and 12.8.1. 

Impact and Affected Components

The vulnerability has a broad impact, potentially affecting various components of the OpenEdge platform, including:

  • OpenEdge Database access through OEAG
  • AdminServer logins via OpenEdge Explorer (OEE) and OpenEdge Management (OEM)
  • Database Servers accepting OEAG-generated tokens
  • Secure Token Service Utilities
  • Pro2 web application utility for Pro2 management

Ptrace SecurityGmbH recently tweeted about a security vulnerability, CVE-2024-1403, that affects Progress OpenEdge software.

The vulnerability allows for authentication bypass, potentially putting sensitive information at risk.

Mitigation and Upgrade Instructions

A Proof of Concept (PoC) exploit has been made available for a significant vulnerability identified in the OpenEdge Authentication Gateway and AdminServer.

This flaw can potentially be exploited by attackers to gain unauthorized

For users running vulnerable versions of OpenEdge, upgrading to the fixed versions is crucial.

The fixed versions are:

  • Vulnerable Version: OpenEdge Release 11.7.18 and earlier

Fixed Version: OpenEdge LTS Update 11.7.19

  • Vulnerable Version: OpenEdge Release 12.2.13 and earlier

Fixed Version: OpenEdge LTS Update 12.2.14

  • Vulnerable Version: OpenEdge Release 12.8.0

Fixed Version: OpenEdge LTS Update 12.8.1

For those unable to upgrade immediately, temporary mitigation steps include library replacement and domain replacement mitigation for OEAG and AdminServer mitigation strategies, such as using AdminServer Group controls and disabling the AdminService.

The release of the PoC exploit for CVE-2024-1403 underscores the importance of maintaining up-to-date security measures in software systems.

OpenEdge users are urged to review their systems, apply the necessary updates or mitigations, and remain vigilant against potential unauthorized access attempts.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

HONOR Magic6 Ultimate Edition design officially revealed

0

[ad_1]

Both the HONOR Magic6 Ultimate Edition and Porsche Design HONOR Magic6 RSR are coming on the same day, March 18. That being said, the design of the HONOR Magic6 Ultimate Edition has just been revealed.

HONOR just revealed the design of the HONOR Magic6 Ultimate Edition handset

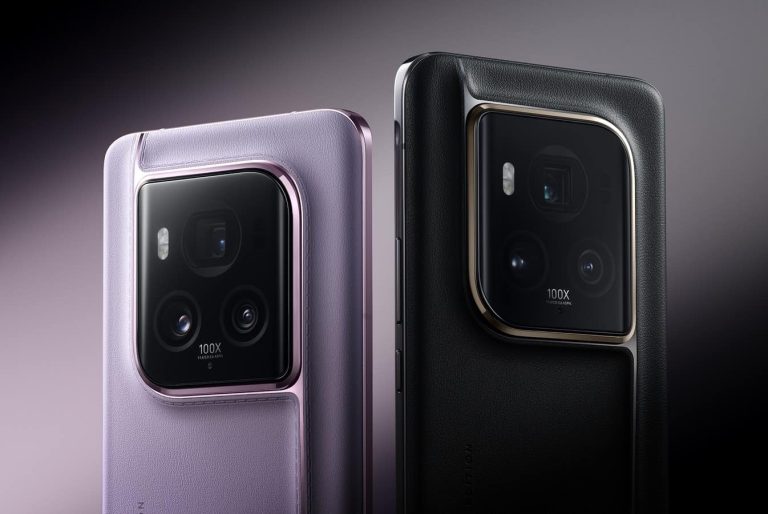
HONOR itself revealed its design. We got to take a look at its camera shape recently, and now we get to see the vast majority of its backplate. If you check out the three images below, you’ll get to see the phone.

As you can see, black and purple color variants are teased here. Those are likely the only color options that we’ll be able to get. You can clearly see that the back side of the phone is vastly different than what the Magic6 Pro delivers.

The camera island has a different shape, and curved glass on top

The camera island on the back has a completely different shape, though the camera layout is still the same. The top-right and bottom-left corners of the camera island are more rounded than the other two corners.

The glass on top of the cameras is also curved towards the sides. HONOR will seemingly use vegan leather on the back of the HONOR Magic6 Ultimate Edition. That goes for both color variants of the phone.

HONOR will add plenty of character to the backplate

You will also notice that HONOR is also using vertical protrusions on the back. A small one above the camera island, and a larger one below it. That will likely be useful for grip purposes, at least based on where it’s located. This phone should be quite grippy in general, though, due to the use of vegan leather.

The phone will be fueled by the Snapdragon 8 Gen 3 SoC. A 6.8-inch 2800 x 1280 LTPO AMOLED display will be used, with up to 120Hz refresh rate. The phone will likely offer up to 16GB of RAM, perhaps even up to 24GB.

A 5,600mAh battery will be used, while 80W wired and 66W wireless charging will be supported. The camera setup will be the same as on the HONOR Magic6 Pro, most likely. You can read our Magic6 Pro review if you’d like to know more about it.


[ad_2]

Source link

X plans to remove likes & reposts from your feed

0

[ad_1]

Twitter, now X, has undergone several changes since its acquisition by business leader Elon Musk. One of the most controversial changes remains its rebranding to X.com, offering verification badges for a price. But if that’s not enough, Musk might’ve other plans. In a series of posts shared by Elon Musk, he may have announced the future overhaul of X. This time, it’s not a minor but a substantial overhaul.

Elon Musk now wants to remove likes and reposts from X’s feed in favor of total views

As indigestible as it may seem, never doubt Elon, especially when he wants something specific. He wants to remove the likes and reposts from the X’s feed in favor of the total “view count” because according to him, that’s “very clean”. Of course, he adds that he’s “been dying to do this for a year”.

This first came to light after DogeDesigner posted that X may be considering removing the likes and reposts from the feed. However, the catch of the account pinned is you can see them once you tap on the post. Musk replied to the post, confirming “That is definitely happening.”

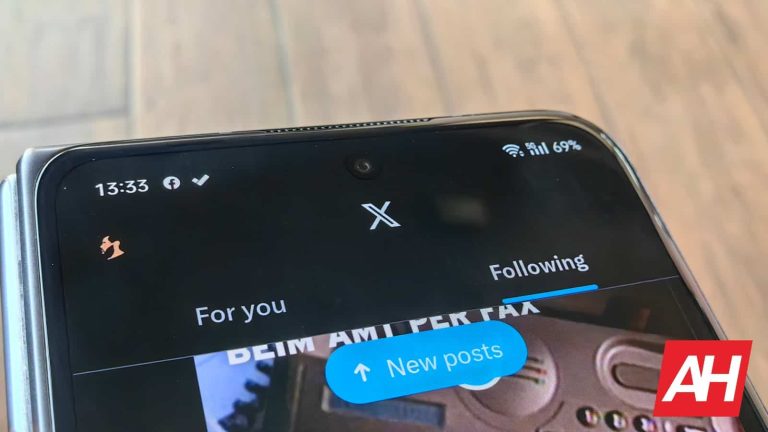
In the tipped layout, the count of views on posts, which tells you how many people are interested, will be shifted to the top right near the posting time. To engage with the post in this updated format, you’ll swipe right to reply and swipe left to favorite it. Musk mentioned that once you tap on the post, you’ll see the number of likes, reposts, and favorites it has, but it’s still being determined if their display will change.

This is how the UI will look like

Another reliable tipster Abhishek Yadav has shared a screenshot of how the platform would look, once this feature comes to life.

If you know Elon Musk, you’d know he has a thing for aesthetics. Notably, he put his platform through some changes earlier, including the removal of URL cards. But he brought it back after a short hiatus.


[ad_2]

Source link

Elon Musk: “OpenAI is a lie”, xAI will open-source Grok. Carl Pei: “Based”

0

[ad_1]

Elon Musk announced that his AI company – xAI, will open-source the Grok chatbot, OpenAI’s ChatGPT rival (via Reuters).

To “open-source” means to share a program’s code with everyone for free, so anyone can use, change, and share it again. It’s like sharing a recipe publicly, so people can tweak it, improve it, or make something new with it. This helps make the program better and more secure because lots of eyes are looking at it and helping fix any problems.

Carl Pei is impressed, and comments:Here’s the original Elon Musk tweet itself:Then, another X user says that “OpenAI should do the same. If they are “open” that is”, to which Elon Musk has this to say: “OpenAI is a lie”. Here’s that post:Earlier this month, Elon Musk filed a lawsuit against OpenAI, the company behind ChatGPT, and its CEO Sam Altman. Musk accused them of straying from the company’s founding goal of developing artificial intelligence to benefit humanity, rather than for profit.This is quite the twist, given that the day after OpenAI’s launch in December 2015, when co-founder Sam Altman emphasized his trust in co-chair Elon Musk and their shared vision for safely distributing AI.

Nearly ten years later, Musk and Altman are disputing the future of AI, as Musk has sued OpenAI in California, accusing Altman and others of deviating from the company’s original altruistic mission by seeking commercial gain.

During a podcast with computer scientist Lex Fridman in November, Musk expressed his appreciation for the idea of AI that is open-source. That same month, his startup released its AI model to a select group of users.

Following this, in December, Musk’s company introduced Grok, a rival to ChatGPT, exclusively for Premium+ subscribers of the social media platform X. Musk’s vision for Grok is to create an AI that is devoted to seeking the truth to the utmost degree.

[ad_2]

Source link

WordPress Sites Exploited To Brute-Force Passwords Via Browsers

0

[ad_1]

According to a recent post from Sucuri, their website scanner detected an active distributed brute-force attack exploiting WordPress sites to steal other sites’ passwords. The attackers inject malicious scripts into the target websites, which execute whenever a visitor reaches those sites. Then, the scripts lure users into performing the action as directed, convincing them to hand over their data.

As explained, the researchers found this tactic in use for some time, attracting Sucuri’s attention for injecting crypto wallet drainers. The researcher followed the initial malware campaigns, observing two iterations. Even since February 2024, they found over 1200 websites infected with malware injected via cachingjs/turboturbo.js script.

Following this campaign, the researchers observed a shift in the attackers’ target, switching from injecting crypto drainers to brute-force scripts. So, when a visitor reaches the compromised website, the script hijacks the visitor’s browser and brute force passwords for other websites.

For this, the scripts are loaded to the browsers via https://dynamic-linx[.]com/chx.js. Once the victim browser connects to the attacker’s server, it receives brute-force tasks from the server https://dynamic-linx[.]com/getTask.php. This task arrives as a JSON file that includes all bruteforce parameters, such as the target site’s URL and a list of passwords to try. Upon successful brute-force of credentials, the browser sends the task completion intimation to the attackers’ server, asking for the next task.

The researchers have shared a detailed technical analysis of this campaign in their post. Since the attack happens sneakily, it gets difficult for the victim users to protect their passwords. Nonetheless, as the researchers suggested, users can still prevent the threat by setting up strong passwords for their accounts. Likewise, WordPress admins may restrict their sites’ login interface to trusted IPs only.

Let us know your thoughts in the comments.

[ad_2]

Source link

Porsche Design HONOR Magic6 RSR will launch on March 18

0

[ad_1]

Last month, HONOR confirmed that the Porsche Design HONOR Magic6 RSR is coming. In a separate announcement, the company also said it’s coming in March. Well, now we know its launch date. The Porsche Design HONOR Magic6 RSR will launch on March 18.

The Porsche Design HONOR Magic6 RSR launch date has been revealed

This confirmation comes from HONOR China, via Weibo (China’s social media network). So, it’s safe to say that the launch will occur in China. That phone is expected to become available globally too, however.

Porsche Design HONOR Magic6 RSR launch date

This device will become the second Porsche Design device that was announced this year. It’s also the second device that Porsche Design and HONOR delivered in general. The Porsche Design HONOR Magic V2 RSR arrived not long ago.

The device will have a different back side than the HONOR Magic6 Pro

The Porsche Design HONOR Magic6 RSR is expected to have a different backplate than the HONOR Magic6 Pro (including the camera island design). Other than that, the two phones will probably be the same.

We are expecting the same specifications under the hood. Well, the Porsche Design model could end up offering more RAM, or something of the sort, but all the rest of its specs are expected to remain the same.

The ‘Ultimate’ version could have the same design

We are expecting the design to be the same or at least similar to what the HONOR Magic6 Ultimate will deliver. That phone is coming on the same date, by the way, March 18. It will also launch during the same event, so… there you go. You can check out the expected camera design and backplate finish below.

HONOR Magic6 Ultimate Edition teaser featured

The Porsche Design HONOR Magic6 RSR will be fueled by the Snapdragon 8 Gen 3 processor. A 6.8-inch 2800 x 1280 LTPO OLED display will be in use, and that will be a 120Hz panel. Android 14 will come pre-installed along with MagicOS 8.0. Advanced facial scanning will also be a part of the package, along with 80W wired, and 66W wireless charging. You can read our HONOR Magic6 Pro review for more information.

[ad_2]

Source link

Russian hackers stole Microsoft’s source code repositories

0

[ad_1]

Microsoft is grappling with the aftermath of a nation-state attack, revealed earlier this year, perpetrated by the group known as Midnight Blizzard or Nobelium. Initially targeting the company’s corporate email systems, the attack has now extended to compromising source code repositories and internal systems, Microsoft disclosed in a recent blog post. This breach poses significant concerns as hackers exploit exfiltrated data from Microsoft’s corporate email systems to gain or attempt to gain unauthorized access. Reportedly, this includes access to some of the company’s source code repositories and internal systems.

Midnight Blizzard attempted to leverage shared secrets between Microsoft and its customers

The attack, attributed to Midnight Blizzard, has evidence that suggests attempts to leverage stolen information. It includes shared secrets between Microsoft and its customers. Microsoft emphasizes that while there is no evidence of compromise to customer-facing systems, the breach underscores the importance of proactive security measures from the company.

Password spray attacks have seen a 10-fold increase in volume since the attack in January. As HYPR notes, this is a type of brute force attack. Threat actors utilize a large dictionary of potential passwords for this purpose. They attempt a single password on many accounts. Then they move on to the next one and repeat the process.  In the context of the Windows maker, it indicates a sustained and coordinated effort to infiltrate the company’s infrastructure.

Despite ongoing investigations into Midnight Blizzard’s activities, the threat landscape remains challenging. Microsoft acknowledges the unprecedented scale of the global threat landscape. The company notes, “It [Midnight Blizzard] may be using the information it has obtained to accumulate a picture of areas to attack and enhance its ability to do so.”

Microsoft says they are taking measures to improve their security infrastructure

Microsoft’s response to the ongoing attack includes bolstering security controls, detection mechanisms, and monitoring capabilities across its infrastructure. “Across Microsoft, we have increased our security investments, cross-enterprise coordination, and mobilization, and have enhanced our ability to defend ourselves and secure and harden our environment against this advanced persistent threat,” notes Microsoft in a recent blog post. “We have and will continue to put in place additional enhanced security controls, detections, and monitoring.”

The company also remains committed to sharing insights from its investigations to enhance industry-wide resilience against cyber threats.

While details of the compromised source code and internal systems remain undisclosed, the breach highlights the need for organizations to prioritize cybersecurity readiness. Microsoft’s experience serves as a stark reminder of the ever-present threat posed by determined adversaries. It necessitates a proactive approach to safeguarding sensitive data and critical infrastructure.

[ad_2]

Source link

Is your WhatsApp chat secure? New feature will tell you

0

[ad_1]

WhatsApp, as one of the world’s most popular messaging apps, is constantly striving to enhance user experience with regular updates and new features. Now, a modest yet handy feature is in the pipeline.

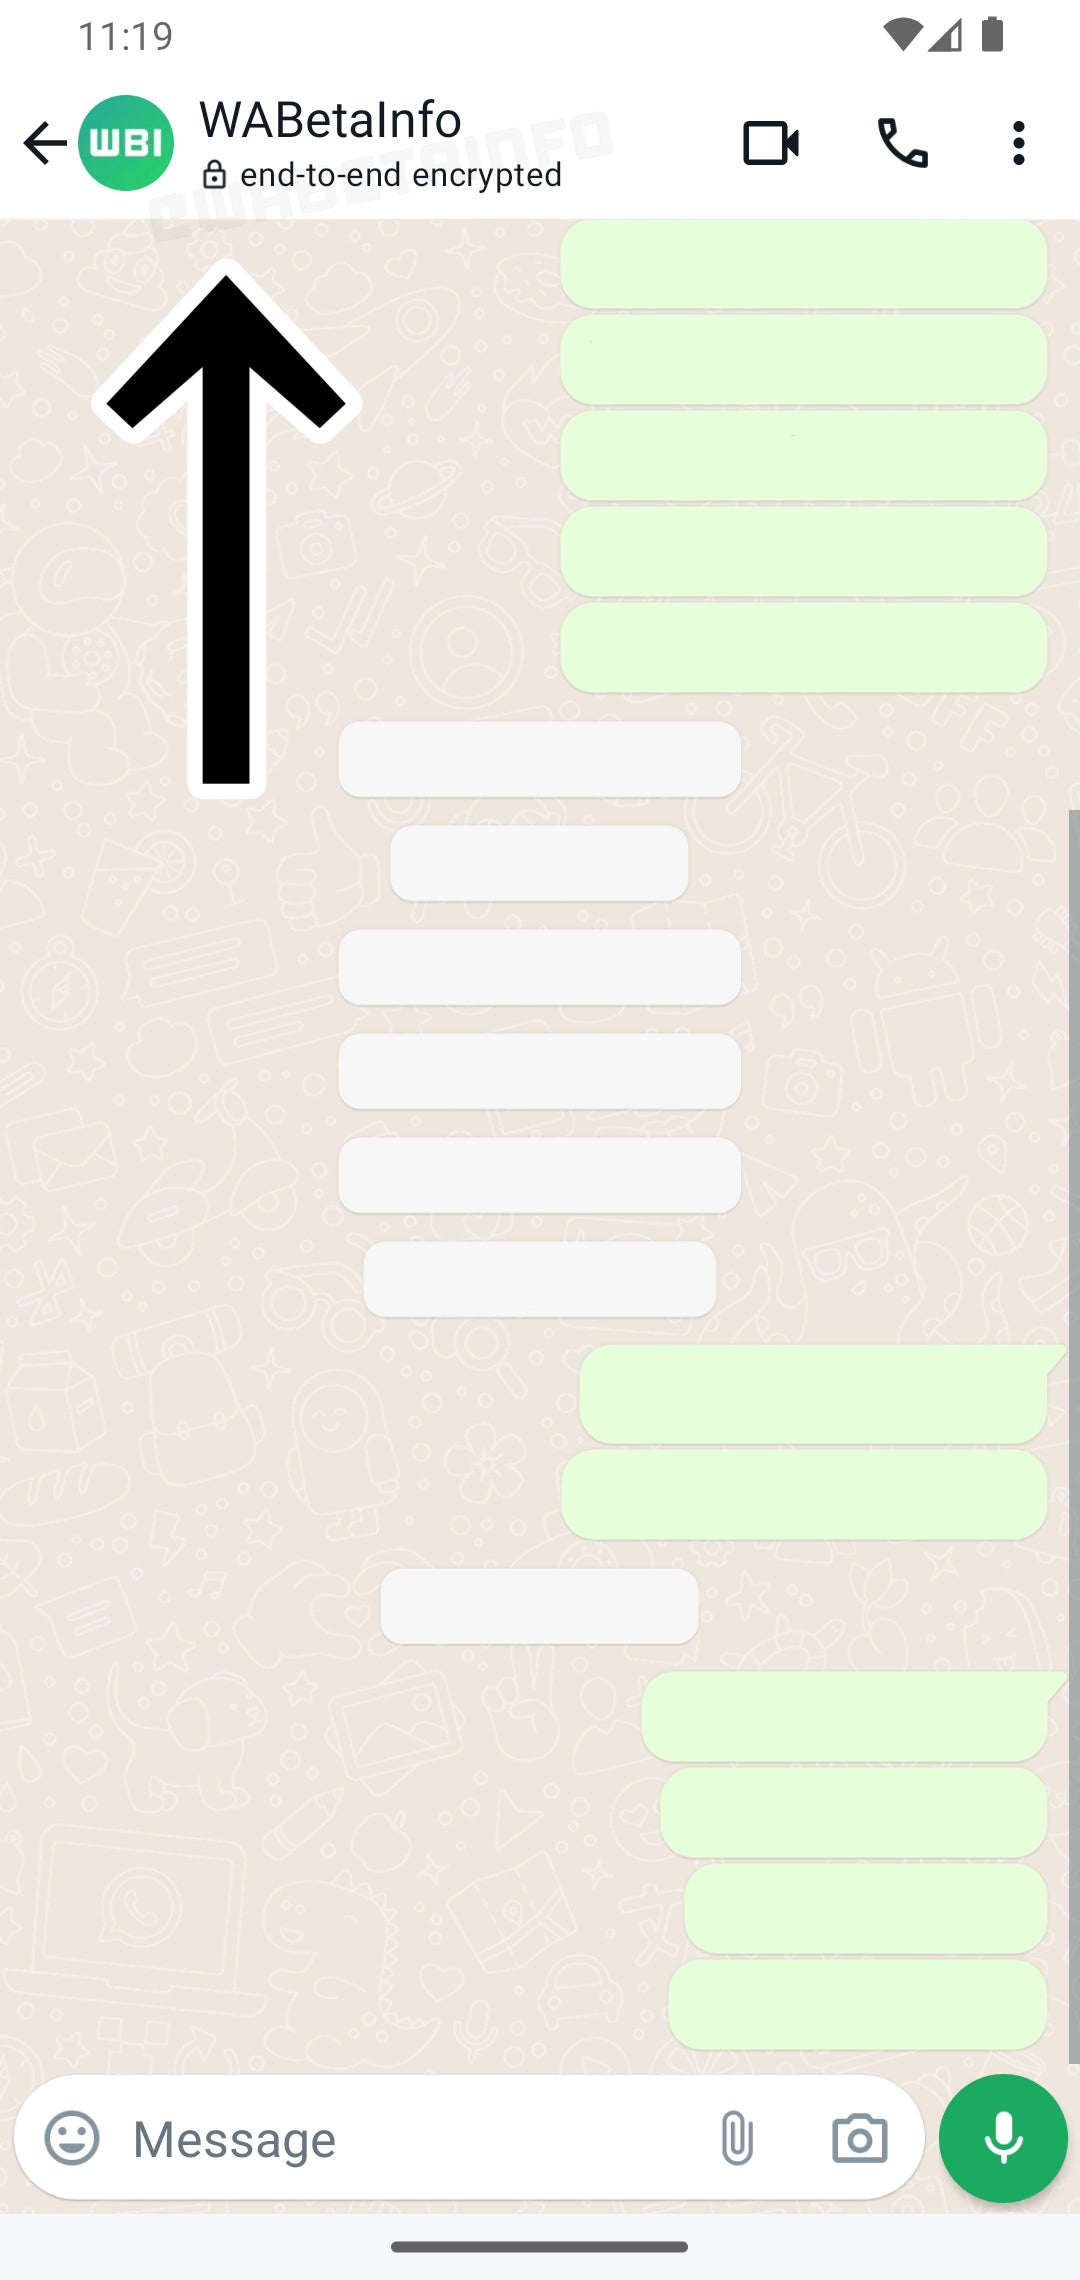
As per WABetaInfo, the reliable source for WhatsApp updates, the Meta-owned app is introducing a feature to indicate end-to-end encrypted conversations. This new feature was discovered in the latest WhatsApp beta for Android 2.24.6.11 update, currently accessible on the Google Play Store.

The purpose of this feature is to make it simple for you to identify which chats are end-to-end encrypted, assuring you that your conversations are secure.

In the screenshot, you can notice a new label under the contact or group name in chats, highlighting the end-to-end encryption status. This feature ensures you always know when your chats are securely encrypted using the Signal protocol. It’s a visual cue that your messages and calls are safe from prying eyes and ears.

Keep in mind that this caption is temporary. According to WABetaInfo, it will only be visible for a short time before being replaced by the last-seen indicator.

This feature, signaling end-to-end encryption in chats, is currently available to beta testers who install the latest updates of WhatsApp beta for Android from the Google Play Store. The rollout is expected to extend to more users over the next few weeks.

Encryption plays a crucial role in modern messaging apps, ensuring that conversations remain protected and secure. End-to-end encryption (E2EE) is a security method that scrambles data between two communicating devices, such as smartphones. The data is only unreadable gibberish (ciphertext) to anyone who doesn’t have the special key to unscramble it (decrypt) into its original form (plaintext).

[ad_2]

Source link