Tecno will take its phones to the next level with powerful AI

0
[ad_1]

Tecno is a brand that’s been making some massive waves in the tech community lately. It was a showstopper at MWC this year with its impressive Dynamic 1 Robodog and the unveiling of the Pova 6 Pro 5G.  However, Tecno just unveiled its future plans for AI, and they are ambitious.

This news should come as no surprise after the recent announcement made by MediaTek. Mediatek and Google partnered to implement the Dimensity 9300 and Dimensity 8300 chips with Google’s Gemini Nano AI model. This means that phones running these chips will have access to powerful generative AI capabilities. This is relevant because Tecno’s phones use MediaTek’s SoCs.

Tecno announced that it had collaborated with MediaTek and Google to help optimize this AI technology for HiOS, Tecno’s Android skin. So, we are certain that some of Tecno’s future phones will use either the Dimensity 9300 or the Dimensity 8300.

Tecno outlines its future AI plans

Starting off the list, Tecno’s phones will be integrated with certain Google AI tools such as Google’s Duet AI, Gemini, and Gmail AI features. So, you’ll be able to easily access these tools on your Tecno phone.

Tecno mentioned Ella. Ella is Tecno’s proprietary AI assistant. It’s an alternative to Google Assistant on Tecno’s phones. Well, Ella will be getting a big generative AI upgrade. You’ll be able to summon Ella to perform certain tasks on your phone just like any voice assistant. Ella will most likely be powered by Gemini Nano, which will increase its capabilities immensely.

When it comes to Photography, Tecno will introduce some new and innovative AI as well. It will use powerful AI for image processing and photo editing. Tecno’s AI will accommodate a broad range of skin tones when optimizing photos to look their best. Also, it’s going to introduce certain tools like AI eraser and AI cutouts. These are tools that utilize generative AI.

Lastly, Tecno AI will help make communication better with certain communication tools like real-time translation, your phone calls, automatic subtitle generation for videos, generating pictures from scratch, wallpaper generation, and searching for photos with simple descriptions.

These AI tools show that Tecno is positioned to be a major force in the tech world. It’s exciting to see what else the company will do to enhance the Tecno phone experience.


[ad_2]
Source link
20 Million+ Cutout.Pro User Records Leaked On Hacking Forums

0
[ad_1]

CutOut.Pro, an AI-powered photo and video editing platform, has reportedly suffered a data breach, exposing personal information belonging to over 20 million users.

The breach was first brought to light by an individual using the alias ‘KryptonZambie’ on the BreachForums hacking forum, where they shared a link to CSV files containing 5.93 GB of data purportedly stolen from CutOut.Pro.

The leaked data encompasses a wide array of personal information, including user IDs, profile pictures, API access keys, account creation dates, email addresses, user IP addresses, mobile phone numbers, hashed and salted passwords, user types, and account statuses.

This breach has been confirmed by the data breach monitoring and alerting service Have I Been Pwned (HIBP), which added the incident to its catalog, verifying that the dataset includes information for 19,972,829 individuals.

CutOut.Pro is renowned for its AI-driven capabilities in enhancing images, removing backgrounds, colorizing, restoring old photos, and generating content, making it a popular choice among users seeking advanced editing tools.

However, the breach has raised serious concerns about the platform’s security measures and the potential risks to users’ privacy and online safety.

The threat actor behind the leak, ‘KryptonZambie’, claimed to still have access to the breached system at the time of the data’s publication, indicating that CutOut.Pro may not have been aware of the compromise.

This ongoing access raises the possibility of further data exfiltration or malicious activities using the compromised information.

Recommendation for CutOut.Pro users

In response to the breach, cybersecurity experts recommend that CutOut.Pro users immediately reset their passwords on the service and any other platforms where they might have reused the same credentials.

Given that the passwords were hashed using MD5, a relatively weak algorithm by modern standards, there is a realistic possibility that threat actors could brute-force the leaked password hashes.

Moreover, users should remain vigilant for targeted phishing scams that may attempt to exploit the leaked information to gather additional personal data or trick individuals into compromising their online accounts further.

Despite the severity of the breach, CutOut.Pro has not yet issued an official statement verifying the security incident.

This lack of communication from CutOut.Pro adds to the concerns surrounding the breach and the company’s handling of the situation.

This is a developing story; we will add further details once we have an update.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Galaxy Z Fold 6 event location tipped; July launch mentioned again

0
[ad_1]

A report surfaced yesterday, claiming that the second Unpacked event of the year will take place in early July. July 10 was highlighted as the most probable date. Well, a new report just appeared, reconfirming the early July launch for the Galaxy Z Fold 6 and Galaxy Z Flip 6, while it also adds the event location.

The Galaxy Z Fold 6 event location has seemingly been revealed, and the choice is interesting

This information comes from The Bell, a South Korean publication, and it has been relayed by Revegnus, a tipster. It is said that the second Unpacked event will take place in Paris, France.

Now, the Summer Olympics are also taking place in Paris, starting on July 26. That was the date of the Galaxy Z Fold 5 and Galaxy Z Flip 5 launch last year. That is also a Wednesday, by the way, and Samsung tends to host Unpacked events on Wednesdays.

Yesterday’s report did mention that the Summer Olympics are probably the reason why Samsung moved up its event. Now it’s even more clear why, as both events will be taking place in the same city.

The July 10 launch date fits, as that’s most probably the final choice for Samsung

In any case, this report does mention that the event will take place in mid-July, 1-2 weeks earlier than last year. So, the July 10 date does fit, definitely. The report also says that we should not expect new form factors, such as double folding or sliding phones.

It’s mentioned that both the Galaxy Z Fold 6 and Galaxy Z Flip 6 will utilize Qualcomm’s AP. That is what everyone expected. It is also mentioned that TM Roh, the head of Samsung Mobile, is “holding a negative perception of budget foldables”.

The Samsung Galaxy Z Fold 6 and Galaxy Z Flip 6 likely won’t be the only devices to launch at the event. The Galaxy Ring will likely arrive too, the company’s very first smart ring, whose design was revealed at MWC 2024.

We may see some additional products on top of these devices, like some new tablets, for example. More info will surface as we get closer to July.


[ad_2]
Source link

RisePro Stealer Attacks Windows Users Steals Sensitive Data

0
[ad_1]

A new wave of cyber threats has emerged as the RisePro information stealer targets Windows users, compromising sensitive data and causing significant security concerns.

RisePro, which shares similarities with the Vidar stealer, is a Trojan-type malware that infiltrates systems to exfiltrate sensitive information in the form of logs, which are then sold on shadow markets.

How RisePro Operates

RisePro is distributed via a malware downloader called PrivateLoader, which tricks users into downloading and executing malicious software through deceptive emails, pirated software, and fake updating tools.

Once executed, RisePro can steal a wide array of data from up to 36 web browsers, including IP addresses, browsing history, cryptocurrency wallets, and passwords.

It can also capture screenshots and extract data from applications such as Authy Desktop, battle.net, and Discord.

The malware’s capabilities are extensive, targeting browser extensions like Authenticator and BinanceChainWallet, and it can potentially hijack online accounts, commit identity theft, and conduct fraudulent transactions.

RisePro is written in C++ and is sold via Telegram, where cybercriminals can interact with infected systems.

A recent tweet has been circulating in the cybersecurity community, warning of the distribution of a new malware called RisePro Stealer.

This malware is coded in C++ and is designed to collect sensitive information from the infected systems.

Once the information is collected, RisePro Stealer attempts to transfer it as logs to an external server.

This type of malware can pose a severe threat to the security of affected systems, as it can be used to steal sensitive data such as login credentials, financial information, and other confidential data.

Security Responses and Recommendations

To combat this threat, it is unnecessary to format the storage device; instead, RisePro can be removed with antivirus software or manually following the provided instructions.

Users are advised to be vigilant about the sources of their downloads and to maintain updated antivirus solutions to prevent such infiltrations.

RisePro is emergence indicates the evolving cybercrime ecosystem, with stealer infections acting as a primary vector for initial attacks.

The malware’s infrastructure includes an administration panel hosted at a domain that allows access to stolen data logs only after signing into an account with valid credentials.

The RisePro stealer represents a significant threat to Windows users, capable of stealing a vast range of sensitive data and causing severe security issues.

Users must exercise caution and employ robust security measures to protect against sophisticated cyber threats.

Cybersecurity communities continue to monitor and analyze these threats to provide users with the necessary tools and knowledge to defend against them.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]
Source link

Google Pixel 8 series wins ‘Best Smartphone’ award at MWC 2024

0
[ad_1]

The Google Pixel 8 series has won the category of “Best Smartphone” of the Global Mobile Awards (GLOMO) at MWC 2024, after winning our AH Award for Best Smartphone of 2023. Hosted by the GSMA, the Global Mobile Awards recognize excellence and innovation in the mobile industry, with the ‘Best Smartphone’ category being one of four in the Device section. The others are ‘Breakthrough Device Innovation’, ‘Best Connected Consumer Device’, and ‘Best in Show’. Notably, judges considered the Samsung Galaxy Tab S9 the ‘Best Connected Consumer Device’ while the HONOR Magic V2 RSR Porsche Design has clinched the honor of ‘Best in Show’.

The GSMA’s criteria for the Best Smartphone award emphasize outstanding performance, innovation, and leadership demonstrated by devices on the market throughout the year. Competing against industry giants such as Apple’s iPhone 15 Pro series and Samsung’s Galaxy S23 series, the Google Pixel 8 series emerged victorious, highlighting its exceptional capabilities and impact on the market.

Google Pixel 8 series marks Google’s first time securing the “Best Smartphone” title at MWC

GLOMO Best Smartphone 2024

Rick Osterloh, Google’s Senior Vice President of Devices & Services, celebrated the win, underscoring the Pixel community’s role in achieving this milestone. This triumph marks Google’s first time getting the Best Smartphone title, reflecting the company’s dedication to pushing boundaries and delivering cutting-edge technology to users worldwide.

The Pixel 8 series’ success builds upon Google’s previous achievements in the mobile space, with the Pixel lineup consistently pushing the envelope in terms of innovation and user experience. Notably, the Pixel 6 Pro was shortlisted in 2021, while the Pixel 3’s Night Sight feature earned a GSMA award for Disruptive Device Innovation in 2019.

Furthermore, reports indicate that Google’s Pixel 8 series achieved significant sales milestones in 2023. With 10 million devices shipped that year, the Google Pixel 8 series has not only garnered critical acclaim but also resonated strongly with consumers, solidifying its position as a frontrunner in the competitive smartphone market.

Google Pixel 8 series comes with some noteworthy features exclusive to Pixel devices

The Google Pixel 8 series runs on the Google Tensor G3 platform and enables a number of exclusive features to the Google Pixel 8 and Google Pixel 8 Pro. These include features like Zoom Enhance, Best Take, and Magic Editor to name a few. ‘Zoom Enhance’ uses generative AI to intelligently fill in the gaps between pixels in the frame. As Google’s SVP Rick Osterloh said during the Made By Google event last year, this feature of the Pixel 8 Pro enables you to take photos without thinking much about the framing, as you can crop in and adjust the framing later without losing image quality.


[ad_2]
Source link

Golden Corral restaurant chain Hacked: 180K+ Users’ Data Stolen

0
[ad_1]

The Golden Corral Corporation, a popular American restaurant chain, has suffered a significant data breach, compromising the personal information of over 180,000 past and present employees, dependents, and beneficiaries.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

On August 15, 2023, Golden Corral experienced a data security incident that led to a temporary disruption in corporate operations.

The company promptly initiated an investigation to determine the nature and extent of the breach and to restore the affected computer systems.

It was discovered that an unauthorized actor had accessed the company’s systems between August 11 and August 15, 2023, and acquired sensitive data.

Golden Corral has since worked closely with federal law enforcement to address the incident and has been taking steps to implement additional safeguards to prevent future breaches.

Golden Corral Corporation has reported a data security breach which has resulted in a temporary interruption to their corporate operations.

The exact nature and scope of the incident have not yet been disclosed, but it is believed that the breach may have compromised sensitive information.

The company is currently investigating the matter and taking appropriate measures to ensure the safety and security of their data systems.

Compromised Information

The unauthorized access resulted in the potential exposure of sensitive information, including names, Social Security numbers, financial account details, driver’s license numbers, medical information, usernames and passwords, and health insurance information.

Golden Corral completed a thorough review of the potentially impacted data on January 26, 2024, and began the process of notifying affected individuals on February 16, 2024.

Golden Corral has offered two years of free credit data monitoring through Experian to the employees affected by the breach.

The company has also guided how to protect against identity theft and fraud, including instructions on placing a fraud alert and security freeze on credit files.

Despite the breach, there is no evidence to suggest that customer data was compromised, as the affected information pertained solely to employees and their dependents.

Several law firms are investigating claims on behalf of the affected employees and are encouraging them to join class action efforts against Golden Corral. 

The company urges all potentially impacted individuals to remain vigilant by monitoring their account statements and credit reports for any unusual activity.

For additional information or assistance, individuals can contact Golden Corral’s dedicated assistance line. Golden Corral Data Breach.

Golden Corral is dealing with the aftermath of a significant data breach affecting a large number of its workforce.

The company has taken steps to address the breach and is working to support the affected individuals while also enhancing its security measures to prevent future incidents.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]
Source link

Meizu launches new flagship, possibly its very last smartphone

0
[ad_1]

The Meizu 21 Pro is now official, the company’s new flagship device, and possibly the company’s very last smartphone. Well, Meizu announced earlier this month that it’s quitting the smartphone business to focus on AI.

Granted, the company could change its mind down the road and introduce new smartphones, possibly AI-centric ones. As things stand at the moment, however, Meizu has no plans to launch any new smartphones past the Meizu 21 Pro.

The Meizu 21 Pro has been announced, and it could be the company’s very last phone

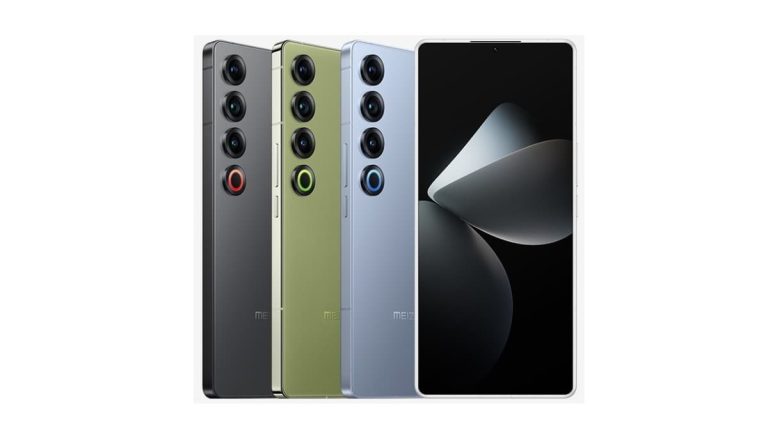
That being said, this phone is quite powerful. Let’s talk about its design first, though. It resembles its predecessor, that’s for sure. The phone has flat sides, and it’s also flat on the front and the back.

There are four small circles on the back, three of which are reserved for the phone’s cameras. They all protrude from the backplate directly, and they’re vertically aligned on the left-hand side of the phone’s backplate.

There is a centered display camera hole at the top of the phone’s display. The bezels around that display are also quite thin. The power/lock button sits on the right-hand side, right below the volume up and down buttons.

The device has a large AMOLED display, while it also includes the Snapdragon 8 Gen 3 SoC

The Meizu 21 Pro features a 6.79-inch QHD+ (3192 x 1368) LTPO AMOLED display. That display has a max refresh rate of 120Hz, and its brightness goes up to 1,250 nits. It also offers a 2,160Hz high-frequency PWM dimming and SGS Low Blue Light Eye Protection.

Qualcomm’s Snapdragon 8 Gen 3 processor fuels this smartphone. The company is offering the phone in 12GB and 16GB RAM variants. The former comes with 256GB of storage, while the latter is available in both 512GB and 1TB flavors. Meizu is using LPDDR5X RAM and UFS 4.0 storage for all models.

A 50-megapixel main camera (f/1.9 aperture, OIS+EIS) is backed by a 13-megapixel ultrawide unit (f/2.4 aperture), and a 10-megapixel telephoto camera (f/2.08 aperture, 3x optical zoom). A single 32-megapixel shooter (f/2.4 aperture) sits on the front.

80W wired charging is supported, in addition to 50W wireless charging

A 5,050mAh battery sits on the inside, while the device supports 80W wired charging. 50W wireless charging is also on offer, as is 10W reverse wireless charging. Quick Charge 4.0/USB PD3.0 PPS protocols are supported.

An in-display fingerprint scanner is also a part of the package, and it’s of the ultrasonic variety. The phone also has two speakers, while the mEngine haptic engine is also on offer. VC liquid cooling is on board too. Android 14 comes pre-installed with Flyme 10.5 on top of it. The phone is also IP68 certified for water and dust resistance.

The device launched in four colors

The Meizu 21 Pro comes in four colors. It comes in Glacier Blue, Laurel Green (vegan leather), Phantom White, and Starry Night Black colors. All models have a glass backplate except the green one.

The device measures 164.98 x 74.42 x 7.98mm, while it weighs 208 grams (vegan leather) / 214 grams (glass). The pricing starts at CNY4,999 ($695), and goes all the way up to CNY5,899 ($820).


[ad_2]
Source link

Spotify gets mystic: Song Psychic answers your questions with music

0
[ad_1]

For those curious about what lies ahead, Spotify is throwing open the doors to the future, not in a literal sense, but with a dash of fun. The music streaming giant is rolling out a fresh feature on its service.

The Swedish company revealed in a blog post (via TechCrunch) that it’s introducing a new Song Psychic feature. This mystical addition promises to blend “cosmic guidance” with a playful musical experience. In a nutshell, you can toss questions at Spotify and receive music-based answers.

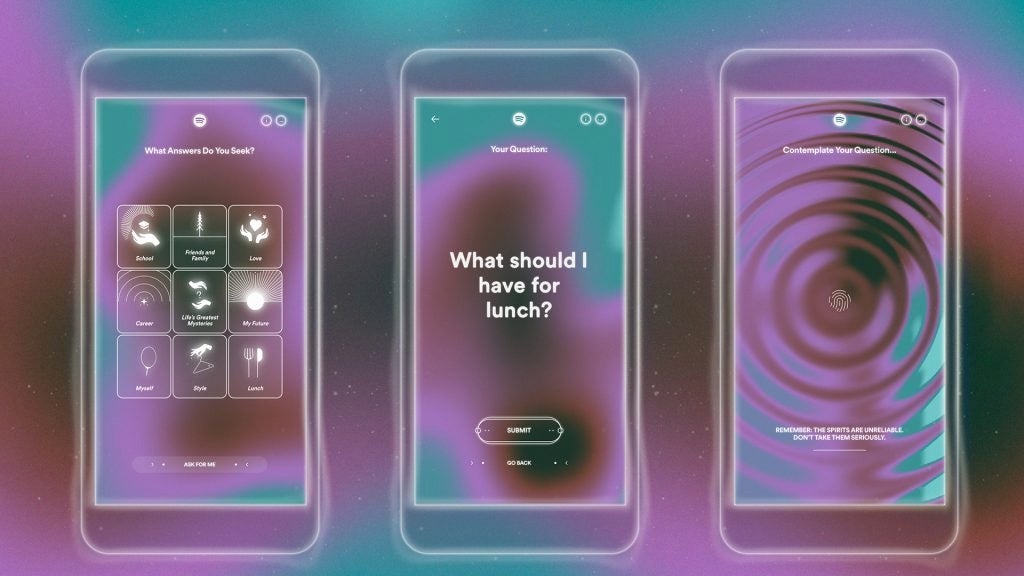
To get your fortune told by the musical psychic, head to spotify.com/songpsychic on your mobile device or scan the QR code on Song Psychic’s website.

Once inside, pick from an array of broader categories such as School, Friends and Family, Love, Career, Life’s Greatest Mysteries, My Future, Myself, Style, and Lunch. While not entirely open-ended, the feature lets you choose from nine different topics and then select from a list of pre-populated questions.

After entering your question, the Song Psychic instructs you to press your finger on the screen. Colors swirl around as mystical music hums in the background, building anticipation before your answer is revealed in the form of a song (check out what answer it gave to my question below).
 

Taking a cue from the success of Spotify’s personalized year-end review, Wrapped, the Song Psychic’s response is shareable. Simply tap on a button below, and a built-in sharing sheet pops up, allowing you to post the answer to WhatsApp, Instagram, Messenger, Facebook, Snapchat, X, Messages, and more.

The Song Psychic isn’t playing favorites. It’s up for grabs by both Spotify’s free and Premium subscribers. Currently, it’s available in 64 markets and in 21 different languages. Apparently, music magic knows no boundaries.

Speaking of the future this whole time, Spotify tests AI-powered playlists, which will be created with the help of short, ChatGPT-like prompts.

[ad_2]
Source link

CISA Warns Of Hackers Exploiting Ivanti VPN Flaw

0
[ad_1]

Threat actors target and abuse VPN flaws because VPNs are often used to secure sensitive data and communications, making them valuable targets for exploitation. 

By exploiting the VPN flaws, threat actors can gain unauthorized access to networks, intercept confidential data, and launch various cyber attacks.

CISA (The Cybersecurity and Infrastructure Security Agency), along with the following partners, recently warned that hackers are actively exploiting multiple vulnerabilities (CVE-2023-46805, CVE-2024-21887, and CVE-2024-21893) in Ivanti VPN:-

  • Federal Bureau of Investigation (FBI)
  • Multi-State Information Sharing & Analysis Center (MS-ISAC)
  • Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC)
  • United Kingdom National Cyber Security Centre (NCSC-UK)
  • Canadian Centre for Cyber Security (Cyber Centre), a part of the Communications Security Establishment
  • New Zealand National Cyber Security Centre (NCSC-NZ)
  • CERT-New Zealand (CERT NZ)

CISA Warns Hackers Exploiting Ivanti VPN

The Ivanti gateways have serious vulnerabilities impacting all supported versions (9.x and 22.x), enabling attackers to bypass authentication, execute commands, and evade detection.

CISA found Ivanti’s ICT systems failed to detect the compromise, due to which they urged network defenders to assume credential compromise and perform the following tasks:-

  • Hunt for malicious activity
  • Run updated ICT
  • Apply patches
Ivanti Domain Join Configuration with ‘Save Credentials’ (Source – CISA)

Organizations should be wary of rootkit-level persistence even after factory resets, as sophisticated threat actors may remain undetected for extended periods. 

Due to significant risks, it’s strongly advised to reconsider using Ivanti Connect Secure and Policy Secure gateways in enterprise environments.

CISA responded to Ivanti vulnerabilities by detecting the threat actors exploiting CVEs to implant web shells and harvest credentials. 

Post-compromise threat actors used Ivanti-native tools like freerdp and SSH for lateral movement, which led to full domain compromises. 

Ivanti’s ICT failed to detect the compromise, while the integrity checker and forensic analysis proved unreliable. Cybercriminals could erase traces by highlighting the unreliability of the ICT scans in indicating compromise. 

Independent research validated Ivanti’s ICT insufficiency that allows cyber threat actors to persist even after factory resets and upgrades.

Mitigations

Here below, we have mentioned all the mitigations provided by the cybersecurity researchers:-

  • Make sure to choose VPNs wisely and avoid proprietary protocols or non-standard features.
  • Secure remote access tools.
  • Restrict outbound connections on SSL VPNs for essential services.
  • Use low-privilege accounts for LDAP bind in SSL VPNs with AD/LDAP authentication.
  • Allow SSL VPN access for unprivileged accounts only to reduce credential exposure.
  • Keep OS, software, and firmware updated.
  • Minimize Remote Desktop Protocols and remote desktop service usage.
  • Configure Windows Registry for UAC approval on PsExec for admin tasks to curb lateral movement.
  • Develop a recovery plan with multiple copies of sensitive data in a secure location.
  • Enforce the NIST password policy for all password-based logins.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Subscribe on LinkedIn

[ad_2]
Source link

Getac ZX80 is a rugged tablet with programmable buttons

0
[ad_1]

Tablets are not nearly as popular as they used to be, mainly due to large smartphones and foldables. They are still very useful, however, especially specialized ones. We’re here to talk about one such tablet, the Getac ZX80.

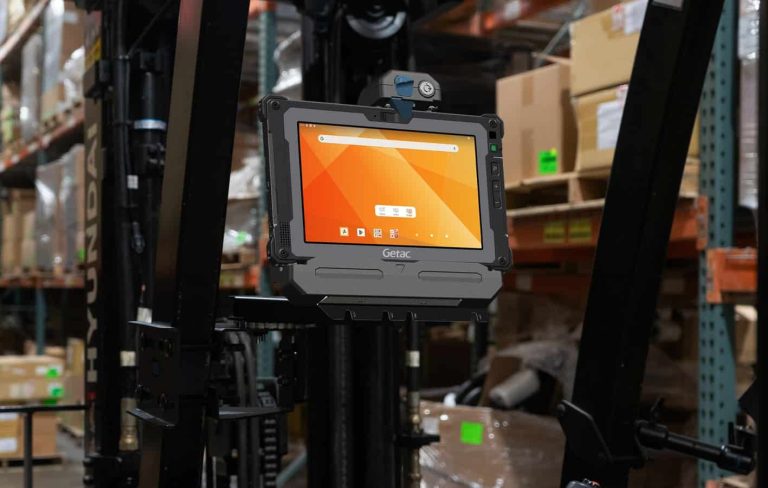
The Getac ZX80 is a brand new rugged tablet with programmable buttons

That brand name may not seem all that familiar to many of you, but if you need a truly rugged tablet, you may be interested. The Getac ZX80 is one such tablet, as you can see in the images provided below the article.

This phone is extremely well-protected, and it even has some physical buttons on the front. Those buttons are programmable. The company says this tablet is “highly customizable”, and that it has been “purpose-built to thrive in challenging work environments”.

It can withstand extreme temperatures

This tablet can withstand temperatures to -29C, and up to 63C. It weighs 590 grams, and it comes with both MIL-STD-810H and IP67 certifications. So not only can it take a hit, but it is also water and dust-resistant.

It has a 16:10 display aspect ratio, and its brightness goes up to 1,000 nits. This is an 8-inch tablet, by the way. Believe it or not, it even includes Getac’s hot-swappable battery technology. That’s not something we usually see in tablets.

65W wired charging is supported here

Speaking of the battery, this tablet supports 65W wired charging, and a charger comes with the device. The company also mentioned a “docking station for efficient use in the office”. We’re not sure if it comes with the tablet, though.

The Qualcomm QCS6490 chip fuels it, while Android 13 comes pre-installed on this device. You’re also getting 12GB of LPDDR5 RAM and 256GB of UFS flash storage.

Various software solutions by Getac come pre-installed

The device is equipped with Bluetooth 5.2, Wi-Fi 6E 802.11ax, and an optional dedicated GPS. Getac’s software solutions come pre-installed too, including the brand-new Log Tool, demployXpress, enrollXpress, GDMS, Driving Safety Utility, and OEMConfig.

The Getac ZX80 is priced at $1,249.99, in case you’re wondering. If you’re interested, you can find more information here.


[ad_2]
Source link