February update rolling out widely to the US Galaxy S22, S23 FE

0
[ad_1]

Samsung‘s most recent Fan Edition (FE) smartphone, the Galaxy S23 FE, is receiving the February 2024 security update in the US. The latest security patch is also rolling out to the factory-unlocked variants of the Galaxy S22 series. These phones have already picked up the new SMR (Security Maintenance Release) in most international markets.

Galaxy S23 FE receives Samsung’s February 2024 security update

Samsung started pushing the February 2024 update to the Galaxy S23 FE around two weeks ago. The company initially released the update for European users before gradually expanding the coverage to other regions. However, users in the US were kept waiting for the new SMR. The wait has finally ended, with Samsung covering both carrier-locked and unlocked units.

The latest update for the Galaxy S24 FE comes with the firmware build number S711USQU2BXBE for locked units and S711U1UES2BXB6 for unlocked ones. For the former group of devices, the rollout seems to be limited to the AT&T network. The remaining carriers should join the party in a few days. Samsung has released the new security patch widely on most carrier networks for the latter group.

Regardless of the build number or carrier variant, the update contains the same changelog. “The security of your device has been improved,” Samsung states in its release notes. This month’s security patch fixes 69 vulnerabilities combined across all Galaxy devices. These include eight vulnerabilities exclusive to Samsung products and three critical Android OS issues.

These security fixes are also rolling out to the unlocked variants of the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra in the US. The update comes with the build number S90*U1UES4DXA1. Their carrier-locked counterparts as well as international versions have already received the update. Once again, the changelog is the same globally. The update is all about the latest security patch with no additional changes.

One UI 6.1 is coming to these Galaxy devices soon

Samsung introduced an upgraded version of its Android-based One UI software with the Galaxy S24 series. Based on Android 14, One UI 6.1 comes with a plethora of on-device and cloud-based AI features. The company plans to push One UI 6.1 and these features to older flagship and mid-range models, starting with the Galaxy S23 series. The rollout is expected to begin soon. Lower-cost models may miss out on some features due to compatibility issues. You can check for new updates on your Samsung phone or tablet from the Settings app.


[ad_2]
Source link

Hackers Abuse Telegram API To Exfiltrate User Information

0
[ad_1]

Attackers have been using keywords like “remittance” and “receipts” to spread phishing scripts using Telegram to steal user data indiscriminately.

In the past, phishing script files were disseminated using various strategies and techniques, like asking users to log in before they can access protected files or pretending to be the Microsoft login page.

Hence, the most recent files are obfuscated to evade detection, in contrast to the phishing script files sent in the early days.

Phishing-Type Malware Using Telegram API

According to the AhnLab Security Intelligence Center (ASEC), the threat actor impersonates the Microsoft login page or requests a login for users to access protected files.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

Additionally, to steal the password in use, the threat actor asks users to input a password that is at least five characters long.

Phishing Page

“After entering a password of at least five characters, the malware sends the stolen information to threat actors via the Telegram API.

The transferred information consists of email addresses, passwords, IPs, and user ASEC researchers shared with Cyber Security News.

Email addresses, passwords, IP addresses, and user agents are among the data transmitted.

The token and Chat ID details are predefined to communicate with the threat actors.

Stealing User information

To hide the malicious activities from the user, the malware then reroutes visitors to the official Microsoft website.

Apart from the malware of the phishing type, researchers mention that the AgentTesla malware also utilized Telegram to obtain user data.

In September 2023, the ASEC researchers reported phishing script files that exploited Telegram to expose user data.

In that case, researchers discovered several phishing script files masquerading as PDF document viewer screens being sent as attachments to emails.

There has been an increase in the theft of user data using Telegram.

Furthermore, the development and dissemination of phishing websites is becoming increasingly sophisticated. 

Hence, users must therefore avoid visiting dubious websites and opening files from suspicious sources.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

How to Avoid Data Leaks

0
[ad_1]

The Internet offers a convenient platform for sharing data, but it also brings the risk of data leaks. A data leak occurs when sensitive information is accidentally exposed, differing from a data breach, which usually stems from a deliberate cyberattack.

To prevent data leaks, companies can implement secure practices to safeguard their information. Explore further to discover effective measures your organization can take to ensure data security.

Why is Data Leak Prevention Important?

Data leaks are a focus for cybercriminals. Many of them monitor accounts, waiting for a leak to occur. Accidental exposure can provide access to financial information, trade secrets, personal identification information, and private records.

When a malicious party accesses sensitive information, there’s no saying what they will do with it. They may visit dark web forums and put the information up for sale or publish it freely. Or they may publish stolen data on dark websites or ransomware blogs to make the information public.

What are Common Data Leak Causes?

Data leaks can happen for various reasons. Understanding common data leak causes can help address the issue. Here are some issues to be aware of:

  • Misconfigured software settings: Security settings that are either not implemented or deployed with errors can cause security gaps that leave data unprotected. 
  • Software vulnerabilities: Unpatched security makes it easy for sensitive data to slip through the cracks. 
  • Weak passwords: Weak passwords make private information vulnerable to cybercrime attacks.  Multi-factor authentication can keep systems protected. 
  • Insider threats: Excessive privileges increase the risk of internal threats. It’s scary to think about, but even a trusted employee can steal data from a company’s system. 
  • Social engineering: Social engineering is the use of deception or manipulation to coerce individuals into divulging confidential information. 
  • Physical theft: An increased focus on cybersecurity makes it difficult to account for devices being lost or stolen. Companies must keep hardware protected. 
  • Spear-phishing: Spear-phishing occurs when a cybercriminal sends out an email requesting financial or sensitive information. These emails often seem legitimate and innocent, but they can have serious implications if sensitive information is transmitted. 
  • Botnets: Botnets are a network of private computers infected with malicious software. They can take over your computer and access important data. 
  • Personal Mobile Devices: Employees’ mobile devices may store sensitive data that can be easily accessed by malicious users. 
  • Remote Work Environments: Remote work environments mean more data is sent over the internet increasing the risk that it will fall into the wrong hands. 

Best Practices for Avoiding Data Leaks

Evaluate Third-Party Risk

Companies risk data leaks when they pass sensitive information on to third-party vendors. Organizations can increase security by ensuring their vendors are compliant with regulatory standards like HIPAA, GDPR, and PCI-DSS. Risk questionnaires can be used to assess potential threats when partnering with new vendors. 

Expanding organizations may find it difficult to maintain risk management regulations for third-party companies that may also experience growth spurts. Scaling vendor risk management as a managed service could streamline the process. Companies can achieve this goal by leveraging automation and protecting their business if a data leak occurs.

Limit Access to Sensitive Data

Organizations must identify sensitive data and classify it with strict security policies. They should restrict privileges to ensure the data is accessed only by those who need it. 

Systems must be implemented to evaluate permissions and ensure access isn’t granted to unauthorized parties. The data should then be categorized into different levels of sensitivity. Only trusted staff members should have access to highly sensitive data. 

The technology may also identify malicious behaviour within the system. 

Enforce Network Access Control

Companies must monitor network access to protect data from unauthorized users. They must review the communication coming into the network to ensure it’s coming from trusted sources. They must integrate data leak prevention solutions to ensure information isn’t compromised when a leak occurs. 

A Network Access Control (NAC) solution may help organizations keep data safe. It denies access to noncompliant devices, places them in a quarantined area, or limits their privileges to prevent infections. 

Data Encryption

Data encryption is a valuable anti-data leak tool. It encrypts data so it can only be read by people with access privileges. Cybercriminals will be unable to decipher sensitive data. 

Portable encryption is recommended because it ensures that data will be automatically encrypted if it leaves the confines of your network. 

However, advanced cybercriminals may be able to translate data encryption. Therefore, it should be combined with other anti-leak strategies to ensure information remains protected. 

Secure Endpoints

Endpoints are physical devices that connect to a network. Examples include mobile devices, desktop computers, servers, embedded devices, IoT devices, and virtual machines. The increased adoption of remote work environments has made these endpoints harder to secure. 

Organizations can protect endpoints with extended endpoint security. Employees with company iPhones should use Security Recommendations which notify them when their information has been compromised by a data leak. 

Firewalls and VPNs also protect endpoints, but many cybercriminals have learned to bypass them. They should be combined with additional security measures for optimal efficiency. 

Utilize Data Loss Prevention (DLP) Software

Data loss prevention applies to data leak prevention. It ensures sensitive data is not lost, misused, or exposed to unauthorized parties. A DLP program performs the following functions:

  • Identifies Data: AI may be used to identify data and streamline processes. 
  • Secures Data: DLP software may be deployed at the end of the network to ensure data transfers align with secure data policies.  
  • Secures Endpoints: Endpoint DLP monitors real-time user behaviour to ensure transfers occur between authorized parties. 
  • Protect Archived Data: The software uses regulatory compliance, access control, and encryption to protect archived data. 
  • Monitors Active Data: DLP tools will monitor data and flag suspicious behaviour. 
  • Detects Data Leaks: Data leak technology will scan for data exposures for fast remediation if a breach occurs. 

Employee Awareness Training 

Employees must be aware of the best anti-leak practices, as they are often susceptible to social engineering tactics, such as falling for phishing emails and similar scams.

To prevent employee-related data leaks, organizations should incorporate cybersecurity training into their onboarding process and provide ongoing training to keep workers informed about the latest cybersecurity trends. This approach ensures that networks remain secure from the ground up.

While data leaks may not constitute a direct attack, they can be just as damaging when sensitive information falls into the wrong hands. Implementing employee training, Data Loss Prevention (DLP) software, data encryption, access control measures, secure endpoints, and mitigating third-party risks are crucial steps to keep your system protected.

Which strategies do you use to ensure your company is safe? 

  1. Exploring Data Privacy and Security in B2B Gaming Data
  2. Approaching Complex Data Security for Small Businesses
  3. Protecting Company Files: Secure Strategies for Data Safety
  4. LoanDepot Ransomware Attack – Data Breach; 17M Impacted
  5. Cyqur Launches Data Encryption, Fragmentation Web Extension
[ad_2]
Source link

Downloads for the YouTube Music web app are finally rolling out

0
[ad_1]

Downloading music is more of a necessity on the YouTube Music mobile app than it is on the web app. Be that as it may, YouTube has been working on rolling out downloads for the YouTube Music web app. After we got a bit of a leak last week, it appears that the feature is now starting to make its way to users.

The issue with rolling out downloads for the web app is the fact that it’s a bit tough to download files that are accessible to your web browser. Not only that, but people are more likely to be out and about with their phones than with their computers. So, downloads weren’t really as much a necessity for the web app as it is for the mobile app.

However, YouTube Music is rolling out downloads for the web app

At this point, we’re not quite certain about YouTube’s rollout pace for this feature. A user on Reddit posted some screenshots of their YouTube Music interface, and they show the feature in action. When you have a song or an album pulled up, you will see a new download button on the interface. It will be in between the three-dot menu and the Save to library button. When you click that button, you will see the button change to show a downloading animation. Also, you will see a download progress indicator at the bottom left corner of the screen.

Just like with any other streaming platform, YouTube Music will try to stream the content online. However, once it detects that you are not connected to the internet, it will switch to offline mode and access the downloaded files.

Also, After 30 days, YouTube Music will require an internet connection to check your subscription status. If it detects that you don’t have an active subscription, it will make those downloads unavailable. So, if you’re the kind of person who likes to download a bunch of music, right before your subscription ends, and keep your computer offline, you’ll only have one month of victory. Right now, we’re uncertain how widespread this rollout is, so you’ll have to keep an eye out for the download button to reach your web app.


[ad_2]
Source link

Micron unveils the world’s smallest UFS 4.0 storage chip

0
[ad_1]

Micron, the Idaho-based producer of storage and memory chips, has unveiled the world’s smallest UFS (Universal Flash Storage) package. Measuring just 9×13mm in dimension, it is an incredibly compact UFS 4.0 chip. The semiconductor company is currently sampling the new solution.

Micron promises faster AI performance with its compact UFS 4.0 chip

Unveiled at the Mobile World Congress (MWC) 2024, Micron’s compact UFS 4.0 storage chip is built on its advanced 232-layer 3D NAND memory. The company claims a sequential read speed of 4,300 MB/s and a sequential write speed of 4,000 MB/s. These speeds are twice as fast as the firm’s 176-layer UFS 3.1 NAND. The new chip is also 25% more power efficient than the previous-gen solution.

According to Micron, these improvements enable faster loading of large language models (LLMs) in generative AI applications. The company touts 40% faster loading for a smoother experience when initializing AI tools. “Micron UFS 4.0 raises the bar for mobile storage with enhanced performance, flexibility, and scalability to accelerate the rollout of generative AI-capable smartphones,” said Mark Montierth, a GM at Micron.

This isn’t the first UFS 4.0 solution from Micron. The American semiconductor firm debuted its next-gen storage chip last June. In its first attempt, the company matched Samsung’s first-gen UFS 4.0 chip in terms of size (11×13mm) while delivering faster speeds. Samsung promised a sequential read speed of 4,200 MB/s and a sequential write speed of 2,800 MB/s for its solution.

Micron hasn’t improved the speed with its latest offering but shrunk the size to save some space inside devices. The company believes this will allow manufacturers to provide larger batteries. “These significant space savings result in an optimal size for next-generation foldable and ultra-slim smartphone designs,” the firm said in a press release. Its enhanced power efficiency will further extend the battery life.

Micron’s UFS 4.0 storage chips also feature some proprietary tech for enhanced performance. High-Performance Mode or HPM optimizes performance during heavy usage. It allows the device to prioritize critical tasks over background tasks, resulting in an over 25% speed boost. One Button Refresh or OBR allows for 10% faster app launches by automatically cleaning and optimizing data.

The company is currently sampling the new storage chip

The world’s smallest UFS 4.0 storage chip will be available in 256GB, 512GB, and 1TB capacities (no UFS 4.0 for 128GB solutions yet). Micron is currently sampling the chip with its clients. It is unclear when the new solution will be available commercially. The company is aiming the chip at the next generation of flagship Android smartphones.


[ad_2]
Source link

Hackers Selling DCRat Malware Subscriptions For $5 on Telegram

0
[ad_1]
DCRat Malware

Researchers from ANY.RUN reported a new wave of DCRat malware, known for its wide array of harmful functions, selling the membership for the low cost of $5.

The detailed report covers the distribution, dynamic, and static analysis of DCRat, also known as Dark Crystal RAT, which is both a Remote Access Trojan (RAT) and an information stealer.

DCRat’s modular architecture allows for customization and mutation to bypass signature-based detection, making it a formidable tool for cybercriminals.

The malware’s low price point has made it accessible to many threat actors, from novices to organized groups.

You can analyze DCRat malware file, network, module, and registry activity with the ANY.RUN malware sandbox.

ANY.RUN is a cloud-based environment for analyzing Windows malware and Linux-based samples. Malware analysts, SOC, DFIR teams can safely examine threats, simulate different scenarios, and gain insights into malware behavior to improve cybersecurity strategies.

ANY.RUN also allows researchers to understand malware behavior, collect IOCs, and easily map malicious actions to TTPs—all in our interactive sandbox.

 The Threat Intelligence Lookup platform helps security researchers find relevant threat data from sandbox tasks of ANY.RUN.

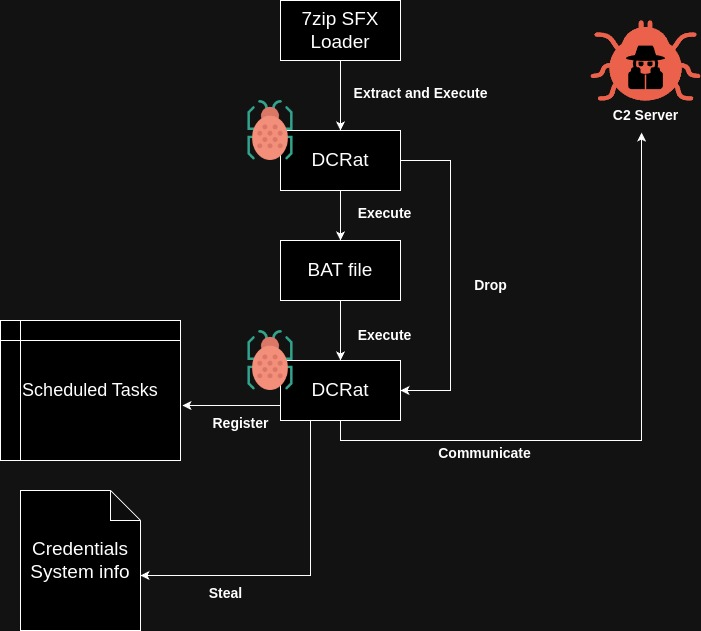
Infection Flow

ANY.RUN’s analysis reveals that DCRat is sold via a Telegram group, operating on a subscription model with prices ranging from $5 for two months to $39 for a lifetime subscription.

  • They do all communication through Telegram. 
  • They only accept crypto payments to burner wallets. 
  • They use crystalpay[.]io to further anonymize transactions. 
infection Flaw

The ANY.RUN Malware Trends Tracker ranks DCRat as the 9th most prevalent malware as of January 18, 2024, indicating its rising trajectory.

The malware is distributed through a Telegram bot, which also provides support and facilitates transactions through the crystalpay[.]io payment platform, demonstrating the DCRat team’s high level of operational security (OPSEC).

Document
Analyse Shopisticated Malware with ANY.RUN

More than 300,000 analysts use ANY.RUN is a malware analysis sandbox worldwide. Join the community to conduct in-depth investigations into the top threats and collect detailed reports on their behavior..

DCRat Malware Dynamic Analysis

The surface analysis of DCRat, identifying it as a password-protected Self-Extracting Archive (SFX) file, often used to evade detection.

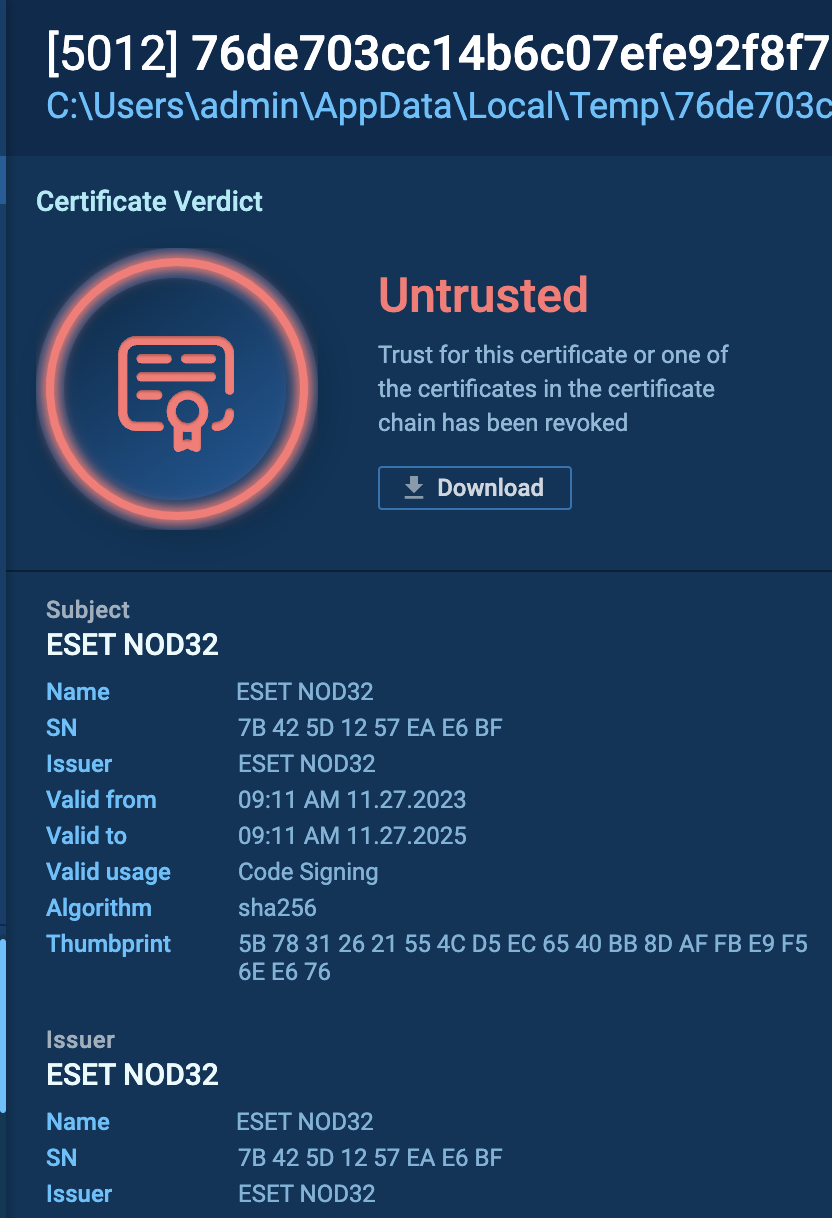
Dynamic analysis in ANY.RUN’s controlled environment revealed the malware’s behavior, including the execution of a digitally signed executable file disguised as a printer driver and the dropping of multiple executables to ensure persistence.

Static Analysis

Static analysis provided insights into the malware’s functions, Indicators of Compromise (IOCs), and configuration details.

The analysis utilized tools such as Detect It Easy (DIE) and decompilers like dnSpy or ILSpy for .NET applications to deobfuscate the executable and understand the malware’s operational logic.

The ANY.RUN team also recommends using Flare FLOSS for extracting strings from binaries to identify hidden information.

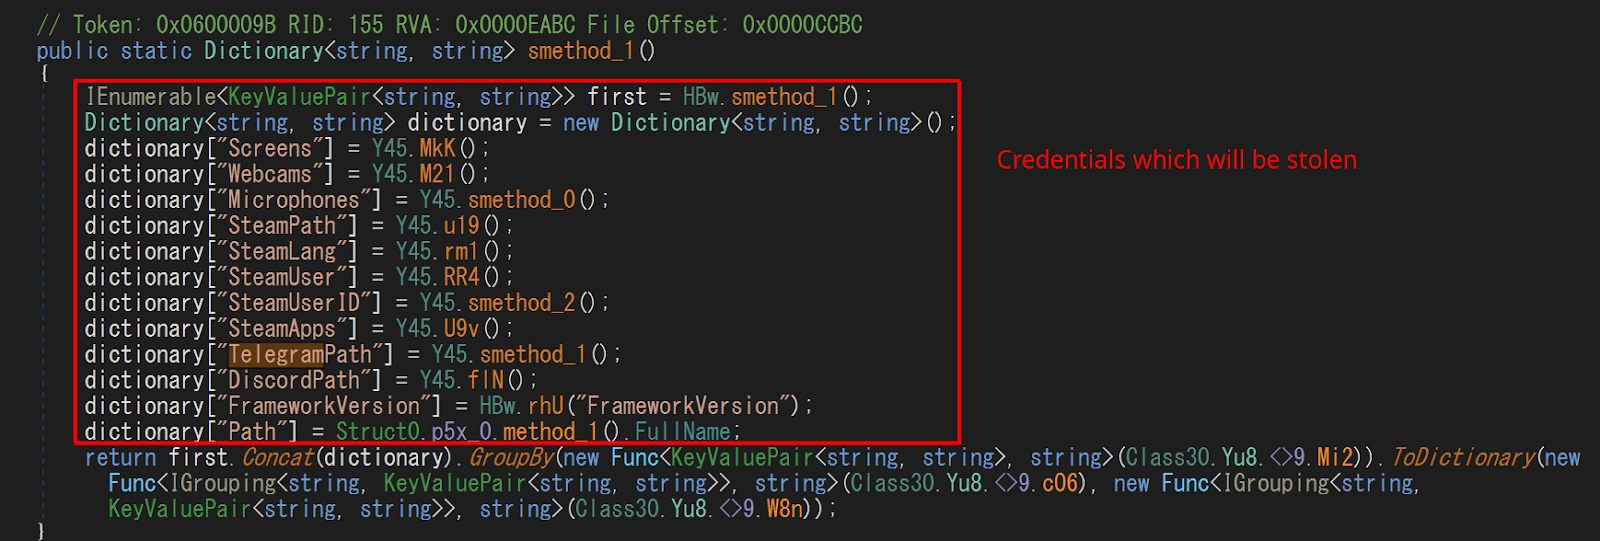
Researchers also noted that the malware is stealing the following data.

  • Screen Capture 
  • Webcam 
  • Microphone 
  • Steam specific data 
  • Telegram specific data 
  • Discord specific data 
  • .NET specific data 

The analysis concludes with the mapping of DCRat’s tactics, techniques, and procedures (TTPs) to the MITRE ATT&CK framework, aiding SOC analysts in understanding the threat quickly. ANY.RUN’s service is invaluable for rapid threat identification and in-depth malware research.

ANY.RUN encourages cybersecurity professionals to access the full analysis on their platform to better understand DCRat’s capabilities and strengthen their cybersecurity posture.

About ANY.RUN

ANY.RUN is an interactive cybersecurity service that enables professionals to analyze malware and understand its behavior in a safe, controlled environment. The service is dedicated to providing comprehensive analysis tools to combat digital threats.

Trusted by over 400,000 security specialists, ANY.RUN empowers SOC and DFIR teams to investigate threats efficiently through its cloud-based malware sandbox.


[ad_2]
Source link

ZTE’s first flip smartphone is part of its 2024 lineup at MWC

0
[ad_1]

ZTE has come back to Mobile World Congress this week with a slate of new devices as part of its lineup for 2024, including the company’s first flip smartphone, which it says will be the “first flip phone for young people.” Called the nubia Flip 5G, it was designed to be the first flip phone for young people and to that end, it features a more affordable price tag and an “abundance of features and applications” that young people will enjoy using ZTE says.

ZTE is also announcing the nubia Z60 Ultra, a flagship device sporting an under-display camera, a massive 6,000mAh battery, and a powerful Snapdragon 8 Gen 3 mobile platform from Qualcomm. If you thought ZTE was done, though, you’d be wrong. Because ZTE has more phones to announce at MWC 2024. This includes the nubia Focus 5G, as well as the nubia Neo 2 5G aimed at mobile gamers. It’s a varied lineup with something for everyone.

The nubia Flip 5G is the first flip smartphone from ZTE

Flip smartphones are not a new device category for the industry but they certainly aren’t common. In fact, there are actually not very many of them out there. The most recognizable flip smartphones are without a doubt the Galaxy Z Flip series and the most recent Moto Razr. There’s also the Oppo Find N3. Beyond that, however, you’d be hard-pressed to find a flip smartphone from most brands. Another thing to consider is that all of those previously mentioned options are considerably expensive. ZTE says the nubia Flip 5G will be more affordable, stating that “consumers will be surprised by the price.”

ZTE also highlights that it’ll have an abundance of apps that can be used on the external display. The phone is said to have a high-strength hinge with a 6.9-inch 120Hz display when unfolded. One of the key factors that ZTE seems keen to highlight is that the phone opens “wrinkleless.” What ZTE is basically saying is that you shouldn’t see any creases on the display when the phone is fully unfolded. The phone also has a 50MP main camera, a 4,310mAh battery, and it’s powered by a Snapdragon 7 Gen 1 mobile platform. In terms of cost, ZTE says it’ll start at $599 USD. Which makes this option from ZTE quite possibly, the most affordable folding flip smartphone on the market.

An affordable gaming phone for all

Gaming phones are still a niche product category when it comes to smartphones. They’ve certainly grown, thanks to the steadfast and headlong attitudes of brands like ASUS and RedMagic with a passion and drive for mobile gaming. But those phones are not necessarily affordable. RedMagic’s most recent offering, the 9 Pro, starts at $649. That isn’t terrible, but it doesn’t hold a candle to the nubia Neo 2 5G that ZTE is releasing this year. ZTE is also expanding the device to other markets where it wasn’t previously available.

With its first model the nubia Neo in 2023, the phone was released in Southeast Asia, the Middle East, and Europe. The Neo 2 5G will expand to the US, with a price point starting at an incredibly low $199 USD. It features shoulder triggers for that controller-like feel when gaming in landscape mode. As well as a 120Hz display at 6.72 inches and a large battery capacity of 6,000mAh. Furthermore, it has 33W fast charging. It’s considerably gamer-focused. Promoting long-lasting battery life for longer game sessions and a quick charge capability when you need to top up in a hurry. The 120Hz display won’t hurt either. As your games should look nice and smooth.

That being said, ZTE doesn’t mention anything about some of the other specs. Such as the chipset, RAM, or storage. With a starting price point of $199 USD though, it’s not likely to be among the most powerful of devices. That doesn’t mean it won’t be capable, however. Also worth noting is that ZTE says the price will change depending on the market and specific specs.

Shift your focus to better phone photography

Some people buy phones for the superior camera while others look for a device that prioritizes performance. If you’re the former type of consumer, then ZTE has your number with the nubia Focus 5G series. The nubia Focus 5G is solely focused on a great smartphone camera experience because, after all, the best camera is the one you have on you. And in most cases, that’s probably going to be the one on your phone because it fits in your pocket.

The core of this experience is the 108MP dual camera system on the nubia Focus Pro 5G. There’s also a non-pro model. Both versions come with a 5,000mAh battery and a 120Hz display. Although each one’s display is slightly different. The nubia Focus 5G comes with a 6.6-inch display while the Pro model bumps it up to 6.72 inches. These phones keep with the affordable theme coming in at a starting cost of $199 USD. ZTE has yet to announce information regarding the release date and availability of these devices.


[ad_2]
Source link

Zyxel Firewall Flaw Let Attackers Execute Remote Code

0
[ad_1]

Four new vulnerabilities have been discovered in some of the Zyxel Firewall and access point (AP) versions that are associated with Denial of Service, OS Command Injection, and Remote code execution.

These vulnerabilities have been assigned with CVE-2023-6397, CVE-2023-6398, CVE-2023-6399, and CVE-2023-6764.

The severity of these vulnerabilities ranges between 6.5 (Medium) and 8.1 (High). However, Zyxel networks have fixed these vulnerabilities, and a security advisory has been released to address these vulnerabilities.

Zyxel Firewall Flaw

CVE-2023-6397: Null Pointer Dereference vulnerability in Zyxel

This vulnerability could allow a LAN-based threat actor to cause a denial-of-service condition by downloading a crafted RAR compressed file onto a LAN-side host if the firewall has “Anti-Malware” feature enabled.

The severity for this vulnerability has been given as 6.5 (Medium).

CVE-2023-6398: Post-authentication Command Injection vulnerability

This vulnerability exists in the file upload binary in Zyxel ATP series devices that could allow an authentication threat actor to execute operating system commands on the affected device via FTP with administrative privileges.

The severity for this vulnerability has been given as 7.2 (High).

CVE-2023-6399: Format String Vulnerability in Zyxel

This vulnerability allows an authenticated IPSec VPN user to perform a denial of service condition against the deviceid daemon.

Successful exploitation of this vulnerability involves sending a crafted hostname to an affected device if the device has the “Device Insight” feature enabled.

The severity for this vulnerability has been given as 5.7 (Medium).

CVE-2023-6764: Format String Vulnerability in Zyxel leading to Unauthenticated RCE

This vulnerability exists in one of the functions of the IPSec VPN feature that could allow a threat actor to achieve unauthenticated remote code execution on the affected device by sending a sequence of specially crafted payloads with an invalid pointer. 

However, this attack requires a detailed knowledge of the affected device’s memory layout and configuration. The severity for this vulnerability has been given as 8.1 (High).

Affected Products And Versions

Users of these products are recommended to upgrade to the latest versions in order to prevent these vulnerabilities from getting exploited by threat actors.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Game Changer for Mobile Video with Sony Imaging Chip

0
[ad_1]

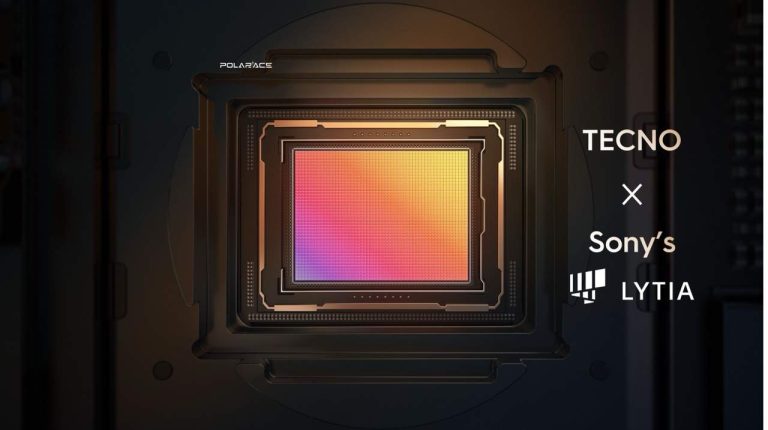
TECNO isn’t done with MWC Barcelona announcements this week. Today, it announced its new PolarAce Imaging System, which it built with Sony’s own imaging chipset. It will debut on the CAMON 30 Premier 5G, which is set to debut in the second quarter of 2024.

The company claims that this new imaging system is “bringing a new pinnacle of mobile video imaging to users around the world.”

“Our commitment and goal has always been to deliver the best mobile imaging experience to TECNO users around the world to meet diverse imaging needs,” said Jack Guo, General Manager of TECNO. “Previously, we have revolutionized smartphone imaging with innovations such as the advanced RGBW Ultra-Sensitive Sensor and the world’s first retractable portrait lens. PolarAce, our first imaging system with an independent imaging chip, leverages our partnership with Sony to signal a new era of extraordinary smartphone video imaging.”

TECNO and Sony worked together to build this imaging system, using the CXD5622GG Sony imaging chip, Sony’s LYTIA components, and also using TECNO’s Universal Tone multi-skin tone imaging technology and its AI imaging technologies.

TECNO wanted to redefine the mobile video experience

Let’s face it: these days, the camera experiences on our phones are pretty impressive. But there is still room for improvement, and TECNO saw a way for even more outstanding results. One of the examples the company uses is the computational power of traditional systems on chips, which is no longer adequate to address user needs. Other pain points that consumers experience include night scene video capture, full-scene HDR shooting, and overall video smoothness.

Thanks to the Sony CXD5622GG independent imaging chip, TECNO was able to build PolarAce, and it can deliver industry-first and industry-leading technologies to achieve a higher level of performance and quality for mobile imaging. Making it easier than ever to be a content creator with just your phone.

Another pain point that consumers experience, especially those with darker complections, is skin tone. TECNO aims to solve that with PolarAce, which has an independent imaging chip that can enhance the incredible performance of TECNO’s new Universal Tone technology. The company first debuted this in October 2023, and it is the industry’s most advanced AI-powered multi-skin tone imaging technology. It was developed to achieve more accurate skin tone capture based on unbiased data.

Of course, AI is involved here too. TECNO is embracing AI to boost the ease and enjoyment of the camera on its new CAMON 30 Premier 5G. It has been enhanced by AI-powered functionalities that make imaging even more impactful and enjoyable. It includes the AIGC Portrait Capture, which allows users to generate a vast array of portrait disguises, from wedding dresses to cartoon dolls, graduation attire, and more. There’s also One Click Erase, which uses AI technology to enable the one-click removal of obstacles and clearing of passersby.

TECNO PolarAce Daylight HDR Effect Large

PolarAce will debut first in the CAMON 30 Premier 5G

As mentioned already, PolarAce will debut in the upcoming CAMON 30 Premier 5G smartphone from TECNO. It’s slated to be released in the second quarter (between April and the end of June). TECNO is releasing some info about this phone now, but not all of the details.

The phone will come with a 70mm golden portrait focal length periscope lens; this is going to allow for some incredible macro shots, as well as being able to use up to 60x hybrid zoom. By using a portrait lens, TECNO is able to ensure less barrel distortion and more convenient framing, and unlike traditional portrait lenses, enables the full use of the sensor in night shots, providing better noise control and clarity.

It’ll also have the industry’s first 4K 30fps full-scene AI NR HDR Video along with a 50-megapixel front-facing camera, which uses eye tracking to take the perfect selfie every time.

This is all powered by the MediaTek Dimensity 8200 Ultimate 5G chipset, along with the new Sony Imaging Chip that’s being used inside PolarAce.  And finally, it’ll have a 1.5k resolution LTPO AMOLED display with 1400 nits peak brightness.

We’ll learn more about the CAMON 30 Premier 5G in the coming months. But it is shaping up to be a pretty impressive phone and camera so far.


[ad_2]
Source link

Meta under fire after investigation into “child influencer” accounts

0
[ad_1]

Meta and its subset platforms have long been accused of knowingly compromising children and letting them use the platform without age verification. But a new report by The New York Times and The Wall Street Journal is shedding light on the hidden aspects of “child influencers” on Instagram and Facebook, revealing how parents behind these accounts are sexually exploiting their children.

While these platforms apparently do not let underage children in or limit their access to sensitive content, they knowingly let parents run accounts for children and sell sexual materials of their kids to users, most likely pedophiles lurking online.

The materials include photos of children, chat sessions with them, and used clothes and leotards. Even worse, some parents reportedly forced children to interact with sexual messages sent by some followers. Meta has not yet commented on the matter.

Meta comes under fire for “knowingly” letting parents post explicit content about their children and sexually exploit them

The content produced by such parents allegedly came under the radar of Meta staff. And they were aware that some parents are creating content of their children that’s attractive to pedophiles. The parents running those children’s accounts even had the chance to use Meta’s paid promotion tools to expand their content’s reach. As per an internal survey conducted by Meta in 2020, over 500,000 child Instagram accounts had “inappropriate” interactions daily.

As the reports read, some child influencers on Instagram make $3,000 per post. This allows parents to make even six-figure incomes out of their children’s content. Meanwhile, such accounts attract a large number of male followers, and a considerable number of them could happen to be pedophiles. Among the 5,000 examined accounts, roughly 32 million male users were found.

Meta staff suggested the company force those child accounts to register for monitoring or ban their subscription. However, those suggestions were all rejected by the firm. Meta instead developed a system to prevent potential pedophiles from subscribing to children’s accounts. That system could be unreliable, of course.

The New York Times also criticized Meta’s content moderation attempts. The outlet reported that the tech firm only took action against 1 out of 50 reported content in an eight-month period.


[ad_2]
Source link