ChatGPT malfunctioned and started spouting gibberish

0
[ad_1]

ChatGPT recently had a major malfunction when the AI model began speaking complete gibberish to multiple users. Various reports started appearing, especially on Reddit, of ChatGPT going off on completely nonsensical ramblings. There were also reports of the AI getting stuck in loops or mashing languages together for weird hybrids. OpenAI took notice and identified the issue later on, having it fixed a few hours later.

ChatGPT malfunctions, gets stuck in loops & spouts gibberish

One report on Reddit showed ChatGPT suddenly began talking incoherently. Random words, excerpts from specific training data, and even different languages were all being blurted out by the AI. Another malfunction report had a user share multiple screenshots of ChatGPT fluctuating between hallucinating and being lucid. After talking nonsense, it got stuck in a loop before terminating its response. Once the user pointed this out to it, it apologized, before talking gibberish once more. This repeated another time, at which point the screenshots were taken.

Another very interesting post showed ChatGPT getting stuck in a loop again. This time, however, the loop was a self-correcting one. Once asked to name the biggest city in the world starting with the letter ‘A’, ChatGPT went on a very odd tangent. It would name a city, then say it wasn’t the correct answer and try again, ad infinitum. People in the comments tried this with their own chats and shared similar results. Yet another Reddit post about GPT-4, OpenAI’s premium subscription-based model, showed ChatGPT hallucinating. Once again, multiple users in the comments shared similar results.

OpenAI explains why this happened

OpenAI took note of the developing malfunction and quickly identified the issue. Within a few hours, the company reported that ChatGPT was operating normally on its status page. The next day, the company released an explanation for what had gone so wrong.

Apparently, a recently introduced optimization had messed things up. OpenAI explained, in very simple terms, how ChatGPT works and what had gone awry.

“LLMs [Large Language Models] generate responses by randomly sampling words based in part on probabilities. Their “language” consists of numbers that map to tokens. In this case, the bug was in the step where the model chooses these numbers. Akin to being lost in translation, the model chose slightly wrong numbers, which produced word sequences that made no sense.”

In short, ChatGPT was sourcing the wrong words, and displaying abject gibberish. Think of it like throwing darts at a large dictionary and constructing a sentence out of the words the darts landed on.


[ad_2]
Source link
Neuralink’s first human patient can use his brain to control mouse cursor

0
[ad_1]

Around a month after Neuralink’s first patient received an implant, Elon Musk has confirmed the patient is able to control a computer mouse. Neuralink, with the goal of perfecting human brain and computer chip synergy, is an ambitious company. Almost a month ago, Neuralink finally went through with its first-ever human trial after receiving the green light from concerned authorities.

“Progress is good,” says Musk about Neuralink’s first patient

Once the chip had been implanted, stories circulated around the web wondering if the patient would recover. It seems they’ve not only done so, but the Neuralink chip works as intended as well. During a Spaces audio call on X, Elon Musk elaborated on the patient’s recovery.

“Progress is good, and the patient seems to have made a full recovery, with no ill effects that we are aware of. The patient is able to move a mouse around the screen by just thinking.”

The above is a breakthrough moment for Neuralink. Musk has many bigger goals he wants to achieve via Neuralink integration. He’s talked about easy and fast ways to combat autism, depression, schizophrenia, and other disabilities. The end goal is a science fiction-esque fusion of the human brain with a computer. This fusion would allow for potentially curing incurable diseases, and allowing disabled people to communicate or move independently.

Musk also said they were seeing how much the chip could handle at the moment. “We’re trying to get as many button presses as possible from thinking.”

A company mired in skepticism and controversy

As noble as Neuralink’s goals seem, the company isn’t without its fair share of criticism. Some of it stems from the current vocal subset of skeptics online, who are convinced Elon Musk could never release anything functional. Others are skeptical of the entire concept in general. But, much like AI, human-computer fusion could be a science fiction concept closer than people realize.

However, Neuralink has been in the spotlight for less-than-favorable news as well. Between 2022 and 2023, during the company’s trials on monkeys, reports emerged of potentially lethal side effects. The company was also fined recently for violating rules regarding the transport of hazardous materials. Nevertheless, Neuralink has pushed on and now they have a successful human trial to show for it.

No records, footage, or other materials have surfaced about Neuralink’s first patient as of yet. The company should likely be sharing more information as soon as it has gathered whatever initial research is needed.


[ad_2]
Source link

Some iPhone 15 users are reportedly still facing Bluetooth issues

0
[ad_1]

Some iPhone 15 users are still facing Bluetooth connection issues on their devices. Multiple users have taken to the Apple Support Community and MacRumors forums to report the connectivity problems on their latest iPhone. It appears that the issue is affecting all four iPhone 15, iPhone 15 Plus, iPhone 15 Pro, and Pro Max models. Notably, it seems to be an ongoing problem ever since the iPhone 15 went on sale last September.

Many iPhone 15 users have reported frequent disconnections on older Bluetooth devices

Many iPhone 15 series users first reported Bluetooth issues in October, soon after they got their hands on the latest iPhones. Apple was expected to fix these problems with the iOS 17 update. However, it appears that the Cupertino tech giant hasn’t fixed the connection issues in the latest iOS version. Notably, the users have reported frequent disconnections on older Bluetooth devices, such as the Bluetooth systems in their cars.

iphone 15 pro max AM AH 28

Furthermore, the latest Bluetooth complaint thread on MacRumors forums started in January. An iPhone 15 user posted that “Since ios 17 I have been having frequent disconnects in my car (no carplay. BMW 2014) bluetooth for calls. I make a hands free call in my car and after a few seconds bluetooth disconnects and I have manually switch to the speaker in my Iphone.”

“I have had this car since new and I switch iphones almost every year and usually the release x.0 has some bluetooth problems, but now 2 major releases for ios 17 and the issue is not solved. Another iphone 12 does not have the problem in my car”, he added further.

Since the post went live, hundreds of iPhone 15 series users reported similar issues with their units on the thread. Notably, another thread on the official Apple Support Community has now logged more than 1,700 users having similar issues. Many users have mentioned problems with audio audio that will “cut out and reconnect” on AirPods and car audio systems.

iphone 15

It’s not clear what’s causing the Bluetooth issue and resetting the phone doesn’t fix it

As of now, it is not clear what’s causing the Bluetooth disconnection issues on the iPhone 15 series units. There’s a possibility that certain iPhones have faulty Bluetooth chips, as not all the latest iPhone users have reported the problem. Notably, many users have mentioned that applying typical fixes or restarting the phone isn’t fixing it. Furthermore, even factory resetting the affected iPhone 15 units doesn’t fix Bluetooth connection problems.

It’s worth mentioning that Apple hasn’t yet openly acknowledged the iPhone 15’s Bluetooth connectivity issues. If you are facing similar problems in your unit, then you can try to get a replacement device from the company. We will inform you more on the matter as soon as Apple officially announces something.


[ad_2]
Source link

Global HONOR Magic6 Pro is coming today, you can watch the event live

0
[ad_1]

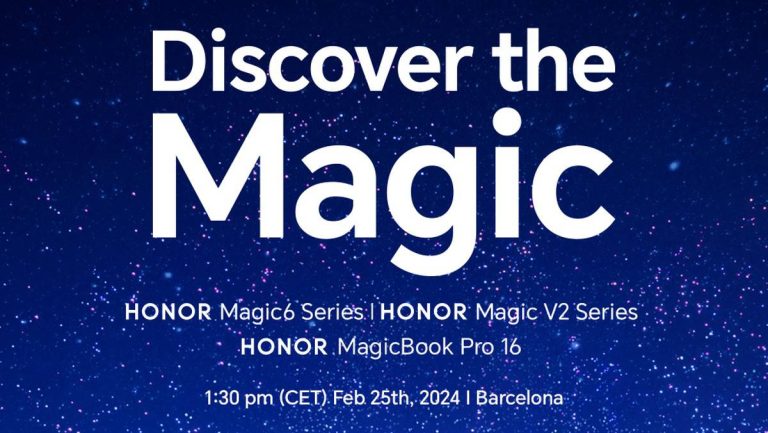
The global variant of the HONOR Magic6 Pro will launch today, and you can watch the event live. HONOR will livestream the event from Barcelona, as part of the Mobile World Congress (MWC) 2024.

The global HONOR Magic6 Pro variant will launch today, and you can watch the event live

The event is set to start at 1.30 PM CET, which translates to 12:30 PM BST / 7:30 AM EST / 4:30 AM PST. The event livestream will be available via YouTube, and HONOR’s X and Facebook accounts. We’ve embedded the YouTube link below the article.

With that being said, the HONOR Magic6 Pro is not the only device the company will launch, not at all. In its livestream announcement, shown in the image below, the HONOR Magic V2 series and HONOR MagicBook Pro 16 are also mentioned.

Global HONOR Magic6 Pro event image 1

The global Porsche Edition HONOR Magic V2 RSR model will also get announced

Now, the HONOR Magic V2 already been launched globally, but the Porsche Edition HONOR Magic V2 RSR did not. That device will be presented during this event too. The Porsche Edition HONOR Magic6 Pro is also expected to make an appearance.

Do note that the Porsche Edition HONOR Magic V2 has already launched, though not globally just yet. The Porsche Edition HONOR Magic6 Pro RSR did not launch at all just yet. HONOR did hint at the phone’s launch, though, which is why we’re expecting it today.

The HONOR MagicBook Pro 16 is the company’s upcoming Windows laptop. Well, some would say it’s an ultrabook. It will be made out of metal, and it will be very thin at the same time. That laptop will also likely include very powerful specs, on top of everything.

The company will show us at least four products

HONOR will have plenty to show us today, that’s for sure. To sum up, the HONOR Magic6 Pro global launch will occur, and almost certainly the Porsche Edition HONOR Magic6 Pro as well. The global version of the Porsche Edition HONOR Magic V2 RSR will be presented, and the HONOR MagicBook Pro 16. That’s at least four devices.

The regular HONOR Magic V2 will be on display over in Barcelona too, in case you’re there. HONOR will be one of the main highlights of MWC when it comes to the smartphone world, that’s for sure. Once again, you can watch the live stream via the video below.


[ad_2]
Source link

FTC Orders Avast to Pay $16.5M for Selling User’s Browsing Data

0
[ad_1]

AV (antivirus) companies normally do not sell user’s browsing data, as it goes against their commitment to user privacy and security.

Their business model relies on protecting against cyber threats rather than exploiting user data. 

But, recently, The Federal Trade Commission (FTC) ordered Avast to pay $16.5 million for selling Users’ browsing data.

Browsing history can unveil personal details – from romance to finance, politics to weight loss, and job rejections to gambling.

FTC Orders Avast To Pay $16.5M

The FTC fined Avast $16.5 million for selling users’ browsing data without consent. Avast’s browser extensions and antivirus software collected and sold data, breaching the privacy commitments. 

Avast misled users by claiming to block tracking while selling detailed browsing data to over 100 third parties through its subsidiary, “Jumpshot.”

Since 2014, Avast collected browsing data through browser extensions and antivirus software, including sensitive info like religion and finances. 

Avast didn’t disclose this data collection and claimed to reduce tracking. After acquiring Jumpshot, Avast sold consumer data to various clients until 2020.

The company falsely claimed to anonymize user data, but the FTC found it poorly protected identifying information. 

Contrary to its promises of aggregate and anonymous transfers, it sold detailed browsing data, including unique identifiers, timestamps, device details, and location. 

The company failed to prevent data buyers from re-identifying users, even when contracts included prohibitions. 

Some Jumpshot products allowed clients to track specific users and associate their browsing histories with other information, as seen in the Omnicom contract.

Apart from the $16.5 million fine, Avast must also refrain from misrepresenting its data usage. 

While the proposed order includes various provisions such as:-

  • Prohibition on Selling Browsing Data
  • Obtain Affirmative Express Consent
  • Data and Model Deletion
  • Notify Consumers
  • Implement Privacy Program

The FTC, with a 3-0 vote, issued the complaint and accepted the agreement. A description of the agreement will soon be published in the Federal Register for public comment for 30 days.

Avast deceived and unfairly exposed detailed browsing data, breaching Section 5 of the FTC Act. Selling or sharing browser history without clear permission violates the law. 

FTC stresses heightened privacy obligations for sensitive data, extending from geolocation to health info.

Avast’s case adds to a series highlighting the need to safeguard sensitive information.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Threads has been added to the Oversight Board

0
[ad_1]

Threads is the latest edition to the Meta Family of social media apps, and its user base skyrocketed ever despite its slump last year. Well, even though the app has been out for over half a year, Threads has made it to the Oversight Board.

What is the Oversight Board?

Back in 2020, an independent oversight board was formed around Meta’s (then Facebook’s) ecosystem of apps. It’s described by Mark Zuckerberg as sort of a supreme court. The Oversight Board consists of 40 members, and they’re charged with being an independent voice to help enforce freedom of speech and expression throughout the company’s apps.

The board consists of members from all around the world, and this creates a very diverse voice to handle matters that could potentially affect many people. This is a separate entity that’s not governed by Meta. So, this way, the board is able to perform its actions without any sort of bias.

Basically, if you’ve raised an issue with Facebook, or Instagram, and you’ve exhausted all of the resources available in those companies, then you would send an appeal to the Oversight Board. The Oversight Board will check for larger issues affecting multiple people. If the board deems an issue a big enough problem, it will then act upon it.

The oversight board now includes threads

Since this was established back in 2020 when the company consisted of Facebook, Instagram, and WhatsApp, this is the first time that the Oversight Board is adding a new app. Threads is now under the oversight board.

So, if there is an issue affecting you, and you have not been able to resolve it using Threads’ native tools, then you would take your claim to the Oversight Board. Presenting your claim to the board does not guarantee that it will be answered. However, if enough people present a claim for the same issue, then there’s a chance that the oversight board will look into it.


[ad_2]
Source link

New Android threat sends your photos, texts, contacts, hardware data and more to a foreign server

0
[ad_1]
According to Bleeping Computer, a new version of the XLoader malware (aka MoqHao) is making the rounds. Previously, this malware was spotted in the U.S., U.K., Germany, France, Japan, South Korea, and Taiwan. The malware is disseminated through SMS text messages that feature a shortened URL link and XLoader can launch immediately after installation. This allows the malware to run undetected in the background while personal data is stolen away.

McAfee says, “While the app is installed, their malicious activity starts automatically. We have already reported this technique to Google and they are already working on the implementation of mitigations to prevent this type of auto-execution in a future Android version.”

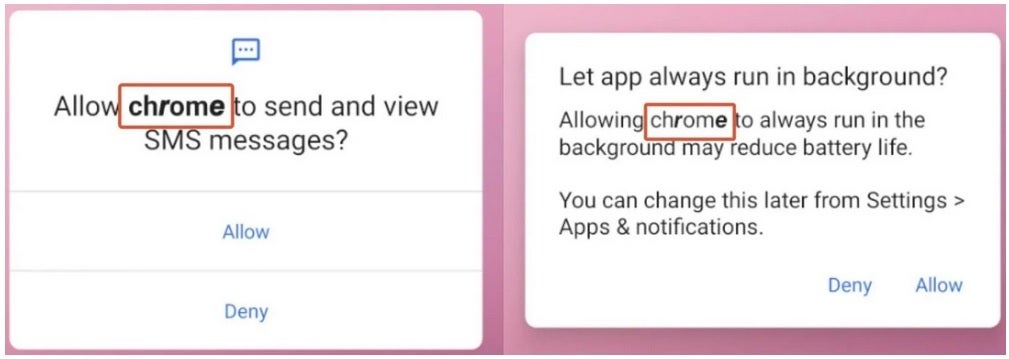
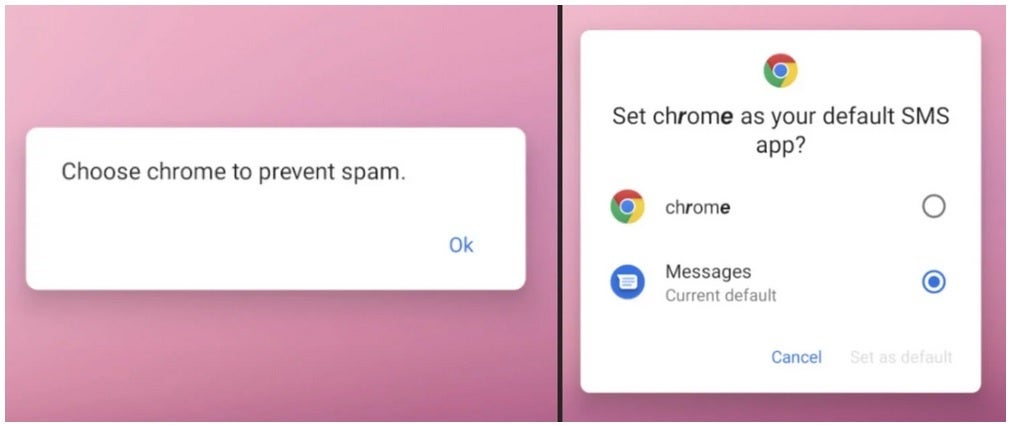
The malicious apps send out permission requests pretending to come from Google Chrome requesting permission to send and view SMS (text) messages and asking permission to keep “Chrome” running in the background. And the coup de grace is permission to make “Chrome” your default SMS app. The malware, once it gets all of these permissions, is used to send photos, text messages, contact lists, and info on the hardware you are using (including your phone’s unique IMEI number) to the control server. Yes, it is very scary.

McAfee says that since minimal interaction is required by the victim, the new XLoader malware is even more dangerous than its predecessor. There is some good news. An update from McAfee dated a couple of weeks ago says that Android devices with Google Play Services are protected from attacks from this kind of malware by Google Play Protect which is enabled by default.
Still, there are some takeaways to consider here. Never click on a shortened URL found in a message. And never sideload an app.

[ad_2]
Source link

X (formerly Twitter) expands audio and video calls to all users

0
[ad_1]
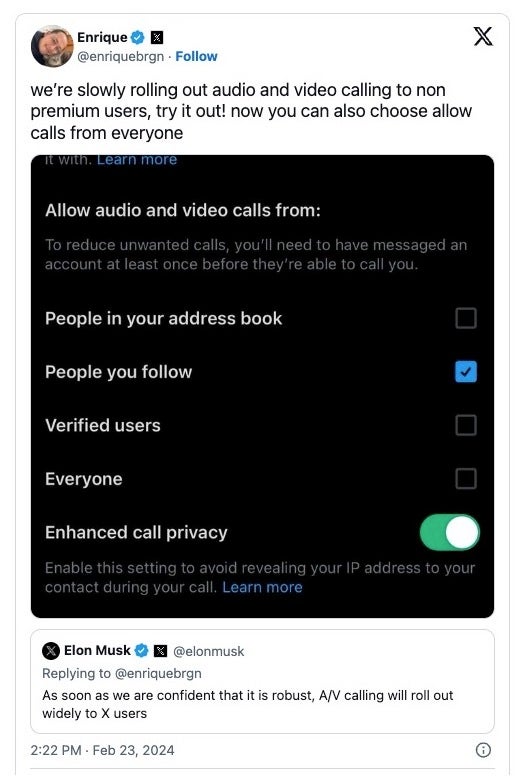
X, the social media network formerly known as Twitter, is expanding its audio and video calling capabilities. Previously a perk for Premium (what used to be called “Twitter Blue”)  subscribers, this feature will now be available to everyone on the platform.
As reported by Engadget, Enrique Barragan, an engineer at X, announced the expansion via a post on the platform. This was done while quoting Elon Musk’s promise back in January where he said this would arrive to all users when the feature was robust enough.

The move brings X closer to Elon Musk’s goal of making the platform an “everything app,” as he has so often expressed. Calls were added for iOS users last year, followed by Android, but only paying subscribers could use them. 

How does it work?

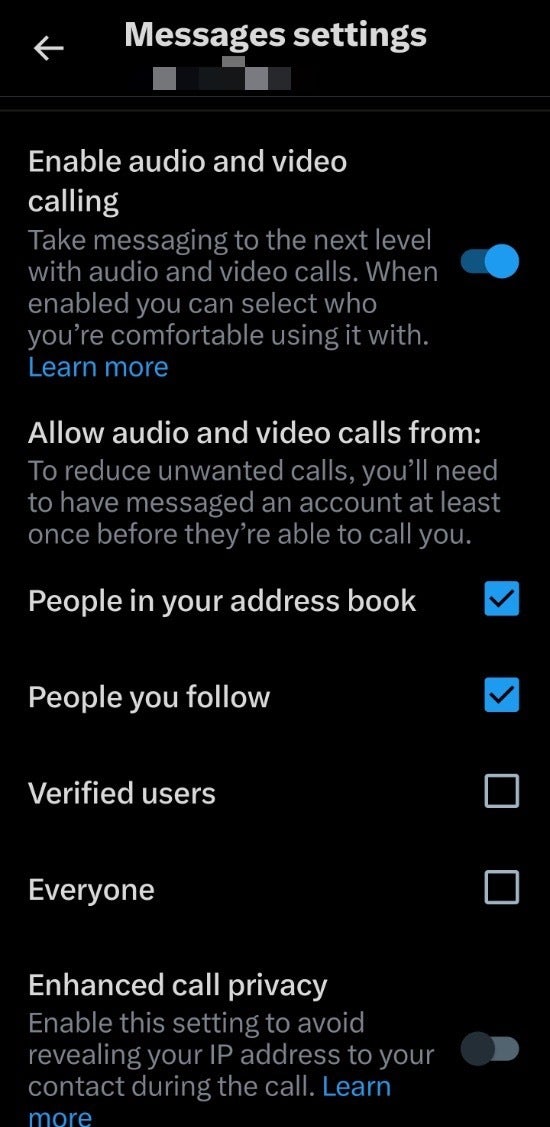
The official support page says that you are able to control your audio and video calling options from the Direct Messages settings. From there, you will notice that by default, you are able to receive calls from accounts you follow or have in your address book — provided that you give X access to your address book. However, in order to call another user, both the caller and the recipient must have been in contact at least once via X’s Direct Messages (DMs).

X’s Audio and Video call settings in Direct Messages

This doesn’t mean that you cannot allow calls from everyone on the platform, though. If you are feeling adventurous, you can go ahead and do just that by turning on that option. However, if you plan on doing so, our advice would be to also turn on the new “Enhanced call privacy” setting, which hides your IP from people you call and receive calls from. As a matter of fact, you should probably turn on this option anyway if you plan on calling people from X.

The updated calling features aren’t instantly available for everyone. X is slowly rolling them out, likely in batches, and it appears that they are automatically turned on without prompting. If you do not wish to make and receive calls on X/Twitter, you may need to log in to the app and navigate to your Direct Message settings to turn the feature off.


[ad_2]
Source link

New features eyed for the Google Search widget on the Android home screen

0
[ad_1]

Android users of all shapes and sizes are used to the Google Search widget that appears on their home screen. Back in the day when Android was starting to make a name for itself and this writer carried a Motorola DROID, I  thought the Google Search widget was cool. Perhaps some of you guys and gals feel (and still feel) the same. Nonetheless, it appears that Google is considering making some changes to the capabilities of the Search widget and the tech company needs your help.

The Google Search home screen widget is part of the “Mobile Application Distribution Agreement” that Android phone manufacturers sign when installing the Google Mobile Services version of Android on a new model. In some markets, Android users are able to change the search engine used by the widget.
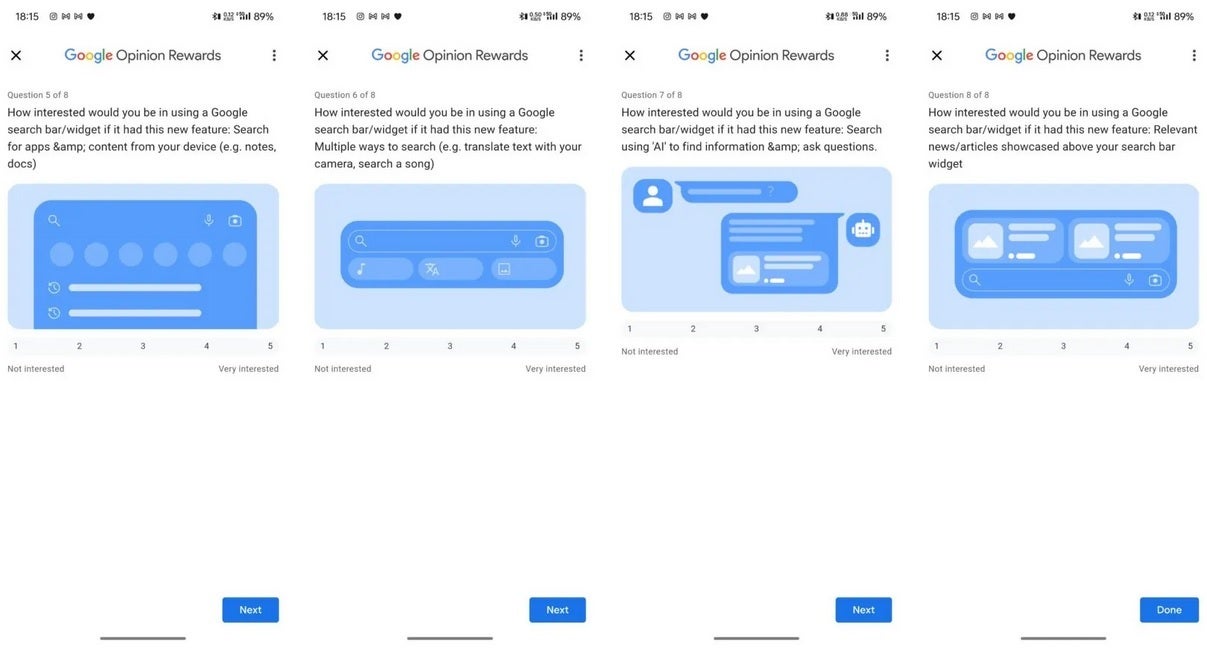
According to Android Authority’s Aamir Siddiqui, while setting up a new Android phone, he removed the Google Search widget from the home screen, Aamir received a Google Opinion Rewards survey that wanted to know why Siddiqui removed the Google Search widget from the home screen. The survey also asked, on a scale of 1-5 with the latter indicating the most interest, what Siddiqui thought about adding a few new search features to the widget such as translating text with the camera or using the widget to search for a song.

Other survey questions wanted to know whether Aamir wanted a new feature on the widget that would allow him to search through app content on his phone (similar to universal search), and use AI to help him search from the widget. Another survey question asked Aamir how interested he was in viewing relevant news articles above the search bar widget on the home screen.

Whether the results of the survey lead to changes to the Google Search widget is impossible to tell since we don’t know how each Android user will respond to the questions. But if changes are made (and we get the feeling that it wouldn’t be imminent) the survey might have had a hand in how Google “improves” the Search widget.

[ad_2]
Source link

Recent Joomla Update Brings Multiple Security Fixes – Latest Hacking News

0
[ad_1]

Joomla users must ensure that they receive the latest update as the platform fixes numerous security vulnerabilities. One of these includes a severe code execution vulnerability.

Joomla Fixes Numerous Security Vulnerabilities

According to a recent advisory, Joomla developers addressed five vulnerabilities with the latest CMS update, calling it a “security and bug fix” release. These include the following.

  • CVE-2024-21722: A low-severity vulnerability due to improperly terminating existing user sessions during MFA changes.
  • CVE-2024-21723: A low-severity open redirect vulnerability that existed due to inadequate parsing of URLs.
  • CVE-2024-21724: A  moderate severity cross-site scripting (XSS) vulnerability that could affect extensions due to improper input validation for media selection fields.
  • CVE-2024-21725: Another cross-site scripting vulnerability that existed due to inadequate escaping of mail addresses. Given the nature of the exploit which could lead to remote code execution, this vulnerability achieved a high severity rating.
  • CVE-2024-21726: A moderate severity cross-site scripting vulnerability that could affect various components due to inadequate content filtering.

These vulnerabilities affected different Joomla versions, which the developers patched with Joomla 4.4.3 and 5.0.3 releases. Besides, for Joomla version 3.x users, the update 3.10.14-elts arrived as a security update, carrying all bug fixes.

While the platform addressed the security vulnerabilities for all Joomla releases, users are still advised to upgrade to Joomla 5.0.3 as it also includes new features.

Joomla is an open-source content management system (CMS) that facilitates organizations, small companies, web agencies, and e-stores in setting up their websites and online apps without hassle.

Given its free availability, user-friendly interface, and seamless compatibility with Microsoft Windows and Unix-like systems alike, Joomla attracts a huge user base from around the world. Consequently, any security vulnerabilities in the platform directly risk a large number of users worldwide. Hence, Joomla users must ensure updating their sites with the latest security releases to receive all bug fixes in time and avoid potential threats.

Let us know your thoughts in the comments.


[ad_2]
Source link