Google Maps’ glanceable directions are finally rolling out widely, but a year late

0

[ad_1]

After nearly a year-long delay, Google Maps’ “glanceable directions” feature is finally rolling out to Android and iOS devices worldwide. This long-awaited addition makes your navigation experience more convenient and safer by bringing vital trip information directly to your lock screen.

Google originally announced this feature way back in February 2023, but the rollout took significantly longer than expected. After a few sporadic sightings over the course of last summer, there were no further updates on its development until January 2024, when it was reported that the feature began silently appearing for users everywhere. Now, according to Android Police, this is now rolling out widely.

What are these “Glanceable directions”?

Glanceable directions give you a quick overview of your journey with essential updates like real-time estimated time of arrival (ETA) and turn-by-turn navigation prompts. You can track your progress along the route overview even without starting full-fledged navigation, making it ideal for confirming your route or when you’re in familiar territory. Maps will also automatically adjust your route if you decide to take a detour without any manual intervention needed, ensuring you stay on track even if unexpected changes occur.

Glanceable directions also make navigating less distracting, which means you won’t need to unlock your phone constantly to check your progress. This is particularly beneficial while driving, making your trips safer.

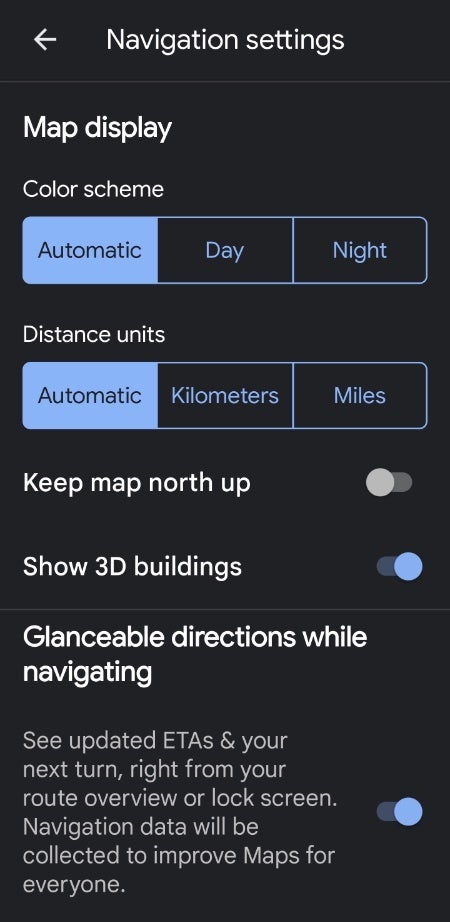
Google Maps on Android settings toggle for “Glanceable directions” | Image via Phone Arena

The feature is present right now in Google Maps version 11.116.0101 from the Google Play Store; however, it is possible that this is a staged rollout, meaning that you may be missing it from your Maps applications until the update reaches your device.

To check if the feature is available to you and to enable it, open Google Maps, tap on your profile icon (top right corner), go to Settings > Navigation Settings, scroll down to find the “Glanceable directions” toggle, and turn it on.

[ad_2]

Source link

Best of MWC 2024: OnePlus Watch 2

0

[ad_1]

The battery life king for Wear OS smartwatches

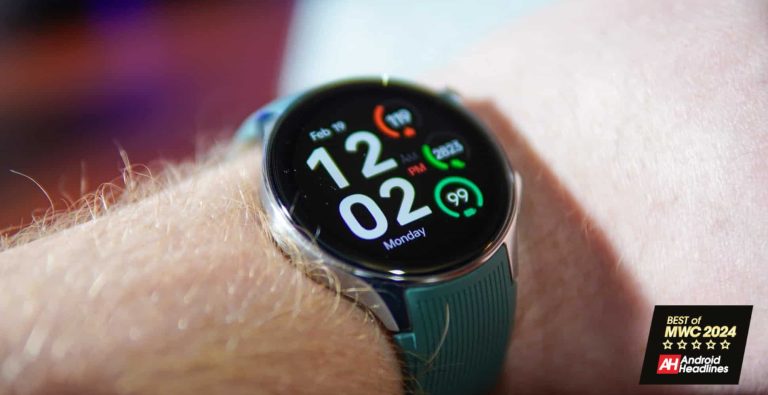
The OnePlus Watch 2 was OnePlus’s big announcement for this week making its debut at MWC 2024, and without mincing words, OnePlus has made a huge splash with this watch, and to our surprise, it might just be our new favorite. When OnePlus launched its original smartwatch, it was running on OnePlus’s own operating system, and compared to other options, it just wasn’t living up to what you’d expect from OnePlus. The company knows it missed the mark with the first model and went to work to improve things for the 2nd model.

There are so many improvements across the board, that the OnePlus Watch 2 is easily capable of becoming the best Wear OS watch out there for many consumers.

The battery life on the OnePlus Watch 2 is setting a new standard

I have no problem saying that the OnePlus Watch 2 will be the undisputed king of battery life when it comes to any Wear OS watch. Battery life has always been an issue with smartwatches in general and Wear OS has been among the worst. Although there have been some standouts ahead of the pack. OnePlus is turning that on its head by touting up to 100 hours of battery life on the OnePlus Watch 2 which is, quite honestly amazing. Now there are some tricks to this that allow for this to be possible. Part of it is on Google’s end with some optimizations it’s made to Wear OS. But the other more substantial part is on the OnePlus Watch 2’s hardware, as well as some software tweaks that OnePlus made.

All-in-all it equals out to a nearly full workweek of battery life on a single charge. In fact, in our review, we got almost five days out of it. If battery life is something you stress over but you don’t want to move off of Wear OS, then the OnePlus Watch 2 is the watch for you. Aside from the battery life, there are a lot of other niceties to capture your attention. Not the least of which is the design. This is a really good-looking smartwatch and it shows. There’s also a sapphire crystal display which means you don’t have to worry so much about scratches, scuffs, or the occasional ding against a counter or something.

That doesn’t mean you don’t need to take care of it still, but you won’t need to baby it. And in the end that’s all you really need. A smartwatch that can enhance your life without you needing to coddle the thing because you’re afraid it might break.

Charging at the speed of light

Other than battery life another complaint of smartwatches sometimes is how long it takes to charge them. OnePlus has consistently been one of the top contenders for fast-charging devices. Without fail, every year, it comes out with new products that charge a lot faster than most if not all of the competition. The OnePlus Watch 2 is no different. You can get to a full battery in about an hour which is lightning quick. In our personal testing, it was about 58 minutes from 4% to 100% and that’s so much faster than any other Wear OS watch out there.

Case in point, when the battery does finally die, just pop it on the charger before you start your day and it’ll be back up to 100% in no time. Then you’re good for almost another week. The watch also has a 5ATM rating and it’s IP68 water resistant. And the best part is that it’s not super expensive. At $299, this is a bargain.

[ad_2]

Source link

Gemini can now integrate with Google Calendar

0

[ad_1]

Slowly but surely, Gemini is working its way to becoming an actual assistant app to replace Google Assistant. So far, it’s been a pretty poor and rushed replacement, and this prompted many people to give the app a very low Google Play Store rating. However, it just scored a small victory. Gemini can now integrate with Google Calendar.

Using Google Assistant, you’re able to set reminders and access Google Calendar simply by voice. This came in handy when you just needed to quickly set a calendar event and be done with it. It’s just a testament to how well-integrated Google Assistant is with Android. Now, Gemini is playing catch-up while simultaneously trying to replace the Assistant.

Google acknowledges that it has a long way to go before Gemini can completely replace Assistant. It outlined a list of changes it needs to make ASAP if it wants Gemini to fill Google Assistant’s shoes, and it’s carving away at that list.

Gemini can now integrate with Google Calendar

Not too long ago, Gemini gained the ability to make tasks through Google Assistant. This was a step in the right direction and this new change adds more functionality to the chatbot. If you’re using Gemini as your phone’s default assistant, you can summon it and ask a question about your calendar. You can ask it questions like “Do I have any events coming up?” You could also ask it to show you your calendar. This is a great and easy way to get a glimpse at your upcoming events.

Along with that, you’re able to ask Gemini to create an event for you. Just say something like, “Add an event to my calendar.” At that point, it will go through the steps of asking you how you want to customize the event. When you’re all finished, the event will be added to your calendar, and you’ll call it a day.

[ad_2]

Source link

New Variant of AMOS Stealer Targets Safari Cookies and Crypto Wallets

0

[ad_1]

The new Atomic variant uses Python and Apple Script code to target browser and system files, obtain user account passwords, and identify sandbox or emulator execution.

Bitdefender researchers have discovered a new variant of the AMOS Stealer (or Atomic Stealer), one of the most prevalent threats for macOS users in the last year. According to Bitdefender, the new variant was discovered while revisiting old or new malware samples to improve detection capabilities for macOS cyber-security products.

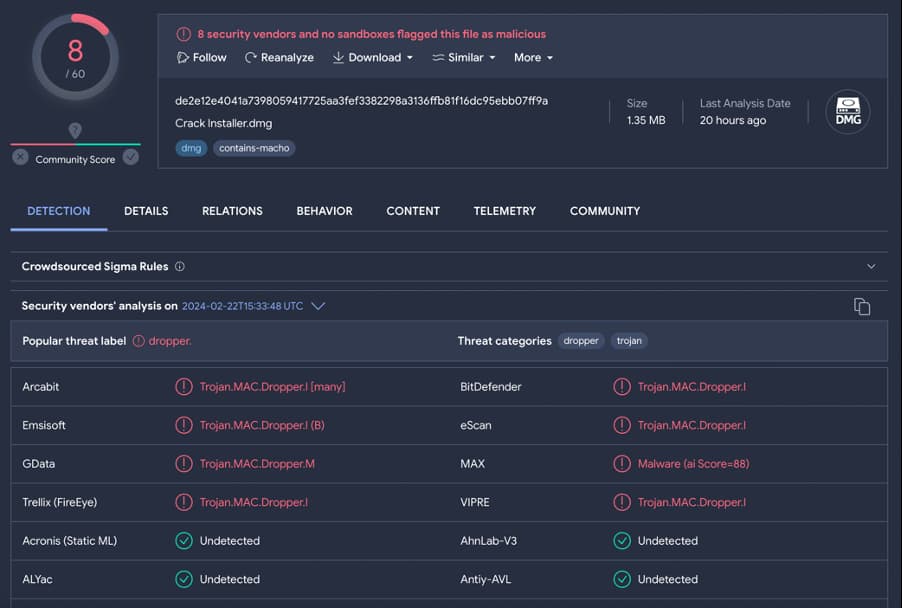
When researchers isolated several suspicious macOS disk image files, which were surprisingly small for their size (1.3 MB), they became suspicious of the emergence of a new variant of the AMOS Stealer.

New Variant of AMOS Stealer Targets Safari Cookies and Crypto Wallets
Screenshot from VirusTotal (Bitdefender)

The new variant combines functionalities of numerous malware families, including information stealers, keyloggers, and cryptocurrency mining tools, allowing it to steal sensitive data while its advanced stealth makes it harder for users to identify/remove the infection.

Further probing revealed that this variant shares similarities with the second variant of RustDoor. “Both seem to focus on collecting sensitive files from the victim’s computer, with the current one being a more developed version of the script used by RustDoor,” researchers noted.

However, the new variant has additional features. It collects the Cookies.binarycookies file, which stores Safari browser cookies, obtains files with targeted extensions from specific locations and uses the system_profiler utility to gather information about the compromised computer. 

The attackers aim to obtain hardware-related details, operating system versions and connected displays and graphic cards. They add sensitive information to the archive, including passwords, encryption keys, and certificates, indicating their growing interest in cryptocurrency platforms.

This version has an unusual technique of combining Python with Apple Scripting where the filegrabber() function executes a large block of Apple script using the osascript -e command. DMG files contain FAT binary and Mach-O files for Intel and ARM architectures, used by threat actors to steal data.

When opened, as noted by researchers in a blog post, the Crack Installer application prompts the user to open the file. The Python script collects sensitive data from multiple sources, including crypto-wallet extensions, browser data, and user account passwords.

The Chromium () function collects files from targeted Chromium-based browsers, including web data, login data, and cookies. It also targets cryptocurrency browser extensions and Mach-O binaries. The parseFF() function targets Firefox and collects files associated with all profiles.

Moreover, the script targets installed crypto wallets like Electrum, Coinomi, Exodus or Atomic. The collected data is stored in a ZIP archive, which is sent to a C2 server using a POST request. The archive structure is confirmed by the C2 server.

The variant is largely undetected at the moment. Bitdefender has released Indicators of Compromise to help organizations and practitioners detect and mitigate this threat.

  1. BlueNoroff APT Targeting macOS with ObjCShellz Malware
  2. Lazarus Group uses KandyKorn macOS malware for crypto theft
  3. Cracked macOS Software Laced with New Trojan Proxy Malware
  4. New macOS Backdoor Steals Data, Linked to Ransomware Gangs
  5. New Malware Turns Windows and macOS Devices into Proxy Nodes


[ad_2]

Source link

February update rolling out widely to the US Galaxy S22, S23 FE

0

[ad_1]

Samsung‘s most recent Fan Edition (FE) smartphone, the Galaxy S23 FE, is receiving the February 2024 security update in the US. The latest security patch is also rolling out to the factory-unlocked variants of the Galaxy S22 series. These phones have already picked up the new SMR (Security Maintenance Release) in most international markets.

Galaxy S23 FE receives Samsung’s February 2024 security update

Samsung started pushing the February 2024 update to the Galaxy S23 FE around two weeks ago. The company initially released the update for European users before gradually expanding the coverage to other regions. However, users in the US were kept waiting for the new SMR. The wait has finally ended, with Samsung covering both carrier-locked and unlocked units.

The latest update for the Galaxy S24 FE comes with the firmware build number S711USQU2BXBE for locked units and S711U1UES2BXB6 for unlocked ones. For the former group of devices, the rollout seems to be limited to the AT&T network. The remaining carriers should join the party in a few days. Samsung has released the new security patch widely on most carrier networks for the latter group.

Regardless of the build number or carrier variant, the update contains the same changelog. “The security of your device has been improved,” Samsung states in its release notes. This month’s security patch fixes 69 vulnerabilities combined across all Galaxy devices. These include eight vulnerabilities exclusive to Samsung products and three critical Android OS issues.

These security fixes are also rolling out to the unlocked variants of the Galaxy S22, Galaxy S22+, and Galaxy S22 Ultra in the US. The update comes with the build number S90*U1UES4DXA1. Their carrier-locked counterparts as well as international versions have already received the update. Once again, the changelog is the same globally. The update is all about the latest security patch with no additional changes.

One UI 6.1 is coming to these Galaxy devices soon

Samsung introduced an upgraded version of its Android-based One UI software with the Galaxy S24 series. Based on Android 14, One UI 6.1 comes with a plethora of on-device and cloud-based AI features. The company plans to push One UI 6.1 and these features to older flagship and mid-range models, starting with the Galaxy S23 series. The rollout is expected to begin soon. Lower-cost models may miss out on some features due to compatibility issues. You can check for new updates on your Samsung phone or tablet from the Settings app.

[ad_2]

Source link

Hackers Abuse Telegram API To Exfiltrate User Information

0

[ad_1]

Attackers have been using keywords like “remittance” and “receipts” to spread phishing scripts using Telegram to steal user data indiscriminately.

In the past, phishing script files were disseminated using various strategies and techniques, like asking users to log in before they can access protected files or pretending to be the Microsoft login page.

Hence, the most recent files are obfuscated to evade detection, in contrast to the phishing script files sent in the early days.

Phishing-Type Malware Using Telegram API

According to the AhnLab Security Intelligence Center (ASEC), the threat actor impersonates the Microsoft login page or requests a login for users to access protected files.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

Additionally, to steal the password in use, the threat actor asks users to input a password that is at least five characters long.

Phishing Page

“After entering a password of at least five characters, the malware sends the stolen information to threat actors via the Telegram API.

The transferred information consists of email addresses, passwords, IPs, and user ASEC researchers shared with Cyber Security News.

Email addresses, passwords, IP addresses, and user agents are among the data transmitted.

The token and Chat ID details are predefined to communicate with the threat actors.

Stealing User information

To hide the malicious activities from the user, the malware then reroutes visitors to the official Microsoft website.

Apart from the malware of the phishing type, researchers mention that the AgentTesla malware also utilized Telegram to obtain user data.

In September 2023, the ASEC researchers reported phishing script files that exploited Telegram to expose user data.

In that case, researchers discovered several phishing script files masquerading as PDF document viewer screens being sent as attachments to emails.

There has been an increase in the theft of user data using Telegram.

Furthermore, the development and dissemination of phishing websites is becoming increasingly sophisticated. 

Hence, users must therefore avoid visiting dubious websites and opening files from suspicious sources.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

How to Avoid Data Leaks

0

[ad_1]

The Internet offers a convenient platform for sharing data, but it also brings the risk of data leaks. A data leak occurs when sensitive information is accidentally exposed, differing from a data breach, which usually stems from a deliberate cyberattack.

To prevent data leaks, companies can implement secure practices to safeguard their information. Explore further to discover effective measures your organization can take to ensure data security.

Why is Data Leak Prevention Important?

Data leaks are a focus for cybercriminals. Many of them monitor accounts, waiting for a leak to occur. Accidental exposure can provide access to financial information, trade secrets, personal identification information, and private records.

When a malicious party accesses sensitive information, there’s no saying what they will do with it. They may visit dark web forums and put the information up for sale or publish it freely. Or they may publish stolen data on dark websites or ransomware blogs to make the information public.

What are Common Data Leak Causes?

Data leaks can happen for various reasons. Understanding common data leak causes can help address the issue. Here are some issues to be aware of:

  • Misconfigured software settings: Security settings that are either not implemented or deployed with errors can cause security gaps that leave data unprotected. 
  • Software vulnerabilities: Unpatched security makes it easy for sensitive data to slip through the cracks. 
  • Weak passwords: Weak passwords make private information vulnerable to cybercrime attacks.  Multi-factor authentication can keep systems protected. 
  • Insider threats: Excessive privileges increase the risk of internal threats. It’s scary to think about, but even a trusted employee can steal data from a company’s system. 
  • Social engineering: Social engineering is the use of deception or manipulation to coerce individuals into divulging confidential information. 
  • Physical theft: An increased focus on cybersecurity makes it difficult to account for devices being lost or stolen. Companies must keep hardware protected. 
  • Spear-phishing: Spear-phishing occurs when a cybercriminal sends out an email requesting financial or sensitive information. These emails often seem legitimate and innocent, but they can have serious implications if sensitive information is transmitted. 
  • Botnets: Botnets are a network of private computers infected with malicious software. They can take over your computer and access important data. 
  • Personal Mobile Devices: Employees’ mobile devices may store sensitive data that can be easily accessed by malicious users. 
  • Remote Work Environments: Remote work environments mean more data is sent over the internet increasing the risk that it will fall into the wrong hands. 

Best Practices for Avoiding Data Leaks

Evaluate Third-Party Risk

Companies risk data leaks when they pass sensitive information on to third-party vendors. Organizations can increase security by ensuring their vendors are compliant with regulatory standards like HIPAA, GDPR, and PCI-DSS. Risk questionnaires can be used to assess potential threats when partnering with new vendors. 

Expanding organizations may find it difficult to maintain risk management regulations for third-party companies that may also experience growth spurts. Scaling vendor risk management as a managed service could streamline the process. Companies can achieve this goal by leveraging automation and protecting their business if a data leak occurs.

Limit Access to Sensitive Data

Organizations must identify sensitive data and classify it with strict security policies. They should restrict privileges to ensure the data is accessed only by those who need it. 

Systems must be implemented to evaluate permissions and ensure access isn’t granted to unauthorized parties. The data should then be categorized into different levels of sensitivity. Only trusted staff members should have access to highly sensitive data. 

The technology may also identify malicious behaviour within the system. 

Enforce Network Access Control

Companies must monitor network access to protect data from unauthorized users. They must review the communication coming into the network to ensure it’s coming from trusted sources. They must integrate data leak prevention solutions to ensure information isn’t compromised when a leak occurs. 

A Network Access Control (NAC) solution may help organizations keep data safe. It denies access to noncompliant devices, places them in a quarantined area, or limits their privileges to prevent infections. 

Data Encryption

Data encryption is a valuable anti-data leak tool. It encrypts data so it can only be read by people with access privileges. Cybercriminals will be unable to decipher sensitive data. 

Portable encryption is recommended because it ensures that data will be automatically encrypted if it leaves the confines of your network. 

However, advanced cybercriminals may be able to translate data encryption. Therefore, it should be combined with other anti-leak strategies to ensure information remains protected. 

Secure Endpoints

Endpoints are physical devices that connect to a network. Examples include mobile devices, desktop computers, servers, embedded devices, IoT devices, and virtual machines. The increased adoption of remote work environments has made these endpoints harder to secure. 

Organizations can protect endpoints with extended endpoint security. Employees with company iPhones should use Security Recommendations which notify them when their information has been compromised by a data leak. 

Firewalls and VPNs also protect endpoints, but many cybercriminals have learned to bypass them. They should be combined with additional security measures for optimal efficiency. 

Utilize Data Loss Prevention (DLP) Software

Data loss prevention applies to data leak prevention. It ensures sensitive data is not lost, misused, or exposed to unauthorized parties. A DLP program performs the following functions:

  • Identifies Data: AI may be used to identify data and streamline processes. 
  • Secures Data: DLP software may be deployed at the end of the network to ensure data transfers align with secure data policies.  
  • Secures Endpoints: Endpoint DLP monitors real-time user behaviour to ensure transfers occur between authorized parties. 
  • Protect Archived Data: The software uses regulatory compliance, access control, and encryption to protect archived data. 
  • Monitors Active Data: DLP tools will monitor data and flag suspicious behaviour. 
  • Detects Data Leaks: Data leak technology will scan for data exposures for fast remediation if a breach occurs. 

Employee Awareness Training 

Employees must be aware of the best anti-leak practices, as they are often susceptible to social engineering tactics, such as falling for phishing emails and similar scams.

To prevent employee-related data leaks, organizations should incorporate cybersecurity training into their onboarding process and provide ongoing training to keep workers informed about the latest cybersecurity trends. This approach ensures that networks remain secure from the ground up.

While data leaks may not constitute a direct attack, they can be just as damaging when sensitive information falls into the wrong hands. Implementing employee training, Data Loss Prevention (DLP) software, data encryption, access control measures, secure endpoints, and mitigating third-party risks are crucial steps to keep your system protected.

Which strategies do you use to ensure your company is safe? 

  1. Exploring Data Privacy and Security in B2B Gaming Data
  2. Approaching Complex Data Security for Small Businesses
  3. Protecting Company Files: Secure Strategies for Data Safety
  4. LoanDepot Ransomware Attack – Data Breach; 17M Impacted
  5. Cyqur Launches Data Encryption, Fragmentation Web Extension


[ad_2]

Source link

Downloads for the YouTube Music web app are finally rolling out

0

[ad_1]

Downloading music is more of a necessity on the YouTube Music mobile app than it is on the web app. Be that as it may, YouTube has been working on rolling out downloads for the YouTube Music web app. After we got a bit of a leak last week, it appears that the feature is now starting to make its way to users.

The issue with rolling out downloads for the web app is the fact that it’s a bit tough to download files that are accessible to your web browser. Not only that, but people are more likely to be out and about with their phones than with their computers. So, downloads weren’t really as much a necessity for the web app as it is for the mobile app.

However, YouTube Music is rolling out downloads for the web app

At this point, we’re not quite certain about YouTube’s rollout pace for this feature. A user on Reddit posted some screenshots of their YouTube Music interface, and they show the feature in action. When you have a song or an album pulled up, you will see a new download button on the interface. It will be in between the three-dot menu and the Save to library button. When you click that button, you will see the button change to show a downloading animation. Also, you will see a download progress indicator at the bottom left corner of the screen.

Just like with any other streaming platform, YouTube Music will try to stream the content online. However, once it detects that you are not connected to the internet, it will switch to offline mode and access the downloaded files.

Also, After 30 days, YouTube Music will require an internet connection to check your subscription status. If it detects that you don’t have an active subscription, it will make those downloads unavailable. So, if you’re the kind of person who likes to download a bunch of music, right before your subscription ends, and keep your computer offline, you’ll only have one month of victory. Right now, we’re uncertain how widespread this rollout is, so you’ll have to keep an eye out for the download button to reach your web app.

[ad_2]

Source link

Micron unveils the world’s smallest UFS 4.0 storage chip

0

[ad_1]

Micron, the Idaho-based producer of storage and memory chips, has unveiled the world’s smallest UFS (Universal Flash Storage) package. Measuring just 9×13mm in dimension, it is an incredibly compact UFS 4.0 chip. The semiconductor company is currently sampling the new solution.

Micron promises faster AI performance with its compact UFS 4.0 chip

Unveiled at the Mobile World Congress (MWC) 2024, Micron’s compact UFS 4.0 storage chip is built on its advanced 232-layer 3D NAND memory. The company claims a sequential read speed of 4,300 MB/s and a sequential write speed of 4,000 MB/s. These speeds are twice as fast as the firm’s 176-layer UFS 3.1 NAND. The new chip is also 25% more power efficient than the previous-gen solution.

According to Micron, these improvements enable faster loading of large language models (LLMs) in generative AI applications. The company touts 40% faster loading for a smoother experience when initializing AI tools. “Micron UFS 4.0 raises the bar for mobile storage with enhanced performance, flexibility, and scalability to accelerate the rollout of generative AI-capable smartphones,” said Mark Montierth, a GM at Micron.

This isn’t the first UFS 4.0 solution from Micron. The American semiconductor firm debuted its next-gen storage chip last June. In its first attempt, the company matched Samsung’s first-gen UFS 4.0 chip in terms of size (11×13mm) while delivering faster speeds. Samsung promised a sequential read speed of 4,200 MB/s and a sequential write speed of 2,800 MB/s for its solution.

Micron hasn’t improved the speed with its latest offering but shrunk the size to save some space inside devices. The company believes this will allow manufacturers to provide larger batteries. “These significant space savings result in an optimal size for next-generation foldable and ultra-slim smartphone designs,” the firm said in a press release. Its enhanced power efficiency will further extend the battery life.

Micron’s UFS 4.0 storage chips also feature some proprietary tech for enhanced performance. High-Performance Mode or HPM optimizes performance during heavy usage. It allows the device to prioritize critical tasks over background tasks, resulting in an over 25% speed boost. One Button Refresh or OBR allows for 10% faster app launches by automatically cleaning and optimizing data.

The company is currently sampling the new storage chip

The world’s smallest UFS 4.0 storage chip will be available in 256GB, 512GB, and 1TB capacities (no UFS 4.0 for 128GB solutions yet). Micron is currently sampling the chip with its clients. It is unclear when the new solution will be available commercially. The company is aiming the chip at the next generation of flagship Android smartphones.

[ad_2]

Source link

Hackers Selling DCRat Malware Subscriptions For $5 on Telegram

0

[ad_1]

DCRat Malware

Researchers from ANY.RUN reported a new wave of DCRat malware, known for its wide array of harmful functions, selling the membership for the low cost of $5.

The detailed report covers the distribution, dynamic, and static analysis of DCRat, also known as Dark Crystal RAT, which is both a Remote Access Trojan (RAT) and an information stealer.

DCRat’s modular architecture allows for customization and mutation to bypass signature-based detection, making it a formidable tool for cybercriminals.

The malware’s low price point has made it accessible to many threat actors, from novices to organized groups.

You can analyze DCRat malware file, network, module, and registry activity with the ANY.RUN malware sandbox.

ANY.RUN is a cloud-based environment for analyzing Windows malware and Linux-based samples. Malware analysts, SOC, DFIR teams can safely examine threats, simulate different scenarios, and gain insights into malware behavior to improve cybersecurity strategies.

ANY.RUN also allows researchers to understand malware behavior, collect IOCs, and easily map malicious actions to TTPs—all in our interactive sandbox.

 The Threat Intelligence Lookup platform helps security researchers find relevant threat data from sandbox tasks of ANY.RUN.

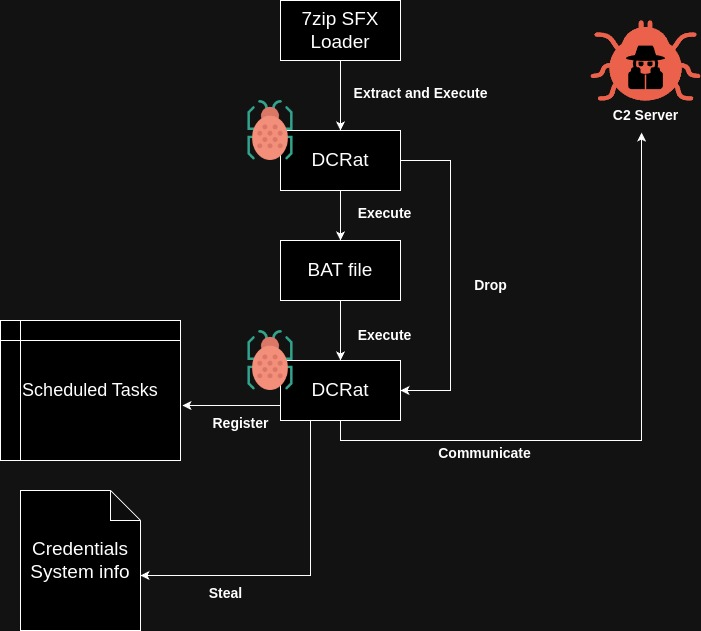
Infection Flow

ANY.RUN’s analysis reveals that DCRat is sold via a Telegram group, operating on a subscription model with prices ranging from $5 for two months to $39 for a lifetime subscription.

  • They do all communication through Telegram. 
  • They only accept crypto payments to burner wallets. 
  • They use crystalpay[.]io to further anonymize transactions. 
infection Flaw

The ANY.RUN Malware Trends Tracker ranks DCRat as the 9th most prevalent malware as of January 18, 2024, indicating its rising trajectory.

The malware is distributed through a Telegram bot, which also provides support and facilitates transactions through the crystalpay[.]io payment platform, demonstrating the DCRat team’s high level of operational security (OPSEC).

Document

Analyse Shopisticated Malware with ANY.RUN

More than 300,000 analysts use ANY.RUN is a malware analysis sandbox worldwide. Join the community to conduct in-depth investigations into the top threats and collect detailed reports on their behavior..

DCRat Malware Dynamic Analysis

The surface analysis of DCRat, identifying it as a password-protected Self-Extracting Archive (SFX) file, often used to evade detection.

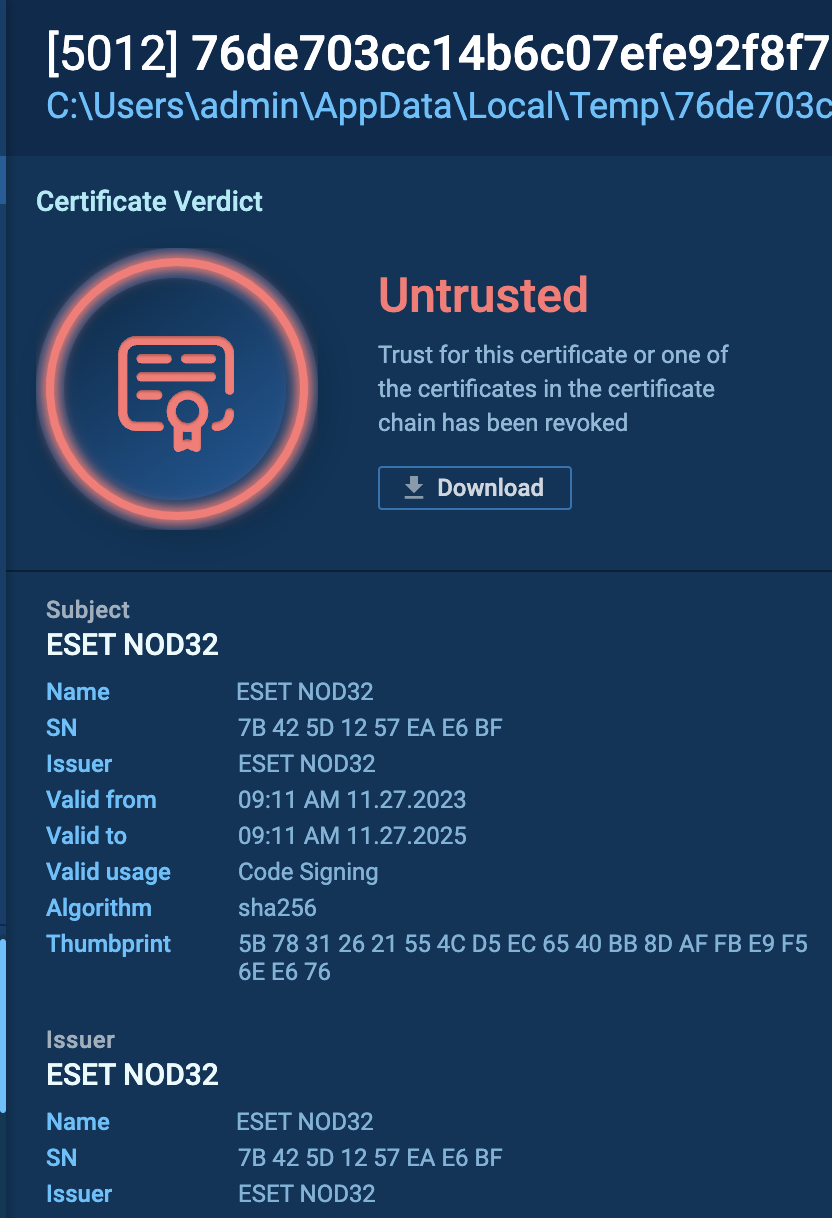
Dynamic analysis in ANY.RUN’s controlled environment revealed the malware’s behavior, including the execution of a digitally signed executable file disguised as a printer driver and the dropping of multiple executables to ensure persistence.

Static Analysis

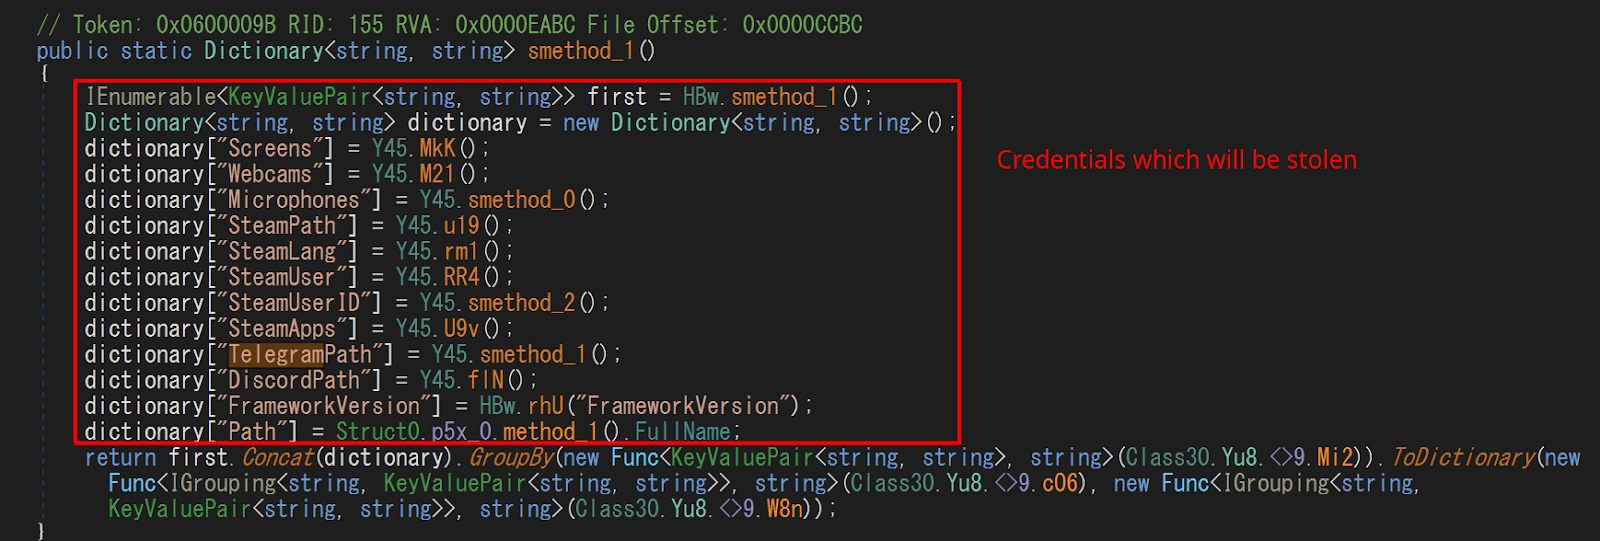
Static analysis provided insights into the malware’s functions, Indicators of Compromise (IOCs), and configuration details.

The analysis utilized tools such as Detect It Easy (DIE) and decompilers like dnSpy or ILSpy for .NET applications to deobfuscate the executable and understand the malware’s operational logic.

The ANY.RUN team also recommends using Flare FLOSS for extracting strings from binaries to identify hidden information.

Researchers also noted that the malware is stealing the following data.

  • Screen Capture 
  • Webcam 
  • Microphone 
  • Steam specific data 
  • Telegram specific data 
  • Discord specific data 
  • .NET specific data 

The analysis concludes with the mapping of DCRat’s tactics, techniques, and procedures (TTPs) to the MITRE ATT&CK framework, aiding SOC analysts in understanding the threat quickly. ANY.RUN’s service is invaluable for rapid threat identification and in-depth malware research.

ANY.RUN encourages cybersecurity professionals to access the full analysis on their platform to better understand DCRat’s capabilities and strengthen their cybersecurity posture.

About ANY.RUN

ANY.RUN is an interactive cybersecurity service that enables professionals to analyze malware and understand its behavior in a safe, controlled environment. The service is dedicated to providing comprehensive analysis tools to combat digital threats.

Trusted by over 400,000 security specialists, ANY.RUN empowers SOC and DFIR teams to investigate threats efficiently through its cloud-based malware sandbox.

[ad_2]

Source link