ZTE’s first flip smartphone is part of its 2024 lineup at MWC

0

[ad_1]

ZTE has come back to Mobile World Congress this week with a slate of new devices as part of its lineup for 2024, including the company’s first flip smartphone, which it says will be the “first flip phone for young people.” Called the nubia Flip 5G, it was designed to be the first flip phone for young people and to that end, it features a more affordable price tag and an “abundance of features and applications” that young people will enjoy using ZTE says.

ZTE is also announcing the nubia Z60 Ultra, a flagship device sporting an under-display camera, a massive 6,000mAh battery, and a powerful Snapdragon 8 Gen 3 mobile platform from Qualcomm. If you thought ZTE was done, though, you’d be wrong. Because ZTE has more phones to announce at MWC 2024. This includes the nubia Focus 5G, as well as the nubia Neo 2 5G aimed at mobile gamers. It’s a varied lineup with something for everyone.

The nubia Flip 5G is the first flip smartphone from ZTE

Flip smartphones are not a new device category for the industry but they certainly aren’t common. In fact, there are actually not very many of them out there. The most recognizable flip smartphones are without a doubt the Galaxy Z Flip series and the most recent Moto Razr. There’s also the Oppo Find N3. Beyond that, however, you’d be hard-pressed to find a flip smartphone from most brands. Another thing to consider is that all of those previously mentioned options are considerably expensive. ZTE says the nubia Flip 5G will be more affordable, stating that “consumers will be surprised by the price.”

ZTE also highlights that it’ll have an abundance of apps that can be used on the external display. The phone is said to have a high-strength hinge with a 6.9-inch 120Hz display when unfolded. One of the key factors that ZTE seems keen to highlight is that the phone opens “wrinkleless.” What ZTE is basically saying is that you shouldn’t see any creases on the display when the phone is fully unfolded. The phone also has a 50MP main camera, a 4,310mAh battery, and it’s powered by a Snapdragon 7 Gen 1 mobile platform. In terms of cost, ZTE says it’ll start at $599 USD. Which makes this option from ZTE quite possibly, the most affordable folding flip smartphone on the market.

An affordable gaming phone for all

Gaming phones are still a niche product category when it comes to smartphones. They’ve certainly grown, thanks to the steadfast and headlong attitudes of brands like ASUS and RedMagic with a passion and drive for mobile gaming. But those phones are not necessarily affordable. RedMagic’s most recent offering, the 9 Pro, starts at $649. That isn’t terrible, but it doesn’t hold a candle to the nubia Neo 2 5G that ZTE is releasing this year. ZTE is also expanding the device to other markets where it wasn’t previously available.

With its first model the nubia Neo in 2023, the phone was released in Southeast Asia, the Middle East, and Europe. The Neo 2 5G will expand to the US, with a price point starting at an incredibly low $199 USD. It features shoulder triggers for that controller-like feel when gaming in landscape mode. As well as a 120Hz display at 6.72 inches and a large battery capacity of 6,000mAh. Furthermore, it has 33W fast charging. It’s considerably gamer-focused. Promoting long-lasting battery life for longer game sessions and a quick charge capability when you need to top up in a hurry. The 120Hz display won’t hurt either. As your games should look nice and smooth.

That being said, ZTE doesn’t mention anything about some of the other specs. Such as the chipset, RAM, or storage. With a starting price point of $199 USD though, it’s not likely to be among the most powerful of devices. That doesn’t mean it won’t be capable, however. Also worth noting is that ZTE says the price will change depending on the market and specific specs.

Shift your focus to better phone photography

Some people buy phones for the superior camera while others look for a device that prioritizes performance. If you’re the former type of consumer, then ZTE has your number with the nubia Focus 5G series. The nubia Focus 5G is solely focused on a great smartphone camera experience because, after all, the best camera is the one you have on you. And in most cases, that’s probably going to be the one on your phone because it fits in your pocket.

The core of this experience is the 108MP dual camera system on the nubia Focus Pro 5G. There’s also a non-pro model. Both versions come with a 5,000mAh battery and a 120Hz display. Although each one’s display is slightly different. The nubia Focus 5G comes with a 6.6-inch display while the Pro model bumps it up to 6.72 inches. These phones keep with the affordable theme coming in at a starting cost of $199 USD. ZTE has yet to announce information regarding the release date and availability of these devices.

[ad_2]

Source link
Zyxel Firewall Flaw Let Attackers Execute Remote Code

0

[ad_1]

Four new vulnerabilities have been discovered in some of the Zyxel Firewall and access point (AP) versions that are associated with Denial of Service, OS Command Injection, and Remote code execution.

These vulnerabilities have been assigned with CVE-2023-6397, CVE-2023-6398, CVE-2023-6399, and CVE-2023-6764.

The severity of these vulnerabilities ranges between 6.5 (Medium) and 8.1 (High). However, Zyxel networks have fixed these vulnerabilities, and a security advisory has been released to address these vulnerabilities.

Zyxel Firewall Flaw

CVE-2023-6397: Null Pointer Dereference vulnerability in Zyxel

This vulnerability could allow a LAN-based threat actor to cause a denial-of-service condition by downloading a crafted RAR compressed file onto a LAN-side host if the firewall has “Anti-Malware” feature enabled.

The severity for this vulnerability has been given as 6.5 (Medium).

CVE-2023-6398: Post-authentication Command Injection vulnerability

This vulnerability exists in the file upload binary in Zyxel ATP series devices that could allow an authentication threat actor to execute operating system commands on the affected device via FTP with administrative privileges.

The severity for this vulnerability has been given as 7.2 (High).

CVE-2023-6399: Format String Vulnerability in Zyxel

This vulnerability allows an authenticated IPSec VPN user to perform a denial of service condition against the deviceid daemon.

Successful exploitation of this vulnerability involves sending a crafted hostname to an affected device if the device has the “Device Insight” feature enabled.

The severity for this vulnerability has been given as 5.7 (Medium).

CVE-2023-6764: Format String Vulnerability in Zyxel leading to Unauthenticated RCE

This vulnerability exists in one of the functions of the IPSec VPN feature that could allow a threat actor to achieve unauthenticated remote code execution on the affected device by sending a sequence of specially crafted payloads with an invalid pointer. 

However, this attack requires a detailed knowledge of the affected device’s memory layout and configuration. The severity for this vulnerability has been given as 8.1 (High).

Affected Products And Versions

Users of these products are recommended to upgrade to the latest versions in order to prevent these vulnerabilities from getting exploited by threat actors.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

Game Changer for Mobile Video with Sony Imaging Chip

0

[ad_1]

TECNO isn’t done with MWC Barcelona announcements this week. Today, it announced its new PolarAce Imaging System, which it built with Sony’s own imaging chipset. It will debut on the CAMON 30 Premier 5G, which is set to debut in the second quarter of 2024.

The company claims that this new imaging system is “bringing a new pinnacle of mobile video imaging to users around the world.”

“Our commitment and goal has always been to deliver the best mobile imaging experience to TECNO users around the world to meet diverse imaging needs,” said Jack Guo, General Manager of TECNO. “Previously, we have revolutionized smartphone imaging with innovations such as the advanced RGBW Ultra-Sensitive Sensor and the world’s first retractable portrait lens. PolarAce, our first imaging system with an independent imaging chip, leverages our partnership with Sony to signal a new era of extraordinary smartphone video imaging.”

TECNO and Sony worked together to build this imaging system, using the CXD5622GG Sony imaging chip, Sony’s LYTIA components, and also using TECNO’s Universal Tone multi-skin tone imaging technology and its AI imaging technologies.

TECNO wanted to redefine the mobile video experience

Let’s face it: these days, the camera experiences on our phones are pretty impressive. But there is still room for improvement, and TECNO saw a way for even more outstanding results. One of the examples the company uses is the computational power of traditional systems on chips, which is no longer adequate to address user needs. Other pain points that consumers experience include night scene video capture, full-scene HDR shooting, and overall video smoothness.

Thanks to the Sony CXD5622GG independent imaging chip, TECNO was able to build PolarAce, and it can deliver industry-first and industry-leading technologies to achieve a higher level of performance and quality for mobile imaging. Making it easier than ever to be a content creator with just your phone.

Another pain point that consumers experience, especially those with darker complections, is skin tone. TECNO aims to solve that with PolarAce, which has an independent imaging chip that can enhance the incredible performance of TECNO’s new Universal Tone technology. The company first debuted this in October 2023, and it is the industry’s most advanced AI-powered multi-skin tone imaging technology. It was developed to achieve more accurate skin tone capture based on unbiased data.

Of course, AI is involved here too. TECNO is embracing AI to boost the ease and enjoyment of the camera on its new CAMON 30 Premier 5G. It has been enhanced by AI-powered functionalities that make imaging even more impactful and enjoyable. It includes the AIGC Portrait Capture, which allows users to generate a vast array of portrait disguises, from wedding dresses to cartoon dolls, graduation attire, and more. There’s also One Click Erase, which uses AI technology to enable the one-click removal of obstacles and clearing of passersby.

TECNO PolarAce Daylight HDR Effect Large

PolarAce will debut first in the CAMON 30 Premier 5G

As mentioned already, PolarAce will debut in the upcoming CAMON 30 Premier 5G smartphone from TECNO. It’s slated to be released in the second quarter (between April and the end of June). TECNO is releasing some info about this phone now, but not all of the details.

The phone will come with a 70mm golden portrait focal length periscope lens; this is going to allow for some incredible macro shots, as well as being able to use up to 60x hybrid zoom. By using a portrait lens, TECNO is able to ensure less barrel distortion and more convenient framing, and unlike traditional portrait lenses, enables the full use of the sensor in night shots, providing better noise control and clarity.

It’ll also have the industry’s first 4K 30fps full-scene AI NR HDR Video along with a 50-megapixel front-facing camera, which uses eye tracking to take the perfect selfie every time.

This is all powered by the MediaTek Dimensity 8200 Ultimate 5G chipset, along with the new Sony Imaging Chip that’s being used inside PolarAce.  And finally, it’ll have a 1.5k resolution LTPO AMOLED display with 1400 nits peak brightness.

We’ll learn more about the CAMON 30 Premier 5G in the coming months. But it is shaping up to be a pretty impressive phone and camera so far.


[ad_2]

Source link

Meta under fire after investigation into “child influencer” accounts

0

[ad_1]

Meta and its subset platforms have long been accused of knowingly compromising children and letting them use the platform without age verification. But a new report by The New York Times and The Wall Street Journal is shedding light on the hidden aspects of “child influencers” on Instagram and Facebook, revealing how parents behind these accounts are sexually exploiting their children.

While these platforms apparently do not let underage children in or limit their access to sensitive content, they knowingly let parents run accounts for children and sell sexual materials of their kids to users, most likely pedophiles lurking online.

The materials include photos of children, chat sessions with them, and used clothes and leotards. Even worse, some parents reportedly forced children to interact with sexual messages sent by some followers. Meta has not yet commented on the matter.

Meta comes under fire for “knowingly” letting parents post explicit content about their children and sexually exploit them

The content produced by such parents allegedly came under the radar of Meta staff. And they were aware that some parents are creating content of their children that’s attractive to pedophiles. The parents running those children’s accounts even had the chance to use Meta’s paid promotion tools to expand their content’s reach. As per an internal survey conducted by Meta in 2020, over 500,000 child Instagram accounts had “inappropriate” interactions daily.

As the reports read, some child influencers on Instagram make $3,000 per post. This allows parents to make even six-figure incomes out of their children’s content. Meanwhile, such accounts attract a large number of male followers, and a considerable number of them could happen to be pedophiles. Among the 5,000 examined accounts, roughly 32 million male users were found.

Meta staff suggested the company force those child accounts to register for monitoring or ban their subscription. However, those suggestions were all rejected by the firm. Meta instead developed a system to prevent potential pedophiles from subscribing to children’s accounts. That system could be unreliable, of course.

The New York Times also criticized Meta’s content moderation attempts. The outlet reported that the tech firm only took action against 1 out of 50 reported content in an eight-month period.

[ad_2]

Source link

Google Chat adds helpful feature to help you pinpoint conversations relevant to you

0

[ad_1]

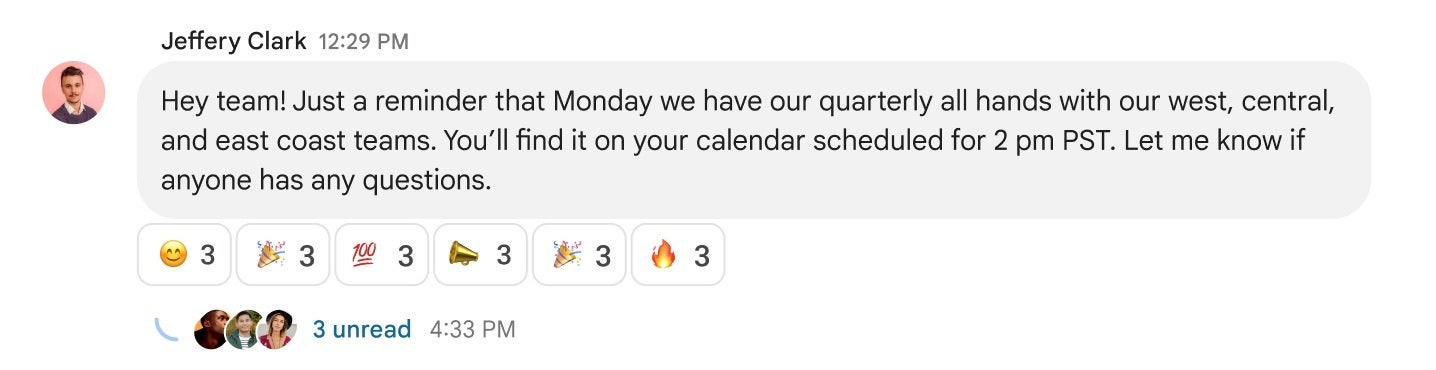
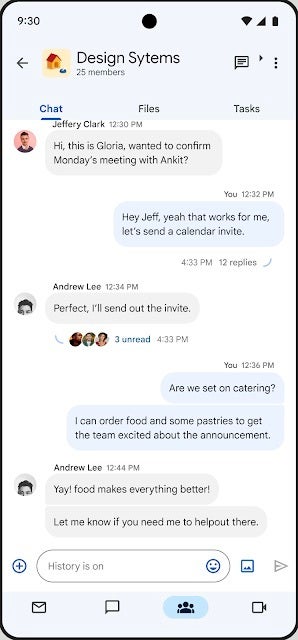
Google Chat is launching a new update that will make it even easier to navigate conversations within its in-line threaded spaces. Following last year’s transition to in-line threading, the latest update continues to improve on that functionality in order to boost productivity and efficiency for its users.With multiple threads running across different spaces, it can be time-consuming to figure out which messages need your immediate attention. The latest update from Google Chat makes it easier to keep track of conversations by showing participant avatars alongside unread threads in the conversation view.

This feature allows you to quickly identify the participants in the conversation and determine if their comments are pertinent to you. You can now efficiently prioritize important threads without having to click on them for additional details.


Google Chat’s new in-line participant avatars for unread threads both on the web and mobile

Google states that it recognizes that dealing with numerous threads across multiple spaces can be overwhelming and that this feature was introduced in order to give you more context upfront. The goal is that it will make it easier for you to prioritize and stay on top of the conversations that matter the most to you. This will ultimately help you stay organized and focused on what’s important.

This feature is rolling out automatically and gradually for up to two weeks, starting today. For all Google Workspace users, including those with free personal Google accounts, it will be by default enabled on the web, Android, and iOS.

Google has been steadily introducing improvements to Chat as it continues to compete with other established messaging platforms, such as Slack and Microsoft Teams, and aims to make Chat a more attractive option for businesses looking to improve collaboration and efficiency within their teams. The company hopes that this new feature will enhance productivity and streamline communication for users across all platforms.

[ad_2]

Source link

Abyss Locker Attacks Microsoft Windows and Linux Users

0

[ad_1]

FortiGuard Labs has released a report detailing the emergence and impact of the Abyss Locker ransomware, which has been targeting Microsoft Windows and Linux platforms.

Abyss Locker, believed to be based on the HelloKitty ransomware source code, has been stealing and encrypting victims’ files, demanding ransom for file decryption, and preventing the release of stolen data.

The Abyss Locker ransomware’s wallpaper

The severity level of this ransomware is classified as high. The first Abyss Locker sample was detected in July 2023, but the ransomware’s origins may date even further.

The Windows version of Abyss Locker was discovered in January 2024, with a second version shortly after. The Linux variant, which targets VMware ESXi systems, has also been identified.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

Attack Method

The Windows version of Abyss Locker performs several actions to ensure the successful encryption of files. It deletes Volume Shadow Copies and system backups using commands like vssadmin.exe delete shadows /all /quiet and wmic SHADOWCOPY DELETE.

It also sets the boot status policy to disable automatic repair and ignore all boot failures.

The ransomware encrypts files and changes the file extension to “.abyss” or a random five-letter extension for the version 1 variant.

A ransom note titled “WhatHappened.txt” is dropped, and the desktop wallpaper is replaced with a message demanding a ransom.

The Linux version of Abyss Locker uses the esxcli command-line tool to manage VMware ESXi systems. It attempts to gracefully shut down running VMs before encrypting files with a “.crypt” extension.

A ransom note with the “.README_TO_RESTORE” extension is created for each encrypted file.

Both versions of the ransomware avoid encrypting specific file extensions and directories to maintain the system’s operability and ensure the victim can communicate with the attackers for ransom negotiation, reads Fortinet report.

Infection Vector

The infection vector for Abyss Locker is not specified, but it is likely similar to other ransomware groups.

Abyss Locker ransomware’s ransom negotiation site

The ransomware samples have been submitted from various regions, indicating a widespread attack.

While no current data leak site exposes victims’ names, a ransom negotiation site on TOR is available. The ransom demands vary, with higher amounts typically set for consumers.

The Abyss Locker ransomware poses a significant threat to Windows and Linux users, particularly those utilizing VMware ESXi systems.

IOCs

Abyss Locker Ransomware File IOCs

SHA2 Note
72310e31280b7e90ebc9a32cb33674060a3587663c0334daef76c2ae2cc2a462 Abyss Locker v2 (Linux)
3fd080ef4cc5fbf8bf0e8736af00af973d5e41c105b4cd69522a0a3c34c96b6d Abyss Locker v2 (Windows)
9243bdcbe30fbd430a841a623e9e1bcc894e4fdc136d46e702a94dad4b10dfdc Abyss Locker v1 (Windows)
0763e887924f6c7afad58e7675ecfe34ab615f4bd8f569759b1c33f0b6d08c64 Abyss Locker v1 (Windows)
dee2af08e1f5bb89e7bad79fae5c39c71ff089083d65da1c03c7a4c051fabae0 Abyss Locker v1 (Windows)
e6537d30d66727c5a306dc291f02ceb9d2b48bffe89dd5eff7aa2d22e28b6d7c Abyss Locker v1 (Windows)
1d04d9a8eeed0e1371afed06dcc7300c7b8ca341fe2d4d777191a26dabac3596 Abyss Locker v1 (Windows)
1a31b8e23ccc7933c442d88523210c89cebd2c199d9ebb88b3d16eacbefe4120 Abyss Locker v1 (Windows)
25ce2fec4cd164a93dee5d00ab547ebe47a4b713cced567ab9aca4a7080afcb7 Abyss Locker v1 (Windows)
b524773160f3cb3bfb96e7704ef31a986a179395d40a578edce8257862cafe5f Abyss Locker v1 (Windows)
362a16c5e86f13700bdf2d58f6c0ab26e289b6a5c10ad2769f3412ec0b2da711 Abyss Locker v1 (Windows)
e5417c7a24aa6f952170e9dfcfdf044c2a7259a03a7683c3ddb72512ad0cd5c7 Abyss Locker v1 (Windows)
056220ff4204783d8cc8e596b3fc463a2e6b130db08ec923f17c9a78aa2032da Abyss Locker v1 (Windows)
877c8a1c391e21727b2cdb2f87c7b0b37fb7be1d8dd2d941f5c20b30eb65ee97 Abyss Locker v1 (Windows)
2e42b9ded573e97c095e45dad0bdd2a2d6a0a99e4f7242695054217e2bba6829 Abyss Locker v1 (Windows)

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link

INTMAX Launches Plasma Next to Scale Ethereum with Stateless Layer

0

[ad_1]

INTMAX, an innovative Layer 2 zkRollup that uses stateless architecture, has officially launched Plasma Next on the mainnet α (Alpha). INTMAX Co-founder and long-time Plasma researcher Leona Hioki unveiled it at ETH Denver. Based on the foundational principles of the Plasma framework, it scales with a constant cost per block regardless of the number of users, and achieves the scalability that the original Plasma aimed for while retaining the same security assumptions as zkRollups.

Plasma Next represents a paradigm shift in how blockchain networks can achieve scalability without compromising on decentralization. By leveraging the power of bulk-token-transfer and Merkle Trees, and integrating ZKP-TLC for conditional payments, Plasma Next introduces a system with the constant state growth per block. This innovative approach eliminates the need for users to provide individual liquidity or remain constantly online, thereby enhancing the user experience and network efficiency.

INTMAX Co-founder Leona Hioki said, “INTMAX goes beyond just presenting theoretical or conceptual papers. It includes the release of code and the network as well. Made available under an open-source license, it allows anyone to fork the code and launch the network.”

One of the most important parts of Plasma Next is its stateless architecture which, according to a16z researchers, is challenging to achieve because validators would need to store only a minimal, constant-size state. Despite significant research and efforts to reduce the storage burden for validators, a16z concludes that a completely stateless blockchain is impractical. However, Plasma Next can scale at a fixed cost per block, regardless of the number of users. The solution theoretically becomes a pseudo solution to the impossibility of statelessness, as proven by a16z.

Stateless solutions are where instead of nodes or validators holding the data, users manage their own data. While the idea of users managing their own data may sound complicated, most of it would be automated along with encrypted backups.

Plasma, a once-prominent Ethereum layer-2 scaling solution conceptualized by Vitalik Buterin and Joseph Poon in 2017, was intended to help bring Visa-level transaction volumes to Ethereum. Plasma networks allow all data and computation, except for deposits, withdrawals and Merkle roots, to be kept off-chain. This opens the door to very large scalability gains that are not bottlenecked by on-chain data availability.

However, Plasma had significant issues with user experience and online requirements such as:

  1. Users had to wait an entire challenge period before withdrawing
  2. Users had to monitor transactions on the Plasma chain

For these reasons, Plasma had been superseded by Rollups. The newly launched Plasma Next is a hybrid between Plasma and Rollups, combining the strengths of both to enhance security and scalability. It incorporates sophisticated zero-knowledge proofs (ZKPs) to ensure transactions are processed with unparalleled privacy and security.

Plasma Next represents a groundbreaking evolution, promising to redefine blockchain scalability and privacy for the digital age. By addressing the need for constant online presence—a significant barrier to user adoption—Plasma Next marks a significant leap forward. It enables constant state growth per block without requiring individual liquidity preparations, thereby enhancing on-chain privacy and simplifying blockchain transactions.

About INTMAX

INTMAX is the Stateless Ethereum Layer built for mass adoption. It is an innovative Layer 2 zkRollup that uses stateless architecture to offer a highly efficient, secure, and scalable solution for blockchain applications. INTMAX provides a ready-to-use solution to empower any applications and services with instant, the most secure, and near-zero cost crypto transactions.

Contact: Sergei Medvedev, [email protected]


[ad_2]

Source link

Infinix shows off its color-changing phone concept at MWC

0

[ad_1]

The Mobile World Congress (MWC) is going on right now, and some of our favorite brands but showing off the latest and greatest devices, technology, and concepts. Infinix is a brand it’s not known by too many people, but it made an appearance at the show. According to a new report, Infinix showed off its color-changing concept phone at MWC. And, looks pretty cool.

Not too many people know about Infinix in the West, but it definitely deserves more recognition. The company made the Infinix Note 30 Pro, a very well-reviewed device that we had the honor of reviewing last year. You can check out our Infinix Note 30 Pro review if you want to see why it gained a five-star score.

Infinix shows off its color-changing phone concept at MWC, and it looks pretty cool

Back in 2021, Infinix gave us a look at its color-changing phone concept, and it definitely caught our attention. It was a phone with a monochromatic display on the back. The display was an E-Ink display that could display different patterns.

This time around, Infinix brought us much the same thing; however, it decided to add color. Looking at the demonstration below, we see the back divided into distinct rectangular sections. Each section looks like a giant pixel and can be triggered independently. 

Because of this, the phone can generate patterns on the back. With as large as these sections are, you couldn’t realistically expect them to form a picture. However, they appear to just be a way to decorate the back of the phone. Say, you want to have a blue device, well, you could change the back panel to blue. If you change your mind and want to switch to red, you could do so.

Since we’re only looking at a concept phone in the video above, it’s not reflective of any final product that Infinix could produce. In the video, we see a diamond pattern in the middle that does not change with the rest of the colors. That section is actually fixed and does not change.

If Infinix does pursue an actual product with this technology, we could probably expect it in the next couple of years.

[ad_2]

Source link

Infinix unveils CoolMax tech for gaming phones, could debut with GT Ultra

0

[ad_1]

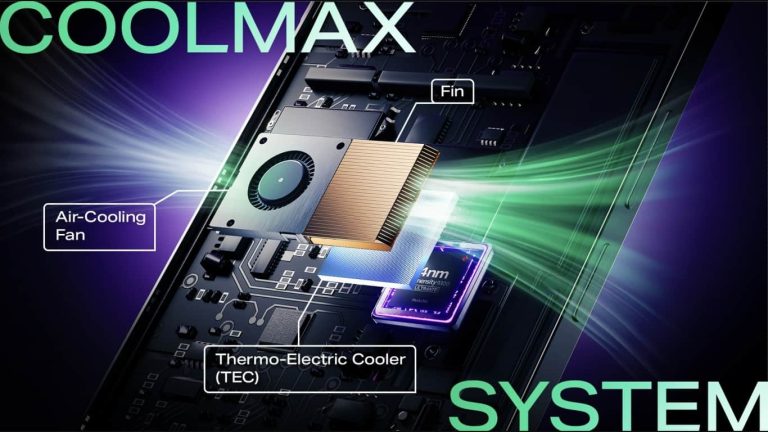
At the ongoing MWC 2024, Infinix has introduced its new flagship cooling technology called CoolMax. Designed specially for high-end gaming smartphones, the brand’s new tech claims to reduce temperature by over 10 degrees Celsius. In addition, the company has also revealed plans to launch its first dual-core flagship gaming smartphone this year. The handset in question is expected to be called the Infinix GT Ultra and could utilize the new CoolMax cooling technology.

CoolMax tech is touted to reduce temperatures by 10 degrees Celsius

Infinix’s CoolMax cooling technology utilizes Thermal-Electric Cooling and the Peltier effect to reduce the heating on gaming smartphones. The tech integrates both a cooling fan and thermoelectric cooling in a phone to achieve this feat. Both the Thermal-Electric Cooling and Peltier effect tech dynamic duo work together to keep the SoC temperature in check. Notably, the brand claims this cooling approach is capable of slashing temperatures by up to 10 degrees Celsius.

Furthermore, Infinix’s CoolMax cooling technology works in tandem with its AI algorithm. The AI algorithm dynamically adjusts large cores for heavy tasks and switches to the smaller/medium cores for lighter operations.

“This AI-driven optimization ensures the chipset operates at peak efficiency without constantly running at maximum performance, leading to reduced heat generation and lower temperature levels. The integration of AI not only enhances gaming experiences but also contributes to energy savings and effective thermal management”, stated the brand in the press release.

Infinix’s gaming phone with CoolMax tech and Dimensity 9300 SoC achieves an AnTuTu benchmark score of over 2 million

Infinix said that it tested the CoolMax tech on a concept gaming smartphone powered by the MediaTek Dimensity 9300 SoC. The device managed to achieve a whopping AnTuTu benchmark score of over 2 million points, 22,156,639 to be precise. Infinix says that it pulled off this major score thanks to its CoolMax cooling system.

Infinix Coolmax concept phone antutu score

The concept gaming phone also flaunts a Pixelworks visual processor, which works alongside the Immortalis-G720 GPU to amplify frames. Notably, this device is capable of offering 180Hz at FHD+ resolution and 144Hz at QHD+.

Infinix is likely to offer its upcoming gaming smartphone with the Dimensity 9300 SoC, CoolMax tech, G720 GPU, and AI enhancements. While it’s not officially revealed, the handset could be called the Infinix GT Ultra. We will know for sure in the near future, so stay tuned for regular updates.

[ad_2]

Source link
14-Year-Old CMS Editor Flaw Exploited to Hack Govt & Edu Sites

0

[ad_1]

Hackers have exploited a vulnerability in a 14-year-old Content Management System (CMS) editor, FCKeditor, to launch SEO poisoning attacks against government and educational websites worldwide.

This campaign has compromised numerous sites, redirecting unsuspecting users to malicious or scam websites through open redirects and poisoned search results.

Open redirects are a critical flaw where websites redirect users to external URLs without proper validation, making them a prime target for cybercriminals.

These redirects are particularly dangerous because they originate from legitimate domains, allowing attackers to bypass security filters and trick users into visiting malicious sites.

This technique has been effectively used to perform phishing attacks, distribute malware, and scam users while maintaining the appearance of legitimacy.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

FCKeditor: The Target of Choice

The focal point of this campaign is the outdated FCKeditor plugin, a web text editor popular for editing HTML content directly within web pages.

Despite being rebranded as CKEditor in 2009 with significant improvements, many sites continue to use the deprecated version, especially in the education and government sectors.

Cybersecurity researcher @g0njxa uncovered the campaign after noticing Google Search results for ‘Free V Bucks’ generators hosted on university sites, revealing the extent of the exploitation.

Malicious Google Search results
Malicious Google Search results 

Educational and Government Sites Compromised

The campaign has not spared prestigious institutions and government entities. Among the affected are MIT, Columbia University, Universitat de Barcelona, Auburn University, University of Washington, Purdue, Tulane, Universidad Central del Ecuador, and the University of Hawaiʻi.

Government and corporate sites, including those belonging to Virginia, Austin, Texas, Spain, and Yellow Pages Canada, have also been targeted, utilizing a combination of static HTML pages and redirects to malicious sites.

In SEO poisoning, attackers manipulate search engine results to promote malicious websites.

By leveraging the trust and authority of compromised domains, these actors can poison search engine results, leading unsuspecting users to scam sites, fake news articles, phishing pages, and malicious browser extensions.

This not only endangers users but also tarnishes the reputation of the compromised sites.

FCKeditor Deprecated

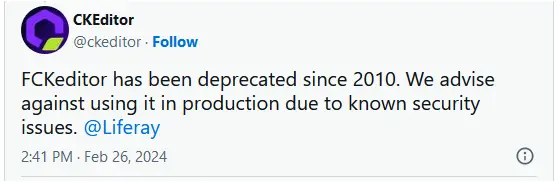
The software maker has responded to the open redirects campaign, emphasizing that FCKeditor has been deprecated since 2010 and should no longer be in use.

However, the persistence of this outdated software on critical sites highlights the broader issue of legacy systems and their vulnerabilities.

It’s a stark reminder for organizations to update and patch their systems to protect against such exploits.

The software maker responded to the open redirects campaign report on X, saying that FCKeditor has been deprecated since 2010 and nobody should be using it anymore.
The software maker responded to the open redirects campaign report on X, saying that FCKeditor has been deprecated since 2010 and nobody should use it anymore.

This campaign underscores the importance of maintaining up-to-date software and the need for vigilance against sophisticated cyber threats.

As attackers continue to exploit vulnerabilities in outdated systems, website administrators and users are responsible for ensuring the security of their digital environments.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]

Source link