AT&T Outage Disrupts Service for Millions of Users Across US

0
[ad_1]

You are not alone, an AT&T outage is happening across the United States, and the company is working to bring back service to normal.

Millions of AT&T customers across the United States woke up to widespread service disruptions on Thursday, February 22nd, 2024. The outage, which began early in the morning, has impacted mobile phone service, leaving users unable to make and receive calls, text messages, and access data.

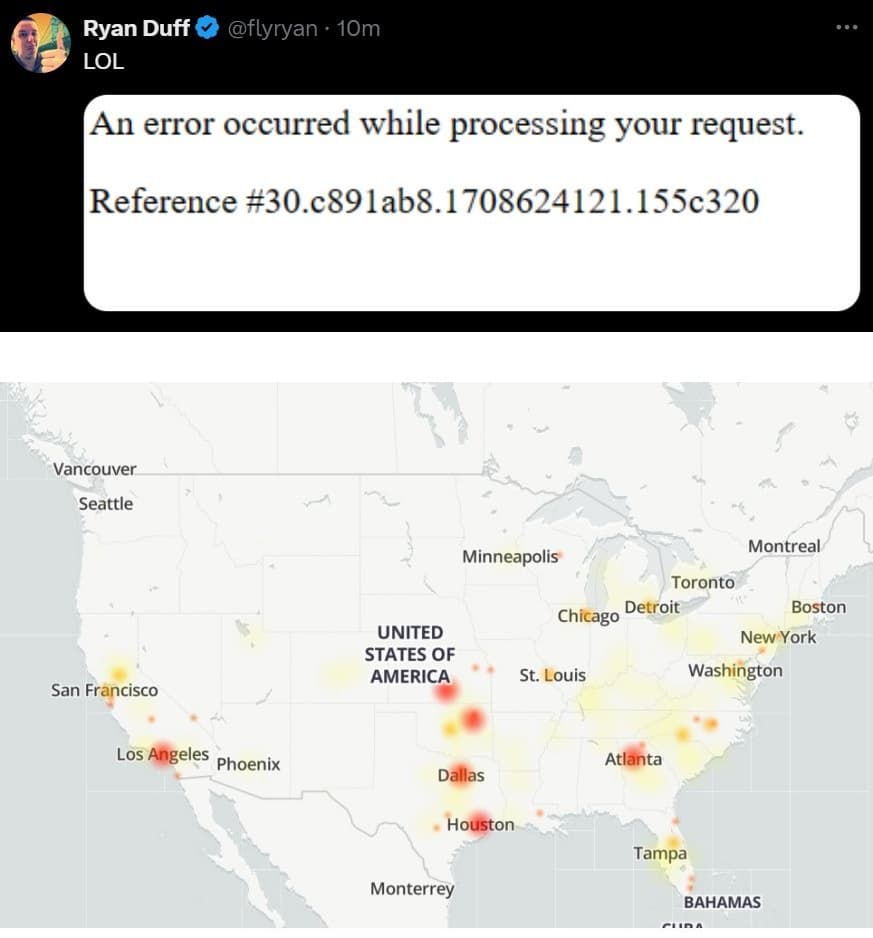
Reports from users and outage tracking websites like Downdetector indicate the issue is nationwide, affecting major cities like New York, Los Angeles, Chicago, Dallas, and Atlanta. Social media is flooded with complaints from frustrated customers, many unable to connect with loved ones or conduct essential business activities.

The cause of the outage remains unclear. AT&T has yet to officially comment on the issue, leaving users in the dark about the root cause and expected resolution timeframe. This lack of communication is further adding to the frustration of affected customers.

Cyber Attack?

The cause behind the widespread outage affecting AT&T services across the United States remains uncertain, with conflicting reports suggesting it could be either a cyber attack or technical issues. Users across various regions have reported difficulties accessing wireless services, prompting concerns about the extent and nature of the disruption.

AT&T is Aware!

Although some users are reporting on social media that their service has been restored, on X (formerly Twitter), AT&T stated, “Some of our customers are experiencing wireless service interruptions. We are working urgently to restore service to all who are impacted.” It is worth noting that the company also provided a link to visit and keep an eye on updates.

Ironically, that link was also down and showing an error message to visitors. However, according to a live outage map from Down Detector, a platform that monitors internet outages, AT&T is still facing service issues across the United States.

The potential impact of this outage is significant. Disruptions to mobile phone service can hinder communication, impact emergency services for some, and cause inconvenience for countless individuals and businesses relying on their mobile devices for daily activities.
AT&T Outage Disrupts Service for Millions of Users Across US

While AT&T is working to restore service, no estimated time for resolution has been announced. In the meantime, users are advised to:

  • Use Wi-Fi calling: If available, utilize Wi-Fi calling to make and receive calls over a Wi-Fi network.
  • Stay informed: Check the AT&T website and social media for updates on the outage.
  • Consider alternative communication methods: Explore options like text messaging apps or social media to connect with others if unable to use your phone.

This latest outage highlights the critical role of reliable mobile phone service in today’s interconnected world. It also underscores the importance of clear and timely communication from service providers during such disruptions to minimize inconvenience and ensure user safety.

As the situation unfolds, we will continue to monitor developments and provide updates on this evolving story.

  1. ChatGPT Down? OpenAI Blames Outages on DDoS Attacks
  2. Amazon Web Services suffer outage taking popular sites down
  3. Facebook down with Messenger, Instagram, WhatsApp disruption

[ad_2]
Source link

Motorola Edge 50 Pro name confirmed, multiple certifications acquired

0
[ad_1]

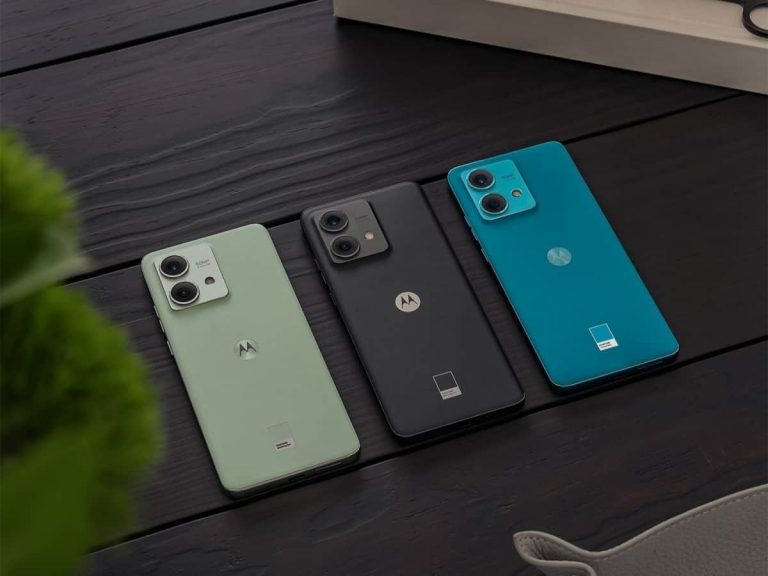
A new Motorola phone is reportedly in the works as it has bagged multiple certifications. It is speculated to be the Motorola Edge 50 Pro. The upcoming offering has been spotted on BIS, FCC, IMEI and TDRA certification websites. The listings also hint at the imminent arrival of the device. We also get to learn some key specifications of the Edge 50 Pro.

Motorola Edge 50 Pro spotted on multiple certification websites

The Motorola Edge 50 Pro is listed on certification sites with multiple model numbers. These include XT2403-1, XT2403-2, XT2403-4, and XT2403-5 on the FCC. The XT2403-1 is a physical SIM variant whereas the XT2403-2 is an e-SIM version. Both have also appeared on BIS and IMEI databases respectively. In fact, the IMEI listing mentions the codename ‘Macan’. This is in line with tipster Evan Blass previously revealing that it corresponds to the Motorola Edge 50 Pro.

Additionally, the Motorola Edge 50 Pro also passed the TDRA certitication in UAE with one of the aforementioned model numbers. It confirms the phone’s moniker as well.

91Mobiles also reports that Motorola has registered the battery and charging details of the Edge 50 Pro on the TUV Rheinland certification website. It includes a 50W wireless charger with model number MW-02, a wired charger up to 120W with model numbers MC-1250 to MC-1258, and a 4,500mAh battery (model number QM45) on the TUV Rheinland website.

The Motorola Edge 50 Pro could be flagship phone arriving soon

Motorola is yet to launch a flagship phone powered by the latest Snapdragon 8 Gen 3 that was announced in October last year. However, the wait is expected to end soon as a leak last month revealed that the Lenovo-owned brand could launch a premium device in Q2, 2024. The company’s flagships are introduced under the X-series in China. These make their way to global markets as rebranded Edge phones. This solidifies the possibility that the upcoming offering could indeed be the Edge 50 Pro.

So far, Motorola has only launched some G-series phones including the G24, G04, and G Play (2024) in multiple global markets.


[ad_2]
Source link

Google spreads Help me write across all of Chrome

0
[ad_1]

We’re fast approaching a world where no one has to type anything. Generative AI can basically type up anything you need with just a little bit of context provided by you. After announcing some great generative AI features, Google is now distributing Help me write across all of Chrome. This feature is currently rolling out, so there’s a chance that you will be able to experience it if you live in the US.

What is Help me write?

Think of Help me write as your personal typing assistant. If you need to jot something down, but you can’t quite find the words, you can use the Help me write feature to help you out. For instance, if you are in Gmail, and you need to write an email to a client requesting a product to review, you can use the Help me write feature to generate the email for you in whatever tone you want.

Currently, Help me write  is available in Google Docs and Gmail. So, if you need assistance writing documents or emails, then Help me write is perfect for you. In order to access this feature, simply look for the little pencil icon on the left side of your document.

Help me write location

Help me write is now available across Chrome

A while back, we got the news that Google wanted to distribute Help me write across all of Chrome. This will put the generative AI power in your hands no matter what website you’re using. Well, in version M112 of Google Chrome, this functionality is finally making it to users.

In order to enable it, click on the three-dot menu at the top-right of your screen, go to your settings, and click on the Experimental AI page on the left side of the screen. There, you’ll have the option to enable Help me write.

Once you enable it, all you have to do is go to whatever text field you want to write in, right-click, and select the Help me write feature. This feature will use context awareness to scan the page and learn what you’re trying to write about.

For instance, if you’re writing a review about a product, Help me write will be able to scan the page to learn what product you’re writing about. Then, it will construct a review for you. However, you will have to tell the feature your thoughts and opinions on the product, so that it could turn that into a full review. What’s neat is that you could use this in Chrome on Mac computers as well as Windows computers.

If you’ve used AI text generators, then you should be familiar with how this feature works. You will describe what you want it to write including what sort of tone you want, how long you want to be, Etc.

Updating Chrome

If you don’t see this feature yet, you’ll have to make sure that your version of Chrome is on the latest update. Click on the three-dot menu, and go all the way down to the Help button.

You will see another drop-down menu pop up showing the About Google Chrome button. When you click on that, you will see the version of Google Chrome you have installed. If it’s under M122, you will see the browser start to update.


[ad_2]
Source link

Google pauses Gemini’s AI image generation of people after inaccuracy backlash

0
[ad_1]

Google’s Gemini AI chatbot has temporarily suspended its ability to generate images of people. This move comes after backlash regarding the AI’s tendency to skew image generation of people towards darker skin tones, especially when it pertains to historical context.

Initially, realizing that the problem was more impactful than originally thought, Google promised to fix the issues via a social media post. However, the situation appears to have escalated, leading to a temporary but complete shutdown of this particular feature on Gemini’s website.

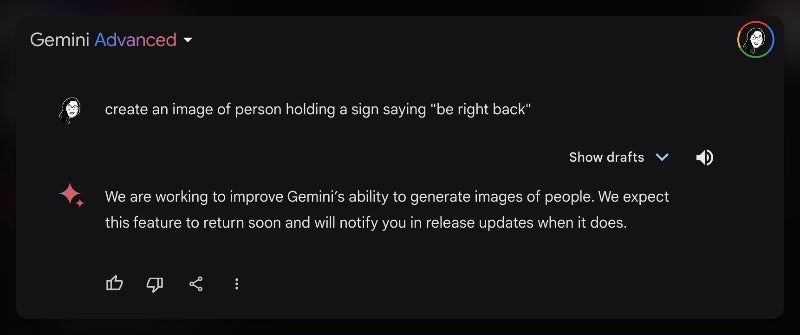
Since Gemini is now unable to generate images including people, when prompted the chatbot displays a placeholder message instead that reads: “We are working to improve Gemini’s ability to generate images of people. We expect this feature to return soon and will notify you in release updates when it does.” This message was also shared by Google in the above social media post, promising that a fixed version would be coming soon.

Gemini’s current error message when trying to generate an image that includes a human

The problem of less diverse results within AI image generation isn’t unique to Gemini. Existing AI models happen to also grapple with this, and Google’s efforts likely over-focused on addressing this known challenge but unfortunately overshot it. While well-intentioned, the results misrepresented history, which can be very concerning considering these tools are used daily for researching. 

While we wait for Google to follow up with an update on this issue via their Gemini release updates hub, users in need of AI generated images involving humans will have to rely on alternative platforms.


[ad_2]
Source link

UOB, Samsung Back Singapore’s Startale Labs in $7 Million Web3 Push

0
[ad_1]

Startale Labs, the developer behind Japan’s leading Web3 products like Astar Network and Startale Web3 Cloud, has secured an additional $3.5 million in funding. This brings their total seed funding to $7 million, following a previous investment from Sony Network Communications in September 2023.

The latest round saw participation from UOB Venture Management, a subsidiary of Singapore’s top bank UOB, and Samsung Next, the investment arm of Samsung. This strategic investment from leading Asian companies positions Startale to become a key player in the region’s Web3 domain.

Startale aims to utilize the fresh capital to accelerate the development of its Web3 products and attract top talent from around the globe. Their vision is to become the leading Web3 company in Asia, leveraging the support of prominent Asian corporations.

It is worth noting that the company has already made significant strides, collaborating with Sony Network Communications on a joint blockchain venture and launching the beta version of Startale Web3 Cloud, a developer-friendly platform for deploying and managing blockchain infrastructure.

Sota Watanabe, CEO of Startale Labs, expressed his enthusiasm, stating, “Within a year, Startale has garnered support from leading Asian companies like Sony, Samsung, and UOB Venture Management, significantly expanding our potential. The raised funds will be directed towards product development and talent acquisition, allowing us to establish ourselves as a prominent Web3 force in Asia and beyond.”

Lead investor Paul Ng, Executive Director of UOB Venture Management, shared his belief in Startale’s potential, stating, “We believe real-world applications are key to onboarding new users to Web3. Startale Labs, with their expertise and experience, is well-positioned to make Web3 accessible to the masses, particularly in Asia. We are excited to support them in bringing billions of users into the Web3 space.”

This successful funding round signals the increasing adoption of Web3 and growing trust within the Asian Web3 community.

  1. Nexo Teams Up with Sift for Enhanced Digital Security
  2. GAM3S.GG Raises $2M to Grow Web3 Gaming Superapp
  3. Particle Network: Securing Web3 with Intent-Centric Approach
  4. Overworld secures $10M for cross-platform ARPG development
  5. READYgg Partners with Aptos Labs – 15M Web2 Players into Web3

[ad_2]
Source link

Why ransomware gangs love using RMM tools—and how to stop them

0
[ad_1]

One of the most alarming trends our ThreatDown Intelligence team has noticed lately is the increased exploitation of legitimate Remote Monitoring and Management (RMM) tools by ransomware gangs in their attacks.

RMM software, such as AnyDesk, Atera, and Splashtop, are essential for IT administrators to remotely access and manage devices within their networks. Unfortunately, ransomware gangs can also exploit these tools to penetrate company networks and exfiltrate data, effectively allowing them to “live off the land”.

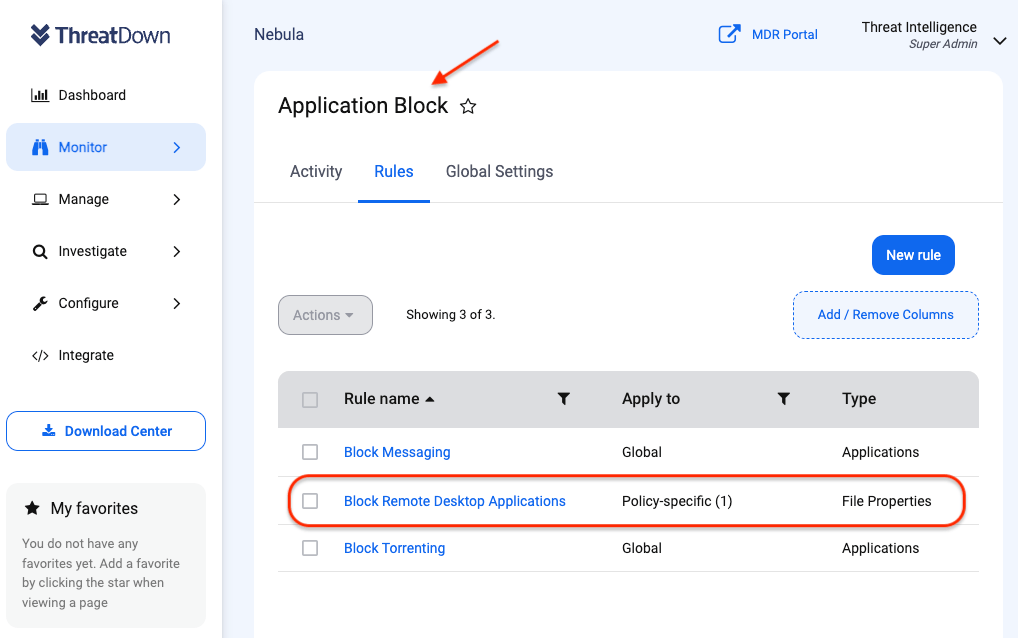
In this post, we will delve into how ransomware gangs use RMM tools, identify the most exploited RMM tools, and discuss how to detect and prevent suspicious RMM tool activity using Application Block and Endpoint Detection and Response (EDR).

How ransomware gangs utilize RMM tools

Ransomware gangs exploit Remote Monitoring and Management (RMM) tools through one of three main strategies:

  1. Gaining initial access via preexisting RMM tools: As RMM tools typically require credentials for system access, attackers can exploit weak or default RMM credentials and vulnerabilities to gain unauthorized access to a network.
  2. Installing RMM tools post-infection: Once inside a network, ransomware attackers can install their own RMM tools to maintain access and control, setting the stage for a ransomware attack. For example, the ThreatDown Intelligence team noted a case where ransomware attackers exploited an unpatched VMWare Horizon server to install Atera.
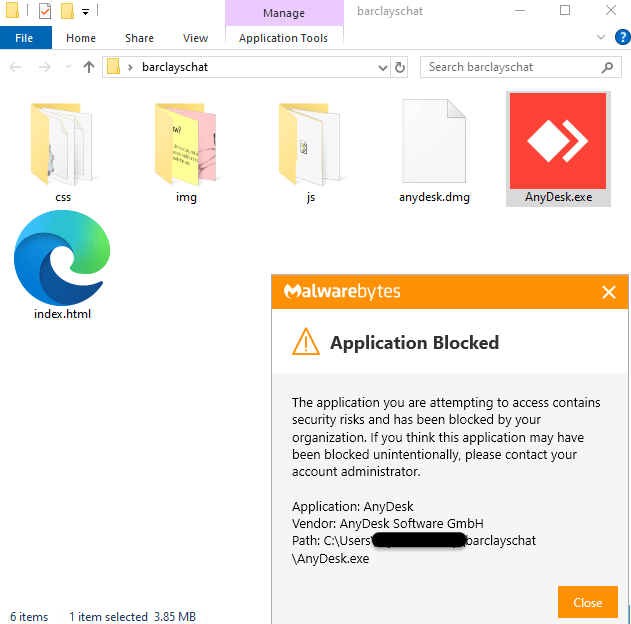
  3. Hybrid approach: Attackers can use a slew of different social engineering scams, such as technical support scams or malvertising, to trick employees into installing RMM tools onto their own machines, enabling both initial access and a mechanism for ransomware deployment. The Barclays banking scam we wrote about in February 2024 is an example of this approach.

Top RMM tools exploited by ransomware gangs

The following RMM tools are commonly used by both ransomware gangs to oversee and control IT infrastructure remotely.

  • Splashtop: A remote access and support solution tailored for businesses, MSPs, and educational institutions. Exploited by the ransomware gangs CACTUS, BianLian, ALPHV, Lockbit.
  • Atera: An integrated RMM tool for MSPs that offers remote access, monitoring, and management. Exploited by Royal, BianLian, ALPHV.
  • TeamViewer: A software for remote access and support. Exploited by BianLian.
  • ConnectWise: A suite that includes solutions for remote support, management, and monitoring. Exploited by Medusa.
  • LogMeIn: Provides secure remote access to computers from any location for IT management and support. Exploited by Royal.
  • SuperOps: An MSP platform that combines RMM, PSA, and other IT management features. Exploited by CACTUS.

Nearly all of the ten ransomware gangs have included one of the above RMM tools in their attacks.

Preventing RMM ransomware attacks with Application Block and EDR

To prevent ransomware gangs from misusing RMM tools, businesses can adopt two strategies: blocking unnecessary RMM tools using application blocking software and utilizing EDR to detect suspicious RMM tool activity.

For instance, by employing applications like ThreatDown’s Application Block, businesses can prevent the use of non-essential RMM applications.

For necessary tools, such as AnyDesk, the EDR/MDR layers within ThreatDown Bundles can offer an additional layer of protection in case of an infection.

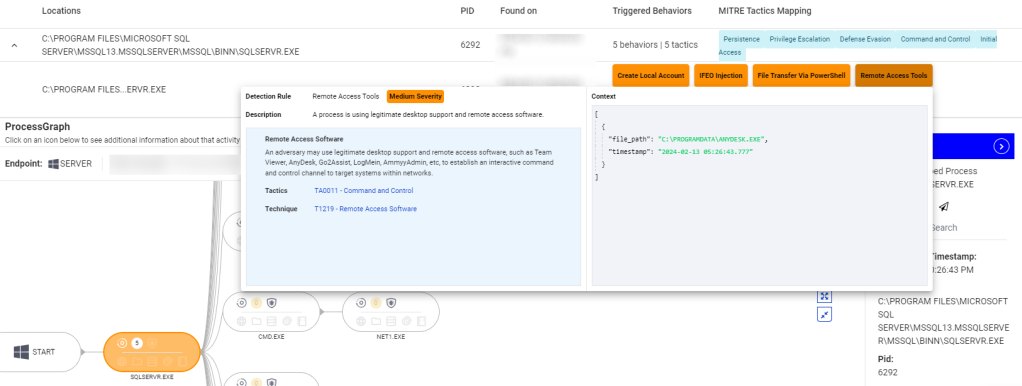
Consider a real example where ransomware attackers used AnyDesk to establish a Command and Control (C&C) server. In one case, a threat actor infiltrated a customers environment by exploiting an unpatched server with open ports exposed to the internet. AnyDesk was installed by the threat actor afterward, as indicated in the EDR alert below. Such activity is typical of what our Threat Intel teams observe just before the widespread encryption carried out in ransomware attacks.

EDR detecting malicious RMM tool usage, with relevant MITRE techniques

After investigating the alert, however, a customer can quickly isolate the affected endpoint to prevent encryption. Alternatively, the ThreatDown MDR service can identify the alert and offer guidance on remediation.

Stop ransomware RMM attacks today

Much like other Living Off the Land tools designed to facilitate IT administration, RMM tools are now double-edged swords.

Whether using RMM tools for initial access, post-infection ransomware deployment, or a combination of the two, ransomware attackers are upping the sophistication of their attacks. However, with ThreatDown, organizations can effectively curtail the abuse of RMM tools through technologies like Application Block and EDR.

Discover the difference with ThreatDown Bundles and elevate your organization’s defense against cyber threats. Get in touch for a free trial and experience the benefits of a simplified, yet robust, security framework.


[ad_2]
Source link

This is the Nothing Phone (2a) launching on March 5!

0
[ad_1]

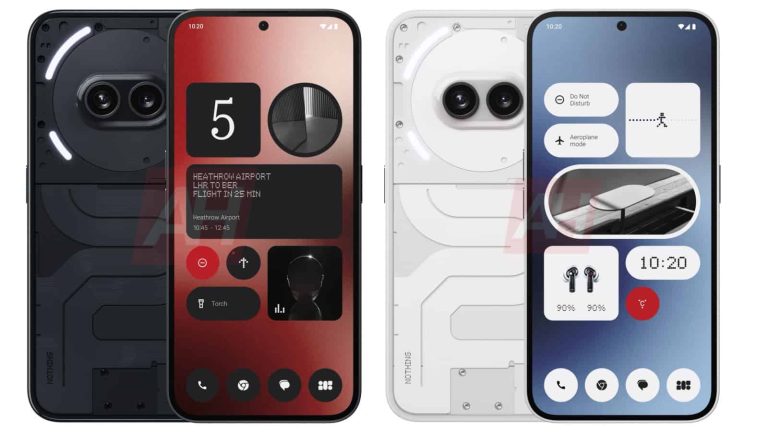
Nothing is set to unveil its latest smartphone, the Nothing Phone (2a), on March 5. The device is expected to be less expensive than the company’s high-end Nothing Phone (2). However, you don’t have to wait until March 5 to catch a glimpse of the device. We have it right here for you to see.

Nothing Phone (2a) will be available in both black and white. It will be a plastic build this time versus the metal and glass build of the Phone (2). Of course, that’s one of a few ways that Nothing can offer this device at a lower price. While Nothing has been confirmed as a price yet, we have learned quite a few aspects of this phone from the company.

Nothing has confirmed that Phone (2a) will run on the MediaTek Dimensity 7200 Pro chipset with 12GB of RAM and a +8GB RAM Booster. Typically, the RAM Booster will come from the storage on the phone. Nothing says that they co-engineered this chipset for Phone (2a) which likely means we won’t see this chipset used on any other devices.

As for other specs, many are expecting to see at least 128GB of storage on board and a 5,000mAh capacity battery, though those two specs have not been confirmed by Nothing just yet.

These do look very similar to the renders Onleaks released a few days ago. Those are based on CADs, so they aren’t always 100% accurate, but they are usually pretty close – about 95% accurate, I’d say. These renders are directly from Nothing, so they are accurate, the only changes we might see are to the home screen.

Nothing Phone (2a) features a less intricate rear design

Compared to the Nothing Phone (2), the Phone (2a) has a less intricate design, at least on the rear. We can also see from these renders that the Phone (2a) won’t feature wireless charging. That’s a bit of a bummer since other “cheaper” phones, like the Pixel 7a, do support wireless charging.

Nothing also uses fewer Glyph modules on the Phone (2a) than the Phone (2), which had 11 glyphs. The Phone (2a) will have only three, which are all around the camera module.

The rear also appears to be in two parts, with the bottom portion looking like a cover and not showing components like the higher-end Nothing Phone (2).

There’s still a camera bump on the back, however with the cameras being centered, that should help avoid any wobbling while on a table. Additionally, with the cameras being centered, your fingers shouldn’t cover them when using them in the landscape for photos and video.

Nothing has been touting that they will announce the Phone (2a) at an online event on March 5. That’s just under two weeks away. So we’ll find out soon whether this is the real deal.


[ad_2]
Source link

Google paused Gemini’s ability to generate images of people

0
[ad_1]

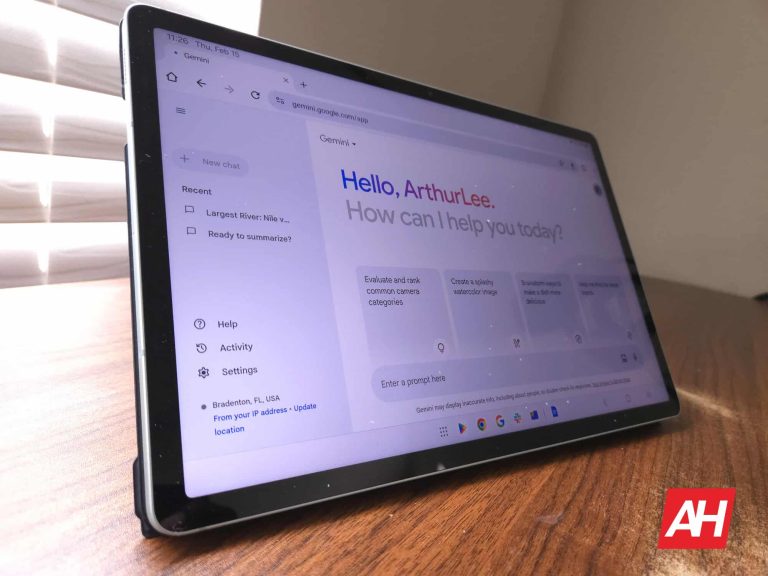
It seems like, from the get-go, Google has been having big issues with all of its generative AI products. These require the company to go back and fix them. In the case of Gemini, Google paused image generation of people because it “missed the mark” when it comes to race and gender depiction.

Not too long ago, Google gave Bard the ability to generate images along with text. That functionality remained during the switch over to Gemini. You’re able to ask Gemini to generate images of pretty much anything. However, people are finding that generating images of people, who would historically be Caucasian or male, are resulting in images of people of color and females.

One person asked Gemini to generate an image of founding fathers, but it generated images of people of Asian descent. The founding father’s image also depicted the two people as being extremely modern with casual t-shirts, business-casual buttoned-up shirts, and no powdered wigs (you can’t forget the wigs, Google!). This is just one example.

Google paused image generation of people for Gemini because it missed the mark

The company posted a statement saying that it’s “aware that Gemini is offering inaccuracies in some historical image generation depictions.” It’s currently working on improving this and delivering accurate depictions of historical figures.

For the time being, this generation of people has been suspended. If you try to generate an image of a person, you’ll get a message saying “We are working to improve Gemini’s ability to generate images of people. We expect this feature to return soon and will notify you in release updates when it does.”

It appears that Google wanted a more inclusive generative AI experience by allowing more people with different skin tones and genders to be generated. The company gets points for that, as many image generators tend to favor generating Caucasian folks whenever asked to create a human being.

However, the company seems to have overshot it and missed the mark. We’re not quite sure when the ability to generate images of people will return. However, it should hopefully be soon.


[ad_2]
Source link

US to Pay $15 Million for Lockbit Ransomware Operator Data

0
[ad_1]

In a significant move against cybercrime, the U.S. government has announced a bounty of up to $15 million for information that could lead to the identification, arrest, or conviction of individuals associated with the notorious LockBit ransomware group.

This announcement comes as part of a broader crackdown on ransomware operations that have caused extensive damage to numerous organizations worldwide.

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Background on LockBit

LockBit is a ransomware-as-a-service (RaaS) operation, which means its developers create ransomware software that affiliates then deploy against victims.

The group has been responsible for high-profile cyberattacks, including those on chipmaker TSMC, consulting firm Accenture, and a Foxconn subsidiary.

LockBit Ransomware Operator Data
LockBit Ransomware Operator Data (Image Source: U.S. Department of State)

In 2022, LockBit was identified as the most deployed ransomware variant globally by the U.S. Cybersecurity and Infrastructure Security Agency (CISA).

Law Enforcement Actions

Recently, international law enforcement agencies, including Europol and the U.K.’s National Crime Agency, have seized LockBit’s dark website, replacing it with a notice of control by authorities.

This operation, known as “Operation Cronos,” involved the FBI and other law enforcement organizations from Australia, Japan, and Europe.

The takedown of LockBit’s operations is considered a significant victory in the fight against ransomware.

The U.S. Department of State’s Rewards for Justice program is offering the bounty, which includes $10 million for information on key leaders of the LockBit group and an additional $5 million for information leading to the arrest or conviction of anyone conspiring or attempting to participate in LockBit’s ransomware attacks.

Ransomware attacks have become increasingly prevalent, with payments to attackers exceeding $1 billion in 2023.

LockBit, in particular, has been one of the most active groups, with its ransomware variant targeting over 2,000 victims and receiving more than $120 million in ransom payments.

The Challenge Ahead

Despite the recent law enforcement success, the adaptability of ransomware gangs poses a continuous challenge.

LockBit’s operators are believed to be based in Russia, complicating efforts for arrest due to geopolitical tensions.

However, the U.S. government’s substantial reward offer underscores the seriousness with which it is pursuing these cyber criminals.

The U.S. government’s reward offer marks a critical step in the global effort to combat ransomware.

By incentivizing information that could lead to the dismantling of LockBit, authorities aim to disrupt the ransomware ecosystem and prevent future attacks.

The fight against cybercrime remains a top priority, with the U.S. and its international partners committed to tracking down and prosecuting those responsible for these malicious activities.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Facebook is testing cross-posting with Threads

0
[ad_1]

Threads is the newest addition to the Meta social media app universe, and it’s been regaining a lot of steam since its user base plummeted last year. As a standalone platform, it’s performing well. However, Meta is looking to integrate it with its other siblings. Because of this, Meta is testing cross-posting between Threads and Facebook.

We’ve already seen some integration between Threads and Instagram; this makes sense, seeing as Threads was basically built from Instagram’s code. While scrolling Instagram, it’s not uncommon for you to see featured Threads. This is one thing that definitely helped boost its user base.

Meta is now testing cross-posting between Threads and Facebook

This is something that we saw coming. Facebook is already pretty closely tied to Instagram. You’re about to cross-post between Instagram and Facebook. This eliminates the need to post the same thing twice across the platforms.

Now, it’s Threads’ turn. The social media platform has been crawling back up the rankings as Meta has been adding more features to it. Now, the app has over 130 million monthly active users. So, it’s obvious that Threads is doing something right.

Meta is currently testing the ability to cross-post between Threads and Facebook. Chances are, you won’t see this functionality just yet, as it’s being tested on a limited number of users. For starters, it’s only being tested on the iOS Facebook app. One user, while making a Facebook post, saw the option to also post it to Threads.

Facebook Threads cross posting

At this point, we’re not quite sure when Meta is going to expand this test to other users. However, it seems to be working fine. When the feature does make it to the public, it’ll be a way for more posts to exist on Threads. Not many people like to post the same content on different social media accounts. This will eliminate the need to double-post, and it gives people more opportunities to gain traction on Threads


[ad_2]
Source link