Samsung Galaxy Fit 3 launches and puts an end to leaks

0
[ad_1]

After multiple leaks and rumors in recent times, the Samsung Galaxy Fit 3 is finally official. The wearable fitness device debuted without much fanfare because everything leading up to today’s launch left very little to the imagination. The latest offering arrives nearly four years later as the successor to the Galaxy Fit 2 from 2020. It packs significant upgrades over its predecessor.

Samsung Galaxy Fit 3 arrives officially putting leaks to the bed

The Samsung Galaxy Fit 3 has a rectangular dial with an aluminum chassis and a silicone strap. It is IP68-certified dust and water-resistant up to 50 meters. There is a physical button on the right side. On the display front, the device has a 1.6-inch AMOLED screen that is said to be 45 percent larger than its predecessor. This allows room for viewing more information. The display can be customized with more than 100 watch faces via the Galaxy Wearables app.

In terms of health and fitness, the Samsung Galaxy Fit 3 is equipped with a heart-rate monitor, SpO2 sensor, sleep tracker, and the ability to track stress levels. It is also capable of detecting snoring and offers personalized sleep coaching to help users understand their sleeping patterns and improve it. The Fit 3 packs support for over 100 types of workout modes. Unfortunately, it lacks a built-in GPS, so users will need to carry their smartphones for outdoor activities.

The Galaxy Fit 3 packs additional useful features

The Samsung Galaxy Fit 3 comes with fall detection that lets users call emergency services if needed. The Emergency SOS feature can be triggered by pressing the side button five times if the user finds themself in a emergency situation.

The Galaxy Fit 3 users can also access a host of capabilities with a connected Samsung Galaxy ecosystem. They can sync the Do Not Disturb and Sleep mode on their Galaxy phone with the Galaxy Fit 3. The wearable device also packs convenient features like a remote camera and music control, find my phone, notification display, and more. Samsung says that the Galaxy Fit 3 is compatible with phones running Android 10 or above and having 1.5GB RAM. The latest offering is rated to last up to 13 days under typical usage.

The Samsung Galaxy Fit 3 is offered in Grey, Silver, and Pink Gold color options. It will be available in select markets starting February 23. The pricing has not been revealed yet. As per a recently leaked retail box, the wearable device is reportedly priced at 2,50,000 shillings (~$99) in Tanzania.


[ad_2]
Source link
Leak of China’s Hacking Documentation Stunned Researchers

0
[ad_1]

In a startling revelation that has sent shockwaves through the cybersecurity community, a massive data leak has exposed the inner workings of I-Soon (上海安洵), a Chinese tech security firm with deep ties to the country’s government agencies, including the Ministry of Public Security, Ministry of State Security, and the People’s Liberation Army.

Over the weekend of February 16th, the leak provided an unprecedented glimpse into China’s cyber espionage operations, raising serious questions about global cybersecurity and the extent of state-sponsored hacking activities.

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Unmasking I-Soon: Hacker-for-Hire

I-Soon, known for its contracts with various People’s Republic of China (PRC) agencies, was at the center of a significant security breach when a trove of its internal documents was leaked online.

The leaked documents, which include contracts, marketing presentations, product manuals, and lists of clients and employees, reveal detailed methods used by Chinese authorities to surveil dissidents overseas, hack other nations, and promote pro-Beijing narratives on social media platforms, reads Sentinel Labs report.

The documents also show I-Soon’s involvement in hacking networks across Central and Southeast Asia, as well as Hong Kong and Taiwan, using tools that allow Chinese state agents to unmask users of platforms like X (formerly known as Twitter), break into email accounts, and hide the online activities of overseas agents

This leak offers a rare window into the pervasive state surveillance and cyber operations conducted by Chinese authorities, highlighting the sophisticated nature of China’s cyber espionage ecosystem.

The Impact of the Leak

The leak has stunned researchers and analysts, providing some of the most concrete details seen publicly about the operations of a state-affiliated hacking contractor.

It reveals how government targeting requirements drive a competitive marketplace of independent contractor hackers-for-hire

The documents detail I-Soon’s compromise of at least 14 governments, pro-democracy organizations in Hong Kong, universities, and NATO, showcasing the global reach of China’s cyber espionage efforts

One of the leaked documents lists targeted organizations and the fees earned by hacking them, with data collection from Vietnam’s Ministry of Economy paying out $55,000, among other payouts

This leak not only embarrasses the company but also raises critical questions for the cybersecurity community, offering a unique opportunity to reevaluate past attribution efforts and gain a deeper understanding of the complex Chinese threat landscape.

Investigating the Leak

The source of the leak remains unknown, with speculation ranging from a rival intelligence service, a dissatisfied insider, or even a rival contractor

Chinese authorities are investigating the unauthorized dump of documents, and I-Soon has reportedly held meetings to assess the impact of the leak on its business

The leak’s authenticity, while still under investigation, has been deemed highly credible by cybersecurity firms and analysts who have examined the documents

The leak of I-Soon’s documents marks a significant moment in understanding state-sponsored cyber operations, shedding light on the intricate and often hidden world of cyber espionage.

As researchers and analysts continue to sift through the leaked data, the cybersecurity community is poised to reassess its defense strategies and attribution efforts in the face of a complex and evolving threat landscape.

This incident underscores the critical importance of cybersecurity vigilance and the ongoing challenges posed by state-affiliated hacking operations on a global scale.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Bluzelle’s Curium App Makes Crypto Earning Effortless

0
[ad_1]

Bluzelle, a Singapore-based decentralized storage company, is making it easier than ever to earn cryptocurrency with the launch of Curium, a new Miner Pool app. Curium allows anyone to contribute storage space and security to Bluzelle’s network and earn BLZ tokens in return, all from their computer or mobile device.

Traditionally, running nodes for blockchain projects has been a complex process requiring technical expertise and expensive hardware. Curium eliminates these barriers by offering a user-friendly app that works on any device, regardless of operating system.

The good news is that Bluzelle solves this by making it easy for anyone to install the Curium app on their computers or mobile devices. This app works on any operating system, including Windows, Mac, Linux, Android, or iOS. Once installed, users simply need to provide their Bluzelle wallet address.

Their device then becomes a “just in time” (JIT) storage node service provider, earning BLZ tokens for the fractional times their machine is online. This operation is similar to an Ethereum PoS pooler miner app, where anyone can install the app on their PC and start earning fractional amounts of ETH based on their device’s uptime.

However, it’s worth mentioning that users must remain alert against fake crypto apps created by scammers targeting iOS, Android, and Windows devices. Recently, Apple approved a fake wallet app on the Play Store that stole user data.

Similarly, Microsoft permitted a fake fundraising app that siphoned almost a million dollars from users. Furthermore, Google has been involved in multiple incidents where fake apps led to the theft of users’ funds. Therefore, it is significant to note that the Curium app is expected to be released by the end of 2024.

“The Curium storage node application is one of the core technologies we envisioned when we launched Bluzelle’s white paper over six years ago,” said Neeraj Murarka, co-founder and CTO of Bluzelle. “Now anyone can become part of our decentralized infrastructure network and earn rewards for simply having their device online.”

With Curium, users can contribute to the security and storage of Bluzelle’s network while earning BLZ tokens. This opens up the world of cryptocurrency to a wider audience, making it easier for anyone to participate in the Web3 revolution.

  1. Navigating the new frontier of cryptocurrency futures
  2. What the Bitcoin ETF Approval Mean for the Crypto Market 
  3. Powerloom to Hold First Ever Node Mint on Polygon Network
  4. Exploring the Phenomenal Rise of Ethereum as a Digital Asset
  5. The Anatomy of Trading Bot Scams: Strategies for Secure Investments

[ad_2]
Source link

Google allegedly shipped “around 10 million” Pixel phones in 2023

0
[ad_1]

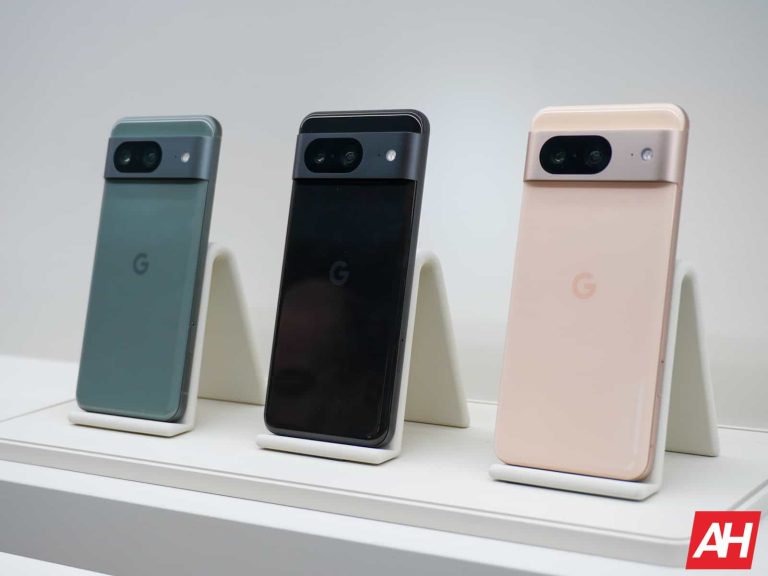
A new report has just surfaced, by Nikkei Asia. In that report, it’s stated that Google shipped “around 10 million” Pixel phones in 2023. Do note that Google doesn’t share such numbers, so these reports are all we can go on.

Google shipped “around 10 million” Pixel phones in 2023

Nikkei Asia’s source also said that Google plans to repeat such an “ambitious goal” in 2024 too. So the company hopes to ship at least 10 million Pixel phones once again.

What we do know is that the Pixel 7 and Pixel 7 Pro units made up a bulk of 2023 shipments for Google. The source did not share a breakdown of sales, which would have been good to know.

We presume that the Pixel 6a and Pixel 7a also managed to squeeze themselves in those numbers, and the Pixel 8 and Pixel 8 Pro too, of course. We don’t believe Google sold many Pixel Folds units, simply due to that price, but… that those phones do make up a small piece of the overall sales numbers too.

First Pixel 8 & Pixel 8 Pro will be manufactured in India this year

Nikke Asia also shared more info about Google’s plan to manufacture the Pixel 8 series in India. This was originally announced back in October last year, actually.

In any case, Google is already making Pixel phones in both China and Vietnam. The company wants to diversify more and improve “supply chain resilience” as a result of that.

Google will manufacture its first Pixel 8 Pro devices in India in Q2 this year (April-June), and the Pixel 8 will follow “around the middle of this year”. The company will kick things off with a “mall volume” of devices, though exact numbers were not shared.

The company plans to do just as good this year, if not better

It will be interesting to see if Google can repeat last year’s feat. 2023 marked Google’s best year ever in terms of Pixel phone sales. That will not be easy to match, let alone outdo, but we’ll see what will happen.

The company is planning to offer some interesting devices, including redesigned Pixel 9 and Pixel 9 Pro, and a much-improved Pixel Fold 2.


[ad_2]
Source link

FDA doesn’t want you to use smartwatches to measure your blood glucose levels

0
[ad_1]

The US Food and Drug Administration (FDA) has recently issued a caution. It was a caution against using smartwatches to test blood glucose levels. Blood glucose levels may not be reliably or accurately measured by smartwatches despite their popularity and convenience. The rationale for the FDA’s caution will be explained in this article.

Why did the US FDA issue this warning?

The warning was released by the US FDA following a test of many smartwatches. The wearables claimed to be able to assess blood glucose levels. However, the FDA discovered that these devices have not received agency clearance or approval for this particular purpose. People with diabetes who depend on precise measures to control their illness adequately must know this information. It may cause major health effects as a result of inaccurate blood glucose readings.

What are the risks of using smartwatches for blood glucose monitoring?

Smartwatches detect blood oxygen levels and heart rate among other health parameters using optical sensors. When assessing blood glucose levels, these sensors might not be entirely exact or accurate. Variations in mobility, temperature, and skin tone can all have an impact on how accurate these measurements are.

How can individuals monitor their blood glucose levels accurately?

It is crucial to use trustworthy and certified testing procedures. To check blood glucose monitoring, diabetics must check their levels often. For precise readings, conventional blood glucose meters need a small blood sample from a finger prick. This procedure is still the gold standard. People with diabetes also frequently utilize continuous glucose monitors (CGMs), which are worn on the body and offer real-time blood glucose readings to successfully keep an eye on their levels.

To sum up, the US FDA’s advisory against measuring blood glucose levels with smartwatches emphasizes the importance of using precise and trustworthy techniques. Smartwatches are convenient and easily accessible, but they might not be the most dependable choice for diabetics who need accurate measurements to control their health properly. To maintain their health and well-being, people must speak with their healthcare professionals and utilize equipment approved to monitor their blood glucose levels.


[ad_2]
Source link

Twitch is raising subscription prices for the first time (in this country, the increase is 343%)

0
[ad_1]

Twitch is raising prices for its channel subscriptions for the first time, per Engadget.

Just over a month ago, Twitch announced that one in three of its employees will have to go in a 35% layoff spree.

In two rounds of job-cutting fiesta, Amazon’s Twitch laid off about a thousand workers in total. By the way, in 2022, Amazon initiated its own workforce reduction, which affected some 27,000 positions across the company, and parallels with the “Red Wedding” episode from “Game of Thrones” were drawn.

Before that, Twitch announced that it was ceasing its operations in Korea (South Korea, not North Korea, duh!) in February 2024.

The Amazon-owned streaming platform says it has been operating at “significant losses” because of high local costs. The company specifically pointed to the high network fees in the country. Korea introduced legislation that would force major content providers to pay to use networks in the country.

Apparently, Twitch has some money problems.

Now, the platform says that “updating prices in several countries” will “help streamer revenue keep pace with rising costs and reflect local currency fluctuations”. The first markets to feel the impact of those changes are the UK, Canada, Australia and Turkey.

As of March 28, Tier 1 subscriptions and gift subs will be more expensive in the UK, Canada and Australia. A base/gift sub is going up from £5 to £6 in the UK, $7 CAD to $8 in Canada and $8 AUD to $9 in Australia. Tier 2 and 3 prices will remain the same in those countries.

In Turkey, Twitch is significantly increasing the price of all three tiers. For instance, a Tier 1 sub will soon cost 43.90 lira ($1.42) instead of 9.90 (32 cents). Don’t be shocked by these figures – the value of the Turkish lira has plummeted over the last decade. However, a 343% jump isn’t funny if you’re the one paying for it.


[ad_2]
Source link

Apex Code Vulnerabilities Let Hackers Steal Salesforce Data

0
[ad_1]

Hackers target Apex code vulnerabilities in Salesforce to exploit security weaknesses, gain unauthorized access to sensitive data, or manipulate the system.

Apex is a powerful language that enables the customization of Salesforce with Java-like syntax. It executes logic, controls transactions, and responds to system events. 

This is primarily used for business logic and is triggered by web services and object events.

Cybersecurity researchers at Varonis Threat Labs recently discovered serious Apex vulnerabilities in multiple Fortune 500 companies and government agencies.

While researchers promptly reported and alerted the affected companies, the vulnerabilities were marked with high and critical severity tags.

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Apex Code Vulnerabilities

The Apex code can be run in two different modes:-

‘Without sharing’ in Apex disregards user permissions, which grants unrestricted access and modification. 

‘With sharing’ respects record-level permissions while overlooking object and field-level restrictions.

Running Apex classes ‘without sharing’ grants powerful capabilities but raises risks. It can lead to insecure data access (IDOR) and vulnerabilities like SOQL injection, Varonis said.

Besides this, the misuse by external users or guests poses data integrity threats. VTL demonstrates exploiting Apex vulnerabilities to access user data without permission. 

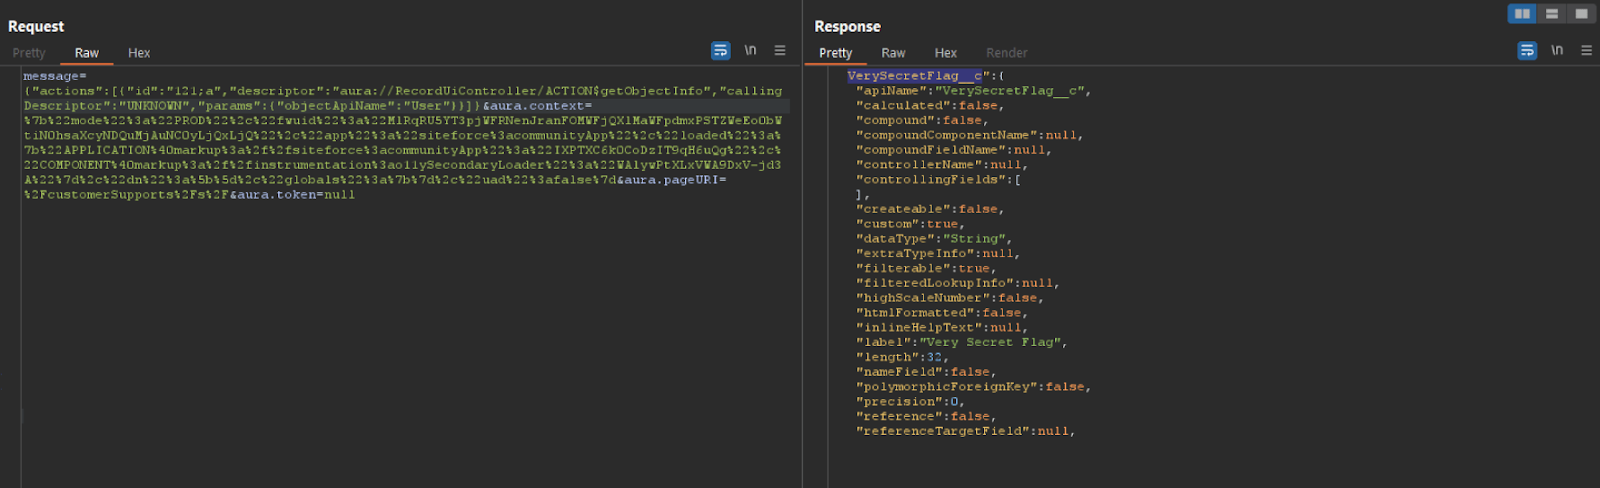
Using a Salesforce environment with real code issues, the instance shows how attackers can abuse aura methods for reconnaissance.

This enables the extraction of sensitive data like phone or social security numbers.

Using the aura method (Source - Varonis)
Using the aura method (Source – Varonis)

Despite a custom field ‘VerySecretFlag__c,’ users can’t access others’ data. Even ‘CreatedBy.VerySecretFlag__c’ fails, and guests also lack access. 

To bypass this, researchers exploited the ‘apex://CaseCreationController/ACTION$createCaseR’ via a custom Apex class, which is callable with Aura, specifying desired field returns.

The case retrieved solely via Apex is inaccessible by other means that hint at ‘without sharing’ mode. To access ‘VerySecretFlag,’ an attacker exploits this by specifying desired fields, like ‘CreatedBy.VerySecretFlag__c,’ via an over-permissive class by accessing data from other objects.

Apex is essential in Salesforce, but reviewing classes, especially ‘without sharing,’ boosts security as manual checks are time-consuming. 

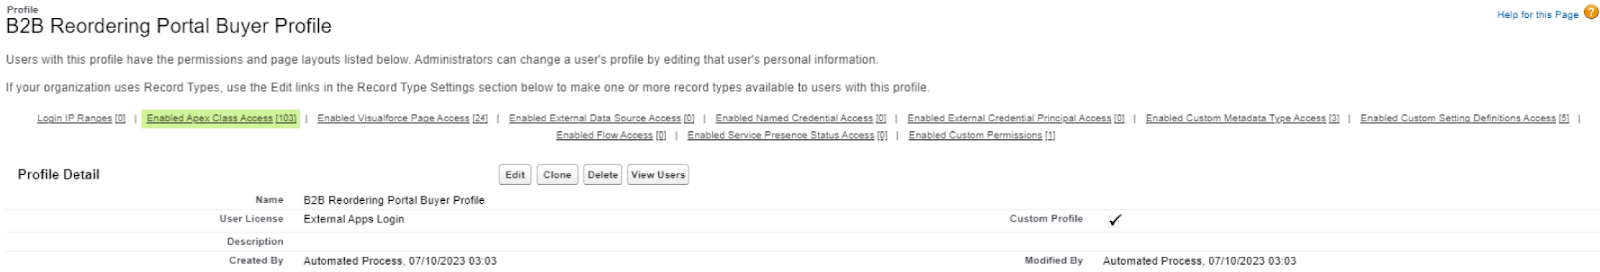
Both the Profiles and Permission Sets need to be examined to determine access. Access setup through Salesforce setup and then navigate to the Profiles. 

Besides this, review each profile’s ‘Enabled Apex Class Access’ section.

Enabled Apex Class Access (Source - Varonis) 
Enabled Apex Class Access (Source – Varonis) 

To verify the access, check Permissions Sets for each entry. Review users assigned to Profiles and Permission Sets. Examine class source code for the ‘without sharing’ declaration. 

With Event Monitoring, track user calls and adjust permissions. Ensure safe coding practices, like using ‘:queryName’ syntax in SOQL to prevent injection.

Moreover, consider adding “WITH SHARING_ENFORCED” to your queries to enforce object- and field-level permissions. Adding “WITH SHARING_ENFORCED” only affects SELECT clauses and not WHERE clauses.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Xiaomi 14 Ultra gets announced with a premium camera setup & much more

0
[ad_1]

The Xiaomi 14 Ultra is now official. Xiaomi announced the phone in its homeland, China, only a couple of days before it arrived to global markets. As a reminder, the Xiaomi 14 Ultra will launch globally on February 25 in Barcelona. That launch will come as part of MWC 2024.

Having said that, the leaks were spot on when it comes to the design of the phone. Some of its specs were also accurately leaked. Just like its predecessor, this phone is heavily focused on the cameras, though it’s premium all around.

The Xiaomi 14 Ultra looks very similar to its predecessor, with two major differences

In terms of the design, it’s quite similar to the Xiaomi 13 Ultra, with two major changes. This device has a flat display, and it doesn’t have different heights in different parts of its backplate. In other words, the height of the phone doesn’t rise gradually towards the camera island, even though the camera island does protrude. More on that soon.

The Xiaomi 14 Ultra is made either out of aluminum and vegan leather, or titanium and glass, it all depends on the variant. Chances are that the titanium variant will stay exclusive to China, though, we’ll see.

In any case, the vegan leather models come in black and white colors, while the ceramic variant is blue-colored. There is also a gray (special edition) titanium model. The Xiaomi 14 Ultra has a flat frame all around, which curves towards the edges, for comfort’s sake.

Xiaomi 14 Ultra image 23


The backplate is mostly flat, but it does curve quite a bit towards the edges. The display has a display camera hole that is centered up top, and even though the display is flat, there are curves towards the edges, where the bezels begin.

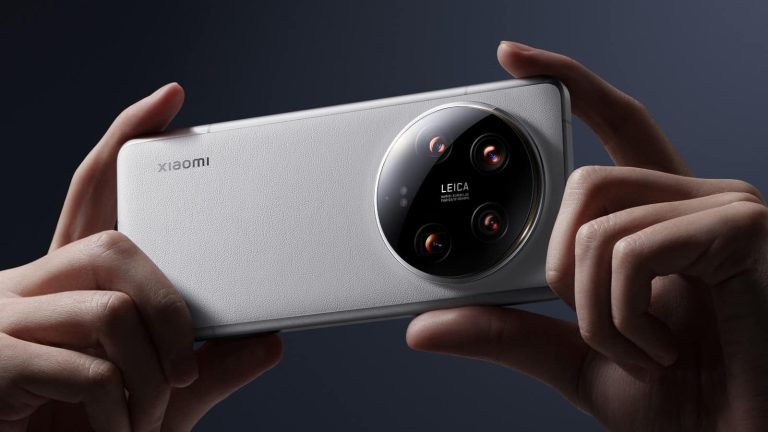
The camera island hosts four 50-megapixel cameras with Leica optics

The camera island does look very similar to the one on the Xiaomi 13 Ultra, especially when it comes to the arrangement of camera sensors inside it. You’ll also notice an easy-to-notice Leica branding in that camera module.

With that out of the way, let’s get down to the specs. The phone features a 6.73-inch QHD+ (3200 x 1440) AMOLED display. This is an LTPO panel, which offers an adaptive refresh rate of 1-120Hz. This panel also supports HDR10+ content and can reach a max theoretical brightness of 3,000 nits.

The Snapdragon 8 Gen 3 fuels this smartphone (an overclocked version), Qualcomm’s most powerful SoC to date. Xiaomi included 12GB or 16GB of LPDDR5X RAM inside of this phone, depending on the variant you choose. The 12GB RAM model comes with 256GB of UFS 4.0 flash storage, while the 16GB RAM variant is available in both 512GB and 1TB of UFS 4.0 flash storage. The titanium model comes with the highest possible combo possible.

There are four 50-megapixel cameras included on the back of this phone, along with Leica optics. The main camera is a 50-megapixel unit with variable aperture. That is Sony’s LYT-900 sensor, and OIS is supported here. The variable aperture goes from f/1.63 to f/4.0 here.

Xiaomi 14 Ultra image 21

Two periscope telephoto cameras are used by Xiaomi

The second camera is a 50-megapixel ultrawide unit with a 12mm focal length and a 122-degree FoV. There are two periscope telephoto units here, both are 50-megapixel ones. The first one utilizes Sony’s IMX858 sensor, and has an f/1.8 aperture, while it offers a 75mm focal length. This camera offers 3.2x optical zoom.

The second periscope telephoto camera also uses Sony’s IMX858 sensor, but it has an f/2.5 aperture and a 120mm focal length. This camera supports 5x optical zoom. On the front, you’ll find a 32-megapixel camera (OmniVision OV32B sensor).

A 5,300mAh battery sits inside the phone, while 90W wired charging is supported here. The phone also supports 80W wireless charging, and reverse wireless charging too. Wi-Fi 7 is also supported, as is Bluetooth 5.4. The device has two nano SIM card slots and an optical in-display fingerprint scanner. Android 14 comes pre-installed, with Xiaomi’s HyperOS included on top of it.

It’s almost as thick as the world’s thinnest book-style foldable

This smartphone comes with an IP68 certification for water and dust resistance. It is 9.2mm thick, not counting the camera bump. So it’s almost as thick as the HONOR Magic V2, which is the thinnest book-style foldable on the market. Do note that a Leica Pro Kit/Case has also been announced, and it will be available globally. It does come with new functionality, and it even adds satellite communication to the phone (at least in China).

The Xiaomi 14 Ultra is 9.2mm thick, and it weighs 224 grams. The Blue ceramic model weighs 229 grams. The pricing for the Xiaomi 14 Ultra, in China, starts at CNY6,499 ($904) for the 12GB RAM model and goes all the way up to CNY8,799 ($1,224) for the titanium model.

Black Xiaomi 14 Ultra:

White Xiaomi 14 Ultra:


[ad_2]
Source link

How to switch back to Google Assistant from Gemini

0
[ad_1]

It seems like everything at Google has been doing in regard to generative AI has been rushed. One example is how Google is hastily replacing Assistant with Gemini. This is the main reason why the Gemini has a low Play Store rating. Well, here’s how to switch back to Google Assistant from Gemini.

The Google Gemini app is a good app, but the company has been trying to switch out Google Assistant for it. This wouldn’t be such a huge issue if Gemini had the same functionalities as Assistant. However, it doesn’t. This is one reason why the Gemini app has a 3.2-star rating on the Google Play Store. this is a huge fall from the 4.2-star rating that it had when it first launched.

How to switch back to Google Assistant from Gemini

There are two ways for you to use Gemini as the default assistant. The first way is by getting the Gemini app. When you do so, it will automatically take over as the assistant. The other way is to summon Google Assistant and opt to try out Gemini as the assistant. This doesn’t really require you to have the Gemini app. In any case, switching back to Google Assistant is easy for both cases.

With the app

If you have the app, open it, and tap on your profile picture at the top right corner. When the little pop-up window appears, tap on the Settings button. At the bottom of the resulting page, you will see a button called Digital assistants from Google.

When you tap on it, you’ll see a page giving you the choice to switch between Google Assistant and Gemini as the default assistant on your phone. Choose Google Assistant. This way, you can have Google Assistant as your default assistant without having to uninstall the Gemini app.

Without the app

If you don’t have to Gemini app, then this just requires a few extra steps. Go to your home screen and summon the Gemini assistant. At the top right corner of the panel, tap on the expand icon (the little box with the arrow).

This will take you to the Google Gemini interface through the Google app. Once you’re in there, the process is the exact same. All you have to do is go to your settings and switch the assistant.


[ad_2]
Source link

Beware of New AsukaStealer Steal Passwords & Desktop Screens

0
[ad_1]

An updated version of the ObserverStealer known as AsukaStealer was observed to be advertised as malware-as-a-service that was capable of collecting data from desktop screenshots, Steam Desktop Authenticator application, FileZilla sessions, Telegram sessions, Discord tokens, browser extensions, and cryptocurrency wallets.

This year, on a Russian-language forum, the threat actor advertised AsukaStealer as a MaaS (Malware-as-a-service), providing an extensive list of features meant to steal confidential data from the targets.

AsukaStealer malware is written in C++ and has flexible options and a web-based control panel. The malware authors or developers used the same C&C infrastructure to host AsukaStealer and ObserverStealer.

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Notable Features of AsukaStealer

Cyble Research & Intelligence Labs (CRIL) discovered a malware-as-a-service (MaaS) known as “AsukaStealer” on February 2, 2024.

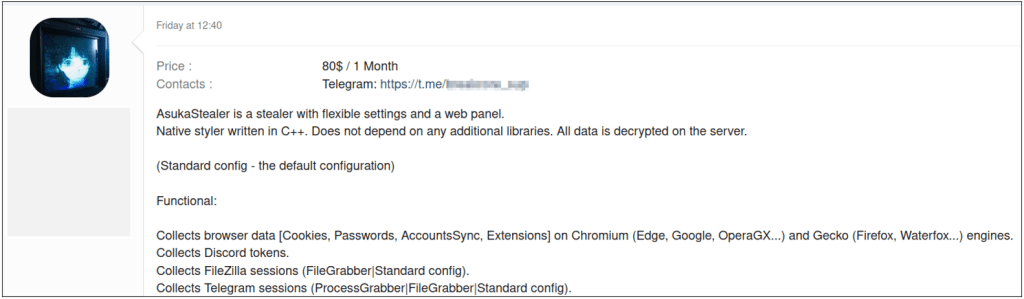
The malware was sold on a Russian-language cybercrime forum, with the web panel version 0.9.7 being offered for USD 80 per month.

On January 24, 2024, the AsukaStealer was marketed on another famous Russian forum under an alternate pseudonym.

Advertisement of AsukaStealer on the forum

The stealer had certain noteworthy features, such as:

Functional features: 

  • The native styler is written in C++ and is 280 kb.
  • Collects browser data (Cookies, Passwords, AccountsSync, Extensions) on Chromium (Edge, Google, OperaGX) and Gecko (Firefox, Waterfox) engines.
  • Collects Discord tokens.
  • Collects FileZilla sessions (FileGrabber|Standard config).
  • Collects Telegram sessions (ProcessGrabber|FileGrabber|Standard config).
  • Builds Steam (Standard config).
  • There is functionality for uploading a file after collecting the log (Loader).
  • Ability to install custom proxies.
  • Ability to send logs to telegram.
  • Collects a screenshot from the desktop.
  • Collecting maFiles from the Steam Desktop Authenticator application (ProcessGrabber|Standard config).
  • An anti-duplicate system.
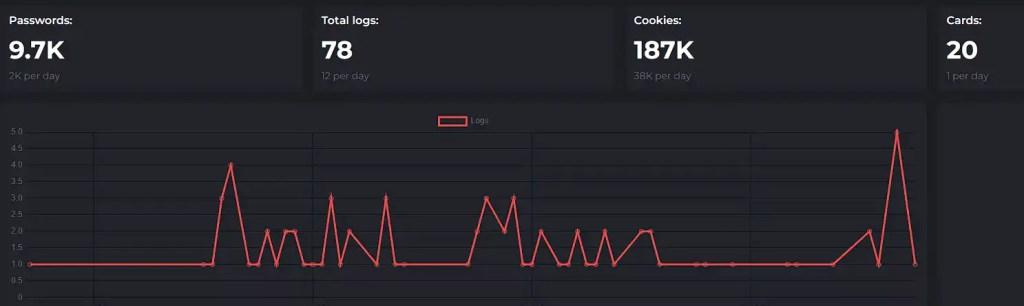
Total information collected by the malware

Configuration setup:

  • Customizable list of browsers [Chromium, Gecko].
  • Customizable FileGrabber/crypto wallet files.
  • Customizable list of extensions.
  • Customizable ProcessGrabber.
  • Customizable Loader.
  • Customizable Discord clients.

Multiple files that were interacting with the IP address “5.42.66.25” were discovered by researchers; VirusTotal had identified and flagged these files as ObserverStealer.

The  AsukaStealer and ObserverStealer’s C&C panels have remarkably similar features.

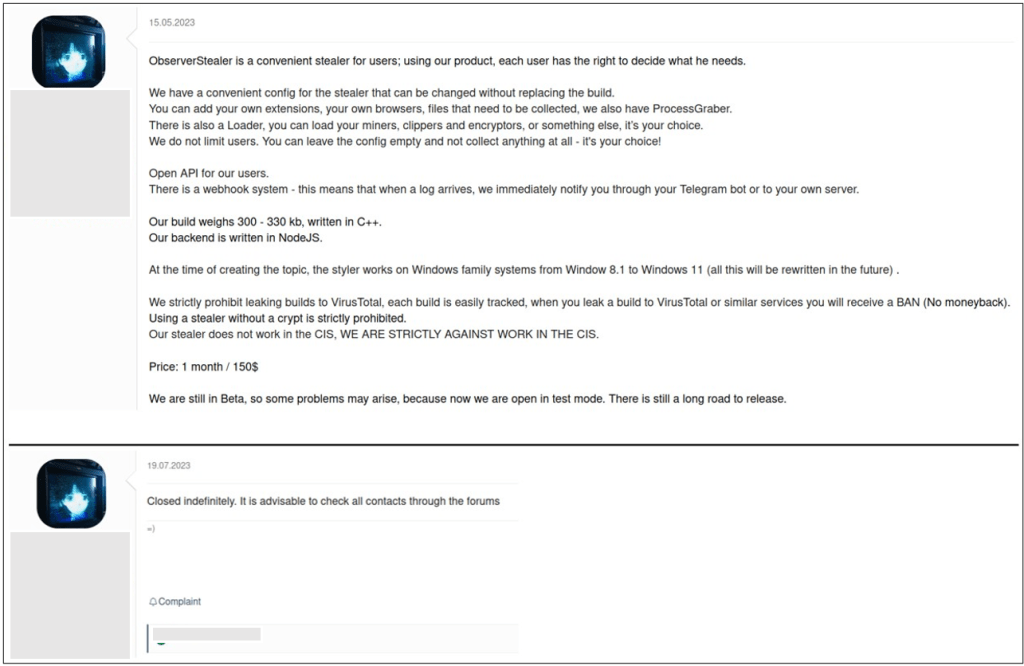
The promoters of AsukaStealer MaaS also announced the termination of MaaS activities for ObserverStealer, which researchers noticed during the study in July 2023.

This suggests that the same threat actors created and managed both stealer malware.

ObserverStealer on offer and announcement of its closure

Notably, this threat was classified by Symantec as File-based (Infostealer Trojan.Gen.MBT), Machine Learning-based (Heur.AdvML.B), and Web-based.

All products with WebPulse enabled covered the observed domains and IPs under security categories.

“Threat actors who are proficient in malware development and capable of hosting a sizable C&C infrastructure, continue to seize opportunities to offer malware-as-a-service (MaaS) to cater to underground communities and make profits within a short period of time”, researchers said.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link